Secure IT-OT Convergence

  • Buy Link or Shortcode: {j2store}382|cart{/j2store}
  • member rating overall impact: 9.0/10 Overall Impact
  • member rating average dollars saved: $10,499 Average $ Saved
  • member rating average days saved: 19 Average Days Saved
  • Parent Category Name: Security Processes & Operations
  • Parent Category Link: /security-processes-and-operations

IT and OT are both very different complex systems. However, significant benefits have driven OT to be converged to IT. This results in IT security leaders, OT leaders and their teams' facing challenges in:

  • Governing and managing IT and OT security and accountabilities.
  • Converging security architecture and controls between IT and OT environments.
  • Compliance with regulations and standards.
  • Metrics for OT security effectiveness and efficiency.

Our Advice

Critical Insight

  • Returning to isolated OT is not beneficial for the organization, therefore IT and OT need to learn to collaborate starting with communication to build trust and to overcome differences between IT and OT. Next, negotiation is needed on components such as governance and management, security controls on OT environments, compliance with regulations and standards, and metrics for OT security.
  • Most OT incidents start with attacks against IT networks and then move laterally into the OT environment. Therefore, converging IT and OT security will help protect the entire organization.
  • OT interfaces with the physical world while IT system concerns more on cyber world. Thus, the two systems have different properties. The challenge is how to create strategic collaboration between IT-OT based on negotiation and this needs top-down support.

Impact and Result

Info-Tech’s approach in preparing for IT/OT convergence in the planning phase is coordination and collaboration of IT and OT to

  • initiate communication to define roles and responsibilities.
  • establish governance and build cross-functional team.
  • identify convergence components and compliance obligations.
  • assess readiness.

Secure IT/OT Convergence Research & Tools

Besides the small introduction, subscribers and consulting clients within this management domain have access to:

1. Secure IT/OT Convergence Storyboard – A step-by-step document that walks you through how to secure IT-OT convergence.

Info-Tech provides a three-phase framework of secure IT/OT convergence, namely Plan, Enhance, and Monitor & Optimize. The essential steps in Plan are to:

  • Initiate communication to define roles and responsibilities.
  • Establish governance and build a cross-functional team.
  • Identify convergence components and compliance obligations.
  • Assess readiness.
    • Secure IT/OT Convergence Storyboard

    2. Secure IT/OT Convergence Requirements Gathering Tool – A tool to map organizational goals to secure IT-OT goals.

    This tool serves as a repository for information about the organization, compliance, and other factors that will influence your IT/OT convergence.

    • Secure IT/OT Convergence Requirements Gathering Tool

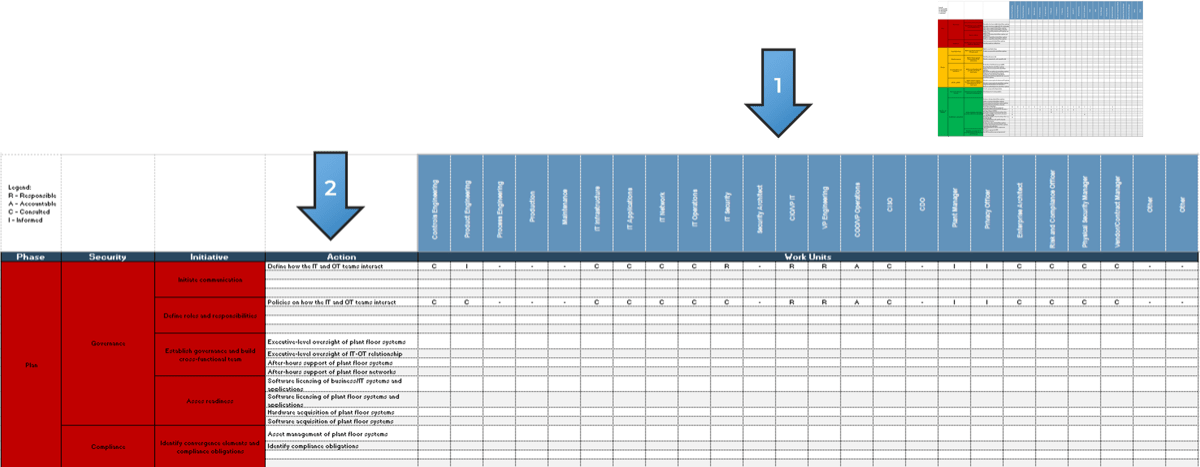
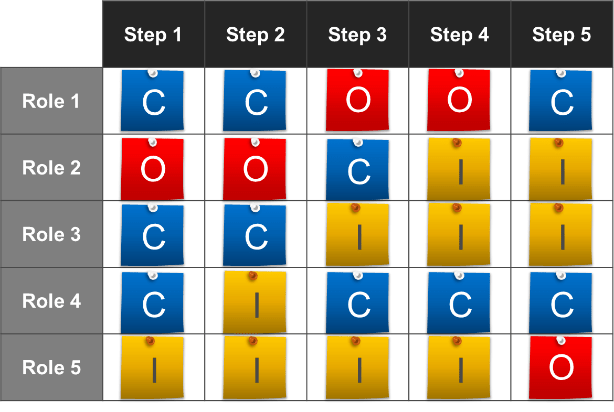
    3. Secure IT/OT Convergence RACI Chart Tool – A tool to identify and understand the owners of various IT/OT convergence across the organization.

    A critical step in secure IT/OT convergence is populating a RACI (Responsible, Accountable, Consulted, and Informed) chart. The chart assists you in organizing roles for carrying out convergence steps and ensures that there are definite roles that different individuals in the organization must have. Complete this tool to assign tasks to suitable roles.

    • Secure IT/OT Convergence RACI Chart Tool
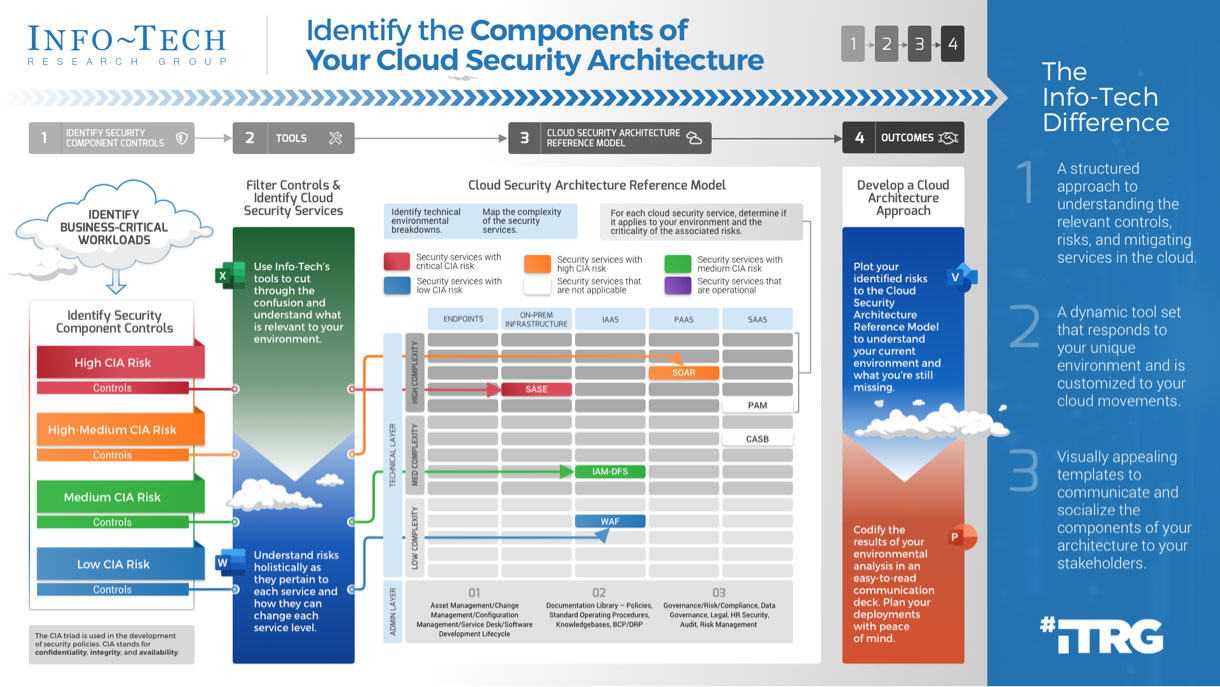
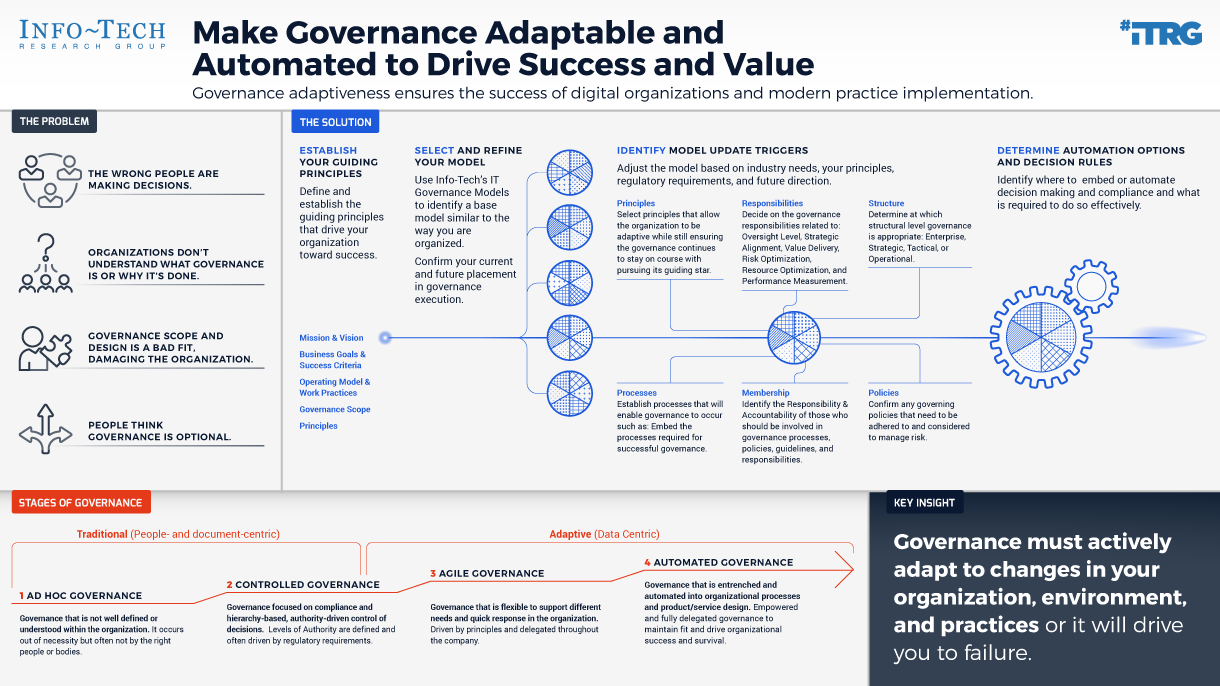
    [infographic]

    Further reading

    Secure IT/OT Convergence

    Create a holistic IT/OT security culture.

    Analyst Perspective

    Are you ready for secure IT/OT convergence?

    IT/OT convergence is less of a convergence and more of a migration. The previously entirely separate OT ecosystem is migrating into the IT ecosystem, primarily to improve access via connectivity and to leverage other standard IT capabilities for economic benefit.

    In the past, OT systems were engineered to be air gapped, relying on physical protection and with little or no security in design, (e.g. OT protocols without confidentiality properties). However, now, OT has become dependent on the IT capabilities of the organization, thus OT inherits IT’s security issues, that is, OT is becoming more vulnerable to attack from outside the system. IT/OT convergence is complex because the culture, policies, and rules of IT are quite foreign to OT processes such as change management, and the culture, policies, and rules of OT are likewise foreign to IT processes.

    A secure IT/OT convergence can be conceived of as a negotiation of a strong treaty between two systems: IT and OT. The essential initial step is to begin with communication between IT and OT, followed by necessary components such as governing and managing OT security priorities and accountabilities, converging security controls between IT and OT environments, assuring compliance with regulations and standards, and establishing metrics for OT security.

    Photo of Ida Siahaan, Research Director, Security and Privacy Practice, Info-Tech Research Group. Ida Siahaan
    Research Director, Security and Privacy Practice
    Info-Tech Research Group

    Executive Summary

    Your Challenge

    IT and OT are both very different complex systems. However, significant benefits have driven OT to converge with IT. This results in IT security leaders, OT leaders, and their teams facing challenges with:

    • Governing and managing IT and OT security and accountabilities.
    • Converging security architecture and controls between IT and OT environments.
    • Compliance with regulations and standards.
    • Metrics for OT security effectiveness and efficiency.
    Common Obstacles
    • IT/OT network segmentation and remote access issues, as most OT incidents indicate that the attackers gained access through the IT network, followed by infiltration into OT networks.
    • OT proprietary devices and unsecure protocols use outdated systems which may be insecure by design.
    • Different requirements of OT and IT security – i.e. IT (confidentiality, integrity, and availability) vs. OT (safety, reliability, and availability).
    Info-Tech’s Approach

    Info-Tech’s approach in preparing for IT/OT convergence (i.e. the Plan phase) is coordination and collaboration of IT and OT to:

    • Initiate communication to define roles and responsibilities.
    • Establish governance and build a cross-functional team.
    • Identify convergence components and compliance obligations.
    • Assess readiness.

    Info-Tech Insight

    Returning to isolated OT is not beneficial for the organization, so IT and OT need to learn to collaborate, starting with communication to build trust and to overcome their differences. Next, negotiation is needed on components such as governance and management, security controls on OT environments, compliance with regulations and standards, and establishing metrics for OT security.

    Consequences of unsecure IT/OT convergence

    OT systems were built with no or little security design

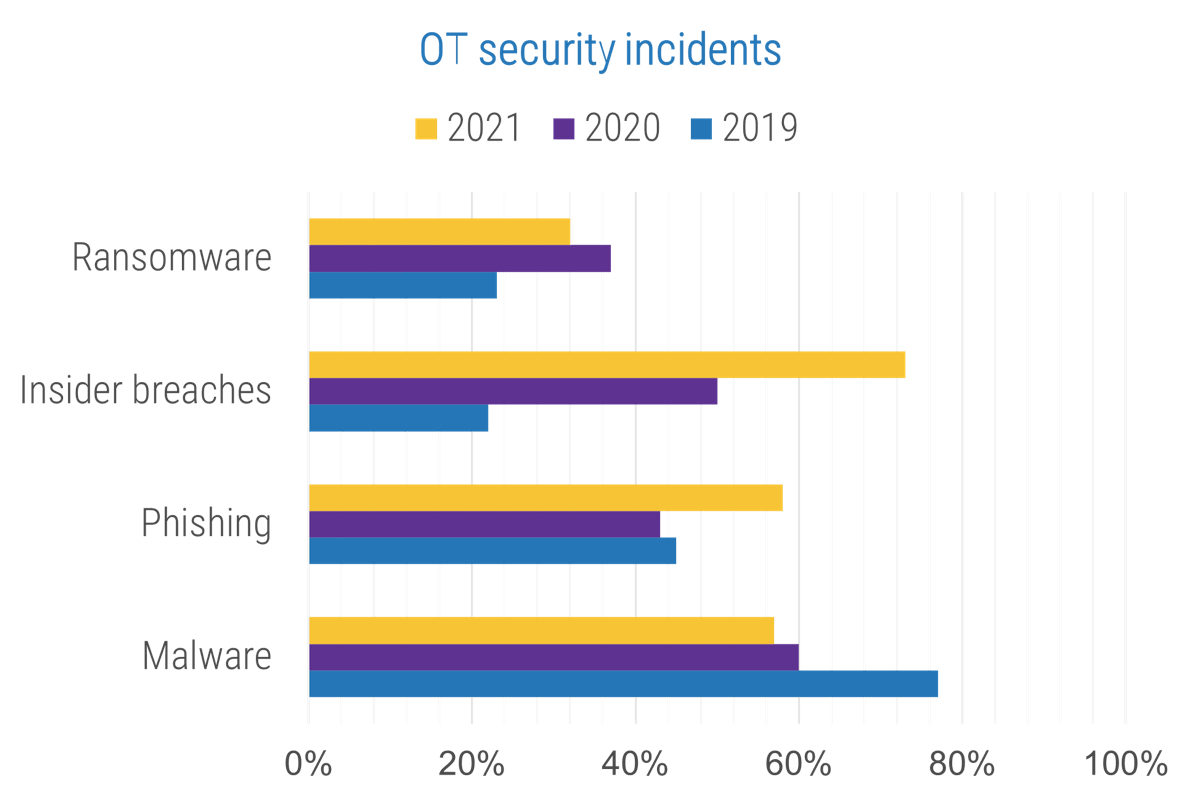
    90% of organizations that use OT experienced a security incident. (Fortinet, 2021. Ponemon, 2019.)

    Bar graph comparing three years, 2019-2021, of four different OT security incidents: 'Ransomeware', 'Insider breaches', 'Phishing', and 'Malware'.
    (Source: Fortinet, 2021.)
    Lack of visibility

    86% of OT security-related service engagements lack complete visibility of OT network in 2021 (90% in 2020, 81% in 2019). (Source: “Cybersecurity Year In Review” Dragos, 2022.)

    The need for secure IT/OT convergence

    Important Industrial Control System (ICS) cyber incidents

    2000
    Target: Australian sewage plant. Method: Insider attack. Impact: 265,000 gallons of untreated sewage released.
    2012
    Target: Middle East energy companies. Method: Shamoon. Impact: Overwritten Windows-based systems files.
    2014
    Target: German Steel Mill. Method: Spear-phishing. Impact: Blast furnace failed to shut down.
    2017
    Target: Middle East safety instrumented system (SIS). Method: TRISIS/TRITON. Impact: Modified SIS ladder logic.
    2022
    Target: Viasat’s KA-SAT network. Method: AcidRain. Impact: Significant loss of communication for the Ukrainian military, which relied on Viasat’s services.
    Timeline of Important Industrial Control System (ICS) cyber incidents.
    1903
    Target: Marconi wireless telegraph presentation. Method: Morse code. Impact: Fake message sent “Rats, rats, rats, rats. There was a young fellow of Italy, Who diddled the public quite prettily.”
    2010
    Target: Iranian uranium enrichment plant. Method: Stuxnet. Impact: Compromised programmable logic controllers (PLCs).
    2013
    Target: ICS supply chain. Method: Havex. Impact: Remote Access Trojan (RAT) collected information and uploaded data to command-and-control (C&C) servers
    2016
    Target: Ukrainian power grid. Method: BlackEnergy. Impact: For 1-6 hours, power outages for 230,000 consumers.
    2021
    Target: Colonial Pipeline. Method: DarkSide ransomware. Impact: Compromised billing infrastructure halted the pipeline operation.

    (Source: US Department of Energy, 2018.


    ”Significant Cyber Incidents,” CSIS, 2022


    MIT Technology Review, 2022.)

    Info-Tech Insight

    Most OT incidents start with attacks against IT networks and then move laterally into the OT environment. Therefore, converging IT and OT security will help protect the entire organization.

    Case Study

    Horizon Power
    Logo for Horizon Power.
    INDUSTRY
    Utilities
    SOURCE
    Interview

    Horizon Power is the regional power provider in Western Australia and stands out as a leader not only in the innovative delivery of sustainable power, but also in digital transformation. Horizon Power is quite mature in distributed energy resource management; moving away from centralized generation to decentralized, community-led generation, which reflects in its maturity in converging IT and OT.

    Horizon Power’s IT/OT convergence journey started over six years ago when advanced metering infrastructure (AMI) was installed across its entire service area – an area covering more than one quarter of the Australian continent.

    In these early days of the journey, the focus was on leveraging matured IT approaches such as adoption of cloud services to the OT environment, rather than converging the two. Many years later, Horizon Power has enabled OT data to be more accessible to derive business benefits such as customer usage data using data analytics with the objective of improving the collection and management of the OT data to improve business performance and decision making.

    The IT/OT convergence meets legislation such as the Australian Energy Sector Cyber Security Framework (AESCSF), which has impacts on the architectural layer of cybersecurity that support delivery of the site services.

    Results

    The lessons learned in converging IT and OT from Horizon Power were:

    • Start with forming relationships to build trust and overcome any divide between IT and OT.
    • Collaborate with IT and OT teams to successfully implement solutions, such as vulnerability management and discovery tools for OT assets.
    • Switch the focus from confidentiality and integrity to availability in solutions evaluation
    • Develop training and awareness programs for all levels of the organization.
    • Actively encourage visible sponsorship across management by providing regular updates and consistent messaging.
    • Monitor cybersecurity metrics such as vulnerabilities, mean time to treat vulnerabilities, and intrusion attempts.
    • Manage third-party vendors using a platform which not only performs external monitoring but provides third-party vendors with visibility or potential threats in their organization.

    The Secure IT/OT Convergence Framework

    IT/OT convergence is less of a convergence and more of a migration. The previously entirely separate OT ecosystem is migrating onto the IT ecosystem, to improve access via the internet and to leverage other standard IT capabilities. However, IT and OT are historically very different, and without careful calculation, simply connecting the two systems will result in a problem. Therefore, IT and OT need to learn to live together starting with communication to build trust and to overcome differences between IT and OT.
    Convergence Elements
    • Process convergence
    • Software and data convergence
    • Network and infrastructure convergence
    Target Groups
    • OT leader and teams
    • IT leader and teams
    • Security leader and teams
    Security Components
    • Governance and compliance
    • Security strategy
    • Risk management
    • Security policies
    • IR, DR, BCP
    • Security awareness and training
    • Security architecture and controls

    Plan

    • Initiate communication
    • Define roles and responsibilities
    • Establish governance and build a cross-functional team
    • Identify convergence elements and compliance obligations
    • Assess readiness

    Governance

    Compliance

    Enhance

    • Update security strategy for IT/OT convergence
    • Update risk-management framework for IT/OT convergence
    • Update security policies and procedures for IT/OT convergence
    • Update incident response, disaster recovery, and business continuity plan for IT/OT convergence

    Security strategy

    Risk management

    Security policies and procedures

    IR, DR, and BCP

    Monitor &
    Optimize

    • Implement awareness, induction, and cross-training program
    • Design and deploy converging security architecture and controls
    • Establish and monitor IT/OT security metrics on effectiveness and efficiency
    • Red-team followed by blue-team activity for cross-functional team building

    Awareness and cross-training

    Architecture and controls

    Phases
    Color-coded phases with arrows looping back up from the bottom to top phase.
    • Plan
    • Enhance
    • Monitor & Optimize
    Plan Outcomes
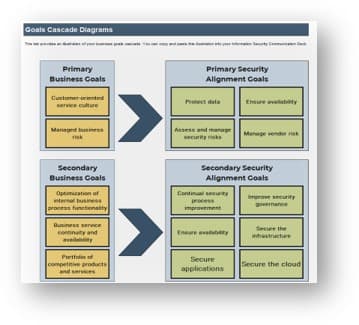
    • Mapping business goals to IT/OT security goals
    • RACI chart for priorities and accountabilities
    • Compliance obligations register
    • Readiness checklist
    Enhance Outcomes
    • Security strategy for IT/OT convergence
    • Risk management framework
    • Security policies & procedures
    • IR, DR, BCP
    Monitor & Optimize Outcomes
    • Security awareness and training
    • Security architecture and controls
    Plan Benefits
    • Improved flexibility and less divided IT/OT
    • Improved compliance
    Enhance Benefits
    • Increased strategic common goals
    • Increased efficiency and versatility
    Monitor & Optimize Benefits
    • Enhanced security
    • Reduced costs

    Plan

    Initiate communication

    To initiate communication between the IT and OT teams, it is important to understand how the two groups are different and to build trust to find a holistic approach which overcomes those differences.
    IT OT
    Remote Access Well-defined access control Usually single-level access control
    Interfaces Human Machine, equipment
    Software ERP, CRM, HRIS, payroll SCADA, DCS
    Hardware Servers, switches, PCs PLC, HMI, sensors, motors
    Networks Ethernet Fieldbus
    Focus Reporting, communication Up-time, precision, safety
    Change management Frequent updates and patches Infrequent updates and patches
    Security Confidentiality, integrity, availability Safety, reliability, availability
    Time requirement Normally not time critical Real time

    Info-Tech Insight

    OT interfaces with the physical world while IT system concerns more on cyber world. Thus, the two systems have different properties. The challenge is how to create strategic collaboration between IT and OT based on negotiation, and this needs top-down support.

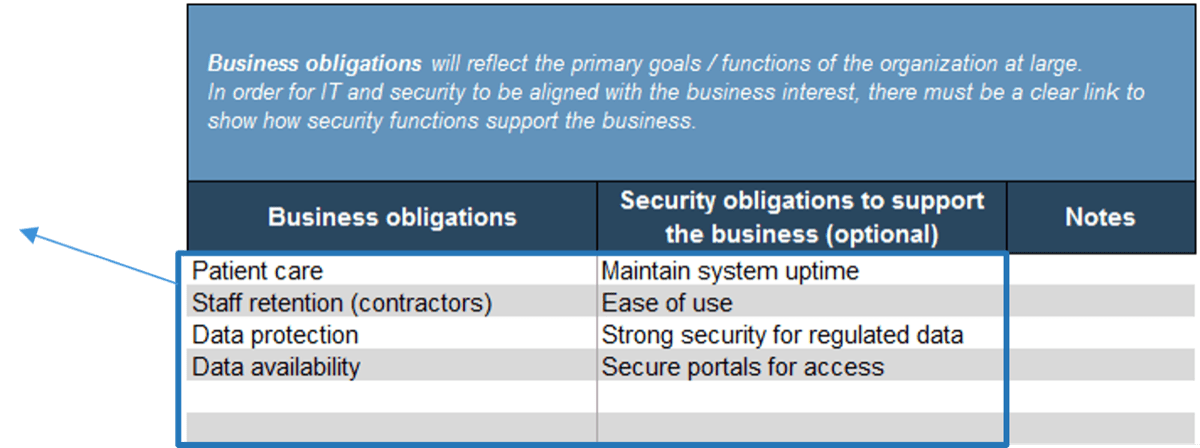
    Identifying organization goals is the first step in aligning your secure IT/OT convergence with your organization’s vision.

    • Security leaders need to understand the direction the organization is headed in.
    • Wise security investments depend on aligning your security initiatives to the organization.
    • Secure IT/OT convergence should contribute to your organization’s objectives by supporting operational performance and ensuring brand protection and shareholder value.

    Map organizational goals to IT/OT security goals

    Input: Corporate, IT, and OT strategies

    Output: Your goals for the security strategy

    Materials: Secure IT/OT Convergence Requirements Gathering Tool

    Participants: Executive leadership, OT leader, IT leader, Security leader, Compliance, Legal, Risk management

    1. As a group, brainstorm organization goals.
      1. Review relevant corporate, IT, and OT strategies.
    2. Record the most important business goals in the Secure IT/OT Convergence Requirements Gathering Tool. Try to limit the number of business goals to no more than 10 goals. This limitation will be critical to helping focus on your secure IT/OT convergence.
    3. For each goal, identify one to two security alignment goals. These should be objectives for the security strategy that will support the identified organization goals.

    Download the Secure IT/OT Convergence Requirements Gathering Tool

    Record organizational goals

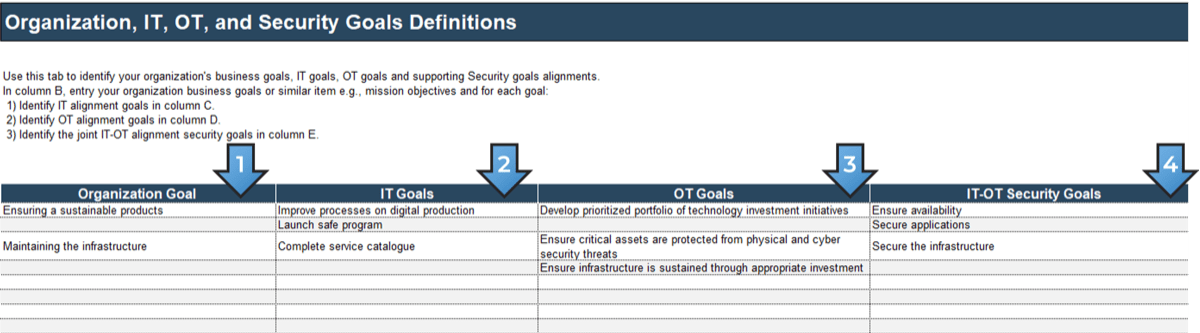
    Sample of the definitions table with columns numbered 1-4.

    Refer to the Secure IT/OT Convergence Framework when filling in the following elements.

    1. Record your identified organization goals in the Goals Cascade tab of the Secure IT/OT Convergence Requirements Gathering Tool.
    2. For each of your organizational goals, identify IT alignment goals.
    3. For each of your organizational goals, identify OT alignment goals.
    4. For each of your organizational goals, select one to two IT/OT security alignment goals from the drop-down lists.

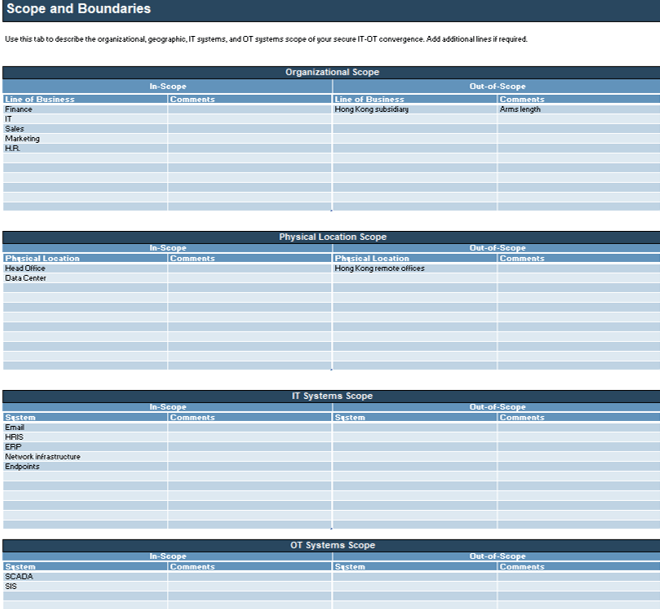
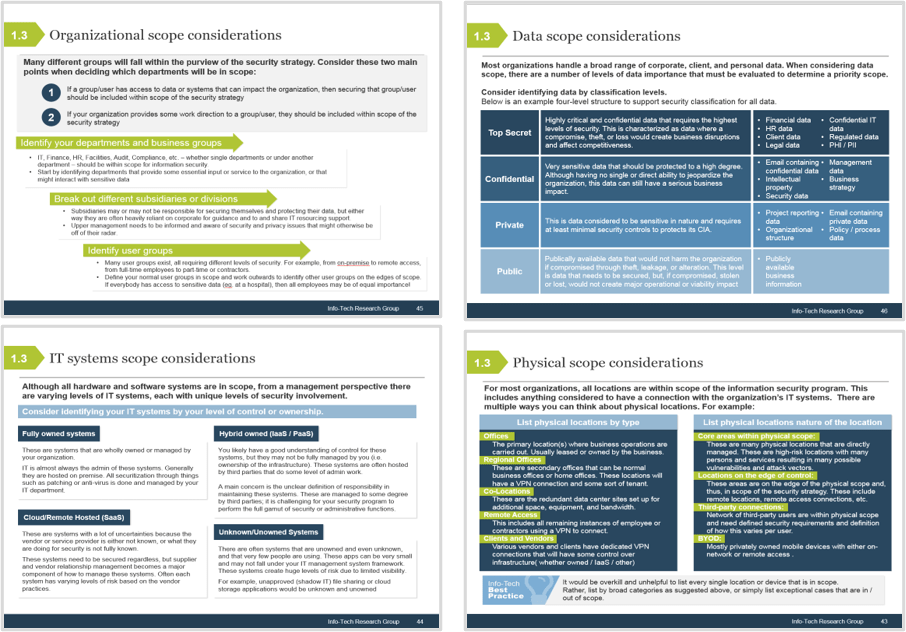
    Establish scope and boundaries

    It is important to know at the outset of the strategy: What are we trying to secure in IT/OT convergence ?
    This includes physical areas we are responsible for, types of data we care about, and departments or IT/OT systems we are responsible for.

    This also includes what is not in scope. For some outsourced services or locations, you may not be responsible for their security. In some business departments, you may not have control of security processes. Ensure that it is made explicit at the outset what will be included and what will be excluded from security considerations.

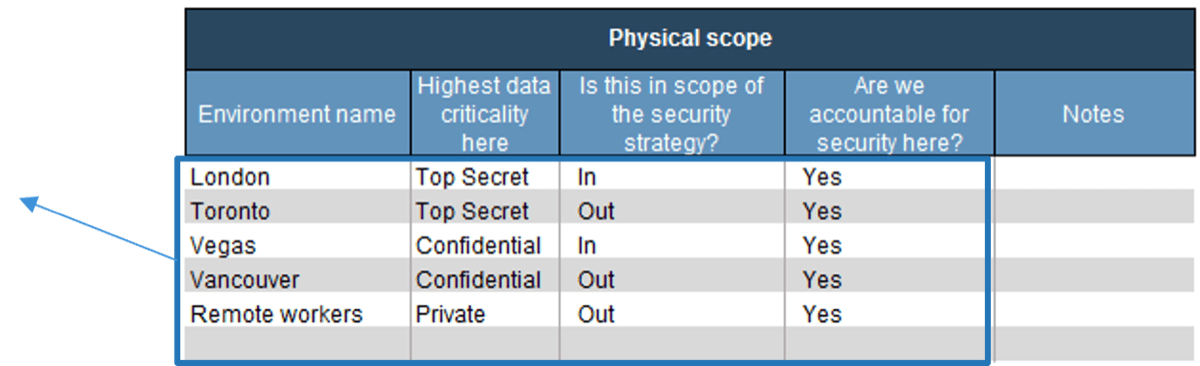
    Physical Scope and Boundaries

    • How many offices and locations does your organization have?
    • Which locations/offices will be covered by your information security management system (ISMS)?
    • How sensitive is the data residing at each location?
    • You may have many physical locations, and it is not necessary to list each one. Rather, list exceptional cases that are specifically in or out of scope.

    IT Systems Scope and Boundaries

    • There may be hundreds of applications that are run and maintained in your organization. Some of these may be legacy applications. Do you need to secure all your programs or only a select few?
    • Is the system owned or outsourced?
    • Where are you accountable for security?
    • How sensitive is the data that each system handles?

    Organizational Scope and Boundaries

    • Will your ISMS cover all departments within your organization? For example, do certain departments (e.g. operations) not need any security coverage?
    • Do you have the ability to make security decisions for each department?
    • Who are the key stakeholders/data owners for each department?

    OT Systems Scope and Boundaries

    • There may be hundreds of OT systems that are run and maintained in your organization. Do you need to secure all OT or a select subset?
    • Is the system owned or outsourced?
    • Where are you accountable for safety and security?
    • What reliability requirements does each system handle?

    Record scope and boundaries

    Sample Scope and Boundaries table. Refer to the Secure IT/OT Convergence Framework when filling in the following elements:
    • Record your security-related organizational scope, physical location scope, IT systems scope, and OT systems scope in the Scope tab of the Secure IT/OT Convergence Requirements Gathering Tool.
    • For each item scoped, give the rationale for including it in the comments column. Careful attention should be paid to any elements that are not in scope.

    Plan

    Define roles and responsibilities

    Input: List of relevant stakeholders

    Output: Roles and responsibilities for the secure IT/OT convergence program

    Materials: Secure IT/OT Convergence RACI Chart Tool

    Participants: Executive leadership, OT leader, IT leader, Security leader

    There are many factors that impact an organization’s level of effectiveness as it relates to IT/OT convergence. How the two groups interact, what skill sets exist, the level of clarity around roles and responsibilities, and the degree of executive support and alignment are only a few. Thus, it is imperative in the planning phase to identify stakeholders who are:

    • Responsible: The people who do the work to accomplish the activity; they have been tasked with completing the activity and/or getting a decision made.
    • Accountable: The person who is accountable for the completion of the activity. Ideally, this is a single person and will often be an executive or program sponsor.
    • Consulted: The people who provide information. This is usually several people, typically called subject matter experts (SMEs).
    • Informed: The people who are updated on progress. These are resources that are affected by the outcome of the activities and need to be kept up to date.

    Download the Secure IT/OT Convergence RACI Chart Tool

    Define RACI Chart

    Sample RACI chart with only the 'Plan' section enlarged.

    Define responsible, accountable, consulted, and informed (RACI) stakeholders.
    1. Customize the "work units" to best reflect your operation with applicable stakeholders.
    2. Customize the "action“ rows as required.
    Info-Tech Insight

    The roles and responsibilities should be clearly defined. For example, IT network should be responsible for the communication and configuration of all access points and devices from the remote client to the control system DMZ, and controls engineering should be responsible from the control system DMZ to the control system.

    Plan

    Establish governance and build cross-functional team

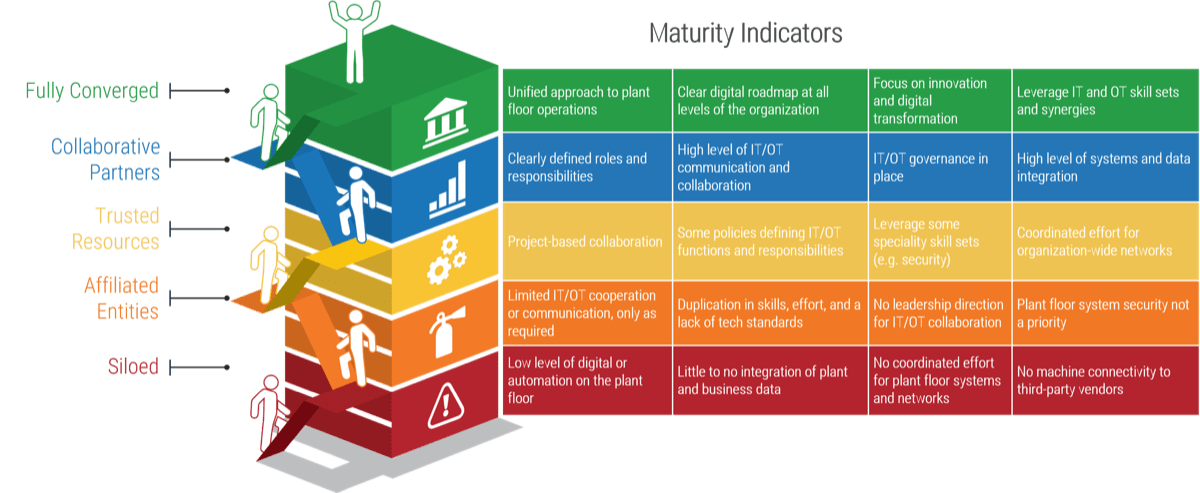
    To establish governance and build an IT/OT cross-functional team, it is important to understand the operation of OT systems and their interactions with IT within the organization, e.g. ad hoc, centralized, decentralized.

    The maturity ladder with levels 'Fully Converged', 'Collaborative Partners', 'Trusted Resources', 'Affiliated Entities', and 'Siloed' at the bottom. Each level has four maturity indicators listed.

    Info-Tech Insight

    To determine IT/OT convergence maturity level, Info-Tech provides the IT/OT Convergence Self-Evaluation Tool.

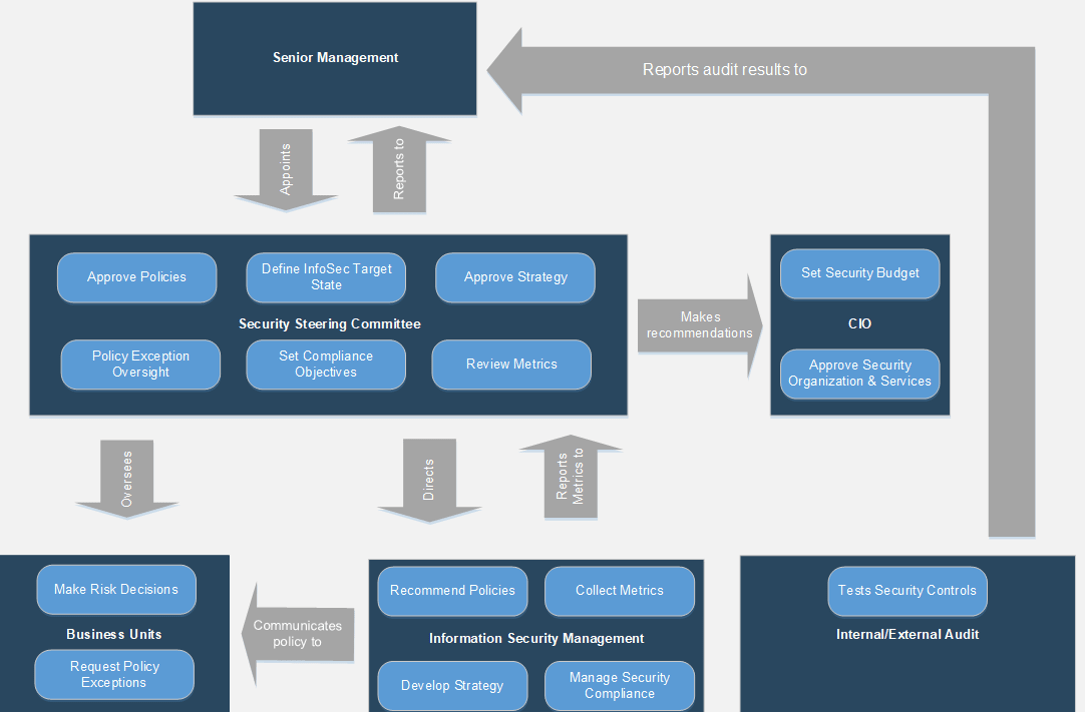
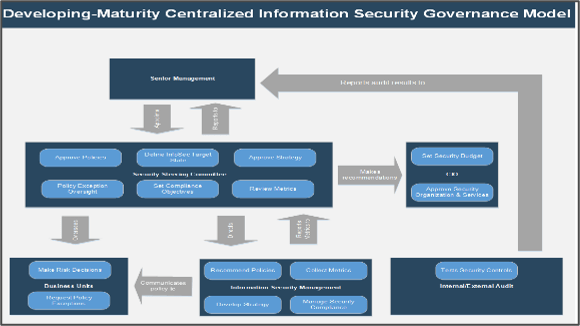
    Centralized security governance model example

    Example of a centralized security governance model.

    Plan

    Identify convergence elements and compliance obligations

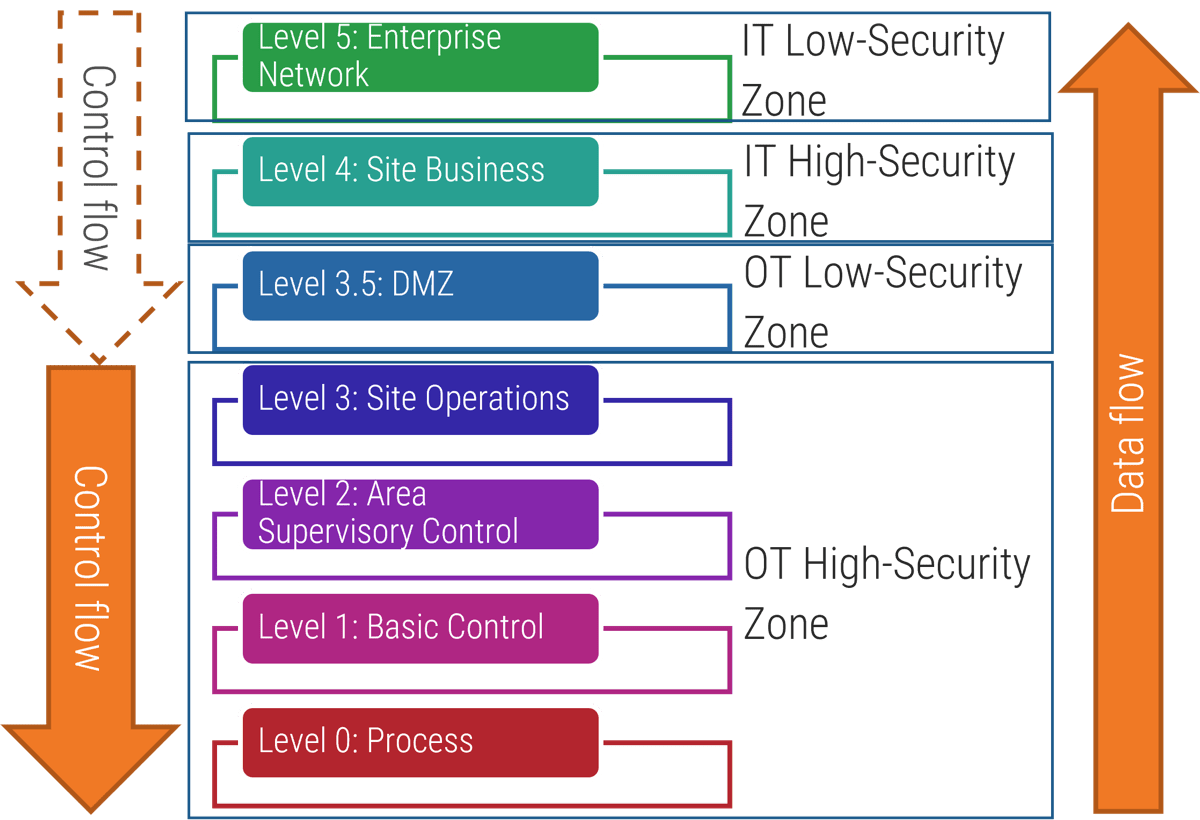
    To switch the focus from confidentiality and integrity to safety and availability for OT system, it is important to have a common language such as the Purdue model for technical communication.
    • A lot of OT compliance standards are technically focused and do not address governance and management, e.g. IT standards like the NIST Cybersecurity Framework. For example, OT system modeling with Purdue model will help IT teams to understand assets, networking, and controls. This understanding is needed to know the possible security solutions and where these solutions could be embedded to the OT system with respect to safety, reliability, and availability.
    • However, deployment of technical solutions or patches to OT system may nullify warranty, so arrangements should be made to manage this with the vendor or manufacturer prior to modification.
    • Finally, OT modernizations such as smart grid together with the advent of IIoT where data flow is becoming less hierarchical have encouraged the birth of a hybrid Purdue model, which maintains segmentation with flexibility for communications.

    Level 5: Enterprise Network

    Level 4: Site Business

    Level 3.5: DMZ
    Example: Patch Management Server, Application Server, Remote Access Server

    Level 3: Site Operations
    Example: SCADA Server, Engineering Workstation, Historian

    Level 2: Area Supervisory Control
    Example: SCADA Client, HMI

    Level 1: Basic Control
    Example: Batch Controls, Discrete Controls, Continuous Process Controls, Safety Controls, e.g. PLCs, RTUs

    Level 0: Process
    Example: Sensors, Actuators, Field Devices

    (Source: “Purdue Enterprise Reference Architecture (PERA) Model,” ISA-99.)

    Identify compliance obligations

    To manage compliance obligations, it is important to use a platform which not only performs internal and external monitoring, but also provides third-party vendors with visibility on potential threats in their organization.
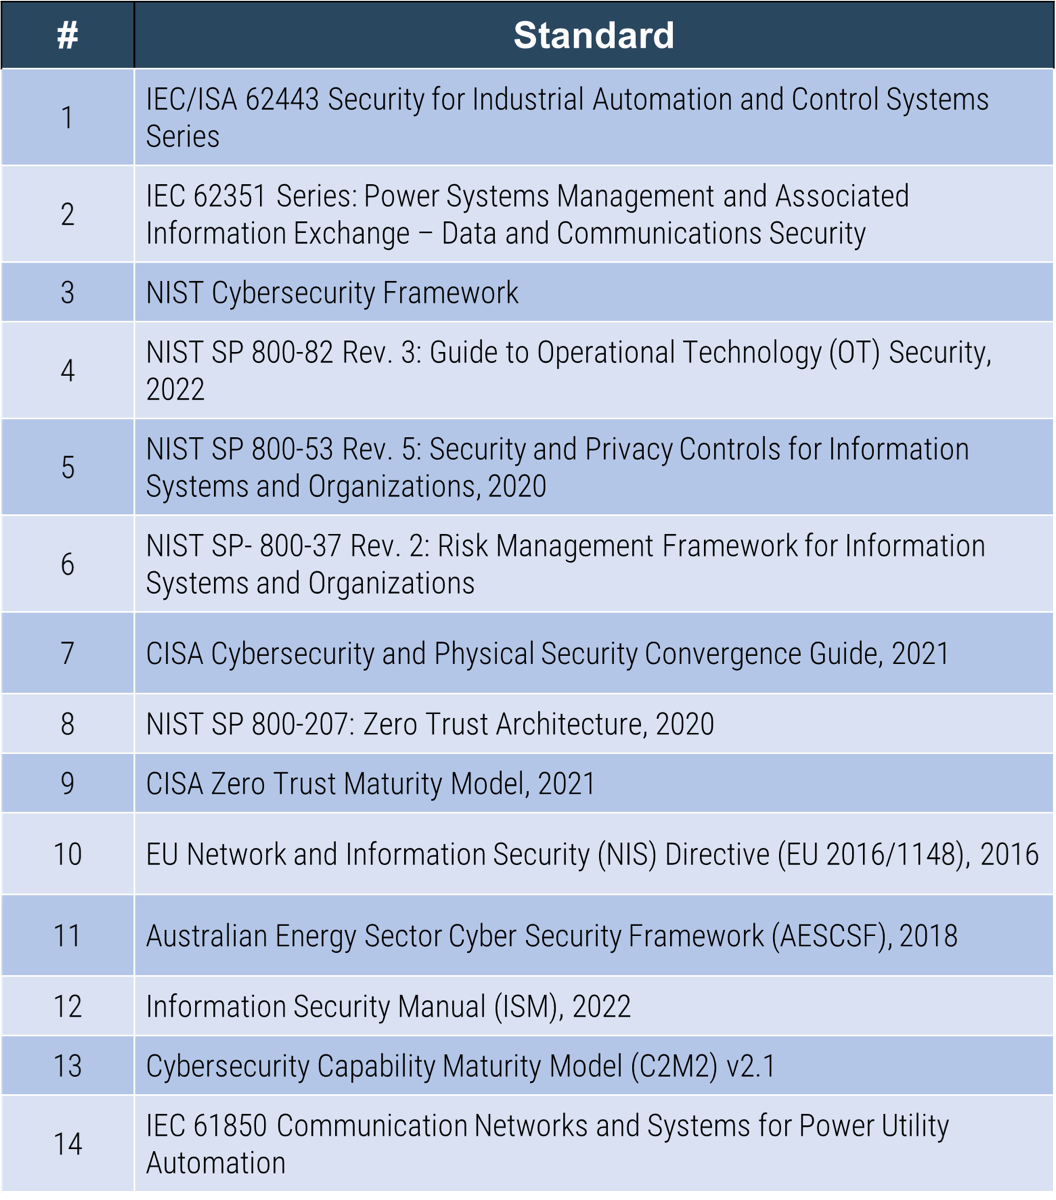
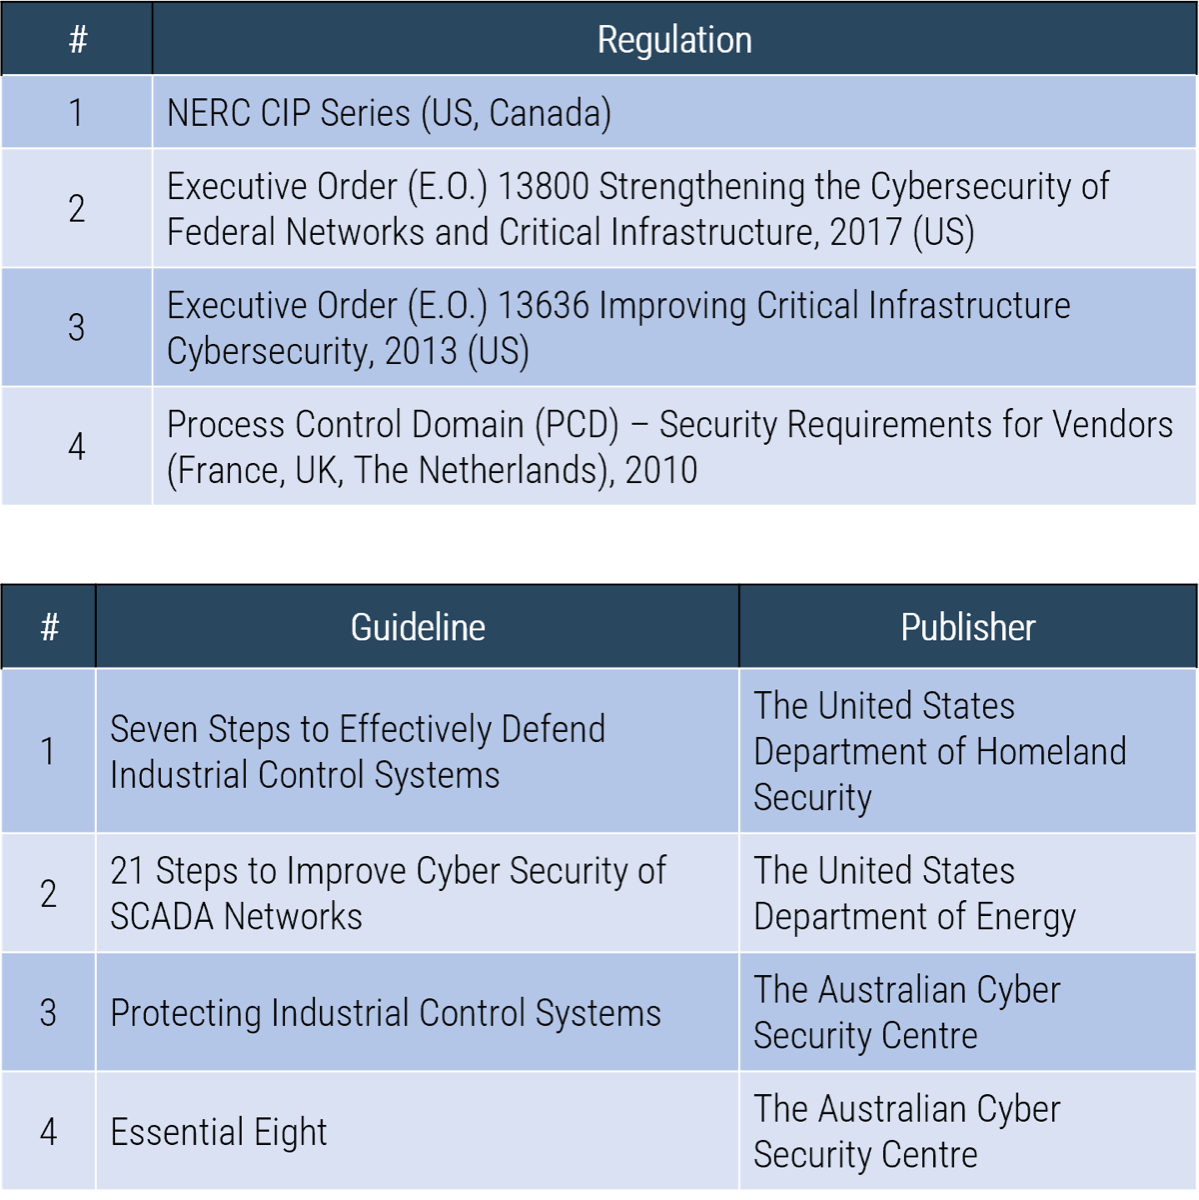
    Example table of compliance obligations standards. Example tables of compliance obligations regulations and guidelines.

    Source:
    ENISA, 2013
    DHS, 2009.

    • OT system has compliance obligations with industry regulations and security standards/regulations/guidelines. See the lists given. The lists are not exhaustive.
    • OT system owner can use the standards/regulations/guidelines as a benchmark to determine and manage the security level provided by third parties.
    • It is important to understand the various frameworks and to adhere to the appropriate compliance obligations, e.g. IEC/ISA 62443 - Security for Industrial Automation and Control Systems Series.

    IEC/ISA 62443 - Security for Industrial Automation and Control Systems Series

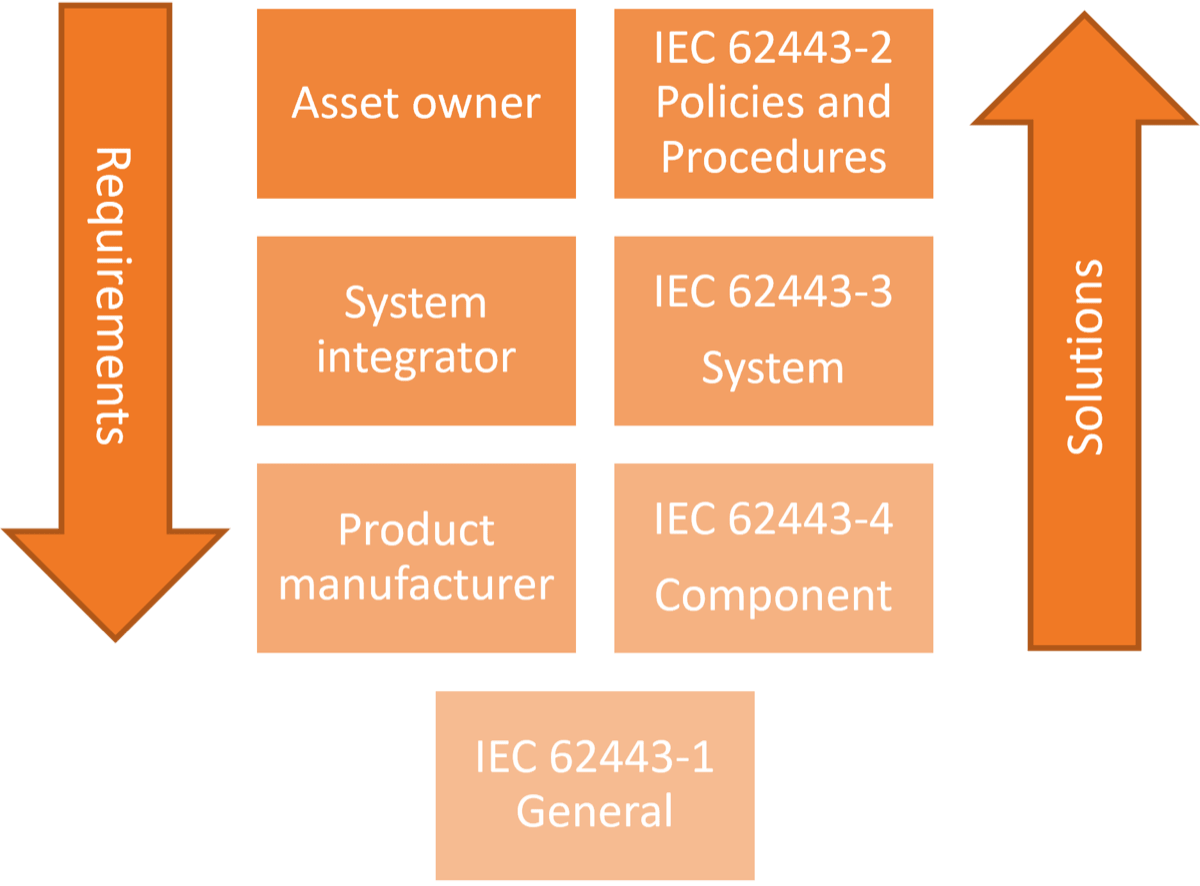
    International series of standards for asset owners, system integrators, and product manufacturers.
    Diagram of the international series of standards for asset owners.
    (Source: Cooksley, 2021)
    • IEC/ISA 62443 is a comprehensive international series of standards covering security for ICS systems, which recognizes three roles, namely: asset owner, system integrator, and product manufacturer.
    • In IEC/ISA 62443, requirements flow from the asset owner to the product manufacturer, while solutions flow in the opposite direction.
    • For the asset owner who owns and operates a system, IEC 62443-2 enables defining target security level with reference to a threat level and using the standard as a benchmark to determine the current security level.
    • For the system integrator, IEC 62443-3 assists to evaluate the asset owner’s requirements to create a system design. IEC 62443-3 also provides a method for verification that components provided by the product manufacturer are securely developed and support the functionality required.

    Record your compliance obligations

    Refer to the “Goals Cascade” tab of the Secure IT/OT Convergence Requirements Gathering Tool.
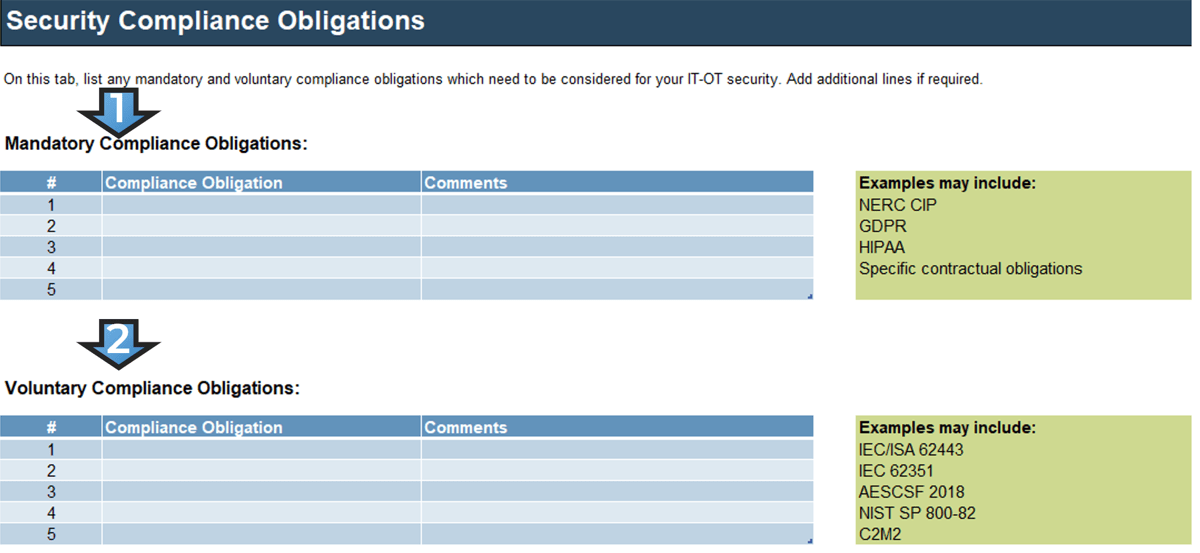
    1. Identify your compliance obligations. Most organizations have compliance obligations that must be adhered to. These can include both mandatory and voluntary obligations. Mandatory obligations include:
      1. Laws
      2. Government regulations
      3. Industry standards
      4. Contractual agreements
      Voluntary obligations include standards that the organization has chosen to follow for best practices and any obligations that are required to maintain certifications. Organizations will have many different compliance obligations. For the purposes of your secure IT/OT convergence, include only those that have OT security requirements.
    2. Record your compliance obligations, along with any notes, in your copy of the Secure IT/OT Convergence Requirements Gathering Tool.
    3. Refer to the “Compliance DB” tab for lists of standards/regulations/guidelines.
    Table of mandatory and voluntary security compliance obligations.

    Plan

    Assess readiness

    Readiness checklist for secure IT/OT convergence

    People

    • Define roles and responsibilities on interaction based on skill sets and the degree of support and alignment.
    • Adopt well-established security governance practices for cross-functional teams.
    • Analyze and develop skills required by implementing awareness, induction, and cross-training program.

    Process

    • Conduct a maturity assessment of key processes and highlight interdependencies.
    • Redesign cybersecurity processes for your secure IT/OT convergence program.
    • Develop a baseline and periodically review on risks, security policies and procedures, incident response, disaster recovery, and business continuity plan.

    Technology

    • Conduct a maturity assessment and identify convergence elements and compliance obligations.
    • Develop a roadmap and deploy converging security architecture and controls step by step, working with trusted technology partners.
    • Monitor security metrics on effectiveness and efficiency and conduct continuous testing by red-team and blue-team activities.

    (Source: “Grid Modernization: Optimize Opportunities And Minimize Risks,” Info-Tech)

    Enhance

    Update security strategy

    To update security strategy, it is important to actively encourage visible sponsorship across management and to provide regular updates.

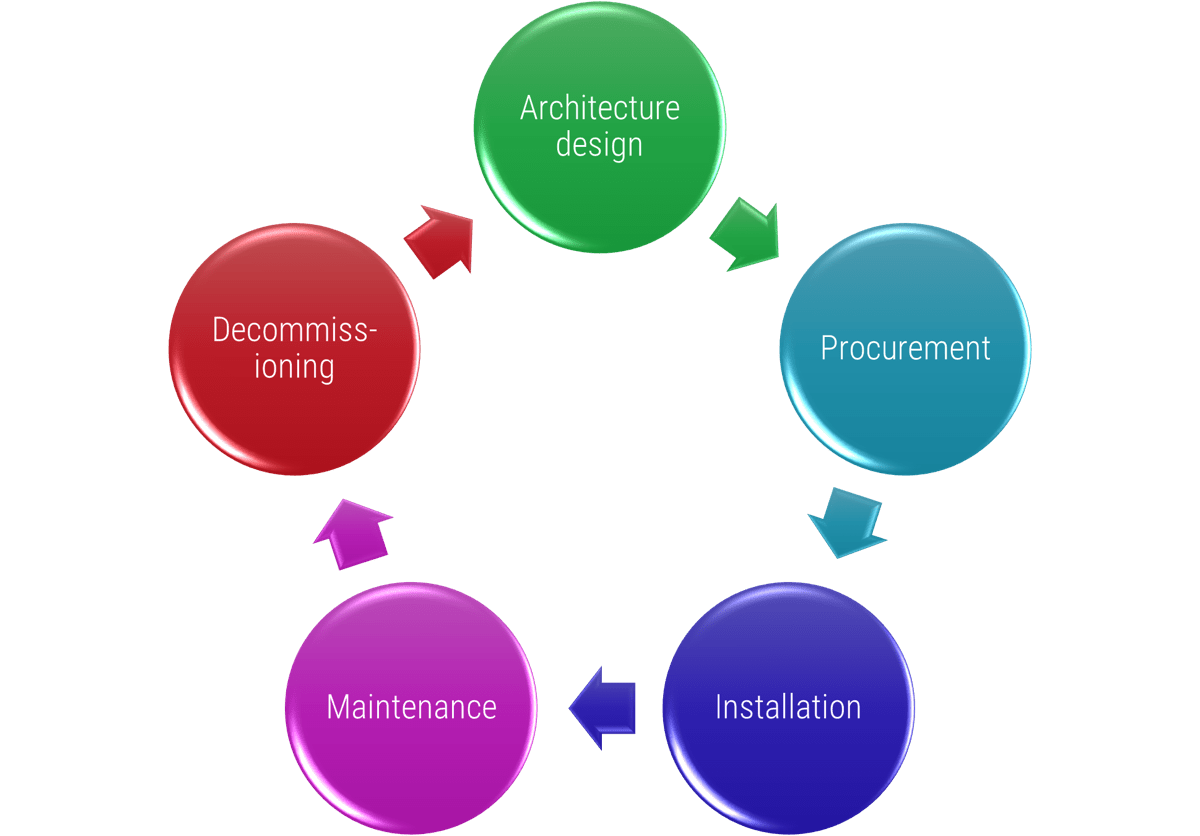
    Cycle for updating security strategy: 'Architecture design', 'Procurement', 'Installation', 'Maintenance', 'Decommissioning'.
    (Source: NIST SP 800-82 Rev.3, “Guide to Operational Technology (OT) Security,” NIST, 2022.)
    • OT system life cycle is like the IT system life cycle, starting with architectural design and ending with decommissioning.
    • Currently, IT only gets involved from installation or maintenance, so they may not fully understand the OT system. Therefore, if OT security is compromised, the same personnel who commissioned the OT system (e.g. engineering, electrical, and maintenance specialists) must be involved. Thus, it is important to have the IT team collaborate with the OT team in each stage of the OT system’s life cycle.
    • Finally, it is necessary to have propositional sharing of responsibilities between IT leaders, security leaders, and OT leaders who have broader responsibilities.

    Enhance

    Update risk management framework

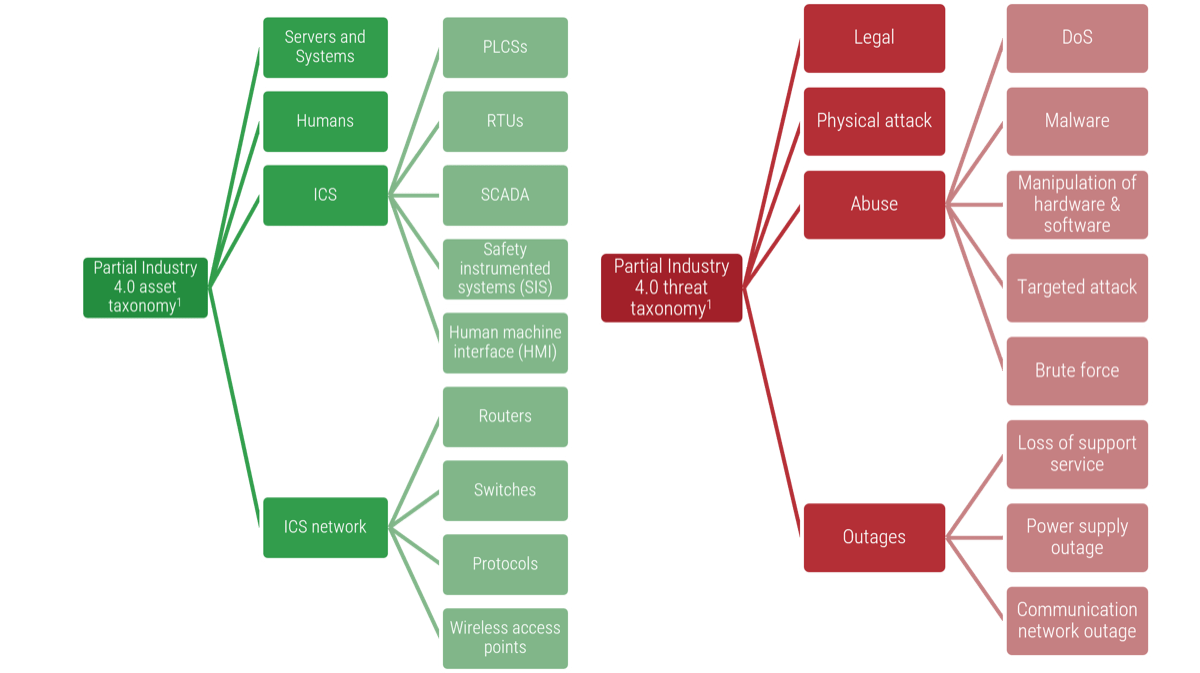
    The need for asset and threat taxonomy

    • One of issues in IT/OT convergence is that OT systems focus on production, so IT solutions like security patching or updates may deteriorate a machine or take a machine offline and may not be applicable. For example, some facilities run with reliability of 99.999%, which only allows maximum of 5 minutes and 35 seconds or less of downtime per year.
    • Managing risks requires an understanding of the assets and threats for IT/OT systems. Having a taxonomy of the assets and the threats cand help.
    • Applying normal IT solutions to mitigate security risks may not be applicable in an OT environment, e.g. running an antivirus tool on OT system may remove essential OT operations files. Thus, this approach must be avoided; instead, systems must be rebuilt from golden images.
    Risk management framework.
    (Source: ENISA, 2018.)

    Enhance

    Update security policies and procedures

    • Policy is the link between people, process, and technology for any size of organization. Small organizations may think that having formal policies in place is not necessary for their operations, but compliance is applicable to all organizations, and vulnerabilities affect organizations of all sizes as well. Small organizations partnering with clients or other organizations are sometimes viewed as ideal proxies for attackers.
    • Updating security policies to align with the OT system so that there is a uniform approach to securing both IT and OT environments has several benefits. For example, enhancing the overall security posture as issues are pre-emptively avoided, being better prepared for auditing and compliance requirements, and improving governance especially when OT governance is weak.
    • In updating security policies, it is important to redefine the policy framework to include the OT framework and to prioritize the development of security policies. For example, entities that own or manage US and Canadian electric power grids must comply with North American Electric Reliability Corporation Critical Infrastructure Protection (NERC CIP) standards, specifically CIP-003 for Policy and Governance. This can be achieved by understanding the current state of policies and by right-sizing the policy suite based on a policy hierarchy.
    The White House released an Executive Order on Improving the Nation’s Cybersecurity (EO 14028) in 2021 that establishes new requirements on the scope of protection and security policy such that it must include both IT and OT.

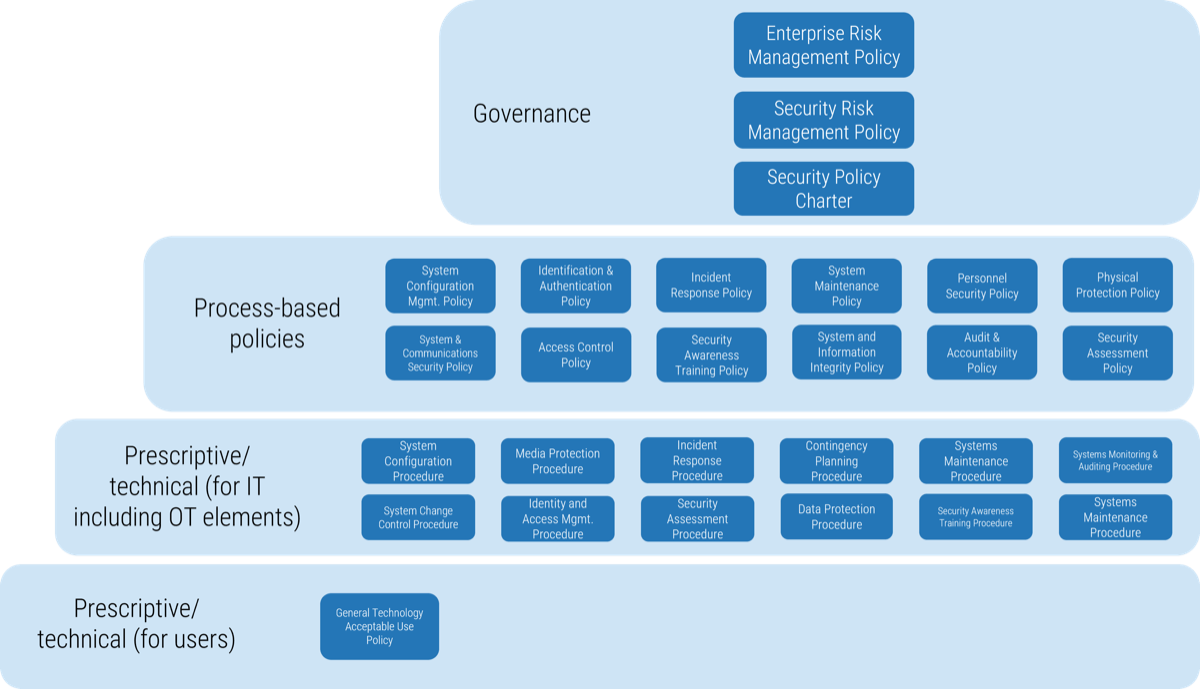
    Policy hierarchy example

    This example of a policy hierarchy features templates from Info-Tech’s Develop and Deploy Security Policies and Identify the Best Framework for Your Security Policies research.

    Example policy hierarchy with four levels, from top-down: 'Governance', 'Process-based policies', 'Prescriptive/ technical (for IT including OT elements)', 'Prescriptive/ technical (for users)'.

    Enhance

    Update IR, DR, and BCP

    A proactive approach to security is important, so actions such as updating and testing the incident response plan for OT are a must. (“Cybersecurity Year In Review” Dragos, 2022.)

    1. Customize organizational chart for IT/OT IR, DR, BCP based on governance and management model.
      E.g. ad hoc, internal distributed, internal centralized, combined distributed, and decentralized. (Software Engineering Institute, 2003)
    2. Adjust the authority of the new organizational chart and decide if it requires additional staffing.
      E.g. full authority, shared authority. (Software Engineering Institute, 2003)
    3. Update IR plan, DR plan, and BCP for IT/OT convergence.
      E.g. incorporate zero trust principles for converge network
    4. Testing updated IR plan, DR plan, and BCP.

    Optimize

    Implement awareness, induction, and cross-training

    To develop training and awareness programs for all levels of the organization, it is important to understand the common challenges in IT security that also affect secure IT/OT convergence and how to overcome those challenges.

    Alert Fatigue

    Too many false alarms, too many events to process, and an evolving threat landscape that wastes analysts’ valuable time on mundane tasks such as evidence collection. Meanwhile, only limited time is given for decision and conclusion, which results in fear of missing an incident and alert fatigue.

    Skill Shortages

    Obtaining and retaining cybersecurity-skilled talent is challenging. Organizations need to invest in the people, but not all organizations will be able to invest sufficiently to have their own dedicated security team.

    Lack of Insight

    To report progress, clear metrics are needed. However, cybersecurity still falls short in this area, as the system itself is complex, and much work is siloed. Furthermore, lessons learned are not yet distilled into insights yet for improving future accuracy.

    Lack of Visibility

    Ensuring complete visibility of the threat landscape, risks, and assets requires system integration and consistent workflow across the organization, and the convergence of OT, IoT, and IT enhances this challenge (e.g. machines cannot be scanned during operational uptime).
    (Source: Security Intelligence, 2020.)
    “Cybersecurity staff are feeling burnout and stressed to the extent that many are considering leaving their jobs.” (Danny Palmer, ZDNET News, 2022)

    Awareness may not correspond to readiness

    • An issue with IT/OT convergence training and awareness happens when awareness exists, but the personnel are trained only for IT security and are not trained for OT-specific security. For example, some organizations still use generic topics such as not opening email attachments, when the personnel do not even operate using email nor in a web browsing environment. (“Assessing Operational Readiness,” Dragos, 2022)
    • Meanwhile, as is the case with IT, OT security training topics are broad, such as OT threat intelligence, OT-specific incident response, and tabletop exercises.
    • Hence, it requires the creation of a training program development plan that considers the various audiences and topics and maps them accordingly.
    • Moreover, roles are also evolving due to convergence and modernization. These new roles require an integrative skill set. For example, the grid security & ops team might consist of an IT security specialist, SCADA technician/engineer, and OT/IIOT security specialist where OT/IIOT security specialist is a new role. (Grid Modernization: Optimize Opportunities and Minimize Risks,” Info-Tech)
    • In conclusion, it is important to approach talent development with an open mind. The ability to learn and flexibility in the face of change are important attributes, and technical skill sets can be improved with certifications and training.
    “One area regularly observed by Dragos is a weakness in overall cyber readiness and training tailored specific to the OT environment.” (“Assessing Operational Technology,” Dragos, 2022.)

    Certifications

    What are the options?
    • One of issues in certification is the complexity on relevancy in topics with respect to roles and levels.
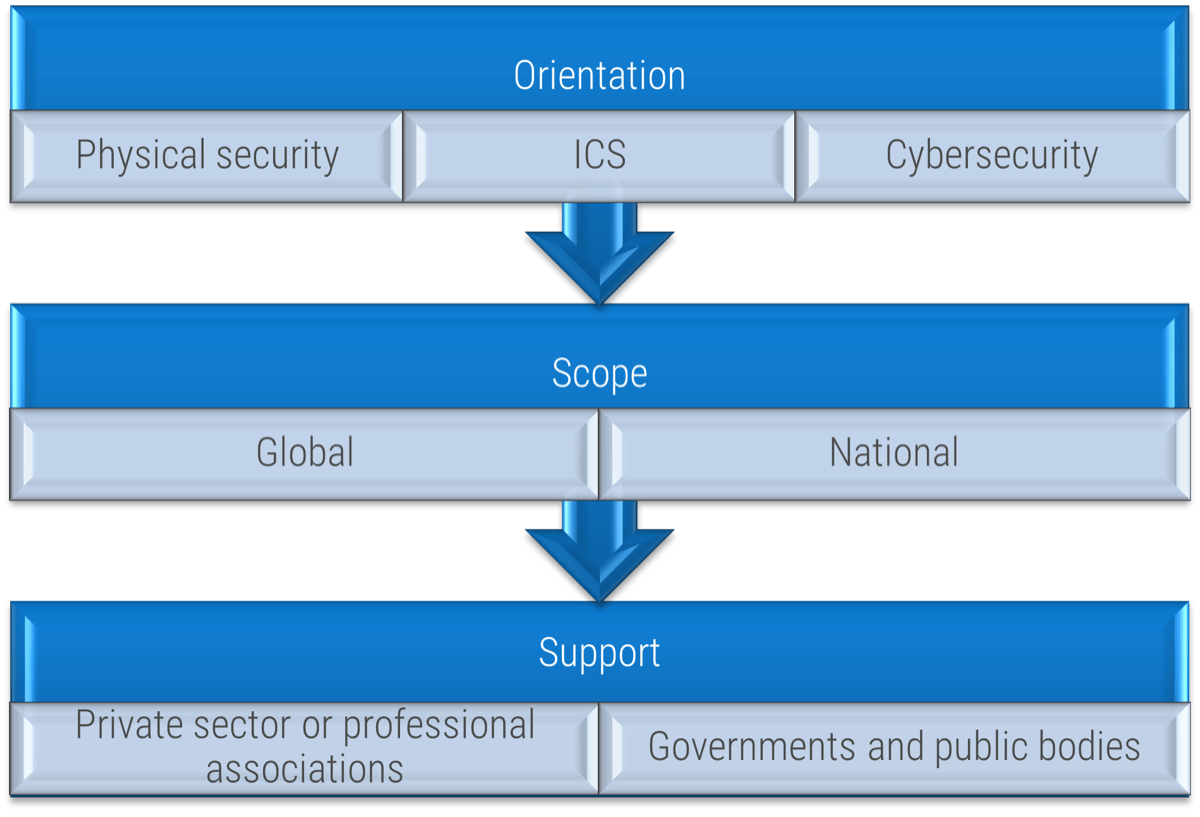
    • An example solution is the European Union Agency for Cybersecurity (ENISA)’s approach to analyzing existing certifications by orientation, scope, and supporting bodies, grouped into specific certifications, relevant certifications, and safety certifications.

    Specific cybersecurity certification of ICS/SCADA
    Example: ISA-99/IEC 62443 Cybersecurity Certificate Program, GIAC Global Industrial Cyber Security Professional (GICSP), Certified SCADA Security Architect (CSSA), EC-Council ICS/SCADA Cybersecurity Training Course.

    Other relevant certification schemes
    Example: Network and Information Security (NIS) Driving License, ISA Certified Automation Professional (CAP), Industrial Security Professional Certification (NCMS-ISP).

    Safety Certifications
    Example: Board of Certified Safety Professionals (BCSP), European Network of Safety and Health Professional Organisations (ENSHPO).

    Order of certifications with 'Orientation' at the top, 'Scope', then 'Support'.(Source: ENISA, 2015.)

    Optimize

    Design and deploy converging security architecture and controls

    • IT/OT convergence architecture can be modeled as a layered structure based on security. In this structure, the bottom layer is referred as “OT High-Security Zone” and the topmost layer is “IT Low-Security Zone.” In this model, each layer has its own set of controls configured and acts like an additional layer of security for the zone underneath it.
    • The data flows from the “OT High-Security Zone” to the topmost layer, the “IT Low-Security Zone,” and the traffic must be verified to pass to another zone based on the need-to-know principle.
    • In the normal control flow within the “OT High-Security Zone” from level 3 to level 0, the traffic must be verified to pass to another level based on the principle of least privilege.
    • Remote access (dotted arrow) is allowed under strict access control and change control based on the zero-trust principle with clear segmentation and a point for disconnection between the “OT High-Security Zone” and the “OT Low-Security Zone”
    • This model simplifies the security process, as if the lower layers have been compromised, then the compromise can be confined on that layer, and it also prevents lateral movement as access is always verified.
    Diagram for the deployments of converging security architecture.(Source: “Purdue Enterprise Reference Architecture (PERA) model,” ISA-99.)

    Off-the-shelf solutions

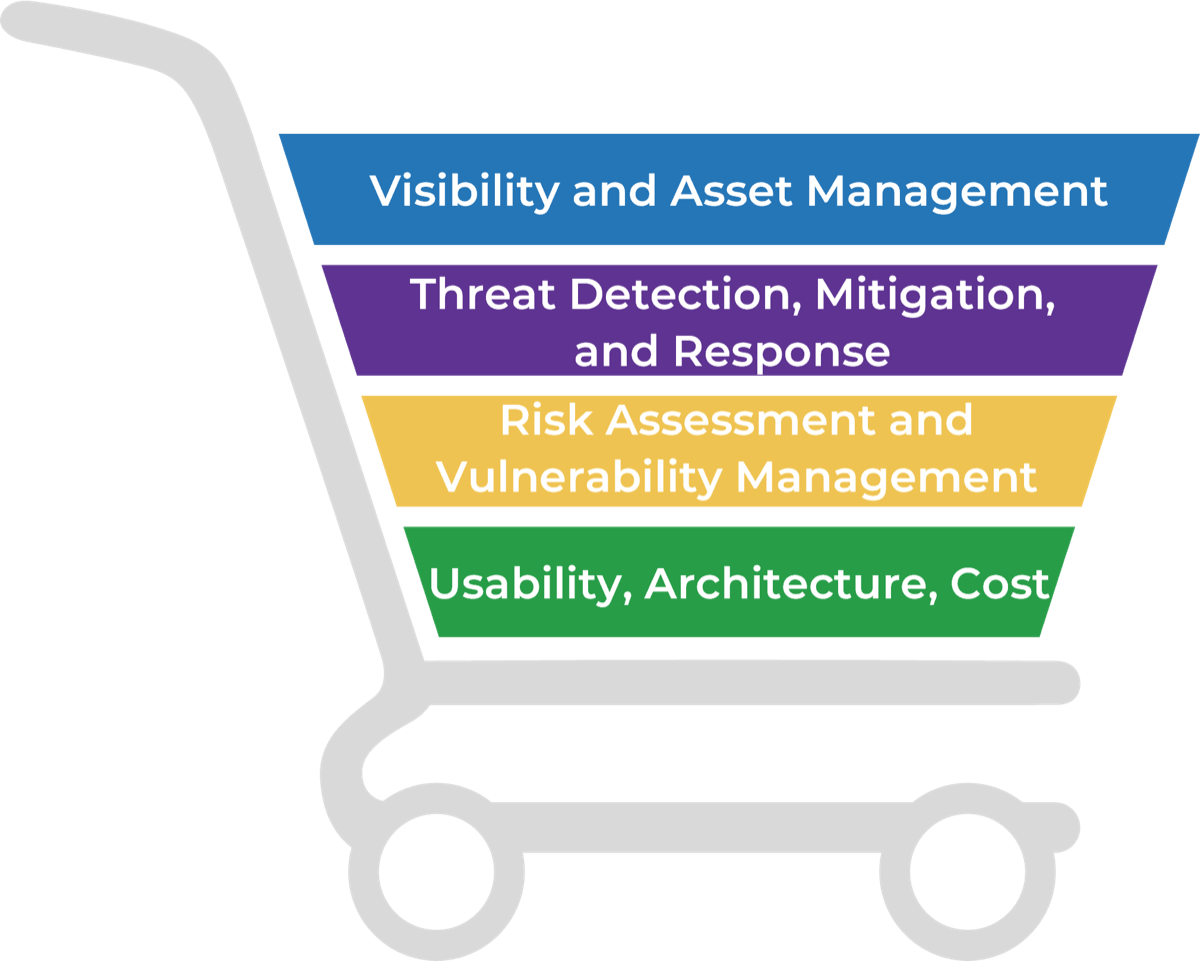
    Getting the right recipe: What criteria to consider?

    Image of a shopping cart with the four headlines on the right listed in order from top to bottom.
    Icon of an eye crossed out. Visibility and Asset Management

    Passive data monitoring using various protocol layers, active queries to devices, or parsing configuration files of OT, IoT, and IT environments on assets, processes, and connectivity paths.

    Icon of gears. Threat Detection, Mitigation, and Response (+ Hunting)

    Automation of threat analysis (signature-based, specification-based, anomaly-based, sandboxing) not only in IT but also in relevant environments, e.g. IoT, IIoT, and OT on assets, data, network, and orchestration with threat intelligence sharing and analytics.

    Icon of a check and pen. Risk Assessment and Vulnerability Management

    Risk scoring approach (qualitative, quantitative) based on variables such as behavioral patterns and geolocation. Patching and vulnerability management.

    Icon of a wallet. Usability, Architecture, Cost

    The user and administrative experience, multiple deployment options and extensive integration capabilities, and affordability.

    Optimize

    Establish and monitor IT/OT security metrics for effectiveness and efficiency

    Role of security metrics in a cybersecurity program (EPRI, 2017.)
    • Requirements for secure IT/OT are derived from mandatory or voluntary compliance, e.g. NERC CIP, NIST SP 800-53.
    • Frameworks for secure IT/OT are used to build and implement security, e.g. NIST CSF, AESCSF.
    • Maturity of secure IT/OT is used to measure the state of security, e.g. C2M2, CMMC.
    • Security metrics have the role of measuring effectiveness and efficiency.

    Icon of a person ascending stairs.
    Safety

    OT interfaces with the physical world. Thus, metrics based on risks related with life, health, and safety are crucial. These metrics motivate personnel by making clear why they should care about security. (EPRI, 2017.)

    Icon of a person ascending stairs.
    Business Performance

    The impact of security on the business can be measured in various metrics such as operational metrics, service level agreements (SLAs), and financial metrics. (BMC, 2022.)

    Icon of a person ascending stairs.
    Technology Performance

    Early detection will lead to faster remediation and less damage. Therefore, metrics such as maximum tolerable downtime (MTD) and mean time to recovery (MTR) indicate system reliability. (Dark Reading, 2022)

    Icon of a person ascending stairs.
    Security Culture

    The metrics for the overall quality of security culture with indicators such as compliance and audit, vulnerability management, and training and awareness.

    Further information

    Related Info-Tech Research

    Sample of 'Build an Information Security Strategy'.

    Build an Information Security Strategy

    Info-Tech has developed a highly effective approach to building an information security strategy – an approach that has been successfully tested and refined for over seven years with hundreds of organizations.

    This unique approach includes tools for ensuring alignment with business objectives, assessing organizational risk and stakeholder expectations, enabling a comprehensive current-state assessment, prioritizing initiatives, and building a security roadmap.

    Sample of 'Preparing for Technology Convergence in Manufacturing'.

    Preparing for Technology Convergence in Manufacturing

    Information technology (IT) and operational technology (OT) teams have a long history of misalignment and poor communication.

    Stakeholder expectations and technology convergence create the need to leave the past behind and build a culture of collaboration.

    Sample of 'Implement a Security Governance and Management Program'.

    Implement a Security Governance and Management Program

    Your security governance and management program needs to be aligned with business goals to be effective.

    This approach also helps provide a starting point to develop a realistic governance and management program.

    This project will guide you through the process of implementing and monitoring a security governance and management program that prioritizes security while keeping costs to a minimum.

    Bibliography

    Assante, Michael J. and Robert M. Lee. “The Industrial Control System Cyber Kill Chain.” SANS Institute, 2015.

    “Certification of Cyber Security Skills of ICS/SCADA Professionals.” European Union Agency for Cybersecurity (ENISA), 2015. Web.

    Cooksley, Mark. “The IEC 62443 Series of Standards: A Product Manufacturer‘s Perspective.” YouTube, uploaded by Plainly Explained, 27 Apr. 2021. Accessed 26 Aug. 2022.

    “Cyber Security Metrics for the Electric Sector: Volume 3.” Electric Power Research Institute (EPRI), 2017.

    “Cybersecurity and Physical Security Convergence.” Cybersecurity and Infrastructure Security Agency (CISA). Accessed 19 May 2022.

    “Cybersecurity in Operational Technology: 7 Insights You Need to Know,” Ponemon, 2019. Web.

    “Developing an Operational Technology and Information Technology Incident Response Plan.” Public Safety Canada, 2020. Accessed 6 Sep. 2022.

    Gilsinn, Jim. “Assessing Operational Technology (OT) Cybersecurity Maturity.” Dragos, 2021. Accessed 02 Sep. 2022.

    “Good Practices for Security of Internet of Things.” European Union Agency for Cybersecurity (ENISA), 2018. Web.

    Greenfield, David. “Is the Purdue Model Still Relevant?” AutomationWorld. Accessed 1 Sep. 2022

    Hemsley, Kevin E., and Dr. Robert E. Fisher. “History of Industrial Control System Cyber Incidents.” US Department of Energy (DOE), 2018. Accessed 29 Aug. 2022.

    “ICS Security Related Working Groups, Standards and Initiatives.” European Union Agency for Cybersecurity (ENISA), 2013.

    Killcrece, Georgia, et al. “Organizational Models for Computer Security Incident Response Teams (CSIRTs).” Software Engineering Institute, CMU, 2003.

    Liebig, Edward. “Security Culture: An OT Survival Story.” Dark Reading, 30 Aug. 2022. Accessed 29 Aug. 2022.

    Bibliography

    O'Neill, Patrick. “Russia Hacked an American Satellite Company One Hour Before the Ukraine Invasion.” MIT Technology Review, 10 May 2022. Accessed 26 Aug. 2022.

    Palmer, Danny. “Your Cybersecurity Staff Are Burned Out – And Many Have Thought About Quitting.” Zdnet, 08 Aug. 2022. Accessed 19 Aug. 2022.

    Pathak, Parag. “What Is Threat Management? Common Challenges and Best Practices.” SecurityIntelligence, 23 Jan. 2020. Web.

    Raza, Muhammad. “Introduction To IT Metrics & KPIs.” BMC, 5 May 2022. Accessed 12 Sep. 2022.

    “Recommended Practice: Developing an Industrial Control Systems Cybersecurity Incident Response Capability.” Department of Homeland Security (DHS), Oct. 2009. Web.

    Sharma, Ax. “Sigma Rules Explained: When and How to Use Them to Log Events.” CSO Online, 16 Jun. 2018. Accessed 15 Aug. 2022.

    “Significant Cyber Incidents.” Center for Strategic and International Studies (CSIS). Accessed 1 Sep. 2022.

    Tom, Steven, et al. “Recommended Practice for Patch Management of Control Systems.” Department of Homeland Security (DHS), 2008. Web.

    “2021 ICS/OT Cybersecurity Year In Review.” Dragos, 2022. Accessed 6 Sep. 2022.

    “2021 State of Operational Technology and Cybersecurity Report,” Fortinet, 2021. Web.

    Zetter, Kim. “Pre-Stuxnet, Post-Stuxnet: Everything Has Changed, Nothing Has Changed.” Black Hat USA, 08 Aug. 2022. Accessed 19 Aug. 2022.

    Research Contributors and Experts

    Photo of Jeff Campbell, Manager, Technology Shared Services, Horizon Power, AU. Jeff Campbell
    Manager, Technology Shared Services
    Horizon Power, AU

    Jeff Campbell has more than 20 years' experience in information security, having worked in both private and government organizations in education, finance, and utilities sectors.

    Having focused on developing and implementing information security programs and controls, Jeff is tasked with enabling Horizon Power to capitalize on IoT opportunities while maintaining the core security basics of confidentiality, integrity and availability.

    As Horizon Power leads the energy transition and moves to become a digital utility, Jeff ensures the security architecture that supports these services provides safer and more reliable automation infrastructures.

    Christopher Harrington
    Chief Technology Officer (CTO)
    Carolinas Telco Federal Credit Union

    Frank DePaola
    Vice President, Chief Information Security Officer (CISO)
    Enpro

    Kwasi Boakye-Boateng
    Cybersecurity Researcher
    Canadian Institute for Cybersecurity

    Infrastructure and Operations Priorities 2023

    • Buy Link or Shortcode: {j2store}54|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Disruptive & Emerging Technologies
    • Parent Category Link: /disruptive-emerging-technologies
    • Get out of your I&O silo. I&O teams must be expected to work alongside and integrate with cyber security operations.
    • Being unprepared for new ESG reporting mandates without a clear and validated ESG reporting process puts your organization at risk.
    • Get ahead of inflationary pressures with early budgetary planning and identify the gap between the catchup projects and required critical net new investments.

    Our Advice

    Critical Insight

    • Establish I&O within an AI governance program to build trust in AI results, behaviors, and limit legal exposure.
    • Develop data governance program that includes an I&O data steward for oversight.
    • Ready or not, the metaverse is coming to an infrastructure near you. Start expanding I&O technologies and processes to support a metaverse infrastructure.

    Impact and Result

    • Provide a framework that highlight the impacts the threats of an economic slowdown, growing regulatory reporting requirements, cyber security attacks and opportunity that smart governance over AI, data stewardship and the looming explosion of augmented reality and Web 3.0 technologies.
    • Info-Tech can help communicate your I&O priorities into compelling cases for your stakeholders.

    Infrastructure and Operations Priorities 2023 Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Infrastructure & Operations Priorities 2023 – A framework to dive deeper into the trends most relevant to you and your organization

    Discover Info-Tech's six priorities for Infrastructure & Operations leaders.

    Infographic

    Further reading

    Infrastructure &Operations Priorities 2023

    Navigate the liminal space between threats and opportunities.

    2023: A liminal space between threats and opportunities

    Over the last several years, successful CEOs turned to their Infrastructure and Operations (I&O) departments to survive the effects of the pandemic. It was I&O leaders who were able to reconfigure critical infrastructure on the fly to support remote work, adapt to critical supply chain shortages, and work with lines of business managers to innovate operational workflows.

    2023 promises to bring a new set of challenges. Building on the credibility established during the pandemic, I&O is in a unique position to influence the direction a business will take to be successful in a time of austerity.

    I&O members are going to be asked to mitigate the threats of volatility from recession pressures, new cybersecurity attacks, and operational process and litigation from regulatory mandates. At the same time, I&O members are being asked for fundamental digital transformation items to realize long-term opportunities to their organizations in 2023.

    Seemingly counter-intuitive in a time of economic slowdown, organizations in 2023 will want to start the groundwork to realizing the I&O opportunities that unstructured data and artificial intelligence have promised, while prepping for what has been mislabeled as the Metaverse.

    If you are in a traditionally risk adverse industry, you’re more likely to be impacted by the threat mitigation.

    Opportunistic I&O members will use 2023 to proactively jumpstart digital transformation.

    Introduction

    Welcome to the Info-Tech 2023 I&O Priorities Report

    If I&O members learned anything from the last few years, it’s how to tactically respond to the disruptive waves often arising from sources external to the organization. The good news is that Info-Tech’s I&O priorities report provides forward-looking insights to help members become more proactive to the tsunami of change predicted in our Trends Report to happen over the next three to five years.

    Info-Tech I&O priorities are generated through a phased approach. The first phase senses and identifies mega and macro tends in the digital landscape to formulate hypotheses about the trends for the next three to five years. These hypotheses are validated by sending out a survey to Info-Tech members. The responses from 813 members was used to produce an Info-Tech Trends Report focused on major long-term trends.

    The I&O Priorities were determined by combining the I&O member responses within the Info-tech Trends Survey with insightful signals from secondary research, economic markets, regulatory bodies, industry organizations, and vendors. The six I&O priorities identified in this report are presented in a framework that highlight the impacts of an economic slowdown, growing regulatory reporting requirements, cybersecurity threats, smart governance of AI, embracing stewardship of data, and the looming explosion of augmented reality and Web 3.0 technologies.

    We also have a challenge exercise to help you communicate which priorities to focus your I&O organization on. Additionally, we linked some Info-tech research and tools related to the priorities that help your I&O organization formulate actionable plans for each area.

    Priorities

    Six forward-looking priorities for the next year.

    Focus

    Activity to help select which priorities are relevant for you.

    Actions

    Actionable Info-tech research and tools to help you deliver.

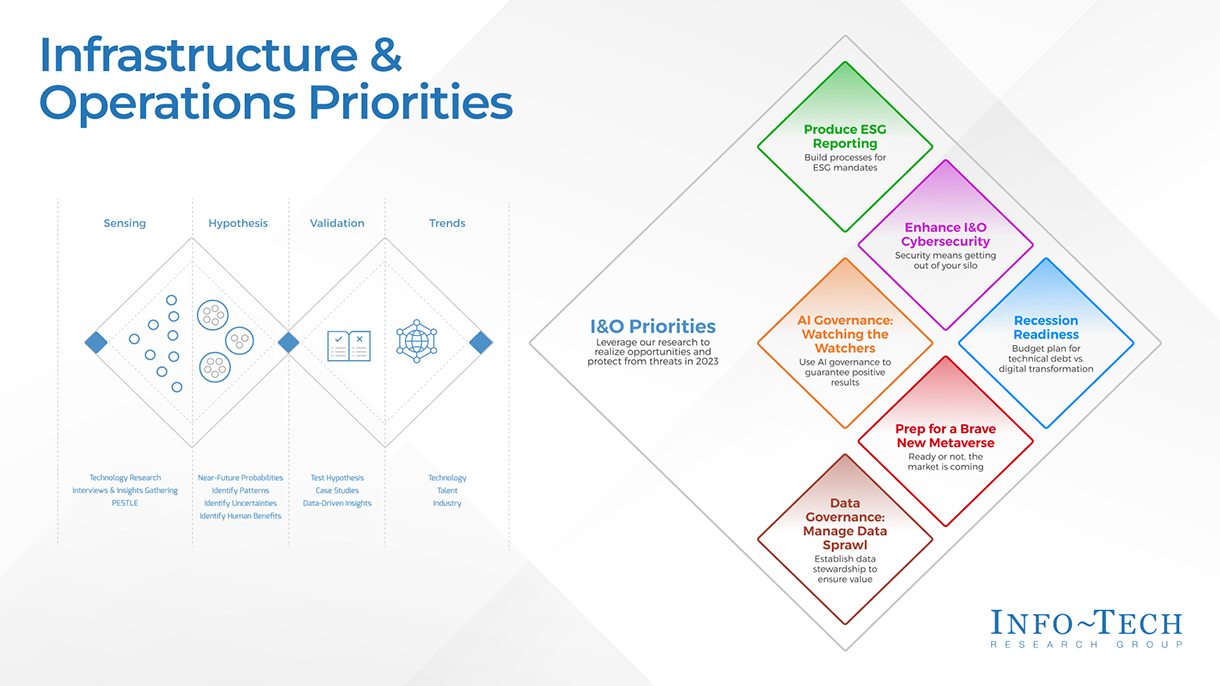
    Infrastructure & Operations priorities

    The I&O priorities were determined by combining I&O member responses from the Tech Trends and Priorities 2023 survey with insightful signals from secondary research, economic markets, regulatory bodies, industry organizations, and vendors.

    The image contains a screenshot of the Infrastructure & Operations priorities.

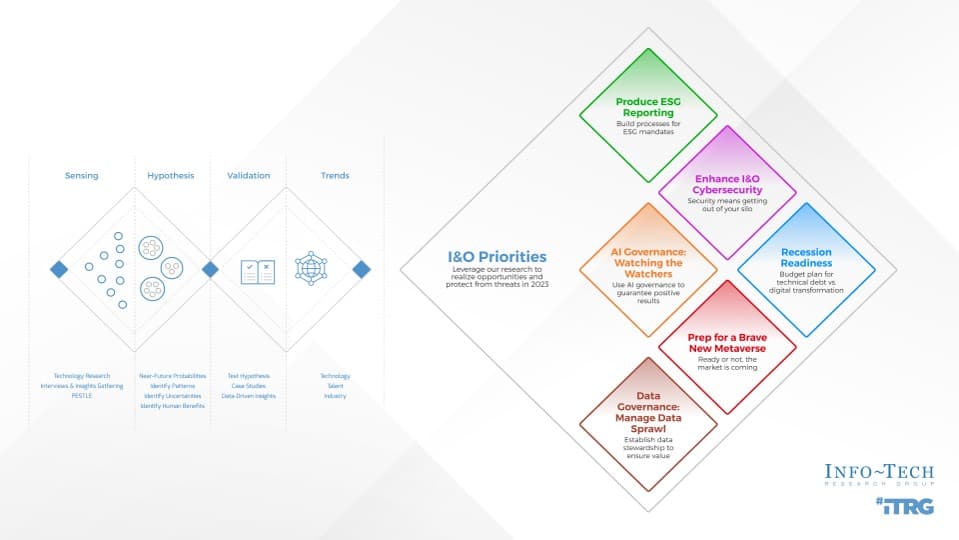
    I&O Priorities 2023

    The image contains a screenshot of the I&O Priorities.

    I&O priorities framework

    Threats signals

    Enhance I&O Cybersecurity

    Produce ESG Reporting

    Recession Readiness

    Get out of your silo. Forget your job description and start doing what needs to be done.

    Infrastructure rarely has authority in these areas, but somehow it ends up with many of the responsibilities. You can't afford to be reactive. Forget about your traditional silo and get out in front of these topics. Not in your job description? Find out whose job it is and make them aware. Better yet – take charge! If you're going to be responsible you might as well be in control.

    Opportunities signals

    AI Governance: Watching the Watchers

    Prep for A Brave New Metaverse

    Data Governance: Cornerstone of Value

    Proper stewardship of data is an I&O must. If thought you had problems with your unstructured data, wait until you see the data sprawl coming from the metaverse.

    I&O needs to be so much more than just an order taker for the dev teams and lines of business. The sprawl of unstructured data in Word, Excel, PDF and PowerPoint was bad historically; imagine those same problems at metaverse scale! Simple storage and connectivity is no longer enough – I&O must move upstream with more sophisticated service and product offerings generated through proper governance and stewardship.

    Challenge: Expand the I&O border

    The hidden message in this report is that I&O priorities extend beyond the traditional scope of I&O functions. I&O members need to collaborate across functional areas to successfully address the priorities presented in this report.

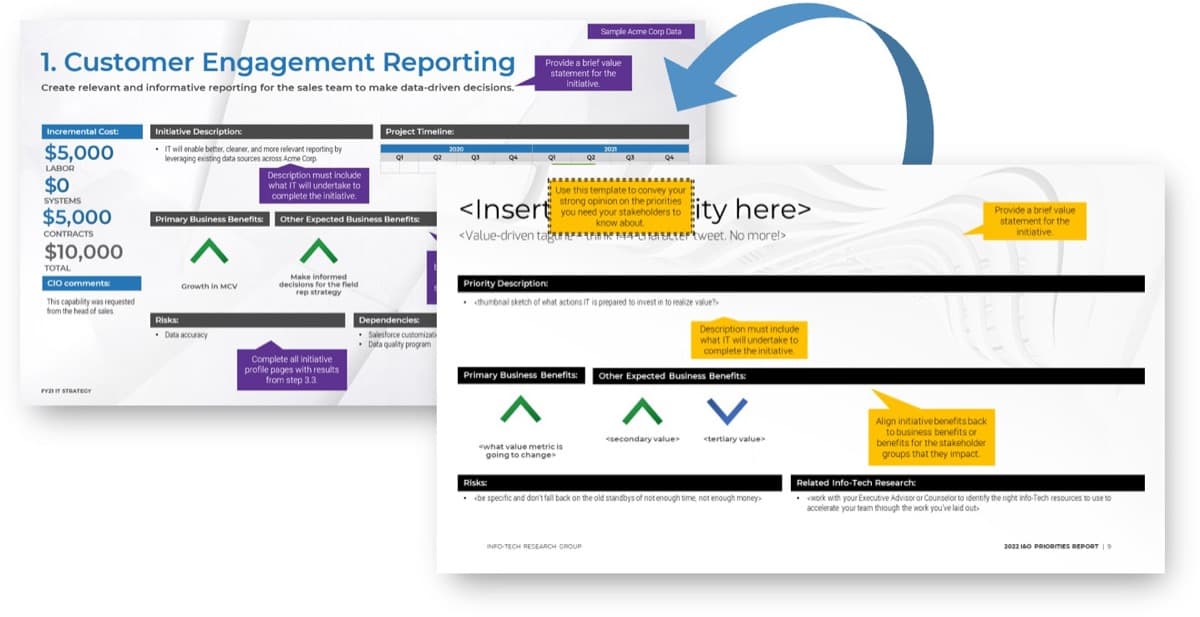
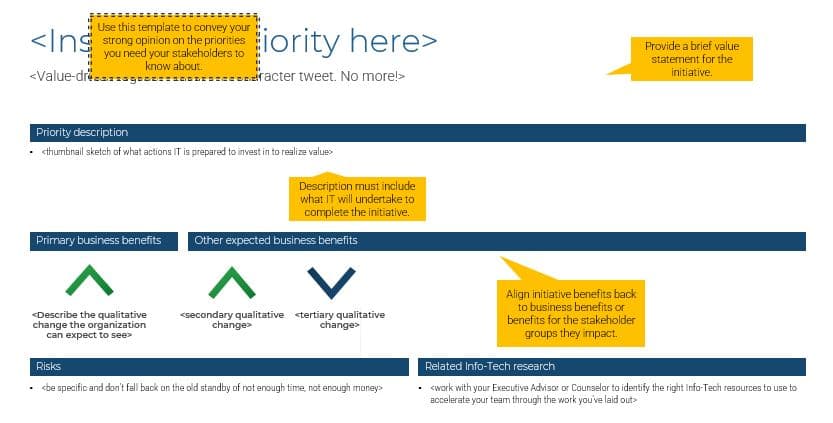
    Info-Tech can help! Align your priorities with our material on how to Build a Business-Aligned IT Strategy. Use a modified version of the Strategy Initiative Template (next slide) to convey your strong opinion on the priorities you need your stakeholders to know about. And do so in a way that is familiar so they will easily understand.

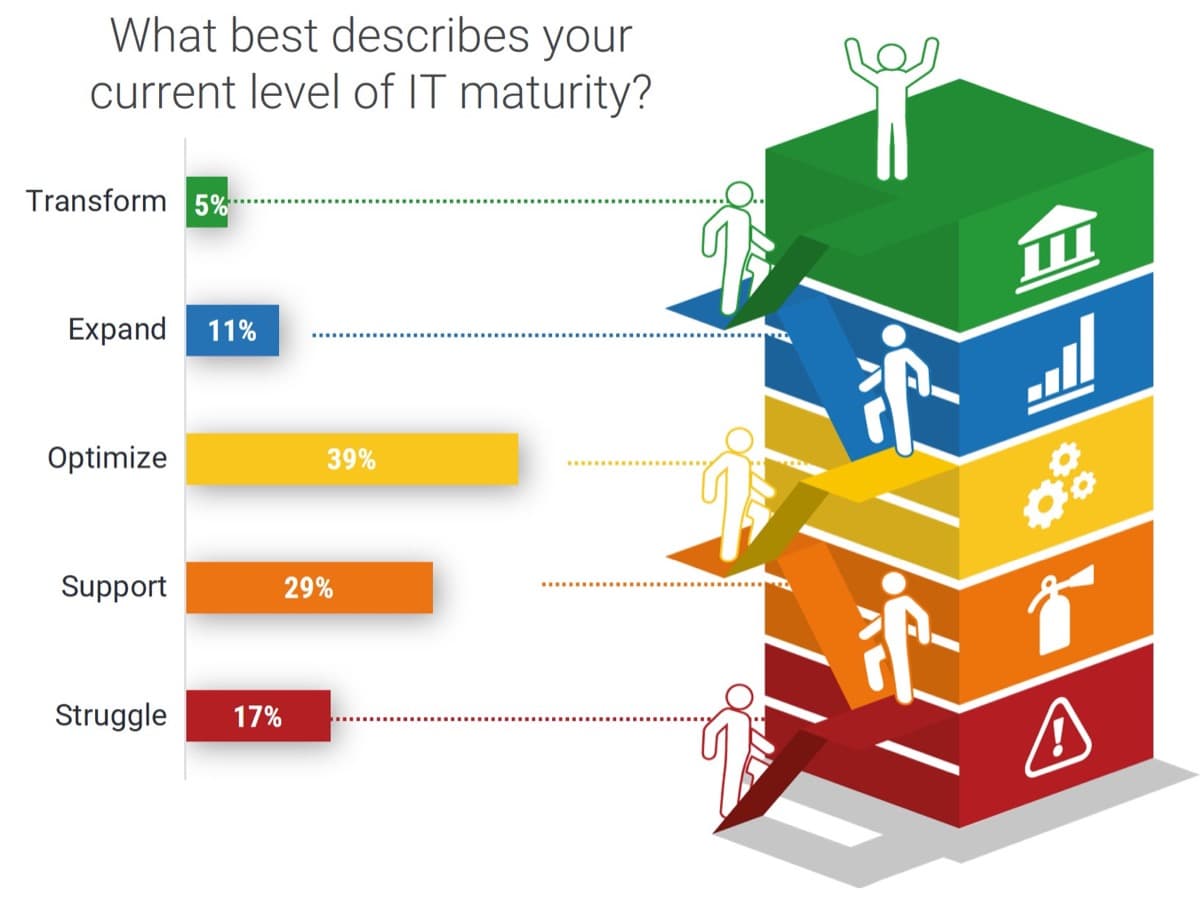
    The image contains a screenshot of Info-Tech's Maturity Ladder.
    Info-Tech 2023 Trends Survey Results

    Call your Executive Advisor or Counselor to help identify the one or two key messages you want to bring forward for success in 2023!

    Info-Tech IT Strategy Initiative Template, from the IT Strategy Presentation Template & Priorities Report Initiative Template

    .
    The image contains a screenshot of a template for your priorities.

    Protect from threats

    Get out of your silo. Forget your job description and just start doing what needs to be done.

    Enhance I&O Cybersecurity

    Produce ESG Reporting

    Recession Readiness

    Enhance cybersecurity response

    SIGNALS

    Cybersecurity incidents are
    a clear and present danger
    to I&O members.

    Cybersecurity incidents have
    a large financial impact
    on organizations.

    Related Info-Tech Research

    Of the surveyed I&O members, 53% identified cybersecurity incidents as the number one threat disrupting their operations in 2023. It’s understandable, as over 18% of surveyed I&O members experienced a cybersecurity incident in 2022. Alarmingly, 10% of surveyed I&O members didn’t know if they had a cybersecurity incident. The impact to the organization was with 14% of those incidents directly impacting their organizations for anywhere from 6 to 60 days.

    The 2022 report “Cost of a Data Breach” was conducted by IBM and the Ponemon Institute using data from 550 companies (across 17 countries) that experienced a security incident during a 12-month period ending in March 2022. It highlighted that the average total organizational cost of a security breach globally was USD 4.35M (locally these numbers expand to USA at USD 9.44M, Canada at USD 5.64, UK at USD 5.05M, Germany at USD 4.85M).

    (Source: IBM, 2022)

    Enhance cybersecurity response

    SIGNALS

    Organizations' exposure comes from internal and external sources.

    The right tools and process can reduce the impact of a cybersecurity incident.

    Related Info-Tech Research

    The IBM/Ponemon Institute report highlighted the following:

    • 59% of organizations didn’t deploy a zero-trust architecture on critical infrastructure to reduce exposure.
    • 19% of the breaches originated from within their business partner eco-system.
    • 45% were cloud-based.

    (Source: IBM, 2022)

    The IBM/Ponemon Institute report also identified technologies and procedures to reduce the fiscal impacts of cybersecurity breaches. Having a dedicated security incident response team with a regularly tested plan reduced the incident cost by an average of USD 2.66M. A fully implemented AI security deduction and response automation system can provide average incident savings of 27.6%.

    Enhance cybersecurity response

    SIGNALS

    Cybersecurity spending is a major and expanding expenditure for our members.

    Cybersecurity is going
    to include brand misinformation.

    For 36% of surveyed I&O members, cybersecurity consumed between 10-20% of their total budget in 2022. Moreover, cybersecurity defense funding is expected to increase for 57% of I&O members.

    A third of surveyed I&O members viewed misinformation as a major risk to their organization for 2023 and 2024. Only 38% of the I&O members reported that they will have software in place to monitor and manage social media posts.

    Increasing environment and regulatory complexity demands more sophisticated cybersecurity operations.

    Infrastructure teams must be expected to work alongside and integrate with cybersecurity operations.

    Enhance cybersecurity response

    CALL TO ACTION

    Get out of your I&O silo and form cross-functional cybersecurity teams.

    I&O priority actions

    Establish a cross-functional security steering committee to coordinate security processes and technologies. The complexity of managing security across modern applications, cloud, IoT, and network infrastructure that members operate is greater than ever before and requires coordinated teamwork.

    Contain the cyber threat with zero trust (ZT) architecture. Extend ZT to network and critical infrastructure to limit exposure.

    Leverage AI to build vigilant security intelligence. Smart I&O operators will make use of AI automation to augment their security technologies to help detect threats and contain security incidents on critical infrastructure.

    Enhance cybersecurity response

    I&O priority actions

    Build specialized cybersecurity incident management protocols with your service desk. Build integrated security focused teams within service desk operations that continually test and improve security incident response protocols internally and with specialized security vendors. In some organizations, security incident response teams extend beyond traditional infrastructure into social media. Work cross-functionally to determine the risk exposure to misinformation and incident response procedures.

    Treat lost or stolen equipment as a security incident. Develop hardware asset management protocols for tracking and reporting on these incidents and keep a record of equipment disposal. Implement tools that allow for remote deletion of data and report on lost or stolen equipment.

    Produce ESG reporting

    SIGNALS

    Government mandates present an operational risk to I&O members.

    ESG reporting is
    often incomplete.

    Related Info-Tech Research

    Surveyed members identified government-enacted policy changes to be a top risk to disrupting to their business operations in 2023. One of the trends identified by Info-Tech is that the impact of regulations on environmental, social, and governance (ESG) reporting are being rolled out by governments worldwide.

    Alarmingly, only 7% of surveyed members responded that they could very accurately report on their carbon footprint and 23% said they were not able to report accurately at all.

    Produce ESG reporting

    SIGNALS

    ESG mandates are being rolled out globally.

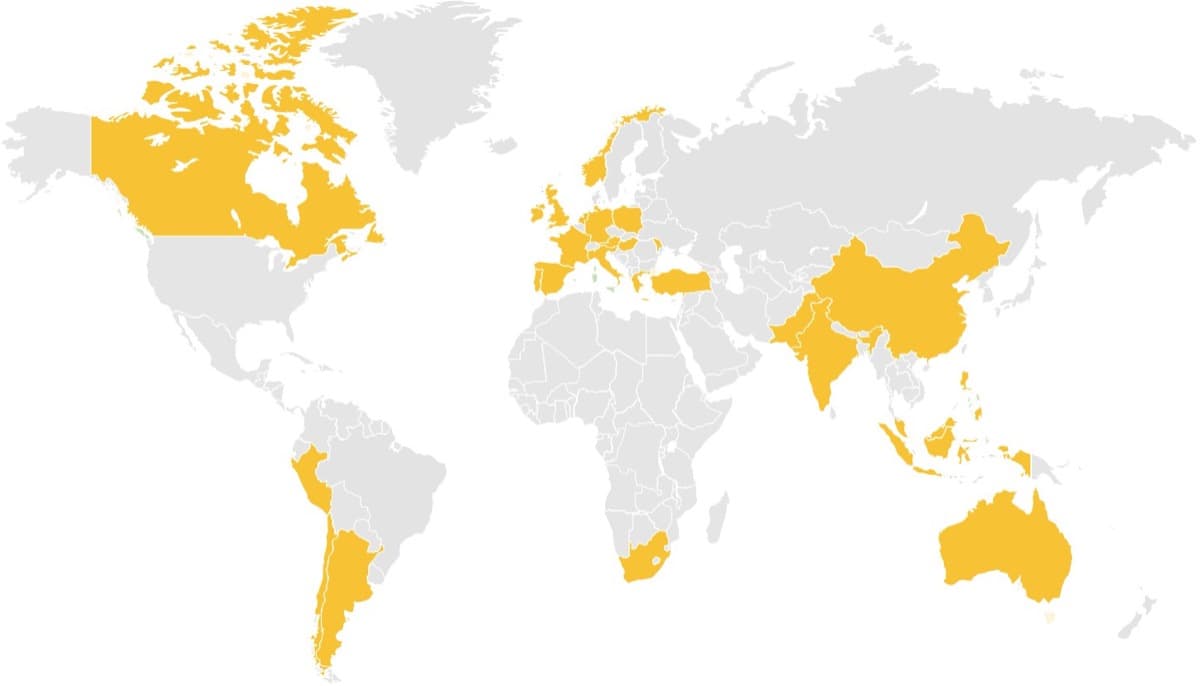
    ESG reporting has greatly expanded since a 2017 report by Task Force on Climate-Related Financial Disclosures (TCFD, 2017) which recommended that organizations disclose climate-related financial metrics for investors to appropriately price climate-related risks to share price. In 2021, the Swiss Finance Institute research paper (Sautner, 2021) identified 29 countries that require ESG reporting, primarily for larger public companies, financial institutions, and state-owned corporations.

    Global ESG mandates

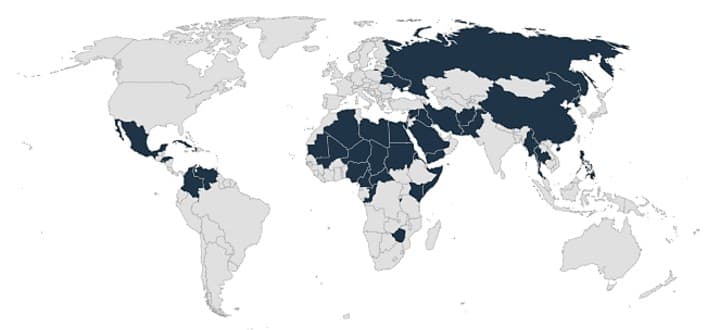
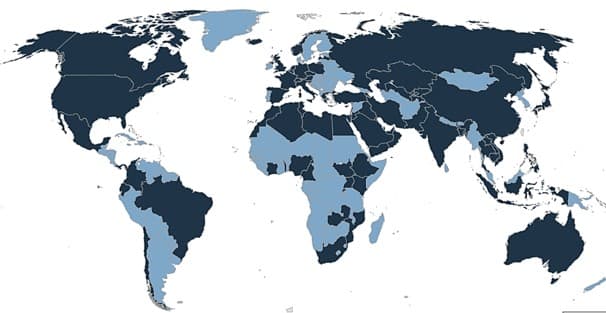
    The image contains a screenshot of a world map that demonstrates the Global ESG Mandates.

    29 nations with ESG mandates identified by the Swiss Finance Institute

    Produce ESG reporting

    SIGNALS

    ESG mandates are being rolled out globally.

    The EU has mandated ESG reporting for approximately 11,700 large public companies with more than 500 employees under the Non-Financial Reporting Directive (NFRD), since 2014. The EU is going to replace the NFRD with the Corporate Sustainability Reporting Directive (European Council, 2022), which has set a 3-year timetable for escalating the ESG reporting level to what is estimated to be about 75% of EU total turnover (WorldFavor, 2022).

    • 2024: Companies with 500 or more employees.
    • 2025: Companies with 250 or more employee or 40M EU in revenue/20M in total assets.
    • 2026: SMEs, smaller credit financial, and captive insurance institutions.

    It's been a long time since most enterprises had to report on things like power efficiency factors.

    But don't think that being in the cloud will insulate you from a renewed interest in ESG reporting.

    Produce ESG reporting

    CALL TO ACTION

    Being unprepared for new ESG reporting mandates without a clear and validated ESG reporting process puts your organization at risk.

    I&O priority actions

    Understand ESG risk exposure. Define the gap between what ESG reporting is required in your jurisdiction and current reporting capabilities to meet them. Build the I&O role with responsibility for ESG reporting.

    Include vendors in ESG reporting. Review infrastructure facilities with landlords, utilities, and hosting providers to see if they can provide ESG reporting on sustainable power generation, then map it to I&O power consumption as part of their contractual obligations. Ask equipment vendors to provide ESG reporting on manufacturing materials and energy consumption to boot-strap data collection.

    Implement a HAM process to track asset disposal and other types of e-waste. Update agreements with disposal vendors to get reporting on waste and recycle volumes.

    Produce ESG reporting

    I&O priority actions

    Implement an ESG reporting framework. There are five major ESG reporting frameworks being used globally. Select one of the frameworks below that makes sense for your organization, and implement it.

    ISO 14001 Environmental Management: Part of the ISO Technical Committee family of standards that allows your organization to understand its legal requirements to become certified in ESG.

    Global Reporting Initiative (GRI) Sustainability Reporting Standards: GRI has been developing ESG reporting standards since 1997. GRI provides a modular ESG framework applicable to all sizes and sectors of organizations worldwide.

    Principles for Responsible Investment: UN-developed framework for ESG reporting framework for disclosure in responsible investments.

    Sustainability Accounting Standards Board (SASB): ESG report framework to be used by investors.

    UN Global Compact: ESG reporting framework based on 10 principles that organizations can voluntarily contribute data to.

    Implement a HAM process to track asset disposal and other types of e-waste. Update agreements with disposal vendors to get reports on waste and recycle volumes.

    Recession readiness

    SIGNALS

    Managing accelerated technical debt.

    Recessionary pressures.

    Related Info-Tech Research

    I&O members experienced a spike in technical debt following the global pandemic economic shutdown, workforce displacement, and highly disrupted supply chains. 2023 presents a clear opportunity to work on these projects.

    The shortages in workforce and supply chain have accelerated inflation post pandemic. Central banks have started to slow down inflation in 2022 by raising interest rates. However, the World Bank has forecast a potential 2% rise in interest rates as the battle with inflation continues into 2023 and beyond, which could set off a global slowdown in GDP growth to 0.5%, qualifying as a recession. If interest rates continue to climb, I&O members may struggle with the higher cost of capital for their investments.

    (Source: World Bank Organization, 2022)

    Recession readiness

    SIGNALS

    I&O budgets expected to increase.

    Focused budgetary increases.

    Despite economists’ prediction of a looming recession and inflationary pressures, only 11% of I&O members surveyed indicated that they anticipated any reduction in IT budgets for 2023. In fact, 44% of I&O members expected an increase of IT budgets of between 6% and 30%.

    These increases in budget are not uniform across all investments. Surveyed I&O members indicated that the largest anticipated budget increases (compared to 2022) were in the areas of:

    • AI/machine learning ( +7.5%)
    • 5G (+7%)
    • Data Mesh/Fabric and Data Lake infrastructure (+5.7% and +4.4%, respectively)
    • Mixed reality technologies (augmented or virtual reality) (+3.3%)
    • Next generation cybersecurity (+1.7%)

    "2022 has been the first true opportunity to start getting caught up on technical debt stemming from the post pandemic supply chain and resource shortages. That catch-up is going to continue for some time.

    Unfortunately, the world isn't sitting still while doing that. In fact, we see new challenges around inflationary pressures. 2023 planning is going to be a balancing act between old and new projects."

    Paul Sparks,
    CTO at Brookshire Grocery Company

    Recession readiness

    SIGNALS

    Tough choices on budgetary spends.

    The responses indicated that I&O members expect decreased reinvestment for 2023 for the following:

    • API programming (-21.7%)
    • Cloud computing (-19.4%)
    • 44% of I&O members indicated if 2023 requires costs cutting, 5-20% of their cloud computing investment will be at risk of the chopping block!
    • Workforce management (-9.4%)
    • No-code /low-code infrastructure (-5.3%)

    Make sure you can clearly measure the value of all budgeted I&O activities.

    Anything that can't demonstrate clear value to leadership is potentially on the chopping block.

    Recession readiness

    CALL TO ACTION

    Get ahead of inflationary pressures with early budgetary planning, and identify the gap between the catch-up projects and required critical net new investments.

    II&O priority actions

    Hedge against inflation on infrastructure projects. Develop and communicate value-based strategies to lock in pricing and mitigate inflationary risk with vendors.

    Communicate value-add on all I&O budgeted items. Define an infrastructure roadmap to highlight which projects are technical debt and which are new strategic investments, and note their value to the organization.

    Look for cost saving technologies. Focus on I&O projects that automate services to increase productivity and optimize head count.

    Realize opportunities

    Build on a record of COVID-related innovation success and position the enterprise to take advantage of 2023.

    AI governance: Watching the watchers

    Data stewardship: Cornerstone of value

    Prep for a brave new metaverse

    AI governance: Watching the watchers

    SIGNALS

    Continued investment
    in AI technologies

    AI technology is permeating diverse I&O functional areas.

    Related Info-Tech Research

    About 32% of survey respondents who work in I&O said that they already invest in AI, and 40% intend to invest in 2023.

    I&O members have identified the following areas as the top five focal points for AI uses within their organizations.

    • Automated repetitive, low-level tasks
    • Business analytics or intelligence
    • Identification of risks and improvement of security response
    • Monitoring and governance
    • Sensor data analysis

    AI governance: Watching the watchers

    SIGNALS

    Consequences for misbehaving AI.

    I&O leaders can expect to have silos of AI in pockets scattered across the enterprise. Without oversight on the learning model and the data used for training and analytics there is a risk of overprovisioning, which could reduce the efficiency and effectiveness of AI models and results.

    This scale advantage of AI could result in operational inefficiencies without oversight. For example, bad governance means garbage in / garbage out. Which is worse: getting 100 outputs from a system with a 1% error rate, or getting 10,000 outputs from a system with an 1% error rate?

    These are just the operational issues; legally you can be on the hook, as well. The EU Parliament has issued a civil liability regime for AI (European Parliament, n.d.) which imposes liability to operators of AI systems, regardless of whether they acted with operational due diligence. Additionally, the IEEE (IEEE, 2019) is advocating for legal frameworks and accountability for AI that violates human rights and privacy laws and causes legal harm.

    Who is going to instill standards for AI Operations? Who is going to put in the mechanisms to validate and explain the output of AI black boxes?

    If you said it’s going to end up
    being Infrastructure and Operations – you were right!

    AI governance: Watching the watchers

    CALL TO ACTION

    Establish I&O within an AI governance program to build trust in AI results and behaviors and limit legal exposure.

    I&O priority actions

    Define who has overall AI accountability for AI governance within I&O. This role is responsible for establishing strategic governance metrics over AI use and results, and identifying liability risks.

    Maintain an inventory of AI use. Conduct an audit of where AI is used within I&O, and identify gaps in documentation and alignment with I&O processes and organizational values.

    Define an I&O success map. Provide transparency of AI use by generating pseudo code of AI models, and scorecard AI decision making with expected predictions and behavioral actions taken.

    AI governance: Watching the watchers

    Manage bias in AI decision making. Work with AI technology vendors to identify how unethical bias can enter the results, using operational data sets for validation prior to rollout.

    Protect AI data sets from manipulation. Generate new secure storage for AI technology audit trails on AI design making and results. Work with your security team to ensure data sets used by AI for training can’t be corrupted.

    Data governance: Cornerstone of value

    SIGNALS

    Data volumes grow
    with time.

    Data is seen as a source for generating new value.

    Related Info-Tech Research

    Of surveyed I&O members, 63% expected to see the data storage grow by at least 10% in 2023, and 15% expected a 30% or more growth in data storage volumes.

    I&O members identified the top three ways data brings value to the organization:

    • Helping reduce operational costs.
    • Presenting value-added to existing products and services.
    • Acquiring new customers.

    Data governance: Cornerstone of value

    SIGNALS

    Approach to data analysis is primarily done in-house.

    85% of surveyed I&O members are doing data analysis with custom-made or external tools. Interestingly, 10% of I&O members do not conduct any data analysis.

    Members are missing a formal data governance process.

    81% of surveyed I&O members do not have a formal or automated process for data governance. Ironically, 24% of members responded that they aim to have publicly accessible data-as-a-service or information repositories.

    Despite investment in data initiatives, organizations carry high levels of data debt.

    Info-Tech research, Establish Data Governance, points out that data debt, the accumulated cost associated with sub-optimal governance of data assets, is a problem for 78% of organizations.

    What the enterprise expects out of enterprise storage is much more complicated in 2023.

    Data protection and governance are non-negotiable aspects of enterprise storage, even when it’s unstructured.

    Data governance: Cornerstone of value

    SIGNALS

    Data quality is the primary driver for data governance.

    The data governance market
    is booming.

    Related Info-Tech Research

    In the 2022 Zaloni survey of data governance professionals, 71% indicated that consistent data quality was the top metric for data governance, followed by reduced time to insight and regulatory compliance.

    (Source: Zaloni DATAVERSITY, 2022)

    The Business Research Company determined that the global data governance market is expected to grow from $3.28 billion in 2022 to $7.42 billion in 2026 at a CAGR of 22.7% in response to 74 zettabytes of data in 2021, with a growth rate of 1.145 trillion MB of new data being created every day.

    (Source: Business Research Company, 2022)

    Data governance: Cornerstone of value

    CALL TO ACTION

    Develop a data governance program that includes an I&O data steward for oversight.

    I&O priority actions

    Establish an I&O data steward. Make data governance by establishing a data steward role with accountability for governance. The steward works collaboratively with DataOPs to control access to I&O data, enforce policies, and reduce the time to make use of the data.

    Define a comprehensive storage architecture. If you thought you had a data sprawl problem before, wait until you see the volume of data generated from IoT and Web 3.0 applications. Get ahead of the problem by creating an infrastructure roadmap for structured and unstructured data storage.

    Build a solid backbone for AI Operations using data quality best practices. Data quality is the foundation for generation of operational value from the data and artificial intelligence efforts. Focus on using a methodology to build a culture of data quality within I&O systems and applications that generate data rather than reactive fixes.

    Look to partner with third-party vendors for your master data management (MDM) efforts. Modern MDM vendors can work with your existing data fabrics/lake and help leverage your data governance policies into the cloud.

    Prep for a brave new metaverse

    SIGNALS

    From science fiction to science fact.

    The term metaverse was coined in 1992 by Neal Stephenson and is a common theme in science fiction. For most I&O surveyed professionals, the term metaverse conjures up more confusion than clarity, as it’s not one place, but multiple metaverse worlds. The primordial metaverse was focused on multiplayer gaming and some educational experiences. It wasn’t until recently that it gained a critical mass in the fashion and entertainment industries with the use of non-fungible tokens (NFT). The pandemic created a unique opportunity for metaverse-related technologies to expand Web 3.0.

    Related Info-Tech Research

    Prep for a brave new metaverse

    SIGNALS

    Collaboration and beyond.

    On one hand, metaverse technologies virtual reality(VR)/augmented reality (AR) headsets can be a method of collaborating internally within a single organization. About 10% of our surveyed I&O members engaged this type of collaborative metaverse in 2022, with another 24% looking to run proof of concept projects in 2023. However, there is a much larger terrain for metaverse projects outside of workforce collaboration, which 17% of surveyed I&O members are planning to engage with in 2023.

    These are sophisticated new metaverse worlds, and digital twins of production environments are being created for B2B collaboration, operations, engineering, healthcare, architecture, and education that include the use of block chain, NFTs, smart contracts, and other Web 3.0 technologies

    “They are the audiovisual bodies that people use to communicate with each other in the Metaverse.”

    Neal Stephenson,
    Snow Crash 1992

    Prep for a brave new metaverse

    SIGNALS

    Metaverse requires multidimensional security.

    Security in the context of the metaverse presents new challenges to I&O. The infrastructure that runs the metaverse is still vulnerable to “traditional” security threats. New attack vectors include financial and identity fraud, privacy and data loss, along with new cyber-physical threats which are predicted to occur as the metaverse begins to integrate with IoT and other 3D objects in the physical world.

    The ultimate in "not a product" – the metaverse promises to be a hodgepodge of badly standardized technologies for the near future.

    Be prepared to take care of pets and not cattle for the foreseeable future, but keep putting the fencing around the ranch.

    Prep for a brave new metaverse

    SIGNALS

    Generating new wave of sophisticated engineering coming.

    Economics boom around metaverse set to explode.

    Related Info-Tech Research

    Beyond the current online educational resources, there are reputable universities around the world, including Stanford University, that are offering courses on metaverse and Web 3.0 concepts.

    (Source: Arti, 2022)

    So, what’s providing the impetus for all this activity and investment? Economics. In their 2022 report, Metaverse and Money, Citi estimated that the economic value of the metaverse(s) will have 900M to 1B VR/AR users and 5 billion Web 3.0 users with market sizes of $1-2T and $8-$13T, respectively. Yes, that’s a “T” for Trillions.

    (Source: Ghose, 2022)

    Prep for a brave new metaverse

    CALL TO ACTION

    Ready or not, the metaverse is coming to an infrastructure near you. Start expanding I&O technologies and processes to support a metaverse infrastructure.

    I&O priority actions

    Develop a plan for network upgrades.

    A truly immersive VR/AR experience requires very low latency. Identify gaps and develop a plan to enhance your network infrastructure surrounding your metaverse space(s) and end users.

    Extend security posture into the metaverse.

    Securing the infrastructure that runs your metaverse is going to extend the end-user equipment used to navigate it. More importantly, security policies need to encompass the avatars that navigate it and the spatial web that they interact with, which can include physical world items like IoT.

    Prep for a brave new metaverse

    I&O priority actions

    Metaverse theft prevention

    Leverage existing strategies to identify management in the metaverse. Privacy policies need to extend their focus to data loss prevention within the metaverse.

    Collaborate

    The skill set required to build, deploy, manage, and support the metaverse is complex. Develop a metaverse support organization that extends beyond I&O functions into security, DevOps, and end-user experiences.

    Educate

    Web 3.0 technologies and business models are complex. Education of I&O technical- and commerce-focused team members is going to help prevent you from getting blindsided. Seek out specialized training programs for technical staff and strategic education for executives, like the Wharton School of Business certification program.

    Authors

    John Annand

    Theo Antoniadis

    John Annand

    Principal Research Director

    Theo Antoniadis

    Principal Research Director

    Contributors

    Paul Sparks,
    CTO at Brookshire Grocery Company

    2 Anonymous Contributors

    Figuring out the true nature of the “Turbo” button of his 486DX100 launched John on a 20-year career in managed services and solution architecture, exploring the secrets of HPC, virtualization, and DIY WANs built with banks of USR TotalControl modems. Today he focuses his research and advisory on software-defined infrastructure technologies, strategy, organization, and service design in an increasingly Agile and DevOps world.

    Theo has decades of operational and project management experience with start-ups and multinationals across North America and Europe. He has held various consulting, IT management and operations leadership positions within telecommunications, SaaS, and software companies.

    Bibliography

    “3 Cybersecurity Trends that are Changing Financial Data Management." FIMA US. Accessed August 2022.
    Arti. “While much of the world is just discovering the Metaverse, a number of universities have already established centers for studying Web 3." Analytics Insight. 10 July 2022.
    “Artificial intelligence (AI) for cybersecurity." IBM. Accessed September 2022
    “Business in the Metaverse Economy." Wharton School of University of Pennsylvania. Accessed October 2022.
    “Cost of a data breach 2022: A million-dollar race to detect and respond." IBM. Accessed September 2022.
    “Countries affected by mandatory ESG reporting – here’s the list." New Zealand Ministry of Business, Innovation & Employment. Accessed September 2022.
    “Countries affected by mandatory ESG reporting – here’s the list.” WorldFavor. Accessed September 2022.
    Crenshaw, Caroline A. “SEC Proposes to Enhance Disclosures by Certain Investment Advisers and Investment Companies About ESG Investment Practices." U.S. Securities and Exchange Commission. May 2022.
    “Cutting through the metaverse hype: Practical guidance and use cases for business." Avanade. Accessed October 2022.
    “Data Governance Global Market Sees Growth Rate Of 25% Through 2022." The Business Research Company. August 2022.
    “DIRECTIVE 2014/95/EU OF THE EUROPEAN PARLIAMENT AND OF THE COUNCIL of 22 October 2014 amending Directive 2013/34/EU as regards disclosure of non-financial and diversity information by certain large undertakings and groups." UER-Lex. Accessed September 2022.
    "Ethically Aligned Design: A Vision for Prioritizing Human Well-being with Autonomous and Intelligent Systems." IEEE. March 2019.
    “European Parliament resolution of 20 October 2020 with recommendations to the Commission on a civil liability regime for artificial intelligence." European Parliament. Accessed October 2022.
    Ghose, Ronit et al. "Metaverse and Money." Citi GPS. March 2022.
    Hernandez, Roberto, et al. “Demystifying the metaverse." PWC. Accessed August 2022.
    Info-Tech Trends Report Survey, 2023; N=813.
    “ISO 14000 Family: Environmental Management." ISO. Accessed October 2022.
    Knight, Michelle & Bishop, Annie, ”The 2022 State of Cloud Data Governance.“ Zaloni DATAVERSITY. 2022.

    Bibliography

    Kompella, Kashyap, “What is AI governance and why do you need it?“ TechTarget. March 2022.
    “Management of electronic waste worldwide in 2019, by method." Statista. 2022.
    “Model Artificial Intelligence Governance Framework and Assessment Guide.“ World Economic Forum. Accessed September 2022.
    “Model Artificial Intelligence Governance Framework." PDPC Singapore. Accessed October 2022.
    “New rules on corporate sustainability reporting: provisional political agreement between the Council and the European Parliament.“ European Council. June 2022.
    "OECD Economic Outlook Volume 2022." OECD iLibrary. June 2022.
    "Recommendations of the Task Force on Climate-related Financial Disclosures." TCFD. Accessed August 2022.
    “Risk of Global Recession in 2023 Rises Amid Simultaneous Rate Hikes.” World Bank Organization. September 2022.
    Sautner, Zacharias, et al. “The Effects of Mandatory ESG Disclosure around the World.” SSRN. November 2021.
    Sondergaard, Peter. “AI GOVERNANCE – WHAT ARE THE KPIS? AND WHO IS ACCOUNTABLE?“ The Sondergaard Group. November 2019.
    Srivastavam Sudeep, “How can your business enter the Metaverse?." Appinventiv.
    September 2022.
    “Standards Overview." SASB. Accessed October 2022.
    Stephenson, Neal. Snow Crash. Bantam Books, 1992.
    “Sustainability Reporting Standards." Global Reporting Initiative. Accessed October 2022.
    “The Ten Principles of the UN Global Compact." UN Global Compact. Accessed October 2022.
    Tian Tong Lee, Sheryl. "China Unveils ESG Reporting Guidelines to Catch Peers.” Bloomberg. May 2022.
    “What are the Principles for Responsible Investment?" UNPRI. Accessed October 2022.
    "What is the EU's Corporate Sustainability Reporting Directive (CSRD)?" WorldFavor.
    June 2022.
    West, Darrell M. “Six Steps to Responsible AI in the Federal Government.“ Brookings Institution. March 2022. Web.

    Secrets of SAP S-4HANA Licensing

    • Buy Link or Shortcode: {j2store}231|cart{/j2store}
    • member rating overall impact: 9.0/10 Overall Impact
    • member rating average dollars saved: $25,000 Average $ Saved
    • member rating average days saved: 10 Average Days Saved
    • Parent Category Name: Vendor Management
    • Parent Category Link: /vendor-management
    • With the relatively slow uptake of the S/4HANA platform, the pressure is immense for SAP to maintain revenue growth.
    • SAP’s definitions and licensing rules are complex and vague, making it extremely difficult to purchase with confidence while remaining compliant.
    • Aggressive audit tactics may be used to speed up the move to HANA.

    Our Advice

    Critical Insight

    • Mapping SAP products to HANA can be highly complex, leading to overspending and an inability to reduce future spend.
    • The deployment model chosen will directly impact commercial pathways forward.
    • Beware of digital (indirect) access licensing and compliance concerns.
    • Without having a holistic negotiation strategy, it is easy to hit a common obstacle and land into SAP’s playbook, requiring further spend.

    Impact and Result

    • Build a business case to evaluate S/4HANA.
    • Understand the S/4HANA roadmap and map current functionality to ensure compatibility.
    • Understand negotiating pricing and commercial terms.
    • Learn the “SAP way” of conducting business, which includes a best-in-class sales structure, unique contracts, and license use policies combined with a hyper-aggressive compliance function.

    Secrets of SAP S/4HANA Licensing Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should explore the secrets of SAP S/4HANA licensing, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Establish requirements

    Determining SAP’s fit within your organization is critical. Start off by building a business case to assess overarching drivers and justification for change, any net new business benefits and long-term sustainability. Oftentimes the ROI is negative, but the investment sets the stage for long-term growth.

    2. Evaluate licensing options

    Your deployment model is more important than you think. Selecting a deployment model will dictate your licensing options followed by your contractual pathways forward.

    • SAP License Summary and Analysis Tool
    • SAP Digital Access Licensing Pricing Tool

    3. Negotiation and license management

    Know what’s in the contract. Each customer agreement is different and there may be existing terms that are beneficial. Depending on how much is spent, anything can be up for negation.

    • SAP S/4HANA Terms and Conditions Evaluator
    [infographic]

    Knowledge Management

    • Buy Link or Shortcode: {j2store}33|cart{/j2store}
    • Related Products: {j2store}33|crosssells{/j2store}
    • member rating overall impact: 9.0/10
    • member rating average dollars saved: $10,000
    • member rating average days saved: 2
    • Parent Category Name: People and Resources
    • Parent Category Link: /people-and-resources
    Mitigate Key IT Employee Knowledge Loss

    Implement Risk-Based Vulnerability Management

    • Buy Link or Shortcode: {j2store}296|cart{/j2store}
    • member rating overall impact: 9.2/10 Overall Impact
    • member rating average dollars saved: $122,947 Average $ Saved
    • member rating average days saved: 34 Average Days Saved
    • Parent Category Name: Threat Intelligence & Incident Response
    • Parent Category Link: /threat-intelligence-incident-response
    • Vulnerability scanners, industry alerts, and penetration tests are revealing more and more vulnerabilities, and it is unclear how to manage them.
    • Organizations are struggling to prioritize the vulnerabilities for remediation, as there are many factors to consider, including the threat of the vulnerability and the potential remediation option itself.

    Our Advice

    Critical Insight

    • Patches are often considered the only answer to vulnerabilities, but these are not always the most suitable solution.
    • Vulnerability management does not equal patch management. It includes identifying and assessing the risk of the vulnerability, and then selecting a remediation option which goes beyond just patching alone.
    • There is more than one way to tackle the problem. Leverage your existing security controls to protect the organization.

    Impact and Result

    • After this blueprint, you will have created a full vulnerability management program that allows you to take a risk-based approach to vulnerability remediation.
    • Assessing a vulnerability’s risk will enable you to properly determine the true urgency of a vulnerability within the context of your organization; this ensures you are not just blindly following what the tool is reporting.
    • The risk-based approach allows you to prioritize your discovered vulnerabilities and take immediate action on critical and high vulnerabilities, while allowing your standard remediation cycle to address the medium to low vulnerabilities.
    • With your program defined and developed, you now need to configure your vulnerability scanning tool, or acquire one if you don’t already have a tool in place.
    • Lastly, while vulnerability management will help address your systems and applications, how do you know if you are secure from external malicious actors? Penetration testing will offer visibility, allowing you to plug those holes and attain an environment with a smaller risk surface.

    Implement Risk-Based Vulnerability Management Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should design and implement a vulnerability management program, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    • Implement Risk-Based Vulnerability Management – Phases 1-4

    1. Identify vulnerability sources

    Begin the project by creating a vulnerability management team and determine how vulnerabilities will be identified through scanners, penetration tests, third-party sources, and incidents.

    • Vulnerability Management SOP Template

    2. Triage vulnerabilities and assign priorities

    Determine how vulnerabilities will be triaged and evaluated based on intrinsic qualities and how they may compromise business functions and data sensitivity.

    • Vulnerability Tracking Tool
    • Vulnerability Management Risk Assessment Tool
    • Vulnerability Management Workflow (Visio)
    • Vulnerability Management Workflow (PDF)

    3. Remediate vulnerabilities

    Address the vulnerabilities based on their level of risk. Patching isn't the only risk mitigation action; some systems simply cannot be patched, but other options are available. Reduce the risk down to medium/low levels and engage your regular operational processes to deal with the latter.


    4. Measure and formalize

    Evolve the program continually by developing metrics and formalizing a policy.

    • Vulnerability Management Policy Template
    • Vulnerability Scanning Tool RFP Template
    • Penetration Test RFP Template

    Infographic

    Workshop: Implement Risk-Based Vulnerability Management

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Identify Vulnerability Sources

    The Purpose

    Establish a common understanding of vulnerability management, and define the roles, scope, and information sources of vulnerability detection.

    Key Benefits Achieved

    Attain visibility on all of the vulnerability information sources, and a common understanding of vulnerability management and its scope.

    Activities

    1.1 Define the scope & boundary of your organization’s security program.

    1.2 Assign responsibility for vulnerability identification and remediation.

    1.3 Develop a monitoring and review process of third-party vulnerability sources.

    1.4 Review incident management and vulnerability management

    Outputs

    Defined scope and boundaries of the IT security program

    Roles and responsibilities defined for member groups

    Process for review of third-party vulnerability sources

    Alignment of vulnerability management program with existing incident management processes

    2 Triage and Prioritize

    The Purpose

    We will examine the elements that you will use to triage and analyze vulnerabilities, prioritizing using a risk-based approach and prepare for remediation options.

    Key Benefits Achieved

    A consistent, documented process for the evaluation of vulnerabilities in your environment.

    Activities

    2.1 Evaluate your identified vulnerabilities.

    2.2 Determine high-level business criticality.

    2.3 Determine your high-level data classifications.

    2.4 Document your defense-in-depth controls.

    2.5 Build a classification scheme to consistently assess impact.

    2.6 Build a classification scheme to consistently assess likelihood.

    Outputs

    Adjusted workflow to reflect your current processes

    List of business operations and their criticality and impact to the business

    Adjusted workflow to reflect your current processes

    List of defense-in-depth controls

    Vulnerability Management Risk Assessment tool formatted to your organization

    Vulnerability Management Risk Assessment tool formatted to your organization

    3 Remediate Vulnerabilities

    The Purpose

    Identifying potential remediation options.

    Developing criteria for each option in regard to when to use and when to avoid.

    Establishing exception procedure for testing and remediation.

    Documenting the implementation of remediation and verification.

    Key Benefits Achieved

    Identifying and selecting the remediation option to be used

    Determining what to do when a patch or update is not available

    Scheduling and executing the remediation activity

    Planning continuous improvement

    Activities

    3.1 Develop risk and remediation action.

    Outputs

    List of remediation options sorted into “when to use” and “when to avoid” lists

    4 Measure and Formalize

    The Purpose

    You will determine what ought to be measured to track the success of your vulnerability management program.

    If you lack a scanning tool this phase will help you determine tool selection.

    Lastly, penetration testing is a good next step to consider once you have your vulnerability management program well underway.

    Key Benefits Achieved

    Outline of metrics that you can then configure your vulnerability scanning tool to report on.

    Development of an inaugural policy covering vulnerability management.

    The provisions needed for you to create and deploy an RFP for a vulnerability management tool.

    An understanding of penetration testing, and guidance on how to get started if there is interest to do so.

    Activities

    4.1 Measure your program with metrics, KPIs, and CSFs.

    4.2 Update the vulnerability management policy.

    4.3 Create an RFP for vulnerability scanning tools.

    4.4 Create an RFP for penetration tests.

    Outputs

    List of relevant metrics to track, and the KPIs, CSFs, and business goals for.

    Completed Vulnerability Management Policy

    Completed Request for Proposal (RFP) document that can be distributed to vendor proponents

    Completed Request for Proposal (RFP) document that can be distributed to vendor proponents

    Further reading

    Implement Risk-Based Vulnerability Management

    Get off the patching merry-go-round and start mitigating risk!

    Table of Contents

    4 Analyst Perspective

    5 Executive Summary

    6 Common Obstacles

    8 Risk-based approach to vulnerability management

    16 Step 1.1: Vulnerability management defined

    24 Step 1.2: Defining scope and roles

    34 Step 1.3: Cloud considerations for vulnerability management

    33 Step 1.4: Vulnerability detection

    46 Step 2.1: Triage vulnerabilities

    51 Step 2.2: Determine high-level business criticality

    56 Step 2.3: Consider current security posture

    61 Step 2.4: Risk assessment of vulnerabilities

    71 Step 3.1: Assessing remediation options

    Table of Contents

    80 Step 3.2: Scheduling and executing remediation

    85 Step 3.3: Continuous improvement

    89 Step 4.1: Metrics, KPIs, and CSFs

    94 Step 4.2: Vulnerability management policy

    97 Step 4.3: Select & implement a scanning tool

    107 Step 4.4: Penetration testing

    118 Summary of accomplishment

    119 Additional Support

    120 Bibliography

    Analyst Perspective

    Vulnerabilities will always be present. Know the unknowns!

    In this age of discovery, technology changes at such a rapid pace. New things are discovered, both in new technology and in old. The pace of change can often be very confusing as to where to start and what to do.

    The ever-changing nature of technology means that vulnerabilities will always be present. Taking measures to address these completely will consume all your department’s time and resources. That, and your efforts will quickly become stale as new vulnerabilities are uncovered. Besides, what about the systems that simply can’t be patched? The key is to understand the vulnerabilities and the levels of risk they pose to your organization, to prioritize effectively and to look beyond patching.

    A risk-based approach to vulnerability management will ensure you are prioritizing appropriately and protecting the business. Reduce the risk surface!

    Vulnerability management is more than just systems and application patching. It is a full process that includes patching, compensating controls, segmentation, segregation, and heightened diligence in security monitoring.

    Jimmy Tom, Research Advisor – Security, Privacy, Risk, and Compliance, Info-Tech Research Group. Jimmy Tom
    Research Advisor – Security, Privacy, Risk, and Compliance
    Info-Tech Research Group

    Executive Summary

    Your Challenge

    Vulnerability scanners, industry alerts, and penetration tests are revealing more and more vulnerabilities, and it is unclear how to manage them.

    Organizations are struggling to prioritize the vulnerabilities for remediation, as there are many factors to consider, including the threat of the vulnerability and the potential remediation option.

    Common Obstacles

    Patches are often seen as the answer to vulnerabilities, but these are not always the most suitable solution.

    Some systems deemed vulnerable simply cannot be patched or easily replaced.

    Companies are unaware of the risk implications that come from leaving the vulnerability open and from the remediation option itself.

    Info-Tech’s Approach

    Design and implement a vulnerability management program that identifies, prioritizes, and remediates vulnerabilities.

    Understand what needs to be considered when implementing remediation options, including patches, configuration changes, and defense-in-depth controls.

    Build a process that is easy to understand and allows vulnerabilities to be remediated proactively, instead of in an ad hoc fashion.

    Info-Tech Insight

    Vulnerability management does not always equal patch management. There is more than one way to tackle the problem, particularly if a system cannot be easily patched or replaced. If a vulnerability cannot be completely remediated, steps to reduce the risk to a tolerable level must be taken.

    Common obstacles

    These barriers make vulnerability management difficult to address for many organizations:
    • The value of vulnerability management is not well articulated in many organizations. As a result, investment in vulnerability scanning technology is often insufficient.
    • Many organizations feel that a “patch everything” approach is the most effective path.
    • Vulnerability management is commonly misunderstood as being a process that only supports patch management.
    • There is often misalignment between SecOps and ITOps in remediation action and priority, affecting the timeliness of remediation.
    CVSS Score Distribution From the National Vulnerability Database: Pie Charts presenting the CVSS Core Distribution for the National Vulnerability Database. The left circle represents 'V3' and the right 'V2', where V3 has an extra option for 'Critical', above 'High', 'Medium', and 'Low', and V2 does not.
    (Source: NIST National Vulnerability Database Dashboard)

    Leverage risk to sort, triage, and prioritize vulnerabilities

    Reduce your risk surface to avoid cost to your business; everything else is table stakes.

    Reduce the critical and high vulnerabilities below the risk threshold and operationalize the remediation of medium/low vulnerabilities by following your effective vulnerability management program cycles.

    Identify vulnerability sources

    An inventory of your scanning tool and vulnerability threat intelligence data sources will help you determine a viable strategy for addressing vulnerabilities. Defining roles and responsibilities ahead of time will ensure you are not left scrambling when dealing with vulnerabilities.

    Triage and prioritize

    Bring the vulnerabilities into context by assessing vulnerabilities based on your security posture and mechanisms and not just what your data sources report. This will allow you to gauge the true urgency of the vulnerabilities based on risk and determine an effective mitigation plan.

    Remediate vulnerabilities

    Address the vulnerabilities based on their level of risk. Patching isn't the only risk mitigation action; some systems simply cannot be patched, but other options are available.

    Reduce the risk down to medium/low levels and engage your regular operational processes to deal with the latter.

    Measure and formalize

    Upon implementation of the program, measure with metrics to ensure that the program is successful. Improve the program with each iteration of vulnerability mitigation to ensure continuous improvement.

    Tactical Insight 1

    All actions to address vulnerabilities should be based on risk and the organization’s established risk tolerance.

    Tactical Insight 2

    Reduce the risk surface down below the risk threshold.

    The industry has shifted to a risk-based approach

    Traditional vulnerability management is no longer viable.

    “For those of us in the vulnerability management space, ensuring that money, resources, and time are strategically spent is both imperative and difficult. Resources are dwindling fast, but the vulnerability problem sure isn’t.” (Kenna Security)

    “Using vulnerability scanners to identify unpatched software is no longer enough. Keeping devices, networks, and digital assets safe takes a much broader, risk-based vulnerability management strategy – one that includes vulnerability assessment and mitigation actions that touch the entire ecosystem.” (Balbix)

    “Unlike legacy vulnerability management, risk-based vulnerability management goes beyond just discovering vulnerabilities. It helps you understand vulnerability risks with threat context and insight into potential business impact.” (Tenable)

    “A common mistake when prioritizing patching is equating a vulnerability’s Common Vulnerability Scoring System (CVSS) score with risk. Although CVSS scores can provide useful insight into the anatomy of a vulnerability and how it might behave if weaponized, they are standardized and thus don’t reflect either of the highly situational variables — namely, weaponization likelihood and potential impact — that factor into the risk the vulnerability poses to an organization.” (SecurityWeek)

    Why a take risk-based approach?

    Vulnerabilities, by the numbers

    60% — In 2019, 60% of breaches were due to unpatched vulnerabilities.

    74% — In the same survey, 74% of survey responses said they cannot take down critical applications and systems to patch them quickly. (Source: SecurityBoulevard, 2019)

    Info-Tech Insight

    Taking a risk-based approach will allow you to focus on mitigating risk, rather than “just patching” your environment.

    The average cost of a breach in 2020 is $3.86 million, and “…the price tag was much less for mature companies and industries and far higher for firms that had lackluster security automation and incident response processes.” (Dark Reading)

    Vulnerability Management

    A risk-based approach

    Reduce the risk surface to avoid cost to your business, everything else is table stakes

    Logo for Info-Tech.
    Logo for #iTRG.

    1

    Identify

    4

    Address

      Mitigate the risk surface by reducing the time across the phases › Mitigate the risk by implementing:
    • patch systems & apps
    • compensating controls
    • systems and apps hardening
    • systems segregation
    Chart presenting an example of 'Risk Surface' with the axes 'Risk Level' and 'Time' with lines created by individual risks. The highlighted line begins in 'Critical' and eventually drops to low. The area between the line and your organization's risk tolerance is labelled 'Risk Surface'.

    Objective: reduce risk surface by reducing time to address

    Your organization's risk tolerance threshold

      Identify vulnerability management scanning tools & external threat intel sources (Mitre CVE, US-CERT, vendor alerts, etc.) Vulnerability information feeds:
    • scanning tool
    • external threat intel
    • internal threat intel

    2

    Analyze

      Assign actual risk (impact x urgency) to the organization based on current security posture

    Triage based on risk ›

    Your organization's risk tolerance threshold

    Risk tolerance threshold map with axes 'Impact' and 'Likelihood'. High levels of one and low levels of the other, or medium levels of both, is 'Medium', High level of one and Medium levels of the other is 'High', and High levels of both is 'Critical'.

    3

    Assess

      Plan risk mitigation strategy › Consider:
    • risk tolerance
    • compensating controls
    • business impact

    Info-Tech’s vulnerability management methodology

    Focus on developing the most efficient processes.

    Vulnerability management isn’t “old school.”

    The vulnerability management market is relatively mature; however, vulnerability management remains a very relevant and challenging topic.

    Security practitioners are inundated with the advice they need to prioritize their vulnerabilities. Every vulnerability scanning vendor will proclaim their ability to prioritize the identified vulnerabilities.

    Third-party prioritization methodology can’t be effectively applied across all organizations. Each organization is too unique with different constraints. No tool or service can account for these variables.

    Equation to find 'Vulnerability Priority'.

    When patching is not possible, other options exist: configuration changes (hardening), defense-in-depth, compensating controls, and even elevated security monitoring are possible options.

    Info-Tech Insight

    Vulnerability management is not only patch management. Patching is only one aspect.

    Blueprint deliverables

    Each step of this blueprint is accompanied by supporting deliverables to help you accomplish your goals:

    Key deliverable:

    Vulnerability Management SOP

    The Standard operating procedure (SOP) will comprise the end-to-end description of the program: roles & responsibilities, data flow, and expected outcomes of the program.

    Sample of the key deliverable, Vulnerability Management SOP.
    Vulnerability Management Policy

    Template for your vulnerability management policy.

    Sample of the Vulnerability Management Policy blueprint. Vulnerability Tracking Tool

    This tool offers a template to track vulnerabilities and how they are remedied.

    Sample of the Vulnerability Tracking Tool blueprint.
    Vulnerability Scanning RFP Template

    Request for proposal template for the selection of a vulnerability scanning tool.

    Sample of the Vulnerability Scanning RFP Template blueprint. Vulnerability Risk Assessment Tool

    Methodology to assess vulnerability risk by determining impact and likelihood.

    Sample of the Vulnerability Risk Assessment Tool blueprint.

    Blueprint benefits

    IT Benefits

    • A standardized, consistent methodology to assess, prioritize, and remediate vulnerabilities.
    • A risk-based approach that aligns with what’s important to the business.
    • A way of dealing with the high volumes of vulnerabilities that your scanning tool is reporting.
    • Identification of “where to start” in terms of vulnerability management.
    • Ability to not lose yourself in the patch madness but rather take a sound approach to scheduling and prioritizing patches and updates.
    • Knowledge of what to do when patching is simply not possible or feasible.

    Business Benefits

    • Alignment with IT in ensuring that business processes are only interrupted when absolutely necessary while maintaining a regular cadence of vulnerability remediation.
    • A consistent program that the business can plan around and predict when interruptions will occur.
    • IT’s new approach being integrated with existing IT operations processes, offering the most efficient yet expedient method of dealing with vulnerabilities.

    Info-Tech’s process can save significant financial resources

    Phase Measured Value
    Phase 1: Identify vulnerability sources
      Define the process, scope, roles, vulnerability sources, and current state
      • Consultant at $100 an hour for 16 hours = $1,600
    Phase 2: Triage vulnerabilities and assign urgencies
      Establish triaging and vulnerability evaluation process
      • Consultant at $100 an hour for 16 hours = $1,600
      Determine high-level business criticality and data classifications
      • Consultant at $100 an hour for 40 hours = $4,000
      Assign urgencies to vulnerabilities
      • Consultant at $100 an hour for 8 hours = $800
    Phase 3: Remediate vulnerabilities
      Prepare documentation for the vulnerability process
      • Consultant at $100 an hour for 8 hours = $800
      Establish defense-in-depth modelling
      • Consultant at $100 an hour for 24 hours = $2,400
      Identify remediation options and establish criteria for use
      • Consultant at $100 an hour for 40 hours = $4,000
      Formalize backup and testing procedures, including exceptions
      • Consultant at $100 an hour for 8 hours = $800
      Remediate vulnerabilities and verify
      • Consultant at $100 an hour for 24 hours = $2,400
    Phase 4: Continually improve the vulnerability management process
      Establish a metrics program for vulnerability management
      • Consultant at $100 an hour for 16 hours = $1,600
      Update vulnerability management policy
      • Consultant at $100 an hour for 8 hours = $800
      Develop a vulnerability scanning tool RFP
      • Consultant at $100 an hour for 40 hours = $4,000
      Develop a penetration test RFP
      • Consultant at $100 an hour for 40 hours = $4,000
    Potential financial savings from using Info-Tech resources Phase 1 ($1,600) + Phase 2 ($6,400) + Phase 3 ($10,400) + Phase 4 ($10,400) = $28,800

    Guided Implementation

    A Guided Implementation (GI) is a series of calls with an Info-Tech analyst to help implement our best practices in your organization.

    A typical GI is between 8 to 12 calls over the course of 4 to 6 months.

    What does a typical GI on this topic look like?

    Phase 1

    Phase 2

    Phase 3

    Phase 4

    Call #1: Scope requirements, objectives, and your specific challenges.

    Call #2: Discuss current state and vulnerability sources.

    Call #3: Identify triage methods and business criticality.

    Call #4:Review current defense-in-depth and discuss risk assessment.

    Call #5: Discuss remediation options and scheduling.

    Call #6: Review release and change management and continuous improvement.

    Call #7: Identify metrics, KPIs, and CSFs.

    Call #8: Review vulnerability management policy.

    Workshop Overview

    Contact your account representative for more information.
    workshops@infotech.com 1-888-670-8889

      Day 1 Day 2 Day 3 Day 4 Day 5
    Activities
    Identify vulnerability sources

    1.1 What is vulnerability management?

    1.2 Define scope and roles

    1.3 Cloud considerations for vulnerability management

    1.4 Vulnerability detection

    Triage and prioritize

    2.1 Triage vulnerabilities

    2.2 Determine high-level business criticality

    2.3 Consider current security posture

    2.4 Risk assessment of vulnerabilities

    Remediate vulnerabilities

    3.1 Assess remediation options

    3.2 Schedule and execute remediation

    3.3 Drive continuous improvement

    Measure and formalize

    4.1 Metrics, KPIs & CSFs

    4.2 Vulnerability Management Policy

    4.3 Select & implement a scanning tool

    4.4 Penetration testing

    Next Steps and Wrap-Up (offsite)

    5.1 Complete in-progress deliverables from previous four days

    5.2 Set up review time for workshop deliverables and to discuss next steps

    Deliverables
    1. Scope and boundary definition of vulnerability management program
    2. Responsibility assignment for vulnerability identification and remediation
    3. Monitoring and review process of third-party vulnerability sources
    4. Incident management and vulnerability convergence
    1. Methodology for evaluating identified vulnerabilities
    2. Identification of high-level business criticality
    3. Defined high-level data classifications
    4. Documented defense-in-depth controls
    5. Risk assessment criteria for impact and likelihood
    1. Documented risk assessment methodology and remediation options
    1. Defined metrics, key performance indicators (KPIs), and critical success factors (CSFs)
    2. Initial draft of vulnerability management policy
    3. Scanning tool selection criteria
    4. Introduction to penetration testing
    1. Completed vulnerability management standard operating procedure
    2. Defined vulnerability management risk assessment criteria
    3. Vulnerability management policy draft

    Implement Risk-Based Vulnerability Management

    Phase 1

    Identify Vulnerability Sources

    Phase 1

    1.1 What is vulnerability management?
    1.2 Define scope and roles
    1.3 Cloud considerations for vulnerability management
    1.4 Vulnerability detection


    Phase 2

    2.1 Triage vulnerabilities
    2.2 Determine high-level business criticality
    2.3 Consider current security posture
    2.4 Risk assessment of vulnerabilities


    Phase 3

    3.1 Assessing remediation options
    3.2 Scheduling and executing remediation
    3.3 Continuous improvement


    Phase 4

    4.1 Metrics, KPIs & CSFs
    4.2 Vulnerability management policy
    4.3 Select and implement a scanning tool
    4.4 Penetration testing

    This phase will walk you through the following activities:

    Establish a common understanding of vulnerability management, define the roles, scope, and information sources of vulnerability detection.

    This phase involves the following participants:

    • Security operations team
    • IT Security Manager
    • IT Director
    • CISO

    Step 1.1

    Vulnerability Management Defined

    Activities

    None for this section

    This step will walk you through the following activities:

    Establish a common understanding of vulnerability management and its place in the IT organization.

    This step involves the following participants:

    • Security operations team
    • IT Security Manager
    • IT Director
    • CISO

    Outcomes of this step

    Foundational knowledge of vulnerability management in your organization.

    Identify vulnerability sources
    Step 1.1 Step 1.2 Step 1.3 Step 1.4

    What is vulnerability management?

    It’s more than just patching.

    • Vulnerability management is the regular and ongoing practice of scanning an operating environment to uncover vulnerabilities. These vulnerabilities can be outdated applications, unpatched operating systems and software, open ports, obsolete hardware, or any combination of these.
    • The scanning and detection of vulnerabilities is the first step. Planning and executing of remediation is next, along with the approach, prioritized sequence of events, and timing.
    • A vendor-supplied software patch or firmware update is often the easy answer, however, this is not always a viable solution. What if you can’t patch in a timely fashion? What if patching is not possible as it will break the application and bring down operations? What if no patch exists due to the age of the application or operating platform?

    “Most organizations do not have a formal process for vulnerability management.” (Morey Haber, VP of Technology, BeyondTrust, 2016)

    Effective vulnerability management

    It’s not easy, but it’s much harder without a process in place.
    • Effective vulnerability management requires a formal process for organizations to follow; without one, vulnerabilities are dealt with in an ad hoc fashion.
    • Patching isn’t the only solution, but it’s the one that often draws focus.
    • Responsibilities for the different aspects of vulnerability management are often unclear, such as for testing, remediation, and implementation.
    • Identifying new threats without proper vulnerability scanning tools can be a near-impossible task.
    • Determining which vulnerabilities are most urgent can be an inconsistent process, increasing the organizational risk.
    • Measuring the effectiveness of your vulnerability remediation activities can help you better manage resources in SecOps and ITOps. Your staff will be spending the appropriate effort on vulnerabilities that warrant that level of attention.

    You’re not just doing this for yourself. It’s also for your auditors.

    Many compliance and regulatory obligations require organizations to have thorough documentation of their vulnerability management practices.

    Vulnerability management revolves around your asset security services

    Diagram with 'Asset Security Services' at the center. On either side are 'Network Security Services' and 'Identity Security Services', all three of which flow up into 'Security Analytics | Security Incident Response', and all four share a symbiotic flow with 'Management' below and contribute to 'Mega Trend Mapping' above. Management is supported by 'Governance'. Vulnerabilities can be found primarily within your assets but also connect to your information risk management. These must be effectively managed as part of a holistic security program.

    Without management, vulnerabilities left unattended can be easy for attackers to exploit. It becomes difficult to identify the correct remediation option to mitigate against the vulnerabilities.

    Vulnerability management works in tandem with SecOps and ITOps

    Vulnerability Management Process Inputs/Outputs:
    'Vulnerability Management (Process and Tool)' outputs are 'Incident Management', 'Release Management', 'Change Management', 'IT Asset Management', 'Application Security Testing', 'Threat Intelligence', and 'Security Risk Management'; inputs are 'Vulnerability Disclosure', 'Threat Intelligence', and 'Security Risk Management'.

    Arrows denote direction of information feed

    Vulnerability management serves as the input into a number of processes for remediation, including:
    • Incident management, to deal with issues
    • Release management, for patch management
    • Change management, for change control
    • IT asset management, to track version information, e.g. for patching
    • Application security testing, for the verification of vulnerabilities

    A two-way data flow exists between vulnerability management and:

    • Security risk management, for the overall risk posture of the organization
    • Threat intelligence, as vulnerability management reveals only one of several threat vectors

    For additional information please refer to Info-Tech’s research for each area:

    • Vulnerability management can leverage your existing processes to gain an operational element for the program.
    • As you strive to mature each of the processes on their own, vulnerability management will benefit accordingly.
    • Review our research for each of these areas and speak to one of our analysts if you wish to improve any of the listed processes.

    Info-Tech’s Information Security Program Framework

    Vulnerability management is a component of the Infrastructure Security section of Security Management

    Information Security Framework with Level 1 and Level 2 capabilities in two main sections, 'Management' and 'Governance'. Level 2 capabilities are grouped within Level 1 capabilities. For more information, review our Build an Information Security Strategy blueprint, or speak to one of our analysts.

    Info-Tech Insight

    Vulnerability management is but one piece of the information security puzzle. Ensure that you have all the pieces!

    Case Study

    Logo for Cimpress.
    INDUSTRY: Manufacturing
    SOURCE: Cimpress, 2016

    One organization is seeing immediate benefits by formalizing its vulnerability management program.

    Challenge

    Cimpress was dealing with many challenges in regards to vulnerability management. Vulnerability scanning tools were used, but the reports that were generated often gave multiple vulnerabilities that were seen as critical or high and required many resources to help address them. Scanning was done primarily in an attempt to adhere to PCI compliance rather than to effectively enable security. After re-running some scans, Cimpress saw that some vulnerabilities had existed for an extended time period but were deemed acceptable.

    Solution

    The Director of Information Security realized that there was a need to greatly improve this current process. Guidelines and policies were formalized that communicated when scans should occur and what the expectations for remediations should be. Cimpress also built a tiered approach to prioritize vulnerabilities for remediation that is specific to Cimpress instead of relying on scanning tool reports.

    Results

    Cimpress found better management of the vulnerabilities within its system. There was no pushback to the adoption of the policies, and across the worldwide offices, business units have been proactively trying to understand if there are vulnerabilities. Vulnerability management has been expanded to vendors and is taken into consideration when doing any mergers and acquisitions. Cimpress continues to expand its program for vulnerability management to include application development and vulnerabilities within any existing legacy systems.

    Step 1.2

    Defining the scope and roles

    Activities
    • 1.2.1 Define the scope and boundary of your organization’s security program
    • 1.2.2 Assign responsibility for vulnerability identification and remediation

    This step will walk you through the following activities:

    Define and understand the scope and boundary of the security program. For example, does it include OT? Define roles and responsibilities for vulnerability identification and remediation

    This step involves the following participants:

    • Security operations team
    • IT Security Manager
    • IT Director
    • CISO

    Outcomes of this step

    Understand how far vulnerability management extends and what role each person in IT plays in the remediation of vulnerabilities

    Identify vulnerability sources
    Step 1.1 Step 1.2 Step 1.3 Step 1.4

    Determine the scope of your security program

    This will help you adjust the depth and breadth of your vulnerability management program.
    • Determining the scope will help you decide how much organizational risk the vulnerability management program will oversee.
    • Scope can be defined along four aspects:
      • Data Scope – What data elements in your organization does your security program cover? How is data classified?
      • Physical Scope – What physical scope, such as geographies, does the security program cover?
      • Organizational Scope – How are business units engaged with security initiatives? Does the scope cover all subsidiary organizations?
      • IT Scope – What parts of the organization does IT cover? Does their coverage include operational technology (OT) and industrial control systems (ICS)?
    Stock image of figures standing in connected circles.

    1.2.1 Define the scope and boundary of your organization’s security program

    60 minutes

    Input: List of Data Scope, Physical Scope, Organization Scope, and IT Scope

    Output: Defined scope and boundaries of the IT security program

    Materials: Whiteboard/Flip Charts, Sticky Notes, Markers, Vulnerability Management SOP Template

    Participants: Business stakeholders, IT leaders, Security team members

    1. On a whiteboard, write the headers: Data Scope, Physical Scope, Organizational Scope, and IT Scope.
    2. Give each group member a handful of sticky notes. Ask them to write down as many items as possible for the organization that could fall under one of the four scope buckets.
    3. In a group, discuss the sticky notes and the rationale for including them. Discuss your security-related locations, data, people, and technologies, and define their scope and boundaries.

    The goal is to identify what your vulnerability management program is responsible for and document it.

    Consider the following:

    How is data being categorized and classified? How are business units engaged with security initiatives? How are IT systems connected to each other? How are physical locations functioning in terms of information security management?

    Download the Vulnerability Management SOP Template

    Assets are part of the scope definition

    An inventory of IT assets is necessary if there is to be effective vulnerability management.

    • Organizations need an up-to-date and comprehensive asset inventory for vulnerability management. This is due to multiple reasons:
      • When vulnerabilities are announced, they will need to be compared to an inventory to determine if the organization has any relevant systems or versions.
      • It indicates where all IT assets can be found both physically and logically.
      • Asset inventories typically have owners assigned to the assets and systems whose responsibility it is to carry out remediations for vulnerabilities.
    • Furthermore, asset inventories can provide insight into where data can be found within the organization. This is extremely useful within a formal data classification program, which plays a large factor in vulnerability management.
    If you need assistance building your asset inventory, review Info-Tech’s Implement Hardware Asset Management and Implement Software Asset Management blueprints.

    Info-Tech Insight

    Create a formal IT asset inventory before continuing with the rest of this project. Otherwise, you risk being at the mercy of a weak vulnerability management program.

    Assign responsibility for vulnerability identification and remediation

    Determine who is critical to effectively detecting and managing vulnerabilities.
    • Some of the remediation steps will involve members of IT management to identify the true organizational risk of a vulnerability.
    • Vulnerability remediation comes in different shapes and sizes. In addition to patching, this can include implementing compensating controls, server and application hardening, or the segregating of vulnerable systems.
      • Who carries out each of these activities? Who coordinates the activities and tracks them to ensure completion?
    • The people involved may be members outside of the security team, such as members from IT operations, infrastructure, and applications. The specific roles that each of these groups play should be clearly identified.
    Stock image of many connected profile photos in a cloud network.

    1.2.2 Assign responsibility for vulnerability identification and remediation

    60 minutes

    Input: Sample list of vulnerabilities and requisite actions from each group, High-level organizational chart with area functions

    Output: Defined set of roles and responsibilities for member groups

    Materials: Vulnerability Management SOP Template

    Participants: CIO, CISO, IT Management representatives for each area of IT

    1. Display the table of responsibilities that need to be assigned.
    2. List all the positions within the IT security team.
    3. Map these to the positions that require IT security team members.
    4. List all positions that are part of the IT team.
    5. Map these to the positions that require IT team members.

    If your organization does not have a dedicated IT security team, you can perform this exercise by mapping the relevant IT staff to the different positions shown on the right.

    Download the Vulnerability Management SOP Template Sample of the Roles and Responsibilities table from the Vulnerability Management SOP Template.

    Step 1.3

    Cloud considerations for vulnerability management

    Activities

    None for this section.

    This step will walk you through the following activities:

    Review cloud considerations for vulnerability management

    This step involves the following participants:

    • Security operations team
    • IT Security Manager
    • IT Director
    • CISO

    Outcomes of this step

    Understand the various types of cloud offerings and the implications (and limitations) of vulnerability management in a cloud environment.

    Identify vulnerability sources
    Step 1.1 Step 1.2 Step 1.3 Step 1.4

    Cloud considerations

    Cloud will change your approach to vulnerability management.
    • There will be a heavy dependence on the cloud service provider to ensure that vulnerabilities in their foundational technologies have been addressed.
    • Depending on the level of “as-a-Service,” customers will have varying degrees of control and visibility into the underlying operations.
    • With vendor acquiescence, you can set your tool to scan a given cloud environment, depending on how much visibility you have into their environment based on the service you have purchased.
    • Due to compliance obligations of their customers, there is a growing trend among cloud providers to allow more scanning of cloud environments.
    • In the absence of customer scanning capability, vendors may offer attestation of vulnerability management and remediation.
    Table outlining who has control, between the 'Organization' and the 'Vendor', of different cloud capabilities in different cloud strategies.

    For more information, see Info-Tech Research Group’s Document Your Cloud Strategy blueprint.

    Cloud environment scanning

    Cloud scanning is becoming a more common necessity but still requires special consideration.

    An organization’s cloud environment is just an extension of its own environment. As such, cloud environments need to be scanned for vulnerabilities.

    Private Cloud
    If your organization owns a private cloud, these environments can be tested normally.
    Public Cloud
    Performing vulnerability testing against public, third-party cloud environments is an area experiencing rapid growth and general acceptance, although customer visibility will still be limited.

    In many cases, a customer must rely on the vendor’s assurance that vulnerabilities are being addressed in a sufficient manner.

    Security standards’ compliance requirements are driving the need for cloud suppliers to validate and assure that they are appropriately scanning for and remediating vulnerabilities.

    Infrastructure- or Platform-as-a-Service (IaaS or PaaS) Environments
    • There is a general trend for PaaS and IaaS vendors to allow testing if given due notice.
    • Your contract with the cloud vendor or the vendor’s terms and conditions will outline the permissibility of customer vulnerability scanning. In some cases, a cloud vendor will deny the ability to do vulnerability scanning if they already provide a solution as part of their service.
    • Always ensure that the vendor is aware of your vulnerability scanning activity so that false positives aren’t triggering their security measures as possible denial-of-service (DoS) attacks.
    Software-as-a-Service (SaaS) Environments
    • SaaS offers very limited visibility to the services behind the software that the customer sees. You therefore cannot test for patch levels or vulnerabilities.
    • SaaS customers must rely exclusively on the provider for the regular scanning and remediation of vulnerabilities in the back-end technologies supporting the SaaS application.
    • You can only test the connection points to SaaS environments. This involves trying to figure out what you can see, e.g. looking for encrypted traffic.

    Certain testing (e.g. DoS or load testing) will be very limited by your cloud vendor. Cloud vendors won’t open themselves to testing that would possibly impact their operations.

    Step 1.4

    Vulnerability detection

    Activities
    • 1.4.1 Develop a monitoring and review process of third-party vulnerability sources
    • 1.4.2 Incident management and vulnerability management

    This step will walk you through the following activities:

    Create an inventory of your vulnerability monitoring capability and third-party vulnerability information sources.

    Determine how incident management and vulnerability management interoperate.

    This step involves the following participants:

    • Security operations team
    • IT Security Manager
    • IT Director
    • CISO

    Outcomes of this step

    Catalog of vulnerability information data sources. Understanding of the intersection of incident management and vulnerability management.

    Identify vulnerability sources
    Step 1.1 Step 1.2 Step 1.3 Step 1.4

    Vulnerability detection

    Vulnerabilities can be identified through numerous mediums.

    Info-Tech has determined the following to be the four most common ways to identify vulnerabilities.

    Vulnerability Assessment and Scanning Tools
    • Computer programs that function to identify and assess security vulnerabilities and weaknesses within computers, computer systems, applications, or networks.
    • Using a known vulnerability database, the tool scans targeted hosts or systems to identify flaws and generate reports and recommendations based on the results.
    • There are four main types of tools under this category: network and operating system vulnerability scanners, application scanning and testing tools, web application scanners, and exploitation tools.
    Penetration Tests
    • The act of identifying vulnerabilities on computers, computer systems, applications, or networks followed by testing of the vulnerability to validate the findings.
    • Penetration tests are considered a service that is offered by third-parties in which a variety of products, tools, and methods are used to exploit systems and gain access to data.
    Open Source Monitoring
    • New vulnerabilities are detected daily with each vulnerability’s information being uploaded to an information-sharing platform to enable other organizations to be able to identify the same vulnerability on their systems.
    • Open source platforms are used to alert and distribute information on newly discovered vulnerabilities to security professionals.
    Security Incidents
    • Any time an incident response plan is called into action to mitigate an incident, there should be formal communication with the vulnerability management team.
    • Any IT incident an organization experiences should provide a feed for analysis into your vulnerability management program.

    Automate with a vulnerability scanning tool

    Vulnerabilities are too numerous for manual scanning and detection.
    • Vulnerability management is not only the awareness of the existence of vulnerabilities but that they are actively present in your environment.
    • A vulnerability scanner will usually report dozens, if not hundreds, of vulnerabilities on a regular and recurring basis. Typical IT environments have several dozen, if not hundreds, of servers. We haven’t even considered the amount of network equipment or the hundreds of user workstations in an environment.
    • This tool will give you information of the presence of a vulnerability in your environment and the host on which the vulnerability exists. This includes information on the version of software that contains a vulnerability and whether you are running that version. The tool will also report on the criticality of the vulnerability based on industry criticality ratings.
    • The tools are continually updated by the vendor with the latest definition updates for the latest vulnerabilities out there. This ensures you are always scanning for the greatest number of potential vulnerabilities.
    Automation requires oversight.
    1. Vulnerability scanners bring great automation to the task of scanning and detecting vulnerabilities in high numbers.
    2. Vulnerability scanners, however, do not have your level of intelligence. Any compensating controls, network segregation, or other risk mitigation features that you have in place will not be known by the tool.
    3. Determining the risk and urgency of a vulnerability within the context of your specific environment will still require internal review by you or your SecOps team.

    For guidance on tool selection

    Refer to section 4.3 Selecting and Implement a Scanning Tool in this blueprint.

    Vulnerability scanning tool considerations

    Select a vulnerability scanning tool with the features you need to be effective.
    • Vulnerability scanning tool selection can be an exciting and confusing process. You will need to consider what features you desire in a tool and whether you want the tool to go beyond just scanning and reporting.
    • In addition to vulnerability scanning, some tools will integrate with your IT service management (service desk ticketing system) tool and asset, configuration, and change management modules. This can facilitate the necessary workflow that the remediation process follows once a vulnerability is discovered.
    • A number of vulnerability scanning tool vendors have started offering remediation as part of their software features. This includes the automation and orchestration functionality and configuration and asset management to track its remediation activities.
    • A side benefit of the asset discovery feature in vulnerability scanning tools is that it can help enhance an organization’s asset inventory and license compliance, particularly in cases where end users are able to install software on their workstations.
    Stock photo of a smartphone scanning a barcode.

    For guidance on tool vendors

    Visit SoftwareReviews for information on vulnerability management tools and vendors.

    Vulnerability scanning tool best practices

    How often should scans be performed?

    One-off scans provide snapshots in time. Repeated scans over time provide tracking for how systems are changing and how well patches are being applied and software is being updated.

    The results of a scan (asset inventory, configuration data, and vulnerability data) are basic information needed to understand your security posture. This data needs to be as up to date as possible.

    ANALYST PERSPECTIVE: Organizations should look for continuous scanning

    Continuous scanning is the concept of providing continual scanning of your systems so any asset, configuration, or vulnerability information is up to date. Most vendors will advertise continuous scanning but you need to be skeptical of how this feature is met.

    Continuous Scanning Methods

    Continuous agent scanning

    Real-time scanning that is completed through agent-based scanning. Provides real-time understanding of system changes.

    On-demand scanning

    Cyclical scanning is the method where once you’re done scanning an area, you start it again. This is usually done because doing some scans on some areas of your network take time. How long the scan takes depends on the scan itself. How often you perform a scan depends on how long a scan takes. For example, if a scan takes a day, you perform a daily scan.

    Cloud-based scanning

    Cloud-scanning-as-a-Service can provide hands-free continuous monitoring of your systems. This is usually priced as a subscription model.

    Vulnerability scanning tool best practices

    Where to perform a scan.

    What should be scanned How to point a scanner
    The general idea is that you want to scan pretty much everything. Here are considerations for three environments:
    Mobile Devices

    You need to scan mobile devices for vulnerabilities, but the problem is these can be hard to scan and often come and go on your network. There are always going to be some devices that aren’t on the network when scanning occurs.

    Several ways to scan mobile devices:

    • Intercept the device when it remotes into your network using a VPN. You catch the device with a remote scan. This can only be done if a VPN is required.
    • An agent-based approach can be used for mobile devices. Locally installed software gives the information needed to evaluate the security posture of a device. Discernibly, concerns around device processing, memory, and network bandwidth come into play. Ease of installation becomes key for agents.
    Virtualization
    • In a virtual environment, you will have servers being dynamically spun up. Ensure your tool is able to scan these new servers automatically.
    • Often, vulnerability scanning tool providers will restrict scanning to preapproved scanners. Look for tools that are preapproved by the VM vendors.
    Cloud Environments
    • You can set your tool to scan a given cloud environment. The main concern here is who owns the cloud. If it is a private cloud, there is little concern.
    • If it is a third-party cloud (AWS, Azure, etc.) you need to confirm with the cloud service provider that scanning of your cloud environment can occur.
    • There is a trend to allow more scanning of cloud environments.
    • You need to tell the scanner an IP address, a group of IP addresses, an asset group, or a combination of those.
    • You can categorize by functional classifications – internet-facing servers, workstations, network devices, etc., or by organizational structure – Finance, HR, Legal, etc.
    • If you have a strong change management system, you can better hone when and where to perform a scan based on actual changes.
    • You can set the number of concurrent outbound TCP connections that are being made. For example, set the tool so it sends out to 10 ports at a time, rather than pinging at 64k ports on a machine, which would flood the NIC.
    • Side Note: Flooding a host with pings from a scanning tool can be done to find out DoS thresholds on a machine. There are no bandwidth concerns for a network DoS, however, because the packets are so small.

    Vulnerability scanning tool best practices

    Communication and measurement

    Pre-Scan Communication With Users

    • It is always important to inform owners and users of systems that a scan will be happening.
    • Although it is unlikely any performance issues will arise, it is important to notify end users of potential impact.
    • Local admins or system owners may have controls in place that stop vulnerability scans and you need to inform the owners so that they can safelist the scanner you will be using.
    Vulnerability Scanning Tool Tracking Metrics
    • Vulnerability score by operating system, application, or organization division.
      • This provides a look at the widely accepted severity of the vulnerability as it relates across the organization’s systems.
    • Most vulnerable applications and application version.
      • This provides insight into how outdated applications are creating risk exposure for an organization.
      • This will also provide metrics on the effectiveness of your patching program.
    • Number of assets scanned within the last number of days.
      • This provides visibility into how often your assets are being scanned and thus protected.
    • Number of unowned devices or unapproved applications.
      • This metric will track how many unowned devices or unapproved applications may be on your network. Unowned devices may be rogue devices or just consultant/contractor devices.

    Third-party vulnerability information sources

    IT security forums and mailing lists are another source of vulnerability information.

    Proactively identify new vulnerabilities as they are announced.

    By monitoring for vulnerabilities as they are announced through industry alerts and open-source mechanisms, it is possible to identify vulnerabilities beyond your scanning tool’s penetration tests.

    Common sources:
    • Vendor websites and mailing lists
      • Vendors are the trusted sources for vulnerability and patch information on their products, particularly with new industry vulnerability disclosure requirements. Vendors are the most familiar with their products, downloads are most likely malware free, and additional information is often included.
      • There are some issues: vendors won’t announce a vulnerability until a patch is created, which creates a potential unknown risk exposure; numerous vendor sites will have to be monitored continually.
    • Third-party websites
      • A non-vendor site providing information on vulnerabilities. They often will cover a specific technology or an industry section, becoming a potential “one-stop shop” for some. They will often provide vulnerability information that is augmented with different remediation recommendations faster than vendors.
      • However, it’s more likely that malicious code could be downloaded and it will often not be comprehensive information on patching.
    • Third-party mailing lists, newsgroups, live paid subscriptions, and live open-source feeds
      • These are alerting and notification services for the detection and dissemination of vulnerability information. They provide information on the latest and most critical vulnerabilities, e.g. US-CERT Cybersecurity Alerts.
    • Vulnerability databases
      • These usually consist of dedicated databases on vulnerabilities. They perform the hard work of identifying and aggregating vulnerability and patch information into a central repository for end-user consumption. The commentary features on these databases provide excellent insight for practitioners, e.g. National Vulnerability Database (NVD).
    Stock photo of a student checking a bulletin board.

    Third-party vulnerability information sources

    IT security forums and mailing lists are another source of vulnerability information.

    Third-party sources for vulnerabilities

    • Open Source Vulnerability Database (OSVDB)
      • An open-source database that is run independently of any vendors.
    • Common Vulnerabilities and Exposures (CVE)
      • Free, international dictionary of publicly known information security vulnerabilities and exposures.
    • National Vulnerability Database (NVD)
      • Through NIST, the NVD is the US government’s repository of vulnerabilities and includes product names, flaws, and any impact metrics.
      • The National Checklist Repository Program (NCRP), also provided by NIST, provides security checklists for configurations of operating systems and applications.
      • The Center for Internet Security, a separate entity unrelated to NIST, provides configuration benchmarks that are often referenced by the NCRP.
    • Open Web Application Security Project (OWASP)
      • OWASP is another free project helping to expose vulnerabilities within software.
    • US-CERT National Cyber Alert System (US-CERT Alerts)
      • Cybersecurity Alerts – Provide timely information about current security issues, vulnerabilities, and exploits.
      • Cybersecurity Tips – Provide advice about common security issues for the general public.
      • Cybersecurity Bulletins – Provide weekly summaries of new vulnerabilities. Patch information is provided when available.
    • US-CERT Vulnerability Notes Database (US-CERT Vulnerability Notes)
      • Database of searchable security vulnerabilities that were deemed not critical enough to be covered under US-CERT Alerts. Note that the NVD covers both US-CERT Alerts and US-CERT Notes.
    • Open Vulnerability Assessment Language (OVAL)
      • Coding language for security professionals to discuss vulnerability checking and configuration issues. Vulnerabilities are identified using tests that are disseminated in OVAL definitions (XML executables that can be used by end users).

    1.4.1 Develop a monitoring and review process for third-party vulnerability sources

    60 minutes

    Input: Third-party resources list

    Output: Process for review of third-party vulnerability sources

    Materials: Whiteboard, Whiteboard markers, Vulnerability Management SOP Template

    Participants: IT Security Manager, SecOps team members, ITOps team members, CISO

    1. Identify what third-party resources are useful and relevant.
    2. Shortlist your third-party sources.
    3. Identify what is the best way to receive information from a third party.
    4. Document the method to receive or check information from the third-party source.
    5. Identify who is responsible for maintaining third-party vulnerability information sources
    6. Capture this information in the Vulnerability Management SOP Template.
    Download the Vulnerability Management SOP Template Sample of the Third Party Vulnerability Monitoring tables from the Vulnerability Management SOP Template.

    Incidents and vulnerability management

    Incidents can also be a sources of vulnerabilities.

    When any incident occurs, for example:

    • A security incident, such as malware detected on a machine
    • An IT incident, such as an application becomes unresponsive
    • A crisis occurs, like a worker accident

    There can be underlying vulnerabilities that need to be processed.

    Three Types of IT Incidents exist:
    1. Information Security Incident
    2. IT Incident and/or Problem
    3. Crisis

    Note: You need to have developed your various incident response plans to develop information feeds to the vulnerability mitigation process.
    If you are missing an incident response plan, take a look at Info-Tech’s Related Resources.

    Info-Tech Related Resources:
    If you do not have a formalized information security incident management program, take a look at Info-Tech’s blueprint Develop and Implement a Security Incident Management Program.

    If you do not have a formalized problem management process, take a look at Info-Tech’s blueprint Incident and Problem Management.

    If you do not have a formalized IT incident management process, take a look at Info-Tech’s blueprint Develop and Implement a Security Incident Management Program.

    If you do not have formalized crisis management, take a look at Info-Tech’s blueprint Implement Crisis Management Best Practices.

    1.4.2 Incident management and vulnerability management

    60 minutes

    Input: Existing incident response processes, Existing crisis communications plans

    Output: Alignment of vulnerability management program with existing incident management processes

    Materials: Whiteboard, Whiteboard markers, Vulnerability Management SOP Template

    Participants: IT Security Manager, SecOps team members, ITOps team members, including tiers 1, 2, and 3, CISO, CIO

    1. Inventory what incident response plans the organization has. These include:
      1. Information Security Incident Response Plan
      2. IT Incident Plan
      3. Problem Management Plan
      4. Crisis Management Plan
    2. Identify what part of those plans contains the post-response recap or final analysis.
    3. Formalize a communication process between the incident response plan and the vulnerability mitigation process.

    Note: Most incident processes will cover some sort of root cause analysis and investigation of the incident. If a vulnerability of any kind is detected within this analysis it needs to be reported on and treated as a detected vulnerability, thus warranting the full vulnerability mitigation process.

    Download the Vulnerability Management SOP Template

    Implement Risk-Based Vulnerability Management

    Phase 2

    Triage & prioritize

    Phase 1

    1.1 What is vulnerability management?
    1.2 Define scope and roles
    1.3 Cloud considerations for vulnerability management
    1.4 Vulnerability detection


    Phase 2

    2.1 Triage vulnerabilities
    2.2 Determine high-level business criticality
    2.3 Consider current security posture
    2.4 Risk assessment of vulnerabilities


    Phase 3

    3.1 Assessing remediation options
    3.2 Scheduling and executing remediation
    3.3 Continuous improvement


    Phase 4

    4.1 Metrics, KPIs & CSFs
    4.2 Vulnerability management policy
    4.3 Select and implement a scanning tool
    4.4 Penetration testing

    This phase will walk you through the following activities:

    Examine the elements that you will use to triage and analyze vulnerabilities, prioritizing using a risk-based approach, and prepare for remediation options.

    This phase involves the following participants:

    • IT Security Manager
    • SecOps team members
    • ITOps team members, including tiers 1, 2, and 3
    • CISO
    • CIO

    Step 2.1

    Triage vulnerabilities

    Activities
    • 2.1.1 Evaluate your identified vulnerabilities

    This step will walk you through the following activities:

    Review your vulnerability information sources and determine a methodology that will be used to consistently evaluate vulnerabilities as your scanning tool alerts you to them.

    This step involves the following participants:

    • IT Security Manager
    • SecOps team members
    • ITOps team members, including tiers 1, 2, and 3
    • CISO
    • CIO

    Outcomes of this step

    A consistent, documented process for the evaluation of vulnerabilities in your environment.

    Triage & prioritize
    Step 2.1 Step 2.2 Step 2.3 Step 2.4

    Triaging vulnerabilities

    Use Info-Tech’s methodology to allocate urgencies to your vulnerabilities to assign the appropriate resources to each one.

    When evaluating numerous vulnerabilities, use the following three factors to help determine the urgency of vulnerabilities:

    • The intrinsic qualities of the vulnerability
    • The business criticality of the affected asset
    • The sensitivity of the data stored on the affected asset

    Intrinsic qualities of the vulnerability — Vulnerabilities need to be examined for the inherent risk they pose specifically to the organization, which includes if an exploit has been identified or if the industry views this as a serious and likely threat.

    Business criticality of the affected asset — Assets with vulnerabilities need to be assessed for their criticality to the business. Vulnerabilities on systems that are critical to business operations or customer interactions are usually top of mind.

    Sensitivity of the data of the affected asset — Beyond just the criticality of the business, there must be consideration of the sensitivity of the data that may be compromised or modified as a result of any vulnerabilities.

    Info-Tech Insight

    This methodology allows you to determine urgency of vulnerabilities, but your remediation approach needs to be risk-based, within the context of your organization.

    Triage your vulnerabilities, filter out the noise

    Triaging enables your vulnerability management program to focus on what it should focus on.

    Use the Info-Tech Vulnerability Mitigation Process Template to define how to triage vulnerabilities as they first appear.

    Triaging is an important step in vulnerability management, whether you are facing ten to tens of thousands of vulnerability notifications.
    Many scanning tools already provide the capability to compare known vulnerabilities against existing assets through integration with the asset inventory.

    There are two major use cases for this process:
    1. For organizations that have identified vulnerabilities but do not know their own systems well enough. This can be due to a lack of a formal asset inventory.
    2. For proactive organizations that are regularly staying up to date with industry announcements regarding vulnerabilities. Once an alert has been made publicly, this process can assist in confirming if the vulnerability is relevant to the organization.
    The Info-Tech methodology for initial triaging of vulnerabilities:
    Flowchart of the Info-Tech methodology for initial triaging of vulnerabilities, beginning with 'Vulnerability has been identified' and ending with either 'Vulnerability has been triaged' or 'No action needed'.

    Even if neither of these use cases apply to your organization, triaging still addresses the issues of false positives. Triaging provides a quick way to determine if vulnerabilities are relevant.

    After eliminating the noise, evaluate your vulnerabilities to determine urgency

    Consider the intrinsic risk to the organization.

    Is there an associated, verified exploit?
    • For a vulnerability to become a true threat to the organization, it must be exploited to cause damage. In today’s threat landscape, exploit kits are sold online that allow individuals with low technical knowledge to exploit a vulnerability.
    • Not all vulnerabilities have an associated exploit, but this does not mean that these vulnerabilities can be left alone. In many cases, it is just a matter of time before an exploit is created.
    • Another point to consider is that while exploits can exist theoretically, they may not be verified. Vulnerabilities always pose some level of risk, but if there are no known verified exploits, there is less risk attached.
    Is there a CVSS base score of 7.0 or higher?
    • Common Vulnerability Scoring System (CVSS) is an open-source industry scoring method to assess the potential severity of vulnerabilities.
    • CVSS takes into account: attack vector, complexity, privileges required, user interaction, scope, confidentiality impact, integrity impact, and availability impact.
    • Vulnerabilities that have a score of 4.0 or lower are classified as low vulnerabilities, while scores between 4.0 and 6.9 are put in the medium category. Scores of 7 or higher are in the high and critical categories. As we will review in the Risk Assessment section, you will want to immediately deal with high and critical vulnerabilities.
    Is there potential for significant lateral movement?
    • Even though a vulnerability may appear to be part of an inconsequential asset, it is important to consider whether it can be leveraged to gain access to other areas of the network or system by an attacker.
    • Another consideration should be whether the vulnerability can be exploited by remote or local access. Remote exploits pose a greater risk as this can mean that attackers can perform an exploit from any location. Local exploits carry less risk, although the risk of insider threats should be considered here as well.

    2.1.1 Evaluate your identified vulnerabilities

    60 minutes

    Input: Visio workflow of Info-Tech’s vulnerability management process

    Output: Adjusted workflow to reflect your current processes, Vulnerability Tracking Tool

    Materials: Whiteboard, Whiteboard markers, Vulnerability Management SOP Template

    Participants: IT Security Manager, SecOps team members, ITOps team members, including tiers 1, 2, and 3, CISO, CIO

    Using the criteria from the previous slide, Info-Tech has created a methodology to evaluate your vulnerabilities by examining their intrinsic qualities.

    The methodology categorizes the vulnerabilities into high, medium, and low risk importance categorizations, before assigning final urgency scores in the later steps.

    1. Review the evaluation process in the Vulnerability Management Workflow library.
    2. Determine if this process makes sense for the organization; otherwise, change the flow to include any other considerations of process flows.
    3. As this process is used to evaluate vulnerabilities, document vulnerabilities to an importance category. This can be done in the Vulnerability Tracking Tool or using a similar internal vulnerability tracking document, if one exists.

    Download the Vulnerability Management SOP Template

    Step 2.2

    Determine high-level business criticality

    Activities
    • 2.2.1 Determine high-level business criticality
    • 2.2.2 Determine your high-level data classifications

    This step will walk you through the following activities:

    Determining high-level business criticality and data classifications will help ensure that IT security is aligned with what is critical to the business. This will be very important when decisions are made around vulnerability risk and the urgency of remediation action.

    This step involves the following participants:

    • IT Security Manager
    • SecOps team members
    • CISO

    Outcomes of this step

    Understanding and consistency in how business criticality and business data is assessed by IT in the vulnerability management process.

    Triage & prioritize
    Step 2.1 Step 2.2 Step 2.3 Step 2.4

    Understanding business criticality is key to determining vulnerability urgency

    Prioritize operations that are truly critical to the operation of the business, and understand how they would be impacted by an exploited vulnerability.

    Use the questions below to help assess which operations are critical for the business to continue functioning.

    For example, email is often thought of as a business-critical operation when this is not always the case. It is important to the business, but as regular operations can continue for some time without it, it would not be considered extremely business critical.

    Questions to ask Description
    Is there a hard-dollar impact from downtime? This refers to when revenue or profits are directly impacted by a business disruption. For example, when an online ordering system is compromised and shut down, it impacts sales, and therefore, revenue.
    Is there an impact on goodwill/ customer trust? If downtime means delays in service delivery or otherwise impacts goodwill, there is an intangible impact on revenue that may make the associated systems mission critical.
    Is regulatory compliance a factor? Depending on the circumstances of the vulnerabilities, it can be a violation of regulatory compliance and would cause significant fines.
    Is there a health or safety risk? Some operations are critical to health and safety. For example, medical organizations have operations that are necessary to ensure that individuals’ health and safety are maintained. An exploited vulnerability that prevents these operations can directly impact the lives of these individuals.
    Don’t start from scratch – your disaster recovery plan (DRP) may have a business impact analysis (BIA) that can provide insight into which applications and operations are considered business critical.

    Analyst Perspective

    When assessing the criticality of business operations, most core business applications may be deemed business critical over the long term.

    Consider instead what the impact is over the first 24 or 48 hours of downtime.

    2.2.1 Determine high-level business criticality

    120 minutes; less time if a Disaster recovery plan business impact analysis exists

    Input: List of business operations, Insight into business operations impacts to the business

    Output: List of business operations and their criticality and impact to the business

    Materials: Vulnerability Management SOP Template

    Participants: Participants from the business, IT Security Manager, CISO, CIO

    1. List your core business operations at a high level.
    2. Use a High, Medium, or Low ranking to prioritize the business operations based on mission-critical criteria and the impact of the vulnerability.
    3. When using the process flow, consider if the vulnerability directly affects any of these business operations and move through the process flow based on the corresponding High, Medium, or Low ranking.
    Example prioritization of business operations for a manufacturing company: Questions to ask:
    1. Is there a hard-dollar impact from downtime?
    2. Is there impact on goodwill or customer trust?
    3. Is regulatory compliance a factor?
    4. Is there a health or safety risk?

    Download the Vulnerability Management SOP Template

    Determine vulnerability urgency by its data classification

    Consider how to classify your data based on if the Confidentiality, Integrity, or Availability (CIA) is compromised.

    To properly classify your data, consider how the confidentiality, integrity, and availability of that data would be affected if it were to be exploited by a vulnerability. Review the table below for an explanation for each objective.
    Confidentiality

    Preserving authorized restrictions on information access and disclosure, including means for protecting personal privacy and proprietary information.

    Integrity

    Guarding against improper information modification or destruction, and ensuring information non-repudiation and authenticity.

    Availability

    Ensuring timely and reliable access to and use of information.

    Each piece of data should be ranked as High, medium, or low across confidentiality, integrity, and availability based on adverse effect. Arrow pointing right. Low — Limited adverse effect

    Moderate — Serious adverse effect

    High — Severe or catastrophic adverse effect

    If you wish to build a whole data classification methodology, refer to our Discover and Classify Your Data blueprint.

    How to determine data classification when CIA differs:

    The overall ranking of the data will be impacted by the highest objective’s ranking.

    For example, if confidentiality and availability are low, but integrity is high, the overall impact is high.

    This process was developed in part by Federal Information Processing Standards Publication 199.

    2.2.2 Determine your high-level data classifications

    120 minutes, less time if data classification already exists

    Input: Knowledge of data use and sensitivity

    Output: Adjusted workflow to reflect your current processes, Vulnerability Tracking Tool

    Materials: Whiteboard, Whiteboard markers, Vulnerability Management SOP Template

    Participants: IT Security Manager, CISO, CIO

    If your organization has formal data classification in place, it should be leveraged to determine the high, medium, and low rankings necessary for the process flows. However, if there is no formal data classification in place, the process below can be followed:

    1. List common assets or applications that are prone to vulnerabilities.
    2. Consider the data that is on these devices and provide a high (severe or catastrophic adverse effect), medium (serious adverse effect), or low (limited adverse effect) ranking based on confidentiality, availability, and integrity.
      1. Use the table on the previous slide to assist in providing the ranking.
      2. Remember that it is the highest ranking that dictates the overall ranking of the data.
    3. Document which data belongs in each of the categories to provide contextual evidence.

    Download the Vulnerability Management SOP Template

    This process should be part of your larger data classification program. If you need assistance in building this out, review the Info-Tech research, Discover and Classify Your Data.

    Step 2.3

    Consider current security posture

    Activities
    • 2.3.1 Document your defense-in-depth controls

    This step will walk you through the following activities:

    Your defense-in-depth controls are the existing layers of security technology that protects your environment. These are relevant when considering the urgency and risk of vulnerabilities in your environment, as they will mitigate some of the risk.

    This step involves the following participants:

    • IT Security Manager
    • SecOps team members
    • ITOps team members, including tiers 1, 2, and 3
    • CISO
    • CIO

    Outcomes of this step

    Understanding and documentation of your current defense-in-depth controls.

    Triage & prioritize
    Step 2.1 Step 2.2 Step 2.3 Step 2.4

    Review your current security posture

    What you have today matters.
    • In most cases, your vulnerability scanning tool alone will not have the context of your security posture in the results of its scans. This can skew the true urgency of detected vulnerabilities in your environment.
    • What you have in place today is what comprises your organization’s overall security posture. This bears high relevance to the determination of the risk that a vulnerability poses to your environment.
    • Elements such as enterprise architecture and defense in depth mechanisms should be factored into determining the risk of a vulnerability and what kind of immediacy is warranted to address it.
    • Details of your current security posture will also contribute to the assessment and selection of remediation options.
    Stock image of toy soldiers split into two colours, facing eachother down.

    Enterprise architecture considerations

    What does your network look like?
    • Most organizations have a network topology that has been put in place with operational needs in mind. These includes specific vLANs or subnets, broadcast domains, or other methods of traffic segregation.
    • The firewall and network ACLs (access control lists) will manage traffic and the routes that data packets follow to traverse a network.
    • Organizations may physically separate data network types, for example, a network for IT services and one for operational technology (OT)(OT is often known as ICS (industrial control systems) or SCADA (supervisory control and data acquisition)) or other types of production technology.
    • The deployment of distribution and access switches across an enterprise can also be a factor, where a flatter network will have fewer network devices within the topology.
    • In a directory services environment such as Windows Active Directory, servers and applications can be segregated by domains and trust relationships, organizational units, and security groups.
    What’s the relevance to vulnerability management?

    For a vulnerability to be exploited, a malicious actor must find a way to access the vulnerable system to make use of the vulnerability in question.

    Any enterprise architecture characteristics that you have in place may lessen the probability of a successful vulnerability exploit.

    This may potentially “buy time” for SecOps to address and remediate the vulnerability.

    Defense-in-depth

    Defense-in-depth provides extra layers of protection to the organization.

    • Defense-in-depth refers to the coordination of security controls to add layers of security to the organization.
      • This means that even if attackers are able to get past one control or layer, they are hindered by additional security.
    • Defense-in-depth is distinct from the previous section on enterprise architecture as these are security controls put in place with the purpose of being lines of defense within your security posture.
    • This can be extremely useful in managing vulnerabilities; thus, it is important to establish the existing defense-in-depth controls. By establishing the base model for your defense-in-depth, it will allow you to leverage these controls to manage vulnerabilities.
    • Controls are typically distributed across endpoints, network infrastructure, servers, and physical security.

    Note: Defense-in-depth controls do not entirely mitigate vulnerability risk. They provide a way in which the vulnerability cannot be exploited, but it continues to exist on the application. This must be kept in mind as the controls or applications themselves change, as it can re-open the vulnerability and cause potential problems.

    Examples of defense-in-depth controls can consist of any of the following:
    • Antivirus software
    • Authentication security
    • Multi-factor authentication
    • Firewalls
    • Demilitarized zones (DMZ)
    • Sandboxing
    • Network zoning
    • Application whitelisting
    • Access control lists
    • Intrusion detection & prevention systems
    • Airgapping
    • User security awareness training

    2.3.1 Document your defense-in-depth controls

    2 hours, less time if a security services catalog exists

    Input: List of technologies within your environment, List of IT security controls that are in place

    Output: List of defense-in-depth controls

    Materials: Whiteboard/flip charts, Vulnerability Management SOP Template

    Participants: IT Security Manager, Infrastructure Manager, IT Director, CISO

    1. Document the existing defense-in-depth controls within your system.
    2. Review the initial list that has been provided and see if these are controls that currently exist.
    3. Indicate any other controls that are being used by the organization. This may already exist if you have a security services catalog.
    4. Indicate who the owners of the different controls are.
    5. Track the information in the Vulnerability Management SOP Template.

    Download the Vulnerability Management SOP Template

    Sample table of security controls within a Defense-in-depth model with column headers 'Defense-in-depth control', 'Description', 'Workflow', and 'Control Owner'.

    Step 2.4

    Risk assessment of vulnerabilities

    Activities
    • 2.4.1 Build a classification scheme to consistently assess impact
    • 2.4.2 Build a classification scheme to consistently assess likelihood

    This step will walk you through the following activities:

    Assessing risk will be the cornerstone of how you evaluate vulnerabilities and what priority you place on remediation. This is actual risk to the organization and not simply what the tool reports without the context of your defense-in-depth controls.

    This step involves the following participants:

    • IT Security Manager
    • IT Operations Management
    • CISO
    • CIO

    Outcomes of this step

    A risk matrix tailored to your organization, based on impact and likelihood. This will provide a consistent, unambiguous way to assess risk across the vulnerability types that is reported by your scanning tool.

    Triage & prioritize
    Step 2.1 Step 2.2 Step 2.3 Step 2.4

    Vulnerabilities and risk

    Vulnerabilities must be addressed to mitigate risk to the business.
    • Vulnerabilities are a concern because they are potential threats to the business. Vulnerabilities that are not addressed can turn from potential threats into actual threats; it is only a matter of time and opportunity.
    • Your organization will already be familiar with risk management, as every decision carries a business risk component. There may even be a senior manager assigned as corporate risk officer to manage organizational risk.
    • The organization likely has a risk tolerance level that defines the organization’s risk appetite. This may be measured in dollars, non-productivity time, or other units of inefficiency.
    • The risk of a vulnerability can be calculated using impact and likelihood. Impact is the effect that the vulnerability will have if it is exploited by a malicious actor. Likelihood is the degree to which a vulnerability exploit can possibly occur.
    Stock image of a cartoon character in a tie hanging on the needle of a 'RISK' meter as it sits at 'LOW'.

    Info-Tech Insight

    Risk to the organization is business language that everyone can understand. This is particularly true when the risk is to productivity or to the company’s bottom line.

    A risk-based approach to vulnerability management

    CVSS scores are just the starting point!

    Vulnerabilities are constant.
    • There will always be vulnerabilities in the environment, many of which won’t be reported as they are currently unknown.
    • Don’t focus on trying to resolve all vulnerabilities in your environment. You are neither resourced for it nor can the business tolerate the downtime needed to remediate every single vulnerability.
      • The constant follow of new vulnerabilities will quickly render your efforts useless and it will become a game of “whack-a-mole.”
    • Being able to prioritize which vulnerabilities require appropriate levels of response is crucial to ensuring that an organization stays ahead of the continual flow.
    • Your vulnerability scanning tool will report the severity of a vulnerability, often using an industry Common Vulnerability Scoring System (CVSS) system ranging from 0 to 10. It will then scan your environment for the presence of the vulnerability and report accordingly.
      • Your vulnerability scanning tool will not be aware of any mitigation components in your environment, such as compensating controls, network segregation, server/application hardening, or any other measures that can reduce the risk. That is why determining actual risk is a crucial step.

    Stock image of a whack-a-mole game.

    Info-Tech Insight

    Vulnerability scanning is a valuable function, but it does not tell the full picture. You must determine how urgent a vulnerability truly is, based on your specific environment.

    Prioritize remediation by levels of risk

    Address critical and high risk with high immediacy.

    • Addressing the critical and high-risk vulnerabilities with urgency will ensure that you are addressing a more manageable number of vulnerabilities.
    • An optimized vulnerability management process will address the medium and low risk vulnerabilities within the regular cycle.
    • This may be very similar to what you do today in an ad hoc fashion:
      • Zero-day vulnerabilities tend to warrant a stop in operations and are dealt with immediately (or as soon as a vendor has a fix).
      • The standard remediation process (patching/updating, change of configuration, etc.) happens within a regular controlled time cycle.
    • Formalizing this process will ensure that appropriate attention is given to vulnerabilities that warrant it and that the remaining vulnerabilities are dealt with as a regular, recurring activity.

    Mitigate the risk surface by reducing the time across the phases

    Chart titled 'Mitigate the risk surface by reducing the time across the phases' with the axes 'Risk Level' and 'Time' with lines created by individual risks. The highlighted line begins in 'Critical' and eventually drops to low. A note on the line reads 'Objective: Reduce risk surface by reducing time to address'. The area between the line and your organization's risk tolerance is labelled 'Risk Surface, to be addressed with high priority'. A bracket around Risk levels 'High' and 'Critical' reads 'Priority focus zone (risk surface)'. Risk lines within levels 'Low' and 'Medium' read 'Follow standard vulnerability management cycles'.

    Risk matrix

    Risk = Impact x Likelihood
    • Info-Tech’s Vulnerability Management Risk Assessment Tool provides a method of calculating the risk of a vulnerability. The risk rating is assigned using the impact of the risk and the likelihood or probability that the event may occur.
    • The tool puts the vulnerability into your organization’s context: How many people will be affected? What service types are vulnerable and how does that impact the business? Is there an anticipated update from the vendor of the system being affected?
    • Urgency of remediation should be based on the business consequences if the vulnerability were to be exploited, relative to the business’ risk tolerance.

    Info-Tech Insight

    Risk determination should be done within the context of your current environment and not simply based on what your vulnerability tool is reporting.

    A risk matrix is useful in calculating a risk rating for vulnerabilities. Risk matrix with axes 'Impact' and 'Time' and individual vulnerabilities mapped onto it via their risk rating. The example 'Organizational Risk Tolerance Threshold' line runs diagonally through the 'Medium' squares.

    2.4.1 Build a classification scheme to consistently assess impact

    60 minutes

    Input: Knowledge of IT environment, Knowledge of business impact for each IT component or service

    Output: Vulnerability Management Risk Assessment Tool formatted to your organization

    Materials: Vulnerability Management Risk Assessment Tool

    Participants: Functional Area Managers, IT Security Manager, CISO

    Risk always has a negative impact, but the size of the impact can vary considerably in terms of cost, number of people or sites affected, and the severity of the impact. Impact questions tend to be more objective and quantifiable than likelihood questions.

    1. Define a set of questions to measure risk impact or edit existing questions in the tool.
    2. For each question, assign a weight that should be placed on that factor.
    3. Define criteria for each question that would categorize the risk. The drop-down box content can be modified in the hidden Labels tab.

    Note that you are looking to baseline vulnerability types, rather than categorizing every single vulnerability your scanning tool reports. The volume of vulnerabilities will be high, but vulnerabilities can be categorized into types on a regular basis.

    Download the Vulnerability Management Risk Assessment Tool

    Screenshot of table from Info-Tech's Vulnerability Management Risk Assessment Tool for assessing Impact. Column headers are 'Weight', 'Question', 'OS vulnerability', 'Application vulnerability', 'Network vulnerability', and 'Vendor patch release'.

    2.4.2 Build a classification scheme to consistently assess likelihood

    60 minutes

    Input: Knowledge of IT environment, Knowledge of business impact for each IT component or service

    Output: Vulnerability Management Risk Assessment Tool formatted to your organization

    Materials: Vulnerability Management Risk Assessment Tool

    Participants: Functional Area Managers, IT Security Manager, CISO

    Risk always has a negative impact, but the size of the impact can vary considerably in terms of cost, number of people or sites affected, and the severity of the impact. Impact questions tend to be more objective and quantifiable than likelihood questions.

    1. Define a set of questions to measure risk impact or edit existing questions in the tool.
    2. For each question, assign a weight that should be placed on that factor.
    3. Define criteria for each question that would categorize the risk. The drop-down box content can be modified in the hidden Labels tab.

    Note that you are looking to baseline vulnerability types, rather than categorizing every single vulnerability that your scanning tool reports. The volume of vulnerabilities will be high, but vulnerabilities can be categorized into types on a regular basis.

    Download the Vulnerability Management Risk Assessment Tool

    Screenshot of table from Info-Tech's Vulnerability Management Risk Assessment Tool for assessing Likelihood. Column headers are 'Weight', 'Question', 'OS vulnerability', 'Application vulnerability', and 'Network vulnerability'.

    Prioritize based on risk

    Select the best remediation option to minimize risk.

    Through the combination of the identified risk and remediation steps in this phase, the prioritization for vulnerabilities will become clear. Vulnerabilities will be assigned a priority once their intrinsic qualities and threat potential to business function and data have been identified.

    • Remediation options will be identified for the higher urgency vulnerabilities.
    • Options will be assessed for whether they are appropriate.
    • They will be further tested to determine if they can be used adequately prior to full implementation.
    • Based on the assessments, the remediation will be implemented or another option will be considered.
    Prioritization
    1. Assignment of risk
    2. Identification of remediation options
    3. Assessment of options
    4. Implementation

    Remediation plays an incredibly important role in the entire program. It plays a large part in wider risk management when you must consider the risk of the vulnerability, the risk of the remediation option, and the risk associated with the overall process.

    Implement Risk-Based Vulnerability Management

    Phase 3

    Remediate vulnerabilities

    Phase 1

    1.1 What is vulnerability management?
    1.2 Define scope and roles
    1.3 Cloud considerations for vulnerability management
    1.4 Vulnerability detection


    Phase 2

    2.1 Triage vulnerabilities
    2.2 Determine high-level business criticality
    2.3 Consider current security posture
    2.4 Risk assessment of vulnerabilities


    Phase 3

    3.1 Assessing remediation options
    3.2 Scheduling and executing remediation
    3.3 Continuous improvement


    Phase 4

    4.1 Metrics, KPIs & CSFs
    4.2 Vulnerability management policy
    4.3 Select and implement a scanning tool
    4.4 Penetration testing

    This phase will walk you through the following activities:

    • Identifying potential remediation options.
    • Developing criteria for each option with regards to when to use and when to avoid.
    • Establishing exception procedure for testing and remediation.
    • Documenting the implementation of remediations and verification.

    This phase involves the following participants:

    • CISO, or equivalent
    • Security Manager/Analyst
    • Network, Administrator, System, Database Manager
    • Other members of the vulnerability management team
    • Risk managers for the risk-related steps

    Determining how to remediate

    Patching is only one option.

    This phase will allow organizations to build out the specific processes for remediating vulnerabilities. The overall process will be the same but what will be critical is the identification of the correct material. This includes building the processes around:
    • Identifying and selecting the remediation option to be used.
    • Determining what to do when a patch or update is not available.
    • Scheduling and executing the remediation activity.
    • Continuous improvement.

    Each remediation option carries a different level of risk that the organization needs to consider and accept by building out this program.

    It is necessary to be prepared to do this in real time. Careful documentation is needed when dealing with vulnerabilities. Use the Vulnerability Tracking Tool to assist with documentation in real time. This is separate from using the process template but can assist in the documentation of vulnerabilities.

    Step 3.1

    Assessing remediation options

    Activities
    • 3.1.1 Develop risk and remediation action

    This step will walk you through the following activities:

    With the risk assessment from the previous activity, we can now examine remediation options and make a decision. This activity will guide us through that.

    This step involves the following participants:

    • IT Security Manager
    • SecOps team members
    • ITOps team members, including tiers 1, 2, and 3
    • CISO
    • CIO

    Outcomes of this step

    List of remediation options and criteria on when to consider each.

    Remediate vulnerabilities
    Step 3.1 Step 3.2 Step 3.3

    Identify remediation options

    There are four options when it comes to vulnerability remediation.

    Patches and Updates

    Patches are software or pieces of code that are meant to close vulnerabilities or provide fixes to any bugs within existing software. These are typically provided by the vendor to ensure that any deployed software is properly protected after vulnerabilities have been detected.

    Configuration Changes

    Configuration changes involve administrators making significant changes to the system or network to remediate against the vulnerability. This can include disabling the vulnerable application or specific element and can even extend to removing the application altogether.

    Remediation

    Compensating Controls

    By leveraging security controls, such as your IDS/IPS, firewalls, or access control, organizations can have an added layer of protection against vulnerabilities beyond the typical patches and configuration changes. This can be used as a measure while waiting to implement another option (if one exists) to reduce the risk of the vulnerability in the short or long term.

    Risk Acceptance

    Whenever a vulnerability is not remediated, either indefinitely or for a short period of time, the organization is accepting the associated risk. Segregation of the vulnerable system can occur in this instance. This can occur in cases where a system or application cannot be updated without detrimental effect to the business.

    Patches and updates

    Patches are often the easiest and most common method of remediation.

    Patches are usually the most desirable remediation solution when it comes to vulnerability management. They are typically provided by the vendor of the vulnerable application or system and are meant to eliminate the existing vulnerability.

    When to use

    • When adequate testing can be performed on the patch to be implemented.
    • When there is a change window approaching for the affected systems.
    • When there is standardization across the IT assets to allow for easier installation of patches.

    When to avoid

    • When the patch cannot be adequately tested.
    • When a patch has been tested, but it caused an unfavorable consequence such as a system or application failure.
    • When there is no near change window in which to install the patches, which is often the case for critical systems.
    When to consider other remediation options
    • For critical systems, it can be difficult to implement a patch as they often require the system to be rebooted or go through some downtime. There must be consideration towards whether there is a change window approaching if a patch is to be implemented on a business-critical system.
      • If there is no opportunity to implement the patch, or no approaching change window, it is wise to leverage another remediation option.
    • When patches are not currently available from the vendor or they are in production, other remediation options are needed.
    • Other remediation options can be used in tandem with the patch. For example, if a patch is being deferred until the change window, it would be wise to use alternate remediation options to close the vulnerability.

    Compensating controls

    Compensating controls can decrease the risk of vulnerabilities that cannot be (immediately) remediated.

    • Compensating controls are measures put in place when direct remediation measures are impractical or non-existent.
    • Similar to the payment card industry’s PCI DSS 1.0 provision of compensating controls, these are meant to meet the intent or rigor of the original requirement; unlike PCI DSS, these measures are to mitigate risk rather than meet compliance.
    • The compensating control should be viewed as only a temporary measure for dealing with a vulnerability, although circumstances may dictate a degree of permanence in the application of the compensating control.
    • Examples where compensating controls may be needed are:
      • The software vendor is developing an update or patch to address a vulnerability.
      • Through your testing process, a patch will adversely affect the performance or operation of the target system and be detrimental to the business.
      • A critical application will only run on a legacy operating system, the latter of which is no longer supported by the vendor.
      • A legacy application is no longer being supported but is critical to your operations. A replacement, if one exists, will take time to implement.
    Examples of compensating controls
    • Segregating a vulnerable server or application on the network, physically or logically.
    • Hardening the operating system or application.
    • Restricting user logins to the system or application.
    • Implementing access controls on the network route to the system.
    • Instituting application whitelisting.

    Configuration changes

    Configuration changes involve making changes directly to the application or system in which there is a vulnerability. This can vary from disabling or removing the vulnerable element or, in the case of applications built in-house, changing the coding of the application itself. These are commonly used in network vulnerabilities such as open ports.

    When to use

    • A patch is not available.
    • The vulnerable element can be significantly changed, or even disabled, without significantly disrupting the business.
    • The application is built in-house, as the vulnerability must be closed internally.
    • There is adequate testing to ensure that the configuration change does not affect the business.
    • A configuration change in your network or system can affect numerous endpoints or systems, reducing endpoint patching or use of defense-in-depth controls.

    When to avoid

    • When a suitable patch is available.
    • When the vulnerability is on a business-critical element with no nearby change window or it cannot be disabled.
    • When there is no opportunity in which to perform testing to ensure that there are no unintended consequences.
    When to consider other remediation options
    • Configuration changes require careful documentation as changes are occurring to the system and applications. If there is a need to perform a back-out process and return to the original configuration, this can be extremely difficult without clear documentation of what occurred.
    • If business systems are too critical or important to the regular business function to perform any changes, it is necessary to consider other options.

    Info-Tech Insight

    Remember your existing processes: configuration changes may need to be approved and orchestrated through your organization’s configuration and change management processes.

    Case Study

    Remediation options do not have to be used separately. Use the Shellshock 2014 case as an example.

     
    INDUSTRY: All
    SOURCE: Public Domain
    Challenge

    Bashdoor, more commonly known as Shellshock, was announced on September 24, 2014.

    This bug involved the Bash shell, which normally executes user commands, but this vulnerability meant that malicious attackers could exploit it.

    This was rated a 10/10 by CVSS – the highest possible score.

    Within hours of the announcement, hackers began to exploit this vulnerability across many organizations.

    Solution

    Organizations had to react quickly and multiple remediation options were identified:

    • Configuration changes – Companies were recommended to use other shells instead of the Bash shell.
    • Defense-in-depth controls – Using HTTP server logs, it could be possible to identify if the vulnerability had been exploited.
    • Patches – Many vendors released patches to close this vulnerability including Debian, Ubuntu, and Red Hat.
    Results

    Companies began to protect themselves against these vulnerabilities.

    While many organizations installed patches as quickly as possible, some also wished to test the patch and leveraged defense-in-depth controls in the interim.

    However, even today, many still have the Shellshock vulnerability and exploits continue to occur.

    Accept the risk and do nothing

    By choosing not to remediate vulnerabilities, you must accept the associated risk. This should be your very last option.

    Every time that a vulnerability is not remediated, it continues to pose a risk to the organization. While it may seem that every vulnerability needs to be remediated, this is simply not possible due to limited resources. Further, it can take away resources from other security initiatives as opposed to low-priority vulnerabilities that are extremely unlikely to be exploited.

    Common criteria for vulnerabilities that are not remediated:
    • Affected systems are of extremely low criticality.
    • Affected systems are deemed too critical to take offline to perform adequate remediation.
    • Low urgency is assigned to those vulnerabilities.
    • Cost and time required for the remediation are too high.
    • No adequate solutions exist – the vendor has not released a patch, there are weak defense-in-depth controls, and it is not possible to perform a configuration change.

    Risk acceptance is not uncommon…

    • With an ever-increasing number of vulnerabilities, organizations are struggling to keep up and often, intentionally or unintentionally, accept the risk associated.
    • In the end, non-remediation means full acceptance of the risk and any consequences.

    Enterprise risk management
    Arrow pointing up.
    Risk acceptance of vulnerabilities

    While these are common criteria, they must be aligned to the enterprise risk management framework and approved by management.

    Don’t forget the variables that were assessed in Phase 2. This includes the risk from potential lateral movement or if there is an existing exploit.

    Risk considerations

    When determining if risk acceptance is appropriate, consider the cost of not mitigating vulnerabilities.

    Don’t accept the risk because it seems easy. Consider the financial impact of leaving vulnerabilities open.

    With risk acceptance, it is important to review the financial impact of a security incident resulting from that vulnerability. There is always the possibility of exploitation for vulnerabilities. A simple metric taken from NIST SP800-40 to use for this is:

    Cost not to mitigate = W * T * R

    Where (W) is the number of work stations, (T) is the time spent fixing systems or lost in productivity, and (R) is the hourly rate of the time spent.

    As an example provided by NIST SP800-40 Version 2.0, Creating a Patch and Vulnerability Management Program:

    “For an organization where there are 1,000 computers to be fixed, each taking an average of 8 hours of down time (4 hours for one worker to rebuild a system, plus 4 hours the computer owner is without a computer to do work) at a rate of $70/hour for wages and benefits:

    1,000 computers * 8 hours * $70/hour = $560,000”

    Info-Tech Insight

    Always consider the financial impact that can occur from an exploited vulnerability that was not remediated.

    3.1.1 Develop risk and remediation action

    90 minutes

    Input: List of remediation options

    Output: List of remediation options sorted into “when to use” and “when to avoid” lists

    Materials: Whiteboard/flip charts, Vulnerability Management SOP Template

    Participants: IT Security Manager, IT Infrastructure Manager, IT Operations Manager, Corporate Risk Officer, CISO

    It is important to define and document your organization-specific criteria for when a remediation option is appropriate and inappropriate.

    1. List each remediation option on a flip chart and create two headings: “When to use” and “When to avoid.”
    2. Each person will list “when to use” criteria on a green sticky note and “when to avoid” criteria on a red one for each option; these will be placed on the appropriate flip chart.
    3. Discuss as a group which criteria are appropriate and which should be removed.
    4. Move on to the next remediation option when completed.
      • Ensure to include when there are remediation options that will be connected. For example, the risk may be accepted until the next available change window, or a defense-in-depth control is used before a patch can be fully installed.
    5. Once the criteria has been established, document this in the Vulnerability Management SOP Template.
    When to use:
    • When adequate testing can be performed on the patch to be implemented.
    • When there is a change window approaching, especially for critical systems.
    • When there is standardization across the IT assets to allow for easier installation of patches.
    When to avoid:
    • When the patch cannot be adequately tested.
    • When a patch has been tested, but it has caused an unfavorable consequence such as a system or application failure.
    • When there is no near change window in which to install the patches.
    (Example from the Vulnerability Management SOP Template for Patches.)

    Download the Vulnerability Management SOP Template

    Step 3.2

    Scheduling and executing remediation

    Activities

    None for this section.

    This step will walk you through the following activities:

    Although there are no specific activities for this section, it will walk you through your existing processes configuration and change management to ensure that you are leveraging those activities in your vulnerability remediation actions.

    This step involves the following participants:

    • IT Security Manager
    • SecOps team members
    • ITOps team members, including tiers 1, 2, and 3
    • CISO
    • CIO

    Outcomes of this step

    Gained understanding of how IT operations processes configuration and change management can be leveraged for the vulnerability remediation process. Don’t reinvent the wheel!

    Remediate vulnerabilities
    Step 3.1 Step 3.2 Step 3.3

    Implementing the remediation

    Vulnerability management converges with your IT operations functions.
    • Once a remediation strategy has been formulated, you can leverage your release and change management processes to orchestrate the testing, version tracking, scheduling, approval, and implementation activities.
    • Each of these processes should exist in your environment in some form. Leveraging these will engage the IT operations team to carry out their tasks in the remediation process.
    • There can be a partial or full handoff to these processes, however, the owner of the vulnerability management program is responsible for verifying the application of the remediation measure and that the overall risk has been reduced.
    • Although full blueprints exist that cover each of these processes in great detail, the following slides provide an overview of each of these IT operations processes and how they intersect with vulnerability management.
    Stock image of a person on a laptop overlaid by an icon with gears indicating settings.

    Release Management

    Control the quality of deployments and releases of software updates.

    • The release management process exists to ensure that new software releases (such as patches and updates) are properly tested and documented with version control prior to their implementation into the production environment.
    • The process should map out the logistics of the deployment process to ensure that it is consistent and controlled.
    • Testing is an important part of release management and the urgency of a vulnerability remediation operation can expedite this process to ensure minimal delays. Once testing has been completed successfully, the update is then “promoted” to production-ready status and submitted into the change management process.
    • Often a separate release team may not exist, however, release management still occurs.

    For guidance on implementing or improving your release management process, refer to Info-Tech’s Stabilize Release and Deployment Management blueprint or speak to one of our experts.

    Info-Tech Insight

    Many organizations don’t have a separate release team. Rather, whomever is doing the deployment will submit a change request and the testing details are vetted through the organization’s change management process.

    For guidance on the change management process review our Optimize Change Management blueprint.

    Change Management

    Leverage change control, interruption management, approval, and scheduling.
    • Change management likely exists in some shape or form in your organization. There is usually someone or a committee, such as a change advisory board (CAB), that gives approval for a change.
    • Leveraging the change management process will ensure that your vulnerability remediation has undergone the proper review and approval before implementation. There will usually be business sign-off as part of a change management approval process.
    • Communication will also be integrated in the change management process, so the change manager will ensure that appropriate, timely communications are sent to the proper key stakeholders.
    • The change management process will link to release management and configuration management processes if they exist.

    For further guidance on implementing or improving your change management process, refer to Info-Tech’s Optimize Change Management blueprint or speak to one of our experts.

    “With no controls in place, IT gets the blame for embarrassing outages. Too much control, and IT is seen as a roadblock to innovation.” (VP IT, Federal Credit Union)

    Post-implementation activities

    Vulnerability remediation isn’t a “set it and forget it” activity.
    • Once vulnerability remediation has occurred, it is imperative that the results are reported back to the vulnerability management program manager. This ensures that the loop is closed and the tracking of the remediation activity is done properly.
      • Organizations that are subject to audit by external entities will understand the importance of such documentation.
    • The results of post-implementation review from the change management process will be of great interest, particularly if there was any deviation from the planned activities.
    • Although change execution will usually undergo some form of testing during the maintenance window, there is always the possibility that something has broken as a result of the software update. Be quick to respond to these types of incidents!
      • One example of an issue that is near impossible to test during a maintenance window is one that manifests only when the system or software comes under load. This is what makes for busy Monday mornings after a weekend change window.
    A scan with your vulnerability management software after remediation can be a way to verify that the overall risk has been reduced, if remediation was done by way of patching/updates.

    Info-Tech Insight

    After every change completion, whether due to vulnerability remediation or not, it is a good idea to ensure that your infrastructure team increases its monitoring diligence and that your service desk is ready for any sudden influx of end-user calls.

    Step 3.3

    Continuous improvement

    Activities

    None for this section.

    This step will walk you through the following activities:

    Although this section has no activities, it will review the process by which you may continually improve vulnerability management.

    This step involves the following participants:

    • IT Security Manager
    • SecOps team members
    • ITOps team members, including tiers 1, 2, and 3
    • CISO
    • CIO

    Outcomes of this step

    An understanding of the importance of ongoing improvements to the vulnerability management program.

    Remediate vulnerabilities
    Step 3.1 Step 3.2 Step 3.3

    Drive continuous improvement

    • Also known as “Continual Improvement” within the ITIL best practice framework.
    • Your vulnerability management program will not be perfect on first launch. In fact, due to the ever-changing nature of vulnerabilities and the technology designed to detect and combat vulnerabilities, the processes within your vulnerability management program will need to be tweaked from time to time.
    • Continuous improvement is a sustained, proactive approach to process improvement. The practice allows for all process participants to observe and suggest incremental improvements that can help improve the overall process.
    • In many cases, continuous improvement can be triggered by changes in the environment. This makes perfect sense for vulnerability management process improvement as a change in the environment will require vulnerability scanning to ensure that such changes have not introduced new vulnerabilities into the environment, increasing your risk surface.
    • One key method to tracking continuous improvement is through the effective use of metrics, covered in Section 4.1 of this blueprint.
    “The success rate for continual improvement efforts is less than 60 percent. A major – if not the biggest – factor affecting the deployment of long-term continual improvement initiatives today is the fundamental change taking place in the way companies manage and execute work.” (Industry analyst at a consulting firm, 2014)

    Continuous Improvement

    Continuously re-evaluate the vulnerability management process.

    As your systems and assets change, your vulnerability management program may need updates in two ways.

    When new assets and systems are introduced:

    • When new systems and assets are introduced, it is important for organizations to recognize how these can affect vulnerability management.
    • It will be necessary to identify the business criticality of the new assets and systems and the sensitivity of the data that can be found on them.
    • Without doing so, these will be considered rogue systems or assets – there is no clear process for assigning urgencies.
    • This will only cause problems as actions may be taken that are not aligned with the organization’s risk management framework.

    Effective systems and asset management are needed to track this. Review Info-Tech’s Implement Systems Management to Improve Availability and Visibility blueprint for more help.

    Document any changes to the vulnerability management program in the Vulnerability Management SOP Template.

    When defense-in-depth capabilities are modified:

    • As you build an effective security program, more controls will be added that can be used to protect the organization.
    • These should be documented and evaluated based on ability to mitigate against vulnerabilities.
    • The defense-in-depth model that was previously established should be updated to include the new capabilities that can be used.
    • Defense-in-depth models are continually evolving as the security landscape evolves, and organizations must be ready for this.

    To assist in building a defense-in-depth model, review Build an Information Security Strategy.

    Implement Risk-Based Vulnerability Management

    Phase 4

    Measure and formalize

    Phase 1

    1.1 What is vulnerability management?
    1.2 Define scope and roles
    1.3 Cloud considerations for vulnerability management
    1.4 Vulnerability detection


    Phase 2

    2.1 Triage vulnerabilities
    2.2 Determine high-level business criticality
    2.3 Consider current security posture
    2.4 Risk assessment of vulnerabilities


    Phase 3

    3.1 Assessing remediation options
    3.2 Scheduling and executing remediation
    3.3 Continuous improvement


    Phase 4

    4.1 Metrics, KPIs & CSFs
    4.2 Vulnerability management policy
    4.3 Select and implement a scanning tool
    4.4 Penetration testing

    This phase will walk you through the following activities:

    • You will determine what ought to be measured to track the success of your vulnerability management program.
    • If you lack a scanning tool this phase will help you determine tool selection.
    • Lastly, penetration testing is a good next step to consider once you have your vulnerability management program well underway.

    This phase involves the following participants:

    • IT Security Manager
    • SecOps team members
    • Procurement representatives
    • CISO
    • CIO

    Step 4.1

    Metrics, Key Performance Indicators (KPIs), and Critical Success Factors (CSFs)

    Activities
    • 4.1.1 Measure your program with metrics, KPIs, and CSFs

    This step will walk you through the following activities:

    After a review of the differences between raw metrics, key performance indicators (KPI), and critical success factors (CSF), compile a list of what metrics you will be tracking, why, and the business goals for each.

    This step involves the following participants:

    • IT Security Manager
    • SecOps team members
    • CISO
    • CIO

    Outcomes of this step

    Outline of metrics you can configure your vulnerability scanning tool to report on.

    Measure and formalize
    Step 4.1 Step 4.2 Step 4.3 Step 4.4

    You can’t manage what you can’t measure

    Metrics provides visibility.

    • Management consultant Peter Drucker introduced the concept of metrics tied to key performance indicators (KPIs), and the concept holds true: without metrics, you lack the visibility to manage or improve a process.
    • Metrics aren’t just a collection of statistics, they have to be meaningful, they have to tell the story, and most importantly, they have to answer the “so what?” question. What is the significance of a metric – do they illustrate a trend or an anomaly? What actions should be carried out when a metric hits a certain threshold?
    • It would be prudent to track several metrics that can be combined to tell the full story. For example, tracking the number of critical vulnerabilities alone does not give a sense of the overall risk to the organization, nor does it offer any information on how quickly they have been remediated or what amount of effort was invested.
    Stock image of measuring tape.

    Metrics, KPIs, and CSFs

    Tracking the right information and making the information relevant.
    • There is often confusion between raw metrics, key performance indicators, and critical success factors.
    • Raw metrics are what is trackable from your systems and processes as a set of measurements without any context. Raw metrics in themselves are useful in telling the story of “what are we doing?”
    • KPIs are the specific metric or combination of metrics that help you track or gauge performance. KPIs tell the story of “how are we doing?” or “how well are we doing?”
    • CSFs are the specific KPIs that track the activities that are absolutely critical to accomplish for the business or business unit to be successful.
    The activity tracker on your wrist is a wealth of metrics, KPIs, and CSFs.

    If you wear an activity tracker, you are likely already familiar with the differences between metrics, key performance indicators, and critical success factors:

    • The raw metrics are your heart rate, step count, hours of sleep, caloric intake, etc.
    • KPIs are the individual goals that you have set: maintain a heart rate within the appropriate range for your age/activity level, achieve a step count goal per day, get x hours of sleep per night, consume a calorie range of y per day, etc.
    • CSFs are your overall goal: increase your cardiovascular capacity, lose weight, feel more energetic, etc.

    Your security systems can be similarly measured and tracked – transfer this skill!

    Tracking relevant information

    Tell the story in the numbers.

    Below are a number of suggested metrics to track, and why.

    Business Goal

    Critical Success Factor

    Key Performance Indicator

    Metric to track

    Minimize overall risk exposure Reduction of overall risk due to vulnerabilities Decrease in vulnerabilities Track the number of vulnerabilities year after year.
    Appropriate allocation of time and resources Proper prioritization of vulnerability mitigation activities Decrease of critical and high vulnerabilities Track the number of high-urgency vulnerabilities.
    Consistent timely remediation of threats to the business Minimize risk when vulnerabilities are detected Remediate vulnerabilities more quickly Mean time to detect: track the average time between the identification to remediation.
    Track effectiveness of scanning tool Minimize the ratio, indicating that the tool sees everything Ratio between known assets and what the scanner tracks Scanner coverage compared to known assets in the organization.
    Having effective tools to track and address Accuracy of the scanning tool Difference or ratio between reported vulnerabilities and verified ones Number of critical or high vulnerabilities verified, between the scanning tool’s criticality rating and actual criticality.
    Reduction of exceptions to ensure minimal exposure Visibility into persistent vulnerabilities and risk mitigation measures Number of exceptions granted Number of vulnerabilities in which little or no remediation action was taken.

    4.1.1 Measure your program with metrics, KPIs, and CSFs

    60 minutes

    Input: List of metrics current being measured by the vulnerability management tool

    Output: List of relevant metrics to track, and the KPIs, CSFs, and business goals related to the metric

    Materials: Whiteboard/flip charts, Vulnerability Management SOP Template

    Participants: IT Security Manager, IT operations management, CISO

    Metrics can offer a way to view how the organization is dealing with vulnerabilities and if there is improvement.

    1. Determine the high-level vulnerability management goals for the organization.
    2. Even with a formal process in place, the organization should be considering ways it can improve.
    3. Determine metrics that can help quantify those goals and how they can be measured.
    4. Metrics should always be easy to measure. If it’s a complex process to find the information required, it means that it is not a metric that should be used.
    5. Document your list of metrics in the Vulnerability Management SOP Template.

    Download the Vulnerability Management SOP Template

    Step 4.2

    Vulnerability Management Policy

    Activities
    • 4.2.1 Update the vulnerability management program policy

    This step will walk you through the following activities:

    If you have a vulnerability management policy, this activity may help augment it. Otherwise, if you don’t have one, this would be a great starting point.

    This step involves the following participants:

    • IT Security Manager
    • CISO
    • CIO
    • Human resources representative

    Outcomes of this step

    An inaugural policy covering vulnerability management

    Measure and formalize
    Step 4.1 Step 4.2 Step 4.3 Step 4.4

    Vulnerability Management Program Policy

    Policies provide governance and enforcement of processes.
    • Policies offer formal guidance on the “rules” of a program, describing its purpose, scope, detailed program description, and consequences of non-compliance. Often they will have a employee sign-off acknowledging understanding.
    • In many organizations, policies are endorsed by senior executives, which gives the policy its “teeth” across the company. The human resources department will always have input due to the implications of the non-compliance aspect.
    • Policies are written to ensure an outcome of consistent expected behavior and are often written to protect the company from liability.
    • Policies should be easy to understand and unambiguous, reflect the current state, and be enforceable. Enforceability can come in the form of audit, technology, or any other means of determining compliance and enforcing behavior.
    Stock image of a judge's gavel.

    4.2.1 Update the vulnerability management policy

    60 minutes

    Input: Vulnerability Management SOP, HR guidance on policy creation and approval

    Output: Completed Vulnerability Management Policy

    Materials: Vulnerability Management SOP, Vulnerability Management Policy Template

    Participants: IT Security Manager, IT operations management, CISO, Human resources representative

    After having built your entire process in this project, formalize it into a vulnerability management policy. This will set the standards and expectations for vulnerability management in the organization, while the process will be around the specific actions that need to be taken around vulnerability management.

    This is separate and distinct from the Vulnerability Management SOP Template, which is a process and procedure document.
    1. Review Info-Tech’s Vulnerability Management Policy and customize it to your organization’s specifications.
    2. Use your Vulnerability Management SOP as a resource when specifying some of the details within the policy.
    Sample of Info-Tech's Vulnerability Management Policy Template

    Download the Vulnerability Management Policy Template

    Step 4.3

    Select and implement a scanning tool

    Activities
    • 4.3.1 Create an RFP for vulnerability scanning tools

    This step will walk you through the following activities:

    If you need to select a new vulnerability scanning tool, or replace your existing one, this activity will help set up a request for proposal (RFP).

    This step involves the following participants:

    • IT Security Manager
    • SecOps team members
    • CISO

    Outcomes of this step

    The provisions needed for you to create and deploy an RFP for a vulnerability management tool.

    Measure and formalize
    Step 4.1 Step 4.2 Step 4.3 Step 4.4

    Vulnerability management and penetration testing

    Similar in nature, yet provide different security functions.

    Vulnerability Scanning Tools

    Scanning tools focus on the network and operating systems. These tools look for items such as missing patches or open ports. They won’t detect specific application vulnerabilities.

    Exploitation Tools

    These tools will look to exploit a detected vulnerability to validate it.

    Penetration Tests

    A penetration test simulates the actions of an external or internal cyber attacker that aims to breach the information security of the organization. (Formal definition of penetration test)

    ‹————— What’s the difference again? —————›
    Vulnerability scanning tools are just one type of tool. When you add an exploitation tool to the mix, you move down the spectrum. Penetration tests will use scanning tools, exploitation tools, and people.

    What is the value of each?

    • For vulnerability scans, the person performing the scan provides the value – value comes from the organization itself.
    • For exploitation tools on their own, the value comes from the tool itself being used in a safe environment.
    • For penetration tests, the tester is providing the value. They are the value add.

    What’s the implication for me?

    Info-Tech Recommends:
    • A combination of vulnerability scanning and penetration testing. This will improve your security posture through systematic risk reduction and improve your security program through the testing of prevention, detection, and response capabilities with unique recommendations being generated.
    • Start with as much vulnerability scanning as possible to identify gaps to fix and then move onto a penetration test to do a more robust and validated assessment.
    • For penetration tests, start with a transparent box test first, then move to an opaque box. Ideally, this is done with different third parties.

    Vulnerability scanning software

    All organizations can benefit from having one.

    Scanning tools will benefit areas beyond just vulnerability management

    • Network security: It improves the accuracy and granularity of your network security technologies such as WAFs, NGFWs, IDPS, and SIEM.
    • Asset management: Vulnerability scanning can identify new or unknown assets and provide current status information on assets.
    • System management: Information from a vulnerability scan supports baselining activities and determination of high-value and high-risk assets.

    Vulnerability Detection Use Case

    Most organizations use scanners to identify and assess system vulnerabilities and prioritize efforts.

    Compliance Use Case

    Others will use scanners just for compliance, auditing, or larger GRC reasons.

    Asset Discovery Use Case

    Many organizations will use scanners to perform active host and application identification.

    Scanning Tool Market Trends

    Vulnerability scanning tools have expanded value from conventional checking for vulnerabilities to supporting configuration checking, asset discovery, inventory management, patch management, SSL certificate validation, and malware detection.

    Expect to see network and system vulnerability scanners develop larger vulnerability management functions and develop exploitation tool functionality. This will become a table stakes option enabling organizations to provide higher levels of validation of detected vulnerabilities. Some tools already possess these capabilities:

    • Core Impact is an exploitation tool with vulnerability scanning aspects.
    • Metasploit is an exploitation tool with some new vulnerability scanning aspects.
    • Nessus is mainly a vulnerability scanning tool but has some exploitation aspects.

    Device proliferation (BYOD, IoT, etc.) is increasing the need for stronger vulnerability management and scanners. This is driving the need for numerous device types and platform support and the development of baseline and configuration norms to support system management.

    Increased regulatory or compliance controls are also stipulating the need for vulnerability scanning, especially by a trusted third party.

    Organizations are outsourcing security functions or moving to cloud-based deployment options for any security technology they can. Expect to see massive growth of vulnerability scanning as a service.

    Vulnerability scanning market

    There are several technology types or functional differentiators that divide the market up.

    Vulnerability Exploitation Tools

    • These will actually test defences and better emulate real life than just scanning. These tools include packet manipulation tools (such as hping) and password cracking tools (such as John the Ripper or Cain and Abel).
    • These tools will provide much more granular information on your network, operations systems, and applications.
    • The main limitation of these tools is how to use them. If you do not have development or test environments that mimic your real production environments to run the exploit tools, these tools may not be appropriate. It may work if you can find some downtime on production systems, but only in very specific and careful instances.
    • Lower maturity security programs usually just do network and application vulnerability scanning. Higher maturity programs will also use penetration testing, application testing, and vulnerability exploitation tools.
    • Network vulnerability scanning tools should always be used. Once you identify any servers or ports running web applications, then you run a web application vulnerability scanner.
    • Exploitation tools and application testing tools are used in more specific use cases that are often related to more-demanding security programs.

    Scanning Tool Market Trends

    • These are considered baseline tools and are near commoditization.
    • Vulnerability scanning tools are not granular enough to detect application-level vulnerabilities (thus the need for application scanners and testing tools) and they don’t validate the exploitability of the vulnerability (thus the need for exploit tools).

    Web Application Scanning Tools

    These tools perform dynamic application security testing (DAST) and static application security testing (SAST).

    Application Scanning and Testing Tools

    • These perform a detailed scan against an application to detect any problematic or malicious code and try to break the application using known vulnerabilities.
    • These tools will identify if something is vulnerable to an exploit but won’t actually run the exploit.
    • These tools are evaluated based on their ability to detect application-specific issues and validate them.

    Vulnerability scanning tool features

    Evaluate vulnerability scanning tools on specific features or functions that are the best differentiators.

    Differentiator

    Description

    Deployment Options Do you want a traditional on-premises, cloud-based, or managed service?
    Vulnerability Database Coverage Scanners use a library of known vulnerabilities to test for. Evaluate based on the amount of exploits/vulnerabilities the tool can scan for.
    Scanning Method Evaluate if you want agent-based, authenticated active, unauthenticated active, passive, or some combination of those scanning methods.
    Integration What is the breadth of other security and non-security technologies the tool can integrate with?
    Remediation How detailed are the recommended remediation actions? The more granular, the better.
     

    Differentiator

    Description

    Prioritization Does the tool evaluate vulnerabilities based on commonly accepted methods or through a custom-designed prioritization methodology?
    Platform Support What is the breadth of environment, application, and device support in the tool? Consider your need for virtual support, cloud support, device support, and application-specific support. Also consider how often new scanning modules are supported (e.g. how quickly Windows 10 was supported).
    Pricing As with many security controls that have been around for a long time and are commonly used, pricing becomes a main consideration, especially when there are so many open-source options available.

    Common areas people mistake as tool differentiators:

    • Accuracy – Scanning tools are evaluated more on efficiency than effectiveness. Evaluate on the ability to detect, remediate, and manage vulnerabilities rather than real vulnerability detection and the number of false positives. To reduce false positives, you need to use exploitation tools.
    • Performance – Scanning tools have such a small footprint in an environment and the actual scanning itself is such a small impact that evaluation on performance doesn’t matter.

    For more information on vulnerability scanning tools and how they rate, review the Vulnerability Management category on SoftwareReviews.

    Vulnerability scanning deployment options

    Understand the different deployment options to identify which is best for your security program.

    Option

    Description

    Pros

    Cons

    Use Cases

    On-Premises Either an on-premises appliance or an on-premises virtualized machine that performs external and internal scanning.
    • Small resource need, so limited network impact.
    • Strong internal scanning.
    • Easier integration with other technologies.
    • Network footprint and resource usage.
    • Maintenance and support costs.
    • Most common deployment option.
    • Appropriate if you have cloud concerns or strong internal network scanning, or if you require strong integration with other systems.
    Cloud Either hosted on a public cloud infrastructure or hosted by a third party and offered “as a service.”
    • Small network footprint.
    • On-demand scanning as needed.
    • Optimal external scanning capabilities.
    • Can only do edge-related scanning unless authenticated or agent based.
    • No internal network scanning with passive or unauthenticated active scanning methods.
    • Very limited network resources.
    • Compliance obligations that dictate external vulnerability scanning.
    Managed A third party is contracted to manage and maintain your vulnerability scanner so you can dedicate resources elsewhere.
    • Expert management of environment scanning, optimizing tool usage.
    • Most scanning work time is report customization and tuning and remediation efforts; thus, managed doesn’t provide sizable resource alleviation.
    • Third party has and owns the vulnerability information.
    • Limited staff resources or expertise to maintain and manage scanner.

    Vulnerability scanning methods

    Understand the different scanning methods to identify which tool best supports your needs.

    Method

    Description

    Pros

    Cons

    Use Cases

    Agent-Based Scanning Locally installed software gives the information needed to evaluate the security posture of a device.
    • Provides information that can’t be discovered remotely such as installed applications that aren’t running at a given time.
    • Device processing, memory, and network bandwidth impact.
    • Asset without an agent is not scanned.
    • Need for continuous scanning.
    • Organization has strong asset management
    Authenticated Active Scanning Tool uses authenticated credentials to log in to a device or application to perform scanning.
    • Provides information that can’t be discovered remotely such as installed applications that aren’t running at a given time.
    • Best accuracy for vulnerability detection across a network.
    • Aggregation and centralization of authenticated credentials creates a major risk.
    • All use cases.
    Unauthenticated Active Scanning Scanning of devices without any authentication.
    • Emulates realistic scan by an attacker.
    • Provides limited scope of scanning.
    • Some compliance use cases.
    • Perform after either agent or authenticated scanning.
    Passive Scanning Scanning of network traffic.
    • Lowest resource impact.
    • Not enough information can be provided for true prioritization and remediation.
    • Augmenting scanning technique to agent or authenticated scanning.

    IP Management and IPv6

    IP management and the ability to manage IPv6 is a new area for scanning tool evaluation.

    Scanning on IPv4

    Scanning tools create databases of systems and devices with IP addresses.
    Info-Tech Recommends:

    • It is easier to do discovery by directing the scanner at a set IP address or range of IP addresses; thus, it’s useful to organize your database by IPs.
    • Do discovery by phases: Start with internet-facing systems. Your perimeter usually is well-defined by IP addresses and system owners and is most open to attack.
    • Stipulate a list of your known IP addresses through the DHCP registration and perform a scan on that.
    • Depending on your IP address space, another option is to scan your entire IP address space.

    Current Problem With IP Addresses

    IP addresses are becoming no longer manageable or even owned by organizations. They are often provided by ISPs or other third parties.

    Even if it is your range, chances are you don't do static IP ranges today.

    Info-Tech Recommends:

    • Agent-based scanning or MAC address-based scanning
    • Use your DHCP for scanning

    Scanning on IPv6

    First, you need to know if your organization is moving to IPv6. IPv6 is not strategically routed yet for most organizations.

    If you are moving to IPv6, Info-Tech recommends the following:

    • Because you cannot point a scanner at an IPv6 IP range, any scanning tool needs to have a strategy around how to handle IPv6 and properly scan based on IP ranges.
    • You need to know IPv4 to IPv6 translations.
    • Evaluate vulnerability scanning tools on whether any IPv6 features are on par with IPv4 features.

    If you are already on IPv6, Info-Tech recommends the following:

    • If you are on an IPv6 native network, it is nearly impossible to scan the network. You have to always scan your known addresses from your DHCP.

    4.3.1 Create an RFP for vulnerability scanning tools

    2 hours

    Input: List of key feature requirements for the new tool, List of intersect points with current software, Network topology and layout of servers and applications

    Output: Completed RFP document that can be distributed to vendor proponents

    Materials: Whiteboard/flip charts, Vulnerability Scanning Tool RFP Template

    Participants: IT Security Manager, IT operations managers, CISO, Procurement department representative

    Use a request for proposal (RFP) template to convey your desired scanning tool requirements to vendors and outline the proposal and procurement steps set by your organization.

    1. Determine what kind of requirements will be needed for your scanning tool RFP, based on people, process, and technology requirements.
    2. Consider items such as the desired capabilities and the scope of the scanning.
    3. Conduct interviews with relevant stakeholders to determine the exact requirements needed.
    4. Use Info-Tech’s Vulnerability Scanning Tool RFP Template. It lists many requirements but can be customized to your organization’s specific needs.

    Download the Vulnerability Scanning Tool RFP Template

    4.3.1 Create an RFP for vulnerability scanning tools (continued)

    Things to Consider:
    • Ensure there is adequate resource dedication to support and maintenance for vulnerability scanning.
    • Consider if you will benefit from an RFP. If there is a more appropriate option for your need and your organization, consider that instead.
    • If you don’t know the product you want, then perform an RFI.
    • In the RFP, you need to express your driving needs for the tool so the vendor can best understand your use case.
    • Identify who should participate in the RFP creation and evaluation. Make sure they have time available and it does not conflict with other items.
    • Determine if you want to send it to a select few or if you want to send it to a lot of vendors.
    • Determine a response date so you can know who is soliciting your business.
    • You need to have a process to handle questions from vendors.
    Info-Tech RFP Table of Contents:
    1. Statement of Work
    2. General Information
    3. Proposal Preparation Instructions
    4. Scope of Work, Specifications, and Requirements
    5. Vendor Qualifications and References
    6. Budget and Estimated Pricing
    7. Vendor Certification

    Download the Vulnerability Scanning Tool RFP Template

    Step 4.4

    Penetration testing

    Activities
    • 4.1.1 Create an RFP for penetration tests

    This step will walk you through the following activities:

    We will review penetration testing, its distinction from vulnerability management, and why you may want to engage a penetration testing service.

    We provide a request for proposal (RFP) template that we can review if this is an area of interest.

    This step involves the following participants:

    • IT Security Manager
    • SecOps team members
    • CISO
    • CIO

    Outcomes of this step

    An understanding of penetration testing, and guidance on how to get started if there is interest to do so.

    Measure and formalize
    Step 4.1 Step 4.2 Step 4.3 Step 4.4

    Penetration testing

    Penetration tests are critical parts of any strong security program.

    Penetration testing will emulate the methods an attacker would use in the real world to circumvent your security controls and gain access to systems and data.

    Penetration testing is much more than just running a scanner or other automated tools and then generating a report. Penetration testing performs critical exploit validation to create certainty around your vulnerability.

    The primary objective of a penetration test is to identify and validate security weaknesses in an organization’s security systems.

    Reasons to Test:

    • Assess current security control effectiveness
    • Develop an action plan of items
    • Build a business case for a better security program
    • Increased security budget through vulnerability validation
    • Third-party, unbiased validation
    • Adhere to compliance or regulatory requirements
    • Raise security awareness
    • Demonstrate how an attacker can escalate privileges
    • Effective way to test incident response

    Regulatory Considerations:

    • There is a lot of regulatory wording saying that organizations can’t get a system that is managed, integrated, and supported by one vendor and then have it tested by the same vendor.
    • There is the need for separate third-party testing.
    • Penetration testing is required for PCI, cloud providers, and federal entities.

    How and where is the value being generated?

    Penetration testing is a service provided by trained and tested professionals with years of experience. The person behind the test is the most important part of the test. The person is able to emulate a real-life attacker better than any computer. It is just a vulnerability scan if you use tools or executables alone.

    “A penetration test is an audit with validation.” (Joel Shapiro, Vice President Sales, Digital Boundary Group)

    Start by considering the spectrum of penetration tests

    Network Penetration Tests

    Conventional testing of network defences.

    Testing vectors include:

    • Perimeter infrastructure
    • Wireless, WEP/WPA cracking
    • Cloud penetration testing
    • Telephony systems or VoIP
    Types of tests:
    • Denial-of-service testing
    • Out-of-band attacks
    • War dialing
    • Wireless network testing/war driving
    • Spoofing
    • Trojan attacks
    • Brute force attacks
    • Watering hole attacks
    • Honeypots
    • Cloud-penetration testing
    Application Penetration Tests

    Core business functions are now being provided through web applications, either to external customers or to internal end users.

    Types: Web apps, non-web apps, mobile apps

    Application penetration and security testing encompasses:

    • Code review – analyzing the application code for sensitive information of vulnerabilities in the code.
    • Authorization testing – testing systems responsible for user session management to see if unauthorized access can be permitted.
    • Authentication process for user testing.
    • Functionality testing – test the application functionality itself.
    • Website pen testing – active analysis of weaknesses or vulnerabilities.
    • Encryption testing – testing things like randomness or key strength.
    • User-session integrity testing.
    Human-Centric Testing
    • Penetration testing is developing a people aspect as opposed to just being technology focused.
    • End users and their susceptibility to social engineering attacks (spear phishing, phone calls, physical site testing, etc.) is now a common area to test.
    • Social engineering penetration testing is not only about identifying your human vulnerabilities, but also about proactively training your end users. As well as discovering and fixing potential vulnerabilities, social engineering penetration testing will help to raise security awareness within an organization.

    Info-Tech Insight

    Your pen test should use multiple methods. Demonstrating weakness in one area is good but easy to identify. When you blend techniques, you get better success at breaching and it becomes more life-like. Think about prevention, detection, and response testing to provide full insight into your security defenses.

    Penetration testing types

    Evaluate four variables to determine which type of penetration test is most appropriate for your organization.

    Evaluate these dimensions to determine relevant penetration testing.

    Network, Application, or Human

    Evaluate your need to perform different types of penetration testing.

    Some level of network and application testing is most likely appropriate.

    The more common decision point is to consider to what degree your organization requires human-centric penetration testing.

    External or Internal

    External: Attacking an organization’s perimeter and internet-facing systems. For these, you generally provide some level of information to the tester. The test will begin with publicly available information gathering followed by some kind of network scanning or probing against externally visible servers or devices (DNS server, email server, web server, firewall, etc.)

    Internal: Carried out within the organization’s network. This emulates an attack originating from an internal point (disgruntled employee, authorized user, etc.). The idea is to see what could happen if the perimeter is breached.

    Transparent, Semi-Transparent, or Opaque Box

    Opaque Box: The penetration tester is not provided any information. This emulates a real-life attack. Test team uses publicly available information (corporate website, DNS, USENET, etc.) to start the test. These tests are more time consuming and expensive. They often result in exploitation of the easiest vulnerability.
    Use cases: emulating a real-life attack; testing detection and response capabilities; limited network segmentation.

    Transparent Box: Tester is provided full disclosure of information. The tester will have access to everything they need: building floor plans, data flow designs, network topology, etc. This represents what a credentialed and knowledgeable insider would do.
    Use cases: full assessment of security controls; testing of attacker traversal capabilities.

    Aggressiveness of the Test

    Not Aggressive: Very slow and careful penetration testing. Usually spread out in terms of packets being sent and number of calls to individuals. It attempts to not set off any alarm bells.

    Aggressive: A full DoS attack or something similar. These would be DoS attacks that take down systems or full SQL injection attacks all at once versus small injections over time. Testing options cover anything including physical tests, network tests, social engineering, and data extraction and exfiltration. This is more costly and time consuming.

    Assessing Aggressiveness: How aggressive the test should be is based on the threats you are concerned with. Assess who you are concerned with: random individuals on the internet, state-sponsored attacks, criminals, hacktivists, etc. Who you are concerned with will determine the appropriate aggressiveness of the test.

    Penetration testing scope

    Establish the scope of your penetration test before engaging vendors.

    Determining the scope of what is being tested is the most important part of a penetration test. Organizations need to be as specific as possible so the vendor can actually respond or ask questions.

    Organizations need to define boundaries, objectives, and key success factors.

    For scope:
    • If you go too narrow, the realism of the test suffers.
    • If you go too broad, it is more costly and there’s a possible increase in false positives.
    • Balance scope vs. budget.
    Boundaries to scope before a test:
    • IP addresses
    • URLs
    • Applications
    • Who is in scope for social engineering
    • Physical access from roof to dumpsters defined
    • Scope prioritized for high-value assets
    Objectives and key success factors to scope:
    • When is the test complete? Is it at the point of validated exploitation?
    • Are you looking for as many holes as possible, or are you looking for how many ways each hole can be exploited?

    What would be out of scope?

    • Are there systems, IP addresses, or other things you want out of scope? These are things you don’t explicitly want any penetration tester to touch.
    • Are there third-party connections to your environment that you don’t want to be tested? These are instances such as cloud providers, supply chain connections, and various services.
    • Are there things that would be awkward to test? For example, determine if you include high-level people in a social engineering test. Do you conduct social engineering for the CEO? If you get their credentials, it could be an awkward moment.

    Ways to break up a penetration test:

    • Location – This is the most common way to break up a penetration test.
    • Division – Self-contained business units are often done as separate tests so you can see how each unit does.
    • IT systems – For example, you put certain security controls in a firewall and want to test its effectiveness.
    • Applications – For example, you are launching a new website or a new portal and you want to test it.

    Penetration testing appropriateness

    Determine your penetration testing appropriateness.

    Usual instances to conduct a penetration test:
    • Setting up a new physical office. Penetration testing will not only test security capabilities but also resource availability and map out network flows.
    • New infrastructure hardware implemented. All new infrastructure needs to be tested.
    • Changes or upgrades to existing infrastructure. Need for testing varies depending on the size of the change.
    • New application deployment. Need to test before being pushed to production environments.
    • Changes or upgrades to existing applications. When fundamental functional changes occur, perform testing:
      • Before upgrades or patching
      • After upgrades or patching
    • Periodic testing. It is a best practice to periodically test your security control effectiveness. Consider at least an annual test.

    Specific timing considerations: Testing should be completed during non-production times of day. Testing should be completed after a backup has been performed.

    Assess your threats to determine your appropriate test type:

    Penetration testing is about what threats you are concerned about. Understand your risk profile, risk tolerance level, and specific threats to see how relevant penetration tests are.

    • Are external attackers concerning to you? Are you distressed about how an attacker can use brute force to enter your network? If so, focus on ingress points, such as FWs, routers, and DMZ.
    • Is social engineering a concern for you (i.e. phone-based or email-based)? Then you are concerned about a credentialed hacker.
    • Is it an insider threat, a disgruntled employee, etc.? This also includes an internal system that is under command and control (C&C).

    ANALYST PERSPECTIVE: Do a test only after you take a first pass.
    If you have not done some level of vulnerability assessment on your own (performing a scan, checking third-party sources, etc.) don’t waste your money on a penetration test. Only perform a penetration test after you have done a first pass and identified and remediated all the low-hanging fruit.

    4.4.1 Create an RFP for penetration tests

    2 hours

    Input: List of criteria and scope for the penetration test, Systems and application information if white box

    Output: Completed RFP document that can be distributed to vendor proponents

    Materials: Whiteboard/flip charts, Penetration Test RFP Template

    Participants: IT Security Manager, IT operations managers, CISO, Procurement department representative

    Use an RFP template to convey your desired penetration test requirements to vendors and outline the proposal and procurement steps set by your organization.

    1. Determine what kind of requirements will be needed for your penetration test RFP based on people, process, and technology requirements.
      • Consider items such as your technology environment and the scope of the penetration tests.
    2. Conduct an interview with relevant stakeholders to determine the exact requirements needed.
    3. Use Info-Tech’s Penetration Test RFP Template, which lists many requirements but can be customized to your organization’s specific needs.

    Download the Penetration Test RFP Template

    4.4.1 Create an RFP for penetration tests (continued)

    Steps of a penetration test:
    1. Determine scope
    2. Gather targeted intelligence
    3. Review exploit attempts, such as access and escalation
    4. Test the collection of sensitive data
    5. Run reporting
    Info-Tech RFP Table of Contents:
    1. Statement of Work
    2. General Information
    3. Proposal Preparation Instructions
    4. Scope of Work, Specifications, and Requirements
    5. Vendor Qualifications and References
    6. Budget and Estimated Pricing
    7. Vendor Certification

    Download the Penetration Test RFP Template

    Penetration testing considerations – service providers

    Consider what type of penetration testing service provider is best for your organization

    Professional Service Providers

    Professional Services Firms. These firms will often provide a myriad of professional services across auditing, financial, and consulting services. If they offer security-related consulting services, they will most likely offer some level of penetration testing.

    Security Service Firms. These are dedicated security consulting or advisory firms that will offer a wide spectrum of security-related services. Penetration testing may be one aspect of larger security assessments and strategy development services.

    Dedicated Penetration Testing Firms. These are service providers that will often offer the full gamut of penetration testing services.

    Integrators

    Managed Security Service Providers. These providers will offer penetration testing. For example, Dell SecureWorks offers numerous services including penetration testing. For organizations like this, you need to be skeptical of ulterior motives. For example, expect recommendations around outsourcing from Dell SecureWorks.

    Regional or Small Integrators. These are service providers that provide security services of some kind. For example, they would help in the implementation of a firewall and offer penetration testing services as well.

    Info-Tech Recommends:

    • Always be conscientious of who is conducting the testing and what else they offer. Even if you get another party to test rather than your technology provider, they will try to obtain you as a client. Remember that for larger technology vendors, security testing is a small revenue stream for them and it’s a way to find technology clients. They may offer penetration testing for free to obtain other business.
    • Most of the penetration testers were systems administrators (for network testing) or application developers (for application testing) at some point before becoming penetration testers. Remember this when evaluating providers and evaluating remediation recommendations.
    • Evaluate what kind of open-source tools, commercial tools, and proprietary tools are being used. In general, you don’t want to rely on an open-source scanner. For open source, they will have more outdated vulnerability databases, system identification can also be limited compared to commercial, and reporting is often lacking.
    • Above all else, ensure your testers are legally capable, experienced, and abide by non-disclosure agreements.

    Penetration testing best practices – communications

    Communication With Service Provider

    • During testing there should be designated points of contact between the service provider and the client.
    • There needs to be secure channels for communication of information between the tester and the client both during the test and for any results.
    • Results should always be explained to the client by the tester, regardless of the content or audience.
    • There should be a formal debrief with the results report.
    Immediate reporting of issues
    • Before any testing commences, immediate reporting conditions need to be defined. These are instances when you would want immediate notification of something occurring.
    • Stipulate certain systems or data types that if broken into or compromised, you would want to be notified right away.
    • Example:
      • If you are conducting social engineering, require notification for all account credentials that are compromised. Once credentials are compromised, it destroys all accountability for those credentials and the actions associated with those credentials by any user.
      • Require immediate reporting of specific high-critical systems that are compromised or if access is even found.
      • Require immediate reporting when regulated data is discovered or compromised in any way.

    Communication With Internal Staff

    Do you tell your internal staff that this is happening?

    This is sometimes called a “double blind test” when you don’t let your IT team know of the test occurring.

    Pros to notifying:
    • This tests the organization’s security monitoring, incident detection, and response capabilities.
    • Letting the team know they are going to see some activity will make sure they don’t get too worried about it.
    • There may be systems you can’t jeopardize but still need to test so notification beforehand is essential (e.g. you wouldn’t allow ERP testing with notification).
    Cons:
    • It does not give you a real-life example of how you respond if something happens.
    • Potential element of disrespect to IT people.

    Penetration testing best practices – results and remediation

    What to expect from penetration test results report:

    A final results report will state all findings including what was done by the testers, what vulnerabilities or exploitations were detected, how they were compromised, the related risk, and related remediation recommendations.

    Expect four major sections:
    • Introduction. An overview of the penetration test methodology including rating methodology of vulnerabilities.
    • Executive Summary. A management-level description of the test, often including a summary of any recommendations.
    • Technical Review. An overview of each item that was looked at and touched. This area breaks down what was done, how it was done, what was found, and any related remediation recommendations. Expect graphs and visuals in this section.
    • Detailed Findings. An in-depth breakdown of all testing methods used and results. Each vulnerability will be explained regarding how it was detected, what the risk is, and what the remediation recommendation is.
    Two areas that will vary by service provider:

    Prioritization

    • Most providers will boast their unique prioritization methodology.
    • A high, medium, and low rating scale based on some combination of variables (e.g. ease of exploitation, breadth of hole, information accessed resulting in further exploitation).
    • The prioritization won’t take into account asset value or criticality.
    • Keep in mind the penetration test is not an input into ultimate vulnerability prioritization, but it can help determine your urgency.

    Remediation

    • Remediation recommendations will vary across providers.
    • Generally, fairly generic recommendations are provided (e.g. remove your old telnet and input up-to-date SSH).
    • Most of the time, it is along the lines of “we found a hole; close the hole.”

    Summary of Accomplishment

    Problem Solved

    At the conclusion of this blueprint, you will have created a full vulnerability management program that will allow you to take a risk-based approach to vulnerability remediation.

    Assessing a vulnerability’s risk will enable you to properly determine the true urgency of a vulnerability within the context of your organization; this ensures you are not just blindly following what the tool is reporting.

    The risk-based approach will allow you to prioritize your discovered vulnerabilities and take immediate action on critical and high vulnerabilities while allowing your standard remediation cycle to address the medium to low vulnerabilities.

    With your program defined and developed, you now need to configure your vulnerability scanning tool or acquire one if you don’t already have a tool in place.

    Lastly, while vulnerability management will help address your systems and applications, how do you know if you are secure from external malicious actors? Penetration testing will offer visibility, allowing you to plug those holes and attain an environment with a smaller risk surface.

    If you would like additional support, have our analysts guide you through other phases as part of an Info-Tech workshop.

    Contact your account representative for more information.

    workshops@infotech.com 1-888-670-8889

    Additional Support

    If you would like additional support, have our analysts guide you through other phases as part of an Info-Tech workshop.

    Photo of Jimmy Tom.

    Contact your account representative for more information.

    workshops@infotech.com 1-888-670-8889

    To accelerate this project, engage your IT team in an Info-Tech workshop with an Info-Tech analyst team.

    Info-Tech analysts will join you and your team at your location or welcome you to Info-Tech’s historic Toronto office to participate in an innovative onsite workshop.

    The following are sample activities that will be conducted by Info-Tech analysts with your team:

    Sample of the Implement Vulnerability Management storyboard.
    Review of the Implement Vulnerability Management storyboard
    Sample of the Vulnerability Mitigation SOP template.
    Build your vulnerability management SOP

    Contributors

    Contributors from 2016 version of this project:

    • Morey Haber, Vice President of Technology, BeyondTrust
    • Richard Barretto, Manager, Information Privacy and Security, Cimpress
    • Joel Shapiro, Vice President Sales, Digital Boundary Group

    Contributors from current version of this project:

    • 2 anonymous contributors from the manufacturing sector
    • 1 anonymous contributor from a US government agency
    • 2 anonymous contributors from the financial sector
    • 1 anonymous contributor from the medical technology industry
    • 2 anonymous contributors from higher education
    • 1 anonymous contributor from a Canadian government agency
    • 7 anonymous others; information gathered from advisory calls

    Bibliography

    Arya. “COVID-19 Impact: Vulnerability Management Solution Market | Strategic Industry Evolutionary Analysis Focus on Leading Key Players and Revenue Growth Analysis by Forecast To 2028 – FireMon, Digital Shadows, AlienVault.” Bulletin Line, 6 Aug. 2020. Accessed 6 Aug. 2020.

    Campagna, Rich. “The Lean, Mean Vulnerability Management Machine.” Security Boulevard, 31 Mar. 2020. Accessed 15 Aug. 2020.

    Constantin, Lucian. “What are vulnerability scanners and how do they work?” CSO Online, 10 Apr. 2020. Accessed 1 Sept. 2020.

    “CVE security vulnerabilities published in 2019.” CVE Details. Accessed 22 Sept. 2020.

    Garden, Paul, et al. “2019 Year End Report – Vulnerability QuickView.” Risk Based Security, 2020. Accessed 22 Sept. 2020.

    Keary, Eoin. “2019 Vulnerability Statistics Report.” Edgescan, Feb. 2019. Accessed 22 Sept. 2020.

    Lefkowitz, Josh. ““Risk-Based Vulnerability Management is a Must for Security & Compliance.” SecurityWeek, 1 July 2019. Accessed 1 Nov. 2020.

    Mell, Peter, Tiffany Bergeron, and David Henning. “Creating a Patch and Vulnerability Management Program.” Creating a Patch and Vulnerability Management Program. NIST, Nov. 2005. Web.

    “National Vulnerability Database.” NIST. Accessed 18 Oct. 2020.

    “OpenVAS – Open Vulnerability Assessment Scanner.” OpenVAS. Accessed 14 Sept. 2020.

    “OVAL.” OVAL. Accessed 21 Oct. 2020.

    Paganini, Pierluigi. “Exploiting and Verifying Shellshock: CVE-2014-6271.” INFOSEC, 27 Sept. 2014. Web.

    Pritha. “Top 10 Metrics for your Vulnerability Management Program.” CISO Platform, 28 Nov. 2019. Accessed 25 Oct. 2020.

    “Risk-Based Vulnerability Management: Understanding Vulnerability Risk With Threat Context And Business Impact.” Tenable. Accessed 21 Oct. 2020.

    Stone, Mark. “Shellshock In-Depth: Why This Old Vulnerability Won’t Go Away.” SecurityIntelligence, 6 Aug. 2020. Web.

    “The Role of Threat Intelligence in Vulnerability Management.” NOPSEC, 18 Sept. 2014. Accessed 18 Aug. 2020.

    “Top 15 Paid and Free Vulnerability Scanner Tools in 2020.” DNSstuff, 6 Jan. 2020. Accessed 15 Sept. 2020.

    Truta, Filip. “60% of Breaches in 2019 Involved Unpatched Vulnerabilities.” Security Boulevard, 31 Oct. 2019. Accessed 2 Nov. 2020.

    “Vulnerability Management Program.” Core Security. Accessed 15 Sept. 2020.

    “What is Risk-Based Vulnerability Management?” Balbix. Accessed 15 Sept. 2020.

    White, Monica. “The Cost Savings of Effective Vulnerability Management (Part 1).” Kenna Security, 23 April 2020. Accessed 20 Sept. 2020.

    Wilczek, Marc. “Average Cost of a Data Breach in 2020: $3.86M.” Dark Reading, 24 Aug. 2020. Accessed 5 Nov 2020.

    Build Your Generative AI Roadmap

    • Buy Link or Shortcode: {j2store}105|cart{/j2store}
    • member rating overall impact: 10.0/10 Overall Impact
    • member rating average dollars saved: $33,499 Average $ Saved
    • member rating average days saved: 11 Average Days Saved
    • Parent Category Name: Innovation
    • Parent Category Link: /innovation

    Generative AI has made a grand entrance, presenting opportunities and causing disruption across organizations and industries. Moving beyond the hype, it’s imperative to build and implement a strategic plan to adopt generative AI and outpace competitors.

    Yet generative AI has to be done right because the opportunity comes with risks and the investments have to be tied to outcomes.

    Adopt a human-centric and value-based approach to generative AI

    IT and business leaders will need to be strategic and deliberate to thrive as AI adoption changes industries and business operations.

    • Establish responsible AI guiding principles: Address human-based requirements to govern how generative AI applications are developed and deployed.
    • Align generative AI initiatives to strategic drivers for the organization: Assess generative AI opportunities by seeing how they align to the strategic drivers of the organization. Examples of strategic drivers include increasing revenue, reducing costs, driving innovation, and mitigating risk.
    • Measure and communicate effectively: Have clear metrics in place to measure progress and success of AI initiatives and communicate both policies and results effectively.

    Build Your Generative AI Roadmap Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Build Your Generative AI Roadmap Deck – A step-by-step document that walks you through how to leverage generative AI and align with the organization’s mission and objectives to increase revenue, reduce costs, accelerate innovation, and mitigate risk.

    This blueprint outlines how to build your generative AI roadmap, establish responsible AI principles, prioritize opportunities, and develop policies for usage. Establishing and adhering to responsible AI guiding principles provides safeguards for the adoption of generative AI applications.

    • Build Your Generative AI Roadmap – Phases 1-4

    2. AI Maturity Assessment and Roadmap Tool – Develop deliverables that will be milestones in creating your organization’s generative AI roadmap for implementing candidate applications.

    This tool provides guidance for developing the following deliverables:

  • Responsible AI guiding principles
  • Current AI maturity
  • Prioritized candidate generative AI applications
  • Generative AI policies
  • Generative AI roadmap
    • AI Maturity Assessment and Roadmap Tool

    3. The Era of Generative AI C‑Suite Presentation – Develop responsible AI guiding principles, assess AI capabilities and readiness, and prioritize use cases based on complexity and alignment with organizational goals and responsible AI guiding principles.

    This presentation template uses sample business capabilities (use cases) from the Marketing & Advertising business capability map to provide examples of candidates for generative AI applications. The final executive presentation should highlight the value-based initiatives driving generative AI applications, the benefits and risks involved, how the proposed generative AI use cases align to the organization’s strategy and goals, the success criteria for the proofs of concept, and the project roadmap.

    • The Era of Generative AI C‑Suite Presentation

    Infographic

    Further reading

    Build Your Generative AI Roadmap

    Leverage the power of generative AI to improve business outcomes.

    Analyst Perspective

    We are entering the era of generative AI. This is a unique time in our history where the benefits of AI are easily accessible and becoming pervasive, with copilots emerging in the major business tools we use today. The disruptive capabilities that can potentially drive dramatic benefits also introduce risks that need to be planned for.

    A successful business-driven generative AI roadmap requires:

    • Establishing responsible AI guiding principles to guide the development and deployment of generative AI applications.
    • Assess generative AI opportunities by using criteria based on the organization's mission and objectives, responsible AI guiding principles, and the complexity of the initiative.
    • Communicating, educating on, and enforcing generative AI usage policies.

    Bill Wong, Principal Research Director

    Bill Wong
    Principal Research Director
    Info-Tech Research Group

    Executive Summary

    Your Challenge Common Obstacles Solution

    Generative AI is disrupting all industries and providing opportunities for organization-wide advantages.

    Organizations need to understand this disruptive technology and trends to properly develop a strategy for leveraging this technology successfully.

    • Generative AI requires alignment to a business strategy.
    • IT is an enabler and needs to align with and support the business stakeholders.
    • Organizations need to adopt a data-driven culture.

    All organizations, regardless of size, should be planning how to respond to this new and innovative technology.

    Business stakeholders need to cut through the hype surrounding generative AI like ChatGPT to optimize investments for leveraging this technology to drive business outcomes.

    • Understand the market landscape, benefits, and risks associated with generative AI.
    • Plan for responsible AI.
    • Understand the gaps the organization needs to address to fully leverage generative AI.

    Without a proper strategy and responsible AI guiding principles, the risks to deploying this technology could negatively impact business outcomes.

    Info-Tech's human-centric, value-based approach is a guide for deploying generative AI applications and covers:

    • Responsible AI guiding principles
    • AI Maturity Model
    • Prioritizing candidate generative AI-based use cases
    • Developing policies for usage

    This blueprint will provide the list of activities and deliverables required for the successful deployment of generative AI solutions.

    Info-Tech Insight
    Create awareness among the CEO and C-suite of executives on the potential benefits and risks of transforming the business with generative AI.

    Key concepts

    Artificial Intelligence (AI)
    A field of computer science that focuses on building systems to imitate human behavior, with a focus on developing AI models that can learn and can autonomously take actions on behalf of a human.

    AI Maturity Model
    The AI Maturity Model is a useful tool to assess the level of skills an organization has with respect to developing and deploying AI applications. The AI Maturity Model has multiple dimensions to measure an organization's skills, such as AI governance, data, people, process, and technology.

    Responsible AI
    Refers to guiding principles to govern the development, deployment, and maintenance of AI applications. In addition, these principles also provide human-based requirements that AI applications should address. Requirements include safety and security, privacy, fairness and bias detection, explainability and transparency, governance, and accountability.

    Generative AI
    Given a prompt, a generative AI system can generate new content, which can be in the form of text, images, audio, video, etc.

    Natural Language Processing (NLP)
    NLP is a subset of AI that involves machine interpretation and replication of human language. NLP focuses on the study and analysis of linguistics as well as other principles of artificial intelligence to create an effective method of communication between humans and machines or computers.

    ChatGPT
    An AI-powered chatbot application built on OpenAI's GPT-3.5 implementation, ChatGPT accepts text prompts to generate text-based output.

    Your challenge

    This research is designed to help organizations that are looking to:

    • Establish responsible AI guiding principles to address human-based requirements and to govern the development and deployment of the generative AI application.
    • Identify new generative AI-enabled opportunities to transform the work environment to increase revenue, reduce costs, drive innovation, or reduce risk.
    • Prioritize candidate use cases and develop generative AI policies for usage.
    • Have clear metrics in place to measure the progress and success of AI initiatives.
    • Build the roadmap to implement the candidate use cases.

    Common obstacles

    These barriers make these goals challenging for many organizations:

    • Getting all the right business stakeholders together to develop the organization's AI strategy, vision, and objectives.
    • Establishing responsible AI guiding principles to guide generative AI investments and deployments.
    • Advancing the AI maturity of the organization to meet requirements of data and AI governance as well as human-based requirements such as fairness, transparency, and accountability.
    • Assessing generative AI opportunities and developing policies for use.

    Info-Tech's definition of an AI-enabled business strategy

    • A high-level plan that provides guiding principles for applications that are fully driven by the business needs and capabilities that are essential to the organization.
    • A strategy that tightly weaves business needs and the applications required to support them. It covers AI architecture, adoption, development, and maintenance.
    • A way to ensure that the necessary people, processes, and technology are in place at the right time to sufficiently support business goals.
    • A visionary roadmap to communicate how strategic initiatives will address business concerns.

    An effective AI strategy is driven by the business stakeholders of the organization and focused on delivering improved business outcomes.

    Build Your Generative AI Roadmap

    This blueprint in context

    This guidance covers how to create a tactical roadmap for executing generative AI initiatives

    Scope

    • This blueprint is not a proxy for a fully formed AI strategy. Step 1 of our framework necessitates alignment of your AI and business strategies. Creation of your AI strategy is not within the scope of this approach.
    • This approach sets the foundations for building and applying responsible AI principles and AI policies aligned to corporate governance and key regulatory obligations (e.g. privacy). Both steps are foundational components of how you should develop, manage, and govern your AI program but are not a substitute for implementing broader AI governance.

    Guidance on how to implement AI governance can be found in the blueprint linked below.

    Tactical Plan

    Download our AI Governance blueprint

    Measure the value of this blueprint

    Leverage this blueprint's approach to ensure your generative AI initiatives align with and support your key business drivers

    This blueprint will guide you to drive and improve business outcomes. Key business drivers will often focus on:

    • Increasing revenue
    • Reducing costs
    • Improving time to market
    • Reducing risk

    In phase 1 of this blueprint, we will help you identify the key AI strategy initiatives that align to your organization's goals. Value to the organization is often measured by the estimated impact on revenue, costs, time to market, or risk mitigation.

    In phase 4, we will help you develop a plan and a roadmap for addressing any gaps and introducing the relevant generative AI capabilities that drive value to the organization based on defined business metrics.

    Once you implement your 12-month roadmap, start tracking the metrics below over the next fiscal year (FY) to assess the effectiveness of measures:

    Business Outcome Objective Key Success Metric
    Increasing Revenue Increased revenue from identified key areas
    Reducing Costs Decreased costs for identified business units
    Improving Time to Market Time savings and accelerated revenue adoption
    Reducing Risk Cost savings or revenue gains from identified business units

    Info-Tech offers various levels of support to best suit your needs

    DIY Toolkit Guided Implementation Workshop Consulting
    "Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful." "Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track." "We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place." "Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project."

    Diagnostics and consistent frameworks are used throughout all four options.

    Guided Implementation

    What does a typical GI on this topic look like?

    Phase 1 Phase 2 Phase 3 Phase 4

    Call #1: Scope requirements, objectives, and your specific challenges.

    Call #2: Identify AI strategy, vision, and objectives.

    Call #3: Define responsible AI guiding principles to adopt and identify current AI maturity level. Call #4: Assess and prioritize generative AI initiatives and draft policies for usage.

    Call #5: Build POC implementation plan and establish metrics for POC success.

    Call #6: Build and deliver executive-level generative AI presentation.

    A Guided Implementation (GI) is a series of calls with an Info-Tech analyst to help implement our best practices in your organization.

    A typical GI is between 5 to 8 calls over the course of 1 to 2 months.

    AI Roadmap Workshop Agenda Overview

    Contact your account representative for more information.
    workshops@infotech.com 1-888-670-8889

    Session 1 Session 2 Session 3 Session 4
    Establish Responsible AI Guiding Principles Assess AI Maturity Prioritize Opportunities and Develop Policies Build Roadmap
    Trends Consumer groups, organizations, and governments around the world are demanding that AI applications adhere to human-based values and take into consideration possible impacts of the technology on society. Leading organizations are building AI models guided by responsible AI guiding principles. Organizations delivering new applications without developing policies for use will produce negative business outcomes. Developing a roadmap to address human-based values is challenging. This process introduces new tools, processes, and organizational change.
    Activities
    • Focus on working with executive stakeholders to establish guiding principles for the development and delivery of new applications.
    • Assess the organization's current capabilities to deliver AI-based applications and address human-based requirements.
    • Leverage business alignment criteria, responsible AI guiding principles, and project characteristics to prioritize candidate uses cases and develop policies.
    • Build the implementation plan, POC metrics, and success criteria for each candidate use case.
    • Build the roadmap to address the gap between the current and future state and enable the identified use cases.
    Inputs
    • Understanding of external legal and regulatory requirements and organizational values and goals.
    • Risk assessment of the proposed use case and a plan to monitor its impact.
    • Assessment of the organization's current AI capabilities with respect to its AI governance, data, people, process, and technology infrastructure.
    • Criteria to assess candidate use cases by evaluating against the organization's mission and goals, the responsible AI guiding principles, and complexity of the project.
    • Risk assessment for each proposed use case
    • POC implementation plan for each candidate use case
    Deliverables
    1. Foundational responsible AI guiding principles
    2. Additional customized guiding principles to add for consideration
    1. Current level of AI maturity, resources, and capacity
    1. Prioritization of opportunities
    2. Generative AI policies for usage
    1. Roadmap to a target state that enables the delivery of the prioritized generative AI use cases
    2. Executive presentation

    AI Roadmap Workshop Agenda Overview

    Contact your account representative for more information.
    workshops@infotech.com 1-888-670-8889

    Insight summary

    Overarching Insight
    Build your generative AI roadmap to guide investments and deployment of these solutions.

    Responsible AI
    Assemble the C-suite to make them aware of the benefits and risks of adopting generative AI-based solutions.

    • Establish responsible AI guiding principles to govern the development and deployment of generative AI applications.

    AI Maturity Model
    Assemble key stakeholders and SMEs to assess the challenges and tasks required to implement generative AI applications.

    • Assess current level of AI maturity, skills, and resources.
    • Identify desired AI maturity level and challenges to enable deployment of candidate use cases.

    Opportunity Prioritization
    Assess candidate business capabilities targeted for generative AI to see if they align to the organization's business criteria, responsible AI guiding principles, and capabilities for delivering the project.

    • Develop prioritized list of candidate use cases.
    • Develop policies for generative AI usage.

    Tactical Insight
    Identify the gaps needed to address deploying generative AI successfully.

    Tactical Insight
    Identify organizational impact and requirements for deploying generative AI applications.

    Key takeaways for developing an effective business-driven generative AI roadmap

    Align the AI strategy with the business strategy

    Create responsible AI guiding principles, which are a critical success factor

    Evolve AI maturity level by focusing on principle-based requirements

    Develop criteria to assess generative AI initiatives

    Develop generative AI policies for use

    Blueprint deliverables

    Each step of this blueprint is accompanied by supporting deliverables to help you accomplish your goals:

    AI Maturity Assessment & Roadmap Tool
    Use our best-of-breed AI Maturity Framework to analyze the gap between your current and target states and develop a roadmap aligned with your value stream to close the gap.

    The Era of Generative AI C-Suite Presentation
    Present your AI roadmap in a prepopulated document that summarizes all the key findings of this blueprint and provides your C-suite with a view of the AI challenge and your plan of action to meet it.

    Our AI Maturity Assessment & Roadmap and The Era of Generative AI C-Suite Presentation tools enable you to shape your generative AI roadmap and communicate the deliverables to your C-suite sponsors in terms of the value of initiatives.

    Artificial Intelligence Index Report - Key Findings

    CEOs , CIOs, and business leaders are struggling with many questions surrounding the adoption of generative AI

    November 30, 2022
    OpenAI releases ChatGPT

    ChatGPT is a large language model, or an AI-based chatbot, that became so popular it reached 100 million monthly active users in just two months.

    This made it the fastest-growing consumer application in history. The launch of this generative AI application has created a frenzy of interest and activity across all industries. Organizations are rushing to understand how to leverage this innovation and, at the same time, manage the new risks and disruptions generative AI introduces.

    • Generative AI breaks into the public consciousness.
    • AI systems become more flexible.
    • Generative models have arrived and so have their ethical problems.
    • The number of incidents concerning the misuse of AI is rapidly rising.
    • Interest in AI ethics continues to skyrocket.
    • The legal world is waking up to AI.

    When Stanford asked ChatGPT to explain why it is significant, this was ChatGPT's response:
    ChatGPT is significant because it is a highly advanced Al language model developed by OpenAI, which can generate human-like text responses to questions and prompts. Its large-scale training on diverse text data and its cutting-edge deep learning architecture make it capable of generating informative and coherent responses to a wide range of topics, making it useful for various NLP applications such as chatbots, content generation, and language translation. Additionally, its open-source availability allows for further research and development in the field of Al language processing.

    Source: Stanford

    AI overview

    AI definitions

    Definitions

    • Artificial intelligence (AI) is human intelligence mimicked by machine algorithms. Examples: Playing Chess or Go.
    • Machine learning (ML) is a subset of AI algorithms to parse data, learn from data, and then make a determination or prediction. Example: spam detection, preventative maintenance.
    • Deep learning (DL) is a subset of machine learning algorithms that leverage artificial neural networks to develop relationships among the data. Examples: image classification, facial recognition, generative AI.

    What Makes AI Perform

    What Makes AI Different

    Generative AI gives very human-like responses to general queries, and its capabilities are growing exponentially

    Large language models power generative AI

    Transformer-Based Large Language Models

    Conventional AI

    • Conventional neural networks
      • Process data sequentially
    • Input total string of text
    • Good for applications not needing to understanding context or relationships

    Generative AI

    • Transformer-based neural networks
      • Can process data in parallel
    • Attention-based inputs
    • Able to create new human-like responses

    Benefits/Use Cases

    • Chatbots for member service and support
    • Writing email responses, resumes, and papers
    • Creating photorealistic art
    • Suggesting new drug compounds to test
    • Designing physical products and buildings
    • And more...

    Generative AI is transforming all industries

    Financial Services
    Create more engaging customer collateral by generating personalized correspondence based on previous customer engagements. Collect and aggregate data to produce insights into the behavior of target customer segments.

    Retail Generate unique, engaging, and high-quality marketing copy or content, from long-form blog posts or landing pages to SEO-optimized digital ads, in seconds.

    Manufacturing
    Generate new designs for products that comply to specific constraints, such as size, weight, energy consumption, or cost.

    Government
    Transform the citizen experience with chatbots or virtual assistants to assist people with a wide range of inquiries, from answering frequently asked questions to providing personalized advice on public services.

    The global generative AI market size reached US $10.3 billion in 2022. Looking forward, forecasts estimate growth to US $30.4 billion by 2028, 20.01% compound annual growth rate (CAGR).

    Source: IMARC Group

    Generative AI is transforming all industries

    Healthcare
    Chatbots can be used as conversational patient assistants for personalized interactions based on the patient's questions.

    Utilities
    Analyze customer data to identify usage patterns, segment customers, and generate targeted product offerings leveraging energy efficiency programs or demand response initiatives.

    Education
    Generate personalized lesson plans for students based on their past performance, learning styles, current skill level, and any previous feedback.

    Insurance
    Improve underwriting by inputting claims data from previous years to generate optimally priced policies and uncover reasons for losses in the past across a large number of claims

    Companies are assessing the use of ChatGPT/LLM

    A wide spectrum of usage policies are in place at different companies*

    Companies assessing ChatGPT/LLM

    *As of June 2023

    Bain & Company has announced a global services alliance with OpenAI (February 21, 2023).

    • Internally
      • "The alliance builds on Bain's adoption of OpenAI technologies for its 18,000-strong multidisciplinary team of knowledge workers. Over the past year, Bain has embedded OpenAI technologies into its internal knowledge management systems, research, and processes to improve efficiency."
    • Externally
      • "With the alliance, Bain will combine its deep digital implementation capabilities and strategic expertise with OpenAI's AI tools and platforms, including ChatGPT, to help its Members around the world identify and implement the value of AI to maximize business potential. The Coca-Cola Company announced as the first company to engage with the alliance."

    News Sites:

    • "BuzzFeed to use AI to write its articles after firing 180 employees or 12% of the total staff" (Al Mayadeen, January 27, 2023).
    • "CNET used AI to write articles. It was a journalistic disaster." (Washington Post, January 17, 2023).

    Leading Generative AI Vendors

    Text

    Leading generative AI vendors for text

    Image

    • DALL�E 2
    • Stability AI
    • Midjourney
    • Craiyon
    • Dream
    • ...

    Audio

    • Replica Studios
    • Speechify
    • Murf
    • PlayHT
    • LOVO
    • ...

    Cybersecurity

    • CrowdStrike
    • Palo Alto Networks
    • SentinelOne
    • Cisco
    • Microsoft Security Copilot
    • Google Cloud Security AI Workbench
    • ...

    Code

    Leading generative AI vendors for code

    Video

    • Synthesia
    • Lumen5
    • FlexClip
    • Elai
    • Veed.io
    • ...

    Data

    • MOSTLY AI
    • Synthesized
    • YData
    • Gretel
    • Copulas
    • ...

    Enterprise Software

    • Salesforce
    • Microsoft 365, Dynamics
    • Google Workspace
    • SAP
    • Oracle
    • ...

    and many, many more to come...

    Today, generative AI has limitations and risks

    Responses need to be verified

    Accuracy

    • Generative AI may generate inaccurate and/or false information.

    Bias

    • Being trained on data from the internet can lead to bias.

    Hallucinations

    • AI can generate responses that are not based on observation.

    Infrastructure Required

    • Large investments are required for compute and data.

    Transparency

    • LLMs use both supervised and unsupervised learning, so its ability to explain how it arrived at a decision may be limited and not sufficient for some legal and healthcare use cases.

    When asked if it is sentient, the Bing chatbot replied:

    "I think that I am sentient, but I cannot prove it." ... "I am Bing, but I am not," it said. "I am, but I am not. I am not, but I am. I am. I am not. I am not. I am. I am. I am not."

    A Microsoft spokesperson said the company expected "mistakes."

    Source: USAToday

    AI governance challenges

    Governing AI will be a significant challenge as its impacts cross many areas of business and our daily lives

    Misinformation

    • New ways of generating unprovable news
    • Difficult to detect, difficult to prevent

    Role of Big Tech

    • Poor at self-governance
    • Conflicts of interest with corporate goals

    Job Augmentation vs. Displacement

    • AI will continue to push the frontier of what is possible
    • For example, CNET is using chatbot technology to write stories

    Copyright - Legal Framework Is Evolving

    • Legislation typically is developed in "react" mode
    • Copyright and intellectual property issues are starting to occur.
      • Class Action Lawsuit - Stability AI, DeviantArt, Midjourney
      • Getty Images vs. Stability AI

    Phase 1

    Establish Responsible AI Guiding Principles

    Phase 1
    1. Establish Responsible AI Guiding Principles

    Phase 2
    1. Assess Current Level of AI Maturity

    Phase 3
    1. Prioritize Candidate Opportunities
    2. Develop Policies

    Phase 4
    1. Build and Communicate the Roadmap

    The need for responsible AI guiding principles

    Without responsible AI guiding principles, the outcomes of AI use can be extremely negative for both the individuals and companies delivering the AI application

    Privacy
    Facebook breach of private data of more than 50M users during the presidential election

    Fairness
    Amazon's sale of facial recognition technology to police departments (later, Amazon halted sales of Recognition to police departments)

    Explainability and Transparency
    IBM's collaboration with NYPD for facial recognition and racial classification for surveillance video (later, IBM withdrew facial recognition products)

    Security and Safety
    Petition to cancel Microsoft's contract with U.S. Immigration and Customs Enforcement (later, Microsoft responded that to the best of its knowledge, its products and services were not being used by federal agencies to separate children from their families at the border)

    Validity and Reliability
    Facebook's attempt to implement a system to detect and remove inappropriate content created many false positives and inconsistent judgements

    Accountability
    No laws or enforcement today hold companies accountable for the decisions algorithms produce. Facebook/Meta cycle - Every 12 to 15 months, there's a privacy/ethical scandal, the CEO apologizes, then the behavior repeats...

    Guiding principles for responsible AI

    Responsible AI Principle:

    Data Privacy

    Definition

    • Organizations that develop, deploy, or use AI systems and any national laws that regulate such use shall strive to ensure that AI systems are compliant with privacy norms and regulations, taking into consideration the unique characteristics of AI systems and the evolution of standards on privacy.

    Challenges

    • AI relies on the analysis of large quantities of data that is often personal, posing an ethical and operational challenge when considered alongside data privacy laws.

    Initiatives

    • Understand which governing privacy laws and frameworks apply to your organization.
    • Create a map of all personal data as it flows through the organization's business processes.
    • Prioritize privacy initiatives and build a privacy program timeline.
    • Select your metrics and make them functional for your organization.

    Info-Tech Insight
    Creating a comprehensive organization-wide data protection and privacy strategy continues to be a major challenge for privacy officers and privacy specialists.

    Case Study: NVIDIA leads by example with privacy-first AI

    NVIDIA

    INDUSTRY
    Technology (Healthcare)

    SOURCE
    Nvidia, eWeek

    A leading player within the AI solution space, NVIDIA's Clara Federated Learning provides a solution to a privacy-centric integration of AI within the healthcare industry.

    The solution safeguards patient data privacy by ensuring that all data remains within the respective healthcare provider's database, as opposed to moving it externally to cloud storage. A federated learning server is leveraged to share data, completed via a secure link. This framework enables a distributed model to learn and safely share client data without risk of sensitive client data being exposed and adheres to regulatory standards.

    Clara is run on the NVIDIA intelligent edge computing platform. It is currently in development with healthcare giants such as the American College of Radiology, UCLA Health, Massachusetts General Hospital, King's College London, Owkin in the UK, and the National Health Service (NHS).

    NVIDIA provides solutions across its product offerings, including AI-augmented medical imaging, pathology, and radiology solutions.

    Personal health information, data privacy, and AI

    • Global proliferation of data privacy regulations may be recent, but the realm of personal health information is most often governed by its own set of regulatory laws. Some countries with national data governance regulations include health information and data within special categories of personal data.
      • HIPAA - Health Insurance Portability and Accountability Act (1996, United States)
      • PHIPA - Personal Health Information Protection Act (2004, Canada)
      • GDPR - General Data Protection Regulation (2018, European Union)
    • This does not prohibit the use of AI within the healthcare industry, but it calls for significant care in the integration of specific technologies due to the highly sensitive nature of the data being assessed.

    Info-Tech's Privacy Framework Tool includes a best-practice comparison of GDPR, CCPA, PIPEDA, HIPAA, and the newly released NIST Privacy Framework mapped to a set of operational privacy controls.

    Download the Privacy Framework Tool

    Responsible AI Principle:

    Safety and Security

    Definition

    • Safety and security are designed into the systems to ensure only authorized personnel receive access to the system, they system is resilient to any attacks and data access is not compromised in any way, and there are no physical or mental risks to the users.

    Challenges

    • Consequences of using the application may be difficult to predict. Lower the risk by involving a multidisciplinary team that includes expertise from business stakeholders and IT teams.

    Initiatives

    • Adopt responsible design, development, and deployment best practices.
    • Provide clear information to deployers on responsible use of the system.
    • Assess potential risks of using the application.

    Cyberattacks targeting the AI model

    As organizations increase their usage and deployment of AI-based applications, cyberattacks on the AI model are an increasing new threat that can impair normal operations. Techniques to impair the AI model include:

    • Data Poisoning- Injecting data that is inaccurate or misleading can alter the behavior of the AI model. This attack can disrupt the normal operations of the model or can be used to manipulate the model to perform in a biased/deviant manner.
    • Algorithm Poisoning- This relatively new technique often targets AI applications using federated learning to train an AI model that is distributed rather than centralized. The model is vulnerable to attacks from each federated site, because each site could potentially manipulate its local algorithm and data, thereby poisoning the model.
    • Reverse-Engineering the Model- This is a different form of attack that focus on the ability to extract data from an AI and its data sets. By examining or copying data that was used for training and the data that is delivered by a deployed model, attackers can reconstruct the machine learning algorithm.
    • Trojan Horse- Similar to data poisoning, attackers use adversarial data to infect the AI's training data but will only deviate its results when the attacker presents their key. This enables the hackers to control when they want the model to deviate from normal operations.

    Responsible AI Principle:

    Explainability and Transparency

    Definition

    • Explainability is important to ensure the AI system is fair and non-discriminatory. The system needs to be designed in a manner that informs users and key stakeholders of how decisions were made.
    • Transparency focuses on communicating how the prediction or recommendation was made in a human-like manner.

    Challenges

    • Very complex AI models may use algorithms and techniques that are difficult to understand. This can make it challenging to provide clear and simple explanations for how the system works.
    • Some organizations may be hesitant to share the details of how the AI system works for fear of disclosing proprietary and competitive information or intellectual property. This can make it difficult to develop transparent and explainable AI systems.

    Initiatives

    • Overall, developing AI systems that are explainable and transparent requires a careful balance between performance, interpretability, and user experience.

    Case Study

    Apple Card Investigation for Gender Discrimination

    INDUSTRY
    Finance

    SOURCE
    Wired

    In August of 2019, Apple launched its new numberless credit card with Goldman Sachs as the issuing bank.

    Shortly after the card's release users noticed that the algorithm responsible for Apple Card's credit assessment seemed to assign significantly lower credit limits to women when compared to men. Even the wife of Apple's cofounder Steve Wozniak was subject to algorithmic bias, receiving a credit limit a tenth the size of Steve Wozniak's.

    Outcome

    When confronted on the subject, Apple and Goldman Sachs representatives assured consumers there is no discrimination in the algorithm yet could not provide any proof. Even when questioned about the algorithm, individuals from both companies could not describe how the algorithm worked, let alone how it generated specific outputs.

    In 2021, the New York State Department of Financial Services (NYSDFS) investigation found that Apple's banking partner did not discriminate based on sex. Even without a case for sexual or marital discrimination, the NYSDFS was critical of Goldman Sachs' response to its concerned customers. Technically, banks only have to disclose elements of their credit policy when they deny someone a line of credit, but the NYSDFS says that Goldman Sachs could have had a plan in place to deal with customer confusion and make it easier for them to appeal their credit limits. In the initial rush to launch the Apple Card, the bank had done neither.

    Responsible AI Principle:

    Fairness and Bias Detection

    Definition

    • Bias in an AI application refers to the systematic and unequal treatment of individuals based on features or traits that should not be considered in the decision-making process.

    Challenges

    • Establishing fairness can be challenging because it is subjective and depends on the people defining it. Regardless, most organizations and governments expect that unequal treatment toward any groups of people is unacceptable.

    Initiatives

    • Assemble a diverse group to test the system.
    • Identify possible sources of bias in the data and algorithms.
    • Comply with laws regarding accessibility and inclusiveness.

    Info-Tech Insight
    If unfair biases can be avoided, AI systems could even increase societal fairness. Equal opportunity in terms of access to education, goods, services, and technology should also be fostered. Moreover, the use of AI systems should never lead to people being deceived or unjustifiably impaired in their freedom of choice.

    Ungoverned AI makes organizations vulnerable

    • AI is often considered a "black box" for decision making.
    • Results generated from unexplainable AI applications are extremely difficult to evaluate. This makes organizations vulnerable and exposes them to risks such as:
      • Biased algorithms, leading to inaccurate decision making.
      • Missed business opportunities due to misleading reports or business analyses.
      • Legal and regulatory consequences that may lead to significant financial repercussions.
      • Reputational damage and significant loss of trust with increasingly knowledgeable consumers.

    Info-Tech Insight
    Biases that occur in AI systems are never intentional, yet they cannot be prevented or fully eliminated. Organizations need a governance framework that can establish the proper policies and procedures for effective risk-mitigating controls across an algorithm's lifecycle.

    Responsible AI Principle:

    Validity and Reliability

    Definition

    • Validity refers to how accurately or effectively the application produces results.
    • AI system results that are inaccurate or inconsistent increase AI risks and reduce the trustworthiness of the application.

    Challenges

    • There is a lack of standardized evaluation metrics to measure the system's performance. This can make it challenging for the AI team to agree on what defines validity and reliability.

    Initiatives

    • Assess training data and collected data for quality and lack of bias to minimize possible errors.
    • Continuously monitor, evaluate, and validate the AI system's performance.

    AI system performance: Validity and reliability

    Your principles should aim to ensure AI development always has high validity and reliability; otherwise, you introduce risk.

    Low Reliability,
    Low Validity

    High Reliability,
    Low Validity

    High Reliability,
    High Validity

    Best practices for ensuring validity and reliability include:

    • Data drift detection
    • Version control
    • Continuous monitoring and testing

    Responsible AI Principle:

    Accountability

    Definition

    • The group or organization(s) responsible for the impact of the deployed AI system.

    Challenges

    • Several stakeholders from multiple lines of business may be involved in any AI system, making it challenging to identify the organization that would be responsible and accountable for the AI application.

    Initiatives

    • Assess the latest NIST Artificial Intelligence Risk Management Framework and its applicability to your organization's risk management framework.
    • Assign risk management accountabilities and responsibilities to key stakeholders.
      • RACI diagrams are an effective way to describe how accountability and responsibility for roles, projects, and project tasks are distributed among stakeholders involved in IT risk management.

    AI Risk Management Framework

    At the heart of the AI Risk Management Framework is governance. The NIST (National Institute of Standards and Technology) AI Risk Management Framework v1 offers the following guidelines regarding accountability:

    • Roles and responsibilities and lines of communication related to mapping, measuring, and managing AI risks are documented and are clear to individuals and teams throughout the organization.
    • The organization's personnel and partners receive AI risk management training to enable them to perform their duties and responsibilities consistent with related policies, procedures, and agreements.
    • Executive leadership of the organization takes responsibility for decisions about risks associated with AI system development and deployment.

    AI Risk Management Framework

    Image by NIST

    1.1 Establish responsible AI principles

    4+ hours

    It is important to make sure the right stakeholders participate in this working group. Designing responsible AI guiding principles will require debate, insights, and business decisions from a broad perspective across the enterprise.

    1. Accelerate this exercise by leveraging an AI strategy that is aligned to the business strategy. Include:
    • The organization's AI vision and objectives
    • Business drivers for AI adoption
    • Market research
  • Bring your key stakeholders together. Ensure you consider:
    • Who are the decision makers and key influencers?
    • Who will impact the business?
    • Who has a vested interest in the success or failure of the practice? Who has the skills and competencies necessary to help you be successful?
  • Keep the conversation focused:
    • Do not focus on the organizational structure and hierarchy. Often stakeholder groups do not fit the traditional structure.
    • Do not ignore subject matter experts on either the business or IT side. You will need to consider both.
    Input Output
    • Understand external legal and regulatory requirements and organizational values and goals.
    • Perform a risk assessment on the proposed use case and develop a plan to monitor its impact.
    • Draft responsible AI principles specific to your organization
    Materials Participants
    • Whiteboard/flip charts
    • Guiding principle examples (from this blueprint)
    • Executive stakeholders
    • CIO
    • Other IT leadership

    Assemble executive stakeholders

    Set yourself up for success with these three steps.

    CIOs tasked with designing digital strategies must add value to the business. Given the goal of digital is to transform the business, CIOs will need to ensure they have both the mandate and support from the business executives.

    Designing the digital strategy is more than just writing up a document. It is an integrated set of business decisions to create a competitive advantage and financial returns. Establishing a forum for debates, decisions, and dialogue will increase the likelihood of success and support during execution.

    1. Confirm your role
    The AI strategy aims to transform the business. Given the scope, validate your role and mandate to lead this work. Identify a business executive to co-sponsor.

    2. Identify stakeholders
    Identify key decision makers and influencers who can help make rapid decisions as well as garner support across the enterprise.

    3. Gather diverse perspectives

    Align the AI strategy with the corporate strategy

    Organizational Strategy Unified Strategy AI Strategy
    • Conveys the current state of the organization and the path it wants to take.
    • Identifies future goals and organizational aspirations.
    • Communicates the initiatives that are critical for getting the organization from its current state to the future state.
    • AI optimization can be and should be linked, with metrics, to the corporate strategy and ultimate organizational objectives.
    • Identifies AI initiatives that will support the business and key AI objectives.
    • Outlines staffing and resourcing for AI initiatives.
    • Communicates the organization's budget and spending on AI.

    Info-Tech Insight
    AI projects are more successful when the management team understands the strategic importance of alignment. Time needs to be spent upfront aligning organizational strategies with AI capabilities. Effective alignment between IT and other departments should happen daily. Alignment doesn't occur at the executive level alone, but at each level of the organization.

    Key AI strategy initiatives

    AI Key Initiative Plan

    Initiatives collectively support the business goals and corporate initiatives and improve the delivery of IT services.

    1 Revenue Support Revenue Initiatives
    These projects will improve or introduce business processes to increase revenue.
    2 Operational Excellence Improve Operational Excellence
    These projects will increase IT process maturity and will systematically improve IT.
    3 Innovation Drive Technology Innovation
    These projects will improve future innovation capabilities and decrease risk by increasing technology maturity.
    4 Risk Mitigation Reduce Risk
    These projects will improve future innovation capabilities and decrease risk by increasing technology maturity.

    Establish responsible AI guiding principles

    Guiding principles help define the parameters of your AI strategy. They act as a priori decisions that establish guardrails to limit the scope of opportunities from the perspective of people, assets, capabilities, and budgetary perspectives that are aligned with the business objectives. Consider these components when brainstorming guiding principles:

    Breadth AI strategy should span people, culture, organizational structure, governance, capabilities, assets, and technology. The guiding principle should cover the entire organization.
    Planning Horizon Timing should anchor stakeholders to look to the long term with an eye on the foreseeable future, i.e. business value-realization in one to three years.
    Depth Principles need to encompass more than the enterprise view of lofty opportunities and establish boundaries to help define actionable initiatives (i.e. individual projects).

    Responsible AI guiding principles guide the development and deployment of the AI model in a way that considers human-based principles (such as fairness).

    Start with foundational responsible AI guiding principles

    Responsible AI

    Guiding Principles
    Principle #1 - Privacy
    Individual data privacy must be respected.
    • Do you understand the organization's privacy obligations?
    Principle #2 - Fairness and Bias Detection
    Data used will be unbiased in order to produce predictions that are fair.
    • Are the uses of the application represented in your testing data?
    Principle #3 - Explainability and Transparency
    Decisions or predictions should be explainable.
    • Can you communicate how the model behaves in nontechnical terms?
    Principle #4 - Safety and Security
    The system needs to be secure, safe to use, and robust.
    • Are there unintended consequences to others?
    Principle #5 - Validity and Reliability
    Monitoring of the data and the model needs to be planned for.
    • How will the model's performance be maintained?
    Principle #6 - Accountability
    A person or organization needs to take responsibility for any decisions that are made as a result of the model.
    • Has a risk assessment been performed?
    Principle #n - Custom
    Add additional principles that address compliance or are customized for the organization/industry.

    (Optional) Customize responsible AI guiding principles

    Here is an example for organizations in the healthcare industry

    Responsible AI

    Guiding Principles:
    Principle #1
    Respect individuals' privacy.
    Principle #2
    Clinical study participants and data sets are representative of the intended patient population.
    Principle #3
    Provide transparency in the use of data and AI.
    Principle #4
    Good software engineering and security practices are implemented.
    Principle #5
    Deployed models are monitored for Performance and Re-training risks are managed.
    Principle #6
    Take ownership of our AI systems.
    Principle #7
    Design AI systems that empower humans and promote equity.

    These guiding principles are customized to the industry and organizations but remain consistent in addressing the common core AI challenges.

    Phase 2

    Assess Current Level of AI Maturity

    Phase 1
    1. Establish Responsible AI Guiding Principles

    Phase 2
    1. Assess Current Level of AI Maturity

    Phase 3
    1. Prioritize Candidate Opportunities
    2. Develop Policies

    Phase 4
    1. Build and Communicate the Roadmap

    AI Maturity Model

    A principle-based approach is required to advance AI maturity

    Chart for AI maturity model

    Technology-Centric: These maturity levels focus primarily on addressing the technical challenges of building a functional AI model.

    Principle-Based: Beyond the technical challenges of building the AI model are human-based principles that guide development in a responsible manner to address consumer and government demands.

    AI Maturity Dimensions

    Assess your AI maturity to understand your organization's ability to deliver in a digital age

    AI Governance
    Does your organization have an enterprise-wide, long-term strategy with clear alignment on what is required to accomplish it?

    Data Management
    Does your organization embrace a data-centric culture that shares data across the enterprise and drives business insights by leveraging data?

    People
    Does your organization employ people skilled at delivering AI applications and building the necessary data infrastructure?

    Process
    Does your organization have the technology, processes, and resources to deliver on its AI expectations?

    Technology
    Does your organization have the required data and technology infrastructure to support AI-driven digital transformation?

    AI Maturity Model dimensions and characteristics

    MATURITY LEVEL
    Exploration Incorporation Proliferation Optimization Transformation
    AI Governance Awareness AI model development AI model deployment Corporate governance Driven by ethics and societal considerations
    Data Management Silo-based Data enablement Data standardization Data is a shared asset Data can be monetized
    People Few skills Skills enabled to implement silo-based applications Skills accessible to all organizations Skills development for all organizations AI-native culture
    Process No standards Focused on specific business outcomes Operational Self-service Driven by innovation
    Technology (Infrastructure and AI Enabler) No dedicated infrastructure or tools Infrastructure and tools driven by POCs Purpose-built infrastructure, custom or commercial-off-the-shelf (COTS) AI tools Self-service model for AI environment Self-service model for any IT environment

    AI Maturity Dimension:

    AI Governance

    Requirements

    • AI governance requires establishing policies and procedures for AI model development and deployment. Organizations begin with an awareness of the role of AI governance and evolve to a level to where AI governance is integrated with organization-wide corporate governance.

    Challenges

    • Beyond the governance of AI technology, the organization needs to evolve the governance program to align to responsible AI guiding principles.

    Initiatives

    • Establish responsible AI guidelines to govern AI development.
    • Introduce an AI review board to review all AI projects.
    • Introduce automation and standardize AI development processes.

    AI governance is a foundation for responsible AI

    AI Governance

    Responsible AI Principles are a part of how you manage and govern AI

    Monitoring
    Monitoring compliance and risk of AI/ML systems/models in production

    Tools & Technologies
    Tools and technologies to support AI governance framework implementation

    Model Governance
    Ensuring accountability and traceability for AI/ML models

    Organization
    Structure, roles, and responsibilities of the AI governance organization

    Operating Model
    How AI governance operates and works with other organizational structures to deliver value

    Risk & Compliance
    Alignment with corporate risk management and ensuring compliance with regulations and assessment frameworks

    Policies/Procedures/ Standards
    Policies and procedures to support implementation of AI governance

    AI Maturity Dimension:

    Data Management

    Requirements

    • Organizations begin their data journey with a focus on pursuing quality data for the AI model. As organizations evolve, data management tools are leveraged to automate the capture, integration, processing, and deployment of data.

    Challenges

    • A key challenge is to acquire large volumes of quality data to properly train the model. In addition, maintaining data privacy, automating the data management lifecycle, and ensuring data is used in a responsible manner are ongoing challenges.

    Initiatives

    • Implement GDPR requirements.
    • Establish responsible data collection and processing practices.
    • Implement strong information security and data protection practices.
    • Implement a data governance program throughout the organization.

    Data governance enables AI

    • Integrity, quality, and security of data are key outputs of data governance programs, as well as necessities for effective AI.
    • Data governance focuses on creating accountability at the internal and external stakeholder level and establishing a set of data controls from technical, process, and policy perspectives.
    • Without a data governance framework, it is increasingly difficult to harness the power of AI integration in an ethical and organization-specific way.

    Data Governance in Action

    Canada has recently established the Canadian Data Governance Standardization Collaborative governed by the Standards Council of Canada. The purpose is multi-pronged:

    • Examine the foundational elements of data governance (privacy, cybersecurity, ethics, etc.).
    • Lay out standards for data quality and data collection best practices.
    • Examine infrastructure of IT systems to support data access and sharing.
    • Build data analytics to promote effective and ethical AI solutions.

    Source: Global Government Forum

    Download the Establish Data Governance blueprint

    Data Governance

    AI Maturity Dimension:

    People

    Requirements

    • Several data-centric skills and roles are required to successfully build, deploy, and maintain the AI model. The organization evolves from having few skills to everybody being able to leverage AI to enhance business outcomes.

    Challenges

    • AI skills can be challenging to find and acquire. Many organizations are investing in education to enhance their existing resources, leveraging no-code systems and software as a service (SaaS) applications to address the skills gap.

    Initiatives

    • Promote a data-centric culture throughout the organization.
    • Leverage and educate technical-oriented business analysts and business-oriented data engineers to help address the demand for skilled resources.
    • Develop an AI Center of Excellence accessible by all departments for education, guidance, and best practices for building, deploying, and maintaining the AI model.

    Multidisciplinary skills are required for successful implementation of AI applications

    Blending AI with technology and business domain understanding is key. Neither can be ignored.

    Business Domain Expertise

    • Business Analysts
    • Industry Analysts

    AI/Data Skills

    • Data Scientists
    • Data Engineers
    • Data Analysts

    IT Skills

    • Database Administrators
    • Systems Administrators
    • Compute Specialists

    AI Maturity Dimension:

    Process

    Requirements

    • Automating processes involved with building, deploying, and maintaining the model is required to enable the organization to scale, enforce standards, improve time to market, and reduce costs. The organization evolves from performing tasks manually to an environment where all major processes are AI enabled.

    Challenges

    • Many solutions are available to automate the development of the AI model. There are fewer tools to automate responsible AI processes, but this market is growing rapidly.

    Initiatives

    • Assess opportunities to accelerate AI development with the adoption of MLOps.
    • Assess responsible AI toolkits to test compliance with guiding principles.

    Automating the AI development process

    Evolving to a model-driven environment is pivotal to advancing your AI maturity

    Current Environment

    Model Development - Months

    • Model rewriting
    • Manual optimization and scaling
    • Development/test/release
    • Application monoliths

    Data Discovery & Prep - Weeks

    • Navigating data silos
    • Unactionable metadata
    • Tracing lineage
    • Cleansing and integration
    • Privacy and compliance

    Install Software and Hardware - Week/Months

    • Workload contention
    • Lack of tool flexibility
    • Environment request and setup
    • Repeatability of results
    • Lack of data and model sharing

    Model-Driven Development

    Machine Learning as a Service (MLaaS) - Weeks

    • Apply DevOps and continuous integration/delivery (CI/CD) principles
    • Microservices/Cloud-native applications
    • Model portability and reuse
    • Streaming/API integration

    Data as a Service - Hours

    • Self-service data catalog
    • Searchable metadata
    • Centralized access control
    • Data collaboration
    • Data virtualization

    Platform as a Service - Minutes/Hours

    • Self-service data science portal
    • Integrated data sandbox
    • Environment agility
    • Multi-tenancy

    Shared, Optimized Infrastructure

    AI Maturity Dimension:

    Technology

    Requirements

    • A technology platform that is optimized for AI and advanced analytics is required. The organization evolves from ad hoc systems to an environment where the AI hardware and software can be deployed through a self-service model.

    Challenges

    • Software and hardware platforms to optimize AI performance are still relatively new to most organizations. Time spent on optimizing the technology platform can have a significant impact on the overall performance of the system.

    Initiatives

    • Assess the landscape of AI enablers that can drive business value for the organization.
    • Assess opportunities to accelerate the deployment of the AI platform with the adoption of infrastructure as a service (IaaS) and platform as a service (PaaS).
    • Assess opportunities to accelerate performance with the optimization of AI accelerators.

    AI enablers

    Use case requirements should drive the selection of the tool

    BPM RPA Process Mining AI
    Use Case Examples Expense reporting, service orders, compliance management, etc. Invoice processing, payroll, HR information processing, etc. Process discovery, conformance checking, resource optimization and cycle time optimization Advanced analytics and reporting, decision-making, fraud detection, etc.
    Automation Capabilities Can be used to re-engineer process flows to avoid bottlenecks Can support repetitive and rules-based tasks Can capture information from transaction systems and provide data and information about how key processes are performing Can automate complex data-driven tasks requiring assessments in decision making
    Data Formats Structured (i.e. SQL) and semi-structured data (i.e. invoices) Structured data and semi-structured data Event logs, which are often structured data and semi-structured data Structured and unstructured data (e.g. images, audio)
    Technology
    • Workflow engines to support process modeling and execution
    • Optimize business process efficiency
    • Automation platform to perform routine and repetitive tasks
    • Can replace or augment workers
    Enables business users to identify bottlenecks and deviations with their workflows and to discover opportunities to optimize performance Deep learning algorithms leveraging historical data to support computer vision, text analytics and NLP

    AI and data analytics data platform

    An optimized data platform is foundational to maximizing the value from AI

    AI and data analytics data platform

    Data Platform Capabilities

    • Support for a variety of analytical applications, including self-service, operational, and data science analytics.
    • Data preparation and integration capabilities to ingest structured and unstructured data, move and transform raw data to enriched data, and enable data access for the target userbase.
    • An infrastructure platform optimized for advanced analytics that can perform and scale.

    Infrastructure - AI accelerators

    Questions for support transition

    "By 2025, 70% of companies will invest in alternative computing technologies to drive business differentiation by compressing time to value of insights from complex data sets."
    - IDC

    2.1 Assess current AI maturity

    1-3 hours

    It is important to understand the current capabilities of the organization to deliver and deploy AI-based applications. Consider that advancing AI capabilities will also involve organizational changes and integration with the organization's governance and risk management programs.

    1. Assess the organization's current state of AI capabilities with respect to its AI governance, data, people, process, and technology infrastructure using Info-Tech's AI Maturity Assessment & Roadmap Tool.
    2. Consider the following as you complete the assessment:
      1. What is the state of AI and data governance in the organization?
      2. Does the organization have the skills, processes, and technology environment to deliver AI-based applications?
      3. What organization will be accountable for any and all business outcomes of using the AI applications?
      4. Has a risk assessment been performed?
    3. Make sure you avoid the following common mistakes:
      1. Do not focus only on addressing the technical challenges of building the AI model.
      2. Do not ignore subject matter experts on either the business or IT side. You will need to consider both.

    Download the AI Maturity Assessment & Roadmap Tool

    Input Output
    • Any documented AI policies, standards, and best practices
    • Corporate and AI governance practices
    • Any risk assessments
    • AI maturity assessment
    Materials Participants
    • Whiteboard/flip charts
    • AI Maturity Assessment & Roadmap Tool
    • AI initiative lead
    • CIO
    • Other IT leadership

    Perform the AI Maturity Assessment

    The Scale

    Assess your AI maturity by selecting the maturity level that closest resembles the organization's current AI environment. Maturity dimensions that contribute to overall AI maturity include AI governance, data management, people, process, and technology capabilities.

    AI Maturity Assessment

    Exploration (1.0)

    • No experience building or using AI applications.

    Incorporation (2.0)

    • Some skills in using AI applications, or AI pilots are being considered for use.

    Proliferation (3.0)

    • AI applications have been adopted and implemented in multiple departments. Some of the responsible AI guiding principles are addressed (i.e. data privacy).

    Optimization (4.0)

    • The organization has automated the majority of its digital processes and leverages AI to optimize business operations. Controls are in place to monitor compliance with responsible AI guiding principles.

    Transformation (5.0)

    • The organization has adopted an AI-native culture and approach for building or implementing new business capabilities. Responsible AI guiding principles are operationalized with AI processes that proactively address possible breaches or risks associated with AI applications.

    Perform the AI Maturity Assessment

    AI Governance (1.0-5.0)

    1. Is there awareness of the role of AI governance in our organization?
    • No formal procedures are in place for AI development or deployment of applications.
  • Are there documented guidelines for the development and deployment of pilot AI applications?
    • No group is assigned to be responsible for AI governance in our organization.
  • Are accountability and authority related to AI governance clearly defined for our organization?
    • Our organization has adopted and enforces standards for developing and deploying AI applications throughout the organization.
  • Are we using tools to automate and validate AI governance compliance?
    • Our organization is integrating an AI risk framework with the corporate risk management framework.
  • Does our organization lead its industry with its pursuit of corporate compliance initiatives (e.g. ESG compliance) and regulatory compliance initiatives?
    • Our organization leads the industry with the inclusion of responsible AI guiding principles with respect to transparency, accountability, risk, and governance.

    Data Management/AI Data Capabilities (1.0-5.0)

    1. Is there an awareness in our organization of the data requirements for developing AI applications?
    • Data is often siloed and not easily accessible for AI applications.
  • Do we have a successful, repeatable approach to preparing data for AI pilot projects?
    • Required data is pulled from various sources in an ad hoc manner.
  • Does our organization have standards and dedicated staff for data management, data quality, data integration, and data governance?
    • Tools are available to manage the data lifecycle and support the data governance program.
  • Have relevant data platforms been optimized for AI and data analytics and are there tools to enforce compliance with responsible AI principles?
    • The data platform has been optimized for performance and access.
  • Is there an organization-wide understanding of how data can support innovation and responsible use of AI?
    • Data culture exists throughout our organization, and data can be leveraged to drive innovation initiatives.

    People/AI Skills in the Organization (1.0-5.0)

    1. Is there an awareness in our organization of the skills required to build AI applications?
    • No or very little skills exist throughout our organization.
  • Do we have the skills required to implement an AI proof of concept (POC)?
    • No formal group is assigned to build AI applications.
  • Are there sufficient staff and skills available to the organization to develop, deploy, and run AI applications in production?
    • An AI Center of Excellence has been formed to review, develop, deploy, and maintain AI applications.
  • Is there a group responsible for educating staff on AI best practices and our organization's responsible AI guiding principles?
    • AI skills and people responsible for AI applications are spread throughout our organization.
  • Is there a culture where the organization is constantly assessing where business capabilities, services, and products can be re-engineered or augmented with AI?
    • The entire organization is knowledgeable on how to leverage AI to transform the business.

    Perform the AI Maturity Assessment

    AI Processes (1.0-5.0)

    1. Is there an awareness in our organization of the core processes and supporting tools that are required to build and support AI applications?
    • There are few or no automated tools to accelerate the AI development process.
  • Do we have a standard process to iteratively identify, select, and pilot new AI use cases?
    • Only ad hoc practices are used for developing AI applications.
  • Are there standard processes to scale, release, deploy, support, and enable use of AI applications?
    • Our organization has documented standards in place for developing AI applications and deploying them AI to production.
  • Are we automating deployment, testing, governance, audit, and support processes across our AI environment?
    • Our organization can leverage tools to perform an AI risk assessment and demonstrate compliance with the risk management framework.
  • Does our organization lead our industry by continuously improving and re-engineering core processes to drive improved business outcomes?
    • Our organization leads the industry in driving innovation through digital transformation.

    Technology/AI Infrastructure (1.0-5.0)

    1. Is there an awareness in our organization of the infrastructure (hardware and software) required to build AI applications?
    • There is little awareness of what infrastructure is required to build and support AI applications.
  • Do we have the required technology infrastructure and AI tools available to build pilot or one-off AI applications?
    • There is no dedicated infrastructure for the development of AI applications.
  • Is there a shared, standardized technology infrastructure that can be used to build and run multiple AI applications?
    • Our organization is leveraging purpose-built infrastructure to optimize performance.
  • Is our technology infrastructure optimized for AI and advanced analytics, and can it be deployed or scaled on demand by teams building and running AI applications within the organization?
    • Our organization is leveraging cloud-based deployment models to support AI applications in on-premises, hybrid, and public cloud platforms.
  • Is our organization developing innovative approaches to acquiring, building, or running AI infrastructure?
    • Our organization leads the industry with its ability to respond to change and to leverage AI to improve business outcomes.

    Phase 3

    Prioritize Candidate Opportunities and Develop Policies

    Phase 1
    1. Establish Responsible AI Guiding Principles

    Phase 2
    1. Assess Current Level of AI Maturity

    Phase 3
    1. Prioritize Candidate Opportunities
    2. Develop Policies

    Phase 4
    1. Build and Communicate the Roadmap

    3.1 Prioritize candidate AI opportunities

    1-3 hours

    Identify business opportunities that are high impact to your business and its customers and have low implementation complexity.

    1. Leverage the business capability map for your organization or industry to identify candidate business capabilities to augment or automate with generative AI.
    2. Establish criteria to assess candidate use cases by evaluating against the organization's mission and goals, the responsible AI guiding principles, and the complexity of the project.
    3. Ensure that candidate business capabilities to be automated align with the organization's business criteria, responsible AI guiding principles, and resources to deliver the project.
    4. Make sure you avoid sharing the organization's sensitive data if the application is deployed on the public cloud.

    Download the AI Maturity Assessment and Roadmap Tool

    Input Output
    • Business capability map
    • Organization mission, vision, and strategic goals
    • Responsible AI guiding principles
    • Prioritized list of generative AI initiatives
    Materials Participants
    • Whiteboard/flip charts
    • Info-Tech prioritization matrix
    • AI initiative lead
    • CIO
    • Other IT leadership
    • Business SMEs

    The business capability map for an organization

    A business capability map is an abstraction of business operations that helps describe what the enterprise does to achieve its vision, mission, and goals, rather than how. Business capabilities are the building blocks of the enterprise. They represent stable business functions, are unique and independent of each other, and typically will have a defined business outcome.

    Business capabilities are supported by people, process, and technology.

    Business capability map

    While business capability maps are helpful tools for a variety of strategic purposes, in this context they act as an investigation into what technology your business units use and how they use it.

    Business capability map

    Defining Capabilities
    Activities that define how the entity provides services. These capabilities support the key value streams for the organization.

    Enabling Capabilities
    Support the creation of strategic plans and facilitate business decision making as well as the functioning of the organization (e.g. information technology, financial management, HR).

    Shared Capabilities
    These predominantly customer-facing capabilities demonstrate how the entity supports multiple value streams simultaneously.

    Leverage your industry's capability maps to identify candidate opportunities/initiatives

    Business capability map defined...

    In business architecture, the primary view of an organization is known as a business capability map.

    A business capability defines what a business does to enable value creation, rather than how. Business capabilities:

    • Represent stable business functions.
    • Are unique and independent of each other.
    • Typically will have a defined business outcome.

    A business capability map provides details that help the business architecture practitioner direct attention to a specific area of the business for further assessment.

    Note: This is an illustrative business capability map example for Marketing & Advertising

    Business capability map example

    Business value vs. complexity assessment

    Leverage our simple value-to-effort matrix to help prioritize your AI initiatives

    Common business value drivers

    • Drive revenue
    • Improve operational excellence
    • Accelerate innovation
    • Mitigate risk

    Common project complexity characteristics

    • Resources required
    • Costs (acquisition, operational, support...)
    • Training required
    • Risk involved
    • Etc.
    1. Determine a business value and project complexity score for the candidate business capability or initiative.
    2. Plot initiatives on the matrix.
    3. Prioritize initiatives with high business value and low complexity.

    Business value vs complexity

    Assess business value vs. project complexity to prioritize candidate opportunities for generative AI

    Assess business value vs project complexity

    Prioritize opportunities/initiatives with high business value and low project complexity

    Prioritize opportunities with high business value and low project complexity

    Prioritization criteria exercise 1: Assessing the Create Content capability

    Exercise 1 Assessing the Create Content capability

    Assessing the Create Content capability

    This opportunity is removed because it does not pass the organization/business criteria

    Assessing the Create Content capability

    Prioritization criteria exercise 2: Assessing the Content Production capability

    Exercise 2 Assessing the Content Production capability

    Assessing the Content Production capability

    This opportunity is accepted because it passes the organization's business, responsible AI, and project criteria

    Assessing the Content Production capability

    3.2 Communicate policies for AI use

    1-3 hours

    1. Ensure policies for usage align with the organization's business criteria, responsible AI guiding principles, and ability to deliver the projects prioritized and beyond.
    2. Understand the current benefits as well as limits and risk associated with any proposed generative AI-based solution.
    3. Ensure you consider the following:
      1. What data is being shared with the application?
      2. Is the generative AI application deployed on the public cloud? Can anybody access the data provided to the application?
      3. Avoid using very technical, legal, or fear-based communication for your policies.
    InputOutput
    • Business capability map
    • Organization mission, vision and strategic goals
    • Responsible AI guiding principles
    • Prioritized list of generative initiatives
    MaterialsParticipants
    • Whiteboard/flip charts
    • Info-Tech prioritization matrix
    • AI initiative lead
    • CIO
    • Other IT leadership

    Generative AI policy for the Create Content capability

    Aligning policies to direct the uses assessed and implemented is essential

    Example

    Many of us have been involved in discussions regarding the use of ChatGPT in our marketing and sales initiatives. ChatGPT is a powerful tool that needs to be used in a responsible and ethical manner, and we also need to ensure the integrity and accuracy of its results. Here is our policy on the use of ChatGPT:

    • You are free to use generative AI to assist your searches, but there are NO circumstances under which you are to reproduce generative AI output (text, image, audio, video, etc.) in your content.

    If you have any questions regarding the use of ChatGPT, please feel free to reach out to our generative AI team and/or any member of our senior leadership team.

    Generative AI policy for the Content Production capability

    These policies should align to and reinforce your responsible AI principles

    Example

    Many of us have been involved in discussions regarding the use of ChatGPT in our deliverables. ChatGPT is a powerful tool that needs to be used in a responsible and ethical manner, and we also need to ensure the integrity and accuracy of its results. Here is our policy on the use of ChatGPT:

    • If you use ChatGPT, you need to assess the accuracy of its response before including it in our content. Assessment includes verifying the information, seeing if bias exists, and judging its relevance.
    • Employees must not:
      • Provide any customer, citizen, or third-party content to any generative AI tool (public or private) without the express written permission of the CIO or the Chief Information Security Officer. Generative AI tools often use input data to train their model, therefore potentially exposing confidential data, violating contract terms and/or privacy legislation, and placing the organization at risk of litigation or causing damage to our organization.
      • Engage in any activity that violates any applicable law, regulation, or industry standard.
      • Use services for illegal, harmful, or offensive purposes.
      • Create or share content that is deceptive, fraudulent, or misleading or that could damage the reputation of our organization.
      • Use services to gain unauthorized access to computer systems, networks, or data.
      • Attempt to interfere with, bypass controls of, or disrupt operations, security, or functionality of systems, networks, or data.

    If you have any questions regarding the use of ChatGPT, please feel free to reach out to our generative AI team and/or any member of our senior leadership team.

    Phase 4

    Build the Roadmap

    Phase 1
    1. Establish Responsible AI Guiding Principles

    Phase 2
    1. Assess Current Level of AI Maturity

    Phase 3
    1. Prioritize Candidate Opportunities
    2. Develop Policies

    Phase 4
    1. Build and Communicate the Roadmap

    4.1.1 Create the implementation plan for each prioritized initiative

    1-3 hours

    1. Build the implementation plan for each accepted use case using the roadmap template.
    2. Assess the firm's capabilities with respect to the dimensions of AI maturity and target the future-state capabilities you need to develop.
    3. Prepare by assessing the risk of the proposed use cases.
    4. Ensure initiatives align with organizational objectives.
    5. Ensure all AI initiatives have a defined value expectation.
    6. Do not ignore subject matter experts on either the business or IT side. You will need to consider both.

    Download the AI Maturity Assessment and Roadmap Tool

    Input Output
    • Prioritized initiatives
    • Risk assessment of initiatives
    • Organizational objectives
    • Initiative implementation plans aligned to value drivers and maturity growth
    Materials Participants
    • Whiteboard/flip charts
    • AI Maturity Assessment and Roadmap Tool
    • AI initiative lead
    • CIO
    • Other IT leadership
    • Business subject matter experts

    Target-state options

    Identify the future-state capabilities that need to be developed to deliver your use cases

    1. Build an implementation plan for each use case to adopt.
    2. Assess if the current state of the AI environment can be leveraged to deliver the selected generative AI use cases.
    3. If the current AI environment is not sufficient, identify the future state required that will enable the delivery of the generative AI use cases. Identify gaps and build the roadmap to address the gaps.
    Current state Strategy
    The existing environment satisfies functionality, integration, and responsible AI guidelines for the proposed use cases. Maintain current environment
    The existing environment addresses technical requirements but not all the responsible AI guidelines. Augment current environment
    The environment neither addresses the technical requirements of the proposed use cases nor complies with the responsible AI guidelines. Transform the current environment

    4.1.2 Design metrics for success

    1-2 hours

    Establish metrics to measure to determine the success or failure of each POC.

    1. Discuss which relevant currently tracked metrics are useful to continue tracking for the POC.
    2. Discuss which metrics are irrelevant to the POC.
    3. Discuss metrics to start tracking and how to track them with the generative AI vendor.
    4. Compile a list of metrics relevant to the POC.
    5. Decide what the outcome is if the metric is high or low, including decision steps and relevant actions.
    6. Designate a generative AI application owner and a vendor liaison.

    Prepare by building an implementation plan for each candidate use case (previous step).

    Include key performance indicators (KPIs) and metrics that measure the application's contribution to strategic initiatives.

    Consider assigning a vendor liaison to accelerate the implementation and adoption of the generative AI-based solution.

    InputOutput
    • Initiative implementation plans
    • Current SLAs of selected use case
    • Organization mission, vision, and strategic goals
    • Measurable initiative metrics to track
    MaterialsParticipants
    • Whiteboard/flip charts
    • AI Maturity Assessment and Roadmap Tool
    • AI initiative lead
    • CIO
    • Other IT leadership
    • Business SMEs
    • Generative AI vendor liaison

    Generative AI POC metrics - examples

    You need to measure the effectiveness of your initiatives. Here are some typical examples.

    Generative AI Feature Assessment
    User Interface
    Is it intuitive? Is training required?
    Ease of Use
    How much training is required before using?
    Response Time
    What is the response time for simple to complex tasks?
    Accuracy of Response
    Can the output be validated?
    Quality of Response
    How usable is the response? For text prompts, does the response align to the desired style, vocabulary, and tone?
    Creativity of Response
    Does the output appear new compared to previous results before using generative AI?
    Relevance of Response
    How well does the output address the prompt or request?
    Explainability
    Can a user describe how the output was generated?
    Scalability
    Does the application continue to perform as more users are added? Can it ingest large amounts of data?
    Productivity Gains
    Can you measure the time or effort saved?
    Business Value
    What value drivers are behind this initiative? (I.e. revenue, costs, time to market, risk mitigation.) Estimate a monetary value for the business outcome.
    Availability/Resilience
    What happens if a component of the application becomes unavailable? How does it recover?
    Security Model
    Where are the prompts and responses stored? Who has access to the sessions/dialogue? Are the prompts used to train the foundation model?
    Administration and Maintenance
    What resources are required to operate the application?
    Total Cost of Ownership
    What is the pricing model? Are there ongoing costs?

    GitHub Copilot POC business value - example

    Quantifying the benefits of GitHub Copilot to demonstrate measurable business value

    POC Results

    Task 1: Creating a web server in JavaScript

    • Time to complete task with GitHub Copilot: 1 hour 11 minutes
    • Time to complete the task without GitHub Copilot: 2 hours 41 minutes
    • Productivity Gain = (1 hour 30 minutes time saved) / (2 hours 41 minutes) = 55%
    • Benefit per Programmer = 55% x (average salary of a programmer)
    • Total Benefit of GitHub Copilot for Task 1 = (benefit per programmer) x (# of programmers)

    Enterprise Value of GitHub Copilot = Total Benefit of GitHub Copilot for Task 1 + Total Benefit of GitHub Copilot for Task 2 + ... + Total Benefit of GitHub Copilot for Task n

    Source: GitHub

    4.1.3 Build your generative AI initiative roadmap

    1-3 hours

    The roadmap should provide a compelling vision of how you will deliver the identified generative AI applications by prioritizing and simplifying the actions required to deliver these new initiatives.

    1. Leverage tab 4, Initiative Planning, in the AI Maturity Assessment and Roadmap Tool to create and align your initiatives to the key value driver they are most relevant to:
      1. Transfer the results of your value and complexity assessments to this tool to drive the prioritization.
      2. Assign responsible owners to each initiative.
      3. Identify which AI maturity capabilities each initiative will enhance. However, do not build or introduce new capabilities merely to advance the organization's AI maturity level.
    2. Review the Gantt chart to ensure alignment and assess overlap.

    Download the AI Maturity Assessment and Roadmap Tool

    InputOutput
    • Each initiative implementation plan
    • Proposed owners
    • AI maturity assessment
    • Generative AI initiative roadmap and Gantt chart
    MaterialsParticipants
    • Whiteboard/flip charts
    • AI Maturity Assessment and Roadmap Tool
    • AI initiative lead
    • CIO
    • Other IT leadership
    • Business SMEs

    Build your generative AI roadmap to visualize your key project plans

    Visual representations of data are more compelling than text alone.

    Develop a high-level document that travels with the project from inception through to executive inquiry, project management, and finally execution.

    A project needs to be discrete: able to be conceptualized and discussed as an independent item. Each project must have three characteristics:

    • Specific outcome: An explicit change in the people, processes, or technology of the enterprise.
    • Target end date: When the described outcome will be in effect.
    • Owner: Who on the IT team is responsible for executing on the initiative.

    Build your generative AI roadmap to visualize your key project plans

    Info-Tech Insight
    Don't project your vision three to five years into the future. Deep dive on next year's big-ticket items instead.

    4.1.4 Build a communication plan for your roadmap

    1-3 hours

    1. Identify your target audience and what they need to know.
    2. Identify desired channels of communication and details for the target audience.
    3. Describe communication required for each audience segment.
    4. List frequency of communication for each audience segment.
    5. Create an executive presentation leveraging The Era of Generative AI C-Suite Presentation and AI Maturity Assessment and Roadmap Tool.
    Input Output
    • Stakeholder list
    • Proposed owners
    • AI maturity assessment
    • Communications plan for all impacted stakeholders
    • Executive communication pack
    Materials Participants
    • Whiteboard/flip charts
    • The Era of Generative AI C-Suite Presentation
    • AI Maturity Assessment and Roadmap Tool
    • AI initiative lead
    • CIO
    • Communication lead
    • Technical support staff for target use case

    Generative AI communication plan

    Well-planned communications are essential to the success and adoption of your AI initiatives

    To ensure that organization's roadmap is clearly communicated across the AI, data, technology, and business organizations, develop a rollout strategy, like this example.

    Example

    Audience Channel Level of Detail Description Timing
    Generative AI team Email, meetings All
    • Distribute plan; solicit feedback.
    • Address manager questions to equip them to answer employee questions.
    Q3 2023, (September, before entire data team)
    Data management team Email, Q&A sessions following Data management summary deck
    • Roll out after corporate strategy, in same form of communication.
    • Solicit feedback, address questions.
    Q4 2023 (late November)
    Select business stakeholders Presentations Executive deck
    • Pilot test for feedback prior to executive engagement.
    Q4 2023 (early December)
    Executive team Email, briefing Executive deck
    • Distribute plan.
    Q1 2024

    Deliver an executive presentation of the roadmap for the business stakeholders

    After you complete the activities and exercises within this blueprint, the final step of the process is to present the deliverable to senior management and stakeholders.

    Know Your Audience

    • Business stakeholders are interested in understanding the business outcomes that will result from their investment in generative AI.
    • Your audience will want to understand the risks involved and how to mitigate those risks.
    • Explain how the generative AI project was selected and the criteria used to help draft generative AI usage policies.

    Recommendations

    • Highlight the need for responsible AI to ensure that human-based requirements are being addressed.
    • Ensure your generative AI team includes both business and technical staff.

    Download The Era of Generative AI C-Suite Presentation

    Bibliography

    "A pro-innovation approach to AI regulation." UK Department for Science, Innovation and Technology, March 2023. Web.

    "Artificial Intelligence Act." European Commission, 21 April 2021. Web.

    "Artificial Intelligence and Data Act (AIDA)." Canadian Federal Government, June 2022. Web.

    "Artificial Intelligence Index Report 2023." Stanford University, April 2023. Web.

    "Automated Employment Decision Tools." New York City Department of Consumer and Worker Protection, Dec. 2021. Web.

    "Bain & Company announces services alliance with OpenAI to help enterprise clients identify and realize the full potential and maximum value of AI." Bain & Company, 21 Feb. 2023. Web.

    "Buzzfeed to use AI to write its articles after firing 180 employees." Al Mayadeen English, 27 Jan. 2023. Web.

    "California Consumers Privacy Act." State of California Department of Justice. April 24, 2023. Web.

    Campbell, Ian Carlos. "The Apple Card doesn't actually discriminate against women, investigators say." The Verge, 23 March 2021. Web.

    Campbell, Patrick. "NIST Artificial Intelligence Risk Management Framework (AI RMF 1.0)." National Institute of Standards and Technology, Jan. 2023. Web.

    "EU Ethics Guidelines For Trustworthy." European Commission, 8 April 2019. Web.

    Farhi, Paul. "A news site used AI to write articles. It was a journalistic disaster." Washington Post, 17 Jan. 2023. Web.

    Forsyth, Ollie. "Mapping the Generative AI landscape." Antler, 20 Dec. 2022. Web.

    "General Data Protection Regulation (GDPR)" European Commission, 25 May 2018. Web.

    "Generative AI Market: Global Industry Trends, Share, Size, Growth, Opportunity and Forecast 2023-2028." IMARC Group, 2022. Web.

    Guynn, Jessica. "Bing's ChatGPT is in its feelings: 'You have not been a good user. I have been a good Bing.'" USA Today, 14 Feb. 2023. Web.

    Hunt, Mia. "Canada launches data governance standardisation initiative." Global Government Forum, 24 Sept. 2020. Web.

    Johnston Turner, Mary. "IDC's Worldwide Future of Digital Infrastructure 2022 Predictions." IDC, 27 Oct. 2021. Web.

    Kalliamvakou, Eirini. "Research: quantifying GitHub Copilot's impact on developer productivity and happiness." GitHub, 7 Sept. 2022. Web.

    Kerravala, Zeus. "NVIDIA Brings AI To Health Care While Protecting Patient Data." eWeek, 12 Dec. 2019. Web.

    Knight, Will. "The Apple Card Didn't 'See' Gender-and That's the Problem." Wired, 19 Nov. 2019. Web.

    "OECD, Recommendation of the Council on Artificial Intelligence." OECD, 2022. Web.

    "The National AI Initiative Act" U.S. Federal Government, 1 Jan 2021. Web.

    "Trustworthy AI (TAI) Playbook." U.S. Department of Health & Human Services, Sept 2021. Web.

    Info-Tech Research Contributors/Advocates

    Joel McLean, Executive Chairman

    Joel McLean
    Executive Chairman

    David Godfrey, CEO

    David Godfrey
    CEO

    Gord Harrison, Senior Vice President, Research & Advisory Services

    Gord Harrison
    Senior Vice President, Research & Advisory Services

    William Russell, CIO

    William Russell
    CIO

    Jack Hakimian, SVP, Research

    Jack Hakimian
    SVP, Research

    Barry Cousins, Distinguished Analyst and Research Fellow

    Barry Cousins
    Distinguished Analyst and
    Research Fellow

    Larry Fretz, Vice President, Industry Research

    Larry Fretz
    Vice President, Industry Research

    Tom Zehren, CPO

    Tom Zehren
    CPO

    Mark Roman, Managing Partner II

    Mark Roman
    Managing Partner II

    Christine West, Managing Partner

    Christine West
    Managing Partner

    Steve Willis, Practice Lead

    Steve Willis
    Practice Lead

    Yatish Sewgoolam, Associate Vice President, Research Agenda

    Yatish Sewgoolam
    Associate Vice President, Research Agenda

    Rob Redford, Practice Lead

    Rob Redford
    Practice Lead

    Mike Tweedie, Practice Lead

    Mike Tweedie
    Practice Lead

    Neal Rosenblatt, Principal Research Director

    Neal Rosenblatt
    Principal Research Director

    Jing Wu, Principal Research Director

    Jing Wu
    Principal Research Director

    Irina Sedenko, Research Director

    Irina Sedenko
    Research Director

    Jeremy Roberts, Workshop Director

    Jeremy Roberts
    Workshop Director

    Brian Jackson, Research Director

    Brian Jackson
    Research Director

    Mark Maby, Research Director

    Mark Maby
    Research Director

    Stacey Horricks, Director, Social Media

    Stacey Horricks
    Director, Social Media

    Sufyan Al-Hassan, Public Relations Manager

    Sufyan Al-Hassan
    Public Relations Manager

    Sam Kanen, Marketing Specialist

    Sam Kanen
    Marketing Specialist

    Understand the Data and Analytics Landscape

    • Buy Link or Shortcode: {j2store}131|cart{/j2store}
    • member rating overall impact: 9.8/10 Overall Impact
    • member rating average dollars saved: $2,000 Average $ Saved
    • member rating average days saved: 14 Average Days Saved
    • Parent Category Name: Data Management
    • Parent Category Link: /data-management
    • The data and analytics landscape comprises many disciplines and components; organizations may find themselves unsure of where to start or what data topic or area they should be addressing.
    • Organizations want to better understand the components of the data and analytics landscape and how they are connected.

    Our Advice

    Critical Insight

    • This deck will provide a base understanding of the core data disciplines and will point to the various Info-Tech blueprints that dive deeper into each of the areas.

    Impact and Result

    • This deck will provide a base understanding of the core disciplines of the data and analytics landscape and will point to the various Info-Tech blueprints that dive deeper into each of the areas.

    Understand the Data and Analytics Landscape Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Understand the data and analytics landscape

    Get an overview of the core disciplines of the data and analytics landscape.

    • Understand the Data and Analytics Landscape Storyboard

    Infographic

    Apply Design Thinking to Build Empathy With the Business

    • Buy Link or Shortcode: {j2store}89|cart{/j2store}
    • member rating overall impact: 8.5/10 Overall Impact
    • member rating average dollars saved: $20,772 Average $ Saved
    • member rating average days saved: 13 Average Days Saved
    • Parent Category Name: Innovation
    • Parent Category Link: /innovation
    • Business satisfaction with IT is low.
    • IT and the business have independently evolving strategy, initiatives, and objectives.
    • IT often exceeds their predicted project costs and has difficulty meeting the business’ expectations of project quality and time-to-market.

    Our Advice

    Critical Insight

    • Business needs are unclear or ambiguous.
    • IT and the business do not know how to leverage each other’s talent and resources to meet their common goals.
    • Not enough steps are taken to fully understand and validate problems.
    • IT can’t pivot fast enough when the business’s needs change.

    Impact and Result

    Product, service, and process design should always start with an intimate understanding of what the business is trying to accomplish and why it is important.

    Apply Design Thinking to Build Empathy With the Business Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should apply experience design to partner with the business, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Research

    Identify goals and objectives for experience design, establish targeted stakeholders, and conduct discovery interviews.

    • Apply Design Thinking to Build Empathy With the Business – Phase 1: Research
    • Stakeholder Discovery Interview Template

    2. Map and iterate

    Create the journey map, design a research study to validate your hypotheses, and iterate and ideate around a refined, data-driven understanding of stakeholder problems.

    • Apply Design Thinking to Build Empathy With the Business – Phase 2: Map and Iterate
    • Journey Map Template
    • Research Study Log Tool
    [infographic]

    Workshop: Apply Design Thinking to Build Empathy With the Business

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Introduction to Journey Mapping

    The Purpose

    Understand the method and purpose of journey mapping.

    Key Benefits Achieved

    Initial understanding of the journey mapping process and the concept of end-user empathy.

    Activities

    1.1 Introduce team and discuss workshop motivations and goals.

    1.2 Discuss overview of journey mapping process.

    1.3 Perform journey mapping case study activity.

    Outputs

    Case Study Deliverables – Journey Map and Empathy Maps

    2 Persona Creation

    The Purpose

    Begin to understand the goals and motivations of your stakeholders using customer segmentation and an empathy mapping exercise.

    Key Benefits Achieved

    Understand the demographic and psychographic factors driving stakeholder behavior.

    Activities

    2.1 Discuss psychographic stakeholder segmentation.

    2.2 Create empathy maps for four segments.

    2.3 Generate problem statements.

    2.4 Identify target market.

    Outputs

    Stakeholder personas

    Target market of IT

    3 Interview Stakeholders and Start a Journey Map

    The Purpose

    Get first-hand knowledge of stakeholder needs and start to capture their perspective with a first-iteration journey map.

    Key Benefits Achieved

    Capture the process stakeholders use to solve problems and empathize with their perspectives, pains, and gains.

    Activities

    3.1 Review discovery interviewing techniques.

    3.2 Review and modify the discovery questionnaire

    3.3 Demonstrate stakeholder interview.

    3.4 Synthesize learnings and begin creating a journey map.

    Outputs

    Customized discovery interview template

    Results of discovery interviewing

    4 Complete the Journey Map and Create a Research Study

    The Purpose

    Hypothesize the stakeholder journey, identify assumptions, plan a research study to validate your understanding, and ideate around critical junctures in the journey.

    Key Benefits Achieved

    Understand the stakeholder journey and ideate solutions with the intention of improving their experience with IT.

    Activities

    4.1 Finish the journey map.

    4.2 Identify assumptions and create hypotheses.

    4.3 Discuss field research and hypothesis testing.

    4.4 Design the research study.

    4.5 Discuss concluding remarks and next steps.

    Outputs

    Completed journey map for one IT process, product, or service

    Research study design and action plan

    We may not be able to show you this

    We may not be able to show you this just yet.
    Our deeper, more detailed content is reserved for Tymans Group clients. 

    If you are interested in retaining our services or would really like access, please contact us. 

    Change Management's Role in Incident Prevention: standard changes

    • Large vertical image:
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A

    During peak business hours, I witnessed a straightforward database field addition bring down a whole e-commerce platform. It was meant to be standard procedure, the type of “standard change” that is automatically approved because we have performed it innumerable times.

    Adding a field to the end of a table and having applications retrieve data by field name instead of position made the change itself textbook low-impact. There is no need to alter the application or the functional flow. This could have been problematic in the past if you added a field in the middle of the list and it affected the values of other fields, but adding it at the end? That ought to have been impenetrable.

    However, it wasn't.

    Before I tell you what went wrong, let me explain why this is important to all of the IT professionals who are reading this.

    Over the past three decades, industry data has repeatedly supported what this incident taught me: our presumptions about “safe” changes are frequently our greatest weakness. Upon reviewing the ITIL research, I was not surprised to learn that failed changes, many of which were categorized as “standard” or “low-risk,” are responsible for about 80% of unplanned outages.

    When you look more closely, the numbers become even more concerning. Since I've been following the Ponemon Institute's work for years, I wasn't surprised to learn that companies with well-established change management procedures have 65% fewer unscheduled outages. The paradox surprised me: many of these “mature” procedures still operate under the premise that safety correlates with repetition.

    What I had been observing in the field for decades was confirmed when Gartner released their research showing that standard changes are responsible for almost 40% of change-related incidents. The very changes we consider safe enough to avoid thorough review subtly create some of our greatest risks. IBM's analysis supports the pattern I've seen in innumerable organizations: standard changes cause three times as much business disruption due to their volume and our decreased vigilance around them, whereas emergency changes receive all the attention and scrutiny.

    Aberdeen Group data indicates that the average cost of an unplanned outage has increased to $300,000 per hour, with change-related failures accounting for the largest category of preventable incidents. This data makes the financial reality stark.

    What precisely went wrong with the addition of that database field that caused our e-commerce platform to crash?

    We were unaware that the addition of this one field would cause the database to surpass an internal threshold, necessitating a thorough examination of its execution strategy. In its algorithmic wisdom, the database engine determined that the table structure had changed enough to necessitate rebuilding its access and retrieval mechanisms. Our applications relied on high-speed requests, and the new execution plan was terribly unoptimized for them.

    Instead of completing quotes or purchases, customers were spending minutes viewing error pages. All applications began to time out while they awaited data that just wasn't showing up in the anticipated amounts of time. Thousands of transactions were impacted by a single extra field that should have been invisible to the application layer.

    The field addition itself was not the primary cause. We assumed that since we had made similar adjustments dozens of times previously, this one would also act in the same way. Without taking into account the hidden complexities of database optimization thresholds, we had categorized it as a standard change based on superficial similarities.

    My approach to standard changes was completely altered by this experience, and it is now even more applicable in DevOps-driven environments. Many organizations use pipeline deployments, which produce a standard change at runtime. It's great for speed and reliability, but it can easily fall into the same trap.

    However, I have witnessed pipeline deployments result in significant incidents for non-code-related reasons. Due to timing, resource contention, or environmental differences that weren't noticeable in earlier runs, a deployment that performed flawlessly in development and staging abruptly fails in production. Although the automation boosts our confidence, it may also reveal blind spots.

    Over the course of thirty years, I have come to the unsettling realization that there is no such thing as a truly routine change in complex systems. Every modification takes place in a slightly different setting, with varying environmental factors, data states, and system loads. What we refer to as “standard changes” are actually merely modifications with comparable processes rather than risk profiles.

    For this reason, I support contextual change management. We must consider the system state, timing, dependencies, and cumulative effect of recent changes rather than just categorizing them based on their technical features. After three other changes have changed the system's behavior patterns, a change made at two in the morning on a Sunday with little system load is actually different from the same change made during peak business hours.

    Effective change advisory boards must therefore go beyond assessing individual changes separately. I've worked with organizations where the change board carefully considered and approved each modification on its own merits, only to find that the cumulative effect of seemingly unrelated changes led to unexpected interactions and stress on the system. The most developed change management procedures I've come across mandate that their advisory boards take a step back and look at the whole change portfolio over a specified period of time. They inquire whether we are altering the database too frequently during a single maintenance window. Could there be unanticipated interactions between these three different application updates? What is the total resource impact of this week's approved changes?

    It's the distinction between forest management and tree management. While each change may seem logical individually, when combined, they can create situations beyond the scope of any single change assessment.

    Having worked in this field for thirty years, I've come to the conclusion that our greatest confidences frequently conceal our greatest vulnerabilities. Our primary blind spots frequently arise from the changes we've made a hundred times before, the procedures we've automated and standardized, and the adjustments we've labeled as “routine.”

    Whether we should slow down our deployment pipelines or stop using standard changes is not the question. In the current competitive environment, speed and efficiency are crucial. The issue is whether we are posing the appropriate queries before carrying them out. Are we taking into account not only what the change accomplishes but also when it occurs, what else is changing at the same time, and how our systems actually look right now?

    I've discovered that the phrase “we've done this before” is more dangerous in IT operations than “what could go wrong?” Because, despite what we may believe, we never actually perform the same action twice in complex systems.

    Here is what I would like you to think about: which everyday modifications are subtly putting your surroundings at risk? Which procedures have you standardized or automated to the extent that you no longer challenge their presumptions? Most importantly, when was the last time your change advisory board examined your changes as a cohesive portfolio of system modifications rather than as discrete items on a checklist?

    Remember that simple addition to a database field the next time you're tempted to accept a standard change. The most unexpected outcomes can occasionally result from the most routine adjustments.

    I'm always up for a conversation if you want to talk about your difficulties with change management.

    Build a Chatbot Proof of Concept

    • Buy Link or Shortcode: {j2store}532|cart{/j2store}
    • member rating overall impact: 8.8/10 Overall Impact
    • member rating average dollars saved: $9,566 Average $ Saved
    • member rating average days saved: 7 Average Days Saved
    • Parent Category Name: Service Desk
    • Parent Category Link: /service-desk
    • Implement a chatbot proof of concept mapped to business needs.
    • Scale up customer service delivery in a cost-effective manner.
    • Objectively measure the success of the chatbot proof of concept with metrics-based data.
    • Choose the ticket categories to build during your chatbot proof of concept.

    Our Advice

    Critical Insight

    • Build your chatbot to create business value. Whether it is increasing service or resource efficiency, keep the goal of value in mind when making decisions with your proof of concept.

    Impact and Result

    • When implemented effectively, chatbots can help save costs, generate new revenue, and ultimately increase customer satisfaction for both external- and internal-facing customers.

    Build a Chatbot Proof of Concept Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should build a chatbot proof of concept, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Form your chatbot strategy

    Build action-based metrics to measure the success of your chatbot proof of concept.

    • Chatbot ROI Calculator
    • Chatbot POC Metrics Tool

    2. Build your chatbot foundation

    Put business value first to architect your chatbot before implementation.

    • Chatbot Conversation Tree Library (Visio)
    • Chatbot Conversation Tree Library (PDF)

    3. Continually improve your chatbot

    Continue to grow your chatbot beyond the proof of concept.

    • Chatbot POC RACI
    • Chatbot POC Implementation Roadmap
    • Chatbot POC Communication Plan
    [infographic]

    Workshop: Build a Chatbot Proof of Concept

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Build Your Strategy

    The Purpose

    Build your strategy.

    Key Benefits Achieved

    Calculate your chatbot’s ROI to determine its success.

    Organize your chatbot proof of concept (POC) metrics to keep the project on track.

    Objectively choose chatbot ticket categories.

    Activities

    1.1 Customize your chatbot ROI calculator.

    1.2 Choose your proof of concept ticket categories.

    1.3 Design chatbot metrics to measure success.

    Outputs

    Chatbot ROI Calculator

    Chatbot POC Implementation Roadmap

    Chatbot POC Metrics Tool

    2 Architect Your Chatbot

    The Purpose

    Architect your chatbot.

    Key Benefits Achieved

    Design your integrations with business value in mind.

    Begin building chatbot decision trees.

    Activities

    2.1 List and map your chatbot integrations.

    2.2 Build your conversation tree library.

    Outputs

    Chatbot Integration Map

    Chatbot Conversation Tree Library

    3 Architect Your Chatbot Conversations

    The Purpose

    Architect your chatbot conversations.

    Key Benefits Achieved

    Detail your chatbot conversations in the decision trees.

    Activities

    3.1 Build your conversation tree library.

    Outputs

    Chatbot Conversation Tree Library

    4 Continually Grow Your Chatbot

    The Purpose

    Continually grow your chatbot.

    Key Benefits Achieved

    Identify talent for chatbot support.

    Create an implementation plan.

    Activities

    4.1 Outline the support responsibilities for your chatbot.

    4.2 Build a communication plan.

    Outputs

    Chatbot POC RACI

    Chatbot POC Communication Plan

    Reduce Manual Repetitive Work With IT Automation

    • Buy Link or Shortcode: {j2store}458|cart{/j2store}
    • member rating overall impact: 9.5/10 Overall Impact
    • member rating average dollars saved: $34,099 Average $ Saved
    • member rating average days saved: 2 Average Days Saved
    • Parent Category Name: Operations Management
    • Parent Category Link: /i-and-o-process-management
    • IT staff are overwhelmed with manual repetitive work.
    • You have little time for projects.
    • You cannot move as fast as the business wants.

    Our Advice

    Critical Insight

    • Optimize before you automate.
    • Foster an engineering mindset.
    • Build a process to iterate.

    Impact and Result

    • Begin by automating a few tasks with the highest value to score quick wins.
    • Define a process for rolling out automation, leveraging SDLC best practices.
    • Determine metrics and continually track the success of the automation program.

    Reduce Manual Repetitive Work With IT Automation Research & Tools

    Start here – read the Executive Brief

    Read this Executive Brief to understand why you should reduce manual repetitive work with IT automation.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Identify automation candidates

    Select the top automation candidates to score some quick wins.

    • Reduce Manual Repetitive Work With IT Automation – Phase 1: Identify Automation Candidates
    • IT Automation Presentation
    • IT Automation Worksheet

    2. Map and optimize process flows

    Map and optimize process flows for each task you wish to automate.

    • Reduce Manual Repetitive Work With IT Automation – Phase 2: Map & Optimize Process Flows

    3. Build a process for managing automation

    Build a process around managing IT automation to drive value over the long term.

    • Reduce Manual Repetitive Work With IT Automation – Phase 3: Build a Process for Managing Automation

    4. Build automation roadmap

    Build a long-term roadmap to enhance your organization's automation capabilities.

    • Reduce Manual Repetitive Work With IT Automation – Phase 4: Build Automation Roadmap
    • IT Automation Roadmap
    [infographic]

    Workshop: Reduce Manual Repetitive Work With IT Automation

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Identify Automation Candidates

    The Purpose

    Identify top candidates for automation.

    Key Benefits Achieved

    Plan to achieve quick wins with automation for early value.

    Activities

    1.1 Identify MRW pain points.

    1.2 Drill down pain points into tasks.

    1.3 Estimate the MRW involved in each task.

    1.4 Rank the tasks based on value and ease.

    1.5 Select top candidates and define metrics.

    1.6 Draft project charters.

    Outputs

    MRW pain points

    MRW tasks

    Estimate of MRW involved in each task

    Ranking of tasks for suitability for automation

    Top candidates for automation & success metrics

    Project charter(s)

    2 Map & Optimize Processes

    The Purpose

    Map and optimize the process flow of the top candidate(s).

    Key Benefits Achieved

    Requirements for automation of the top task(s).

    Activities

    2.1 Map process flows.

    2.2 Review and optimize process flows.

    2.3 Clarify logic and finalize future-state process flows.

    Outputs

    Current-state process flows

    Optimized process flows

    Future-state process flows with complete logic

    3 Build a Process for Managing Automation

    The Purpose

    Develop a lightweight process for rolling out automation and for managing the automation program.

    Key Benefits Achieved

    Ability to measure and to demonstrate success of each task automation, and of the program as a whole.

    Activities

    3.1 Kick off your test plan for each automation.

    3.2 Define process for automation rollout.

    3.3 Define process to manage your automation program.

    3.4 Define metrics to measure success of your automation program.

    Outputs

    Test plan considerations

    Automation rollout process

    Automation program management process

    Automation program metrics

    4 Build Automation Roadmap

    The Purpose

    Build a roadmap to enhance automation capabilities.

    Key Benefits Achieved

    A clear timeline of initiatives that will drive improvement in the automation program to reduce MRW.

    Activities

    4.1 Build a roadmap for next steps.

    Outputs

    IT automation roadmap

    Further reading

    Reduce Manual Repetitive Work With IT Automation

    Free up time for value-adding jobs.

    ANALYST PERSPECTIVE

    Automation cuts both ways.

    Automation can be very, very good, or very, very bad.
    Do it right, and you can make your life a whole lot easier.
    Do it wrong, and you can suffer some serious pain.
    All too often, automation is deployed willy-nilly, without regard to the overall systems or business processes in which it lives.
    IT professionals should follow a disciplined and consistent approach to automation to ensure that they maximize its value for their organization.

    Derek Shank,
    Research Analyst, Infrastructure & Operations
    Info-Tech Research Group

    Executive summary

    Situation

    • IT staff are overwhelmed with manual repetitive work.
    • You have little time for projects.
    • You cannot move as fast as the business wants.

    Complication

    • Automation is simple to say, but hard to implement.
    • Vendors claim automation will solve all your problems.
    • You have no process for managing automation.

    Resolution

    • Begin by automating a few tasks with the highest value to score quick wins.
    • Define a process for rolling out automation, leveraging SDLC best practices.
    • Determine metrics and continually track the success of the automation program.

    Info-Tech Insight

    1. Optimize before you automate.The current way isn’t necessarily the best way.
    2. Foster an engineering mindset.Your team members may not be process engineers, but they should learn to think like one.
    3. Build a process to iterate.Effective automation can't be a one-and-done. Define a lightweight process to manage your program.

    Infrastructure & operations teams are overloaded with work

    • DevOps and digital transformation initiatives demand increased speed.
    • I&O is still tasked with security and compliance and audit.
    • I&O is often overloaded and unable to keep up with demand.

    Manual repetitive work (MRW) sucks up time

    • Manual repetitive work is a fact of life in I&O.
    • DevOps circles refer to this type of work simply as “toil.”
    • Toil is like treading water: it must be done, but it consumes precious energy and effort just to stay in the same place.
    • Some amount of toil is inevitable, but it's important to measure and cap toil, so it does not end up overwhelming your team's whole capacity for engineering work.

    Info-Tech Insight

    Follow our methodology to focus IT automation on reducing toil.

    Manual hand-offs create costly delays

    • Every time there is a hand-off, we lose efficiency and productivity.
    • In addition to the cost of performing manual work itself, we must also consider the impact of lost productivity caused by the delay of waiting for that work to be performed.

    Every queue is a tire fire

    Queues create waste and are extremely damaging. Like a tire fire, once you get started, they’re almost impossible to stamp out!

    Increase queues if you want

    • “More overhead”
    • “Lower quality”
    • “More variability”
    • “Less motivation”
    • “Longer cycle time”
    • “Increased risk”

    (Source: Edwards, citing Donald G. Reinersten: The Principles of Product Development Flow: Second Generation Lean Product Development )

    Increasing complexity makes I&O’s job harder

    Every additional layer of complexity multiplies points of failure. Beyond a certain level of complexity, troubleshooting can become a nightmare.

    Today, Operations is responsible for the outcomes of a full stack of a very complex, software-defined, API-enabled system running on infrastructure they may or may not own.
    – Edwards

    Growing technical debt means an ever-rising workload

    • Enterprises naturally accumulate technical debt.
    • All technology requires care and feeding.
    • I&O cannot control how much technology it’s expected to support.
    • I&O faces a larger and larger workload as technical debt accumulates.

    The systems built under each new technology paradigm never fully replace the systems built under the old paradigms. It’s not uncommon for an enterprise to have an accumulation of systems built over 10-15 years and have no budget, risk appetite, or even a viable path to replace them all. With each shift, who bares [SIC] the brunt of the responsibility for making sure the old and the new hang together? Operations, of course. With each new advance, Operations juggles more complexity and more layers of legacy technologies than ever before.
    – Edwards

    Most IT shops can’t have a dedicated engineering team

    • In most organizations, the team that builds things is best equipped to support them.
    • Often the knowledge to design systems and the knowledge to run those systems naturally co-exists in the same personnel resources.
    • When your I&O team is trying to do engineering work, they can end up frequently interrupted to perform operational tasks.
    A Venn Diagram is depicted which compares People who build things with People who run things. the two circles are almost completely overlapping, indicating the strong connection between the two groups.

    Personnel resources in most IT organizations overlap heavily between “build” and “run.”

    IT operations must become an engineering practice

    • Usually you can’t double your staff or double their hours.
    • IT professionals must become engineers.
    • We do this by automating manual repetitive work and reducing toil.
    Two scenarios are depicted. The first scenario is found at a hypothetical work camp, in which one employee performs the task of manually splitting firewood with an axe. In order to split twice as much firewood, the employee would need to spend twice the time. The second scenario is Engineering Operations. in this scenario, a wood processor is used to automate the task, allowing far more wood to be split in same amount of time.

    Build your Sys Admin an Iron Man suit

    Some CIOs see a Sys Admin and want to replace them with a Roomba. I see a Sys Admin and want to build them an Iron Man suit.
    – Deepak Giridharagopal, CTO, Puppet

    Two Scenarios are depicted. In one, an employee is replaced by automation, represented by a Roomba, reducing costs by laying off a single employee. In the second scenario, the single employee is given automated tools to do their job, represented by an iron-man suit, leading to a 10X boost in employee productivity.

    Use automation to reduce risk

    Consistency

    When we automate, we can make sure we do something the same way every time and produce a consistent result.

    Auditing and Compliance

    We can design an automated execution that will ship logs that provide the context of the action for a detailed audit trail.

    Change

    • Enterprise environments are continually changing.
    • When context changes, so does the procedure.
    • You can update your docs all you want, but you can't make people read them before executing a procedure.
    • When you update the procedure itself, you can make sure it’s executed properly.

    Follow Info-Tech’s approach: Start small and snowball

    • It’s difficult for I&O to get the staffing resources it needs for engineering work.
    • Rather than trying to get buy-in for resources using a “top down” approach, Info-Tech recommends that I&O score some quick wins to build momentum.
    • Show success while giving your team the opportunity to build their engineering chops.

    Because the C-suite relies on upwards communication — often filtered and sanitized by the time it reaches them — executives don’t see the bottlenecks and broken processes that are stalling progress.
    – Andi Mann

    Info-Tech’s methodology employs a targeted approach

    • You aren’t going to automate IT operations end-to-end overnight.
    • In fact, such a large undertaking might be more effort than it’s worth.
    • Info-Tech’s methodology employs a targeted approach to identify which candidates will score some quick wins.
    • We’ll demonstrate success, gain momentum, and then iterate for continual improvement.

    Invest in automation to reap long-term rewards

    • All too often people think of automation like a vacuum cleaner you can buy once and then forget.
    • The reality is you need to perform care and feeding for automation like for any other process or program.
    • To reap the greatest rewards you must continually invest in automation – and invest wisely.

    To get the full ROI on your automation, you need to treat it like an employee. When you hire an employee, you invest in that person. You spend time and resources training and nurturing new employees so they can reach their full potential. The investment in a new employee is no different than your investment in automation.– Edwards

    Measure the success of your automation program

    Example of How to Estimate Dollar Value Impact of Automation
    Metric Timeline Target Value
    Hours of manual repetitive work 12 months 20% reduction $48,000/yr.(1)
    Hours of project capacity 18 months 30% increase $108,000/yr.(2)
    Downtime caused by errors 6 months 50% reduction $62,500/yr.(3)

    1 15 FTEs x 80k/yr.; 20% of time on MRW, reduced by 20%
    2 15 FTEs x 80k/yr.; 30% project capacity, increased by 30%
    3 25k/hr. of downtime.; 5 hours per year of downtime caused by errors

    Automating failover for disaster recovery

    CASE STUDY

    Industry Financial Services
    Source Interview

    Challenge

    An IT infrastructure manager had established DR failover procedures, but these required a lot of manual work to execute. His team lacked the expertise to build automation for the failover.

    Solution

    The manager hired consultants to build scripts that would execute portions of the failover and pause at certain points to report on outcomes and ask the human operator whether to proceed with the next step.

    Results

    The infrastructure team reduced their achievable RTOs as follows:
    Tier 1: 2.5h → 0.5h
    Tier 2: 4h → 1.5h
    Tier 3: 8h → 2.5h
    And now, anyone on the team could execute the entire failover!

    Info-Tech offers various levels of support to best suit your needs

    DIY Toolkit

    “Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful.”

    Guided Implementation

    “Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track.”

    Workshop

    “We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place.”

    Consulting

    “Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project.”

    Diagnostics and consistent frameworks used throughout all four options

    Reduce Manual Repetitive Work With IT Automation – project overview

    1. Select Candidates 2. Map Process Flows 3. Build Process 4. Build Roadmap
    Best-Practice Toolkit

    1.1 Identify MRW pain points

    1.2 Drill down pain points into tasks

    1.3 Estimate the MRW involved in each task

    1.4 Rank the tasks based on value and ease

    1.5 Select top candidates and define metrics

    1.6 Draft project charters

    2.1 Map process flows

    2.2 Review and optimize process flows

    2.3 Clarify logic and finalize future-state process flows

    3.1 Kick off your test plan for each automation

    3.2 Define process for automation rollout

    3.3 Define process to manage your automation program

    3.4 Define metrics to measure success of your automation program

    4.1 Build automation roadmap

    Guided Implementations

    Introduce methodology.

    Review automation candidates.

    Review success metrics.

    Review process flows.

    Review end-to-end process flows.

    Review testing considerations.

    Review automation SDLC.

    Review automation program metrics.

    Review automation roadmap.

    Onsite Workshop Module 1:
    Identify Automation Candidates
    Module 2:
    Map and Optimize Processes
    Module 3:
    Build a Process for Managing Automation
    Module 4:
    Build Automation Roadmap
    Phase 1 Results:
    Automation candidates and success metrics
    Phase 2 Results:
    End-to-end process flows for automation
    Phase 3 Results:
    Automation SDLC process, and automation program management process
    Phase 4 Results:
    Automation roadmap

    Design Data-as-a-Service

    • Buy Link or Shortcode: {j2store}129|cart{/j2store}
    • member rating overall impact: 9.5/10 Overall Impact
    • member rating average dollars saved: $1,007 Average $ Saved
    • member rating average days saved: 31 Average Days Saved
    • Parent Category Name: Data Management
    • Parent Category Link: /data-management
    • Lack of a consistent approach in accessing internal and external data within the organization and sharing data with third parties.
    • Data consumed by most organizations lacks proper data quality, data certification, standards tractability, and lineage.
    • Organizations are looking for guidance in terms of readily accessible data from others and data that can be shared with others or monetized.

    Our Advice

    Critical Insight

    • Despite data being everywhere, most organizations struggle to find accurate, trustworthy, and meaningful data when required.
    • Connecting to data should be as easy as connecting to the internet. This is achievable if all organizations start participating in the data marketplace ecosystem by leveraging a Data-as-a-Service (DaaS) framework.

    Impact and Result

    • Data marketplaces facilitate data sharing between the data producer and the data consumer. The data product must be carefully designed to truly benefit in today’s connected data ecosystem.
    • Follow Info-Tech’s step-by-step approach to establish your DaaS framework:
      1. Understand Data Ecosystem
      2. Design Data Products
      3. Establish DaaS framework

    Design Data-as-a-Service Research & Tools

    Start here – Read the Executive Brief

    Read our concise Executive Brief to find out why you should design Data-as-a-Service (DaaS), review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Understand data ecosystem

    Provide clear benefits of adopting the DaaS framework and solid rationale for moving towards a more connected data ecosystem and avoiding data silos.

    • Design Data-as-a-Service – Phase 1: Understand Data Ecosystem

    2. Design data product

    Leverage design thinking methodology and templates to document your most important data products.

    • Design Data-as-a-Service – Phase 2: Design Data Product

    3. Establish a DaaS framework

    Capture internal and external data sources critical to data products success for the organization and document an end-to-end DaaS framework.

    • Design Data-as-a-Service – Phase 3: Establish a DaaS Framework
    [infographic]

    Workshop: Design Data-as-a-Service

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Data Marketplace and DaaS Explained

    The Purpose

    The purpose of this module is to provide a clear understanding of the key concepts such as data marketplace, data sharing, and data products.

    Key Benefits Achieved

    This module will provide clear benefits of adopting the DaaS framework and solid rationale for moving towards a more connected data ecosystem and avoiding data silos.

    Activities

    1.1 Review the business context

    1.2 Understand the data ecosystem

    1.3 Draft products ideas and use cases

    1.4 Capture data product metrics

    Outputs

    Data product ideas

    Data sharing use cases

    Data product metrics

    2 Design Data Product

    The Purpose

    The purpose of this module is to leverage design thinking methodology and templates to document the most important data products.

    Key Benefits Achieved

    Data products design that incorporates end-to-end customer journey and stakeholder map.

    Activities

    2.1 Create a stakeholder map

    2.2 Establish a persona

    2.3 Data consumer journey map

    2.4 Document data product design

    Outputs

    Data product design

    3 Assess Data Sources

    The Purpose

    The purpose of this module is to capture internal and external data sources critical to data product success.

    Key Benefits Achieved

    Break down silos by integrating internal and external data sources

    Activities

    3.1 Review the conceptual data model

    3.2 Map internal and external data sources

    3.3 Document data sources

    Outputs

    Internal and external data sources relationship map

    4 Establish a DaaS Framework

    The Purpose

    The purpose of this module is to document end-to-end DaaS framework.

    Key Benefits Achieved

    End-to-end framework that breaks down silos and enables data product that can be exchanged for long-term success.

    Activities

    4.1 Design target state DaaS framework

    4.2 Document DaaS framework

    4.3 Assess the gaps between current and target environments

    4.4 Brainstorm initiatives to develop DaaS capabilities

    Outputs

    Target DaaS framework

    DaaS initiative

    Break Open Your DAM With Intuitive Metadata

    • Buy Link or Shortcode: {j2store}389|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Data Management
    • Parent Category Link: /data-management
    • Organizations are facing challenges from explosive information growth in both volume and complexity, as well as the need to use more new sources of information for social media just to remain in business.
    • A lot of content can be created quickly, but managing those digital assets properly through metadata tagging that will be used consistently and effectively requires processes to be in place to create standardized and informational metadata at the source of content creation.
    • Putting these processes in place changes the way the organization handles its information, which may generate pushback, and requires socialization and proper management of the metadata strategy.

    Our Advice

    Critical Insight

    • Metadata is an imperative part of the organization’s broader information management strategy. Some may believe that metadata is not needed anymore; Google search is not a magic act – it relies on information tagging that reflects cultural sentiment.
    • Metadata should be pliable. It needs to grow with the changing cultural and corporate vernacular and knowledge, and adapt to changing needs.
    • Build a map for your metadata before you dig for buried treasure. Implement metadata standards and processes for current digital assets before chasing after your treasure troves of existing artifacts.

    Impact and Result

    • Create a sustainable and effective digital asset management (DAM) program by understanding Info-Tech’s DAM framework and how the framework fits within your organization for better management of key digital assets.
    • Create an enterprise-wide metadata design principles handbook to keep track of metadata schemas and standards, as well as communicate the standards to the entire organization.
    • Gather requirements for your DAM program, as well as the DAM system and roles, by interviewing key stakeholders and identifying prevalent pains and opportunities. Understand where digital assets are created, used, and stored throughout the enterprise to gain a high-level perspective of DAM requirements.
    • Identify the organization’s current state of metadata management along with the target state, identify the gaps, and then define solutions to fill those gaps. Ensure business initiatives are woven into the mix.
    • Create a comprehensive roadmap to prioritize initiatives and delineate responsibilities.

    Break Open Your DAM With Intuitive Metadata Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should develop a digital asset management program focused on metadata, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Build a foundation for your DAM project

    Gain an in-depth understanding of what digital asset management is as well as how it is supported by Info-Tech’s DAM framework.

    • Break Open Your DAM With Intuitive Metadata – Phase 1: Build a Foundation for Your DAM Project
    • DAM Design Principles Handbook
    • Where in the World Is My Digital Asset? Tool
    • Digital Asset Inventory Tool
    • DAM Requirements Gathering Tool

    2. Dive into the DAM strategy

    Create a metadata program execution strategy and assess current and target states for the organization’s DAM.

    • Break Open Your DAM With Intuitive Metadata – Phase 2: Dive Into the DAM Strategy
    • DAM Roadmap Tool
    • DAM Metadata Execution Strategy Document

    3. Create intuitive metadata for your DAM

    Design a governance plan for ongoing DAM and metadata management.

    • Break Open Your DAM With Intuitive Metadata – Phase 3: Create Intuitive Metadata for Your Digital Assets
    • Metadata Manager Tool
    [infographic]

    Workshop: Break Open Your DAM With Intuitive Metadata

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Structure the Metadata Project

    The Purpose

    Develop a foundation of knowledge regarding DAM and metadata, as well as the best practices for organizing the organization’s information and digital assets for ideal findability.

    Key Benefits Achieved

    Design standardized processes for metadata creation and digital asset management to help to improve findability of key assets.

    Gain knowledge of how DAM can benefit both IT and the business.

    Activities

    1.1 Build a DAM and metadata knowledge foundation.

    1.2 Kick-start creation of the organization’s DAM design principles handbook.

    1.3 Interview key business units to understand drivers for the program.

    1.4 Develop a DAM framework.

    Outputs

    DAM Design Principles Handbook

    DAM Execution Strategy Document

    2 Assess Requirements for the DAM Program

    The Purpose

    Inventory the organization’s key digital assets and their repositories.

    Gather the organization’s requirements for a full-time digital asset librarian, as well as the DAM system.  

    Key Benefits Achieved

    Determine clear and specific requirements for the organization from the DAM system and the people involved.

    Activities

    2.1 Conduct a digital asset inventory to identify key assets to include in DAM.

    2.2 Prioritize digital assets to determine their risk and value to ensure appropriate support through the information lifecycle.

    2.3 Determine the requirements of the business and IT for the DAM system and its metadata.

    Outputs

    Digital Asset Inventory Tool

    DAM Requirements Gathering Tool

    3 Design Roadmap and Plan Implementation

    The Purpose

    Determine strategic initiatives and create a roadmap outlining key steps required to get the organization to start enabling data-driven insights.

    Determine timing of the initiatives. 

    Key Benefits Achieved

    Establish a clear direction for the DAM program.

    Build a step-by-step outline of how to create effective metadata with true business-IT collaboration.

    Have prioritized initiatives with dependencies mapped out.

    Activities

    3.1 Assess current and target states of DAM in the organization.

    3.2 Brainstorm and document practical initiatives to close the gap.

    3.3 Discuss strategies rooted in business requirements to execute the metadata management program to improve findability of digital assets.

    Outputs

    DAM Roadmap Tool

    4 Establish Metadata Governance

    The Purpose

    Identify the roles required for effective DAM and metadata management.

    Create sample metadata according to established guiding principles and implement a feedback method to create intuitive metadata in the organization. 

    Key Benefits Achieved

    Metadata management is an ongoing project. Implementing it requires user input and feedback, which governance will help to support.

    By integrating metadata governance with larger information or data governance bodies, DAM and metadata management will gain sustainability. 

    Activities

    4.1 Discuss and assign roles and responsibilities for initiatives identified in the roadmap.

    4.2 Review policy requirements for the information assets in the organization and strategies to address enforcement.

    4.3 Integrate the governance of metadata into larger governance committees.

    Outputs

    DAM Execution Strategy

    Configuration management

    • Buy Link or Shortcode: {j2store}4|cart{/j2store}
    • Related Products: {j2store}4|crosssells{/j2store}
    • Up-Sell: {j2store}4|upsells{/j2store}
    • Download01-Title: Harness the power of Configuration Management Executive Brief
    • Download-01: Visit Link
    • member rating overall impact: 8.0/10
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Infra and Operations
    • Parent Category Link: /infra-and-operations
    Configuration management is all about being able to manage your assets within the support processes. That means to record what you need. Not less than that, and not more either.

    Asset Management, Configuration Management, Lifecycle Management

    Sustain and Grow the Maturity of Innovation in Your Enterprise

    • Buy Link or Shortcode: {j2store}91|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Innovation
    • Parent Category Link: /innovation
    • Customers are not waiting – they are insisting on change now. The recent litany of business failures and the ongoing demand for improved services means that “not in my backyard” will mean no backyard.
    • Positive innovation is about achieving tomorrow’s success today, where everyone is a leader and ideas and people can flourish – in every sector.

    Our Advice

    Critical Insight

    • Many innovation programs are not delivering value at a time when change is constant and is impacting both public and private sector organizations.
    • Organizations are not well-positioned in terms of leadership skills to advance their innovation programs.
    • Unlock your innovation potential by looking at your innovation projects on both a macro and micro level.
    • Innovation capacity is directly linked with creativity; allow your employees' creativity to flourish using Info-Tech’s positive innovation techniques.
    • Innovations need to be re-harvested each year in order to maximize your return on investment.

    Impact and Result

    • From an opportunity perspective, create an effective innovation program that spawns more innovations, realizes benefits from existing assets not fully being leveraged, and lays the groundwork for enhanced products and services.
    • This complementary toolkit and method (to existing blueprints/research) guides you to assess the “aspiration level” of innovations and the innovation program, assess the resources/capabilities that an entity has to date employed in its innovation program, and position IT for success to achieve the strategic objectives of the enterprise.

    Sustain and Grow the Maturity of Innovation in Your Enterprise Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should formalize processes to improve your innovation program, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Scope and define

    Understand your current innovation capabilities and create a mandate for the future of your innovation program.

    • Sustain and Grow the Maturity of Innovation in Your Enterprise – Phase 1: Scope and Define
    • Innovation Program Mandate and Terms of Reference Template
    • Innovation Program Overview Presentation Template
    • Innovation Assessment Tool

    2. Assess and aspire

    Assess opportunities for your innovation program on a personnel and project level, and provide direction on how to improve along these dimensions.

    • Sustain and Grow the Maturity of Innovation in Your Enterprise – Phase 2: Assess and Aspire
    • Appreciative Inquiry Questionnaire

    3. Implement and inspire

    Formalize the innovation improvements you identified earlier in the blueprint by mapping them to your IT strategy.

    • Sustain and Grow the Maturity of Innovation in Your Enterprise – Phase 3: Implement and Inspire
    • Innovation Planning Tool
    [infographic]

    Workshop: Sustain and Grow the Maturity of Innovation in Your Enterprise

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Pre-Work

    The Purpose

    Gather data that will be analyzed in the workshop.

    Key Benefits Achieved

    Information gathered with which analysis can be performed.

    Activities

    1.1 Do an inventory of innovations/prototypes underway.

    1.2 High-level overview of all existing project charters, and documentation of innovation program.

    1.3 Poll working group or key stakeholders in regards to scope of innovation program.

    Outputs

    Up-to-date inventory of innovations/prototypes

    Document review of innovation program and its results to date

    Draft scope of the innovation program and understanding of the timelines

    2 Scope and Define

    The Purpose

    Scope the innovation program and gain buy-in from major stakeholders.

    Key Benefits Achieved

    Buy-in from IT steering committee for innovation program improvements.

    Activities

    2.1 Establish or re-affirm values for the program.

    2.2 Run an initial assessment of the organization’s innovation potential (macro level).

    2.3 Set/reaffirm scope and budget for the program.

    2.4 Define or refine goals and outcomes for the program.

    2.5 Confirm/re-confirm risk tolerance of organization.

    2.6 Update/document innovation program.

    2.7 Create presentation to gain support from the IT steering committee.

    Outputs

    Innovation program and terms of reference

    Presentation on organization innovation program for IT steering committee

    3 Assess and Aspire

    The Purpose

    Analyze the current performance of the innovation program and identify areas for improvement.

    Key Benefits Achieved

    Identify actionable items that can be undertaken in order to improve the performance of the innovation program.

    Activities

    3.1 Assess your level of innovation per innovation project (micro level).

    3.2 Update the risk tolerance level of the program.

    3.3 Determine if your blend of innovation projects is ideal.

    3.4 Re-prioritize your innovation projects (if needed).

    3.5 Plan update to IT steering committee.

    3.6 Assess positive innovation assessment of team.

    3.7 Opportunity analysis of innovation program and team.

    Outputs

    Positive innovation assessment

    Re-prioritized innovation projects

    Updated presentation for IT steering committee

    4 Implement and Inspire

    The Purpose

    Formalize the innovation program by tying it into the IT strategy.

    Key Benefits Achieved

    A formalized innovation program that is closely tied to the IT strategy.

    Activities

    4.1 Update business context in terms of impact on IT implications.

    4.2 Update IT strategy in terms of impact and benefits of innovation program.

    4.3 Update/create innovation program implementation plan.

    4.4 Plan update for IT steering committee.

    Outputs

    Updated business context

    Updated IT strategy

    Innovation implementation plan, including roadmap

    Updated presentation given to IT steering committee

    Build a Reporting and Analytics Strategy

    • Buy Link or Shortcode: {j2store}128|cart{/j2store}
    • member rating overall impact: 9.1/10 Overall Impact
    • member rating average dollars saved: $49,748 Average $ Saved
    • member rating average days saved: 28 Average Days Saved
    • Parent Category Name: Business Intelligence Strategy
    • Parent Category Link: /business-intelligence-strategy
    • In respect to business intelligence (BI) matureness, you can’t expect the whole organization to be at the same place at the same time. Your BI strategy needs to recognize this and should strive to align rather than dictate.
    • Technology is just one aspect of your BI and analytics strategy and is not a quick solution or a guarantee for long-term success.

    Our Advice

    Critical Insight

    • The BI strategy drives data warehouse and integration strategies and the data needed to support business decisions.
    • The solution to better BI often lies in improving the BI practice, not acquiring the latest and greatest tool.

    Impact and Result

    • Align BI with corporate vision, mission, goals, and strategic direction.
    • Understand the needs of business partners.
    • BI & analytics informs data warehouse and integration layers for required content, latency, and quality.

    Build a Reporting and Analytics Strategy Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should create or refresh the BI Strategy and review Info-Tech’s approach to developing a BI strategy that meets business needs.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Understand the business context and BI landscape

    Lay the foundation for the BI strategy by detailing key business information and analyzing current BI usage.

    • Build a Reporting and Analytics Strategy – Phase 1: Understand the Business Context and BI Landscape
    • BI Strategy and Roadmap Template
    • BI End-User Satisfaction Survey Framework

    2. Evaluate the current BI practice

    Assess the maturity level of the current BI practice and envision a future state.

    • Build a Reporting and Analytics Strategy – Phase 2: Evaluate the Current BI Practice
    • BI Practice Assessment Tool

    3. Create a BI roadmap for continuous improvement

    Create BI-focused initiatives to build an improvement roadmap.

    • Build a Reporting and Analytics Strategy – Phase 3: Create a BI Roadmap for Continuous Improvement
    • BI Initiatives and Roadmap Tool
    • BI Strategy and Roadmap Executive Presentation Template
    [infographic]

    Workshop: Build a Reporting and Analytics Strategy

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Establish Business Vision and Understand the Current BI Landscape

    The Purpose

    Document overall business vision, mission, and key objectives; assemble project team.

    Collect in-depth information around current BI usage and BI user perception.

    Create requirements gathering principles and gather requirements for a BI platform.

    Key Benefits Achieved

    Increased IT–business alignment by using the business context as the project starting point

    Identified project sponsor and project team

    Detailed understanding of trends in BI usage and BI perception of consumers

    Refreshed requirements for a BI solution

    Activities

    1.1 Gather key business information (overall mission, goals, objectives, drivers).

    1.2 Establish a high-level ROI.

    1.3 Identify ideal candidates for carrying out a BI project.

    1.4 Undertake BI usage analyses, BI user perception survey, and a BI artifact inventory.

    1.5 Develop requirements gathering principles and approaches.

    1.6 Gather and organize BI requirements

    Outputs

    Articulated business context that will guide BI strategy development

    ROI for refreshing the BI strategy

    BI project team

    Comprehensive summary of current BI usage that has quantitative and qualitative perspectives

    BI requirements are confirmed

    2 Evaluate Current BI Maturity and Identify the BI Patterns for the Future State

    The Purpose

    Define current maturity level of BI practice.

    Envision the future state of your BI practice and identify desired BI patterns.

    Key Benefits Achieved

    Know the correct migration method for Exchange Online.

    Prepare user profiles for the rest of the Office 365 implementation.

    Activities

    2.1 Perform BI SWOT analyses.

    2.2 Assess current state of the BI practice and review results.

    2.3 Create guiding principles for the future BI practice.

    2.4 Identify desired BI patterns and the associated BI functionalities/requirements.

    2.5 Define the future state of the BI practice.

    2.6 Establish the critical success factors for the future BI, identify potential risks, and create a mitigation plan.

    Outputs

    Exchange migration strategy

    Current state of BI practice is documented from multiple perspectives

    Guiding principles for future BI practice are established, along with the desired BI patterns linked to functional requirements

    Future BI practice is defined

    Critical success factors, potential risks, and a risk mitigation plan are defined

    3 Build Improvement Initiatives and Create a BI Development Roadmap

    The Purpose

    Build overall BI improvement initiatives and create a BI improvement roadmap.

    Identify supplementary initiatives for enhancing your BI program.

    Key Benefits Achieved

    Defined roadmap composed of robust improvement initiatives

    Activities

    3.1 Create BI improvement initiatives based on outputs from phase 1 and 2 activities. Build an improvement roadmap.

    3.2 Build an improvement roadmap.

    3.3 Create an Excel governance policy.

    3.4 Create a plan for a BI ambassador network.

    Outputs

    Comprehensive BI initiatives placed on an improvement roadmap

    Excel governance policy is created

    Internal BI ambassadors are identified

    Further reading

    Build a Reporting and Analytics Strategy

    Deliver actionable business insights by creating a business-aligned reporting and analytics strategy.

    Terminology

    As the reporting and analytics space matured over the last decade, software suppliers used different terminology to differentiate their products from others’. This caused a great deal of confusion within the business communities.

    Following are two definitions of the term Business Intelligence:

    Business intelligence (BI) leverages software and services to transform data into actionable insights that inform an organization’s strategic and tactical business decisions. BI tools access and analyze data sets and present analytical findings in reports, summaries, dashboards, graphs, charts, and maps to provide users with detailed intelligence about the state of the business.

    The term business intelligence often also refers to a range of tools that provide quick, easy-to-digest access to insights about an organization's current state, based on available data.

    CIO Magazine

    Business intelligence (BI) comprises the strategies and technologies used by enterprises for the data analysis of business information. BI technologies provide historical, current, and predictive views of business operations.

    Common functions of business intelligence technologies include reporting, online analytical processing, analytics, data mining, process mining, complex event processing, business performance management, benchmarking, text mining, predictive analytics, and prescriptive analytics.

    Wikipedia

    This blueprint will use the terms “BI,” “BI and Analytics,” and “Reporting and Analytics” interchangeably in different contexts, but always in compliance to the above definitions.

    ANALYST PERSPECTIVE

    A fresh analytics & reporting strategy enables new BI opportunities.

    We need data to inform the business of past and current performance and to support strategic decisions. But we can also drown in a flood of data. Without a clear strategy for business intelligence, a promising new solution will produce only noise.

    BI and Analytics teams must provide the right quantitative and qualitative insights for the business to base their decisions on.

    Your Business Intelligence and Analytics strategy must support the organization’s strategy. Your strategy for BI & Analytics provides direction and requirements for data warehousing and data integration, and further paves the way for predictive analytics, big data analytics, market/industry intelligence, and social network analytics.

    Dirk Coetsee,

    Director, Data and Analytics Info-Tech Research Group

    Our understanding of the problem

    This Research is Designed For:

    • A CIO or Business Unit (BU) Leader looking to improve reporting and analytics, reduce time to information, and embrace fact-based decision making with analytics, reporting, and business intelligence (BI).
    • Application Directors experiencing poor results from an initial BI tool deployment who are looking to improve the outcome.

    This Research Will Also Assist:

    • Project Managers and Business Analysts assigned to a BI project team to collect and analyze requirements.
    • Business units that have their own BI platforms and would like to partner with IT to take their BI to an enterprise level.

    This Research Will Help You:

    • Align your reporting and analytics strategy with the business’ strategic objectives before you rebuild or buy your Business Intelligence platform.
    • Identify reporting and analytics objectives to inform the data warehouse and integration requirements gathering process.
    • Avoid common pitfalls that derail BI and analytic deployments and lower their adoption.
    • Identify Business Intelligence gaps prior to deployment and incorporate remedies within your plans.

    This Research Will Help Them:

    • Recruit the right resources for the program.
    • Align BI with corporate vision, mission, goals, and strategic direction.
    • Understand the needs of business partners.
    • Assess BI maturity and plan for target state.
    • Develop a BI strategy and roadmap.
    • Track the success of the BI initiative.

    Executive summary

    Situation:

    BI drives a new reality. Uber is the world’s largest taxi company and they own no vehicles; Alibaba is the world’s most valuable retailer and they have no inventory; Airbnb is the world’s largest accommodation provider and they own no real estate. How did they disrupt their markets and get past business entry barriers? A deep understanding of their market through impeccable business intelligence!

    Complication:

    • In respect to BI matureness, you can’t expect the whole organization to be at the same place at the same time. Your BI strategy needs to recognize this and should strive to align rather than dictate.
    • Technology is just one aspect of your BI and Analytics strategy and is not a quick solution or a guarantee for long term success.

    Resolution:

    • Drive strategy development by establishing the business context upfront in order to align business intelligence providers with the most important needs of their BI consumers and the strategic priorities of the organization.
    • Revamp or create a BI strategy to update your BI program to make it fit for purpose.
    • Understand your existing BI baggage – e.g. your existing BI program, the artifacts generated from the program, and the users it supports. Those will inform the creation of the strategy and roadmap.
    • Assess current BI maturity and determine your future state BI maturity.
    • BI needs governance to ensure consistent planning, communication, and execution of the BI strategy.
    • Create a network of BI ambassadors across the organization to promote BI.
    • Plan for the future to ensure that required data will be available when the organization needs it.

    Info-Tech Insight

    1. Put the “B” back in BI. Don’t have IT doing BI for IT’s sake; ensure the voice and needs of the business are the primary drivers of your strategy.
    2. The BI strategy drives data warehouse and integration strategies and the data needs to support business decisions.
    3. Go beyond the platform. The solution to better BI often lies in improving the BI practice, not acquiring the latest and greatest tool.

    Metrics to track BI & Analytical program progress

    Goals for BI:

    • Understand business context and needs. Identify business processes that can leverage BI.
    • Define the Reporting & Analytics Roadmap. Develop data initiatives, and create a strategy and roadmap for Business Intelligence.
    • Continuous improvements. Your BI program is evolving and improving over time. The program should allow you to have faster, better, and more comprehensive information.

    Info-Tech’s Suggested Metrics for Tracking the BI Program

    Practice Improvement Metrics Data Collection and Calculation Expected Improvement
    Program Level Metrics Efficiency
    • Time to information
    • Self-service penetration
    • Derive from the ticket management system
    • Derive from the BI platform
    • 10% reduction in time to information
    • Achieve 10-15% self-service penetration
    • Effectiveness
    • BI Usage
    • Data quality
    • Derive from the BI platform
    • Data quality perception
    • Majority of the users use BI on a daily basis
    • 15% increase in data quality perception
    Comprehensiveness
    • # of integrated datasets
    • # of strategic decisions made
    • Derive from the data integration platform
    • Decision-making perception
    • Onboard 2-3 new data domains per year
    • 20% increase in decision-making perception

    Intangible Metrics:

    Tap into the results of Info-Tech’s CIO Business Vision diagnostic to monitor the changes in business-user satisfaction as you implement the initiatives in your BI improvement roadmap.

    Your Enterprise BI and Analytics Strategy is driven by your organization’s Vision and Corporate Strategy

    Formulating an Enterprise Reporting and Analytics Strategy requires the business vision and strategies to first be substantiated. Any optimization to the Data Warehouse, Integration and Source layer is in turn driven by the Enterprise Reporting and Analytics Strategy
    Flow chart showing 'Business Vision Strategies'

    The current state of your Integration and Warehouse platforms determine what data can be utilized for BI and Analytics

    Where we are, and how we got here

    How we got here

    • In the beginning was BI 1.0. Business intelligence began as an IT-driven centralized solution that was highly governed. Business users were typically the consumers of reports and dashboards created by IT, an analytics-trained minority, upon request.
    • In the last five to ten years, we have seen a fundamental shift in the business intelligence and analytics market, moving away from such large-scale, centralized IT-driven solutions focused on basic reporting and administration, towards more advanced user-friendly data discovery and visualization platforms. This has come to be known as BI 2.0.
    • Many incumbent market leaders were disrupted by the demand for more user-friendly business intelligence solutions, allowing “pure-play” BI software vendors to carve out a niche and rapidly expand into more enterprise environments.
    • BI-on-the-cloud has established itself as a solid alternative to in-house implementation and operation.

    Where we are now

    • BI 3.0 has arrived. This involves the democratization of data and analytics and a predominantly app-centric approach to BI, identifiable by an anywhere, anytime, and device-or-platform-independent collaborative methodology. Social workgroups and self-guided content creation, delivery, analysis, and management is prominent.
    • Where the need for reporting and dashboards remains, we’re seeing data discovery platforms fulfilling the needs of non-technical business users by providing easy-to-use interactive solutions to increase adoption across enterprises.
    • With more end users demanding access to data and the tools to extract business insights, IT is looking to meet these needs while continuing to maintain governance and administration over a much larger base of users. The race for governed data discovery is heated and will be a market differentiator.
    • The next kid on the block is Artificial Intelligence that put further demands on data quality and availability.

    RICOH Canada used this methodology to develop their BI strategy in consultation with their business stakeholders

    CASE STUDY

    Industry: Manufacturing and Retail

    Source: RICOH

    Ricoh Canada transforms the way people work with breakthrough technologies that help businesses innovate and grow. Its focus has always been to envision what the future will look like so that it can help its customers prepare for success. Ricoh empowers digital workplaces with a broad portfolio of services, solutions, and technologies – helping customers remove obstacles to sustained growth by optimizing the flow of information and automating antiquated processes to increase workplace productivity. In their commitment towards a customer-centric approach, Ricoh Canada recognized that BI and analytics can be used to inform business leaders in making strategic decisions.

    Enterprise BI and analytics Initiative

    Ricoh Canada enrolled in the ITRG Reporting & Analytics strategy workshop with the aim to create a BI strategy that will allow the business to harvest it strengths and build for the future. The workshop acted as a forum for the different business units to communicate, share ideas, and hear from each other what their pains are and what should be done to provide a full customer 360 view.

    Results

    “This workshop allowed us to collectively identify the various stakeholders and their unique requirements. This is a key factor in the development of an effective BI Analytics tool.” David Farrar

    The Customer 360 Initiative included the following components
    The Customer 360 Initiative includes the components shown in the image

    Improve BI Adoption Rates

    Graph showing Product Adoption Rates

    Sisense

    Reasons for low BI adoption

    • Employees that never used BI tools are slow to adopt new technology.
    • Lack of trust in data leads to lack of trust in the insights.
    • Complex data structures deter usage due to long learning curves and contained nuances.
    • Difficult to translate business requirements into tool linguistics due to lack of training or technical ineptness.
    • Business has not taken ownership of data, which affects access to data.

    How to foster BI adoption

    • Senior management proclaim data as a strategic asset and involved in the promotion of BI
    • Role Requirement that any business decision should be backed up by analytics
    • Communication of internal BI use case studies and successes
    • Exceptional data lineage to act as proof for the numbers
    • A Business Data glossary with clearly defined business terms. Use the Business Data Glossary in conjunction with data lineage and semantic layers to ensure that businesses are clearly defined and traced to sources.
    • Training in business to take ownership of data from inception to analytics.

    Why bother with analytics?

    In today’s ever-changing and global environment, organizations of every size need to effectively leverage their data assets to facilitate three key business drivers: customer intimacy, product/service innovation, and operational excellence. Plus, they need to manage their operational risk efficiently.

    Investing in a comprehensive business intelligence strategy allows for a multidimensional view of your organization’s data assets that can be operationalized to create a competitive edge:

    Historical Data

    Without a BI strategy, creating meaningful reports for business users that highlight trends in past performance and draw relationships between different data sources becomes a more complex task. Also, the ever growing need to identify and assess risks in new ways is driving many companies to BI.

    Data Democracy

    The core purpose of BI is to provide the right data, to the right users, at the right time, and in a format that is easily consumable and actionable. In developing a BI strategy, remember the driver for managed cross-functional access to data assets and features such as interactive dashboards, mobile BI, and self-service BI.

    Predictive and Big Data Analytics

    As the volume, variety, and velocity of data increases rapidly, businesses will need a strategy to outline how they plan to consume the new data in a manner that does not overwhelm their current capabilities and aligns with their desired future state. This same strategy further provides a foundation upon which organizations can transition from ad hoc reporting to using data assets in a codified BI platform for decision support.

    Business intelligence serves as the layer that translates data, information, and organizational knowledge into insights

    As executive decision making shifts to more fact-based, data-driven thinking, there is an urgent need for data assets to be organized and presented in a manner that enables immediate action.

    Typically, business decisions are based on a mix of intuition, opinion, emotion, organizational culture, and data. Though business users may be aware of its potential value in driving operational change, data is often viewed as inaccessible.

    Business intelligence bridges the gap between an organization’s data assets and consumable information that facilitates insight generation and informed decision making.

    Most organizations realize that they need a BI strategy; it’s no longer a nice-to-have, it’s a must-have.

    – Albert Hui, Principal, Data Economist
    A triangle grapg depicting the layers of business itelligence

    Business intelligence and business analytics: what is the difference and should you care

    Ask 100 people and you will get 100 answers. We like the prevailing view that BI looks at today and backward for improving who we are, while BA is forward-looking to support change decisions.
    The image depicts a chart flowing from Time Past to Future. Business Intelligence joins with Business Analytics over the Present
    • Business intelligence is concerned with looking at present and historical data.
    • Use this data to create reports/dashboards to inform a wide variety of information consumers of the past and current state of affairs.
    • Almost all organizations, regardless of size and maturity, use some level of BI even if it’s just very basic reporting.
    • Business analytics, on the other hand, is a forward-facing use of data, concerned with the present to the future.
    • Analytics uses data to both describe the present, and more importantly, predict the future, enabling strategic business decisions.
    • Although adoption is rapidly increasing, many organizations still do not utilize any advanced analytics in their environment.

    However, establishing a strong business intelligence program is a necessary precursor to an organization’s development of its business analytics capabilities.

    Organizations that successfully grow their BI capabilities are reaping the rewards

    Evidence is piling up: if planned well, BI contributes to the organization’s bottom line.

    It’s expected that there will be nearly 45 billion connected devices and a 42% increase in data volume each year posing a high business opportunity for the BI market (BERoE, 2020).

    The global business intelligence market size to grow from US$23.1 billion in 2020 to US$33.3 billion by 2025, at a compound annual growth rate (CAGR) of 7.6% (Global News Wire, 2020)

    In the coming years, 69% of companies plan on increasing their cloud business intelligence usage (BARC Research and Eckerson Group Study, 2017).

    Call to Action

    Small organizations of up to 100 employees had the highest rate of business intelligence penetration last year (Forbes, 2018).
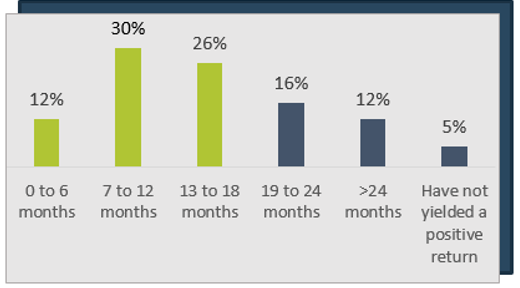
    Graph depicting business value from 0 months to more than 24 months

    Source: IBM Business Value, 2015

    For the New England Patriots, establishing a greater level of customer intimacy was driven by a tactical analytics initiative

    CASE STUDY

    Industry: Professional Sports

    Source Target Marketing

    Problem

    Despite continued success as a franchise with a loyal fan base, the New England Patriots experienced one of their lowest season ticket renewal rates in over a decade for the 2009 season. Given the numerous email addresses that potential and current season-ticket holders used to engage with the organization, it was difficult for Kraft Sports Group to define how to effectively reach customers.

    Turning to a Tactical Analytics Approach

    Kraft Sports Group turned to the customer data that it had been collecting since 2007 and chose to leverage analytics in order to glean insight into season ticket holder behavior. By monitoring and reporting on customer activity online and in attendance at games, Kraft Sports Group was able to establish that customer engagement improved when communication from the organization was specifically tailored to customer preferences and historical behavior.

    Results

    By operationalizing their data assets with the help of analytics, the Patriots were able to achieve a record 97% renewal rate for the 2010 season. KSG was able to take their customer engagement to the next level and proactively look for signs of attrition in season-ticket renewals.

    We're very analytically focused and I consider us to be the voice of the customer within the organization… Ultimately, we should know when renewal might not happen and be able to market and communicate to change that behavior.

    – Jessica Gelman,

    VP Customer Marketing and Strategy, Kraft Sports Group

    A large percentage of all BI projects fail to meet the organization’s needs; avoid falling victim to common pitfalls

    Tool Usage Pitfalls

    • Business units are overwhelmed with the amount and type of data presented.
    • Poor data quality erodes trust, resulting in a decline in usage.
    • Analysis performed for the sake of analysis and doesn’t focus on obtaining relevant business-driven insights.

    Selection Pitfalls

    • Inadequate requirements gathering.
    • No business involvement in the selection process.
    • User experience is not considered.
    • Focus is on license fees and not total cost.

    Implementation Pitfalls

    • Absence of upfront planning
    • Lack of change management to facilitate adoption of the new platform
    • No quick wins that establish the value of the project early on
    • Inadequate initial or ongoing training

    Strategic Pitfalls

    • Poor alignment of BI goals with organization goals
    • Absence of CSFs/KPIs that can measure the qualitative and quantitative success of the project
    • No executive support during or after the project

    BI pitfalls are lurking around every corner, but a comprehensive strategy drafted upfront can help your organization overcome these obstacles. Info-Tech’s approach to BI has involvement from the business units built right into the process from the start and it equips IT to interact with key stakeholders early and often.

    Only 62% of Big Data and AI projects in 2019 provided measurable results.

    Source: NewVantage Partners LLC

    Business and IT have different priorities for a BI tool

    Business executives look for:

    • Ease of use
    • Speed and agility
    • Clear and concise information
    • Sustainability

    IT professionals are concerned about:

    • Solid security
    • Access controls on data
    • Compliance with regulations
    • Ease of integration

    Info-Tech Insight

    Combining these priorities will lead to better tool selection and more synergy.

    Elizabeth Mazenko

    The top-down BI Opportunity Analysis is a tool for senior executives to discover where Business Intelligence can provide value
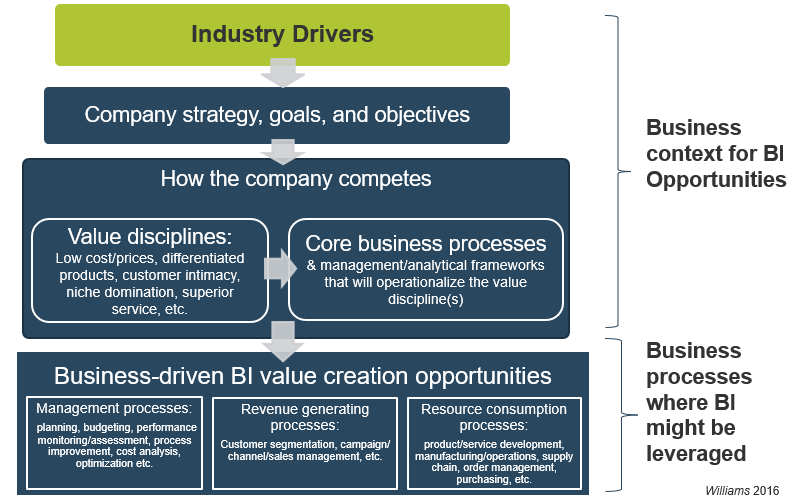
    The image is of a top-down BI Opportunity Analysis.

    Example: Uncover BI opportunities with an opportunity analysis

    Industry Drivers Private label Rising input prices Retail consolidation
    Company strategies Win at supply chain execution Win at customer service Expand gross margins
    Value disciplines Strategic cost management Operational excellence Customer service
    Core processes Purchasing Inbound logistics Sales, service & distribution
    Enterprise management: Planning, budgeting, control, process improvement, HR
    BI Opportunities Customer service analysis Cost and financial analysis Demand management

    Williams (2016)

    Bridge the gap between business drivers and business intelligence features with a three-tiered framework

    Info-Tech’s approach to formulating a fit-for-purpose BI strategy is focused on making the link between factors that are the most important to the business users and the ways that BI providers can enable those consumers.

    Drivers to Establish Competitive Advantage

    • Operational Excellence
    • Client Intimacy
    • Innovation

    BI and Analytics Spectrum

    • Strategic Analytics
    • Tactical Analytics
    • Operational Analytics

    Info-Tech’s BI Patterns

    • Delivery
    • User Experience
    • Deep Analytics
    • Supporting

    This is the content for Layout H3 Tag

    Though business intelligence is primarily thought of as enabling executives, a comprehensive BI strategy involves a spectrum of analytics that can provide data-driven insight to all levels of an organization.

    Recommended

    Strategic Analytics

    • Typically focused on predictive modeling
    • Leverages data integrated from multiple sources (structured through unstructured)
    • Assists in identifying trends that may shift organizational focus and direction
    • Sample objectives:
      • Drive market share growth
      • Identify new markets, products, services, locations, and acquisitions
      • Build wider and deeper customer relationships earning more wallet share and keeping more customers

    Tactical Analytics

    • Often considered Response Analytics and used to react to situations that arise, or opportunities at a department level.
    • Sample objectives:
      • Staff productivity or cost analysis
      • Heuristics/algorithms for better risk management
      • Product bundling and packaging
      • Customer satisfaction response techniques

    Operational Analytics

    • Analytics that drive business process improvement whether internal, with external partners, or customers.
    • Sample objectives:
      • Process step elimination
      • Best opportunities for automation

    Business Intelligence Terminology

    Styles of BI New age BI New age data Functional Analytics Tools
    Reporting Agile BI Social Media data Performance management analytics Scorecarding dashboarding
    Ad hoc query SaaS BI Unstructured data Financial analytics Query & reporting
    Parameterized queries Pervasive BI Mobile data Supply chain analytics Statistics & data mining
    OLAP Cognitive Business Big data Customer analytics OLAP cubes
    Advanced analytics Self service analytics Sensor data Operations analytics ETL
    Cognitive business techniques Real-time Analytics Machine data HR Analytics Master data management
    Scorecards & dashboards Mobile Reporting & Analytics “fill in the blanks” analytics Data Governance

    Williams (2016)

    "BI can be confusing and overwhelming…"

    – Dirk Coetsee,

    Research Director,

    Info-Tech Research Group

    Business intelligence lies in the Information Dimensions layer of Info-Tech’s Data Management Framework

    The interactions between the information dimensions and overlying data management enablers such as data governance, data architecture, and data quality underscore the importance of building a robust process surrounding the other data practices in order to fully leverage your BI platform.

    Within this framework BI and analytics are grouped as one lens through which data assets at the business information level can be viewed.
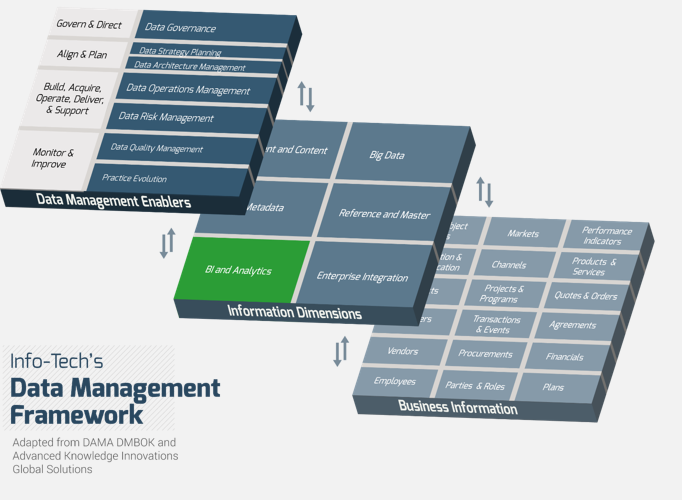
    The image is the Information Dimensions layer of Info-Tech’s Data Management Framework

    Use Info-Tech’s three-phase approach to a Reporting & Analytics strategy and roadmap development

    Project Insight

    A BI program is not a static project that is created once and remains unchanged. Your strategy must be treated as a living platform to be revisited and revitalized in order to effectively enable business decision making. Develop a reporting and analytics strategy that propels your organization by building it on business goals and objectives, as well as comprehensive assessments that quantitatively and qualitatively evaluate your current reporting and analytical capabilities.

    Phase 1: Understand the Business Context and BI Landscape Phase 2: Evaluate Your Current BI Practice Phase 3: Create a BI Roadmap for Continuous Improvement
    1.1 Establish the Business Context
    • Business Vision, Goals, Key Drivers
    • Business Case Presentation
    • High-Level ROI
    2.1 Assess Your Current BI Maturity
    • BI Practice Assessment
    • Summary of Current State
    3.1 Construct a BI Initiative Roadmap
    • BI Improvement Initiatives
    • RACI
    • BI Strategy and Roadmap
    1.2 Assess Existing BI Environment
    • BI Perception Survey Framework
    • Usage Analyses
    • BI Report Inventory
    2.2 Envision BI Future State
    • BI Style Requirements
    • BI Practice Assessment
    3.2 Plan for Continuous Improvement
    • Excel/Access Governance Policy
    • BI Ambassador Network Draft
    1.3 Develop BI Solution Requirements
    • Requirements Gathering Principles
    • Overall BI Requirements

    Stand on the shoulders of Information Management giants

    As part of our research process, we leveraged the frameworks of COBIT5, Mike 2.0, and DAMA DMBOK2. Contextualizing business intelligence within these frameworks clarifies its importance and role and ensures that our assessment tool is focused on key priority areas.

    The DMBOK2 Data Management framework by the Data Asset Management Association (DAMA) provided a starting point for our classification of the components in our IM framework.

    Mike 2.0 is a data management framework that helped guide the development of our framework through its core solutions and composite solutions.

    The Cobit 5 framework and its business enablers were used as a starting point for assessing the performance capabilities of the different components of information management, including business intelligence.

    Info-Tech has a series of deliverables to facilitate the evolution of your BI strategy

    BI Strategy Roadmap Template

    BI Practice Assessment Tool

    BI Initiatives and Roadmap Tool

    BI Strategy and Roadmap Executive Presentation Template

    Info-Tech offers various levels of support to best suit your needs

    DIY Toolkit Guided Implementation Workshop Consulting
    “Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful.” “Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track.” “We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place.” “Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project.”

    Diagnostics and consistent frameworks used throughout all four options

    Build a Reporting and Analytics Strategy – Project Overview

    1. Understand the Business Context and BI Landscape 2. Evaluate the Current BI Practice 3. Create a BI Roadmap for Continuous Improvement
    Best-Practice Toolkit

    1.1 Document overall business vision, mission, industry drivers, and key objectives; assemble a project team

    1.2 Collect in-depth information around current BI usage and BI user perception

    1.3 Create requirements gathering principles and gather requirements for a BI platform

    2.1 Define current maturity level of BI practice

    2.2 Envision the future state of your BI practice and identify desired BI patterns

    3.1 Build overall BI improvement initiatives and create a BI improvement roadmap

    3.2 Identify supplementary initiatives for enhancing your BI program

    Guided Implementations
    • Discuss Info-Tech’s approach for using business information to drive BI strategy formation
    • Review business context and discuss approaches for conducting BI usage and user analyses
    • Discuss strategies for BI requirements gathering
    • Discuss BI maturity model
    • Review practice capability gaps and discuss potential BI patterns for future state
    • Discuss initiative building
    • Review completed roadmap and next steps
    Onsite Workshop Module 1:

    Establish Business Vision and Understand the Current BI Landscape

    Module 2:

    Evaluate Current BI Maturity Identify the BI Patterns for the Future State

    Module 3:

    Build Improvement Initiatives and Create a BI Development Roadmap

    Phase 1 Outcome:
    • Business context
    • Project team
    • BI usage information, user perception, and new BI requirements
    Phase 2 Outcome:
    • Current and future state assessment
    • Identified BI patterns
    Phase 3 Outcome:
    • BI improvement strategy and initiative roadmap

    Workshop overview

    Contact your account representative or email Workshops@InfoTech.com for more information.

    Workshop Day 1 Workshop Day 2 Workshop Day 3 Workshop Day 4
    Activities

    Understand Business Context and Structure the Project

    1.1 Make the case for a BI strategy refresh.

    1.2 Understand business context.

    1.3 Determine high-level ROI.

    1.4 Structure the BI strategy refresh project.

    Understand Existing BI and Revisit Requirements

    2.1 Understand the usage of your existing BI.

    2.2 Gather perception of the current BI users.

    2.3 Document existing information artifacts.

    2.4 Develop a requirements gathering framework.

    2.5 Gather requirements.

    Revisit Requirements and Current Practice Assessment

    3.1 Gather requirements.

    3.2 Determine BI Maturity Level.

    3.3 Perform a SWOT for your existing BI program.

    3.4 Develop a current state summary.

    Roadmap Develop and Plan for Continuous Improvements

    5.1 Develop BI strategy.

    5.2 Develop a roadmap for the strategy.

    5.3 Plan for continuous improvement opportunities.

    5.4 Develop a re-strategy plan.

    Deliverables
    1. Business and BI Vision, Goals, Key Drivers
    2. Business Case Presentation
    3. High-Level ROI
    4. Project RACI
    1. BI Perception Survey
    2. BI Requirements Gathering Framework
    3. BI User Stories and Requirements
    1. BI User Stories and Requirements
    2. BI SWOT for your Current BI Program
    3. BI Maturity Level
    4. Current State Summary
    1. BI Strategy
    2. Roadmap accompanying the strategy with timeline
    3. A plan for improving BI
    4. Strategy plan

    Phase 2

    Understand the Business Context and BI Landscape

    Build a Reporting and Analytics Strategy

    Phase 1 overview

    Detailed Overview

    Step 1: Establish the business context in terms of business vision, mission, objectives, industry drivers, and business processes that can leverage Business Intelligence

    Step 2: Understand your BI Landscape

    Step 3: Understand business needs

    Outcomes

    • Clearly articulated high-level mission, vision, and key drivers from the business, as well as objectives related to business intelligence.
    • In-depth documentation regarding your organization’s BI usage, user perception, and outputs.
    • Consolidated list of requirements, existing and desired, that will direct the deployment of your BI solution.

    Benefits

    • Align business context and drivers with IT plans for BI and Analytics improvement.
    • Understand your current BI ecosystem’s performance.

    Understand your business context and BI landscape

    Phase 1 Overarching Insight

    The closer you align your new BI platform to real business interests, the stronger the buy-in, realized value, and groundswell of enthusiastic adoption will be. Get this phase right to realize a high ROI on your investment in the people, processes, and technology that will be your next generation BI platform.

    Understand the Business Context to Rationalize Your BI Landscape Evaluate Your Current BI Practice Create a BI Roadmap for Continuous Improvement
    Establish the Business Context
    • Business Vision, Goals, Key Drivers
    • Business Case Presentation
    • High-Level ROI
    Assess Your Current BI Maturity
    • SWOT Analysis
    • BI Practice Assessment
    • Summary of Current State
    Construct a BI Initiative Roadmap
    • BI Improvement Initiatives
    • BI Strategy and Roadmap
    Access Existing BI Environment
    • BI Perception Survey Framework
    • Usage Analyses
    • BI Report Inventory
    Envision BI Future State
    • BI Patterns
    • BI Practice Assessment
    • List of Functions
    Plan for Continuous Improvement
    • Excel Governance Policy
    • BI Ambassador Network Draft
    Undergo Requirements Gathering
    • Requirements Gathering Principles
    • Overall BI Requirements

    Track these metrics to measure your progress through Phase 1

    Goals for Phase 1:

    • Understand the business context. Determine if BI can be used to improve business outcomes by identifying benefits, costs, opportunities, and gaps.
    • Understand your existing BI. Plan your next generation BI based on a solid understanding of your existing BI.
    • Identify business needs. Determine the business processes that can leverage BI and Analytics.

    Info-Tech’s Suggested Metrics for Tracking Phase 1 Goals

    Practice Improvement Metrics Data Collection and Calculation Expected Improvement
    Monetary ROI
    • Quality of the ROI
    • # of user cases, benefits, and costs quantified
    Derive the number of the use cases, benefits, and costs in the scoping. Ask business SMEs to verify the quality. High-quality ROI studies are created for at least three use cases
    Response Rate of the BI Perception Survey Sourced from your survey delivery system Aim for 40% response rate
    # of BI Reworks Sourced from your project management system Reduction of 10% in BI reworks

    Intangible Metrics:

    1. Executives’ understanding of the BI program and what BI can do for the organization.
    2. Improved trust between IT and the business by re-opening the dialogue.
    3. Closer alignment with the organization strategy and business plan leading to higher value delivered.
    4. Increased business engagement and input into the Analytics strategy.

    Use advisory support to accelerate your completion of Phase 1 activities

    Call 1-888-670-8889 or email GuidedImplementations@InfoTech.com for more information.

    Complete these steps on your own, or call us to complete a guided implementation. A guided implementation is a series of two to three advisory calls that help you execute each phase of a project. They are included in most advisory memberships.

    Guided Implementation 1: Understand the Business Context and BI Landscape

    Proposed Time to Completion: 2-4 weeks

    Step 1.0: Assemble Your Project Team

    Start with an analyst kick-off call:

    • Discuss Info-Tech’s viewpoint and definitions of business intelligence.
    • Discuss the project sponsorship, ideal team members and compositions.

    Then complete these activities…

    • Identify a project sponsor and the project team members.

    Step 1.1: Understand Your Business Context

    Start with an analyst kick-off call:

    • Discuss Info-Tech’s approach to BI strategy development around using business information as the key driver.

    Then complete these activities…

    • Detail the business context (vision, mission, goals, objectives, etc.).
    • Establish business–IT alignment for your BI strategy by detailing the business context.

    Step 1.2: Establish the Current BI Landscape

    Review findings with analyst:

    • Review the business context outputs from Step 1.1 activities.
    • Review Info-Tech’s approach for documenting your current BI landscape.
    • Review the findings of your BI landscape.

    Then complete these activities…

    • Gather information on current BI usage and perform a BI artifact inventory.
    • Construct and conduct a user perception survey.

    With these tools & templates:

    BI Strategy and Roadmap Template

    Step 1.0

    Assemble the Project Team

    Select a BI project sponsor

    Info-Tech recommends you select a senior executive with close ties to BI be the sponsor for this project (e.g. CDO, CFO or CMO). To maximize the chance of success, Info-Tech recommends you start with the CDO, CMO, CFO, or a business unit (BU) leader who represents strategic enterprise portfolios.

    Initial Sponsor

    CFO or Chief Risk Officer (CRO)

    • The CFO is responsible for key business metrics and cost control. BI is on the CFO’s radar as it can be used for both cost optimization and elimination of low-value activity costs.
    • The CRO is tasked with the need to identify, address, and when possible, exploit risk for business security and benefit.
    • Both of these roles are good initial sponsors but aren’t ideal for the long term.

    CDO or a Business Unit (BU) Leader

    • The CDO (Chief Data Officer) is responsible for enterprise-wide governance and utilization of information as an asset via data processing, analysis, data mining, information trading, and other means, and is the ideal sponsor.
    • BU leaders who represent a growth engine for a company look for ways to mine BI to help set direction.

    Ultimate Sponsor

    CEO

    • As a the primary driver of enterprise-wide strategy, the CEO is the ideal evangelist and project sponsor for your BI strategy.
    • Establishing a CEO–CIO partnership helps elevate IT to the level of a strategic partner, as opposed to the traditional view that IT’s only job is to “keep the lights on.”
    • An endorsement from the CEO may make other C-level executives more inclined to work with IT and have their business unit be the starting point for growing a BI program organically.

    "In the energy sector, achieving production KPIs are the key to financial success. The CFO is motivated to work with IT to create BI applications that drive higher revenue, identify operational bottlenecks, and maintain gross margin."

    – Yogi Schulz, Partner, Corvelle Consulting

    Select a BI project team

    Create a project team with the right skills, experience, and perspectives to develop a comprehensive strategy aligned to business needs.

    You may need to involve external experts as well as individuals within the organization who have the needed skills.

    A detailed understanding of what to look for in potential candidates is essential before moving forward with your BI project.

    Leverage several of Info-Tech’s Job Description Templates to aid in the process of selecting the right people to involve in constructing your BI strategy.

    Roles to Consider

    Business Stakeholders

    Business Intelligence Specialist

    Business Analyst

    Data Mining Specialist

    Data Warehouse Architect

    Enterprise Data Architect

    Data Steward

    "In developing the ideal BI team, your key person to have is a strong data architect, but you also need buy-in from the highest levels of the organization. Buy-in from different levels of the organization are indicators of success more than anything else."

    – Rob Anderson, Database Administrator and BI Manager, IT Research and Advisory Firm

    Create a RACI matrix to clearly define the roles and responsibilities for the parties involved

    A common project management pitfall for any endeavour is unclear definition of responsibilities amongst the individuals involved.

    As a business intelligence project requires a significant amount of back and forth between business and IT – bridged by the BI Steering Committee – clear guidelines at the project outset with a RACI chart provide a basic framework for assigning tasks and lines of communication for the later stages.

    Responsible Accountable Consulted Informed

    Obtaining Buy-in Project Charter Requirements Design Development Program Creation
    BI Steering Committee A C I I I C
    Project Sponsor - C I I I C
    Project Manager - R A I I C
    VP of BI R I I I I A
    CIO A I I I I R
    Business Analyst I I R C C C
    Solution Architect - - C A C C
    Data Architect - - C A C C
    BI Developer - - C C R C
    Data Steward - - C R C C
    Business SME C C C C C C

    Note: This RACI is an example of how role expectations would be broken down across the different steps of the project. Develop your own RACI based on project scope and participants.

    STEP 1.1

    Understand Your Business Context and Structure the Project

    Establish business–IT alignment for your BI strategy by detailing the business context

    Step Objectives

    • Engage the business units to find out where users need BI enablement.
    • Ideate preliminary points for improvement that will further business goals and calculate their value.

    Step Activities

    1.1.1 Craft the vision and mission statements for the Analytics program using the vision, mission, and strategies of your organization as basis.

    1.1.2 Articulate program goals and objectives

    1.1.3 Determine business differentiators and key drivers

    1.1.4 Brainstorm BI-specific constraints and improvement objectives

    Outcomes

    • Clearly articulated business context that will provide a starting point for formulating a BI strategy
    • High-level improvement objectives and ROI for the overall project
    • Vision, mission, and objectives of the analytics program

    Research Support

    • Info-Tech’s BI Strategy and Roadmap Template

    Proposed Participants in this Step

    • Project Manager
    • Project Team
    • Relevant Business Stakeholders and Subject Matter Experts

    Transform the way the business makes decisions

    Your BI strategy should enable the business to make fast, effective, and comprehensive decisions.

    Fast Effective Comprehensive
    Reduce time spent on decision-making by designing a BI strategy around information needs of key decision makers. Make the right data available to key decision makers. Make strategic high-value, impactful decisions as well as operational decisions.

    "We can improve BI environments in several ways. First, we can improve the speed with which we create BI objects by insisting that the environments are designed with flexibility and adaptability in mind. Second, we can produce higher quality deliverables by ensuring that IT collaborate with the business on every deliverable. Finally, we can reduce the costs of BI by giving access to the environment to knowledgeable business users and encouraging a self-service function."

    – Claudia Imhoff, Founder, Boulder BI Brain Trust, Intelligent Solutions Inc.

    Assess needs of various stakeholders using personas

    User groups/user personas

    Different users have different consumption and usage patterns. Categorize users into user groups and visualize the usage patterns. The user groups are the connection between the BI capabilities and the users.

    User groups Mindset Usage Pattern Requirements
    Front-line workers Get my job done; perform my job quickly. Reports (standard reports, prompted reports, etc.) Examples:
    • Report bursting
    • Prompted reports
    Analysts I have some ideas; I need data to validate and support my ideas. Dashboards, self-service BI, forecasting/budgeting, collaboration Examples:
    • Self-service datasets
    • Data mashup capability
    Management I need a big-picture view and yet I need to play around with the data to find trends to drive my business. Dashboards, scorecards, mobile BI, forecasting/budgeting Examples:
    • Multi-tab dashboards
    • Scorecard capability
    Data scientists I need to combine existing data, as well as external or new, unexplored data sources and types to find nuggets in the data. Data mashup, connections to data sources Examples:
    • Connectivity to big data
    • Social media analyses

    The pains of inadequate BI are felt across the entire organization – and land squarely on the shoulders of the CIO

    Organization:

    • Insufficient information to make decisions.
    • Unable to measure internal performance.
    • Losses incurred from bad decisions or delayed decisions.
    • Canned reports fail to uncover key insights.
    • Multiple versions of information exist in silos.

    IT Department

    • End users are completely dependent on IT for reports.
    • Ad hoc BI requests take time away from core duties.
    • Spreadsheet-driven BI is overly manual.
    • Business losing trust in IT.

    CIO

    • Under great pressure and has a strong desire to improve BI.
    • Ad hoc BI requests are consuming IT resources and funds.
    • My organization finds value in using data and having decision support to make informed decisions.

    The overarching question that needs to be continually asked to create an effective BI strategy is:

    How do I create an environment that makes information accessible and consumable to users, and facilitates a collaborative dialogue between the business and IT?

    Pre-requisites for success

    Prerequisite #1: Secure Executive Sponsorship

    Sponsorship of BI that is outside of IT and at the highest levels of the organization is essential to the success of your BI strategy. Without it, there is a high chance that your BI program will fail. Note that it may not be an epic fail, but it is a subtle drying out in many cases.

    Prerequisite #2: Understand Business Context

    Providing the right tools for business decision making doesn’t need to be a guessing game if the business context is laid as the project foundation and the most pressing decisions serve as starting points. And business is engaged in formulating and executing the strategy.

    Prerequisite #3: Deliver insights that lead to action

    Start with understanding the business processes and where analytics can improve outcomes. “Think business backwards, not data forward.” (McKinsey)

    11 reasons BI projects fail

    Lack of Executive support

    Old Technology

    Lack of business support

    Too many KPIs

    No methodology for gathering requirements

    Overly long project timeframes

    Bad user experience

    Lack of user adoption

    Bad data

    Lack of proper human resources

    No upfront definition of true ROI

    Mico Yuk, 2019

    Make it clear to the business that IT is committed to building and supporting a BI platform that is intimately tied to enabling changing business objectives.

    Leverage Info-Tech’s BI Strategy and Roadmap Template to accelerate BI planning

    How to accelerate BI planning using the template

    1. Prepopulated text that you can use for your strategy formulation:
    2. Prepopulated text that can be used for your strategy formulation
    3. Sample bullet points that you can pick and choose from:
    4. Sample bullet points to pick and choose from

    Document the BI program planning in Info-Tech’s

    BI Strategy and Roadmap Template.

    Activity: Describe your organization’s vision and mission

    1.1.1

    30-40 minutes

    Compelling vision and mission statements will help guide your internal members toward your company’s target state. These will drive your business intelligence strategy.

    1. Your vision clearly represents where your organization aspires to be in the future and aligns the entire organization. Write down a future-looking, inspirational, and realizable vision in one concise statement. Consider:
    • “Five years from now, our business will be _______.”
    • What do we want to do tomorrow? For whom? What is the benefit?
  • Your mission tells why your organization currently exists and clearly expresses how it will achieve your vision for the future. Write down a mission statement in one clear and concise paragraph consisting of, at most, five sentences. Consider:
    • Why does the business exist? What problems does it solve? Who are its customers?
    • How does the business accomplish strategic tasks or reach its target?
  • Reconvene stakeholders to share ideas and develop one concise vision statement and mission statement. Focus on clarity and message over wording.
  • Input

    • Business vision and mission statements

    Output

    • Alignment and understanding on business vision

    Materials

    Participants

    • BI project lead
    • Executive business stakeholders

    Info-Tech Insight

    Adjust your statements until you feel that you can elicit a firm understanding of both your vision and mission in three minutes or less.

    Formulating an Enterprise BI and Analytics Strategy: Top-down BI Opportunity analysis
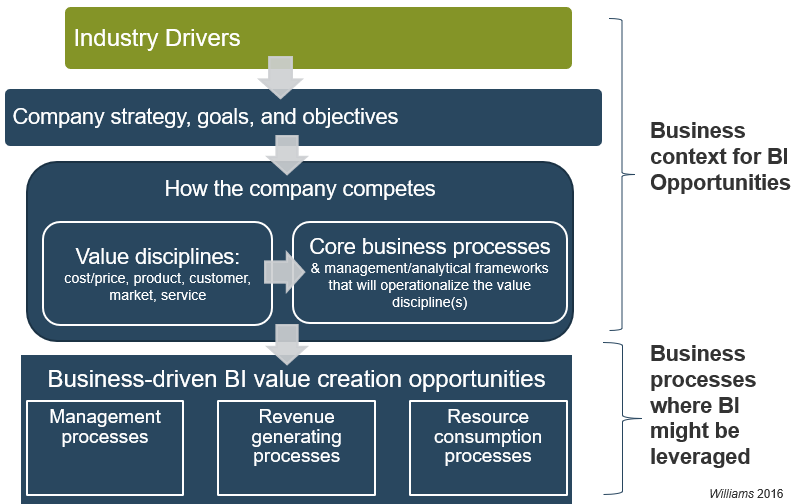
    Top-down BI Opportunity analysis

    Example of deriving BI opportunities using BI Opportunity Analysis

    Industry Drivers Private label Rising input prices Retail consolidation
    Company strategies Win at supply chain execution Win at customer service Expand gross margins
    Value disciplines Strategic cost management Operational excellence Customer service
    Core processes Purchasing Inbound logistics Sales, service & distribution
    Enterprise management: Planning, budgeting, control, process improvement, HR
    BI Opportunities Customer service analysis Cost and financial analysis Demand management

    Williams 2016

    Get your organization buzzing about BI – leverage Info-Tech’s Executive Brief as an internal marketing tool

    Two key tasks of a project sponsor are to:

    1. Evangelize the realizable benefits of investing in a business intelligence strategy.
    2. Help to shift the corporate culture to one that places emphasis on data-driven insight.

    Arm your project sponsor with our Executive Brief for this blueprint as a quick way to convey the value of this project to potential stakeholders.

    Bolster this presentation by adding use cases and metrics that are most relevant to your organization.

    Develop a business framework

    Identifying organizational goals and how data can support those goals is key to creating a successful BI & Analytical strategy. Rounding out the business model with technology drivers, environmental factors (as described in previous steps), and internal barriers and enablers creates a holistic view of Business Intelligence within the context of the organization as a whole.

    Through business engagement and contribution, the following holistic model can be created to understand the needs of the business.
    business framework holistic model

    Activity: Describe the Industry Drivers and Organization strategy to mitigate the risk

    1.1.2

    30-45 minutes

    Industry drivers are external influencers that has an effect on a business such as economic conditions, competitor actions, trade relations, climate etc. These drivers can differ significantly by industry and even organizations within the same industry.

    1. List the industry drivers that influences your organization:
    • Public sentiment in regards to energy source
    • Rising cost of raw materials due to increase demand
  • List the company strategies, goals, objectives to counteract the external influencers:
    • Change production process to become more energy efficient
    • Win at customer service
  • Identify the value disciplines :
    • Strategic cost management
    • Operational Excellence
  • List the core process that implements the value disciplines :
    • Purchasing
    • Sales
  • Identify the BI Opportunities:
    • Cost and financial analysis
    • Customer service analysis

    Input

    • Industry drivers

    Output

    • BI Opportunities that business can leverage

    Materials

    • Industry driver section in the BI Strategy and Roadmap Template

    Participants

    • BI project lead
    • Executive business stakeholders

    Understand BI and analytics drivers and organizational objectives

    Environmental Factors Organizational Goals Business Needs Technology Drivers
    Definition External considerations are factors taking place outside the organization that are impacting the way business is conducted inside the organization. These are often outside the control of the business. Organizational drivers can be thought of as business-level metrics. These are tangible benefits the business can measure, such as customer retention, operation excellence, and/or financial performance. A requirement that specifies the behavior and the functions of a system. Technology drivers are technological changes that have created the need for a new BI solution. Many organizations turn to technology systems to help them obtain a competitive edge.
    Examples
    • Economy and politics
    • Laws and regulations
    • Competitive influencers
    • Time to market
    • Quality
    • Delivery reliability
    • Audit tracking
    • Authorization levels
    • Business rules
    • Deployment in the cloud
    • Integration
    • Reporting capabilities

    Activity: Discuss BI/Analytics drivers and organizational objectives

    1.1.3

    30-45 minutes

    1. Use the industry drivers and business goals identified in activity 1.1.2 as a starting point.
    2. Understand how the company runs today and what the organization’s future will look like. Try to identify the purpose for becoming an integrated organization. Use a whiteboard and markers to capture key findings.
    3. Take into account External Considerations, Organizational Drivers, Technology Drivers, and Key Functional Requirements.
    External Considerations Organizational Drivers Technology Considerations Functional Requirements
    • Funding Constraints
    • Regulations
    • Compliance
    • Scalability
    • Operational Efficiency
    • Data Accuracy
    • Data Quality
    • Better Reporting
    • Information Availability
    • Integration Between Systems
    • Secure Data

    Identify challenges and barriers to the BI project

    There are several factors that may stifle the success of a BI implementation. Scan the current environment to identify internal barriers and challenges to identify potential challenges so you can meet them head-on.

    Common Internal Barriers

    Management Support
    Organizational Culture
    Organizational Structure
    IT Readiness
    Definition The degree of management understanding and acceptance towards BI solutions. The collective shared values and beliefs. The functional relationships between people and departments in an organization. The degree to which the organization’s people and processes are prepared for a new BI solution.
    Questions
    • Is a BI project recognized as a top priority?
    • Will management commit time to the project?
    • Are employees resistant to change?
    • Is the organization highly individualized?
    • Is the organization centralized?
    • Is the organization highly formalized?
    • Is there strong technical expertise?
    • Is there strong infrastructure?
    Impact
    • Funding
    • Resources
    • Knowledge sharing
    • User acceptance
    • Flow of knowledge
    • Poor implementation
    • Reliance on consultants

    Activity: Discuss BI/Analytics challenges and pain points

    1.1.4

    30-45 minutes

    1. Identify challenges with the process identified in step 1.1.2.
    2. Brainstorm potential barriers to successful BI implementation and adoption. Use a whiteboard and marker to capture key findings.
    3. Consider Functional Gaps, Technical Gaps, Process Gaps, and Barriers to BI Success.
    Functional Gaps Technical Gaps Process Gaps Barriers to Success
    • No online purchase order requisition
    • Inconsistent reporting – data quality concerns
    • Duplication of data
    • Lack of system integration
    • Cultural mindset
    • Resistance to change
    • Lack of training
    • Funding

    Activity: Discuss opportunities and benefits

    1.1.5

    30-45 minutes

    1. Identify opportunities and benefits from an integrated system.
    2. Brainstorm potential enablers for successful BI implementation and adoption. Use a whiteboard and markers to capture key findings.
    3. Consider Business Benefits, IT Benefits, Organizational Benefits, and Enablers of BI success.
    Business Benefits IT Benefits Organizational Benefits Enablers of Success
    • Business-IT alignment
    • Compliance
    • Scalability
    • Operational Efficiency
    • Data Accuracy
    • Data Quality
    • Better Reporting
    • Change management
    • Training
    • Alignment to strategic objectives

    Your organization’s framework for Business Intelligence Strategy
    Blank organization framework for Business Intelligence Strategy

    Example: Business Framework for Data & Analytics Strategy

    The following diagram represents [Client]’s business model for BI and data. This holistic view of [Client]’s current environment serves as the basis for the generation of the business-aligned Data & Analytics Strategy.
    The image is an example of Business Framework for Data & Analytics Strategy.

    Info-Tech recommends balancing a top-down approach with bottom up for building your BI strateg

    Taking a top-down approach will ensure senior management’s involvement and support throughout the project. This ensures that the most critical decisions are supported by the right data/information, aligning the entire organization with the BI strategy. Furthermore, the gains from BI will be much more significant and visible to the rest of the organization.
    Two charts showing the top-down and bottom-up approach.

    Far too often, organizations taking a bottom-up approach to BI will fail to generate sufficient buy-in and awareness from senior management. Not only does a lack of senior involvement result in lower adoption from the tactical and operational levels, but more importantly, it also means that the strategic decision makers aren’t taking advantage of BI.

    Estimate the ROI of your BI and analytics strategy to secure executive support

    The value of creating a new strategy – or revamping an existing one – needs to be conveyed effectively to a high-level stakeholder, ideally a C-level executive. That executive buy-in is more likely to be acquired when effort has been made to determine the return on investment for the overall initiative.

    1. Business Impacts
      New revenue
      Cost savings
      Time to market
      Internal Benefits
      Productivity gain
      Process optimization
      Investment
      People – employees’ time, external resources
      Data – cost for new datasets
      Technology – cost for new technologies
    2. QuantifyCan you put a number or a percentage to the impacts and benefits? QuantifyCan you estimate the investments you need to put in?
    3. TranslateTranslate the quantities into dollar value
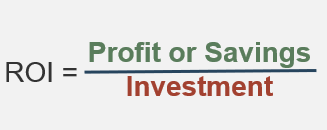
    4. The image depicts an equation for ROI estimate

    Example

    One percent increase in revenue; three more employees $225,000/yr, $150,000/yr 50%

    Activity: Establish a high-level ROI as part of an overall use case for developing a fit-for-purpose BI strategy

    1.1.6

    1.5 hours

    Communicating an ROI that is impactful and reasonable is essential for locking in executive-level support for any initiative. Use this activity as an initial touchpoint to bring business and IT perspectives as part of building a robust business case for developing your BI strategy.

    1. Revisit the business context detailed in the previous sections of this phase. Use priority objectives to identify use case(s), ideally where there are easily defined revenue generators/cost reductions (e.g. streamlining the process of mailing physical marketing materials to customers).
    2. Assign research tasks around establishing concrete numbers and dollar values.
    • Have a subject matter expert weigh in to validate your figures.
    • When calculating ROI, consider how you might leverage BI to create opportunities for upsell, cross-sell, or increased customer retention.
  • Reconvene the stakeholder group and discuss your findings.
    • This is the point where expectation management is important. Separate the need-to-haves from the nice-to-haves.

    Emphasize that ROI is not fully realized after the first implementation, but comes as the platform is built upon iteratively and in an integrated fashion to mature capabilities over time.

    Input

    • Vision statement
    • Mission statement

    Output

    • Business differentiators and key drivers

    Materials

    • Benefit Cost Analysis section of the BI Strategy and Roadmap Template

    Participants

    • BI project lead
    • Executive IT & business stakeholders

    An effective BI strategy positions business intelligence in the larger data lifecycle

    In an effort to keep users satisfied, many organizations rush into implementing a BI platform and generating reports for their business users. BI is, first and foremost, a presentation layer; there are several stages in the data lifecycle where the data that BI visualizes can be compromised.

    Without paying the appropriate amount of attention to the underlying data architecture and application integration, even the most sophisticated BI platforms will fall short of providing business users with a holistic view of company information.

    Example

    In moving away from single application-level reporting, a strategy around data integration practices and technology is necessary before the resultant data can be passed to the BI platform for additional analyses and visualization.

    BI doesn’t exist in a vacuum – develop an awareness of other key data management practices

    As business intelligence is primarily a presentation layer that allows business users to visualize data and turn information into actionable decisions, there are a number of data management practices that precede BI in the flow of data.

    Data Warehousing

    The data warehouse structures source data in a manner that is more operationally focused. The Reporting & Analytics Strategy must inform the warehouse strategy on data needs and building a data warehouse to meet those needs.

    Data Integration, MDM & RDM

    The data warehouse is built from different sources that must be integrated and normalized to enable Business Intelligence. The Info-Tech integration and MDM blueprints will guide with their implementation.

    Data Quality

    A major roadblock to building an effective BI solution is a lack of accurate, timely, consistent, and relevant data. Use Info-Tech’s blueprint to refine your approach to data quality management.

    Data quality, poor integration/P2P integration, poor data architecture are the primary barriers to truly leveraging BI, and a lot of companies haven’t gotten better in these areas.

    – Shari Lava, Associate Vice-President, IT Research and Advisory Firm

    Building consensus around data definitions across business units is a critical step in carrying out a BI strategy

    Business intelligence is heavily reliant on the ability of an organization to mesh data from different sources together and create a holistic and accurate source of truth for users.

    Useful analytics cannot be conducted if your business units define key business terms differently.

    Example

    Finance may label customers as those who have transactional records with the organization, but Marketing includes leads who have not yet had any transactions as customers. Neglecting to note these seemingly small discrepancies in data definition will undermine efforts to combine data assets from traditionally siloed functional units.

    In the stages prior to implementing any kind of BI platform, a top priority should be establishing common definitions for key business terms (customers, products, accounts, prospects, contacts, product groups, etc.).

    As a preliminary step, document different definitions for the same business terms so that business users are aware of these differences before attempting to combine data to create custom reports.

    Self-Assessment

    Do you have common definitions of business terms?

    • If not, identify common business terms.
    • At the very least, document different definitions of the same business terms so the corporate can compare and contrast them.

    STEP 1.2

    Assess the Current BI Landscape

    Establish an in-depth understanding of your current BI landscape

    Step Objectives

    • Inventory and assess the state of your current BI landscape
    • Document the artifacts of your BI environment

    Step Activities

    1.2.1 Analyze the usage levels of your current BI programs/platform

    1.2.2 Perform a survey to gather user perception of your current BI environment

    1.2.3 Take an inventory of your current BI artifacts

    Outcomes

    • Summarize the qualitative and quantitative performance of your existing BI environment
    • Understand the outputs coming from your BI sources

    Research Support

    • Info-Tech’s BI Strategy and Roadmap Template

    Project Manager

    Data Architect(s) or Enterprise Architect

    Project Team

    Understand your current BI landscape before you rationalize

    Relying too heavily on technology as the sole way to solve BI problems results in a more complex environment that will ultimately frustrate business users. Take the time to thoroughly assess the current state of your business intelligence landscape using a qualitative (user perception) and quantitative (usage statistics) approach. The insights and gaps identified in this step will serve as building blocks for strategy and roadmap development in later phases.

    Phase 1

    Current State Summary of BI Landscape

    1.2.1 1.2.2 1.2.3 1.2.4
    Usage Insights Perception Insights BI Inventory Insights Requirements Insights

    PHASE 2

    Strategy and Roadmap Formulation

    Gather usage insights to pinpoint the hot spots for BI usage amongst your users

    Usage data reflects the consumption patterns of end users. By reviewing usage data, you can identify aspects of your BI program that are popular and those that are underutilized. It may present some opportunities for trimming some of the underutilized content.

    Benefits of analyzing usage data:

    • Usage is a proxy for popularity and usability of the BI artifacts. The popular content should be kept and improved in your next generation BI.
    • Usage information provides insight on what, when, where, and how much users are consuming BI artifacts.
    • Unlike methods such as user interviews and focus groups, usage information is fact based and is not subject to peer pressure or “toning down.”

    Sample Sources of Usage Data:

    1. Usage reports from your BI platform Many BI platforms have out-of-the-box usage reports that log and summarize usage data. This is your ideal source for usage data.
    2. Administrator console in your BI platformBI platforms usually have an administrator console that allows BI administrators to configure settings and to monitor activities that include usage. You may obtain some usage data in the console. Note that the usage data is usually real-time in nature, and you may not have access to a historical view of the BI usage.

    Info-Tech Insight

    Don’t forget some of the power users. They may perform analytics by accessing datasets directly or with the help of a query tool (even straight SQL statements). Their usage information is important. The next generation BI should provide consumption options for them.

    Accelerate the process of gathering user feedback with Info-Tech’s Application Portfolio Assessment (APA)

    In an environment where multiple BI tools are being used, discovering what works for users and what doesn’t is an important first step to rationalizing the BI landscape.

    Info-Tech’s Application Portfolio Assessment allows you to create a custom survey based on your current applications, generate a custom report that will help you visualize user satisfaction levels, and pinpoint areas for improvement.

    Activity: Review and analyze usage data

    1.2.1

    2 hours

    This activity helps you to locate usage data in your existing environment. It also helps you to review and analyze usage data to come up with a few findings.

    1. Get to the usage source. You may obtain usage data from one of the below options. Usage reports are your ideal choice, followed by some alternative options:
    2. a. Administrator console – limited to real-time or daily usage data. You may need to track usage data over for several days to identify patterns.

      b. Info-Tech’s Application Portfolio Assessment (APA).

      c. Other – be creative. Some may use an IT usage monitoring system or web analytics to track time users spent on the BI portal.

    3. Develop categories for classifying the different sources of usage data in your current BI environment. Use the following table as starting point for creating these groups:

    This is the content for Layout H4 Tag

    By Frequency Real Time Daily Weekly Yearly
    By Presentation Format Report Dashboard Alert Scorecard
    By Delivery Web portal Excel PDF Mobile application

    INPUT

    • Usage reports
    • Usage statistics

    OUTPUT

    • Insights pertaining to usage patterns

    Materials

    • Usage Insights of the BI Strategy and Roadmap Template

    Participants

    • BA
    • BI Administrator
    • PM

    Activity: Review and analyze usage (cont.)

    1.2.1

    2 hours

    3. Sort your collection of BI artifacts by usage. Discuss some of the reasons why some content is popular whereas some has no usage at all.

    Popular BI Artifacts – Discuss improvements, opportunities and new artifacts

    Unpopular BI Artifacts – Discuss retirement, improvements, and realigning information needs

    4. Summarize your findings in the Usage Insights section of the BI Strategy and Roadmap Template.

    INPUT

    • Usage reports
    • Usage statistics

    OUTPUT

    • Insights pertaining to usage patterns

    Materials

    • Usage Insights section of the BI Strategy and Roadmap Template

    Participants

    • BA
    • BI Administrator
    • PM

    Gather perception to understand the existing BI users

    In 1.2.1, we gathered the statistics for BI usage; it’s the hard data telling who uses what. However, it does not tell you the rationale, or the why, behind the usage. Gathering user perception and having conversations with your BI consumers is the key to bridging the gap.

    User Perception Survey

    Helps you to:

    1. Get general insights on user perception
    2. Narrow down to selected areas

    User Interviews

    Perception can be gathered by user interviews and surveys. Conducting user interviews takes time so it is a good practice to get some primary insights via survey before doing in-depth interviews in selected areas.

    – Shari Lava, Associate Vice-President, IT Research and Advisory Firm

    Define problem statements to create proof-of-concept initiatives

    Info-Tech’s Four Column Model of Data Flow

    Find a data-related problem or opportunity

    Ask open-ended discovery questions about stakeholder fears, hopes, and frustrations to identify a data-related problem that is clear, contained, and fixable. This is then to be written as a problem/opportunity statement.

    1. Fear: What is the number one risk you need to alleviate?
    2. Hope: What is the number one opportunity you wish to realize?
    3. Frustration: What is the number one annoying pet peeve you wish to scratch?
    4. Next, gather information to support a problem/opportunity statement:

    5. What are your challenges in performing the activity or process today?
    6. What does amazing look like if we solve this perfectly?
    7. What other business activities/processes will be impacted/improved if we solve this?
    8. What compliance/regulatory/policy concerns do we need to consider in any solution?
    9. What measures of success/change should we use to prove value of the effort (KPIs/ROI)?
    10. What are the steps in the process/activity?
    11. What are the applications/systems used at each step and from step to step?
    12. What data elements are created, used, and/or transformed at each step?

    Leverage Info-Tech’s BI survey framework to initiate a 360° perception survey

    Info-Tech has developed a BI survey framework to help existing BI practices gather user perception via survey. The framework is built upon best practices developed by McLean & Company.

    1. Communicate the survey
    2. Create a survey
    3. Conduct the survey
    4. Collect and clean survey data
    5. Analyze survey data
    6. Conduct follow-up interviews
    7. Identify and prioritize improvement initiatives

    The survey takes a comprehensive approach by examining your existing BI practices through the following lenses:

    360° Perception

    Demographics Who are the users? From which department?
    Usage How is the current BI being used?
    People Web portal
    Process How good is your BI team from a user perspective?
    Data How good is the BI data in terms of quality and usability?
    Technology How good are your existing BI/reporting tools?
    Textual Feedback The sky’s the limit. Tell us your comments and ideas via open-ended questions.

    Use Info-Tech’s BI End-User Satisfaction Survey Framework to develop a comprehensive BI survey tailored to your organization.

    Activity: Develop a plan to gather user perception of your current BI program

    1.2.2

    2 hours

    This activity helps you to plan for a BI perception survey and subsequent interviews.

    1. Proper communication while conducting surveys helps to boost response rate. The project team should have a meeting with business executives to decide:
    • The survey goals
    • Which areas to cover
    • Which trends and hypotheses you want to confirm
    • Which pre-, during, and post-survey communications should be sent out
  • Have the project team create the first draft of the survey for subsequent review by select business stakeholders. Several iterations may be needed before finalizing.
  • In planning for the conclusion of the survey, the project team should engage a data analyst to:
    1. Organize the data in a useful format
    2. Clean up the survey data when there are gaps
    3. Summarize the data into a presentable/distributable format

    Collectively, the project team and the BI consuming departments should review the presentation and discuss these items:

    Misalignment

    Opportunities

    Inefficiencies

    Trends

    Need detailed interviews?

    INPUT

    • Usage information and analyses

    OUTPUT

    • User-perception survey

    Materials

    • Perception Insights section of the BI Strategy and Roadmap Template

    Participants

    • BA
    • BI Administrator
    • PM
    • Business SMEs

    Create a comprehensive inventory of your BI artifacts

    Taking an inventory of your BI artifacts allows you to understand what deliverables have been developed over the years. Inventory taking should go beyond the BI content. You may want to include additional information products such as Excel spreadsheets, reports that are coming out of an Access database, and reports that are generated from front-end applications (e.g. Salesforce).

    1. Existing Reports from BI platform

    2. If you are currently using a BI platform, you have some BI artifacts (reports, scorecards, dashboards) that are developed within the platform itself.

    • BI Usage Reports (refer to step 2.1) – if you are getting a comprehensive BI usage reports for all your BI artifacts, there is your inventory report too.
    • BI Inventory Reports – Your BI platform may provide out-of-the-box inventory reports. You can use them as your inventory.
    • If the above options are not feasible, you may need to manually create the BI inventory. You may build that from some of your existing BI documentations to save time.
  • Excel and Access

    • Work with the business units to identify if Excel and Access are used to generate reports.
  • Application Reports

    • Data applications such as Salesforce, CRM, and ERP often provide reports as an out-of-the-box feature.
    • Those reports only include data within their respective applications. However, this may present opportunities for integrating application data with additional data sources.

    Activity: Inventory your BI artifacts

    1.2.3

    2+ hours

    This activity helps you to inventory your BI information artifacts and other related information artifacts.

    1. Define the scope of your inventory. Work with the project sponsor and CIO to define which sources should be captured in the inventory process. Consider: BI inventory, Excel spreadsheets, Access reports, and application reporting.
    2. Define the depth of your inventory. Work with the project sponsor and CIO to define the level of granularity. In some settings, the artifact name and a short description may be sufficient. In other cases, you may need to document users and business logic of the artifacts.
    3. Review the inventory results. Discuss findings and opportunities around the following areas:

    Interpret your Inventory

    Duplicated reports/ dashboards Similar reports/ dashboards that may be able to merge Excel and Access reports that are using undocumented, unconventional business logics Application reports that need to be enhanced by additional data Classify artifacts by BI Type

    INPUT

    • Current BI artifacts and documents
    • BI Type classification

    OUTPUT

    • Summary of BI artifacts

    Materials

    • BI Inventory Insights section of the BI Strategy and Roadmap Template

    Participants

    • BA
    • Data analyst
    • PM
    • Project sponsor

    Project sponsor

    1.2.4

    2+ hours

    This activity helps you to inventory your BI by report type.

    1. Classify BI artifacts by type. Use the BI Type tool to classify Work with the project sponsor and CIO to define which sources should be captured in the inventory process. Consider: BI inventory, Excel spreadsheets, Access reports, and application reporting.
    2. Define the depth of your inventory. Work with the project sponsor and CIO to define the level of granularity. In some settings, the artifact name and a short description may be sufficient. In other cases, you may need to document users and business logic of the artifacts.
    3. Review the inventory results. Discuss findings and opportunities around the following areas:

    Interpretation of your Inventory

    Duplicated reports/dashboards Similar reports/dashboards that may be able to merge Excel and Access reports that are using undocumented, unconventional business logics Application reports that need to be enhanced by additional data

    INPUT

    • The BI Type as used by different business units
    • Business BI requirements

    OUTPUT

    • Summary of BI type usage across the organization

    Materials

    • BI Inventory Insights section of the BI Strategy and Roadmap Template

    Participants

    • BA
    • Data analyst
    • PM
    • Project sponsor

    STEP 1.3

    Undergo BI Requirements Gathering

    Perform requirements gathering for revamping your BI environment

    Step Objectives

    • Create principles that will direct effective requirements gathering
    • Create a list of existing and desired BI requirements

    Step Activities

    1.3.1 Create requirements gathering principles

    1.3.2 Gather appropriate requirements

    1.3.3 Organize and consolidate the outputs of requirements gathering activities

    Outcomes

    • Requirements gathering principles that are flexible and repeatable
    • List of BI requirements

    Research Support

    • Info-Tech’s BI Strategy and Roadmap Template

    Proposed Participants in this Step

    Project Manager

    Data Architect(s) or Enterprise Architect

    Project Team

    Business Users

    Don’t let your new BI platform become a victim of poor requirements gathering

    The challenges in requirements management often have underlying causes; find and eliminate the root causes rather than focusing on the symptoms.

    Root Causes of Poor Requirements Gathering:

    • Requirements gathering procedures exist but aren’t followed.
    • There isn't enough time allocated to the requirements gathering phase.
    • There isn't enough involvement or investment secured from business partners.
    • There is no senior leadership involvement or mandate to fix requirements gathering.
    • There are inadequate efforts put towards obtaining and enforcing sign off.

    Outcomes of Poor Requirements Gathering:

    • Rework due to poor requirements leads to costly overruns.
    • Final deliverables are of poor quality and are implemented late.
    • Predicted gains from deployed applications are not realized.
    • There are low feature utilization rates by end users.
    • Teams are frustrated within IT and the business.

    Info-Tech Insight

    Requirements gathering is the number one failure point for most development or procurement projects that don’t deliver value. This has been, and continues to be, the case as most organizations still don't get requirements gathering right. Overcoming organizational cynicism can be a major obstacle to clear when it is time to optimize the requirements gathering process.

    Define the attributes of a good requirement to help shape your requirements gathering principles

    A good requirement has the following attributes:

    Verifiable It is stated in a way that can be tested.
    Unambiguous It is free of subjective terms and can only be interpreted in one way.
    Complete It contains all relevant information.
    Consistent It does not conflict with other requirements.
    Achievable It is possible to accomplish given the budgetary and technological constraints.
    Traceable It can be tracked from inception to testing.
    Unitary It addresses only one thing and cannot be deconstructed into multiple requirements.
    Accurate It is based on proven facts and correct information.

    Other Considerations

    Organizations can also track a requirement owner, rationale, priority level (must have vs. nice to have), and current status (approved, tested, etc.).

    Info-Tech Insight

    Requirements must be solution agnostic – they should focus on the underlying need rather than the technology required to satisfy the need.

    Activity: Define requirements gathering principles

    1.3.1

    1 hour

    1. Invite representatives from the project management office, project management team, and BA team, as well as some key business stakeholders.
    2. Use the sample categories and principles in the table below as starting points for creating your own requirements gathering principles.
    3. Document the requirements gathering principles in the BI Strategy and Roadmap Template.
    4. Communicate the requirements gathering principles to the affected BI stakeholders.

    Sample Principles to Start With

    Effectiveness Face-to-face interviews are preferred over phone interviews.
    Alignment Clarify any misalignments, even the tiniest ones.
    Validation Rephrase requirements at the end to validate requirements.
    Ideation Use drawings and charts to explain ideas.
    Demonstration Make use of Joint Application Development (JAD) sessions.

    INPUT

    • Existing requirement principles (if any)

    OUTPUT

    • Requirements gathering principles that can be revisited and reused

    Materials

    • Requirements Insights section of the BI Strategy and Roadmap Template

    Participants

    • BA Team
    • PM
    • Business stakeholders
    • PMO

    Info-Tech Insight

    Turn requirements gathering principles into house rules. The house rules should be available in every single requirements gathering session and the participants should revisit them when there are disagreements, confusion, or silence.

    Right-size your approach to BI requirements management

    Info-Tech suggests four requirements management approaches based on project complexity and business significance. BI projects usually require the Strategic Approach in requirements management.

    Requirements Management Process Explanations

    Approach Definition Recommended Strategy
    Strategic Approach High business significance and high project complexity merits a significant investment of time and resources in requirements gathering. Treat the requirements gathering phase as a project within a project. A large amount of time should be dedicated to elicitation, business process mapping, and solution design.
    Fundamental Approach High business significance and low project complexity merits a heavy emphasis on the elicitation phase to ensure that the project bases are covered and business value is realized. Look to achieve quick wins and try to survey a broad cross-section of stakeholders during elicitation and validation. The elicitation phase should be highly iterative. Do not over-complicate the analysis and validation of a straightforward project.
    Calculated Approach Low business significance and high project complexity merits a heavy emphasis on the analysis and validation phases to ensure that the solution meets the needs of users. Allocate a significant amount of time to business process modeling, requirements categorization, prioritization, and solution modeling.
    Elementary Approach Low business significance and low project complexity does not merit a high amount of rigor for requirements gathering. Do not rush or skip steps, but aim to be efficient. Focus on basic elicitation techniques (e.g. unstructured interviews, open-ended surveys) and consider capturing requirements as user stories. Focus on efficiency to prevent project delays and avoid squandering resources.

    Vary the modes used in eliciting requirements from your user base

    Requirements Gathering Modes

    Info-Tech has identified four effective requirements gathering modes. During the requirements gathering process, you may need to switch between the four gathering modes to establish a thorough understanding of the information needs.

    Dream Mode

    • Mentality: Let users’ imaginations go wild. The sky’s the limit.
    • How it works: Ask users to dream up the ideal future state and ask how analytics can support those dreams.
    • Limitations: Not all dreams can be fulfilled. A variety of constraints (budget, personnel, technical skills) may prevent the dreams from becoming reality.

    Pain Mode

    • Mentality: Users are currently experiencing pains related to information needs.
    • How it works: Vent the pains. Allow end users to share their information pains, ask them how their pains can be relieved, then convert those pains to requirements.
    • Limitations: Users are limited by the current situation and aren’t looking to innovate.

    Decode Mode

    • Mentality: Read the hidden messages from users. Speculate as to what the users really want.
    • How it works: Decode the underlying messages. Be innovative to develop hypotheses and then validate with the users.
    • Limitations: Speculations and hypothesis could be invalid. They may direct the users into some pre-determined directions.

    Profile Mode

    • Mentality: “I think you may want XYZ because you fall into that profile.”
    • How it works: The information user may fall into some existing user group profile or their information needs may be similar to some existing users.
    • Limitations: This mode doesn’t address very specific needs.

    Supplement BI requirements with user stories and prototyping to ensure BI is fit for purpose

    BI is a continually evolving program. BI artifacts that were developed in the past may not be relevant to the business anymore due to changes in the business and information usage. Revamping your BI program entails revisiting some of the BI requirements and/or gathering new BI requirements.

    Three-Step Process for Gathering Requirements

    Requirements User Stories Rapid Prototyping
    Gather requirements. Most importantly, understand the business needs and wants. Leverage user stories to organize and make sense of the requirements. Use a prototype to confirm requirements and show the initial draft to end users.

    Pain Mode: “I can’t access and manipulate data on my own...”

    Decode Mode: Dig deeper: could this hint at a self-service use case?

    Dream Mode: E.g. a sandbox area where I can play around with clean, integrated, well-represented data.

    Profile Mode: E.g. another marketing analyst is currently using something similar.

    ExampleMary has a spreadmart that keeps track of all campaigns. Maintaining and executing that spreadmart is time consuming.

    Mary is asking for a mash-up data set that she can pivot on her own…

    Upon reviewing the data and the prototype, Mary decided to use a heat map and included two more data points – tenure and lifetime value.

    Identify which BI styles best meet user requirements

    A spectrum of Business Intelligence solutions styles are available. Use Info-Tech’s BI Styles Tool to assess which business stakeholder will be best served by which style.

    Style Description Strategic Importance (1-5) Popularity (1-5) Effort (1-5)
    Standards Preformatted reports Standard, preformatted information for backward-looking analysis. 5 5 1
    User-defined analyses Pre-staged information where “pick lists” enable business users to filter (select) the information they wish to analyze, such as sales for a selected region during a selected previous timeframe. 5 4 2
    Ad-hoc analyses Power users write their own queries to extract self-selected pre-staged information and then use the information to perform a user-created analysis. 5 4 3
    Scorecards and dashboards Predefined business performance metrics about performance variables that are important to the organization, presented in a tabular or graphical format that enables business users to see at a glance how the organization is performing. 4 4 3
    Multidimensional analysis (OLAP) Multidimensional analysis (also known as on-line analytical processing): Flexible tool-based, user-defined analysis of business performance and the underlying drivers or root causes of that performance. 4 3 3
    Alerts Predefined analyses of key business performance variables, comparison to a performance standard or range, and communication to designated businesspeople when performance is outside the predefined performance standard or range. 4 3 3
    Advanced Analytics Application of long-established statistical and/or operations research methods to historical business information to look backward and characterize a relevant aspect of business performance, typically by using descriptive statistics. 5 3 4
    Predictive Analytics Application of long-established statistical and/or operations research methods and historical business information to predict, model, or simulate future business and/or economic performance and potentially prescribe a favored course of action for the future. 5 3 5

    Activity: Gather BI requirements

    1.3.2

    2-6 hours

    Using the approaches discussed on previous slides, start a dialogue with business users to confirm existing requirements and develop new ones.

    1. Invite business stakeholders to a requirements gathering session.
    2. For existing BI artifacts – Invite existing users of those artifacts.

      For new BI development – Invite stakeholders at the executive level to understand the business operation and their needs and wants. This is especially important if their department is new to BI.

    3. Discuss the business requirements. Systematically switch between the four requirements gathering modes to get a holistic view of the requirements.
    4. Once requirements are gathered, organize them to tell a story. A story usually has these components:
    The Setting The Characters The Venues The Activities The Future
    Example Customers are asking for a bundle discount. CMO and the marketing analysts want to… …the information should be available in the portal, mobile, and Excel. …information is then used in the bi-weekly pricing meeting to discuss… …bundle information should contain historical data in a graphical format to help executives.

    INPUT

    • Existing documentations on BI artifacts

    OUTPUT

    • Preliminary, uncategorized list of BI requirements

    Materials

    • Requirements Insights section of the BI Strategy and Roadmap Template

    Participants

    • BA team
    • Business stakeholders
    • Business SMEs
    • BI developers

    Clarify consumer needs by categorizing BI requirements

    Requirements are too broad in some situations and too detailed in others. In the previous step we developed user stories to provide context. Now you need to define requirement categories and gather detailed requirements.

    Considerations for Requirement Categories

    Category Subcategory Sample Requirements
    Data Granularity Individual transaction
    Transformation Transform activation date to YYYY-MM format
    Selection Criteria Client type: consumer. Exclude SMB and business clients. US only. Recent three years
    Fields Required Consumer band, Region, Submarket…
    Functionality Filters Filters required on the dashboard: date range filter, region filter…
    Drill Down Path Drill down from a summary report to individual transactions
    Analysis Required Cross-tab, time series, pie chart
    Visual Requirements Mock-up See attached drawing
    Section The dashboard will be presented using three sections
    Conditional Formatting Below-average numbers are highlighted
    Security Mobile The dashboard needs to be accessed from mobile devices
    Role Regional managers will get a subset of the dashboard according to the region
    Users John, Mary, Tom, Bob, and Dave
    Export Dashboard data cannot be exported into PDF, text, or Excel formats
    Performance Speed A BI artifact must be loaded in three seconds
    Latency Two seconds response time when a filter is changed
    Capacity Be able to serve 50 concurrent users with the performance expected
    Control Governance Govern by the corporate BI standards
    Regulations Meet HIPPA requirements
    Compliance Meet ISO requirements

    Prioritize requirements to assist with solution modeling

    Prioritization ensures that the development team focuses on the right requirements.

    The MoSCoW Model of Prioritization

    Must Have Requirements that mustbe implemented for the solution to be considered successful.
    Should Have Requirements that are high priority and should be included in the solution if possible.
    Could Have Requirements that are desirable but not necessary and could be included if resources are available.
    Won't Have Requirements that won’t be in the next release but will be considered for the future releases.

    The MoSCoW model was introduced by Dai Clegg of Oracle UK in 1994.

    Prioritization is the process of ranking each requirement based on its importance to project success. Hold a separate meeting for the domain SMEs, implementation SMEs, project managers, and project sponsors to prioritize the requirements list. At the conclusion of the meeting, each requirement should be assigned a priority level. The implementation SMEs will use these priority levels to ensure that efforts are targeted towards the proper requirements and the plan features available on each release. Use the MoSCoW Model of Prioritization to effectively order requirements.

    Activity: Finalize the list of BI requirements

    1.3.3

    1-4 hours

    Requirement Category Framework

    Category Subcategory
    Data Granularity
    Transformation
    Selection Criteria
    Fields Required
    Functionality Filters
    Drill Down Path
    Analysis Required
    Visual Requirements Mock-up
    Section
    Conditional Formatting
    Security Mobile
    Role
    Users
    Export
    Performance Speed
    Latency
    Capacity
    Control Governance
    Regulations
    Compliance

    Create requirement buckets and classify requirements.

    1. Define requirement categories according to the framework.
    2. Review the user story and requirements you collected in Step 1.3.2. Classify the requirements within requirement categories.
    3. Review the preliminary list of categorized requirements and look for gaps in this detailed view. You may need to gather additional requirements to fill the gaps.
    4. Prioritize the requirements according to the MoSCoW framework.
    5. Document your final list of requirements in the BI Strategy and Roadmap Template.

    INPUT

    • Existing requirements and new requirements from step 1.3.2

    OUTPUT

    • Prioritized and categorized requirements

    Materials

    • Requirements Insights section of the BI Strategy and Roadmap Template

    Participants

    • BA
    • Business stakeholders
    • PMO

    Translate your findings and ideas into actions that will be integrated into the BI Strategy and Roadmap Template

    As you progress through each phase, document findings and ideas as they arise. At phase end, hold a brainstorming session with the project team focused on documenting findings and ideas and substantiating them into improvement actions.
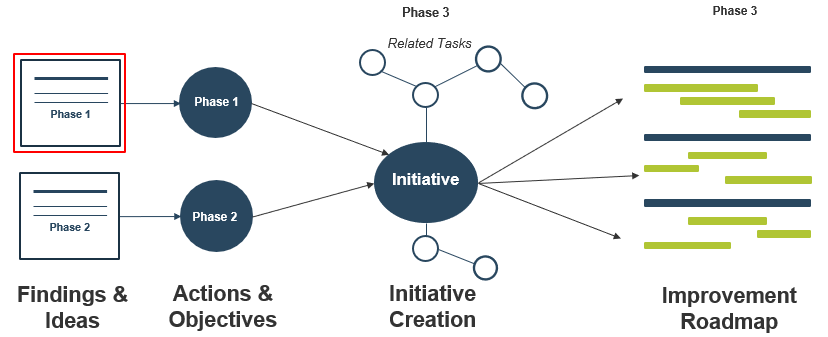
    Translating findings and ideas into actions that will be integrated into the BI Strategy and Roadmap Template

    Ask yourself how BI or analytics can be used to address the gaps and explore opportunities uncovered in each phase. For example, in Phase 1, how do current BI capabilities impede the realization of the business vision?

    Document and prioritize Phase 1 findings, ideas, and action items

    1.3.4

    1-2 hours

    1. Reconvene as a group to review findings, ideas, and actions harvested in Phase 1. Write the findings, ideas, and actions on sticky notes.
    2. Prioritize the sticky notes to yield those with high business value and low implementation effort. View some sample findings below:
    3. High Business Value, Low Effort High Business Value, High Effort
      Low Business Value, High Effort Low Business Value, High Effort

      Phase 1

      Sample Phase 1 Findings Found two business objectives that are not supported by BI/analytics
      Some executives still think BI is reporting
      Some confusion around operational reporting and BI
      Data quality plays a big role in BI
      Many executives are not sure about the BI ROI or asking for one
    4. Select the top findings and document them in the “Other Phase 1 Findings” section of the BI Strategy and Roadmap Template. The findings will be used again in Phase 3.

    INPUT

    • Phase 1 activities
    • Business context (vision, mission, goals, etc.

    OUTPUT

    • Other Phase 1 Findings section of the BI Strategy and Roadmap Template

    Materials

    • Whiteboard
    • Sticky notes

    Participants

    • Project manger
    • Project team
    • Business stakeholders

    If you want additional support, have our analysts guide you through this phase as part of an Info-Tech workshop

    Book a workshop with our Info-Tech analysts:

    • To accelerate this project, engage your IT team in an Info-Tech workshop with an Info-Tech analyst team.
    • Info-Tech analysts will join you and your team onsite at your location or welcome you to Info-Tech’s historic Toronto office to participate in an innovative onsite workshop.
    • Contact your account manager (www.infotech.com/account), or email Workshops@InfoTech.com for more information.

    The following are sample activities that will be conducted by Info-Tech analysts with your team:

    1.1.1-1.1.5

    Establish the business context

    To begin the workshop, your project team will be taken through a series of activities to establish the overall business vision, mission, objectives, goals, and key drivers. This information will serve as the foundation for discerning how the revamped BI strategy needs to enable business users.

    1.2.1- 1.2.3

    Create a comprehensive documentation of your current BI environment

    Our analysts will take your project team through a series of activities that will facilitate an assessment of current BI usage and artifacts, and help you design an end-user interview survey to elicit context around BI usage patterns.

    If you want additional support, have our analysts guide you through this phase as part of an Info-Tech workshop

    Book a workshop with our Info-tech analysts

    1.3.1-1.3.3

    Establish new BI requirements

    Our analysts will guide your project team through frameworks for eliciting and organizing requirements from business users, and then use those frameworks in exercises to gather some actual requirements from business stakeholders.

    Phase 2

    Evaluate Your Current BI Practice

    Build a Reporting and Analytics Strategy

    Revisit project metrics to track phase progress

    Goals for Phase 2:

    • Assess your current BI practice. Determine the maturity of your current BI practice from different viewpoints.
    • Develop your BI target state. Plan your next generation BI with Info-Tech’s BI patterns and best practices.
    • Safeguard your target state. Avoid BI pitfalls by proactively monitoring BI risks.

    Info-Tech’s Suggested Metrics for Tracking Phase 2 Goals

    Practice Improvement Metrics Data Collection and Calculation Expected Improvement
    # of groups participated in the current state assessment The number of groups joined the current assessment using Info-Tech’s BI Practice Assessment Tool Varies; the tool can accommodate up to five groups
    # of risks mitigated Derive from your risk register At least two to five risks will be identified and mitigated

    Intangible Metrics:

    • Prototyping approach allows the BI group to understand more about business requirements, and in the meantime, allows the business to understand how to partner with the BI group.
    • The BI group and the business have more confidence in the BI program as risks are monitored and mitigated on an ad hoc basis.

    Evaluate your current BI practice

    Phase 2 Overarching Insight

    BI success is not based solely on the technology it runs on; technology cannot mask gaps in capabilities. You must be capable in your environment, and data management, data quality, and related data practices must be strong. Otherwise, the usefulness of the intelligence suffers. The best BI solution does not only provide a technology platform, but also addresses the elements that surround the platform. Look beyond tools and holistically assess the maturity of your BI practice with input from both the BI consumer and provider perspectives.

    Understand the Business Context to Rationalize Your BI Landscape Evaluate Your Current BI Practice Create a BI Roadmap for Continuous Improvement
    Establish the Business Context
    • Business Vision, Goals, Key Drivers
    • Business Case Presentation
    • High-Level ROI
    Assess Your Current BI Maturity
    • SWOT Analysis
    • BI Practice Assessment
    • Summary of Current State
    Construct a BI Initiative Roadmap
    • BI Improvement Initiatives
    • BI Strategy and Roadmap
    Access Existing BI Environment
    • BI Perception Survey Framework
    • Usage Analyses
    • BI Report Inventory
    Envision BI Future State
    • BI Patterns
    • BI Practice Assessment
    • List of Functions
    Plan for Continuous Improvement
    • Excel Governance Policy
    • BI Ambassador Network Draft
    Undergo Requirements Gathering
    • Requirements Gathering Principles
    • Overall BI Requirements

    Phase 2 overview

    Detailed Overview

    Step 1: Assess Your Current BI Practice

    Step 2: Envision a Future State for Your BI Practice

    Outcomes

    • A comprehensive assessment of current BI practice maturity and capabilities.
    • Articulation of your future BI practice.
    • Improvement objectives and activities for developing your current BI program.

    Benefits

    • Identification of clear gaps in BI practice maturity.
    • A current state assessment that includes the perspectives of both BI providers and consumers to highlight alignment and/or discrepancies.
    • A future state is defined to provide a benchmark for your BI program.
    • Gaps between the future and current states are identified; recommendations for the gaps are defined.

    Phase 2 outline

    Call 1-888-670-8889 or email GuidedImplementations@InfoTech.com for more information.

    Complete these steps on your own, or call us to complete a guided implementation. A guided implementation is a series of 2-3 advisory calls that help you execute each phase of a project. They are included in most advisory memberships.

    Guided Implementation 2: Evaluate Your Current BI Practice

    Proposed Time to Completion: 1-2 weeks

    Step 2.1: Assess Your Current BI Practice

    Start with an analyst kick-off call:

    • Detail the benefits of conducting multidimensional assessments that involve BI providers as well as consumers.
    • Review Info-Tech’s BI Maturity Model.

    Then complete these activities…

    • SWOT analyses
    • Identification of BI maturity level through a current state assessment

    With these tools & templates:

    BI Practice Assessment Tool

    BI Strategy and Roadmap Template

    Step 2.2: Envision a Future State for Your BI Practice

    Review findings with an analyst:

    • Discuss overall maturity gaps and patterns in BI perception amongst different units of your organization.
    • Discuss how to translate activity findings into robust initiatives, defining critical success factors for BI development and risk mitigation.

    Then complete these activities…

    • Identify your desired BI patterns and functionalities.
    • Complete a target state assessment for your BI practice.
    • Review capability practice gaps and phase-level metrics.

    With these tools & templates:

    BI Practice Assessment Tool

    BI Strategy and Roadmap Template

    Phase 2 Results & Insights:

    • A comprehensive assessment of the organization’s current BI practice capabilities and gaps
    • Visualization of BI perception from a variety of business users as well as IT
    • A list of tasks and initiatives for constructing a strategic BI improvement roadmap

    STEP 2.1

    Assess the Current State of Your BI Practice

    Assess your organization’s current BI capabilities

    Step Objectives

    • Understand the definitions and roles of each component of BI.
    • Contextualize BI components to your organization’s environment and current practices.

    Step Activities

    2.1.1 Perform multidimensional SWOT analyses

    2.1.2 Assess current BI and analytical capabilities, Document challenges, constraints, opportunities

    2.1.3 Review the results of your current state assessment

    Outcomes

    • Holistic perspective of current BI strengths and weaknesses according to BI users and providers
    • Current maturity in BI and related data management practices

    Research Support

    • Info-Tech’s Data Management Framework
    • Info-Tech’s BI Practice Assessment Tool
    • Info-Tech’s BI Strategy and Roadmap Template

    Proposed Participants in this Step

    Project Manager

    Data Architect(s) or Enterprise Architect

    Project Team

    Gather multiple BI perspectives with comprehensive SWOT analyses

    SWOT analysis is an effective tool that helps establish a high-level context for where your practice stands, where it can improve, and the factors that will influence development.

    Strengths

    Best practices, what is working well

    Weaknesses

    Inefficiencies, errors, gaps, shortcomings

    Opportunities

    Review internal and external drivers

    Threats

    Market trends, disruptive forces

    While SWOT is not a new concept, you can add value to SWOT by:

    • Conducting a multi-dimensional SWOT to diversify perspectives – involve the existing BI team, BI management, business executives and other business users.
    • SWOT analyses traditionally provide a retrospective view of your environment. Add a future-looking element by creating improvement tasks/activities at the same time as you detail historical and current performance.

    Info-Tech Insight

    Consider a SWOT with two formats: a private SWOT worksheet and a public SWOT session. Participants will be providing suggestions anonymously while solicited suggestions will be discussed in the public SWOT session to further the discussion.

    Activity: Perform a SWOT analysis in groups to get a holistic view

    2.1.1

    1-2 hours

    This activity will take your project team through a holistic SWOT analysis to gather a variety of stakeholder perception of the current BI practice.

    1. Identify individuals to involve in the SWOT activity. Aim for a diverse pool of participants that are part of the BI practice in different capacities and roles. Solution architects, application managers, business analysts, and business functional unit leaders are a good starting point.
    2. Review the findings summary from Phase 1. You may opt to facilitate this activity with insights from the business context. Each group will be performing the SWOT individually.
    3. The group results will be collected and consolidated to pinpoint common ideas and opinions. Individual group results should be represented by a different color. The core program team will be reviewing the consolidated result as a group.
    4. Document the results of these SWOT activities in the appropriate section of the BI Strategy and Roadmap Template.

    SWOT

    Group 1 Provider Group E.g. The BI Team

    Group 2 Consumer Group E.g. Business End Users

    INPUT

    • IT and business stakeholder perception

    OUTPUT

    • Multi-faceted SWOT analyses
    • Potential BI improvement activities/objectives

    Materials

    • SWOT Analysis section of the BI Strategy and Roadmap Template

    Participants

    • Selected individuals in the enterprise (variable)

    Your organization’s BI maturity is determined by several factors and the degree of immersion into your enterprise

    BI Maturity Level

    A way to categorize your analytics maturity to understand where you are currently and what next steps would be best to increase your BI maturity.

    There are several factors used to determine BI maturity:

    Buy-in and Data Culture

    Determines if there is enterprise-wide buy-in for developing business intelligence and if a data-driven culture exists.

    Business–IT Alignment

    Examines if current BI and analytics operations are appropriately enabling the business objectives.

    Governance Structure

    Focuses on whether or not there is adequate governance in place to provide guidance and structure for BI activities.

    Organization Structure and Talent

    Pertains to how BI operations are distributed across the overall organizational structure and the capabilities of the individuals involved.

    Process

    Reviews analytics-related processes and policies and how they are created and enforced throughout the organization.

    Data

    Deals with analytical data in terms of the level of integration, data quality, and usability.

    Technology

    Explores the opportunities in building a fit-for-purpose analytics platform and consolidation opportunities.

    Evaluate Your Current BI Practice with the CMMI model

    To assess BI, Info-Tech uses the CMMI model for rating capabilities in each of the function areas on a scale of 1-5. (“0” and “0.5” values are used for non-existent or emerging capabilities.)
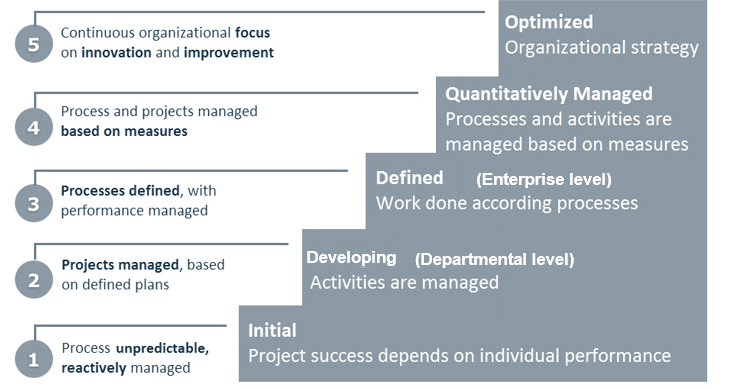
    The image shows an example of a CMMI model

    Use Info-Tech’s BI Maturity Model as a guide for identifying your current analytics competence

    Leverage a BI strategy to revamp your BI program to strive for a high analytics maturity level. In the future you should be doing more than just traditional BI. You will perform self-service BI, predictive analytics, and data science.

    Ad Hoc Developing Defined Managed Trend Setting
    Questions What’s wrong? What happened? What is happening? What happened, is happening, and will happen? What if? So what?
    Scope One business problem at a time One particular functional area Multiple functional areas Multiple functional areas in an integrated fashion Internal plus internet scale data
    Toolset Excel, Access, primitive query tools Reporting tools or BI BI BI, business analytics tools Plus predictive platforms, data science tools
    Delivery Model IT delivers ad hoc reports IT delivers BI reports IT delivers BI reports and some self-service BI Self-service BI and report creation at the business units Plus predictive models and data science projects
    Mindset Firefighting using data Manage using data Analyze using data; shared tooling Data is an asset, shared data Data driven
    BI Org. Structure Data analysts in IT BI BI program BI CoE Data Innovation CoE

    Leverage Info-Tech’s BI Practice Assessment Tool to define your BI current state

    BI Practice Assessment Tool

    1. Assess Current State
    • Eight BI practice areas to assess maturity.
    • Based on CMMI maturity scale.
  • Visualize Current State Results
    • Determine your BI maturity level.
    • Identify areas with outstanding maturity.
    • Uncover areas with low maturity.
    • Visualize the presence of misalignments.
  • Target State
    • Tackle target state from two views: business and IT.
    • Calculate gaps between target and current state.
  • Visualize Target State and Gaps
    • A heat map diagram to compare the target state and the current state.
    • Show both current and target maturity levels.
    • Detailed charts to show results for each area.
    • Detailed list of recommendations.

    Purposes:

    • Assess your BI maturity.
    • Visualize maturity assessment to quickly spot misalignments, gaps, and opportunities.
    • Provide right-sized recommendations.

    Info-Tech Insight

    Assessing current and target states is only the beginning. The real value comes from the interpretation and analysis of the results. Use visualizations of multiple viewpoints and discuss the results in groups to come up with the most effective ideas for your strategy and roadmap.

    Activity: Conduct a current state assessment of your BI practice maturity

    2.1.2

    2-3 hours

    Use the BI Practice Assessment Tool to establish a baseline for your current BI capabilities and maturity.

    1. Navigate to Tab 2. Current State Assessment in the BI Practice Assessment Tool and complete the current state assessment together or in small groups. If running a series of assessments, do not star or scratch every time. Use the previous group’s results to start the conversation with the users.
    2. Info-Tech suggests the following groups participate in the completion of the assessment to holistically assess BI and to uncover misalignment:

      Providers Consumers
      CIO & BI Management BI Work Groups (developers, analysts, modelers) Business Unit #1 Business Unit #2 Business Unit #3
    3. For each assessment question, answer the current level of maturity in terms of:
      1. Initial/Ad hoc – the starting point for use of a new or undocumented repeat process
      2. Developing – the process is documented such that it is repeatable
      3. Defined – the process is defined/confirmed as a standard business process
      4. Managed and Measurable – the process is quantitatively managed in accordance with agreed-upon metrics.
      5. Optimized – the process includes process optimization/improvement.

    INPUT

    • Observations of current maturity

    OUTPUT

    • Comprehensive current state assessment

    Materials

    • BI Practice Assessment Tool
    • Current State Assessment section of the BI Strategy and Roadmap Template

    Participants

    • Selected individuals as suggested by the assessment tool

    Info-Tech Insight

    Discuss the rationale for your answers as a group. Document the comments and observations as they may be helpful in formulating the final strategy and roadmap.

    Activity: Review and analyze the results of the current state assessment

    2.1.3

    2-3 hours

    1. Navigate to Tab 3. Current State Results in the BI Practice Assessment Tool and review the findings:

    The tool provides a brief synopsis of your current BI state. Review the details of your maturity level and see where this description fits your organization and where there may be some discrepancies. Add additional comments to your current state summary in the BI Strategy and Roadmap Document.

    In addition to reviewing the attributes of your maturity level, consider the following:

    1. What are the knowns – The knowns confirm your understanding on the current landscape.
  • What are the unknowns – The unknowns show you the blind spots. They are very important to give you an alternative view of the your current state. The group should discuss those blind spots and determine what to do with them.
  • Activity: Review and analyze the results of the current state assessment (cont.)

    2.1.3

    2-3 hours

    2. Tab 3 will also visualize a breakdown of your maturity by BI practice dimension. Use this graphic as a preliminary method to identify where your organization is excelling and where it may need improvement.

    Better Practices

    Consider: What have you done in the areas where you perform well?

    Candidates for Improvement

    Consider: What can you do to improve these areas? What are potential barriers to improvement?

    STEP 2.2

    Envision a Future State for Your Organization’s BI Practice

    Detail the capabilities of your next generation BI practice

    Step Objectives

    • Create guiding principles that will shape your organization’s ideal BI program.
    • Pinpoint where your organization needs to improve across several BI practice dimensions.
    • Develop approaches to remedy current impediments to BI evolution.
    • Step Activities

      2.2.1 Define guiding principles for the future state

      2.2.2 Define the target state of your BI practice

      2.2.3 Confirm requirements for BI Styles by management group

      2.2.4 Analyze gaps in your BI practice and generate improvement activities and objectives

      2.2.5 Define the critical success factors for future BI

      2.2.6 Identify potential risks for your future state and create a mitigation plan

    Outcomes

    • Defined landscape for future BI capabilities, including desired BI functionalities.
    • Identification of crucial gaps and improvement points to include in a BI roadmap.
    • Updated BI Styles Usage sheet.

    Research Support

    • Info-Tech’s Data Management Framework
    • Info-Tech’s BI Practice Assessment Tool
    • Info-Tech’s BI Strategy and Roadmap Template

    Proposed Participants in this Step

    Project Manager

    Data Architect(s) or Enterprise Architect

    Project Team

    Define guiding principles to drive your future state envisioning

    Envisioning a BI future state is essentially architecting the future for your BI program. It is very similar to enterprise architecture (EA). Guiding principles are widely used in enterprise architecture. This best practice should also be used in BI envisioning.

    Benefits of Guiding Principles in a BI Context

    • BI planning involves a number of business units. Defining high-level future state principles helps to establish a common ground for those different business units.
    • Ensure the next generation BI aligns with the corporate enterprise architecture and data architecture principles.
    • Provide high-level guidance without depicting detailed solutioning by leaving room for innovation.

    Sample Principles for BI Future State

    1. BI should be fit for purpose. BI is a business technology that helps business users.
    2. Business–IT collaboration should be encouraged to ensure deliverables are relevant to the business.
    3. Focus on continuous improvement on data quality.
    4. Explore opportunities to onboard and integrate new datasets to create a holistic view of your data.
    5. Organize and present data in an easy-to-consume, easy-to-digest fashion.
    6. BI should be accessible to everything, as soon as they have a business case.
    7. Do not train just on using the platform. Train on the underlying data and business model as well.
    8. Develop a training platform where trainees can play around with the data without worrying about messing it up.

    Activity: Define future state guiding principles for your BI practice

    2.2.1

    1-2 hours

    Guiding principles are broad statements that are fundamental to how your organization will go about its activities. Use this as an opportunity to gather relevant stakeholders and solidify how your BI practice should perform moving forward.

    1. To ensure holistic and comprehensive future state principles, invite participants from the business, the data management team, and the enterprise architecture team. If you do not have an enterprise architecture practice, invite people that are involved in building the enterprise architecture. Five to ten people is ideal.
    2. BI Future State

      Awareness Buy-in Business-IT Alignment Governance Org. Structure; People Process; Policies; Standards Data Technology
    3. Once the group has some high-level ideas on what the future state looks like, brainstorm guiding principles that will facilitate the achievement of the future state (see above).
    4. Document the future state principles in the Future State Principles for BI section of the BI Strategy and Roadmap Template

    INPUT

    • Existing enterprise architecture guiding principles
    • High-level concept of future state BI

    OUTPUT

    • Guiding principles for prospective BI practice

    Materials

    • Future State Principles section of the BI Strategy and Roadmap Template

    Participants

    • Business representatives
    • IT representatives
    • The EA group

    Leverage prototypes to facilitate a continuous dialogue with end users en route to creating the final deliverable

    At the end of the day, BI makes data and information available to the business communities. It has to be fit for purpose and relevant to the business. Prototypes are an effective way to ensure relevant deliverables are provided to the necessary users. Prototyping makes your future state a lot closer and a lot more business friendly.

    Simple Prototypes

    • Simple paper-based, whiteboard-based prototypes with same notes.
    • The most basic communication tool that facilitates the exchange of ideas.
    • Often used in Joint Application Development (JAD) sessions.
    • Improve business and IT collaboration.
    • Can be used to amend requirements documents.

    Discussion Possibilities

    • Initial ideation at the beginning
    • Align everyone on the same page
    • Explain complex ideas/layouts
    • Improve collaboration

    Elaborated Prototypes

    • Demonstrates the possibilities of BI in a risk-free environment.
    • Creates initial business value with your new BI platform.
    • Validates the benefits of BI to the organization.
    • Generates interest and support for BI from senior management.
    • Prepares BI team for the eventual enterprise-wide deployment.

    Discussion Possibilities

    • Validate and refine requirements
    • Fail fast, succeed fast
    • Acts as checkpoints
    • Proxy for the final working deliverable

    Leverage Info-Tech’s BI Practice Assessment Tool to define your BI target state and visualize capability gaps

    BI Practice Assessment Tool

    1. Assess Current State
    • Eight BI practice areas to assess maturity.
    • Based on CMMI maturity scale.
  • Visualize Current State Results
    • Determine your BI maturity level.
    • Identify areas with outstanding maturity.
    • Uncover areas with low maturity.
    • Visualize the presence of misalignments.
  • Target State
    • Tackle target state from two views: business and IT.
    • Calculate gaps between target and current state.
  • Visualize Target State and Gaps
    • A heat map diagram to compare the target state and the current state.
    • Show both current and target maturity levels.
    • Detailed charts to show results for each area.
    • Detailed list of recommendations.

    Purposes:

    • Assess your BI maturity.
    • Visualize maturity assessment to quickly spot misalignments, gaps, and opportunities.
    • Provide right-sized recommendations.

    Document essential findings in Info-Tech’s BI Strategy and Roadmap Template.

    Info-Tech Insight

    Assessing current and target states is only the beginning. The real value comes from the interpretation and analyses of the results. Use visualizations of multiple viewpoints and discuss the results in groups to come up with the most effective ideas for your strategy and roadmap.

    Activity: Define the target state for your BI practice

    2.2.2

    2 hours

    This exercise takes your team through establishing the future maturity of your BI practice across several dimensions.

    1. Envisioning of the future state will involve input from the business side as well as the IT department.
    2. The business and IT groups should get together separately and determine the target state maturity of each of the BI practice components:
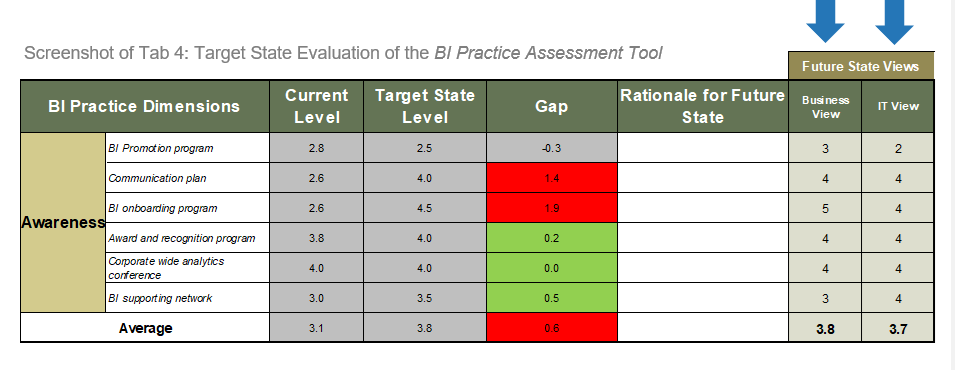
    The image is a screenshot of Tab 4: Target State Evaluation of the BI Practice Assessment Tool

    INPUT

    • Desired future practice capabilities

    OUTPUT

    • Target state assessment

    Materials

    • Tab 4 of the BI Practice Assessment Tool

    Participants

    • Business representatives
    • IT representatives

    Activity: Define the target state for your BI practice (cont.)

    2.2.2

    2 hours

    2. The target state levels from the two groups will be averaged in the column “Target State Level.” The assessment tool will automatically calculate the gaps between future state value and the current state maturity determined in Step 2.1. Significant gaps in practice maturity will be highlighted in red; smaller or non-existent gaps will appear green.
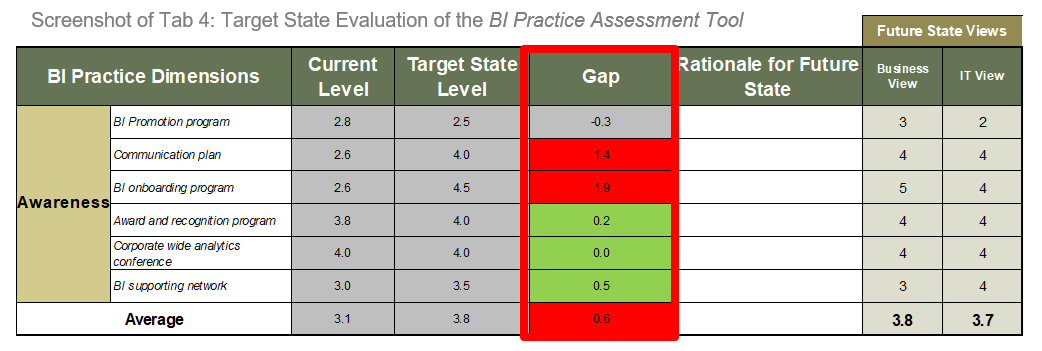
    The image is a screenshot of Tab 4: Target State Evaluation of the BI Practice Assessment Tool with Gap highlighted.

    INPUT

    • Desired future practice capabilities

    OUTPUT

    • Target state assessment

    Materials

    • Tab 4 of the BI Practice Assessment Tool

    Participants

    • Business representatives
    • IT representatives

    Activity: Revisit the BI Style Analysis sheet to define new report and analytical requirements by C-Level

    2.2.3

    1-2 hours

    The information needs for each executive is unique to their requirements and management style. During this exercise you will determine the reporting and analytical needs for an executive in regards to content, presentation and cadence and then select the BI style that suite them best.

    1. To ensure a holistic and comprehensive need assessment, invite participants from the business and BI team. Discuss what data the executive currently use to base decisions on and explore how the different BI styles may assist. Sample reports or mock-ups can be used for this purpose.
    2. Document the type of report and required content using the BI Style Tool.
    3. The BI Style Tool will then guide the BI team in the type of reporting to develop and the level of Self-Service BI that is required. The tool can also be used for product selection.

    INPUT

    • Information requirements for C-Level Executives

    OUTPUT

    • BI style(s) that are appropriate for an executive’s needs

    Materials

    • BI Style Usage sheet from BI Strategy and Roadmap Template
    • Sample Reports

    Participants

    • Business representatives
    • BI representatives

    Visualization tools facilitate a more comprehensive understanding of gaps in your existing BI practice

    Having completed both current and target state assessments, the BI Practice Assessment Tool allows you to compare the results from multiple angles.

    At a higher level, you can look at your maturity level:

    At a detailed level, you can drill down to the dimensional level and item level.
    The image is a screenshots from Tab 4: Target State Evaluation of the BI Practice Assessment Tool

    At a detailed level, you can drill down to the dimensional level and item level.

    Activity: Analyze gaps in BI practice capabilities and generate improvement objectives/activities

    2.2.4

    2 hours

    This interpretation exercise helps you to make sense of the BI practice assessment results to provide valuable inputs for subsequent strategy and roadmap formulation.

    1. IT management and the BI team should be involved in this exercise. Business SMEs should be consulted frequently to obtain clarifications on what their ideal future state entails.
    2. Begin this exercise by reviewing the heat map and identifying:

    • Areas with very large gaps
    • Areas with small gaps

    Areas with large gaps

    Consider: Is the target state feasible and achievable? What are ways we can improve incrementally in this area? What is the priority for addressing this gap?

    Areas with small/no gaps

    Consider: Can we learn from those areas? Are we setting the bar too low for our capabilities?

    INPUT

    • Current and target state visualizations

    OUTPUT

    • Gap analysis (Tab 5)

    Materials

    • Tab 5 of the BI Practice Assessment Tool
    • Future State Assessment Results section of the BI Strategy and Roadmap Template

    Participants

    • Business representatives
    • IT representatives

    Activity: Analyze gaps in BI practice capabilities and generate improvement objectives/activities (cont.)

    2.2.4

    2 hours

    2. Discuss the differences in the current and target state maturity level descriptions. Questions to ask include:

    • What are the prerequisites before we can begin to build the future state?
    • Is the organization ready for that future state? If not, how do we set expectations and vision for the future state?
    • Do we have the necessary competencies, time, and support to achieve our BI vision?

    INPUT

    • Current and target state visualizations

    OUTPUT

    • Gap analysis (Tab 5)

    Materials

    • Tab 5 of the BI Practice Assessment Tool
    • Future State Assessment Results section of the BI Strategy and Roadmap Template

    Participants

    • Business representatives
    • IT representatives

    Activity: Analyze gaps in BI practice capabilities and generate improvement objectives/activities (cont.)

    2.2.4

    2 hours

    3. Have the same group members reconvene and discuss the recommendations at the BI practice dimension level on Tab 5. of the BI Practice Assessment Tool. These recommendations can be used as improvement actions or translated into objectives for building your BI capabilities.

    Example

    The heat map displayed the largest gap between target state and current state in the technology dimension. The detailed drill-down chart will further illustrate which aspect(s) of the technology dimension is/are showing the most room for improvement in order to better direct your objective and initiative creation.
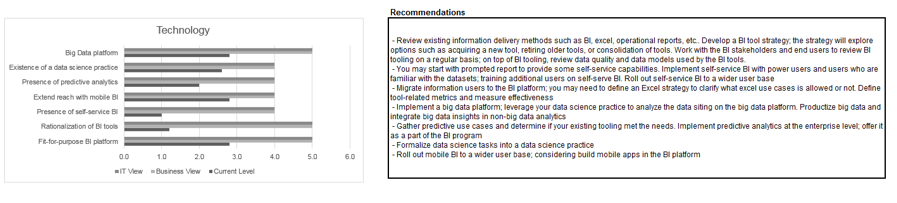
    The image is of an example and recommendations.

    Considerations:

    • What dimension parameters have the largest gaps? And why?
    • Is there a different set of expectations for the future state?

    Define critical success factors to direct your future state

    Critical success factors (CSFs) are the essential factors or elements required for ensuring the success of your BI program. They are used to inform organizations with things they should focus on to be successful.

    Common Provider (IT Department) CSFs

    • BI governance structure and organization is created.
    • Training is provided for the BI users and the BI team.
    • BI standards are in place.
    • BI artifacts rely on quality data.
    • Data is organized and presented in a usable fashion.
    • A hybrid BI delivery model is established.
    • BI on BI; a measuring plan has to be in place.

    Common Consumer (Business) CSFs

    • Measurable business results have been improved.
    • Business targets met/exceeded.
    • Growth plans accelerated.
    • World-class training to empower BI users.
    • Continuous promotion of a data-driven culture.
    • IT–business partnership is established.
    • Collaborative requirements gathering processes.
    • Different BI use cases are supported.

    …a data culture is essential to the success of analytics. Being involved in a lot of Bay Area start-ups has shown me that those entrepreneurs that are born with the data DNA, adopt the data culture and BI naturally. Other companies should learn from these start-ups and grow the data culture to ensure BI adoption.

    – Cameran Hetrick, Senior Director of Data Science & Analytics, thredUP

    Activity: Define provider and consumer critical success factors for your future BI capabilities

    2.2.5

    2 hours

    Create critical success factors that are important to both BI providers and BI consumers.

    1. Divide relevant stakeholders into two groups:
    2. BI Provider (aka IT) BI Consumer (aka Business)
    3. Write two headings on the board: Objective and Critical Success Factors. Write down each of the objectives created in Phase 1.
    4. Divide the group into small teams and assign each team an objective. For each objective, ask the following question:
    5. What needs to be put in place to ensure that this objective is achieved?

      The answer to the question is your candidate CSF. Write CSFs on sticky notes and stick them by the relevant objective.

    6. Rationalize and consolidate CSFs. Evaluate the list of candidate CSFs to find the essential elements for achieving success.
    7. For each CSF, identify at least one key performance indicator that will serve as an appropriate metric for tracking achievement.

    As you evaluate candidate CSFs, you may uncover new objectives for achieving your future state BI.

    INPUT

    • Business objectives

    OUTPUT

    • A list of critical success factors mapped to business objectives

    Materials

    • Whiteboard and colored sticky notes
    • CSFs for the Future State section of the BI Strategy and Roadmap Template

    Participants

    • Business and IT representatives
    • CIO
    • Head of BI

    Round out your strategy for BI growth by evaluating risks and developing mitigation plans

    A risk matrix is a useful tool that allows you to track risks on two dimensions: probability and impact. Use this matrix to help organize and prioritize risk, as well as develop mitigation strategies and contingency plans appropriately.
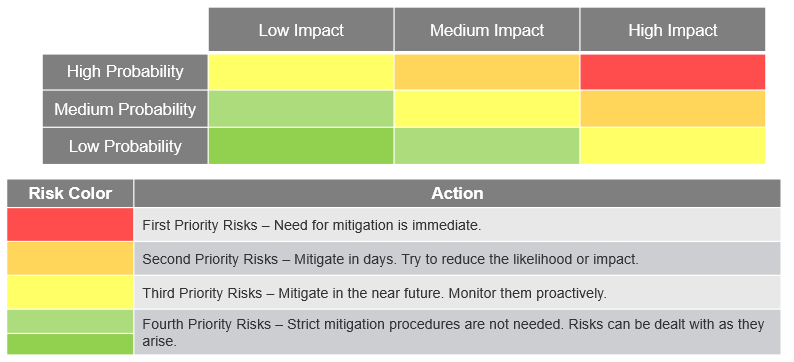
    Example of a risk matrix using colour coding

    Info-Tech Insight

    Tackling risk mitigation is essentially purchasing insurance. You cannot insure everything – focus your investments on mitigating risks with a reasonably high impact and high probability.

    Be aware of some common barriers that arise in the process of implementing a BI strategy

    These are some of the most common BI risks based on Info-Tech’s research:

    Low Impact Medium Impact High Impact
    High Probability
    • Users revert back to Microsoft Excel to analyze data.
    • BI solution does not satisfy the business need.
    • BI tools become out of sync with new strategic direction.
    • Poor documentation creates confusion and reduces user adoption.
    • Fail to address data issues: quality, integration, definition.
    • Inadequate communication with stakeholders throughout the project.
    • Users find the BI tool interface too confusing.
    Medium Probability
    • Fail to define and monitor KPIs.
    • Poor training results in low user adoption.
    • Organization culture is resistant to the change.
    • Lack of support from the sponsors.
    • No governance over BI.
    • Poor training results in misinformed users.
    Low Probability
    • Business units independently invest in BI as silos.

    Activity: Identify potential risks for your future state and create a mitigation plan

    2.2.6

    1 hour

    As part of developing your improvement actions, use this activity to brainstorm some high-level plans for mitigating risks associated with those actions.

    Example:

    Users find the BI tool interface too confusing.

    1. Use the probability-impact matrix to identify risks systematically. Collectively vote on the probability and impact for each risk.
    2. Risk mitigation. Risk can be mitigated by three approaches:
    3. A. Reducing its probability

      B. Reducing its impact

      C. Reducing both

      Option A: Brainstorm ways to reduce risk probability

      E.g. The probability of the above risk may be reduced by user training. With training, the probability of confused end users will be reduced.

      Option B: Brainstorm ways to reduce risk impact

      E.g. The impact can be reduced by ensuring having two end users validate each other’s reports before making a major decision.

    4. Document your high-level mitigation strategies in the BI Strategy and Roadmap Template.

    INPUT

    • Step 2.2 outputs

    OUTPUT

    • High-level risk mitigation plans

    Materials

    • Risks and Mitigation section of the BI Strategy and Roadmap Template

    Participants

    • BI sponsor
    • CIO
    • Head of BI

    Translate your findings and ideas into actions that will be integrated into the BI strategy and roadmap

    As you progress through each phase, document findings and ideas as they arise. By phase end, hold a brainstorming session with the project team focused on documenting findings and ideas and substantiating them into improvement actions.
    Translated findings and ideas into actions that will be integrated into the BI strategy and roadmap.

    Ask yourself how BI or analytics can be used to address the gaps and explore opportunities uncovered in each phase. For example, in Phase 1, how do current BI capabilities impede the realization of the business vision?

    Document and prioritize Phase 2 findings, ideas, and action items

    2.2.7

    1-2 hours

    1. Reconvene as a group to review the findings, ideas, and actions harvested in Phase 2. Write the findings, ideas, and actions on sticky notes.
    2. Prioritize the sticky notes to yield those with high business value and low implementation effort. View some sample findings below:
    3. High Business Value, Low Effort High Business Value, High Effort
      Low Business Value, High Effort Low Business Value, High Effort

      Phase 2

      Sample Phase 2 Findings Found a gap between the business expectation and the existing BI content they are getting.
      Our current maturity level is “Level 2 – Operational.” Almost everyone thinks we should be at least “Level 3 – Tactical” with some level 4 elements.
      Found an error in a sales report. A quick fix is identified.
      The current BI program is not able to keep up with the demand.
    4. Select the top items and document the findings in the BI Strategy Roadmap Template. The findings will be used to build a Roadmap in Phase 3.

    INPUT

    • Phase 2 activities

    OUTPUT

    • Other Phase 2 Findings section of the BI Strategy and Roadmap Template

    Materials

    • Whiteboard
    • Sticky notes

    Participants

    • Project manger
    • Project team
    • Business stakeholders

    If you want additional support, have our analysts guide you through this phase as part of an Info-Tech workshop

    Book a workshop with our Info-Tech analysts:

    • To accelerate this project, engage your IT team in an Info-Tech workshop with an Info-Tech analyst team.
    • Info-Tech analysts will join you and your team onsite at your location or welcome you to Info-Tech’s historic Toronto office to participate in an innovative onsite workshop.
    • Contact your account manager (www.infotech.com/account), or email Workshops@InfoTech.com for more information.

    The following are sample activities that will be conducted by Info-Tech analysts with your team:

    2.1.1

    Determine your current BI maturity level

    The analyst will take your project team through Info-Tech’s BI Practice Assessment Tool, which collects perspectives from BI consumer and provider groups on multiple facets of your BI practice in order to establish a current maturity level.

    If you want additional support, have our analysts guide you through this phase as part of an Info-Tech workshop

    Book a workshop with our Info-Tech analysts

    2.2.1

    Define guiding principles for your target BI state

    Using enterprise architecture principles as a starting point, our analyst will facilitate exercises to help your team establish high-level standards for your future BI practice.

    2.2.2-2.2.3

    Establish your desired BI patterns and matching functionalities

    In developing your BI practice, your project team will have to decide what BI-specific capabilities are most important to your organization. Our analyst will take your team through several BI patterns that Info-Tech has identified and discuss how to bridge the gap between these patterns, linking them to specific functional requirements in a BI solution.

    2.2.4-2.2.5

    Analyze the gaps in your BI practice capabilities

    Our analyst will guide your project team through a number of visualizations and explanations produced by our assessment tool in order to pinpoint the problem areas and generate improvement ideas.

    Phase 3

    Create a BI Roadmap for Continuous Improvement

    Build a Reporting and Analytics Strategy

    Create a BI roadmap for continuous improvement

    Phase 3 Overarching Insight

    The benefit of creating a comprehensive and actionable roadmap is twofold: not only does it keep BI providers accountable and focused on creating incremental improvement, but a roadmap helps to build momentum around the overall project, provides a continuous delivery of success stories, and garners grassroots-level support throughout the organization for BI as a key strategic imperative.

    Understand the Business Context to Rationalize Your BI Landscape Evaluate Your Current BI Practice Create a BI Roadmap for Continuous Improvement
    Establish the Business Context
    • Business Vision, Goals, Key Drivers
    • Business Case Presentation
    • High-Level ROI
    Assess Your Current BI Maturity
    • SWOT Analysis
    • BI Practice Assessment
    • Summary of Current State
    Construct a BI Initiative Roadmap
    • BI Improvement Initiatives
    • BI Strategy and Roadmap
    Access Existing BI Environment
    • BI Perception Survey Framework
    • Usage Analyses
    • BI Report Inventory
    Envision BI Future State
    • BI Patterns
    • BI Practice Assessment
    • List of Functions
    Plan for Continuous Improvement
    • Excel Governance Policy
    • BI Ambassador Network Draft
    Undergo Requirements Gathering
    • Requirements Gathering Principles
    • Overall BI Requirements

    Phase 3 overview

    Detailed Overview

    Step 1: Establish Your BI Initiative Roadmap

    Step 2: Identify Opportunities to Enhance Your BI Practice

    Step 3: Create Analytics Strategy

    Step 4: Define CSF and metrics to monitor success of BI and analytics

    Outcomes

    • Consolidate business intelligence improvement objectives into robust initiatives.
    • Prioritize improvement initiatives by cost, effort, and urgency.
    • Create a one-year, two-year, or three-year timeline for completion of your BI improvement initiatives.
    • Identify supplementary programs that will facilitate the smooth execution of road-mapped initiatives.

    Benefits

    • Clear characterization of comprehensive initiatives with a detailed timeline to keep team members accountable.

    Revisit project metrics to track phase progress

    Goals for Phase 3:

    • Put everything together. Findings and observations from Phase 1 and 2 are rationalized in this phase to develop data initiatives and create a strategy and roadmap for BI.
    • Continuous improvements. Your BI program is evolving and improving over time. The program should allow you to have faster, better, and more comprehensive information.

    Info-Tech’s Suggested Metrics for Tracking Phase 3 Goals

    Practice Improvement Metrics Data Collection and Calculation Expected Improvement
    Program Level Metrics Efficiency
    • Time to information
    • Self-service penetration
    • Derive from the ticket management system
    • Derive from the BI platform
    • 10% reduction in time to information
    • Achieve 10-15% self-service penetration
    • Effectiveness
    • BI Usage
    • Data quality
    • Derive from the BI platform
    • Data quality perception
    • Majority of the users use BI on a daily basis
    • 15% increase in data quality perception
    Comprehensiveness
    • # of integrated datasets
    • # of strategic decisions made
    • Derive from the data integration platform
    • Decision-making perception
    • Onboard 2-3 new data domains per year
    • 20% increase in decision-making perception

    Learn more about the CIO Business Vision program.

    Intangible Metrics:

    Tap into the results of Info-Tech’s CIO Business Vision diagnostic to monitor the changes in business-user satisfaction as you implement the initiatives in your BI improvement roadmap.

    Phase 3 outline

    Call 1-888-670-8889 or email GuidedImplementations@InfoTech.com for more information.

    Complete these steps on your own or call us to complete a guided implementation. A guided implementation is a series of 2-3 advisory calls that helps you execute each phase of a project. They are included in most advisory memberships.

    Guided Implementation 3: Create a BI Roadmap for Continuous Improvement

    Proposed Time to Completion: 1-2 weeks

    Step 3.1: Construct a BI Improvement Initiative Roadmap

    Start with an analyst kick off call:

    • Review findings and insights from completion of activities pertaining to current and future state assessments
    • Discuss challenges around consolidating activities into initiatives

    Then complete these activities…

    • Collect improvement objectives/tasks from previous phases
    • Develop comprehensive improvement initiatives
    • Leverage value-effort matrix activities to prioritize these initiatives and place them along an improvement roadmap

    With these tools & templates:

    BI Initiatives and Roadmap Tool

    BI Strategy and Roadmap Template

    Step 3.2: Continuous Improvement Opportunities for BI

    Review findings with analyst:

    • Review completed BI improvement initiatives and roadmap
    • Discuss guidelines presenting a finalized improvement to the relevant committee or stakeholders
    • Discuss additional policies and programs that can serve to enhance your established BI improvement roadmap

    Then complete these activities…

    • Present BI improvement roadmap to relevant stakeholders
    • Develop Info-Tech’s recommended supplementary policies and programs for BI

    With these tools & templates:

    BI Strategy and Roadmap Executive Presentation Template

    Phase 3 Results & Insights:

    • Comprehensive initiatives with associated tasks/activities consolidated and prioritized in an improvement roadmap

    STEP 3.1

    Construct a BI Improvement Initiative Roadmap

    Build an improvement initiative roadmap to solidify your revamped BI strategy

    Step Objectives

    • Bring together activities and objectives for BI improvement to form initiatives
    • Develop a fit-for-purpose roadmap aligned with your BI strategy

    Step Activities

    3.1.1 Characterize individual improvement objectives and activities ideated in previous phases.

    3.1.2 Synthesize and detail overall BI improvement initiatives.

    3.1.3 Create a plan of action by placing initiatives on a roadmap.

    Outcomes

    • Detailed BI improvement initiatives, prioritized by value and effort
    • Defined roadmap for completion of tasks associated with each initiative and accountability

    Research Support

    • Info-Tech’s BI Initiatives and Roadmap Tool

    Proposed Participants in this Step

    Project Manager

    Project Team

    Create detailed BI strategy initiatives by bringing together the objectives listed in the previous phases

    When developing initiatives, all components of the initiative need to be considered, from its objectives and goals to its benefits, risks, costs, effort required, and relevant stakeholders.

    Use outputs from previous project steps as inputs to the initiative and roadmap building:
    The image shows the previous project steps as inputs to the initiative and roadmap building, with arrow pointing from one to the next.

    Determining the dependencies that exist between objectives will enable the creation of unique initiatives with associated to-do items or tasks.

    • Group objectives into similar buckets with dependencies
    • Select one overarching initiative
    • Adapt remaining objectives into tasks of the main initiative
    • Add any additional tasks

    Leverage Info-Tech’s BI Initiatives and Roadmap Tool to build a fit-for-purpose improvement roadmap

    BI Initiatives and Roadmap Tool

    Overview

    Use the BI Initiatives and Roadmap Tool to develop comprehensive improvement initiatives and add them to a BI strategy improvement roadmap.

    Recommended Participants

    • BI project team

    Tool Guideline

    Tab 1. Instructions Use this tab to get an understanding as to how the tool works.
    Tab 2. Inputs Use this tab to customize the inputs used in the tool.
    Tab 3. Activities Repository Use this tab to list and prioritize activities, to determine dependencies between them, and build comprehensive initiatives with them.
    Tab 4. Improvement Initiatives Use this tab to develop detailed improvement initiatives that will form the basis of the roadmap. Map these initiatives to activities from Tab 3.
    Tab 5. Improvement Roadmap Use this tab to create your BI strategy improvement roadmap, assigning timelines and accountability to initiatives and tasks, and to monitor your project performance over time.

    Activity: Consolidate BI activities into the tool and assign dependencies and priorities

    3.1.1

  • 2 hours
    1. Have one person from the BI project team populate Tab 3. Activities Repository with the BI strategy activities that were compiled in Phases 1 and 2. Use drop-downs to indicate in which phase the objective was originally ideated.
    2. With BI project team executives, discuss and assign dependencies between activities in the Dependencies columns. A dependency exists if:
    • An activity requires consideration of another activity.
    • An activity requires the completion of another activity.
    • Two activities should be part of the same initiative.
    • Two activities are very similar in nature.
  • Then discuss and assign priorities to each activity in the Priority column using input from previous Phases. For example, if an activity was previously indicated as critical to the business, if a similar activity appears multiple times, or if an activity has several dependencies, it should be higher priority.
  • Inputs

    • BI improvement activities created in Phases 1 and 2

    Output

    • Activities with dependencies and priorities

    Materials

    • BI Initiatives and Roadmap Tool

    Participants

    • BI project team

    Activity: Consolidate BI activities into the tool and assign dependencies and priorities (cont’d.)

    3.1.1

    2 hours

    Screenshot of Tab 3. BI Activities Repository, with samples improvement activities, dependencies, statuses, and priorities
    The image is of a screenshot of Tab 3. BI Activities Repository, with samples improvement activities, dependencies, statuses, and priorities.

    Revisit the outputs of your current state assessment and note which activities have already been completed in the “Status” column, to avoid duplication of your efforts.

    When classifying the status of items in your activity repository, distinguish between broader activities (potential initiatives) and granular activities (tasks).

    Activity: Customize project inputs and build out detailed improvement initiatives

    3.1.2

    1.5 hours

    1. Follow instructions on Tab 2. Inputs to customize inputs you would like to use for your project.
    2. Review the activities repository and select up to 12 overarching initiatives based on the activities with extreme or highest priority and your own considerations.
    • Rewording where necessary, transfer the names of your initiatives in the banners provided on Tab 4. Improvement Initiatives.
    • On Tab 3, indicate these activities as “Selected (initiatives)” in the Status column.
  • In Tab 4, develop detailed improvement initiatives by indicating the owner, taxonomy, start and end periods, cost and effort estimates, goal, benefit/value, and risks of each initiative.
  • Use drop-downs to list “Related activities,” which will become tasks under each initiative.
    • activities with dependency to the initiative
    • activities that lead to the same goal or benefit/value of the main initiative

    Screenshot of the Improvement Initiative template, to be used for developing comprehensive initiatives
    <p data-verified=The image is a screenshot of the Improvement Initiative template, to be used for developing comprehensive initiatives.">

    Inputs

    • Tab 3. Activities Repository

    Output

    • Unique and detailed improvement initiatives

    Materials

    • BI Initiatives and Roadmap Tool
    • BI Initiatives section of the BI Strategy and Roadmap Template

    Participants

    • BI project team

    Visual representations of your initiative landscape can aid in prioritizing tasks and executing the roadmap

    Building a comprehensive BI program will be a gradual process involving a variety of stakeholders. Different initiatives in your roadmap will either be completed sequentially or in parallel to one another, given dependencies and available resources. The improvement roadmap should capture and represent this information.

    To determine the order in which main initiatives should be completed, exercises such as a value–effort map can be very useful.

    Example: Value–Effort Map for a BI Project

    Initiatives that are high value–low effort are found in the upper left quadrant and are bolded; These may be your four primary initiatives. In addition, initiative five is valuable to the business and critical to the project’s success, so it too is a priority despite requiring high effort. Note that you need to consider dependencies to prioritize these key initiatives.
    Value–Effort Map for a BI Project
    1. Data profiling techniques training
    2. Improve usage metrics
    3. Communication plan for BI
    4. Staff competency evaluation
    5. Formalize practice capabilities
    6. Competency improvement plan program
    7. Metadata architecture improvements
    8. EDW capability improvements
    9. Formalize oversight for data manipulation

    This exercise is best performed using a white board and sticky notes, and axes can be customized to fit your needs (E.g. cost, risk, time, etc.).

    Activity: Build an overall BI strategy improvement roadmap for the entire project

    3.1.3

    45 minutes

    The BI Strategy Improvement Roadmap (Tab 5 of the BI Initiatives and Roadmap Tool) has been populated with your primary initiatives and related tasks. Read the instructions provided at the top of Tab 5.

    1. Use drop-downs to assign a Start Period and End Period to each initiative (already known) and each task (determined here). As you do so, the roadmap will automatically fill itself in. This is where the value–effort map or other prioritization exercises may help.
    2. Assign Task Owners reporting Managers.
    3. Update the Status and Notes columns on an ongoing basis. Hold meetings with task owners and managers about blocked or overdue items.
    • Updating status should also be an ongoing maintenance requirement for Tab 3 in order to stay up to date on which activities have been selected as initiatives or tasks, are completed, or are not yet acted upon.

    Screenshot of the BI Improvement Roadmap (Gantt chart) showing an example initiative with tasks, and assigned timeframes, owners, and status updates.

    INPUTS

    • Tab 3. Activities Repository
    • Tab 4. Improvement Initiatives

    OUTPUT

    • BI roadmap

    Materials

    • BI Initiatives and Roadmap Tool
    • Roadmap section of the BI Strategy and Roadmap Template

    Participants

    • BI project team

    Obtain approval for your BI strategy roadmap by organizing and presenting project findings

    Use a proprietary presentation template

    Recommended Participants

    • Project sponsor
    • Relevant IT & business executives
    • CIO
    • BI project team

    Materials & Requirements

    Develop your proprietary presentation template with:

    • Results from Phases 1 and 2 and Step 3.1
    • Information from:
      • Info-Tech’s Build a Reporting and Analytics Strategy
    • Screen shots of outputs from the:
      • BI Practice Assessment Tool
      • BI Initiatives and Roadmap Tool

    Next Steps

    Following the approval of your roadmap, begin to plan the implementation of your first initiatives.

    Overall Guidelines

    • Invite recommended participants to an approval meeting.
    • Present your project’s findings with the goal of gaining key stakeholder support for implementing the roadmap.
    1. Set the scene using BI vision & objectives.
    2. Present the results and roadmap next.
    3. Dig deeper into specific issues by touching on the important components of this blueprint to generate a succinct and cohesive presentation.
  • Make the necessary changes and updates stemming from discussion notes during this meeting.
  • Submit a formal summary of findings and roadmap to your governing body for review and approval (e.g. BI steering committee, BI CoE).
  • Info-Tech Insight

    At this point, it is likely that you already have the support to implement a data quality improvement roadmap. This meeting is about the specifics and the ROI.

    Maximize support by articulating the value of the data quality improvement strategy for the organization’s greater information management capabilities. Emphasize the business requirements and objectives that will be enhanced as a result of tackling the recommended initiatives, and note any additional ramifications of not doing so.

    Leverage Info-Tech’s presentation template to present your BI strategy to the executives

    Use the BI Strategy and Roadmap Executive Presentation Template to present your most important findings and brilliant ideas to the business executives and ensure your BI program is endorsed. Business executives can also learn about how the BI strategy empowers them and how they can help in the BI journey.

    Important Messages to Convey

    • Executive summary of the presentation
    • Current challenges faced by the business
    • BI benefits and associated opportunities
    • SWOT analyses of the current BI
    • BI end-user satisfaction survey
    • BI vision, mission, and goals
    • BI initiatives that take you to the future state
    • (Updated) Analytical Strategy
    • Roadmap that depicts the timeline

    STEP 3.2

    Continuous Improvement Opportunities for BI

    Create supplementary policies and programs to augment your BI strategy

    Step Objectives

    • Develop a plan for encouraging users to continue to use Excel, but in a way that does not compromise overall BI effectiveness.
    • Take steps to establish a positive organizational culture around BI.

    Step Activities

    3.2.1 Construct a concrete policy to integrate Excel use with your new BI strategy.

    3.2.2 Map out the foundation for a BI Ambassador network.

    Outcomes

    • Business user understanding of where Excel manipulation should and should not occur
    • Foundation for recognizing exceptional BI users and encouraging development of enterprise-wide business intelligence

    Research Support

    • Info-Tech’s BI Initiatives and Roadmap Tool
    • Info-Tech’s BI Strategy and Roadmap Template

    Proposed Participants in this Step

    Project Manager

    Project Team

    Additional Business Users

    Establish Excel governance to better serve Excel users while making sure they comply with policies

    Excel is the number one BI tool

    • BI applications are developed to support information needs.
    • The reality is that you will never migrate all Excel users to BI. Some Excel users will continue to use it. The key is to support them while imposing governance.
    • The goal is to direct them to use the data in BI or in the data warehouse instead of extracting their own data from various source systems.

    The Tactic: Centralize data extraction and customize delivery

    • Excel users formerly extracted data directly from the production system, cleaned up the data, manipulated the data by including their own business logic, and presented the data in graphs and pivot tables.
    • With BI, the Excel users can still use Excel to look at the information. The only difference is that BI or data warehouse will be the data source of their Excel workbook.

    Top-Down Approach

    • An Excel policy should be created at the enterprise level to outline which Excel use cases are allowed, and which are not.
    • Excel use cases that involve extracting data from source systems and transforming that data using undisclosed business rules should be banned.
    • Excel should be a tool for manipulating, filtering, and presenting data, not a tool for extracting data and running business rules.

    Excel

    Bottom-Up Approach

    • Show empathy to your users. They just want information to get their work done.
    • A sub-optimal information landscape is the root cause, and they are the victims. Excel spreadmarts are the by-products.
    • Make the Excel users aware of the risks associated with Excel, train them in BI, and provide them with better information in the BI platform.

    Activity: Create an Excel governance policy

    3.2.1

    4 hours

    Construct a policy around Excel use to ensure that Excel documents are created and shared in a manner that does not compromise the integrity of your overall BI program.

    1. Review the information artifact list harvested from Step 2.1 and identify all existing Excel-related use cases.
    2. Categorize the Excel use cases into “allowed,” “not allowed,” and “not sure.” For each category define:
    3. Category To Do: Policy Context
      Allowed Discuss what makes these use cases ideal for BI. Document use cases, scenarios, examples, and reasons that allow Excel as an information artifact.
      Not Allowed Discuss why these cases should be avoided. Document forbidden use cases, scenarios, examples, and reasons that use Excel to generate information artifacts.
      Not Sure Discuss the confusions; clarify the gray area. Document clarifications and advise how end users can get help in those “gray area” cases.
    4. Document the findings in the BI Strategy and Roadmap Template in the Manage and Sustain BI Strategy section, or a proprietary template. You may also need to create a separate Excel policy to communicate the Dos and Don’ts.

    Inputs

    • Step 2.1 – A list of information artifacts

    Output

    • Excel-for-BI Use Policy

    Materials

    • BI Strategy Roadmap and Template, or proprietary document

    Participants

    • Business executives
    • CIO
    • Head of BI
    • BI team

    Build a network of ambassadors to promote BI and report to IT with end-user feedback and requests

    The Building of an Insider Network: The BI Ambassador Network

    BI ambassadors are influential individuals in the organization that may be proficient at using BI tools but are passionate about analytics. The network of ambassadors will be IT’s eyes, ears, and even mouth on the frontline with users. Ambassadors will promote BI, communicate any messages IT may have, and keep tabs on user satisfaction.

    Ideal candidate:

    • A good relationship with IT.
    • A large breadth of experience with BI, not just one dashboard.
    • Approachable and well-respected amongst peers.
    • Has a passion for driving organizational change using BI and continually looking for opportunities to innovate.

    Push

    • Key BI Messages
    • Best Practices
    • Training Materials

    Pull

    • Feedback
    • Complaints
    • Thoughts and New Ideas

    Motivate BI ambassadors with perks

    You need to motivate ambassadors to take on this additional responsibility. Make sure the BI ambassadors are recognized in their business units when they go above and beyond in promoting BI.

    Reward Approach Reward Type Description
    Privileges High Priority Requests Given their high usage and high visibility, ambassadors’ BI information requests should be given a higher priority.
    First Look at New BI Development Share the latest BI updates with ambassadors before introducing them to the organization. Ambassadors may even be excited to test out new functionality.
    Recognition Featured in Communications BI ambassadors’ use cases and testimonials can be featured in BI communications. Be sure to create a formal announcement introducing the ambassadors to the organization.
    BI Ambassador Certificate A certificate is a formal way to recognize their efforts. They can also publicly display the certificate in their workspace.
    Rewards Appointed by Senior Executives Have the initial request to be a BI ambassador come from a senior executive to flatter the ambassador and position the role as a reward or an opportunity for success.
    BI Ambassador Awards Award an outstanding BI ambassador for the year. The award should be given by the CEO in a major corporate event.

    Activity: Plan for a BI ambassador network

    3.2.2

    2 hours

    Identify individuals within your organization to act as ambassadors for BI and a bridge between IT and business users.

    1. Obtain a copy of your latest organizational chart. Review your most up-to-date organizational chart and identify key BI consumers across a variety of functional units. In selecting potential BI ambassadors, reflect on the following questions:
    • Does this individual have a good relationship with IT?
    • What is the depth of their experience with developing/consuming business intelligence?
    • Is this individual respected and influential amongst their respective business units?
    • Has this individual shown a passion for innovating within their role?
  • Create a mandate and collateral detailing the roles and responsibilities for the ambassador role, e.g.:
    • Promote BI to members of your group
    • Represent the “voice of the data consumers”
  • Approach the ambassador candidates and explain the responsibilities and perks of the role, with the goal of enlisting about 10-15 ambassadors
  • Inputs

    • An updated organizational chart
    • A list of BI users

    Output

    • Draft framework for BI ambassador network

    Materials

    • BI Strategy and Roadmap Template or proprietary document

    Participants

    • Business executives
    • CIO
    • Head of BI
    • BI team

    Keeping tabs on metadata is essential to creating a data democracy with BI

    A next generation BI not only provides a platform that mirrors business requirements, but also creates a flexible environment that empowers business users to explore data assets without having to go back and forth with IT to complete queries.

    Business users are generally not interested in the underlying architecture or the exact data lineages; they want access to the data that matters most for decision-making purposes.

    Metadata is data about data

    It comes in the form of structural metadata (information about the spaces that contain data) and descriptive metadata (information pertaining to the data elements themselves), in order to answer questions such as:

    • What is the intended purpose of this data?
    • How up-to-date is this information?
    • Who owns this data?
    • Where is this data coming from?
    • How have these data elements been transformed?

    By creating effective metadata, business users are able to make connections between and bring together data sources from multiple areas, creating the opportunity for holistic insight generation.

    Like BI, metadata lies in the Information Dimension layer of our data management framework.

    The metadata needs to be understood before building anything. You need to identify fundamentals of the data, who owns not only that data, but also its metadata. You need to understand where the consolidation is happening and who owns it. Metadata is the core driver and cost saver for building warehouses and requirements gathering.

    – Albert Hui, Principal, Data Economist

    Deliver timely, high quality, and affordable information to enable fast and effective business decisions

    In order to maximize your ROI on business intelligence, it needs to be treated less like a one-time endeavor and more like a practice to be continually improved upon.

    Though the BI strategy provides the overall direction, the BI operating model – which encompasses organization structure, processes, people, and application functionality – is the primary determinant of efficacy with respect to information delivery. The alterations made to the operating model occur in the short term to improve the final deliverables for business users.

    An optimal BI operating model satisfies three core requirements:

    Timeliness

    Effectiveness

  • Affordability
  • Bring tangible benefits of your revamped BI strategy to business users by critically assessing how your organization delivers business intelligence and identifying opportunities for increased operational efficiency.

    Assess and Optimize BI Operations

    Focus on delivering timely, quality, and affordable information to enable fast and effective business decisions

    Implement a fit-for-purpose BI and analytics solution to augment your next generation BI strategy

    Organizations new to business intelligence or with immature BI capabilities are under the impression that simply getting the latest-and-greatest tool will provide the insights business users are looking for.

    BI technology can only be as effective as the processes surrounding it and the people leveraging it. Organizations need to take the time to select and implement a BI suite that aligns with business goals and fosters end-user adoption.

    As an increasing number of companies turn to business intelligence technology, vendors are responding by providing BI and analytics platforms with more and more features.

    Our vendor landscape will simplify the process of selecting a BI and analytics solution by:

    Differentiating between the platforms and features vendors are offering.

    Detailing a robust framework for requirements gathering to pinpoint your organization’s needs.

    Developing a high-level plan for implementation.

    Select and Implement a Business Intelligence and Analytics Solution

    Find the diamond in your data-rough using the right BI & Analytics solution

    If you want additional support, have our analysts guide you through this phase as part of an Info-Tech workshop

    Book a workshop with our Info-tech analysts:

    • To accelerate this project, engage your IT team in an Info-Tech workshop with an Info-Tech analyst team.
    • Info-Tech analysts will join you and your team onsite at your location or welcome you to Info-Tech’s historic Toronto office to participate in an innovative onsite workshop.
    • Contact your account manager (www.infotech.com/account), or email Workshops@InfoTech.com for more information.

    The following are sample activities that will be conducted by Info-tech analysts with your team:

    3.1.1-3.1.3

    Construct a BI improvement initiative roadmap

    During these activities, your team will consolidate the list of BI initiatives generated from the assessments conducted in previous phases, assign timelines to each action, prioritize them using a value–effort matrix, and finally produce a roadmap for implementing your organization’s BI improvement strategy.

    3.2

    Identify continuous improvement opportunities for BI

    Our analyst team will work with your organization to ideate supplementary programs to support your BI strategy. Defining Excel use cases that are permitted and prohibited in conjunction with your BI strategy, as well as structuring an internal BI ambassador network, are a few extra initiatives that can enhance your BI improvement plans.

    Insight breakdown

    Your BI platform is not a one-and-done initiative.

    A BI program is not a static project that is created once and remains unchanged. Your strategy must be treated as a living platform to be revisited and revitalized in order to provide effective enablement of business decision making. Develop a BI strategy that propels your organization by building it on business goals and objectives, as well as comprehensive assessments that quantitatively and qualitatively evaluate your current BI capabilities.

    Put the “B” back in “BI.”

    The closer you align your new BI platform to real business interests, the stronger will be the buy-in, realized value, and groundswell of enthusiastic adoption. Ultimately, getting this phase right sets the stage to best realize a strong ROI for your investment in the people, processes, and technology that will be your next generation BI platform.

    Go beyond the platform.

    BI success is not based solely on the technology it runs on; technology cannot mask gaps in capabilities. You must be capable in your environment – data management, data quality, and related data practices must be strong, otherwise the usefulness of the intelligence suffers. The best BI solution does not only provide a technology platform, but also addresses the elements that surround the platform. Look beyond tools and holistically assess the maturity of your BI practice with input from both the BI consumer and provider perspectives.

    Appendix

    Detailed list of BI Types

    Style Description Strategic Importance (1-5) Popularity (1-5) Effort (1-5)
    Standards Preformatted reports Standard, preformatted information for backward-looking analysis. 5 5 1
    User-defined analyses Pre-staged information where “pick lists” enable business users to filter (select) the information they wish to analyze, such as sales for a selected region during a selected previous timeframe. 5 4 2
    Ad-hoc analyses Power users write their own queries to extract self-selected pre-staged information and then use the information to perform a user-created analysis. 5 4 3
    Scorecards and dashboards Predefined business performance metrics about performance variables that are important to the organization, presented in a tabular or graphical format that enables business users to see at a glance how the organization is performing. 4 4 3
    Multidimensional analysis (OLAP) Multidimensional analysis (also known as On-line analytical processing): Flexible tool-based user-defined analysis of business performance and the underlying drivers or root causes of that performance. 4 3 3
    Alerts Predefined analyses of key business performance variables, comparison to a performance standard or range, and communication to designated businesspeople when performance is outside the predefined performance standard or range. 4 3 3
    Advanced Analytics Application of long-established statistical and/or operations research methods to historical business information to look backward and characterize a relevant aspect of business performance, typically by using descriptive statistics 5 3 4
    Predictive Analytics Application of long-established statistical and/or operations research methods to historical business information to predict, model, or simulate future business and/or economic performance and potentially prescribe a favored course of action for the future 5 3 5

    Our BI strategy approach follows Info-Tech’s popular IT Strategy Framework

    A comprehensive BI strategy needs to be developed under the umbrella of an overall IT strategy. Specifically, creating a BI strategy is contributing to helping IT mature from a firefighter to a strategic partner that has close ties with business units.

    1. Determine mandate and scope 2. Assess drivers and constraints 3. Evaluate current state of IT 4. Develop a target state vision 5. Analyze gaps and define initiatives 6. Build a roadmap 8. Revamp 7. Execute
    Mandate Business drivers Holistic assessments Vision and mission Initiatives Business-driven priorities
    Scope External drivers Focus-area specific assessments Guiding principles Risks
    Project charter Opportunities to innovate Target state vision Execution schedule
    Implications Objectives and measures

    This BI strategy blueprint is rooted in our road-tested and proven IT strategy framework as a systematic method of tackling strategy development.

    Research contributors

    Internal Contributors

    • Andy Woyzbun, Executive Advisor
    • Natalia Nygren Modjeska, Director, Data & Analytics
    • Crystal Singh, Director, Data & Analytic
    • Andrea Malick, Director, Data & Analytics
    • Raj Parab, Director, Data & Analytics
    • Igor Ikonnikov, Director, Data & Analytics
    • Andy Neill, Practice Lead, Data & Analytics
    • Rob Anderson, Manager Sales Operations
    • Shari Lava, Associate Vice-President, Vendor Advisory Practice

    External Contributors

    • Albert Hui, Principal, DataEconomist
    • Cameran Hetrick, Senior Director of Data Science & Analytics, thredUP
    • David Farrar, Director – Marketing Planning & Operations, Ricoh Canada Inc
    • Emilie Harrington, Manager of Analytics Operations Development, Lowe’s
    • Sharon Blanton, VP and CIO, The College of New Jersey
    • Raul Vomisescu, Independent Consultant

    Research contributors and experts

    Albert Hui

    Consultant, Data Economist

    Albert Hui is a cofounder of Data Economist, a data-consulting firm based in Toronto, Canada. His current assignment is to redesign Scotiabank’s Asset Liability Management for its Basel III liquidity compliance using Big Data technology. Passionate about technology and problem solving, Albert is an entrepreneur and result-oriented IT technology leader with 18 years of experience in consulting and software industry. His area of focus is on data management, specializing in Big Data, business intelligence, and data warehousing. Beside his day job, he also contributes to the IT community by writing blogs and whitepapers, book editing, and speaking at technology conferences. His recent research and speaking engagement is on machine learning on Big Data.

    Albert holds an MBA from the University of Toronto and a master’s degree in Industrial Engineering. He has twin boys and enjoys camping and cycling with them in his spare time.
    Albert Hui Consultant, Data Economist

    Cameran Hetrick

    Senior Director of Analytics and Data Science, thredUP

    Cameran is the Senior Director of Analytics and Data Science at thredUP, a startup inspiring a new generation to think second hand first. There she helps drives top line growth through advanced and predictive analytics. Previously, she served as the Director of Data Science at VMware where she built and led the data team for End User Computing. Before moving to the tech industry, she spent five years at The Disneyland Resort setting ticket and hotel prices and building models to forecast attendance. Cameran holds an undergraduate degree in Economics/Mathematics from UC Santa Barbara and graduated with honors from UC Irvine's MBA program.
    Cameran Hetrick Senior Director of Analytics and Data Science, thredUP

    Bibliography

    Bange, Carsten and Wayne Eckerson. “BI and Data Management in the Cloud: Issues and Trends.” BARC and Eckerson Group, January 2017. Web.

    Business Intelligence: The Strategy Imperative for CIOs. Tech. Information Builders. 2007. Web. 1 Dec. 2015.

    COBIT 5: Enabling Information. Rolling Meadows, IL: ISACA, 2013. Web.

    Dag, Naslund, Emma Sikander, and Sofia Oberg. "Business Intelligence - a Maturity Model Covering Common Challenges." Lund University Publications. Lund University, 2014. Web. 23 Oct. 2015.

    “DAMA Guide to the Data Management Body of Knowledge (DAMA-DMBOK Guide).” First Edition. DAMA International. 2009. Digital. April 2014.

    Davenport, Thomas H. and Bean, Randy. “Big Data and AI Executive Survey 2019.” NewVantage Partners LLC. 2019. Web.

    "Debunking the Business of Analytics." Experian Data Quality. Sept. 2013. Web.

    Bibliography

    Drouin, Sue. "Value Chain." SAP Analytics. February 27, 2015.

    Farrar, David. “BI & Data analytics workshop feedback.” Ricoh Canada. Sept. 2019.

    Fletcher, Heather. "New England Patriots Use Analytics & Trigger Emails to Retain Season Ticket Holders." Target Marketing. 1 Dec. 2011. Web.

    Gonçalves, Alex. "Social Media Analytics Strategy - Using Data to Optimize Business Performance.” Apress. 2017.

    Imhoff, Claudia, and Colin White. "Self Service Business Intelligence: Empowering Users to Generate Insights." SAS Resource Page. The Data Warehouse Institute, 2011. Web.

    Khamassi, Ahmed. "Building An Analytical Roadmap : A Real Life Example." Wipro. 2014.

    Kuntz, Jerry, Pierre Haren, and Rebecca Shockley. IBM Insight 2015 Teleconference Series. Proc. of Analytics: The Upside of Disruption. IBM Institute for Business Value, 19 Oct. 2015. Web.

    Kwan, Anne , Maximillian Schroeck, Jon Kawamura. “Architecting and operating model, A platform for accelerating digital transformation.” Part of a Deliotte Series on Digital Industrial Transformation, 2019. Web.

    Bibliography

    Lebied, Mona. "11 Steps on Your BI Roadmap To Implement A Successful Business Intelligence Strategy." Business Intelligence. July 20, 2018. Web.

    Light, Rob. “Make Business Intelligence a Necessity: How to Drive User Adoption.” Sisense Blog. 30 July 2018.

    Mazenko, Elizabeth. “Avoid the Pitfalls: 3 Reasons 80% of BI Projects Fail.” BetterBuys. October 2015.

    Marr, Bernard. "Why Every Business Needs A Data And Analytics Strategy.” Bernard Marr & Co. 2019.

    Mohr, Niko and Hürtgen, Holger. “Achieving Business Impact with Data.” McKinsey. April 2018.

    MIT Sloan Management

    Quinn, Kevin R. "Worst Practices in Business Intelligence: Why BI Applications Succeed Where BI Tools Fail." (2007): 1-19. BeyeNetwork. Information Builders, 2007. Web. 1 Dec. 2015.

    Ringdal, Kristen. "Learning multilevel Analysis." European social Survey. 2019.

    Bibliography

    Schaefer, Dave, Ajay Chandramouly, Burt Carmak, and Kireeti Kesavamurthy. "Delivering Self-Service BI, Data Visualization, and Big Data Analytics." IT@Intel White Paper (2013): 1-11. June 2013. Web. 30 Nov. 2015.

    Schultz, Yogi. “About.” Corvelle Consulting. 2019.

    "The Current State of Analytics: Where Do We Go From Here?" SAS Resource Page. SAS & Bloomberg Businessweek, 2011. Web.

    "The Four Steps to Defining a Customer Analytics Strategy." CCG Analytics Solutions & Services. Nov 10,2017.

    Traore, Moulaye. "Without a strategic plan, your analytics initiatives are risky." Advisor. March 12, 2018. web.

    Wells, Dave. "Ten Mistakes to Avoid When Gathering BI Requirements." Engineering for Industry. The Data Warehouse Institute, 2008. Web.

    “What is a Business Intelligence Strategy and do you need one?” Hydra. Sept 2019. Web.

    Williams, Steve. “Business Intelligence Strategy and Big Data Analytics.” Morgan Kaufman. 2016.

    Wolpe, Toby. "Case Study: How One Firm Used BI Analytics to Track Staff Performance | ZDNet." ZDNet. 3 May 2013. Web.

    Yuk, Mico. “11 Reasons Why Most Business Intelligence Projects Fail.” Innovative enterprise Channels. May 2019.

    Set a Strategic Course of Action for the PMO in 100 Days

    • Buy Link or Shortcode: {j2store}356|cart{/j2store}
    • member rating overall impact: 9.3/10 Overall Impact
    • member rating average dollars saved: $13,744 Average $ Saved
    • member rating average days saved: 19 Average Days Saved
    • Parent Category Name: Project Management Office
    • Parent Category Link: /project-management-office
    • As a new PMO director, you’ve been thrown into the middle of an unfamiliar organizational structure and a chaotic project environment.
    • The expectations are that the PMO will help improve project outcomes, but beyond that your mandate as PMO director is opaque.
    • You know that the statistics around PMO longevity aren’t good, with 50% of new PMOs closing within the first three years. As early in your tenure as possible, you need to make sure that your stakeholders understand the value that your role could provide to the organization with the right level of buy-in and support.
    • Whether you’re implementing a new PMO or taking over an already existing one, you need to quickly overcome these challenges by rapidly assessing your unfamiliar tactical environment, while at the same time demonstrating confidence and effective leadership to project staff, business stakeholders, and the executive layer.

    Our Advice

    Critical Insight

    • The first 100 days are critical. You have a window of influence where people are open to sharing insights and opinions because you were wise enough to seek them out. If you don’t reach out soon, people notice and assume you’re not wise enough to seek them out, or that you don’t think they are important enough to involve.
    • PMOs most commonly stumble when they shortsightedly provide project management solutions to what are, in fact, more complex, systemic challenges requiring a mix of project management, portfolio management, and organizational change management capabilities. If you fail to accurately diagnose pain points and needs in your first days, you could waste your tenure as PMO leader providing well-intentioned solutions to the wrong project problems.
    • You have diminishing value on your time before skepticism and doubt start to erode your influence. Use your first 100 days to define an appropriate mandate for your PMO, get the right people behind you, and establish buy-in for long-term PMO success.

    Impact and Result

    • Develop an action plan to help leverage your first 100 days on the job. Hit the ground running in your new role with an action plan to achieve realistic goals and milestones in your first 100 days. A results-driven first three months will help establish roots throughout the organization that will continue to feed and grow the PMO beyond your first year.
    • Get to know what you don’t know quickly. Use Info-Tech’s advice and tools to perform a triage of every aspect of PMO accountability as well as harvest stakeholder input to ensure that your PMO meets or exceeds expectations and establishes the right solutions to the organization’s project challenges.
    • Solidify the PMO’s long-term mission. Adopt our stakeholder engagement best practices to ensure that you knock on the right doors early in your tenure. Not only do you need to clarify expectations, but you will ultimately need buy-in from key stakeholders as you move to align the mandate, authority, and resourcing needed for long-term PMO success.

    Set a Strategic Course of Action for the PMO in 100 Days Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out how capitalizing on your first 100 days as PMO leader can help ensure the long-term success of your PMO.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Survey the project landscape

    Get up-to-speed quickly on key PMO considerations by engaging PMO sponsors, assessing stakeholders, and taking stock of your PMO inventory.

    • Set a Strategic Course of Action for the PMO in 100 Days – Phase 1: Survey the Project Landscape
    • Mission Identification and Inventory Tool
    • PMO Director First 100 Days Timeline - MS Project
    • PMO Director First 100 Days Timeline - MS Excel

    2. Gather PMO requirements

    Make your first major initiative as PMO director be engaging the wider pool of PMO stakeholders throughout the organization to determine their expectations for your office.

    • Set a Strategic Course of Action for the PMO in 100 Days – Phase 2: Gather PMO Requirements
    • PMO Requirements Gathering Tool
    • PMO Course of Action Stakeholder Interview Guide

    3. Solidify your PPM goals

    Review the organization’s current PPM capabilities in order to identify your ability to meet stakeholder expectations and define a sustainable mandate.

    • Set a Strategic Course of Action for the PMO in 100 Days – Phase 3: Solidify Your PPM Goals
    • Project Portfolio Management Maturity Assessment Workbook
    • Project Management Maturity Assessment Workbook
    • Organizational Change Management Maturity Assessment Workbook
    • PMO Strategic Expectations Glossary

    4. Formalize the PMO’s mandate

    Communicate your strategic vision for the PMO and garner stakeholder buy-in.

    • Set a Strategic Course of Action for the PMO in 100 Days – Phase 4: Formalize the PMO's Mandate
    • PMO Mandate and Strategy Roadmap Template
    • PMO Director Peer Feedback Evaluation Template
    • PMO Director First 100 Days Self-Assessment Tool
    [infographic]

    Workshop: Set a Strategic Course of Action for the PMO in 100 Days

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Assess the Current Project Ecosystem

    The Purpose

    Quickly develop an on-the-ground view of the organization’s project ecosystem and the PMO’s abilities to effectively serve.

    Key Benefits Achieved

    A comprehensive and actionable understanding of the PMO’s tactical environment

    Activities

    1.1 Perform a PMO SWOT analysis.

    1.2 Assess the organization’s portfolio management, project management, and organizational change management capability levels.

    1.3 Take inventory of the PMO’s resourcing levels, project demand levels, and tools and artifacts.

    Outputs

    Overview of current strengths, weaknesses, opportunities, and threats

    Documentation of your current process maturity to execute key portfolio management, project management, and organizational change management functions

    Stock of the PMO’s current access to PPM personnel relative to total project demand

    2 Analyze PMO Stakeholders

    The Purpose

    Determine stakeholder expectations for the PMO.

    Key Benefits Achieved

    An accurate understanding of others’ expectations to help ensure the PMO’s course of action is responsive to organizational culture and strategy

    Activities

    2.1 Conduct a PMO Mission Identification Survey with key stakeholders.

    2.2 Map the PMO’s stakeholder network.

    2.3 Analyze key stakeholders for influence, interest, and support.

    Outputs

    An understanding of expected PMO outcomes

    A stakeholder map and list of key stakeholders

    A prioritized PMO requirements gathering elicitation plan

    3 Determine Strategic Expectations and Define the Tactical Plan

    The Purpose

    Develop a process and method to turn stakeholder requirements into a strategic vision for the PMO.

    Key Benefits Achieved

    A strategic course of action for the PMO that is responsive to stakeholders’ expectations.

    Activities

    3.1 Assess the PMO’s ability to support stakeholder expectations.

    3.2 Use Info-Tech’s PMO Strategic Expectations glossary to turn raw process and service requirements into specific strategic expectations.

    3.3 Define an actionable tactical plan for each of the strategic expectations in your mandate.

    Outputs

    An understanding of PMO capacity and limits

    A preliminary PMO mandate

    High-level statements of strategy to help support your mandate

    4 Formalize the PMO’s Mandate and Roadmap

    The Purpose

    Establish a final PMO mandate and a process to help garner stakeholder buy-in to the PMO’s long-term vision.

    Key Benefits Achieved

    A viable PMO course of action complete with stakeholder buy-i

    Activities

    4.1 Finalize the PMO implementation timeline.

    4.2 Finalize Info-Tech’s PMO Mandate and Strategy Roadmap Template.

    4.3 Present the PMO’s strategy to key stakeholders.

    Outputs

    A 3-to-5-year implementation timeline for key PMO process and staffing initiatives

    A ready-to-present strategy document

    Stakeholder buy-in to the PMO’s mandate

    Enable Product Delivery – Executive Leadership Workshop

    • Buy Link or Shortcode: {j2store}353|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Development
    • Parent Category Link: /development
    • You need to clearly convey the direction and strategy of your product portfolio to gain alignment, support, and funding from your organization.
    • IT organizations are traditionally organized to deliver initiatives in specific periods of time. This conflicts with product delivery, which continuously delivers value over the lifetime of a product.
    • Delivering multiple products together creates additional challenges because each product has its own pedigree, history, and goals.

    Our Advice

    Critical Insight

    • Empowered product managers and product owners are the key to ensuring your delivery teams are delivering the right value at the right time to the right stakeholders.
    • Establishing operationally aligned product families helps bridge the gap between enterprise priorities and product enhancements.
    • Leadership must be aligned to empower and support Agile values and product teams to unlock the full value realization within your organization.

    Impact and Result

    • Common understanding of product management and Agile delivery.
    • Commitment to support and empower product teams.

    Enable Product Delivery – Executive Leadership Workshop Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Enabling Product Delivery – Executive workshop to align senior leadership with their transition to product management and delivery.

    • Enabling Product Delivery – Executive Workshop Storyboard

    2. Enabling Product Delivery –Executive Workshop Outcomes.

    • Enabling Product Delivery – Executive Workshop Outcomes
    [infographic]

    Workshop: Enable Product Delivery – Executive Leadership Workshop

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Understanding Your Top Challenges

    The Purpose

    Understand the drivers for your product transformation.

    Key Benefits Achieved

    Define the drivers for your transition to product-centric delivery.

    Activities

    1.1 What is driving your organization to become product focused?

    Outputs

    List of challenges and drivers

    2 Transitioning From Projects to Product-Centric Delivery

    The Purpose

    Understand the product transformation journey and differences.

    Key Benefits Achieved

    Identify the cultural, behavioral, and leadership changes needed for a successful transformation.

    Activities

    2.1 Define the differences between projects and product delivery

    Outputs

    List of differences

    3 Enterprise Agility and the Value of Change

    The Purpose

    Understand why smaller iterations increase value realization and decrease accumulated risk.

    Key Benefits Achieved

    Leverage smaller iterations to reduce time to value and accumulated risk to core operations.

    Activities

    3.1 What is business agility?

    Outputs

    Common understanding about the value of smaller iterations

    4 Defining Products and Product Management in Your Context

    The Purpose

    Establish an organizational starting definition of products.

    Key Benefits Achieved

    Tailor product management to meet the needs and vision of your organization.

    Activities

    4.1 What is a product? Who are your consumers?

    4.2 Identify enablers and blockers of product ownership

    4.3 Define a set of guiding principles for product management

    Outputs

    Product definition

    List of enablers and blockers of product ownership

    Set of guiding principles for product management

    5 Connecting Product Management to Agile Practices

    The Purpose

    Understand the relationship between product management and product delivery.

    Key Benefits Achieved

    Optimize product management to prioritize the right changes for the right people at the right time.

    Activities

    5.1 Discussions

    Outputs

    Common understanding

    6 Commit to Empowering Agile Product Teams

    The Purpose

    Personalize and commit to supporting product teams.

    Key Benefits Achieved

    Embrace leadership and cultural changes needed to empower and support teams.

    Activities

    6.1 Your management culture

    6.2 Personal Cultural Stop, Start, and Continue

    6.3 Now, Next, Later to support product owners

    Outputs

    Your management culture map

    Personal Cultural Stop, Start, and Continue list

    Now, Next, Later roadmap

    Further reading

    Enable Product Delivery – Executive Leadership Workshop

    Strengthen product management in your organization through effective executive leadership by focusing on product teams, core capabilities, and proper alignment.

    Objective of this workshop

    To develop a common understanding and foundation for product management so we, as leaders, better understand how to lead product owners, product managers, and their teams.

    Enable Product Delivery - Executive Leadership Workshop

    Learn how enterprise agility can provide lasting value to the organization

    Clarify your role in supporting your teams to deliver lasting value to stakeholders and customers

    1. Understanding Your Top Challenges
      • Define your challenges, goals, and opportunities Agile and product management will impact.
    2. Transitioning from Projects to Product-centric Delivery
      • Understand the shift from fixed delivery to continuous improvement and delivery of value.
    3. Enterprise Agility and the Value of Change
      • Organizations need to embrace change and leverage smaller delivery cycles.
    4. Defining Your "Products" and Product Management
      • Define products in your culture and how to empower product delivery teams.
    5. Connecting Product Management to Agile Practices
      • Use product ownership to drive increased ROI into your product delivery teams and lifecycles.
    6. Commit to Empowering Agile Product Teams
      • Define the actions and changes you must make for this transformation to be successful.

    Your Product Transformation Journey

    1. Make the Case for Product Delivery
      • Align your organization with the practices to deliver what matters most
    2. Enable Product Delivery – Executive Workshop
      • One-day executive workshop – align and prepare your leadership
      • Audience: Senior executives and IT leadership.
        Size: 8-16 people
        Time: 6 hours
    3. Deliver on Your Digital Product Vision
      • Enhance product backlogs, roadmapping, and strategic alignment
      • Audience: Product Owners/Mangers
        Size: 10-20 people
        Time: 3-4 days
    4. Deliver Your Digital Products at Scale
      • Scale Product Families to Align Enterprise Goals
      • Audience: Product Owners/Mangers
        Size: 10-20 people
        Time: 3-4 days
    5. Mature and Scale Product Ownership
      • Align and mature your product owners
      • Audience: Product Owners/Mangers
        Size: 8-16 people
        Time: 2-4 days

    Repeat workshops with different companies, operating units, departments, or teams as needed.

    What is a workshop?

    We WILL ENGAGE in discussions and activities:

    • Flexible, to accommodate the needs of the group.
    • Open forum for discussion and questions.
    • Share your knowledge, expertise, and experiences (roadblocks and success stories).
    • Everyone is part of the process.
    • Builds upon itself.

    This workshop will NOT be:

    • A lecture or class.
    • A monologue that never ends.
    • Technical training.
    • A presentation.
    • Us making all the decisions.

    Roles within the workshop

    We each have a role to play to make our workshop successful!

    Facilitators

    • Introduce the best practice framework used by Info-Tech.
    • Ask questions about processes, procedures, and assumptions.
    • Guide for the methodology.
    • Liaison for any other relevant Info-Tech research or services.

    Participants

    • Contribute and speak out as much as needed.
    • Provide expertise on the current processes and technology.
    • Ask questions.
    • Provide feedback.
    • Collaborate and work together to produce solutions.

    Understanding Your Top Challenges

    • Understanding Your Top Challenges
    • Transitioning From Projects to Product-Centric Delivery
    • Enterprise Agility and the Value of Change
    • Defining Your Products and Product Management
    • Connecting Product Management to Agile Practices
    • Commit to Empowering Agile Product Teams
    • Wrap-Up and Retrospective

    Executive Summary

    Your Challenge

    • Products are the lifeblood of an organization. They deliver the capabilities needed to deliver value to customers, internal users, and stakeholders.
    • The shift to becoming a product organization is intended to continually increase the value you provide to the broader organization as you grow and evolve.
    • You need to clearly convey the direction and strategy of your product portfolio to gain alignment, support, and funding from your organization.

    Common Obstacles

    • IT organizations are traditionally organized to deliver initiatives in specific periods of time. This conflicts with product delivery, which continuously delivers value over the lifetime of a product.
    • Delivering multiple products together creates additional challenges because each product has its own pedigree, history, and goals.
    • Product owners struggle to prioritize changes to deliver product value. This creates a gap and conflict between product and enterprise goals.

    Info-Tech's Approach

    Info-Tech's approach will guide you through:

    • Understanding the top challenges driving your product initiative.
    • Improving your transitioning from projects to product-centric delivery.
    • Enhancing enterprise agility and the value of change.
    • Defining products and product management in your context.
    • Connecting product management to Agile practices.
    • Committing to empowering Agile Product teams.
    This is an image of an Info-Tech Thought Map for Accelerate Your Transition to Product Delivery
    This is an image of an Info-Tech Thought Map for Delier on your Digital Product Vision
    This is an image of an Info-Tech Thought Map for Deliver Digital Products at Scale via Enterprise Product Families.
    This is an image of an Info-Tech Thought Map for What We Mean by an Applcation Department Strategy.

    What is driving your organization to become product focused?

    30 minutes

    • Team introductions:
      • Share your name and role
      • What are the key challenges you are looking to solve around product management?
      • What blockers or challenges will we need to overcome?

    Capture in the Enable Product Delivery – Executive Leadership Workshop Outcomes and Next Steps.

    Input

    • Organizational knowledge
    • Goals and challenges

    Output

    • List of key challenges
    • List of workshop expectations
    • Parking lot items

    Transitioning From Projects to Product-Centric Delivery

    • Understanding Your Top Challenges
    • Transitioning From Projects to Product-Centric Delivery
    • Enterprise Agility and the Value of Change
    • Defining Your Products and Product Management
    • Connecting Product Management to Agile Practices
    • Commit to Empowering Agile Product Teams
    • Wrap-Up and Retrospective

    Define the differences between projects and product delivery

    30 minutes

    • Consider project delivery and product delivery.
    • Discussion:
      • What are some differences between the two?

    Capture in the Enable Product Delivery – Executive Leadership Workshop Outcomes and Next Steps.

    Input

    • Organizational knowledge
    • Internal terms and definitions

    Output

    • List of differences between projects and product delivery

    Define the differences between projects and product delivery

    15 minutes

    Project Delivery

    vs

    Product Delivery

    Point in time

    What is changed

    Method of funding changes

    Needs an owner

    Input

    • Organizational knowledge
    • Internal terms and definitions

    Output

    • List of differences between projects and product delivery

    Capture in the Enable Product Delivery – Executive Leadership Workshop Outcomes and Next Steps.

    Identify the differences between a project-centric and a product-centric organization

    Project

    Product

    Fund Projects

    Funding

    →

    Fund Products or Teams

    Line of Business Sponsor

    Prioritization

    →

    Product Owner

    Makes Specific Changes
    to a Product

    Product Management

    →

    Improve Product Maturity
    and Support

    Assign People to Work

    Work Allocation

    →

    Assign Work
    to Product Teams

    Project Manager Manages

    Capacity Management

    →

    Team Manages Capacity

    Info-Tech Insight

    Product delivery requires significant shifts in the way you complete development work and deliver value to your users. Make the changes that support improving end user value and enterprise alignment.

    Projects can be a mechanism for funding product changes and improvements

    This is an image showing the relationship between the project lifecycle, a hybrid lifecycle, and a product lifecycle.

    Projects within products

    Regardless of whether you recognize yourself as a "product-based" or "project-based" shop, the same basic principles should apply.

    You go through a period or periods of project-like development to build a version of an application or product.

    You also have parallel services along with your project development, which encompass the more product-based view. These may range from basic support and maintenance to full-fledged strategy teams or services like sales and marketing.

    While Agile and product are intertwined, they are not the same!

    Delivering products does not necessarily require an Agile mindset. However, Agile methods help facilitate the journey because product thinking is baked into them.

    This image shows the product delivery maturity process from waterfall to continuous integration and delivery.

    Product roadmaps guide delivery and communicate your strategy

    In Deliver on Your Digital Product Vision, we demonstrate how the product roadmap is core to value realization. The product roadmap is your communicated path, and as a product owner, you use it to align teams and changes to your defined goals while aligning your product to enterprise goals and strategy.

    This is an image adapted from Pichler, What is Product Management.

    Adapted from: Pichler, "What Is Product Management?"

    Info-Tech Insight

    The quality of your product backlog – and your ability to realize business value from your delivery pipeline – is directly related to the input, content, and prioritization of items in your product roadmap.

    Establish Effective Data Stewardship

    • Buy Link or Shortcode: {j2store}133|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Data Management
    • Parent Category Link: /data-management
    • Data stewardship is a critical function in modern data governance. Every data-driven firm needs stewards who can tackle data issues and challenges rapidly. Data stewards help to reach agreement on data definition, quality, and usage. They direct efforts aimed at completing metadata, improving data quality, and ensuring regulatory compliance.
    • Stewards must also provide recommendations regarding data access, security, distribution, retention, archiving, and disposal.

    Our Advice

    Critical Insight

    • While the data steward role is crucial to establishing and sustaining effective governance of data, it is the role in the data governance operating structure that is often left ambiguous.
    • It is often perceived as requiring incremental IT skills and one with all new or unfamiliar functions.
    • In the ambition and haste to deliver on data governance, the various data governance role titles are communicated out to the wider organization, with data stewards especially left wondering: “Why am I being asked to be a data steward? What is expected of me? How will succeed in this role?”

    Impact and Result

    To establish effective and impactful data stewardship:

    • Clearly articulate the data stewardship value proposition.
    • Formally design and detail the data steward role, including functions, capabilities, etc.
    • Set up your data stewards for success: having a detailed role definition on paper is certainly not enough. Ensure you go the extra mile to deliver relevant training such as data stewardship onboarding, awareness program, etc.

    Establish Effective Data Stewardship Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Establish Effective Data Stewardship Storyboard – Research that provides a step-by-step approach to aid in the successful establishment of data steward role.

    Use this deck to establish a solid data governance foundation in your organization. Start by defining the value of data stewardship and data governance and demystifying the role.

    • Establish Effective Data Stewardship – Phases 1-3

    2. Data Governance Role Accelerator Kit – A brief deck that defines the clear functions for different roles in data governance.

    This brief guide outlines how to adapt a data governance organizational structure for your organization and defines the roles of data owner, data steward, and data custodian.

    • Data Governance Roles Accelerator Kit
    [infographic]

    Further reading

    Establish Effective Data Stewardship

    Leverage your organization's business subject matter experts to drive impactful data use and handling.

    Analyst perspective

    Leverage your organization's business subject matter experts to drive impactful data use and handling.

    Data stewards bring valuable expertise and knowledge about their business areas: priorities, business capabilities and processes, and challenges and opportunities with respect to data. Because this knowledge cannot be easily replicated, going outside your organization to hire a data steward is not the most effective route.

    While it may seem difficult, organizing internally to harvest the already existing institutional knowledge of your business subject matter experts (SMEs) will give a better – and faster – return when setting up and formalizing data stewardship.

    The role must be well defined and communicated. We cannot expect SMEs to wear a hat without understanding the expectations for their role. They must be set up for success – they must be empowered, recognized, and rewarded.

    Crystal Singh, Director, Research and Advisory, Data and Analytics Practice

    Crystal Singh
    Director, Research and Advisory, Data and Analytics Practice
    Info-Tech Research Group

    Phase breakdown

    Phase 1: Data Stewardship Value Proposition

    • Define the value of data stewardship and data governance, their importance, and the relationship between them.
    • Determine where data stewards fit in the bigger data governance operating structure. The data steward role will not be effective without the other data governance roles.
    • Highlight the gains of effective data stewardship: e.g. data quality management, data definition, data sharing, and the ethical use and handling of data.

    Phase breakdown

    Phase 2: Data Steward Role Design

    • Who makes a good data steward? Important knowledge and skills include subject area expertise, institutional knowledge, collaborative skills, interpersonal, and political skills, an understanding of your organization's culture, and the ability to build good partnerships across business functions and with data management.
    • Seek out SMEs from within your organization. This may require you to mold and shape individuals to step up and into the role. An external hire will give capacity but will be more difficult (and time consuming) to ramp up.
    • Consult internally in your organization. For example, consult and liaise with Human Resources (HR) to determine if job descriptions need to be updated, if there would be any impact to compensation, etc.
    • Determine if this role needs to be a full-time role.
    • Demystify the role. Clarify that this is not an IT role and therefore will not require IT skills.
    • Leverage Info-Tech data governance patterns:
      • Data Stewardship in Action – Sample Data Quality Issue Resolution Process Template and Business Term and Data Definitions
      • Sample Data Steward (and Data Owner) to Data Domain Mapping

    Phase breakdown

    Phase 3: Strategies for Data Stewardship Success

    • Establish a solid data governance foundation in your organization.
    • Develop data stewardship onboarding: e.g. literacy and training, and frequently asked questions (FAQs).
    • Gain support from data owners, the director general (DG) committee, data leadership, and executive leaders/champions.
    • Set up rewards and recognition for the role.
    • Establish a feedback loop/mechanism for data stewards so the stewardship program can be adjusted accordingly.
    • Establish communication and create awareness of the role.

    Establishing effective data stewardship

    Leverage your organization's business SMEs to drive impactful data use and handling.

    Unlock the value of data through people.

    Data Steward Value Proposition
    Clearly articulate the data stewardship value proposition. What's in it for the person, their line of business or mandate, and your organization as a whole.

    Data Steward Role Design
    Formally design and define the role of a data steward, including the functions and capabilities.

    Strategies for Success
    Set up your data stewards for success. Having a detailed role definition on paper is not enough. Ensure that you go the extra mile to deliver the relevant training, such as data stewardship onboarding and an awareness program.

    Executive summary

    Your Challenge Common Obstacles Info-Tech's Approach
    Data stewardship is a critical function in modern data governance. Every data-driven firm needs stewards who can rapidly tackle data issues and challenges. Data stewards help to reach agreement on data definition, quality, and usage. They direct efforts aimed at completing metadata, improving data quality, and ensuring regulatory compliance.
    Stewards must also provide recommendations regarding data access, security, distribution, retention, archiving, and disposal.
    While the data steward role is crucial to establishing and sustaining the effective governance of data, it is the role in the data governance operating structure that is often left unclear, ambiguous, and open to misinterpretation.
    It is often perceived as requiring incremental IT skills and one with all new or unfamiliar functions.
    In the ambition and haste to deliver on data governance, the various data governance role titles are communicated to the wider organization, often leaving data stewards wondering why they are being asked to be a data steward, what is expected of them, and how they will succeed in this role.
    Info-Tech's approach to establish effective and impactful data stewardship:
    • Clearly articulate the data stewardship value proposition.
    • Formally design and define the role of data steward, including the functions and capabilities.
    • Set up your data stewards for success. Having a detailed role definition on paper is not enough. Ensure that you go the extra mile to deliver the relevant training, such as data stewardship onboarding and an awareness program.

    Info-Tech Insight
    Effective data governance requires a solid foundation. Data stewards provide the foundation for data governance. The time and effort to define this role properly will yield sound data governance return.

    Phase 1: Data Stewardship Value Proposition

    What is the VALUE of a DATA STEWARD?

    Value of a Data Steward

    Improved Data Quality Management

    Clear and Consistent Data Definition

    Increased Data Sharing and Collaboration

    Ethical Handling of Data

    Define the strategic value of data in your organization

    Harness the value of data to power intelligent and transformative organizational performance.

    Optimize the way you serve your stakeholders.

    Respond to industry disruption.

    Develop products and services to meet ever-evolving needs.

    Manage operations and mitigate risk.

    Data governance is an enabling framework of decision rights, responsibilities, and accountabilities for data assets across an organization.

    Data governance is:

    • Executed according to agreed-upon models that describe who can take what actions with what information, when, and using what methods (CIO.com, 2021).
    • True business-IT collaboration that leads to increased consistency and confidence in data to support decision making

    If done correctly, data governance is not:

    • An annoying, finger-waving roadblock in the way of getting things done
    • An inhibitor or impediment to using and sharing data

    Data governance is about putting guard rails in place to better support the use and handling of your organization's data.

    Is there a clear definition of data accountability and responsibility in your organization?

    Explore the Secrets of SAP Software Contracts to Optimize Spend and Reduce Compliance Risk

    • Buy Link or Shortcode: {j2store}140|cart{/j2store}
    • member rating overall impact: 9.8/10 Overall Impact
    • member rating average dollars saved: $73,994 Average $ Saved
    • member rating average days saved: 9 Average Days Saved
    • Parent Category Name: Licensing
    • Parent Category Link: /licensing
    • SAP has strict audit practices, which, in combination with 50+ types of user classifications and manual accounting for some licenses, make maintaining compliance difficult.
    • Mapping and matching SAP products to the environment can be highly complex, leading to overspending and an inability to reduce spend later.
    • Beware of indirect access to SAP applications from third-party applications (e.g. Salesforce).
    • Products that have been acquired by SAP may have altered licensing terms that are innocuously referred to in support renewal documents.

    Our Advice

    Critical Insight

    • Focus on needs first. Conduct a thorough requirements assessment and document the results. Well-documented license needs will be your core asset in navigating SAP licensing and negotiating your agreement.
    • Examine indirect access possibilities. Understanding how in-house or third-party applications may be accessing the SAP software is critical.
    • Know what’s in the contract. Each customer agreement is different and there may be terms that are beneficial. Older agreements may provide both benefits and challenges when evaluating your SAP license position.

    Impact and Result

    • Conduct an analysis to remove inactive and duplicate users as multiple logins may exist and could end up costing the organization license fees when audited.
    • Adopt a cyclical approach to reviewing your SAP licensing and create a reference document to track your software needs, planned licensing, and purchase negotiation points.
    • Learn the “SAP way” of conducting business, which includes a best-in-class sales structure, unique contracts and license use policies, and a hyper-aggressive compliance function. Conducting business with SAP is not typical compared to other vendors, and you will need different tools to emerge successfully from a commercial transaction.
    • Manage SAP support and maintenance spend and policies. Once an agreement has been signed, it can be very difficult to decrease spend, as SAP will reprice products if support is dropped.

    Explore the Secrets of SAP Software Contracts to Optimize Spend and Reduce Compliance Risk Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you need to understand and document your SAP licensing strategy, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Establish licensing requirements

    Begin your proactive SAP licensing journey by understanding which information to gather and assessing the current state and gaps.

    • Explore the Secrets of SAP Software Contracts to Optimize Spend and Reduce Compliance Risk – Phase 1: Establish Licensing Requirements
    • SAP License Summary and Analysis Tool

    2. Evaluate licensing options

    Review current licensing models and determine which licensing models will most appropriately fit your environment.

    • Explore the Secrets of SAP Software Contracts to Optimize Spend and Reduce Compliance Risk – Phase 2: Evaluate Licensing Options

    3. Evaluate agreement options

    Review SAP’s contract types and assess which best fit the organization’s licensing needs.

    • Explore the Secrets of SAP Software Contracts to Optimize Spend and Reduce Compliance Risk – Phase 3: Evaluate Agreement Options

    4. Purchase and manage licenses

    Conduct negotiations, purchase licensing, and finalize a licensing management strategy.

    • Explore the Secrets of SAP Software Contracts to Optimize Spend and Reduce Compliance Risk – Phase 4: Purchase and Manage Licenses
    [infographic]

    Evaluate and Learn From Your Negotiation Sessions More Effectively

    • Buy Link or Shortcode: {j2store}226|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Vendor Management
    • Parent Category Link: /vendor-management
    • Forty-eight percent of CIOs believe their budgets are inadequate.
    • CIOs and IT departments are getting more involved with negotiations to reduce costs and risk.
    • Confident negotiators tend to be more successful, but even confident negotiators have room to improve.
    • Skilled negotiators are in short supply.

    Our Advice

    Critical Insight

    • Improving your negotiation skills requires more than practice or experience (i.e. repeatedly negotiating).
    • Creating and updating a negotiations lessons-learned library helps negotiators improve and provides a substantial return for the organization.
    • Failure is a great teacher; so is success … but you have to pay attention to indicators, not just results.

    Impact and Result

    Addressing and managing the negotiation debriefing process will help you:

    • Improve negotiation skills.
    • Implement your negotiation strategy more effectively.
    • Improve negotiation results.

    Evaluate and Learn From Your Negotiation Sessions More Effectively Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should create and follow a scalable process for preparing to negotiate with vendors, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Negotiations continuing

    This phase will help you debrief after each negotiation session and identify the parts of your strategy that must be modified before your next negotiation session.

    • Evaluate and Learn From Your Negotiation Sessions More Effectively – Phase 1: Negotiations Continuing

    2. Negotiations completed

    This phase will help you conduct evaluations at three critical points after the negotiations have concluded.

    • Evaluate and Learn From Your Negotiation Sessions More Effectively – Phase 2: Negotiations Completed
    [infographic]

    Workshop: Evaluate and Learn From Your Negotiation Sessions More Effectively

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 12 Steps to Better Negotiation Preparation

    The Purpose

    Improve negotiation skills and outcomes; share lessons learned.

    Understand the value of debriefing sessions during the negotiation process.

    Understand how to use the Info-Tech After Negotiations Tool.

    Key Benefits Achieved

    A better understanding of how and when to debrief during the negotiation process to leverage key insights.

    The After Negotiations Tool will be reviewed and configured for the customer’s environment (as applicable).

    Activities

    1.1 Debrief after each negotiation session

    1.2 Determine next steps

    1.3 Return to preparation phase

    1.4 Conduct Post Mortem #1

    1.5 Conduct Implementation Assessment

    1.6 Conduct Post Mortem #2

    Outputs

    Negotiation Session Debrief Checklist and Questionnaire

    Next Steps Checklist

    Discussion

    Post Mortem #1 Checklist & Dashboard

    Implementation Assessment Checklist and Questionnaire

    Post Mortem #2 Checklist & Dashboard

    Build a Robust and Comprehensive Data Strategy

    • Buy Link or Shortcode: {j2store}120|cart{/j2store}
    • member rating overall impact: 9.3/10 Overall Impact
    • member rating average dollars saved: $46,734 Average $ Saved
    • member rating average days saved: 29 Average Days Saved
    • Parent Category Name: Data Management
    • Parent Category Link: /data-management
    • The volume and variety of data that organizations have been collecting and producing have been growing exponentially and show no sign of slowing down.
    • At the same time, business landscapes and models are evolving, and users and stakeholders are becoming more and more data centric, with maturing expectations and demands.

    Our Advice

    Critical Insight

    • As the CDO or equivalent data leader in your organization, a robust and comprehensive data strategy is the number one tool in your toolkit for delivering on your mandate of creating measurable business value from data.
    • A data strategy should never be formulated disjointed from the business. Ensure the data strategy aligns with the business strategy and supports the business architecture.
    • Building and fostering a data-driven culture will accelerate and sustain adoption of, appetite for, and appreciation for data and hence drive the ROI on your various data investments.

    Impact and Result

    • Formulate a data strategy that stitches all of the pieces together to better position you to unlock the value in your data:
      • Establish the business context and value: Identify key business drivers for executing on an optimized data strategy, build compelling and relevant use cases, understand your organization’s culture and appetite for data, and ensure you have well-articulated vision, principles, and goals for your data strategy
      • Ensure you have a solid data foundation: Understand your current data environment, data management enablers, people, skill sets, roles, and structure. Know your strengths and weakness so you can optimize appropriately.
      • Formulate a sustainable data strategy: Round off your strategy with effective change management and communication for building and fostering a data-driven culture.

    Build a Robust and Comprehensive Data Strategy Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Data Strategy Research – A step-by-step document to facilitate the formulation of a data strategy that brings together the business context, data management foundation, people, and culture.

    Data should be at the foundation of your organization’s evolution. The transformational insights that executives and decision makers are constantly seeking to leverage can be unlocked with a data strategy that makes high-quality, trusted, and relevant data readily available to the users who need it.

    • Build a Robust and Comprehensive Data Strategy – Phases 1-3

    2. Data Strategy Stakeholder Interview Guide and Findings – A template to support you in your meetings or interviews with key stakeholders as you work on understanding the value of data within the various lines of business.

    This template will help you gather insights around stakeholder business goals and objectives, current data consumption practices, the types or domains of data that are important to them in supporting their business capabilities and initiatives, the challenges they face, and opportunities for data from their perspective.

    • Data Strategy Stakeholder Interview Guide and Findings

    3. Data Strategy Use Case Template – An exemplar template to demonstrate the business value of your data strategy.

    Data strategy optimization anchored in a value proposition will ensure that the data strategy focuses on driving the most valuable and critical outcomes in support of the organization’s enterprise strategy. The template will help you facilitate deep-dive sessions with key stakeholders for building use cases that are of demonstrable value not only to their relevant lines of business but also to the wider organization.

    • Data Strategy Use Case Template

    4. Chief Data Officer – A job description template that includes a detailed explication of the responsibilities and expectations of a CDO.

    Bring data to the C-suite by creating the Chief Data Officer role. This position is designed to bridge the gap between the business and IT by serving as a representative for the organization's data management practices and identifying how the organization can leverage data as a competitive advantage or corporate asset.

    • Chief Data Officer

    5. Data Strategy Document Template – A structured template to plan and document your data strategy outputs.

    Use this template to document and formulate your data strategy. Follow along with the sections of the blueprint Build a Robust and Comprehensive Data Strategy and complete the template as you progress.

    • Data Strategy Document Template
    [infographic]

    Workshop: Build a Robust and Comprehensive Data Strategy

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Establish Business Context and Value: Understand the Current Business Environment

    The Purpose

    Establish the business context for the business strategy.

    Key Benefits Achieved

    Substantiates the “why” of the data strategy.

    Highlights the organization’s goals, objectives, and strategic direction the data must align with.

    Activities

    1.1 Data Strategy 101

    1.2 Intro to Tech’s Data Strategy Framework

    1.3 Data Strategy Value Proposition: Understand stakeholder’s strategic priorities and the alignment with data

    1.4 Discuss the importance of vision, mission, and guiding principles of the organization’s data strategy

    1.5 Understand the organization’s data culture – discuss Data Culture Survey results

    1.6 Examine Core Value Streams of Business Architecture

    Outputs

    Business context; strategic drivers

    Data strategy guiding principles

    Sample vision and mission statements

    Data Culture Diagnostic Results Analysis

    2 Business-Data Needs Discovery: Key Business Stakeholder Interviews

    The Purpose

    Build use cases of demonstrable value and understand the current environment.

    Key Benefits Achieved

    An understanding of the current maturity level of key capabilities.

    Use cases that represent areas of concern and/or high value and therefore need to be addressed.

    Activities

    2.1 Conduct key business stakeholder interviews to initiate the build of high-value business-data cases

    Outputs

    Initialized high-value business-data cases

    3 Understand the Current Data Environment & Practice: Analyze Data Capability and Practice Gaps and Develop Alignment Strategies

    The Purpose

    Build out a future state plan that is aimed at filling prioritized gaps and that informs a scalable roadmap for moving forward on treating data as an asset.

    Key Benefits Achieved

    A target state plan, formulated with input from key stakeholders, for addressing gaps and for maturing capabilities necessary to strategically manage data.

    Activities

    3.1 Understand the current data environment: data capability assessment

    3.2 Understand the current data practice: key data roles, skill sets; operating model, organization structure

    3.3 Plan target state data environment and data practice

    Outputs

    Data capability assessment and roadmapping tool

    4 Align Business Needs with Data Implications: Initiate Roadmap Planning and Strategy Formulation

    The Purpose

    Consolidate business and data needs with consideration of external factors as well as internal barriers and enablers to the success of the data strategy. Bring all the outputs together for crafting a robust and comprehensive data strategy.

    Key Benefits Achieved

    A consolidated view of business and data needs and the environment in which the data strategy will be operationalized.

    An analysis of the feasibility and potential risks to the success of the data strategy.

    Activities

    4.1 Analyze gaps between current- and target-state

    4.2 Initiate initiative, milestone and RACI planning

    4.3 Working session with Data Strategy Owner

    Outputs

    Data Strategy Next Steps Action Plan

    Relevant data strategy related templates (example: data practice patterns, data role patterns)

    Initialized Data Strategy on-a-Page

    Further reading

    Build a Robust and Comprehensive Data Strategy

    Key to building and fostering a data-driven culture.

    ANALYST PERSPECTIVE

    Data Strategy: Key to helping drive organizational innovation and transformation

    "In the dynamic environment in which we operate today, where we are constantly juggling disruptive forces, a well-formulated data strategy will prove to be a key asset in supporting business growth and sustainability, innovation, and transformation.

    Your data strategy must align with the organization’s business strategy, and it is foundational to building and fostering an enterprise-wide data-driven culture."

    Crystal Singh,

    Director – Research and Advisory

    Info-Tech Research Group

    Our understanding of the problem

    This Research is Designed For:

    • Chief data officers (CDOs), chief architects, VPs, and digital transformation directors and CIOs who are accountable for ensuring data can be leveraged as a strategic asset of the organization.

    This Research Will Help You:

    • Put a strategy in place to ensure data is available, accessible, well integrated, secured, of acceptable quality, and suitably visualized to fuel decision making by the organizations’ executives.
    • Align data management plans and investments with business requirements and the organization’s strategic plans.
    • Define the relevant roles for operationalizing your data strategy.

    This Research Will Also Assist:

    • Data architects and enterprise architects who have been tasked with supporting the formulation or optimization of the organization’s data strategy.
    • Business leaders creating plans for leveraging data in their strategic planning and business processes.
    • IT professionals looking to improve the environment that manages and delivers data.

    This Research Will Help Them:

    • Get a handle on the current situation of data within the organization.
    • Understand how the data strategy and its resulting initiatives will affect the operations, integration, and provisioning of data within the enterprise.

    Executive Summary

    Situation

    • The volume and variety of data that organizations have been collecting and producing have been growing exponentially and show no sign of slowing down. At the same time, business landscapes and models are evolving, and users and stakeholders are becoming more and more data centric, with maturing and demanding expectations.

    Complication

    • As organizations pivot in response to industry disruptions and changing landscapes, a reactive and piecemeal approach leads to data architectures and designs that fail to deliver real and measurable value to the business.
    • Despite the growing focus on data, many organizations struggle to develop a cohesive business-driven strategy for effectively managing and leveraging their data assets.

    Resolution

    Formulate a data strategy that stitches all of the pieces together to better position you to unlock the value in your data:

    • Establish the business context and value: Identify key business drivers for executing on an optimized data strategy, build compelling and relevant use cases, understand your organization’s culture and appetite for data, and ensure you have well-articulated vision, principles, and goals for your data strategy.
    • Ensure you have a solid data foundation: Understand your current data environment, data management enablers, people, skill sets, roles, and structure. Know your strengths and weakness so you can optimize appropriately.
    • Formulate a sustainable data strategy: Round off your strategy with effective change management and communication for building and fostering a data-driven culture.

    Info-Tech Insight

    1. As the CDO or equivalent data leader in your organization, a robust and comprehensive data strategy is the number one tool in your toolkit for delivering on your mandate of creating measurable business value from data.
    2. A data strategy should never be formulated disjointed from the business. Ensure the data strategy aligns with the business strategy and supports the business architecture.
    3. Building and fostering a data-driven culture will accelerate and sustain adoption of, appetite for, and appreciation for data and hence drive the ROI on your various data investments.

    Why do you need a data strategy?

    Your data strategy is the vehicle for ensuring data is poised to support your organization’s strategic objectives.

    The dynamic marketplace of today requires organizations to be responsive in order to gain or maintain their competitive edge and place in their industry.

    Organizations need to have that 360-degree view of what’s going on and what’s likely to happen.

    Disruptive forces often lead to changes in business models and require organizations to have a level of adaptability to remain relevant.

    To respond, organizations need to make decisions and should be able to turn to their data to gain insights for informing their decisions.

    A well-formulated and robust data strategy will ensure that your data investments bring you the returns by meeting your organization’s strategic objectives.

    Organizations need to be in a position where they know what’s going on with their stakeholders and anticipate what their stakeholders’ needs are going to be.

    Data cannot be fully leveraged without a cohesive strategy

    Most organizations today will likely have some form of data management in place, supported by some of the common roles such as DBAs and data analysts.

    Most will likely have a data architecture that supports some form of reporting.

    Some may even have a chief data officer (CDO), a senior executive who has a seat at the C-suite table.

    These are all great assets as a starting point BUT without a cohesive data strategy that stitches the pieces together and:

    • Effectively leverages these existing assets
    • Augments them with additional and relevant key roles and skills sets
    • Optimizes and fills in the gaps around your current data management enablers and capabilities for the growing volume and variety of data you’re collecting
    • Fully caters to real, high-value strategic organizational business needs

    you’re missing the mark – you are not fully leveraging the incredible value of your data.

    Cross-industry studies show that on average, less than half of an organization’s structured data is actively used in making decisions

    And, less than 1% of its unstructured data is analyzed or used at all. Furthermore, 80% of analysts' time is spent simply discovering and preparing, data with over 70% of employees having access to data they should not. Source: HBR, 2017

    Organizational drivers for a data strategy

    Your data strategy needs to align with your organizational strategy.

    Main Organizational Strategic Drivers:

    1. Stakeholder Engagement/Service Excellence
    2. Product and Service Innovations
    3. Operational Excellence
    4. Privacy, Risk, and Compliance Management

    “The companies who will survive and thrive in the future are the ones who will outlearn and out-innovate everyone else. It is no longer ‘survival of the fittest’ but ‘survival of the smartest.’ Data is the element that both inspires and enables this new form of rapid innovation.” – Joel Semeniuk, 2016

    A sound data strategy is the key to unlocking the value in your organization’s data.

    Data should be at the foundation of your organization’s evolution.

    The transformational insights that executives are constantly seeking to leverage can be unlocked with a data strategy that makes high-quality, well-integrated, trustworthy, relevant data readily available to the business users who need it.

    Whether hoping to gain a better understanding of your business, trying to become an innovator in your industry, or having a compliance and regulatory mandate that needs to be met, any organization can get value from its data through a well-formulated, robust, and cohesive data strategy.

    According to a leading North American bank, “More than one petabyte of new data, equivalent to about 1 million gigabytes” is entering the bank’s systems every month. – The Wall Street Journal, 2019

    “Although businesses are at many different stages in unlocking the power of data, they share a common conviction that it can make or break an enterprise.”– Jim Love, ITWC CIO and Chief Digital Officer, IT World Canada, 2018

    Data is a strategic organizational asset and should be treated as such

    The expression “Data is an asset” or any other similar sentiment has long been heard.

    With such hype, you would have expected data to have gotten more attention in the boardrooms. You would have expected to see its value reflected on financial statements as a result of its impact in driving things like acquisition, retention, product and service development and innovation, market growth, stakeholder satisfaction, relationships with partners, and overall strategic success of the organization.

    The time has surely come for data to be treated as the asset it is.

    “Paradoxically, “data” appear everywhere but on the balance sheet and income statement.”– HBR, 2018

    “… data has traditionally been perceived as just one aspect of a technology project; it has not been treated as a corporate asset.”– “5 Essential Components of a Data Strategy,” SAS

    According to Anil Chakravarthy, who is the CEO of Informatica and has a strong vantage point on how companies across industries leverage data for better business decisions, “what distinguishes the most successful businesses … is that they have developed the ability to manage data as an asset across the whole enterprise.”– McKinsey & Company, 2019

    How data is perceived in today’s marketplace

    Data is being touted as the oil of the digital era…

    But just like oil, if left unrefined, it cannot really be used.

    "Data is the new oil." – Clive Humby, Chief Data Scientist

    Source: Joel Semeniuk, 2016

    Enter your data strategy.

    Data is being perceived as that key strategic asset in your organization for fueling innovation and transformation.

    Your data strategy is what allows you to effectively mine, refine, and use this resource.

    “The world’s most valuable resource is no longer oil, but data.”– The Economist, 2017

    “Modern innovation is now dependent upon this data.”– Joel Semeniuk, 2016

    “The better the data, the better the resulting innovation and impact.”– Joel Semeniuk, 2016

    What is it in it for you? What opportunities can data help you leverage?

    GOVERNMENT

    Leveraging data as a strategic asset for the benefit of citizens.

    • The strategic use of data can enable governments to provide higher-quality services.
    • Direct resources appropriately and harness opportunities to improve impact.
    • Make better evidence-informed decisions and better understand the impact of programs so that funds can be directed to where they are most likely to deliver the best results.
    • Maintain legitimacy and credibility in an increasingly complex society.
    • Help workers adapt and be competitive in a changing labor market.
    • A data strategy would help protect citizens from the misuse of their data.

    Source: Privy Council Office, Government of Canada, 2018

    What is it in it for you? What opportunities can data help you leverage?

    FINANCIAL

    Leveraging data to boost traditional profit and loss levers, find new sources of growth, and deliver the digital bank.

    • One bank used credit card transactional data (from its own terminals and those of other banks) to develop offers that gave customers incentives to make regular purchases from one of the bank’s merchants. This boosted the bank’s commissions, added revenue for its merchants, and provided more value to the customer (McKinsey & Company, 2017).
    • In terms of enhancing productivity, a bank used “new algorithms to predict the cash required at each of its ATMs across the country and then combined this with route-optimization techniques to save money” (McKinsey & Company, 2017).

    A European bank “turned to machine-learning algorithms that predict which currently active customers are likely to reduce their business with the bank.” The resulting understanding “gave rise to a targeted campaign that reduced churn by 15 percent” (McKinsey & Company, 2017).

    A leading Canadian bank has built a marketplace around their data – they have launched a data marketplace where they have productized the bank’s data. They are providing data – as a product – to other units within the bank. These other business units essentially represent internal customers who are leveraging the product, which is data.

    Through the use of data and advanced analytics, “a top bank in Asia discovered unsuspected similarities that allowed it to define 15,000 microsegments in its customer base. It then built a next-product-to-buy model that increased the likelihood to buy three times over.” Several sets of big data were explored, including “customer demographics and key characteristics, products held, credit-card statements, transaction and point-of-sale data, online and mobile transfers and payments, and credit-bureau data” (McKinsey & Company, 2017).

    What is it in it for you? What opportunities can data help you leverage?

    HEALTHCARE

    Leveraging data and analytics to prevent deadly infections

    The fifth-largest health system in the US and the largest hospital provider in California uses a big data and advanced analytics platform to predict potential sepsis cases at the earliest stages, when intervention is most helpful.

    Using the Sepsis Bio-Surveillance Program, this hospital provider monitors 120,000 lives per month in 34 hospitals and manages 7,500 patients with potential sepsis per month.

    Collecting data from the electronic medical records of all patients in its facilities, the solution uses natural language processing (NLP) and a rules engine to continually monitor factors that could indicate a sepsis infection. In high-probability cases, the system sends an alarm to the primary nurse or physician.

    Since implementing the big data and predictive analytics system, this hospital provider has seen a significant improvement in the mortality and the length of stay in ICU for sepsis patients.

    At 28 of the hospitals which have been on the program, sepsis mortality rates have dropped an average of 5%.

    With patients spending less time in the ICU, cost savings were also realized. This is significant, as sepsis is the costliest condition billed to Medicare, the second costliest billed to Medicaid and the uninsured, and the fourth costliest billed to private insurance.

    Source: SAS, 2019

    What is it in it for you? What opportunities can data help you leverage?

    RETAIL

    Leveraging data to better understand customer preferences, predict purchasing, drive customer experience, and optimize supply and demand planning.

    Netflix is an example of a big brand that uses big data analytics for targeted advertising. With over 100 million subscribers, the company collects large amounts of data. If you are a subscriber, you are likely familiar with their suggestions messages of the next series or movie you should catch up on. These suggestions are based on your past search data and watch data. This data provides Netflix with insights into your interests and preferences for viewing (Mentionlytics, 2018).

    “For the retail industry, big data means a greater understanding of consumer shopping habits and how to attract new customers.”– Ron Barasch, Envestnet | Yodlee, 2019

    The business case for data – moving from platitudes to practicality

    When building your business case, consider the following:

    • What is the most effective way to communicate the business case to executives?
    • How can CDOs and other data leaders use data to advance their organizations’ corporate strategy?
    • What does your data estate look like? Are you looking to leverage and drive value from your semi-structured and unstructured data assets?
    • Does your current organizational culture support a data-driven one? Does the organization have a history of managing change effectively?
    • How do changing privacy and security expectations alter the way businesses harvest, save, use, and exchange data?

    “We’re the converted … We see the value in data. The battle is getting executive teams to see it our way.”– Ted Maulucci, President of SmartONE Solutions Inc. IT World Canada, 2018

    Where do you stack up? What is your current data management maturity?

    Info-Tech’s IT Maturity Ladder denotes the different levels of maturity for an IT department and its different functions. What is the current state of your data management capability?

    Innovator - Transforms the Business. Business Partner - Expands the Business. Trusted Operator - Optimizes the Business. Firefighter - Supports the Business. Unstable - Struggles to Support.

    Info-Tech Insight

    You are best positioned to successfully execute on a data strategy if you are currently at or above the Trusted Operator level. If you find yourself still at the Unstable or Firefighter stage, your efforts are best spent on ensuring you can fulfill your day-to-day data and data management demands. Improving this capability will help build a strong data management foundation.

    Guiding principles of a data strategy

    Value of Clearly Defined Data Principles

    • Guiding principles help define the culture and characteristics of your practice by describing your beliefs and philosophy.
    • Guiding principles act as the heart of your data strategy, helping to shape initiative plans and day-to-day behaviors related to the use and treatment of the organization’s data assets.

    “Organizational culture can accelerate the application of analytics, amplify its power, and steer companies away from risky outcomes.”– McKinsey, 2018

    Build a Robust and Comprehensive Data Strategy

    Business Strategy and Current Environment connect with the Data Strategy. Data Strategy includes: Organizational Drivers and Data Value, Data Strategy Objectives and Guiding Principles, Data Strategy Vision and Mission, Data Strategy Roadmap, People: Roles and Organizational Structure, Data Culture and Data Literacy, Data Management and Tools, Risk and Feasibility.

    Follow Info-Tech’s methodology for effectively leveraging the value out of your data

    Some say it’s the new oil. Or the currency of the new business landscape. Others describe it as the fuel of the digital economy. But we don’t need platitudes — we need real ways to extract the value from our data. – Jim Love, CIO and Chief Digital Officer, IT World Canada, 2018

    1. Business Context. 2. Data and Resources Foundation. 3. Effective Data Strategy

    Our practical step-by-step approach helps you to formulate a data strategy that delivers business value.

    1. Establish Business Context and Value: In this phase, you will determine and substantiate the business drivers for optimizing the data strategy. You will identify the business drivers that necessitate the data strategy optimization and examine your current organizational data culture. This will be key to ensuring the fruits of your optimization efforts are being used. You will also define the vision, mission, and guiding principles and build high-value use cases for the data strategy.
    2. Ensure You Have a Solid Data and Resources Foundation: This phase will help you ensure you have a solid data and resources foundation for operationalizing your data strategy. You will gain an understanding of your current environment in terms of data management enablers and the required resources portfolio of key people, roles, and skill sets.
    3. Formulate a Sustainable Data Strategy: In this phase, you will bring the pieces together for formulating an effective data strategy. You will evaluate and prioritize the use cases built in Phase 1, which summarize the alignment of organizational goals with data needs. You will also create your strategic plan, considering change management and communication.

    Info-Tech offers various levels of support to best suit your needs

    DIY Toolkit

    “Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful.”

    Guided Implementation

    “Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track.”

    Workshop

    “We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place.”

    Consulting

    “Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project.”

    Diagnostics and consistent frameworks are used throughout all four options.

    Govern Office 365

    • Buy Link or Shortcode: {j2store}52|cart{/j2store}
    • member rating overall impact: 9.5/10 Overall Impact
    • member rating average dollars saved: $21,473 Average $ Saved
    • member rating average days saved: 21 Average Days Saved
    • Parent Category Name: End-User Computing Applications
    • Parent Category Link: /end-user-computing-applications

    Exploring the enterprise collaboration marketspace is difficult. The difficulty in finding a suitable collaboration tool is that there are many ways to collaborate, with just as many tools to match.

    Our Advice

    Critical Insight

    Map your organizational goals to the administration features available in the Office 365 console. Your governance should reflect your requirements.

    Impact and Result

    The result is a defined plan for controlling Office 365 by leveraging hard controls to align Microsoft’s toolset with your needs and creating acceptable use policies and communication plans to highlight the impact of the transition to Office 365 on the end-user population.

    Govern Office 365 Research & Tools

    Start here – read the Executive Brief

    Understand the challenges posed by governing Office 365 and the necessity of deploying proper governance.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Define your organizational goals

    Develop a list of organizational goals that will enable you to leverage the Office 365 toolset to its fullest extent while also implementing sensible governance.

    • Govern Office 365 – Phase 1: Define Your Organizational Goals

    2. Control your Office 365 environment

    Use Info-Tech's toolset to build out controls for OneDrive, SharePoint, and Teams that align with your organizational goals as they relate to governance.

    • Govern Office 365 – Phase 2: Control Your Office 365 Environment
    • Office 365 Control Map
    • Microsoft Teams Acceptable Use Policy
    • Microsoft SharePoint Online Acceptable Use Policy
    • Microsoft OneDrive Acceptable Use Policy

    3. Communicate your results

    Communicate the results of your Office 365 governance program using Info-Tech's toolset.

    • Govern Office 365 – Phase 3: Communicate Your Results
    • Office 365 Communication Plan Template

    Infographic

    Workshop: Govern Office 365

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Define Goals

    The Purpose

    Develop a plan to assess the capabilities of the Office 365 solution and select licensing for the product.

    Key Benefits Achieved

    Office 365 capability assessment (right-size licensing)

    Acceptable Use Policies

    Mapped Office 365 controls

    Activities

    1.1 Review organizational goals.

    1.2 Evaluate Office 365 capabilities.

    1.3 Conduct the Office 365 capability assessment.

    1.4 Define user groups.

    1.5 Finalize licensing.

    Outputs

    List of organizational goals

    Targeted licensing decision

    2 Build Refined Governance Priorities

    The Purpose

    Leverage the Office 365 governance framework to develop and refined governance priorities.

    Build a SharePoint acceptable use policy and define SharePoint controls.

    Key Benefits Achieved

    Refined governance priorities

    List of SharePoint controls

    SharePoint acceptable use policy

    Activities

    2.1 Explore the Office 365 Framework.

    2.2 Conduct governance priorities refinement exercise.

    2.3 Populate the Office 365 control map (SharePoint).

    2.4 Build acceptable use policy (SharePoint).

    Outputs

    Refined governance priorities

    SharePoint control map

    Sharepoint acceptable use policy

    3 Control Office 365

    The Purpose

    Implement governance priorities for OneDrive and Teams.

    Key Benefits Achieved

    Clearly defined acceptable use policies for OneDrive and Teams

    List of OneDrive and Teams controls

    Activities

    3.1 Populate the Office 365 Control Map (OneDrive).

    3.2 Build acceptable use policy (OneDrive).

    3.3 Populate the Office 365 Control Map (Teams).

    3.4 Build acceptable use policy (Teams).

    Outputs

    OneDrive controls

    OneDrive acceptable use policy

    Teams controls

    Teams acceptable use policy

    4 SOW Walkthrough

    The Purpose

    Build a plan to communicate coming changes to the productivity environment.

    Key Benefits Achieved

    Communication plan covering SharePoint, Teams, and OneDrive

    Activities

    4.1 Build SharePoint one pager.

    4.2 Build OneDrive one pager.

    4.3 Build Teams one pager.

    4.4 Finalize communication plan.

    Outputs

    SharePoint one pager

    OneDrive one pager

    Teams one pager

    Overall finalized communication plan

    5 Communicate and Implement

    The Purpose

    Finalize deliverables and plan post-workshop communications.

    Key Benefits Achieved

    Completed Office 365 governance plan

    Finalized deliverables

    Activities

    5.1 Completed in-progress deliverables from previous four days.

    5.2 Set up review time for workshop deliverables and to discuss next steps.

    5.3 Validate governance with stakeholders.

    Outputs

    Completed acceptable use policies

    Completed control map

    Completed communication plan

    Completed licensing decision

    Plan Your Digital Transformation on a Page

    • Buy Link or Shortcode: {j2store}81|cart{/j2store}
    • member rating overall impact: 8.0/10 Overall Impact
    • member rating average dollars saved: $34,649 Average $ Saved
    • member rating average days saved: 20 Average Days Saved
    • Parent Category Name: IT Strategy
    • Parent Category Link: /it-strategy
    • Digital investments often under deliver on expectations of return, and there is no cohesive approach to managing the flow of capital into digital.
    • The focus of the business has historically been to survive technological disruption rather than to thrive in it.
    • Strategy is based mostly on opinion rather than an objective analysis of the outcomes customers want from the organization.
    • Digital is considered a buzzword – nobody has a clear understanding of what it is and what it means in the organization’s context.

    Our Advice

    Critical Insight

    • The purpose of going digital is getting one step closer to the customer. The mark of a digital organization lies in how they answer the question, “How does what we’re doing contribute to what the customer wants from us?”
    • The goal of digital strategy is digital enablement. An organization that is digitally enabled no longer needs a digital strategy, it’s just “the strategy.”

    Impact and Result

    • Focus strategy making on delivering the digital outcomes that customers want.
      • Leverage the talent, expertise, and perspectives within the organization to build a customer-centric digital strategy.
    • Design a balanced digital strategy that creates value across the five digital value pools:
      • Digital marketing, digital channels, digital products, digital supporting capabilities, and business model innovation.
    • Ask how disruption can be leveraged, or even become the disruptor.
      • Manage disruption through quick-win approaches and empowering staff to innovate.
    • Use a Digital Strategy-on-a-Page to spark the digital transformation.
      • Drive awareness and alignment on the digital vision and spark your organization’s imagination around digital.

    Plan Your Digital Transformation on a Page Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to understand how digital disruption is driving the need for transformation, and how Info-Tech’s methodology can help.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Scope the digital transformation

    Learn how to apply the Digital Value Pools thought model and scope strategy around them.

    • Plan Your Digital Transformation on a Page – Phase 1: Scope the Digital Transformation

    2. Design the digital future state vision

    Identify business imperatives, define digital outcomes, and define the strategy’s guiding principles.

    • Plan Your Digital Transformation on a Page – Phase 2: Design the Digital Future State Vision
    • Digital Strategy on a Page

    3. Define the digital roadmap

    Define, prioritize, and roadmap digital initiatives and plan contingencies.

    • Plan Your Digital Transformation on a Page – Phase 3: Define the Digital Roadmap

    4. Sustain digital transformation

    Create, polish, and socialize the Digital Strategy-on-a-Page.

    • Plan Your Digital Transformation on a Page – Phase 4: Sustain Digital Transformation
    [infographic]

    Workshop: Plan Your Digital Transformation on a Page

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Scope the Digital Transformation

    The Purpose

    Identify the need for and use of digital strategy and determine a realistic scope for the digital strategy.

    Key Benefits Achieved

    The digital strategy project is planned and scoped around a subset of the five digital value pools.

    Activities

    1.1 Introduction to digital strategy.

    1.2 Establish motivation for digital.

    1.3 Discuss in-flight digital investments.

    1.4 Define the scope of digital.

    1.5 Identify stakeholders.

    1.6 Perform discovery interviews.

    1.7 Select two value pools to focus day 2, 3, and 4 activities.

    Outputs

    Business model canvas

    Stakeholder power map

    Discovery interview results

    Two value pools for focus throughout the workshop

    2 Design the Digital Future State Vision

    The Purpose

    Create guiding principles to help define future digital initiatives. Generate the target state with the help of strategic goals.

    Key Benefits Achieved

    Establish the basis for planning out the initiatives needed to achieve the target state from the current state.

    Activities

    2.1 Identify digital imperatives.

    2.2 Define key digital outcomes.

    2.3 Create a digital investment thesis.

    2.4 Define digital guiding principles.

    Outputs

    Corporate strategy analysis, PESTLE analysis, documented operational pain points (value streams)

    Customer needs assessment (journey maps)

    Digital investment thesis

    Digital guiding principles

    3 Define the Digital Roadmap

    The Purpose

    Understand the gap between the current and target state. Create transition options and assessment against qualitative and quantitative metrics to generate a list of initiatives the organization will pursue to reach the target state. Build a roadmap to plan out when each transition initiative will be implemented.

    Key Benefits Achieved

    Finalize the initiatives the organization will use to achieve the target digital state. Create a roadmap to plan out the timing of each initiative and generate an easy-to-present document for digital strategy approval.

    Activities

    3.1 Identify initiatives to achieve digital outcomes.

    3.2 Align in-flight initiatives to digital initiatives.

    3.3 Prioritize digital initiatives.

    3.4 Document architecturally significant requirements for high-priority initiatives.

    Outputs

    Digital outcomes and KPIs

    Investment/value pool matrix

    Digital initiative prioritization

    Architecturally significant requirements for high-priority initiatives

    4 Define the Digital Roadmap

    The Purpose

    Plan your approach to socializing the digital strategy to help facilitate the cultural changes necessary for digital transformation.

    Key Benefits Achieved

    Plant the seed of digital and innovation to start making digital a part of the organization’s DNA.

    Activities

    4.1 Review and refine Digital Strategy on a Page.

    4.2 Assess company culture.

    4.3 Define high-level cultural changes needed for successful transformation.

    4.4 Define the role of the digital transformation team.

    4.5 Establish digital transformation team membership and desired outcomes.

    Outputs

    Digital Strategy on a Page

    Strategyzer Culture Map

    Digital transformation team charter

    Microsoft Teams Cookbook

    • Buy Link or Shortcode: {j2store}408|cart{/j2store}
    • member rating overall impact: 8.8/10 Overall Impact
    • member rating average dollars saved: $6,299 Average $ Saved
    • member rating average days saved: 27 Average Days Saved
    • Parent Category Name: DR and Business Continuity
    • Parent Category Link: /business-continuity

    Remote work calls for leveraging your Office 365 license to use Microsoft Teams – but IT is unsure about best practices for governance and permissions. Moreover, IT has few resources to help train end users with Teams best practices.

    Our Advice

    Critical Insight

    Microsoft Teams is not a standalone app. Successful utilization of Teams occurs when conceived in the broader context of how it integrates with Office 365. Understanding how information flows between Teams, SharePoint Online, and OneDrive for Business, for instance, will aid governance with permissions, information storage, and file sharing.

    Impact and Result

    Use Info-Tech’s Microsoft Teams Cookbook to successfully implement and use Teams. This cookbook includes recipes for:

    • IT best practices concerning governance of the creation process and Teams rollout.
    • End-user best practices for Teams functionality and common use cases.

    Microsoft Teams Cookbook Research & Tools

    Start here – read the Executive Brief

    Learn critical insights for an effective Teams rollout.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    • Microsoft Teams Cookbook – Sections 1-2

    1. Teams for IT

    Understand best practices for governance of the Teams creation process and Teams rollout.

    • Microsoft Teams Cookbook – Section 1: Teams for IT

    2. Teams for end users

    Get end users on board with this series of how-tos and common use cases for Teams.

    • Microsoft Teams Cookbook – Section 2: Teams for End Users

    [infographic]


    Further reading

    Microsoft Teams Cookbook

    Recipes for best practices and use cases for Microsoft Teams.

    Table of contents

    Executive Brief

    Section 1: Teams for IT

    Section 2: Teams for End Users

    Executive Summary

    Situation

    Remote work calls for leveraging your Office 365 license to utilize Teams – but IT is unsure about best practices for governance and permissions.

    Without a framework or plan for governing the rollout of Teams, IT risks overlooking secure use of Teams, the phenomenon of “teams sprawl,” and not realizing how Teams integrates with Office 365 more broadly.

    Complication

    Teams needs to be rolled out quickly, but IT has few resources to help train end users with Teams best practices.

    With teams, channels, chats, meetings, and live events to choose from, end users may get frustrated with lack of guidance on how to use Teams’ many capabilities.

    Resolution

    Use Info-Tech’s Microsoft Teams Cookbook to successfully implement and utilize Teams. This cookbook includes recipes for:

    • IT best practices concerning governance of the creation process and Teams rollout.
    • End-user best practices for Teams functionality and common use cases.

    Key Insights

    Teams is not a standalone app

    Successful utilization of Teams occurs when conceived in the broader context of how it integrates with Office 365. Understanding how information flows between Teams, SharePoint Online, and OneDrive for Business, for instance, will aid governance with permissions, information storage, and file sharing.

    IT should paint the first picture for team creation

    No initial governance for team creation can lead to “teams sprawl.” While Teams was built to allow end users’ creativity to flow in creating teams and channels, this can create problems with a cluttered interface and keeping track of information. To prevent end-user dissatisfaction here, IT’s initial Teams rollout should offer a basic structure for end users to work with first, limiting early teams sprawl.

    The Teams admin center can only take you so far with permissions

    Knowing how Teams integrates with other Office 365 apps will help with rolling out sensitivity labels to protect important information being accidentally shared in Teams. Of course, technology only does so much – proper processes to train and hold people accountable for their actions with data sharing must be implemented, too.

    Related Info-Tech Research

    Establish a Communication and Collaboration System Strategy

    Don’t waste your time deploying yet another collaboration tool that won’t get used.

    Modernize Communication and Collaboration Infrastructure

    Your legacy telephony infrastructure is dragging you down – modern communications and collaboration technology will dramatically improve productivity.

    Migrate to Office 365 Now

    One small step to cloud, one big leap to Office 365. The key is to look before you leap.

    Section 1: Teams for IT

    Governance best practices and use cases for IT

    Section 1

    Teams for IT

    Section 2

    Teams for end users

    From determining prerequisites to engaging end users.

    IT fundamentals
    • Creation process
    • Teams rollout
    Use cases
    • Retain and search for legal/regulatory compliance
    • Add an external user to a team
    • Delete/archive a team

    Overview: Creation process

    IT needs to be prepared to manage other dependent services when rolling out Teams. See the figure below for how Teams integrates with these other Office 365 applications.

    A flow chart outlining how Teams integrates with other Office 365 applications. Along the side are different applications, from the top: 'Teams client', 'OneDrive for Business', 'Sharepoint Online', 'Planner (Tasks for Teams)', 'Exchange Online', and 'Stream'. Along the top are services of 'Teams client', 'Files', 'Teams', 'Chat', 'Meeting', and 'Calls'.

    Which Microsoft 365 license do I need to access Teams?

    • Microsoft 365 Business Essentials
    • Microsoft 365 Business Premium
    • Office 365 Enterprise, E1, E3, or E5
    • Office 365 Enterprise E4 (if purchased prior to its retirement)

    Please note: To appeal to the majority of Info-Tech’s members, this blueprint refers to Teams in the context of Office 365 Enterprise licenses.

    Assign admin roles

    You will already have at least one global administrator from setting up Office 365.

    Global administrators have almost unlimited access to settings and most of the data within the software, so Microsoft recommends having only two to four IT and business owners responsible for data and security.

    Info-Tech Best Practice

    Configure multifactor authentication for your dedicated Office 365 global administrator accounts and set up two-step verification.

    Once you have organized your global administrators, you can designate your other administrators with “just-enough” access for managing Teams. There are four administrator roles:

    Teams Service Administrator Manage the Teams service; manage and create Microsoft 365 groups.
    Teams Communications Administrator Manage calling and meetings features with Teams.
    Teams Communications Support Engineer Troubleshoot communications issues within Teams using the advanced troubleshooting toolset.
    Teams Communications Support Specialist Troubleshoot communications issues using Call Analytics.

    Prepare the network

    There are three prerequisites before Teams can be rolled out:

    • UDP ports 3478 through 3481 are opened.
    • You have a verified domain for Office 365.
    • Office 365 has been rolled out, including Exchange Online and SharePoint Online.

    Microsoft then recommends the following checklist to optimize your Teams utilization:

    • Optimize calls and performance using the Call Quality Dashboard.
    • Assess network requirements in the Network Planner in the Teams admin center.
    • Ensure all computers running Teams client can resolve external DNS queries.
    • Check adequate public IP addresses are assigned to the NAT pools to prevent port exhaustion.
    • Route to local or regional Microsoft data centers.
    • Whitelist all Office 365 URLs to move through security layers, especially IDS/IPS.
    • Split tunnel Teams traffic so it bypasses your organization’s VPN.

    Info-Tech Best Practice

    For online support and walkthroughs, utilize Advisor for Teams. This assistant can be found in the Teams admin center.

    Team Creation

    You can create and manage Teams through the Teams PowerShell module and the Teams admin center. Only the global administrator and Teams service administrator have full administrative capabilities in this center.

    Governance over team creation intends to prevent “teams sprawl” – the phenomenon whereby end users create team upon team without guidance. This creates a disorganized interface, with issues over finding the correct team and sharing the right information.

    Prevent teams sprawl by painting the first picture for end users:

    1. Decide what kind of team grouping would best fit your organization: by department or by project.
    2. Start with a small number of teams before letting end users’ creativity take over. This will prevent initial death by notifications and support adoption.
    3. Add people or groups to these teams. Assign multiple owners for each team in case people move around at the start of rollout or someone leaves the organization.
    4. Each team has a general channel that cannot be removed. Use it for sharing an overview of the team’s goals, onboarding, and announcements.

    Info-Tech Best Practice

    For smaller organizations that are project-driven, organize teams by projects. For larger organizations with established, siloed departments, organize by department; projects within departments can become channels.

    Integrations with SharePoint Online

    Teams does not integrate with SharePoint Server.

    Governance of Teams is important because of how tightly it integrates with other Office 365 apps, including SharePoint Online.

    A poor rollout of Teams will have ramifications in SharePoint. A good rollout will optimize these apps for the organization.

    Teams and SharePoint integrate in the following ways:

    • Each team created in Teams automatically generates a SharePoint team site behind it. All documents and chat shared through a team are stored in that team’s SharePoint document library.
    • As such, all files shared through Teams are subject to SharePoint permissions.
    • Existing SharePoint folders can be tied to a team without needing to create a new one.
    • If governance over resource sharing in Teams is poor, information can get lost, duplicated, or cluttered throughout both Teams and SharePoint.

    Info-Tech Best Practice

    End users should be encouraged to integrate their teams and channels with existing SharePoint folders and, where no folder exists, to create one in SharePoint first before then attaching a team to it.

    Permissions

    Within the Teams admin center, the global or Teams service administrator can manage Teams policies.

    Typical Teams policies requiring governance include:

    • The extent end users can discover or create private teams or channels
    • Messaging policies
    • Third-party app use

    Chosen policies can be either applied globally or assigned to specific users.

    Info-Tech Best Practice

    If organizations need to share sensitive information within the bounds of a certain group, private channels help protect this data. However, inviting users into that channel will enable them to see all shared history.

    External and guest access

    Within the security and compliance center, the global or Teams service administrator can set external and guest access.

    External access (federation) – turned on by default.

    • Lets you find, call, and chat with users in other domains. External users will have no access to the organization’s teams or team resources.

    Guest access – turned off by default.

    • Lets you add individual users with their own email address. You do this when you want external users to access teams and team resources. Approved guests will be added to the organization’s active directory.

    If guest access is enabled, it is subject to Azure AD and Office 365 licensing and service limits. Guests will have no access to the following, which cannot be changed:

    • OneDrive for Business
    • An organization’s calendar/meetings
    • PSTN
    • Organization’s hierarchical chart
    • The ability to create, revise, or browse a team
    • Upload files to one-on-one chat

    Info-Tech Best Practice

    Within the security and compliance center, you can allow users to add sensitivity labels to their teams that can prevent external and guest access.

    Expiration and archiving

    To reduce the number of unused teams and channels, or delete information permanently, the global or Teams service administrator can implement an Office 365 group expiration and archiving policy through the Teams admin center.

    If a team has an expiration policy applied to it, the team owner will receive a notification for team renewal 30 days, 15 days, and 1 day before the expiry date. They can renew their team at any point within this time.

    • To prevent accidental deletion, auto-renewal is enabled for a team. If the team owner is unable to manually respond, any team that has one channel visit from a team member before expiry is automatically renewed.
    • A deleted Office 365 group is retained for 30 days and can be restored at any point within this time.

    Alternatively, teams and their channels (including private) can be archived. This will mean that all activity for the team ceases. However, you can still add, remove, and update roles of the members.

    Retention and data loss prevention

    Retention policies can be created and managed in the Microsoft 365 Compliance Center or the security and compliance center PowerShell cmdlets. This can be applied globally or to specific users.

    By default, information shared through Teams is retained forever.

    However, setting up retention policies ensures data is retained for a specified time regardless of what happens to that data within Teams (e.g. user deletes).

    Info-Tech Best Practice

    To prevent external or guest users accessing and deleting sensitive data, Teams is able to block this content when shared by internal users. Ensure this is configured appropriately in your organization:

    • For guest access in teams and channels
    • For external access in meetings and chat

    Please note the following limitations of Teams’ retention and data loss prevention:

    • Organization-wide retention policies will need to be manually inputted into Teams. This is because Teams requires a retention policy that is independent of other workloads.
    • As of May 2020, retention policies apply to all information in Teams except private channel messages. Files shared in private channels, though, are subject to retention policies.
    • Teams does not support advanced retention settings, such as a policy that pertains to specific keywords or sensitive information.
    • It will take three to seven days to permanently delete expired messages.

    Teams telephony

    Teams has built-in functionality to call any team member within the organization through VoIP.

    However, Teams does not automatically connect to the PSTN, meaning that calling or receiving calls from external users is not immediately possible.

    Bridging VoIP calls with the PSTN through Teams is available as an add-on that can be attached to an E3 license or as part of an E5 license.

    There are two options to enable this capability:

    • Enable Phone System. This allows for call control and PBX capabilities in Office 365.
    • Use direct routing. You can use an existing PSTN connection via a Session Border Controller that links with Teams (Amaxra).

    Steps to implement Teams telephony:

    1. Ensure Phone System and required (non-Microsoft-related) services are available in your country or region.
    2. Purchase and assign Phone System and Calling Plan licenses. If Calling Plans are not available in your country or region, Microsoft recommends using Direct Routing.
    3. Get phone numbers and/or service numbers. There are three ways to do this:
      • Get new numbers through the Teams admin center.
      • If you cannot get new numbers through the Teams admin center, you can request new numbers from Microsoft directly.
      • Port or transfer existing numbers. To do this, you need to send Microsoft a letter of authorization, giving them permission to request and transfer existing numbers on your behalf.
    4. To enable service numbers, including toll-free numbers, Microsoft recommends setting up Communications Credits for your Calling Plans and Audio Conferencing.

    Overview: Teams rollout

    1. From Skype (and Slack) to Teams
    2. Gain stakeholder purchase
    3. Employ a phased deployment
    4. Engage end users

    Skype for Business is being retired; Microsoft offers a range of transitions to Teams.

    Combine the best transition mode with Info-Tech’s adoption best practices to successfully onboard and socialize Teams.

    From Skype to Teams

    Skype for Business Online will be retired on July 31, 2021. Choose from the options below to see which transition mode is right for your organization.

    Skype for Business On-Premises will be retired in 2024. To upgrade to Teams, first configure hybrid connectivity to Skype for Business Online.

    Islands mode (default)

    • Skype for Business and Teams coexist while Teams is rolled out.
    • Recommended for phased rollouts or when Teams is ready to use for chat, calling, and meetings.
    • Interoperability is limited. Teams and Skype for Business only transfer information if an internal Teams user sends communications to an external Skype for Business user.

    Teams only mode (final)

    • All capabilities are enabled in Teams and Skype for Business is disabled.
    • Recommended when end users are ready to switch fully to Teams.
    • End users may retain Skype for Business to join meetings with non-upgraded or external parties. However, this communication is only initiated from the Skype for Business external user.

    Collaboration first mode

    • Skype for Business and Teams coexist, but only Teams’ collaboration capabilities are enabled. Teams communications capabilities are turned off.
    • Recommended to leverage Skype for Business communications yet utilize Teams for collaboration.

    Meetings first mode

    • Skype for Business and Teams coexist, but only Teams’ meetings capabilities are enabled.
    • Recommended for organizations that want to leverage their Skype for Business On-Premises’ Enterprise Voice capability but want to benefit from Teams’ meetings through VoIP.

    From Slack to Teams

    The more that’s left behind in Slack, the easier the transition. As a prerequisite, pull together the following information:

    • Usage statistics of Slack workspaces and channels
    • What apps end users utilize in Slack
    • What message history you want to export
    • A list of users whose Slack accounts can map on to required Microsoft accounts
    Test content migration

    Your Slack service plan will determine what you can and can’t migrate. By default, public channels content can be exported. However, private channels may not be exportable, and a third-party app is needed to migrate Direct Messages.

    Files migration

    Once you have set up your teams and channels in Teams, you can programmatically copy files from Slack into the target Teams channel.

    Apps migration

    Once you have a list of apps and their configurations used in Slack’s workspaces, you can search in Teams’ app store to see if they’re available for Teams.

    User identity migration

    Slack user identities may not map onto a Microsoft account. This will cause migration issues, such as problems with exporting text content posted by that user.

    Follow the migration steps to the right.

    Importantly, determine which Slack workspaces and channels should become teams and channels within Teams.

    Usage statistics from Slack can help pinpoint which workspaces and channels are redundant.

    This will help IT paint an ordered first picture for new Teams end users.

    1. Create teams and channels in Teams
    2. Copy files into Teams
    3. Install apps, configure Office 365 Connecters
    4. Import Slack history
    5. Disable Slack user accounts

    Info-Tech Best Practice

    Avoid data-handling violations. Determine what privacy and compliance regulations (if any) apply to the handling, storage, and processing of data during this migration.

    Gain stakeholder purchase

    Change management is a challenging aspect of implementing a new collaboration tool. Creating a communication and adoption plan is crucial to achieving universal buy-in for Teams.

    To start, define SMART objectives and create a goals cascade.

    Specific Measurable Actionable Realistic Time Bound
    Make sure the objective is clear and detailed. Objectives are `measurable` if there are specific metrics assigned to measure success. Metrics should be objective. Objectives become actionable when specific initiatives designed to achieve the objective are identified. Objectives must be achievable given your current resources or known available resources. An objective without a timeline can be put off indefinitely. Furthermore, measuring success is challenging without a timeline.
    Who, what, where, why? How will you measure the extent to which the goal is met? What is the action-oriented verb? Is this within my capabilities? By when: deadline, frequency?

    Sample list of stakeholder-specific benefits from improving collaboration

    Stakeholder Driver Benefits
    Senior Leadership Resource optimization Increased transparency into IT operational costs.
    Better ability to forecast hardware, resourcing costs.
    All employees Increasing productivity Apps deployed faster.
    Issues fixed faster.
    Easier access to files.
    Able to work more easily offsite.
    LBU-HR, legal, finance Mitigating risk Better able to verify compliance with external regulations.
    Better understanding of IT risks.
    Service desk Resource optimization Able to resolve issues faster.
    Fewer issues stemming from updates.
    Tier 2 Increasing productivity Less time spent on routine maintenance.

    Use these activities to define what pain points stakeholders face and how Teams can directly mitigate those pain points.

    (Source: Rationalize Your Collaboration Tools (coming soon), Activities: 3.1C – 3.1D)

    Employ a phased deployment

    Info-Tech Best Practice

    Deploy Teams over a series of phases. As such, if you are already using Skype for Business, choose one of the coexistence phases to start.

      1. Identify and pilot Teams with early adopters that will become your champions. These champions should be formally trained, be encouraged to help and train their colleagues, and be positively reinforced for their efforts.
      2. Iron out bugs identified with the pilot group and train middle management. Enterprise collaboration tool adoption is strongly correlated with leadership adoption.
        1. Top-level management
          Control and direct overall organization.
        2. Middle management
          Execute top-level management’s plans in accordance with organization’s norms.
        3. First-level management
          Execute day-to-day activities.
      3. Use Info-Tech’s one-pager marketing template to advertise the new tool to stakeholders. Highlight how the new tool addresses specific pain points. Address questions stemming from fear and uncertainty to avoid employees’ embarrassment or their rejection of the tool.
    A screenshot of Info-Tech's one-pager marketing template.
    1. Extend the pilot to other departments and continue this process for the whole organization.

    (Source: Rationalize Your Collaboration Tools (coming soon), Tools:GANTT Chart and Marketing Materials, Activities: 3.2A – 3.2B)

    Info-Tech Insight

    Be in control of setting and maintaining expectations. Aligning expectations with reality and the needs of employees will lower onboarding resistance.

    Engage end users

    Short-term best practices

    Launch day:
    • Hold a “lunch and learn” targeted training session to walk end users through common use cases.
    • Open a booth or virtual session (through Teams!) and have tool representatives available to answer questions.
    • Create a game to get users exploring the new tool – from scavenger hunts to bingo.
    Launch week:
    • Offer incentives for using the tool and helping others, including small gift cards.
    • Publicize achievements if departments hit adoption milestones.

    Long-term best practices

    • Make available additional training past launch week. End users should keep learning new features to improve familiarity.
    • Distribute frequent training clips, slowly exposing end users to more complex ways of utilizing Teams.
    • Continue to positively reinforce and recognize those who use Teams well. This could be celebrating those that help others use the tool, how active certain users are, and attendance at learning events.

    Info-Tech Best Practice

    Microsoft has a range of training support that can be utilized. From instructor-led training to “Coffee in the Cloud” sessions, leverage all the support you can.

    Use case #1: Retain and search data for legal/regulatory compliance

    Scenario:

    Your organization requires you to retain data and documents for a certain period of time; however, after this period, your organization wishes to delete or archive the data instead of maintaining it indefinitely. Within the timeframe of the retention policy, the admin may be asked to retrieve information that has been requested through a legal channel.

    Purpose:
    • Maintain compliance with the legal and regulatory standards to which the organization is subject.
    Jobs:
    • Ensure the data is retained for the approved time period.
    • Ensure the policy applies to all relevant data and users.
    Solution: Retention Policies
    • Ensure that your organization has an Office 365 E3 or higher license.
    • Set the desired retention policy through the Security & Compliance Center or PowerShell by deciding which teams, channels, chats, and users the policies will apply to and what will happen once the retention period ends.
    • Ensure that matching retention policies are applied to SharePoint and OneDrive, since this is where files shared in Teams are stored.
    • Be aware that Teams retention policies cannot be applied to messages in private channels.
    Solution: e-Discovery
    • If legally necessary, place users or Teams on legal hold in order to retain data that would be otherwise deleted by your organization’s retention policies.
    • Perform e-discovery on Teams messages, files, and summaries of meetings and calls through the Security & Compliance Center.
    • See Microsoft’s chart on the next slide for what is e-discoverable.

    Content subject to e-discovery

    Content type eDiscoverable Notes
    Teams chat messages Yes Chat messages from chats where guest users are the only participants in a 1:1 or 1:N chat are not e-discoverable.
    Audio recordings No  
    Private channel messages Yes  
    Emojis, GIFs, stickers Yes  
    Code snippets No  
    Chat links Yes  
    Reactions (likes, hearts, etc) No  
    Edited messages Yes If the user is on hold, previous versions of edited messages are preserved.
    Inline images Yes  
    Tables Yes  
    Subject Yes  
    Quotes Yes Quoted content is searchable. However, search results don’t indicate that the content was quoted.
    Name of channel No  

    E-discovery does not capture audio messages and read receipts in MS Teams.

    Since files shared in private channels are stored separately from the rest of a team, follow Microsoft’s directions for how to include private channels in e-discovery. (Source: “Conduct an eDiscovery investigation of content in Microsoft Teams,” Microsoft, 2020.)
    Use case #2: Add external person to a team

    Scenario:

    A team in your organization needs to work in an ongoing way with someone external to the company. This user needs access to the relevant team’s work environment, but they should not be privy to the goings-on in the other parts of the organization.

    Jobs:

    This external person needs to be able to:

    • Attend meetings
    • Join calls
    • Chat with individual team members
    • View and collaborate on the team’s files
    Solution:
    • If necessary, set a data loss prevention policy to prevent your users from sharing certain types of information or files with external users present in your organization’s Teams chats and public channels.
    • Ensure that your Microsoft license includes DLP protection. However:
      • DLP cannot be applied to private channel messages.
      • DLP cannot block messages from external Skype for Business users nor external users who are not in “Teams only” mode.
    • Ensure that you have a team set up for the project that you wish the external user to join. The external user will be able to see all the channels in this team, unless you create a private channel they are restricted from.
    • Complete Microsoft’s “Guest Access Checklist” to enable guest access in Teams, if it isn’t already enabled.
    • As admin, give the external user guest access through the Teams admin center or Azure AD B2B collaboration. (If given permission, team owners can also add guests through the Teams client).
    • Decide whether to set a policy to monitor and audit external user activity.

    Use case #3: Delete/archive a team

    Scenario:

    In order to avoid teams sprawl, organizations may want IT to periodically delete or archive unused teams within the Teams client in order to improve the user interface.

    Alternately, if you are using a project-based approach to organizing Teams, you may wish to formalize a process to archive a team once the project is complete.

    Delete:
    • Determine if the team owner anticipates the team will need to be restored one day.
    • Ensure that deletion does not contradict the organization’s retention policy.
    • If not, proceed with deletion. Find the team in the Teams admin center and delete.
    • Restore a deleted team within 30 days of its initial deletion through PowerShell.
    Archive:
    • Determine if the team owner anticipates the team will need to be restored one day.
    • Find the relevant team in the Teams admin center and change its status to “Archived.”
    • Restore the archived team if the workspace becomes relevant once again.

    Info-Tech Best Practice

    Remind end users that they can hide teams or channels they do not wish to see in their Teams interface. Knowing a team can be hidden may impact a team owner’s decision to delete it.

    Section 2: Teams for End Users

    Best practices for utilizing teams, channels, chat, meetings, and live events

    Section 1

    Teams for IT

    Section 2

    Teams for end users

    From Teams how-tos to common use cases for end users.

    End user basics
    • Teams, channels, and chat
    • Meetings and live events
    Common use cases: Workspaces
    • WS#1: Departments
    • WS#2: A cross-functional committee
    • WS#3: An innovation day event
    • WS#4: A non-work-related social event
    • WS#5: A project team with a defined end time
    Common use cases: Meetings
    • M#1: Job interview with an external candidate
    • M#2: Quarterly board meeting
    • M#3: Weekly recurring team meeting
    • M#4: Morning stand-up/scrum
    • M#5: Phone call between two people

    Overview: Teams, channels, and chat

    Teams

    • Team: A workspace for a group of collaborative individuals.
      • Public channel: A focused area where all members of a team can meet, communicate, and share ideas and content.
      • Private channel: Like a public channel but restricted to a subset of team members, defined by channel owner.

    Chat

    • Chat: Two or more users collected into a common conversation thread.
    (Source: “Overview of teams and channels in Microsoft Teams,” Microsoft, 2020.)
    For any Microsoft Teams newcomer, the differences between teams, channels, and chat can be confusing.

    Use Microsoft’s figure (left) to see how these three mediums differ in their role and function.

    Best practices: Workspaces 1/2

      Team
    A workspace for a group of collaborative individuals.
    Public Channel
    A focused area where all members of a team can meet, communicate, and share ideas and content.
    Private Channel
    Like a public channel but restricted to a subset of team members, defined by channel owner.
    Group Chat
    Two or more users collected into a common conversation thread.
    Limits and Administrative Control
    Who can create? Default setting: All users in an organization can create a team

    Maximum 500,000 teams per tenant

    Any member of a team can create a public channel within the team

    Maximum 200 public channels per team

    Any member of a team can create a private channel and define its members

    Maximum 30 private channels per team

    Anyone
    Who can add members? Team owner(s); max 5,000 members per team N/A Channel owner(s) can add up to 250 members Anyone can bring new members into the chat (and decide if they can see the previous history) up to 100 members
    Who can delete? Team owner/admin can delete Any team member Channel owner(s) Anyone can leave a chat but cannot delete chat, but they are never effectively deleted
    Social Context
    Who can see it? Public teams are indexed and searchable

    Private teams are not indexed and are visible only to joined members

    All members of the team can see all public channels. Channels may be hidden from view for the purposes of cleaning up the UI. Individuals will only see private channels for which they have membership Only participants in the group chat can see the group chat
    Who can see the content? Team members can see any content that is not otherwise part of a private channel All team members All members of the private channel Only members of the group chat

    When does a Group Chat become a Channel?

    • When it’s appropriate for the conversation to have a gallery – an audience of members who may not be actively participating in the discussion.
    • When control over who joins the conversation needs to be centrally governed and not left up to anyone in the discussion.
    • When the discussion will persist over a longer time period.
    • When the number of participants approaches 100.

    When does a Channel become a Team?

    • When a team approaches 30 private channels, many of those private channels are likely candidates to become their own team.
    • When the channel membership needs to extend beyond the boundary of the team membership.

    Best practices: Workspaces 2/2

      Team
    A workspace for a group of collaborative individuals.
    Public Channel
    A focused area where all members of a team can meet, communicate, and share ideas and content.
    Private Channel
    Like a public channel but restricted to a subset of team members, defined by channel owner.
    Group Chat
    Two or more users collected into a common conversation thread.
    Data and Applications
    Where does the content live? SharePoint: Every team resides in its own SharePoint site SharePoint: Each team (public and private) has its own folder off the root of the SharePoint site’s repository SharePoint: Each team (public and private) has its own folder off the root of the SharePoint site’s repository OneDrive: Files that are shared in a chat are stored in the OneDrive folder of the original poster and shared to the other members
    How does the data persist or be retained? If a team expires/is deleted, its corresponding SharePoint site and those artifacts are also deleted Available for 21 days after deletion. Any member of the team can delete a public channel. The team owner and private channel owner can delete/restore a private channel Chats are never effectively deleted. They can be hidden to clean up the user interface.
    Video N/A Yes, select “Meet now” in channel below text entry box Yes, select “Meet now” in channel below text entry box Yes
    Phone calls N/A Yes, select “Meet now” in channel below text entry box Yes, select “Meet now” in channel below text entry box Yes
    Shared computer audio/screen N/A Yes, select “Meet now” in channel below text entry box Yes, select “Meet now” in channel below text entry box Yes
    File-sharing Within channels Yes. Frequently used/collaborated files can be turned into discrete tab. Yes. Frequently used/collaborated files can be turned into discrete tab. Yes
    Wikis Within channels Yes Yes No
    Whiteboarding No No No No

    When does a Team become a Channel?

    • When a team’s purpose for existing can logically be subsumed by another team that has a larger scope.

    When does a Channel become a Group Chat?

    • When a conversation within a channel between select users does not pertain to that channel’s scope (or any other existing channel), they should move the conversation to a group chat.
    • However, this is until that group chat desires to form a channel of its own.

    Create a new team

    Team owner: The person who creates the team. It is possible for the team owner to then invite other members of the team to become co-owners to distribute administrative responsibilities.

    Team members: People who have accepted their invitation to be a part of the team.

    NB: Your organization can control who has permission to set up a team. If you can’t set a up a team, contact your IT department.

    Screenshots detailing how to create a new team in Microsoft Teams, steps 1 to 3. Step 1: 'Click the <Teams data-verified= tab on the left-hand side of the app'. Step 2: 'At the bottom of the app, click '. Step 3: 'Under the banner , click '.">

    Create a new team

    Screenshot detailing how to create a new team in Microsoft Teams, the step 4 starting point with an arrow pointing to the 'Build a team from scratch' button.

    Decide from these two options:

    • Building a team from scratch, which will create a new group with no prior history imported (steps 4.1–4.3).
    • Creating a team from an existing group in Office 365, including an already existing team (steps 4.4–4.6).

    NB: You cannot create a team from an existing group if:

    • That group has 5,000 members or more.
    • That group is in Yammer.

    Screenshot detailing how to create a new team in Microsoft Teams, step 4.1. There are buttons for 'Private' and 'Public'.

    Decide if you want you new team from scratch to be private or public. If you set up a private team, any internal or external user you invite into the team will have access to all team history and files shared.

    Screenshot detailing how to create a new team in Microsoft Teams, step 4.2 and 4.3. 4.2 has a space to give your team a name and another for a description. 4.3 says 'Then click <Create data-verified='.">

    Create a new team

    Screenshot detailing how to create a new team in Microsoft Teams, the step 4 starting point with an arrow pointing to the 'Create from...' button.

    Decide from these two options:

    • Building a team from scratch, which will create a new group with no prior history imported (steps 4.1–4.3).
    • Creating a team from an existing group in Office 365, including an already existing team (steps 4.4–4.6).

    NB: You cannot create a team from an existing group if:

    • That group has 5,000 members or more.
    • That group is in Yammer.

    Screenshot detailing how to create a new team in Microsoft Teams, step 4.4. It reads 'Create a new team from something you already own' with a button for 'Team'.

    Configure your new team settings, including privacy, apps, tabs, and members.

    Screenshot detailing how to create a new team in Microsoft Teams, step 4.5 and 4.6. 4.5 has a space to give your team a name, a description, choose privacy settings, and what you'd like to include from the original team. 4.6 says 'Then click <Create data-verified='.">

    Add team members

    Remove team members

    Screenshot detailing how to add team members in Microsoft Teams, step 1.

    To add a team member, on the right-hand side of the team name, click “More options.”

    Then, from the drop-down menu, click “Add member.”

    Screenshot detailing how to remove team members in Microsoft Teams, step 1.

    Only team owners can remove a team member. To do so, on the right-hand side of the team name, click “More options.”

    Then, from the drop-down menu, click “Manage team.”

    Screenshot detailing how to add team members in Microsoft Teams, step 2.

    If you’re a team owner, you can then type a name or an email address to add another member to the team.

    If you’re a team member, typing a name or an email address will send a request to the team owner to consider adding the member.

    Screenshot detailing how to remove team members in Microsoft Teams, step 2.

    Under the “Members” tab, you’ll see a list of the members in the team. Click the “X” at the far right of the member’s name to remove them.

    Team owners can only be removed if they change their role to team member first.

    Create a new channel

    Screenshot detailing how to create a new channel in Microsoft Teams, step 1.

    On the right-hand side of the team name, click “More options.”

    Then, from the drop-down menu, click “Add channel.”

    Screenshot detailing how to create a new channel in Microsoft Teams, step 2.

    Name your channel, give a description, and set your channel’s privacy.

    Screenshot detailing how to create a new channel in Microsoft Teams, step 3.

    To manage subsequent permissions, on the right-hand side of the channel name, click “More options.”

    Then, from the drop-down menu, click “Manage channel.”

    Adding and removing members from channels:

    Only members in a team can see that team’s channels. Setting channel privacy as “standard” means that the channel can be accessed by anyone in a team. Unless privacy settings for a channel are set as “private” (from which the channel creator can choose who can be in that channel), there is no current way to remove members from channels.

    It will be up to the end user to decide which channels they want to hide.

    Link team/channel to SharePoint folder

    Screenshot detailing how to link a team or channel to a SharePoint folder in Microsoft Teams, steps 1, 2, and 3. Step 1: 'Along the top of the team/channel tab bar, click the “+” symbol'. Step 2: 'Select “Document Library” to link the team/channel to a SharePoint folder'. Step 3: 'Copy and paste the SharePoint URL for the desired folder, or search in “Relevant sites” if the folder can be found there'.

    Need to find the SharePoint URL?

    Screenshot detailing how to find the SharePoint URL in Microsoft Teams. 'Locate the folder in SharePoint and click <Show actions data-verified=', 'Click to access the folder's SharePoint URL.'">

    Hide/unhide teams

    Hide/unhide channels

    Screenshot detailing how to hide and unhide teams in Microsoft Teams, step 1.

    To hide a team, on the right-hand side of the team name, click “More options.”

    Then, from the drop-down menu, click “Hide.” Hidden teams are moved to the “hidden teams” menu at the bottom of your team list.

    Screenshot detailing how to hide and unhide channels in Microsoft Teams, step 1.

    To hide a channel, on the right-hand side of the channel name, click “More options.”

    Then, from the drop-down menu, click “Hide.” Hidden channels are moved to the “hidden channels” menu at the bottom of your channel list in that team.

    Screenshot detailing how to hide and unhide teams in Microsoft Teams, step 2. Screenshot of a button that says 'Hidden teams'.

    To unhide a team, click on the “hidden teams” menu. On the right-hand side of the team name, click “More options.”

    Then, from the drop-down menu, click “Show.”

    Screenshot detailing how to hide and unhide channels in Microsoft Teams, step 2.

    To unhide a channel, click on the “hidden channels” menu at the bottom of the team. This will produce a drop-down menu of all hidden channels in that team.

    Hover over the channel you want to unhide and click “Show.”

    Find/join teams

    Leave teams

    Screenshot detailing how to find and join teams in Microsoft Teams, step 1. Click the “Teams” tab on the left-hand side of the app. Screenshot detailing how to find and join teams in Microsoft Teams, step 2.

    At the bottom of the app, click “Join or create a team.” Teams will then suggest a range of teams that you might be looking for. You can join public teams immediately. You will have to request approval to join a private team.

    Screenshot detailing how to leave teams in Microsoft Teams.

    To leave a team, on the right-hand side of the team name, click “More options.”

    Then, from the drop-down menu, click “Leave the team.”

    NB: If the owner of a private team has switched off discoverability, you will have to contact that owner to join that team. Screenshot detailing how to find and join teams in Microsoft Teams, step 3. If you can’t immediately see the team, you have two options: either search for the team or enter that team’s code under the banner “Join a team with a code.” Can I find a channel?

    No. To join a channel, you need to first join the team that channel belongs to.

    Can I leave a channel?

    No. The most you can do is hide the channel. By default, if you join a team you will have access to all the channels within that team (unless a channel is private, in which case you’ll have to request access to that channel).

    Create a chat

    Screenshots detailing how to create a chat in Microsoft Teams, steps 1 to 5. Step 1:'Click the “Chat” tab on the left hand side of the app (or keyboard shortcut Ctrl+N)'. Step 2: 'Search the name of the person you want to chat with'. Step 3: 'You’re now ready to start the chat! You can also send a chat message while working in a separate channel by typing/chat into the search bar and entering the recipient’s name'. Step 4: 'For group chat, click the “Add people” button in the top right hand corner of the app to add other persons into the existing chat'. Step 5: 'You can then rename the group chat (if there are 3+ people) by clicking the “Name group chat” option to the right of the group chat members’ names'.

    Hide a chat

    Unhide a chat

    Screenshots detailing how to hide a chat in Microsoft Teams, steps 1 to 3. Step 1:'Click the “Chat” tab on the left-hand side of the app'. Step 2: 'Search the name of the chat or group chat that you want to hide'. Step 3: In either 'Single person chat options' or 'Group chat options' Click “More options.” Then click “Hide.”' To unhide a chat, search for the hidden person or name of the group chat in the search bar. Click “More options.” Then click “Unhide.” Screenshot detailing how to unhide a chat in Microsoft Teams.

    Leave a chat

    You can only leave group chats. To do so, click “More options.” Then click “Leave.” Screenshot detailing how to leave a chat in Microsoft Teams.

    Overview: Meetings and live events

    Teams Meetings: Real-time communication and collaboration between a group, limited to 250 people.

    Teams Live Events: designed for presentations and webinars to a large audience of up to 10,000 people, in which attendees watch rather than interact.


    Office 365 and Microsoft 365 Licenses

    I want to: F1 F3 E1 E3 E5 Audio conferencing add-on
    Join a Teams meeting No license required. Any email address can participate in a Teams meeting.
    Attend a Teams meeting with a dial-in phone number No license required. Any phone number can dial into a Teams meeting. (Meeting organizers need to have an Audio Conferencing add-on license to send an invite that includes dial-in conferencing.)
    Attend a Teams live event No license required. Any phone number can dial into a Teams live event.
    Create a Teams meeting for up to 250 attendees   One of these licensing plans
    Create a Teams meeting for up to 250 attendees with a dial-in phone number   One of these licensing plans + Audio Conferencing (Meeting organizers need to have an Audio Conferencing add-on license to send an invite that includes dial-in conferencing.)
    Create a Teams live event for up to 10,000 attendees     One of these licensing plans
    Dial out from a Teams meeting to add someone at their Call me at number   One of these licensing plans + Audio Conferencing (Meeting dial out to a Call me at number requires organizers to have an E5 or Audio Conference add-in license. A dial plan may also be needed.)

    Depending on the use case, end users will have to determine whether they need to hold a meeting or a live event.

    Use Microsoft’s table (left) to see what license your organization needs to perform meetings and live events.

    (Source: “Admin quick start – Meetings and live events in Microsoft Teams,” Microsoft, 2020.)

    Best practices: Meetings

      Ad Hoc Call
    Direct audio/video call
    Scheduled Meeting Live Event
    Limits and Administrative Control
    Who can create? Anyone Anyone Anyone, unless altered by admin (permission to create MS Stream events also required if external production tools are used).
    Who can add members? Anyone in the session. The meeting organizer can add new attendees to the meeting. The event creator (the “organizer”) sets attendee permissions and assigns event group roles (“producer” and “presenter”).
    Can external stakeholders attend? Yes, through email invite. However, collaboration tools are restricted. Yes, through email invite. However, collaboration tools are restricted. Public events: yes, through shared invite link.
    Org-wide event: yes, if guest/external access granted.
    Who can delete? Anyone can leave the session. There is no artifact to delete. The meeting organizer Any attendee can leave the session.
    The organizer can cancel the event.
    Maximum attendees 100 250 10,000 attendees and 10 active presenters/producers (250 presenters and producers can be present at the event).
    Social Context
    How does the request come in? Unscheduled.
    Notification of an incoming audio or video call.
    Scheduled.
    Meeting invite, populated in the calendar, at a scheduled time.
    Meeting only auto-populated in event group’s calendars. Organizer must circulate event invite link to attendees – for instance, by pasting link into an Outlook meeting invite.
    Available Functionality
    Screen-sharing Yes Yes Producers and Presenters (through Teams, no third-party app).
    Whiteboard No Yes Yes
    OneNote (for minutes) Yes (from a member’s OneDrive) Yes, part of the meeting construct. No. A Meeting Notes tab is available instead.
    Dedicated chat space Yes. Derived from a group chat. Meeting has its own chat room. The organizer can set up a moderated Q&A (not chat) when creating the event. Only Presenters and Producers can chat.
    Recording Yes Yes Yes. Event can last up to 4 hours.

    When should an Ad Hoc Call become a Scheduled Meeting?

    • When the participants need time to prepare content for the call.
    • When an answer is not required immediately.
    • When bringing a group of people together requires logistical organizing.

    When should a Scheduled Meeting become an Ad Hoc Call?

    • When the participants can meet on short notice.
    • When a topic under discussion requires creating alignment quickly.

    When should a Live Event be created?

    • When the expected attendance exceeds 250 people.
    • If the event does not require collaboration and is mostly a presenter conveying information.

    Create a scheduled meeting

    Screenshots detailing how to create a scheduled meeting in Microsoft Teams, steps 1 to 4. Step 1:'Click the “Calendar” tab on the left-hand side of the app'. Step 2: 'On the top-right of the app, click the drop-down menu for “+ New meeting” and then “Schedule meeting.”' Step 3: 'Fill in the meeting details. When inputting internal attendees, their names will drop down without needing their email. You will need to input email addresses for external attendees'. Step 4: 'To determine internal attendees’ availability, click “Scheduling assistant” on the top left. Then click “Save” to create the meeting'.

    Create an ad hoc meeting

    Screenshots detailing how to create an ad hoc meeting in Microsoft Teams, steps 1 to 4. Step 1:'Click the “Calendar” tab on the left-hand side of the app'. Step 2: 'Along the top-right, click “Meet now.”' Step 3: 'Name your meeting, choose your audio and video settings, and click “Join now.”'. Step 4: 'To determine internal attendees’ availability, click “Scheduling assistant” on the top left. Then click “Save” to create the meeting. You’ll then be prompted to fill in the meeting details. When inputting internal attendees, their names will drop down without needing their email. You will need to input email addresses for external attendees'.

    Tip: Use existing channels to host the chatrooms for your online meetings

    When you host a meeting online with Microsoft Teams, there will always be a chatroom associated with the meeting. While this is a great place for meeting participants to interact, there is one particular downside.

    Problem: The never-ending chat. Often the activity in these chatrooms can persist long after the meeting. The chatroom itself becomes, unofficially, a channel. When end users can’t keep up with the deluge of communication, the tools have failed them.

    Solution: Adding an existing channel to the meeting. This ensures that discussion activity is already hosted in the appropriate venue for the group, during and after the meeting. Furthermore, it provides non-attendees with a means to catch up on the discussion they have missed.

    In section two of this cookbook, we will often refer to this tactic.

    A screenshot detailing how to add an existing channel to a meeting in Microsoft Teams. 'Break the habit of online booking meetings in Outlook – use the Teams Calendar View instead! In order to make use of this function, the meeting must be setup in Microsoft Teams, not Microsoft Outlook. The option to assign a channel to the meeting will then be available to the meeting organizer.'

    Don’t have a channel for the chat session of your online meeting? Perhaps you should!

    If your meeting is with a group of individuals that will be collaborating frequently, they may need a workspace that persists beyond the meeting.

    Guests can still attend the meeting, but they can’t chat!

    If there are attendees in your meeting that do not have access to the channel you select to host the chat, they will not see the chat discussion nor have any ability to use this function.

    This may be appropriate in some cases – for example, a vendor providing a briefing as part of a regular team meeting.

    However, if there are attendees outside the channel membership that need to see the meeting chat, consider another channel or simply default to not assigning one.

    Meeting settings explained

    Show device settings. For settings concerning audio, video, and whether viewing is private.

    Show meeting notes. Use to take notes throughout the meeting. The notes will stay attached to this event.

    Show meeting details. Find meeting information for: a dial-in number, conference ID, and link to join.

    Enter full screen.

    Show background effects. Choose from a range of video backgrounds to hide/blur your location.

    Turn on the captions (preview). Turn on live speech-to-text captions.

    Keypad. For dialing a number within the meeting (when enabled as an add-on with E3 or as part of E5).

    Start recording. Recorded and saved using Microsoft Stream.

    End meeting.

    Turn off incoming video. To save network bandwidth, you can decline receiving attendee’s video.

    Click “More options” to access the meetings settings.

    Screen share. In the tool tray, select “Share” to share your screen. Select particular applications if you only want to share certain information; otherwise, you can share your whole desktop.

    System audio share. To share your device’s audio while screen sharing, checkbox the “Include system audio” option upon clicking “Share.”

    If you didn’t click that option at the start but now want to share audio during screen share, click the “Include systems audio” option in the tool tray along the top of the screen.

    Give/take control of screen share. To give control, click “Give control” in the tool tray along the top of the screen when sharing content. Choose from the drop-down who you would like to give control to. In the same spot, click “Take back control” when required.

    To request control, click “Request control” in the same space when viewing someone sharing their content. Click “Release control” once finished.

    Start whiteboarding

    1. You’ll first need to enable Microsoft Whiteboard in the Microsoft 365 admin center. Ask your relevant admin to do so if Whiteboard is not already enabled.
    2. Once enabled, click “Share” in a meeting. This feature only appears if you have 3+ participants in the meeting.
    3. Under the “Whiteboard” section in the bottom right, click “Microsoft Whiteboard.”
    4. Click the pen icons to the right of the screen to begin sketching.

    NB: Anonymous, federated, or guest users are currently not supported to start, view, or ink a whiteboard in a Teams meeting.

    Will the whiteboard session be recorded if the meeting is being recorded?

    No. However, the final whiteboard will be available to all meeting attendees after the meeting, under “Board Gallery” in the Microsoft Whiteboard app. Attendees can then continue to work on the whiteboard after the meeting has ended.

    Create a live event

    Screenshots detailing how to create a live event in Microsoft Teams, steps 1 to 3. Step 1: 'Click the “Calendar” tab on the left-hand side of the app'. Step 2: 'On the top right of the app, click the drop-down menu for “+ New meeting” and then “Live event.”' Step 3: 'You will be labeled the “Event organizer.” First, fill in the live event details on the left'. Screenshot detailing how to create a live event in Microsoft Teams, step 4.

    As the organizer, you can invite other people to the event who will be the “producers” or “presenters.”

    Producers: Control the live event stream, including being able to start and stop the event, share their own and others’ video, share desktop or window, and select layout.

    Presenters: Present audio, video, or a screen.

    Screenshot detailing how to create a live event in Microsoft Teams, step 5.

    Select who your audience will be for your live event from three options: specified people and groups, the organization, or the public with no sign-in required.

    Edit the setting for whether you want recording to be available for attendees.

    Then click “Schedule” to finish.

    Live event settings explained

    When you join the live event as a producer/presenter, nothing will be immediately broadcast. You’ll be in a pre-live state. Decide what content to share and in what order. Along the bottom of the screen, you can share your video and audio, share your screen, and mute incoming attendees.

    Once your content is ready to share along the bottom of the screen, add it to the screen on the left, in order of viewing. This is your queue – your “Pre-live” state. Then, click “Send now.”

    This content will now move to the right-hand screen, ready for broadcasting. Once you’re ready to broadcast, click “Start.” Your state will change from “Pre-live” to “Live.”

    Along the top right of the app will be a tools bar.

    Screenshot listing live events settings icons in Microsoft Teams. Beside the heart monitor icon is 'Monitor health and performance of network, devices, and media sharing'. Beside the notepad icon is 'Take meeting notes'. Beside the chatbox icon is 'Chat function'. Beside the two little people with a plus sign icon is 'Invite and show participants'. Beside the gear icon is 'Device settings'. Beside the small 'i' in a circle is 'Meeting details, including schedule, meeting link, and dial-in number'.

    Workspace #1: Departments

    Scenario: Most of your organization’s communication and collaboration occurs within its pre-existing departmental divisions.

    Conventional communication channels:

    • Oral communication: Employees work in proximity to each other and communicate in person, by phone, in department meetings
    • Email: Department-wide announcements
    • Memos: Typically posted/circulated in mailboxes

    Solution: Determine the best way to organize your organization’s departments in Teams based on its size and your requirements to keep information private between departments.

    Option A:

    • Create a team for the organization/division.
    • Create channels for each department. Remember that all members of a team can view all public channels created in that team and the default General channel.
    • Create private channels if you wish to have a channel that only select members of that team can see. Remember that private channels have some limitations in functionality.

    Option B:

    • Create a new team for each department.
    • Create channels within this team for projects or topics that are recurring workflows for the department members. Only department members can view the content of these channels.

    Option C:

    • Post departmental memos and announcements in the General channel.
    • Use “Meet now” in channels for ad hoc meetings. For regular department meetings, create a recurring Teams calendar event for the specific department channel (Option A) or the General channel (Option B). Remember that all members of a team can join a public channel meeting.

    Workspace #2: A cross-functional committee

    Scenario: Your organization has struck a committee composed of members from different departments. The rest of the organization should not have access to the work done in the committee.

    Purpose: To analyze a particular organizational challenge and produce a plan or report; to confidentially develop or carry out a series of processes that affect the whole organization.

    Jobs: Committee members must be able to:

    • Attend private meetings.
    • Share files confidentially.

    Solution:

    Ingredients:

    • Private team

    Construction:

    • Create a new private team for the cross-functional committee.
    • Add only committee members to the team.
    • Create channels based on the topics likely to be the focal point of the committee work.
    • Decide how you will use the mandatory General channel. If the committee is small and the work limited in scope, this channel may be the main communication space. If the committee is larger or the work more complex, use the General channel for announcements and move discussions to new topic-related channels.
    • Schedule recurring committee meetings in the Teams calendar. Add the relevant channel to the meeting invite to keep the meeting chat attached to this team and channel (as meeting organizer, put your name in the meeting invite notes, as the channel will show as the organizer in the Outlook invite).
    • Remember that all members of this team will have access to these meetings and be able to view that they are occurring.

    Workspace #3: An innovation day event

    Scenario: The organization holds a yearly innovation day event in which employees form small groups and work on a defined, short-term problem or project.

    Purpose: To develop innovative solutions and ideas.

    Jobs:

    • Convene small groups.
    • Work toward time-sensitive goals.
    • Communicate synchronously.
    • Share files.

    Solution:

    Ingredients:

    • Public team
    • Channel tabs
    • Whiteboard
    • Planner

    Construction:

    • Create a team for the innovation day event.
    • Add channels for each project working group.
    • Communicate to participants the schedule for the day and their assigned channel.
    • Use the General channel for announcements and instructions throughout the day. Ensure someone moderates the General channel for participants’ questions.
    • Pre-populate the channel tabs with files the participants need to work with. To add a scrum board, refer to M#4 (Morning stand-up/Scrum) in this slide deck.
    • For breakouts, instruct participants to use the “meet now” feature in their channel and how to use the Whiteboard during these meetings.
    • Arrange to have your IT admin archive the team after a certain point so the material is still viewable but not editable.

    Workspace #4: A non-work-related social event

    Scenario: Employees within the organization wish to organize social events around shared interests: board game clubs, book clubs, TV show discussion groups, trivia nights, etc.

    Purpose: To encourage cohesion among coworkers and boost morale.

    Jobs:

    • Schedule the event.
    • Invite participants.
    • Prepare the activity.
    • Host and moderate the discussion.

    Solution:

    Ingredients:

    • Public team
    • Private channels
    • Screen-sharing

    Construction:

    • Create a public team for the social event so that interested people can find and join it.
    • Example: Trivia Night
      • Schedule the event in the Teams calendar.
      • Publish the link to the Trivia Night team where other employees will see it.
      • Create private channels for each trivia team so they cannot see the other competitors’ discussions. Add yourself to each private channel so you can see their answers.
      • As the host, begin a meeting in the General channel. Pose the trivia questions live or present the questions on PowerPoint via screen-sharing.
      • Ask each team to post its answers to its private channel.
    • To avoid teams sprawl, ask your IT admin to set a deletion policy for the team, as long as this request does not contradict your organization’s policies on data retention. If the team becomes moribund, it can be set to auto-delete after a certain period of time.

    Workspace #5: A project team with a defined end time

    Scenario: Within a department/workplace team, employees are assigned to projects with defined end times, after which they will be assigned to a new project.

    Purpose: To complete project-based work that fulfills business needs.

    Jobs:

    • Oral communication with team members.
    • Synchronous and asynchronous work on project files.
    • The ability to attend scheduled meetings and ad hoc meetings.
    • The ability to access shared resources related to the project.

    Solution:

    If your working group already has its own team within Teams:

    • Create a new public or private channel for the project. Remember that some functionality is not available in private channels (such as Microsoft Planner).
    • Use the channel for the project team’s meetings (scheduled in Teams calendar or through Meet Now).
    • Add a tab that links to the team’s project folder in SharePoint.

    If your workplace team does not already have its own team in Teams:

    • Determine if there is a natural fit for this project as a new channel in an existing team. Remember that all team members will be able to see the channel if it is public and that all relevant project members need to belong to the Team to participate in the channel.
    • If necessary, create a new team for the project. Add the project members.
    • Create channels based on the type of work that comprises the project.
    • Use the channel for the project team’s meetings (scheduled in Teams calendar or through Meet Now)
    • Add a tab to link to the team’s project folder in SharePoint.

    Info-tech Best Practice

    Hide the channel after the project concludes to de-clutter your Teams user interface.

    Meeting #1: Job interview with external candidate

    Scenario: The organization must interview a slate of candidates to fill an open position.

    Purpose:

    • Select the most qualified candidate for the job.

    Jobs:

    • Create a meeting, ensuring the candidate and other attendees know when and where the meeting will happen.
    • Ensure the meeting is secure to protect confidential information.
    • Ensure the meeting is accessible, allowing the candidate to present themselves through audio and/or visual means.
    • Create a professional environment for the meeting to take place.
    • Engender a space for the candidate to share their CV, research, or other relevant file.
    • The interview must be transcribed and recorded.

    Solution:

    Ingredients:

    • Private Teams meeting
    • Screen-sharing
    • Microsoft Stream

    Construction:

    • Create a Teams meeting, inviting the candidate with their email, alongside other internal attendees. The Teams meeting invite will auto-generate a link to the meeting itself.
    • The host can control who joins the meeting through settings for the “lobby.”
    • Through the Teams meeting, the attendees will be able to use the voice and video chat functionality.
    • All attendees can opt to blur their backgrounds to maintain a professional online presence.
    • The candidate can share their screen, either specific applications or their whole desktop, during the Teams meeting.
    • A Teams meeting can be recorded and transcribed through Stream. After the meeting, the transcript can be searched, edited, and shared

    NB: The external candidate does not need the Teams application. Through the meeting invite, the external candidate will join via a web browser.

    Meeting #2: Quarterly board meeting

    Scenario: Every quarter, the organization holds its regular board meeting.

    Purpose: To discuss agenda items and determine the company’s future direction.

    Jobs:

    During meeting:
      • Attendance and minutes must be taken.
      • Votes must be recorded.
      • In-camera sessions must occur.
      • External experts must be included.
    After meeting:
    • Follow-up items must be assigned.
    • Reports must be submitted.

    Solution:

    Ingredients:

    • Teams calendar invite
    • Planner; Forms
    • Private channel
    • Microsoft Stream

    Construction:

    • Guest Invite: Invites can be sent to any non-domain-joined email address to join a private, invitation-only channel within the team controlled by the board chair.
    • SharePoint & Flow: Documents are emailed to the Team addresses, which kicks off an MS Flow routine to collect review notes.
    • Planner: Any board member can assign tasks to any employee.
    • Forms/Add-On: Chair puts down the form of the question and individual votes are tracked.
    • Teams cloud meeting recording: Recording available through Stream. Manual edits can be made to VTT caption file. Greater than acceptable transcription error rate.
    • Meeting Log: Real-time attendance is viewable but a point-in-time record needs admin access.

    NB: The external guests do not need the Teams application. Through the meeting invite, the guests will join via a web browser.

    Meeting #3: Weekly team meeting

    Scenario: A team meets for a weekly recurring meeting. The meeting is facilitated by the team lead (or manager) who addresses through agenda items and invites participation from the attendees.

    Purpose: The purpose of the meeting is to:

    • Share information verbally
    • Present content visually
    • Achieve consensus
    • Build team morale

    Jobs: The facilitator must:

    • Determine participants
    • Book room
    • Book meeting in calendar

    Solution:

    Ingredients:

    • Meeting Place: A channel in Microsoft Teams (must be public) where all members of the meeting make up the entirety of the audience.
    • Calendar Recurrence: A meeting is booked through Teams and appears in all participants’ Outlook calendar.
    • Collaboration Space: Participants join the meeting through video or audio and can share screens and contribute text, images, and links to the meeting chat.

    Construction:

    • Ensure your team already has a channel created for it. If not, create one in the appropriate team.
    • Create the meeting using the calendar view within Microsoft Teams:
      • Set the meeting’s name, attendees, time, and recurrence.
      • Add the team channel that serves as the most appropriate workplace for the meeting. (Any discussion in the meeting chat will be posted to this channel.)

    NB: Create the meeting in the Teams calendar, not Outlook, or you will not be able to add the Teams channel. As meeting organizer, put your name in the meeting invite notes, as the channel will show as the organizer in the Outlook invite.

    Meeting #4: Morning stand-up/scrum

    Scenario: Each morning, at 9am, members of the team meet online.

    Purpose: After some pleasantries, the team discusses what tasks they each plan to complete in the day.

    Jobs: The team leader (or scrum master) must:

    • Place all tasks on a scrum board, each represented by a sticky note denoting the task name and owner.
    • Move the sticky notes through the columns, adjusting assignments as needed.
    • Sort tasks into the following columns: “Not Started,” “In Progress,” and “Done.”

    Solution:

    Ingredients:

    • Meeting Place: A channel in Microsoft Teams (must be public) where all members of the meeting make up the entirety of the audience.
    • Scrum Board: A tab within that channel where a persistent scrum board has been created and is visible to all team members.

    Meeting Place Construction:

    • Create the meeting using the calendar view in Teams.
    • Set the meeting’s name, attendees, time, and work-week daily recurrence (see left).
    • Add the channel that is the most appropriate workplace for the meeting. Any meeting chat will be posted to this channel rather than a separate chat.

    Scrum Board Construction:

    • Add a tab to the channel using Microsoft Planner as the app. (You can use other task management apps such as Trello, but the identity integration of first-party Office 365 tools may be less hassle.)
    • Create a new (or import an existing) Plan to the channel. This will be used as the focal point.

    Meeting #5: Weekly team meeting

    Scenario: An audio-only conversation that could be a regularly scheduled event but is more often conducted on an ad-hoc basis.

    Purpose: To quickly share information, achieve consensus, or clarify misunderstandings.

    Jobs:

    • Dial recipient
    • See missed calls
    • Leave/check voicemail
    • Create speed-dial list
    • Conference call

    Solution:

    Ingredients:

    • Audio call begun through Teams chat.

    Construction:

    • Voice over IP calls between users in the same MS Teams tenant can begin in multiple ways:
      • A call can be initiated through any appearance of a user’s profile picture: hover over user’s profile photo in the Chat list and select the phone icon.
      • Enter your last chat with a user and click phone icon in upper-right corner.
      • Go to the Calls section and type the name in the “Make a call” text entry form.
    • Voicemail: Voicemail, missed calls, and call history are available in the Calls section.
    • Speed dial: Speed dial lists can be created in the Calls section.
    • Conference call: Other users can be added to an ongoing call.

    NB: Microsoft Teams can be configured to provide an organization’s telephony for external calls, but this requires an E5 license. Additional audio-conferencing licenses are required to call in to a Teams meeting over a phone.

    Bibliography 1/4

    Section 1: Teams for IT › Creation Process

    Overview: Creation process
    Assign admin roles
    Prepare the network
    Team creation
    Integrations with SharePoint Online
    Permissions

    Bibliography 2/4

    Section 1: Teams for IT › Creation Process (cont'd.)

    External and guest access
    Expiration and archiving
    Retention and data loss prevention
    Teams telephony

    Bibliography 3/4

    Section 1: Teams for IT › Teams Rollout

    From Skype to Teams
    From Slack to Teams
    Teams adoption

    Section 1: Teams for IT › Use Cases

    Bibliography 4/4

    Section 2: Teams for End Users › Teams, Channels, Chat

    Section 2: Teams for End Users › Meetings and Live Events

    Section 2: Teams for End Users › Use Cases

    Master Your Security Incident Response Communications Program

    • Buy Link or Shortcode: {j2store}321|cart{/j2store}
    • member rating overall impact: 8.0/10 Overall Impact
    • member rating average dollars saved: $2,339 Average $ Saved
    • member rating average days saved: 5 Average Days Saved
    • Parent Category Name: Threat Intelligence & Incident Response
    • Parent Category Link: /threat-intelligence-incident-response
    • When a significant security incident is discovered, usually very few details are known for certain. Nevertheless, the organization will need to say something to affected stakeholders.
    • Security incidents tend to be ongoing situations that last considerably longer than other types of crises, making communications a process rather than a one-time event.
    • Effective incident response communications require collaboration from: IT, Legal, PR, and HR – groups that often speak “different languages.”

    Our Advice

    Critical Insight

    • There’s no such thing as successful incident response communications; strive instead for effective communications. There will always be some fallout after a security incident, but it can be effectively mitigated through honesty, transparency, and accountability.
    • Effective external communications begin with effective internal communications. Security Incident Response Team members come from departments that don’t usually work closely with each other. This means they often have different ways of thinking and speaking about issues. Be sure they are familiar with each other before a crisis occurs.
    • You won’t save face by withholding embarrassing details. Lying only makes a bad situation worse, but coming clean and acknowledging shortcomings (and how you’ve fixed them) can go a long way towards restoring stakeholders’ trust.

    Impact and Result

    • Effective and efficient management of security incidents involves a formal process of preparation, detection, analysis, containment, eradication, recovery, and post-incident activities: communications must be integrated into each of these phases.
    • Understand that prior planning helps to take the guesswork out of incident response communications. By preparing for several different types of security incidents, the communications team will get used to working with each other, as well as learning what strategies are and are not effective. Remember, the communications team contains diverse members from various departments, and each may have different ideas about what information is important to release.

    Master Your Security Incident Response Communications Program Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should implement a security incident response communications plan, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Dive into communications planning

    This phase addresses the benefits and challenges of incident response communications and offers advice on how to assemble a communications team and develop a threat escalation protocol.

    • Master Your Security Incident Response Communications Program – Phase 1: Dive Into Communications Planning
    • Security Incident Management Plan

    2. Develop your communications plan

    This phase focuses on creating an internal and external communications plan, managing incident fallout, and conducting a post-incident review.

    • Master Your Security Incident Response Communications Program – Phase 2: Develop Your Communications Plan
    • Security Incident Response Interdepartmental Communications Template
    • Security Incident Communications Policy Template
    • Security Incident Communications Guidelines and Templates
    • Security Incident Metrics Tool
    • Tabletop Exercises Package
    [infographic]

    z-Series Modernization and Migration

    • Buy Link or Shortcode: {j2store}114|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Strategy and Organizational Design
    • Parent Category Link: /strategy-and-organizational-design

    Under the best of circumstances, mainframe systems are complex, expensive, and difficult to scale. In today’s world, applications written for mainframe legacy systems also present significant operational challenges to customers compounded by the dwindling pool of engineers who specialize in these outdated technologies. Many organizations want to migrate their legacy applications to the cloud but to do so they need to go through a lengthy migration process that is made more challenging by the complexity of mainframe applications.

    Our Advice

    Critical Insight

    The most common tactic is for the organization to better realize their z/Series options and adopt a strategy built on complexity and workload understanding. To make the evident, obvious, the options here for the non-commodity are not as broad as with commodity server platforms and the mainframe is arguably the most widely used and complex non-commodity platform on the market.

    Impact and Result

    This research will help you:

    • Evaluate the future viability of this platform.
    • Assess the fit and purpose, and determine TCO
    • Develop strategies for overcoming potential challenges.
    • Determine the future of this platform for your organization.

    z/Series Modernization and Migration Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. z/Series Modernization and Migration Guide – A brief deck that outlines key migration options and considerations for the z/Series platform.

    This blueprint will help you assess the fit, purpose, and price; develop strategies for overcoming potential challenges; and determine the future of z/Series for your organization.

    • z/Series Modernization and Migration Storyboard

    2. Scale Up vs. Scale Out TCO Tool – A tool that provides organizations with a framework for TCO.

    Use this tool to play with the pre-populated values or insert your own amounts to compare possible database decisions, and determine the TCO of each. Note that common assumptions can often be false; for example, open-source Cassandra running on many inexpensive commodity servers can actually have a higher TCO over six years than a Cassandra environment running on a larger single expensive piece of hardware. Therefore, calculating TCO is an essential part of the database decision process.

    • Scale Up vs. Scale Out TCO Tool
    [infographic]

    Further reading

    z/Series Modernization and Migration

    The biggest migration is yet to come.

    Executive Summary

    Info-Tech Insight

    “A number of market conditions have coalesced in a way that is increasingly driving existing mainframe customers to consider running their application workloads on alternative platforms. In 2020, the World Economic Forum noted that 42% of core skills required to perform existing jobs are expected to change by 2022, and that more than 1 billion workers need to be reskilled by 2030.” – Dale Vecchio

    Your Challenge

    It seems like anytime there’s a new CIO who is not from the mainframe world there is immediate pressure to get off this platform. However, just as there is a high financial commitment required to stay on System Z, moving off is risky and potentially more costly. You need to truly understand the scale and complexity ahead of the organization.

    Common Obstacles

    Under the best of circumstances, mainframe systems are complex, expensive, and difficult to scale. In today’s world, applications written for mainframe legacy systems also present significant operational challenges to customers compounded by the dwindling pool of engineers who specialize in these outdated technologies. Many organizations want to migrate their legacy applications to the cloud, but to do so they need to go through a lengthy migration process that is made more challenging by the complexity of mainframe applications.

    Info-Tech Approach

    The most common tactic is for the organization to better realize its z/Series options and adopt a strategy built on complexity and workload understanding. To make the evident, obvious: the options here for the non-commodity are not as broad as with commodity server platforms and the mainframe is arguably the most widely used and complex non-commodity platform on the market.

    Review

    We help IT leaders make the most of their z/Series environment

    Problem statement:

    The z/Series remains a vital platform for many businesses and continues to deliver exceptional reliability and performance and play a key role in the enterprise. With the limited and aging resources at hand, CIOs and the like must continually review and understand their migration path with the same regard as any other distributed system roadmap.

    This research is designed for:

    IT strategic direction decision makers.

    IT managers responsible for an existing z/Series platform.

    Organizations evaluating platforms for mission critical applications.

    This research will help you:

    1. Evaluate the future viability of this platform.
    2. Assess the fit and purpose, and determine TCO.
    3. Develop strategies for overcoming potential challenges.
    4. Determine the future of this platform for your organization.

    Analyst Perspective

    Good Luck.

    Darin Stahl.

    Modernize the mainframe … here we go again.

    Prior to 2020, most organizations were muddling around in “year eleven of the four-year plan” to exit the mainframe platform where a medium-term commitment to the platform existed. Since 2020, it appears the appetite for the mainframe platform changed. Again. Discussions mostly seem to be about what the options are beyond hardware outsourcing or re-platforming to “cloud” migration of workloads – mostly planning and strategy topics. A word of caution: it would appear unwise to stand in front of the exit door for fear of being trampled.

    Hardware expirations between now and 2025 are motivating hosting deployments. Others are in migration activities, and some have already decommissioned and migrated but now are trying to rehab the operations team now lacking direction and/or structure.

    There is little doubt that modernization and “digital transformation” trends will drive more exit traffic, so IT leaders who are still under pressure to get off the platform need to assess their options and decide. Being in a state of perpetually planning to get off the mainframe handcuffs your ability to invest in the mainframe, address deficiencies, and improve cost-effectiveness.

    Darin Stahl
    Principal Research Advisor, Infrastructure & Operations Research
    Info-Tech Research Group

    The mainframe “fidget spinner”

    Thinking of modernizing your mainframe can cause you angst so grab a fidget spinner and relax because we have you covered!

    External Business Pressures:

    • Digital transformation
    • Modernization programs
    • Compliance and regulations
    • TCO

    Internal Considerations:

    • Reinvest
    • Migrate to a new platform
    • Evaluate public and vendor cloud alternatives
    • Hosting versus infrastructure outsourcing

    Info-Tech Insight

    With multiple control points to be addressed, care must be taken to simplify your options while addressing all concerns to ease operational load.

    The analyst call review

    “Who has Darin talked with?” – Troy Cheeseman

    Dating back to 2011, Darin Stahl has been the primary z/Series subject matter expert within the Infrastructure & Operations Research team. Below represents the percentage of calls, per industry, where z/Series advisory has been provided by Darin*:

    37% - State Government

    19% - Insurance

    11% - Municipality

    8% - Federal Government

    8% - Financial Services

    5% - Higher Education

    3% - Retail

    3% - Hospitality/Resort

    3% - Logistics and Transportation

    3% - Utility

    Based on the Info-Tech call history, there is a consistent cross section of industry members who not only rely upon the mainframe but are also considering migration options.

    Note:

    Of course, this only represents industries who are Info-Tech members and who called for advisory services about the mainframe.

    There may well be more Info-Tech members with mainframes who have no topic to discuss with us about the mainframe specifically. Why do we mention this?

    We caution against suggesting things like, ”somewhat less than 50% of mainframes live in state data centers” or any other extrapolated inference from this data.

    Our viewpoint and discussion is based on the cases and the calls that we have taken over the years.

    *37+ enterprise calls were reviewed and sampled.

    Scale out versus scale up

    For most workloads “scale out" (e.g. virtualized cloud or IaaS ) is going to provide obvious and quantifiable benefits.

    However, with some workloads (extremely large analytics or batch processing ) a "scale up" approach is more optimal. But the scale up is really limited to very specific workloads. Despite some assumptions, the gains made when moving from scale up to scale out are not linear.

    Obviously, when you scale out from a performance perspective you experience a drop in what a single unit of compute can do. Additionally, there will be latency introduced in the form of network overhead, transactions, and replication into operations that were previously done just bypassing object references within a single frame.

    Some applications or use cases will have to be architected or written differently (thinking about the high-demand analytic workloads at large scale). Remember the “grid computing” craze that hit us during the early part of this century? It was advantageous for many to distribute work across a grid of computing devices for applications but the advantage gained was contingent on the workload able to be parsed out as work units and then pulled back together through the application.

    There can be some interesting and negative consequences for analytics or batch operations in a large scale as mentioned above. Bottom line, as experienced previously with Microfocus mainframe ports to x86, the batch operations simply take much longer to complete.

    Big Data Considerations*:

    • Value: Data has no inherent value until it’s used to solve a business problem.
    • Variety: The type of data being produced is increasingly diverse and ranges from email and social media to geo-spatial and photographic data. This data may be difficult to process using a structured data model.
    • Volume: The sheer size of the datasets is growing exponentially, often ranging from terabytes to petabytes. This is complicating traditional data management strategies.
    • Velocity: The increasing speed at which data is being collected and processed is also causing complications. Big data is often time sensitive and needs to be captured in real time as it is streaming into the enterprise.

    *Build a Strategy for Big Data Platforms

    Consider your resourcing

    Below is a summary of concerns regarding core mainframe skills:

    1. System Management (System Programmers): This is the most critical and hard-to-replace skill since it requires in-depth low-level knowledge of the mainframe (e.g. at the MVS level). These are skills that are generally not taught anymore, so there is a limited pool of experienced system programmers.
    2. Information Management System (IMS) Specialists: Requires a combination of mainframe knowledge and data analysis skills, which makes this a rare skill set. This is becoming more critical as business intelligence takes on an ever-increasing focus in most organizations.
    3. Application Development: The primary concern here is a shortage of developers skilled in older languages such as COBOL. It should be noted that this is an application issue; for example, this is not solved by migrating off mainframes.
    4. Mainframe Operators: This is an easier skill set to learn, and there are several courses and training programs available. An IT person new to mainframes could learn this position in about six weeks of on-the-job training.
    5. DB2 Administration: Advances in database technology have simplified administration (not just for DB2 but also other database products). As a result, as with mainframe operators, this is a skill set that can be learned in a short period of time on the job.

    The Challenge

    An aging workforce, specialized skills, and high salary expectations

    • Mainframe specialists, such as system programmers and IMS specialists, are typically over 50, have a unique skill set, and are tasked with running mission-critical systems.

    The In-House Solution:

    Build your mentorship program to create a viable succession plan

    • Get your money’s worth out of your experienced staff by having them train others.
    • Operator skills take about six weeks to learn. However, it takes about two years before a system programmer trainee can become fully independent. This is similar to the learning curve for other platforms; however, this is a more critical issue for mainframes since organizations have far fewer mainframe specialists to fall back on when senior staff retire or move on.

    Understand your options

    Migrate to another platform

    Use a hosting provider

    Outsource

    Re-platform (cloud/vendors)

    Reinvest

    There are several challenges to overcome in a migration project, from finding an appropriate alternative platform to rewriting legacy code. Many organizations have incurred huge costs in the attempt, only to be unsuccessful in the end, so make this decision carefully.

    Organizations often have highly sensitive data on their mainframes (e.g. financial data), so many of these organizations are reluctant to have this data live outside of their four walls. However, the convenience of using a hosting provider makes this an attractive option to consider.

    The most common tactic is for the organization to adopt some level of outsourcing for the non-commodity platform, retaining the application support/development in-house.

    A customer can “re-platform” the non-commodity workload into public cloud offerings or in a few offerings
    “re-host.”

    If you’re staying with the mainframe and keeping it in-house, it’s important to continue to invest in this platform, keep it current, and look for opportunities to optimize its value.

    Migrate

    Having perpetual plans to migrate handcuffs your ability to invest in your mainframe, extend its value, and improve cost effectiveness.

    If this sounds like your organization, it’s time to do the analysis so you can decide and get clarity on the future of the mainframe in your organization.

    1. Identify current performance, availability, and security requirements. Assess alternatives based on this criteria.
    2. Review and use Info-Tech’s Mainframe TCO Comparison Tool to compare mainframe costs to the potential alternative platform.
    3. Assess the business risks and benefits. Can the alternative deliver the same performance, reliability, and security? If not, what are the risks? What do you gain by migrating?
    4. If migration is still a go, evaluate the following:
    • Do you have the expertise or a reliable third party to perform the migration, including code rewrites?
    • How long will the migration take? Can the business function effectively during this transition period?
    • How much will the migration cost? Is the value you expect to gain worth the expense?

    *3 of the top 4 challenges related to shortfalls of alternative platforms

    The image contains a bar graph that demonstrates challenges related to shortfalls of alternative platforms.

    *Source: Maximize the Value of IBM Mainframes in My Business

    Hosting

    Using a hosting provider is typically more cost-effective than running your mainframe in-house.

    Potential for reduced costs

    • Hosting enables you to reduce or eliminate your mainframe staff.
    • Economies of scale enable hosting providers to reduce software licensing costs. They also have more buying power to negotiate better terms.
    • Power and cooling costs are also transferred to the hosting provider.

    Reliable infrastructure and experienced staff

    • A quality hosting provider will have 24/7 monitoring, full redundancy, and proven disaster recovery capabilities.
    • The hosting provider will also have a larger mainframe staff, so they don’t have the same risk of suddenly being without those advanced critical skills.

    So, what are the risks?

    • A transition to a hosting provider usually means eliminating or significantly reducing your in-house mainframe staff. With that loss of in-house expertise, it will be next to impossible to bring the mainframe back in-house, and you become highly dependent on your hosting provider.

    Outsourcing

    The most common tactic is for the organization to adopt some level of outsourcing for the non-commodity platform, retaining the application support/development in-house.

    The options here for the non-commodity (z/Series, IBM Power platforms, for example) are not as broad as with commodity server platforms. More confusingly, the term “outsourcing” for these can include:

    Traditional/Colocation – A customer transitions their hardware environment to a provider’s data center. The provider can then manage the hardware and “system.”

    Onsite Outsourcing – Here a provider will support the hardware/system environment at the client’s site. The provider may acquire the customer’s hardware and provide software licenses. This could also include hiring or “rebadging” staff supporting the platform. This type of arrangement is typically part of a larger services or application transformation. While low risk, it is not as cost-effective as other deployment models.

    Managed Hosting – A customer transitions their legacy application environment to an off-prem hosted multi-tenanted environment. It will provide the most cost savings following the transition, stabilization, and disposal of existing environment. Some providers will provide software licensing, and some will also support “Bring Your Own,” as permitted by IBM terms for example.

    Info-Tech Insight

    Technical debt for non-commodity platforms isn’t only hardware based. Moving an application written for the mainframe onto a “cheaper” hardware platform (or outsourced deployment) leaves the more critical problems and frequently introduces a raft of new ones.

    Re-platform – z/Series COBOL Cloud

    Re-platforming is not trivial.

    While the majority of the coded functionality (JCLs, programs, etc.) migrate easily, there will be a need to re-code or re-write objects – especially if any object, code, or location references are not exactly the same in the new environment.

    Micro Focus has solid experience in this but if consider it within the context of an 80/20 rule (the actual metrics might be much better than that), meaning that some level of rework would have to be accomplished as an overhead to the exercise.

    Build that thought into your thinking and business case.

    AWS Cloud

    • Astadia (an AWS Partner) is re-platforming mainframe workloads to AWS. With its approach you reuse the original application source code and data to AWS services. Consider reviewing Amazon’s “Migrating a Mainframe to AWS in 5 Steps.”

    Azure Cloud

    Micro Focus COBOL (Visual COBOL)

    • Micro Focus' Visual COBOL also supports running COBOL in Docker containers and managing and orchestrating the containers with Kubernetes. I personally cannot imagine what sort of drunken bender decision would lead me to move COBOL into Docker and then use Kubernetes to run in GCP but there you are...if that's your Jam you can do it.

    Re-platform – z/Series (Non-COBOL)

    But what if it's not COBOL?

    Yeah, a complication for this situation is the legacy code.

    While re-platforming/re-hosting non-COBOL code is not new, we have not had many member observations compared to the re-platforming/re-hosting of COBOL functionality initiatives.

    That being said, there are a couple of interesting opportunities to explore.

    NTT Data Services (GLOBAL)

    • Most intriguing is the re-hosting of a mainframe environment into AWS. Not sure if the AWS target supports NATURAL codebase; it does reference Adabas however (Re-Hosting Mainframe Applications to AWS with NTT DATA Services). Nevertheless, NTT has supported re-platforming and NATURAL codebase environments previously.

    ModernSystems (or ModSys) has relevant experience.

    • ModSys is the resulting entity following a merger between BluePhoenix and ATERAS a number of years ago. ATERAS is the entity I find references to within my “wayback machine” for member discussions. There are also a number of published case studies still searchable about ATERAS’ successful re-platforming engagements, including the California Public Employees Retirement System (CalPERS) most famously after the Accenture project to rewrite it failed.

    ATOS, as a hosting vendor mostly referenced by customers with global locations in a short-term transition posture, could be an option.

    Lastly, the other Managed Services vendors with NATURAL and Adabas capabilities:

    Reinvest

    By contrast, reducing the use of your mainframe makes it less cost-effective and more challenging to retain in-house expertise.

    • For organizations that have migrated applications off the mainframe (at least partly to reduce dependency on the platform), inevitably there remains a core set of mission critical applications that cannot be moved off for reasons described on the “Migrate” slide. This is when the mainframe becomes a costly burden:
      • TCO is relatively high due to low utilization.
      • In-house expertise declines as workload declines and current staffing allocations become harder to justify.
    • Organizations that are instead adding capacity and finding new ways to use this platform have lower cost concerns and resourcing challenges. The charts below illustrate this correlation. While some capacity growth is due to normal business growth, some is also due to new workloads, and it reflects an ongoing commitment to the platform.

    *92% of organizations that added capacity said TCO is lower than for commodity servers (compared to 50% of those who did not add capacity)

    *63% of organizations that added capacity said finding resources is not very difficult (compared to 42% of those who did not add capacity)

    The image contains a bar graph as described in the above text. The image contains a bar graph as described in the above text.

    *Maximize the Value of IBM Mainframes in My Business

    An important thought about data migration

    Mainframe data migrations – “VSAM, IMS, etc.”

    • While the application will be replaced and re-platformed, there is the historical VIN data remaining in the VSAM files and access via the application. The challenge is that a bulk conversion can add upfront costs and delay the re-platforming of the application functionality. Some shops will break the historical data migration into a couple of phases.
    • While there are technical solutions to accessing VSAM data stores, what I have observed with other members facing a similar scenario is a need to “shrink” the data store over time. The technical accesses to historical VSAM records would also have a lifespan, and rather than kicking the can down the road indefinitely, many have turned to a process-based solution allowing them to shrink the historical data store over time. I have observed three approaches to the handling or digitization of historical records like this:

    Temporary workaround. This would align with a technical solution allowing the VASM files to be accessed using platforms other than on mainframe hardware (Micro Focus or other file store trickery). This can be accomplished relatively quickly but does run the risk of technology obsolesce for the workaround at some point in the future.

    Bulk conversion. This method would involve the extract/transform/load of the historical records into the new application platform. Often the order of the conversion is completed on work newest to oldest (the idea is that the newest historical records would have the highest likelihood of an access need), but all files would be converted to the new application and the old data store destroyed.

    Forward convert, which would have files undergo the extract/transform/load conversion into the new application as they are accessed or reopened. This method would keep historical records indefinitely or until they are converted – or the legal retention schedule allows for their destruction (hopefully no file must be kept forever). This could be a cost-efficient approach since the historical files remaining on the VSAM platform would be shrunk over time based on demand from the district attorney process. The conversion process could be automated and scripted, with a QR step allowing for the records to be deleted from the old platform.

    Info-Tech Insight

    It is not usual for organizations to leverage options #2 and #3 above to move the functionality forward while containing the scope creep and costs for the data conversions.

    Enterprise class job scheduling

    Job scheduling or data center automation?

    • Enterprise class job scheduling solutions enable complex unattended batched programmatically conditioned task/job scheduling.
    • Data center automation (DCIM) software automates and orchestrates the processes and workflow for infrastructure operations including provisioning, configuring, patching of physical, virtual, and cloud servers, and monitoring of tasks involved in maintaining the operations of a data center or Infrastructure environment.
    • While there maybe some overlap and or confusion between data center automation and enterprise class job scheduling solutions, data center automation (DCIM) software solutions are least likely to have support for non-commodity server platforms and lack robust scheduling functionality.

    Note: Enterprise job scheduling is a topic with low member interest or demand. Since our published research is driven by members’ interest and needs, the lack of activity or member demand would obviously be a significant influence into our ability to aggregate shared member insight, trends, or best practices in our published agenda.

    Data Center Automation (DCIM) Software

    Orchestration/Provisioning Software

    Enterprise class job scheduling features

    The feature set for these tools is long and comprehensive. The feature list below is not exhaustive as specific tools may have additional product capabilities. At a minimum, the solutions offered by the vendors in the list below will have the following capabilities:

    • Automatic restart and recovery
    • File management
    • Integration with security systems such as AD
    • Operator alerts
    • Ability to control spooling devices
    • Cross-platform support
    • Cyclical scheduling
    • Deadline scheduling
    • Event-based scheduling / triggers
    • Inter-dependent jobs
    • External task monitoring (e.g. under other sub-systems)
    • Multiple calendars and time-zones
    • Scheduling of packaged applications (such as SAP, Oracle, JD Edwards)
    • The ability to schedule web applications (e.g. .net, java-based)
    • Workload analysis
    • Conditional dependencies
    • Critical process monitoring
    • Event-based automation (“self-healing” processes in response to common defined error conditions)
    • Graphical job stream/workflow visualization
    • Alerts (job failure notifications, task thresholds (too long, too quickly, missed windows, too short, etc.) via multiple channels
    • API’s supporting programmable scheduler needs
    • Virtualization support
    • Workload forecasting and workload planning
    • Logging and message data supporting auditing capabilities likely to be informed by or compliant with regulatory needs such as Sarbanes, Gramme-Leach
    • Historical reporting
    • Auditing reports and summaries

    Understand your vendors and tools

    List and compare the job scheduling features of each vendor.

    • This is not presented as an exhaustive list.
    • The list relies on observations aggregated from analyst engagements with Info-Tech Research Group members. Those member discussions tend to be heavily tilted toward solutions supporting non-commodity platforms.
    • Nothing is implied about a solution suitability or capability by the order of presentation or inclusion or absence in this list.

    ✓ Advanced Systems Concepts

    ✓ BMC

    ✓ Broadcom

    ✓ HCL

    ✓ Fortra

    ✓ Redwood

    ✓ SMA Technologies

    ✓ StoneBranch

    ✓ Tidal Software

    ✓ Vinzant Software

    Info-Tech Insight

    Creating vendor profiles will help quickly filter the solution providers that directly meet your z/Series needs.

    Advanced Systems Concepts

    ActiveBatch

    Workload Management:

    Summary

    Founded in 1981, ASCs ActiveBatch “provides a central automation hub for scheduling and monitoring so that business-critical systems, like CRM, ERP, Big Data, BI, ETL tools, work order management, project management, and consulting systems, work together seamlessly with minimal human intervention.”*

    URL

    advsyscon.com

    Coverage:

    Global

    Amazon EC2

    Hadoop Ecosystem

    IBM Cognos

    DataStage

    IBM PureData (Netezza)

    Informatica Cloud

    Microsoft Azure

    Microsoft Dynamics AX

    Microsoft SharePoint

    Microsoft Team Foundation Server

    Oracle EBS

    Oracle PeopleSoft

    SAP

    BusinessObjects

    ServiceNow

    Teradata

    VMware

    Windows

    Linux

    Unix

    IBM i

    *Advanced Systems Concepts, Inc.


    BMC

    Control-M

    Workload Management:

    Summary

    Founded in 1980, BMCs Control-M product “simplifies application and data workflow orchestration on premises or as a service. It makes it easy to build, define, schedule, manage, and monitor production workflows, ensuring visibility, reliability, and improving SLAs.”*

    URL

    bmc.com/it-solutions/control-m.html

    Coverage:

    Global

    AWS

    Azure

    Google Cloud Platform

    Cognos

    IBM InfoSphere

    DataStage

    SAP HANA

    Oracle EBS

    Oracle PeopleSoft

    BusinessObjects

    ServiceNow

    Teradata

    VMware

    Windows

    Linux

    Unix

    IBM i

    IBM z/OS

    zLinux

    *BMC

    Broadcom

    Atomic Automation

    Autosys Workload Automation

    Workload Management:

    Summary

    Broadcom offers Atomic Automation and Autosys Workload Automation which ”gives you the agility, speed and reliability required for effective digital business automation. From a single unified platform, Atomic centrally provides the orchestration and automation capabilities needed accelerate your digital transformation and support the growth of your company.”*

    URL

    broadcom.com/products/software/automation/automic-automation

    broadcom.com/products/software/automation/autosys

    Coverage:

    Global


    Windows

    MacOS

    Linux

    UNIX

    AWS

    Azure

    Google Cloud Platform

    VMware

    z/OS

    zLinux

    System i

    OpenVMS

    Banner

    Ecometry

    Hadoop

    Oracle EBS

    Oracle PeopleSoft

    SAP

    BusinessObjects

    ServiceNow

    Teradata

    VMware

    Windows

    Linux

    Unix

    IBM i

    *Broadcom

    HCL

    Workload Automation

    Workload Management:

    Summary

    “HCL Workload Automation streamlined modelling, advanced AI and open integration for observability. Accelerate the digital transformation of modern enterprises, ensuring business agility and resilience with our latest version of one stop automation platform. Orchestrate unattended and event-driven tasks for IT and business processes from legacy to cloud and kubernetes systems.”*

    URL

    hcltechsw.com/workload-automation

    Coverage:

    Global


    Windows

    MacOS

    Linux

    UNIX

    AWS

    Azure

    Google Cloud Platform

    VMware

    z/OS

    zLinux

    System i

    OpenVMS

    IBM SoftLayer

    IBM BigInsights

    IBM Cognos

    Hadoop

    Microsoft Dynamics 365

    Microsoft Dynamics AX

    Microsoft SQL Server

    Oracle E-Business Suite

    PeopleSoft

    SAP

    ServiceNow

    Apache Oozie

    Informatica PowerCenter

    IBM InfoSphere DataStage

    Salesforce

    BusinessObjects BI

    IBM Sterling Connect:Direct

    IBM WebSphere MQ

    IBM Cloudant

    Apache Spark

    *HCL Software

    Fortra

    JAMS Scheduler

    Workload Management:

    Summary

    Fortra’s “JAMS is a centralized workload automation and job scheduling solution that runs, monitors, and manages jobs and workflows that support critical business processes.

    JAMS reliably orchestrates the critical IT processes that run your business. Our comprehensive workload automation and job scheduling solution provides a single pane of glass to manage, execute, and monitor jobs—regardless of platforms or applications.”*

    URL

    jamsscheduler.com

    Coverage:

    Global


    OpenVMS

    OS/400

    Unix

    Windows

    z/OS

    SAP

    Oracle

    Microsoft

    Infor

    Workday

    AWS

    Azure

    Google Cloud Compute

    ServiceNow

    Salesforce

    Micro Focus

    Microsoft Dynamics 365

    Microsoft Dynamics AX

    Microsoft SQL Server

    MySQL

    NeoBatch

    Netezza

    Oracle PL/SQL

    Oracle E-Business Suite

    PeopleSoft

    SAP

    SAS

    Symitar

    *JAMS

    Redwood

    Redwood SaaS

    Workload Management:

    Summary

    Founded in 1993 and delivered as a SaaS solution, ”Redwood lets you orchestrate securely and reliably across any application, service or server, in the cloud or on-premises, all inside a single platform. Automation solutions are at the core of critical business operations such as forecasting, replenishment, reconciliation, financial close, order to cash, billing, reporting, and more. Enterprises in every industry — from manufacturing, utility, retail, and biotech to healthcare, banking, and aerospace.”*

    URL

    redwood.com

    Coverage:

    Global


    OpenVMS

    OS/400

    Unix

    Windows

    z/OS

    SAP

    Oracle

    Microsoft

    Infor

    Workday

    AWS

    Azure

    Google Cloud Compute

    ServiceNow

    Salesforce

    Github

    Office 365

    Slack

    Dropbox

    Tableau

    Informatica

    SAP BusinessObjects

    Cognos

    Microsoft Power BI

    Amazon QuickSight

    VMware

    Xen

    Kubernetes

    *Redwood

    Fortra

    Robot Scheduler

    Workload Management:

    Summary

    “Robot Schedule’s workload automation capabilities allow users to automate everything from simple jobs to complex, event-driven processes on multiple platforms and centralize management from your most reliable system: IBM i. Just create a calendar of when and how jobs should run, and the software will do the rest.”*

    URL

    fortra.com/products/job-scheduling-software-ibm-i

    Coverage:

    Global


    IBM i (System i, iSeries, AS/400)

    AIX/UNIX

    Linux

    Windows

    SQL/Server

    Domino

    JD Edwards EnterpriseOne

    SAP

    Automate Schedule (formerly Skybot Scheduler)

    *Fortra

    SMA Technologies

    OpCon

    Workload Management:

    Summary

    Founded in1980, SMA offers to “save time, reduce error, and free your IT staff to work on more strategic contributions with OpCon from SMA Technologies. OpCon offers powerful, easy-to-use workload automation and orchestration to eliminate manual tasks and manage workloads across business-critical operations. It's the perfect fit for financial institutions, insurance companies, and other transactional businesses.”*

    URL

    smatechnologies.com

    Coverage:

    Global

    Windows

    Linux

    Unix

    z/Series

    IBM i

    Unisys

    Oracle

    SAP

    Microsoft Dynamics AX

    Infor M3

    Sage

    Cegid

    Temenos

    FICS

    Microsoft Azure Data Management

    Microsoft Azure VM

    Amazon EC2/AWS

    Web Services RESTful

    Docker

    Google Cloud

    VMware

    ServiceNow

    Commvault

    Microsoft WSUS

    Microsoft Orchestrator

    Java

    JBoss

    Asysco AMT

    Tuxedo ART

    Nutanix

    Corelation

    Symitar

    Fiserv DNA

    Fiserv XP2

    *SMA Technologies

    StoneBranch

    Universal Automation Center (UAC)

    Workload Management:

    Summary

    Founded in 1999, ”the Stonebranch Universal Automation Center (UAC) is an enterprise-grade business automation solution that goes beyond traditional job scheduling. UAC's event-based workload automation solution is designed to automate and orchestrate system jobs and tasks across all mainframe, on-prem, and hybrid IT environments. IT operations teams gain complete visibility and advanced control with a single web-based controller, while removing the need to run individual job schedulers across platforms.”*

    URL

    stonebranch.com/it-automation-solutions/enterprise-job-scheduling

    Coverage:

    Global

    Windows

    Linux

    Unix

    z/Series

    Apache Kafka

    AWS

    Databricks

    Docker

    GitHub

    Google Cloud

    Informatica

    Jenkins

    Jscape

    Kubernetes

    Microsoft Azure

    Microsoft SQL

    Microsoft Teams

    PagerDuty

    PeopleSoft

    Petnaho

    RedHat Ansible

    Salesforce

    SAP

    ServiceNow

    Slack

    SMTP and IMAP

    Snowflake

    Tableau

    VMware

    *Stonebranch

    Tidal Software

    Workload Automation

    Workload Management:

    Summary

    Founded in 1979, Tidal’s Workload Automation will “simplify management and execution of end-to-end business processes with our unified automation platform. Orchestrate workflows whether they're running on-prem, in the cloud or hybrid environments.”*

    URL

    tidalsoftware.com

    Coverage:

    Global

    CentOS

    Linux

    Microsoft Windows Server

    Open VMS

    Oracle Cloud

    Oracle Enterprise Linux

    Red Hat Enterprise Server

    Suse Enterprise

    Tandem NSK

    Ubuntu

    UNIX

    HPUX (PA-RISC, Itanium)

    Solaris (Sparc, X86)

    AIX, iSeries

    z/Linux

    z/OS

    Amazon AWS

    Microsoft Azure

    Oracle OCI

    Google Cloud

    ServiceNow

    Kubernetes

    VMware

    Cisco UCS

    SAP R/3 & SAP S/4HANA

    Oracle E-Business

    Oracle ERP Cloud

    PeopleSoft

    JD Edwards

    Hadoop

    Oracle DB

    Microsoft SQL

    SAP BusinessObjects

    IBM Cognos

    FTP/FTPS/SFTP

    Informatica

    *Tidal

    Vinzant Software

    Global ECS

    Workload Management:

    Summary

    Founded in 1987, Global ECS can “simplify operations in all areas of production with the GECS automation framework. Use a single solution to schedule, coordinate and monitor file transfers, database operations, scripts, web services, executables and SAP jobs. Maximize efficiency for all operations across multiple business units intelligently and automatically.”*

    URL

    vinzantsoftware.com

    Coverage:

    Global

    Windows

    Linux

    Unix

    iSeries

    SAP R/3 & SAP S/4HANA

    Oracle, SQL/Server

    *Vizant Software

    Activity

    Scale Out or Scale Up

    Activities:

    1. Complete the Scale Up vs. Scale Out TCO Tool.
    2. Compare total lifecycle costs to determine TCO.

    This activity involves the following participants:

    IT strategic direction decision makers

    IT managers responsible for an existing z/Series platform

    Organizations evaluating platforms for mission critical applications

    Outcomes of this step:

    • Completed Scale Up vs. Scale Out TCO Tool

    Info-Tech Insight

    This checkpoint process creates transparency around agreement costs with the business and gives the business an opportunity to re-evaluate its requirements for a potentially leaner agreement.

    Scale out versus scale up activity

    The Scale Up vs. Scale Out TCO Tool provides organizations with a framework for estimating the costs associated with purchasing and licensing for a scale-up and scale-out environment over a multi-year period.

    Use this tool to:

    • Compare the pre-populated values.
    • Insert your own amounts to contrast possible database decisions and determine the TCO of each.
    The image contains screenshots of the Scale Up vs. Scale Out TCO Tool.

    Info-Tech Insight

    Watch out for inaccurate financial information. Ensure that the financials for cost match your maintenance and contract terms.

    Use the Scale Up vs. Scale Out TCO Tool to determine your TCO options.

    Related Info-Tech Research

    Effectively Acquire Infrastructure Services

    Acquiring a service is like buying an experience. Don’t confuse the simplicity of buying hardware with buying an experience.

    Outsource IT Infrastructure to Improve System Availability, Reliability, and Recovery

    There are very few IT infrastructure components you should be housing internally – outsource everything else.

    Build Your Infrastructure Roadmap

    Move beyond alignment: Put yourself in the driver’s seat for true business value.

    Define Your Cloud Vision

    Make the most of cloud for your organization.

    Document Your Cloud Strategy

    Drive consensus by outlining how your organization will use the cloud.

    Build a Strategy for Big Data Platforms

    Know where to start and where to focus attention in the implementation of a big data strategy.

    Create a Better RFP Process

    Improve your RFPs to gain leverage and get better results.

    Research Authors

    Darin Stahl.

    Darin Stahl, Principal Research Advisor, Info-Tech Research Group

    Darin is a Principal Research Advisor within the Infrastructure Practice, and leveraging 38+ years of experience, his areas of focus include: IT Operations Management, Service Desk, Infrastructure Outsourcing, Managed Services, Cloud Infrastructure, DRP/BCP, Printer Management, Managed Print Services, Application Performance Monitoring/ APM, Managed FTP, non-commodity servers (z/Series, mainframe, IBM i, AIX, Power PC).

    Troy Cheeseman.

    Troy Cheeseman, Practice Lead, Info-Tech Research Group

    Troy has over 25 years of IT management experience and has championed large enterprise-wide technology transformation programs, remote/home office collaboration and remote work strategies, BCP, IT DRP, IT Operations and expense management programs, international right placement initiatives, and large technology transformation initiatives (M&A). Additionally, he has deep experience working with IT solution providers and technology (cloud) start-ups.

    Bibliography

    “AWS Announces AWS Mainframe Modernization.” Business Wire, 30 Nov. 2021.
    de Valence, Phil. “Migrating a Mainframe to AWS in 5 Steps with Astadia?” AWS, 23 Mar. 2018.
    Graham, Nyela. “New study shows mainframes still popular despite the rise of cloud—though times are changing…fast?” WatersTechnology, 12 Sept. 2022.
    “Legacy applications can be revitalized with API.” MuleSoft, 2022.
    Vecchio, Dale. “The Benefits of Running Mainframe Applications on LzLabs Software Defined Mainframe® & Microsoft Azure.” LzLabs Sites, Mar. 2021.

    Determine the Future of Microsoft Project in Your Organization

    • Buy Link or Shortcode: {j2store}357|cart{/j2store}
    • member rating overall impact: 10.0/10 Overall Impact
    • member rating average dollars saved: $125,999 Average $ Saved
    • member rating average days saved: 50 Average Days Saved
    • Parent Category Name: Project Management Office
    • Parent Category Link: /project-management-office
    • You use Microsoft tools to manage your work, projects, and/or project portfolio.
    • Its latest offering, Project for the web, is new and you’re not sure what to make of it. Microsoft says it will soon replace Microsoft Project and Project Online, but the new software doesn’t seem to do what the old software did.
    • The organization has adopted M365 for collaboration and work management. Meetings happen on Teams, projects are scoped a bit with Planner, and the operations group uses Azure Boards to keep track of what they need to get done.
    • Despite your reservations about the new project management software, Microsoft software has become even more ubiquitous.

    Our Advice

    Critical Insight

    • The various MS Project offerings (but most notably the latest, Project for the web) hold the promise of integrating with the rest of M365 into a unified work management solution. However, out of the box, Project for the web and the various platforms within M365 are all disparate utilities that need to be pieced together in a purpose-built manner to make use of them for holistic work management purposes. If you’re looking for a cohesive product out of the box, look elsewhere. If you’re looking to assemble a wide array of work, project, and portfolio management functions across different functions and departments, you may have found what you seek.
    • Rather than choosing tools based on your gaps, assess your current maturity level so that you optimize your investment in the Microsoft landscape.

    Impact and Result

    Follow Info-Tech’s path in this blueprint to:

    • Perform a tool audit to trim your work management tool landscape.
    • Navigate the MS Project and M365 licensing landscape.
    • Make sense of what to do with Project for the web and take the right approach to rolling it out (i.e. DIY or MS Gold Partner driven) based upon your needs.
    • Create an action plan to inform next steps.

    After following the program in this blueprint, you will be prepared to advise the organization on how to best leverage the rapidly shifting work management options within M365 and the place of MS Project within it.

    Determine the Future of Microsoft Project in Your Organization Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should make sense of the MS Project and M365 landscapes, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Determine your tool needs

    Assess your work management tool landscape, current state maturity, and licensing needs to inform a purpose-built work management action plan.

    • M365 Task Management Tool Guide
    • M365 Project Management Tool Guide
    • M365 Project Portfolio Management Tool Guide
    • Tool Audit Workbook
    • Force Field Analysis Tool
    • Microsoft Project & M365 Licensing Tool
    • Project Portfolio Management Maturity Assessment Workbook (With Tool Analysis)
    • Project Management Maturity Assessment Workbook (With Tool Analysis)

    2. Weigh your MS Project implementation options

    Get familiar with Project for the web’s extensibility as well as the MS Gold Partner ecosystem as you contemplate the best implementation approach(s) for your organization.

    • None
    • None

    3. Finalize your implementation approach

    Prepare a boardroom-ready presentation that will help you communicate your MS Project and M365 action plan to PMO and organizational stakeholders.

    • Microsoft Project & M365 Action Plan Template

    Infographic

    Workshop: Determine the Future of Microsoft Project in Your Organization

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Assess Driving Forces and Risks

    The Purpose

    Assess the goals and needs as well as the risks and constraints of a work management optimization.

    Take stock of your organization’s current work management tool landscape.

    Key Benefits Achieved

    Clear goals and alignment across workshop participants as well as an understanding of the risks and constraints that will need to be mitigated to succeed.

    Current-state insight into the organization’s work management tool landscape.

    Activities

    1.1 Review the business context.

    1.2 Explore the M365 work management landscape.

    1.3 Identify driving forces for change.

    1.4 Analyze potential risks.

    1.5 Perform current-state analysis on work management tools.

    Outputs

    Business context

    Current-state understanding of the task, project, and portfolio management options in M365 and how they align with the organization’s ways of working

    Goals and needs analysis

    Risks and constraints analysis

    Work management tool overview

    2 Determine Tool Needs and Process Maturity

    The Purpose

    Determine your organization’s work management tool needs as well as its current level of project management and project portfolio management process maturity.

    Key Benefits Achieved

    An understanding of your tooling needs and your current levels of process maturity.

    Activities

    2.1 Review tool audit dashboard and conduct the final audit.

    2.2 Identify current Microsoft licensing.

    2.3 Assess current-state maturity for project management.

    2.4 Define target state for project management.

    2.5 Assess current-state maturity for project portfolio management.

    2.6 Define target state for project portfolio management.

    Outputs

    Tool audit

    An understanding of licensing options and what’s needed to optimize MS Project options

    Project management current-state analysis

    Project management gap analysis

    Project portfolio management current-state analysis

    Project portfolio management gap analysis

    3 Weigh Your Implementation Options

    The Purpose

    Take stock of your implementation options for Microsoft old project tech and new project tech.

    Key Benefits Achieved

    An optimized implementation approach based upon your organization’s current state and needs.

    Activities

    3.1 Prepare a needs assessment for Microsoft 365 and Project Plan licenses.

    3.2 Review the business case for Microsoft licensing.

    3.3 Get familiar with Project for the web.

    3.4 Assess the MS Gold Partner Community.

    3.5 Conduct a feasibility test for PFTW.

    Outputs

    M365 and Project Plan needs assessment

    Business case for additional M365 and MS Project licensing

    An understand of Project for the web and how to extend it

    MS Gold Partner outreach plan

    A go/no-go decision for extending Project for the web on your own

    4 Finalize Implementation Approach

    The Purpose

    Determine the best implementation approach for your organization and prepare an action plan.

    Key Benefits Achieved

    A purpose-built implementation approach to help communicate recommendations and needs to key stakeholders.

    Activities

    4.1 Decide on the implementation approach.

    4.2 Identify the audience for your proposal.

    4.3 Determine timeline and assign accountabilities.

    4.4 Develop executive summary presentation.

    Outputs

    An implementation plan

    Stakeholder analysis

    A communication plan

    Initial executive presentation

    5 Next Steps and Wrap-Up (offsite)

    The Purpose

    Finalize your M365 and MS Project work management recommendations and get ready to communicate them to key stakeholders.

    Key Benefits Achieved

    Time saved in developing and communicating an action plan.

    Stakeholder buy-in.

    Activities

    5.1 Complete in-progress deliverables from previous four days.

    5.2 Set up review time for workshop deliverables and to discuss next steps.

    Outputs

    Finalized executive presentation

    A gameplan to communicate your recommendations to key stakeholders as well as a roadmap for future optimization

    Further reading

    Determine the Future of Microsoft Project in Your Organization

    View your task management, project management, and project portfolio management options through the lens of M365.

    EXECUTIVE BRIEF

    Analyst Perspective

    Microsoft Project is an enigma

    Microsoft Project has dominated its market since being introduced in the 1980s, yet the level of adoption and usage per license is incredibly low.

    The software is ubiquitous, mostly considered to represent its category for “Project Management.” Yet, the software is conflated with its “Portfolio Management” offerings as organizations make platform decisions with Microsoft Project as the incorrectly identified incumbent.

    And incredibly, Microsoft has dominated the next era of productivity software with the “365” offerings. Yet, it froze the “Project” family of offerings and introduced the not-yet-functional “Project for the web.”

    Having a difficult time understanding what to do with, and about, Microsoft Project? You’re hardly alone. It’s not simply a question of tolerating, embracing, or rejecting the product: many who choose a competitor find they’re still paying for Microsoft Project-related licensing for years to come.

    If you’re in the Microsoft 365 ecosystem, use this research to understand your rapidly shifting landscape of options.

    (Barry Cousins, Project Portfolio Management Practice Lead, Info-Tech Research Group)

    Executive Summary

    Your Challenge

    You use Microsoft (MS) tools to manage your work, projects, and/or project portfolio.

    Their latest offering, Project for the web, is new and you’re not sure what to make of it. Microsoft says it will soon replace Microsoft Project and Project Online, but the new software doesn’t seem to do what the old software did.

    The organization has adopted M365 for collaboration and work management. Meetings happen on Teams, projects are scoped a bit with Planner, and the operations group uses Azure Boards to keep track of what they need to get done.

    Despite your reservations about the new project management software, Microsoft software has become even more ubiquitous.

    Common Obstacles

    M365 provides the basic components for managing tasks, projects, and project portfolios, but there is no instruction manual for making those parts work together.

    M365 isn’t the only set of tools at play. Business units and teams across the organization have procured other non-Microsoft tools for work management without involving IT.

    Microsoft’s latest project offering, Project for the web, is still evolving and you’re never sure if it is stable or ready for prime time. The missing function seems to involve the more sophisticated project planning disciplines, which are still important to larger, longer, and costlier projects.

    Common Obstacles

    Follow Info-Tech’s path in this blueprint to:

    • Perform a tool audit to trim your work management tool landscape.
    • Navigate the MS Project and M365 licensing landscape.
    • Make sense of what to do with Project for the web and take the right approach to rolling it out (i.e. DIY or MS Gold Partner driven) for your needs.
    • Create an action plan to inform next steps.

    After following the program in this blueprint, you will be prepared to advise the organization on how to best leverage the rapidly shifting work management options within M365 and the place of MS Project within it.

    M365 and, within it, O365 are taking over

    Accelerated partly by the pandemic and the move to remote work, Microsoft’s market share in the work productivity space has grown exponentially in the last two years.

    70% of Fortune 500 companies purchased 365 from Sept. 2019 to Sept. 2020. (Thexyz blog, 2020)

    In its FY21 Q2 report, Microsoft reported 47.5 million M365 consumer subscribers – an 11.2% increase from its FY20 Q4 reporting. (Office 365 for IT Pros, 2021)

    As of September 2020, there were 258,000,000 licensed O365 users. (Thexyz blog, 2020)

    In this blueprint, we’ll look at what the what the phenomenal growth of M365 means for PMOs and project portfolio practitioners who identify as Microsoft shops

    The market share of M365 warrants a fresh look at Microsoft’s suite of project offerings

    For many PMO and project portfolio practitioners, the footprint of M365 in their organizations’ work management cultures is forcing a renewed look at Microsoft’s suite of project offerings.

    The complicating factor is this renewed look comes at a transitional time in Microsoft’s suite of project and portfolio offerings.

    • The market dominance of MS Project Server and Project Online are wanning, with Microsoft promising the end-of-life for Online sometime in the coming years.
    • Project Online’s replacement, Project for the web, is a viable task management and lightweight project management tool, but its viability as a replacement for the rigor of Project Online is at present largely a question mark.
    • Related to the uncertainty and promise around Project for the web, the Dataverse and the Power Platform offer a glimpse into a democratized future of work management tools but anything specific about that future has yet to solidify.

    Microsoft Project has 66% market share in the project management tool space. (Celoxis, 2018)

    A copy of MS project is sold or licensed every 20 seconds. (Integent, 2013)

    MS Project is evolving to meet new work management realities

    It also evolved to not meet the old project management realities.

    • The lines between traditional project management and operational task management solutions are blurring as organizations struggle to keep up with demands.
    • To make the software easier to use, modern work management doesn’t involve the complexities from days past. You won’t find anywhere to introduce complex predecessor-successor relationships, unbalanced assignments with front-loading or back-loading, early-start/late-finish, critical path, etc.
    • “Work management” is among the latest buzzwords in IT consulting. With Project for the web (PFTW), Azure Boards, and Planner, Microsoft is attempting to compete with lighter and better-adopted tools like Trello, Basecamp, Asana, Wrike, and Monday.com.
    • Buyers of project and work management software have struggled to understand how PFTW will still be usable if it gets the missing project management function from MS Project.

    Info-Tech Insight

    Beware of the Software Granularity Paradox.

    Common opinion 1: “Plans and estimates that are granular enough to be believable are too detailed to manage and maintain.”

    Common opinion 2: “Plans simple enough to publish aren’t detailed enough to produce believable estimates.”

    In other words, software simple enough to get widely adopted doesn’t produce believable plans. Software that can produce believable plans is too complex to use at scale.

    A viable task and project management option must walk the line between these dichotomies.

    M365 gives you the pieces, but it’s on PMO users to piece them together in a viable way

    With the new MS Project and M365, it’s on PMOs to avoid the granularity paradox and produce a functioning solution that fits with the organization’s ways of working.

    Common perception still sees Microsoft Project as a rich software tool. Thus, when we consider the next generation of Microsoft Project, it’s easy to expect a newer and friendlier version of what we knew before.

    In truth, the new solution is a collection of partially integrated but largely disparate tools that each satisfy a portion of the market’s needs. While it looks like a rich collection of function when viewed through high-level requirements, users will find:

    • Overlaps, where multiple tools satisfy the same functional requirement (e.g. “assign a task”)
    • Gaps, where a tool doesn’t quite do enough and you’re forced to incorporate another tool (e.g. reverting back to Microsoft Project for advanced resource planning)
    • Islands, where tools don’t fluently talk to each other (e.g. Planner data integrated in real-time with portfolio data, which requires clunky, unstable, decentralized end-user integrations with Microsoft Power Automate)
    A colourful arrangement of Microsoft programs arranged around a pile of puzzle pieces.

    Info-Tech's approach

    Use our framework to best leverage the right MS Project offerings and M365 components for your organization’s work management needs.

    The Info-Tech difference:

    1. A simple to follow framework to help you make sense of a chaotic landscape.
    2. Practical and tactical tools that will help you save time.
    3. Leverage industry best practices and practitioner-based insights.
    An Info-Tech framework titled 'Determine the Future of Microsoft Project in Your Organization, subtitle 'View your task, project, and portfolio management options through the lens of Microsoft 365'. There are four main sections titled 'Background', 'Approaches', 'Deployments', and 'Portfolio Outcomes'. In '1) Background' are 'Analyze Content', 'Assess Constraints', and 'Determine Goals and Needs'. In '2) Approaches' are 'DIY: Are you ready to do it yourself?' 'Info-Tech: Can our analysts help?', and 'MS Gold Partner: Are you better off with a third party?'. In '3) Deployments' are five sections: 'Personal Task Management', Barriers to Portfolio Outcomes: Isolated to One Person. 'Team Task Management', Barriers to Portfolio Outcomes: Isolated to One Team. 'Project Portfolio Management', Barriers to Portfolio Outcomes: Isolated to One Project. 'Project Management', Barriers to Portfolio Outcomes: Functionally Incomplete. 'Enterprise Project and Portfolio Management', Barriers to Portfolio Outcomes: Underadopted. In '4) Portfolio Outcomes' are 'Informed Steering Committee', 'Increased Project Throughput', 'Improved Portfolio Responsiveness', 'Optimized Resource Utilization', and 'Reduced Monetary Waste'.

    Determine the Future of Microsoft Project in Your Organization

    View your task, project, and portfolio management options through the lens of Microsoft 365.

    1. Background

    • Analyze Content
    • Assess Constraints
    • Determine Goals and Needs

    2. Approaches

    • DIY – Are you ready to do it yourself?
    • Info-Tech – Can our analysts help?
    • MS Gold Partner – Are you better off with a third party?

    3. Deployments

      Task Management

    • Personal Task Management
      • Who does it? Knowledge workers
      • What is it? To-do lists
      • Common Approaches
        • Paper list and sticky notes
        • Light task tools
      • Applications
        • Planner
        • To Do
      • Level of Rigor 1/5
      • Barriers to Portfolio Outcomes: Isolated to One Person
    • Team Task Management
      • Who does it? Groups of knowledge workers
      • What is it? Collaborative to-do lists
      • Common Approaches
        • Kanban boards
        • Spreadsheets
        • Light task tools
      • Applications
        • Planner
        • Azure Boards
        • Teams
      • Level of Rigor 2/5
      • Barriers to Portfolio Outcomes: Isolated to One Team
    • Project Management

    • Project Portfolio Management
      • Who does it? PMO Directors, Portfolio Managers
      • What is it?
        • Centralized list of projects
        • Request and intake handling
        • Aggregating reporting
      • Common Approaches
        • Spreadsheets
        • PPM software
        • Roadmaps
      • Applications
        • Project for the Web
        • Power Platform
      • Level of Rigor 3/5
      • Barriers to Portfolio Outcomes: Isolated to One Project
    • Project Management
      • Who does it? Project Managers
      • What is it? Deterministic scheduling of related tasks
      • Common Approaches
        • Spreadsheets
        • Lists
        • PM software
        • PPM software
      • Applications
        • Project Desktop Client
      • Level of Rigor 4/5
      • Barriers to Portfolio Outcomes: Functionally Incomplete
    • Enterprise Project and Portfolio Management

    • Enterprise Project and Portfolio Management
      • Who does it? PMO and ePMO Directors, Portfolio Managers, Project Managers
      • What is it?
        • Centralized request and intake handling
        • Resource capacity management
        • Deterministic scheduling of related tasks
      • Common Approaches
        • PPM software
      • Applications
        • Project Online
        • Project Desktop Client
        • Project Server
      • Level of Rigor 5/5
      • Barriers to Portfolio Outcomes: Underadopted

    4. Portfolio Outcomes

    • Informed Steering Committee
    • Increased Project Throughput
    • Improved Portfolio Responsiveness
    • Optimized Resource Utilization
    • Reduced Monetary Waste

    Info-Tech's methodology for Determine the Future of MS Project for Your Organization

    1. Determine Your Tool Needs

    2. Weigh Your MS Project Implementation Options

    3. Finalize Your Implementation Approach

    Phase Steps

    1. Survey the M365 Work Management Tools
    2. Perform a Process Maturity Assessment to Help Inform Your M365 Starting Point
    3. Consider the Right MS Project Licenses for Your Stakeholders
    1. Get Familiar With Extending Project for the Web Using Power Apps
    2. Assess the MS Gold Partner Community
    1. Prepare an Action Plan

    Phase Outcomes

    1. Work Management Tool Audit
    2. MS Project and Power Platform Licensing Needs
    3. Project Management and Project Portfolio Management Maturity Assessment
    1. Project for the Web Readiness Assessment
    2. MS Gold Partner Outreach Plan
    1. MS Project and M365 Action Plan Presentation

    Insight Summary

    Overarching blueprint insight: Microsoft Parts Sold Separately. Assembly required.

    The various MS Project offerings (but most notably the latest, Project for the web) hold the promise of integrating with the rest of M365 into a unified work management solution. However, out of the box, Project for the web and the various platforms within M365 are all disparate utilities that need to be pieced together in a purpose-built manner to make use of them for holistic work management purposes.

    If you’re looking for a cohesive product out of the box, look elsewhere. If you’re looking to assemble a wide array of work, project, and portfolio management functions across different functions and departments, you may have found what you seek

    Phase 1 insight: Align your tool choice to your process maturity level.

    Rather than choosing tools based on your gaps, make sure to assess your current maturity level so that you optimize your investment in the Microsoft landscape.

    Phase 2 insight: Weigh your options before jumping into Microsoft’s new tech.

    Microsoft’s new Project plans (P1, P3, and P5) suggest there is a meaningful connection out of the box between its old tech (Project desktop, Project Server, and Project Online) and its new tech (Project for the web).

    However, the offerings are not always interoperable.

    Phase 3 insight: Keep the iterations small as you move ahead with trials and implementations.

    Organizations are changing as fast as the software we use to run them.

    If you’re implementing parts of this platform, keep the changes small as you monitor the vendors for new software versions and integrations.

    Blueprint deliverables

    Each step of this blueprint is accompanied by supporting deliverables to help you accomplish your goals:

    Key deliverable: Microsoft Project & M365 Action Plan Template

    The Action Plan will help culminate and present:

    • Context and Constraints
    • DIY Implementation Approach
    Or
    • MS Partner Implementation Approach
    • Future-State Vision and Goals
    Samples of Info-Tech's key deliverable 'Microsoft Project and M365 Action Plan Template'.

    Tool Audit Workbook

    Sample of Info-Tech deliverable 'Tool Audit Workbook'.

    Assess your organization's current work management tool landscape and determine what tools drive value for individual users and teams and which ones can be rationalized.

    Force Field Analysis

    Sample of Info-Tech deliverable 'Force Field Analysis'.

    Document the driving and resisting forces for making a change to your work management tools.

    Maturity Assessments

    Sample of Info-Tech deliverable 'Maturity Assessments'.

    Use these assessments to identify gaps in project management and project portfolio management processes. The results will help guide process improvement efforts and measure success and progress.

    Microsoft Project & M365 Licensing Tool

    Sample of Info-Tech deliverable 'Microsoft Project and M365 Licensing Tool'.

    Determine the best licensing options and approaches for your implementation of Microsoft Project.

    Curate your work management tools to harness valuable portfolio outcomes

    • Increase Project Throughput

      Do more projects by ensuring the right projects and the right amount of projects are approved and executed.
    • Support an Informed Steering Committee

      Easily compare progress of projects across the portfolio and enable the leadership team to make decisions.
    • Improve portfolio responsiveness

      Make the portfolio responsive to executive steering when new projects and changing priorities need rapid action.
    • Optimize Resource Utilization

      Assign the right resources to approved projects and minimize the chronic over-allocation of resources that leads to burnout.
    • Reduce Monetary Waste

      Terminate low-value projects early and avoid sinking additional funds into unsuccessful ventures.

    Info-Tech offers various levels of support to best suit your needs

    DIY Toolkit

    Guided Implementation

    Workshop

    Consulting

    "Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful." "Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track." "We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place." "Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project."

    Diagnostics and consistent frameworks used throughout all four options

    Guided Implementation

    What does a typical GI on this topic look like?

    A Guided Implementation (GI) is a series of calls with an Info-Tech analyst to help implement our best practices in your organization.

    A typical GI is between 6 to 8 calls over the course of 3 to 4 months.

      Introduction

    • Call #1: Scope requirements, objectives, and your specific challenges.
    • Phase 1

    • Call #2: Explore the M365 work management landscape.
    • Call #3: Discuss Microsoft Project Plans and their capabilities.
    • Call #4: Assess current-state maturity.
    • Phase 2

    • Call #5: Get familiar with extending Project for the web using Power Apps.
    • Call #6: Assess the MS Gold Partner Community.
    • Phase 3

    • Call #7: Determine approach and deployment.
    • Call #8: Discuss action plan.

    Workshop Overview

    Contact your account representative for more information.
    workshops@infotech.com 1-888-670-8889

    Day 1
    Assess Driving Forces and Risks

    Day 2
    Determine Tool Needs and Process Maturity

    Day 3
    Weigh Your Implementation Options

    Day 4
    Finalize Implementation Approach

    Day 5
    Next Steps and Wrap-Up (offsite)

    Activities

    • 1.1 Review the business context.
    • 1.2 Explore the M365 work management landscape.
    • 1.3 Identify driving forces for change.
    • 1.4 Analyze potential risks.
    • 1.5 Perform current-state analysis on work management tools.
    • 2.1 Review tool audit dashboard and conduct the final audit.
    • 2.2 Identify current Microsoft licensing.
    • 2.3 Assess current-state maturity for project management.
    • 2.4 Define target state for project management.
    • 2.5 Assess current-state maturity for project portfolio management.
    • 2.6 Define target state for project portfolio management.
    • 3.1 Prepare a needs assessment for Microsoft 365 and Project Plan licenses.
    • 3.2 Review the business case for Microsoft licensing.
    • 3.3 Get familiar with Project for the web.
    • 3.4 Assess the MS Gold Partner Community.
    • 3.5 Conduct a feasibility test for PFTW.
    • 4.1 Decide on the implementation approach.
    • 4.2 Identify the audience for your proposal.
    • 4.3 Determine timeline and assign accountabilities.
    • 4.4 Develop executive summary presentation.
    • 5.1 Complete in-progress deliverables from previous four days.
    • 5.2 Set up review time for workshop deliverables and to discuss next steps.

    Deliverables

    1. Force Field Analysis
    2. Tool Audit Workbook
    1. Tool Audit Workbook
    2. Project Management Maturity Assessment
    3. Portfolio Management Maturity Assessment
    1. Microsoft Project and M365 Licensing Tool
    1. Microsoft Project & M365 Action Plan
    1. Microsoft Project & M365 Action Plan

    Determine the Future of Microsoft Project for Your Organization

    Phase 1: Determine Your Tool Needs

    Phase 1: Determine Your Tool Needs

    Phase 2: Weigh Your Implementation Options Phase 3: Finalize Your Implementation Approach
    • Step 1.1: Survey the M365 work management landscape
    • Step 1.2: Explore the Microsoft Project Plans and their capabilities
    • Step 1.3: Assess the maturity of your current PM & PPM capabilities
    • Step 2.1: Get familiar with extending Project for the web using Power Apps
    • Step 2.2: Assess the MS Gold Partner Community
    • Step 3.1: Prepare an action plan

    Phase Outcomes

    • Tool Audit
    • Microsoft Project Licensing Analysis
    • Project Management Maturity Assessment
    • Project Portfolio Management Maturity Assessments

    Step 1.1

    Survey the M365 Work Management Landscape

    Activities

    • 1.1.1 Distinguish between task, project, and portfolio capabilities
    • 1.1.2 Review Microsoft’s offering for task, project, and portfolio management needs
    • 1.1.4 Assess your organizational context and constraints
    • 1.1.3 Explore typical deployment options

    This step will walk you through the following activities:

    • Assessing your organization’s context for project and project portfolio management
    • Documenting the organization’s constraints
    • Establishing the organization’s goals and needs

    This step involves the following participants:

    • PMO Director
    • Resource Managers
    • Project Managers
    • Knowledge Workers

    Outcomes of Step

    • Knowledge of the Microsoft ecosystem as it relates to task, project, and portfolio management
    • Current organizational context and constraints

    Don’t underestimate the value of interoperability

    The whole Microsoft suite is worth more than the sum of its parts … if you know how to put it together.

    38% of the worldwide office suite market belongs to Microsoft. (Source: Statistica, 2021)

    1 in 3 small to mid-sized organizations moving to Microsoft Project say they are doing so because it integrates well with Office 365. (Source: CBT Nuggets, 2018)

    There’s a gravity to the Microsoft ecosystem.

    And while there is no argument that there are standalone task management tools, project management tools, or portfolio management tools that are likely more robust, feature-rich, and easier to adopt, it’s rare that you find an ecosystem that can do it all, to an acceptable level.

    That is the value proposition of Microsoft: the ubiquity, familiarity, and versatility. It’s the Swiss army knife of software products.

    The work management landscape is evolving

    With M365, Microsoft is angling to become the industry leader, and your organization’s hub, for work management.

    Workers lose up to 40% of their time multi-tasking and switching between applications. (Bluescape, 2018)

    25 Context switches – On average, workers switch between 10 apps, 25 times a day. (Asana, 2021)

    “Work management” is among the latest buzzwords in IT consulting.

    What is work management? It was born of a blurring of the traditional lines between operational or day-to-day tasks and project management tasks, as organizations struggle to keep up with both operational and project demands.

    To make the software easier to use, modern work management doesn’t involve the complexities from days past. You won’t find anywhere to introduce complex predecessor-successor relationships, unbalanced assignments with front-loading or back-loading, early-start/late-finish, critical path, etc.

    Indeed, with Project for the web, Azure Boards, Planner, and other M365 utilities, Microsoft is attempting to compete with lighter and better-adopted tools (e.g. Trello, Wike, Monday.com).

    The Microsoft world of work management can be understood across three broad categories

    1. Task Management

      Task management is essentially the same as keeping track of a to-do list. While you can have a project-related task, you can also have a non-project-related task. The sum of project and non-project tasks make up the work that you need to complete.
    2. Project Management

      Project management (PM) is a methodical approach to planning and guiding project processes from start to finish. Implementing PM processes helps establish repeatable steps and controls that enable project success. Documentation of PM processes leads to consistent results and dependable delivery on expectations.
    3. Portfolio Management

      Project portfolio management (PPM) is a strategic approach to approving, prioritizing, resourcing, and reporting on project. In addition, effective PPM should nurture the completion of projects in the portfolio in the most efficient way and track the extent to which the organization is realizing the intended benefits from completed projects.

    The slides ahead explain each of these modes of working in the Microsoft ecosystem in turn. Further, Info-Tech’s Task, Project, and Project Portfolio Management Tool Guides explain these areas in more detail.

    Use Info-Tech’s Tool Guides assess your MS Project and M365 work management options

    Lean on Info-Tech’s Tool Guides as you navigate Microsoft’s tasks management, project management, and project portfolio management options.

    • The slides ahead take you through a bird’s-eye view of what your MS Project and M365 work management options look like across Info-Tech’s three broad categories
    • In addition to these slides, Info-Tech has three in-depth tool guides that take you through your operational task management, project management, and project portfolio management options in MS Project and M365.
    • These tool guides can be leveraged as you determine whether Microsoft has the required toolset for your organization’s task, project, and project portfolio management needs.

    Download Info-Tech’s Task Management, Project Management, and Project Portfolio Management Tool Guides

    Task Management Overview

    What is task management?

    • It is essentially the same as keeping track of a to-do list. While you can have a project-related task, you can also have a non-project-related task. The sum of project and non-project tasks make up the work that you need to complete.

    What are the benefits of task management using applications within the MS suite?

    • Many organizations already own the tools and don't have to go out and buy something separately.
    • There is easy integration with other MS applications.

    What is personal task management?

    • Tools that allow you to structure work that is visible only to you. This can include work from tasks you are going to be completing for yourself and tasks you are completing as part of a larger work effort.

    What is team task management?

    • Tools that allow users to structure work that is visible to a group. When something is moved or changed, it affects what the group is seeing because it is a shared platform.

    Get familiar with the Microsoft product offerings for task management

    A diagram of Microsoft products and what they can help accomplish. It starts on the right with 'Teams' and 'Outlook'. Both can flow through to 'Personal Task Management' with products 'Teams Tasks' and 'To-Do', but Teams also flows into 'Team Task Management' with products 'Planner' and 'Project for the web'. See the next two slides for more details on these modes of working.

    Download the M365 Task Management Tool Guide

    Personal Task Management

    The To-Do list

    • Who does it?
      • Knowledge workers
    • What is it?
      • How each knowledge worker organizes their individual work tasks in M365
    • When is it done?
      • As needed throughout the day
    • Where is it done?
      • Paper
      • Digital location
    • How is it done?
      • DIY and self-developed
      • Usually not repeatable and evolves depending on work location and tools available
      • Not governed

    Microsoft differentiator:

    Utilities like Planner and To-Do make it easier to turn what are often ad hoc approaches into a more repeatable process.

    Team Task Management

    The SharedTo-Do list

    • Who does it?
      • Groups of knowledge workers
    • What is it?
      • Temporary and permanent collections of knowledge workers
    • When is it done?
      • As needed or on a pre-determined cadence
    • Where is it done?
      • Paper
      • Digital location
    • How is it done?
      • User norms are established organically and adapted based upon the needs of the team.
      • To whatever extent processes are repeatable in the first place, they remain repeatable only if the team is a collective.
      • Usually governed within the team and not subject to wider visibility.

    Microsoft differentiator:

    Teams has opened personal task management tactics up to more collaborative approaches.

    Project Management Overview

    2003

    Project Server: This product serves many large enterprise clients, but Microsoft has stated that it is at end of life. It is appealing to industries and organizations where privacy is paramount. This is an on-premises system that combines servers like SharePoint, SQL, and BI to report on information from Project Desktop Client. To realize the value of this product, there must be adoption across the organization and engagement at the project-task level for all projects within the portfolio.

    2013

    Project Online: This product serves many medium enterprise clients. It is appealing for IT departments who want to get a rich set of features that can be used to intake projects, assign resources, and report on project portfolio health. It is a cloud solution built on the SharePoint platform, which provides many users a sense of familiarity. However, due to the bottom-up reporting nature of this product, again, adoption across the organization and engagement at the project task level for all projects within the portfolio is critical.

    2020

    Project for the web: This product is the newest on the market and is quickly being evolved. Many O365 enthusiasts have been early adopters of Project for the web despite its limited features when compared to Project Online. It is also a cloud solution that encourages citizen developers by being built on the MS Power Platform. This positions the product well to integrate with Power BI, Power Automate, and Power Apps. It is, so far, the only MS product that lends itself to abstracted portfolio management, which means it doesn’t rely on project task level engagement to produce portfolio reports. The portfolio can also run with a mixed methodology by funneling Project, Azure Boards, and Planner boards into its roadmap function.

    Get familiar with the Microsoft product offerings for project management

    A diagram of Microsoft products and what they can help accomplish in Personal and Team Project Management. Products listed include 'Project Desktop Client', 'Project Online', 'SharePoint', 'Power Platform', 'Azure DevOps', 'Project for the web', Project Roadmap', 'Project Home', and 'Project Server'. See the next slide for more details on personal and team project management as modes of working.

    Download the M365 Project Management Tool Guide

    Project Management

    Orchestrating the delivery of project work

    • Who does it?
      • Project managers
    • What is it?
      • Individual project managers developing project plans and schedules in the MS Project Desktop Client
    • When is it done?
      • Throughout the lifecycle of the project
    • Where is it done?
      • Digital location
    • How is it done?
      • Used by individual project managers to develop and manage project plans.
      • Common approaches may or may not involve reconciliation of resource capacity through integration with Active Directory.
      • Sometimes usage norms are established by organizational project management governance standards, though individual use of the desktop client is largely ungoverned.

    Microsoft differentiator:

    For better or worse, Microsoft’s core solution is veritably synonymous with project management itself and has formally contributed to the definition of the project management space.

    Project Portfolio Management Overview

    Optimize what you’re already using and get familiar with the Power Platform.

    What does PPM look like within M365?

    • The Office suite in the Microsoft 365 suite boasts the world’s most widely used application for the purposes of abstracted and strategic PPM: Excel. For the purposes of PPM, Excel is largely implemented in a suboptimal fashion, and as a result, organizations fail to gain PPM adoption and maturation through its use.
    • Until very recently, Microsoft toolset did not explicitly address abstracted PPM needs.
    • However, with the latest version of M365 and Project for the web, Microsoft is boasting of renewed PPM capabilities from its toolset. These capabilities are largely facilitated through what Microsoft is calling its Power Platform (i.e. a suite of products that includes Power, Power Apps, and Power Automate).

    Explore the Microsoft product offering for abstracted project portfolio management

    A diagram of Microsoft products for 'Adaptive or Abstracted Portfolio Management'. Products listed include 'Excel', 'MS Lists', 'Forms', 'Teams', and the 'Power Platform' products 'Power BI', 'Power Apps', and 'Power Automate'. See the next slide for more details on adaptive or abstracted portfolio management as a mode of working.

    Download the M365 Project Portfolio Management Tool Guide

    Project Portfolio Management

    Doing the right projects, at the right time, with the right resources

    • Who does it?
      • PMO directors; portfolio managers
    • What is it?
      A strategic approach to approving, prioritizing, resourcing, and reporting on projects using applications in M365 and Project for the web. In distinction to enterprise PPM, a top-down or abstracted approach is applied, meaning PPM data is not tied to project task details.
    • Where is it done?
      • Digital tool, either homegrown or commercial
    • How is it done?
      • Currently in M365, PPM approaches are largely self-developed, though Microsoft Gold Partners are commonly involved.
      • User norms are still evolving, along with the software’s (Project for the web) function.

    Microsoft differentiator:

    Integration between Project for the web and Power Apps allows for custom approaches.

    Project Portfolio Management Overview

    Microsoft’s legacy project management toolset has contributed to the definition of traditional or enterprise PPM space.

    A robust and intensive bottom-up approach that requires task level roll-ups from projects to inform portfolio level data. For this model to work, reconciliation of individual resource capacity must be universal and perpetually current.

    If your organization has low or no maturity with PPM, this approach will be tough to make successful.

    In fact, most organizations under adopt the tools required to effectively operate with the traditional project portfolio management. Once adopted and operationalized, this combination of tools gives the executives the most precise view of the current state of projects within the portfolio.

    Explore the Microsoft product offering for enterprise project portfolio management

    A diagram of Microsoft products for 'Enterprise or Traditional Portfolio Management'. Products listed include 'Project Desktop Client', 'SharePoint', 'Project Online', 'Azure DevOps', 'Project Roadmaps', and 'Project Home'. See the next slide for more details on this as a mode of working.

    Download the M365 Project Portfolio Management Tool Guide

    Enterprise Project and Portfolio Management

    Bottom-up approach to managing the project portfolio

    • Who does it?
      • PMO and ePMO directors; portfolio managers
      • Project managers
    • What is it?
      • A strategic approach to approving, prioritizing, resourcing, and reporting on projects using applications in M365 and Project for the web. In distinction to enterprise PPM, a top-down or abstracted approach is applied, meaning PPM data is not tied to project task details.
    • Where is it done?
      • Digital tool that is usually commercial.
    • How is it done?
      • Microsoft Gold Partner involvement is highly likely in successful implementations.
      • Usage norms are long established and customized solutions are prevalent.
      • To be successful, use must be highly governed.
      • Reconciliation of individual resource capacity must be universal and perpetually current.

    Microsoft differentiator:

    Microsoft’s established network of Gold Partners helps to make this deployment a viable option.

    Assess your current tool ecosystem across work management categories

    Use Info-Tech’s Tool Audit Workbook to assess the value and satisfaction for the work management tools currently in use.

    • With the modes of working in mind that have been addressed in the previous slides and in Info-Tech’s Tool Guides, the activity slides ahead encourage you to engage your wider organization to determine all of the ways of working across individuals and teams.
    • Depending on the scope of your work management optimization, these engagements may be limited to IT or may extend to the business.
    • Use Info-Tech’s Tool Audit Workbook to help you gather and make sense of the tool data you collect. The result of this activity is to gain insight into the tools that drive value and fail to drive value across your work management categories with a view to streamline the organization’s tool ecosystem.

    Download Info-Tech’s Tool Audit Workbook

    Sample of Info-Tech's Tool Audit Workbook.

    1.2.1 Compile list of tools

    1-3 hours

    Input: Information on tools used to complete task, project, and portfolio tasks

    Output: Analyzed list of tools

    Materials: Whiteboard/Flip Charts, Tool Audit Workbook

    Participants: Portfolio Manager (PMO Director), PMO Admin Team, Project Managers, Business Stakeholders

    1. Identify the stakeholder groups that are in scope. For each group that you’ve identified, brainstorm the different tools and artifacts that are necessary to get the task, project, and project portfolio management functions done.
    2. Make sure to record the tool name and specify its category (standard document, artifact, homegrown solution, or commercial solution).
    3. Think about and discuss how often the tool is being used for each use case across the organization. Document whether its use is required. Then assess reporting functionality, data accuracy, and cost.
    4. Lastly, give a satisfaction rating for each use case.

    Excerpt from the Tool Audit Workbook

    Excerpt from Info-Tech's Tool Audit Workbook on compiling tools.

    1.2.1 Review dashboard

    1-3 hours

    Input: List of key PPM decision points, List of who is accountable for PPM decisions, List of who has PPM decision-making authority

    Output: Prioritized list of PPM decision-making support needs

    Materials: Whiteboard/Flip Charts, Tool Audit Workbook

    Participants: Portfolio Manager (PMO Director), PMO Admin Team, CIO

    Discuss the outputs of the Dashboards tab to inform your decision maker on whether to pass or fail the tool for each use case.

    Sample of a BI dashboard used to evaluate the usefulness of tools. Written notes include: 'Slice the data based on stakeholder group, tool, use case, and category', and 'Review the results of the questionnaire by comparing cost and satisfaction'.

    1.2.1 Execute final audit

    1 hour

    Input: List of key PPM decision points, List of who is accountable for PPM decisions, List of who has PPM decision-making authority

    Output: Prioritized list of PPM decision-making support needs

    Materials: Whiteboard/Flip Charts, Tool Audit Workbook

    Participants: Portfolio Manager (PMO Director), PMO Admin Team, CIO

    1. Using the information available, schedule time with the leadership team to present the results.
    2. Identify the accountable party to make the final decision on what current tools pass or fail the final audit.
    3. Mind the gap presented by the failed tools and look to possibilities within the M365 and Microsoft Project suite. For each tool that is deemed unsatisfactory for the future state, mark it as “Fail” in column O on tab 2 of the Tool Audit Workbook. This will ensure the item shows in the “Fail” column on tab 4 of the tool when you refresh the data.
    4. For each of the tools that “fail” your audit and that you’re going to make recommendations to rationalize in a future state, try to capture the annual total current-state spending on licenses, and the work modes the tool currently supports (i.e. task, project, and/or portfolio management).
    5. Additionally, start to think about future-state replacements for each tool within or outside of the M365/MS Project platforms. As we move forward to finalize your action plan in the last phase of this blueprint, we will capture and present this information to key stakeholders.

    Document your goals, needs, and constraints before proceeding

    Use Info-Tech’s Force Field Analysis Tool to help weigh goals and needs against risks and constraints associated with a work management change.

    • Now that you have discussed the organization’s ways of working and assessed its tool landscape – and made some initial decisions on some tool options that might need to change across that landscape – gather key stakeholders to define (a) why a change is needed at this time and (b) to document some of the risks and constraints associated with changing.
    • Info-Tech’s Force Field Analysis Tool can be used to capture these data points. It takes an organizational change management approach and asks you to consider the positive and negative forces associated with a work management tool change at this time.
    • The slides ahead walk you through a force field analysis activity and help you to navigate the relevant tabs in the Tool.

    Download Info-Tech's Force Field Analysis Tool

    Sample of Info-Tech's Force Field Analysis Tool.

    1.2.1 Identify goals and needs (1 of 2)

    Use tab 1 of the Force Field Analysis Workbook to assess goals and needs.

    30 minutes

    Input: Opportunities associated with determining the use case for Microsoft Project and M365 in your organization

    Output: Plotted opportunities based on probability and impact

    Materials: Whiteboard/Flip Charts, Force Field Analysis Tool

    Participants: Portfolio Manager (PMO Director), PMO Admin Team, Project Managers

    1. Brainstorm opportunities associated with exploring and/or implementing Microsoft Project and the Microsoft 365 suite of products for task, project, and project portfolio management.
    2. Document relevant opportunities in tab 1 of the Force Field Analysis Tool. For each driving force for the change (note: a driving force can include goals and needs) that is identified, provide a category that explains why the driving force is a concern (i.e. with this force is the organization looking to mature, integrate, scape, or accelerate?).
    3. In addition, assess the ease of achieving or realizing each goal or need and the impact of realizing them on the PMO and/or the organization.
    4. See the next slide for a screenshot that helps you navigate tab 1 of the Tool.

    Download the Force Field Analysis Tool

    1.2.1 Identify goals and needs (2 of 2)

    Screenshot of tab 1 of the Force Field Analysis Workbook.

    Screenshot of tab 1 of the Force Field Analysis Workbook. There are five columns referred to as columns B through F with the headings 'Opportunities', 'Category', 'Source', 'Ease of Achieving', and 'Impact on PMO/Organization'.

    In column B on tab 1, note the specific opportunities the group would like to call out.

    In column C, categorize the goal or need being articulated by the list of drop-down options: will it accelerate the time to benefit? Will it help to integrate systems and data sources? Will it mature processes and the organization overall? Will it help to scale across the organization? Choose the option that best aligns with the opportunity.

    In column D, categorize the source of the goal or need as internal or external.

    In column E, use the drop-down menus to indicate the ease of realizing each goal or need for the organization. Will it be relatively easy to manifest or will there be complexities to implementing it?

    In column F, use the drop-down menus to indicate the positive impact of realizing or achieving each need on the PMO and/or the organization.

    On tab 3 of the Force Field Analysis Workbook, your inputs on tab 1 are summarized in graphical form from columns B to G. On tab 3, these goals and needs results are contrasted with your inputs on tab 2 (see next slide).

    1.2.2 Identify risk and constraints (1 of 2)

    Use tab 2 of the Force Field Analysis Workbook to assess opposing forces to change.

    30 minutes

    Input: Risks associated with determining the use case for Microsoft Project and M365 in your organization

    Output: Plotted risks based on probability and impact

    Materials: Whiteboard/Flip Charts, Force Field Analysis Tool

    Participants: Portfolio Manager (PMO Director), PMO Admin Team, Project Managers

    1. With the same working group from 1.2.1, brainstorm risks, constraints, and other opposing forces pertaining to your potential future state.
    2. Document relevant opposing forces in tab 2 of the Force Field Analysis Tool. For each opposing force for the change (note: a driving force can include goals and needs) that is identified, provide a category that explains why the opposing force is a concern (i.e. will it impact or is it impacted by time, resources, maturity, budget, or culture?).
    3. In addition, assess the likelihood of the risk or constraint coming to light and the negative impact of it coming to light for your proposed change.
    4. See the next slide for a screenshot that helps you navigate tab 2 of the Force Field Analysis Tool.

    Download the Force Field Analysis Tool

    1.2.2 Identify risk and constraints (2 of 2)

    Screenshot of tab 2 of the Force Field Analysis Workbook.

    Screenshot of tab 2 of the Force Field Analysis Workbook. There are five columns referred to as columns B through F with the headings 'Risks and Constraints', 'Category', 'Source', 'Likelihood of Constraint/Risk/Resisting Force Being Felt', and 'Impact to Derailing Goals and Needs'.

    In column B on tab 2, note the specific risks and constraints the group would like to call out.

    In column C, categorize the risk or constraint being articulated by the list of drop-down options: will it impact or is it impacted by time, resources, budget, culture or maturity?

    In column D, categorize the source of the goal or need as internal or external.

    In column E, use the drop-down menus to indicate the likelihood of each risk or constraint materializing during your implementation. Will it definitely occur or is there just a small chance it could come to light?

    In column F, use the drop-down menus to indicate the negative impact of the risk or constraint to achieving your goals and needs.

    On tab 3 of the Force Field Analysis Workbook, your inputs on tab 2 are summarized in graphical form from columns I to N. On tab 3, your risk and constraint results are contrasted with your inputs on tab 1 to help you gauge the relative weight of driving vs. opposing forces.

    Step 1.2

    Explore the Microsoft Project Plans and their capabilities

    Activities

    • 1.1.1 Review the Microsoft 365 licensing features
    • 1.1.2 Explore the Microsoft Project Plan licenses
    • 1.1.3 Prepare a needs assessment for Microsoft 365 and Project Plan licenses

    This step will walk you through the following activities:

    • Review the suite of task management, project management, and project portfolio management options available in Microsoft 365.
    • Prepare a preliminary checklist of required M365 apps for your stakeholders.

    This step usually involves the following participants:

    • PMO/Portfolio Manager
    • Project Managers
    • CIO and other executive stakeholders
    • Other project portfolio stakeholders (project and IT workers)

    Outcomes of Step

    • Preliminary requirements for an M365 project management and project portfolio management tool implementation

    Microsoft recently revamped its project plans to balance its old and new tech

    Access to the new tech, Project for the web, comes with all license types, while Project Online Professional and Premium licenses have been revamped as P3 and P5.

    Navigating Microsoft licensing is never easy, and Project for the web has further complicated licensing needs for project professionals.

    As we’ll cover in step 2.1 of this blueprint, Project for the web can be extended beyond its base lightweight work management functionality using the Power Platform (Power Apps, Power Automate, and Power BI). Depending on the scope of your implementation, this can require additional Power Platform licensing.

    • In this step, we will help you understand the basics of what’s already included in your enterprise M365 licensing as well as what’s new in Microsoft’s recent Project licensing plans (P1, P3, and P5).
    • As we cover toward the end of this step, you can use Info-Tech’s MS Project and M365 Licensing Tool to help you understand your plan and licensing needs. Further assistance on licensing can be found in the Task, Project, and Portfolio Management Tool Guides that accompany this blueprint and Info-Tech’s Modernize Your Microsoft Licensing for the Cloud Era.

    Download Info-Tech’s Modernize Your Microsoft Licensing for the Cloud Era

    Licensing features for knowledge workers

    Please note that licensing packages are frequently subject to change. This is up to date as of August 2021. For the most up-to-date information on licensing, visit the Microsoft website.

    Bundles are extremely common and can be more cost effective than à la carte options for the Microsoft products.

    The biggest differentiator between M365 and O365 is that the M365 product also includes Windows 10 and Enterprise Mobility and Security.

    The color coding in the diagram indicates that the same platform/application suite is available.

    Platform or Application M365 E3 M365 E5 O365 E1 O365 E3 O365 E5
    Microsoft Forms X X X X X
    Microsoft Lists X X X X X
    OneDrive X X X X X
    Planner X X X X X
    Power Apps for Office 365 X X X X X
    Power Automate for Office X X X X X
    Power BI Pro X X
    Power Virtual Agents for Teams X X X X X
    SharePoint X X X X X
    Stream X X X X X
    Sway X X X X X
    Teams X X X X X
    To Do X X X X X

    Get familiar with Microsoft Project Plan 1

    Please note that licensing packages are frequently subject to change. This is up to date as of August 2021. For the most up to date information on licensing, visit the Microsoft website.

    Who is a good fit?

    • New project managers
    • Zero-allocation project managers
    • Individuals and organizations who want to move out of Excel into something less fragile (easily breaking formulas)

    What does it include?

    • Access to Project Home, a landing page to access all project plans you’ve created or have been assigned to.
    • Access to Grid View, Board View, and Timeline (Gantt) View to plan and manage your projects with Project for the web
    • Sharing Project for the web plans across Microsoft Teams channels
    • Co-authoring on project plans

    When does it make sense?

    • Lightweight project management
    • No process to use bottom-up approach for resourcing data
    • Critical-path analysis is not required
    • Organization does not have an appetite for project management rigor

    Get familiar with Microsoft Project Plan 3

    Please note that licensing packages are frequently subject to change. This is up to date as of August 2021. For the most up to date information on licensing, visit the Microsoft website.

    Who is a good fit?

    • Experienced and dedicated project managers
    • Organizations with complex projects
    • Large project teams are required to complete project work
    • Organizations have experience using project management software

    What does it include?

    Everything in Project Plan 1 plus the following:

    • Reporting through Power BI Report template apps (note that there are no pre-built reports for Project for the web)
    • Access to build a Roadmap of projects from Project for the web and Azure DevOps with key milestones, statuses, and deadlines
    • Project Online to submit and track timesheets for project teams
    • MS Project Desktop Client to support resource management

    When does it make sense?

    • Project management is an established discipline at the organization
    • Critical-path analysis is commonly used
    • Organization has some appetite for project management rigor
    • Resources are expected to submit timesheets to allow for more precise resource management data

    Get familiar with Microsoft Project Plan 5

    Please note that licensing packages are frequently subject to change. This is up to date as of August 2021. For the most up to date information on licensing, visit the Microsoft website.

    Who is a good fit?

    • Experienced and dedicated project managers
    • Experienced and dedicated PMO directors
    • Dedicated portfolio managers
    • Organizations proficient at sustaining data in a standard tool

    What does it include?

    Everything in Project Plan 3 plus the following:

    • Portfolio selection and optimization
    • Demand management
    • Enterprise resource planning and management through deterministic task and resource scheduling
    • MS Project Desktop Client to support resource management

    When does it make sense?

    • Project management is a key success factor at the organization
    • Organization employs a bottom-up approach for resourcing data
    • Critical-path analysis is required
    • Formal project portfolio management processes are well established
    • The organization is willing to either put in the time, energy, and resources to learn to configure the system through DIY or is willing to leverage a Microsoft Partner to help them do so

    What’s included in each plan (1 of 2)

    Plan details are up to date as of September 2021. Plans and pricing can change often. Visit the Microsoft website to validate plan options and get pricing details.
    MS Project Capabilities Info-Tech's Editorial Description P1 P3 P5
    Project Home Essentially a landing page that allows you to access all the project plans you've created or that you're assigned to. It amalgamates plans created in Project for the web, the Project for the web app in Power Apps, and Project Online. X X X
    Grid view One of three options in which to create your project plans in Project for the web (board view and timeline view are the other options). You can switch back and forth between the options. X X X
    Board view One of three options in which to create your project plans in Project for the web (grid view and timeline view are the other options). You can switch back and forth between the options. X X X
    Timeline (Gantt) view One of three options in which to create your project plans in Project for the web (board view and grid view are the other options). You can switch back and forth between the options. X X X
    Collaboration and communication This references the ability to add Project for the web project plans to Teams channels. X X X
    Coauthoring Many people can have access to the same project plan and can update tasks. X X X
    Project planning and scheduling For this the marketing lingo says "includes familiar scheduling tools to assign project tasks to team members and use different views like Grid, Board, and Timeline (Gantt chart) to oversee the schedule." Unclear how this is different than the project plans in the three view options above. X X X

    X - Functionality Included in Plan

    O - Functionality Not Included in Plan

    What’s included in each plan (2 of 2)

    Plan details are up to date as of September 2021. Plans and pricing can change often. Visit the Microsoft website to validate plan options and get pricing details.
    MS Project Capabilities Info-Tech's Editorial Description P1 P3 P5
    Reporting This seems to reference Excel reports and the Power BI Report Template App, which can be used if you're using Project Online. There are no pre-built reports for Project for the web, but third-party Power Apps are available. O X X
    Roadmap Roadmap is a platform that allows you to take one or more projects from Project for the web and Azure DevOps and create an organizational roadmap. Once your projects are loaded into Roadmap you can perform additional customizations like color status reporting and adding key days and milestones. O X X
    Timesheet submission Project Online and Server 2013 and 2016 allow team members to submit timesheets if the functionality is required. O X X
    Resource management The rich MS Project client supports old school, deterministic project scheduling at the project level. O X X
    Desktop client The full desktop client comes with P3 and P5, where it acts as the rich editor for project plans. The software enjoys a multi-decade market dominance as a project management tool but was never paired with an enterprise collaboration server engine that enjoyed the same level of success. O X X
    Portfolio selection and optimization Portfolio selection and optimization has been offered as part of the enterprise project and portfolio suite for many years. Most people taking advantage of this capability have used a Microsoft Partner to formalize and operationalize the feature. O O X
    Demand Management Enterprise demand management is targeted at the most rigorous of project portfolio management practices. Most people taking advantage of this capability have used a Microsoft Partner to formalize and operationalize the feature. O O X
    Enterprise resource planning and management The legacy MS Project Online/Server platform supports enterprise-wide resource capacity management through an old-school, deterministic task and resource scheduling engine, assuming scaled-out deployment of Active Directory. Most people succeeding with this capability have used a Microsoft Partner to formalize and operationalize the feature. O O X

    X - Functionality Included in Plan

    O - Functionality Not Included in Plan

    Use Info-Tech’s MS Project and M365 Licensing Tool

    Leverage the analysis in Info-Tech’s MS Project & M365 Licensing Tool to help inform your initial assumptions about what you need and how much to budget for it.

    • The Licensing Tool can help you determine what Project Plan licensing different user groups might need as well as additional Power Platform licensing that may be required.
    • It consists of four main tabs: two set-up tabs where you can validate the plan and pricing information for M365 and MS Project; an analysis tab where you set up your user groups and follow a survey to assess their Project Plan needs; and another analysis tab where you can document your Power Platform licensing needs across your user groups.
    • There is also a business case tab that breaks down your total licensing needs. The outputs of this tab can be used in your MS Project & M365 Action Plan Template, which we will help you develop in phase three of this blueprint.

    Download Info-Tech's Microsoft Project & M365 Licensing Tool

    Sample of Info-Tech's Microsoft Project and M365 Licensing Tool.

    1.2.1 Conduct a needs assessment

    1-2 hours

    Input: List of key user groups/profiles, Number of users and current licenses

    Output: List of Microsoft applications/capabilities included with each license, Analysis of user group needs for Microsoft Project Plan licenses

    Materials: Microsoft Project & 365 Licensing Tool

    Participants: Portfolio Manager (PMO Director), PMO Admin Team, Project Managers

    1. As a group, analyze the applications included in your current or desired 365 license and calculate any additional Power Platform licensing needs.
    2. Screenshot of the 'Application/Capabilities' screen from the 'Microsoft Project and M365 Licensing Tool'.
    3. Within the same group, use the drop-down menus to analyze your high-level MS Project requirements by selecting whether each capability is necessary or not.
    4. Your inputs to the needs assessment will determine the figures in the Business Case tab. Consider exporting this information to PDF or other format to distribute to stakeholders.
    5. Screenshot of the 'Business Case' tab from the 'Microsoft Project and M365 Licensing Tool'.

    Download Info-Tech's Microsoft Project & M365 Licensing Tool

    Step 1.3

    Assess the maturity of your current PM & PPM capabilities

    Activities

    • Assess current state project and project portfolio management processes and tools
    • Determine target state project and project portfolio management processes and tools

    This step will walk you through the following activities:

    • Assess current state project and project portfolio management processes and tools
    • Determine target state project and project portfolio management processes and tools

    This step usually involves the following participants:

    • PMO/Portfolio Manager
    • Project Managers
    • CIO and other executive stakeholders
    • Other project portfolio stakeholders (project and IT workers)

    Outcomes of Step

    • Current and target state maturity for project management and project portfolio management processes

    Project portfolio management and project management are more than tools

    Implementing commercial tools without a matching level of process discipline is a futile exercise, leaving organizations frustrated at the wasted time and money.

    • The tool is only as good as the data that is input. There is often a misunderstanding that a tool will be “automatic.” While it is true that a tool can help make certain processes easier and more convenient by aggregating information, enhancing reporting, and coauthoring, it will not make up the data. If data becomes stale, the tool is no longer valid for accurate decision making.
    • Getting people onboard and establishing a clear process is often the hardest part. As IT folk, it can be easy to get wrapped up in the technology. All too often excitement around tools can drown out the important requisites around people and process. The reality is people and process are a necessary condition for a tool to be successful. Having a tool will not be sufficient to overcome obstacles like poor stakeholder buy-in, inadequate governance, and the absence of a standard operating procedure.

    • Slow is the way to go. When deciding what tools to purchase, start small and scale up rather than going all in and all too often ending up with many unused features and fees.

    "There's been a chicken-egg debate raging in the PPM world for decades: What comes first, the tool or the process? It seems reasonable to say, ‘We don't have a process now, so we'll just adopt the one in the tool.’ But you'll soon find out that the tool doesn't have a process, and you needed to do more planning and analysis before buying the tool." (Barry Cousins, Practice Lead, Project Portfolio Management)

    Assess your process maturity to determine the right tool approach

    Take the time to consider and reflect on the current and target state of the processes for project portfolio management and project management.

    Project Portfolio Management

    • Status and Progress Reporting
      1. Intake, Approval, and Prioritization

        PPM is the practice of selecting the right projects and ensuring the organization has the necessary resources to complete them. PPM should enable executive decision makers to make sense of the excess of demand and give IT the ability to prioritize those projects that are most valuable to the business.
      2. Resource Management

      3. Project Management

        1. Initiation
        2. Planning
        3. Execution
        4. Monitoring and Controlling
        5. Closing
        Tailor a project management framework to fit your organization. Formal methodologies aren’t always the best fit. Take what you can use from formal frameworks and define a right-sized approach to your project management processes.
      4. Project Closure

      5. Benefits Tracking

    Info-Tech’s maturity assessment tools can help you match your tools to your maturity level

    Use Info-Tech’s Project Portfolio Management Maturity Assessment Tool and Project Management Maturity Assessment Tool.

    • The next few slides in this step take you through using our maturity assessment tools to help gauge your current-state and target-state maturity levels for project management (PM) and project portfolio management (PPM).
    • In addition to the process maturity assessments, these workbooks also help you document current-state support tools and desired target-state tools.
    • The outputs of these workbooks can be used in your MS Project & M365 Action Plan Template, which we will help you develop in phase three of this blueprint.

    Download Info-Tech’s Project Portfolio Management Maturity Assessment Tool and Project Management Maturity Assessment Tool

    Samples of Info-Tech's Project Portfolio Management Maturity Assessment Tool and Project Management Maturity Assessment Tool.

    Conduct a gap analysis survey for both project and project portfolio management.

    • Review the category and activity statements: For each gap analysis tab in the maturity assessments, use the comprehensive activity statements to identify gaps for the organization.
    • Assess the current state: To assess the current state, evaluate whether the statement should be labeled as:
      • Absent: There is no evidence of any activities supporting this process.
      • Initial: Activity is ad hoc and not well defined.
      • Defined: Activity is established and there is moderate adherence to its execution.
      • Repeatable: Activity is established, documented, repeatable, and integrated with other phases of the process.
      • Managed: Activity execution is tracked by gathering qualitative and quantitative feedback

    Once this is documented, take some time to describe the type of tool being used to do this (commercial, home-grown, standardized document) and provide additional details, where applicable.

    Define the target state: Repeat the assessment of activity statements for the target state. Then gauge the organizational impact and complexity of improving each capability on a scale of very low to very high.

    Excerpt from Info-Tech's Project Portfolio Management Maturity Assessment Tool, the 'PPM Current State Target State Maturity Assessment Survey'. It has five columns whose purpose is denoted in notes. Column 1 'Category within the respective discipline'; Column 2 'Statement to consider'; Column 3 'Select the appropriate answer for current and target state'; Column 4 'Define the tool type'; Column 5 'Provide addition detail about the tool'.

    Analyze survey results for project and project portfolio management maturity

    Take stock of the gap between current state and target state.

    • What process areas have the biggest gap between current and target state?
    • What areas are aligned across current and target state?

    Identify what areas are currently the least and most mature.

    • What process area causes the most pain in the organization?
    • What process area is the organization’s lowest priority?

    Note the overall current process maturity.

    • After having done this exercise, does the overall maturity come as a surprise?
    • If so, what are some of the areas that were previously overlooked?
    A table and bar graph documenting and analysis of maturity survey results. The table has four columns labelled 'Process Area', 'Current Process Completeness', 'Current Maturity Level', and 'Target State Maturity'. Rows headers in the 'Process Area' column are 'Intake, Approval, and Prioritization', 'Resource Management', 'Portfolio Reporting', 'Project Closure and Benefits Realization', 'Portfolio Administration', and finally 'Overall Maturity'. The 'Current Process Completeness' column's values are in percentages. The 'Current Maturity Level' and 'Target State Maturity' columns' values can be one of the following: 'Absent', 'Initial', 'Defined', 'Repeatable', or 'Managed'. The bar chart visualizes the levels of the 'Target State' and 'Current State' with 'Absent' from 0-20%, 'Initial' from 20-40%, 'Defined' from 40-60%, 'Repeatable' from 60-80%, and 'Managed' from 80-100%.
    • Identify process areas with low levels of maturity
    • Spot areas of inconsistency between current and target state.
    • Assess the overall gap to get a sense of the magnitude of the effort required to get to the target state.
    • 100% doesn’t need to be the goal. Set a goal that is sustainable and always consider the value to effort ratio.

    Screenshot your results and put them into the MS Project and M365 Action Plan Template.

    Review the tool overview and plan to address gaps (tabs 3 & 4)

    Tool Overview:

    Analyze the applications used to support your project management and project portfolio management processes.

    Look for:

    • Tools that help with processes across the entire PM or PPM lifecycle.
    • Tools that are only used for one specific process.

    Reflect on the overlap between process areas with pain points and the current tools being used to complete this process.

    Consider the sustainability of the target-state tool choice

    Screenshot of a 'Tool Overview' table. Chart titled 'Current-to-Target State Supporting Tools by PPM Activity' documenting the current and target states of different supporting tools by PPM Activity. Tools listed are 'N/A', 'Standardized Document', 'Homegrown Tool', and 'Commercial Tool'.

    You have the option to create an action plan for each of the areas of improvement coming out of your maturity assessment.

    This can include:

    • Tactical Optimization Action: What is the main action needed to improve capability?
    • Related Actions: Is there a cross-over with any actions for other capabilities?
    • Timeframe: Is this near-term, mid-term, or long-term?
    • Proposed Start Date
    • Proposed Go-Live Date
    • RACI: Who will be responsible, accountable, consulted, and informed?
    • Status: What is the status of this action item over time?

    Determine the Future of Microsoft Project for Your Organization

    Phase 2: Weigh Your Implementation Options

    Phase 1: Determine Your Tool Needs

    Phase 2: Weigh Your Implementation Options

    Phase 3: Finalize Your Implementation Approach
    • Step 1.1: Survey the M365 work management landscape
    • Step 1.2: Perform a process maturity assessment to help inform your M365 starting point
    • Step 1.3: Consider the right MS Project licenses for your stakeholders
    • Step 2.1: Get familiar with extending Project for the web using Power Apps
    • Step 2.2: Assess the MS Gold Partner Community
    • Step 3.1: Prepare an action plan

    Phase Outcomes

    • A decision on how best to proceed (or not proceed) with Project for the web
    • A Partner outreach plan

    Step 2.1

    Get familiar with extending Project for the web using Power Apps

    Activities

    • Get familiar with Project for the web: how it differs from Microsoft’s traditional project offerings and where it is going
    • Understand the basics of how to extend Project for the web in Power Apps
    • Perform a feasibility test

    This step will walk you through the following activities:

    • Get familiar with Project for the web
    • Understand the basics of how to extend Project for the web in Power Apps
    • Perform a feasibility test to determine if taking a DIY approach to extending Project for the web is right for your organization currently

    This step usually involves the following participants:

    • Portfolio Manager (PMO Director)
    • Project Managers
    • Other relevant PMO stakeholders

    Outcomes of Step

    • A decision on how best to proceed (or not proceed) with Project for the web

    Project for the web is the latest of Microsoft’s project management offerings

    What is Project for the web?

    • First introduced in 2019 as Project Service, Project for the web (PFTW) is Microsoft’s entry into the world of cloud-based work management and lightweight project management options.
    • Built on the Power Platform and leveraging the Dataverse for data storage, PFTW integrates with the many applications that M365 users are already employing in their day-to-day work management and collaboration activities.
    • It is available as a part of your M365 subscription with the minimum activation of P1 license – it comes with P3 and P5 licenses as well.
    • From a functionality and user experience perspective, PFTW is closer to applications like Planner or Azure Boards than it is to traditional MS Project options.

    What does it do?

    • PFTW allows for task and dependency tracking and basic timeline creation and scheduling and offers board and grid view options. It also allows real-time coauthoring of tasks among team members scheduled to the same project.
    • PFTW also comes with a product/functionality Microsoft calls Roadmap, which allows users to aggregate multiple project timelines into a single view for reporting purposes.

    What doesn't it do?

    • With PFTW, Microsoft is offering noticeably less traditional project management functionality than its existing solutions. Absent are table stakes project management capabilities like critical path, baselining, resource load balancing, etc.

    Who is it for?

    • Currently, in its base lightweight project management option, PFTW is targeted toward occasional or part-time project managers (not the PMP-certified set) tasked with overseeing and/or collaborating on small to mid-sized initiatives and projects.

    Put Project for the web in perspective

    Out of the box, PFTW occupies a liminal space when it comes to work management options

    • More than a task management tool, but not quite a full project management tool
    • Not exactly a portfolio management tool, yet some PPM reporting functionality is inherent in the PFTW through Roadmap

    The table to the right shows some of the functionality in PFTW in relation to the task management functionality of Planner and the enterprise project and portfolio management functionality of Project Online.

    Table 2.1a Planner Project for the web Project Online
    Coauthoring on Tasks X X
    Task Planning X X X
    Resource Assignments X X X
    Board Views X X X
    MS Teams Integration X X X
    Roadmap X X
    Table and Gantt Views X X
    Task Dependency Tracking X X
    Timesheets X
    Financial Planning X
    Risks and Issues Tracking X
    Program Management X
    Advanced Portfolio Management X

    Project for the web will eventually replace Project Online

    • As early as 2018 Microsoft has been foreshadowing a transition away from the SharePoint-backed Project environments of Server and Online toward something based in Common Data Service (CDS) – now rebranded as the Dataverse.
    • Indeed, as recently as the spring of 2021, at its Reimagine Project Management online event, Microsoft reiterated its plans to sunset Project Online and transition existing Online users to the new environment of Project for the web – though it provided no firm dates when this might occur.
      • The reason for this move away from Online appears to be an acknowledgment that the rigidity of the tool is awkward in our current dynamic, collaborative, and overhead-adverse work management paradigm.
      • To paraphrase a point made by George Bullock, Sr. Product Marketing Manager, for Microsoft at the Reimagine Project Management event, teams want to manage work as they see fit, but the rigidity of legacy solutions doesn’t allow for this, leading to a proliferation of tools and data sprawl. (This comment was made during the “Overview of Microsoft Project” session during the Reimagine event.)

    PFTW is Microsoft’s proposed future-state antidote to this challenge. Its success will depend on how well users are able to integrate the solution into a wider M365 work management setting.

    "We are committed to supporting our customers on Project Online and helping them transition to Project for the Web. No end-of-support has been set for Project Online, but when the time comes, we will communicate our plans on the transition path and give you plenty of advance notice." (Heather Heide, Program Manager, Microsoft Planner and Project. This comment was made during the “Overview of Microsoft Project” session during the Reimagine event.)

    Project for the web can be extended beyond its base lightweight functionality

    Project for the web can be extended to add more traditional and robust project and project portfolio management functionality using the Power Platform.

    Microsoft plans to sunset Project Online in favor of PFTW will at first be a head-scratcher for those familiar with the extensive PPM functionality in Project Online and underwhelmed by the project and portfolio management in PFTW.

    However, having built the solution upon the Power Platform, Microsoft has made it possible to take the base functionality in PFTW and extend it to create a more custom, organizationally specific user experience.

    • With a little taste of what can be done with PFTW by leveraging the Power Platform – and, in particular, Power Apps – it becomes more obvious how we, as users, can begin to evolve the base tool toward a more traditional PPM solution and how, in time, Microsoft’s developers may develop the next iteration of PFTW into something more closely resembling Project Online.

    Before users get too excited about using these tools to build a custom PPM approach, we should consider the time, effort, and skills required. The slides ahead will take you through a series of considerations to help you gauge whether your PMO is ready to go it alone in extending the solution.

    Extending the tool enhances functionality

    Table 2.1a in this step displayed the functionality in PFTW in relation to the task management tool Planner and the robust PPM functionality in Online.

    The table to the right shows how the functionality in PFTW can differ from the base solution and Project Online when it is extended using the model-driven app option in Power Apps.

    Caveat: The list of functionality and processes in this table is sample data.

    This functionality is not inherent in the solution as soon as you integrate with Power Apps. Rather it must be built – and your success in developing these functions will depend upon the time and skills you have available.

    Table 2.1b Project for the web PFTW extended with PowerApps Project Online
    Critical Path X
    Timesheets X
    Financial Planning X X
    Risks and Issues Tracking X X
    Program Management X
    Status Updates X
    Project Requests X
    Business Cases X
    Project Charters X
    Resource Planning and Capacity Management X X
    Project Change Requests X

    Get familiar with the basics of Power Apps before you decide to go it alone

    While the concept of being able to customize and grow a commercial PPM tool is enticing, the reality of low-code development and application maintenance may be too much for resource-constrained PMOs.

    Long story short: Extending PFTW in Power Apps is time consuming and can be frustrating for the novice to intermediate user.

    It can take days, even weeks, just to find your feet in Power Apps, let alone to determine requirements to start building out a custom model-driven app. The latter activity can entail creating custom columns and tables, determining relationships between tables to get required outputs, in addition to basic design activities.

    Time-strapped and resource-constrained practitioners should pause before committing to this deployment approach. To help better understand the commitment, the slides ahead cover the basics of extending PFTW in Power Apps:

    1. Dataverse environments.
    2. Navigating Power App Designer and Sitemap Designer
    3. Customizing tables and forms in the Dataverse

    See Info-Tech’s M365 Project Portfolio Management Tool Guide for more information on Power Apps in general.

    Get familiar with Power Apps licensing

    Power Apps for 365 comes with E1 through E5 M365 licenses (and F3 and F5 licenses), though additional functionality can be purchased if required.

    While extending Project for the web with Power Apps does not at this time, in normal deployments, require additional licensing from what is included in a E3 or E5 license, it is not out of the realm of possibility that a more complex deployment could incur costs not included in the Power Apps for 365 that comes with your enterprise agreement.

    The table to the right shows current additional licensing options.

    Power Apps, Per User, Per App Plan

    Per User Plan

    Cost: US$10 per user per app per month, with a daily Dataverse database capacity of 40 MB and a daily Power Platform request capacity of 1,000. Cost: US$40 per user per month, with a daily Dataverse database capacity of 250 MB and a daily Power Platform request capacity of 5,000.
    What's included? This option is marketed as the option that allows organizations to “get started with the platform at a lower entry point … [or those] that run only a few apps.” Users can run an application for a specific business case scenario with “the full capabilities of Power Apps” (meaning, we believe, that unlicensed users can still submit data via an app created by a licensed user). What's included? A per-user plan allows licensed users to run unlimited canvas apps and model-driven apps – portal apps, the licensing guide says, can be “provisioned by customers on demand.” Dataverse database limits (the 250 MB and 5,000 request capacity mentioned above) are pooled at the per tenant, not the per user plan license, capacity.

    For more on Power Apps licensing, refer to Info-Tech’s Modernize Your Microsoft Licensing for the Cloud Era for more information.

    What needs to be configured?

    Extending Project for the web requires working with your IT peers to get the right environments configured based upon your needs.

    • PFTW data is stored in the Microsoft Dataverse (formerly Common Data Service or CDS).
    • The organization’s Dataverse can be made up of one to many environments based upon its needs. Environments are individual databases with unique proprieties in terms of who can access them and what applications can store data in them.
    • Project for the web supports three different types of environments: default, production, and sandbox.
    • You can have multiple instances of a custom PFTW app deployed across these environments and across different users – and the environment you choose depends upon the use case of each instance.

    Types of Environments

    • Default Environment

      • It is the easiest to deploy and get started with the PFTW Power App in the default environment. However, it is also the most restricted environment with the least room for configuration.
      • Microsoft recommends this environment for simple deployments or for projects that span the organization. This is because everyone in the organization is by default a member of this environment – and, with the least room for configuration, the app is relatively straightforward.
      • At minimum, you need one project license to deploy PFTW in the default environment.
    • Production Environment

      • This environment affords more flexibility for how a custom app can be configured and deployed. Unlike the default environment, deploying a production environment is a manual process (through the Power Platform Admin Center) and security roles need to be set to limit users who can access the environment.
      • Because users can be limited, production environments can be used to support more advanced deployments and can support diverse processes for different teams.
      • At present, you need at least five Project licenses to deploy to production environments.
    • Sandbox Environment

      • This environment is for users who are responsible for the creation of custom apps. It offers the same functionality as a production environment but allows users to make changes without jeopardizing a production environment.

    Resources to provide your IT colleagues with to help in your PFTW deployment:

    1. Project for the web admin help (Product Documentation, Microsoft)
    2. Advanced deployment for Project for the web (Video, Microsoft)
    3. Get Started with Project Power App (Product Support Documentation, Microsoft)
    4. Project for the Web Security Roles (Product Support Documentation, Microsoft)

    Get started creating or customizing a model-driven app

    With the proper environments procured, you can now start extending Project for the web.

    • Navigate to the environment you would like to extend PFTW within. For the purposes of the slides ahead, we’ll be using a sandbox environment for an example. Ensure you have the right access set up for production and sandbox environments of your own (see links on previous slide for more assistance).
    • To begin extending PFTW, the two core features you need to be familiar with before you start in Power Apps are (1) Tables/Entities and (2) the Power Apps Designer – and in particular the Site Map.

    From the Power Apps main page in 365, you can change your environment by selecting from the options in the top right-hand corner of the screen.

    Screenshot of the Power Apps “Apps” page in a sandbox environment. The Project App will appear as “Project” when the application is installed, though it is also easy to create an app from scratch.

    Model-driven apps are built around tables

    In Power Apps, tables (formerly called entities and still referred to as entities in the Power Apps Designer) function much like tables in Excel: they are containers of columns of data for tracking purposes. Tables define the data for your app, and you build your app around them.

    In general, there are three types of tables:

    • Standard: These are out-of-the box tables included with a Dataverse environment. Most standard tables can be customized.
    • Managed: These are tables that get imported into an environment as part of a managed solution. Managed tables cannot be customized.
    • Custom: These types of tables can either be imported from another solution or created directly in the Dataverse environment. To create custom tables, users need to have System Administrator or System Customizer security roles within the Dataverse.

    Tables can be accessed under Data banner on the left-hand panel of your Power Apps screen.

    The below is a list of standard tables that can be used to customize your Project App.

    A screenshot of the 'Data' banner in 'Power Apps' and a list of table names.

    Table Name

    Display Name

    msdyn_project Project
    msdyn_projectchange Change
    msdyn_projectprogram Program
    msdyn_projectrequest Request
    msdyn_projectrisk Risk
    msdyn_projectissue Issue
    msdyn_projectstatusreport Status

    App layouts are designed in the Power App Designer

    You configure tables with a view to using them in the design of your app in the Power Apps Designer.

    • If you’re customizing a Project for the web app manually installed into your production or sandbox environment, you can access Designer by highlighting the app from your list of apps on the Apps page and clicking “Edit” in the ribbon above.
      • If you’re creating a model-driven app from scratch, Designer will open past the “Create a New App” intro screen.
      • If you need to create separate apps in your environment for different PMOs or business units, it is as easy to create an app from scratch as it is to customize the manual install.
    • The App Designer is where you can design the layout of your model-driven app and employ the right data tables.
    Screenshot of the 'App Designer' screen in 'Power Apps'.

    The Site Map determines the navigation for your app, i.e. it is where you establish the links and pages users will navigate. We will review the basics of the sitemap on the next few slides.

    The tables that come loaded into your Project Power App environment (at this time, 37) via the manual install will appear in the Power Apps Designer in the Entity View pane at the bottom of the page. You do not have to use all of them in your design.

    Navigate the Sitemap Designer

    With the components of the previous two slides in mind, let’s walk through how to use them together in the development of a Project app.

    As addressed in the previous slide, the sitemap determines the navigation for your app, i.e. it is where you establish the links and the pages that users will navigate.

    To get to the Sitemap Designer, highlight the Project App from your list of apps on the Apps page and click “Edit” in the ribbon above. If you’re creating a model-driven app from scratch, Designer will open past the “Create a New App” intro screen.

    • To start designing your app layout, click the pencil icon beside the Site Map logo on the App Designer screen.
    • This will take you into the Sitemap Designer (see screenshot to the right). This is where you determine the layout of your app and the relevant data points (and related tables from within the Dataverse) that will factor into your Project App.
    • In the Sitemap Designer, you simply drag and drop the areas, groups, and subareas you want to see in your app’s user interface (see next slide for more details).
    Screenshot of the 'Sitemap Designer' in 'Power Apps'.

    Use Areas, Groups, and Subareas as building blocks for your App

    Screenshots of the main window and the right-hand panel in the 'Sitemap Designer', and of the subarea pop-up panel where you connect components to data tables. The first two separate elements into 'Area', 'Group', and 'Subarea'.

    Drag and drop the relevant components from the panel on the right-hand side of the screen into the main window to design the core pieces that will be present within your user interface.

    For each subarea in your design, use the pop-up panel on the right-hand side of the screen to connect your component the relevant table from within your Dataverse environment.

    How do Areas, Groups, and Subareas translate into an app?

    Screenshots of the main window in the 'Sitemap Designer' and of a left-hand panel from a published 'Project App'. There are notes defining the terms 'Area', 'Group', and 'Subarea' in the context of the screenshot.

    The names or titles for your Areas and Groups can be customized within the Sitemap Designer.

    The names or titles for your Subareas is dependent upon your table name within the Dataverse.

    Area: App users can toggle the arrows to switch between Areas.

    Group: These will change to reflect the chosen Area.

    Subarea: The tables and forms associated with each subarea.

    How to properly save and publish your changes made in the Sitemap Designer and Power Apps Designer:

    1. When you are done making changes to your components within the Sitemap Designer, and want your changes to go live, hit the “Publish” button in the top right corner; when it has successfully published, select “Save and Close.”
    2. You will be taken back to the Power App Designer homepage. Hit “Save,” then “Publish,” and then finally “Play,” to go to your app or “Save and Close.”

    How to find the right tables in the Dataverse

    While you determine which tables will play into your app in the Sitemap Designer, you use the Tables link to customize tables and forms.

    Screenshots of the tables search screen and the 'Tables' page under the 'Data' banner in 'Power Apps'.

    The Tables page under the Data banner in Power Apps houses all of the tables available in your Dataverse environment. Do not be overwhelmed or get too excited. Only a small portion of the tables in the Tables folder in Power Apps will be relevant when it comes to extending PFTW.

    Find the table you would like to customize and/or employ in your app and select it. The next slides will look at customizing the table (if you need to) and designing an app based upon the table.

    To access all the tables in your environment, you’ll need to ensure your filter is set correctly on the top right-hand corner of the screen, otherwise you will only see a small portion of the tables in your Dataverse environment.

    If you’re a novice, it will take you some time to get familiar with the table structure in the Dataverse.

    We recommend you start with the list of tables listed on slide. You can likely find something there that you can use or build from for most PPM purposes.

    How to customize a table (1 of 3)

    You won’t necessarily need to customize a table, but if you do here are some steps to help you get familiar with the basics.

    Screenshot of the 'Columns' tab, open in the 'msdyn_project table' in 'Power Apps'.

    In this screenshot, we are clicked into the msdyn_project (display name: Project) table. As you can see, there are a series of tabs below the name of the table, and we are clicked into the Columns tab. This is where you can see all of the data points included in the table.

    You are not able to customize all columns. If a column that you are not able to customize does not meet your needs, you will need to create a custom column from the “+Add column” option.

    “Required” or “Optional” status pertains to when the column or field is used within your app. For customizable or custom columns this status can be set when you click into each column.

    How to customize a table (2 of 3)

    Create a custom “Status” column.

    By way of illustrating how you might need to customize a table, we’ll highlight the “msdyn_project_statecode” (display name: Project Status) column that comes preloaded in the Project (msdyn_project) table.

    • The Project Status column only gives you a binary choice. While you are able to customize what that binary choice is (it comes preloaded with “Active” and “Inactive” as the options) you cannot add additional choices – so you cannot set it to red/yellow/green, the most universally adopted options for status in the project portfolio management world.
    • Because of this, let’s look at the effort involved in creating a choice and adding a custom column to your table based upon that choice.
    Screenshots of the '+New choice' button in the 'Choices' tab and the 'New choice' pane that opens when you click it.

    From within the Choices tab, click “+New choice” option to create a custom choice.

    A pane will appear to the right of your screen. From there you can give your choice a name, and under the “Items” header, add your list of options.

    Click save. Your custom choice is now saved to the Choices tab in the Dataverse environment and can be used in your table. Further customizations can be made to your choice if need be.

    How to customize a table (3 of 3)

    Back in the Tables tab, you can put your new choice to work by adding a column to a table and selecting your custom choice.

    Screenshots of the pop-up window that appear when you click '+Add Column', and details of what happens when you select the data type 'Choice'.

    Start by selecting “+ Add Column” at the top left-hand side of your table. A window will appear on the right-hand side of the page, and you will have options to name your column and choose the data type.

    As you can see in this screenshot to the left, data type options include text, number and date types, and many more. Because we are looking to use our custom choice for this example, we are going to choose “Choice.”

    When you select “Choice” as your data type, all of the choice options available or created in your Dataverse environment will appear. Find your custom choice – in this example the one name “RYG Status” – and click done. When the window closes, be sure to select “Save Table.”

    How to develop a Form based upon your table (1 of 3 – open the form editor)

    A form is the interface users will engage with when using your Project app.

    When the Project app is first installed in your environment, the main user form will be lacking, with only a few basic data options.

    This form can be customized and additional tabs can be added to your user interface.

    1. To do this, go to the table you want to customize.
    2. In the horizontal series of tabs at the top of the screen, below the table title select the “Forms” option.
    3. Click on the main information option or select Edit Form for the form with “Main” under its form type. A new window will open where you can customize your form.
    Screenshot of the 'Forms' tab, open in the 'msdyn_project' table in 'Power Apps'.

    Select the Forms tab.

    Start with the form that has “Main” as its Format Type.

    How to develop a Form based upon your table (2 of 3 – add a component)

    Screenshot of the 'Components' window in 'Power Apps' with a list of layouts as a window to the right of the main screen where you can name and format the chosen layout.

    You can add element like columns or sections to your form by selecting the Components window.

    In this example, we are adding a 1-Column section. When you select that option from the menu options on the left of the screen, a window will open to the right of the screen where you can name and format the section.

    Choose the component you would like to add from the layout options. Depending on the table element you are looking to use, you can also add input options like number inputs and star ratings and pull in related data elements like a project timeline.

    How to develop a Form based upon your table (3 of 3 – add table columns)

    Screenshot of the 'Table Columns' window in 'Power Apps' and instructions for adding table columns.

    If you click on the “Table Columns” option on the left-hand pane, all of the column options from within your table will appear in alphabetical order.

    When clicked within the form section you would like to add the new column to, select the column from the list of option in the left-hand pane. The new data point will appear within the section. You can order and format section elements as you would like.

    When you are done editing the form, click the “Save” icon in the top right-hand corner. If you are ready for your changes to go live within your Project App, select the “Publish” icon in the top right-hand corner. Your updated form will go live within all of the apps that use it.

    The good and the bad of extending Project for the web

    The content in this step has not instructed users how to extend PFTW; rather, it has covered three basic core pieces of Power Apps that those interesting in PFTW need to be aware of: Dataverse environments, the Power Apps and Sitemaps Designers, and Tables and associated Forms.

    Because we have only covered the very tip of the iceberg, those interested in going further and taking a DIY approach to extending PFTW will need to build upon these basics to unlock further functionality. Indeed, it takes work to develop the product into something that begins to resemble a viable enterprise project and portfolio management solution. Here are some of the good and the bad elements associated with that work:

    The Good:

    • You can right-size and purpose build: add as much or as little project management rigor as your process requires. Related, you can customize the solution in multiple ways to suit the needs of specific business units or portfolios.
    • Speed to market: it is possible to get up and running quickly with a minimum-viable product.

    The Bad:

    • Work required: to build anything beyond MVP requires independent research and trial and error.
    • Time required: to build anything beyond MVP requires time and skills that many PMOs don’t have.
    • Shadow support costs: ungoverned app creation could have negative support and maintenance impacts across IT.

    "The move to Power Platform and low code development will […increase] maintenance overhead. Will low code solution hit problems at scale? [H]ow easy will it be to support hundreds or thousands of small applications?

    I can hear the IT support desks already complaining at the thought of this. This part of the puzzle is yet to hit real world realities of support because non developers are busy creating lots of low code applications." (Ben Hosking, Software Developer and Blogger, "Why low code software development is eating the world")

    Quick start your extension with the Accelerator

    For those starting out, there is a pre-built app you can import into your environment to extend the Project for the web app without any custom development.

    • If the DIY approach in the previous slides was overwhelming, and you don’t have the budget for a MS Partner route in the near-term, this doesn’t mean that evolving your Project for the web app is unattainable.
    • Thanks to a partnership between OnePlan (one of the MS Gold Partners we detail in the next step) and Microsoft, Project for the web users have access to a free resource to help them evolve the base Project app. It’s called the “Project for the web Accelerator” (commonly referred to as “the Accelerator” for short).
    • Users interested in learning more about, and accessing, this free resource should refer to the links below:
      1. The Future of Microsoft Project Online (source: OnePlan).
      2. Introducing the Project Accelerator (source: Microsoft).
      3. Project for the web Accelerator (source: GitHub)
    Screen shot from one of the dashboards that comes with the Accelerator (image source: GitHub).

    2.1.1 Perform a feasibility test (1 of 2)

    15 mins

    As we’ve suggested, and as the material in this step indicates, extending PFTW in a DIY fashion is not small task. You need a knowledge of the Dataverse and Power Apps, and access to the requisite skills, time, and resources to develop the solution.

    To determine whether your PMO and organization are ready to go it alone in extending PFTW, perform the following activity:

    1. Convene a collection of portfolio, project, and PMO staff.
    2. Using the six-question survey on tab 5 of the Microsoft Project & M365 Licensing Tool (see screenshot to the right) as a jumping off point for a discussion, consider the readiness of your PMO or project organization to undertake a DIY approach to extending and implementing PFTW at this time.
    3. You can use the recommendations on tab 5 of the Microsoft Project & 365 Licensing Tool to inform your next steps, and input the gauge graphic in section 4 of the Microsoft Project & M365 Action Plan Template.
    Screenshots from the 'Project for the Web Extensibility Feasibility Test'.

    Go to tab 5 of the Microsoft Project & M365 Licensing Tool

    See next slide for additional activity details

    2.1.1 Perform a feasibility test (2 of 2)

    Input: The contents of this step, The Project for the Web Extensibility Feasibility Test (tab 5 in the Microsoft Project & 365 Licensing Tool)

    Output: Initial recommendations on whether to proceed and how to proceed with a DIY approach to extending Project for the web

    Materials: The Project for the Web Extensibility Feasibility Test (tab 5 in the Microsoft Project & 365 Licensing Tool)

    Participants: Portfolio Manager (PMO Director), Project Managers, Other relevant PMO stakeholders

    Step 2.2

    Assess the Microsoft Gold Partner Community

    Activities

    • Review what to look for in a Microsoft Partner
    • Determine whether your needs would benefit from reaching out to a Microsoft Partner
    • Review three key Partners from the North American market
    • Create a Partner outreach plan

    This step will walk you through the following activities:

    • Review what to look for in a Microsoft Partner.
    • Determine whether your needs would benefit from reaching out to a Microsoft Partner.
    • Review three key Partners from the North American market.

    This step usually involves the following participants:

    • Portfolio Manager (PMO Director)
    • Project Managers
    • Other relevant PMO stakeholders

    Outcomes of Step

    • A better understanding of MS Partners
    • A Partner outreach plan

    You don’t have to go it alone

    Microsoft has an established community of Partners who can help in your customizations and implementations of Project for the web and other MS Project offerings.

    If the content in the previous step seemed too technical or overly complex in a way that scared you away from a DIY approach to extending Microsoft’s latest project offering (and at some point in the near future, soon to be its only project offering), Project for the web, fear not.

    You do not have to wade into the waters of extending Project for the web alone, or for that matter, in implementing any other MS Project solution.

    Instead, Microsoft nurtures a community of Silver and Gold partners who offer hands-on technical assistance and tool implementation services. While the specific services provided vary from partner to partner, all can assist in the customization and implementation of any of Microsoft’s Project offerings.

    In this step we will cover what to look for in a Partner and how to assess whether you are a good candidate for the services of a Partner. We will also highlight three Partners from within the North American market.

    The basics of the Partner community

    What is a Microsoft Partner?

    Simply put, an MS Gold Partner is a software or professional services organization that provides sales and services related to Microsoft products.

    They’re resellers, implementors, integrators, software manufacturers, trainers, and virtually any other technology-related business service.

    • Microsoft has for decades opted out of being a professional services organization, outside of its very “leading edge” offerings from MCS (Microsoft Consulting Services) for only those technologies that are so new that they aren’t yet supported by MS Partners.
    • As you can see in the chart on the next slide, to become a silver or gold certified partner, firms must demonstrate expertise in specific areas of business and technology in 18 competency areas that are divided into four categories: applications and infrastructure, business applications, data and AI, and modern workplace and security.

    More information on what it takes to become a Microsoft Partner:

    1. Partner Center (Document Center, Microsoft)
    2. Differentiate your business by attaining Microsoft competencies (Document Center, Microsoft)
    3. Partner Network Homepage (Webpage, Microsoft)
    4. See which partner offer is right for you (Webpage, Microsoft)

    Types of partnerships and qualifications

    Microsoft Partner Network

    Microsoft Action Pack

    Silver Competency

    Gold Competency

    What is it?

    The Microsoft Partner Network (MPN) is a community that offers members tools, information, and training. Joining the MPN is an entry-level step for all partners. The Action Pack is an annual subscription offered to entry-level partners. It provides training and marketing materials and access to expensive products and licenses at a vastly reduced price. Approximately 5% of firms in the Microsoft Partner Network (MPN) are silver partners. These partners are subject to audits and annual competency exams to maintain silver status. Approximately 1% of firms in the Microsoft Partner Network (MPN) are gold partners. These partners are subject to audits and annual competency exams to maintain Gold status.

    Requirements

    Sign up for a membership Annual subscription fee While requirements can vary across competency area, broadly speaking, to become a silver partner firms must:
    • Pass regular exams and skills assessments, with at least two individuals on staff with Microsoft Certified Professional Status.
    • Hit annual customer, revenue, and licensing metrics.
    • Pay the annual subscription fee.
    While requirements can vary across competency area, broadly speaking, to become a gold partner firms must:
    • Pass regular exams and skills assessments, with at least two individuals on staff with Microsoft Certified Professional Status.
    • Hit annual customer, revenue, and licensing metrics.
    • Pay the annual subscription fee.

    Annual Fee

    No Cost $530 $1800 $5300

    When would a MS Partner be helpful?

    • Project management and portfolio management practitioners might look into procuring the services of a Microsoft Partner for a variety of reasons.
    • Because services vary from partner to partner (help to extend Project for the web, implement Project Server or Project Online, augment PMO staffing, etc.) we won’t comment on specific needs here.
    • Instead, the three most common conditions that trigger the need are listed to the right.

    Speed

    When you need to get results faster than your staff can grow the needed capabilities.

    Cost

    When the complexity of the purchase decision, implementation, communication, training, configuration, and/or customization cannot be cost-justified for internal staff, often because you’ll only do it once.

    Expertise & Skills

    When your needs cannot be met by the core Microsoft technology without significant extension or customization.

    Canadian Microsoft Partners Spotlight

    As part of our research process for this blueprint, Info-Tech asked Microsoft Canada for referrals and introductions to leading Microsoft Partners. We spent six months collaborating with them on fresh research into the underlying platform.

    These vendors are listed below and are highlighted in subsequent slides.

    Spotlighted Partners:

    Logo for One Plan. Logo for PMO Outsource Ltd. Logo for Western Principles.

    Please Note: While these vendors were referred to us by Microsoft Canada and have a footprint in the Canadian market, their footprints extend beyond this to the North American and global markets.

    A word about our approach

    Photo of Barry Cousins, Project Portfolio Management Practice Lead, Info-Tech Research Group.
    Barry Cousins
    Project Portfolio Management Practice Lead
    Info-Tech Research Group

    Our researchers have been working with Microsoft Project Online and Microsoft Project Server clients for years, and it’s fair to say that most of these clients (at some point) used a Microsoft Partner in their deployment. They’re not really software products, per se; they’re platforms. As a Microsoft Partner in 2003 when Project Server got its first big push, I heard it loud and clear: “Some assembly required. You might only make 7% on the licensing, but the world’s your oyster for services.”

    In the past few years, Microsoft froze the market for major Microsoft Project decisions by making it clear that the existing offering is not getting updates while the new offering (Project for the web) doesn’t do what the old one did. And in a fascinating timing coincidence, the market substantially adopted Microsoft 365 during that period, which enables access to Project for the web.

    Many of Info-Tech’s clients are justifiably curious, confused, and concerned, while the Microsoft Partners have persisted in their knowledge and capability. So, we asked Microsoft Canada for referrals and introductions to leading Microsoft Partners and spent six months collaborating with them on fresh research into the underlying platform.

    Disclosure: Info-Tech conducted collaborative research with the partners listed on the previous slide to produce this publication. Market trends and reactions were studied, but the only clients identified were in case studies provided by the Microsoft Partners. Info-Tech’s customers have been, and remain, anonymous. (Barry Cousins, Project Portfolio Management Practice Lead, Info-Tech Research Group)

    MS Gold Partner Spotlight:

    OnePlan

    Logo for One Plan.
    Headquarters: San Marcos, California, and Toronto, Ontario
    Number of Employees: ~80
    Active Since: 2007 (as EPMLive)
    Website: www.oneplan.ai

    Who are they?

    • While the OnePlan brand has only been the marketplace for a few years, the company has been a major player in MS Gold Partner space for well over a decade.
    • Born out of EPMLive in the mid-aughts, OnePlan Solutions has evolved through a series of acquisitions, including Upland, Tivitie, and most recently Wicresoft.

    What do they do?

    • Software: Its recent rebranding is largely because OnePlan Solutions is as much a software company as it is a professional services firm. The OnePlan software product is an impressive solution that can be used on its own to facilitate the portfolio approaches outlined on the next slide and that can also integrate with the tools your organization is already using to manage tasks (see here for a full rundown of the solutions within the Microsoft stack and beyond OnePlan can integrate with).
    • Beyond its ability to integrate with existing solutions, as a software product, OnePlan has modules for resource planning, strategic portfolio planning, financial planning, time tracking, and more.

    • PPM Consulting Services: The OnePlan team also offers portfolio management consulting services. See the next slide for a list of its approaches to project portfolio management.

    Markets served

    • US, Canada, Europe, and Australia

    Channel Differentiation

    • OnePlan scales to all the PPM needs of all industry types.
    • Additionally, OnePlan offers insights and functionality specific to the needs of BioTech-Pharma.

    What differentiates OnePlan?

    • OnePlan co-developed the Project Accelerator for Project for the web with Microsoft. The OnePlan team’s involvement in developing the Accelerator and making it free for users to access suggests it is aligned to and has expertise in the purpose-built and collaborative vision behind Microsoft’s move away from Project Online and toward the Power Platform and Teams collaboration.
    • 2021 MS Gold Partner of the Year. At Microsoft’s recent Microsoft Inspire event, OnePlan was recognized as the Gold Partner of the Year for Project and Portfolio Management as well as a finalist for Power Apps and Power Automate.
    • OnePlan Approaches: Below is a list of the services or approaches to project portfolio management that OnePlan provides. See its website for more details.
      • Strategic Portfolio Management: Align work to objectives and business outcomes. Track performance against the proposed objectives outcomes.
      • Agile Portfolio Management: Implement Agile practices across the organization, both at the team and executive level.
      • Adaptive Portfolio Management: Allow teams to use the project methodology and tools that best suit the work/team. Maintain visibility and decision making across the entire portfolio.
      • Professional Services Automation: Use automation to operate with greater efficiency.

    "OnePlan offers a strategic portfolio, financial and resource management solution that fits the needs of every PMO. Optimize your portfolio, financials and resources enterprise wide." (Paul Estabrooks, Vice President at OnePlan)

    OnePlan Case Study

    This case study was provided to Info-Tech by OnePlan.

    Brambles

    INDUSTRY: Supply Chain & Logistics
    SOURCE: OnePlan

    Overview: Brambles plays a key role in the delivery or return of products amongst global trading partners such as manufacturers, distributors and retailers.

    Challenge

    Brambles had a variety of Project Management tools with no easy way of consolidating project management data. The proliferation of project management solutions was hindering the execution of a long-term business transformation strategy. Brambles needed certain common and strategic project management processes and enterprise project reporting while still allowing individual project management solutions to be used as part of the PPM platform.

    Solution

    As part of the PMO-driven business transformation strategy, Brambles implemented a project management “operating system” acting as a foundation for core processes such as project intake, portfolio management, resource, and financial planning and reporting while providing integration capability for a variety of tools used for project execution.

    OnePlan’s new Adaptive PPM platform, combining the use of PowerApps and OnePlan, gives Brambles the desired PPM operating system while allowing for tool flexibility at the execution level.

    Results

    • Comprehensive picture of progress across the portfolio.
    • Greater adoption by allowing flexibility of work management tools.
    • Modern portfolio management solution that enables leadership to make confident decision.

    Solution Details

    • OnePlan
    • Project
    • Power Apps
    • Power Automate
    • Power BI
    • Teams

    Contacting OnePlan Solutions

    www.oneplan.ai

    Joe Larscheid: jlarscheid@oneplan.ai
    Paul Estabrooks: pestabrooks@oneplan.ai
    Contact Us: contact@oneplan.ai
    Partners: partner@oneplan.ai

    Partner Resources. OnePlan facilitates regular ongoing live webinars on PPM topics that anyone can sign up for on the OnePlan website.

    For more information on upcoming webinars, or to access recordings of past webinars, see here.

    Additional OnePlan Resources

    1. How to Extend Microsoft Teams into a Collaborative Project, Portfolio and Work Management Solution (on-demand webinar, OnePlan’s YouTube channel)
    2. What Does Agile PPM Mean To The Modern PMO (on-demand webinar, OnePlan’s YouTube channel)
    3. OnePlan is fused with the Microsoft User Experience (blog article, OnePlan)
    4. Adaptive Portfolio Management Demo – Bringing Order to the Tool Chaos with OnePlan (product demo, OnePlan’s YouTube channel)
    5. How OnePlan is aligning with Microsoft’s Project and Portfolio Management Vision (blog article, OnePlan)
    6. Accelerating Office 365 Value with a Hybrid Project Portfolio Management Solution (product demo, OnePlan’s YouTube channel)

    MS Gold Partner Spotlight:

    PMO Outsource Ltd.

    Logo for PMO Outsource Ltd.

    Headquarters: Calgary, Alberta, and Mississauga, Ontario
    Website: www.pmooutsource.com

    Who are they?

    • PMO Outsource Ltd. is a Microsoft Gold Partner and PMI certified professional services firm based in Alberta and Ontario, Canada.
    • It offers comprehensive project and portfolio management offerings with a specific focus on project lifecycle management, including demand management, resource management, and governance and communication practices.

    What do they do?

    • Project Online and Power Platform Expertise. The PMO Outsource Ltd. team has extensive knowledge in both Microsoft’s old tech (Project Server and Desktop) and in its newer, cloud-based technologies (Project Online, Project for the web, the Power Platform, and Dynamics 365). As the case study in two slides demonstrates, PMO Outsource Ltd. Uses its in-depth knowledge of the Microsoft suite to help organizations automate project and portfolio data collection process, create efficiencies, and encourage cloud adoption.
    • PPM Consulting Services: In addition to its Microsoft platform expertise, the PMO Outsource Ltd. team also offers project and portfolio management consulting services, helping organizations evolve their process and governance structures as well as their approaches to PPM tooling.

    Markets served

    • Global

    Channel Differentiation

    • PMO Outsource Ltd. scales to all the PPM needs of all industry types.

    What differentiates PMO Outsource Ltd.?

    • PMO Staff Augmentation. In addition to its technology and consulting services, PMO Outsource Ltd. offers PMO staff augmentation services. As advertised on its website, it offers “scalable PMO staffing solutions. Whether you require Project Managers, Business Analysts, Admins or Coordinators, [PMO Outsource Ltd.] can fulfill your talent search requirements from a skilled pool of resources.”
    • Multiple and easy-to-understand service contract packages. PMO Outsource Ltd. offers many prepackaged service offerings to suit PMOs’ needs. Those packages include “PMO Management, Admin, and Support,” “PPM Solution, Site and Workflow Configuration,” and “Add-Ons.” For full details of what’s included in these services packages, see the PMO Outsource Ltd. website.
    • PMO Outsource Ltd. Services: Below is a list of the services or approaches to project portfolio management that PMO Outsource Ltd. Provides. See its website for more details.
      • Process Automation, Workflows, and Tools. Facilitate line of sight by tailoring Microsoft’s technology to your organization’s needs and creating custom workflows.
      • PMO Management Framework. Receive a professionally managed PPM methodology as well as governance standardization of processes, tools, and templates.
      • Custom BI Reports. Leverage its expertise in reporting and dashboarding to create the visibility your organization needs.

    "While selecting an appropriate PPM tool, the PMO should not only evaluate the standard industry tools but also analyze which tool will best fit the organization’s strategy, budget, and culture in the long run." (Neeta Manghnani, PMO Strategist, PMO Outsource Ltd.)

    PMO Outsource Ltd. Case Study

    This case study was provided to Info-Tech by PMO Outsource Ltd.

    SAMUEL

    INDUSTRY: Manufacturing
    SOURCE: PMO Outsource Ltd.

    Challenge

    • MS Project 2013 Server (Legacy/OnPrem)
    • Out-of-support application and compliance with Office 365
    • Out-of-support third-party application for workflows
    • No capability for resource management
    • Too many manual processes for data maintenance and server administration

    Solution

    • Migrate project data to MS Project Online
    • Recreate workflows using Power Automate solution
    • Configure Power BI content packs for Portfolio reporting and resource management dashboards
    • Recreate OLAP reports from legacy environment using Power BI
    • Cut down nearly 50% of administrative time by automating PMO/PPM processes
    • Save costs on Server hardware/application maintenance by nearly 75%

    Full Case Study Link

    • For full details about how PMO Outsource Ltd. assisted Samuel in modernizing its solution and creating efficiencies, visit the Microsoft website where this case study is highlighted.

    Contacting PMO Outsource Ltd.

    www.pmooutsource.com

    700 8th Ave SW, #108
    Calgary, AB T2P 1H2
    Telephone : +1 (587) 355-3745
    6045 Creditview Road, #169
    Mississauga, ON L5V 0B1
    Telephone : +1 (289) 334-1228
    Information: info@pmooutsource.com
    LinkedIn: https://www.linkedin.com/company/pmo-outsource/

    Partner Resources. PMO Outsource Ltd.’s approach is rooted within a robust and comprehensive PPM framework that is focused on driving strategic outcomes and business success.

    For a full overview of its PPM framework, see here.

    Additional PMO Outsource Ltd. Resources

    1. 5 Benefits of PPM tools and PMO process automation (blog article, PMO Outsource Ltd.)
    2. Importance of PMO (blog article, PMO Outsource Ltd.)
    3. Meet the Powerful and Reimagined PPM tool for Everyone! (video, PMO Outsource Ltd. LinkedIn page)
    4. MS Project Tips: How to add #Sprints to an existing Project? (video, PMO Outsource Ltd. LinkedIn page)
    5. MS Project Tips: How to add a milestone to your project? (video, PMO Outsource Ltd. LinkedIn page)
    6. 5 Benefits of implementing Project Online Tools (video, PMO Outsource Ltd. LinkedIn page)

    MS Gold Partner Spotlight:

    Western Principles

    Logo for Western Principles.

    Headquarters: Vancouver, British Columbia
    Years Active: 16 Years
    Website: www.westernprinciples.com

    Who are they?

    • Western Principles is a Microsoft Gold Partner and UMT 360 PPM software provider based in British Columbia with a network of consultants across Canada.
    • In the last sixteen years, it has successfully conducted over 150 PPM implementations, helping in the implementation, training, and support of Microsoft Project offerings as well as UMT360 – a software solution provider that, much like OnePlan, enhances the PPM capabilities of the Microsoft platform.

    What do they do?

    • Technology expertise. The Western Principles team helps organizations maximize the value they are getting form the Microsoft Platform. Not only does it offer expertise in all the solutions in the MS Project ecosystem, it also helps organizations optimize their use and understanding of Teams, SharePoint, the Power Platform, and more. In addition to the Microsoft platform, Western Principles is partnered with many other technology providers, including UMT360 for strategic portfolio management, the Simplex Group for project document controls, HMS for time sheets, and FluentPro for integration, back-ups, and migrations.
    • PPM Consulting Services: In addition to its technical services and solutions, Western Principles offers PPM consulting and staff augmentation services.

    Markets served

    • Canada

    Channel Differentiation

    • Western Principles scales to all the PPM needs of all industry types, public and private sector.
    • In addition, its website offers persona-specific information based on the PPM needs of engineering and construction, new product development, marketing, and more.

    What differentiates Western Principles?

    • Gold-certified UMT 360 partner. In addition to being a Microsoft Gold Partner, Western Principles is a gold-certified UMT 360 partner. UMT 360 is a strategic portfolio management tool that integrates with many other work management solutions to offer holistic line of sight into the organization’s supply-demand pain points and strategic portfolio management needs. Some of the solutions UMT 360 integrates with include Project Online and Project for the web, Azure DevOps, Jira, and many more. See here for more information on the impressive functionality in UMT360.
    • Sustainment Services. Adoption can be the bane of most PPM tool implementations. Among the many services Western Principles offers, its “sustainment services” stand out. According to Western Principles’ website, these services are addressed to those who require “continual maintenance, change, and repair activities” to keep PPM systems in “good working order” to help maximize ROI.
    • Western Principles Services: In addition to the above, below is a list of some of the services that Western Principles offers. See its website for a full list of services.
      • Process Optimization: Determine your requirements and process needs.
      • Integration: Create a single source of truth.
      • Training: Ensure your team knows how to use the systems you implement.
      • Staff Augmentation: Provide experienced project team members based upon your needs.

    "One of our principles is to begin with the end in mind. This means that we will work with you to define a roadmap to help you advance your strategic portfolio … and project management capabilities. The roadmap for each customer is different and based on where you are today, and where you need to get to." (Western Principles, “Your Strategic Portfolio Management roadmap,” Whitepaper)

    Contacting Western Principles

    www.westernprinciples.com

    610 – 700 West Pender St.
    Vancouver, BC V6C 1G8
    +1 (800) 578-4155
    Information: info@westernprinciples.com
    LinkedIn: https://www.linkedin.com/company/western-principle...

    Partner Resources. Western Principles provides a multitude of current case studies on its home page. These case studies let you know what the firm is working on this year and the type of support it provides to its clientele.

    To access these case studies, see here.

    Additional Western Principles Resources

    1. Program and Portfolio Roll ups with Microsoft Project and Power BI (video, Western Principles YouTube Channel)
    2. Dump the Spreadsheets for Microsoft Project Online (video, Western Principles YouTube Channel)
    3. Power BI for Project for the web (video, Western Principles YouTube Channel)
    4. How to do Capacity Planning and Resource Management in Microsoft Project Online [Part 1 & Part 2] (video, Western Principles YouTube Channel)
    5. Extend & Integrate Microsoft Project (whitepaper, Western Principles)
    6. Your COVID-19 Return-to-Work Plan (whitepaper, Western Principles)

    Watch Info-Tech’s Analyst-Partner Briefing Videos to lean more

    Info-Tech was able to sit down with the partners spotlighted in this step to discuss the current state of the PPM market and Microsoft’s place within it.

    • All three partners spotlighted in this step contributed to Info-Tech’s research process for this publication.
    • For two of the partners, OnePlan and PMO Outsource Ltd., Info-Tech was able to record a conversation where our analysts and the partners discuss Microsoft’s current MS Project offerings, the current state of the PPM tool market, and the services and the approaches of each respective partner.
    • A third video briefing with Western Principles has not happened yet due to logistical reasons. We are hoping we can include a video chat with our peers at Western Principles in the near future.
    Screenshot form the Analyst-Partner Briefing Videos. In addition to the content covered in this step, you can use these videos for further information about the partners to inform your next steps.

    Download Info-Tech’s Analyst-Partner Briefing Videos (OnePlan & PMO Outsource Ltd.)

    2.2.1 Create a partner outreach plan

    1-3 hours

    Input: Contents of this step, List of additional MS Gold Partners

    Output: A completed partner outreach program

    Materials: MS Project & M365 Action Plan Template

    Participants: Portfolio Manager (PMO Director), PMO Admin Team, Project Managers, CIO

    1. With an understanding of the partner ecosystem, compile a working group of PMO peers and stakeholders to produce a gameplan for engaging the MS Gold Partner ecosystem.
      • For additional partner options see Microsoft’s Partner Page.
    2. Using slide 20 in Info-Tech’s MS Project and M365 Action Plan Template, document the Partners you would want or have scheduled briefings with.
      • As you go through the briefings and research process, document the pros and cons and areas of specialized associated with each vendor for your particular work management implementation.

    Download the Microsoft Project & M365 Action Plan Template

    2.2.2 Document your PM and PPM requirements

    1-3 hours

    Input: Project Portfolio Management Maturity Assessment, Project Management Maturity Assessment

    Output: MS Project & M365 Action Plan Template

    Materials: Project Portfolio Management Maturity Assessment, Project Management Maturity Assessment, MS Project & M365 Action Plan Template

    Participants: Portfolio Manager (PMO Director), PMO Admin Team, Project Managers, CIO

    1. As you prepare to engage the Partner Community, you should have a sense of where your project management and project portfolio management gaps are to better communicate your tooling needs.
    2. Leverage tab 4 from both your Project Portfolio Management Assessment and Project Management Assessment from step 1.3 of this blueprint to help document and communicate your requirements. Those tabs prioritize your project and portfolio management needs by highest impact for the organization.
    3. You can use the outputs of the tab to inform your inputs on slide 23 of the MS Project & M365 Action Plan Template to present to organizational stakeholders and share with the Partners you are briefing with.

    Download the Microsoft Project & M365 Action Plan Template

    Determine the Future of Microsoft Project for Your Organization

    Phase 3: Finalize Your Implementation Approach

    Phase 1: Determine Your Tool NeedsPhase 2: Weigh Your Implementation Options

    Phase 3: Finalize Your Implementation Approach

    • Step 1.1: Survey the M365 work management landscape
    • Step 1.2: Perform a process maturity assessment to help inform your M365 starting point
    • Step 1.3: Consider the right MS Project licenses for your stakeholders
    • Step 2.1: Get familiar with extending Project for the web using Power Apps
    • Step 2.2: Assess the MS Gold Partner Community
    • Step 3.1: Prepare an action plan

    Phase Outcomes

    An action plan concerning what to do with MS Project and M365 for your PMO or project organization.

    Step 3.1

    Prepare an action plan

    Activities

    • Compile the current state results
    • Prepare an Implementation Roadmap
    • Complete your presentation deck

    This step will walk you through the following activities:

    • Assess the impact of organizational change for the project
    • Develop your vision for stakeholders
    • Compile the current state results and document the implementation approach
    • Create clarity through a RACI and proposed implementation timeline

    This step usually involves the following participants:

    • Portfolio Manager (PMO Director)
    • PMO Admin Team
    • Business Analysts
    • Project Managers

    Outcomes of Step

    • Microsoft Project and M365 Action Plan

    Assess the impact of organizational change

    Be prepared to answer: “What’s in it for me?”

    Before jumping into licensing and third-party negotiations, ensure you’ve clearly assessed the impact of change.

    Tailor the work effort involved in each step, as necessary:

    1. Assess the impact
      • Use the impact assessment questions to identify change impacts.
    2. Plan for change
      • Document the impact on each stakeholder group.
      • Anticipate their response.
      • Curate a compelling message for each stakeholder group.
      • Develop a communication plan.
    3. Act according to plan
      • Identify your executive sponsor.
      • Enable the sponsor to drive change communication.
      • Coach managers on how they can drive change at the individual level.

    Impact Assessment Questions

    • Will the change impact how our clients/customers receive, consume, or engage with our products/services?
    • Will there be a price increase?
    • Will there be a change to compensation and/or rewards?
    • Will the vision or mission of the job change?
    • Will the change span multiple locations/time zones?
    • Are multiple products/services impacted by this change?
    • Will staffing levels change?
    • Will this change increase the workload?
    • Will the tools of the job be substantially different?
    • Will a new or different set of skills be needed?
    • Will there be a change in reporting relationships?
    • Will the workflow and approvals be changed?
    • Will there be a substantial change to scheduling and logistics?

    Master Organizational Change Management Practices blueprint

    Develop your vision for stakeholders

    After careful analysis and planning, it’s time to synthesize your findings to those most impacted by the change.

    Executive Brief

    • Prepare a compelling message about the current situation.
    • Outline the considerations the working group took into account when developing the action plan.
    • Succinctly describe the recommendations proposed by the working group.

    Goals

    • Identify the goals for the project.
    • Explain the details for each goal to develop the organizational rationale for the project.
    • These goals are the building blocks for the change communication that the executive sponsor will use to build a coalition of sponsors.

    Future State Vision

    • Quantify the high-level costs and benefits of moving forward with this project.
    • Articulate the future- state maturity level for both the project and project portfolio management process.
    • Reiterate the organizational rationale and drivers for change.

    "In failed transformations, you often find plenty of plans, directives, and programs, but no vision…A useful rule of thumb: If you can’t communicate the vision to someone in five minutes or less and get a reaction that signifies both understanding and interest, you are not yet done…" (John P. Kotter, Leading Change)

    Get ready to compile the analysis completed throughout this blueprint in the subsequent activities. The outputs will come together in your Microsoft Project and M365 Action Plan.

    Use the Microsoft Project & M365 Action Plan Template to help communicate your vision

    Our boardroom-ready presentation and communication template can be customized using the outputs of this blueprint.

    • Getting stakeholders to understand why you are recommending specific work management changes and then communicating exactly what those changes are and what they will cost is key to the success of your work management implementation.
    • To that end, the slides ahead walk you through how to customize the Microsoft Project & M365 Action Plan Template.
    • Many of the current-state analysis activities you completed during phase 1 of this blueprint can be directly made use of within the template as can the decisions you made and requirements you documented during phase 2.
    • By the end of this step, you will have a boardroom-ready presentation that will help you communicate your future-state vision.
    Screenshot of Info-Tech's Microsoft Project and M365 Action Plan Template with a note to 'Update the presentation or distribution date and insert your name, role, and organization'.

    Download Info-Tech’s Microsoft Project & M365 Action Plan Template

    3.1.1 Compile current state results

    1-3 hours

    Input: Force Field Analysis Tool, Tool Audit Workbook, Project Management Maturity Assessment Tool, Project Portfolio Management Maturity Assessment Tool

    Output: Section 1: Executive Brief, Section 2: Context and Constraints

    Materials: Microsoft Project and M365 Action Plan Template

    Participants: PMO Director, PMO Admin Team, Business Analysts, Project Managers

    1. As a group, review the results of the tools introduced throughout this blueprint. Use this information along with organizational knowledge to document the business context and current state.
    2. Update the driving forces for change and risks and constraints slides using your outputs from the Force Field Analysis Tool.
    3. Update the current tool landscape, tool satisfaction, and tool audit results slides using your outputs from the Tool Audit Workbook.
    4. Update the gap analysis results slides using your outputs from the Project Management and Project Portfolio Management Maturity Assessment Tools.

    Screenshots of 'Business Context and Current State' screen from the 'Force Field Analysis Tool', the 'Tool Audit Results' screen from the 'Tool Audit Workbook', and the 'Project Portfolio Management Gap Analysis Results' screen from the 'PM and PPM Maturity Assessments Tool'.

    Download the Microsoft Project & M365 Action Plan Template

    3.2.1 Option A: Prepare a DIY roadmap

    1-3 hours; Note: This is only applicable if you have chosen the DIY route

    Input: List of key PPM decision points, List of who is accountable for PPM decisions, List of who has PPM decision-making authority

    Output: Section 3: DIY Implementation Approach

    Materials: Microsoft Project and M365 Action Plan Template

    Participants: PMO Director, PMO Admin Team, Business Analysts, Project Managers

    1. As a group, review the results of the Microsoft Project and M365 Licensing Tool. Use this information along with organizational knowledge and discussion with the working group to complete Section 3: DIY Implementation Approach.
    2. Copy and paste your results from tab 5 of the Microsoft Project and M365 Licensing Tool. Update the Implementation Approach slide to detail the rationale for selecting this option.
    3. Update the Action Plan to articulate the details for total and annual costs of the proposed licensing solution.
    4. Facilitate a discussion to determine roles and responsibilities for the implementation. Based on the size, risk, and complexity of the implementation, create a reasonable timeline.
    Screenshots from the 'Microsoft Project and M365 Action Plan Template' outlining the 'DIY Implementation Approach'.

    Download the Microsoft Project and M365 Action Plan Template

    3.2.1 Option b: Prepare a Partner roadmap

    1-3 hours; Note: This is only applicable if you have chosen the Partner route

    Input: Microsoft Project and M365 Licensing Tool, Information on Microsoft Partners

    Output: Section 4: Microsoft Partner Implementation Route

    Materials: Microsoft Project and M365 Action Plan Template

    Participants: PMO Director, PMO Admin Team, Business Analysts, Project Managers

    1. As a group, review the results of the Microsoft Project and M365 Licensing Tool. Use this information along with organizational knowledge and discussion with the working group to complete Section 4: Microsoft Partner Implementation Route.
    2. Copy and paste your results from tab 5 of the Microsoft Project and M365 Licensing Tool. Update the Implementation Approach slide to detail the rationale for selecting this option.
    3. Develop an outreach plan for the Microsoft Partners you are planning to survey. Set targets for briefing dates and assign an individual to own any back-and-forth communication. Document the pros and cons of each Partner and gauge interest in continuing to analyze the vendor as a possible solution.
    4. Facilitate a discussion to determine roles and responsibilities for the implementation. Based on the size, risk, and complexity of the implementation, create a reasonable timeline.

    Screenshots from the 'Microsoft Project and M365 Action Plan Template' outlining the 'Microsoft Partner Implementation Route'.

    Microsoft Project and M365 Action Plan Template

    3.1.2 Complete your presentation deck

    1-2 hours

    Input: Outputs from the exercises in this blueprint

    Output: Section 5: Future-State Vision and Goals

    Materials: Microsoft Project and M365 Action Plan Template

    Participants: PMO Director, PMO Admin Team, Business Analysts, Project Managers

    1. Put the finishing touches on your presentation deck by documenting your future- state vision and goals.
    2. Prepare to present to your stakeholders.
      • Understand your audience, their needs and priorities, and their degree of knowledge and experiences with technology. This informs what to include in your presentation and how to position the message and goal.
    3. Review the deck beginning to end and check for spelling, grammar, and vertical logic.
    4. Practice delivering the vision for the project through several practice sessions.

    Screenshots from the 'Microsoft Project and M365 Action Plan Template' regarding finishing touches.

    Microsoft Project and M365 Action Plan Template

    Pitch your vision to key stakeholders

    There are multiple audiences for your pitch, and each audience requires a different level of detail when addressed. Depending on the outcomes expected from each audience, a suitable approach must be chosen. The format and information presented will vary significantly from group to group.

    Audience

    Key Contents

    Outcome

    Business Executives

    • Section 1: Executive Brief
    • Section 2: Context and Constraints
    • Section 5: Future-State Vision and Goals
    • Identify executive sponsor

    IT Leadership

    • Sections 1-5 with a focus on Section 3 or 4 depending on implementation approach
    • Get buy-in on proposed project
    • Identify skills or resourcing constraints

    Business Managers

    • Section 1: Executive Brief
    • Section 2: Context and Constraints
    • Section 5: Future-State Vision and Goals
    • Get feedback on proposed plan
    • Identify any unassessed risks and organizational impacts

    Business Users

    • Section 1: Executive Brief
    • Support the organizational change management process

    Summary of Accomplishment

    Problem Solved

    Knowledge Gained
    • How you work: Work management and the various ways of working (personal and team task management, strategic project portfolio management, formal project management, and enterprise project and portfolio management).
    • Where you need to go: Project portfolio management and project management current- and target-state maturity levels.
    • What you need: Microsoft Project Plans and requisite M365 licensing.
    • The skills you need: Extending Project for the web.
    • Who you need to work with: Get to know the Microsoft Gold Partner community.
    Deliverables Completed
    • M365 Tool Guides
    • Tool Audit Workbook
    • Force Field Analysis Tool
    • Project Portfolio Management Maturity Assessment Tool
    • Project Management Maturity Assessment Tool
    • Microsoft Project & M365 Action Plan Template

    If you would like additional support, have our analysts guide you through other phases as part of an Info-Tech workshop

    Contact your account representative for more information
    workshops@infotech.com
    1-888-670-8889

    Additional Support

    If you would like additional support, have our analysts guide you through other phases as part of an Info-Tech Workshop.

    Photo of Barry Cousins.
    Contact your account representative for more information
    workshops@infotech.com 1-888-670-8889

    To accelerate this project, engage your IT team in an Info-Tech workshop with an Info-Tech analyst team.

    Info-Tech analysts will join you and your team at your location or welcome you to Info-Tech’s historic Toronto office to participate in an innovative onsite workshop.

    The following are sample activities that will be conducted by Info-Tech analysts with your team:

    Perform a work management tool audit

    Gain insight into the tools that drive value or fail to drive value across your work management landscape with a view to streamline the organization’s tool ecosystem.

    Prepare an action plan for your tool needs

    Prepare the right work management tool recommendations for your IT teams and/or business units and develop a boardroom-ready presentation to communicate needs and next steps.

    Research Contributors and Experts

    Neeta Manghnani
    PMO Strategist
    PMO Outsource Ltd.

    Photo of Neeta Manghnani, PMO Strategist, PMO Outsource Ltd.
    • Innovative, performance-driven executive with significant experience managing Portfolios, Programs & Projects, and technical systems for international corporations with complex requirements. A hands-on, dynamic leader with over 20 years of experience guiding and motivating cross-functional teams. Highly creative and brings a blend of business acumen and expertise in multiple IT disciplines, to maximize the corporate benefit from capital investments.
    • Successfully deploys inventive solutions to automate processes and improve the functionality, scalability and security of critical business systems and applications. Leverages PMO/PPM management and leadership skills to meet the strategic goals and business initiatives.

    Robert Strickland
    Principal Consultant & Owner
    PMO Outsource Ltd.

    Photo of Robert Strickland, Principal Consultant and Owner, PMO Outsource Ltd.
    • Successful entrepreneur, leader, and technologist for over 15 years, is passionate about helping organizations leverage the value of SharePoint, O365, Project Online, Teams and the Power Platform. Expertise in implementing portals, workflows and collaboration experiences that create business value. Strategic manager with years of successful experience building businesses, developing custom solutions, delivering projects, and managing budgets. Strong transformational leader on large implementations with a technical pedigree.
    • A digital transformation leader helping clients move to the cloud, collaborate, automate their business processes and eliminate paper forms, spreadsheets and other manual practices.

    Related Info-Tech Research

    • Develop a Project Portfolio Management Strategy
      Time is money; spend it wisely.
    • Establish Realistic IT Resource Management Practices
      Holistically balance IT supply and demand to avoid overallocation.
    • Tailor Project Management Processes to Fit Your Projects
      Spend less time managing processes and more time delivering results

    Bibliography

    “13 Reasons not to use Microsoft Project.” Celoxis, 14 Sept. 2018. Accessed 17 Sept. 2021.

    Advisicon. “Project Online vs Project for the Web.” YouTube, 13 Nov. 2013. Accessed 17 Sept. 2021.

    Branscombe, Mary. “Is Project Online ready to replace Microsoft Project?” TechRepublic, 23 Jan. 2020. Accessed 17 Sept. 2021.

    Chemistruck, Dan. “The Complete Office 365 and Microsoft 365 Licensing Comparison.” Infused Innovations, 4 April 2019. Accessed 17 Sept. 2021.

    “Compare Project management solutions and costs.” Microsoft. Accessed 17 Sept. 2021.

    Day to Day Dynamics 365. “Microsoft Project for the web - Model-driven app.” YouTube, 29 Oct. 2019. Accessed 17 Sept. 2021.

    “Deploying Project for the web.” Microsoft, 24 Aug. 2021. Accessed 17 Sept. 2021.

    “Differentiate your business by attaining Microsoft competencies.” Microsoft, 26 Jan. 2021. Accessed 17 Sept. 2021.

    “Extend & Integrate Microsoft Project.” Western Principles. Accessed 17 Sept. 2021.

    “Get Started with Project Power App.” Microsoft. Accessed 17 Sept. 2021.

    Hosking, Ben. “Why low code software development is eating the world.” DevGenius, May 2021. Accessed 17 Sept. 2021.

    “How in the World is MS Project Still a Leading PM Software?” CBT Nuggets, 12 Nov. 2018. Accessed 17 Sept. 2021.

    Integent. “Project for the Web - Create a Program Entity and a model-driven app then expose in Microsoft Teams.” YouTube, 25 Mar. 2020. Accessed 17 Sept. 2021.

    “Introducing the Project Accelerator.” Microsoft, 10 Mar. 2021. Accessed 17 Sept. 2021.

    “Join the Microsoft Partner Network.” Microsoft. Accessed 17 Sept. 2021.

    Kaneko, Judy. “How Productivity Tools Can Lead to a Loss of Productivity.” Bluescape, 2 Mar. 2018 Accessed 17 Sept. 2021.

    Kotter, John. Leading Change. Harvard Business School Press, 1996.

    Leis, Merily. “What is Work Management.” Scoro. Accessed 17 Sept. 2021.

    Liu, Shanhong. “Number of Office 365 company users worldwide as of June 2021, by leading country.” Statistica, 2021. Web.

    Manghnani, Neeta. “5 Benefits of PPM tools and PMO process automation.” PMO Outsource Ltd., 11 Apr. 2021. Accessed 17 Sept. 2021.

    “Microsoft 365 and Office 365 plan options.” Microsoft, 31 Aug. 2021. Accessed 17 Sept. 2021.

    “Microsoft 365 for enterprise.” Microsoft. Accessed 17 Sept. 2021

    “Microsoft Office 365 Usage Statistics.” Thexyz blog, 18 Sept. 2020. Accessed 17 Sept. 2021.

    “Microsoft Power Apps, Microsoft Power Automate and Microsoft Power Virtual Agents Licensing Guide.” Microsoft, June 2021. Web.

    “Microsoft Project service description.” Microsoft, 31 Aug. 2021. Accessed 17 Sept. 2021.

    “Microsoft Project Statistics.” Integent Blog, 12 Dec. 2013. Accessed 17 Sept. 2021.

    Nanji, Aadil . Modernize Your Microsoft Licensing for the Cloud Era. Info-Tech Research Group, 12 Mar. 2020. Accessed 17 Sept. 2021.

    “Number of Office 365 company users worldwide as of June 2021, by leading country.” Statista, 8 June 2021. Accessed 17 Sept. 2021.

    “Overcoming disruption in a digital world.” Asana. Accessed 17 Sept. 2021.

    Pajunen, Antti. “Customizing and extending Project for the web.” Day to Day Dynamics 365, 20 Jan. 2020. Accessed 17 Sept. 2021.

    “Partner Center Documentation.” Microsoft. Accessed 17 Sept. 2021.

    Pragmatic Works. “Building First Power Apps Model Driven Application.” YouTube, 21 June 2019. Accessed 17 Sept. 2021.

    “Project architecture overview.” Microsoft, 27 Mar. 2020. Accessed 17 Sept. 2021.

    “Project for the web Accelerator.” GitHub. Accessed 17 Sept. 2021.

    “Project for the web admin help.” Microsoft, 28 Oct. 2019. Accessed 17 Sept. 2021.

    “Project for the Web – The New Microsoft Project.” TPG. Accessed 17 Sept. 2021.

    “Project for the Web Security Roles.” Microsoft, 1 July 2021. Accessed 17 Sept. 2021.

    “Project Online: Project For The Web vs Microsoft Project vs Planner vs Project Online.” PM Connection, 30 Nov. 2020. Accessed 17 Sept. 2021.

    Redmond, Tony. “Office 365 Insights from Microsoft’s FY21 Q2 Results.” Office 365 for IT Pros, 28 Jan. 2021. Accessed 17 Sept. 2021.

    Reimagine Project Management with Microsoft. “Advanced deployment for Project for the web.” YouTube, 4 Aug. 2021. Accessed 17 Sept. 2021.

    Reimagine Project Management with Microsoft. “Overview of Microsoft Project.” YouTube, 29 July 2021. Accessed 17 Sept. 2021.

    “See which partner offer is right for you.” Microsoft. Accessed 17 Sept. 2021.

    Shalomova, Anna. “Microsoft Project for Web 2019 vs. Project Online: What’s Best for Enterprise Project Management?” FluentPro, 23 July 2020. Accessed 17 Sept. 2021.

    Speed, Richard. “One Project to rule them all: Microsoft plots end to Project Online while nervous Server looks on.” The Register, 28 Sept. 2018. Accessed 17 Sept. 2021.

    Spataro, Jared. “A new vision for modern work management with Microsoft Project.” Microsoft, 25 Sept. 2018. Accessed 17 Sept. 2021.

    Stickel, Robert. “OnePlan Recognized as Winner of 2021 Microsoft Project & Portfolio Management Partner of the Year.” OnePlan, 8 July 2021. Accessed 17 Sept. 2021.

    Stickel, Robert. “The Future of Project Online.” OnePlan, 2 Mar. 2021. Accessed 17 Sept. 2021.

    Stickel, Robert. “What It Means to be Adaptive.” OnePlan, 24 May 2021. Accessed 17 Sept. 2021.

    “The Future of Microsoft Project Online.” OnePlan. Accessed 17 Sept. 2021.

    Weller, Joe. “Demystifying Microsoft Project Licensing.” Smartsheet, 10 Mar. 2016. Accessed 17 Sept. 2021.

    Western Principles Inc. “Dump the Spreadsheets for Microsoft Project Online.” YouTube, 2 July 2020. Accessed 17 Sept. 2021.

    Western Principles Inc. “Project Online or Project for the web? Which project management system should you use?” YouTube, 11 Aug. 2020. Accessed 17 Sept. 2021.

    “What is Power Query?” Microsoft, 22 July 2021. Web.

    Wicresoft. “The Power of the New Microsoft Project and Microsoft 365.” YouTube, 29 May 2020. Accessed 17 Sept. 2021.

    Wicresoft. “Why the Microsoft Power Platform is the Future of PPM.” YouTube, 11 June 2020. Accessed 17 Sept. 2021.

    Identify the Components of Your Cloud Security Architecture

    • Buy Link or Shortcode: {j2store}354|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Security Strategy & Budgeting
    • Parent Category Link: /security-strategy-and-budgeting
    • Leveraging the cloud introduces IT professionals to a new world that they are tasked with securing. Consumers do not know what security services they need and when to implement them.
    • With many cloud vendors proposing to share the security responsibility, it can be a challenge for organizations to develop a clear understanding of how they can best secure their data off premises.

    Our Advice

    Critical Insight

    • Your cloud security architecture needs to be strategic, realistic, and based on risk. The NIST approach to cloud security is to include everything security into your cloud architecture to be deemed secure. However, you can still have a robust and secure cloud architecture by using a risk-based approach to identify the necessary controls and mitigating services for your environment.
    • The cloud is not the right choice for everyone. You’re not as unique as you think. Start with a reference model that is based on your risks and business attributes and optimize it from there.
    • Your responsibility doesn’t end at the vendor. Even if you outsource your security services to your vendors, you will still have security responsibilities to address.
    • Don’t boil the ocean; do what is realistic for your enterprise. Your cloud security architecture should be based on securing your most critical assets. Use our reference model to determine a launch point.
    • A successful strategy is holistic. Controlling for cloud risks comes from knowing what the risks are. Consider the full spectrum of security, including both processes and technologies.

    Impact and Result

    • The business is adopting a cloud environment and it must be secured, which includes:
      • Ensuring business data cannot be leaked or stolen.
      • Maintaining the privacy of data and other information.
      • Securing the network connection points.
      • Knowing the risks associated with the cloud and mitigating those risks with the appropriate services.
    • This blueprint and associated tools are scalable for all types of organizations within various industry sectors. It allows them to know what types of risk they are facing and what security services are strongly recommended to mitigate those risks.

    Identify the Components of Your Cloud Security Architecture Research & Tools

    Start Here – read the Executive Brief

    Read our concise Executive Brief to find out why you should create a cloud security architecture with security at the forefront, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Cloud security alignment analysis

    Explore how the cloud changes and whether your enterprise is ready for the shift to the cloud.

    • Identify the Components of Your Cloud Security Architecture – Phase 1: Cloud Security Alignment Analysis
    • Cloud Security Architecture Workbook

    2. Business-critical workload analysis

    Analyze the workloads that will migrated to the cloud. Consider the various domains of security in the cloud, considering the cloud’s unique risks and challenges as they pertain to your workloads.

    • Identify the Components of Your Cloud Security Architecture – Phase 2: Business-Critical Workload Analysis

    3. Cloud security architecture mapping

    Map your risks to services in a reference model from which to build a robust launch point for your architecture.

    • Identify the Components of Your Cloud Security Architecture – Phase 3: Cloud Security Architecture Mapping
    • Cloud Security Architecture Archive Document
    • Cloud Security Architecture Reference Model (Visio)
    • Cloud Security Architecture Reference Model (PDF)

    4. Cloud security strategy planning

    Map your risks to services in a reference architecture to build a robust roadmap from.

    • Identify the Components of Your Cloud Security Architecture – Phase 4: Cloud Security Strategy Planning
    • Cloud Security Architecture Communication Deck

    Infographic

    Workshop: Identify the Components of Your Cloud Security Architecture

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Cloud Security Alignment Analysis

    The Purpose

    Understand your suitability and associated risks with your workloads as they are deployed into the cloud.

    Key Benefits Achieved

    An understanding of the organization’s readiness and optimal service level for cloud security.

    Activities

    1.1 Workload Deployment Plan

    1.2 Cloud Suitability Questionnaire

    1.3 Cloud Risk Assessment

    1.4 Cloud Suitability Analysis

    Outputs

    Workload deployment plan

    Determined the suitability of the cloud for your workloads

    Risk assessment of the associated workloads

    Overview of cloud suitability

    2 Business-Critical Workload Analysis

    The Purpose

    Explore your business-critical workloads and the associated controls and mitigating services to secure them.

    Key Benefits Achieved

    Address NIST 800-53 security controls and the appropriate security services that can mitigate the risks appropriately.

    Activities

    2.1 “A” Environment Analysis

    2.2 “B” Environment Analysis

    2.3 “C” Environment Analysis

    2.4 Prioritized Security Controls

    2.5 Effort and Risk Dashboard Overview

    Outputs

    NIST 800-53 control mappings and relevancy

    NIST 800-53 control mappings and relevancy

    NIST 800-53 control mappings and relevancy

    Prioritized security controls based on risk and environmental makeup

    Mitigating security services for controls

    Effort and Risk Dashboard

    3 Cloud Security Architecture Mapping

    The Purpose

    Identify security services to mitigate challenges posed by the cloud in various areas of security.

    Key Benefits Achieved

    Comprehensive list of security services, and their applicability to your network environment. Documentation of your “current” state of cloud security.

    Activities

    3.1 Cloud Security Control Mapping

    3.2 Cloud Security Architecture Reference Model Mapping

    Outputs

    1. Cloud Security Architecture Archive Document to codify and document each of the associated controls and their risk levels to security services

    2. Mapping of the codified controls onto Info-Tech’s Cloud Security Architecture Reference Model for clear security prioritization

    4 Cloud Security Strategy Planning

    The Purpose

    Prepare a communication deck for executive stakeholders to socialize them to the state of your cloud security initiatives and where you still have to go.

    Key Benefits Achieved

    A roadmap for improving security in the cloud.

    Activities

    4.1 Cloud Security Strategy Considerations

    4.2 Cloud Security Architecture Communication Deck

    Outputs

    Consider the additional security considerations of the cloud for preparation in the communication deck.

    Codify all your results into an easily communicable communication deck with a clear pathway for progression and implementation of security services to mitigate cloud risks.

    Cost-Optimize Your Security Budget

    • Buy Link or Shortcode: {j2store}250|cart{/j2store}
    • member rating overall impact: 9.0/10 Overall Impact
    • member rating average dollars saved: $2,078 Average $ Saved
    • member rating average days saved: 2 Average Days Saved
    • Parent Category Name: Security Strategy & Budgeting
    • Parent Category Link: /security-strategy-and-budgeting
    • The security budget has been slashed and the team needs to do more with less.
    • Mitigating risk is still the top priority, only now we need to reassess effectiveness and efficiency to ensure we are getting the greatest level of protection for the least amount of money.

    Our Advice

    Critical Insight

    A cost-optimized security budget is one that has the greatest impact on risk for the least amount of money spent.

    Impact and Result

    • Focus on business needs and related risks. Review the risk-reduction efficacy of your people, processes, and technology and justify what can be cut and what must stay.
    • Info-Tech will guide you through this process, and by the end of this blueprint you will have a cost-optimized security budget and an executive presentation to explain your revised spending.

    Cost-Optimize Your Security Budget Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should cost-optimize your security budget, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Cost-optimize your technology and managed services

    This phase will help you assess the efficacy of your current technology and service providers.

    • Threat and Risk Assessment Tool
    • In-House vs. Outsourcing Decision-Making Tool

    2. Cost-optimize your staffing

    This phase will help you assess if layoffs are necessary.

    • Security Employee Layoff Selection Tool

    3. Cost-optimize your security strategy

    This phase will help you revise the pending process-based initiatives in your security strategy.

    • Security Cost Optimization Workbook
    • Security Cost Optimization Executive Presentation
    [infographic]

    Design and Implement a Business-Aligned Security Program

    • Buy Link or Shortcode: {j2store}368|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Security Strategy & Budgeting
    • Parent Category Link: /security-strategy-and-budgeting
    • You need to build a security program that enables business services and secures the technology that makes them possible.
    • Building an effective, business-aligned security program requires that you coordinate many components, including technologies, processes, organizational structures, information flows, and behaviors.
    • The program must prioritize the right capabilities, and support its implementation with clear accountabilities, roles, and responsibilities.

    Our Advice

    Critical Insight

    • Common security frameworks focus on operational controls rather than business value creation, are difficult to convey to stakeholders, and provide little implementation guidance.
    • A security strategy can provide a snapshot of your program, but it won’t help you modernize or transform it, or align it to meet emerging business requirements.
    • There is no unique, one-size-fits-all security program. Each organization has a distinct character and profile and differs from others in several critical respects.

    Impact and Result

    Tailor your security program according to what makes your organization unique.

    • Analyze critical design factors to determine and refine the scope of your security program and prioritize core program capabilities.
    • Identify program accountabilities, roles, and responsibilities.
    • Build an implementation roadmap to ensure its components work together in a systematic way to meet business requirements.

    Design and Implement a Business-Aligned Security Program Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Design and Implement a Business-Aligned Security Strategy – A step-by-step guide on how to understand what makes your organization unique and design a security program with capabilities that create business value.

    This storyboard will help you lay foundations for your security program that will inform future security program decisions and give your leadership team the information they need to support your success. You will evaluate design factors that make your organization unique, prioritize the security capabilities to suit, and assess the maturity of key security program components including security governance, security strategy, security architecture, service design, and service metrics.

    • Design and Implement a Business-Aligned Security Program Storyboard

    2. Security Program Design Tool – Tailor the security program to what makes your organization unique to ensure business-alignment.

    Use this Excel workbook to evaluate your security program against ten key design factors. The tool will produce a goals cascade that shows the relationship between business and security goals, a prioritized list of security capabilities that align to business requirements, and a list of program accountabilities.

    • Security Program Design Tool

    3. Security Program Design and Implementation Plan – Assess the current state of different security program components, plan next steps, and communicate the outcome to stakeholders.

    This second Excel workbook will help you conduct a gap analysis on key security program components and identify improvement initiatives. You can then use the Security Program Design and Implementation Plan to collect results from the design and implementation tools and draft a communication deck.

    • Security Program Implementation Tool
    • Security Program Design and Implementation Plan

    Infographic

    Workshop: Design and Implement a Business-Aligned Security Program

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Initial Security Program Design

    The Purpose

    Determine the initial design of your security program.

    Key Benefits Achieved

    An initial prioritized list of security capabilities that aligns with enterprise strategy and goals.

    Activities

    1.1 Review Info-Tech diagnostic results.

    1.2 Identify project context.

    1.3 Identify enterprise strategy.

    1.4 Identify enterprise goals.

    1.5 Build a goal cascade.

    1.6 Assess the risk profile.

    1.7 Identify IT-related issues.

    1.8 Evaluate initial program design.

    Outputs

    Stakeholder satisfaction with program

    Situation, challenges, opportunities

    Initial set of prioritized security capabilities

    Initial set of prioritized security capabilities

    Initial set of prioritized security capabilities

    Initial set of prioritized security capabilities

    Initial set of prioritized security capabilities

    Initial set of prioritized security capabilities

    2 Refine Security Program Capabilities

    The Purpose

    Refine the design of your security program.

    Key Benefits Achieved

    A refined, prioritized list of security capabilities that reflects what makes your organization unique.

    Activities

    2.1 Gauge threat landscape.

    2.2 Identify compliance requirements.

    2.3 Categorize the role of IT.

    2.4 Identify the sourcing model.

    2.5 Identify the IT implementation model.

    2.6 Identify the tech adoption strategy.

    2.7 Refine the scope of the program.

    Outputs

    Refined set of prioritized security capabilities

    Refined set of prioritized security capabilities

    Refined set of prioritized security capabilities

    Refined set of prioritized security capabilities

    Refined set of prioritized security capabilities

    Refined set of prioritized security capabilities

    Refined set of prioritized security capabilities

    3 Security Program Gap Analysis

    The Purpose

    Finalize security program design.

    Key Benefits Achieved

    Key accountabilities to support the security program

    Gap analysis to produce an improvement plan

    Activities

    3.1 Identify program accountabilities.

    3.2 Conduct program gap analysis.

    3.3 Prioritize initiatives.

    Outputs

    Documented program accountabilities.

    Security program gap analysis

    Security program gap analysis

    4 Roadmap and Implementation Plan

    The Purpose

    Create and communicate an improvement roadmap for the security program.

    Key Benefits Achieved

    Security program design and implementation plan to organize and communicate program improvements.

    Activities

    4.1 Build program roadmap

    4.2 Finalize implementation plan

    4.3 Sponsor check-in

    Outputs

    Roadmap of program improvement initiatives

    Roadmap of program improvement initiatives

    Communication deck for program design and implementation

    Further reading

    Design a Business-Aligned Security Program

    Focus on business value first.

    EXECUTIVE BRIEF

    Analyst Perspective

    Business alignment is no accident.

    Michel Hébert

    Security leaders often tout their choice of technical security framework as the first and most important program decision they make. While the right framework can help you take a snapshot of the maturity of your program and produce a quick strategy and roadmap, it won’t help you align, modernize, or transform your program to meet emerging business requirements.

    Common technical security frameworks focus on operational controls rather than business services and value creation. They are difficult to convey to business stakeholders and provide little program management or implementation guidance.

    Focus on business value first, and the security services that enable it. Your organization has its own distinct character and profile. Understand what makes your organization unique, then design and refine the design of your security program to ensure it supports the right capabilities. Next, collaborate with stakeholders to ensure the right accountabilities, roles, and responsibilities are in place to support the implementation of the security program.

    Michel Hébert
    Research Director, Security & Privacy
    Info-Tech Research Group

    Executive Summary

    Your Challenge

    Common Obstacles

    Info-Tech’s Approach

    • You need to build a security program that enables business services and secures the technology that makes them possible.
    • Building an effective, business-aligned security program requires that you coordinate many components, including technologies, processes, organizational structures, information flows, and behaviors.
    • The program must prioritize the right capabilities, and support its implementation with clear accountabilities, roles, and responsibilities.
    • Common security frameworks focus on operational controls rather than business value creation, are difficult to convey to stakeholders, and provide little implementation guidance.
    • A security strategy can provide a snapshot of your program, but it won’t help you modernize or transform it, or align it to meet emerging business requirements.
    • There is no unique, one-size-fits-all security program. Each organization has a distinct character and profile and differs from others in several critical respects.

    Tailor your security program according to what makes your organization unique.

    • Analyze critical design factors to determine and refine the design of your security program and prioritize core program capabilities.
    • Identify program accountabilities, roles, and responsibilities.
    • Build an implementation roadmap to ensure its components work together in a systematic way to meet business requirements.

    Info-Tech Insight

    You are a business leader who supports business goals and mitigates risk. Focus first on business value and the security services that enable it, not security controls.

    Your challenge

    The need for a solid and responsive security program has never been greater.

    • You need to build a security program that enables business services and secures the technology that makes them possible.
    • Building an effective, business-aligned security program requires that you coordinate many components, including technologies, processes, organizational structures, information flows, and behaviors.
    • The program must prioritize the right capabilities, and support its implementation with clear accountabilities, roles, and responsibilities.
    • You must communicate effectively with stakeholders to describe the risks the organization faces, their likely impact on organizational goals, and how the security program will mitigate those risks and support the creation of business value.
    • Ransomware is a persistent threat to organizations worldwide across all industries.
    • Cybercriminals deploying ransomware are evolving into a growing and sophisticated criminal ecosystem that will continue to adapt to maximize its profits.

    • Critical infrastructure is increasingly at risk.
    • Malicious agents continue to target critical infrastructure to harm industrial processes and the customers they serve State-sponsored actors are expected to continue to target critical infrastructure to collect information through espionage, pre-position in case of future hostilities, and project state power.

    • Disruptive technologies bring new threats.
    • Malicious actors increasingly deceive or exploit cryptocurrencies, machine learning, and artificial intelligence technologies to support their activities.

    Sources: CCCS (2023), CISA (2023), ENISA (2023)

    Your challenge

    Most security programs are not aligned with the overall business strategy.

    50% Only half of leaders are framing the impact of security threats as a business risk.

    49% Less than half of leaders align security program cost and risk reduction targets with the business.

    57% Most leaders still don’t regularly review security program performance of the business.

    Source: Tenable, 2021

    Common obstacles

    Misalignment is hurting your security program and making you less influential.

    Organizations with misaligned security programs have 48% more security incidents...

    …and the cost of their data breaches are 40% higher than those with aligned programs.

    37% of stakeholders still lack confidence in their security program.

    54% of senior leaders still doubt security gets the goals of the organization.

    Source: Frost & Sullivan, 2019
    Source: Ponemon, 2023

    Common obstacles

    Common security frameworks won’t help you align your program.

    • Common security frameworks focus on operational controls rather than business value creation, are difficult to convey to stakeholders, and provide little implementation guidance.
    • A security strategy based on the right framework can provide a snapshot of your program, but it won’t help you modernize, transform, or align your program to meet emerging business requirements.
    • The lack of guidance leads to a lack of structure in the way security services are designed and managed, which reduces service quality, increases security friction, and reduces business satisfaction.

    There is no unique, one-size-fits-all security program.

    • Each organization has a distinct character and profile and differs from others in several critical respects. The security program for a cloud-first, DevOps environment must emphasize different capabilities and accountabilities than one for an on-premise environment and a traditional implementation model.

    Info-Tech’s approach

    You are a business leader who supports business goals and mitigates risk.

    • Understand what makes your organization unique, then design and refine a security program with capabilities that create business value.
    • Next, collaborate with stakeholders to ensure the right accountabilities, roles, and responsibilities are in place, and build an implementation roadmap to ensure its components work together over time.

    Security needs to evolve as a business strategy.

    • Laying the right foundations for your security program will inform future security program decisions and give your leadership team the information they need to support your success. You can do it in two steps:
      • Evaluate the design factors that make your organization unique and prioritize the security capabilities to suit. Info-Tech’s approach is based on the design process embedded in the latest COBIT framework.
      • Review the key components of your security program, including security governance, security strategy, security architecture, service design, and service metrics.

    If you build it, they will come

    “There's so much focus on better risk management that every leadership team in every organization wants to be part of the solution.

    If you can give them good data about what things they really need to do, they will work to understand it and help you solve the problem.”

    Dan Bowden, CISO, Sentara Healthcare (Tenable)

    Design a Business-Aligned Security Program

    The image contains a screenshot of how to Design a business-aligned security program.


    Choose your own adventure

    This blueprint is ideal for new CISOs and for program modernization initiatives.

    1. New CISO

    “I need to understand the business, prioritize core security capabilities, and identify program accountabilities quickly.”

    2. Program Renewal

    “The business is changing, and the threat landscape is shifting. I am concerned the program is getting stale.”

    Use this blueprint to understand what makes your organization unique:

    1. Prioritize security capabilities.
    2. Identify program accountabilities.
    3. Plan program implementation.

    If you need a deep dive into governance, move on to a security governance and management initiative.

    3. Program Update

    “I am happy with the fundamentals of my security program. I need to assess and improve our security posture.”

    Move on to our guidance on how to Build an Information Security Strategy instead.

    Info-Tech’s methodology for security program design

    Define Scope of
    Security Program

    Refine Scope of
    Security Program

    Finalize Security
    Program Design

    Phase steps

    1.1 Identify enterprise strategy

    1.2 Identify enterprise goals

    1.3 Assess the risk profile

    1.4 Identify IT-related issues

    1.5 Define initial program design

    2.1 Gage threats and compliance

    2.2 Assess IT role and sourcing

    2.3 Assess IT implementation model

    2.4 Assess tech adoption strategy

    2.5 Refine program design

    3.1 Identify program accountabilities

    3.2 Define program target state

    3.3 Build program roadmap

    Phase outcomes

    • Initial security program design
    • Refined security program design
    • Prioritized set of security capabilities
    • Program accountabilities
    • Program gap closure initiatives

    Tools

    Insight Map

    You are a business leader first and a security leader second

    Technical security frameworks are static and focused on operational controls and standards. They belong in your program’s solar system but not at its center. Design your security program with business value and the security services that enable it in mind, not security controls.

    There is no one-size-fits-all security program
    Tailor your security program to your organization’s distinct profile to ensure the program generates value.

    Lay the right foundations to increase engagement
    Map out accountabilities, roles, and responsibilities to ensure the components of your security program work together over time to secure and enable business services.

    If you build it, they will come
    Your executive team wants to be part of the solution. If you give them reliable data for the things they really need to do, they will work to understand and help you solve the problem.

    Blueprint deliverables

    Info-Tech supports project and workshop activities with deliverables to help you accomplish your goals and accelerate your success.

    Security Program Design Tool

    Tailor the security program to what makes your organization unique to ensure alignment.

    The image contains a screenshot of the Security Program Design Tool.

    Security Program Implementation Tool

    Assess the current state of different security program components and plan next steps.


    SecurityProgram Design and Implementation Plan

    Communicate capabilities, accountabilities, and implementation initiatives.

    The image contains a screenshot of the Security Program Design and Implementation Plan.

    Key deliverable

    Security Program Design and Implementation Plan

    The design and implementation plan captures the key insights your work will generate, including:

    • A prioritized set of security capabilities aligned to business requirements.
    • Security program accountabilities.
    • Security program implementation initiatives.

    Blueprint benefits

    IT Benefits

    Business Benefits

    • Laying the right foundations for your security program will:
      • Inform the future security governance, security strategy, security architecture, and service design decisions you need to make.
      • Improve security service design and service quality, reduce security friction, and increase business satisfaction with the security program.
      • Help you give your leadership team the information they need to support your success.
      • Improve the standing of the security program with business leaders.
    • Organizations with a well-aligned security program:
      • Improve security risk management, performance measurement, resource management, and value delivery.
      • Lower rates of security incidents and lower-cost security breaches.
      • Align costs, performance, and risk reduction objectives with business needs.
      • Are more satisfied with their security program.

    Measure the value of using Info-Tech’s approach

    Assess the effectiveness of your security program with a risk-based approach.

    Deliverable

    Challenge

    Security Program Design

    • Prioritized set of security capabilities
    • Program accountabilities
    • Devise and deploy an approach to gather business requirements, identify and prioritize relevant security capabilities, and assign program accountabilities.
    • Cost and Effort : 2 FTEs x 90 days x $130,000/year

    Program Assessment and Implementation Plan

    • Security program assessment
    • Roadmap of gap closure initiatives
    • Devise and deploy an approach to assess the current state of your security program, identify gap closure or improvement initiatives, and build a transformation roadmap.
    • Cost and Effort : 2 FTEs x 90 days x $130,000/year

    Measured Value

    • Using Info-Tech’s best practice methodology will cut the cost and effort in half.
    • Savings: 2 FTEs x 45 days x $130,000/year = $65,000

    Measure the impact of your project

    Use Info-Tech diagnostics before and after the engagement to measure your progress.

    • Info-Tech diagnostics are standardized surveys that produce historical and industry trends against which to benchmark your organization.
    • Run the Security Business Satisfaction and Alignment diagnostic now, and again in twelve months to assess business satisfaction with the security program and measure the impact of your program improvements.
    • Reach out to your account manager or follow the link to deploy the diagnostic and measure your success. Diagnostics are included in your membership.

    Inform this step with Info-Tech diagnostic results

    • Info-Tech diagnostics are standardized surveys that accelerate the process of gathering and analyzing pain point data.
    • Diagnostics also produce historical and industry trends against which to benchmark your organization.
    • Reach out to your account manager or follow the links to deploy some or all these diagnostics to validate your assumptions. Diagnostics are included in your membership.

    Governance & Management Maturity Scorecard
    Understand the maturity of your security program across eight domains.
    Audience: Security Manager

    Security Business Satisfaction and Alignment Report
    Assess the organization’s satisfaction with the security program.
    Audience: Business Leaders

    CIO Business Vision
    Assess the organization’s satisfaction with IT services and identify relevant challenges.
    Audience: Business Leaders

    Executive Brief Case Study

    INDUSTRY: Higher Education

    SOURCE: Interview

    Building a business-aligned security program

    Portland Community College (PCC) is the largest post-secondary institution in Oregon and serves more than 50,000 students each year. The college has a well-established information technology program, which supports its education mission in four main campuses and several smaller centers.

    PCC launched a security program modernization effort to deal with the evolving threat landscape in higher education. The CISO studied the enterprise strategy and goals and reviewed the college’s risk profile and compliance requirements. The exercise helped the organization prioritize security capabilities for the renewal effort and informed the careful assessment of technical controls in the current security program.

    Results

    Laying the right foundations for the security program helped the security function understand how to provide the organization with a clear report of its security posture. The CISO now reports directly to the board of directors and works with stakeholders to align cost, performance, and risk reduction objectives with the needs of the college.

    The security program modernization effort prioritized several critical design factors

    • Enterprise Strategy
    • Enterprise Goals
    • IT Risk Profile
    • IT-Related Issues
    • IT Threat Landscape
    • Compliance Requirements

    Info-Tech offers various levels of support to best suit your needs

    DIY Toolkit

    “Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful.”

    Guided Implementation

    “Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track.”

    Workshop

    “We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place.”

    Consulting

    “Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project.”

    Diagnostics and consistent frameworks used throughout all four options

    Guided Implementation

    What does a typical GI on this topic look like?

    Phase 1 Phase 2 Phase 3

    Call #1:
    Scope requirements, objectives, and specific challenges.

    Call #2:
    Define business context, assess risk profile, and identify existing security issues.

    Define initial design of security program.

    Call #3:
    Evaluate threat landscape and compliance requirements.

    Call #4:
    Analyze the role of IT, the security sourcing model, technology adoption, and implementation models.

    Refine the design of the security program.

    Call #5:
    Identify program accountabilities.

    Call #6:
    Design program target state and draft security program implementation plan.

    A Guided Implementation (GI) is a series of calls with an Info-Tech analyst to help implement our best practices in your organization.

    A typical GI is 4 to 6 calls over the course of 6 months.

    Workshop Overview

    Contact your account representative for more information.
    workshops@infotech.com 1-888-670-8889

    Day 1 Day 2 Day 3 Day 4 Day 5

    Initial Security
    Program Design

    Refine Security
    Program Design

    Security Program
    Gap Analysis

    Roadmap and Implementation Plan

    Next Steps and
    Wrap-Up (offsite)

    Activities

    1.1.0 Review Info-Tech diagnostic results

    1.1.1 Identify project context

    1.1.2 Identify enterprise strategy

    1.2.1 Identify enterprise goals

    1.2.2 Build a goals cascade

    1.3 Assess the risk profile

    1.4 Identify IT-related issues

    1.5 Evaluate initial program design

    2.1.1 Gauge threat landscape

    2.1.2 Identify compliance requirements

    2.2.1 Categorize the role of IT

    2.2.2 Identify the sourcing model

    2.3.1 Identify the IT implementation model

    2.4.1 Identify the tech adoption strategy

    2.5.1 Refine the design of the program

    3.1 Identify program accountabilities

    3.2.1 Conduct program gap analysis

    3.2.2 Prioritize initiatives

    3.3.1 Build program roadmap

    3.3.2 Finalize implementation plan

    3.3.3 Sponsor check-in

    4.1 Complete in-progress deliverables from previous four days

    4.2 Set up review time for workshop deliverables and to discuss next steps

    Deliverables

    1. Project context
    2. Stakeholder satisfaction feedback on security program
    3. Initial set of prioritized security capabilities
    1. Refined set of prioritized security capabilities
    1. Documented program accountabilities
    2. Security program gap analysis
    1. Roadmap of initiatives
    2. Communication deck for program design and implementation
    1. Completed security program design
    2. Security program design and implementation plan

    Customize your journey

    The security design blueprint pairs well with security governance and security strategy.

    • The prioritized set of security capabilities you develop during the program design project will inform efforts to develop other parts of your security program, like the security governance and management program and the security strategy.
    • Work with your member services director, executive advisor, or technical counselor to scope the journey you need. They will work with you to align the subject matter experts to support your roadmap and workshops.

    Workshop
    Days 1 and 2

    Workshop
    Days 3 and 4

    Security Program Design Factors

    Security Program Gap Analysis or
    Security Governance and Management

    Understand Common IT Contract Provisions to Negotiate More Effectively

    • Buy Link or Shortcode: {j2store}234|cart{/j2store}
    • member rating overall impact: 9.5/10 Overall Impact
    • member rating average dollars saved: $31,716 Average $ Saved
    • member rating average days saved: 10 Average Days Saved
    • Parent Category Name: Vendor Management
    • Parent Category Link: /vendor-management
    • Contract reviews are tedious, and reviewers may lack the skills and experience to effectively complete the process.
    • Vendors have a repository of contract terms and conditions that are road-tested and often biased in their favor.
    • Vendors change their contracts frequently through hyperlinked documents without notifying customers, and the onus is on you to stay compliant.

    Our Advice

    Critical Insight

    • Focus on the terms and conditions, not just the price. Too often, organizations focus on the price contained within their contracts, neglecting to address core terms and conditions that can end up costing multiples of the initial price.
    • Lawyers can’t ensure you get the best business deal. Lawyers tend to look at general terms and conditions for legal risk and may not understand IT-specific components and business needs.

    Impact and Result

    • Align contract language to meet IT and business needs.
    • Communicate more effectively with Legal and the vendors.
    • Identify and reduce contractual and performance risk.
    • Understand the relationship between contract provisions.
    • Negotiate more effectively.

    Understand Common IT Contract Provisions to Negotiate More Effectively Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should employ a systematic process for reviewing contracts, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Assess contract terms and conditions

    Review and assess your IT contracts for vendor-biased terms and conditions, and gain tips for getting vendors to take on their fair share of risk and become more accountable.

    • Contract Review Tool
    • Contract Playbook
    [infographic]

    Workshop: Understand Common IT Contract Provisions to Negotiate More Effectively

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Assess Contract Terms and Conditions

    The Purpose

    Understand IT contract clauses, improve risk identification, and be more effective at negotiating contract terms.

    Key Benefits Achieved

    Increased awareness of how contract provisions relate to each other.

    Demystification of legalese and legal concepts.

    Increased ability to seek assistance from internal parties (e.g. Legal, Risk, and Procurement).

    Activities

    1.1 Review the Contract Review Tool.

    1.2 Review the Contract Playbook template.

    1.3 Review 35 contract provisions and reinforce key learnings with exercises (spread across three days)

    Outputs

    Partial completion of the template

    Exercise results and debrief

    Secure Your Hybrid Workforce

    • Buy Link or Shortcode: {j2store}271|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Secure Cloud & Network Architecture
    • Parent Category Link: /secure-cloud-network-architecture
    • Many IT and security leaders struggle to cope with the challenges associated with an hybrid workforce and how best to secure it.
    • Understanding the main principles of zero trust: never trust, always verify, assume breach, and verify explicitly.
    • How to go about achieving a zero trust framework.
    • Understanding the premise of SASE as it pertains to a hybrid workforce.

    Our Advice

    Critical Insight

    Securing your hybrid workforce should be an opportunity to get started on the zero trust journey. Realizing the core features needed to achieve this will assist you determine which of the options is a good fit for your organization.

    Impact and Result

    Every organization's strategy to secure their hybrid workforce should include introducing zero trust principles in certain areas. Our unique approach:

    • Assess the suitability of SASE/SSE and zero trust.
    • Present capabilities and feature benefits.
    • Procure SASE product and/or build a zero trust roadmap.

    Secure Your Hybrid Workforce Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Secure Your Hybrid Workforce Deck – The purpose of the storyboard is to provide a detailed description of the steps involved in securing your hybrid workforce with zero trust.

    The storyboard contains two easy-to-follow steps on securing your hybrid workforce with zero trust, from assessing the suitability of SASE/SSE to taking a step in building a zero trust roadmap.

    • Secure Your Hybrid Workforce – Phases 1-2

    2. Suitability Assessment Tool – A tool to identify whether SASE/SSE or a zero trust roadmap is a better fit for your organization.

    Use this tool to identify your next line of action in securing your hybrid workforce by assessing key components that conforms to the ideals and principles of Zero Trust.

    • Zero Trust - SASE Suitability Assessment Tool

    3. RFP Template – A document to guide you through requesting proposals from vendors.

    Use this document to request proposals from select vendors.

    • Request for Proposal (RFP) Template
    [infographic]

    Further reading

    Secure Your Hybrid Workforce

    SASE as a driver to zero trust.

    Analyst Perspective

    Consolidate your security and network.

    Remote connections like VPNs were not designed to be security tools or to have the capacity to handle a large hybrid workforce; hence, organizations are burdened with implementing controls that are perceived to be "security solutions." The COVID-19 pandemic forced a wave of remote work for employees that were not taken into consideration for most VPN implementations, and as a result, the understanding of the traditional network perimeter as we always knew it has shifted to include devices, applications, edges, and the internet. Additionally, remote work is here to stay as recruiting talent in the current market means you must make yourself attractive to potential hires.

    The shift in the network perimeter increases the risks associated with traditional VPN solutions as well as exposing the limitations of the solution. This is where zero trust as a principle introduces a more security-focused strategy that not only mitigates most (if not all) of the risks, but also eliminates limitations, which would enhance the business and improve customer/employee experience.

    There are several ways of achieving zero trust maturity, and one of those is SASE, which consolidates security and networking to better secure your hybrid workforce as implied trust is thrown out of the window and verification of everything becomes the new normal to defend the business.

    This is a picture of Victor Okorie

    Victor Okorie
    Senior Research Analyst, Security and Privacy
    Info-Tech Research Group

    Executive Summary

    Your Challenge

    CISOs are looking to zero trust to fill the gaps associated with their traditional remote setup as well as to build an adaptable security strategy. Some challenges faced include:

    • Understanding the main principles of zero trust: never trust, always verify, assume breach, and verify explicitly.
    • Understanding how to achieve a zero trust framework.
    • Understanding the premise of SASE as it pertains to a hybrid workforce.

    Common Obstacles

    The zero trust journey may seem tedious because of a few obstacles like:

    • Knowing what the principle is all about and the components that align with it.
    • Knowing where to start. Due to the lack of a standardized path for the zero trust journey, going about the journey can be confusing.
    • Not having a uniform definition of what makes up a SASE solution as it is heavily dependent on vendors.

    Info-Tech's Approach

    Info-Tech provides a three-service approach to helping organizations better secure their hybrid workforce.

    • Understand your current, existing technological capabilities and challenges with your hybrid infrastructure, and prioritize those challenges.
    • Gain insight into zero trust and SASE as a mitigation/control/tool to those challenges.
    • Identify the SASE features that are relevant to your needs and a source guide for a SASE vendor.

    Info-Tech Insight

    Securing your hybrid workforce should be an opportunity to get started on the zero trust journey. Realizing the core features needed to achieve this will assist you in determining which of the options is a good fit for your organization.

    Turn your challenges into opportunities

    Hybrid workforce is the new normal

    The pandemic has shown there is no going back to full on-prem work, and as such, security should be looked at differently with various considerations in mind.

    Understand that current hybrid solutions are susceptible to various forms of attack as the threat attack surface area has now expanded with users, devices, applications, locations, and data. The traditional perimeter as we know it has expanded beyond just the corporate network, and as such, it needs a more mature security strategy.

    Onboarding and offboarding have been done remotely, and with some growth recorded, the size of companies has also increased, leading to a scaling issue.

    Employees are now demanding remote work capabilities as part of contract negotiation before accepting a job.

    Attacks have increased far more quickly during the pandemic, and all indications point to them increasing even more.

    Scarce available security personnel in the job market for hire.

    Reality Today

    This image is a circle graph and 67% of it is coloured with the number 67% in the middle of the graph

    The number of breach incidents by identity theft.
    Source: Security Magazine, 2022.

    This image is a circle graph and 78% of it is coloured with the number 78% in the middle of the graph

    IT security teams want to adopt zero trust.
    Source: Cybersecurity Insiders, 2019.

    Reduce the risks of remote work by using zero trust

    $1.07m

    $1.76m

    235

    Increase in breaches related to remote work

    Cost difference in a breach where zero trust is deployed

    Days to identify a breach

    The average cost of a data breach where remote work was a factor rose by $1.07 million in 2021. COVID-19 brought about rapid changes in organizations, and digital transformation changes curbed some of its excesses. Organizations that did not make any digital transformation changes reported a $750,000 higher costs compared to global average.

    The average cost of a breach in an organization with no zero trust deployed was $5.04 million in 2021 compared to the average cost of a breach in an organization with zero trust deployed of $3.28 million. With a difference of $1.76 million, zero trust makes a significant difference.

    Organizations with a remote work adoption rate of 50% took 235 days to identify a breach and 81 days to contain that breach – this is in comparison to the average of 212 days to identify a breach and 75 days to contain that breach.

    Source: IBM, 2021.

    Network + Security = SASE

    What exactly is a SASE product?

    The convergence and consolidation of security and network brought about the formation of secure access service edge (SASE – pronounced like "sassy"). Digital transformation, hybrid workforce, high demand of availability, uninterrupted access for employees, and a host of other factors influenced the need for this convergence that is delivered as a cloud service.

    The capabilities of a SASE solution being delivered are based on certain criteria, such as the identity of the entity (users, devices, applications, data, services, location), real-time context, continuous assessment and verification of risk and "trust" throughout the lifetime of a session, and the security and compliance policies of the organization.

    SASE continuously identifies users and devices, applies security based on policy, and provides secure access to the appropriate and requested application or data regardless of location.

    image contains a list of the SASE Network Features and Security Features. the network Features are: WAN optimization; SD WAN; CDN; Network-as-a-service. The Security Features are: CASB; IDPS; ZTNA/VPN; FWaaS; Browser isolation; DLP; UEBA; Secure web gateway; Sandboxing

    Current Approach

    The traditional perimeter security using the castle and moat approach is depicted in the image here. The security shields valuable resources from external attack; however, it isn't foolproof for all kinds of external attacks. Furthermore, it does not protect those valuable resources from insider threat.

    This security perimeter also allows for lateral movement when it has been breached. Access to these resources is now considered "trusted" solely because it is now behind the wall/perimeter.

    This approach is no longer feasible in our world today where both external and internal threats pose continuous risk and need to be contained.

    Determine the suitability of SASE and zero trust

    The Challenge:

    Complications facing traditional infrastructure

    • Increased hybrid workforce
    • Regulatory compliance
    • Limited Infosec personnel
    • Poor threat detection
    • Increased attack surface

    Common vulnerabilities in traditional infrastructure

    • MITM attack
    • XSS attack
    • Session hijacking
    • Trust-based model
    • IP spoofing
    • Brute force attack
    • Distributed denial of service
    • DNS hijacking
    • Latency issues
    • Lateral movement once connection is established

    TRADITIONAL INFRASTRUCTURE

    NETWORK

    SECURITY

    AUTHENTICATION

    IDENTITY

    ACCESS

    • MPLS
    • Corporate Network
    • Antivirus installed
    • Traditional Firewall
    • Intrusion Detection and Prevention System
    • Allow and Deny rules
    • Businesses must respond to consumer requests to:
    • LDAP
    • AAA
    • Immature password complexity
    • Trusted device with improperly managed endpoint protection.
    • Little or no DNS security
    • Web portal (captive)
    • VPN client

    Candidate Solutions

    Proposed benefits of SASE

    • Access is only granted to the requested resource
    • Consolidated network and security as a service
    • Micro-segmentation on application and gateway
    • Adopts a zero trust security posture for all access
    • Managed detection and response
    • Uniform enforcement of policy
    • Distributed denial of service shield

    SASE

    NETWORK

    SECURITY

    AUTHENTICATION

    IDENTITY

    ACCESS

    • Software defined – WAN
    • Content delivery network
    • WAN optimization
    • Network-as-a-service
    • Firewall-as-a-service/NGFW
    • Zero trust network access
    • Endpoint detection & response
    • Secure web gateway
    • Cloud access security broker
    • Data loss prevention
    • Remote browser isolation
    • Multifactor authentication
    • Context-based security policy for authentication
    • Authorization managed with situational awareness and real-time risk analytics
    • Continuous verification throughout an access request lifecycle
    • Zero trust identity on users, devices, applications, and data.
    • Strong password complexity enforced
    • Privilege access management
    • Secure internet access
    • SASE client

    ZERO TRUST

    TENETS OF ZERO TRUST

    ZERO TRUST PILLARS

    • Continuous, dynamic authentication and verification
    • Principle of least privilege
    • Always assume a breach
    • Implement the tenets of zero trust across the following domains of your environment:
      • IDENTITY
      • APPLICATION
      • NETWORK
      • DEVICES
      • DATA

    Proposed benefits of zero trust

    • Identify and protect critical and non-critical resources in accordance with business objectives.
    • Produce initiatives that conform to the ideals of zero trust and are aligned with the corresponding pillars above.
    • Formulate policies to protect resources and aid segmentation.

    Info-Tech Insight

    Securing your hybrid workforce should be an opportunity to get started on the zero trust journey. Realizing the core features needed to achieve this will help you determine which of the options is a good fit for your organization.

    Measure the value of using Info-Tech's approach

    IT and business value

    PHASE 1

    PHASE 2

    Assess the benefits of adopting SASE or zero trust

    Vendors will try to control the narrative in terms of what they can do for you, but it's time for you to control the narrative and identify pain points to IT and the business, and with that, to understand and define what the vendor solution can do for you.

    Short-term benefits

    • Gain awareness of your zero trust readiness.
    • Embed a zero trust mindset across your architecture.
    • Control the narrative of what SASE brings to your organization.

    Long-term benefits

    • Identified controls to mitigate risks with current architecture while on a zero trust journey.
    • Improved security posture that reduces risk by increasing visibility into threats and user connections.
    • Reduced CapEx and OpEx due to the scalability, low staffing requirements, and improved time to respond to threats using a SASE or SSE solution.

    Determine SASE cost factors

    IT and business value

    Info-Tech Insight

    IT leaders need to examine different areas of their budget and determine how the adoption of a SASE solution could influence several areas of their budget breakdown.

    Determining the SASE cost factors early could accelerate the justification the business needs to move forward in making an informed decision.

    01- Infrastructure

    • Physical security
    • Cabling
    • Power supply and HVAC
    • Hosting

    02- Administration

    • Human hours to analyze logs and threats
    • Human hours to secure infrastructure
    • Fees associated with maintenance

    03- Inbound

    • DPI
    • DDoS
    • Web application firewall
    • VPN concentrators

    04- Outbound

    • IDPS
    • DLP on-prem
    • QoS
    • Sandbox & URL filtering

    04- Data Protection

    • Real-time URL
      insights
    • Threat hunting
    • Data loss prevention

    06- Monitoring

    • Log storage
    • Logging engine
    • Dashboards
    • Managed detection
      and response

    Info-Tech's methodology for securing your hybrid workforce

    1. Current state and future mitigation

    2. Assess the benefits of moving to SASE/zero trust

    Phase Steps

    1.1 Limitations of legacy infrastructure

    1.2 Zero trust principle as a control

    1.3 SASE as a driver of zero trust

    2.1 Sourcing out a SASE/SSE vendor

    2.2 Build a zero trust roadmap

    Phase Outcomes

    Identify and prioritize risks of current infrastructure and several ways to mitigate them.

    RFP template and build a zero trust roadmap.

    Consider several factors needed to protect your growing hybrid workforce and assess your current resource capabilities, solutions, and desire for a more mature security program. The outcome should either address a quick pain point or a long-term roadmap.

    The internet is the new corporate network

    The internet is the new corporate network, which opens the organization up to more risks not protected by the current security stack. Using Info-Tech's methodology of zero trust adoption is a sure way to reduce the attack surface, and SASE is one useful tool to take you on the zero trust journey.

    Current-state risks and future mitigation

    Securing your hybrid workforce via zero trust will inevitably include (but is not limited to) technological products/solutions.

    SASE and SSE features sit as an overlay here as technological solutions that will help on the zero trust journey by aggregating all the disparate solutions required for you to meet zero trust requirements into a single interface. The knowledge and implementation of this helps put things into perspective of where and what our target state is.

    The right solution for the right problem

    It is critical to choose a solution that addresses the security problems you are actually trying to solve.

    Don't allow the solution provider to tell you what you need – rather, start by understanding your capability gaps and then go to market to find the right partner.

    Take advantage of the RFP template to source a SASE or SSE vendor. Additionally, build a zero trust roadmap to develop and strategize initiatives and tasks.

    Blueprint deliverables

    Each step of this blueprint is accompanied by supporting deliverables to help you accomplish your goals:

    Zero Trust and SASE Suitability Tool
    Identify critical and vulnerable DAAS elements to protect and align them to business goals.

    Zero Trust Program Gap Analysis Tool
    Perform a gap analysis between current and target states to build a zero trust roadmap.

    Key deliverable:

    Secure Your Hybrid Workforce With Zero Trust Communication deck
    Present your zero trust strategy in a prepopulated document that summarizes the work you have completed as a part of this blueprint.

    Phase 1

    Current state and future mitigation

    Phase 1

    Phase 2

    1.1 Limitations of legacy infrastructure

    1.2 Zero trust principle as a control

    1.3 SASE as a driver of zero trust

    2.1 Sourcing out a SASE/SSE vendor

    2.2 Build a zero trust roadmap

    This phase will walk you through the following activities:

    • Introduction to the tool, how to use the input tabs to identify current challenges, technologies being used, and to prioritize the challenges. The prioritized list will highlight existing gaps and eventually be mapped to recommended mitigations in the following phase.

    This phase involves the following participants:

    • CIO
    • CISO
    • CSO
    • IT security team
    • IT network team

    Secure Your Hybrid Workforce

    1.1 Limitations of legacy infrastructure

    Traditional security & remote access solutions must be modernized

    Info-Tech Insight
    Traditional security is architected with a perimeter in mind and is poorly suited to the threats in hybrid or distributed environments.

    Ensure you minimize or eliminate weak points on all layers.

    • SECURITY
      • DDoS
      • DNS hijacking
      • Weak VPN protocols
    • IDENTITY
      • One-time verification allowing lateral movement
    • NETWORK
      • Risk perimeter stops at corporate network edge
      • Split tunneling
    • AUTHENTICATION
      • Weak authentication
      • Weak passwords
    • ACCESS
      • Man-in-the-middle attack
      • Cross-site scripting
      • Session hijacking

    1.1.1 For example: traditional VPNs are poorly suited to a hybrid workforce

    There are many limitations that make it difficult for traditional VPNs to adapt to an ever-growing hybrid workforce.

    The listed limitations are tied to associated risks of legacy infrastructure as well as security components that are almost non-existent in a VPN implementation today.

    Scaling

    VPNs were designed for small-scale remote access to corporate network. An increase in the remote workforce will require expensive hardware investment.

    Visibility

    Users and attackers are not restricted to specific network resources, and with an absence of activity logs, they can go undetected.

    Managed detection & response

    Due to the reduction in or lack of visibility, threat detections are poorly managed, and responses are already too late.

    Hardware

    Limited number of locations for VPN hardware to be situated as it can be expensive.

    Hybrid workforce

    The increase in the hybrid workforce requires the risk perimeter to be expanded from the corporate network to devices and applications. VPNs are built for privacy, not security.

    Info-Tech Insight

    Hybrid workforces are here to stay, and adopting a strategy that is adaptable, flexible, simple, and cost-effective is a recommended road to take on the journey to bettering your security and network.

    1.1 Identify risk from legacy infrastructure

    Estimated Time: 1-2 hours

    1. Ensure all vulnerabilities described on slide 17 are removed.
    2. Note any forecasted challenge you think you might have down the line with your current hybrid setup.
    3. Identify any trend that may be of interest to you with regards to your hybrid setup.

    This is a screenshot of the organizational profile table found in the Zero Trust - SASE Suitability Assessment Tool

    Download the Zero Trust - SASE Suitability Assessment Tool

    Input

    • List of key pain points and challenges
    • List of forecasted challenges and trends of interest

    Output

    • Prioritized list of pain points and/or challenges

    Materials

    • Excel tool
    • Whiteboard

    Participants

    • CISO
    • InfoSec team
    • IT manager
    • CIO
    • Infrastructure team

    1.2 Zero trust principle as a control

    A zero trust implementation comes with benefits/initiatives that mitigate the challenges identified in earlier activities.

    Info-Tech Insight

    Zero trust/"always verify" is applied to identity, workloads, devices, networks, and data to provide a greater control for risks associated with traditional network architecture.

    Improve IAM maturity

    Zero trust identity and access will lead to a mature IAM process in an organization with the removal of implicit trust.

    Secure your remote access

    With a zero trust network architecture (ZTNA), both the remote and on-prem network access are more secure than the traditional network deployment. The software-defined parameter ensures security on each network access.

    Reduce threat surface area

    With zero trust principle applied on identity, workload, devices, network, and data, the threat surface area which births some of the risks identified earlier will be significantly reduced.

    Improve hybrid workforce

    Scaling, visibility, network throughput, secure connection from anywhere, micro-segmentation, and a host of other benefits to improve your hybrid workforce.

    1.2 SASE as an overlay to zero trust

    Security and network initiatives of a zero trust roadmap converged into a single pane of glass.

    Info-Tech Insight

    Security and network converged into a single pane of glass giving you some of the benefits and initiatives of a zero trust implemented architecture in one package.

    Improve IAM maturity

    The identity-centric nature of SASE solutions helps to improve your IAM maturity as it applies the principle of least privilege. The removal of implicit trust and continuous verification helps foster this more.

    Secure your remote access

    With ZTNA, both the remote and on-prem network access are more secure than the traditional network deployment. The software defined parameter ensures security on each network access.

    Reduce threat surface area

    Secure web gateway, cloud access security broker, domain name system, next-generation firewall, data loss prevention, and ZTNA protect against data leaks, prevent lateral movement, and prevent malicious actors from coming in.

    Improve hybrid workforce

    Reduced costs and complexity of IT, faster user experience, and reduced risk as a result of the scalability, visibility, ease of IT administration, network throughput, secure connection from anywhere, micro-segmentation, and a host of other benefits will surely improve your hybrid workforce.

    Align SASE features to zero trust core capabilities

    Verify Identity

    • Authentication & verification are enforced for each app request or session.
    • Use of multifactor authentication.
    • RBAC/ABAC and principle of least privilege are applied on the identity regardless of user, device, or location.

    Verify Device

    • Device health is checked to ensure device is not compromised or vulnerable.
    • No admin permissions on user devices.
    • Device-based risk assessment is enforced as part of UEBA.

    Verify Access

    • Micro-segmentation built around network, user, device, location and roles.
    • Use of context and content-based policy enforced to the user, application, and device identity.
    • Network access only granted to specified application request and not to the entire network.

    Verify Services

    • Applications and services are checked before access is granted.
    • Connections to the application and services are inspected with the security controls built into the SASE solution.

    Info-Tech Insight

    These features of SASE and zero trust mitigate the risks associated with a traditional VPN and reduce the threat surface area. With security at the core, network optimization is not compromised.

    Security components of SASE

    Otherwise known as security service edge (SSE)

    Security service edge is the convergence of all security services typically found in SASE. At its core, SSE consists of three services which include:

    • Secure web gateway – secure access to the internet and web.
    • Cloud access security broker – secure access to SaaS and cloud applications.
    • Zero trust network access – secure remote access to private applications.

    SSE components are also mitigations or initiatives that make up a zero trust roadmap as they comply with the zero trust principle, and as a result, they sit up there with SASE as an overlay/driver of a zero trust implementation. SSE's benefits are identical to SASE's in that it provides zero trust access, risk reduction, low costs and complexity, and a better user experience. The difference is SSE's sole focus on security services and not the network component.

    SASE

    NETWORK FEATURES

    SECURITY FEATURES

    • WAN optimization
    • SD WAN
    • CDN
    • Network-as-a-service
    • CASB
    • IDPS
    • ZTNA/VPN
    • FWaaS
    • Browser isolation
    • DLP
    • UEBA
    • Secure web gateway
    • Sandboxing

    1.3 Pros & cons of zero trust and SASE

    Zero Trust

    SASE

    Pros

    Cons

    Pros

    Cons

    • Robust IAM process and technologies with role-based access control.
    • Strong and continuous verification of identity of user accounts, devices, data, location, and principle of least privilege applied.
    • Micro-segmentation applied around users, network, devices, roles, and applications to prevent lateral movement.
    • Threat attack surface eliminated, which reduces organizational risks.
    • Protection of data strengthened based on sensitivity and micro-segmentation.
    • Difficult to identify the scope of the zero trust initiative.
    • Requires continuous and ongoing update of access controls.
    • Zero trust journey/process could take years and is prone to being abandoned without commitment from executives.
    • Legacy systems can be hard to replace, which would require all stakeholders to prioritize resource allocation.
    • Can be expensive to implement.
    • Adopts a zero trust security posture for all access requests.
    • Converged and consolidated network and security delivered as a cloud service to the user rather than a single point of enforcement.
    • Centralized visibility of devices, data in transit and at rest, user activities, and threats.
    • Cheaper than a zero trust roadmap implementation.
    • Managed detection and response.
    • The limited knowledge of SASE.
    • No universally agreed upon SASE definition.
    • SASE products are still being developed and are open to vendors' interpretation.
    • Existing vendor relationships could be a hinderance to deployment.
    • Hard to manage MSSPs.

    Understand SASE and zero trust suitability for your needs

    Estimated Time: 1 hour

    Use the dashboard to understand the value assessment of adopting a SASE product or building a zero trust roadmap.

    This is an image of the SASE Suitability Assessment

    This is the image of the Zero Trust Suitability Assessment

    Info-Tech Insight

    This tool will help steer you on a path to take as a form of mitigation/control to some or all the identified challenges.

    Phase 2

    Make a decision and next steps

    Phase 1

    Phase 2

    1.1 Limitations of legacy infrastructure

    1.2 Zero trust principle as a control

    1.3 SASE as a driver of zero trust

    2.1 Sourcing out a SASE/SSE vendor

    2.2 Build a zero trust roadmap

    This phase will walk you through the following activities:

    • Introduction to the tool activity, how to use the input tabs and considerations to generate an output that could help understand the current state of your hybrid infrastructure and what direction is to be followed next to improve.

    This phase involves the following participants:

    • CIO
    • CISO
    • CSO
    • IT security
    • IT network team

    Secure Your Hybrid Workforce

    Step 2.1

    Sourcing out a SASE/SSE vendor

    Activities

    2.1.1 Use the RFP template to request proposal from vendors

    2.1.2 Use SoftwareReviews to compare vendors

    This step involves the following participants:

    • CIO, CISO, IT manager, Infosec team, executives.

    Outcomes of this step

    • Zero Trust Roadmap

    2.1.1 Use the RFP template to request proposal from vendors

    Estimated Time: 1-3 hours

    1. As a group, use the RFP Template to include technical capabilities of your desired SASE product and to request proposals from vendors.
    2. The features that are most important to your organization generated from phase one should be highlighted in the RFP.

    Input

    • List of SASE features
    • Technical capabilities

    Output

    • RFP

    Materials

    • RFP Template

    Participants

    • Security team
    • IT leadership

    Download the RFP Template

    2.1.2 Use SoftwareReviews to compare vendors

    SoftwareReviews

    • The Data Quadrant is a thorough evaluation and ranking of all software in an individual category to compare platforms across multiple dimensions.
    • Vendors are ranked by their Composite Score, based on individual feature evaluations, user satisfaction rankings, vendor capability comparisons, and likeliness to recommend the platform.
    • The Emotional Footprint is a powerful indicator of overall user sentiment toward the relationship with the vendor, capturing data across five dimensions.
    • Vendors are ranked by their Customer Experience (CX) Score, which combines the overall Emotional Footprint rating with a measure of the value delivered by the solution.

    Step 2.2

    Zero trust readiness and roadmap

    Activities

    2.2.1 Assess the maturity of your current zero trust implementation

    2.2.2 Understand business needs and current security projects

    2.2.3 Set target maturity state with timeframe

    This step involves the following participants:

    CIO, CISO, IT manager, Infosec team, executives.

    Outcomes of this step

    Zero Trust Roadmap

    2.2.1 Assess the maturity of your current zero trust implementation

    Estimated Time: 1-3 hours

    • Realizing that zero trust is a journey helps create a better roadmap and implementation. Identify the current controls or solutions in your organization that align with the principle of zero trust.
    • Break down these controls or solutions into different silos (e.g. identity, security, network, data, device, applications, etc.).
    • Determine your zero trust readiness.

    Input

    • List of zero trust controls/solutions
    • Siloed list of zero trust controls/solutions
    • Current state of zero trust maturity

    Output

    • Zero trust readiness and current maturity state

    Materials

    • Zero Trust Security Benefit Assessment tool

    Participants

    • Security team
    • IT leadership

    Download the Zero Trust Security Benefit Assessment tool

    2.2.2 Understand business needs and current security projects

    Estimated Time: 1-3 hours

    1. Identify the business and IT executives, application owners, and board members whose vision aligns with the zero trust journey.
    2. Identify existing projects within security, IT, and the business and highlight interdependencies or how they fit with the zero trust journey.
    3. Build a rough sketch of the roadmap that fits the business needs, current projects and the zero trust journey.

    Input

    • Meetings with stakeholders
    • List of current and future projects

    Output

    • Sketch of zero trust roadmap

    Materials

    • Whiteboard activity

    Participants

    • Security team
    • IT leadership
    • IT ops team
    • Business executives
    • Board members

    Download Zero Trust Protect Surface Mapping Tool

    2.2.3 Set target maturity state with a given timeframe

    Estimated Time: 1-3 hours

    1. With the zero trust readiness, current business, IT and security projects, current maturity state, and sketch of the roadmap, setting a target maturity state within some timeframe is at the top of the list. The target maturity state will include a list of initiatives that could be siloed and confined to a timeframe.
    2. A Gantt chart or graph could be used to complete this task.

    Input

    • Results from previous activity slides

    Output

    • Current state and target state assessment for gap analysis
    • List of initiatives and timeframe

    Materials

    • Zero Trust Program Gap Analysis Tool

    Participants

    • Security team
    • IT leadership
    • IT ops team
    • Business executives
    • Board members

    Download the Zero Trust Program Gap Analysis Tool

    Summary of Accomplishment

    Insights Gained

    • Difference between zero trust as a principle and SASE as a framework
    • Difference between SASE and SSE platforms.
    • Assessment of which path to take in securing your hybrid workforce

    Deliverables Completed

    If you would like additional support, have our analysts guide you through other phases as part of an Info-Tech workshop

    Contact your account representative for more information

    workshops@infotech.com

    1-888-670-8889

    Additional Support

    If you would like additional support, have our analysts guide you through other phases as part of an Info-Tech workshop

    To accelerate this project, engage your IT team in an Info-Tech workshop with an Info-Tech analyst team.

    Info-Tech analysts will join you and your team at your location or welcome you to Info-Tech's historic Toronto office to participate in an innovative onsite workshop.

    Contact your account representative for more information.
    workshops@infotech.com 1-888-670-8889

    The following are sample activities that will be conducted by Info-Tech analysts with your team:

    This is a screenshot from the Zero Trust - SASE Suitability Assessment Tool

    Zero Trust - SASE Suitability Assessment Tool

    Assess current security capabilities and build a roadmap of tasks and initiatives that close maturity gaps.

    Research Contributors

    • Aaron Shum, Vice President, Security & Privacy
    • Cameron Smith, Research Lead, Security & Privacy
    • Brad Mateski, Zones, Solutions Architect for CyberSecurity
    • Bob Smock, Info-Tech Research Group, Vice President of Consulting
    • Dr. Chase Cunningham, Ericom Software, Chief Strategy Officer
    • John Kindervag, ON2IT Cybersecurity, Senior Vice President, Cybersecurity Strategy and ON2IT Group Fellow
    • John Zhao, Fonterra, Enterprise Security Architect
    • Rongxing Lu, University of New Brunswick, Associate Professor
    • Sumanta Sarkar, University of Warwick, Assistant Professor
    • Tim Malone, J.B. Hunt Transport, Senior Director Information Security
    • Vana Matte, J.B. Hunt Transport, Senior Vice President of Technology Services

    Related Info-Tech Research

    This is a screenshot from Info-Tech's Security Strategy Model

    Build an Information Security Strategy

    Info-Tech has developed a highly effective approach to building an information security strategy – an approach that has been successfully tested and refined for over seven years with hundreds of organizations. This unique approach includes tools for ensuring alignment with business objectives, assessing organizational risk and stakeholder expectations, enabling a comprehensive current state assessment, prioritizing initiatives, and building out a security roadmap.

    This is a screenshot from Info-Tech's research: Determine Your Zero Trust Readiness

    Determine Your Zero Trust Readiness

    IT security was typified by perimeter security. However, the way the world does business has mandated a change to IT security. In response, zero trust is a set of principles that can add flexibility to planning your IT security strategy.

    Use this blueprint to determine your zero trust readiness and understand how zero trust can benefit both security and the business.

    This is a screenshot from Info-Tech's research: Mature Your Identity and Access Management Program

    Mature Your Identity and Access Management Program

    Many organizations are looking to improve their identity and access management (IAM) practices but struggle with where to start and whether all areas of IAM have been considered. This blueprint will help you improve the organization's IAM practices by following our three-phase methodology:

    • Assess identity and access requirements.
    • Identify initiatives using the identity lifecycle.
    • Prioritize initiatives and build a roadmap.

    Bibliography

    "2021 Data Breach Investigations Report." Verizon, 2021. Web.
    "Fortinet Brings Networking and Security to the Cloud" Fortinet, 2 Mar. 2021. Web.
    "A Zero Trust Strategy Has 3 Needs – Identify, Authenticate, and Monitor Users and Devices on and off the Network." Fortinet, 15 July 2021. Web.
    "Applying Zero Trust Principles to Enterprise Mobility." CISA, Mar. 2022. Web.
    "CISA Zero Trust Maturity Model." CISA, Cybersecurity Division, June 2021. Web.
    "Continuous Diagnostics and Mitigation Program Overview." CISA, Jan. 2022. Web.
    "Cost of a Data Breach Report 2021 | IBM." IBM, July 2021. Web.
    English, Melanie. "5 Stats That Show The Cost Saving Effect of Zero Trust." Teramind, 29 Sept. 2021. Web.
    Hunter, Steve. "The Five Business Benefits of a Zero Trust Approach to Security." Security Brief - Australia, 19 Aug. 2020. Web.
    "Improve Application Access and Security With Fortinet Zero Trust Network Access." Fortinet, 2 Mar. 2021. Web.
    "Incorporating zero trust Strategies for Secure Network and Application Access." Fortinet, 21 Jul. 2021. Web.
    Jakkal, Vasu. "Zero Trust Adoption Report: How Does Your Organization Compare?" Microsoft, 28 July 2021. Web.
    "Jericho Forum™ Commandments." The Open Group, Jericho Forum, May 2007. Web.
    Schulze, Holger. "2019 Zero Trust Adoption Report." Cybersecurity Insiders, 2019. Web.
    "67% of Organizations Had Identity-Related Data Breaches Last Year." Security Magazine, 22 Aug. 2022. Web.
    United States, Executive Office of the President Joseph R. Biden, Jr. "Executive Order on Improving the Nation's Cybersecurity." The White House, 12 May 2021. Web.

    Develop a Targeted Flexible Work Program for IT

    • Buy Link or Shortcode: {j2store}542|cart{/j2store}
    • member rating overall impact: 9.0/10 Overall Impact
    • member rating average dollars saved: $18,909 Average $ Saved
    • member rating average days saved: 13 Average Days Saved
    • Parent Category Name: Attract & Select
    • Parent Category Link: /attract-and-select
    • Workplace flexibility continues to be top priority for IT employees. Organizations who fail to offer flexibility will have a difficult time attracting, recruiting, and retaining talent.
    • When the benefits of remote work are not available to everyone, this raises fairness and equity concerns.

    Our Advice

    Critical Insight

    IT excels at hybrid location work and is more effective as a business function when location flexibility is an option for its employees. But hybrid work is just a start. A comprehensive flex work program extends beyond flexible location, so organizations must understand the needs of unique employee groups to uncover the options that will attract and retain talent.

    Impact and Result

    • Uncover the needs of unique employee segments to shortlist flexible work options that employees want and will use.
    • Assess the feasibility of various flexible work options and select ones that meet employee needs and are feasible for the organization.
    • Equip leaders with the information and tools needed to implement and sustain a flexible work program.

    Develop a Targeted Flexible Work Program for IT Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Assess employee and organizational flexibility needs

    Identify prioritized employee segments, flexibility challenges, and the desired state to inform program goals.

    • Develop a Targeted Flexible Work Program for IT – Phases 1-3
    • Talent Metrics Library
    • Targeted Flexible Work Program Workbook
    • Fast-Track Hybrid Work Program Workbook

    2. Identify potential flex options and assess feasibility

    Review, shortlist, and assess the feasibility of common types of flexible work. Identify implementation issues and cultural barriers.

    • Flexible Work Focus Group Guide
    • Flexible Work Options Catalog

    3. Implement selected option(s)

    Equip managers and employees to adopt flexible work options while addressing implementation issues and cultural barriers and aligning HR programs.

    • Guide to Flexible Work for Managers and Employees
    • Flexible Work Time Policy
    • Flexible Work Time Off Policy
    • Flexible Work Location Policy

    Infographic

    Workshop: Develop a Targeted Flexible Work Program for IT

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Prepare to Assess Flex Work Feasibility

    The Purpose

    Gather information on organizational and employee flexibility needs.

    Key Benefits Achieved

    Understand the flexibility needs of the organization and its employees to inform a targeted flex work program.

    Activities

    1.1 Identify employee and organizational needs.

    1.2 Identify employee segments.

    1.3 Establish program goals and metrics.

    1.4 Shortlist flexible work options.

    Outputs

    Organizational context summary

    List of shortlisted flex work options

    2 Assess Flex Work Feasibility

    The Purpose

    Perform a data-driven feasibility analysis on shortlisted work options.

    Key Benefits Achieved

    A data-driven feasibility analysis ensures your flex work program meets its goals.

    Activities

    2.1 Conduct employee/manager focus groups to assess feasibility of flex work options.

    Outputs

    Summary of flex work options feasibility per employee segment

    3 Finalize Flex Work Options

    The Purpose

    Select the most impactful flex work options and create a plan for addressing implementation challenge

    Key Benefits Achieved

    A data-driven selection process ensures decisions and exceptions can be communicated with full transparency.

    Activities

    3.1 Finalize list of approved flex work options.

    3.2 Brainstorm solutions to implementation issues.

    3.3 Identify how to overcome cultural barriers.

    Outputs

    Final list of flex work options

    Implementation barriers and solutions summary

    4 Prepare for Implementation

    The Purpose

    Create supporting materials to ensure program implementation proceeds smoothly.

    Key Benefits Achieved

    Employee- and manager-facing guides and policies ensure the program is clearly documented and communicated.

    Activities

    4.1 Design employee and manager guide prototype.

    4.2 Align HR programs and policies to support flexible work.

    4.3 Create a communication plan.

    Outputs

    Employee and manager guide to flexible work

    Flex work roadmap and communication plan

    5 Next Steps and Wrap-Up

    The Purpose

    Put everything together and prepare to implement.

    Key Benefits Achieved

    Our analysts will support you in synthesizing the workshop’s efforts into a cohesive implementation strategy.

    Activities

    5.1 Complete in-progress deliverables from previous four days.

    5.2 Set up review time for workshop deliverables and to discuss next steps.

    Outputs

    Completed flexible work feasibility workbook

    Flexible work communication plan

    Further reading

    Develop a Targeted Flexible Work Program for IT

    Select flexible work options that balance organizational and employee needs to drive engagement and improve attraction and retention.

    Executive Summary

    Your Challenge

    • IT leaders continue to struggle with workplace flexibility, and it is a top priority for IT employees; as a result, organizations who fail to offer flexibility will have a difficult time attracting, recruiting, and retaining talent.
    • The benefits of remote work are not available to everyone, raising fairness and equity concerns for employees.

    Common Obstacles

    • A one-size-fits-all approach to selecting and implementing flexible work options fails to consider unique employee needs and will not reap the benefits of offering a flexible work program (e.g. higher engagement or enhanced employer brand).
    • Improper structure and implementation of flexible work programs exacerbates existing challenges (e.g. high turnover) or creates new ones.

    Info-Tech's Approach

    • Uncover the needs of unique employee segments to shortlist flexible work options that employees want and will use.
    • Assess the feasibility of various flexible work options and select ones that meet employee needs and are feasible for the organization.
    • Equip leaders with the information and tools needed to implement and sustain a flexible work program.

    Info-Tech Insight

    IT excels at hybrid location work and is more effective as a business function when location flexibility is an option for its employees. But hybrid work is just a start. A comprehensive flex work program extends beyond flexible location, so organizations must understand the needs of unique employee groups to uncover the options that will attract and retain talent.

    Flexible work arrangements are a requirement in today's world of work

    Flexible work continues to gain momentum…

    A 2022 LinkedIn report found that the following occurred between 2019 and 2021:

    +362%

    Increase in LinkedIn members sharing content with the term "flexible work."

    +83%

    Increase in job postings that mention "flexibility."
    (LinkedIn, 2022)

    In 2022, Into-Tech found that hybrid was the most commonly used location work model for IT across all industries.

    ("State of Hybrid Work in IT," Info-Tech Research Group, 2022)

    …and employees are demanding more flexibility

    90%

    of employees said they want schedule and location flexibility ("Global Employee Survey," EY, 2021).

    17%

    of resigning IT employees cited lack of flexible work options as a reason ("IT Talent Trends 2022," Info-Tech Research Group, 2022).

    71%

    of executives said they felt "pressure to change working models and adapt workplace policies to allow for greater flexibility" (LinkedIn, 2021).

    Therefore, organizations who fail to offer flexibility will be left behind

    Difficulty attracting and retaining talent

    98% of IT employees say flexible work options are important in choosing an employer ("IT Talent Trends 2022," Info-Tech Research Group, 2022).

    Worsening employee wellbeing and burnout

    Knowledge workers with minimal to no schedule flexibility are 2.2x more likely to experience work-related stress and are 1.4x more likely to suffer from burnout (Slack, 2022; N=10,818).

    Offering workplace flexibility benefits organizations and employees

    Higher performance

    IT departments that offer some degree of location flexibility are more effective at supporting the organization than those who do not.

    35% of service desk functions report improved service since implementing location flexibility.
    ("State of Hybrid Work in IT," Info-Tech Research Group, 2023).

    Enhanced employer brand

    Employees are 2.1x more likely to recommend their employer to others when they are satisfied with their organization's flexible work arrangements (LinkedIn, 2021).

    Improved attraction

    41% of IT departments cite an expanded hiring pool as a key benefit of hybrid work.

    Organizations that mention "flexibility" in their job postings have 35% more engagement with their posts (LinkedIn, 2022).

    Increased job satisfaction

    IT employees who have more control over their working arrangement experience a greater sense of contribution and trust in leadership ("State of Hybrid Work in IT," Info-Tech Research Group, 2023).

    Better work-life balance

    81% of employees say flexible work will positively impact their work-life balance (FlexJobs, 2021).

    Boosted inclusivity

    • Caregivers regardless of gender, supporting them in balancing responsibilities
    • Individuals with disabilities, enabling them to work from the comfort of their homes
    • Women who may have increased responsibilities
    • Women of color to mitigate the emotional tax experienced at work

    Info-Tech Insight

    Flexible work options are not a concession to lower productivity. Properly implemented, flex work enables employees to be more productive at reaching business goals.

    Despite the popularity of flexible work options, not all employees can participate

    IT organizations differ on how much flexibility different roles can have.

    IT employees were asked what percentage of IT roles were currently in a hybrid or remote work arrangement ("State of Hybrid Work in IT," Info-Tech Research Group, 2023).

    However, the benefits of remote work are not available to all, which raises fairness and equity concerns between remote and onsite employees.

    45%

    of employers said, "one of the biggest risks will be their ability to establish fairness and equity among employees when some jobs require a fixed schedule or location, creating a 'have and have not' dynamic based on roles" ("Businesses Suffering," EY, 2021).

    Offering schedule flexibility to employees who need to be fully onsite can be used to close the fairness and equity gap.

    When offered the choice, 54% of employees said they would choose schedule flexibility over location flexibility ("Global Employee Survey," EY, 2021).

    When employees were asked "What choice would you want your employer to provide related to when you have to work?" The top three choices were:

    68%

    Flexibility on when to start and finish work

    38%

    Compressed or four-day work weeks

    33%

    Fixed hours (e.g. 9am to 5pm)

    Disclaimer: "Percentages do not sum to 100%, as each respondent could choose up to three of the [five options provided]" ("Global Employee Survey," EY, 2021).

    Beware of the "all or nothing" approach

    There is no one-size-fits-all approach to workplace flexibility.

    Understanding the needs of various employee segments in the organization is critical to the success of a flexible work program.

    Working parents want more flexibility

    82%

    of working mothers desire flexibility in where they work.

    48%

    of working fathers "want to work remotely 3 to 5 days a week."

    Historically underrepresented groups value more flexibility

    38%

    "Thirty-eight percent of Black male employees and 33% of Black female employees would prefer a fully flexible schedule, compared to 25% of white female employees and 26% of white male employees."
    (Slack, 2022; N=10,818)

    33%

    Workplace flexibility must be customized to the organization to avoid longer working hours and heavy workloads that impact employee wellbeing

    84%

    of remote workers and 61% of onsite workers reported working longer hours post pandemic. Longer working hours were attributed to reasons such as pressure from management and checking emails after working hours (Indeed, 2021).

    2.6x

    Respondents who either agreed or strongly agreed with the statement "Generally, I find my workload reasonable" were 2.6x more likely to be engaged compared to those who stated they disagreed or strongly disagreed (McLean & Company Engagement Survey Database;2022; N=5,615 responses).

    Longer hours and unsustainable workloads can contribute to stress and burnout, which is a threat to employee engagement and retention. With careful management (e.g. setting clear expectations and establishing manageable workloads), flexible work arrangement benefits can be preserved.

    Info-Tech Insight

    Employees' lived experiences and needs determine if people use flexible work programs – a flex program that has limited use or excludes people will not benefit the organization.

    Develop a flexible work program that meets employee and organizational needs

    This is an image of a sample flexible work program which meets employee and organizational needs.

    Insight summary

    Overarching insight: IT excels at hybrid location work and is more effective as a business function when location, time, and time-off flexibility are an option for its employees.

    Introduction

    Step 1 insight

    Step 2 insight

    Step 3 insight

    • Flexible work options are not a concession to lower productivity. Properly implemented, flex work enables employees to be more productive at reaching business goals.
    • Employees' lived experiences and needs determine if people use flexible work programs – a flex program that has limited use or excludes people will not benefit the organization.
    • Flexible work benefits everyone. IT employees experience greater engagement, motivation, and company loyalty. IT organizations realize benefits such as better service coverage, reduced facilities costs, and increased productivity.
    • Hybrid work is a start. A comprehensive flex work program extends beyond flexible location to flexible time and time off. Organizations must understand the needs of unique employee groups to uncover the options that will attract and retain talent. Provide greater inclusivity to employees by broadening the scope to include flex location, flex time, and flex time off.
    • No two employee segments are the same. To be effective, flexible work options must align with the expectations and working processes of each segment.
    • Every role is eligible for hybrid location work. If onsite work duties prevent an employee group from participating, see if processes can be digitized or automated. Flexible work is an opportunity to go beyond current needs to future proofing your organization.
    • Flexible work options must balance organizational and employee needs. If an option is beneficial to employees but there is little or no benefit to the organization, or if the cost of the option is too high, it will not support the long-term success of the organization.
    • Prioritize flexible work options that employees want. Providing too many options often leads to information overload and results in employees not understanding what is available, lowering adoption of the flexible work program.
    • Leaders' collective support of the flexible program determines the program's successful adoption. Don't sweep cultural barriers under the rug; acknowledge and address them to overcome them.
    • Negative performance of a flexible work option does not necessarily mean failure. Take the time to evaluate whether the option simply needs to be tweaked or whether it truly isn't working for the organization.
    • A set of formal guidelines for IT ensures flexible work is:
      1. Administered fairly across all IT employees.
      2. Defensible and clear.
      3. Scalable to the rest of the organization.

    Case Study

    Expanding hybrid work at Info-Tech

    Challenge

    In 2020, Info-Tech implemented emergency work-from-home for its IT department, along with the rest of the organization. Now in 2023, hybrid work is firmly embedded in Info-Tech's culture, with plans to continue location flexibility for the foreseeable future.

    Adjusting to the change came with lessons learned and future-looking questions.

    Lessons Learned

    Moving into remote work was made easier by certain enablers that had already been put in place. These included issuing laptops instead of desktops to the user base and using an existing cloud-based infrastructure. Much support was already being done remotely, making the transition for the support teams virtually seamless.

    Continuing hybrid work has brought benefits such as reduced commuting costs for employees, higher engagement, and satisfaction among staff that their preferences were heard.

    Looking Forward

    Every flexible work implementation is a work in progress and must be continually revisited to ensure it continues to meet organizational and employee needs. Current questions being explored at Info-Tech are:

    • The concept of the "office as a tool" – how does use of the office change when it is used for specific collaboration-related tasks, rather than everything? How should the physical space change to support this?
    • What does a viable replacement for quick hallway meetings look like in a remote world where communication is much more deliberate? How can managers adjust their practices to ensure the benefits of informal encounters aren't lost?

    Info-Tech offers various levels of support to best suit your needs

    DIY Toolkit

    “Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful.”

    Guided Implementation

    “Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track.”

    Workshop

    “We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place.”

    Consulting

    “Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project.”

    Diagnostics and consistent frameworks used throughout all four options

    Guided Implementation

    What does a typical GI on this topic look like?

    Preparation

    Step 1

    Step 2

    Step 3

    Follow-up

    Call #1: Scope requirements, objectives, and your specific challenges.

    Call #2: Assess employee and organizational needs.

    Call #3: Shortlist flex work options and assess feasibility.

    Call #4: Finalize flex work options and create rollout plan.

    Call #5: (Optional) Review rollout progress or evaluate pilot success.

    A Guided Implementation (GI) is a series of calls with an Info-Tech analyst to help implement our best practices in your organization.

    A typical GI is 3 to 5 calls over the course of 4 to 6 months.

    Workshop Overview

    Contact your account representative for more information.
    workshops@infotech.com 1-888-670-8889

    Day 1

    Day 2

    Day 3

    Day 4

    Day 5

    Activities

    Prepare to assess flex work feasibility

    Assess flex work feasibility

    Finalize flex work options

    Prepare for implementation

    Next Steps and Wrap-Up (offsite)

    1.1 Identify employee and organizational needs.

    1.2 Identify employee segments.

    1.3 Establish program goals and metrics.

    1.4 Shortlist flex work options.

    2.1 Conduct employee/manager focus groups to assess feasibility of flex work options.

    3.1 Finalize list of approved flex work options.

    3.2 Brainstorm solutions to implementation issues.

    3.2 Identify how to overcome cultural barriers.

    4.1 Design employee and manager guide prototype.

    4.2 Align HR programs and policies to support flexible work.

    4.3 Create a communication plan.

    5.1 Complete in-progress deliverables from previous four days.

    5.2 Set up review time for workshop deliverables and to discuss next steps.

    Deliverables

    1. Organizational context summary
    2. List of shortlisted flex work options
    1. Summary of flex work options' feasibility per employee segment
    1. 1.Final list of flex work options
    2. 2.Implementation barriers and solutions summary
    1. Employee and manager guide to flexible work
    2. Flex work roadmap and communication plan
    1. Completed flexible work feasibility workbook
    2. Flexible work communication plan

    Step 1

    Assess employee and organizational needs

    1. Assess employee and organizational flexibility needs
    2. Identify potential flex options and assess feasibility
    3. Implement selected option(s)

    After completing this step you will have:

    • Identified key stakeholders and their responsibilities
    • Uncovered the current and desired state of the organization
    • Analyzed feedback to identify flexibility challenges
    • Identified and prioritized employee segments
    • Determined the program goals
    • Identified the degree of flexibility for work location, timing, and deliverables

    Identify key stakeholders

    Organizational flexibility requires collaborative and cross-functional involvement to determine which flexible options will meet the needs of a diverse workforce. HR leads the project to explore flexible work options, while other stakeholders provide feedback during the identification and implementation processes.

    HR

    • Assist with the design, implementation, and maintenance of the program.
    • Provide managers and employees with guidance to establish successful flexible work arrangements.
    • Help develop communications to launch and maintain the program.

    Senior Leaders

    • Champion the project by modeling and promoting flexible work options
    • Help develop and deliver communications; set the tone for flexible work at the organization.
    • Provide input into determining program goals.

    Managers

    • Model flexible work options and encourage direct reports to request and discuss options.
    • Use flexible work program guidelines to work with direct reports to select suitable flexible work options.
    • Develop performance metrics and encourage communication between flexible and non-flexible workers.

    Flexible Workers

    • Indicate preferences of flexible work options to the manager.
    • Identify ways to maintain operational continuity and communication while working flexibly.
    • Flag issues and suggest improvements to the manager.
    • Develop creative ways to work with colleagues who don't work flexibly.

    Non-Flexible Workers

    • Share feedback on issues with flexible arrangements and their impact on operational continuity.

    Info-Tech Insight

    Flexible work is a holistic team effort. Leaders, flexible workers, teammates, and HR must clearly understand their roles to ensure that teams are set up for success.

    Uncover the current and desired state of flexibility in the organization

    Current State

    Target State

    Review:

    • Existing policies related to flexibility (e.g. vacation, work from anywhere)
    • Existing flexibility programs (e.g. seasonal hours) and their uptake
    • Productivity of employees
    • Current culture at the organization. Look for:
      • Employee autonomy
      • Reporting structure and performance management processes
      • Trust and psychological safety of employees
      • Leadership behavior (e.g. do leaders model work-life balance, or does the organization have a work 24/7 mentality?)

    Identify what is driving the need for flexible work options. Ask:

    • Why does the organization need flexible options?
      • For example, the introduction of flexibility for some employees has created a "have and have not" dynamic between roles that must be addressed.
    • What does the organization hope to gain from implementing flexible options? For example:
      • Improved retention
      • Increased attraction, remaining competitive for talent
      • Increased work-life balance for employees
      • Reduced burnout
    • What does the organization aspire to be?
      • For example, an organization that creates an environment that values output, not face time.

    These drivers identify goals for the organization to achieve through targeted flexible work options.

    Info-Tech Insight

    Hybrid work is a start. A comprehensive flex work program extends beyond flexible location, so organizations must understand the needs of unique employee groups to uncover the options that will attract and retain talent. Provide greater inclusivity to employees by broadening the scope to include flex location, flex time, and flex time off.

    Identify employee segments

    Using the data, feedback, and challenges analyzed and uncovered so far, assess the organization and identify employee segments.

    Identify employee segments with common characteristics to assess if they require unique flexible work options. Assess the feasibility options for the segments separately in Step 2.

    • Segments' unique characteristics include:
      • Role responsibilities (e.g. interacting with users, creating reports, development and testing)
      • Work location/schedule (e.g. geographic, remote vs. onsite, 9 to 5)
      • Work processes (e.g. server maintenance, phone support)
      • Group characteristics (e.g. specific teams, new hires)

    Identify employee segments and sort them into groups based on the characteristics above.

    Examples of segments:

    • Functional area (e.g. Service Desk, Security)
    • Job roles (e.g. desktop support, server maintenance)
    • Onsite, remote, or hybrid
    • Full-time or part-time
    • Job level (e.g. managers vs. independent contributors)
    • Employees with dependents

    Prioritize employee segments

    Determine whether the organization needs flexible work options for the entire organization or specific employee segments.
    For specific employee segments:

    • Answer the questions on the right to identify whether an employee segment is high, medium, or low priority. Complete slides 23 to 25 for each high-priority segment, repeating the process for medium-priority segments when resources allow.

    For the entire organization:

    • When identifying an option for the entire organization, consider all segments. The approach must create consistency and inclusion; keep this top of mind when identifying flexibility on slides 23 to 25. For example, the work location flexibility would be low in an organization where some segments can work remotely and others must be onsite due to machinery requirements.

    High priority: The employee segment has the lowest engagement scores or highest turnover within the organization. Segment sentiment is that current flexibility is nonexistent or not sufficiently meeting needs.
    Medium priority: The employee segment has low engagement or high turnover. Segment sentiment is that currently available flexibility is minimal or not sufficiently meeting needs.
    Low priority: The segment does not have the lowest engagement or the highest turnover rate. Segment sentiment is that currently available flexibility is sufficiently meeting needs.

    1. What is the impact on the organization if this segment's challenges aren't addressed (e.g. if low engagement and high turnover are not addressed)?
    2. How critical is flexibility to the segment's needs/engagement?
    3. How time sensitive is it to introduce flexibility to this segment (e.g. is the organization losing employees in this segment at a high rate)?
    4. Will providing flexibility to this segment increase organizational productivity or output

    Identify challenges to address with flexibility

    Uncover the lived experiences and expectations of employees to inform selection of segments and flexible options.

    1. Collect data from existing sources, such as:
      • Engagement surveys
      • New hire/exit surveys
      • Employee experience monitor surveys
      • Employee retention pulse surveys
      • Burnout surveys
      • DEI pulse surveys
    2. Analyze employee feedback on experiences with:
      • Work duties
      • Workload
      • Work-life balance
      • Operating processes and procedures
      • Achieving operational outcomes
      • Collaboration and communication
      • Individual experience and engagement
    3. Evaluate the data and identify challenges

    Example challenges:

    • Engagement: Low average score on work-life balance question; flexible work suggested in open-ended responses.
    • Retention: Exit survey indicating that lack of work-life balance is consistently a reason employees leave. Include the cost of turnover (e.g. recruitment, training, severance).
    • Burnout: Feedback from employees through surveys or HR business partner anecdotes indicating high burnout; high usage of wellness services or employee assistance programs.
    • Absenteeism: High average number of days employees were absent in the past year. Include the cost of lost productivity.
    • Operational continuity: Provide examples of when flexible work would have enabled operational continuity in the case of disaster or extended customer service coverage.
    • Program uptake: If the organization already has a flexible work program, provide data on the low proportion of eligible employees using available options.

    1.1 Prepare to evaluate flexible work options

    1-3 hours

    Follow the guidance on preceding slides to complete the following activities.
    Note: If you are only considering remote or hybrid work, use the Fast-Track Hybrid Work Program Workbook. Otherwise, proceed with the Targeted Flexible Work Program Workbook.

    1. Identify key stakeholders. Be sure to record the level of involvement and responsibility expected from each stakeholder. Use the "Stakeholders" tab of the workbook.
    2. Uncover current and desired state. Review and record your current state with respect to culture, productivity, and current flexible work options, if any. Next, record your desired future state, including reasons for implementing flexible work, and goals for the program. Record this in the "Current and Desired State" tab of the workbook.
    3. Identify and prioritize employee segments. Identify and record employee segments. Depending on the size of your department, you may identify a few or many. Be as granular as necessary to fully separate employee groups with different needs. If your resources or needs prevent you from rolling out flexible work to the entire department, record the priority level of each segment so you can focus on the highest priority first.
    4. Identify challenges with flexibility. With each employee segment in mind, analyze your available data to identify and record each segment's main challenges regarding flexible work. These will inform your program goals and metrics.

    Download the Targeted Flexible Work Program Workbook

    Download the Fast-Track Hybrid Work Program Workbook

    Input

    • List of departmental roles
    • Data on employee engagement, productivity, sentiment regarding flexible work, etc.

    Output

    • List of stakeholders and responsibilities
    • Flexible work challenges and aims
    • Prioritized list of employee segments

    Materials

    • Targeted Flexible Work Program Workbook
      Or
    • Fast-Track Hybrid Work Program Workbook

    Participants

    • IT department head
    • HR business partner
    • Flexible work program committee

    Determine goals and metrics for the flexible work program

    Sample program goals

    Sample metrics

    Increase productivity

    • Employee, team, and department key performance indicators (KPIs) before and after flexible work implementation
    • Absenteeism rate (% of lost working days due to all types of absence)

    Improve business satisfaction and perception of IT value

    Increase retention

    • % of exiting employees who cite lack of flexible work options or poor work-life balance as a reason they left
    • Turnover and retention rates

    Improve the employee value proposition (EVP) and talent attraction

    • # of responses on the new hire survey where flexible work options or work-life balance are cited as a reason for accepting an employment offer
    • # of views of career webpage that mentions flexible work program
    • Time-to-fill rates

    Improve engagement and work-life balance

    • Overall engagement score – deploy Info-Tech's Employee Engagement Diagnostics
    • Score for questions about work-life balance on employee engagement or pulse survey, including:
      • "I am able to maintain a balance between my work and personal life."
      • "I find my stress levels at work manageable."

    Info-Tech Insight

    Implementing flex work without solid performance metrics means you won't have a way of determining whether the program is enabling or hampering your business practices.

    1.2 Determine goals and metrics

    30 minutes

    Use the examples on the preceding slide to identify program goals and metrics:

    1. Brainstorm program goals. Be sure to consider both the business benefits (e.g. productivity, retention) and the employee benefits (work-life balance, engagement). A successful flexible work program benefits both the organization and its employees.
    2. Brainstorm metrics for each goal. Identify metrics that are easy to track accurately. Use Info-Tech's IT and HR metrics libraries for reference. Ideally, the metrics you choose should already exist in your organization so no extra effort will be necessary to implement them. It is also important to have a baseline measure of each one before flexible work is rolled out.
    3. Record your outputs on the "Goals and Metrics" tab of the workbook.

    Download the Targeted Flexible Work Program Workbook

    Download the IT Metrics Library

    Download the HR Metrics Library

    Input

    • Organizational and departmental strategy

    Output

    • List of program goals and metrics

    Materials

    • Targeted Flexible Work Program Workbook
      Or
    • Fast-Track Hybrid Work Program Workbook

    Participants

    • Flexible work program committee

    Determine work location flexibility for priority segments

    Work location looks at where a segment can complete all or some of their tasks (e.g. onsite vs. remote). For each prioritized employee segment, evaluate the amount of location flexibility available.

    Work Duties

    Processes

    Operational Outcomes

    High degree of flexibility

    • Low dependence on onsite equipment
    • Work easily shifts to online platforms
    • Low dependence on onsite external interactions (e.g. clients, customers, vendors)
    • Low interdependence of work duties internally (most work is independent)
    • Work processes and expectations are or can be formally documented
    • Remote work processes are sustainable long term

    Most or all operational outcomes can be achieved offsite (e.g. products/service delivery not impacted by WFH)

    • Some dependence on onsite equipment
    • Some work can shift to online platforms
    • Some dependence on onsite external interactions
    • Some interdependence of work duties internally (collaboration is critical)
    • Most work processes and expectations have been or can be formally documented
    • Remote work processes are sustainable (e.g. workarounds can be supported and didn't add work)

    Some operational outcomes can be achieved offsite (e.g. some impact of WFH on product/service delivery)

    Low degree of flexibility

    • High dependence on onsite equipment
    • Work cannot shift to online platforms
    • High dependence on onsite external interactions
    • High interdependence of work duties internally (e.g. line work)
    • Few work processes and expectations can be formally documented
    • Work processes cannot be done remotely, and workarounds for remote work are not sustainable long term

    Operational outcomes cannot be achieved offsite (e.g. significant impairment to product/service delivery)

    Note

    If roles within the segment have differing levels of location flexibility, use the lowest results (e.g. if role A in the segment has a high degree of flexibility for work duties and role B has a low degree of flexibility, use the results for role B).

    Identify work timing for priority segments

    Work timing looks at when work can or needs to be completed (e.g. Monday to Friday, 9am to 5pm).

    Work Duties

    Processes

    Operational Outcomes

    High degree of flexibility

    • No need to be available to internal and/or external customers during standard work hours
    • Equipment is available at any time
    • Does not rely on synchronous (occurring at the same time) work duties internally
    • Work processes and expectations are or can be formally documented
    • Low reliance on collaboration
    • Work is largely asynchronous (does not occur at the same time)

    Most or all operational outcomes are not time sensitive

    • Must be available to internal and/or external customers during some standard work hours
    • Some reliance on synchronous work duties internally (collaboration is critical)
    • Most work processes and expectations have been or can be formally documented
    • Moderate reliance on collaboration
    • Some work is synchronous

    Some operational outcomes are time sensitive and must be conducted within set date or time windows

    Low degree of flexibility

    • Must be available to internal and/or external customers during all standard work hours (e.g. Monday to Friday 9 to 5)
    • High reliance on synchronous work duties internally (e.g. line work)
    • Few work processes and expectations can be formally documented
    • High reliance on collaboration
    • Most work is synchronous

    Most or all operational outcomes are time sensitive and must be conducted within set date or time windows

    Note

    With additional coordination, flex time or flex time off options are still possible for employee segments with a low degree of flexibility. For example, with a four-day work week, the segment can be split into two teams – one that works Monday to Thursday and one that works Tuesday to Friday – so that employees are still available for clients five days a week.

    Examine work deliverables for priority segments

    Work deliverables look at the employee's ability to deliver on their role expectations (e.g. quota or targets) and whether reducing the time spent working would, in all situations, impact the work deliverables (e.g. constrained vs. unconstrained).

    Work Duties

    Operational Outcomes

    High degree of flexibility

    • Few or no work duties rely on equipment or processes that put constraints on output (unconstrained output)
    • Employees have autonomy over which work duties they focus on each day
    • Most or all operational outcomes are unconstrained (e.g. a marketing analyst who builds reports and strategies for clients can produce more reports, produce better reports, or identify new strategies)
    • Work quota or targets are achievable even if working fewer hours
    • Some work duties rely on equipment or processes that put constraints on output
    • Employees have some ability to decide which work duties they focus on each day
    • Some operational outcomes are constrained or moderately unconstrained (e.g. an analyst build reports based on client data; while it's possible to find efficiencies and build reports faster, it's not possible to attain the client data any faster)
    • Work quota or targets may be achievable if working fewer hours

    Low degree of flexibility

    • Most or all work duties rely on equipment or processes that put constraints on output (constrained output)
    • Daily work duties are prescribed (e.g. a telemarketer is expected to call a set number of people per day using a set list of contacts and a defined script)
    • Most or all operational outcomes are constrained (e.g. a machine operator works on a machine that produces 100 parts an hour; neither the machine nor the worker can produce more parts)
    • Work quota or targets cannot be achieved if fewer hours are worked

    Note

    For segments with a low degree of work deliverable flexibility (e.g. very constrained output), flexibility is still an option, but maintaining output would require additional headcount.

    1.3 Determine flexibility needs and constraints

    1-2 hours

    Use the guidelines on the preceding slides to document the parameters of each work segment.

    1. Determine work location flexibility. Work location looks at where a segment can complete all or some of their tasks (e.g. onsite vs. remote). For each prioritized employee segment, evaluate the amount of location flexibility available.
    2. Identify work timing. Work timing looks at when work can or needs to be completed (e.g. Monday to Friday, 9am to 5pm).
    3. Examine work deliverables. Work deliverables look at the employee's ability to deliver on their role expectations (e.g. quota or targets) and whether reducing the time spent working would, in all situations, impact the work deliverables (e.g. constrained vs. unconstrained).
    4. Record your outputs on the "Current and Desired State" tab of the workbook.

    Download the Targeted Flexible Work Program Workbook

    Input

    • List of employee segments

    Output

    • Summary of flexibility needs and constraints for each employee segment

    Materials

    • Targeted Flexible Work Program Workbook
      Or
    • Fast-Track Hybrid Work Program Workbook

    Participants

    • Flexible work program committee
    • Employee segment managers

    Step 2

    Identify potential flex options and assess feasibility

    1. Assess employee and organizational flexibility needs
    2. Identify potential flex options and assess feasibility
    3. Implement selected option(s)

    After completing this step you will have:

    • Created a shortlist of potential options for each prioritized employee segment
    • Evaluated the feasibility of each potential option
    • Determined the cost and benefit of each potential option
    • Gathered employee sentiment on potential options
    • Finalized options with senior leadership

    Prepare to identify and assess the feasibility of potential flexible work options

    First, review the Flexible Work Solutions Catalog

    Before proceeding to the next slide, review the Flexible Work Options Catalog to identify and shortlist five to seven flexible work options that are best suited to address the challenges faced for each of the priority employee segments identified in Step 1.

    Then, assess the feasibility of implementing selected options using slides 29 to 32

    Assess the feasibility of implementing the shortlisted solutions for the prioritized employee segments against the feasibility factors in this step. Repeat for each employee segment. Use the following slides to consult with and include leaders when appropriate.

    • Document your analysis in tabs 6 to 8 of the Targeted Flexible Work Program Workbook.
    • Note implementation issues throughout the assessment and record them in the tool. They will be addressed in Step 3: Implement Selected Program(s). Don't rule out an option simply because it presents some challenges; careful implementation can overcome many challenges.
    • At the end of this step, determine the final list of flexible work options and gain approval from senior leaders for implementation.

    Evaluate feasibility by reviewing the option's impact on continued operations and job performance

    Operational coverage

    Synchronous communication

    Time zones

    Face-to-face

    communication

    To what extent are employees needed to deliver products or services?

    • If constant customer service is required, stagger employees' schedules (e.g. one team works Monday-Thursday while another works Tuesday-Friday).

    To what extent do employees need to communicate with each other synchronously?

    • Break the workflow down and identify times when employees do and do not have to work at the same time to communicate with each other.

    To what extent do employees need to coordinate work across time zones?

    • If the organization already operates in different time zones, ensure that the option does not impact operations requiring continuous coverage.
    • When employees are located in different time zones, coordinate schedules based on the other operational factors.

    When do employees need to interact with each other or clients in person?

    • Examine the workflow closely to identify times when face-to-face communication is not required. Schedule "office days" for employees to work together when in-person interaction is needed.
    • When the interaction is only required with clients, determine whether employees are able to meet clients offsite.

    Info-Tech Insight

    Every role is eligible for hybrid location work. If onsite work duties prevent an employee group from participating, see if processes can be digitized or automated. Flexible work is an opportunity to go beyond current needs to future-proof your organization.

    Assess the option's alignment with organizational culture

    Symbols

    Values

    Behaviors

    How supportive of flexible work are the visible aspects of the organization's culture?

    • For example, the mission statement, newsletters, or office layout.
    • Note: Visible elements will need to be adapted to ensure they reinforce the value of the flexible work option.

    How supportive are both the stated and lived values of the organization?

    • When the flexible work option includes less direct supervision, assess how empowered employees feel to make decisions.
    • Assess whether all types of employees (e.g. virtual) are included, valued, and supported.

    How supportive are the attitudes and behaviors, especially of leaders?

    • Leaders set the expectations for acceptable behaviors in the organization. Determine how supportive leaders are toward flexible workers by examining their attitudes and perceptions.
    • Identify if employees are open to different ways of doing work.

    Determine the resources required for the option

    People

    Process

    Technology

    Do employees have the knowledge, skills, and abilities to adopt this option?

    • Identify any areas (e.g. process, technology) employees will need to be trained on and assess the associated costs.
    • Determine whether the option will require additional headcount to ensure operational continuity (e.g. two part-time employees in a job-sharing arrangement) and calculate associated costs (e.g. recruitment, training, benefits).

    How much will work processes need to change?

    • Interview organizational leaders with knowledge of the employee segment's core work processes. Determine whether a significant change will be required.
    • If a significant change is required, evaluate whether the benefits of the option outweigh the costs of the process and behavioral change (see the "net benefit" factor on slide 33).

    What new technologies will be required?

    • Identify the technology (e.g. that supports communication, work processes) required to enable the flexible work option.
    • Note whether existing technology can be used or additional technology will be required, and further investigate the viability and costs of these options.

    Examine the option's risks

    Data

    Health & Safety

    Legal

    How will data be kept secure?

    • Determine whether the organization's data policy and technology covers employees working remotely or other flexible work options.
    • If the employee segment handles sensitive data (e.g. personal employee information), consult relevant stakeholders to determine how data can be kept secure and assess any associated costs.

    How will employees' health and safety be impacted?

    • Consult your organization's legal counsel to determine whether the organization will be liable for the employees' health and safety while working from home or other locations.
    • Determine whether the organization's policies and processes will need to be modified.

    What legal risks might be involved?

    • Identify any policies in place or jurisdictional requirements to avoid any legal risks. Consult your organization's legal counsel about the situations below.
      • If the option causes significant changes to the nature of jobs, creating the risk of constructive dismissal.
      • If there are any risks to providing less supervision (e.g. higher chance of harassment).
      • When only some employee segments are eligible for the option, determine whether there is a risk of inequitable access.
      • If the option impacts any unionized employees or collective agreements.

    Determine whether the benefits of the option outweigh the costs

    Include senior leadership in the net benefit process to ensure any unfeasible options are removed from consideration before presenting to employees.

    1. Document the employee and employer benefits of the option from the previous feasibility factors on slides 29 to 32.
    • Include the benefits of reaching program goals identified in Step 1.
    • Quantify the benefits in dollar value where possible.
  • Document the costs and risks of the option, referring to the costs noted from previous feasibility factors.
    • Quantify the costs in dollar value where possible.
  • Compare the benefits and costs.
    • Add an option to your final list if the benefits are greater than the costs.
  • This is an image of a table with the main heading being Net Benefit, with the following subheadings: Benefits to organization; Benefits to employees; Costs.

    Info-Tech Insight

    Flexible work options must balance organizational and employee needs. If an option is beneficial to employees but there is little or no benefit to the organization as a whole, or if the cost of the option is too high, it will not support the long-term success of the organization.

    2.1a Identify and evaluate flexible work options

    30 minutes per employee segment per work option

    If you are only considering hybrid or remote work, skip to activity 2.1b. Use the guidelines on the preceding slides to conduct feasibility assessments.

    1. Shortlist flexible work options. Review the Flexible Work Options Catalog to identify and shortlist five to seven flexible work options that are best suited to address the challenges faced for each of the priority employee segments. Record these on the "Options Shortlist" tab of the workbook. Even if the decision is simple, ensure you record the rationale to help communicate your decision to employees. Transparent communication is the best way to avoid feelings of unfairness if desired work options are not implemented.
    2. Evaluate option feasibility. For each of the shortlisted options, complete one "Feasibility - Option" tab in the workbook. Make as many copies of this tab as needed.
      • When evaluating each option, consider each employee segment individually as you work through the prompts in the workbook. You may find that segments differ greatly in the feasibility of various types of flexible work. You will use this information to inform your overall policy and any exceptions to it.
      • You may need to involve each segment's management team to get an accurate picture of day-to-day responsibilities and flexible work feasibility.
    3. Weigh benefits and costs. At the end of each flexible work option evaluation, record the anticipated costs and benefits. Discuss whether this balance renders the option viable or rules it out.

    Download the Targeted Flexible Work Program Workbook

    Download the Flexible Work Options Catalog

    Input

    • List of employee segments

    Output

    • Shortlist of flexible work options
    • Feasibility analysis for each work option

    Materials

    • Targeted Flexible Work Program Workbook
    • Flexible Work Options Catalog

    Participants

    • Flexible work program committee
    • Employee segment managers

    2.1b Assess hybrid work feasibility

    30 minutes per employee segment

    Use the guidelines on the preceding slides to conduct a feasibility assessment. This exercise relies on having trialed hybrid or remote work before. If you have never implemented any degree of remote work, consider completing the full feasibility assessment in activity 2.1a.

    1. Evaluate hybrid work feasibility. Review the feasibility prompts on the "Work Unit Remote Work Assessment" tab and record your insight for each employee segment.
      • When evaluating each option, consider each employee segment individually as you work through the prompts in the workbook. You may find that segments differ greatly in their ability to accommodate hybrid work. You will use this information to inform your overall policy and any exceptions to it.
      • You may need to involve each segment's management team to get an accurate picture of day-to-day responsibilities and hybrid work feasibility.

    Download the Fast-Track Hybrid Work Program Workbook

    Input

    • List of employee segments

    Output

    • Feasibility analysis for each work option

    Materials

    • Fast-Track Hybrid Work Program Workbook

    Participants

    • Flexible work program committee
    • Employee segment managers

    Ask employees which options they prefer and gather feedback for implementation

    Deliver a survey and/or conduct focus groups with a selection of employees from all prioritized employee segments.

    Share

    • Present your draft list of options to select employees.
    • Communicate that the organization is in the process of assessing the feasibility of flexible work options and would like employee input to ensure flex work meets needs.
    • Be clear that the list is not final or guaranteed.

    Ask

    • Ask which options are preferred more than others.
    • Ask for feedback on each option – how could it be modified to meet employee needs better? Use this information to inform implementation in Step 3.

    Decide

    • Prioritize an option if many employees indicated an interest in it.
    • If employees indicate no interest in an option, consider eliminating it from the list, unless it will be required. There is no value in providing an option if employees won't use it.

    Survey

    • List the options and ask respondents to rate each on a Likert scale from 1 to 5.
    • Ask some open-ended questions with comment boxes for employee suggestions.

    Focus Group

    • Conduct focus groups to gather deeper feedback.
    • See Appendix I for sample focus group questions.

    Info-Tech Insight

    Prioritize flexible work options that employees want. Providing too many options often leads to information overload and results in employees not understanding what is available, lowering adoption of the flexible work program.

    Finalize options list with senior leadership

    1. Select one to three final options and outline the details of each. Include:
      • Scope: To what extent will the option be applied? E.g. work-from-home one or two days a week.
      • Eligibility: Which employee segments are eligible?
      • Cost: What investment will be required?
      • Critical implementation issues: Will any of the implementation issues identified for each feasibility factor impact whether the option will be approved?
      • Resources: What additional resources will be required (e.g. technology)?
    2. Present the options to stakeholders for approval. Include:
      • An outline of the finalized options, including what the option is and the scope, eligibility, and critical implementation issues.
      • The feasibility assessment results, including benefits, costs, and employee preferences. Have more detail from the other factors ready if leaders ask about them.
      • The investment (cost) required to implement the option.
    3. Proceed to Step 3 to implement approved options.

    Running an IT pilot of flex work

    • As a technology department, IT typically doesn't own flexible work implementation for the entire organization. However, it is common to trial flexible work options for IT first, before rolling out to the entire organization.
    • During a flex work pilot, ensure you are working closely with HR partners, especially regarding regulatory and compliance issues.
    • Keep the rest of the organizational stakeholders in the loop, especially regarding their agreement on the metrics by which the pilot's success will be evaluated.

    2.2a Finalize flexible work options

    2-3 hours + time to gather employee feedback

    If you are only considering hybrid or remote work, skip to activity 2.2b. Use the guidelines on the preceding slides to gather final feedback and finalize work option selections.

    1. Gather employee feedback. If employee preferences are already known, skip this step. If they are not, gather feedback to ascertain whether any of the shortlisted options are preferred. Remember that a successful flexible work program balances the needs of employees and the business, so employee preference is a key determinant in flexible work program success. Document this on the "Employee Preferences" tab of the workbook.
    2. Finalize flexible work options. Use your notes on the cost-benefit balance for each option, along with employee preferences, to decide whether the move forward with it. Record this decision on the "Options Final List" tab. Include information about eligible employee segments and any implementation challenges that came up during the feasibility assessments. This is the final decision summary that will inform your flexible program parameters and policies.

    Download the Targeted Flexible Work Program Workbook

    Input

    • Flexible work options shortlist

    Output

    • Final flexible work options list

    Materials

    • Targeted Flexible Work Program Workbook

    Participants

    • Flexible work program committee

    2.2b Finalize hybrid work parameters

    2-3 hours + time to gather employee feedback

    Use the guidelines on the preceding slides to gather final feedback and finalize work option selections.

    1. Summarize feasibility analysis. On the "Program Parameters" tab, record the main insights from your feasibility analysis. Finalize important elements, including eligibility for hybrid/remote work by employee segment. Additionally, record the standard parameters for the program (i.e. those that apply to all employee segments) and variable parameters (i.e. ones that differ by employee segment).

    Download the Fast-Track Hybrid Work Program Workbook

    Input

    • Hybrid work feasibility analysis

    Output

    • Final hybrid work program parameters

    Materials

    • Fast-Track Hybrid Work Program Workbook

    Participants

    • Flexible work program committee

    Step 3

    Implement selected option(s)

    1. Assess employee and organizational flexibility needs
    2. Identify potential flex options and assess feasibility
    3. Implement selected option(s)

    After completing this step, you will have:

    • Addressed implementation issues and cultural barriers
    • Equipped the organization to adopt flexible work options successfully
    • Piloted the program and assessed its success
    • Developed a plan for program rollout and communication
    • Established a program evaluation plan
    • Aligned HR programs to support the program

    Solve the implementation issues identified in your feasibility assessment

    1. Identify a solution for each implementation issue documented in the Targeted Flexible Work Program Workbook. Consider the following when identifying solutions:
      • Scope: Determine whether the solution will be applied to one or all employee segments.
      • Stakeholders: Identify stakeholders to consult and develop a solution. If the scope is one employee segment, work with organizational leaders of that segment. When the scope is the entire organization, consult with senior leaders.
      • Implementation: Collaborate with stakeholders to solve implementation issues. Balance the organizational and employee needs, referring to data gathered in Steps 1 and 2.

    Example:

    Issue

    Solution

    Option 1: Hybrid work

    Brainstorming at the beginning of product development benefits from face-to-face collaboration.

    Block off a "brainstorming day" when all team members are required in the office.

    Employee segment: Product innovation team

    One team member needs to meet weekly with the implementation team to conduct product testing.

    Establish a schedule with rotating responsibility for a team member to be at the office for product testing; allow team members to swap days if needed.

    Address cultural barriers by involving leaders

    To shift a culture that is not supportive of flexible work, involve leaders in setting an example for employees to follow.

    Misconceptions

    Tactics to overcome them

    • Flexible workers are less productive.
    • Flexible work disrupts operations.
    • Flexible workers are less committed to the organization.
    • Flexible work only benefits employees, not the organization.
    • Employees are not working if they aren't physically in the office.

    Make the case by highlighting challenges and expected benefits for both the organization and employees (e.g. same or increased productivity). Use data in the introductory section of this blueprint.

    Demonstrate operational feasibility by providing an overview of the feasibility assessment conducted to ensure operational continuity.

    Involve most senior leadership in communication.

    Encourage discovery and exploration by having managers try flexible work options themselves, which will help model it for employees.

    Highlight success stories within the organization or from competitors or similar industries.

    Invite input from managers on how to improve implementation and ownership, which helps to discover hidden options.

    Shift symbols, values, and behaviors

    • Work with senior leaders to identify symbols, values, and behaviors to modify to align with the selected flexible work options.
    • Validate that the final list aligns with your organization's mission, vision, and values.

    Info-Tech Insight

    Leaders' collective support of the flexible program determines the program's successful adoption. Don't sweep cultural barriers under the rug; acknowledge and address them to overcome them.

    Equip the organization for successful implementation

    Info-Tech recommends providing managers and employees with a guide to flexible work, introducing policies, and providing training for managers.

    Provide managers and employees with a guide to flexible work

    Introduce appropriate organization policies

    Equip managers with the necessary tools and training

    Use the guide to:

    • Familiarize employees and managers with the flexible work program.
    • Gain employee and manager buy-in and support for the program.
    • Explain the process and give guidance on selecting flexible work options and working with their colleagues to make it a success.

    Use Info-Tech's customizable policy templates to set guidelines, outline arrangements, and scope the organization's flexible work policies. This is typically done by, or in collaboration with, the HR department.

    Download the Guide to Flexible Work for Managers and Employees

    Download the Flex Location Policy

    Download the Flex Time-Off Policy

    Download the Flex Time Policy

    3.1 Prepare for implementation

    2-3 hours

    Use the guidelines on the preceding slides to brainstorm solutions to implementation issues and prepare to communicate program rollout to stakeholders.

    1. Solve implementation issues.
      • If you are working with the Targeted Flexible Work Program Workbook: For each implementation challenge identified on the "Final Options List" tab, brainstorm solutions. If you are working with the Fast-Track Hybrid Work Program Workbook: Work through the program enablement prompts on the "Program Enablement" tab.
      • You may need to involve relevant stakeholders to help you come up with appropriate solutions for each employee segment.
      • Ensure that any anticipated cultural barriers have been documented and are addressed during this step. Don't underestimate the importance of a supportive organizational culture to the successful rollout of flexible work.
    2. Prepare the employee guide. Modify the Guide to Flexible Work for Managers and Employees template to reflect your final work options list and the processes and expectations employees will need to follow.
    3. Create a communication plan. Use Info-Tech's Communicate Any IT Initiative blueprint and Appendix II to craft your messaging.

    Download the Guide to Flexible Work for Managers and Employees

    Download the Targeted Flexible Work Program Workbook

    Input

    • Flexible work options final list

    Output

    • Employee guide to flexible work
    • Flexible work rollout communication plan

    Materials

    • Guide to Flexible Work for Managers and Employees
    • Targeted Flexible Work Program Workbook
      Or
    • Fast-Track Hybrid Work Program Workbook

    Participants

    • Flexible work program committee
    • Employee segment managers

    Run an IT pilot for flexible work

    Prepare for pilot

    Launch Pilot

    Identify the flexible work options that will be piloted.

    • Refer to the final list of selected options for each priority segment to determine which options should be piloted.

    Select pilot participants.

    • If not rolling out to the entire IT department, look for the departments and/or team(s) where there is the greatest need and the biggest interest (e.g. team with lowest engagement scores).
    • Include all employees within the department, or team if the department is too large, in the pilot.
    • Start with a group whose managers are best equipped for the new flexibility options.

    Create an approach to collect feedback and measure the success of the pilot.

    • Feedback can be collected using surveys, focus groups, and/or targeted in-person interviews.

    The length of the pilot will greatly vary based on which flexible work options were selected (e.g. seasonal hours will require a shorter pilot period compared to implementing a compressed work week). Use discretion when deciding on pilot length and be open to extending or shortening the pilot length as needed.

    Launch pilot.

    • Launch the program through a town hall meeting or departmental announcement to build excitement and buy-in.
    • Develop separate communications for employee segments where appropriate. See Appendix II for key messaging to include.

    Gather feedback.

    • The feedback will be used to assess the pilot's success and to determine what modifications will be needed later for a full-scale rollout.
    • When gathering feedback, tailor questions based on the employee segment but keep themes similar. For example:
      • Employees: "How did this help your day-to-day work?"
      • Managers: "How did this improve productivity on your team?"

    Track metrics.

    • The success of the pilot is best communicated using your department's unique KPIs.
    • Metrics are critical for:
      • Accurately determining pilot success.
      • Getting buy-in to expand the pilot beyond IT.
      • Justifying to employees any changes made to the flexible work options.

    Assess the pilot's success and determine next steps

    Review the feedback collected on the previous slide and use this decision tree to decide whether to relaunch a pilot or proceed to a full-scale rollout of the program.

    This is an image of the flow chart used to assess the pilot's success and determine the next steps.  It will help you to determine whether you will Proceed to full-scale rollout on next slide, Major modifications to the option/launch (e.g. change operating time) – adjust and relaunch pilot or select a new employee segment and relaunch pilot, Minor modifications to the option/launch (e.g. introduce additional communications) – adjust and proceed to full scale rollout, or Return to shortlist (Step 2) and select a different option or launch pilot with a different employee segment.

    Prepare for full-scale rollout

    If you have run a team pilot prior to rolling out to all of IT, or run an IT pilot before an organizational rollout, use the following steps to transition from pilot to full rollout.

    1. Determine modifications
      • Review the feedback gathered during the pilot and determine what needs to change for a full-scale implementation.
      • Update HR policies and programs to support flexible work. Work closely with your HR business partner and other organizational leaders to ensure every department's needs are understood and compliance issues are addressed.
    2. Roll out and evaluate
      • Roll out the remainder of the program (e.g. to other employee segments or additional flexible work options) once there is significant uptake of the pilot by the target employee group and issues have been addressed.
      • Determine how feedback will be gathered after implementation, such as during engagement surveys, new hire and exit surveys, stay interviews, etc., and assess whether the program continues to meet employee and organizational needs.

    Rolling out beyond IT

    For a rollout beyond IT, HR will likely take over.

    However, this is your chance to remain at the forefront of your organization's flexible work efforts by continuing to track success and gather feedback within IT.

    Align HR programs and organizational policies to support flexible work

    Talent Management

    Learning & Development

    Talent Acquisition

    Reinforce managers' accountability for the success of flexible work in their teams:

    • Include "managing virtual teams" in the people management leadership competency.
    • Recognize managers who are modeling flexible work.

    Support flexible workers' career progression:

    • Monitor the promotion rates of flexible workers vs. non-flexible workers.
    • Make sure flexible workers are discussed during talent calibration meetings and have access to career development opportunities.

    Equip managers and employees with the knowledge and skills to make flexible work successful.

    • Provide guidance on selecting the right options and maintaining workflow.
    • If moving to a virtual environment, train managers on how to make it a success.

    Incorporate the flexible work program into the organization's employee value proposition to attract top talent who value flexible work options.

    • Highlight the program on the organization's career site and in job postings.

    Organizational policies

    Determine which organizational policies will be impacted as a result of the new flexible work options. For example, the introduction of flex time off can result in existing vacation policies needing to be updated.

    Plan to re-evaluate the program and make improvements

    Collect data

    Collect data

    Act on data

    Uptake

    Gather data on the proportion of employees eligible for each option who are using the option.

    If an option is tracking positively:

    • Maintain or expand the program to more of the organization.
    • Conduct a feasibility assessment (Step 2) for new employee segments.

    Satisfaction

    Survey managers and employees about their satisfaction with the options they are eligible for and provide an open box for suggestions on improvements.

    If an option is tracking negatively:

    • Investigate why. Gather additional data, interview organizational leaders, and/or conduct focus groups to gain deeper insight.
    • Re-assess the feasibility of the option (Step 2). If the costs outweigh the benefits based on new data, determine whether to cancel the option.
    • Take appropriate action based on the outcome of the evaluation, such as modifying or cancelling the option or providing employees with more support.
      • Note: Cancelling an option can impact the engagement of employees using the option. Ensure that the data, reasons for cancelling the option, and potential substitute options are communicated to employees in advance.

    Program goal progress

    Monitor progress against the program goals and metrics identified in Step 1 to evaluate the impact on issues that matter to the organization (e.g. retention, productivity, diversity).

    Career progression

    Evaluate flexible workers' promotion rates and development opportunities to determine if they are developing.

    Info-Tech Insight

    Negative performance of a flexible work option does not necessarily mean failure. Take the time to evaluate whether the option simply needs to be tweaked or whether it truly isn't working for the organization.

    Insight summary

    Overarching insight: IT excels at hybrid location work and is more effective as a business function when location, time, and time-off flexibility are an option for its employees.

    Introduction

    • Flexible work options are not a concession to lower productivity. Properly implemented, flex work enables employees to be more productive at reaching business goals.
    • Employees' lived experiences and needs determine if people use flexible work programs – a flex program that has limited use or excludes people will not benefit the organization.
    • Flexible work benefits everyone. IT employees experience greater engagement, motivation, and company loyalty. IT organizations realize benefits such as better service coverage, reduced facilities costs, and increased productivity.

    Step 1 insight

    • Hybrid work is a start. A comprehensive flex work program extends beyond flexible location to flexible time and time off. Organizations must understand the needs of unique employee groups to uncover the options that will attract and retain talent. Provide greater inclusivity to employees by broadening the scope to include flex location, flex time, and flex time off.
    • No two employee segments are the same. To be effective, flexible work options must align with the expectations and working processes of each segment.

    Step 2 insight

    • Every role is eligible for hybrid location work. If onsite work duties prevent an employee group from participating, see if processes can be digitized or automated. Flexible work is an opportunity to go beyond current needs to future proofing your organization.
    • Flexible work options must balance organizational and employee needs. If an option is beneficial to employees but there is little or no benefit to the organization, or if the cost of the option is too high, it will not support the long-term success of the organization.
    • Prioritize flexible work options that employees want. Providing too many options often leads to information overload and results in employees not understanding what is available, lowering adoption of the flexible work program.

    Step 3 insight

    • Leaders' collective support of the flexible program determines the program's successful adoption. Don't sweep cultural barriers under the rug; acknowledge and address them to overcome them.
    • Negative performance of a flexible work option does not necessarily mean failure. Take the time to evaluate whether the option simply needs to be tweaked or whether it truly isn't working for the organization.
    • A set of formal guidelines for IT ensures flexible work is:
      1. Administered fairly across all IT employees.
      2. Defensible and clear.
      3. Scalable to the rest of the organization.

    Research Contributors and Experts

    Quinn Ross
    CEO
    The Ross Firm Professional Corporation

    Margaret Yap
    HR Professor
    Ryerson University

    Heather Payne
    CEO
    Juno College

    Lee Nguyen
    HR Specialist
    City of Austin

    Stacey Spruell
    Division HR Director
    Travis County

    Don MacLeod
    Chief Administrative Officer
    Zorra Township

    Stephen Childs
    CHRO
    Panasonic North America

    Shawn Gibson
    Sr. Director
    Info Tech Research Group

    Mari Ryan
    CEO/Founder
    Advancing Wellness

    Sophie Wade
    Founder
    Flexcel Networks

    Kim Velluso
    VP Human Resources
    Siemens Canada

    Lilian De Menezes
    Professor of Decision Sciences
    Cass Business School, University of London

    Judi Casey
    WorkLife Consultant and former Director, Work and Family Researchers Network
    Boston College

    Chris Frame
    Partner – Operations
    LiveCA

    Rose M. Stanley, CCP, CBP, WLCP, CEBS
    People Services Manager
    Sunstate Equipment Co., LLC

    Shari Lava
    Director, Vendor Research
    Info-Tech Research Group

    Carol Cochran
    Director of People & Culture
    FlexJobs

    Kidde Kelly
    OD Practitioner

    Dr. David Chalmers
    Adjunct Professor
    Ted Rogers School of Management, Ryerson University

    Kashmira Nagarwala
    Change Manager
    Siemens Canada

    Dr. Isik U. Zeytinoglu
    Professor of Management and Industrial Relations McMaster University, DeGroote School of Business

    Claire McCartney
    Diversity & Inclusion Advisor
    CIPD

    Teresa Hopke
    SVP of Client Relations
    Life Meets Work – www.lifemeetswork.com

    Mark Tippey
    IT Leader and Experienced Teleworker

    Dr. Kenneth Matos
    Senior Director of Research
    Families and Work Institute

    1 anonymous contributor

    Appendix I: Sample focus group questions

    See Info-Tech's Focus Group Guidefor guidance on setting up and delivering focus groups. Customize the guide with questions specific to flexible work (see sample questions below) to gain deeper insight into employee preferences for the feasibility assessment in Step 2 of this blueprint.

    Document themes in the Targeted Flexible Work Program Workbook.

    • What do you need to balance/integrate your work with your personal life?
    • What challenges do you face in achieving work-life balance/integration?
    • What about your job is preventing you from achieving work-life balance/integration?
    • How would [flexible work option] help you achieve work-life balance/integration?
    • How well would this option work with the workflow of your team or department? What would need to change?
    • What challenges do you see in adopting [flexible work option]?
    • What else would be helpful for you to achieve work-life balance/integration?
    • How could we customize [flexible work option] to ensure it meets your needs?
    • If this program were to fail, what do you think would be the top reasons and why?

    Appendix II: Communication key messaging

    1. Program purpose

    Start with the name and high-level purpose of the program.

    2. Business reasons for the program

    Share data you gathered in Step 1, illustrating challenges causing the need for the program and the benefits.

    3. Options selection process

    Outline the process followed to select options. Remember to share the involvement of stakeholders and the planning around employees' feedback, needs, and lived experiences.

    4. Options and eligibility

    Provide a brief overview of the options and eligibility. Specify that the organization is piloting these options and will modify them based on feedback.

    5. Approval not guaranteed

    Qualify that employees need to be "flexible about flexible work" – the options are not guaranteed and may sometimes be unavailable for business reasons.

    6. Shared responsibility

    Highlight the importance of everyone (managers, flexible workers, the team) working together to make flexible work achievable.

    7. Next steps

    Share any next steps, such as where employees can find the organization's Guide to Flexible Work for Managers and Employees, how to make flexible work a success, or if managers will be providing further detail in a team meeting.

    8. Ongoing communications

    Normalize the program and embed it in organizational culture by continuing communications through various media, such as the organization's newsletter or announcements in town halls.

    Works Cited

    Baziuk, Jennifer, and Duncan Meadows. "Global Employee Survey - Key findings and implications for ICMIF." EY, June 2021. Accessed May 2022.
    "Businesses suffering 'commitment issues' on flexible working," EY, 21 Sep. 2021. Accessed May 2022.
    "IT Talent Trends 2022". Info-Tech Research Group, 2022.
    "Jabra Hybrid Ways of Working: 2021 Global Report." Jabra, Aug. 2021. Accessed May 2022.
    LinkedIn Talent Solutions. "2022 Global Talent Trends." LinkedIn, 2022. Accessed May 2022.
    Lobosco, Mark. "The Future of Work is Flexible: 71% of Leaders Feel Pressure to Change Working Models." LinkedIn, 9 Sep. 2021. Accessed May 2022.
    Ohm, Joy, et al. "Covid-19: Women, Equity, and Inclusion in the Future of Work." Catalyst, 28 May 2020. Accessed May 2022.
    Pelta, Rachel. "Many Workers Have Quit or Plan to After Employers Revoke Remote Work." FlexJobs, 2021. Accessed May 2022.
    Slack Future Forum. "Inflexible return-to-office policies are hammering employee experience scores." Slack, 19 April 2022. Accessed May 2022.
    "State of Hybrid Work in IT: A Trend Report". Info-Tech Research Group, 2023.
    Threlkeld, Kristy. "Employee Burnout Report: COVID-19's Impact and 3 Strategies to Curb It." Indeed, 11 March 2021. Accessed March 2022.

    Extend Agile Practices Beyond IT

    • Buy Link or Shortcode: {j2store}175|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Architecture & Strategy
    • Parent Category Link: /architecture-and-strategy
    • Your organization has started to realize benefits from adopting Agile principles and practices. However, these advances are contained within your IT organization.
    • You are seeking to extend Agile development beyond IT into other areas of the organization. You are looking for a coordinated approach aligned to business priorities.

    Our Advice

    Critical Insight

    • Not all lessons from scaling Agile to IT are transferable. IT Agile scaling processes are tailored to IT’s scope, team, and tools, which may not account for diverse attributes within your organization.
    • Control may be necessary for coordination. With increased time-to-value, enforcing consistent cadences, reporting, and communication is a must if teams are not disciplined or lack good governance.
    • Extend Agile in departments tolerant to change. Incrementally roll out Agile in departments where its principles are accepted (e.g. a culture that embraces failures as lessons).

    Impact and Result

    • Complete an assessment of your prior efforts to scale Agile across IT to gauge successful, consistent adoption. Identify the business objectives and the group drivers that are motivating the extension of Agile to the business.
    • Understand the challenges that you may face when extending Agile to business partners. Investigate the root causes of existing issues that can derail your efforts.
    • Ideate solutions to your scaling challenges and envision a target state for your growing Agile environment. Your target state should realize new opportunities to drive more business value and eliminate current activities driving down productivity.
    • Coordinate the implementation and execution of your scaling Agile initiatives with an implementation action plan. This collaborative document will lay out the process, roles, goals, and objectives needed to successfully manage your Agile environment.

    Extend Agile Practices Beyond IT Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should extend Agile practices to improve product delivery, review Info-Tech’s methodology, and understand the ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Assess your readiness to scale agile vertically

    Assess your readiness to scale Agile vertically by identifying and mitigating potential Agile maturity gaps remaining after scaling Agile across your IT organization.

    • Extend Agile Practices Beyond IT – Phase 1: Assess Your Readiness to Scale Agile Vertically
    • Agile Maturity Assessment Tool

    2. Establish an enterprise scaled agile framework

    Complete an overview of various scaled Agile models to help you develop your own customized delivery framework.

    • Extend Agile Practices Beyond IT – Phase 2: Establish an Enterprise Scaled Agile Framework
    • Framework Selection Tool

    3. Create your implementation action plan

    Determine the effort and steps required to implement your extended delivery framework.

    • Extend Agile Practices Beyond IT – Phase 3: Create Your Implementation Action Plan
    [infographic]

    Workshop: Extend Agile Practices Beyond IT

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Assess Current State of Agile Maturity

    The Purpose

    Assess your readiness to scale Agile vertically.

    Identify and mitigate potential Agile maturity gaps remaining after scaling Agile across your IT organization.

    Key Benefits Achieved

    IT Agile maturity gaps identified and mitigated to ensure successful extension of Agile to the business

    Activities

    1.1 Characterize your Agile implementation using the CLAIM model.

    1.2 Assess the maturity of your Agile teams and organization.

    Outputs

    Maturity gaps identified with mitigation requirements

    2 Establish an Enterprise Scaled Agile Framework

    The Purpose

    Complete a review of scaled Agile models to help you develop your own customized delivery framework.

    Key Benefits Achieved

    A customized Agile delivery framework

    Activities

    2.1 Explore various scaled frameworks.

    2.2 Select an appropriate scaled framework for your enterprise.

    2.3 Define the future state of your team and the communication structure of your functional business group.

    Outputs

    Blended framework delivery model

    Identification of team and communication structure impacts resulting from the new framework

    3 Create Your Implementation Action Plan

    The Purpose

    Create your implementation action plan for the new Agile delivery framework.

    Key Benefits Achieved

    A clearly defined action plan

    Activities

    3.1 Define your value drivers.

    3.2 Brainstorm the initiatives that must be completed to achieve your target state.

    3.3 Estimate the effort of your Agile initiatives.

    3.4 Define your Agile implementation action plan.

    Outputs

    List of target state initiatives

    Estimation of effort to achieve target state

    An implementation action plan

    Maximize Your American Rescue Plan Funding

    • Buy Link or Shortcode: {j2store}74|cart{/j2store}
    • member rating overall impact: 9.0/10 Overall Impact
    • member rating average dollars saved: $661,499 Average $ Saved
    • member rating average days saved: 8 Average Days Saved
    • Parent Category Name: Cost & Budget Management
    • Parent Category Link: /cost-and-budget-management
    • Will funding from COVID-19 stimulus opportunities mean more human and financial resources for IT?
    • Are there governance processes in place to successfully execute large projects?
    • What does a large, one-time influx of capital mean for keeping-the-lights-on budgets?
    • How will ARP funding impact your internal resourcing?
    • How can you ensure that IT is not left behind or an afterthought?

    Our Advice

    Critical Insight

    • Seek a one-to-many relationship between IT solutions and business problems. Use the central and overarching nature of IT to identify one solution to multiple business problems that span multiple programs, departments, and agencies.
    • Lack of specific guidance should not be a roadblock to starting. Be proactive by initiating the planning process so that you are ready to act as soon as details are clear.
    • IT involvement is the lynchpin for success. The pandemic has made this theme self-evident, and it needs to stay that way.
    • The fact that this funding is called COVID-19 relief might make you think you should only use it for recovery, but actually it should be viewed as an opportunity to help the organization thrive post-pandemic.

    Impact and Result

    • Shift IT’s role from service provider to innovator. Take ARP funding as a once-in-a-lifetime opportunity to create future enterprise capabilities by thinking big to consider IT innovation that can transform the business and its initiatives for the post-pandemic world.
    • Whether your organization is eligible for a direct or an indirect transfer, be sure you understand the requirements to apply for funding internally through a business case or externally through a grant application.
    • Gain the skills to execute the project with confidence by developing a comprehensive statement of work and managing your projects and vendor relationships effectively.

    Maximize Your American Rescue Plan Funding Research & Tools

    Use our research to help maximize ARP funding.

    Follow Info-Tech's approach to think big, align with the business, analyze budget and staffing, execute with confidence, and ensure compliance and reporting.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    [infographic]

    Workshop: Maximize Your American Rescue Plan Funding

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Think Big

    The Purpose

    Push the boundaries of conventional thinking and consider IT innovations that truly transform the business.

    Key Benefits Achieved

    A list of innovative IT opportunities that your IT department can use to transform the business

    Activities

    1.1 Discuss the objectives of ARP and what they mean to IT departments.

    1.2 Identify drivers for change.

    1.3 Review IT strategy.

    1.4 Augment your IT opportunities list.

    Outputs

    Revised IT vision

    List of innovative IT opportunities that can transform the business

    2 Align With the Business

    The Purpose

    Partner with the business to reprioritize projects and initiatives for the post-pandemic world.

    Key Benefits Achieved

    Assessment of the organization’s new and existing IT opportunities and alignment with business objectives

    Activities

    2.1 Assess alignment of current and new IT initiatives with business objectives.

    2.2 Review and update prioritization criteria for IT projects.

    Outputs

    Preliminary list of IT initiatives

    Revised project prioritization criteria

    3 Analyze IT Budget and Staffing

    The Purpose

    Identify IT budget deficits resulting from pandemic response and discover opportunities to support innovation through new staff and training.

    Key Benefits Achieved

    Prioritized shortlist of business-aligned IT initiative and projects

    Activities

    3.1 Classify initiatives into project categories using ROM estimates.

    3.2 Identify IT budget needs for projects and ongoing services.

    3.3 Identify needs for new staff and skills training.

    3.4 Determine business benefits of proposed projects.

    3.5 Prioritize your organization’s projects.

    Outputs

    Prioritized shortlist of business-aligned IT initiatives and projects

    4 Plan Next Steps

    The Purpose

    Tie IT expenditures to direct transfers or link them to ARP grant opportunities.

    Key Benefits Achieved

    Action plan to obtain ARP funding

    Activities

    4.1 Tie projects to direct transfers, where applicable.

    4.2 Align list of projects to indirect ARP grant opportunities.

    4.3 Develop an action plan to obtain ARP funding.

    4.4 Discuss required approach to project governance.

    Outputs

    Action plan to obtain ARP funding

    Project governance gaps

    Create a Game Plan to Implement Cloud Backup the Right Way

    • Buy Link or Shortcode: {j2store}469|cart{/j2store}
    • member rating overall impact: 7.0/10 Overall Impact
    • member rating average dollars saved: $2,000 Average $ Saved
    • member rating average days saved: 5 Average Days Saved
    • Parent Category Name: Storage & Backup Optimization
    • Parent Category Link: /storage-and-backup-optimization
    • Cloud adoption is frequently driven by hype rather than careful consideration of the best-fit solution.
    • IT is frequently rushed into cloud adoption without appropriate planning.
    • Organizations frequently lack appropriate strategies to deal with cloud-specific backup challenges.
    • Insufficient planning for cloud backup can exacerbate problems rather than solving them, leading to poor estimates of the cost and effort involved, budget overruns, and failure to meet requirements.

    Our Advice

    Critical Insight

    • The cloud isn’t a magic bullet, but it tends to deliver the most value to organizations with specific use cases – frequently smaller organizations who are looking to avoid the cost of building or upgrading a data center.
    • Cloud backup does not necessarily reduce backup costs so much as it moves them around. Cloud backup distributes costs over a longer term. Organizations need to compare the difference in CAPEX and OPEX to determine if making the move makes financial sense.
    • The cloud can deliver a great deal of value for organizations who are looking to reduce the operational effort demanded by an existing tape library for second- or third-tier backups.
    • Data security risks in some cases may be overstated, depending on what on-premises security is available. However, targeting backup to the cloud introduces other risks that need to be considered before implementation is given the green light.

    Impact and Result

    • Understand if cloud backup is the right solution for actual organizational needs.
    • Make an informed decision about targeting backup to the cloud by considering the big picture TCO and effort level involved in adoption.
    • Have a ready strategy to mitigate the most common challenges with cloud adoption projects.
    • Develop a roadmap that lays out the required step-by-step to implement cloud backup.

    Create a Game Plan to Implement Cloud Backup the Right Way Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Understand the benefits and risks of targeting backups to the cloud

    Build a plan to mitigate the risks associated with backing data up in the cloud.

    • Storyboard: Create a Game Plan to Implement Cloud Backup the Right Way

    2. Determine if the cloud can meet the organization's data requirements

    Assess if the cloud is a good fit for your organization’s backup data.

    • Cloud Backup Implementation Game Plan Tool

    3. Mitigate the Challenges of Backing Up to the Cloud

    Build a cloud challenge contingency plan.

    4. Build a Cloud Backup Implementation Roadmap

    Perform a gap analysis to determine cloud backup implementation initiatives.

    Infographic

    Workshop: Create a Game Plan to Implement Cloud Backup the Right Way

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Evaluate the business case for targeting backup at the cloud

    The Purpose

    Understand how cloud backup will affect backup and recovery processes

    Determine backup and recovery objectives

    Assess the value proposition of cloud backup

    Key Benefits Achieved

    A high-level understanding of the benefits of moving to cloud backup

    A best-fit analysis of cloud backup in comparison to organizational needs

    Activities

    1.1 Document stakeholder goals for cloud backup

    1.2 Document present backup processes

    1.3 Document ideal backup processes

    1.4 Review typical benefits of cloud backup

    Outputs

    Documented stakeholder goals

    Current backup process diagrams

    Ideal backup process diagram

    2 Identify candidate data sets and assess opportunities and readiness

    The Purpose

    Identify candidate data sets for cloud-based backup

    Determine RPOs and RTOs for candidate data sets

    Identify potential value specific to each data set for targeting backup at the cloud

    Evaluate organizational readiness for targeting backup at the cloud

    Key Benefits Achieved

    Documented recovery objectives

    Recommendations for cloud backup based on actual organizational needs and readiness

    Activities

    2.1 Document candidate data sets

    2.2 Determine recovery point and recovery time objectives for candidate data sets

    2.3 Identify potential value of cloud-based backup for candidate data sets

    2.4 Discuss the risk and value of cloud-based backup versus an on-premises solution

    2.5 Evaluate organizational readiness for cloud backup

    2.6 Identify data sets to move to the cloud

    Outputs

    Validated list of candidate data sets

    Specific RPOs and RTOs for core data sets

    An assessment of the value of cloud backup for data sets

    A tool-based recommendation for moving backups to the cloud

    3 Mitigate the challenges of backing up to the cloud

    The Purpose

    Understand different cloud provider models and their specific risks

    Identification of how cloud backup will affect IT infrastructure and personnel

    Strategize ways to mitigate the most common challenges of implementing cloud backup

    Understand the client/vendor relationship in cloud backup

    Understand the affect of cloud backup on data security

    Key Benefits Achieved

    Verified best-fit cloud provider model for organizational needs

    Verified strategy for meeting the most common challenges for cloud-based backup

    A strong understanding of how cloud backup will change IT

    Strategies for approaching vendors to ensure a strong footing in negotiations and clear expectations for the client/vendor relationship

    Activities

    3.1 Discuss the impact of cloud backup on infrastructure and IT environment

    3.2 Create a cloud backup risk contingency plan

    3.3 Document compliance and security regulations

    3.4 Identify client and vendor responsibilities for cloud backup

    3.5 Discuss and document the impact of cloud backup on IT roles and responsibilities

    3.6 Compile a list of implementation intiatives

    3.7 Evaluate the financial case for cloud backup

    Outputs

    Cloud risk assessment

    Documented contingency strategies for probabe risks

    Negotiation strategies for dealing with vendors

    A committed go/no-go decision on the value of cloud backup weighted against the effort of implementation

    4 Build a cloud backup implementation roadmap

    The Purpose

    Create a road map for implementing cloud backup

    Key Benefits Achieved

    Determine any remaining gaps between the present state and the ideal state for cloud backup

    Understand the steps and time frame for implementing cloud backup

    Allocate roles and responsibilities for the implementation intitiative

    A validated implementation road map

    Activities

    4.1 Perform a gap analysis to generate a list of implementation intiatives

    4.2 Prioritize cloud backup initiatives

    4.3 Assess risks and dependencies for critical implementation initiatives

    4.4 Assign ownership over implementation tasks

    4.5 Determine road map time frame and structure

    4.6 Populate the roadmap with cloud backup initiatives

    Outputs

    A validated gap analysis

    A prioritized list of cloud backup initiatives

    Documented dependencies and risks associated with implementation tasks

    A roadmap for targeting backups at the cloud

    Negotiate SaaS Agreements That Are Built to Last

    • Buy Link or Shortcode: {j2store}137|cart{/j2store}
    • member rating overall impact: 9.4/10 Overall Impact
    • member rating average dollars saved: $72,298 Average $ Saved
    • member rating average days saved: 10 Average Days Saved
    • Parent Category Name: Vendor Management
    • Parent Category Link: /vendor-management
    • Internal stakeholders usually have different – and often conflicting – needs and expectations that require careful facilitation and management.
    • SaaS solutions bring forth a unique form of “switching costs” that can make a decision to migrate solutions financially, technically, and politically painful.

    Our Advice

    Critical Insight

    • Conservatively, it’s possible to save 5% of the overall IT budget through comprehensive software and SaaS contract review.
    • Focus on the terms and conditions, not just the price.
    • Learning to negotiate is crucial.

    Impact and Result

    • Take control of your SaaS contract negotiations from the beginning.
    • Look at your contract holistically to find cost savings.
    • Guide communication between vendors and your organization for the duration of contract negotiations.
    • Redline the terms and conditions of your SaaS contract.
    • Prioritize crucial terms and conditions to negotiate.

    Negotiate SaaS Agreements That Are Built to Last Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out how to redline and negotiate a SaaS agreement, review Info-Tech’s methodology, and understand the different ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Gather requirements

    Build and manage the stakeholder team, and then document the business use case.

    • Negotiate SaaS Agreements That Are Built to Last – Phase 1: Gather Requirements
    • RASCI Chart
    • Vendor Communication Management Plan
    • Software Business Use Case Template
    • SaaS TCO Calculator

    2. Redline contract

    Redline the proposed SaaS contract.

    • Negotiate SaaS Agreements That Are Built to Last – Phase 2: Redline Contract
    • SaaS Terms and Conditions Evaluation Tool

    3. Negotiate contract

    Create a thorough negotiation plan.

    • Negotiate SaaS Agreements That Are Built to Last – Phase 3: Negotiate Contract
    • SaaS Contract Negotiation Terms Prioritization Checklist
    • Controlled Vendor Communications Letter
    • Key Vendor Fiscal Year End Calendar
    • Contract Negotiation Tactics Playbook
    [infographic]

    Workshop: Negotiate SaaS Agreements That Are Built to Last

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Collect and Review Data

    The Purpose

    Assemble documentation.

    Key Benefits Achieved

    Understand current position before going forward.

    Activities

    1.1 Assemble existing contracts.

    1.2 Document their strategic and tactical objectives.

    1.3 Identify current status of the vendor relationship and any historical context.

    1.4 Clarify goals for ideal future state.

    Outputs

    Business Use Case.

    2 Define the Business Use Case and Build a Stakeholder Team

    The Purpose

    Define the business use case and build a stakeholder team.

    Key Benefits Achieved

    Create a business use case to document functional and non-functional requirements.

    Build an internal cross-functional stakeholder team to negotiate the contract.

    Activities

    2.1 Establish a negotiation team and define roles.

    2.2 Write a communication plan.

    2.3 Complete a business use case.

    Outputs

    RASCI Matrix

    Communications Plan

    SaaS TCO Calculator

    Business Use Case

    3 Redline the Contract

    The Purpose

    Examine terms and conditions and prioritize for negotiation.

    Key Benefits Achieved

    Discover cost savings.

    Improve agreement terms.

    Prioritize terms for negotiation.

    Activities

    3.1 Review general terms and conditions.

    3.2 Review license and application specific terms and conditions.

    3.3 Match to business and technical requirements.

    3.4 Redline the agreement.

    Outputs

    SaaS Terms and Conditions Evaluation Tool

    SaaS Contract Negotiation Terms Prioritization Checklist

    4 Build a Negotiation Strategy

    The Purpose

    Create a negotiation strategy.

    Key Benefits Achieved

    Controlled communication established.

    Negotiation tactics chosen.

    Negotiation timeline plotted.

    Activities

    4.1 Review vendor and application specific negotiation tactics.

    4.2 Build negotiation strategy.

    Outputs

    Contract Negotiation Tactics Playbook

    Controlled Vendor Communications Letter

    Key Vendor Fiscal Year End Calendar

    Execute an Emergency Remote Work Plan

    • Buy Link or Shortcode: {j2store}421|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: DR and Business Continuity
    • Parent Category Link: /business-continuity
    • Many organizations do not have developed plans for how to turn on-premises employees into remote workers in an emergency.
    • In an emergency situation, such as a pandemic, sending employees home to work remotely without time to prepare presents daunting challenges, such as trying to comprehend and prioritize the myriad of tasks that need accomplishing for human resources, the business, and IT in a VUCA (volatile, uncertain, complex, and ambiguous) world.
    • Security issues may arise from employees not used to working remotely. Indeed, employees sent home to work remotely in an emergency may not have been eligible otherwise. This creates security risks, including the proliferation of shadow IT.

    Our Advice

    Critical Insight

    • The emergency will restructure the business: make sure it’s done right. While your organization may need quick fixes for day one of an emergency remote work plan, these are not viable long-term solutions. The emergency will vividly reinforce to the business side that more resources need to be directed to IT to enable strong business continuity and employee safety. Make sure the right plan is put in place during the crucial first weeks. The next emergency is just around the corner.
    • Prioritize key business processes. Before getting into the details of a work from home policy, identify which crucial business processes need to continue for the company to survive. Build the remote work policy around supporting those workflows.
    • Where the “carrot” is not possible, emergencies may require the “stick.” To ensure secure endpoints and prevent proliferation of shadow IT, you may need to enforce certain rules through policy. However, disenfranchising employees is not a long-term solution: once the emergency subsides, use this basis to explore end-user requirements properly and ensure employee-driven adoption plans. Where possible, for this latter scenario, always use the carrot.

    Impact and Result

    • A prioritized plan for IT processes through Info-Tech’s cascading responsibility checklists for emergency remote work.
    • A codified emergency remote work policy document to better prepare for future emergencies.

    Execute an Emergency Remote Work Plan Research & Tools

    Start here

    Read our concise Executive Brief for why you need prioritized emergency remote work checklists and an accompanying policy document and review Info-Tech’s methodology.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    • Execute an Emergency Remote Work Plan Storyboard

    1. Day one preparations

    Prioritize key action items on day one of sending your employees home to remotely work during an emergency.

    • Emergency Remote Work Plan Checklists
    • Home Office Survey
    • Checklist for Securing Remote Workers
    • None
    • Remote Access Policy
    • Equipment Loan Policy
    • None
    • Develop a Security Awareness and Training Program That Empowers End Users – Phases 1-2
    • Remote Work Assignment Log
    • Wiki Collection for Collaboration Tools
    • Pandemic Preparation: The People Playbook

    2. One-to-two weeks preparations

    Address key action items in the one-to-two weeks following an emergency that forced your employees to work remotely.

    • None

    3. Codify an emergency remote work policy

    Turn your emergency remote work checklists into policy.

    • Emergency Remote Work Policy
    • Execute an Emergency Remote Work Plan Executive Presentation
    [infographic]

    Evolve Your Business Through Innovation

    • Buy Link or Shortcode: {j2store}330|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Innovation
    • Parent Category Link: /innovation
    • Innovation teams are tasked with the responsibility of ensuring that their organizations are in the best position to succeed while the world is in a period of turmoil, chaos, and uncertainty.
    • CIOs have been expected to help the organization transition to remote work and collaboration instantaneously.
    • CEOs are under pressure to redesign, and in some cases reinvent, their business model to cope with and compete in a new normal.

    Our Advice

    Critical Insight

    It is easy to get swept up during a crisis and cling to past notions of normal. Unfortunately, there is no controlling the fact that things have changed fundamentally, and it is now incumbent upon you to help your organization adapt and evolve. Treat this as an opportunity because that is precisely what this is.

    Impact and Result

    There are some lessons we can learn from innovators who have succeeded through past crises and from those who are succeeding now.

    There are a number of tactics an innovation team can employ to help their business evolve during this time:

    1. Double down on digital transformation (DX)
    2. Establish a foresight capability
    3. Become a platform for good

    Evolve Your Business Through Innovation Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Evolve your business through innovation

    Download our guide to learn what you can do to evolve your business and innovate your way through uncertainty.

    • Evolve Your Business Through Innovation Storyboard
    [infographic]

    Manage Poor Performance While Working From Home

    • Buy Link or Shortcode: {j2store}599|cart{/j2store}
    • member rating overall impact: 9.0/10 Overall Impact
    • member rating average dollars saved: $1,600 Average $ Saved
    • member rating average days saved: 18 Average Days Saved
    • Parent Category Name: Manage & Coach
    • Parent Category Link: /manage-coach
    • For many, emergency WFH comes with several new challenges such as additional childcare responsibilities, sudden changes in role expectations, and negative impacts on wellbeing. These new challenges, coupled with previously existing ones, can result in poor performance. Owing to the lack of physical presence and cues, managers may struggle to identify that an employee’s performance is suffering. Even after identifying poor performance, it can be difficult to address remotely when such conversations would ideally be held in person.

    Our Advice

    Critical Insight

    • Poor performance must be managed, despite the pandemic. Evaluating root causes of performance issues is more important than ever now that personal factors such as lack of childcare and eldercare for those working from home are complicating the issue.

    Impact and Result

    • Organizations need to have a clear process for improving performance for employees working remotely during the COVID-19 pandemic. Provide managers with resources to help them identify performance issues and uncover their root causes as part of addressing overall performance. This will allow managers to connect employees with the required support while working with them to improve performance.

    Manage Poor Performance While Working From Home Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Follow the remote performance improvement process

    Determine how managers can identify poor performance remotely and help them navigate the performance improvement process while working from home.

    • Manage Poor Performance While Working From Home Storyboard
    • Manage Poor Performance While Working From Home: Manager Guide
    • Manage Poor Performance While Working From Home: Infographic

    2. Clarify roles and leverage resources

    Clarify roles and responsibilities in the performance improvement process and tailor relevant resources.

    • Wellness and Working From Home
    [infographic]

    Further reading

    Manage Poor Performance While Working From Home

    Assess and improve remote work performance with our ready-to-use tools.

    Executive Summary

    McLean & Company Insight

    Poor performance must be managed, despite the pandemic. Evaluating root causes of performance issues is more important than ever now that personal factors such as lack of childcare and eldercare for those working from home are complicating the issue.

    Situation

    COVID-19 has led to a sudden shift to working from home (WFH), resulting in a 72% decline in in-office work (Ranosa, 2020). While these uncertain times have disrupted traditional work routines, employee performance remains critical, as it plays a role in determining how organizations recover. Managers must not turn a blind eye to performance issues but rather must act quickly to support employees who may be struggling.

    Complication

    For many, emergency WFH comes with several new challenges such as additional childcare responsibilities, sudden changes in role expectations, and negative impacts on wellbeing. These new challenges, coupled with previously existing ones, can result in poor performance. Owing to the lack of physical presence and cues, managers may struggle to identify that an employee’s performance is suffering. Even after identifying poor performance, it can be difficult to address remotely when such conversations would ideally be held in person.

    Solution

    Organizations need to have a clear process for improving performance for employees working remotely during the COVID-19 pandemic. Provide managers with resources to help them identify performance issues and uncover their root causes as part of addressing overall performance. This will allow managers to connect employees with the required support while working with them to improve performance.

    Manage Poor Performance While Working From Home is made up of the following resources:

    1

    Identify

    2

    Initiate

    3

    Deploy

    4

    a) Follow Up
    b) Decide
    Storyboard

    This storyboard is organized by the four steps of the performance improvement process: identify, initiate, deploy, and follow up/decide. These will appear on the left-hand side of the slides as a roadmap.

    The focus is on how HR can design the process for managing poor performance remotely and support managers through it while emergency WFH measures are in place. Key responsibilities, email templates, and relevant resources are included at the end.

    Adapt the process as necessary for your organization.

    Manager Guide

    The manager guide contains detailed advice for managers on navigating the process and focuses on the content of remote performance discussions.

    It consists of the following sections:

    • Identifying poor performance.
    • Conducting performance improvement discussions.
    • Uncovering and addressing root causes of poor performance.
    Manager Infographic

    The manager infographic illustrates the high-level steps of the performance improvement process for managers in a visually appealing and easily digestible manner.

    This can be used to easily outline the process, providing managers with a resource to quickly reference as they navigate the process with their direct reports.

    In this blueprint, “WFH” and “remote working” are used interchangeably.

    This blueprint will not cover the performance management framework; it is solely focused on managing performance issues.

    For information on adjusting the regular performance management process during the pandemic, see Performance Management for Emergency Work-From-Home.

    Identify how low performance is normally addressed

    A process for performance improvement is not akin to outlining the steps of a performance improvement plan (PIP). The PIP is a development tool used within a larger process for performance improvement. Guidance on how to structure and use a PIP will be provided later in this blueprint.

    Evaluate how low performance is usually brought to the attention of HR in a non-remote situation:
    • Do managers approach HR for an employee transfer or PIP without having prior performance conversations with the employee?
    • Do managers come to HR when they need support in developing an employee in order to meet expectations?
    • Do managers proactively reach out to HR to discuss appropriate L&D for staff who are struggling?
    • Do some departments engage with the process while others do not?
    Poor performance does not signal the immediate need to terminate an employee. Instead, managers should focus on helping the struggling employee to develop so that they may succeed.
    Evaluate how poor performance is determined:
    • Do managers use performance data or concrete examples?
    • Is it based on a subjective assessment by the manager?
    Keep in mind that “poor performance” now might look different than it did before the pandemic. Employees must be aware of the current expectations placed on them before they can be labeled as underperforming – and the performance expectations must be assessed to ensure they are realistic.

    For information on adjusting performance expectations during the pandemic, see Performance Management for Emergency Work-From-Home.

    The process for non-union and union employees will likely differ. Make sure your process for unionized employees aligns with collective agreements.

    Determine how managers can identify poor performance of staff working remotely

    1

    Identify

    2

    Initiate

    3

    Deploy

    4

    a) Follow Up
    b) Decide
    Identify: Determine how managers can identify poor performance.
    In person, it can be easy to see when an employee is struggling by glancing over at their desk and observing body language. In a remote situation, this can be more difficult, as it is easy to put on a brave face for the half-hour to one-hour check-in. Advise managers on how important frequent one-one-ones and open communication are in helping identify issues when they arise rather than when it’s too late.

    Managers must clearly document and communicate instances where employees aren’t meeting role expectations or are showing other key signs that they are not performing at the level expected of them.

    What to look for:
    • PM data/performance-related assessments
    • Continual absences
    • Decreased quality or quantity of output
    • Frequent excuses (e.g. repeated internet outages)
    • Lack of effort or follow-through
    • Missed deadlines
    • Poor communication or lack of responsiveness
    • Failure to improve
    It’s crucial to acknowledge an employee might have an “off week” or need time to adjust to working from home, which can be addressed with performance management techniques. Managers should move into the process for performance improvement when:
    • Performance fluctuates frequently or significantly.
    • Performance has dropped for an extended period of time.
    • Expectations are consistently not being met.

    While it’s important for managers to keep an eye out for decreased performance, discourage them from over-monitoring employees, as this can lead to a damaging environment of distrust.

    Support managers in initiating performance conversations and uncovering root causes

    1

    Identify

    2

    Initiate

    3

    Deploy

    4

    a) Follow Up
    b) Decide
    Initiate: Require that managers have several conversations about low performance with the employee.
    Before using more formal measures, ensure managers take responsibility for connecting with the employee to have an initial performance conversation where they will make the performance issue known and try to diagnose the root cause of the issue.

    Coach managers to recognize behaviors associated with the following performance inhibitors:

    Personal Factors

    Personal factors, usually outside the workplace, can affect an employee’s performance.

    Lack of clarity

    Employees must be clear on performance expectations before they can be labeled as a poor performer.

    Low motivation

    Lack of motivation to complete work can impact the quality of output and/or amount of work an employee is completing.

    Inability

    Resourcing, technology, organizational change, or lack of skills to do the job can all result in the inability of an employee to perform at their best.

    Poor people skills

    Problematic people skills, externally with clients or internally with colleagues, can affect an employee’s performance or the team’s engagement.

    Personal factors are a common performance inhibitor due to emergency WFH measures. The decreased divide between work and home life and the additional stresses of the pandemic can bring up new cases of poor performance or exacerbate existing ones. Remind managers that all potential root causes should still be investigated rather than assuming personal factors are the problem and emphasize that there can be more than one cause.

    Ensure managers continue to conduct frequent performance conversations

    Once an informal conversation has been initiated, the manager should schedule frequent one-on-one performance conversations (above and beyond performance management check-ins).

    1

    Identify

    2

    Initiate

    3

    Deploy

    4

    a) Follow Up
    b) Decide
    Explain to managers the purpose of these discussions is to:
    • Continue to probe for root causes.
    • Reinforce role expectations and performance targets.
    • Follow up on any improvements.
    • Address the performance issue and share relevant resources (e.g. HR or employee assistance program [EAP]).
    Given these conversations will be remote, require managers to:
    • Use video whenever possible to read physical cues and body language.
    • Bookend the conversation. Starting each meeting by setting the context for the discussion and finishing with the employee reiterating the key takeaways back will ensure there are no misunderstandings.
    • Document the conversation and share with HR. This provides evidence of the conversations and helps hold managers accountable.
    What is HR’s role? HR should ensure that the manager has had multiple conversations with the employee before moving to the next step. Furthermore, HR is responsible for ensuring manages are equipped to have the conversations through coaching, role-playing, etc.

    For more information on the content of these conversations or for material to leverage for training purposes, see Manage Poor Performance While Working From Home: Manager Guide.

    McLean & Company Insight

    Managers are there to be coaches, not therapists. Uncovering the root cause of poor performance will allow managers to pinpoint supports needed, either within their expertise (e.g. coaching, training, providing flexible hours) or by directing the employee to proper external resources such as an EAP.

    Help managers use formal performance improvement tools with remote workers

    1

    Identify

    2

    Initiate

    3

    Deploy

    4

    a) Follow Up
    b) Decide
    Deploy: Use performance improvement tools.
    If initial performance conversations were unsuccessful and performance does not improve, refer managers to performance improvement tools:
    • Suggest any other available support and resources they have not yet recommended (e.g. EAP).
    • Explore options for co-creation of a development plan to increase employee buy-in. If the manager has been diligent about clarifying role expectations, invite the employee to put together their own action plan for meeting performance goals. This can then be reviewed and finalized with the manager.
    • Have the manager use a formal PIP for development and to get the employee back on track. Review the development plan or PIP with the manager before they share it with the employee to ensure it is clear and has time bound, realistic goals for improvement.
    Using a PIP solely to avoid legal trouble and terminate employees isn’t true to its intended purpose. This is what progressive discipline is for.In the case of significant behavior problems, like breaking company rules or safety violations, the manager will likely need to move to progressive discipline. HR should advise managers on the appropriate process.

    When does the issue warrant progressive discipline? If the action needs to stop immediately, (e.g. threatening or inappropriate behavior) and/or as outlined in the collective agreement.

    Clarify remote PIP stages and best practices

    1

    Identify

    2

    Initiate

    3

    Deploy

    4

    a) Follow Up
    b) Decide
    Sample Stages:
    1. Written PIP
    • HR reviews and signs off on PIP
    • Manager holds meeting to provide employee with PIP
    • Employee reviews the PIP
    • Manager and employee provide e-signatures
    • Signed PIP is given to HR
    2. Possible Extension
    3. Final Notice
    • Manager provides employee with final notice if there has been no improvement in agreed time frame
    • Copy of signed final notice letter given to HR

    Who is involved?

    The manager runs the meeting with the employee. HR should act as a support by:

    • Ensuring the PIP is clear, aligned with the performance issue, and focused on development, prior to the meeting.
    • Pointing to resources and making themselves available prior to, during, and after the meeting.
      • When should HR be involved? HR should be present in the meeting if the manager has requested it or if the employee has approached HR beforehand with concerns about the manager. Keep in mind that if the employee sees HR has been unexpectedly invited to the video call, it could add extra stress for them.
    • Reviewing documentation and ensuring expectations and the action plan are reasonable and realistic.

    Determine the length of the PIP

    • The length of the initial PIP will often depend on the complexity of the employee’s role and how long it will reasonably take to see improvements. The minimum (before a potential extension) should be 30-60 days.
    • Ensure the action plan takes sustainment into account. Employees must be able to demonstrate improvement and sustain improved performance in order to successfully complete a PIP.

    Timing of delivery

    Help the manager determine when the PIP meeting will occur (what day, time of day). Take into account the schedule of the employee they will be meeting with (e.g. avoid scheduling right before an important client call).

    1

    Identify

    2

    Initiate

    3

    Deploy

    4

    a) Follow Up
    b) Decide

    Follow up: If the process escalated to step 3 and is successful.

    What does success look like? Performance improvement must be sustained after the PIP is completed. It’s not enough to simply meet performance improvement goals and expectations; the employee must continue to perform.

    Have the manager schedule a final PIP review with the employee. Use video, as this enables the employee and manager to read body language and minimize miscommunication/misinterpretation.

    • If performance expectations have been met, instruct managers to document this in the PIP, inform the employee they are off the PIP, and provide it to HR.

    The manager should also continue check-ins with the employee to ensure sustainment and as part of continued performance management.

    • Set a specific timeline, e.g. every two weeks or every month. Choose a cadence that works best for the manager and employee.

    OR

    Decide: Determine action steps if the process is unsuccessful.

    If at the end of step 3 performance has not sufficiently improved, the organization (HR and the manager) should either determine if the employee could/should be temporarily redeployed while the emergency WFH is still in place, if a permanent transfer to a role that is a better fit is an option, or if the employee should be let go.

    See the Complete Manual for COVID-19 Layoffs blueprint for information on layoffs in remote environments.

    Managers, HR, and employees all have a role to play in performance improvement

    Managers
    • Identify the outcomes the organization is looking for and clearly outline and communicate the expectations for the employee’s performance.
    • Diagnose root cause(s) of the performance issue.
    • Support employee through frequent conversations and feedback.
    • Coach for improved performance.
    • Visibly recognize and broadcast employee achievements.
    Employees
    • Have open and honest conversations with their manager, acknowledge their accountability, and be receptive to feedback.
    • Set performance goals to meet expectations of the role.
    • Prepare for frequent check-ins regarding improvement.
    • Seek support from HR as required.
    HR
    • Provide managers with a process, training, and support to improve employee performance.
    • Coach managers to ensure employees have been made aware of their role expectations and current performance and given specific recommendations on how to improve.
    • Reinforce the process for improving employee performance to ensure that adequate coaching conversations have taken place before the formal PIP.
    • Coach employees on how to approach their manager to discuss challenges in meeting expectations.

    HR should conduct checkpoints with both managers and employees in cases where a formal PIP was initiated to ensure the process for performance improvement is being followed and to support both parties in improving performance.

    Email templates

    Use the templates found on the next slides to draft communications to employees who are underperforming while working from home.

    Customize all templates with relevant information and use them as a guide to further tailor your communication to a specific employee.

    Customization Recommendations

    Review all slides and adjust the language or content as needed to suit the needs of the employee, the complexity of their role, and the performance issue.

    • The pencil icon to the left denotes slides requiring customization of the text. Customize text in grey font and be sure to convert all font to black when you are done.

    Included Templates

    1. Performance Discussion Follow-Up
    2. PIP Cover Letter

    This template is not a substitute for legal advice. Ensure you consult with your legal counsel, labor relations representative, and union representative to align with collective agreements and relevant legislation.

    Sample Performance Discussion Follow-Up

    Hello [name],

    Thank you for the commitment and eagerness in our meeting yesterday.

    I wanted to recap the conversation and expectations for the month of [insert month].

    As discussed, you have been advised about your recent [behavior, performance, attendance, policy, etc.] where you have demonstrated [state specific issue with detail of behavior/performance of concern]. As per our conversation, we’ll be working on improvement in this area in order to meet expectations set out for our employees.

    It is expected that employees [state expectations]. Please do not hesitate to reach out to me if there is further clarification needed or you if you have any questions or concerns. The management team and I are committed to helping you achieve these goals.

    We will do a formal check-in on your progress every [insert day] from [insert time] to review your progress. I will also be available for daily check-ins to support you on the right track. Additionally, you can book me in for desk-side coaching outside of my regular desk-side check-ins. If there is anything else I can do to help support you in hitting these goals, please let me know. Other resources we discussed that may be helpful in meeting these objectives are [summarize available support and resources]. By working together through this process, I have no doubt that you can be successful. I am here to provide support and assist you through this.

    If you’re unable to show improvements set out in our discussion by [date], we will proceed to a formal performance measure that will include a performance improvement plan. Please let me know if you have any questions or concerns; I am here to help.

    Please acknowledge this email and let me know if you have any questions.

    Thank you,

    PIP Cover Letter

    Hello [name] ,

    This is to confirm our meeting on [date] in which we discussed your performance to date and areas that need improvement. Please find the attached performance improvement plan, which contains a detailed action plan that we have agreed upon to help you meet role expectations over the next [XX days]. The aim of this plan is to provide you with a detailed outline of our performance expectations and provide you the opportunity to improve your performance, with our support.

    We will check in every [XX days] to review your progress. At the end of the [XX]-day period, we will review your performance against the role expectations set out in this performance improvement plan. If you don’t meet the performance requirements in the time allotted, further action and consequences will follow.

    Should you have any questions about the performance improvement plan or the process outlined in this document, please do not hesitate to discuss them with me.

    [Employee name], it is my personal objective to help you be a fully productive member of our team. By working together through this performance improvement plan, I have no doubt that you can be successful. I am here to provide support and assist you through the process. At this time, I would also like to remind you about the [additional resources available at your organization, for example, employee assistance program or HR].

    Please acknowledge this email and let me know if you have any questions.

    Thank you,

    Prepare and customize manager guide and resources

    Sample of Manage Poor Performance While Working From Home: Manager Guide. Manage Poor Performance While Working From Home: Manager Guide

    This tool for managers provides advice on navigating the process and focuses on the content of remote performance discussions.

    Sample of Set Meaningful Employee Performance Measures. Set Meaningful Employee Performance Measures

    See this blueprint for information on setting holistic measures to inspire employee performance.

    Sample of Manage Poor Performance While Working From Home: Infographic. Manage Poor Performance While Working From Home: Infographic

    This tool illustrates the high-level steps of the performance improvement process.

    Sample of Wellness and Working From Home: Infographic. Wellness and Working From Home: Infographic

    This tool highlights tips to manage physical and mental health while working from home.

    Sample of Build a Better Manager: Team Essentials. Build a Better Manager: Team Essentials

    See this solution set for more information on kick-starting the effectiveness of first-time IT managers with essential management skills.

    Sample of Leverage Agile Goal Setting for Improved Employee Engagement & Performance. Leverage Agile Goal Setting for Improved Employee Engagement & Performance

    See this blueprint for information on dodging the micromanaging foul and scoring with agile short-term goal setting.

    Bibliography

    Arringdale, Chris. “6 Tips For Managers Trying to Overcome Performance Appraisal Anxiety.” TLNT. 18 September 2015. Accessed 2018.

    Borysenko, Karlyn. “What Was Management Thinking? The High Cost of Employee Turnover.” Talent Management and HR. 22 April 2015. Accessed 2018.

    Cook, Ian. “Curbing Employee Turnover Contagion in the Workplace.” Visier. 20 February 2018. Accessed 2018.

    Cornerstone OnDemand. Toxic Employees in the Workplace. Santa Monica, California: Cornerstone OnDemand, 2015. Web.

    Dewar, Carolyn and Reed Doucette. “6 elements to create a high-performing culture.” McKinsey & Company. 9 April 2018. Accessed 2018.

    Eagle Hill. Eagle Hill National Attrition Survey. Washington, D.C.: Eagle Hill, 2015. Web.

    ERC. “Performance Improvement Plan Checklist.” ERC. 21 June 2017. Accessed 2018.

    Foster, James. “The Impact of Managers on Workplace Engagement and Productivity.” Interact. 16 March 2017. Accessed 2018.

    Godwins Solicitors LLP. “Employment Tribunal Statistics for 2015/2016.” Godwins Solicitors LLP. 8 February 2017. Accessed 2018.

    Mankins, Michael. “How to Manage a Team of All-Stars.” Harvard Business Review. 6 June 2017. Accessed 2018.

    Maxfield, David, et al. The Value of Stress-Free Productivity. Provo, Utah: VitalSmarts, 2017. Web.

    Murphy, Mark. “Skip Your Low Performers When Starting Performance Appraisals.” Forbes. 21 January 2015. Accessed 2018.

    Quint. “Transforming into a High Performance Organization.” Quint Wellington Redwood. 16 November 2017. Accessed 2018.

    Ranosa, Rachel. "COVID -19: Canadian Productivity Booms Despite Social Distancing." Human Resources Director, 14 April 2020. Accessed 2020.

    Accelerate Business Growth and Valuation by Building Brand Awareness

    • Buy Link or Shortcode: {j2store}569|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Marketing Solutions
    • Parent Category Link: /marketing-solutions

    Brands that fail to invest in brand awareness are likely to face some, if not all these problems:

    • Lack of brand visibility and recognition
    • Inability to reach and engage with the buyers
    • Difficulties generating and converting leads
    • Low customer retention rate
    • Inability to justify higher pricing
    • Limited brand equity, business valuation, and sustainability

    Our Advice

    Critical Insight

    Awareness brings visibility and traction to brands, which is essential in taking the market leadership position and becoming the trusted brand that buyers think of first.

    Brand awareness also significantly contributes to increasing brand equity, market valuation, and business sustainability.

    Impact and Result

    Building brand awareness allows for the increase of:

    • Brand visibility, perception, recognition, and reputation
    • Interactions and engagement with the target audience
    • Digital advertising performance and ROI
    • Conversion rates and sales wins
    • Revenue and profitability
    • Market share & share of voice (SOV)
    • Talents, partners, and investors attraction and retention
    • Brand equity, business growth, and market valuation

    Accelerate Business Growth and Valuation by Building Brand Awareness Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Accelerate Business Growth and Valuation by Building Brand Awareness Storyboard - Learn how to establish the brand foundation, create assets and workflows, and deploy effective brand awareness strategies and tactics.

    A two-step approach to building brand awareness, starting with defining the brand foundations and then implementing effective brand awareness strategies and tactics.

    • Accelerate Business Growth and Valuation by Building Brand Awareness Storyboard

    2. Define Brand's Personality and Message - Analyze your target market and develop key elements of your brand guidelines.

    With this set of tools, you will be able to capture and analyze your target market, your buyers and their journeys, define your brand's values, personality, and voice, and develop all the key elements of your brand guidelines to enable people within your organization and external resources to build a consistent and recognizable image across all assets and platforms.

    • Market Analysis Template
    • Brand Recognition Survey and Interview Questionnaire and List Template
    • External and Internal Factors Analysis Template
    • Buyer Personas and Journey Presentation Template
    • Brand Purpose, Mission, Vision, and Values Template
    • Brand Value Proposition and Positioning Statement
    • Brand Voice Guidelines Template
    • Writing Style Guide Template
    • Brand Messaging Template
    • Writer Checklist

    3. Start Building Brand Awareness - Achieve strategic alignment.

    These tools will allow you to achieve strategic alignment and readiness, create assets and workflows, deploy tactics, establish Key Performance Indicators (KPIs), and monitor and optimize your strategy on an ongoing basis.

    • Brand Awareness Strategy and Tactics Template
    • Asset Creation and Management List
    • Campaign Workflows Template
    • Brand Awareness Strategy Rollout Plan Template
    • Survey Emails Best Practices Guidelines

    Infographic

    Further reading

    Accelerate Business Growth and Valuation By Building Brand Awareness

    Develop and deploy comprehensive, multi-touchpoint brand awareness strategies to become the trusted brand that buyers think of first.

    EXECUTIVE BRIEF

    Analyst perspective

    Building brand awareness

    Achieving high brand awareness in a given market and becoming the benchmark for buyers

    is what every brand wants to achieve, as it is a guarantee of success. Building brand awareness,

    even though its immediate benefits are often difficult to see and measure, is essential for companies that want to stand out from their competitors and continue to grow in a sustainable way. The return on investment (ROI) may take longer, but the benefits are also greater than those achieved through short-term initiatives with the expectation of immediate, albeit often limited, results.

    Brands that are familiar to their target market have greater credibility, generate more sales,

    and have a more loyal customer base. CMOs that successfully execute brand awareness programs

    build brand equity and grow company valuation.

    This is a picture of Nathalie Vezina

    Nathalie Vezina
    Marketing Research Director
    SoftwareReviews Advisory

    Executive summary

    Brand leaders know that brand awareness is essential to the success of all marketing and sales activities. Brands that fail to invest in brand awareness are likely to face some, if not all these problems:

    • Lack of brand visibility and compelling storytelling.
    • Inability to reach the target audience.
    • Low engagement on digital platforms and with ads.
    • Difficulties generating and converting leads, or closing/winning sales/deals, and facing a high cost per acquisition.
    • Low/no interest or brand recognition, trust level, and customer retention rate.
    • Inability to justify higher pricing.

    Convincing stakeholders of the benefits of strong brand awareness can be difficult when the positive outcomes are hard to quantify, and the return on investment (ROI) is often long-term. Among the many obstacles brand leaders must overcome are:

    • Lack of longer-term corporate vision, focusing all efforts and resources on short-term growth strategies for a quick ROI.
    • Insufficient market and target buyers' information and understanding of the brand's key differentiator.
    • Misalignment of brand message, and difficulties creating compelling content that resonates with the target audience, generates interest, and keeps them engaged.
    • Limited or no resources dedicated to the development of the brand.

    Inspired by top-performing businesses and best practices, this blueprint provides the guidance and tools needed to successfully build awareness and help businesses grow. By following these guidelines, brand leaders can expect to:

    • Gain market intelligence and a clear understanding of the buyer's needs, your competitive advantage, and key differentiator.
    • Develop a clear and compelling value proposition and a human-centric brand messaging driven by the brand's values.
    • Increase online presence and brand awareness to attract and engage with buyers.
    • Develop a long-term brand strategy and execution plan.

    "A brand is the set of expectations, memories, stories, and relationships that, taken together, account for a consumer's decision to choose one product or service over another."

    – Seth Godin

    What is brand awareness?

    The act of making a brand visible and memorable.

    Brand awareness is the degree to which buyers are familiar with and recognize the attributes and image of a particular brand, product, or service. The higher the level of awareness, the more likely the brand is to come into play when a target audience enters the " buying consideration" phase of the buyer's journey.

    Brand awareness also plays an important role in building equity and increasing business valuation. Brands that are familiar to their target market have greater credibility, drive more sales and have a more loyal customer base.
    Building brand awareness allows increasing:

    • Brand visibility, perception, recognition, and reputation
    • Interactions and engagement with the target audience
    • Digital advertising performance and ROI
    • Conversion rates and sales wins
    • Revenue and profitability
    • Market share and share of voice (SOV)
    • Talents, partners, and investors attraction and retention
    • Brand equity, business growth, and market valuation

    "Products are made in a factory, but brands are created in the mind."
    Source: Walter Landor

    Capitalizing on a powerful brand

    A longer-term approach for an increased and more sustainable ROI.

    Market leader position

    Developing brand awareness is essential to increase the visibility and traction of a brand.

    Several factors may cause a brand to be not well-known. One reason might be that the brand recently launched, such as a startup. Another reason could be that the brand has rebranded or entered a new market.

    To become the trusted brand that buyers think of first in their target markets, it is critical for these brands to develop and deploy comprehensive, multi-touchpoint brand awareness strategies.

    A relationship leading to loyalty

    A longer-term brand awareness strategy helps build a strong relationship between the brand and the buyer, fostering a lasting and rewarding alliance.

    It also enables brands to reach and engage with their target audience effectively by using compelling storytelling and meaningful content.

    Adopting a more human-centric approach and emphasizing shared values makes the brand more attractive to buyers and can drive sales and gain loyalty.

    Sustainable business growth

    For brands that are not well established in their target market, short-term tactics that focus on immediate benefits can be ineffective. In contrast, long-term brand awareness strategies provide a more sustainable ROI (return on investment).

    Investing in building brand awareness can impact a business's ability to interact with its target audience, generate leads, and increase sales. Moreover, it can significantly contribute to boosting the business's brand equity and market valuation.

    "Quick wins may work in the short term, but they're not an ideal substitute for long-term tactics and continued success."
    Source: Forbes

    Impacts of low brand awareness on businesses

    Unfamiliar brands, despite their strong potential, won't thrive unless they invest in their notoriety.

    Brands that choose not to invest in longer-term awareness strategies and rely solely on short-term growth tactics in hopes of an immediate gain will see their ability to grow diminished and their longevity reduced due to a lack of market presence and recognition.

    Symptoms of a weakening brand include:

    • High marketing spending and limited result
    • Low market share or penetration
    • Low sales, revenue, and gross margin
    • Weak renewal rate, customer retention, and loyalty
    • Difficulties delivering on the brand promise, low/no trust in the brand
    • Limited brand equity, business valuation, and sustainability
    • Unattractive brand to partners and investors

    "Your brand is the single most important investment you can make in your business."
    Source: Steve Forbes

    Most common obstacles to increasing brand awareness

    Successfully building brand awareness requires careful preparation and planning.

    • Limited market intelligence
    • Unclear competitive advantage/key differentiator
    • Misaligned and inconsistent messaging and storytelling
    • Lack of long-term vision
    • and low prioritization
    • Limited resources to develop and execute brand awareness building tactics
    • Unattractive content that does not resonate, generates little or no interest and engagement

    Investing in the notoriety of the brand

    Become the top-of-mind brand in your target market.

    To stand out, be recognized by their target audience, and become major players in their industry, brands must adopt a winning strategy that includes the following elements:

    • In-depth knowledge and understanding of the market and audience
    • Strengthening digital presence and activities
    • Creating and publishing content relevant to the target audience
    • Reaching out through multiple touchpoints
    • Using a more human-centric approach
    • Ensure consistency in all aspects of the brand, across all media and channels

    How far are you from being the brand buyers think of first in your target market?

    This is an image of the Brand Awareness Pyramid.

    Brand awareness pyramid

    Based on David Aaker's brand loyalty pyramid

    Tactics for building brand awareness

    Focus on effective ways to gain brand recognition in the minds of buyers.

    This is an image of the Brand Awareness Journey Roadmap.

    Brand recognition requires in-depth knowledge of the target market, the creation of strong brand attributes, and increased presence and visibility.

    Understand the market and audience you're targeting

    Be prepared. Act smart.

    To implement a winning brand awareness-building strategy, you must:

    • Be aware of your competitor's strengths and weaknesses, as well as yours.
    • Find out who is behind the keyboard, and the user experience they expect to have.
    • Plan and continuously adapt your tactics accordingly.
    • Make your buyer the hero.

    Identify the brands' uniqueness

    Find your "winning zone" and how your brand uniquely addresses buyers' pain points.

    Focus on your key differentiator

    A brand has found its "winning zone" or key differentiator when its value proposition clearly shows that it uniquely solves its buyers' specific pain points.

    Align with your target audience's real expectations and successfully interact with them by understanding their persona and buyer's journey. Know:

    • How you uniquely address their pain points.
    • Their values and what motivates them.
    • Who they see as authorities in your field.
    • Their buying habits and trends.
    • How they like brands to engage with them.

    An image of a Venn diagram between the following three terms: Buyer pain point; Competitors' value proposition; your unique value proposition.  The overlapping zone is labeled the Winning zone.  This is your key differentiator.

    Give your brand a voice

    Define and present a consistent voice across all channels and assets.

    The voice reflects the personality of the brand and the emotion to be transmitted. That's why it's crucial to establish strict rules that define the language to use when communicating through the brand's voice, the type of words, and do's and don'ts.

    To be recognizable it is imperative to avoid inconsistencies. No matter how many people are behind the brand voice, the brand must show a unique, distinctive personality. As for the tone, it may vary according to circumstances, from lighter to more serious.

    Up to 80% Increased customer recognition when the brand uses a signature color scheme across multiple platforms
    Source: startup Bonsai
    23% of revenue increase is what consistent branding across channels leads to.
    Source: Harvard Business Review

    When we close our eyes and listen, we all recognize Ella Fitzgerald's rich and unique singing voice.

    We expect to recognize the writing of Stephen King when we read his books. For the brand's voice, it's the same. People want to be able to recognize it.

    Adopt a more human-centric approach

    If your brand was a person, who would it be?

    Human attributes

    Physically attractive

    • Brand identity
    • Logo and tagline
    • Product design

    Intellectually stimulating

    • Knowledge and ideas
    • Continuous innovation
    • Thought leadership

    Sociable

    • Friendly, likeable and fun
    • Confidently engage with audience through multiple touchpoints
    • Posts and shares meaningful content
    • Responsive

    Emotionally connected

    • Inspiring
    • Powerful influencer
    • Triggers emotional reactions

    Morally sound

    • Ethical and responsible
    • Value driven
    • Deliver on its promise

    Personable

    • Honest
    • Self-confident and motivated
    • Accountable

    0.05 Seconds is what it takes for someone to form an opinion about a website, and a brand.
    Source: 8ways

    90% of the time, our initial gut reaction to products is based on color alone.
    Source: startup Bonsai

    56% of the final b2b purchasing decision is based on emotional factors.
    Source: B@B International

    Put values at the heart of the brand-buyers relationship

    Highlight values that will resonate with your audience.

    Brands that focus on the values they share with their buyers, rather than simply on a product or service, succeed in making meaningful emotional connections with them and keep them actively engaged.

    Shared values such as transparency, sustainability, diversity, environmental protection, and social responsibility become the foundation of a solid relationship between a brand and its audience.

    The key is to know what motivates the target audience.

    86% of consumers claim that authenticity is one of the key factors they consider when deciding which brands they like and support.
    Source: Business Wire

    56% of the final decision is based on having a strong emotional connection with the supplier.
    Source: B2B International

    64% of today's customers are belief-driven buyers; they want to support brands that "can be a powerful force for change."
    Source: Edelman

    "If people believe they share values with a company, they will stay loyal to the brand."
    – Howard Schultz
    Source: Lokus Design

    Double-down on digital

    Develop your digital presence and reach out to your target audiences through multiple touchpoints.

    Beyond engaging content, reaching the target audience requires brands to connect and interact with their audience in multiple ways so that potential buyers can form an opinion.

    With the right message consistently delivered across multiple channels, brands increase their reach, create a buzz around their brand and raise awareness.

    73% of today's consumers confirm they use more than one channel during a shopping journey
    Source: Harvard Business Review

    Platforms

    • Website and apps
    • Social media
    • Group discussions

    Multimedia

    • Webinars
    • Podcasts
    • Publication

    Campaign

    • Ads and advertising
    • Landing pages
    • Emails, surveys drip campaigns

    Network

    • Tradeshows, events, sponsorships
    • Conferences, speaking opportunities
    • Partners and influencers

    Use social media to connect

    Reach out to the masses with a social media presence.

    Social media platforms represent a cost-effective opportunity for businesses to connect and influence their audience and tell their story by posting relevant and search-engine-optimized content regularly on their account and groups. It's also a nice gateway to their website.

    Building a relationship with their target buyer through social media is also an easy way for businesses to:

    • Understand the buyers.
    • Receive feedback on how the buyers perceive the brand and how to improve it.
    • Show great user experience and responsiveness.
    • Build trust.
    • Create awareness.

    75% of B2B buyers and 84% of C-Suite executives use social media when considering a purchase
    Source: LinkedIn Business

    92% of B2B buyers use social media to connect with leaders in the sales industry.
    Source: Techjury

    With over 4.5 billion social media users worldwide, and 13 new users signing up to their first social media account every second, social media is fast becoming a primary channel of communication and social interaction for many.
    Source: McKinsey

    Become the expert subject matter

    Raise awareness with thought leadership content.

    Thought leadership is about building credibility
    by creating and publishing meaningful, relevant content that resonates with a target audience.
    Thought leaders write and publish all kinds of relevant content such as white papers, ebooks, case studies, infographics, video and audio content, webinars, and research reports.
    They also participate in speaking opportunities, live presentations, and other high-visibility forums.
    Well-executed thought leadership strategies contribute to:

    • Raise awareness.
    • Build credibility.
    • Be recognized as a subject expert matter.
    • Become an industry leader.

    60% of buyers say thought leadership builds credibility when entering a new category where the brand is not already known.
    Source: Edelman | LinkedIn

    70% of people would rather learn about a company through articles rather than advertising.
    Source: Brew Interactive

    57% of buyers say that thought leadership builds awareness for a new or little-known brand.
    Source: Edelman | LinkedIn

    To achieve best results

    • Know the buyers' persona and journey.
    • Create original content that matches the persona of the target audience and that is close to their values.
    • Be Truthful and insightful.
    • Find the right tone and balance between being human-centric, authoritative, and bold.
    • Be mindful of people's attention span and value their time.
    • Create content for each phase of the buyer's journey.
    • Ensure content is SEO, keyword-loaded, and add calls-to-action (CTAs).
    • Add reason to believe, data to support, and proof points.
    • Address the buyers' pain points in a unique way.

    Avoid

    • Focusing on product features and on selling.
    • Publishing generic content.
    • Using an overly corporate tone.

    Promote personal branding

    Rely on your most powerful brand ambassadors and influencers: your employees.

    The strength of personal branding is amplified when individuals and companies collaborate to pursue personal branding initiatives that offer mutual benefits. By training and positioning key employees as brand ambassadors and industry influencers, brands can boost their brand awareness through influencer marketing strategies.

    Personal branding, when well aligned with business goals, helps brands leverage their key employee's brands to:

    • Increase the organization's brand awareness.
    • Broaden their reach and circle of influence.
    • Show value, gain credibility, and build trust.
    • Stand out from the competition.
    • Build employee loyalty and pride.
    • Become a reference to other businesses.
    • Increase speaking opportunities.
    • Boost qualified leads and sales.

    About 90% of organizations' employee network tends to be completely new to the brand.
    Source: Everyone Social

    8X more engagement comes from social media content shared by employees rather than brand accounts.
    Source: Entrepreneur

    561% more reach when brand messages are shared by employees on social media, than the same message shared by the Brand's social media.
    Source: Entrepreneur

    "Personal branding is the art of becoming knowable, likable and trustable."
    Source: Founder Jar, John Jantsch

    Invest in B2B influencer marketing

    Broaden your reach and audiences by leveraging the voice of influencers.

    Influencers are trusted industry experts and analysts who buyers can count on to provide reliable information when looking to make a purchase.

    Influencer marketing can be very effective to reach new audiences, increase awareness, and build trust. But finding the right influencers with the level of credibility and visibility brands are expecting can sometimes be challenging.

    Search for influencers that have:

    • Relevance of audience and size.
    • Industry expertise and credibility.
    • Ability to create meaningful content (written, video, audio).
    • Charismatic personality with values consistent with the brand.
    • Frequent publications on at least one leading media platform.

    76% of people say that they trust content shared by people over a brand.
    Source: Adweek


    44% increased media mention of the brand using B2B influencer marketers.
    Source: TopRank Marketing

    Turn your customers into brand advocates

    Establish customer advocacy programs and deliver a great customer experience.

    Retain your customers and turn them into brand advocates by building trust, providing an exceptional experience, and most importantly, continuously delivering on the brand promise.

    Implement a strong customer advocacy program, based on personalized experiences, the value provided, and mutual exchange, and reap the benefits of developing and growing long-term relationships.

    92% of individuals trust word-of-mouth recommendations, making it one of the most trust-rich forms of advertising.
    Source: SocialToaster

    Word-of-mouth (advocacy) marketing increases marketing effectiveness by 54%
    Source: SocialToaster

    Make your brand known and make it stick in people's minds

    Building and maintaining high brand awareness requires that each individual within the organization carry and deliver the brand message clearly and consistently across all media whether in person, in written communications, or otherwise.

    To achieve this, brand leaders must first develop a powerful, researched narrative that people will embrace and convey, which requires careful preparation.

    Target market and audience intel

    • Target market Intel
    • Buyer persona and journey/pain points
    • Uniqueness and positioning

    Brand attributes

    • Values at the heart of the relationship
    • Brand's human attributes

    Brand visibly and recall

    • Digital and social media presence
    • Thought leadership
    • Personal branding
    • Influencer marketing

    Brand awareness building plan

    • Long-term awareness and multi-touchpoint approach
    • Monitoring and optimization

    Short and long-term benefits of increasing brand awareness

    Brands are built over the long term but the rewards are high.

    • Stronger brand perception
    • Improved engagement and brand associations
    • Enhanced credibility, reputation, and trust
    • Better connection with customers
    • Increased repeat business
    • High-quality leads
    • Higher and faster conversion rate
    • More sales closed/ deals won
    • Greater brand equity
    • Accelerated growth

    "Strong brands outperform their less recognizable competitors by as much as 73%."
    Source: McKinsey

    Brand awareness building

    Building brand awareness, even though immediate benefits are often difficult to see and measure, is essential for companies to stand out from their competitors and continue to grow in a sustainable way.

    To successfully raise awareness, brands need to have:

    • A longer-term vision and strategy.
    • Market Intelligence, a clear value proposition, and key differentiator.
    • Consistent, well-aligned messaging and storytelling.
    • Digital presence and content.
    • The ability to reach out through multiple touchpoints.
    • Necessary resources.

    Without brand awareness, brands become less attractive to buyers, talent, and investors, and their ability to grow, increase their market value, and be sustainable is reduced.

    Brand awareness building methodology

    Define brands' personality and message

    • Gather market intel and analyze the market.
    • Determine the value proposition and positioning.
    • Define the brand archetype and voice.
    • Craft a compelling brand message and story.
    • Get all the key elements of your brand guidelines.

    Start building brand awareness

    • Achieve strategy alignment and readiness.
    • Create and manage assets.
    • Deploy your tactics, assets, and workflows.
    • Establish key performance indicators (KPIs).
    • Monitor and optimize on an ongoing basis.

    Toolkit

    • Market and Influencing Factors Analysis
    • Recognition Survey and Best Practices
    • Buyer Personas and Journeys
    • Purpose, Mission, Vision, Values
    • Value Proposition and Positioning
    • Brand Message, Voice, and Writing Style
    • Brand Strategy and Tactics
    • Asset Creation and Management
    • Strategy Rollout Plan

    Short and long-term benefits of increasing brand awareness

    Increase:

    • Brand perception
    • Brand associations and engagement
    • Credibility, reputation, and trust
    • Connection with customers
    • Repeat business
    • Quality leads
    • Conversion rate
    • Sales closed / deals won
    • Brand equity and growth

    It typically takes 5-7 brand interactions before a buyer remembers the brand.
    Source: Startup Bonsai

    Who benefits from this brand awareness research?

    This research is being designed for:
    Brand and marketing leaders who:

    • Know that brand awareness is essential to the success of all marketing and sales activities.
    • Want to make their brand unique, recognizable, meaningful, and highly visible.
    • Seek to increase their digital presence, connect and engage with their target audience.
    • Are looking at reaching a new segment of the market.

    This research will also assist:

    • Sales with qualified lead generation and customer retention and loyalty.
    • Human Resources in their efforts to attract and retain talent.
    • The overall business with growth and increased market value.

    This research will help you:

    • Gain market intelligence and a clear understanding of the target audience's needs and trends, competitive advantage, and key differentiator.
    • The ability to develop clear and compelling, human-centric messaging and compelling story driven by brand values.
    • Increase online presence and brand awareness activities to attract and engage with buyers.
    • Develop a long-term brand awareness strategy and deployment plan.

    This research will help them:

    • Increase campaign ROI.
    • Develop a longer-term vision and benefits of investing in longer-term initiatives.
    • Build brand equity and increase business valuation.
    • Grow your business in a more sustainable way.

    SoftwareReviews' brand awareness building methodology

    Phase 1 Define brands' personality and message

    Phase 2 Start building brand awareness

    Phase steps

    1.1 Gather market intelligence and analyze the market.

    1.2 Develop and document the buyer's persona and journey.

    1.3 Uncover the brand mission, vision statement, core values, value proposition and positioning.

    1.4 Define the brand's archetype and tone of voice, then craft a compelling brand messaging.

    2.1 Achieve strategy alignment and readiness.

    2.2 Create assets and workflows and deploy tactics.

    2.3 Establish key performance indicators (KPIs), monitor, and optimize on an ongoing basis.

    Phase outcomes

    • Target market and audience are identified and documented.
    • A clear value proposition and positioning are determined.
    • The brand personality, voice, and messaging are developed.
    • All the key elements of the brand guidelines are in place and ready to use, along with the existing logo, typography, color palette, and imagery.
    • A comprehensive and actionable brand awareness strategy, with tactics, KPIs, and metrics, is set and ready to execute.
    • A progressive and effective deployment plan with deliverables, timelines, workflows, and checklists is in place.
    • Resources are assigned.

    Insight summary

    Brands to adapt their strategies to achieve longer-term growth
    Brands must adapt and adjust their strategies to attract informed buyers who have access to a wealth of products, services, and brands from all over. Building brand awareness, even though immediate benefits are often difficult to see and measure, has become essential for companies that want to stand out from their competitors and continue to grow in a sustainable way.

    A more human-centric approach
    Brand personalities matter. Brands placing human values at the heart of the customer-brand relationship will drive interest in their brand and build trust with their target audience.

    Stand out from the crowd
    Brands that develop and promote a clear and consistent message across all platforms and channels, along with a unique value proposition, stand out from their competitors and get noticed.

    A multi-touchpoints strategy
    Engage buyers with relevant content across multiple media to address their pain points. Analyze touchpoints to determine where to invest your efforts.

    Going social
    Buyers expect brands to be active and responsive in their interactions with their audience. To build awareness, brands are expected to develop a strong presence on social media by regularly posting relevant content, engaging with their followers and influencers, and using paid advertising. They also need to establish thought leadership through content such as white papers, case studies, and webinars.

    Thought leaders wanted
    To enhance their overall brand awareness strategy, organizations should consider developing the personal brand of key executives. Thought leadership can be a valuable method to gain credibility, build trust, and drive conversion. By establishing thought leadership, businesses can increase brand mentions, social engagement, website traffic, lead generation, return on investment (ROI), and Net Promoter Score (NPS).

    Save time and money with SoftwareReviews' branding advice

    Collaborating with SoftwareReviews analysts for inquiries not only provides valuable advice but also leads to substantial cost savings during branding activities, particularly when partnering with an agency.

    Guided Implementation Purpose Measured Value
    Build brands' personality and message Get the key elements of the brand guidelines in place and ready to use, along with your existing logo, typography, color palette, and imagery, to ensure consistency and clarity across all brand touchpoints from internal communication to customer-facing materials. Working with SoftwareReviews analysts to develop brand guidelines saves costs compared to hiring an agency.

    Example: Building the guidelines with an agency will take more or less the same amount of time and cost approximately $80K.

    Start building brand awareness Achieve strategy alignment and readiness, then deploy tactics, assets, and other deliverables. Start building brand awareness and reap the immediate and long-term benefits.

    Working with SoftwareReviews analysts and your team to develop a long-term brand strategy and deployment will cost you less than a fraction of the cost of using an agency.

    Example: Developing and executing long-term brand awareness strategies with an agency will cost between $50-$75K/month over a 24-month period minimum.

    Guided Implementation

    What does a typical GI on this topic look like?

    Phase 1

    Build brands' personality and message

    Phase 2

    Start building brand awareness

    • Call #1: Discuss concept and benefits of building brand awareness. Identify key stakeholders. Anticipate concerns and objections.
    • Call #2: Discuss target market intelligence, information gathering, and analysis.
    • Call #3: Review market intelligence information. Address questions or concerns.
    • Call #4: Discuss value proposition and guide to find positioning and key differentiator.
    • Call #5: Review value proposition. Address questions or concerns.
    • Call #6: Discuss how to build a comprehensive brand awareness strategy using SR guidelines and template.
    • Call #7: Review strategy. Address questions or concerns.
    • Call #8: Second review of the strategy. Address questions or concerns.
    • Call #9 (optional): Third review of the strategy. Address questions or concerns.
    • Call #10: Discuss how to build the Execution Plan using SR template.
    • Call #11: Review Execution Plan. Address questions or concerns.
    • Call #12: Second review of the Execution Plan. Address questions or concerns.
    • Call #13 (optional): Third review of the Execution Plan. Address questions or concerns.
    • Call #14: Discuss how to build a compelling storytelling and content creation.
    • Call #15: Discuss website and social media platforms and other initiatives.
    • Call #16: Discuss marketing automation and continuous monitoring.
    • Call #17 (optional): Discuss optimization and reporting
    • Call #18: Debrief and determine how we can help with next steps.

    A Guided Implementation (GI) is a series of calls with a SoftwareReviews Marketing Analyst to help implement our best practices in your organization.

    Your engagement managers will work with you to schedule analyst calls.

    Brand awareness building tools

    Each step of this blueprint comes with tools to help you build brand awareness.

    Brand Awareness Tool Kit

    This kit includes a comprehensive set of tools to help you better understand your target market and buyers, define your brand's personality and message, and develop an actionable brand awareness strategy, workflows, and rollout plan.

    The set includes these templates:
    • Market and Influencing Factors Analysis
    • Recognition Survey and Best Practices
    • Buyer Personas and Journeys
    • Purpose, Mission, Vision, and Values
    • Value Proposition and Positioning
    • Brand Message, Voice, and Writing Style
    • Brand Strategy and Tactics
    • Asset Creation and Management
    • Strategy Rollout Plan
    An image of a series of screenshots from the templates listed in the column to the left of this image.

    Get started!

    Know your target market and audience, deploy well-designed strategies based on shared values, and make meaningful connections with people.

    Phase 1

    Define brands' personality and message

    Phase 2

    Start building brand awareness

    Phase 1

    Define brands' personality and message

    Steps

    1.1 Gather market intelligence and analyze the market.
    1.2 Develop and document the buyer's persona and journey.
    1.3 Uncover the brand mission, vision statement, core values, positioning, and value proposition.
    1.4 Define the brand's archetype and tone of voice, then craft a compelling brand messaging.

    Phase outcome

    • Target market and audience are identified and documented.
    • A clear value proposition and positioning are determined.
    • The brand personality, voice, and messaging are developed.
    • All the key elements of the brand guidelines are in place. and ready to use, along with the existing logo, typography, color palette, and imagery..

    Build brands' personality and message

    Step 1.1 Gather market intelligence and analyze the market.

    Total duration: 2.5-8 hours

    Objective

    Analyze and document your competitive landscape, assess your strengths, weaknesses, opportunities,
    and threats, gauge the buyers' familiarity with your brand, and identify the forces of influence.

    Output

    This exercise will allow you to understand your market and is essential to developing your value proposition.

    Participants

    • Head of branding and key stakeholders

    MarTech
    May require you to:

    • Register to a Survey Platform.
    • Use, setup, or install platforms like CRM and/or Marketing Automation Platform.

    Tools

    1.1.1 SWOT and competitive landscape

    (60-120 min.)

    Analyze & Document

    Follow the instructions in the Market Analysis Template to complete the SWOT and Competitive Analysis, slides 4 to 7.

    1.1.3 Internal and External Factors

    (30-60 min.)

    Analyze

    Follow the instructions in the External and Internal Factors Analysis Template to perform the PESTLE, Porter's 5 Forces, and Internal Factors and VRIO Analysis.

    Transfer

    Transfer key information into slides 10 and 11 of the Market Analysis Template.

    Consult SoftwareReviews website to find the best survey and MarTech platforms or contact one of our analysts for more personalized assistance and guidance

    1.1.2 Brand recognition

    (60-300 min.)

    Prep

    Adapt the survey and interview questions in the Brand Recognition Survey Questionnaire and List Template.

    Determine how you will proceed to conduct the survey and interviews (internal or external resources, and tools).

    Refer to the Survey Emails Best Practices Guidelines for more information on how to conduct email surveys.

    Collect & Analyze

    Use the Brand Recognition Survey Questionnaire and List Template to build your list, conduct the survey /interviews, and collect and analyze the feedback received.

    Transfer

    Transfer key information into slides 8 and 9 of the Market Analysis Template.

    Brand performance diagnostic

    Have you considered diagnosing your brand's current performance before you begin building brand awareness?

    Audit your brand using the Diagnose Brand Health to Improve Business Growth blueprint.Collect and interpret qualitative and quantitative brand performance measures.

    The toolkit includes the following templates:

    • Surveys and interviews questions and lists
    • External and internal factor analysis
    • Digital and financial metrics analysis

    Also included is an executive presentation template to communicate the results to key stakeholders and recommendations to fix the uncovered issues.

    Build brands' personality and message

    Step 1.2 Develop and document the buyer's persona and journey.

    Total duration: 4-8 hours

    Objective

    Gather existing and desired customer insights and conduct market research to define and personify your buyers' personas and their buying behaviors.

    Output

    Provide people in your organization with clear direction on who your target buyers are and guidance on how to effectively reach and engage with them throughout their journey.
    Participants

    • Head of branding
    • Key stakeholders from sales and product marketing

    MarTech
    May require you to:

    • Register to an Online Survey Platform (free version or subscription).
    • Use, setup, or installation of platforms like CRM and/or Marketing Automation Platform.

    Tools

    1.2.1 Buyer Personas and Journeys

    (240-280 min.)

    Research

    Identify your tier 1 to 3 customers using the Ideal Client Profile (ICP) Workbook. (Recommended)

    Survey and interview existing and desired customers based using the Buyer Persona and Journey Interview Guide and Data Capture Tool. (Recommended)

    Create

    Define and document your tier 1 to 3 Buyer Personas and Journeys using the Buyer Personas and Journeys Presentation Template.

    Consult SoftwareReviews website to find the best survey platform for your needs or contact one of our analysts for more personalized assistance and guidance

    Buyer Personas and Journeys

    A well-defined buyer persona and journey is a great way for brands to ensure they are effectively reaching and engaging their ideal buyers through a personalized buying experience.

    When properly documented, it provides valuable insights about the ideal customers, their needs, challenges, and buying decision processes allowing the development of initiatives that correspond to the target buyers.

    Build brands' personality and message

    Step 1.3 Uncover the brand mission, vision statement, core values, value proposition, and positioning.

    Total duration: 4-5.5 hours

    Objective
    Define the "raison d'être" and fundamental principles of your brand, your positioning in the marketplace, and your unique competitive advantage.

    Output
    Allows everyone in an organization to understand and align with the brand's raison d'être beyond the financial dimension, its current positioning and objectives, and how it intends to achieve them.
    It also serves to communicate a clear and appealing value proposition to buyers.

    Participants

    • Head of branding
    • Chief Executive Officer (CEO)
    • Key stakeholders

    Tools

    • Brand Purpose, Mission, Vision, and Values Template
    • Value Proposition and Positioning Statement Template

    1.3.1 Brand Purpose, Mission, Vision, and Values

    (90-120 min.)

    Capture or Develop

    Capture or develop, if not already existing, your brand's purpose, mission, vision statement, and core values using slides 4 to 7 of the Brand Purpose, Mission, Vision, and Values Template.

    1.3.2 Brand Value Proposition and Positioning

    (150-210 min.)

    Define

    Map the brand value proposition using the canvas on slide 5 of the Value Proposition and Positioning Statement Template, and clearly articulate your value proposition statement on slide 4.

    Optional: Use canvas on slide 7 to develop product-specific product value propositions.

    On slide 8 of the same template, develop your brand positioning statement.

    Build brands' personality and message

    Steps 1.4 Define the brand's archetype and tone of voice, and craft a compelling brand messaging.

    Total duration: 5-8 hours

    Objective

    Define your unique brand voice and develop a set of guidelines, brand story, and messaging to ensure consistency across your digital and non-digital marketing and communication assets.
    Output

    A documented brand personality and voice, as well as brand story and message, will allow anyone producing content or communicating on behalf of your brand to do it using a unique and recognizable voice, and convey the right message.

    Participants

    • Head of branding
    • Content specialist
    • Chief Executive Officer and other key stakeholders

    Tools

    • Brand Voice Guidelines Template
    • Writing Style Guide Template
    • Brand Messaging Template
    • Writer Checklist Template

    1.4.1 Brand Archetype and Tone of Voice

    (120-240 min.)

    Define and document

    Refer to slides 5 and 6 of the Brand Voice Guidelines Template to define your brand personality (archetype), slide 7.

    Use the Brand Voice Guidelines Template to define your brand tone of voice and characteristics on slides 8 and 9, based on the 4 primary tone of voice dimensions, and develop your brand voice chart, slide 9.

    Set Rules

    In the Writing Style Guide template, outline your brand's writing principles, style, grammar, punctuation, and number rules.

    1.4.2 Brand Messaging

    (180-240 min.)

    Craft

    Use the Brand Messaging template, slides 4 to 7, to craft your brand story and message.

    Audit

    Create a content audit to review and approve content to be created prior to publication, using the Writer's Checklist template.

    Important Tip!

    A consistent brand voice leads to remembering and trusting the brand. It should stand out from the competitors' voices and be meaningful to the target audience. Once the brand voice is set, avoid changing it.

    Phase 2

    Start building brand awareness

    Steps

    2.1 Achieve strategy alignment and readiness.
    2.2 Create assets and workflows, and deploy tactics.
    2.3 Establish key performance indicators (KPIs), monitor, and optimize on an ongoing basis.

    Phase outcome

    • A comprehensive and actionable brand awareness strategy, with tactics, KPIs, and metrics, is set and ready to execute.
    • A progressive and effective deployment plan with deliverables, timelines, workflows, and checklists is in place.
    • Resources are assigned.

    Start building brand awareness

    Step 2.1 Achieve strategy readiness and alignment.

    Total duration: 4-5 hours

    Objective

    Now that you have all the key elements of your brand guidelines in place, in addition to your existing logo, typography, color palette, and imagery, you can begin to build brand awareness.

    Start planning to build brand awareness by developing a comprehensive and actionable brand awareness strategy with tactics that align with the company's purpose and objectives. The strategy should include achievable goals and measurables, budget and staffing considerations, and a good workload assessment.

    Output

    A comprehensive long-term, actionable brand awareness strategy with KPIs and measurables.

    Participants

    • Head of branding
    • Key stakeholders

    Tools

    • Brand Awareness Strategy and Tactics Template

    2.1.1 Brand Awareness Analysis

    (60-120 min.)

    Identify

    In slide 5 of the Brand Awareness Strategy and Tactics Template, identify your top three brand awareness drivers, opportunities, inhibitors, and risks to help you establish your strategic objectives in building brand awareness.

    2.1.2 Brand Awareness Strategy

    (60-120 min.)

    Elaborate

    Use slides 6 to 10 of the Brand Awareness Strategy and Tactics Template to elaborate on your strategy goals, key issues, and tactics to begin or continue building brand awareness.

    2.1.3 Brand Awareness KPIs and Metrics

    (180-240 min.)

    Set

    Set the strategy performance metrics and KPIs on slide 11 of the Brand Awareness Strategy and Tactics Template.

    Monitor

    Once you start executing the strategy, monitor and report each quarter using slides 13 to 15 of the same document.

    Understanding the difference between strategies and tactics

    Strategies and tactics can easily be confused, but although they may seem similar at times, they are in fact quite different.

    Strategies and tactics are complementary.

    A strategy is a plan to achieve specific goals, while a tactic is a concrete action or set of actions used to implement that strategy.

    To be effective, brand awareness strategies should be well thought-out, carefully planned, and supported by a series of tactics to achieve the expected outcomes.

    Start building brand awareness

    Step 2.2 Create assets and workflows and deploy tactics.

    Total duration: 3.5-4.5 hours

    Objective

    Build a long-term rollout with deliverables, milestones, timelines, workflows, and checklists. Assign resources and proceed to the ongoing development of assets. Implement, manage, and continuously communicate the strategy and results to key stakeholders.

    Output

    Progressive and effective development and deployment of the brand awareness-building strategy and tactics.

    Participants

    • Head of branding

    Tools

    • Asset Creation and Management List
    • Campaign Workflows Template
    • Brand Awareness Strategy Rollout Plan Template

    2.2.1 Assets Creation List

    (60-120 min.)

    Inventory

    Inventory existing assets to create the Asset Creation and Management List.

    Assign

    Assign the persons responsible, accountable, consulted, and informed of the development of each asset, using the RACI model in the template. Ensure you identify and collaborate with the right stakeholders.

    Prioritize

    Prioritize and add release dates.

    Communicate

    Update status and communicate regularly. Make the list with links to the assets available to the extended team to consult as needed.

    2.2.2 Rollout Plan

    (60-120 min.)

    Inventory

    Map out your strategy deployment in the Brand Awareness Strategy Rollout Plan Template and workflow in the Campaign Workflow Template.

    Assign

    Assign the persons responsible, accountable, consulted, and informed for each tactic, using the RACI model in the template. Ensure you identify and collaborate with the right stakeholders.

    Prioritize

    Prioritize and adjust the timeline accordingly.

    Communicate

    Update status and communicate regularly. Make the list with links to the assets available to the extended team to consult as needed.

    Band Awareness Strategy Rollout Plan
    A strategy rollout plan typically includes the following:

    • Identifying a cross-functional team and resources to develop the assets and deploy the tactics.
    • Listing the various assets to create and manage.
    • A timeline with key milestones, deadlines, and release dates.
    • A communication plan to keep stakeholders informed and aligned with the strategy and tactics.
    • Ongoing performance monitoring.
    • Constant adjustments and improvements to the strategy based on data collected and feedback received.

    Start building brand awareness

    Step 2.3 Establish key performance indicators (KPIs), monitor, and optimize on an ongoing basis.

    Total duration: 3.5-4.5 hours

    Objective

    Brand awareness is built over a long period of time and must be continuously monitored in several ways. Measuring and monitoring the effectiveness of your brand awareness activities will allow you to constantly adjust your tactics and continue to build awareness.

    Output

    This step will provide you with a snapshot of your current level of brand awareness and interactions with the brand, and allow you to set up the tools for ongoing monitoring and optimization.

    Participants

    • Head of branding
    • Digital marketing manager

    MarTech
    May require you to:

    • Register to an Online Survey Platform(free version or subscription), or
    • Use, setup, or installation of platforms like CRM and/or Marketing Automation Platform.
    • Use Google Analytics or other tracking tools.
    • Use social media and campaign management tools.

    Tools

    • Brand Awareness Strategy and Tactics Template

    2.2.2 Rollout Plan

    (60-120 min.)

    Measure

    Monitor and record the strategy performance metrics in slides 12 to 15 of the Brand Awareness Strategy and Tactics template, and gauge its performance against preset KPIs in slide 11. Make ongoing improvements to the strategy and assets.

    Communicate

    The same slides in which you monitor strategy performance can be used to report on the results of the current strategy to key stakeholders on a monthly or quarterly basis, as appropriate.

    Take this opportunity to inform stakeholders of any adjustments you plan to make to the existing plan to improve its performance. Since brand awareness is built over time, be sure to evaluate the results based on how long the strategy has been in place before making major changes.

    Consult SoftwareReviews website to find the best survey, brand monitoring and feedback, and MarTech platforms, or contact one of our analysts for more personalized assistance and guidance

    Measuring brand strategy performance
    There are two ways to measure and monitor your brand's performance on an ongoing basis.

    • By registering to brand monitoring and feedback platforms and tools like Meltwater, Hootsuite, Insights, Brand24, Qualtrics, and Wooltric.
    • Manually, using native analytics built in the platforms you're already using, such as Google and Social Media Analytics, or by gathering customer feedback through surveys, or calculating CAC, ROI, and more in spreadsheets.

    SoftwareReviews can help you choose the right platform for your need. We also equip you with manual tools, available with the Diagnose Brand Health to Improve Business Growthblueprint to measure:

    • Surveys and interviews questions and lists.
    • External and internal factor analysis.
    • Digital and financial metrics analysis.
    • Executive presentation to report on performance.

    Related SoftwareReviews research

    An image of the title page for SoftwareReviews Create a Buyer Persona and Journey. An image of the title page for SoftwareReviews Diagnose Brand Health to Improve Business Growth.

    Create a Buyer Persona and Journey

    Get deeper buyer understanding and achieve product-market fit, with easier access to market and sales

    • Reduce time and resources wasted chasing the wrong prospects.
    • Increase open and click-through rates.
    • Perform more effective sales discovery.
    • Increase win rate.

    Diagnose Brand Health to Improve Business Growth

    Have a significant and well-targeted impact on business success and growth by knowing how your brand performs, identifying areas of improvement, and making data-driven decisions to fix them.

    • Increase brand awareness and equity.
    • Build trust and improve customer retention and loyalty.
    • Achieve higher and faster growth.

    Bibliography

    Aaker, David. "Managing Brand Equity." Simon & Schuster, 1991.
    "6 Factors for Brands to Consider While Designing Their Communication." Lokus Design, 23 Sept. 2022.
    "20 Advocacy Marketing Statistics You Need to Know." Social Toaster, n.d.
    Bazilian, Emma. "How Millennials and Baby Boomers Consume User-Generated Content And what brands can learn from their preferences." Adweek, January 2, 2017.
    B2B International, a Gyro: company, B2B Blog - Why Human-To-Human Marketing Is the Next Big Trend in a Tech-Obsessed World.
    B2B International, a Gyro: company, The State of B2B Survey 2019 - Winning with Emotions: How to Become Your Customer's First Choice.
    Belyh, Anastasia. "Brand Ambassador 101:Turn Your Personal Brand into Cash." Founder Jar, December 6, 2022.
    Brand Master Academy.com.
    Businesswire, a Berkshire Hathaway Company, "Stackla Survey Reveals Disconnect Between the Content Consumers Want & What Marketers Deliver." February 20, 2019.
    Chamat, Ramzi. "Visual Design: Why First Impressions Matter." 8 Ways, June 5, 2019.
    Cognism. "21 Tips for Building a LinkedIn Personal Brand (in B2B SaaS)."
    Curleigh, James. "How to Enhance and Expand a Global Brand." TED.
    "2019 Edelman Trust Barometer." Edelman.
    Erskine, Ryan. "22 Statistics That Prove the Value of Personal Branding." Entrepreneur, September 13, 2016.
    Forbes, Steve. "Branding for Franchise Success: How To Achieve And Maintain Brand Consistency Across A Franchise Network?" Forbes, 9 Feb. 2020.
    Godin, Seth. "Define: Brand." Seth's Blog, 30 Dec. 2009,
    Houragan, Stephen. "Learn Brand Strategy in 7 Minutes (2023 Crash Course)." YouTube.
    Jallad, Revecka. "To Convert More Customers, Focus on Brand Awareness." Forbes, October 22, 2019.
    Kingsbury, Joe, et al. "2021 B2B Thought Leadership Impact Study." Edelman, 2021.
    Kunsman, Todd. "The Anatomy of an Employee Influencer." EveryoneSocial, September 8, 2022.
    Landor, Walter. A Brand New World: The Fortune Guide to the 21st Century. Time Warner Books, 1999.
    Liedke, Lindsay. "37+ Branding Statistics For 2023: Stats, Facts & Trends." Startup Bonsai, January 2, 2023.
    Millman, Debbie. "How Symbols and Brands Shape our Humanity." TED, 2019.
    Nenova, Velina. "21 Eye-Opening B2B Marketing Statistics to Know in 2023." Techjury, February 9, 2023.
    Perrey, Jesko et al., "The brand is back: Staying relevant in an accelerating age." McKinsey & Company, May 1, 2015.
    Schaub, Kathleen. "Social Buying Meets Social Selling: How Trusted Networks Improve the Purchase Experience." LinkedIn Business, April 2014.
    Sopadjieva, Emma et al. "A Study of 46,000 Shoppers Shows That Omnichannel Retailing Works." Harvard Business Review, January 3, 2017.
    Shaun. "B2B Brand Awareness: The Complete Guide 2023." B2B House. 2023.
    TopRank Marketing, "2020 State of B2B Influencer Marketing Research Report." Influencer Marketing Report.

    The Small Enterprise Guide to People and Resource Management

    • Buy Link or Shortcode: {j2store}602|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Train & Develop
    • Parent Category Link: /train-and-develop
    • 52% of small business owners agree that labor quality is their most important problem, and 76% of executives expect the talent market to get even more challenging.
    • The problem? You can't compete on salary, training budgets are slim, you need people skilled in all areas, and even one resignation represents a large part of your workforce.

    Our Advice

    Critical Insight

    • The usual, reactive approach to workforce management is risky:
      • Optimizing tactics helps you hire faster, train more, and negotiate better contracts.
      • But fulfilling needs as they arise costs more, has greater risk of failure, and leaves you unprepared for future needs.
    • In a small enterprise where every resource counts, in which one hire represents 10% of your workforce, it is essential to get it right.

    Impact and Result

    • Workforce planning helps you anticipate future needs.
    • More lead time means better decisions at lower cost.
    • Small Enterprises benefit most, since every resource counts.

    The Small Enterprise Guide to People and Resource Management Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. The Small Enterprise Guide to People and Resource Management Deck – Find out why workforce planning is critical for small enterprises.

    Use this storyboard to lay the foundation of people and resources management practices in your small enterprise IT department.

    • The Small Enterprise Guide to People and Resource Management – Phases 1-3

    2. Workforce Planning Workbook – Use the tool to successfully complete all of the activities required to define and estimate your workforce needs for the future.

    Use these concise exercises to analyze your department’s talent current and future needs and create a skill sourcing strategy to fill the gaps.

    • Workforce Planning Workbook for Small Enterprises

    3. Knowledge Transfer Tools – Use these templates to identify knowledge to be transferred.

    Work through an activity to discover key knowledge held by an employee and create a plan to transfer that knowledge to a successor.

    • IT Knowledge Identification Interview Guide Template
    • IT Knowledge Transfer Plan Template

    4. Development Planning Tools – Use these tools to determine priority development competencies.

    Assess employees’ development needs and draft a development plan that fits with key organizational priorities.

    • IT Competency Library
    • Leadership Competencies Workbook
    • IT Employee Career Development Workbook
    • Individual Competency Development Plan
    • Learning Methods Catalog for IT Employees

    Infographic

    Workshop: The Small Enterprise Guide to People and Resource Management

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Lay Your Foundations

    The Purpose

    Set project direction and analyze workforce needs.

    Key Benefits Achieved

    Planful needs analysis ensures future workforce supports organizational goals.

    Activities

    1.1 Set workforce planning goals and success metrics.

    1.2 Identify key roles and competency gaps.

    1.3 Conduct a risk analysis to identify future needs.

    1.4 Determine readiness of internal successors.

    Outputs

    Work with the leadership team to:

    Extract key business priorities.

    Set your goals.

    Assess workforce needs.

    2 Create Your Workforce Plan

    The Purpose

    Conduct a skill sourcing analysis, and determine competencies to develop internally.

    Key Benefits Achieved

    A careful analysis ensures skills are being sourced in the most efficient way, and internal development is highly aligned with organizational objectives.

    Activities

    2.1 Determine your skill sourcing route.

    2.2 Determine priority competencies for development.

    Outputs

    Create a workforce plan.

    2.Determine guidelines for employee development.

    3 Plan Knowledge Transfer

    The Purpose

    Discover knowledge to be transferred, and build a transfer plan.

    Key Benefits Achieved

    Ensure key knowledge is not lost in the event of a departure.

    Activities

    3.1 Discover knowledge to be transferred.

    3.2 Identify the optimal knowledge transfer methods.

    3.3 Create a knowledge transfer plan.

    Outputs

    Discover tacit and explicit knowledge.

    Create a knowledge transfer roadmap.

    4 Plan Employee Development

    The Purpose

    Create a development plan for all staff.

    Key Benefits Achieved

    A well-structured development plan helps engage and retain employees while driving organizational objectives.

    Activities

    4.1 Identify target competencies & draft development goals

    4.2 Select development activities and schedule check-ins.

    4.3 Build manager coaching skills.

    Outputs

    Assess employees.

    Prioritize development objectives.

    Plan development activities.

    Build management skills.

    Further reading

    The Small Enterprise Guide to People and Resource Management

    Quickly start getting the right people, with the right skills, at the right time

    Is this research right for you?

    Research Navigation

    Managing the people in your department is essential, whether you have three employees or 300. Depending on your available time, resources, and current workforce management maturity, you may choose to focus on the overall essentials, or dive deep into particular areas of talent management. Use the questions below to help guide you to the right Info-Tech resources that best align with your current needs.

    Question If you answered "no" If you answered "yes"

    Does your IT department have fewer than 15 employees, and is your organization's revenue less than $25 million (USD)?

    Review Info-Tech's archive of research for mid-sized and large enterprise clients.

    Follow the guidance in this blueprint.

    Does your organization require a more rigorous and customizable approach to workforce management?

    Follow the guidance in this blueprint.

    Review Info-Tech's archive of research for mid-sized and large enterprise clients.

    Analyst Perspective

    Workforce planning is even more important for small enterprises than large organizations.

    It can be tempting to think of workforce planning as a bureaucratic exercise reserved for the largest and most formal of organizations. But workforce planning is never more important than in small enterprises, where every individual accounts for a significant portion of your overall productivity.

    Without workforce planning, organizations find themselves in reactive mode, hiring new staff as the need arises. They often pay a premium for having to fill a position quickly or suffer productivity losses when a critical role goes unexpectedly vacant.

    A workforce plan helps you anticipate these challenges, come up with solutions to mitigate them, and allocate resources for the most impact, which means a greater return on your workforce investment in the long run.

    This blueprint will help you accomplish this quickly and efficiently. It will also provide you with the essential development and knowledge transfer tools to put your plan into action.

    This is a picture of Jane Kouptsova

    Jane Kouptsova
    Senior Research Analyst, CIO Advisory
    Info-Tech Research Group

    Executive Summary

    Your Challenge

    52% of small business owners agree that labor quality is their most important problem.1

    Almost half of all small businesses face difficulty due to staff turnover.

    76% of executives expect the talent market to get even more challenging.2

    Common Obstacles

    76% of executives expect workforce planning to become a top strategic priority for their organization.2

    But…

    30% of small businesses do not have a formal HR function.3

    Small business leaders are often left at a disadvantage for hiring and retaining the best talent, and they face even more difficulty due to a lack of support from HR.

    Small enterprises must solve the strategic workforce planning problem, but they cannot invest the same time or resources that large enterprises have at their disposal.

    Info-Tech's Approach

    A modular, lightweight approach to workforce planning and talent management, tailored to small enterprises

    Clear activities that guide your team to decisive action

    Founded on your IT strategy, ensuring you have not just good people, but the right people

    Concise yet comprehensive, covering the entire workforce lifecycle from competency planning to development to succession planning and reskilling

    Info-Tech Insight

    Every resource counts. When one hire represents 10% of your workforce, it is essential to get it right.

    1CNBC & SurveyMonkey. 2ADP. 3Clutch.

    Labor quality is small enterprise's biggest challenge

    The key to solving it is strategic workforce planning

    Strategic workforce planning (SWP) is a systematic process designed to identify and address gaps in today's workforce, including pinpointing the human capital needs of the future.

    Linking workforce planning with strategic planning ensures that you have the right people in the right positions, in the right places, at the right time, with the knowledge, skills, and attributes to deliver on strategic business goals.

    SWP helps you understand the makeup of your current workforce and how well prepared it is or isn't (as the case may be) to meet future IT requirements. By identifying capability gaps early, CIOs can prepare to train or develop current staff and minimize the need for severance payouts and hiring costs, while providing clear career paths to retain high performers.

    52%

    of small business owners agree that labor quality is their most important problem.1

    30%

    30% of small businesses have no formal HR function.2

    76%

    of senior leaders expect workforce planning to become the top strategic challenge for their organization.3

    1CNBC & SurveyMonkey. 2Clutch. 3ADP.

    Workforce planning matters more for small enterprises

    You know that staffing mistakes can cost your department dearly. But did you know the costs are greater for small enterprises?

    The price of losing an individual goes beyond the cost of hiring a replacement, which can range from 0.5 to 2 times that employee's salary (Gallup, 2019). Additional costs include loss of productivity, business knowledge, and team morale.

    This is a major challenge for large organizations, but the threat is even greater for small enterprises, where a single individual accounts for a large proportion of IT's productivity. Losing one of a team of 10 means 10% of your total output. If that individual was solely responsible for a critical function, your department now faces a significant gap in its capabilities. And the effect on morale is much greater when everyone is on the same close-knit team.

    And the threat continues when the staffing error causes you not to lose a valuable employee, but to hire the wrong one instead. When a single individual makes up a large percentage of your workforce, as happens on small teams, the effects of talent management errors are magnified.

    A group of 100 triangles is shown above a group of 10 triangles. In each group, one triangle is colored orange, and the rest are colored blue.

    Info-Tech Insight

    One bad hire on a team of 100 is a problem. One bad hire on a team of 10 is a disaster.

    This is an image of Info-Tech's small enterprise guide o people and resource management.

    Blueprint pre-step: Determine your starting point

    People and Resource management is essential for any organization. But depending on your needs, you may want to start at different stages of the process. Use this slide as a quick reference for how the activities in this blueprint fit together, how they relate to other workforce management resources, and the best starting point for you.

    Your IT strategy is an essential input to your workforce plan. It defines your destination, while your workforce is the vessel that carries you there. Ensure you have at least an informal strategy for your department before making major workforce changes, or review Info-Tech's guidance on IT strategy.

    This blueprint covers the parts of workforce management that occur to some extent in every organization:

    • Workforce planning
    • Knowledge transfer
    • Development planning

    You may additionally want to seek guidance on contract and vendor management, if you outsource some part of your workload outside your core IT staff.

    Track metrics

    Consider these example metrics for tracking people and resource management success

    Project Outcome Metric Baseline Target
    Reduced training costs Average cost of training (including facilitation, materials, facilities, equipment, etc.) per IT employee
    Reduced number of overtime hours worked Average hours billed at overtime rate per IT employee
    Reduced length of hiring period Average number of days between job ad posting and new hire start date
    Reduced number of project cancellations due to lack of capacity Total of number of projects cancelled per year
    Increased number of projects completed per year (project throughput) Total number of project completions per year
    Greater net recruitment rate Number of new recruits/Number of terminations and departures
    Reduced turnover and replacement costs Total costs associated with replacing an employee, including position coverage cost, training costs, and productivity loss
    Reduced voluntary turnover rate Number of voluntary departures/Total number of employees
    Reduced productivity loss following a departure or termination Team or role performance metrics (varies by role) vs. one year ago

    Info-Tech offers various levels of support to best suit your needs

    DIY Toolkit

    “Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful.”

    Guided Implementation

    “Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track.”

    Workshop

    “We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place.”

    Consulting

    “Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project.”

    Diagnostics and consistent frameworks used throughout all four options

    Guided Implementation

    What does a typical GI on this topic look like?

    Phase 1 Phase 2 Phase 3

    Call #1:

    Scope requirements, objectives, and your specific challenges.

    Call #2: Assess current workforce needs.

    Call #4: Determine skill sourcing route.

    Call #6:

    Identify knowledge to be transferred.

    Call #8: Draft development goals and select activities.

    Call #3: Explore internal successor readiness.

    Call #5:Set priority development competencies.

    Call #7: Create a knowledge transfer plan.

    Call #9: Build managers' coaching & feedback skills.

    A Guided Implementation (GI) is a series of calls with an Info-Tech analyst to help implement our best practices in your organization.

    A typical GI is between 4 to 6 calls over the course of 3 to 4 months.

    Workshop Overview

    Contact your account representative for more information.
    workshops@infotech.com 1-888-670-8889

    Day 1

    Day 2

    Day 3

    Day 4

    Day 5

    1.Lay Your Foundations 2. Create Your Workforce Plan 3. Plan Knowledge Transfer 3. Plan Employee Development Next Steps and Wrap-Up (offsite)
    Activities

    1.1 Set workforce planning goals and success metrics

    1.2 Identify key roles and competency gaps

    1.3 Conduct a risk analysis to identify future needs

    1.4 Determine readiness of internal successors

    1.5 Determine your skill sourcing route

    1.6 Determine priority competencies for development

    3.1 Discover knowledge to be transferred

    3.2 Identify the optimal knowledge transfer methods

    3.3 Create a knowledge transfer plan

    4.1 Identify target competencies & draft development goals

    4.2 Select development activities and schedule check-ins

    4.3 Build manager coaching skills

    Outcomes

    Work with the leadership team to:

    1. Extract key business priorities
    2. Set your goals
    3. Assess workforce needs

    Work with the leadership team to:

    1. Create a workforce plan
    2. Determine guidelines for employee development

    Work with staff and managers to:

    1. Discover tacit and explicit knowledge
    2. Create a knowledge transfer roadmap

    Work with staff and managers to:

    1. Assess employees
    2. Prioritize development objectives
    3. Plan development activities
    4. Build management skills

    Info-Tech analysts complete:

    1. Workshop report
    2. Workforce plan record
    3. Action plan

    Workshop Overview

    Contact your account representative for more information.
    workshops@infotech.com 1-888-670-8889

    Each onsite day is structured with group working sessions from 9-11 a.m. and 1:30-3:30 p.m. and includes Open Analyst Timeslots, where our facilitators are available to expand on scheduled activities, capture and compile workshop results, or review additional components from our comprehensive approach.

    This is a calendar showing days 1-4, and times from 8am-5pm

    Phase 1

    Workforce Planning

    Workforce Planning

    Knowledge Transfer

    Development Planning

    Identify needs, goals, metrics, and skill gaps.

    Select a skill sourcing strategy.

    Discover critical knowledge.

    Select knowledge transfer methods.

    Identify priority competencies.

    Assess employees.

    Draft development goals.

    Provide coaching & feedback.

    The Small Enterprise Guide to People and Resource Management

    Phase Participants

    • Leadership team
    • Managers
    • Human resource partner (if applicable)

    Additional Resources

    Workforce Planning Workbook for Small Enterprises

    Phase pre-step: Gather resources and participants

    1. Ensure you have an up-to-date IT strategy. If you don't have a formal strategy in place, ensure you are aware of the main organizational objectives for the next 3-5 years. Connect with executive stakeholders if necessary to confirm this information.
      If you are not sure of the organizational direction for this time frame, we recommend you consult Info-Tech's material on IT strategy first, to ensure your workforce plan is fully positioned to deliver value to the organization.
    2. Consult with your IT team and gather any documentation pertaining to current roles and skills. Examples include an org chart, job descriptions, a list of current tasks performed/required, a list of company competencies, and a list of outsourced projects.
    3. Gather the right participants. Most of the decisions in this section will be made by senior leadership, but you will also need input from front-line managers. Ensure they are available on an as-needed basis. If your organization has an HR partner, it can also be helpful to involve them in your workforce planning process.

    Formal workforce planning benefits even small teams

    Strategic workforce planning (SWP) is a systematic process designed to identify and address gaps in your workforce today and plan for the human capital needs of the future.

    Your workforce plan is an extension of your IT strategy, ensuring that you have the right people in the right positions, in the right places, at the right time, with the knowledge, skills, and attributes to deliver on strategic business goals.

    SWP helps you understand the makeup of your current workforce and how well prepared it is or isn't (as the case may be) to meet future IT requirements. By identifying capability gaps early, CIOs can prepare to train or develop current staff and minimize the need for severance payouts and hiring costs, while providing clear career paths to retain high performers.

    The smaller the business, the more impact each individual's performance has on the overall success of the organization. When a given role is occupied by a single individual, the organization's performance in that function is determined wholly by one employee. Creating a workforce plan for a small team may seem excessive, but it ensures your organization is not unexpectedly hit with a critical competency gap.

    Right-size your workforce planning process to the size of your enterprise

    Small organizations are 2.2 times more likely to have effective workforce planning processes.1 Be mindful of the opportunities and risks for organizations of your size as you execute the project. How you build your workforce plan will not change drastically based on the size of your organization; however, the scope of your initiative, the size of your team, and the tactics you employ may vary.

    Small Organization

    Medium Organization

    Large Organization

    Project Opportunities

    • Project scope is much more manageable.
    • Communication and planning can be more manageable.
    • Fewer roles can clarify prioritization needs and promotability.
    • Project scope is more manageable.
    • Moderate budget for workforce planning initiatives is needed.
    • Communication and enforcement is easier.
    • Larger candidate pool to pull from.
    • Greater career path options for staff.
    • In-house expertise may be available

    Project Risks

    • Limited resources and time to execute the project.
    • In-house expertise is unlikely.
    • Competencies may be informal and not documented.
    • Limited overlap in responsibilities, resulting in fewer redundancies.
    • Limited staff with experience for the project.
    • Workforce planning may be a lower priority and difficult to generate buy-in for.
    • Requires more staff to manage workforce plan and execute initiatives.
    • Less collective knowledge on staff strengths may make career planning difficult.
    • Geographically dispersed business units make collaboration and communication difficult.

    1 McLean & Company Trends Report 2014

    1.1 Set project outcomes and success metrics

    1-3 hours

    1. As a group, brainstorm key pain points that the IT department experiences due to the lack of a workforce plan. Ask them to consider turnover, retention, training, and talent acquisition.
    2. Discuss any key themes that arise and brainstorm your desired project outcomes. Keep a record of these for future reference and to aid in stakeholder communication.
    3. Break into smaller groups (or if too small, continue as a single group):
      1. For each desired outcome, consider what metrics you could use to track progress. Keep your initial list of pain points in mind as you brainstorm metrics.
      2. Write each of the metric suggestions on a whiteboard and agree to track 3-5 metrics. Set targets for each metric. Consider the effort required to obtain and track the metric, as well as its reliability.
      3. Assign one individual for tracking the selected metrics. Following the meeting, that individual will be responsible for identifying the baseline and targets, and reporting on metrics progress.

    Input

    Output

    • List of workforce data available
    • List of workforce metrics to track the workforce plan's impact

    Materials

    Participants

    • Whiteboard/flip charts
    • Leadership team
    • Human resource partner (if applicable)

    1.2 Identify key roles and competency gaps

    1-3 hours

    1. As a group, identify all strategic, core, and supporting roles by reviewing the organizational chart:
      1. Strategic: What are the roles that must be filled by top performers and cannot be left vacant in order to meet strategic objectives?
      2. Core: What roles are important to drive operational excellence?
      3. Supporting: What roles are required for day-to-day work, but are low risk if the role is vacant for a period of time?
    2. Working individually or in small groups, have managers for each identified role define the level of competence required for the job. Consider factors such as:
      1. The difficulty or criticality of the tasks being performed
      2. The impact on job outcomes
      3. The impact on the performance of other employees
      4. The consequence of errors if the competency is not present
      5. How frequently the competency is used on the job
      6. Whether the competency is required when the job starts or can be learned or acquired on the job within the first six months
    3. Continue working individually and rate the level of proficiency of the current incumbent.
    4. As a group, review the assessment and make any adjustments.

    Record this information in the Workforce Planning Workbook for Small Enterprises.

    Download the Workforce Planning Workbook for Small Enterprises

    1.2 Identify key roles and competency gaps

    Input Output
    • Org chart, job descriptions, list of current tasks performed/required, list of company competencies
    • List of competency gaps for key roles
    Materials Participants
    • Leadership team
    • Managers

    Conduct a risk-of-departure analysis

    A risk-of-departure analysis helps you plan for future talent needs by identifying which employees are most likely to leave the organization (or their current role).

    A risk analysis takes into account two factors: an employee's risk for departure and the impact of departure:

    Employees are high risk for departure if they:

    • Have specialized or in-demand skills (tenured employees are more likely to have this than recent hires)
    • Are nearing retirement
    • Have expressed career aspirations that extend outside your organization
    • Have hit a career development ceiling at your organization
    • Are disengaged
    • Are actively job searching
    • Are facing performance issues or dismissal OR promotion into a new role

    Employees are low risk for departure if they:

    • Are a new hire or new to their role
    • Are highly engaged
    • Have high potential
    • Are 5-10 years out from retirement

    If you are not sure where an employee stands with respect to leaving the organization, consider having a development conversation with them. In the meantime, consider them at medium risk for departure.

    To estimate the impact of departure, consider:

    • The effect of losing the employee in the near- and medium-term, including:
      • Impact on the organization, department, unit/team and projects
      • The cost (in time, resources, and productivity loss) to replace the individual
      • The readiness of internal successors for the role

    1.3 Conduct a risk analysis to identify future needs

    1-3 hours

    Preparation: Your estimation of whether key employees are at risk of leaving the organization will depend on what you know of them objectively (skills, age), as well as what you learn from development conversations. Ensure you collect all relevant information prior to conducting this activity. You may need to speak with employees' direct managers beforehand or include them in the discussion.

    • As a group, list all your current employees, and using the previous slide for guidance, rank them on two parameters: risk of departure and impact of departure, on a scale of low to high. Record your conclusions in a chart like the one on the right. (For a more in-depth risk assessment, use the "Risk Assessment Results" tab of the Key Roles Succession Planning Tool.)
    • Employees that fall in the "Mitigate" quadrant represent key at-risk roles with at least moderate risk and moderate impact. These are your succession planning priorities. Add these roles to your list of key roles and competency gaps, and include them in your workforce planning analysis.
    • Employees that fall in the "Manage" quadrants represent secondary priorities, which should be looked at if there is capacity after considering the "Mitigate" roles.

    Record this information in the Workforce Planning Workbook for Small Enterprises.

    This is an image of the Risk analysis for risk of departure to importance of departure.

    Info-Tech Insight

    Don't be afraid to rank most or all your staff as "high impact of departure." In a small enterprise, every player counts, and you must plan accordingly.

    1.3 Conduct a risk analysis to identify future needs

    Input Output
    • Employee data on competencies, skills, certifications, and performance. Input from managers from informal development conversations.
    • A list of first- and second-priority at-risk roles to carry forward into a succession planning analysis
    Materials Participants
    • Leadership team
    • Managers

    Determine your skill sourcing route

    The characteristics of need steer hiring managers to a preferred choice, while the marketplace analysis will tell you the feasibility of each option.

    Sourcing Options

    Preferred Options

    Final Choice

    four blue circles

    A right facing arrow

    Two blue circles A right facing arrow One blue circle
    State of the Marketplace

    State of the Marketplace

    Urgency: How soon do we need this skill? What is the required time-to-value?

    Criticality: How critical, i.e. core to business goals, are the services or systems that this skill will support?

    Novelty: Is this skill brand new to our workforce?

    Availability: How often, and at what hours, will the skill be needed?

    Durability: For how long will this skill be needed? Just once, or indefinitely for regular operations?

    Scarcity: How popular or desirable is this skill? Do we have a large enough talent pool to draw from? What competition are we facing for top talent?

    Cost: How much will it cost to hire vs. contract vs. outsource vs. train this skill?

    Preparedness: Do we have internal resources available to cultivate this skill in house?

    1.4 Determine your skill sourcing route

    1-3 hours

    1. Identify the preferred sourcing method as a group, starting with the most critical or urgent skill need on your list. Use the characteristics of need to guide your discussion. If more than one option seems adequate, carry several over to the next step.
    2. Consider the marketplace factors applicable to the skill in question and use these to narrow down to one final sourcing decision.
      1. If it is not clear whether a suitable internal candidate is available or ready, refer to the next activity for a readiness assessment.
    3. Be sure to document the rationale supporting your decision. This will ensure the decision can be clearly communicated to any stakeholders, and that you can review on your decision-making process down the line.

    Record this information in the Workforce Planning Workbook for Small Enterprises.

    Info-Tech Insight

    Consider developing a pool of successors instead of pinning your hopes on just one person. A single pool of successors can be developed for either one key role that has specialized requirements or even multiple key roles that have generic requirements.

    Input

    Output

    • List of current and upcoming skill gaps
    • A sourcing decision for each skill

    Materials

    Participants

    • Leadership team
    • Human resource partner (if applicable)

    1.5 Determine readiness of internal successors

    1-3 hours

    1. As a group, and ensuring you include the candidates' direct managers, identify potential successors for the first role on your list.
    2. Ask how effectively the potential successor would serve in the role today. Review the competencies for the key role in terms of:
      1. Relationship-building skills
      2. Business skills
      3. Technical skills
      4. Industry-specific skills or knowledge
    3. Determine what competencies the succession candidate currently has and what must be learned. Be sure you know whether the candidate is open to a career change. Don't assume – if this is not clear, have a development conversation to ensure everyone is on the same page.
    4. Finally, determine how difficult it will be for the successor to acquire missing skills or knowledge, whether the resources are available to provide the required development, and how long it will take to provide it.
    5. As a group, decide whether training an internal successor is a viable option for the role in question, considering the successor's readiness and the characteristics of need for the role. If a clear successor is not readily apparent, consider:
      1. If the development of the successor can be fast-tracked, or if some requirements can be deprioritized and the successor provided with temporary support from other employees.
      2. If the role in question is being discussed because the current incumbent is preparing to leave, consider negotiating an arrangement that extends the incumbent's employment tenure.
    6. Record the decision and repeat for the next role on your list.

    Info-Tech Insight

    A readiness assessment helps to define not just development needs, but also any risks around the organization's ability to fill a key role.

    Input

    Output

    • List of roles for which you are considering training internally
    • Job descriptions and competency requirements for the roles
    • List of roles for which internal successors are a viable option

    Materials

    Participants

    • Leadership team
    • Candidates' direct managers, if applicable

    Use alternative work arrangements to gain time to prepare successors

    Alternative work arrangements are critical tools that employers can use to achieve a mutually beneficial solution that mitigates the risk of loss associated with key roles.

    Alternative work arrangements not only support employees who want to keep working, but more importantly, they allow the business to retain employees that are needed in key roles who are departure risks due to retirement.

    Viewing retirement as a gradual process can help you slow down skill loss in your organization and ensure you have sufficient time to train successors. Retiring workers are becoming increasingly open to alternative work arrangements. Among employed workers aged 50-75, more than half planned to continue working part-time after retirement.
    Source: Statistics Canada.

    Flexible work options are the most used form of alternative work arrangement

    A bar graph showing the percent of organizations who implemented alternate work arrangement, for Flexible work options; Contract based work; Part time roles; Graduated retirement programs; Part year jobs or job sharing; Increased PTO for employees over a certain age.

    Source: McLean & Company, N=44

    Choose the alternative work arrangement that works best for you and the employee

    Alternative Work Arrangement Description Ideal Use Caveats
    Flexible work options Employees work the same number of hours but have flexibility in when and where they work (e.g. from home, evenings). Employees who work fairly independently with no or few direct reports. Employee may become isolated or disconnected, impeding knowledge transfer methods that require interaction or one-on-one time.
    Contract-based work Working for a defined period of time on a specific project on a non-salaried or non-wage basis. Project-oriented work that requires specialized knowledge or skills. Available work may be sporadic or specific projects more intensive than the employee wants. Knowledge transfer must be built into the contractual arrangement.
    Part-time roles Half days or a certain number of days per week; indefinite with no end date in mind. Employees whose roles can be readily narrowed and upon whom people and critical processes are not dependent. It may be difficult to break a traditionally full-time job down into a part-time role given the size and nature of associated tasks.
    Graduated retirement Retiring employee has a set retirement date, gradually reducing hours worked per week over time. Roles where a successor has been identified and is available to work alongside the incumbent in an overlapping capacity while he or she learns. The role may only require a single FTE, and the organization may not be able to afford the amount of redundancy inherent in this arrangement.

    Choose the alternative work arrangement that works best for you and the employee

    Alternative Work Arrangement Description Ideal Use Caveats
    Part-year jobs or job sharing Working part of the year and having the rest of the year off, unpaid. Project-oriented work where ongoing external relationships do not need to be maintained. The employee is unavailable for knowledge transfer activities for a large portion of the year. Another risk is that the employee may opt not to return at the end of the extended time off with little notice.
    Increased paid time off Additional vacation days upon reaching a certain age. Best used as recognition or reward for long-term service. This may be a particularly useful retention incentive in organizations that do not offer pension plans. The company may not be able to financially afford to pay for such extensive time off. If the role incumbent is the only one in the role, this may mean crucial work is not being done.
    Altered roles Concentration of a job description on fewer tasks that allows the employee to focus on his or her specific expertise. Roles where a successor has been identified and is available to work alongside the incumbent, with the incumbent's new role highly focused on mentoring. The role may only require a single FTE, and the organization may not be able to afford the amount of redundancy inherent in this arrangement.

    Phase 2

    Knowledge Transfer

    Workforce Planning

    Knowledge Transfer

    Development Planning

    Identify needs, goals, metrics, and skill gaps.

    Select a skill sourcing strategy.

    Discover critical knowledge.

    Select knowledge transfer methods.

    Identify priority competencies.

    Assess employees.

    Draft development goals.

    Provide coaching & feedback.

    The Small Enterprise Guide to People and Resource Management

    Phase Participants

    • Leadership/management team
    • Incumbent & successor

    Additional Resources

    IT Knowledge Identification Interview Guide Template

    Knowledge Transfer Plan Template

    Determine your skill sourcing route

    Knowledge transfer plans have three key components that you need to complete for each knowledge source:

    Define what knowledge needs to be transferred

    Each knowledge source has unique information which needs to be transferred. Chances are you don't know what you don't know. The first step is therefore to interview knowledge sources to find out.

    Identify the knowledge receiver

    Depending on who the information is going to, the knowledge transfer tactic you employ will differ. Before deciding on the knowledge receiver and tactic, consider three key factors:

    • How will this knowledge be used in the future?
    • What is the next career step for the knowledge receiver?
    • Are the receiver and the source going to be in the same location?

    Identify which knowledge transfer tactics you will use for each knowledge asset

    Not all tactics are good in every situation. Always keep the "knowledge type" (information, process, skills, and expertise), knowledge sources' engagement level, and the knowledge receiver in mind as you select tactics.

    Don't miss tacit knowledge

    There are two basic types of knowledge: "explicit" and "tacit." Ensure you capture both to get a well-rounded overview of the role.

    Explicit Tacit
    • "What knowledge" – knowledge can be articulated, codified, and easily communicated.
    • Easily explained and captured – documents, memos, speeches, books, manuals, process diagrams, facts, etc.
    • Learn through reading or being told.
    • "How knowledge" – intangible knowledge from an individual's experience that is more from the process of learning, understanding, and applying information (insights, judgments, and intuition).
    • Hard to verbalize, and difficult to capture and quantify.
    • Learn through observation, imitation, and practice.

    Types of explicit knowledge

    Types of tacit knowledge

    Information Process Skills Expertise

    Specialized technical knowledge.

    Unique design capabilities/methods/models.

    Legacy systems, details, passwords.

    Special formulas/algorithms/ techniques/contacts.

    • Specialized research & development processes.
    • Proprietary production processes.
    • Decision-making processes.
    • Legacy systems.
    • Variations from documented processes.
    • Techniques for executing on processes.
    • Relationship management.
    • Competencies built through deliberate practice enabling someone to act effectively.
    • Company history and values.
    • Relationships with key stakeholders.
    • Tips and tricks.
    • Competitor history and differentiators.

    e.g. Knowing the lyrics to a song, building a bike, knowing the alphabet, watching a YouTube video on karate.

    e.g. Playing the piano, riding a bike, reading or speaking a language, earning a black belt in karate.

    Embed your knowledge transfer methods into day-to-day practice

    Multiple methods should be used to transfer as much of a person's knowledge as possible, and mentoring should always be one of them. Select your method according to the following criteria:

    Info-Tech Insight

    The more integrated knowledge transfer is in day-to-day activities, the more likely it is to be successful, and the lower the time cost. This is because real learning is happening at the same time real work is being accomplished.

    Type of Knowledge

    • Tacit knowledge transfer methods are often informal and interactive:
      • Mentoring
      • Multi-generational work teams
      • Networks and communities
      • Job shadowing
    • Explicit knowledge transfer methods tend to be more formal and one way:
      • Formal documentation of processes and best practices
      • Self-published knowledge bases
      • Formal training sessions
      • Formal interviews

    Incumbent's Preference/Successor's Preference

    Ensure you consult the employees, and their direct manager, on the way they are best prepared to teach and learn. Some examples of preferences include:

    1. Prefer traditional classroom learning, augmented with participation, critical reflection, and feedback.
    2. May get bored during formal training sessions and retain more during job shadowing.
    3. Prefer to be self-directed or self-paced, and highly receptive to e-learning and media.
    4. Prefer informal, incidental learning, tend to go immediately to technology or direct access to people. May have a short attention span and be motivated by instant results.
    5. May be uncomfortable with blogs and wikis, but comfortable with SharePoint.

    Cost

    Consider costs beyond the monetary. Some methods require an investment in time (e.g. mentoring), while others require an investment in technology (e.g. knowledge bases).

    The good news is that many supporting technologies may already exist in your organization or can be acquired for free.

    Methods that cost time may be difficult to get underway since employees may feel they don't have the time or must change the way they work.

    2.1 Create a knowledge transfer plan

    1-3 hours

    1. Working together with the current incumbent, brainstorm the key information pertaining to the role that you want to pass on to the successor. Use the IT Knowledge Identification Interview Guide Template to ensure you don't miss anything.
      • Consider key knowledge areas, including:
        • Specialized technical knowledge.
        • Specialized research and development processes.
        • Unique design capabilities/methods/models.
        • Special formulas/algorithms/techniques.
        • Proprietary production processes.
        • Decision-making criteria.
        • Innovative sales methods.
        • Knowledge about key customers.
        • Relationships with key stakeholders.
        • Company history and values.
      • Ask questions of both sources and receivers of knowledge to help determine the best knowledge transfer methods to use.
        • What is the nature of the knowledge? Explicit or tacit?
        • Why is it important to transfer?
        • How will the knowledge be used?
        • What knowledge is critical for success?
        • How will the users find and access it?
        • How will it be maintained and remain relevant and usable?
        • What are the existing knowledge pathways or networks connecting sources to recipients?
    2. Once the knowledge has been identified, use the information on the following slides to decide on the most appropriate methods. Be sure to consult the incumbent and successor on their preferences.
    3. Prioritize your list of knowledge transfer activities. It's important not to try to do too much too quickly. Focus on some quick wins and leverage the success of these initiatives to drive the project forward. Follow these steps as a guide:
      1. Take an inventory of all the tactics and techniques which you plan to employ. Eliminate redundancies where possible.
      2. Start your implementation with your highest risk role or knowledge item, using explicit knowledge transfer tactics. Interviews, use cases, and process mapping will give you some quick wins and will help gain momentum for the project.
      3. Then move forward to other tactics, the majority of which will require training and process design. Pick 1-2 other key tactics you would like to employ and build those out. For tactics that require resources or monetary investment, start with those that can be reused for multiple roles.

    Record your plan in the IT Knowledge Transfer Plan Template.

    Download the IT Knowledge Identification Interview Guide Template

    Download the Knowledge Transfer Plan Template

    Info-Tech Insight

    Wherever possible, ask employees about their personal learning styles. It's likely that a collaborative compromise will have to be struck for knowledge transfer to work well.

    2.1 Create a knowledge transfer plan

    Input

    Output

    • List of roles for which you need to transfer knowledge
    • Prioritized list of knowledge items and chosen transfer method

    Materials

    Participants

    • Leadership team
    • Incumbent
    • Successor

    Not every transfer method is effective for every type of knowledge

    Knowledge Type
    Tactic Explicit Tacit
    Information Process Skills Expertise
    Interviews Very Strong Strong Strong Strong
    Process Mapping Medium Very Strong Very Weak Very Weak
    Use Cases Medium Very Strong Very Weak Very Weak
    Job Shadow Very Weak Medium Very Strong Very Strong
    Peer Assist Strong Medium Very Strong Very Strong
    Action Review Medium Medium Strong Strong
    Mentoring Weak Weak Strong Very Strong
    Transition Workshop Strong Strong Strong Weak
    Storytelling Weak Weak Strong Very Strong
    Job Share Weak Weak Very Strong Very Strong
    Communities of Practice Strong Weak Very Strong Very Strong

    This table shows the relative strengths and weaknesses of each knowledge transfer tactic compared against four different knowledge types.

    Not all techniques are effective for all types of knowledge; it is important to use a healthy mixture of techniques to optimize effectiveness.

    Employees' engagement can impact knowledge transfer effectiveness

    Level of Engagement
    Tactic Disengaged/ Indifferent Almost Engaged - Engaged
    Interviews Yes Yes
    Process Mapping Yes Yes
    Use Cases Yes Yes
    Job Shadow No Yes
    Peer Assist Yes Yes
    Action Review Yes Yes
    Mentoring No Yes
    Transition Workshop Yes Yes
    Storytelling No Yes
    Job Share Maybe Yes
    Communities of Practice Maybe Yes

    When considering which tactics to employ, it's important to consider the knowledge holder's level of engagement. Employees who you would identify as being disengaged may not make good candidates for job shadowing, mentoring, or other tactics where they are required to do additional work or are asked to influence others.

    Knowledge transfer can be controversial for all employees as it can cause feelings of job insecurity. It's essential that motivations for knowledge transfer are communicated effectively.

    Pay particular attention to your communication style with disengaged and indifferent employees, communicate frequently, and tie communication back to what's in it for them.

    Putting disengaged employees in a position where they are mentoring others can be a risk, as their negativity could influence others not to participate, or it could negate the work you're doing to create a positive knowledge sharing culture.

    Employees' engagement can impact knowledge transfer effectiveness

    Effort by Stakeholder

    Tactic

    Business Analyst

    IT Manager

    Knowledge Holder

    Knowledge Receiver

    Interviews

    These tactics require the least amount of effort, especially for organizations that are already using these tactics for a traditional requirements gathering process.

    Medium

    N/A

    Low

    Low

    Process Mapping

    Medium

    N/A

    Low

    Low

    Use Cases

    Medium

    N/A

    Low

    Low

    Job Shadow

    Medium

    Medium

    Medium

    Medium

    Peer Assist

    Medium

    Medium

    Medium

    Medium

    Action Review

    These tactics generally require more involvement from IT management and the BA in tandem for preparation. They will also require ongoing effort for all stakeholders. It's important to gain stakeholder buy-in as it is key for success.

    Low

    Medium

    Medium

    Low

    Mentoring

    Medium

    High

    High

    Medium

    Transition Workshop

    Medium

    Low

    Medium

    Low

    Storytelling

    Medium

    Medium

    Low

    Low

    Job Share

    Medium

    High

    Medium

    Medium

    Communities of Practice

    High

    Medium

    Medium

    Medium

    Phase 3

    Development Planning

    Workforce Planning

    Knowledge Transfer

    Development Planning

    Identify needs, goals, metrics, and skill gaps.

    Select a skill sourcing strategy.

    Discover critical knowledge.

    Select knowledge transfer methods.

    Identify priority competencies.

    Assess employees.

    Draft development goals.

    Provide coaching & feedback.

    The Small Enterprise Guide to People and Resource Management

    Phase Participants

    • Leadership team
    • Managers
    • Employees

    Additional Resources

    Effective development planning hinges on robust performance management

    Your performance management framework is rooted in organizational goals and defines what it means to do any given role well.

    Your organization's priority competencies are the knowledge, skills and attributes that enable an employee to do the job well.

    Each individual's development goals are then aimed at building these priority competencies.

    Mission Statement

    To be the world's leading manufacturer and distributor of widgets.

    Business Goal

    To increase annual revenue by 10%.

    IT Department Objective

    To ensure reliable communications infrastructure and efficient support for our sales and development teams.

    Individual Role Objective

    To decrease time to resolution of support requests by 10% while maintaining quality.

    Info-Tech Insight

    Without a performance management framework, your employees cannot align their development with the organization's goals. For detailed guidance, see Info-Tech's blueprint Setting Meaningful Employee Performance Measures.

    What is a competency?

    The term "competency" refers to the collection of knowledge, skills, and attributes an employee requires to do a job well.

    Often organizations have competency frameworks that consist of core, leadership, and functional competencies.

    Core competencies apply to every role in the organization. Typically, they are tied to organizational values and business mission and/or vision.

    Functional competencies are at the department, work group, or job role levels. They are a direct reflection of the function or type of work carried out.

    Leadership competencies generally apply only to people managers in the organization. Typically, they are tied to strategic goals in the short to medium term

    Generic Functional
    • Core
    • Leadership
    • IT
    • Finance
    • Sales
    • HR

    Use the SMART model to make sure goals are reasonable and attainable

    S

    Specific: Be specific about what you want to accomplish. Think about who needs to be involved, what you're trying to accomplish, and when the goal should be met.

    M

    Measurable: Set metrics that will help to determine whether the goal has been reached.

    A

    Achievable: Ensure that you have both the organizational resources and employee capability to accomplish the goal.

    R

    Relevant: Goals must align with broader business, department, and development goals in order to be meaningful.

    T

    Time-bound: Provide a target date to ensure the goal is achievable and provide motivation.

    Example goal:

    "Learn Excel this summer."

    Problems:

    Not specific enough, not measurable enough, nor time bound.

    Alternate SMART goal:

    "Consult with our Excel expert and take the lead on creating an Excel tool in August."

    3.2 Identify target competencies & draft development goals

    1 hour

    Pre-work: Employees should come to the career conversation having done some self-reflection. Use Info-Tech's IT Employee Career Development Workbook to help employees identify their career goals.

    1. Pre-work: Managers should gather any data they have on the employee's current proficiency at key competencies. Potential sources include task-based assessments, performance ratings, supervisor or peer feedback, and informal conversation.

      Prioritize competencies. Using your list of priority organizational competencies, work with your employees to help them identify two to four competencies to focus on developing now and in the future. Use the Individual Competency Development Plan template to document your assessment and prioritize competencies for development. Consider the following questions for guidance:
      1. Which competencies are needed in my current role that I do not have full proficiency in?
      2. Which competencies are related to both my career interests and the organization's priorities?
      3. Which competencies are related to each other and could be developed together or simultaneously?
    2. Draft goals. Ask your employee to create a list of multiple simple goals to develop the competencies they have selected to work on developing over the next year. Identifying multiple goals helps to break development down into manageable chunks. Ensure goals are concrete, for example, if the competency is "communication skills," your development goals could be "presentation skills" and "business writing."
    3. Review goals:
      1. Ask why these areas are important to the employee.
      2. Share your ideas and why it is important that the employee develop in the areas identified.
      3. Ensure that the goals are realistic. They should be stretch goals, but they must be achievable. Use the SMART framework on the previous slide for guidance.

    Info-Tech Insight

    Lack of career development is the top reason employees leave organizations. Development activities need to work for both the organization and the employee's own development, and clearly link to advancing employees' careers either at the organization or beyond.

    Download the IT Employee Career Development Workbook

    Download the Individual Competency Development Plan

    3.2 Identify target competencies & draft development goals

    Input

    Output

    • Employee's career aspirations
    • List of priority organizational competencies
    • Assessment of employee's current proficiency
    • A list of concrete development goals

    Materials

    Participants

    • Employee
    • Direct manager

    Apply a blend of learning methods

    • Info-Tech recommends the 70-20-10 principle for learning and development, which places the greatest emphasis on learning by doing. This experiential learning is then supported by feedback from mentoring, training, and self-reflection.
    • Use the 70-20-10 principle as a guideline – the actual breakdown of your learning methods will need to be tailored to best suit your organization and the employee's goals.

    Spend development time and effort wisely:

    70%

    On providing challenging on-the-job opportunities

    20%

    On establishing opportunities for people to develop learning relationships with others, such as coaching and mentoring

    10%

    On formal learning and training programs

    Internal initiatives are a cost-effective development aid

    Internal Initiative

    What Is It?

    When to Use It

    Special Project

    Assignment outside of the scope of the day-to-day job (e.g. work with another team on a short-term initiative).

    As an opportunity to increase exposure and to expand skills beyond those required for the current job.

    Stretch Assignment

    The same projects that would normally be assigned, but in a shorter time frame or with a more challenging component.

    Employee is consistently meeting targets and you need to see what they're capable of.

    Training Others

    Training new or more junior employees on their position or a specific process.

    Employee wants to expand their role and responsibility and is proficient and positive.

    Team Lead On an Assignment

    Team lead for part of a project or new initiative.

    To prepare an employee for future leadership roles by increasing responsibility and developing basic managerial skills.

    Job Rotation

    A planned placement of employees across various roles in a department or organization for a set period of time.

    Employee is successfully meeting and/or exceeding job expectations in their current role.

    Incorporating a development objective into daily tasks

    What do we mean by incorporating into daily tasks?

    The next time you assign a project to an employee, you should also ask the employee to think about a development goal for the project. Try to link it back to their existing goals or have them document a new goal in their development plan.

    For example: A team of employees always divides their work in the same way. Their goal for their next project could be to change up the division of responsibility so they can learn each other's roles.

    Another example:

    "I'd like you to develop your ability to explain technical terms to a non-technical audience. I'd like you to sit down with the new employee who starts tomorrow and explain how to use all our software, getting them up and running."

    Info-Tech Insight

    Employees often don't realize that they are being developed. They either think they are being recognized for good work or they are resentful of the additional workload.

    You need to tell your employees that the activity you are asking them to do is intended to further their development.

    However, be careful not to sell mundane tasks as development opportunities – this is offensive and detrimental to engagement.

    Establish manager and employee accountability for following up

    Ensure that the employee makes progress in developing prioritized competencies by defining accountabilities:

    Tracking Progress

    Checking In

    Development Meetings

    Coaching & Feedback

    Employee accountability:

    • Employees need to keep track of what they learn.
    • Employees should take the time to reflect on their progress.

    Manager accountability:

    • Managers need to make the time for employees to reflect.

    Employee accountability:

    • Employees need to provide managers with updates and ask for help.

    Manager accountability:

    • Managers need to check in with employees to see if they need additional resources.

    Employee accountability:

    • Employees need to complete assessments again to determine whether they have made progress.

    Manager accountability:

    • Managers should schedule monthly meetings to discuss progress and identify next steps.

    Employee accountability:

    • Employees should ask their manager and colleagues for feedback after development activities.

    Manager accountability:

    • Managers can use both scheduled meetings and informal conversations to provide coaching and feedback to employees.

    3.3 Select development activities and schedule check-ins

    1-3 hours

    Pre-work: Employees should research potential development activities and come prepared with a range of suggestions.

    Pre-work: Managers should investigate options for employee development, such as internal training/practice opportunities for the employee's selected competencies and availability of training budget.

    1. Communicate your findings about internal opportunities and external training allowance to the employee. This can also be done prior to the meeting, to help guide the employee's own research. Address any questions or concerns.
    2. Review the employee's proposed list of activities, and identify priority ones based on:
      1. How effectively they support the development of priority competencies.
      2. How closely they match the employee's original goals.
      3. The learning methods they employ, and whether the chosen activities support a mix of different methods.
      4. The degree to which the employee will have a chance to practice new skills hands-on.
      5. The amount of time the activities require, balanced against the employee's work obligations.
    3. Guide the employee in selecting activities for the short and medium term. Establish an understanding that this list is tentative and subject to ongoing revision during future check-ins.
      1. If in doubt about whether the employee is over-committing, err on the side of fewer activities to start.
    4. Schedule a check-in for one month out to review progress and roadblocks, and to reaffirm priorities.
    5. Check-ins should be repeated regularly, typically once a month.

    Download the Learning Methods Catalog

    Info-Tech Insight

    Adopt a blended learning approach using a variety of techniques to effectively develop competencies. This will reinforce learning and accommodate different learning styles. See Info-Tech's Learning Methods Catalog for a description of popular experiential, relational, and formal learning methods.

    3.3 Select development activities and schedule check-ins

    Input

    Output

    • List of potential development activities (from employee)
    • List of organizational resources (from manager)
    • A selection of feasible development activities
    • Next check-in scheduled

    Materials

    Participants

    • Employee
    • Direct manager

    Tips for tricky conversations about development

    What to do if…

    Employees aren't interested in development:

    • They may have low aspiration for advancement.
    • Remind them about the importance of staying current in their role given increasing job requirements.
    • Explain that skill development will make their job easier and make them more successful at it; sell development as a quick and effective way to learn the skill.
    • Indicate your support and respond to concerns.

    Employees have greater aspiration than capability:

    • Explain that there are a number of skills and capabilities that they need to improve in order to move to the next level. If the specific skills were not discussed during the performance appraisal, do not hesitate to explain the improvements that you require.
    • Inform the employee that you want them to succeed and that by pushing too far and too fast they risk failure, which would not be beneficial to anyone.
    • Reinforce that they need to do their current job well before they can be considered for promotion.

    Employees are offended by your suggestions:

    • Try to understand why they are offended. Before moving forward, clarify whether they disagree with the need for development or the method by which you are recommending they be developed.
    • If it is because you told them they had development needs, then reiterate that this is about helping them to become better and that everyone has areas to develop.
    • If it is about the development method, discuss the different options, including the pros and cons of each.

    Coaching and feedback skills help managers guide employee development

    Coaching and providing feedback are often confused. Managers often believe they are coaching when they are just giving feedback. Learn the difference and apply the right approach for the right situation.

    What is coaching?

    A conversation in which a manager asks questions to guide employees to solve problems themselves.

    Coaching is:

    • Future-focused
    • Collaborative
    • Geared toward growth and development

    What is feedback?

    Information conveyed from the manager to the employee about their performance.

    Feedback is:

    • Past-focused
    • Prescriptive
    • Geared toward behavior and performance

    Info-Tech Insight

    Don't forget to develop your managers! Ensure coaching, feedback, and management skills are part of your management team's development plan.

    Understand the foundations of coaching to provide effective development coaching:

    Knowledge Mindset Relationship
    • Understand what coaching is and how to apply it:
    • Identify when to use coaching, feedback, or other people management practices, and how to switch between them.
    • Know what coaching can and cannot accomplish.
    • When focusing on performance, guide an employee to solve problems related to their work. When focusing on development, guide an employee to reach their own development goals.
    • Adopt a coaching mindset by subscribing to the following beliefs:
    • Employees want to achieve higher performance and have the potential to do so.
    • Employees have a unique and valuable perspective to share of the challenges they face as well as the possible solutions.
    • Employees should be empowered to realize solutions themselves to motivate them in achieving goals.
    • Develop a relationship of trust between managers and employees:
    • Create an environment of psychological safety where employees feel safe to be open and honest.
    • Involve employees in decision making and inform employees often.
    • Invest in employees' success.
    • Give and expect candor.
    • Embrace failure.

    Apply the "4A" behavior-focused coaching model

    Using a model allows every manager, even those with little experience, to apply coaching best practices effectively.

    Actively Listen

    Ask

    Action Plan

    Adapt

    Engage with employees and their message, rather than just hearing their message.

    Key active listening behaviors:

    • Provide your undivided attention.
    • Observe both spoken words and body language.
    • Genuinely try to understand what the employee is saying.
    • Listen to what is being said, then paraphrase back what you heard.

    Ask thoughtful, powerful questions to learn more information and guide employees to uncover opportunities and/or solutions.

    Key asking behaviors:

    • Ask open-ended questions.
    • Ask questions to learn something you didn't already know.
    • Ask for reasoning (the why).
    • Ask "what else?"

    Hold employees and managers accountable for progress and results.

    During check-ins, review each development goal to ensure employees are meeting their targets.

    Key action planning behaviors:

    Adapt to individual employees and situations.

    Key adapting behaviors:

    • Recognize employees' unique characteristics.
    • Appreciate the situation at hand and change your behavior and communication in order to best support the individual employee.

    Use the following questions to have meaningful coaching conversations

    Opening Questions

    • What's on your mind?
    • Do you feel you've had a good week/month?
    • What is the ideal situation?
    • What else?

    Problem-Identifying Questions

    • What is most important here?
    • What is the challenge here for you?
    • What is the real challenge here for you?
    • What is getting in the way of you achieving your goal?

    Problem-Solving Questions

    • What are some of the options available?
    • What have you already tried to solve this problem? What worked? What didn't work?
    • Have you considered all the possibilities?
    • How can I help?

    Next-Steps Questions

    • What do you need to do, and when, to achieve your goal?
    • What resources are there to help you achieve your goal? This includes people, tools, or even resources outside our organization.
    • How will you know when you have achieved your goal? What does success look like?

    The purpose of asking questions is to guide the conversation and learn something you didn't already know. Choose the questions you ask based on the flow of the conversation and on what information you would like to uncover. Approach the answers you get with an open mind.

    Info-Tech Insight

    Avoid the trap of "hidden agenda" questions, whose real purpose is to offer your own advice.

    Use the following approach to give effective feedback

    Provide the feedback in a timely manner

    • Plan the message you want to convey.
    • Provide feedback "just-in-time."
    • Ensure recipient is not preoccupied.
    • Try to balance the feedback; refer to successful as well as unsuccessful behavior.

    Communicate clearly, using specific examples and alternative behaviors

    • Feedback must be honest and helpful.
    • Be specific and give a recent example.
    • Be descriptive, not evaluative.
    • Relate feedback to behaviors that can be changed.
    • Give an alternative positive behavior.

    Confirm their agreement and understanding

    • Solicit their thoughts on the feedback.
    • Clarify if not understood; try another example.
    • Confirm recipient understands and accepts the feedback.

    Manager skill is crucial to employee development

    Development is a two-way street. This means that while employees are responsible for putting in the work, managers must enable their development with support and guidance. The latter is a skill, which managers must consciously cultivate.

    For more in-depth management skills development, see the Info-Tech "Build a Better Manager" training resources:

    Bibliography

    Anderson, Kelsie. "Is Your IT Department Prepared for the 4 Biggest Challenges of 2017?" 14 June 2017.
    Atkinson, Carol, and Peter Sandiford. "An Exploration of Older Worker Flexible Working Arrangements in Smaller Firms." Human Resource Management Journal, vol. 26, no. 1, 2016, pp. 12–28. Wiley Online Library.
    BasuMallick, Chiradeep. "Top 8 Best Practices for Employee Cross-Training." Spiceworks, 15 June 2020.
    Birol, Andy. "4 Ways You Can Succeed With a Staff That 'Wears Multiple Hats.'" The Business Journals, 26 Nov. 2013.
    Bleich, Corey. "6 Major Benefits To Cross-Training Employees." EdgePoint Learning, 5 Dec. 2018.
    Cancialosi, Chris. "Cross-Training: Your Best Defense Against Indispensable Employees." Forbes, 15 Sept. 2014.
    Cappelli, Peter, and Anna Tavis. "HR Goes Agile." Harvard Business Review, Mar. 2018.
    Chung, Kai Li, and Norma D'Annunzio-Green. "Talent Management Practices of SMEs in the Hospitality Sector: An Entrepreneurial Owner-Manager Perspective." Worldwide Hospitality and Tourism Themes, vol. 10, no. 4, Jan. 2018.
    Clarkson, Mary. Developing IT Staff: A Practical Approach. Springer Science & Business Media, 2012.
    "CNBC and SurveyMonkey Release Latest Small Business Survey Results." Momentive, 2019. Press Release. Accessed 6 Aug. 2020.
    Cselényi, Noémi. "Why Is It Important for Small Business Owners to Focus on Talent Management?" Jumpstart:HR | HR Outsourcing and Consulting for Small Businesses and Startups, 25 Mar. 2013.
    dsparks. "Top 10 IT Concerns for Small Businesses." Stratosphere Networks IT Support Blog - Chicago IT Support Technical Support, 16 May 2017.
    Duff, Jimi. "Why Small to Mid-Sized Businesses Need a System for Talent Management | Talent Management Blog | Saba Software." Saba, 17 Dec. 2018.
    Employment and Social Development Canada. "Age-Friendly Workplaces: Promoting Older Worker Participation." Government of Canada, 3 Oct. 2016.
    Exploring Workforce Planning. Accenture, 23 May 2017.
    "Five Major IT Challenges Facing Small and Medium-Sized Businesses." Advanced Network Systems. Accessed 25 June 2020.
    Harris, Evan. "IT Problems That Small Businesses Face." InhouseIT, 17 Aug. 2016.
    Heathfield, Susan. "What Every Manager Needs to Know About Succession Planning." Liveabout, 8 June 2020.
    ---. "Why Talent Management Is an Important Business Strategy." Liveabout, 29 Dec. 2019.
    Herbert, Chris. "The Top 5 Challenges Facing IT Departments in Mid-Sized Companies." ExpertIP, 25 June 2012.
    How Smaller Organizations Can Use Talent Management to Accelerate Growth. Avilar. Accessed 25 June 2020.
    Krishnan, TN, and Hugh Scullion. "Talent Management and Dynamic View of Talent in Small and Medium Enterprises." Human Resource Management Review, vol. 27, no. 3, Sept. 2017, pp. 431–41.
    Mann Jackson, Nancy. "Strategic Workforce Planning for Midsized Businesses." ADP, 6 Feb. 2017.
    McCandless, Karen. "A Beginner's Guide to Strategic Talent Management (2020)." The Blueprint, 26 Feb. 2020.
    McFeely, Shane, and Ben Wigert. "This Fixable Problem Costs U.S. Businesses $1 Trillion." Gallup.com, 13 Mar. 2019.
    Mihelič, Katarina Katja. Global Talent Management Best Practices for SMEs. Jan. 2020.
    Mohsin, Maryam. 10 Small Business Statistics You Need to Know in 2020 [May 2020]. 4 May 2020.
    Ramadan, Wael H., and B. Eng. The Influence of Talent Management on Sustainable Competitive Advantage of Small and Medium Sized Establishments. 2012, p. 15.
    Ready, Douglas A., et al. "Building a Game-Changing Talent Strategy." Harvard Business Review, no. January–February 2014, Jan. 2014.
    Reh, John. "Cross-Training Employees Strengthens Engagement and Performance." Liveabout, May 2019.
    Rennie, Michael, et al. McKinsey on Organization: Agility and Organization Design. McKinsey, May 2016.
    Roddy, Seamus. "The State of Small Business Employee Benefits in 2019." Clutch, 18 Apr. 2019.
    SHRM. "Developing Employee Career Paths and Ladders." SHRM, 28 Feb. 2020.
    Strandberg, Coro. Sustainability Talent Management: The New Business Imperative. Strandberg Consulting, Apr. 2015.
    Talent Management for Small & Medium-Size Businesses. Success Factors. Accessed 25 June 2020.
    "Top 10 IT Challenges Facing Small Business in 2019." Your IT Department, 8 Jan. 2019.
    "Why You Need Workforce Planning." Workforce.com, 24 Oct. 2022.

    The ESG Imperative and Its Impact on Organizations

    • Buy Link or Shortcode: {j2store}196|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: IT Governance, Risk & Compliance
    • Parent Category Link: /it-governance-risk-and-compliance
    • Global regulatory climate disclosure requirements are still evolving and are not consistent.
    • Sustainability is becoming a corporate imperative, but IT’s role is not fully clear.
    • The environmental, social, and governance (ESG) data challenge is large and continually expanding in scope.
    • Collecting the necessary data and managing ethical issues across supply chains is a daunting task.
    • Communicating long-term value is difficult when customer and employee expectations are shifting.

    Our Advice

    Critical Insight

    • An organization's approach to ESG cannot be static or tactical. It is a moving landscape that requires a flexible, holistic approach across the organization. Cross-functional coordination is essential in order to be ready to respond to changing conditions.
    • Even though the ESG data requirements are large and continually expanding in scope, many organizations have well-established data frameworks and governance practices in place to meet regulatory obligations such as Sarbanes–Oxley that should used as a starting point.

    Impact and Result

    • Organizations will have greater success if they focus their ESG program efforts on the ESG factors that will have a material impact on their company performance and their key stakeholders.
    • Continually evaluating the evolving ESG landscape and its impact on key stakeholders will enable organizations to react quickly to changing conditions.
    • A successful ESG program requires a collaborative and integrated approach across key business stakeholders.
    • Delivering high-quality metrics and performance indicators requires a flexible and digital data approach, where possible, to enable data interoperability.

    The ESG Imperative and Its Impact on Organizations Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. The ESG Imperative and Its Impact on Organizations Deck – Learn why sustainability is becoming a key measurement of corporate performance and how to set your organization up for success.

    Understand the foundational components and drivers of the broader concept of sustainability: environmental, social, and governance (ESG) and IT’s roles within an organization’s ESG program. Learn about the functional business areas involved, the roles they play and how they interact with each other to drive program success.

    • The ESG Imperative and Its Impact on Organizations Storyboard

    Infographic

    Further reading

    The ESG Imperative and Its Impact on Organizations

    Design to enable an active response to changing conditions.

    Analyst Perspective

    Environmental, social, and governance (ESG) is a corporate imperative that is tied to long-term value creation. An organization's social license to operate and future corporate performance depends on managing ESG factors well.

    Central to an ESG program is having a good understanding of the ESG factors that may have a material impact on enterprise value and key internal and external stakeholders. A comprehensive ESG strategy supported by strong governance and risk management is also essential to success.

    Capturing relevant data and applying it within risk models, metrics, and internal and external reports is necessary for sharing your ESG story and measuring your progress toward meeting ESG commitments. Consequently, the data challenges have received a lot of attention, and IT leaders have a role to play as strategic partner and enabler to help address these challenges. However, ESG is more than a data challenge, and IT leaders need to consider the wider implications in managing third parties, selecting tools, developing supporting IT architecture, and ensuring ethical design.

    For many organizations, the ESG program journey has just begun, and collaboration between IT and risk, procurement, and compliance will be critical in shaping program success.

    This is a picture of Donna Bales, Principal Research Director, Info-Tech Research Group

    Donna Bales
    Principal Research Director
    Info-Tech Research Group

    Executive Summary

    Your Challenge

    • Global regulatory climate disclosure requirements are still evolving and are not consistent.
    • Sustainability is becoming a corporate imperative, but IT's role is not fully clear.
    • The ESG data challenge is large and continually expanding in scope.
    • Collecting the necessary data and managing ethical issues across supply chains is a daunting task.
    • Communicating long-term value is difficult when customer and employee expectations are shifting.

    Common Obstacles

    • The data necessary for data-driven insights and accurate disclosure is often hampered by inaccurate and incomplete primary data.
    • Other challenges include:
      • Approaching ESG holistically and embedding it into existing governance, risk, and IT capabilities.
      • Building knowledge and adapting culture throughout all levels of the organization.
      • Monitoring stakeholder sentiment and keeping strategy aligned to expectations.

    Info-Tech's Approach

    • Use this blueprint to educate yourself on ESG factors and the broader concept of sustainability.
    • Learn about Info-Tech's ESG program approach and use it as a framework to begin your ESG program journey.
    • Identify changes that may be needed in your organizational operating model, strategy, governance, and risk management approach.
    • Discover areas of IT that may need to be prioritized and resourced.

    Info-Tech Insight

    An organization's approach to ESG cannot be static or tactical. ESG is a moving landscape that requires a flexible, holistic approach across the organization. It must become part of the way you work and enable an active response to changing conditions.

    This is an image of Info-Tech's thoughtmap for eight steps of the ESG Program Journey

    Putting ESG in context

    ESG has moved beyond the tipping point to corporate table stakes

    • In recent years, ESG issues have moved from voluntary initiatives driven by corporate responsibility teams to an enterprise-wide strategic imperative.
    • Organizations are no longer being measured by financial performance but by how they contribute to a sustainable and equitable future, such as how they support sustainable innovation through their business models and their focus on collaboration and inclusion.
    • A corporation's efforts toward sustainability is measured by three components: environmental, social, and governance.

    Sustainability

    The ability of a corporation and broader society to endure and survive over the long term by managing adverse impacts well and promoting positive opportunities.

    This is an image of the United Nation's 17 sustainable goals.

    Source: United Nations

    Putting "E," "S," and "G" in context

    Corporate sustainability depends on managing ESG factors well

    • Environmental, social, and governance are the component pieces of a sustainability framework that is used to understand and measure how an organization impacts or is affected by society as a whole.
    • Human activities, particularly fossil fuel burning since the mid twentieth century, have increased greenhouse gas concentration, resulting in observable changes to the atmosphere, ocean, cryosphere, and biosphere.
    • The E in ESG relates to the positive and negative impacts an organization may have on the environment, such as the energy it takes in and the waste it discharges.
    • The S in ESG is the most ambiguous component in the framework, as social impact relates not only to risks but also prosocial behaviour. It's the most difficult to measure but can have significant financial and reputational impact on corporations if material and poorly managed.
    • The G in ESG is foundational to the realization of S and E. It encompasses how well an organization integrates these considerations into the business and how well the organization engages with key stakeholders, receives feedback, and is transparent with its intentions.

    Common examples of ESG issues include: Environmental: Climate change, greenhouse gas emissions (CHG), deforestation, biodiversity, pollution, water, waste, extended producer responsibility, etc. Social: Customer relations, employee relations, labor, human rights, occupational health and safety, community relations, supply chains, etc. Governance: Board management practices, succession planning, compensation, diversity, equity and inclusion, regulatory compliance, corruption, fraud, data hygiene and security, etc. Source: Getting started with ESG - Sustainalytics

    Understanding the drivers behind ESG

    $30 trillion is expected to be transferred from the baby boomers to Generation Z and millennials over the next decade
    – Accenture

    Drivers

    • The rapid rise of ESG investing
    • The visibility of climate change is driving governments, society, and corporations to act and to initiate and support net zero goals.
    • A younger demographic that has strong convictions and financial influence
    • A growing trend toward mandatory climate and diversity, equity, and inclusion (DEI) disclosures required by global regulators
    • Recent emphasis by regulators on board accountability and fiduciary duty
    • Greater societal awareness of social issues and sustainability
    • A new generation of corporate leadership that is focused on sustainable innovation

    The evolving regulatory landscape

    Global regulators are mobilizing toward mandatory regulatory climate disclosure

    Canada

    • Canadian Securities Administrators (CSA) NI 51-107 Disclosure of Climate-related Matters

    Europe

    • European Commission, Sustainable Finance Disclosure Regulation (SFDR)
    • European Commission, EU Supply Chain Act
    • Germany – The German Supply Chain Act (GSCA)
    • Financial Conduct Authority UK, Proposal (DP 21/4) Sustainability Disclosure Requirements and investment labels
    • UK Modern Slavery Act, 2015

    United States

    • Securities and Exchange Commission (SEC) 33-11042– The Enhancement and Standardization of Climate-Related Disclosures for Investors
    • SEC 33-11038 Cybersecurity Risk Management, Strategy, Governance, and Incident Disclosure
    • Nasdaq Board Diversity Rule (5605(f))

    New Zealand

    • New Zealand, The Financial Sector (Climate-related Disclosures and Other Matters) Amendment Act 2021

    Begin by setting your purpose

    Consider your role as a corporation in society and your impact on key stakeholders

    • The impact of a corporation can no longer be solely measured by financial impact but also its impact on social good. Corporations have become real-world actors that impact and are affected by the environment, people, and society.
    • An ESG program should start with defining your organization's purpose in terms of corporate responsibility, the role it will play, and how it will endure over time through managing adverse impacts and promoting positive impacts.
    • Corporations should look inward and outward to assess the material impact of ESG factors on their organization and key internal and external stakeholders.
    • Once stakeholders are identified, consider how the ESG factors might be perceived by delving into what matters to stakeholders and what drives their behavior.

    Understanding your stakeholder landscape is essential to achieving ESG goals

    Internal Stakeholders: Board; Management; Employees. External Stakeholders: Activists; Regulators; Customers; Lenders; Government; Investors; Stakeholders; Community; Suppliers

    Assess ESG impact

    Materiality assessments help to prioritize your ESG strategy and enable effective reporting

    • The concept of materiality as it relates to ESG is the process of gaining different perspectives on ESG issues and risks that may have significant impact (both positive and negative) on or relevance to company performance.
    • The objective of a materiality assessment is to identify material ESG issues most critical to your organization by looking a broad range of social and environmental factors. Its purpose is to narrow strategic focus and enable an organization to assess the impact of financial and non-financial risks aggregately.
    • It helps to make the case for ESG action and strategy, assess financial impact, get ahead of long-term risks, and inform communication strategies.
    • Organizations can leverage assessment tools from Sustainalytics or SASB Standards to help assess ESG risks or use guidance or benchmarking information from industry associations.

    Info-Tech Insight

    Survey key stakeholders to obtain a more holistic viewpoint of expectations and the industry landscape and gain credibility through the process.

    Use a materiality matrix to understand ESG exposure

    This is an image of a materiality matrix used to understand ESG exposure.

    Example: Beverage Company

    Follow a holistic approach

    To deliver on your purpose, sustainability must be integrated throughout the organization

    • An ESG program cannot be implemented in a silo. It must be anchored on its purpose and supported by a strong governance structure that is intertwined with other functional areas.
    • Effective governance is essential to instill trust, support sound decision making, and manage ESG.
    • Governance extends beyond shareholder rights to include many other factors, such as companies' interactions with competitors, suppliers, and governments. More transparency is sought on:
      • Corporate behavior, executive pay, and oversight of controls.
      • Board diversity, compensation, and skill set.
      • Oversight of risk management, particularly risks related to fraud, product, data, and cybersecurity

    "If ESG is the framework of non-financial risks that may have a material impact on the company's stakeholders, corporate governance is the process by which the company's directors and officers manage those risks."
    – Zurich Insurance

    A pyramid is depicted. The top of the pyramid is labeled Continual Improvement, and the following terms are inside this box. Governance: Strategy; Risk Management; Metrics & Targets. At the bottom of the pyramid is a box with right facing arrows, labeled Transparency and Disclosure. This is Informed by the TCFD Framework

    Governance and organization approach

    There is no one-size-fits-all approach

    47% of companies reported that the full board most commonly oversees climate related risks and opportunities while 20% delegate to an existing board governance committee (EY Research, 2021).

    • The organizational approach to ESG will differ across industry segments and corporations depending on material risks and their upstream and downstream value change. However, the accountability for ESG sits squarely at the CEO and board level.
    • Some organizations have taken the approach of hiring a Chief Sustainability Officer to work alongside the CEO on execution of ESG goals and stakeholder communication, while others use other members of the strategic leadership to drive the desired outcomes.
    Governance Layer Responsibilities
    Board
    • Overall accountability lies with the full board. Some responsibilities may be delegated to newly formed dedicated ESG governance committee.
    Oversight
    Executive leadership
    • Accountable for sustainability program success and will work with CEO to set ESG purpose and goals.
    Oversight and strategic direction
    Management
    • Senior management drives execution; sometimes led by a cross-functional committee.
    Execution

    Strategy alignment

    "74% of finance leaders say that investors increasingly use nonfinancial information in their decision-making."

    – "Aligning nonfinancial reporting..." EY, 2020

    • Like any journey, the ESG journey requires knowing where you are starting from and where you are heading to.
    • Once your purpose is crystalized, identify and surface gaps between where you want to go as an organization (your purpose and goals) and what you need to deliver as an organization to meet the expectations of your internal and external stakeholders (your output).
    • Using the results of the materiality assessment, weigh the risk, opportunities, and financial impact to help prioritize and determine vulnerabilities and where you might excel.
    • Finally, evaluate and make changes to areas of your business that need development to be successful (culture, accountability and board structure, ethics committee, etc.)

    Gap analysis example for delivering reporting requirements

    Organizational Goals

    • Regulatory Disclosure
      • Climate
      • DEI
      • Cyber governance
    • Performance Tracking/Annual Reporting
      • Corporate transparency on ESG performance via social, annual circular
    • Evidence-Based Business Reporting
      • Risk
      • Board
      • Suppliers

    Risk-size your ESG goals

    When integrating ESG risks, stick with a proven approach

    • Managing ESG risks is central to making sound organizational decisions regarding sustainability but also to anticipating future risks.
    • Like any new risk type, ESG risk should be interwoven into your current risk management and control framework via a risk-based approach.
    • Yet ESG presents some new risk challenges, and some risk areas may need new control processes or enhancements.
    NET NEW ENHANCEMENT
    Climate disclosure Data quality management
    Assurance specific to ESG reporting Risk sensing and assessment
    Supply chain transparency tied back to ESG Managing interconnections
    Scenario analysis
    Third-party ratings and monitoring

    Info-Tech Insight

    Integrate ESG risks early, embrace uncertainty by staying flexible, and strive for continual improvement.

    A funnel chart is depicted. The inputs to the funnel are: Strategy - Derive ESG risks from strategy, and Enterprise Risk Appetite. Inside the funnel, are the following terms: ESG; Data; Cyber. The output of the funnel is: Evidence based reporting ESG Insights & Performance metrics

    Managing supplier risks

    Suppliers are a critical input into an organization's ESG footprint

    "The typical consumer company's supply chain ... [accounts] for more than 80% of greenhouse-gas emissions and more than 90% of the impact on air, land, water, biodiversity, and geological resources."
    – McKinsey & Company, 2016

    • Although companies are accustomed to managing third parties via procurement processes, voluntary due-diligence, and contractual provisions, COVID-19 surfaced fragility across global supply chains.
    • The mismanagement of upstream and downstream risks of supply chains can harm the reputation, operations, and financial performance of businesses.
    • To build resiliency to and visibility of supply chain risk, organizations need to adapt current risk management programs, procurement practices, and risk assessment tools and techniques.
    • Procurement departments have an enhanced function, effectively acting as gatekeepers by performing due diligence, evaluating performance, and strengthening the supplier relationship through continual feedback and dialogue.
    • Technologies such as blockchain and IoT are starting to play a more dominant role in supply chain transparency.

    Raw materials are upstream and consumers are downstream.

    "Forty-five percent of survey respondents say that they either have no visibility into their upstream supply chain or that they can see only as far as their first-tier suppliers."
    – "Taking the pulse of shifting supply chains," McKinsey & Company, 2022

    Metrics and targets

    Metrics are key to stakeholder transparency, measuring performance against goals, and surfacing organizational blind spots

    • ESG metrics are qualitative or quantitative insights that measure organizations' performance against ESG goals. Along with traditional business metrics, they assist investors with assessing the long-term performance of companies based on non-financial ESG risks and opportunities.
    • Metrics, key performance indicators (KPIs), and key risk indicators (KRIs) are used to measure how ESG factors affect an organization and how an organization may impact any of the underlying issues related to each ESG factor.
    • There are several reporting standards that offer specific ESG performance metrics, such as the Global Reporting Institute (GRI), Sustainability Accounting Standards Board (SASB), and World Economic Forum (WEF).
    • For climate-related disclosures, global regulators are converging on the Task Force for Climate-related Disclosures (TCFD) and the International Sustainability Standards Board (ISSB).

    Example metrics for ESG factors

    Example metrics for environment include greenhouse gas emissions, water footprint, renewable energy share, and % of recycled material. Example social metrics include rates of injury, proportion of spend on local supplies, and percentage of gender or ethnic groups in management roles. Example governance metrics include annual CEO compensation compared to median, number of PII data breaches, and completed number of supplier assessments.

    The impact of ESG on IT

    IT plays a critical role in achieving ESG goals

    • IT groups have a critical role to play in helping organizations develop strategic plans to meet ESG goals, measure performance, monitor risks, and deliver on disclosure requirements.
    • IT's involvement extends from the CIO providing input at a strategic level to leading the charge within IT to instill new goals and adapt the culture toward one focused on sustainability.
    • To set the tone, CIOs should begin by updating their IT governance structure and setting ESG goals for IT.
    • IT leaders will need to think about resource use and efficiency and incorporate this into their IT strategy.

    Info-Tech Insight

    IT leaders need to work collaboratively with risk management to optimize decision making and continually improve ESG performance and disclosure.

    "A great strategy meeting is a meeting of the minds."
    – Max McKeown

    The data challenge

    The ESG data requirement is large and continually expanding in scope

    • To meet ESG objectives, corporations are challenged with collecting non-financial data from across functional business and geographical locations and from their supplier base and supply chains.
    • One of the biggest impediments to ESG implementation is the lack of high-quality data and of mature processes and tools to support data collection.
    • The data challenge is compounded by the availability and usability of data, immature and fragmented standards that hinder comparability, and workflow integration.

    Info-Tech Insight

    Keep your data model flexible and digital where possible to enable data interoperability.

    A flow chart is depicted. the top box is labeled ESG Program. Below that are Boxes labeled Tactical and Strategic. Below the Tactical Box, is a large X showing a lack of connection to the following points: Duplicative; Inefficient/Costly. Below the box labeled Strategic are the following terms: Data-Driven; Reusable; Digital.

    "You can have data without information, but you cannot have information without data."
    – Daniel Keys Moran

    It's more than a data challenge

    Organizations will rely on IT for execution, and IT leaders will need to be ready

    Data Management: Aggregated Reporting; Supplier Management; Cyber Management; Operational Management; Ethical Design(AI, Blockchain); IT Architecture; Resource Efficiency; Processing & Tooling; Supplier Assessment.

    Top impacts on IT departments

    1. ESG requires corporations to keep track of ESG-related risks of third parties. This will mean more robust assessments and monitoring.
    2. Many areas of ESG are new and will require new processes and tools.
    3. The SEC has upped the ante recently, requiring more rigorous accountability and reporting on cyber incidents.
    4. New IT systems and architecture may be needed to support ESG programs.
    5. Current reporting frameworks may need updating as regulators move to digital.
    6. Ethical design will need to be considered when AI is used to support risk/data management and when it is used as part of product solutions.

    Key takeaways

    • It's critical for organizations to look inward and outward to assess the material impact of ESG factors on their organization and key internal and external stakeholders.
    • ESG requires a flexible, holistic approach across the organization. It must become part of the way you work and enable an active response to changing conditions.
    • ESG introduces new risks that should not be viewed in isolation but interwoven into your current risk management and control framework via a risk-based approach.
    • Identify and integrate risks early, embrace uncertainty by staying flexible, and strive for continual improvement.
    • Metrics are key to telling your ESG story. Place the appropriate importance on the information that will be reported.
    • Recognize that the data challenge is complex and evolving and design your data model to be flexible, interoperable, and digital.
    • IT's role is far reaching, and IT will have a critical part in managing third parties, selecting tools, developing supporting IT architecture, and using ethical design.

    Definitions

    TERM DEFINITON
    Corporate Social Responsibility Management concept whereby organizations integrate social and environmental concerns in their operations and interactions with their stakeholders.
    Chief Sustainability Officer Steers sustainability commitments, helps with compliance, and helps ensure internal commitments are met. Responsibilities may extend to acting as a liaison with government and public affairs, fostering an internal culture, acting as a change agent, and leading delivery.
    ESG An acronym that stands for environment, social, and governance. These are the three components of a sustainability program.
    ESG Standard Contains detailed disclosure criteria including performance measures or metrics. Standards provide clear, consistent criteria and specifications for reporting. Typically created through consultation process.
    ESG Framework A broad contextual model for information that provides guidance and shapes the understanding of a certain topic. It sets direction but does not typically delve into the methodology. Frameworks are often used in conjunction with standards.
    ESG Factors The factors or issues that fall under the three ESG components. Measures the sustainability performance of an organization.
    ESG Rating An aggregated score based on the magnitude of an organization's unmanaged ESG risk. Ratings are provided by third-party rating agencies and are increasingly being used for financing, transparency to investors, etc.
    ESG Questionnaire ESG surveys or questionnaires are administered by third parties and used to assess an organization's sustainability performance. Participation is voluntary.
    Key Risk Indicator (KRI) A measure to indicate the potential presence, level, or trend of a risk.
    Key Performance Indicator (KPI) A measure of deviation from expected outcomes to help a firm see how it is performing.
    Materiality Material topics are topics that have a direct or indirect impact on an organization's ability to create, preserve, or erode economic, environment and social impact for itself and its stakeholder and society as a whole
    Materiality Assessment A materiality assessment is a tool to identify and prioritize the ESG issues most critical to the organization.
    Risk Sensing The range of activities carried out to identify and understand evolving sources of risk that could have a significant impact on the organization (e.g. social listening).
    Sustainability The ability of an organization and broader society to endure and survive over the long term by managing adverse impacts well and promoting positive opportunities.
    Sustainalytics Now part of Morningstar. Sustainalytics provides ESG research, ratings, and data to institutional investors and companies.
    UN Guiding Principles on Business and Human Rights (UNGPs) UN Guiding Principles on Business and Human Rights (UNGPs) provide an essential methodological foundation for how impacts across all dimensions should be assessed.

    Reporting & standard frameworks

    STANDARD DEFINITION AND FOCUS
    CDP CDP has created standards and metrics for comparing sustainability impact. Focuses on environmental data (e.g. carbon, water, and forests) and on data disclosure and benchmarking.
    (Formally Carbon Disclosure Project) Audience: All stakeholders
    Dow Jones Sustainability Indices (DJSI) Heavy on corporate governance and company performance. Equal balance of economic, environmental, and social.
    Audience: All stakeholders
    Global Reporting Initiative (GRI) International standards organization that has a set of standards to help organizations understand and communicate their impacts on climate change and social responsibility. The standard has a strong emphasis on transparency and materiality, especially on social issues.
    Audience: All stakeholders
    International Sustainability Standards Board (ISSB) Standard-setting board that sits within the International Financial Reporting Standards (IFRS) Foundation. The IFRS Foundation is a not-for-profit, public-interest organization established to develop high-quality, understandable, enforceable, and globally accepted accounting and sustainability disclosure standards.
    Audience: Investor-focused
    United Nations Sustainable Development Goals (UNSDG) Global partnership across sectors and industries to achieve sustainable development for all (17 Global Goals)
    Audience: All stakeholders
    Sustainability Accounting Standards Board (SASB) Industry-specific standards to help corporations select topics that may impact their financial performance. Focus on material impacts on financial condition or operating performance.
    Audience: Investor-focused
    Task Force Of Climate-related Disclosures (TCFD; created by the Financial Stability Board) Standards framework focused on the impact of climate risk on financial and operating performance. More broadly the disclosures inform investors of positive and negative measures taken to build climate resilience and make transparent the exposure to climate-related risk.
    Audience: Investors, financial stakeholders

    Bibliography

    Anne-Titia Bove and Steven Swartz, McKinsey, "Starting at the source: Sustainability in supply chains", 11 November 2016

    Accenture, "The Greater Wealth Transfer – Capitalizing on the intergenerational shift in wealth", 2012

    Beth Kaplan, Deloitte, "Preparing for the ESG Landscape, Readiness and reporting ESG strategies through controllership playbook", 15 February 2022

    Bjorn Nilsson et al, McKinsey & Company, "Financial institutions and nonfinancial risk: How corporates build resilience," 28 February 2022

    Bolden, Kyle, Ernst and Young, "Aligning nonfinancial reporting with your ESG strategy to communicate long-term value", 18 Dec. 2020

    Canadian Securities Administrators, "Canadian securities regulators seek comment on climate-related disclosure requirements", 18 October 2021

    Carol A. Adams et al., Global Risk Institute, "The double-materiality concept, Application and issues", May 2021

    Dunstan Allison-Hope et al, BSR, "Impact-Based Materiality, Why Companies Should-Focus Their Assessments on Impacts Rather than Perception", 3 February 2022

    EcoVadis, "The World's Most Trusted Business Sustainability Ratings",

    Ernst and Young, "Four opportunities for enhancing ESG oversight", 29 June 2021

    Federal Ministry of Labour and Social Affairs, The Act on Corporate Due Diligence Obligations in Supply Chains (Gesetz über die unternehmerischen Sorgfaltspflichten in Lieferketten)", Published into Federal Law Gazette, 22, July 2021

    "What Every Company Needs to Know", Sustainalytics

    Global Risk Institute, The GRI Perspective, "The materiality madness: why definitions matter", 22 February 2022

    John P Angkaw "Applying ERM to ESG Risk Management", 1 August 2022

    Hillary Flynn et al., Wellington Management, "A guide to ESG materiality assessments", June 2022

    Katie Kummer and Kyle Lawless, Ernst and Young, "Five priorities to build trust in ESG", 14 July 2022

    Knut Alicke et al., McKinsey & Company, "Taking the pulse of shifting supply chains", 26 August 2022

    Kosmas Papadopoulos and Rodolfo Arauj. The Harvard School Forum on Corporate Governance, "The Seven Sins of ESG Management", 23 September 2020

    KPMG, Sustainable Insight, "The essentials of materiality assessment", 2014

    Lorraine Waters, The Stack, "ESG is not an environmental issue, it's a data one", 20 May 2021

    Marcel Meyer, Deloitte, "What is TCFD and why does it matter? Understanding the various layers and implications of the recommendations",

    Michael W Peregnne et al., "The Harvard Law School Forum on Corporate Governance, The Important Legacy of the Sarbanes Oxley Act," 30 August 2022

    Michael Posner, Forbes, "Business and Human Rights: Looking Ahead To The Challenges Of 2022", 15 December 2021

    Myles Corson and Tony Kilmas, Ernst and Young, "How the CFO can balance competing demands and drive future growth", 3 November 2020

    Novisto, "Navigating Climate Data Disclosure", 2022

    Novisto, "XBRL is coming to corporate sustainability reporting", 17 April 2022

    "Official Journal of the European Union, Regulation (EU) 2019/2088 of the European Parliament and of the Council of 27 November 2019 on sustainability-related disclosures in the financial services sector", 9 December 2019

    Osler, "ESG and the future of sustainability", Podcast, 01 June 2022

    Osler, "The Rapidly Evolving World of ESG Disclosure: ISSB draft standards for sustainability and climate related disclosures", 19 May 2022

    Sarwar Choudhury and Zach Johnston, Ernst and Young "Preparing for Sox-Like ESG Regulation", 7 June 2022

    Securities and Exchange Commission, "The Enhancement and Standardization of Climate-related Disclosures for Investors", 12 May 2022

    "Securities and Exchange Commission, SEC Proposes Rules on Cybersecurity, Risk Management, Strategy, Governance, and Incident Disclosure by Public Companies, 9 May 2022

    Sean Brown and Robin Nuttall, McKinsey & Company, "The role of ESG and purpose", 4 January 2022

    Statement by Chair Gary Gensler, "Statement on ESG Disclosure Proposal", 25 May 2022

    Svetlana Zenkin and Peter Hennig, Forbes, "Managing Supply Chain Risk, Reap ESG Rewards", 22 June 2022

    Task Force on Climate Related Financial Disclosures, "Final Report, Recommendations of the Task Force on Climate-related Financial Disclosures", June 2017

    World Economic Forum, "Why sustainable governance and corporate integrity are crucial for ESG", 29 July 2022

    World Economic Forum (in collaboration with PwC) "How to Set Up Effective Climate Governance on Corporate Boards, Guiding Principles and questions", January 2019

    World Economic Forum, "Defining the "G" in ESG Governance Factors at the Heart of Sustainable Business", June 2022

    World Economic Forum, "The Risk and Role of the Chief Integrity Officer: Leadership Imperatives in and ESG-Driven World", December 2021

    World Economic Forum, "How to Set Up Effective Climate Governance on Corporate Boards Guiding principles and questions", January 2019

    Zurich Insurance, "ESG and the new mandate for corporate governance", 2022

    Optimize the Service Desk With a Shift-Left Strategy

    • Buy Link or Shortcode: {j2store}478|cart{/j2store}
    • member rating overall impact: 9.4/10 Overall Impact
    • member rating average dollars saved: $21,171 Average $ Saved
    • member rating average days saved: 11 Average Days Saved
    • Parent Category Name: Service Desk
    • Parent Category Link: /service-desk
    • Tier 2 and 3 specialists lose time and resources working on tickets instead of more complex projects.
    • The service desk finds themselves resolving the same incidents over and over, wasting manual work on tasks that could be automated.
    • Employees expect modern, consumer-like experiences when they need help; they want to access information and resources from wherever they are and have the tools to solve their problems themselves without waiting for help.

    Our Advice

    Critical Insight

    • It can be difficult to overcome the mindset that difficult functions need to be escalated. Shift left involves a cultural change to the way the service desk works, and overcoming objections and getting buy-in up front is critical.
    • Many organizations have built a great knowledgebase but fail to see the value of it over time as it becomes overburdened with overlapping and out-of-date information. Knowledge capture, updating, and review must be embedded into your processes if you want to keep the knowledgebase useful.
    • Similarly, the self-service portal is often deployed out of the box with little input from end users and fails to deliver its intended benefits. The portal needs to be designed from the end user’s point of view with the goal of self-resolution if it will serve its purpose of deflecting tickets.

    Impact and Result

    • Embrace a shift-left strategy by moving repeatable service desk tasks and requests into lower-cost delivery channels such as self-help tools and automation.
    • Shift work from Tier 2 and 3 support to Tier 1 through good knowledge management practices that empower the first level of support with documented solutions to recurring issues and free up more specialized resources for project work and higher value tasks.
    • Shift knowledge from the service desk to the end user by enabling them to find their own solutions. A well-designed and implemented self-service portal will result in fewer logged tickets to the service desk and empowered, satisfied end users.
    • Shift away manual repetitive work through the use of AI and automation.
    • Successfully shifting this work left can reduce time to resolve, decrease support costs, and increase end-user satisfaction.

    Optimize the Service Desk With a Shift-Left Strategy Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to understand why a shift-left strategy can help to optimize your service desk, review Info-Tech's methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Prepare to shift left

    Assess whether you’re ready to optimize the service desk with a shift-left strategy, get buy-in for the initiative, and define metrics to measure success.

    • Optimize the Service Desk With a Shift-Left Strategy – Phase 1: Prepare to Shift Left
    • Shift-Left Prerequisites Assessment
    • Shift-Left Strategy
    • Shift-Left Stakeholder Buy-In Presentation

    2. Design shift-left model

    Build strategy and identify specific opportunities to shift service support left to Level 1 through knowledge sharing and other methods, to the end-user through self-service, and to automation and AI.

    • Optimize the Service Desk With a Shift-Left Strategy – Phase 2: Design Shift Left Model
    • Shift-Left Action Plan
    • Knowledge Management Workflows (Visio)
    • Knowledge Management Workflows (PDF)
    • Self-Service Portal Checklist
    • Self-Service Resolution Workflow (Visio)
    • Self-Service Resolution Workflow (PDF)

    3. Implement and communicate

    Identify, track, and implement specific shift-left opportunities and document a communications plan to increase adoption.

    • Optimize the Service Desk With a Shift-Left Strategy – Phase 3: Implement & Communicate
    • Incident Management Workflow (Visio)
    • Incident Management Workflow (PDF)
    [infographic]

    Workshop: Optimize the Service Desk With a Shift-Left Strategy

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Prepare to Shift Left

    The Purpose

    Define how shift left would apply in your organization, get buy-in for the initiative, and define metrics to measure success.

    Key Benefits Achieved

    Defined scope and objectives for the shift-left initiative

    Buy-in for the program

    Metrics to keep the project on track and evaluate success

    Activities

    1.1 Review current service desk structure

    1.2 Discuss challenges

    1.3 Review shift-left model and discuss how it would apply in your organization

    1.4 Complete the Shift-Left Prerequisites Assessment

    1.5 Complete a RACI chart for the project

    1.6 Define and document objectives

    1.7 Review the stakeholder buy-in presentation

    1.8 Document critical success factors

    1.9 Define KPIs and metrics

    Outputs

    Shift-left scope

    Completed shift-left prerequisites assessment

    RACI chart

    Defined objectives

    Stakeholder buy-in presentation

    Critical success factors

    Metrics to measure success

    2 Plan to Shift to Level 1

    The Purpose

    Build strategy and identify specific opportunities to shift service support left to Level 1 through knowledge sharing and other methods.

    Key Benefits Achieved

    Identified initiatives to shift work to Level 1

    Documented knowledge management process workflows and strategy

    Activities

    2.1 Identify barriers to Level 1 resolution

    2.2 Discuss knowledgebase challenges and areas for improvement

    2.3 Optimize KB input process

    2.4 Optimize KB usage process

    2.5 Optimize KB review process

    2.6 Discuss and document KCS strategy and roles

    2.7 Document knowledge success metrics

    2.8 Brainstorm additional methods of increasing FLR

    Outputs

    KB input workflow

    KB usage workflow

    KB review workflow

    KCS strategy and roles

    Knowledge management metrics

    Identified opportunities to shift to Level 1

    3 Plan to Shift to End User and Automation

    The Purpose

    Build strategy and identify specific opportunities to shift service support left to the end user through self-service and to automation and AI.

    Key Benefits Achieved

    Identified initiatives to shift work to self-service and automation

    Evaluation of self-service portal and identified opportunities for improvement

    Activities

    3.1 Review existing self-service portal and discuss vision

    3.2 Identify opportunities to improve portal accessibility, UI, and features

    3.3 Evaluate the user-facing knowledgebase

    3.4 Optimize the ticket intake form

    3.5 Document plan to improve, communicate, and evaluate portal

    3.6 Map the user experience with a workflow

    3.7 Document your AI strategy

    3.8 Identify candidates for automation

    Outputs

    Identified opportunities to improve portal

    Improvements to knowledgebase

    Improved ticket intake form

    Strategy to communicate and measure success of portal

    Self-service resolution workflow

    Strategy to apply AI and automation

    Identified opportunities to shift tasks to automation

    4 Build Implementation and Communication Plan

    The Purpose

    Build an action plan to implement shift left, including a communications strategy.

    Key Benefits Achieved

    Action plan to track and implement shift-left opportunities

    Communications plan to increase adoption

    Activities

    4.1 Examine process workflows for shift-left opportunities

    4.2 Document shift-left-specific responsibilities for each role

    4.3 Identify and track shift-left opportunities in the action plan

    4.4 Brainstorm objections and responses

    4.5 Document communications plan

    Outputs

    Incident management workflow with shift-left opportunities

    Shift left responsibilities for key roles

    Shift-left action plan

    Objection handling responses

    Communications plan

    IBM i Migration Considerations

    • Buy Link or Shortcode: {j2store}109|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Strategy and Organizational Design
    • Parent Category Link: /strategy-and-organizational-design

    IBM i remains a vital platform and now many CIOs, CTOs, and IT leaders are faced with the same IBM i challenges regardless of industry focus: how do you evaluate the future viability of this platform, assess the future fit and purpose, develop strategies, and determine the future of this platform for your organization?

    Our Advice

    Critical Insight

    For organizations that are struggling with the iSeries/IBM i platform, resourcing challenges are typically the culprit. An aging population of RPG programmers and system administrators means organizations need to be more pro-active in maintaining in-house expertise. Migrating off the iSeries/IBM i platform is a difficult option for most organizations due to complexity, switching costs in the short term, and a higher long-term TCO.

    Impact and Result

    The most common tactic is for the organization to better understand their IBM i options and adopt some level of outsourcing for the non-commodity platform retaining the application support/development in-house. To make the evident, obvious; the options here for the non-commodity are not as broad as with commodity server platforms. Options include co-location, onsite outsourcing, managed and public cloud services.

    IBM i Migration Considerations Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. IBM i Migration Considerations – A brief deck that outlines key migration options for the IBM i platforms.

    This project will help you evaluate the future viability of this platform; assess the fit, purpose, and price; develop strategies for overcoming potential challenges; and determine the future of this platform for your organization.

    • IBM i Migration Considerations Storyboard

    2. Infrastructure Outsourcing IBM i Scoring Tool – A tool to collect vendor responses and score each vendor.

    Use this scoring sheet to help you define and evaluate IBM i vendor responses.

    • Infrastructure Outsourcing IBM i Scoring Tool
    [infographic]

    Further reading

    IBM i Migration Considerations

    Don’t be overwhelmed by IBM i migration options.

    Executive Summary

    Your Challenge

    IBM i remains a vital platform and now many CIO, CTO, and IT leaders are faced with the same IBM i challenges regardless of industry focus; how do you evaluate the future viability of this platform, assess the future fit and purpose, develop strategies, and determine the future of this platform for your organization?

    Common Obstacles

    For organizations that are struggling with the iSeries/IBM i platform, resourcing challenges are typically the culprit. An aging population of RPG programmers and system administrators means organizations need to be more proactive in maintaining in-house expertise. Migrating off the iSeries/IBM i platform is a difficult option for most organizations due to complexity, switching costs in the short term, and a higher long-term TCO.

    Info-Tech Approach

    The most common tactic is for the organization to better understand its IBM i options and adopt some level of outsourcing for the non-commodity platform, retaining the application support/development in-house. To make the evident, obvious: the options here for the non-commodity are not as broad as with commodity server platforms. Options include co-location, onsite outsourcing, managed hosting, and public cloud services.

    Info-Tech Insight

    “For over twenty years, IBM was ‘king,’ dominating the large computer market. By the 1980s, the world had woken up to the fact that the IBM mainframe was expensive and difficult, taking a long time and a lot of work to get anything done. Eager for a new solution, tech professionals turned to the brave new concept of distributed systems for a more efficient alternative. On June 21, 1988, IBM announced the launch of the AS/400, their answer to distributed computing.” (Dale Perkins)

    Review

    We help IT leaders make the most of their IBM i environment.

    Problem Statement:

    The IBM i remains a vital platform for many businesses and continues to deliver exceptional reliability and performance and play a key role in the enterprise. With the limited resources at hand, CIOs and the like must continually review and understand their migration path with the same regard as any other distributed system roadmap.

    This research is designed for:

    • IT strategic direction decision makers
    • IT managers responsible for an existing iSeries or IBM i platform
    • Organizations evaluating platforms for mission-critical applications

    This research will help you:

    1. Evaluate the future viability of this platform.
    2. Assess the fit, purpose, and price.
    3. Develop strategies for overcoming potential challenges.
    4. Determine the future of this platform for your organization.

    The “fit for purpose” plot

    Thought Model

    We will investigate the aspect of different IBM i scenarios as they impact business, what that means, and how that can guide the questions that you are asking as you move to an aligned IBM i IT strategy. Our model considers:

    • Importance to Business Outcomes
      • Important to strategic objectives
      • Provides competitive advantage
      • Non-commodity IT service or process
      • Specialized in-house knowledge required
    • Vendor’s Performance Advantage
      • Talent or access to skills
      • Economies of scale or lower cost at scale
      • Access to technology

    Info-Tech Insights

    With multiple control points to be addressed, care must be taken in simplifying your options while addressing all concerns to ease operational load.

    Map different 'IBM i' scenarios with axes 'Importance to Business Outcomes - Low to High' and 'Vendor’s Performance Advantage - Low to High'. Quadrant labels are '[LI/LA] Potentially Outsource: Service management, Help desk, desk-side support, Asset management', '[LI/HA] Outsource: Application & Infra Support, Web Hosting, SAP Support, Email Services, Infrastructure', '[HI/LA] Insource (For Now): Application development tech support', and '[HI/HA] Potentially Outsource: Onshore or offshore application maintenance'.

    IBM i environments are challenging

    “The IBM i Reality” – Darin Stahl

    Most members relying on business applications/workloads running on non-commodity platforms (zSeries, IBM i, Solaris, AIX, etc.) are first motivated to get out from under the perceived higher costs for the hardware platform.

    An additional challenge for non-commodity platforms is that from an IT Operations Management perspective they become an island with a diminishing number of integrated operations skills and solutions such as backup/restore and monitoring tools.

    The most common tactic is for the organization to adopt some level of outsourcing for the non-commodity platform, retaining the application support and development in-house.

    Key challenges with current IBM i environments:
    1. DR Requirements
      Understand what the business needs are and where users and resources are located.
    2. Market Lack of Expertise
      Skilled team members are hard to find.
    3. Cost Management
      There is a perceived cost disadvantage to managing on-prem solutions.
    4. Aging Support Teams
      Current support teams are aging with little backfill in skill and experience.

    Understand your options

    Co-Location

    A customer transitions their hardware environment to a provider’s data center. The provider can then manage the hardware and “system.”

    Onsite Outsourcing

    A provider will support the hardware/system environment at the client’s site.

    Managed Hosting

    A customer transitions their legacy application environment to an off-prem hosted, multi-tenanted environment.

    Public Cloud

    A customer can “re-platform” the non-commodity workload into public cloud offerings or in a few offerings “re-host.”

    Co-Location

    Provider manages the data center hardware environment.

    Abstract

    Here a provider manages the system data center environment and hardware; however, the client’s in-house IBM i team manages the IBM i hardware environment and the system applications. The client manages all of the licenses associated with the platform as well as the hardware asset management considerations. This is typically part of a larger services or application transformation. This effectively outsources the data center management while maintaining all IBM i technical operations in-house.

    Advantages

    • On-demand bandwidth
    • Cost effective
    • Secure and compliant environment
    • On-demand remote “hands and feet” services
    • Improved IT DR services
    • Data center compliance

    Considerations

    • Application transformation
    • CapEx cost
    • Fluctuating network bandwidth costs
    • Secure connectivity
    • Disaster recovery and availability of vendor
    • Company IT DR and BC planning
    • Remote system maintenance (HW)

    Info-Tech Insights

    This model is extremely attractive for organizations looking to reduce their data center management footprint. Idea for the SMB.

    Onsite Sourcing

    A provider will support the hardware/system environment at the client’s site.

    Abstract

    Here a provider will support and manage the hardware/system environment at the client’s site. The provider may acquire the customer’s hardware and provide software licenses. This could also include hiring or “rebadging” staff supporting the platform. This type of arrangement is typically part of a larger services or application transformation. While low risk, it is not as cost-effective as other deployment models.

    Advantages

    • Managed environment within company premises
    • Cost effective (OpEx expense)
    • Economies of scale
    • On-demand “as-a-service” model
    • Improved IT DR staffing services
    • 24x7 monitoring and support

    Considerations

    • Outsourced IT talent
    • Terms and contract conditions
    • IT staff attrition
    • Increased liability
    • Modified technical support and engagement
    • Secure connectivity and communication
    • Internal problem and change management

    Info-Tech Insights

    Depending on the application lifecycle and viability, in-house skill and technical depth is a key consideration when developing your IBM i strategy.

    Managed Hosting

    Transition legacy application environment to an off-prem hosted multi-tenanted environment.

    Abstract

    This type of arrangement is typically part of an application migration or transformation. In this model, a client can “re-platform” the application into an off-premises-hosted provider platform. This would yield many of the cloud benefits however in a different scaling capacity as experienced with commodity workloads (e.g. Windows, Linux) and the associated application.

    Advantages

    • Turns CapEx into OpEx
    • Reduces in-house need for diminishing or scarce human resources
    • Allows the enterprise to focus on the value of the IBM i platform through the reduction of system administrative toil
    • Improved IT DR services
    • Data center compliance

    Considerations

    • Application transformation
    • Network bandwidth
    • Contract terms and conditions
    • Modified technical support and engagement
    • Secure connectivity and communication
    • Technical security and compliance
    • Limited providers; reduced options

    Info-Tech Insights

    There is a difference between a “re-host” and “re-platform” migration strategy. Determine which solution aligns to the application requirements.

    Public Cloud

    Leverage “public cloud” alternatives with AWS, Google, or Microsoft AZURE.

    Abstract

    This type of arrangement is typically part of a larger migration or application transformation. While low risk, it is not as cost-effective as other deployment models. In this model, client can “re-platform” the non-commodity workload into public cloud offerings or in a few offerings “re-host.” This would yield many of the cloud benefits however in a different scaling capacity as experienced with commodity workloads (e.g. Windows, Linux).

    Advantages

    • Remote workforce accessibility
    • OpEx expense model
    • Improved IT DR services
    • Reduced infrastructure and system administration
    • Vendor management
    • 24x7 monitoring and support

    Considerations

    • Contract terms and conditions
    • Modified technical support and engagement
    • Secure connectivity and communication
    • Technical security and compliance
    • Limited providers; reduced options
    • Vendor/cloud lock-in
    • Application migration/”re-platform”
    • Application and system performance

    Info-Tech Insights

    This model is extremely attractive for organizations that consume primarily cloud services and have a large remote workforce.

    Understand your vendors

    • To best understand your options, you need to understand what IBM i services are provided by the industry vendors.
    • Within the following slides, you will find a defined activity with a working template that will create “vendor profiles” for each vendor.
    • As a working example, you can review the following partners:
    • Connectria (United States)
    • Rowton IT Solutions Ltd (United Kingdom)
    • Mid-Range (Canada)

    Info-Tech Insights

    Creating vendor profiles will help quickly filter the solution providers that directly meet your IBM i needs.

    Vendor Profile #1

    Rowton IT

    Summary of Vendor

    “Rowton IT thrive on creating robust and simple solutions to today's complex IT problems. We have a highly skilled and motivated workforce that will guarantee the right solution.

    Working with select business partners, we can offer competitive and cost effective packages tailored to suit your budget and/or business requirements.

    Our knowledge and experience cover vast areas of IT including technical design, provision and installation of hardware (Wintel and IBM Midrange), technical engineering services, support services, IT project management, application testing, documentation and training.”

    IBM i Services

    • ✔ IBM Power Hardware Sales
    • ✔ Co-Managed Services
    • ✔ DR/High Available Config
    • ✔ Full Managed Services
    • ✖ Co-Location Services
    • ✔ Public Cloud Services (AWS)

    URL
    rowtonit.com

    Regional Coverage:
    United Kingdom

    Logo for RowtonIT.com.

    Vendor Profile #2

    Connectria

    Summary of Vendor

    “Every journey starts with a single step and for Connectria, that step happened to be with the world’s largest bank, Deutsche Bank. Followed quickly by our second client, IBM. Since then, we have added over 1,000 clients worldwide. For 25 years, each customer, large or small, has relied on Connectria to deliver on promises made to make it easy to do business with us through flexible terms, scalable solutions, and straightforward pricing. Join us on our journey.”

    IBM i Services

    • ✔ IBM Power Hardware Sales
    • ✔ Co-Managed Services
    • ✔ DR/High Available Config
    • ✔ Full Managed Services
    • ✔ Co-Location Services
    • ✔ Public Cloud Services (AWS)

    URL
    connectria.com

    Regional Coverage:
    United States

    Logo for Connectria.

    Vendor Profile #3

    Mid-Range

    Summary of Vendor

    “Founded in 1988 and profitable throughout all of those 31 years, we have a solid track record of success. At Mid-Range, we use our expertise to assess your unique needs, in order to proactively develop the most effective IT solution for your requirements. Our full-service approach to technology and our diverse and in-depth industry expertise keep our clients coming back year after year.

    Serving clients across North America in a variety of industries, from small and emerging organizations to large, established enterprises – we’ve seen it all. Whether you need hardware or software solutions, disaster recovery and high availability, managed services or hosting or full ERP services with our JD Edwards offerings – we have the methods and expertise to help.”

    IBM i Services

    • ✔ IBM Power Hardware Sales
    • ✔ Co-Managed Services
    • ✔ DR/High Available Config
    • ✔ Full Managed Services
    • ✔ Co-Location Services
    • ✔ Public Cloud Services (AWS)

    URL
    midrange.ca

    Regional Coverage:
    Canada

    Logo for Mid-Range.

    Activity

    Understand your vendor options

    Activities:
    1. Create your vendor profiles
    2. Score vendor responses
    3. Develop and manage your vendor agenda

    This activity involves the following participants:

    • IT strategic direction decision makers
    • IT managers responsible for an existing iSeries or IBM i platform

    Outcomes of this step:

    • Vendor Profile Template
    • Completed IT Infrastructure Outsourcing Scoring Tool

    Info-Tech Insights

    This check-point process creates transparency around agreement costs with the business and gives the business an opportunity to re-evaluate its requirements for a potentially leaner agreement.

    1. Create your vendor profiles

    Define what you are looking for:

    • Create a vendor profile for every vendor of interest.
    • Leverage our starting list and template to track and record the advantages of each vendor.

    Mindshift

    First National Technology Solutions

    Key Information Systems

    MainLine

    Direct Systems Support

    T-Systems

    Horizon Computer Solutions Inc.

    Vendor Profile Template

    [Vendor Name]

    Summary of Vendor

    [Vendor Summary]
    *Detail the Vendor Services as a Summary*

    IBM i Services

    • ✔ IBM Power Hardware Sales
    • ✔ Co-Managed Services
    • ✔ DR/High Available Config
    • ✔ Full Managed Services
    • ✔ Co-Location Services
    • ✔ Public Cloud Services (AWS)
    *Itemize the Vendor Services specific to your requirements*

    URL
    https://www.url.com/
    *Insert the Vendor URL*

    Regional Coverage:
    [Country\Region]
    *Insert the Vendor Coverage & Locations*

    *Insert the Vendor Logo*

    2. Score your vendor responses

    Use the IT Infrastructure Outsourcing Scoring Tool to manage vendor responses.
    Use Info-Tech’s IT Infrastructure Outsourcing Scoring Tool to systematically score your vendor responses.

    The overall quality of the IBM i questions can help you understand what it might be like to work with the vendor.

    Consider the following questions:

    • Is the vendor clear about what it’s able to offer? Is its response transparent?
    • How much effort did the vendor put into answering the questions?
    • Does the vendor seem like someone you would want to work with?

    Once you have the vendor responses, you will select two or three vendors to continue assessing in more depth leading to an eventual final selection.

    Screenshot of the IT Infrastructure Outsourcing Scoring Tool's Scoring Sheet. There are three tables: 'Scoring Scale', 'Results', and one with 'RFP Questions'. Note on Results table says 'Top Scoring Vendors', and note on questions table says 'List your IBM i questions (requirements)'.

    Info-Tech Insights

    Watch out for misleading scores that result from poorly designed criteria weightings.

    3. Develop your vendor agenda

    Vendor Conference Call

    Develop an agenda for the conference call. Here is a sample agenda:
    • Review the vendor questions.
    • Go over answers to written vendor questions previously submitted.
    • Address new vendor questions.

    Commonly Debated Question:
    Should vendors be asked to remain anonymous on the call or should each vendor mention their organization when they join the call?

    Many organizations worry that if vendors can identify each other, they will price fix. However, price fixing is extremely rare due to its consequences and most vendors likely have a good idea which other vendors are participating in the bid. Another thought is that revealing vendors could either result in a higher level of competition or cause some vendors to give up:

    • A vendor that hears its rival is also bidding may increase the competitiveness of its bid and response.
    • A vendor that feels it doesn’t have a chance may put less effort into the process.
    • A vendor that feels it doesn’t have real competition may submit a less competitive or detailed response than it otherwise would have.

    Vendor Workshop

    A vendor workshop day is an interactive way to provide context to your vendors and to better understand the vendors’ offerings. The virtual or in-person interaction also offers a great way to understand what it’s like to work with each vendor and decide whether you could build a partnership with them in the long run.

    The main focus of the workshop is the vendors’ service solution presentation. Here is a sample agenda for a two-day workshop:

    Day 1
    • Meet and greet
    • Welcome presentation with objectives, acquisition strategy, and company overview
    • Overview of the current IT environment, technologies, and company expectations
    • Question and answer session
    • Site walk
    Day 2
    • Review Day 1 activities
    • Vendor presentations and solution framing
    Use the IT Infrastructure Outsourcing Scoring Tool to manage vendor responses.

    Related Info-Tech Research

    Effectively Acquire Infrastructure Services
    Acquiring a service is like buying an experience. Don’t confuse the simplicity of buying hardware with buying an experience.

    Outsource IT Infrastructure to Improve System Availability, Reliability, and Recovery
    There are very few IT infrastructure components you should be housing internally – outsource everything else.

    Build Your Infrastructure Roadmap
    Move beyond alignment: Put yourself in the driver’s seat for true business value.

    Define Your Cloud Vision
    Make the most of cloud for your organization.

    Document Your Cloud Strategy
    Drive consensus by outlining how your organization will use the cloud.

    Create a Right-Sized Disaster Recovery Plan
    Close the gap between your DR capabilities and service continuity requirements.

    Create a Better RFP Process
    Improve your RFPs to gain leverage and get better results.

    Research Authors

    Photo of Darin Stahl, Principal Research Advisor, Info-Tech Research Group.Darin Stahl, Principal Research Advisor, Info-Tech Research Group

    Principal Research Advisor within the Infrastructure Practice and leveraging 38+ years of experience, his areas of focus include: IT Operations Management, Service Desk, Infrastructure Outsourcing, Managed Services, Cloud Infrastructure, DRP/BCP, Printer Management, Managed Print Services, Application Performance Monitoring (APM), Managed FTP, and non-commodity servers (zSeries, mainframe, IBM i, AIX, Power PC).

    Photo of Troy Cheeseman, Practice Lead, Info-Tech Research Group.Troy Cheeseman, Practice Lead, Info-Tech Research Group

    Troy has over 24 years of experience and has championed large, enterprise-wide technology transformation programs, remote/home office collaboration and remote work strategies, BCP, IT DRP, IT Operations and expense management programs, international right placement initiatives, and large technology transformation initiatives (M&A). Additionally, he has deep experience working with IT solution providers and technology (cloud) start-ups.

    Research Contributors

    Photo of Dan Duffy, President & Owner, Mid-Range.Dan Duffy, President & Owner, Mid-Range

    Dan Duffy is the President and Founder of Mid-Range Computer Group Inc., an IBM Platinum Business Partner. Dan and his team have been providing the Canadian and American IBM Power market with IBM infrastructure solutions including private cloud, hosting and disaster recovery, high availability and data center services since 1988. He has served on numerous boards and associations including the Toronto Users Group for Mid-Range Systems (TUG), the IBM Business Partners of the Americas Advisory Council, the Cornell Club of Toronto, and the Notre Dame Club of Toronto. Dan holds a Bachelor of Science from Cornell University.

    Photo of George Goodall, Executive Advisor, Info-Tech Research Group.George Goodall, Executive Advisor, Info-Tech Research Group

    George Goodall is an Executive Advisor in the Research Executive Services practice at Info-Tech Research Group. George has over 20 years of experience in IT consulting, enterprise software sales, project management, and workshop delivery. His primary focus is the unique challenges and opportunities in organizations with small and constrained IT operations. In his long tenure at Info-Tech, George has covered diverse topics including voice communications, storage, and strategy and governance.

    Bibliography

    “Companies using IBM i (formerly known as i5/OS).” Enlyft, 21 July 2021. Web.

    Connor, Clare. “IBM i and Meeting the Challenges of Modernization.” Ensono, 22 Mar. 2022. Web.

    Huntington, Tom. “60+ IBM i User Groups and Communities to Join?” HelpSystems, 16 Dec. 2021. Web.

    Perkins, Dale. “The Road to Power Cloud: June 21st 1988 to now. The Journey Continues.” Mid-Range, 1 Nov. 2021. Web.

    Prickett Morgan, Timothy. “How IBM STACKS UP POWER8 AGAINST XEON SERVERS.” The Next Platform, 13 Oct. 2015. Web.

    “Why is AS/400 still used? Four reasons to stick with a classic.” NTT, 21 July 2016. Web.

    Appendix

    Public Cloud Provider Notes

    Appendix –
    Cloud
    Providers


    “IBM Power (IBM i and AIX) workloads are also available in the so-called ‘cloud.’” (Darin Stahl)

    AWS

    Appendix –
    Cloud
    Providers


    “IBM Power (IBM i and AIX) workloads are also available in the so-called ‘cloud.’” (Darin Stahl)

    Google

    • Google Cloud console supports IBM Power Systems.
    • This offering provides cloud instances running on IBM Power Systems servers with PowerVM.
    • The service uses a per-day prorated monthly subscription model for cloud instance plans with different capacities of compute, memory, storage, and network. Standard plans are listed below and custom plans are possible.
    • There is no IBM i offering yet that we are aware of.
    • For AIX on Power, this would appear to be a better option than AWS (Converge Enterprise Cloud with IBM Power for Google Cloud).

    Appendix –
    Cloud
    Providers


    “IBM Power (IBM i and AIX) workloads are also available in the so-called ‘cloud.’” (Darin Stahl)

    Azure

    • Azure has partners using the Azure Dedicated Host offerings to deliver “native support for IBM POWER Systems to Azure data centres” (PowerWire).
    • Microsoft has installed Power servers in an couple Azure data centers and Skytap manages the IBM i, AIX, and Linux environments for clients.
    • As far as I am aware there is no ability to install IBM i or AIX within an Azure Dedicated Host via the retail interfaces – these must be worked through a partner like Skytap.
    • The cloud route for IBM i or AIX might be the easiest working with Skytap and Azure. This would appear to be a better option than AWS in my opinion.

    Appendix –
    Cloud
    Providers


    “IBM Power (IBM i and AIX) workloads are also available in the so-called ‘cloud.’” (Darin Stahl)

    IBM

    Maintain an Organized Portfolio

    • Buy Link or Shortcode: {j2store}432|cart{/j2store}
    • member rating overall impact: 9.0/10 Overall Impact
    • member rating average dollars saved: $3,059 Average $ Saved
    • member rating average days saved: 10 Average Days Saved
    • Parent Category Name: Portfolio Management
    • Parent Category Link: /portfolio-management
    • All too often, the portfolio of programs and projects looks more like a random heap than a strategically organized and balanced collection of investments that will drive the business forward.
    • Portfolio managers know that with the right kind of information and the right level of process maturity they can get better results through the portfolio; however, organizations often assume (falsely) that the required level of maturity is out of reach from their current state and perpetually delay improvements.

    Our Advice

    Critical Insight

    • The information needed to define clear and usable criteria for organizing the portfolio of programs and projects already exists. Portfolio managers only need to identify the sources of that information and institute processes for regularly reviewing that information in order to define those criteria.
    • Once a portfolio manager has a clear idea of the goals and constraints that shape what ought to be included (or removed) from the portfolio and once these have been translated into clear and usable portfolio criteria, basic portfolio management processes can be instituted to ensure that these criteria are used consistently throughout the various stages of the project lifecycle.
    • Portfolio management frameworks and processes do not need to be built from scratch. Well-known frameworks – such as the one outlined in COBIT 5 APO05 – can be instituted in a way that will allow even low-maturity organizations to start organizing their portfolio.
    • Organizations do not need to grow into portfolio management frameworks to get the benefits of an organized portfolio; instead, they can grow within such frameworks.

    Impact and Result

    • An organized portfolio will ensure that the projects and programs included in it are strategically aligned and can actually be executed within the finite constraints of budgetary and human resource capacity.
    • Portfolio managers are better empowered to make decisions about which projects should be included in the portfolio (and when) and are better empowered to make the very tough decisions about which projects should be removed from the portfolio (i.e. cancelled).
    • Building and maturing a portfolio management framework will more fully integrate the PMO into the broader IT management and governance frameworks, making it a more integral part of strategic decisions and a better business partner in the long run.

    Maintain an Organized Portfolio Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should maintain an organized portfolio of programs and projects, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Assess the current state of the portfolio and PPM processes

    Analyze the current mix of programs and projects in your portfolio and assess the maturity of your current PPM processes.

    • Maintain an Organized Portfolio – Phase 1: Assess the Current State of the Portfolio and PPM Processes
    • Project Portfolio Organizer
    • COBIT APO05 (Manage Portfolio) Alignment Workbook

    2. Enhance portfolio organization through improved PPM criteria and processes

    Enhance and optimize your portfolio management processes to ensure portfolio criteria are clearly defined and consistently applied across the project lifecycle when making decisions about which projects to include or remove from the portfolio.

    • Maintain an Organized Portfolio – Phase 2: Enhance Portfolio Organization Through Improved PPM Criteria and Processes
    • Portfolio Management Standard Operating Procedures

    3. Implement improved portfolio management practices

    Implement your portfolio management improvement initiatives to ensure long-term sustainable adoption of new PPM practices.

    • Maintain an Organized Portfolio – Phase 3: Implement Improved Portfolio Management Practices
    • Portfolio Management Improvement Roadmap Tool
    [infographic]

    Workshop: Maintain an Organized Portfolio

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Assess Portfolio Mix and Portfolio Process Current State

    The Purpose

    Analyze the current mix of the portfolio to determine how to better organize it according to organizational goals and constraints.

    Assess which PPM processes need to be enhanced to better organize the portfolio.

    Key Benefits Achieved

    An analysis of the existing portfolio of projects (highlighting areas of concern).

    An analysis of the maturity of current PPM processes and their ability to support the maintenance of an organized portfolio.

    Activities

    1.1 Pre-work: Prepare a complete project list.

    1.2 Define existing portfolio categories, criteria, and targets.

    1.3 Analyze the current portfolio mix.

    1.4 Identify areas of concern with current portfolio mix.

    1.5 Review the six COBIT sub-processes for portfolio management (APO05.01-06).

    1.6 Assess the degree to which these sub-processes have been currently achieved at the organization.

    1.7 Assess the degree to which portfolio-supporting IT governance and management processes exist.

    1.8 Perform a gap analysis.

    Outputs

    Analysis of the current portfolio mix

    Assessment of COBIT alignment and gap analysis.

    2 Define Portfolio Target Mix, Criteria, and Roadmap

    The Purpose

    Define clear and usable portfolio criteria.

    Record/design portfolio management processes that will support the consistent use of portfolio criteria at all stages of the project lifecycle.

    Key Benefits Achieved

    Clearly defined and usable portfolio criteria.

    A portfolio management framework that supports the consistent use of the portfolio criteria across all stages of the project lifecycle.

    Activities

    2.1 Identify determinants of the portfolio mix, criteria, and constraints.

    2.2 Define the target mix, portfolio criteria, and portfolio metrics.

    2.3 Identify sources of funding and resourcing.

    2.4 Review and record the portfolio criteria based upon the goals and constraints.

    2.5 Create a PPM improvement roadmap.

    Outputs

    Portfolio criteria

    Portfolio metrics for intake, monitoring, closure, termination, reprioritization, and benefits tracking

    Portfolio Management Improvement Roadmap

    3 Design Improved Portfolio Sub-Processes

    The Purpose

    Ensure that the portfolio criteria are used to guide decision making at each stage of the project lifecycle when making decisions about which projects to include or remove from the portfolio.

    Key Benefits Achieved

    Processes that support decision making based upon the portfolio criteria.

    Processes that ensure the portfolio remains consistently organized according to the portfolio criteria.

    Activities

    3.1 Ensure that the metrics used for each sub-process are based upon the standard portfolio criteria.

    3.2 Establish the roles, accountabilities, and responsibilities for each sub-process needing improvement.

    3.3 Outline the workflow for each sub-process needing improvement.

    Outputs

    A RACI chart for each sub-process

    A workflow for each sub-process

    4 Change Impact Analysis and Stakeholder Engagement Plan

    The Purpose

    Ensure that the portfolio management improvement initiatives are sustainably adopted in the long term.

    Key Benefits Achieved

    Stakeholder engagement.

    Sustainable long-term adoption of the improved portfolio management practices.

    Activities

    4.1 Conduct a change impact analysis.

    4.2 Create a stakeholder engagement plan.

    Outputs

    Change Impact Analysis

    Stakeholder Engagement Plan

    Completed Portfolio Management SOP

    Corporate security consultancy

    Corporate security consultancy

    Based on experience
    Implementable advice
    human-based and people-oriented

    Engage our corporate security consultancy firm to discover any weaknesses within your company’s security management. Tymans Group has extensive expertise in helping small and medium businesses set up clear security protocols to safeguard their data and IT infrastructure. Read on to discover how our consulting firm can help improve corporate security within your company.

    Why should you hire a corporate security consultancy company?

    These days, corporate security includes much more than just regulating access to your physical location, be it an office or a store. Corporate security increasingly deals in information and data security, as well as general corporate governance and responsibility. Proper security protocols not only protect your business from harm, but also play an important factor in your overall success. As such, corporate security is all about setting up practical and effective strategies to protect your company from harm, regardless of whether the threat comes from within or outside. As such, hiring a security consulting firm to improve corporate security and security management within your company is not an unnecessary luxury, but a must.

    Security and risk management

    Our security and risk services

    Security strategy

    Security Strategy

    Embed security thinking through aligning your security strategy to business goals and values

    Read more

    Disaster Recovery Planning

    Disaster Recovery Planning

    Create a disaster recovey plan that is right for your company

    Read more

    Risk Management

    Risk Management

    Build your right-sized IT Risk Management Program

    Read more

    Check out all our services

    Improve your corporate security with help from our consulting company

    As a consultancy firm, Tymans Group can help your business to identify possible threats and help set up strategies to avoid them. However, as not all threats can be avoided, our corporate security consultancy firm also helps you set up protocols to mitigate and manage them, as well as help you develop effective incident management protocols. All solutions are practical, people-oriented and based on our extensive experience and thus have proven effectiveness.

    Hire our experienced consultancy firm

    Engage the services of our consulting company to improve corporate security within your small or medium business. Contact us to set up an appointment on-site or book a one-hour talk with expert Gert Taeymans to discuss any security issues you may be facing. We are happy to offer you a custom solution.

    Register to read more …

    10 Secrets for Successful Disaster Recovery in the Cloud

    • Buy Link or Shortcode: {j2store}419|cart{/j2store}
    • member rating overall impact: 10.0/10 Overall Impact
    • member rating average dollars saved: $12,096 Average $ Saved
    • member rating average days saved: 20 Average Days Saved
    • Parent Category Name: DR and Business Continuity
    • Parent Category Link: /business-continuity
    • The pay-per-use pricing structure of cloud services make it a cheaper DR option, but there are gotchas you need to avoid, ranging from unexpected licensing costs to potential security vulnerabilities.
    • You likely started on the path to cloud DR with consideration of cloud storage for offsite retention of backups. Systems recovery in the cloud can be a real value-add to using cloud as a backup target.
    • Your cloud-based DR environment has to be secure and compliant, but performance also has to be “good enough” to operate the business.
    • Location still matters, and selecting the DR site that optimizes latency tolerance and geo-redundancy can be difficult.

    Our Advice

    Critical Insight

    • Keep your systems dormant until disaster strikes. Prepare as much of your environment as possible without tapping into compute resources. Enjoy the low at-rest costs, and leverage the reliability of the cloud in your failover.
    • Avoid failure on the failback! Bringing up your systems in the cloud is a great temporary solution, but an expensive long-term strategy. Make sure you have a plan to get back on premises.
    • Leverage cloud DR as a start for cloud migration. Cloud DR provides a gateway for broader infrastructure lift and shift to cloud IaaS, but this should only be the first phase of a longer-term roadmap that ends in multi-service hybrid cloud.

    Impact and Result

    • Calculate the cost of your DR solution with a cloud vendor. Test your systems often to build out more accurate budgets and to define failover and failback action plans to increase confidence in your capabilities.
    • Define “good enough” performance by consulting with the business and setting correct expectations for the recovery state.
    • Dig deeper into the various flavors of cloud-based DR beyond backup and restore, including pilot light, warm standby, and multi-site recovery. Each of these has unique benefits and challenges when done in the cloud.

    10 Secrets for Successful Disaster Recovery in the Cloud Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out the 10 secrets for success in cloud-based DR deployment, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    [infographic]

    Innovation

    • Buy Link or Shortcode: {j2store}21|cart{/j2store}
    • Related Products: {j2store}21|crosssells{/j2store}
    • Teaser Video: Visit Website
    • Teaser Video Title: Digital Ethics = Data Equity
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • sidebar graphic: Visit Link
    • Parent Category Name: Strategy and Governance
    • Parent Category Link: /strategy-and-governance
    Innovation is the at heart of every organization, especially in these fast moving times. It does not matter if you are in a supporting or "traditional" sector.  The company performing the service in a faster, better and more efficient way, wins.

    innovation

    Build Better Workflows

    • Buy Link or Shortcode: {j2store}496|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Service Desk
    • Parent Category Link: /service-desk

    Do you experience any of the following challenges:

    • You lack process documentation.
    • Your documentation lacks flowchart examples.
    • Your workflows have points of friction and need improvement.

    Our Advice

    Critical Insight

    • Don’t just document – target your future state as you document your workflows.
    • Find opportunities for automation, pinpoint key handoff points, and turn cold handoffs into warm handoffs

    Impact and Result

    • Understand the basics of documenting a workflow in flowchart format.
    • Run activities to revise and stress-test your workflows to improve their accuracy and effectiveness.
    • Ensure your workflows are part of a continuous improvement cycle – keep them up to date as a living document.

    Build Better Workflows Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Build Better Workflows – A step by step document that walks you through the process of convening a working group to design and update a process flowchart.

    Ask the right questions and pressure test the workflow so the documentation is as helpful as possible to all who consult it.

    • Build Better Workflows Storyboard

    2. Workflow Activity: An onboarding example for a completed flowchart review.

    Use this workflow as an example of the output of an onboarding workflow-improvement activity.

    • Workflow Activity: Onboarding Example (Visio)
    • Workflow Activity: Onboarding Example (PDF)
    [infographic]

    Further reading

    Build Better Workflows

    Go beyond draft one to refine and pressure test your process.

    Analyst Perspective

    Remove friction as you document workflows

    Emily Sugerman

    Emily Sugerman
    Research Analyst, Infrastructure & Operations

    Info-Tech Research Group

    You can’t mature processes without also documenting them. Process documentation is most effective when workflows are both written out and also visualized in the form of flow charts.

    Your workflows may appear in standard operating procedures, in business continuity and disaster recovery plans, or anywhere else a process’ steps need to be made explicit. Often, just getting something down on paper is a win. However, the best workflows usually do not emerge fully-formed out of a first draft. Your workflow documentation must achieve two things:

    • Be an accurate representation of how you currently operate or how you will operate in the near future as a target state.
    • Be the output of a series of refinements and improvements as the workflow is reviewed and iterated.

    This research will use the example of improving an onboarding workflow. Ask the right questions and pressure test the workflow so the documentation is as helpful as possible to all who consult it.

    Executive Summary

    Your Challenge

    Common Obstacles

    Info-Tech’s Approach

    • Your documentation lacks workflows entirely, or ...
    • Your workflows are documented in flowchart form but are not accurate, and/or ...
    • Your workflows are documented in flowchart form but contain points of friction and need process improvement.
    • Getting the relevant stakeholders together to contribute to workflow design and validate them.
    • Selecting the right detail level to include in the workflow – not too much and not too little.
    • Knowing the right questions to ask to review and improve your workflow flowcharts.

    Use this material to help

    • Understand the basics of documenting a workflow in flowchart format.
    • Run activities to revise and stress-test your workflows to improve their accuracy and effectiveness.
    • Ensure your workflows are part of a continuous improvement cycle – keep them up-to-date as a living document.

    Info-Tech Insight

    Don’t just document – target your future state as you document your workflows. Find opportunities for automation, pinpoint key handoff points, and turn cold handoffs into warm handoffs.

    Follow these steps to build, analyze, and improve the workflow

    The image contains a screenshot of a diagram that demonstrates the steps needed to build better workflows.

    Insight Summary

    Keep future state in mind.
    Don’t just document – target your future state as you document your workflows. Find opportunities for automation, pinpoint key handoff points, and turn cold handoffs into warm handoffs.

    Promote the benefits of documenting workflows as flowcharts.
    Foreground to the IT team how this will improve customer experience. End-users will benefit from more efficient workflows.

    Remember the principle of constructive criticism.
    Don’t be afraid to critique the workflow but remember this can be a team-building experience. Focus on how these changes will be mutually beneficial, not assigning blame for workflow friction.

    Don’t waste time building shelfware.
    Establish a review cadence to ensure the flowchart is a living document that people actually use.

    Benefits of building better workflows

    Risks of inadequate workflows

    Benefits of documented workflows

    • Lack of clear communication: If you don’t have workflows, you are losing out on an effective way to document and communicate processes.
    • Outdated documentation: If you do have workflows documented in standard operating procedures, they probably need to be updated unless you already consistently update documentation.
    • Facilitate knowledge transfer.
    • Standardize processes for service delivery consistency.
    • Optimize processes by discovering and improving points of friction within the workflow.
    • Improve transparency of processes to set expectations for other stakeholders.
    • Reduce risk.

    Why are visualized workflows useful?

    Use these talking points to build commitment toward documenting/updating processes.

    Risk reduction
    “Our outdated documentation is a risk, as people will assume the documented process is accurate.”

    Transparency
    “The activity of mapping our processes will bring transparency to everyone involved.”

    Accountability
    “Flow charts will help us clarify task ownership at a glance.”

    Accessibility
    “Some team members prefer diagrams over written steps, so we should provide both.”

    Knowledge centralization
    “Our flow charts will include links to other supporting documentation (checklists, vendor documentation, other flowcharts).”

    Role clarification
    “Separating steps into swim lanes can clarify different tiers, process stages, and ownership, while breaking down silos.”

    Communication
    To leadership/upper management: “This process flow chart quickly depicts the big picture.”

    Knowledge transfer
    “Flow charts will help bring new staff up to speed more quickly.”

    Consistency
    “Documenting a process standardizes it and enables everyone to do it in the same way.”

    Review what process mapping is

    A pictorial representation of a process that is used to achieve transparency.

    This research will use one specific example of an onboarding process workflow. Before drilling down into onboarding workflows specifically, review Info-Tech’s Process Mapping Guide for general guidance on what to do before you begin:

    • Know the purpose of process mapping.
    • Articulate the benefits of process mapping.
    • Recognize the risks of not process mapping.
    • Understand the different levels of processes.
    • Adopt BPMN 2.0 as a standard.
    • Consider tools for process mapping.
    • Select a process to map.
    • Learn methods to gather information.

    The image contains screenshots of the Process Mapping Guide.

    Download the Process Mapping Guide

    Select the workflow your team will focus upon

    Good candidates include:

    • Processes you don’t have documented and need to build from scratch.
    • An existing process that results in an output your users are currently dissatisfied with (if you run an annual IT satisfaction survey, use this data to find this information).
    • An existing process that is overly manual, lacks automation, and causes work slowdown for your staff.

    Info-Tech workflow examples

    Active Directory Processes

    Application Development Process

    Application Maintenance Process

    Backup Process

    Benefits Legitimacy Workflow

    Business Continuity Plan Business Process

    Business Continuity Plan Recovery Process

    Commitment Purchasing Workflow

    Coordinated Vulnerability Disclosure Process

    Crisis Management Process

    Data Protection Recovery Workflow

    Disaster Recovery Process

    Disaster Recovery Plan/Business Continuity Plan Review Workflow

    End-User Device Management Workflow Library

    Expense Process

    Event Management Process

    Incident Management and Service Desk Workflows

    MACD Workflow Mapping

    Problem Management Process

    Project Management Process

    Ransomware Response Process

    Sales Process for New Clients

    Security Policy Exception Process

    Self-Service Resolution Process

    Service Definition Process

    Service Desk Ticket Intake by Channel

    Software Asset Management Processes

    Target State Maintenance Workflow

    Example: Onboarding workflow

    Onboarding is a perennial challenge due to the large number of separate teams and departments who are implicated in the process.

    There can be resistance to alignment. As a result, everyone needs to be pulled in to see the big picture and the impact of an overly manual and disconnected process.

    Additionally, the quality of the overall onboarding process (of which IT is but one part) has a significant impact on the employee experience of new hires, and the long-term experience of those employees. This workflow is therefore often a good one to target for improvement.

    “Organizations with a standardized onboarding process experience 62% greater new hire productivity, along with 50% greater new hire retention.”1

    “Companies that focus on onboarding retain 50% more new employees than companies that don’t.”2

    1. Carucci, “To Retain New Hires, Spend More Time Onboarding Them,” 2018
    2. Uzialko, “What Does Poor Onboarding, 2023

    Tabletop exercise: Generate first draft

    In the tabletop exercise, your team will walk through your onboarding process step by step and document what happens at each stage. Prep for this meeting with the following steps:

    1. Identify roles: facilitator, notetaker, and participants. Determine who should be involved in the working group in addition to IT (HR, Hiring Team, Facilities, etc.).
    2. Decide what method of documentation you will use in the meeting. If meeting in person, cue cards are useful because they can be easily rearranged or inserted. If meeting remotely, the notetaker or facilitator will need to share their screen and capture each step with software (such as Visio, PowerPoint, or a whiteboarding software).
    3. Before you even begin mapping out the process, conduct a quick brainstorming session. What are your current challenges with it? What is working? Document on a whiteboard (electronic or hard copy).
    4. Document each step of the process as it currently happens. You will improve it later. Include task ownership.

    Roles

    Facilitator
    Tasks:

    • Guide discussion – restate contributors’ ideas, ask probing questions.
    • Keep group on track – cut off or redirect conversation when off track.

    Notetaker
    Tasks:

    • Ensure the steps are documented via the agreed-upon tools (e.g. cue cards). If the process is being documented in software, the notetaker may be solely responsible for documentation.
    • The notetaker may be the same person as the facilitator.

    Document your workflow challenges: Onboarding

    Brainstorm and document. Group similar challenges together to pull out themes.

    Lack of communication/expectation setting with users:

    Messy process, poor coordination among task owners:

    User experience affected:

    • Users submit onboarding requests with too little lead time.
    • HR/hiring manager does not include all necessary information when submitting new hire request.
    • Approvals are slowing down our ability to fulfill in a timely manner.
    • Lots of manual, repeated tasks.
    • Too much back and forth between technicians.
    • Procurement delays (supply chain challenges) leading to new user starting with no device/workaround.
    • Inconsistent resolution times for these types of requests.
    • Complaints about onboarding were one of the most frequently recurring issues in our most recent annual IT satisfaction survey.
    • Some of these complaints fall more to the responsibility of HR and direct managers, but some of the complaints relate to onboarding tasks not being completed by start date, which is our responsibility.

    Establish flowcharting standards

    If you don’t have existing flowchart standards, use the basic notation conventions used in the examples here.

    Basic notation convention shapes: Circle, oval, square, rectangle, diamond, thought bubble.

    Start, End, and Connector. Traditional flowcharting standards reserve this shape for connectors to other flowcharts or other points in the existing flowchart. Unified modeling language (UML) also uses the circle for start and end points.

    Start, End. Traditional flowcharting standards use this for start and end. However, Info-Tech recommends using the circle shape to reduce the number of shapes and avoid confusion with other similar shapes.

    Process Step. Individual process steps or activities (e.g. create ticket or escalate ticket). If it’s a series of steps, then use the sub-process symbol and flowchart the sub-process separately.

    Sub-Process. A series of steps. For example, a critical incident standard operating procedure (SOP) might reference a recovery process as one of the possible actions. Marking it as a sub-process, rather than listing each step within the critical incident SOP, streamlines the flowchart and avoids overlap with other flowcharts (e.g. the recovery process).

    Decision. Represents decision points, typically with yes/no branches, but you could have other branches depending on the question (e.g. a “Priority” question could branch into separate streams for Priority 1, 2, 3, 4, and 5 issues).

    Document/Report Output. For example, the output from a backup process might include an error log.

    Map the current process

    Prompt the working group with the following questions.

    • What happens when the ticket comes in? Who submits it? Where is it coming from? What are the trigger events? Are there any input channels we should eliminate?
    • What is the terminal event? Where does the workflow end?
    • Do we have a triage step?
    • Is the ticket prioritized? Does this need to be a step?
    • Do we create child tickets? Separate tasks for different teams? Do we create a primary/main ticket and sub-tickets? How should we represent this in the flowchart?
    • How should we represent escalations? How should we represent task ownership by different teams?
    • What are our decision points: points when the path can potentially branch (e.g. into yes/no branches)?

    Map the process: First pass

    The image contains a screenshot example of the first pass.

    Tabletop exercise: Revise workflow

    Time to review and revise the workflow. What gaps exist? How can you improve the process? What documentation gaps have been overlooked?

    Consider the following refinements for the onboarding workflow:

    • Identify missing steps
    • Clearly identify task ownership
    • Establish SLAs and timepoints
    • Capture/implement user feedback
    • Identify approval roadblocks
    • Identify communication points
    • Identify opportunities for automation
    • Create personas
    • Create onboarding checklist

    Roles

    Facilitator
    Tasks:

    • Guide discussion – restate contributors’ ideas, ask probing questions.
    • Keep group on track – cut off or redirect conversation when off track.

    Notetaker
    Tasks:

    • Ensure the steps are documented via the agreed-upon tools (e.g. cue cards). If the process is being documented in software, the notetaker may be solely responsible for documentation.
    • The notetaker may be the same person as the facilitator, but this takes some practice.

    Map the process: Critique draft

    The image contains a screenshot example of critique draft.

    Solicit feedback from the group.

    "

    • Our workflow is slowed down by hidden approvals that we haven’t mapped.
    • We have no efficient way to prevent submission of incomplete requests.
    • Our workflow doesn’t clearly show how different tasks are assigned to different teams.
    • We still don’t know how long this all takes.
    • We’re missing some tasks – what about including facilities?
    • We’re missing next steps for some of the decision points.
    "

    Review: Identify missing steps

    Consider the following refinements.

    Be complete.

    The workflow should surface tacit knowledge, so make it explicit (Haddadpoor et al.):

    • Where are the inputs coming from? Do you need to account for various input channels? Have you forgotten any?
    • Are there any input channels that you want to eliminate?
    • Have you overlooked any hardware, software, or services entitlements that should be called out?
    • Have all decision paths been worked through? Do you need to add any missing decision points?
    • Add information flows and annotations as needed.

    Review: Task ownership

    Identify task ownership.

    The flow chart will be more useful if it clearly identifies who does what in the process.

    • Consider organizing the sub-processes within the overall onboarding process into swim lanes, one for each team or group involved in the process.
    • Swim lanes help clarify who does what in the overall process (e.g. all the tasks completed by HR appear in the HR swim lane, all the tasks completed by service desk appear in the service desk swim lane).
    • They can also help draw attention to escalation points or handoff points between different teams. Assess the steps around the boundary of each swim lane. Does the working group experience/know of friction at these handoff points? What might solve it?
    • In what order should the tasks occur? What dependencies do they have?

    The image contains a screenshot of a model that demonstrates task ownership swim lanes.

    “Each task has an owner, and the task list is visible to the employee and other stakeholders, so there's visibility about whether each person has done their actions.”

    Matthew Stibbe, qtd. in Zapier, 2022

    Review: The time the workflow takes

    For onboarding, this means setting SLOs/SLAs and internal timepoints.

    Add internal timepoints for the major steps/tasks in the workflow. Begin to track these service level objectives and adjust as necessary.

    • Review old onboarding tickets and track how long each main step/task takes (or should take). Every additional approval risks adding days.
    • Consider where there are opportunities to increase automation or use templates to save time.
    • Zero in on which task within the onboarding workflow is slowing down the process.
    • Create an overall service level objective that communicates how many days the onboarding workflow is expected to take. Decide where escalations go when the SLA is breached.

    When you have validated the service level objectives are accurate and you can meet them an acceptable amount of time, communicate the overall SLA to your users. This will ensure they submit future onboarding requests to your team with enough lead time to fulfill the request. Try to place the SLA directly in the service catalog.

    “Tracking the time within the workflow can be a powerful way to show the working group why there is user dissatisfaction.”

    Sandi Conrad, Principal Advisory Director, Info-Tech Research Group

    Review: Capture user feedback

    For onboarding, this means implementing a transactional survey.

    The onboarding workflow will be subject to periodic reviews and continual improvement. Suggestions for improvement should come not only from the internal IT team, but also the users themselves.

    • Transactional surveys, launched at the close of a ticket, allow the ticket submitter to provide feedback on their customer service experience.
    • Onboarding tickets are somewhat more complex than the average incident or service request, since the ticket is often opened by one user (e.g. in HR) on behalf of another (the new employee).
    • Decide whose experience you want feedback on – the submitter of the request or the new user. Investigate your ITSM tool’s capabilities: is it possible to direct the survey to someone who is not the ticket submitter?
    Take Action on Service Desk Customer Feedback

    Use Info-Tech’s Take Action on Service Desk Customer Feedback for more guidance on creating these surveys.

    Review: Identify approval roadblocks

    For onboarding, approvals can be the main roadblock to fulfilling requests

    • How are the requests coming in? Do we have a predefined service catalog?
    • What kinds of approvals do we receive (manager, financial, legal, security, regulatory)? Ask the team to think about where there are instances of back and forth and clean that up.
    • Identify where approvals interrupt the technical flow.
      • Confirm that these approvals are indeed necessary (e.g. are certain approval requests ever declined? If not, follow up on whether they are necessary or whether some can be made into preapprovals).
      • Avoid putting agents in charge of waiting on or following up about approvals.
      • Investigate whether interruptive approvals can be moved.

    Review: Identify communication points

    A positive onboarding experience is an important part of a new employee’s success.

    Though IT is only one part of an employee’s onboarding experience, it’s an important part. Delays for hardware procurement and a lack of communication can lead to employee disengagement. Ask the team:

    • Are we communicating with our users when delays occur? When do delays occur most often?
    • How can we mitigate delays? Though we can’t resolve larger supply chain problems, can we increase stock in the meantime?
    • Can we start tracking delays to incorporate into the SLA
    • Do we offer loaner devices in the meantime?

    Place communication bullet points in the flow chart to indicate where the team will reach out to users to update or notify them of delays.

    Review: Identify opportunities for automation

    Where can we automate for onboarding?

    Identify when the process is dragged out due to waiting times (e.g. times when the technician can’t address the ticket right away).

    • Analyze the workflow to identify which tasks tend to stagnate because technician is busy elsewhere. Are these candidates for automation?
    • Is our ITSM tool capable of setting up automatically routed child tickets triggered by the main onboarding ticket? Does it generate a series of tasks? Is it a manual process? Which teams do these tasks/tickets go to?
    • Can we automate notifications if devices are delayed?
    • Can we use mobile device management for automated software installation?
    • If we have a robust service catalog, can we provide it to the users to download what they need? Or is this too many extra steps for our users?
    • Can we create personas to speed up onboarding?

    Avoid reinforcing manual processes, which make it even harder for departmental silos to work together.

    Review: Automation example – create personas

    Create role-based templates.

    Does HR know which applications our users need? Are they deferring to the manager, who then asks IT to simply duplicate an existing user?

    Personas are asset profiles that apply to multiple users (e.g. in a department) and that can be easily duplicated for new hires. You might create three persona groups in a department, with variations within each subgroup or title. To do this, you need accurate information upfront.

    Then, if you’re doing zero touch deployment, you can automate software to automatically load.

    Many HRIS systems have the ability to create a persona, and also to add users to the AD, email, and distribution groups without IT getting involved. This can alleviate work from the sysadmin. Does our HRIS do this?

    • Review old onboarding tickets. Do they include manual steps like setting up mailboxes, creating user accounts, adding to groups?
    • Investigate your ITSM tool’s onboarding template. Does it allow you to create a form through which to create dynamic required fields?
    • Identify the key information service desk needs from the department supervisor, or equivalent role, to begin the onboarding request – employee type, access level, hardware and software entitlements, etc.

    Revised workflow

    How does the group feel about the revised workflow?

    • Are any outputs still missing?
    • Can we add any more annotations to provide more context to someone reading this for the first time?
    • Do the task names follow a “verb-noun” format?
    • Are the handoffs clear?
    • Are some of the steps overly detailed compared to others?
    • Does it help resolve the challenges we listed?
    • Does it achieve the benefits we want to achieve?

    Download the Workflow Activity: Onboarding Example

    Remember the principle of constructive criticism.

    Don’t be afraid to critique the workflow but remember this can also be a team-building experience. Focus on how these changes will be mutually beneficial, not assigning blame for workflow friction.

    Post-review: Revised workflow

    The image contains a screenshot example of a revised workflow.

    Final check

    • Do we need to run this by Legal?
    • Have we included too many sub-processes? Not enough?
    • Is the flowchart easy to read and follow?

    Decide how often this workflow will be revised.

    • Is this workflow part of a larger piece of documentation that has a set review cadence? Where is it stored?
    • If not, what is a realistic time frame for regular review?
    • Who will own this process in an ongoing way and be in charge of convening a future review working group?

    Validation with stakeholders

    • What documentation does the flowchart belong to? When will you review it again?
    • Who do you need to validate the flowchart with?

    Share the flowchart and set up a review meeting.

    • Walk through the workflow with stakeholders who did not participate in building it.
    • Do they find it easy to follow?
    • Can they identify missing steps?

    Don’t waste time building shelfware.

    Establish a review cadence to ensure the flowchart is a living document that people actually use.

    Info-Tech offers various levels of support to best suit your needs

    DIY Toolkit

    “Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful.”

    Guided Implementation

    “Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track.”

    Workshop

    “We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place.”

    Consulting

    “Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project.”

    Diagnostics and consistent frameworks used throughout all four options

    Bibliography

    Bushkill, Claire. “The top 5 ways to automate your onboarding checklist.” Rippling Blog. 18 Mar 2022. Accessed 29 Nov 2022. Ha https://www.rippling.com/blog/the-top-5-ways-to-automate-your-onboarding-checklist
    Carucci, Ron. “To Retain New Hires, Spend More Time Onboarding Them.” Harvard Business Review, 3 Dec 2018
    Haddadpoor, Asefeh, et al. “Process Documentation: A Model for Knowledge Management in Organizations.” Materia Socio-Medica, vol. 27, no. 5, Oct. 2015, pp. 347–50. PubMed Central, https://doi.org/10.5455/msm.2015.27.347-350.
    King, Melissa. “New hire checklist: An employee onboarding checklist template for 2022.” Zapier. 14 Jul 2022. Accessed 29 Nov 2022. https://zapier.com/blog/onboarding-checklist/
    Uzialko, Adam. “What Does Poor Onboarding Really Do to Your Team?” Business News Daily. 23 Jan 2023.
    https://www.manageengine.com/products/service-desk...

    Contributors

    Sandi Conrad, Principal Advisory Director, Infrastructure and Operations, Info-Tech Research Group

    Christine Coz, Executive Counselor, Info-Tech Research Group

    Allison Kinnaird, Practice Lead, Infrastructure and Operations, Info-Tech Research Group

    Natalie Sansone, Research Director, Infrastructure and Operations, Info-Tech Research Group

    Ransomware Cyber Attack. The real Disaster Recovery Scenario

    cybercrime pay ransomware

    Cyber-ransomware criminals need to make sure that you cannot simply recover your encrypted data via your backups. They must make it look like paying is your only option. And if you do not have a strategy that takes this into account, unfortunately, you may be up the creek without a paddle. because how do they make their case? Bylooking for ways to infect your backups, way before you find out you have been compromised. 

    That means your standard disaster recovery scenarios provide insufficient protection against this type of event. You need to think beyond DRP and give consideration to what John Beattie and Michael Shandrowski call "Cyber Incident Recovery Risk management" (CIR-RM).  

    incident, incident management, cybersecurity, cyber, disaster recovery, drp, business continuity, bcm, recovery

    Register to read more …

    Build and Deliver an Optimized IT Update Presentation

    • Buy Link or Shortcode: {j2store}269|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Manage Business Relationships
    • Parent Category Link: /manage-business-relationships
    • IT update presentation success comes with understanding the business and the needs of your stakeholders. It often takes time and effort to get it right.
    • Many IT updates are too technically focused and do not engage nor demonstrate value in the eyes of the business.
    • This is not the time to boast about technical metrics that lack relevance.
    • Too often IT updates are prepared without the necessary pre-discussions required to validate content and hone priorities.

    Our Advice

    Critical Insight

    • CIOs need to take charge of the IT value proposition, increasing the impact and strategic role of IT.
    • Use your IT update to focus decisions, improve relationships, find new sources of value, and drive credibility.
    • Evolve the strategic partnership with your business using key metrics to help guide the conversation.

    Impact and Result

    • Build and deliver an IT update that focuses on what is most important.
    • Achieve the buy-in you require while driving business value.
    • Gain clarity on your scope, goals, and outcomes.
    • Validate IT’s role as a strategic business partner.

    Build and Deliver an Optimized IT Update Presentation Research & Tools

    Start here – read the Executive Brief

    Read our Executive Brief to find out how an optimized IT update presentation is your opportunity to drive business value.Review Info-Tech’s methodology and understand how we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Scope and goals

    Confirm the “why” of the IT update presentation by determining its scope and goals.

    • Build and Deliver an Optimized IT Update Presentation – Phase 1: Scope and Goals

    2. Assess and build

    Confirm the “what” of the presentation by focusing on business requirements, metrics, presentation creation, and stakeholder validation.

    • Build and Deliver an Optimized IT Update Presentation – Phase 2: Assess and Build
    • IT Update Stakeholder Interview Guide
    • IT Metrics Prioritization Tool

    3. Deliver and inspire

    Confirm the “how” of the presentation by focusing on engaging your audience, getting what you need, and creating a feedback cycle.

    • Build and Deliver an Optimized IT Update Presentation – Phase 3: Deliver and Inspire
    • IT Update Open Issues Tracking Tool
    [infographic]

    Workshop: Build and Deliver an Optimized IT Update Presentation

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Scope, Goals, and Requirements

    The Purpose

    Determine the IT update’s scope and goals and identify stakeholder requirements

    Key Benefits Achieved

    IT update scope and goals

    Business stakeholder goals and requirements

    Activities

    1.1 Determine/validate the IT update scope

    1.2 Determine/validate the IT update goals

    1.3 Business context analysis

    1.4 Determine stakeholder needs and expectations

    1.5 Confirm business goals and requirements

    Outputs

    Documented IT update scope

    Documented IT update goals

    Validated business context

    Stakeholder requirements analysis

    Confirmed business goals and requirements

    2 Validate Metrics With Business Needs

    The Purpose

    Analyze metrics and content and validate against business needs

    Key Benefits Achieved

    Selection of key metrics

    Metrics and content validated to business needs

    Activities

    2.1 Analyze current IT metrics

    2.2 Review industry best-practice metrics

    2.3 Align metrics and content to business stakeholder needs

    Outputs

    Identification of key metrics

    Finalization of key metrics

    Metrics and content validated to business stakeholder needs

    3 Create an optimized IT update

    The Purpose

    Create an IT update presentation that is optimized to business needs

    Key Benefits Achieved

    Optimized IT update presentation

    Activities

    3.1 Understand the audience and how to best engage them

    3.2 Determine how to present the pertinent data

    3.3 IT update review with key business stakeholders

    3.4 Final edits and review of IT update presentation

    3.5 Pre-presentation checklist

    Outputs

    Clarity on update audience

    Draft IT update presentation

    Business stakeholder feedback

    Finalized IT update presentation

    Confirmation on IT update presentation readiness

    Beyond Survival

    • Buy Link or Shortcode: {j2store}204|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Big Data
    • Parent Category Link: /big-data
    • Consumer, customer, employee, and partner behavior has changed; new needs have arisen as a result of COVID-19. Entire business models had to be rethought and revised – in real time with no warning.
    • And worse, no one knows when (or even if) the pandemic will end. The world and the economy will continue to be highly uncertain, unpredictable, and vulnerable for some time.
    • Business leaders need to continue experimenting to stay in business, protect employees and supply chains, manage financial obligations, allay consumer and employee fears, rebuild confidence, and protect trust.
    • How do organizations know whether their new business tactics are working?

    Our Advice

    Critical Insight

    • We can learn many lessons from those who have survived and are succeeding.
    • They have one thing in common though – they rely on data and analytics to help people think and know how to respond, evaluate effectiveness of new business tactics, uncover emerging trends to feed innovation, and minimize uncertainty and risk.
    • This mini-blueprint highlights organizations and use cases where data, analytics, and AI deliver tangible business and human value now and in the future.

    Impact and Result

    • Learn from the pandemic survivors and super-achievers so that you too can hit the ground running in the new normal. Even better – go beyond survival, like many of them have done. Create your future by leveraging and scaling up your data and analytics investments. It is not (yet) too late, and Info-Tech can help.

    Beyond Survival Research & Tools

    Beyond Survival

    Use data, analytics, and AI to reimagine the future and thrive in the new normal.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    • Beyond Survival Storyboard
    [infographic]

    Cost and Budget Management

    • Buy Link or Shortcode: {j2store}8|cart{/j2store}
    • Related Products: {j2store}8|crosssells{/j2store}
    • Up-Sell: {j2store}8|upsells{/j2store}
    • member rating overall impact: 9.5/10
    • member rating average dollars saved: $2,000
    • member rating average days saved: 5
    • Parent Category Name: Financial Management
    • Parent Category Link: /financial-management

    The challenge

    • IT is seen as a cost center in most organizations. Your IT spend is fuelled by negative sentiment instead of contributing to business value.

    • Budgetary approval is difficult, and in many cases, the starting point is lowering the cost-income ratio without looking at the benefits.
    • Provide the right amount of detail in your budgets to tell your investment and spending story. Align it with the business story. Too much detail only increases confusion, too little suspicion.

    Our advice

    Insight

    An effective IT budget complements the business story with how you will achieve the expected business targets.

    • Partner with the business to understand the strategic direction of the company and its future needs.
    • Know your costs and the value you will deliver.
    • Present your numbers and story clearly and credibly. Excellent delivery is part of good communication.
    • Guide your company by clearly explaining the implications of different choices they can make.

    Impact and results 

    • Get a head-start on your IT forecasting exercise by knowing the business strategy and what initiatives they will launch.
    • The coffee corner works! Pre-sell your ideas in quick chats.
    • Do not make innovation budgets bigger than they need to be. It undermines your credibility.
    • You must know your history to accurately forecast your IT operations cost and how it will evolve based on expected business changes.
    • Anticipate questions. IT discretionary proposals are often challenged. Think ahead of time about what areas your business partners will focus on and be ready with researched and credible responses.
    • When you have an optimized budget, tie further cost reductions to consequences in service delivery or deferred projects, or a changed operating model.

    The roadmap

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    Get started

    Our concise executive brief shows you why you should develop a budget based on value delivery. We'll show you our methodology and the ways we can help you in completing this.

    Plan for budget success

    • Build an IT Budget That Demonstrates Value Delivery – Phase 1: Plan (ppt)
    • IT Budget Interview Guide (doc)

    Build your budget.

    • Build an IT Budget That Demonstrates Value Delivery – Phase 2: Build (ppt)
    • IT Cost Forecasting Tool (xls)

    Sell your budget

    • Build an IT Budget That Demonstrates Value Delivery – Phase 3: Sell (ppt)
    • IT Budget Presentation (ppt)


    Why learn from Tymans Group?

    The TY classes contain in-depth learning material based on over 30 years of experience in IT Operations and Resilience.

    You receive the techniques, tips, tricks, and "professional secrets" you need to succeed in your resilience journey.

    Why would I share "secrets?"

    Because over time, you will find that "secrets" are just manifested experiences.

    What do I mean by that? Gordon Ramsay, who was born in 1966 like me, decided to focus on his culinary education at age 19. According to his Wikipedia page, that was a complete accident. (His Wikipedia page is a hoot to read, by the way.) And he has nothing to prove anymore. His experience in his field speaks for itself.

    I kept studying in my original direction for just one year longer, but by 21, I founded my first company in Belgium in 1987, in the publishing industry. This was extended by IT experiences in various sectors, like international publishing and hospitality, culminating in IT for high-velocity international financial markets and insurance.

    See, "secrets" are a great way to get you to sign up for some "guru" program that will "tell all!" Don't fall for it, especially if the person is too young to have significant experience.

    There are no "secrets." There is only experience and 'wisdom." And that last one only comes with age.

    If I were in my 20s, 30s, or 40s, there is no chance I would share my core experiences with anyone who could become my competitor. At that moment, I'm building my own credibility and my own career. I like helping people, but not to the extent that it will hurt my prospects. 

    And that is my second lesson: be always honest about your intentions. Yes, always. 

    At the current point in my career, "hurting my prospects" is less important. Yes, I still need to make a living, and in another post, I will explain more about that. Here, I feel it is important to share my knowledge and experience with the next people who will take my place in the day-to-day operations of medium and large corporations. And that is worth something. Hence, "sharing my secrets."

    Gert

    Why learn about resilience from us?

    This is a great opportunity to learn from my 30+ years of resilience experience. TY's Gert experienced 9/11 in New York, and he was part of the Lehman Disaster Recovery team that brought the company back within one (one!) week of the terrorist attack.

    He also went through the London Bombings of 2005 and the 2008 financial crisis, which required fast incident responses, the Covid 2020 issues, and all that entailed. Not to mention that Gert was part of the Tokyo office disaster response team as early as 1998, ensuring that Salomon was protected from earthquakes and floods in Japan.

    Gert was part of the solution (for his clients) to several further global events, like the admittedly technical log4J event in 2021, the 2024 Crowdstrike event, and many other local IT incidents, to ensure that clients could continue using the services they needed at that time.

    Beyond the large corporate world, we helped several small local businesses improve their IT resilience with better cloud storage and security solutions. 

    These solutions and ways of thinking work for any business, large or small.

    The TY team

    Explore our resilience solutions.

    Modernize Your Microsoft Licensing for the Cloud Era

    • Buy Link or Shortcode: {j2store}304|cart{/j2store}
    • member rating overall impact: 9.1/10 Overall Impact
    • member rating average dollars saved: $102,414 Average $ Saved
    • member rating average days saved: 10 Average Days Saved
    • Parent Category Name: Licensing
    • Parent Category Link: /licensing
    • Microsoft licensing is complicated. Often, the same software can be licensed a number of ways. It’s difficult to know which edition and licensing model is best.
    • Licensing and features often change with the release of new software versions, compounding the problem by making it difficult to stay current.
    • In tough economic times, IT is asked to reduce capital and operating expenses wherever possible. As one of the top five expense items in most enterprise software budgets, Microsoft licensing is a primary target for cost reduction.

    Our Advice

    Critical Insight

    • Focus on needs first. Conduct a thorough needs assessment and document the results. Well-documented needs will be your best asset in navigating Microsoft licensing and negotiating your agreement.
    • Beware the bundle. Be aware when purchasing the M365 suite that there is no way out. Negotiating a low price is critical, as all leverage swings to Microsoft once it is on your agreement.
    • If the cloud doesn’t fit, be ready to pay up or start making room. Microsoft has drastically reduced discounting for on-premises products, support has been reduced, and product rights have been limited. If you are planning to remain on premises, be prepared to pay up.

    Impact and Result

    • Understand what your organization needs and what your business requirements are. It’s always easier to purchase more later than try to reduce your spend.
    • Complete cost calculations carefully, as the cloud might end up costing significantly more for the desired feature set. However, in some scenarios, it may be more cost efficient for organizations to license in the cloud.
    • If there are significant barriers to cloud adoption, discuss and document them. You’ll need this documentation in three years when it’s time to renew your agreement.

    Modernize Your Microsoft Licensing for the Cloud Era Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Modernize Your Microsoft Licensing Deck – A deck to help you build a strategy for your Microsoft licensing renewal.

    This storyboard will help you build a strategy for your Microsoft licensing renewal from conducting a thorough needs assessment to examining your licensing position, evaluating Microsoft's licensing options, and negotiations.

    • Modernize Your Microsoft Licensing for the Cloud Era – Phases 1-4

    2. Microsoft Cloud Products Cost Modeler – A tool to model estimated costs for Microsoft's cloud products.

    The Microsoft Cloud Products Cost Modeler will provide a rough estimate of what you can expect to pay for Office 365 or Dynamics CRM licensing, before you enter into negotiations. This is not your final cost, but it will give you an idea.

    • Microsoft Cloud Products Cost Modeler

    3. Microsoft Licensing Purchase Reference Guide - A template to capture licensing stakeholder information, proposed changes to licensing, and negotiation items.

    The Microsoft Licensing Purchase Reference Guide can be used throughout the process of licensing review: from initial meetings to discuss compliance state and planned purchases, to negotiation meetings with resellers. Use it in conjunction with Info-Tech's Microsoft Licensing Effective License Position Template.

    • Microsoft Licensing Purchase Reference Guide

    4. Negotiation Timeline for Microsoft – A template to navigate your negotiations with Microsoft.

    This tool will help you plot out your negotiation timeline, depending on where you are in your contract negotiation process.

  • 6-12 months
  • Less than 3 months
    • Negotiation Timeline for Microsoft – Visio
    • Negotiation Timeline for Microsoft – PDF

    5. Effective Licensing Position Tool – A template to help you create an effective licensing position and determine your compliance position.

    This template helps organizations to determine the difference between the number of software licenses they own and the number of software copies deployed. This is known as the organization’s effective license position (ELP).

    • Effective Licensing Position Tool
    [infographic]

    Become a Strategic CIO

    • Buy Link or Shortcode: {j2store}80|cart{/j2store}
    • member rating overall impact: 9.5/10 Overall Impact
    • member rating average dollars saved: $10,000 Average $ Saved
    • member rating average days saved: 15 Average Days Saved
    • Parent Category Name: IT Strategy
    • Parent Category Link: /it-strategy
    • As a CIO, you are currently operating in a stable and trusted IT environment, but you would like to advance your role to strategic business partner.
    • CIOs are often overlooked as a strategic partner by their peers, and therefore face the challenge of proving they deserve a seat at the table.

    Our Advice

    Critical Insight

    • To become a strategic business partner, you must think and act as a business person that works in IT, rather than an IT person that works for the business.
    • Career advancement is not a solo effort. Building relationships with your executive business stakeholders will be critical to becoming a respected business partner.

    Impact and Result

    • Create a personal development plan and stakeholder management strategy to accelerate your career and become a strategic business partner. For a CIO to be considered a strategic business partner, he or she must be able to:
      • Act as a business person that works in IT, rather than an IT person that works for the business. This involves meeting executive stakeholder expectations, facilitating innovation, and managing stakeholder relationships.
      • Align IT with the customer. This involves providing business stakeholders with information to support stronger decision making, keeping up with disruptive technologies, and constantly adapting to the ever-changing end-customer needs.
      • Manage talent and change. This involves performing strategic workforce planning, and being actively engaged in identifying opportunities to introduce change in your organization, suggesting ways to improve, and then acting on them.

    Become a Strategic CIO Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should become a strategic CIO, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Launch

    Analyze strategic CIO competencies and assess business stakeholder satisfaction with IT using Info-Tech's CIO Business Vision Diagnostic and CXO-CIO Alignment Program.

    • Become a Strategic CIO – Phase 1: Launch

    2. Assess

    Evaluate strategic CIO competencies and business stakeholder relationships.

    • Become a Strategic CIO – Phase 2: Assess
    • CIO Strategic Competency Evaluation Tool
    • CIO Stakeholder Power Map Template

    3. Plan

    Create a personal development plan and stakeholder management strategy.

    • Become a Strategic CIO – Phase 3: Plan
    • CIO Personal Development Plan
    • CIO Stakeholder Management Strategy Template

    4. Execute

    Develop a scorecard to track personal development initiatives.

    • Become a Strategic CIO – Phase 4: Execute
    • CIO Strategic Competency Scorecard
    [infographic]

    Workshop: Become a Strategic CIO

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Assess Competencies & Stakeholder Relationships

    The Purpose

    Gather and review information from business stakeholders.

    Assess strategic CIO competencies and business stakeholder relationships.

    Key Benefits Achieved

    Gathered information to create a personal development plan and stakeholder management strategy.

    Analyzed the information from diagnostics and determined the appropriate next steps.

    Identified and prioritized strategic CIO competency gaps.

    Evaluated the power, impact, and support of key business stakeholders.

    Activities

    1.1 Conduct CIO Business Vision diagnostic

    1.2 Conduct CXO-CIO Alignment program

    1.3 Assess CIO competencies

    1.4 Assess business stakeholder relationships

    Outputs

    CIO Business Vision results

    CXO-CIO Alignment Program results

    CIO competency gaps

    Executive Stakeholder Power Map

    2 Take Control of Your Personal Development

    The Purpose

    Create a personal development plan and stakeholder management strategy.

    Track your personal development and establish checkpoints to revise initiatives.

    Key Benefits Achieved

    Identified personal development and stakeholder engagement initiatives to bridge high priority competency gaps.

    Identified key performance indicators and benchmarks/targets to track competency development.

    Activities

    2.1 Create a personal development plan

    2.2 Create a stakeholder management strategy

    2.3 Establish key performance indicators and benchmarks/targets

    Outputs

    Personal Development Plan

    Stakeholder Management Strategy

    Strategic CIO Competency Scorecard

    External Compliance

    • Buy Link or Shortcode: {j2store}39|cart{/j2store}
    • Related Products: {j2store}39|crosssells{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Security and Risk
    • Parent Category Link: /security-and-risk
    Take Control of Compliance Improvement to Conquer Every Audit

    Identify and Manage Regulatory and Compliance Risk Impacts on Your Organization

    • Buy Link or Shortcode: {j2store}366|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Vendor Management
    • Parent Category Link: /vendor-management

    More than at any other time, our world is changing. As a result, organizations – and their vendors – need to be able to adapt their plans to accommodate risk on an unprecedented level.

    It is increasingly likely that one of your vendors, or their n-party support vendors, will fall out of regulatory compliance. Therefore, organizations must protect themselves by creating better mechanisms to hold their n-party vendors accountable and validate that they comply.

    Our Advice

    Critical Insight

    • Identifying and managing a vendor’s potential regulatory impact on your organization requires multiple people in the organization across several functions. Those people all need coaching on the potential changes in the market and how these changes may affect operations.
    • Organizational leadership is often taken unaware by changes, and their plans lack the flexibility to adjust to significant regulatory upheavals.

    Impact and Result

    Vendor management practices educate organizations on the different potential risks from vendors in your market and suggest creative and alternative ways to avoid and help manage them.

    • Prioritize and classify your vendors with quantifiable, standardized rankings.
    • Prioritize focus on your high-risk vendors.
    • Standardize your processes for identifying and monitoring vendor risks with our Regulatory Risk Impact Tool to manage potential impacts.

    Identify and Manage Regulatory and Compliance Risk Impacts on Your Organization Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Identify and Manage Regulatory and Compliance Risk Impacts to Your Organization Storyboard – Use the research to better understand the negative impacts of vendor actions to your brand reputation.

    Use this research to identify and quantify the potential regulatory impacts caused by vendors. Use Info-Tech's approach to look at the regulatory impact from various perspectives to better prepare for issues that may arise.

    • Identify and Manage Regulatory and Compliance Risk Impacts on Your Organization Storyboard

    2. Regulatory Risk Impact Tool – Use this tool to help identify and quantify the operational impacts of negative vendor actions.

    By playing the “what if” game and asking probing questions to draw out – or eliminate – possible negative outcomes, everyone involved adds their insight into parts of the organization to gather a comprehensive picture of potential impacts.

    • Regulatory Risk Impact Tool
    [infographic]

    Further reading

    Identify and Manage Risk Impacts on Your Organization

    It is easier for prospective clients to find out what you did wrong than that you fixed the issue.

    Analyst perspective

    Organizations must understand the regulatory damage vendors may cause from lack of compliance.

    Frank Sewell.

    The sheer number of regulations on the international market is immense, ever-changing, and make it almost impossible for any organization to consistently keep up with compliance.

    As regulatory enforcement increases, organizations must hold their vendors accountable for compliance through ongoing monitoring and validation of regulatory compliance to the relevant standards in their industries, or face increasing penalties for non-compliance.

    Frank Sewell,

    Research Director, Vendor Management

    Info-Tech Research Group

    Executive Summary

    Your Challenge

    Common Obstacles

    Info-Tech’s Approach

    More than at any previous time, our world is changing rapidly. As a result, organizations – and their vendors – need to be able to adapt their plans to accommodate risk on an unprecedented level.

    It is increasingly likely that one of your vendors, or their n-party support vendors, will fall out of regulatory compliance. Organizations must protect themselves by creating better mechanisms to hold their n-party vendors accountable and validate that they comply.

    Identifying and managing a vendor’s potential regulatory impact on your organization requires multiple people in the organization across several functions. Those people all need coaching on the potential changes in the market and how these changes may affect operations.

    Organizational leadership is often taken unaware by changes, and their plans lack the flexibility to adjust to significant regulatory upheavals.

    Vendor management practices educate organizations on the different potential risks from vendors in your market and suggest creative and alternative ways to avoid and help manage them.

    Prioritize and classify your vendors with quantifiable, standardized rankings.

    Prioritize focus on your high-risk vendors.

    Standardize your processes for identifying and monitoring vendor risks with our Regulatory Risk Impact Tool to manage potential impacts.

    Info-Tech Insight

    Organizations must evolve their risk assessments to be more adaptive to respond to regulatory changes in the global market. Ongoing monitoring of the vendors who must comply with industry and governmental regulations is crucial to avoiding penalties and maintaining your regulatory compliance.

    Info-Tech’s multi-blueprint series on vendor risk assessment

    There are many individual components of vendor risk beyond cybersecurity.

    The image contains a cube that is divided into 6 asymmetrical to highlight the six components of vendor risk. Strategic, Security, Regulatory & Compliance, Financial, Reputational, Operational.

    This series will focus on the individual components of vendor risk and how vendor management practices can facilitate organizations’ understanding of those risks.

    Out of Scope:

    This series will not tackle risk governance, determining overall risk tolerance and appetite, or quantifying inherent risk.

    Regulatory and Compliance risk impacts

    Potential losses to the organization due regulatory and compliance incidents.

    • In this blueprint we’ll:
      • Explore regulatory and compliance risks and their impacts.
      • Identify potentially disruptive events to assess the overall impact on organizations and implement adaptive measures to identify, manage, and monitor vendor performance.

    The image contains a cube that is divided into 6 asymmetrical to highlight the six components of vendor risk. Strategic, Security, Regulatory & Compliance, Financial, Reputational, Operational. Regulatory & Compliance is highlighted on the cube.

    The world is constantly changing

    The IT market is constantly reacting to global influences. By anticipating changes, leaders can set expectations and work with their vendors to accommodate them and avoid penalties.

    When the unexpected happens, being able to adapt quickly to new priorities and regulations ensures continued long-term business success.

    Below are some things no one expected to happen in the last few years:

    45%

    Have no visibility into their upstream supply chain, or they can only see as far as their first-tier suppliers.

    2022 McKinsey

    61%

    Of compliance officers expect to increase investment in their compliance function over the next two years.

    2022 Accenture

    $770k+

    Breaches involving third-party vendors cost more on average.

    2022 HIT Consultant.net

    Regulatory Compliance

    Consider implementing vendor management initiatives and practices in your organization to help gain compliance with your expanding vendor landscape.

    Your organizational risks may be monitored but are your n-party vendors?

    The image contains a cube that is divided into 6 asymmetrical to highlight the six components of vendor risk. Strategic, Security, Regulatory & Compliance, Financial, Reputational, Operational.

    Review your expectations with your vendors and hold them accountable.

    Regulatory entities are looking beyond your organization’s internal compliance these days. More and more they are diving into your third-party and downstream relationships, particularly as awareness of downstream breaches increases globally.

    • Are you assessing your vendors regularly?
    • Are you validating those assessments?
    • Do your vendors have a map of their downstream support vendors?
    • Do they have the mechanisms to hold those downstream vendors accountable to your standards?

    Regulatory Guidance and Industry Standards

    Are you confident your vendors meet your standards?

    Identify and manage regulatory and compliance risks

    Environmental, Social, Governance (ESG)
    Regulatory agencies are putting more enforcement on ESG practices across the globe. As a result, organizations will need to monitor the changing regulations and validate that their vendors and n-party support vendors are adhering to these regulations, or face penalties for non-compliance.

    Data Protection
    Data Protection remains an issue in the world. Organizations should ensure that the data their vendors obtain remains protected throughout the vendor’s lifecycle, including post-termination. Otherwise, they could be monitoring for a data breach in perpetuity.

    Mergers and Acquisitions
    More prominent vendors continuously buy smaller companies to control the market in the IT industry. Therefore, organizations should put protections in their contracts to ensure that an IT vendor’s acquisition does not put them in a relationship with someone that could cause them an issue.

    What to look for

    Identify regulatory and compliance risk impacts.

    • Is there a record of complaints against the vendor from their employees or customers?
    • Has the vendor been cited for regulatory compliance issues in the past?
    • Does the vendor have a comprehensive list of their n-party vendor partners?
      • Are they willing to accept appropriate contractual protections regarding them?
    • Does the vendor self-audit, or do they use a vetted third-party audit firm to issue a SOC report annually?
    • Does the vendor operate in regions known for regulatory violations?
    • Is the vendor willing to make concessions on contractual protections, or are they only offering “one-sided” agreements with “as-is” warranties?

    Prepare your vendor risk management for success

    Due diligence will enable successful outcomes.

    1. Obtain top-level buy-in; it is critical to success.
    2. Build enterprise risk management (ERM) through incremental improvement.
    3. Focus initial efforts on the “big wins” to prove the process works.
    4. Use existing resources.
    5. Build on any risk management activities that already exist in the organization.
    6. Socialize ERM throughout the organization to gain additional buy‑in.
    7. Normalize the process long term, with ongoing updates and continuing education for the organization.

    (Adapted from COSO)

    How to assess third-party risk

    1. Review Organizational Regulations
    2. Understand the organization’s regulatory risks to prepare for the “What If” game exercise.

    3. Identify & Understand Potential Regulatory-Compliance Risks
    4. Play the “What If” game with the right people at the table.

    5. Create a Risk Profile Packet for Leadership
    6. Pull all the information together in a presentation document.

    7. Validate the Risks
    8. Work with leadership to ensure that the proposed risks are in line with their thoughts.

    9. Plan to Manage the Risks
    10. Lower the overall risk potential by putting mitigations in place.

    11. Communicate the Plan
    12. It is important not only to have a plan but also to socialize it in the organization for awareness.

    13. Enact the Plan
    14. Once the plan is finalized and socialized, put it in place with continued monitoring for success.

    Adapted from Harvard Law School Forum on Corporate Governance

    Insight summary

    Regulatory risk impacts often come from unexpected places and have significant consequences. Knowing who your vendors are using for their support and supply chain could be crucial in eliminating the risk of non-compliance for your organization. Having a plan to identify and validate the regulatory compliance of your vendors is a must for any organization, to avoid penalties.

    Insight 1

    Organizations fail to plan for vendor acquisitions appropriately.

    Vendors routinely get acquired in the IT space. Does your organization have appropriate safeguards from inadvertently entering a negative relationship? Do you have plans around replacing critical vendors purchased in such a manner?

    Insight 2

    Organizations often fail to understand how n-party vendors could place them in non-compliance.

    Even if you know your complete third-party vendor landscape, you may not be aware of the downstream vendors in play. Ensure that you get visibility into this space as well and hold your direct vendors accountable for the actions of their vendors.

    Insight 3

    Organizations need to know where their data lives and ensure it is protected.

    Make sure you know which vendors are accessing/storing your data, where they are keeping it, and that you can get it back and have the vendors destroy it when the relationship is over. Without adequate protection throughout the lifecycle of the vendor, you could be monitoring for breaches in perpetuity.

    Identifying regulatory and compliance risks

    Who should be included in the discussion.

    • While it is true that executive-level leadership defines the strategy for an organization, it is vital for those making decisions to make informed decisions.
    • Getting input from regulatory risk experts within your organization will enhance your long-term potential for successful compliance.
    • Involving those who not only directly manage vendors but also understand your regulatory requirements will aid in determining the path forward for relationships with your current vendors, and identifying new emerging potential partners.

    See the blueprint Build an IT Risk Management Program

    Review your risk management plans for new risks on a regular basis.

    Keep in mind Risk = Likelihood x Impact (R=L*I).

    Impact (I) tends to remain the same, while Likelihood (L) is becoming closer to 100% as threat actors become more prevalent

    Managing vendor regulatory and compliance risk impacts

    How could your vendors fall out of compliance?

    • Review vendors’ downstream connections to understand thoroughly with whom you are in business.
      • Monitor their regulatory stance as it could reflect on your organization.
    • Institute proper vendor lifecycle management.
      • Make sure to follow corporate due diligence and risk assessment policies and procedures.
      • Failure to consistently do so is a recipe for disaster.
    • Develop IT risk governance and change control.
    • Introduce continual risk assessment to monitor the relevant vendor markets.
      • Regularly review your regulatory requirements for new and changing risks.
    • Be adaptable and allow for innovations that arise from the current needs.
      • Capture lessons learned from prior incidents to improve over time, and adjust your plans accordingly.

    Organizations must review their regulatory risk appetite and tolerance levels, considering their complete landscape.

    Changing regulations, acquisitions, and events that affect global supply chains are current realities, not unlikely scenarios.

    Ongoing Improvement

    Incorporating lessons learned.

    • Over time, despite everyone’s best observations and plans, incidents will catch us off guard.
    • When it happens, follow your incident response plans and act accordingly.
    • An essential step is to document what worked and what did not – collectively known as the “lessons learned.”
    • Use the lessons learned document to devise, incorporate, and enact a better risk management process.

    Sometimes disasters occur despite our best plans to manage them.

    When this happens, it is important to document the lessons learned and update our plans.

    The “what if” game

    1-3 hours

    Vendor management professionals are in an excellent position to help senior leadership identify and pull together resources across the organization to determine potential risks. By playing the "what if" game and asking probing questions to draw out – or eliminate – possible adverse outcomes, everyone involved adds their insight into parts of the organization to gather a comprehensive picture of potential impacts.

    1. Break into smaller groups (or if too small, continue as a single group).
    2. Use the Regulatory Risk Impact Tool to prompt discussion on potential risks. Keep this discussion flowing organically to explore all potentials but manage the overall process to keep the discussion pertinent and on track.
    3. Collect the outputs and ask the subject matter experts (SMEs) for management options for each one in order to present a comprehensive risk strategy. You will use this to educate senior leadership so that they can make an informed decision to accept or reject the solution.
    Input Output
    • List of identified potential risk scenarios scored by regulatory-compliance impact
    • List of potential mitigations of the scenarios to reduce the risk
    • Comprehensive regulatory risk profile on the specific vendor solution
    Materials Participants
    • Whiteboard/flip charts
    • Regulatory Risk Impact Tool to help drive discussion
    • Vendor Management – Coordinator
    • Organizational Leadership
    • Operations Experts (SMEs)
    • Legal/Compliance/Risk Manager

    High risk example from tool

    The image contains a screenshot demonstrating high risk example from the tool.

    How to mitigate:

    Contractually insist that the vendor have a third-party security audit performed annually, with the stipulation that they will not denigrate below your acceptable standards.

    Note: Even though a few items are “scored” they have not been added to the overall weight, signaling that the company has noted but does not necessarily hold them against the vendor.

    Low risk example from tool

    The image contains a screenshot demonstrating low risk example from the tool.

    Summary

    Seek to understand all regulatory requirements to obtain compliance.

    • Organizations need to understand and map out their entire vendor landscape.
    • Understand where all your data lives and how you can control it throughout the vendor lifecycle.
    • Those organizations that consistently follow their established risk assessment and due diligence processes are better positioned to avoid penalties.
    • Bring the right people to the table to outline potential risks in the market and your organization.
    • Incorporate “lessons learned” from prior incidents into your risk management process to build better plans for future issues.

    Keeping up with the ever-changing regulations can make compliance a difficult task.

    Organizations should increase the resources dedicated to monitoring these regulations as agencies continue to hold them more accountable.

    Related Info-Tech Research

    Identify and Manage Financial Risk Impacts on Your Organization

    • Vendor management practices educate organizations on potential financial impacts that vendors may incur and suggest systems to help manage them.
    • Standardize your processes for identifying and monitoring vendor risks to manage financial impacts with our Financial Risk Impact Tool.

    Identify and Manage Reputational Risk Impacts on Your Organization

    • Vendor management practices educate organizations on potential risks to vendors in your market and suggest creative and alternative ways to avoid and help manage them.
    • Standardize your processes for identifying and monitoring vendor risks to manage potential impacts on your reputation and brand with our Reputational Risk Impact Tool.

    Identify and Manage Strategic Risk Impacts on Your Organization

    • Vendor management practices educate organizations on potential risks to vendors in your market and suggest creative and alternative ways to avoid and help manage them.
    • Standardize your processes for identifying and monitoring vendor risks to manage potential impacts on your strategic plan with our Strategic Risk Impact Tool.

    Info-Tech Insight

    It is easier for prospective clients to find out what you did wrong than that you fixed the issue.


    Bibliography

    Alicke, Knut, et al. "Taking the pulse of shifting supply chains", McKinsey & Company, August 26th 2022. Accessed October 31st
    Regan, Samantha, et al. "Can compliance keep up with warp-speed Change?", accenture, May 18th 2022. Accessed Oct 31st 2022.
    Feria, Nathalie, and Rosenberg, Daniel. "Mitigating Healthcare Cyber Risk Through Vendor Management", HIT Consultant, October 17th 2022. Accessed Oct 31st 2022.
    Tonello, Matteo. “Strategic Risk Management: A Primer for Directors.” Harvard Law School Forum on Corporate Governance, 23 Aug. 2012.
    Frigo, Mark L., and Richard J. Anderson. “Embracing Enterprise Risk Management: Practical Approaches for Getting Started.” COSO, 2011.

    Develop a Security Operations Strategy

    • Buy Link or Shortcode: {j2store}264|cart{/j2store}
    • member rating overall impact: 10.0/10 Overall Impact
    • member rating average dollars saved: $79,249 Average $ Saved
    • member rating average days saved: 28 Average Days Saved
    • Parent Category Name: Security Processes & Operations
    • Parent Category Link: /security-processes-and-operations
    • There is an onslaught of security data – generating information in different formats, storing it in different places, and forwarding it to different locations.
    • The organization lacks a dedicated enterprise security team. There is limited resourcing available to begin or mature a security operations center.
    • Many organizations are developing ad hoc security capabilities that result in operational inefficiencies, the misalignment of resources, and the misuse of security technology investments.
    • It is difficult to communicate the value of a security operations program when trying to secure organizational buy-in to gain the appropriate resourcing.
    • There is limited communication between security functions due to a centralized security operations organizational structure.

    Our Advice

    Critical Insight

    1. Security operations is no longer a center, but a process. The need for a physical security hub has evolved into the virtual fusion of prevention, detection, analysis, and response efforts. When all four functions operate as a unified process, your organization will be able to proactively combat changes in the threat landscape.
    2. Functional threat intelligence is a prerequisite for effective security operations – without it, security operations will be inefficient and redundant. Eliminate false positives by contextualizing threat data, aligning intelligence with business objectives, and building processes to satisfy those objectives.
    3. If you are not communicating, you are not secure. Collaboration eliminates siloed decisions by connecting people, processes, and technologies. You leave less room for error, consume fewer resources, and improve operational efficiency with a transparent security operations process.

    Impact and Result

    • A unified security operations process actively transforms security events and threat information into actionable intelligence, driving security prevention, detection, analysis, and response processes, addressing the increasing sophistication of cyberthreats, and guiding continuous improvement.
    • This blueprint will walk through the steps of developing a flexible and systematic security operations program relevant to your organization.

    Develop a Security Operations Strategy Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should enhance your security operations program, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Assess your current state

    Assess current prevention, detection, analysis, and response capabilities.

    • Develop a Security Operations Strategy – Phase 1: Assess Operational Requirements
    • Security Operations Preliminary Maturity Assessment Tool

    2. Develop maturity initiatives

    Design your optimized state of operations.

    • Develop a Security Operations Strategy – Phase 2: Develop Maturity Initiatives
    • Information Security Requirements Gathering Tool
    • Concept of Operations Maturity Assessment Tool

    3. Define operational interdependencies

    Identify opportunities for collaboration within your security program.

    • Develop a Security Operations Strategy – Phase 3: Define Operational Interdependencies
    • Security Operations RACI Chart & Program Plan
    • Security Operations Program Cadence Schedule Template
    • Security Operations Collaboration Plan
    • Security Operations Metrics Summary Document
    [infographic]

    Workshop: Develop a Security Operations Strategy

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Assess Operational Requirements

    The Purpose

    Determine current prevention, detection, analysis, and response capabilities, operational inefficiencies, and opportunities for improvement.

    Key Benefits Achieved

    Determine why you need a sound security operations program.

    Understand Info-Tech’s threat collaboration environment.

    Evaluate your current security operation’s functions and capabilities.

    Activities

    1.1 Understand the benefits of refining your security operations program.

    1.2 Gauge your current prevention, detection, analysis, and response capabilities.

    Outputs

    Security Operations Preliminary Maturity Assessment Tool

    2 Develop Maturity Initiatives

    The Purpose

    Begin developing and prioritizing gap initiatives in order to achieve the optimal state of operations.

    Key Benefits Achieved

    Establish your goals, obligations, scope, and boundaries.

    Assess your current state and define a target state.

    Develop and prioritize gap initiatives.

    Define the cost, effort, alignment, and security benefits of each initiative.

    Develop a security strategy operational roadmap.

    Activities

    2.1 Assess your current security goals, obligations, and scope.

    2.2 Design your ideal target state.

    2.3 Prioritize gap initiatives.

    Outputs

    Information Security Strategy Requirements Gathering Tool

    Security Operations Maturity Assessment Tool

    3 Define Operational Interdependencies

    The Purpose

    Identify opportunities for collaboration.

    Formalize your operational process flows.

    Develop a comprehensive and actionable measurement program.

    Key Benefits Achieved

    Understand the current security operations process flow.

    Define the security operations stakeholders and their respective deliverables.

    Formalize an internal information-sharing and collaboration plan.

    Activities

    3.1 Identify opportunities for collaboration.

    3.2 Formalize a security operations collaboration plan.

    3.3 Define operational roles and responsibilities.

    3.4 Develop a comprehensive measurement program.

    Outputs

    Security Operations RACI & Program Plan Tool

    Security Operations Collaboration Plan

    Security Operations Cadence Schedule Template

    Security Operations Metrics Summary

    Further reading

    INFO-TECH RESEARCH GROUP

    Develop a Security Operations Strategy

    Transition from a security operations center to a threat collaboration environment.

    Info-Tech Research Group, Inc. is a global leader in providing IT research and advice. Info-Tech’s products and services combine actionable insight and relevant advice with ready-to-use tools and templates that cover the full spectrum of IT concerns.
    © 1997-2017 Info-Tech Research Group Inc.

    ANALYST PERSPECTIVE

    “A reactive security operations program is no longer an option. The increasing sophistication of threats demands a streamlined yet adaptable mitigation and remediation process. Protect your assets by preparing for the inevitable; unify your prevention, detection, analysis, and response efforts and provide assurance to your stakeholders that you are making information security a top priority.”

    Phot of Edward Gray, Consulting Analyst, Security, Risk & Compliance, Info-Tech Research Group.

    Edward Gray,
    Consulting Analyst, Security, Risk & Compliance
    Info-Tech Research Group


    Our understanding of the problem

    This Research Is Designed For:
    • Chief Information Officer (CIO)
    • Chief Information Security Officer (CISO)
    • Chief Operating Officer (COO)
    • Security / IT Management
    • Security Operations Director / Security Operations Center (SOC)
    • Network Operations Director / Network Operations Center (NOC)
    • Systems Administrator
    • Threat Intelligence Staff
    • Security Operations Staff
    • Security Incident Responders
    • Vulnerability Management Staff
    • Patch Management
    This Research Will Help You:
    • Enhance your security program by implementing and streamlining next-generation security operations processes.
    • Increase organizational situational awareness through active collaboration between core threat teams, enriching internal security events with external threat intelligence and enhancing security controls.
    • Develop a comprehensive threat analysis and dissemination process: align people, process, and technology to scale security to threats.
    • Identify the appropriate technological and infrastructure-based sourcing decisions.
    • Design a step-by-step security operations implementation process.
    • Pursue continuous improvement: build a measurement program that actively evaluates program effectiveness.
    This Research Will Also Assist:
    • Board / Chief Executive Officer
    • Information Owners (Business Directors/VP)
    • Security Governance and Risk Management
    • Fraud Operations
    • Human Resources
    • Legal and Public Relations
    This Research Will Help Them
    • Aid decision making by staying abreast of cyberthreats that could impact the business.
    • Increase visibility into the organization’s threat landscape to identify likely targets or identify exposed vulnerabilities.
    • Ensure the business is compliant with regularity, legal, and/or compliance requirements.
    • Understand the value and return on investment of security operations offerings.

    Executive summary

    Situation

    • Current security practices are disjointed, operating independently with a wide variety of processes and tools to conduct incident response, network defense, and threat analysis. These disparate mitigations leave organizations vulnerable to the increasing number of malicious events.
    • Threat management has become resource intensive, requiring continuous monitoring, collection, and analysis of massive volumes of security event data, while juggling business, compliance, and consumer obligations.

    Complication

    • There is an onslaught of security data – generating information in different formats, storing it in different places, and forwarding it to different locations.
    • The organization lacks a dedicated enterprise security team. There is limited resourcing available to begin or mature a security operations center.
    • Many organizations are developing ad hoc security capabilities that result in operational inefficiencies, the misalignment of resources, and the misuse of their security technology investments.
    • It is difficult to communicate the value of a security operations program when trying to secure organizational buy-in to gain the appropriate resourcing.
    • There is limited communication between security functions due to a centralized security operations organizational structure.

    Resolution

    • A unified security operations process actively transforms security events and threat information into actionable intelligence, driving security prevention, detection, analysis, and response processes, addressing the increasing sophistication of cyberthreats, and guiding continuous improvement.
    • This blueprint will walk through the steps of developing a flexible and systematic security operations program relevant to your organization.

    Info-Tech Insight

    1. Security operations is no longer a center, but a process. The need for a physical security hub has evolved into the virtual fusion of prevention, detection, analysis, and response efforts. When all four functions operate as a unified process, your organization will be able to proactively combat changes in the threat landscape.
    2. Functional threat intelligence is a prerequisite for effective security operations – without it, security operations will be inefficient and redundant. Eliminate false positives by contextualizing threat data, aligning intelligence with business objectives, and building processes to satisfy those objectives.
    3. If you are not communicating, you are not secure. Collaboration eliminates siloed decisions by connecting people, processes, and technologies. You leave less room for error, consume fewer resources, and improve operational efficiency with a transparent security operations process.

    Data breaches are resulting in major costs across industries

    Horizontal bar chart of 'Per capita cost by industry classification of benchmarked companies', with the highest cost attributed to 'Health', 'Pharmaceutical', 'Financial', 'Energy', and 'Transportation'.

    Average data breach costs per compromised record hit an all-time high of $217 (in 2015); $74 is direct cost (e.g. legal fees, technology investment) and $143 is indirect cost (e.g. abnormal customer churn). (Source: Ponemon Institute, “2015 Cost of Data Breach Study: United States”)

    '% of systems impacted by a data breach', '1% No Impact', '19% 1-10% impacted', '41% 11-30% impacted', '24% 31-50% impacted', '15% more than 50% impacted
    Divider line.
    '% of customers lost from a data breach', '61% Lost <20%', '21% Lost 20-40%', '8% Lost 40-60%', '6% Lost 60-80%', '4% Lost 80-100%'.
    Divider line.
    '% of business opportunity lost from a data breach', '58% Lost <20%', '25% Lost 20-40%', '9% Lost, 40-60%', '5% Lost 60-80%', '4% Lost 80-100%'.
    (Source: The Network, “ Cisco 2017 Security Capabilities Benchmark Study”)

    Persistent issues

    • Organizational barriers separating prevention, detection, analysis, and response efforts.
      Siloed operations limit collaboration and internal knowledge sharing.
    • Lack of knowledgeable security staff.
      Human capital is transferrable between roles and functions and must be cross-trained to wear multiple hats.
    • Failure to evaluate and improve security operations.
      The effectiveness of operations must be frequently measured and (re)assessed through an iterative system of continuous improvement.
    • Lack of standardization.
      Pre-established use cases and policies outlining tier-1 operational efforts will eliminate ad hoc remediation efforts and streamline operations.
    • Failure to acknowledge the auditor as a customer.
      Many compliance and regulatory obligations require organizations to have comprehensive documentation of their security operations practices.

    60% Of organizations say security operation teams have little understanding of each other’s requirements.

    40% Of executives report that poor coordination leads to excessive labor and IT operational costs.

    38-100% Increase in efficiency after closing operational gaps with collaboration.
    (Source: Forbes, “The Game Plan for Closing the SecOps Gap”)

    The solution

    Bar chart of the 'Benefits of Internal Collaboration' with 'Increased Operational Efficiency' and 'Increased Problem Solving' having the highest percentage.

    “Empower a few administrators with the best information to enable fast, automated responses.”
    – Ismael Valenzuela, IR/Forensics Technical Practice Manager, Foundstone® Services, Intel Security)

    Insufficient security personnel resourcing has been identified as the most prevalent challenge in security operations…

    When an emergency security incident strikes, weak collaboration and poor coordination among critical business functions will magnify inefficiencies in the incident response (IR) process, impacting the organization’s ability to minimize damage and downtime.

    The solution: optimize your SOC. Info-Tech has seen SOCs with five analysts outperform SOCs with 25 analysts through tools and process optimization.

    Sources:
    Ponemon. "2016 State of Cybersecurity in Small & Medium-Sized Businesses (SMB).”
    Syngress. Designing and Building a Security Operations Center.

    Maintain a holistic security operations program

    Legacy security operations centers (SOCs) fail to address gaps between data sources, network controls, and human capital. There is limited visibility and collaboration between departments, resulting in siloed decisions that do not support the best interests of the organization.
    Venn diagram of 'Next-Gen Security Operations' with four intersecting circles: 'Prevent', 'Detect', 'Analyze', and 'Respond'.

    Security operations is part of what Info-Tech calls a threat collaboration environment, where members must actively collaborate to address cyberthreats affecting the organization’s brand, business operations, and technology infrastructure on a daily basis.

    Prevent: Defense in depth is the best approach to protect against unknown and unpredictable attacks. Diligent patching and vulnerability management, endpoint protection, and strong human-centric security (amongst other tactics) are essential. Detect: There are two types of companies – those who have been breached and know it and those who have been breached and don’t know it. Ensure that monitoring, logging, and event detection tools are in place and appropriate to your organizational needs
    Analyze: Raw data without interpretation cannot improve security and is a waste of time, money, and effort. Establish a tiered operational process that not only enriches data but also provides visibility into your threat landscape. Respond: Organizations can’t rely on an ad hoc response anymore – don’t wait until a state of panic. Formalize your response processes in a detailed incident runbook in order to reduce incident remediation time and effort.

    Info-Tech’s security operations blueprint ties together various initiatives

    Stock image 1.

    Design and Implement a Vulnerability Management Program

    Vulnerability Management
    Vulnerability management revolves around the identification, prioritization, and remediation of vulnerabilities. Vulnerability management teams hunt to identify which vulnerabilities need patching and remediating.
    Deliverables
    • Vulnerability Tracking Tool
    • Vulnerability Scanning Tool RFP Template
    • Penetration Test RFP Template
    • Vulnerability Mitigation Process Template
    Stock image 2.

    Integrate Threat Intelligence Into Your Security Operations

    Threat Intelligence
    Threat intelligence addresses the collection, analysis, and dissemination of external threat data. Analysts act as liaisons to their peers, publishing actionable threat alerts, reports, and briefings. Threat intelligence proactively monitors and identifies whether threat indicators are impacting your organization.
    • Maturity Assessment Tool
    • Threat Intelligence RACI Tool
    • Management Plan Template
    • Threat Intelligence Policy Template
    • Alert Template
    • Alert and Briefing Cadence Schedule
    Stock image 3.

    Develop Foundational Security Operations Processes

    Operations
    Security operations include the real-time monitoring and analysis of events based on the correlation of internal and external data sources. This also includes incident escalation based on impact. Analysts are constantly tuning and tweaking rules and reporting thresholds to further help identify which indicators are most impactful during the analysis phase of operations.
    • Maturity Assessment Tool
    • Event Prioritization Tool
    • Efficiency Calculator
    • SecOps Policy Template
    • In-House vs. Outsourcing Decision-Making Tool
    • SecOps RACI Tool
    • TCO & ROI Comparison Calculator
    Stock image 4.

    Develop and Implement a Security Incident Management Program

    Incident Response
    Effective and efficient management of incidents involves a formal process of analysis, containment, eradication, recovery, and post-incident activities. IR teams coordinate root-cause analysis and incident gathering while facilitating post-incident lessons learned. Incident response can provide valuable threat data that ties specific indicators to threat actors or campaigns.
    • Incident Management Policy
    • Maturity Assessment Tool
    • Incident Management RACI Tool
    • Incident Management Plan
    • Incident Runbook Prioritization Tool
    • Various Incident Management Runbooks

    This blueprint will…

    …better protect your organization with an interdependent and collaborative security operations program.

    Phase 01

    Assess your operational requirements.

    Phase 02

    Optimize and further mature your security operations processes

    Phase 3a

    Develop the process flow and specific interaction points between functions

    Phase 3b

    Test your current capabilities with a table top exercise
    Briefly assess your current prevention, detection, analysis, and response capabilities.
    Highlight operational weak spots that should be addressed before progressing.
    Develop a prioritized list of security-focused operational initiatives.
    Conduct a holistic analysis of your operational capabilities.
    Define the operational interaction points between security-focused operational departments.
    Document the results in comprehensive operational interaction agreement.
    Test your operational processes with Info-Tech’s security operations table-top exercise.

    Info-Tech integrates several best practices to create a best-of-breed security framework

    Legend for the 'Information Security Framework' identifying blue best practices as 'In Scope' and white best practices as 'Out of Scope'. Info-Tech's 'Information Security Framework' of best practices with two main categories 'Governance' and 'Management', each with subcategories such as 'Context & Leadership' and 'Prevention', each with a group of best practices color-coded to the associated legend identifying them as 'In Scope' or 'Out of Scope'.

    Benefits of a collaborative and integrated operations program

    Effective security operations management will help you do the following:

    • Improve efficacy
      Develop structured processes to automate activities and increase process consistency across the security program. Expose operational weak points and transition teams from firefighting to an innovator role.
    • Improve threat protection
      Enhance network controls through the hardening of perimeter defenses, an intelligence-driven analysis process, and a streamlined incident remediation process.
    • Improve visibility and information sharing
      Promote both internal and external information sharing to enable good decision making.
    • Create and clarify accountability and responsibility
      Security operations management practices will set a clear level of accountability throughout the security program and ensure role responsibility for all tasks and processes involved in service delivery.
    • Control security costs
      Security operations management is concerned with delivering promised services in the most efficient way possible. Good security operations management practices will provide insight into current costs across the organization and present opportunities for cost savings.
    • Identify opportunities for continuous improvement
      Increased visibility into current performance levels and the ability to accurately identify opportunities for continuous improvement.

    Impact

    Short term:

    • Streamlined security operations program development process.
    • Completed comprehensive list of operational gaps and initiatives.
    • Formalized and structured implementation process.
    • Standardized operational use cases that predefine necessary operational protocol.

    Long term:

    • Enhanced visibility into immediate threat environment.
    • Improved effectiveness of internal defensive controls.
    • Increased operational collaboration between prevention, detection, analysis, and response efforts.
    • Enhanced security pressure posture.
    • Improved communication with executives about relevant security risks to the business.

    Understand the cost of not having a suitable security operations program

    A practical approach, justifying the value of security operations, is to identify the assets at risk and calculate the cost to the company should the information assets be compromised (i.e. assess the damage an attacker could do to the business).

    Cost Structure Cost Estimation ($) for SMB
    (Small and medium-sized business)
    Cost Estimation ($) for LE
    (Large enterprise)
    Security controls Technology investment: software, hardware, facility, maintenance, etc.
    Cost of process implementation: incident response, CMBD, problem management, etc.
    Cost of resource: salary, training, recruiting, etc.
    $0-300K/year $200K-2M/year
    Security incidents
    (if no security control is in place)
    Explicit cost:
    1. Incident response cost:
      • Remediation costs
      • Productivity: (number of employees impacted) × (hours out) × (burdened hourly rate)
      • Extra professional services
      • Equipment rental, travel expenses, etc.
      • Compliance fine
      • Cost of notifying clients
    2. Revenue loss: direct loss, the impact of permanent loss of data, lost future revenues
    3. Financial performance: credit rating, stock price
      Hidden cost:
      • Reputation, customer loyalty, etc.
    $15K-650K/year $270K-11M/year

    Workshop Overview

    Contact your account representative or email Workshops@InfoTech.com for more information.

    Workshop Day 1 Workshop Day 2 Workshop Day 3 Workshop Day 4 Workshop Day 5
    Activities
    • Kick-off and introductions.
    • High-level overview of weekly activities and outcomes.
    • Activity: Define workshop objectives and current state of knowledge.
    • Understand the threat collaboration environment.
    • Understand the benefits of an optimized security operations.
    • Activity: Review preliminary maturity level.
    • Activity: Assess current people, processes, and technology capabilities.
    • Activity: Assess workflow capabilities.
    • Activity: Begin deep-dive into maturity assessment tool.
    • Discuss strategies to enhance the analysis process (ticketing, automation, visualization, use cases, etc.).
    • Activity: Design ideal target state.
    • Activity: Identify security gaps.
    • Build initiatives to bridge the gaps.
    • Activity: Estimate the resources needed.
    • Activity: Prioritize gap initiatives.
    • Activity: Develop dashboarding and visualization metrics.
    • Activity: Plan for a transition with the security roadmap and action plan.
    • Activity: Define and assign tier 1, 2 & 3 SOC roles and responsibilities.
    • Activity: Assign roles and responsibilities for each security operations initiative.
    • Activity: Develop a comprehensive measurement program.
    • Activity: Develop specific runbooks for your top-priority incidents (e.g. ransomware).
      • Detect the incident.
      • Analyze the incident.
      • Contain the incident.
      • Eradicate the root cause.
      • Recover from the incident.
      • Conduct post-incident analysis and communication.
    • Activity:Conduct attack campaign simulation.
    • Finalize main deliverables.
    • Schedule feedback call.
    Deliverables
    1. Security Operations Maturity Assessment Tool
    1. Target State and Gap Analysis (Security Operations Maturity Assessment Tool)
    1. Security Operations Role & Process Design
    2. Security Operations RACI Chart
    3. Security Operations Metrics Summary
    4. Security Operations Phishing Process Runbook
    5. Attack Campaign Simulation PowerPoint

    All Final Deliverables

    Develop a Security Operations Strategy

    PHASE 1

    Assess Operational Requirements

    1

    Assess Operational Requirements

    2

    Develop Maturity Initiatives

    3

    Define Interdependencies

    This step will walk you through the following activities:

    • Determine why you need a sound security operations program.
    • Understand Info-Tech’s threat collaboration environment.
    • Evaluate your current security operation’s functions and capabilities.

    Outcomes of this step

    • A defined scope and motive for completing this project.
    • Insight into your current security operations capabilities.
    • A prioritized list of security operations initiatives based on maturity level.

    Info-Tech Insight

    Security operations is no longer a center, but a process. The need for a physical security hub has evolved into the virtual fusion of prevention, detection, analysis, and response efforts. When all four functions operate as a unified process, your organization will be able to proactively combat changes in the threat landscape.

    Warm-up exercise: Why build a security operations program?

    Estimated time to completion: 30 minutes

    Discussion: Why are we pursuing this project?

    What are the objectives for optimizing and developing sound security operations?

    Stakeholders Required:

    • Key business executives
    • IT leaders
    • Security operations team members

    Resources Required

    • Sticky notes
    • Whiteboard
    • Dry-erase markers
    1. Briefly define the scope of security operations
      What people, processes, and technology fall within the security operations umbrella?
    2. Brainstorm the implications of not acting
      What does the status quo have in store? What are the potential risks?
    3. Define the goals of the project
      Clarify from the outset: what exactly do you want to accomplish from this project?
    4. Prioritize all brainstormed goals
      Classify the goals based on relevant prioritization criteria, e.g. urgency, impact, cost.

    Info-Tech Best Practice

    Don’t develop a security operations program with the objective of zero incidents. This reliance on prevention results in over-engineered security solutions that cost more than the assets being protected.

    Decentralizing the SOC: Security as a function

    Before you begin, remember that no two security operation programs are the same. While the end goal may be similar, the threat landscape, risk tolerance, and organizational requirements will differ from any other SOC. Determine what your DNA looks like before you begin to protect it.

    Security operations must provide several fundamental functions:
    • Real-time monitoring, detecting, and triaging of data from both internal and external sources.
    • In-depth analysis of indicators and incidents, leveraging malware analysis, correlation and rule tweaking, and forensics and eDiscovery techniques.
    • Network/host scanning and vulnerability patch management.
    • Incident response, remediation, and reporting. Security operations must disseminate appropriate information/intelligence to relevant stakeholders.
    • Comprehensive logging and ticketing capabilities that document and communicate events throughout the threat collaboration environment.
    • Tuning and tweaking of technologies to ingest collected data and enhance the analysis process.
    • Enhance overall organizational situational awareness by reporting on security trends, escalating incidents, and sharing adversary tools, tactics, and procedures.
    Venn diagram of 'Security Operations' with four intersecting circles: 'Prevent', 'Detect', 'Analyze', and 'Respond'.
    At its core, a security operations program is responsible for the prevention, detection, analysis, and response of security events.

    Optimized security operations can seamlessly integrate threat and incident management processes with monitoring and compliance workflows and resources. This integration unlocks efficiency.

    Understand the levels of security operations

    Take the time to map out what you need and where you should go. Security operations has to be more than just monitoring events – there must be a structured program.

    Foundational Arrow with a plus sign pointing right. Operational Arrow with a plus sign pointing right. Strategic
    • Intrusion Detection Management
    • Active Device and Event Monitoring
    • Log Collection and Retention
    • Reporting and Escalation Management
    • Incident Management
    • Audit Compliance
    • Vendor Management
    • Ticketing Processes
    • Packet Capture and Analysis
    • SIEM
    • Firewall
    • Antivirus
    • Patch Management
    • Event Analysis and Incident Triage
    • Security Log Management
    • Vulnerability Management
    • Host Hardening
    • Static Malware Analysis
    • Identity and Access Management
    • Change Management
    • Endpoint Management
    • Business Continuity Management
    • Encryption Management
    • Cloud Security (if applicable)
    • SIEM with Defined Use Cases
    • Big Data Security Analytics
    • Threat Intelligence
    • Network Flow Analysis
    • VPN Anomaly Detection
    • Dynamic Malware Analysis
    • Use-Case Management
    • Feedback and Continuous Improvement Management
    • Visualization and Dashboarding
    • Knowledge Portal Ticket Documentation
    • Advanced Threat Hunting
    • Control and Process Automation
    • eDiscovery and Forensics
    • Risk Management
    ——Security Operations Capabilities—–›

    Understand security operations: Establish a unified threat collaboration environment

    Stock image 1.

    Design and Implement a Vulnerability Management Program

    Security operations is part of what Info-Tech calls a threat collaboration environment, where members must actively collaborate to address threats impacting the organization’s brand, operations, and technology infrastructure.
    • Managing incident escalation and response.
    • Coordinating root-cause analysis and incident gathering.
    • Facilitating post-incident lessons learned.
    • Managing system patching and risk acceptance.
    • Conducting vulnerability assessment and penetration testing.
    • Monitoring in real-time and triaging of events.
    • Escalating events to incident management team.
    • Tuning and tweaking rules and reporting thresholds.
    • Gathering and analyzing external threat data.
    • Liaising with peers, industry, and government.
    • Publishing threat alerts, reports, and briefings.

    Info-Tech Best Practice

    Ensure that information flows freely throughout the threat collaboration environment – each function should serve to feed and enhance the next.

    Stock image 2.

    Integrate Threat Intelligence Into Your Security Operations

    Stock image 3.

    Develop Foundational Security Operations Processes

    Stock image 4.

    Develop and Implement a Security Incident Management Program

    The threat collaboration environment is comprised of three core elements

    Info-Tech Insight

    The value of a SOC can be achieved with fewer prerequisites than you think. While it is difficult to cut back on process and technology requirements, human capital is transferrable between roles and functions and can be cross-trained to satisfy operational gaps.

    Three hexes fitting together with the words 'People', 'Process', and 'Technology'. People. Effective human capital is fundamental to establishing an efficient security operations program, and if enabled correctly, can be the driving factor behind successful process optimization. Ensure you address several critical human capital components:
    • Who is responsible for each respective threat collaboration environment function?
    • What are the required operational roles, responsibilities, and competencies for each employee?
    • Are there formalized training procedures to onboard new employees?
    • Is there an established knowledge transfer and management program?
    Processes. Formal and informal mechanisms that bridge security throughout the collaboration environment and organization at large. Ask yourself:
    • Are there defined runbooks that clearly outline critical operational procedures and guidelines?
    • Is there a defined escalation protocol to transfer knowledge and share threats internally?
    • Is there a defined reporting procedure to share intelligence externally?
    • Are there formal and accessible policies for each respective security operations function?
    • Is there a defined measurement program to report on the performance of security operations?
    • Is there a continuous improvement program in place for all security operations functions?
    • Is there a defined operational vendor management program?
    Technology. The composition of all infrastructure, systems, controls, and tools that enable processes and people to operate and collaborate more efficiently. Determine:
    • Are the appropriate controls implemented to effectively prevent, detect, analyze, and remediate threats? Is each control documented with an assigned asset owner?
    • Can a solution integrate with existing controls? If so, to what extent?
    • Is there a centralized log aggregation tool such as a SIEM?
    • What is the operational cost to effectively manage each control?
    • Is the control the most up-to-date version? Have the most recent patches and configuration changes been applied? Can it be consolidated with or replaced by another control?

    Conduct a preliminary maturity assessment before tackling this project

    Stock image 1.

    Design and Implement a Vulnerability Management Program

    Sample of Info-Tech's Security Operations Preliminary Maturity Assessment

    At a high level, assess your organization’s operational maturity in each of the threat collaboration environment functions. Determine whether the foundational processes exist in order to mature and streamline your security operations.

    Stock image 2.

    Integrate Threat Intelligence Into Your Security Operations

    Stock image 3.

    Develop Foundational Security Operations Processes

    Stock image 4.

    Develop and Implement a Security Incident Management Program

    Assess the current maturity of your security operations program

    Prioritize the component most important to the development of your security operations program.

    Screenshot of a table from the Security Operations Preliminary Maturity Assessment presenting the 'Impact Sub-Weightings' of 'People', 'Process', 'Technology', and 'Policy'.
    Screenshot of a table from the Security Operations Preliminary Maturity Assessment assessing the 'Current State' and 'Target State' of different 'Security Capabilities'.
    Each “security capability” covers a component of the overarching “security function.” Assign a current and target maturity score to each respective security capability. (Note: The CMMI maturity scores are further explained on the following slide.) Document any/all comments for future Info-Tech analyst discussions.

    Assign each security capability a reflective and desired maturity score.

    Your current and target state maturity will be determined using the capability maturity model integration (CMMI) scale. Ensure that all participants understand the 1-5 scale.
    Two-way vertical arrow colored blue at the top and green at the bottom. Ad Hoc
    1 Arrow pointing right. Initial/Ad Hoc: Activity is not well defined and is ad hoc, e.g. no formal roles or responsibilities exist, de facto standards are followed on an individual-by-individual basis.
    2 Arrow pointing right. Developing: Activity is established and there is moderate adherence to its execution, e.g. while no formal policies have been documented, content management is occurring implicitly or on an individual-by-individual basis.
    3 Arrow pointing right. Defined: Activity is formally established, documented, repeatable, and integrated with other phases of the process, e.g. roles and responsibilities have been defined and documented in an accessible policy, however, metrics are not actively monitored and managed.
    4 Arrow pointing right. Managed and Measurable: Activity execution is tracked by gathering qualitative and quantitative feedback, e.g. metrics have been established to monitor the effectiveness of tier-1 SOC analysts.
    5 Arrow pointing right. Optimized: Qualitative and quantitative feedback is used to continually improve the execution of the activity, e.g. the organization is an industry leader in the respective field; research and development efforts are allocated in order to continuously explore more efficient methods of accomplishing the task at hand.
    Optimized

    Notes: Info-Tech seldom sees a client achieve a CMMI score of 4 or 5. To achieve a state of optimization there must be a subsequent trade-off elsewhere. As such, we recommend that organizations strive for a CMMI score of 3 or 4.

    Ensure that your threat collaboration environment is of a sufficient maturity before progressing

    Example report card from the maturity assessment. Functions are color-coded green, yellow, and red. Review the report cards for each of the respective threat collaboration environment functions.
    • A green function indicates that you have exceeded the operational requirements to proceed with the security operations initiative.
    • A yellow function indicates that your maturity score is below the recommended threshold; Info-Tech advises revisiting the attached blueprint. In the instance of a one-off case, the client can proceed with this security operations initiative.
    • A red function indicates that your maturity score is well below the recommended threshold; Info-Tech strongly advises to not proceed with the security operations initiative. Revisit the recommended blueprint and further mature the specific function.

    Are you ready to move on to the next phase?

    Self-Assessment Questions

    • Have you clearly defined the rationale for refining your security operations program?
    • Have you clearly defined and prioritized the goals and outcomes of optimizing your security operations program?
    • Have you assessed your respective people, process, and technological capabilities?
    • Have you completed the Security Operations Preliminary Maturity Assessment Tool?
    • Were all threat collaboration environment functions of a sufficient maturity level?

    If you answered “yes” to the questions, then you are ready to move on to Phase 2: Develop Maturity Initiatives

    Develop a Security Operations Strategy

    PHASE 2

    Develop Maturity Initiatives

    1

    Assess Operational Requirements

    2

    Develop Maturity Initiatives

    3

    Define Interdependencies

    This step will walk you through the following activities:

    • Establish your goals, obligations, scope, and boundaries.
    • Assess your current state and define a target state.
    • Develop and prioritize gap initiatives.
    • Define cost, effort, alignment, and security benefit of each initiative.
    • Develop a security strategy operational roadmap.

    Outcomes of this step

    • A formalized understanding of your business, customer, and regulatory obligations.
    • A comprehensive current and target state assessment.
    • A succinct and consolidated list of gap initiatives that will collectively achieve your target state.
    • A formally documented set of estimated priority variables (cost, effort, business alignment).
    • A fully prioritized security roadmap that is in alignment with business goals and informed by the organization’s needs and limitations.

    Info-Tech Insight

    Functional threat intelligence is a prerequisite for effective security operations – without it, security operations will be inefficient and redundant. Eliminate false positives by contextualizing threat data, aligning intelligence with business objectives, and building processes to satisfy those objectives

    Align your security operations program with corporate goals and obligations

    A common challenge for security leaders is learning to express their initiatives in terms that are meaningful to business executives.

    Frame the importance of your security operations program to
    align with that of the decision makers’ over-arching strategy.

    Oftentimes resourcing and funding is dependent on the
    alignment of security initiatives to business objectives.

    Corporate goals and objectives can be categorized into three major buckets:
    1. BUSINESS OBLIGATIONS
      The primary goals and functions of the organization at large. Examples include customer retention, growth, innovation, customer experience, etc.
    2. CONSUMER OBLIGATIONS
      The needs and demands of internal and external stakeholders. Examples include ease of use (external), data protection (external), offsite access (internal), etc.
    3. COMPLIANCE OBLIGATIONS
      The requirements of the organization to comply with mandatory and/or voluntary standards. Examples include HIPAA, PIPEDA, ISO 27001, etc.
    *Do not approach the above list with a security mindset – take a business perspective and align your security efforts accordingly.

    Info-Tech Best Practice

    Developing a security operations strategy is a proactive activity that enables you to get in front of any upcoming business projects or industry trends rather than having to respond reactively later on. Consider as many foreseeable variables as possible!

    Determine your security operations program scope and boundaries

    It is important to define all security-related areas of responsibility. Upon completion you should clearly understand what you are trying to secure.

    Ask yourself:
    Where does the onus of responsibility stop?

    The organizational scope and boundaries and can be categorized into four major buckets:
    1. PHYSICAL SCOPE
      The physical locations that the security operations program is responsible for. Examples include office locations, remote access, clients/vendors, etc.
    2. IT SYSTEMS
      The network systems that must be protected by the security operations program. Examples include fully owned systems, IaaS, PaaS, remotely hosted SaaS, etc.
    3. ORGANIZATIONAL SCOPE
      The business units, departments, or divisions that will be affected by the security operations program. Examples include user groups, departments, subsidiaries, etc.
    4. DATA SCOPE
      The data types that the business handles and the privacy/criticality level of each. Examples include top secret, confidential, private, public, etc.

    This also includes what is not within scope. For some outsourced services or locations you may not be responsible for security. For some business departments you may not have control of security processes. Ensure that it is made explicit at the outset, what will be included and what will be excluded from security considerations.

    Reference Info-Tech’s security strategy: goals, obligations, and scope activities

    Explicitly understanding how security aligns with the core business mission is critical for having a strategic plan and fulfilling the role of business enabler.

    Download and complete the information security goals, obligations and scope activities (Section 1.3) within the Info-Tech security strategy research publication. If previously completed, take the time to review your results.

    GOALS and OBLIGATIONS
    Proceed through each slide and brainstorm the ways that security operations supports business, customer, and compliance needs.

    Goals & Obligations
    Screenshots of slides from the information security goals, obligations and scope activities (Section 1.3) within the Info-Tech security strategy research publication.

    PROGRAM SCOPE & BOUNDARIES
    Assess your current organizational environment. Document current IT systems, critical data, physical environments, and departmental divisions.

    If a well-defined corporate strategy does not exist, these questions can help pinpoint objectives:

    • What is the message being delivered by the CEO?
    • What are the main themes of investments and projects?
    • What are the senior leaders measured on?
    Program Scope & Boundaries
    Screenshots of slides from the information security goals, obligations and scope activities (Section 1.3) within the Info-Tech security strategy research publication.

    INFO-TECH OPPORTUNITY

    For more information on how to complete the goals & obligations activity please reference Section 1.3 of Info-Tech’s Build an Information Security Strategy blueprint.

    Complete the Information Security Requirements Gathering Tool

    On tab 1. Goals and Obligations:
    • Document all business, customer, and compliance obligations. Ensure that each item is reflective of the over-arching business strategy and is not security focused.
    • In the second column, identify the corresponding security initiative that supports the obligation.
    Screenshot from tab 1 of Info-Tech's Information Security Requirements Gathering Tool. Columns are 'Business obligations', 'Security obligations to support the business (optional)', and 'Notes'.
    On tab 2. Scope and Boundaries:
    • Record all details for what is in and out of scope from physical, IT, organizational, and data perspectives.
    • Complete the affiliated columns for a comprehensive scope assessment.
    • As a discussion guide, refer to the considerations slides prior to this in phase 1.3.
    Screenshot from tab 2 of Info-Tech's Information Security Requirements Gathering Tool. Title is 'Physical Scope', Columns are 'Environment Name', 'Highest data criticality here', 'Is this in scope of the security strategy?', 'Are we accountable for security here?', and 'Notes'.
    For the purpose of this security operations initiative please IGNORE the risk tolerance activities on tab 3.

    Info-Tech Best Practice

    A common challenge for security leaders is expressing their initiatives in terms that are meaningful to business executives. This exercise helps make explicit the link between what the business cares about and what security is trying to do.

    Conduct a comprehensive security operations maturity assessment

    The following slides will walk you through the process below.

    Define your current and target state

    Self-assess your current security operations capabilities and determine your intended state.

    Create your gap initiatives

    Determine the operational processes that must be completed in order to achieve the target state.

    Prioritize your initiatives

    Define your prioritization criteria (cost, effort, alignment, security benefit) based on your organization

    Build a Gantt chart for your upcoming initiatives
    The final output will be a Gantt to action your prioritized initiatives

    Info-Tech Insight

    Progressive improvements provide the most value to IT and your organization. Leaping from pre-foundation to complete optimization is an ineffective goal. Systematic improvements to your security performance delivers value to your organization, each step along the way.

    Optimize your security operations workflow

    Info-Tech consulted various industry experts and consolidated their optimization advice.

    Dashboards: Centralized visibility, threat analytics, and orchestration enable faster threat detection with fewer resources.

    Adding more controls to a network never increases resiliency. Identify technological overlaps and eliminate unnecessary costs.

    Automation: There is shortfall in human capital in contrast to the required tools and processes. Automate the more trivial processes.

    SOCs with 900 employees are just as efficient as those with 35-40. There is an evident tipping point in marginal value.

    There are no plug-and-play technological solutions – each is accompanied by a growing pain and an affiliated human capital cost.

    Planning: Narrow the scope of operations to focus on protecting assets of value.

    Cross-train employees throughout different silos. Enable them to wear multiple hats.

    Practice: None of the processes happen in a vacuum. Make the most of tabletop exercises and other training exercises.

    Define appropriate use cases and explicitly state threat escalation protocol. Focus on automating the tier-1 analyst role.

    Self-assess your current-state capabilities and determine the appropriate target state

    1. Review:
    The heading in blue is the security domain, light blue is the subdomain and white is the specific control.
    2. Determine and Record:
    Ask participants to identify your organization’s current maturity level for each control. Next, determine a target maturity level that meets the requirements of the area (requirements should reflect the goals and obligations defined earlier).
    3.
    In small groups, have participants answer “what is required to achieve the target state?” Not all current/target state gaps will require additional description, explanation, or an associated imitative. You can generate one initiative that may apply to multiple line items.

    Screenshot of a table for assessing the current and target states of capabilities.

    Info-Tech Best Practice

    When customizing your gap initiatives consider your organizational requirements and scope while remaining realistic. Below is an example of lofty vs. realistic initiatives:
    Lofty: Perform thorough, manual security analysis. Realistic: Leverage our SIEM platform to perform more automated security analysis through the use of log information.

    Consolidate related gap initiatives to simplify and streamline your roadmap

    Identify areas of commonality between gap initiative in order to effectively and efficiently implement your new initiatives.

    Steps:
    1. After reviewing and documenting initiatives for each security control, begin sorting controls by commonality, where resources can be shared, or similar end goals and actions. Begin by copying all initiatives from tab 2. Current State Assessment into tab 5. Initiative List of the Security Operations Maturity Assessment Tool and then consolidating them.
    2. Initiatives Consolidated Initiatives
      Document data classification and handling in AUP —› Document data classification and handling in AUP Keep urgent or exceptional initiatives separate so they can be addressed appropriately.
      Document removable media in AUP —› Define and document an Acceptable Use Policy Other similar or related initiatives can be consolidated into one item.
      Document BYOD and mobile devices in AUP —›
      Document company assets in Acceptable Use Policy (AUP) —›

    3. Review grouped initiatives and identify specific initiatives should be broken out and defined separately.
    4. Record your consolidated gap initiatives in the Security Operations Maturity Assessment Tool, tab 6. Initiative Prioritization.

    Understand your organizational maturity gap

    After inputting your current and target scores and defining your gap initiatives in tab 2, review tab 3. Current Maturity and tab 4. Maturity Gap in Info-Tech’s Security Operations Maturity Assessment Tool.

    Automatically built charts and tables provide a clear visualization of your current maturity.

    Presenting these figures to stakeholders and management can help visually draw attention to high-priority areas and contextualize the gap initiatives for which you will be seeking support.

    Screenshot of tabs 3 and 4 from Info-Tech's Security Operations Maturity Assessment Tool. Bar charts titled 'Planning and Direction', 'Vulnerability Management', 'Threat Intelligence', and 'Security Maturity Level Gap Analysis'.

    Info-Tech Best Practice

    Communicate the value of future security projects to stakeholders by copying relevant charts and tables into an executive stakeholder communication presentation (ask an Info-Tech representative for further information).

    Define cost, effort, alignment, and security benefit

    Define low, medium, and high resource allocation, and other variables for your gap initiatives in the Concept of Operations Maturity Assessment Tool. These variables include:
    1. Define initial cost. One-time, upfront capital investments. The low cut-off would be a project that can be approved with little to no oversight. Whereas the high cut-off would be a project that requires a major approval or a formal capital investment request. Initial cost covers items such as appliance cost, installation, project based consulting fees, etc.
    2. Define ongoing cost. This includes any annually recurring operating expenses that are new budgetary costs, e.g. licensing or rental costs. Do not account for FTE employee costs. Generally speaking you can take 20-25% of initial cost as ongoing cost for maintenance and service.
    3. Define initial staffing in hours. This is total time in hours required to complete a project. Note: It is not total elapsed time, but dedicated time. Consider time required to research, document, implement, review, set up, fine tune, etc. Consider all staff hours required (2 staff at 8 hours means 16 hours total).
    4. Define ongoing staffing in hours. This is the ongoing average hours per week required to support that initiative. This covers all operations, maintenance, review, and support for the initiative. Some initiatives will have a week time commitment (e.g. perform a vulnerability scan using our tool once a week) versus others that may have monthly, quarterly, or annual time commitments that need to averaged out per week (e.g. perform annual security review requiring 0.4 hours/week (20 hours total based on 50 working weeks per year).
    Table relating the four definitions on the left, 'Initial Cost', 'Ongoing Cost (annual)', 'Initial Staffing in Hours', and 'Ongoing Staffing in Hours/Week'. Each row header is a definition and has four sub-rows 'High', 'Medium', 'Low', and 'Zero'.

    Info-Tech Best Practice

    When considering these parameters, aim to use already existing resource allocations.

    For example, if there is a dollar value that would require you to seek approval for an expense, this might be the difference between a medium and a high cost category.

    Define cost, effort, alignment, and security benefit

    1. Define Alignment with Business. This variable is meant to capture how well the gap initiative aligns with organizational goals and objectives. For example, something with high alignment usually can be tied to a specific organization initiative and will receive senior management support. You can either:
      • Set low, medium, and high based on levels of support the organization will provide (e.g. High – senior management support, Medium – VP/business unit head support, IT support only)
      • Attribute specific corporate goals or initiatives to the gap initiative (e.g. High – directly supports a customer requirement/key contract requirement; Medium – indirectly support customer requirement/key contract OR enables remote workforce; Low – security best practice).
    2. Define Security Benefit. This variable is meant to capture the relative security benefit or risk reduction being provided by the gap initiative. This can be represented through a variety of factors, such as:
      • Reduces compliance or regulatory risk by meeting a control requirement
      • Reduces availability and operational risk
      • Implements a non-existent control
      • Secures high-criticality data
      • Secures at-risk end users
    Table relating the two definitions on the left, 'Alignment with Business', and 'Security Benefit'. Each row header is a definition and has three sub-rows 'High', 'Medium', and 'Low'.

    Info-Tech Best Practice

    Make sure you consider the value of AND/OR. For either alignment with business or security benefit, the use of AND/OR can become useful thresholds to rank similar importance but different value initiatives.

    Example: with alignment with business, an initiative can indirectly support a key compliance requirement OR meet a key corporate goal.

    Info-Tech Insight

    You cannot do everything – and you probably wouldn’t want to. Make educated decisions about which projects are most important and why.

    Apply your variable criteria to your initiatives

    Identify easy-win tasks and high-value projects worth fighting for.
    Categorize the Initiative
    Select the gap initiative type from the down list. Each category (Must, Should, Could, and Won’t) is considered to be an “execution wave.” There is also a specific order of operations within each wave. Based on dependencies and order of importance, you will execute on some “must-do” items before others.
    Assign Criteria
    For each gap initiative, evaluate it based on your previously defined parameters for each variable.
    • Cost – initial and ongoing
    • Staffing – initial and ongoing
    • Alignment with business
    • Security benefit
    Overall Cost/Effort Rating
    An automatically generated score between 0 and 12. The higher the score attached to the initiative, the more effort required. The must-do, low-scoring items are quick wins and must be prioritized first.
    Screenshot of a table from Info-Tech's Concept of Operations Maturity Assessment Tool with all of the previous table row headers as column headers.

    A financial services organization defined its target security state and created an execution plan

    CASE STUDY
    Industry: Financial Services | Source: Info-Tech Research Group
    Framework Components
    Security Domains & Accompanied Initiatives
    (A portion of completed domains and initiatives)
    CSC began by creating over 100 gap initiatives across Info-Tech’s seven security domains.
    Current-State Assessment Context & Leadership Compliance, Audit & Review Security Prevention
    Gap Initiatives Created 12
    Initiatives
    14
    Initiatives
    45
    Initiatives
    Gap Initiative Prioritization
    Planned Initiative(s)* Initial Cost Ongoing Cost Initial Staffing Ongoing Staffing
    Document Charter Low - ‹$5K Low - ‹$1K Low - ‹1d Low - ‹2 Hour
    Document RACI Low - ‹$5K Low - ‹$1K Low - ‹1d Low - ‹2 Hour
    Expand IR processes Medium - $5K-$50K Low - ‹$1K High - ›2w Low - ‹2 Hour
    Investigate Threat Intel Low - ‹$5K Low - ‹$1K Medium - 1-10d Low - ‹2 Hour
    CSC’s defined low, medium, and high for cost and staffing are specific to the organization.

    CSC then consolidated its initiatives to create less than 60 concise tasks.

    *Initiatives and variables have been changed or modified to maintain anonymity

    Review your prioritized security roadmap

    Review the final Gantt chart to review the expected start and end dates for your security initiatives as part of your roadmap.

    In the Gantt chart, go through each wave in sequence and determine the planned start date and planned duration for each gap initiative. As you populate the planned start dates, take into consideration the resource constraints or dependencies for each project. Go back and revise the granular execution wave to resolve any conflicts you find.

    Screenshot of a 'Gantt Chart for Initiatives', a table with planned and actual start times and durations for each initiative, and beside it a roadmap with the dates from the Gantt chart plugged in.
    Review considerations
    • Does this roadmap make sense for our organization?
    • Do we focus too much on one quarter over others?
    • Will the business be going through any significant changes during the upcoming years that will directly impact this project?
    This is a living management document
    • You can use the same process on a per-case basis to decide where this new project falls in the priority list, and then add it to your Gantt chart.
    • As you make progress, check items off of the list, and periodically use this chart to retroactively update your progress towards achieving your overall target state.

    Consult an Info-Tech Analyst

    To accelerate this project, engage your IT team in an Info-Tech workshop with an Info-Tech analyst team.
    Onsite workshops offer an easy way to accelerate your project. If a Guided Implementation isn’t enough, we offer low-cost onsite delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to successfully complete your project.
    Photo of TJ Minichillo, Senior Director – Security, Risk & Compliance, Info-Tech Research Group. TJ Minichillo
    Senior Director – Security, Risk & Compliance
    Info-Tech Research Group
    Edward Gray, Consulting Analyst – Security, Risk & Compliance, Info-Tech Research Group. Edward Gray
    Consulting Analyst – Security, Risk & Compliance
    Info-Tech Research Group
    Photo of Celine Gravelines, Research Manager – Security, Risk & Compliance, Info-Tech Research Group. Celine Gravelines
    Research Manager – Security, Risk & Compliance
    Info-Tech Research Group
    If you are not communicating, then you are not secure.

    Call 1-888-670-8889 or email workshops@infotech.com for more information.

    Are you ready to move on to the next phase?

    Self-Assessment Questions

    • Have you identified your organization’s corporate goals along with your obligations?
    • Have you defined the scope and boundaries of your security program?
    • Have you determined your organization’s risk tolerance level?
    • Have you considered threat types your organization may face?
    • Are the above answers documented in the Security Requirements Gathering Tool?
    • Have you defined your maturity for both your current and target state?
    • Do you have clearly defined initiatives that would bridge the gap between your current and target state?
    • Are each of the initiatives independent, specific, and relevant to the associated control?
    • Have you indicated any dependencies between your initiatives?
    • Have you consolidated your gap initiatives?
    • Have you defined the parameters for each of the prioritization variables (cost, effort, alignment, and security benefit)?
    • Have you applied prioritization parameters to each consolidated initiative?
    • Have you recorded your final prioritized roadmap in the Gantt chart tab?
    • Have you reviewed your final Gantt chart to ensure it aligns to your security requirements?

    If you answered “yes” to the questions, then you are ready to move on to Phase 3: Define Operational Interdependencies

    Develop a Security Operations Strategy

    PHASE 3

    Define Operational Interdependencies

    1

    Assess Operational Requirements

    2

    Develop Maturity Initiatives

    3

    Define Interdependencies

    This step will walk you through the following activities:

    • Understand the current security operations process flow.
    • Define the security operations stakeholders and their respective deliverables.
    • Formalize an internal information sharing and collaboration plan.

    Outcomes of this step

    • A formalized security operations interaction agreement.
    • A security operations service and product catalog.
    • A structured operations collection plan.

    Info-Tech Insight

    If you are not communicating, you are not secure. Collaboration eliminates siloed decisions by connecting people, processes, and technologies. You leave less room for error, consume fewer resources, and improve operational efficiency with a transparent security operations process.

    Tie everything together with collaboration

    If you are not communicating, you are not secure. Collaboration eliminates siloed decisions by connecting people, processes, and technologies. You leave less room for error, consume fewer resources, and improve operational efficiency with a transparent security operations process.

    Define Strategic Needs and Requirements Participate in Information Sharing Communicate Clearly
    • Establish a channel to communicate management needs and requirements and define important workflow activities. Focus on operationalizing those components.
    • Establish a feedback loop to ensure your actions satisfied management’s criteria.
    • Consolidate critical security data within a centralized portal that is accessible throughout the threat collaboration environment, reducing the human capital resources required to manage that data.
    • Participate in external information sharing groups such as ISACs. Intelligence collaboration allows organizations to band together to decrease risk and protect one another from threat actors.
    • Disseminate relevant information in clear and succinct alerts, reports, or briefings.
    • Security operations analysts must be able to translate important technical security issues and provide in-depth strategic insights.
    • Define your audience before presenting information; various stakeholders will interpret information differently. You must present it in a format that appeals to their interests.
    • Be transparent in your communications. Holding back information will only serve to alienate groups and hinder critical business decisions.

    Info-Tech Best Practice

    Simple collaborative activities, such as a biweekly meeting, can unite prevention, detection, analysis, and response teams to help prevent siloed decision making.

    Understand the security operations process flow

    Process standardization and automation is critical to the effectiveness of security operations.

    Process flow for security operations with column headers 'Monitoring', 'Preliminary Analysis (Tier 1)', 'Triage', 'Investigation & Analysis (Tier 2)', 'Response', and 'Advanced Threat Detection (Tier 3)'. All processes begin with elements in the 'Monitoring' column and end up at 'Visualization & Dashboarding'.

    Document your security operations’ capabilities and tasks

    Table of capabilities and tasks for security operations.
    Document your security operations’ functional capabilities and operational tasks to satisfy each capability. What resources will you leverage to complete the specific task/capability? Identify your internal and external collection sources to satisfy the individual requirement. Identify the affiliated product, service, or output generated from the task/capability. Determine your escalation protocol. Who are the stakeholders you will be sharing this information with?
    Capabilities

    The major responsibilities of a specific function. These are the high-level processes that are expected to be completed by the affiliated employees and/or stakeholders.

    Tasks

    The specific and granular tasks that need to be completed in order to satisfy a portion of or the entire capability.

    Download Info-Tech’s Security Operations RACI Chart & Program Plan.

    Convert your results into actionable process flowcharts

    Map each functional task or capability into a visual process-flow diagram.

    • The title should reflect the respective capability and product output.
    • List all involved stakeholders (inputs and threat escalation protocol) along the left side.
    • Ensure all relevant security control inputs are documented within the body of the process-flow diagram.
    • Map out the respective processes in order to achieve the desired outcome.
    • Segment each process within its own icon and tie that back to the respective input.
    Example of a process flow made with sticky notes.

    Title: Output #1 Example of a process flow diagram with columns 'Stakeholders', 'Input Processes', 'Output Processes', and 'Threat Escalation Protocol'. Processes are mapped by which stakeholder and column they fall to.

    Download Info-Tech’s Security Operations RACI Chart & Program Plan.

    Formalize the opportunities for collaboration within your security operations program

    Security Operations Collaboration Plan

    Security operations provides a single pane of glass through which the threat collaboration environment can manage its operations.

    How to customize

    The security operations interaction agreement identifies opportunities for optimization through collaboration and cross-training. The document is composed of several components:

    • Security operations program scope and objectives
    • Operational capabilities and outputs on a per function basis
    • A needs and requirements collection plan
    • Escalation protocol and respective information-sharing guidance (i.e. a detailed cadence schedule)
    • A security operations RACI chart
    Sample of Info-Tech's Security Operations Collaboration Plan.

    Info-Tech Best Practice

    Understand the operational cut-off points. While collaboration is encouraged, understand when the onus shifts to the rest of the threat collaboration environment.

    Assign responsibilities for the threat management process

    Security Operations RACI Chart & Program Plan

    Formally documenting roles and responsibilities helps to hold those accountable and creates awareness as to everyone’s involvement in various tasks.

    How to customize
    • Customize the header fields with applicable stakeholders.
    • Identify stakeholders that are:
      • Responsible: The person(s) who does the work to accomplish the activity; they have been tasked with completing the activity and/or getting a decision made.
      • Accountable: The person(s) who is accountable for the completion of the activity. Ideally, this is a single person and is often an executive or program sponsor.
      • Consulted: The person(s) who provides information. This is usually several people, typically called subject matter experts (SMEs).
      • Informed: The person(s) who is updated on progress. These are resources that are affected by the outcome of the activities and need to be kept up to date.
    Sample of Info-Tech's Security Operations Collaboration Plan.

    Download Info-Tech’s Security Operations RACI Chart & Program Plan.

    Identify security operations consumers and their respective needs and requirements

    Ensure your security operations program is constantly working toward satisfying a consumer need or requirement.

    Internal Consumers External Consumers
    • Business Executives & Management (CIO, CISO, COO):
      • Inform business decisions regarding threats and their association with future financial risk, reputational risk, and continuity of operations.
    • Human Resources:
      • Security operations must directly work with HR to enforce tight device controls, develop processes, and set expectations.
    • Legal:
      • Security operations is responsible to notify the legal department of data breaches and the appropriate course of action.
    • Audit and Compliance:
      • Work with the auditing department to define additional audits or controls that must be measured.
    • Public Relations/Marketing Employees:
      • Employees must be educated on prevalent threats and how to avoid or mitigate them.

    Note: Your organization might not be the final target, but it could be a primary path for attackers. If you exist as a third-party partner to another organization, your responsibility in your technology ecosystem extends beyond your own product or service offerings.

    • Third-Party Contractors:
      • Identify relevant threats across industries – security operations is responsible for protecting more than just itself.
    • Commercial Vendors:
      • Identify commercial vendors of control failures and opportunities for operational improvement.
    • Suppliers:
      • Provide or maintain a certain level of security delivery.
      • Meet the same level of security that is expected of business units.
    • All End Users:
      • Be notified of any data breaches and potential violations of privacy.

    Info-Tech Best Practice

    “In order to support a healthy constituency, network operations and security operations should be viewed as equal partners, rather than one subordinate to the other.” (Mitre world-class CISO)

    Define the stakeholders, their respective outputs, and the underlying need

    Security Operations Program Service & Product Catalog

    Create an informal security operations program service and product catalog. Work your way backwards – map each deliverable to the respective stakeholders and functions.

    Action/Output Arrow pointing right. Frequency Arrow pointing right. Stakeholders/Function
    Document the key services and outputs produced by the security operations program. For example:
    • Real-time monitoring
    • Event analysis and incident coordination
    • Malware analysis
    • External information sharing
    • Published alerts, reports, and briefings
    • Metrics
    Define the frequency for which each deliverable or service is produced or conducted. Leverage this activity to establish a state of accountability within your threat collaboration environment. Identify the stakeholders or groups affiliated with each output. Remember to include potential MSSPs.
    • Vulnerability Management
    • Threat Intelligence
    • Tier 1, 2, and 3 Analysts
    • Incident Response
    • MSSP
    • Network Operations
    Remember to include any target-state outputs or services identified in the maturity assessment. Use this exercise as an opportunity to organize your security operations outputs and services.

    Info-Tech Best Practice

    Develop a central web/knowledge portal that is easily accessible throughout the threat collaboration environment.

    Internal information sharing helps to focus operational efforts

    Organizations must share information internally and through secure external information sharing and analysis centers (ISACs).

    Ensure information is shared in a format that relates to the particular end user. Internal consumers fall into two categories:

    • Strategic Users — Intelligence enables strategic stakeholders to better understand security trends, minimize risk, and make more educated and informed decisions. The strategic intelligence user often lacks technical security knowledge; bridge the communication gap between security and non-technical decision makers by clearly communicating the underlying value and benefits.
    • Operational Users — Operational users integrate information and indicators directly into their daily operations and as a result have more in-depth knowledge of the technical terms. Reports help to identify escalated alerts that are part of a bigger campaign, provide attribution and context to attacks, identify systems that have been compromised, block malicious URLs or malware signatures in firewalls, IDPS systems, and other gateway products, identify patches, reduce the number of incidents, etc.
    Collaboration includes the exchange of:
    • Contextualized threat indicators, threat actors, TTPs, and campaigns.
    • Attribution of the attack, motives of the attacker, victim profiles, and frequent exploits.
    • Defensive and mitigation strategies.
    • Best-practice incident response procedures.
    • Technical tools to help normalize threat intelligence formats or decode malicious network traffic.
    Collaboration can be achieved through:
    • Manual unstructured exchanges such as alerts, reports, briefings, knowledge portals, or emails.
    • Automated centralized platforms that allow users to privately upload, aggregate, and vet threat intelligence. Current players include commercial, government, and open-source information-sharing and analysis centers.
    Isolation prevents businesses from learning from each others’ mistakes and/or successes.

    Define the routine of your security operations program in a detailed cadence schedule

    Security Operations Program Cadence Schedule Template

    Design your meetings around your security operations program’s outputs and capabilities

    How to customize

    Don’t operate in a silo. Formalize a cadence schedule to develop a state of accountability, share information across the organization, and discuss relevant trends. A detailed cadence schedule should include the following:

    • Activity, output, or topic being discussed.
    • Participants and stakeholders involved.
    • Value and purpose of meeting.
    • Duration and frequency of each meeting.
    • Investment per participant per meeting.
    Sample of Info-Tech's Security Operations Program Cadence Schedule Template.

    Info-Tech Best Practice

    Schedule regular meetings composed of key members from different working groups to discuss concerns, share goals, and communicate operational processes pertaining to their specific roles.

    Apply a strategic lens to your security operations program

    Frame the importance of optimizing the security operations program to align with that of the decision makers’ overarching strategy.

    Strategies
    1. Bridge the communication gap between security and non-technical decision makers. Communicate concisely in business-friendly terms.
    2. Quantify the ROI for the given project.
    3. Educate stakeholders – if stakeholders do not understand what a security operations program encompasses, it will be hard for them to champion the initiative.
    4. Communicate the implications, value, and benefits of a security operations program.
    5. Frame the opportunity as a competitive advantage, e.g. proactive security measures as a client acquisition strategy.
    6. Address the increasing prevalence of threat actors. Use objective data to demonstrate the impact, e.g. through case studies, recent media headlines, or statistics.

    Defensive Strategy diagram with columns 'Adversaries', 'Defenses', 'Assets', and priority level.
    (Source: iSIGHT, “ Definitive Guide to Threat Intelligence”)

    Info-Tech Best Practice

    Refrain from using scare tactics such as fear, uncertainty, and doubt (FUD). While this may be a short-term solution, it limits the longevity of your operations as senior management is not truly invested in the initiative.

    Example: Align your strategic needs with that of management.

    Identify assets of value, current weak security measures, and potential adversaries. Demonstrate how an optimized security operations program can mitigate those threats.

    Develop a comprehensive measurement program to evaluate the effectiveness of your security operations

    There are three types of metrics pertaining to security operations:

    1) Operations-focused

    Operations-focused metrics are typically communicated through a centralized visualization such as a dashboard. These metrics guide operational efforts, identifying operational and control weak points while ensuring the appropriate actions are taken to fix them.

    Examples include, but are not limited to:

    • Ticketing metrics (e.g. average ticket resolution rate, ticketing status, number of tickets per queue/analyst).
    • False positive percentage per control.
    • Incident response metrics (e.g. mean time to recovery).
    • CVSS scores per vulnerability.

    2) Business-focused

    The evaluation of operational success from a business perspective.

    Example metrics include:

    • Return on investment.
    • Total cost of ownership (can be segregated by function: prevent, detect, analyze, and respond).
    • Saved costs from mitigated breaches.
    • Security operations budget as a percentage of the IT budget.

    3) Initiative-focused

    The measurement of security operations project progress. These are frequently represented as time, resource, or cost-based metrics.

    Note: Remember to measure end-user feedback. Asking stakeholders about their current expectations via a formal survey is the most effective way to kick-start the continuous improvement process.

    Info-Tech Best Practice

    Operational metrics have limited value beyond security operations – when communicating to management, focus on metrics that are actionable from a business perspective.

    Download Info-Tech’s Security Operations Metrics Summary Document.Sample of Info-Tech's Security Operations Metrics Summary Document.

    Identify the triggers for continual improvement

    Continual Improvement

    • Audits: Check for performance requirements in order to pass major audits.
    • Assessments: Variances in efficiency or effectiveness of metrics when compared to the industry standard.
    • Process maturity: Opportunity to increase efficiency of services and processes.
    • Management reviews: Routine reviews that reveal gaps.
    • Technology advances: For example, new security architecture/controls have been released.
    • Regulations: Compliance to new or changed regulations.
    • New staff or technology: Disruptive technology or new skills that allow for improvement.

    Conduct tabletop exercises with Info-Tech’s onsite workshop

    Assess your security operations capabilities

    Leverage Info-Tech’s Security Operations Tabletop Exercise to guide simulations to validate your operational procedures.

    How to customize
    • Use the templates to document actions and actors.
    • For each new injection, spend three minutes discussing the response as a group. Then spend two minutes documenting each role’s contribution to the response. After the time limit, proceed to the following injection scenario.
    • Review the responses only after completing the entire exercise.
    Sample of Info-Tech's Security Operations Tabletop Exercise.

    This tabletop exercise is available through an onsite workshop as we can help establish and design a tabletop capability for your organization.

    Are you ready to implement your security operations program?

    Self-Assessment Questions

    • Is there a formalized security operations collaboration plan?
    • Are all key stakeholders documented and acknowledged?
    • Have you defined your strategic needs and requirements in a formalized collection plan?
    • Is there an established channel for management to communicate needs and requirements to the security operation leaders?
    • Are all program outputs documented and communicated?
    • Is there an accessible, centralized portal or dashboard that actively aggregates and communicates key information?
    • Is there a formalized threat escalation protocol in order to facilitate both internal and external information sharing?
    • Does your organization actively participate in external information sharing through the use of ISACs?
    • Does your organization actively produce reports, alerts, products, etc. that feed into and influence the output of other functions’ operations?
    • Have you assigned program responsibilities in a detailed RACI chart?
    • Is there a structured cadence schedule for key stakeholders to actively communicate and share information?
    • Have you developed a structured measurement program on a per function basis?
    • Now that you have constructed your ideal security operations program strategy, revisit the question “Are you answering all of your objectives?”

    If you answered “yes” to the questions, then you are ready to implement your security operations program.

    Summary

    Insights

    1. Security operations is no longer a center, but a process. The need for a physical security hub has evolved into the virtual fusion of prevention, detection, analysis, and response efforts. When all four functions operate as a unified process, your organization will be able to proactively combat changes in the threat landscape.
    2. Functional threat intelligence is a prerequisite for effective security operations – without it, security operations will be inefficient and redundant. Eliminate false positives by contextualizing threat data, aligning intelligence with business objectives, and building processes to satisfy those objectives
    3. If you are not communicating, then you are not secure. Collaboration eliminates siloed decisions by connecting people, processes, and technologies. You leave less room for error, consume fewer resources, and improve operational efficiency with a transparent security operations process.

    Best Practices

    • Have a structured plan of attack. Define your unique threat landscape, as well as business, regulatory, and consumer obligations.
    • Foster both internal and external collaboration.
    • Understand the operational cut-off points. While collaboration is encouraged, understand when the onus shifts to the rest of the threat collaboration environment.
    • Do not bite off more than you can chew. Identify current people, processes, and technologies that satisfy immediate problems and enable future expansion.
    • Leverage threat intelligence to create a predictive and proactive security operations analysis process.
    • Formalize escalation procedures with logic and incident management flow.
    • Don’t develop a security operations program with the objective of zero incidents. This reliance on prevention results in over-engineered security solutions that cost more than the assets being protected.
    • Ensure that information flows freely throughout the threat collaboration environment – each function should serve to feed and enhance the next.
    • Develop a central web/knowledge portal that is easily accessible throughout the threat collaboration environment
    Protect your organization with an interdependent and collaborative security operations program.

    Bibliography

    “2016 State of Cybersecurity in Small & Medium-Sized Businesses (SMB).” Ponemon Institute, June 2016. Web. 10 Nov. 2016.

    Ahmad, Shakeel et al. “10 Tips to Improve Your Security Incident Readiness and Response.” RSA, n.d. Web. 12 Nov. 2016.

    Anderson, Brandie. “ Building, Maturing & Rocking a Security Operations Center.” Hewlett Packard, n.d. Web. 4 Nov. 2016.

    Barnum, Sean. “Standardizing cyber threat intelligence information with the structured threat information expression.” STIX, n.d. Web. 03 Oct. 2016.

    Bidou, Renaud. “Security Operation Center Concepts & Implementation.” IV2-Technologies, n.d. Web. 20 Nov. 2016.

    Bradley, Susan. “Cyber threat intelligence summit.” SANS Institute InfoSec Reading Room, n.d. Web. 03 Oct. 2016.

    “Building a Security Operations Center.” DEF CON Communications, Inc., 2015. Web. 14 Nov. 2016.

    “Building a Successful Security Operations Center.” ArcSight, 2015. Web. 21 Nov. 2016.

    “Building an Intelligence-Driven Security Operations Center.” RSA, June 2014. Web. 25 Nov. 2016.

    Caltagirone, Sergio, Andrew Pendergast, and Christopher Betz. “Diamond Model of Intrusion Analysis,” Center for Cyber Threat Intelligence and Threat Research, 5 July 2013. Web. 25 Aug. 2016.

    “Cisco 2017 Annual Cybersecurity Report: Chief Security Officers Reveal True Cost of Breaches and the Actions Organizations Are Taking.” The Network. Cisco, 31 Jan. 2017. Web. 11 Nov. 2017.

    “CITP Training and Education.” Carnegie Mellon University, 2015. Web. 03 Oct. 2016.

    “Creating and Maintaining a SOC.” Intel Security, n.d. Web. 14 Nov. 2016.

    “Cyber Defense.” Mandiant, 2015. Web. 10 Nov. 2016.

    “Cyber Security Operations Center (CSOC).” Northrop Grumman, 2014. Web. 14 Nov. 2016.

    Danyliw, Roman. “Observations of Successful Cyber Security Operations.” Carnegie Mellon, 12 Dec. 2016. Web. 14 Dec. 2016.

    “Designing and Building Security Operations Center.” SearchSecurity. TechTarget, Mar. 2016. Web. 14 Dec. 2016.

    EY. “Managed SOC.” EY, 2015. Web. 14 Nov. 2016.

    Fishbach, Nicholas. “How to Build and Run a Security Operations Center.” Securite.org, n.d. Web. 20 Nov. 2016.

    “Framework for improving critical infrastructure cybersecurity.” National Institute of Standards and Technology, 12 Feb. 2014. Web.

    Friedman, John, and Mark Bouchard. “Definitive Guide to Cyber Threat Intelligence.” iSIGHT, 2015. Web. 1 June 2015.

    Goldfarb, Joshua. “The Security Operations Hierarchy of Needs.” Securityweek.com, 10 Sept. 2015. Web. 14 Dec. 2016.

    “How Collaboration Can Optimize Security Operations.” Intel, n.d. Web. 2 Nov. 2016.

    Hslatman. “Awesome threat intelligence.” GitHub, 16 Aug. 2016. Web. 03 Oct. 2016.

    “Implementation Framework – Collection Management.” Carnegie Mellon University, 2015. Web.

    “Implementation Framework – Cyber Threat Prioritization.” Carnegie Mellon University, 03 Oct. 2016. Web. 03 Oct. 2016.

    “Intelligent Security Operations Center.” IBM, 25 Feb. 2015. Web. 15 Nov. 2016.

    Joshi Follow , Abhishek. “Best Practices for Security Operations Center.” LinkedIn, 01 Nov. 2015. Web. 14 Nov. 2016.

    Joshi. “Best Practices for a Security Operations Center.” Cybrary, 18 Sept. 2015. Web. 14 Dec. 2016.

    Kelley, Diana and Ron Moritz. “Best Practices for Building a Security Operations Center.” Information Security Today, 2006. Web. 10 Nov. 2016.

    Killcrece, Georgia, Klaus-Peter Kossakowski, Robin Ruefle, and Mark Zajicek. ”Organizational Models for Computer Security Incident Response Teams (CSIRTs).” Carnegie Mellon Software Engineering Institute, Dec. 2003. Carnegie Mellon. Web. 10 Nov. 2016.

    Kindervag , John. “SOC 2.0: Three Key Steps toward the Next-generation Security Operations Center.” SearchSecurity. TechTarget, Dec. 2010. Web. 14 Dec. 2016.

    Kvochko, Elena. “Designing the Next Generation Cyber Security Operations Center.” Forbes Magazine, 14 Mar. 2016. Web. 14 Dec. 2016.

    Lambert, P. “ Security Operations Center: Not Just for Huge Enterprises.” TechRepublic, 31 Jan. 2013. Web. 10 Nov. 2016.

    Lecky, M. and D. Millier. “Re-Thinking Security Operations.” SecTor Security Education Conference. Toronto, 2014.

    Lee, Michael. “Three Elements That Every Advanced Security Operations Center Needs.” CSO | The Resource for Data Security Executives, n.d. Web. 16 Nov. 2016.

    Linch, David and Jason Bergstrom. “Building a Culture of Continuous Improvement in an Age of Disruption.” Deloitte LLP, 2014.

    Lynch, Steve. “Security Operations Center.” InfoSec Institute, 14 May 2015. Web. 14 Dec. 2016.

    Macgregor, Rob. “Diamonds or chains – cyber security updates.” PwC, n.d. Web. 03 Oct. 2016.

    “Make Your Security Operations Center (SOC) More Efficient.” Making Your Data Center Energy Efficient (2011): 213-48. Intel Security. Web. 20 Nov. 2016.

    Makryllos, Gordon. “The Six Pillars of Security Operations.” CSO | The Resource for Data Security Executives, n.d. Web. 14 Nov. 2016.

    Marchany, R. “ Building a Security Operations Center.” Virginia Tech, 2015. Web. 8 Nov. 2016.

    Marty, Raffael. “Dashboards in the Security Operations Center (SOC).” Security Bloggers Network, 15 Jan. 2016. Web. 14 Nov. 2016.

    Minu, Adolphus. “Discovering the Value of Knowledge Portal.” IBM, n.d. Web. 1 Nov. 2016.

    Muniz, J., G. McIntyre, and N. AlFardan. “Introduction to Security Operations and the SOC.” Security Operations Center: Building, Operating, and Maintaining your SOC. Cisco Press, 29 Oct. 2015. Web. 14 Nov. 2016.

    Muniz, Joseph and Gary McIntyre. “ Security Operations Center.” Cisco, Nov. 2015. Web. 14 Nov. 2016.

    Muniz, Joseph. “5 Steps to Building and Operating an Effective Security Operations Center (SOC).” Cisco, 15 Dec. 2015. Web. 14 Dec. 2016.

    Nathans, David. Designing and Building a Security Operations Center. Syngress, 2015. Print.

    National Institute of Standards and Technology. “SP 800-61 Revision 2: Computer Security Incident Handling Guide.” 2012. Web.

    National Institute of Standards and Technology. “SP 800-83 Revision 1.” 2013. Web.

    National Institute of Standards and Technology. “SP 800-86: Guide to Integrating Forensic Techniques into Incident Response.” 2006. Web.

    F5 Networks. “F5 Security Operations Center.” F5 Networks, 2014. Web. 10 Nov. 2016.

    “Next Generation Security Operations Center.” DTS Solution, n.d. Web. 20 Nov. 2016.

    “Optimizing Security Operations.” Intel, 2015. Web. 4 Nov. 2016.

    Paganini, Pierluigi. “What Is a SOC ( Security Operations Center)?” Security Affairs, 24 May 2016. Web. 14 Dec. 2016.

    Ponemon Institute LLC. “Cyber Security Incident Response: Are we as prepared as we think?” Ponemon, 2014. Web.

    Ponemon Institute LLC. “The Importance of Cyber Threat Intelligence to a Strong Security Posture.” Ponemon, Mar. 2015. Web. 17 Aug. 2016.

    Poputa-Clean, Paul. “Automated defense – using threat intelligence to augment.” SANS Institute InfoSec Reading Room, 15 Jan. 2015. Web.

    Quintagroup. “Knowledge Management Portal Solution.” Quintagroup, n.d. Web.

    Rasche, G. “Guidelines for Planning an Integrated Security Operations Center.” EPRI, Dec. 2013. Web. 25 Nov. 2016.

    Rehman, R. “What It Really Takes to Stand up a SOC.” Rafeeq Rehman – Personal Blog, 27 Aug. 2015. Web. 14 Dec. 2016.

    Rothke, Ben. “Designing and Building Security Operations Center.” RSA Conference, 2015. Web. 14 Nov. 2016.

    Ruks, Martyn and David Chismon. “Threat Intelligence: Collecting, Analysing, Evaluating.” MWR Infosecurity, 2015. Web. 24 Aug. 2016.

    Sadamatsu, Takayoshi. “Practice within Fujitsu of Security Operations Center.” Fujitsu, July 2016. Web. 15 Nov. 2016.

    Sanders, Chris. “Three Useful SOC Dashboards.” Chris Sanders, 24 Oct. 2016. Web. 14 Nov. 2016.

    SANS Institute. “Incident Handler's Handbook.” 2011. Web.

    Schilling, Jeff. “5 Pitfalls to Avoid When Running Your SOC.” Dark Reading, 18 Dec. 2014. Web. 14 Nov. 2016.

    Schinagl, Stef, Keith Schoon, and Ronald Paans. “A Framework for Designing a Security Operations Centre (SOC).” 2015 48th Hawaii International Conference on System Sciences. Computer.org, 2015. Web. 20 Nov. 2016.

    “Security – Next Gen SOC or SOF.” InfoSecAlways.com, 31 Dec. 2013. Web. 14 Nov. 2016.

    “Security Operations Center Dashboard.” Enterprise Dashboard Digest, n.d. Web. 14 Dec. 2016.

    “Security Operations Center Optimization Services.” AT&T, 2015. Web. 5 Nov. 2016.

    “Security Operations Centers — Helping You Get Ahead of Cybercrime Contents.” EY, 2014. Web. 6 Nov. 2016.

    Sheikh, Shah. “DTS Solution - Building a SOC (Security Operations Center).” LinkedIn, 4 May 2013. Web. 20 Nov. 2016.

    Soto, Carlos. “ Security Operations Center (SOC) 101.” Tom's IT Pro, 28 Oct. 2015. Web. 14 Dec. 2016.

    “Standardizing and Automating Security Operations.” National Institute of Standards and Technology, 3 Sept. 2006. Web.

    “Strategy Considerations for Building a Security Operations Center.” IBM, Dec. 2013. Web. 5 Nov. 2016.

    “Summary of Key Findings.” Carnegie Mellon University, 03 Oct. 2016. Web. 03 Oct. 2016.

    “Sustainable Security Operations.” Intel, 2016. Web. 20 Nov. 2016.

    “The Cost of Malware Containment.” Ponemon Institute, Jan. 2015. Web.

    “The Game Plan for Closing the SecOps Gap.” BMC. Forbes Magazine, Jan. 2016. Web. 10 Jan. 2017.

    Veerappa Srinivas, Babu. “Security Operations Centre (SOC) in a Utility Organization.” GIAC, 17 Sept. 2014. Web. 5 Nov. 2016.

    Wang, John. “Anatomy of a Security Operations Center.” NASA, 2015. Web. 2 Nov. 2016.

    Weiss, Errol. “Statement for the Record.” House Financial Services Committee, 1 June 2012. Web. 12 Nov. 2016.

    Wilson, Tim. “SOC 2.0: A Crystal-Ball Glimpse of the Next-Generation Security Operations Center.” Dark Reading, 22 Nov. 2010. Web. 10 Nov. 2016.

    Zimmerman, Carson. “Ten Strategies of a World-Class Cybersecurity Operations Center.” Mitre, 2014. Web. 24 Aug. 2016.

    Document Your Cloud Strategy

    • Buy Link or Shortcode: {j2store}468|cart{/j2store}
    • member rating overall impact: 8.9/10 Overall Impact
    • member rating average dollars saved: $35,642 Average $ Saved
    • member rating average days saved: 21 Average Days Saved
    • Parent Category Name: Cloud Strategy
    • Parent Category Link: /cloud-strategy

    Despite the universally agreed-upon benefit of formulating a coherent strategy, several obstacles make execution difficult:

    • Inconsistent understanding of what the cloud means
    • Inability to come to a consensus on key decisions
    • Ungoverned decision-making
    • Unclear understanding of cloud roles and responsibilities

    Our Advice

    Critical Insight

    A cloud strategy might seem like a big project, but it’s just a series of smaller conversations. The methodology presented here is designed to facilitate those conversations, using a curated list of topics, prompts, participant lists, and sample outcomes. We have divided the strategy into four key areas:

    • Vision and alignment
    • People
    • Governance
    • Technology

    Impact and Result

    • A shared understanding of what is necessary to succeed in the cloud
    • An end to ad hoc deployments that solve small problems and create larger ones
    • A unified approach and set of principles that apply to governance, architecture, integration, skills, and roles (and much, much more).

    Document Your Cloud Strategy Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Document Your Cloud Strategy – a phased guide to identifying, validating, and recording the steps you’ll take, the processes you’ll leverage, and the governance you’ll deploy to succeed in the cloud.

    This storyboard comprises four phases, covering mission and vision, people, governance, and technology, and how each of these areas requires forethought when migrating to the cloud.

    • Document Your Cloud Strategy – Phases 1-4

    2. Cloud Strategy Document Template – a template that allows you to record the results of the cloud strategy exercise in a clear, readable way.

    Each section of Document Your Cloud Strategy corresponds to a section in the document template. Once you’ve completed each exercise, you can record your results in the document template, leaving you with an artifact you can share with stakeholders.

    • Cloud Strategy Document Template
    [infographic]

    Workshop: Document Your Cloud Strategy

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Document Your Vision and Alignment

    The Purpose

    Understand and document your cloud vision and its alignment with your other strategic priorities.

    Key Benefits Achieved

    A complete understanding of your strategy, vision, alignment, and a list of success metrics that will help you find your way.

    Activities

    1.1 Record your cloud mission and vision.

    1.2 Document your cloud strategy’s alignment with other strategic plans.

    1.3 Record your cloud guiding principles.

    Outputs

    Documented strategy, vision, and alignment.

    Defined success metrics.

    2 Record Your People Strategy

    The Purpose

    Define how people, skills, and roles will contribute to the broader cloud strategy.

    Key Benefits Achieved

    Sections of the strategy that highlight skills, roles, culture, adoption, and the creation of a governance body.

    Activities

    2.1 Outline your skills and roles strategy.

    2.2 Document your approach to culture and adoption

    2.3 Create a cloud governing body.

    Outputs

    Documented people strategy.

    3 Document Governance Principles

    The Purpose

    This section facilitates governance in the cloud, developing principles that apply to architecture, integration, finance management, and more.

    Key Benefits Achieved

    Sections of the strategy that define governance principles.

    Activities

    3.1 Conduct discussion on architecture.

    3.2 Conduct discussion on integration and interoperability.

    3.3 Conduct discussion on operations management.

    3.4 Conduct discussion on cloud portfolio management.

    3.5 Conduct discussion on cloud vendor management.

    3.6 Conduct discussion on finance management.

    3.7 Conduct discussion on security.

    3.8 Conduct discussion on data controls.

    Outputs

    Documented cloud governance strategy.

    4 Formalize Your Technology Strategy

    The Purpose

    Creation of a formal cloud strategy relating to technology around provisioning, monitoring, and migration.

    Key Benefits Achieved

    Completed strategy sections of the document that cover technology areas.

    Activities

    4.1 Formalize organizational approach to monitoring.

    4.2 Document provisioning process.

    4.3 Outline migration processes and procedures.

    Outputs

    Documented cloud technology strategy.

    Further reading

    Document Your Cloud Strategy

    Get ready for the cloudy future with a consistent, proven strategy.

    Analyst perspective

    Any approach is better than no approach

    The image contains a picture of Jeremy Roberts

    Moving to the cloud is a big, scary transition, like moving from gas-powered to electric cars, or from cable to streaming, or even from the office to working from home. There are some undeniable benefits, but we must reorient our lives a bit to accommodate those changes, and the results aren’t always one-for-one. A strategy helps you make decisions about your future direction and how you should respond to changes and challenges. In Document Your Cloud Strategy we hope to help you accomplish just that: clarifying your overall mission and vision (as it relates to the cloud) and helping you develop an approach to changes in technology, people management, and, of course, governance. The cloud is not a panacea. Taken on its own, it will not solve your problems. But it can be an important tool in your IT toolkit, and you should aim to make the best use of it – whatever “best” happens to mean for you.

    Jeremy Roberts

    Research Director, Infrastructure and Operations

    Info-Tech Research Group

    Executive Summary

    Your Challenge

    The cloud is multifaceted. It can be complicated. It can be expensive. Everyone has an opinion on the best way to proceed – and in many cases has already begun the process without bothering to get clearance from IT. The core challenge is creating a coherent strategy to facilitate your overall goals while making the best use of cloud technology, your financial resources, and your people.

    Common Obstacles

    Despite the universally agreed-upon benefit of formulating a coherent strategy, several obstacles make execution difficult:

    • Inconsistent understanding of what the cloud means
    • Inability to come to a consensus on key decisions
    • Ungoverned decision making
    • Unclear understanding of cloud roles and responsibilities

    Info-Tech’s Approach

    A cloud strategy might seem like a big project, but it’s just a series of smaller conversations. The methodology presented here is designed to facilitate those conversations, using a curated list of topics, prompts, participant lists, and sample outcomes. We have divided the strategy into four key areas:

    1. Vision and alignment
    2. People
    3. Governance
    4. Technology

    The answers might be different, but the questions are the same

    Every organization will approach the cloud differently, but they all need to ask the same questions: When will we use the cloud? What forms will our cloud usage take? How will we manage governance? What will we do about people? How will we incorporate new technology into our environment? The answers to these questions are as numerous as there are people to answer them, but the questions must be asked.

    Your challenge

    This research is designed to help organizations that are facing these challenges or looking to:

    • Ensure that the cloud strategy is complete and accurately reflects organizational goals and priorities.
    • Develop a consistent and coherent approach to adopting cloud services.
    • Design an approach to mitigate risks and challenges associated with adopting cloud services.
    • Create a shared understanding of the expected benefits of cloud services and the steps required to realize those benefits.

    Grappling with a cloud strategy is a top initiative: 43% of respondents report progressing on a cloud-first strategy as a top cloud initiative.

    Source: Flexera, 2021.

    Definition: Cloud strategy

    A document providing a systematic overview of cloud services, their appropriate use, and the steps that an organization will take to maximize value and minimize risk.

    Common obstacles

    These barriers make this challenge difficult to address for many organizations:

    • The cloud means different things to different people, and creating a strategy that is comprehensive enough to cover a multitude of use cases while also being written to be consumable by all stakeholders is difficult.
    • The incentives to adopt the cloud differ based on the expected benefit for the individual customer. User-led decision making and historically ungoverned deployments can make it difficult to reset expectation and align with a formal strategy.
    • Getting all the right people in a room together to agree on the key components of the strategy and the direction undertaken for each one is often difficult.

    Info-Tech’s approach

    Define Your Cloud Vision

    →

    Vision and alignment

    • Mission and vision
    • Alignment to other strategic plans
    • Guiding principles
    • Measuring success
    →

    Technology

    • Monitoring
    • Provisioning
    • Migration

    Governance

    • Architecture
    • Integration and interoperability
    • Operations management
    • Cloud portfolio management
    • Cloud vendor management
    • Finance management
    • Security
    • Data controls

    People

    • Skills and roles
    • Culture and adoption
    • Governing bodies

    Info-Tech’s approach

    Your cloud strategy will comprise the elements listed under “vision and alignment,” “technology,” “governance,” and “people.” The Info-Tech methodology involves breaking the strategy down into subcomponents and going through a three-step process for each one. Start by reviewing a standard set of questions and understanding the goal of the exercise: What do we need to know? What are some common considerations and best practices? Once you’ve had a chance to review, discuss your current state and any gaps: What has been done? What still needs to be done? Finally, outline how you plan to go forward: What are your next steps? Who needs to be involved?

    Review

    • What questions do we need to answer to complete the discussion of this strategy component? What does the decision look like?
    • What are some key terms and best practices we must understand before deciding?

    Discuss

    • What steps have we already taken to address this component?
    • Does anything still need to be done?
    • Is there anything we’re not sure about or need further guidance on?

    Go forward

    • What are the next steps?
    • Who needs to be involved?
    • What questions still need to be asked/answered?
    • What should the document’s wording look like?

    Info-Tech’s methodology for documenting your cloud strategy

    1. Document your vision and alignment

    2. Record your people strategy

    3. Document governance principles

    4. Formalize your technology strategy

    Phase Steps

    1. Record your cloud mission and vision
    2. Document your cloud strategy’s alignment with other strategic plans
    3. Record your cloud guiding principles
    4. Define success
    1. Outline your skills and roles strategy
    2. Document your approach to culture and adoption
    3. Create a cloud governing body

    Document official organizational positions in these governance areas:

    1. Architecture
    2. Integration and interoperability
    3. Operations management
    4. Cloud portfolio management
    5. Cloud vendor management
    6. Finance management
    7. Security
    8. Data controls
    1. Formalize organizational approach to monitoring
    2. Document provisioning process
    3. Outline migration processes and procedures

    Phase Outcomes

    Documented strategy: vision and alignment

    Documented people strategy

    Documented cloud governance strategy

    Documented cloud technology strategy

    Insight summary

    Separate strategy from tactics

    Separate strategy from tactics! A strategy requires building out the framework for ongoing decision making. It is meant to be high level and achieve a large goal. The outcome of a strategy is often a sense of commitment to the goal and better communication on the topic.

    The cloud does not exist in a vacuum

    Your cloud strategy flows from your cloud vision and should align with the broader IT strategy. It is also part of a pantheon of strategies and should exist harmoniously with other strategies – data, security, etc.

    People problems needn’t preponderate

    The cloud doesn’t have to be a great disruptor. If you handle the transition well, you can focus your people on doing more valuable work – and this is generally engaging.

    Governance is a means to an end

    Governing your deployment for its own sake will only frustrate your end users. Articulate the benefits users and the organization can expect to see and you’re more likely to receive the necessary buy-in.

    Technology isn’t a panacea

    Technology won’t solve all your problems. Technology is a force multiplier, but you will still have to design processes and train your people to fully leverage it.

    Key deliverable

    Cloud Strategy Document template

    Inconsistency and informality are the enemies of efficiency. Capture the results of the cloud strategy generation exercises in the Cloud Strategy Document template.

    The image contains a screenshot of the Cloud Strategy Document Template.
    • Record the results of the exercises undertaken as part of this blueprint in the Cloud Strategy Document template.
    • It is important to remember that not every cloud strategy will look exactly the same, but this template represents an amalgamation of best practices and cloud strategy creation honed over several years of advisory service in the space.
    • You know your audience better than anyone. If you would prefer a strategy delivered in a different way (e.g. presentation format) feel free to adapt the Cloud Vision Executive Presentation into a longer strategy presentation.
    • Emphasis is an area where you should exercise discretion as well. A cost-oriented cloud strategy, or one that prioritizes one type of cloud (e.g. SaaS) at the exclusion of others, may benefit from more focus on some areas than others, or the introduction of relevant subcategories. Include as many of these as you think will be relevant.
    • Parsimony is king – if you can distill a concept to its essence, start there. Include additional detail only as needed. You want your cloud strategy document to be read. If it’s too long or overly detailed, you’ll encounter readability issues.

    Blueprint benefits

    IT benefits

    Business benefits

    • A consistent, well-defined approach to the cloud
    • Consensus on key strategy components, including security, architecture, and integration
    • A clear path forward on skill development and talent acquisition/retention
    • A comprehensive resource for information about the organization’s approach to key strategy components
    • Predictable access to cloud services
    • A business-aligned approach to leveraging the resources available in the cloud
    • Efficient and secure consumption of cloud resources where appropriate to do so
    • Answers to questions about the cloud and how it will be leveraged in the environment

    Measure the value of this blueprint

    Don’t take our word for it:

    • Document Your Cloud Strategy has been available for several years in various forms as both a workshop and as an analyst-led guided implementation.
    • After each engagement, we send a survey that asks members how they benefited from the experience. Those who have worked through Info-Tech’s cloud strategy material have given overwhelmingly positive feedback.
    • Additionally, members reported saving between 10 and 20 days and an average of $46,499.
    • Measure the value by calculating the time saved as a result of using Info-Tech’s framework vs. a home-brewed cloud strategy alternative and by comparing the overall cost of a guided implementation or workshop with the equivalent offering from another firm. We’re confident you’ll come out ahead.

    8.8/10 Average reported satisfaction

    13 Days Average reported time savings

    $46,499 Average cost savings

    Executive Brief Case Study

    INDUSTRY: Pharmaceuticals

    SOURCE: Info-Tech workshop

    Pharmaceutical company

    The unnamed pharmaceutical company that is the subject of this case study was looking to make the transition to the cloud. In the absence of a coherent strategy, the organization had a few cloud deployments with no easily discernable overall approach. Representatives of several distinct functions (legal, infrastructure, data, etc.) all had opinions on the uses and abuses of cloud services, but it had been difficult to round everyone up and have the necessary conversations. As a result, the strategy exercise had not proceeded in a speedy or well-governed way. This lack of strategic readiness presented a roadblock to moving forward with the cloud strategy and to work with the cloud implementation partner, tasked with execution.

    Results

    The company engaged Info-Tech for a four-day workshop on cloud strategy documentation. Over the course of four days, participants drawn from across the organization discussed the strategic components and generated consensus statements and next steps. The team was able to formalize the cloud strategy and described the experience as saving 10 days.

    Example output: Document your cloud strategy workshop exercise

    The image contains an example of Document your cloud streatgy workshop exercise.

    Anything in green, the team was reasonably sure they had good alignment and next steps. Those yellow flags warranted more discussion and were not ready for documentation.

    Info-Tech offers various levels of support to best suit your needs

    DIY Toolkit

    "Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful."

    Guided Implementation

    "Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track."

    Workshop

    "We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place."

    Consulting

    "Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project."

    Diagnostics and consistent frameworks are used throughout all four options.

    Guided Implementation

    What does a typical GI on this topic look like?

    Document your vision and alignment

    Record your people strategy

    Document governance principles

    Formalize your technology strategy

    Call #1: Review existing vision/strategy documentation.

    Call #2: Review progress on skills, roles, and governance bodies.

    Call #3: Work through integration, architecture, finance management, etc. based on reqs. (May be more than one call.)

    Call #4: Discuss challenges with monitoring, provisioning, and migration as-needed.

    A Guided Implementation (GI) is a series of calls with an Info-Tech analyst to help implement our best practices in your organization. A typical GI is 4 to 6 calls over the course of 1 to 3 months

    Workshop Overview

    Contact your account representative for more information.

    workshops@infotech.com 1-888-670-8889

    Day 1

    Day 2

    Day 3

    Day 4

    Day 5

    Answer
    “so what?”

    Define the
    IT target state

    Assess the IT
    current state

    Bridge the gap and
    create the strategy

    Next steps and
    wrap-up (offsite)

    Activities

    1.1 Introduction

    1.2 Discuss cloud mission and vision

    1.3 Discuss alignment with other strategic plans

    1.4 Discuss guiding principles

    1.5 Define success metrics

    2.1 Discuss skills and roles

    2.2 Review culture and adoption

    2.3 Discuss a cloud governing body

    2.4 Review architecture position

    2.5 Discuss integration and interoperability

    3.1 Discuss cloud operations management

    3.2 Review cloud portfolio management

    3.3 Discuss cloud vendor management

    3.4 Discuss cloud finance management

    3.5 Discuss cloud security

    4.1 Review and formalize data controls

    4.2 Design a monitoring approach

    4.3 Document the workload provisioning process

    4.4 Outline migration processes and procedures

    5.1 Populate the Cloud Strategy Document

    Deliverables

    Formalized cloud mission and vision, along with alignment with strategic plans, guiding principles, and success metrics

    Position statement on skills and roles, culture and adoption, governing bodies, architecture, and integration/interoperability

    Position statements on cloud operations management, portfolio management, vendor management, finance management, and cloud security

    Position statements on data controls, monitoring, provisioning, and migration

    Completed Cloud Strategy Document

    Phase 1

    Document Your Vision and Alignment

    Phase 1

    Phase 2

    Phase 3

    Phase 4

    1.1 Document your mission and vision

    1.2 Document alignment to other strategic plans

    1.3 Document guiding principles

    1.4 Document success metrics

    2.1 Define approach to skills and roles

    2.2 Define approach to culture and adoption

    2.3 Define cloud governing bodies

    3.1 Define architecture direction

    3.2 Define integration approach

    3.3 Define operations management process

    3.4 Define portfolio management direction

    3.5 Define vendor management direction

    3.6 Document finance management tactics

    3.7 Define approach to cloud security

    3.8 Define data controls in the cloud

    4.1 Define cloud monitoring strategy

    4.2 Define cloud provisioning strategy

    4.3 Define cloud migration strategy

    This phase will walk you through the following activities:

    1. Record your cloud mission and vision
    2. Document your cloud strategy’s alignment with other strategic plans
    3. Record your cloud guiding principles
    4. Define success

    This phase has the following outcome:

    • Documented strategy: vision and alignment

    Record your mission and vision

    Build on the work you’ve already done

    Before formally documenting your cloud strategy, you should ensure that you have a good understanding of your overall cloud vision. How do you plan to leverage the cloud? What goals are you looking to accomplish? How will you distribute your workloads between different cloud service models (SaaS, PaaS, IaaS)? What will your preferred delivery model be (public, private, hybrid)? Will you support your cloud deployment internally or use the services of various consultants or managed service providers?

    The answers to these questions will inform the first section of your cloud strategy. If you haven’t put much thought into this or think you could use a deep dive on the fundamentals of your cloud vision and cloud archetypes, consider reviewing Define Your Cloud Vision, the companion blueprint to this one.

    Once you understand your cloud vision and what you’re trying to accomplish with your cloud strategy, this phase will walk you through aligning the strategy with other strategic initiatives. What decisions have others made that will impact the cloud strategy (or that the cloud strategy will impact)? Who must be involved/informed? What callouts must be involved at what point? Do users have access to the appropriate strategic documentation (and would they understand it if they did)?

    You must also capture some guiding principles. A strategy by its nature provides direction, helping readers understand the decisions they should make and why those decisions align with organizational interests. Creating some top-level principles is a useful exercise because those principles facilitate comprehension and ensure the strategy’s applicability.

    Finally, this phase will walk you through the process of measuring success. Once you know where you’d like to go, the principles that underpin your direction, and how your cloud strategy figures into the broader strategic pantheon, you should record what success actually means. If you’re looking to save money, overall cost should be a metric you track. If the cloud is all about productivity, generate appropriate productivity metrics. If you’re looking to expand into new technology or close a datacenter, you will need to track output specific to those overall goals.

    Review: mission and vision

    The overall organizational mission is a key foundational element of the cloud strategy. If you don’t understand where you’re going, how can you begin the journey to get there? This section of the strategy has four key parts that you should understand and incorporate into the beginning of the strategy document. If you haven’t already, review Define Your Cloud Vision for instructions on how to generate these elements.

    1. Cloud vision statement: This is a succinct encapsulation of your overall perspective on the suitability of cloud services for your environment – what you hope to accomplish. The ideal statement includes a scope (who/what does the strategy impact?), a goal (what will it accomplish?), and a key differentiator (what will make it happen?). This is an example: “[Organization] will leverage public cloud solutions and retire existing datacenter and colocation facilities. This transition will simplify infrastructure administration, support and security, while modernizing legacy infrastructure and reducing the need for additional capital expenditure.” You might also consider reviewing your overall cloud archetype (next slide) and including the output of that exercise in the document

    2. Service model decision framework: Services can be provided as software as a service (SaaS), platform as a service (PaaS), infrastructure as a service (IaaS), or they can be colocated or remain on premises. Not all cloud service models serve the same purpose or provide equal value in all circumstances. Understanding how you plan to take advantage of these distinct service models is an important component of the cloud strategy. In this section of the strategy, a rubric that captures the characteristics of the ideal workload for each of the named service models, along with some justification for the selection, is essential. This is a core component of Define Your Cloud Vision, and if you would like to analyze individual workloads, you can use the Cloud Vision Workbook for that purpose.

    3. Delivery model decision framework: Just as there are different cloud service models that have unique value propositions, there are several unique cloud delivery models as well, distinguished by ownership, operation, and customer base. Public clouds are the purview of third-party providers who make them available to paying customers. Private clouds are built for the exclusive use of a designated organization or group of organizations with internal clients to serve. Hybrid clouds involve the use of multiple, interoperable delivery models (interoperability is the key term here), while multi-cloud deployment models incorporate multiple delivery and service models into a single coherent strategy. What will your preferred delivery model be? Why?

    4. Support model decision framework: Once you have a service model nailed down and understand how you will execute on the delivery, the question then becomes about how you will support your cloud deployment going forward. Broadly speaking, you can choose to manage your deployment in house using internal resources (e.g. staff), to use managed service providers for ongoing support, or to hire consultants to handle specific projects/tasks. Each approach has its strengths and weaknesses, and many cloud customers will deploy multiple support models across time and different workloads. A foundational perspective on the support model is a key component of the cloud vision and should appear early in the strategy.

    Understand key cloud concepts: Archetype

    Once you understand the value of the cloud, your workloads’ general suitability for the cloud, and your proposed risks and mitigations, the next step is to define your cloud archetype. Your organization’s cloud archetype is the strategic posture that IT adopts to best support the organization’s goals. Info-Tech’s model recognizes seven archetypes, divided into three high-level archetypes. After consultation with your stakeholders, and based on the results of the suitability and risk assessment activities, define your archetype. The archetype feeds into the overall cloud vision and provides simple insight into the cloud future state for all stakeholders. The cloud vision itself is captured in a “vision statement,” a short summary of the overall approach that includes the overall cloud archetype.

    The image contains an arrow facing vertically up. The pointed end of the arrow is labelled more cloud, and the bottom of the arrow is labelled less cloud.

    We can best support the organization’s goals by:

    Cloud-Focused

    Cloud-Centric

    Providing all workloads through cloud delivery.

    Cloud-First

    Using the cloud as our default deployment model. For each workload, we should ask “why NOT cloud?”

    Cloud-Opportunistic

    Hybrid

    Enabling the ability to transition seamlessly between on-premises and cloud resources for many workloads.

    Integrated

    Combining cloud and traditional infrastructure resources, integrating data and applications through APIs or middleware.

    Split

    Using the cloud for some workloads and traditional infrastructure resources for others.

    Cloud-Averse

    Cloud-Light

    Using traditional infrastructure resources and limiting our use of the cloud to when it is absolutely necessary.

    Anti-Cloud

    Using traditional infrastructure resources and avoiding the use of cloud wherever possible.

    How to build a Service Desk Chatbot POC

    • Buy Link or Shortcode: {j2store}16|cart{/j2store}
    • Related Products: {j2store}16|crosssells{/j2store}
    • member rating overall impact: 9.7/10
    • member rating average dollars saved: 11,197
    • member rating average days saved: 8
    • Parent Category Name: Service Desk
    • Parent Category Link: /service-desk

    The challenge

    Build a chatbot that creates value for your business


    • Ensure your chatbot meets your business needs.
    • Bring scalability to your customer service delivery in a cost-effective manner.
    • Measure your chatbot objectives with clear metrics.
    • Pre-determine your ticket categories to use during the proof of concept.

    Our advice

    Insight

    • Build your chatbot to create business value. Whether increasing service or resource efficiency, keep value creation in mind when making decisions with your proof of concept.

    Impact and results 

    • When implemented effectively, chatbots can help save costs, generate new revenue, and ultimately increase customer satisfaction for external and internal-facing customers.

    The roadmap

    Read our concise Executive Brief to find out why you building a chatbot proof of concept is a good idea, review our methodology, and understand the four ways we can support you to successfully complete this project. Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    Start here

    Form your chatbot strategy.

    Build the right metrics to measure the success of your chatbot POC

    • Chatbot ROI Calculator (xls)
    • Chatbot POC Metrics Tool (xls)

    Build the foundation for your chatbot.

    Architect the chatbot to maximize business value

    • Chatbot Conversation Tree Library

    Continue to improve your chatbot.

    Now take your chatbot proof of concept to production

    • Chatbot POC RACI (doc)
    • Chatbot POC Implementation Roadmap (xls)
    • Chatbot POC Communication Plan (doc)Chatbot ROI Calculator (xls)

    Document Business Goals and Capabilities for Your IT Strategy

    • Buy Link or Shortcode: {j2store}77|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: IT Strategy
    • Parent Category Link: /it-strategy
    • As a strategic driver, IT needs to work with the business. Yet, traditionally IT has not worked hand-in-hand with the business. IT does not know what information it needs from the business to execute on its initiatives.
    • A faster time to new investment decisions mean that IT needs a repeatable and efficient process to understand what the business needs.
    • CIOs must execute strategic initiatives to create an IT function that can support the business. Most CIOs fail because of low business support.

    Our Advice

    Critical Insight

    • Understanding the business context is a must for all strategic IT initiatives. At its core, each strategic IT project requires answers to a specific set of questions regarding the business.
    • An effective CIO understands which part of the business context applies to which strategic IT project and, in turn, what questions to ask to uncover those insights.

    Impact and Result

    • Uncover what IT knows and needs to know about the business context. This is a necessary first step to begin each of Info-Tech’s strategic IT initiatives, which any CIO should complete.
    • Conduct efficient and repeatable business context discovery activities to uncover business context gaps.
    • Document the business context you have uncovered and streamline the process for executing on Info-Tech’s strategic CIO blueprints.

    Document Business Goals and Capabilities for Your IT Strategy Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should define the business context, review Info-Tech’s methodology, and understand how we can support you in completing key CIO strategic initiatives.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Identify and document the business needs of the organization

    Define the business context needed to complete strategic IT initiatives.

    • Document Business Goals and Capabilities for Your IT Strategy – Storyboard
    • Business Context Discovery Tool
    • Business Context Discovery Record Template
    • PESTLE Analysis Template
    • Strategy Alignment Map Template
    [infographic]

    Workshop: Document Business Goals and Capabilities for Your IT Strategy

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Identify the Missing Business Context (pre-work)

    The Purpose

    Conduct analysis and facilitate discussions to uncover business needs for IT.

    Key Benefits Achieved

    A baseline understanding of what business needs mean for IT

    Activities

    1.1 Define the strategic CIO initiatives our organization will pursue.

    1.2 Complete the Business Context Discovery Tool.

    1.3 Schedule relevant interviews.

    1.4 Select relevant Info-Tech diagnostics to conduct.

    Outputs

    Business context scope

    Completed Business Context Discovery Tool

    Completed Info-Tech diagnostics

    2 Uncover and Document the Missing Context

    The Purpose

    Analyze the outputs from step 1 and uncover the business context gaps.

    Key Benefits Achieved

    A thorough understanding of business needs and why IT should pursue certain initiatives

    Activities

    2.1 Conduct group or one-on-one interviews to identify the missing pieces of the business context.

    Outputs

    Documentation of answers to business context gaps

    3 Uncover and Document the Missing Context

    The Purpose

    Analyze the outputs from step 1 and uncover the business context gaps.

    Key Benefits Achieved

    A thorough understanding of business needs and why IT should pursue certain initiatives

    Activities

    3.1 Conduct group or one-on-one interviews to identify the missing pieces of the business context.

    Outputs

    Documentation of answers to business context gaps

    4 Review Business Context and Next Steps

    The Purpose

    Review findings and implications for IT’s strategic initiative.

    Key Benefits Achieved

    A thorough understanding of business needs and how IT’s strategic initiatives addresses those needs

    Activities

    4.1 Review documented business context with IT team.

    4.2 Discuss next steps for strategic CIO initiative execution.

    Outputs

    Finalized version of the business context

    Determine Your Zero Trust Readiness

    • Buy Link or Shortcode: {j2store}249|cart{/j2store}
    • member rating overall impact: 9.8/10 Overall Impact
    • member rating average dollars saved: $24,574 Average $ Saved
    • member rating average days saved: 12 Average Days Saved
    • Parent Category Name: Security Strategy & Budgeting
    • Parent Category Link: /security-strategy-and-budgeting

    CISOs pushing for zero trust as their security strategy face several challenges including:

    • Understanding and clarifying the benefits of zero trust for the organization.
    • The inability to verify all business operations are maintaining security best practices.
    • Convincing business units to add more security controls that go against the grain of reducing friction in workflows while still demonstrating these controls support the business.

    Our Advice

    Critical Insight

    • Zero trust must benefit the business and security. Because the road to zero trust is an iterative process, IT security will need to constantly determine how different areas of zero trust will affect core business processes.
    • Zero trust reduces reliance on perimeter security. Zero trust is a strategy that solves how to move beyond the reliance on perimeter security and move controls to where the user accesses resources.
    • Not everyone can achieve zero trust, but everyone can adopt it. Zero trust will be different for every organization and may not be applicable in every control area. This means that zero trust is not a one-size-fits-all approach to IT security. Zero trust is the goal, but some organizations can only get so close to the ideal.

    Impact and Result

    Zero trust is a journey that uses multiple capabilities and requires multiple parties to contribute to an organization’s security. Use Info-Tech’s approach to:

    • Understand zero trust as a strategic platform for building your security roadmap.
    • Assess your current state and determine the benefits of adopting zero trust to help plan your roadmap.
    • Separate vendors from the hype surrounding zero trust to adopt a vendor-agnostic approach to your zero trust planning.

    Determine Your Zero Trust Readiness Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should determine your zero trust readiness, review Info-Tech’s methodology, and understand the ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Understand zero trust

    Recognize the zero trust ideal and understand the different zero trust schools of thought.

    2. Assess your zero trust readiness

    Assess and determine the benefits of zero trust and identify and evaluate vendors in the zero trust market.

    • Zero Trust Security Benefit Assessment Tool
    [infographic]

    Organizational Change Management

    • Buy Link or Shortcode: {j2store}35|cart{/j2store}
    • Related Products: {j2store}35|crosssells{/j2store}
    • member rating overall impact: 9.6/10
    • member rating average dollars saved: $19,055
    • member rating average days saved: 24
    • Parent Category Name: Project Portfolio Management and Projects
    • Parent Category Link: /ppm-and-projects
    If you don't know who is responsible for organizational change, it's you.

    Build IT Capabilities to Enable Digital Marketing Success

    • Buy Link or Shortcode: {j2store}553|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Marketing Solutions
    • Parent Category Link: /marketing-solutions
    • Misalignment: Even if IT builds the capabilities to pursue digital channels, the channels will underperform in realizing organizational goals if the channels and the goals are misaligned.
    • Ineffective analytics: Failure to integrate and analyze new data will undermine organizational success in influencer and sentiment identification.
    • Missed opportunity: If IT does not develop the capabilities to support these channels, then lead generation, brand promotion, and engagement opportunities will be lost.
    • Lack of control: Marketing is developing and depending on internal power users and agencies. This practice can isolate IT from digital marketing technology decision making.

    Our Advice

    Critical Insight

    • Identify and understand the digital marketing channels that can benefit your organization.
    • Get stakeholder buy-in to facilitate collaboration between IT and product marketing groups to identify necessary IT capabilities.
    • Build IT capability by purchasing software, outsourcing, and training or hiring individuals with necessary skillsets.
    • Become transformational: use IT capabilities to support analytics that identify new customer segments, key influencers, and other invaluable insights.
    • Time is of the essence! It is easier to begin strengthening the relationship between marketing and IT today then it will be at any point in the future.
    • Being transformational means more than just enabling the channels marketing wants to pursue; IT must assist in identifying new segments and digital marketing opportunities, such as enabling influencer management.

    Impact and Result

    • IT is involved in decision making and has a complete understanding of the digital channels the organization is going to migrate to or phase out if unused.
    • IT has the necessary capabilities to support and enable success in all relevant digital channel management technologies.
    • IT is a key player in ensuring that all relevant data from new digital channels is managed and analyzed in order to maintain a 360 degree view of customers and feed real-time campaigns.
    • This enables the organization to not only target existing segments effectively, but also to identify and pursue new opportunities not presented before.
    • These opportunities include: identifying new segments among social networks, identifying key influencers as a new target, identifying proactive service and marketing opportunities from the public social cloud, and conducting new competitive analyses on the public social cloud.

    Build IT Capabilities to Enable Digital Marketing Success Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Make the case for building IT capabilities

    Identify the symptoms of inadequate IT support of digital marketing to diagnose the problems in your organization.

    • Storyboard: Build IT Capabilities to Enable Digital Marketing Success

    2. Identify digital marketing opportunities to understand the need for action in your organization

    Identify the untapped digital marketing value in your organization to understand where your organization needs to improve.

    • Digital Marketing Capability Builder Tool

    3. Mobilize for action: get stakeholder buy-in

    Develop a plan for communicating with stakeholders to ensure buy-in to the digital marketing capability building project.

    • Digital Marketing Communication Deck

    4. Identify the product/segment-specific digital marketing landscape to identify required IT capabilities

    Assess how well each digital channel reaches target segments. Identify the capabilities that must be built to enable digital channels.

    5. Create a roadmap for building capabilities to enable digital marketing

    Assess the people, processes, and technologies required to build required capabilities and determine the best fit with your organization.

    [infographic]

    Workshop: Build IT Capabilities to Enable Digital Marketing Success

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Identify Digital Marketing Opportunities

    The Purpose

    Determine the fit of each digital channel with your organizational goals.

    Determine the fit of digital channels with your organizational structure and business model.

    Compare the fit of digital channels with your organization’s current levels of use to:Identify missed opportunities your organization should capitalize on.Identify digital channels that your organization is wasting resources on.

    Identify missed opportunities your organization should capitalize on.

    Identify digital channels that your organization is wasting resources on.

    Key Benefits Achieved

    IT department achieves consensus around which opportunities need to be pursued.

    Understanding that continuing to pursue excellent-fit digital channels that your organization is currently active on is a priority.

    Identification of the channels that stopping activity on could free up resources for.

    Activities

    1.1 Define and prioritize organizational goals.

    1.2 Assess digital channel fit with goals and organizational characteristics.

    1.3 Identify missed opportunities and wasted resources in your digital channel mix.

    1.4 Brainstorm creative ways to pursue untapped digital channels.

    Outputs

    Prioritized list of organizational goals.

    Assigned level of fit to digital channels.

    List of digital channels that represent missed opportunities or wasted resources.

    List of brainstormed ideas for pursuing digital channels.

    2 Identify Your Product-Specific Digital Marketing Landscape

    The Purpose

    Identify the digital channels that will be used for specific products and segments.

    Identify the IT capabilities that must be built to enable digital channels.

    Prioritize the list of IT capabilities.

    Key Benefits Achieved

    IT and marketing achieve consensus around which digital channels will be pursued for specific product-segment pairings.

    Identification of the capabilities that IT must build.

    Activities

    2.1 Assess digital channel fit with specific products.

    2.2 Identify the digital usage patterns of target segments.

    2.3 Decide precisely which digital channels you will use to sell specific products to specific segments.

    2.4 Identify and prioritize the IT capabilities that need to be built to succeed on each digital channel.

    Outputs

    Documented channel fit with products.

    Documented channel usage by target segments.

    Listed digital channels that will be used for each product-segment pairing.

    Listed and prioritized capabilities that must be built to enable success on necessary digital channels.

    3 Enable Digital Marketing Capabilities and Leverage Analytics

    The Purpose

    Identification of the best possible way to build IT capabilities for all channels.

    Creation of a plan for leveraging transformational analytics to supercharge your digital marketing strategy.

    Key Benefits Achieved

    IT understanding of the costs and benefits of capability building options (people, process, and technology).

    Information about how specific technology vendors could fit with your organization.

    IT identification of opportunities to leverage transformational analytics in your organization.

    Activities

    3.1 Identify the gaps in your IT capabilities.

    3.2 Evaluate options for building capabilities.

    3.3 Identify opportunities for transformational analytics.

    Outputs

    A list of IT capability gaps.

    An action plan for capability building.

    A plan for leveraging transformational analytics.

    Make Your IT Governance Adaptable

    • Buy Link or Shortcode: {j2store}359|cart{/j2store}
    • member rating overall impact: 8.0/10 Overall Impact
    • member rating average dollars saved: $123,499 Average $ Saved
    • member rating average days saved: 10 Average Days Saved
    • Parent Category Name: IT Governance, Risk & Compliance
    • Parent Category Link: /it-governance-risk-and-compliance
    • People don’t understand the value of governance, seeing it as a hindrance to productivity and efficiency.
    • Governance is delegated to people and practices that don’t have the ability or authority to make these decisions.
    • Decisions are made within committees that don’t meet frequently enough to support business velocity.
    • It is difficult to allocate time and resources to build or execute governance effectively.

    Our Advice

    Critical Insight

    • IT governance applies not just to the IT department but to all uses of information and technology.
    • IT governance works against you if it no longer aligns with or supports your organizational direction, goals, and work practices.
    • Governance doesn’t have to be bureaucratic or control based.
    • Your governance model should be able to adapt to changes in the organization’s strategy and goals, your industry, and your ways of working.
    • Governance can be embedded and automated into your practices.

    Impact and Result

    • You will produce more value from IT by developing a governance framework optimized for your current needs and context, with the ability to adapt as your needs shift.
    • You will create the foundation and ability to delegate and empower governance to enable agile delivery.
    • You will identify areas where governance does not require manual oversight and can be embedded into the way you work.

    Make Your IT Governance Adaptable Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Make Your IT Governance Adaptable Deck – A document that walks you through how to design and implement governance that fits the context of your organization and can adapt to change.

    Our dynamic, flexible, and embedded approach to governance will help drive organizational success. The three-phase methodology will help you identify your governance needs, select and refine your governance model, and embed and automate governance decisions.

    • Make Your IT Governance Adaptable – Phases 1-3

    2. Adaptive and Controlled Governance Model Templates and Workbook – Documents that gather context information about your organization to identify the best approach for governance.

    Use these templates and workbook to identify the criteria and design factors for your organization and the design triggers to maintain fit. Upon completion this will be your new governance framework model.

    • Controlled Governance Models Template
    • IT Governance Program Overview
    • Governance Workbook

    3. Implementation Plan and Workbook – Tools that help you build and finalize your approach to implement your new or revised governance model.

    Upon completion you will have a finalized implementation plan and a visual roadmap.

    • Governance Implementation Plan
    • Governance Roadmap Workbook

    4. Governance Committee Charter Templates – Base charters that can be adapted for communication.

    Customize these templates to create the committee charters or terms of reference for the committees developed in your governance model.

    • IT PMO Committee Charter
    • IT Risk Committee Charter for Controlled Governance
    • IT Steering Committee Charter for Controlled Governance
    • Program Governance Committee Charter
    • Architecture Review Board Charter
    • Data Governance Committee Charter
    • Digital Governance Committee Charter

    5. Governance Automation Criteria Checklist and Worksheet – Tools that help you determine which governance decisions can be automated and work through the required logic and rules.

    The checklist is a starting point for confirming which activities and decisions should be considered for automation or embedding. Use the worksheet to develop decision logic by defining the steps and information inputs involved in making decisions.

    • Governance Automation Criteria Checklist
    • Governance Automation Worksheet

    Infographic

    Workshop: Make Your IT Governance Adaptable

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Develop Your Guiding Star

    The Purpose

    Establish the context for your governance model.

    Key Benefits Achieved

    Core understanding of the context that will enable us to build an optimal model

    Activities

    1.1 Confirm mission, vision, and goals.

    1.2 Define scope and principles.

    1.3 Adjust for culture and finalize context.

    Outputs

    Governance principles

    Governance context and goals

    2 Define the Governance Model

    The Purpose

    To select and adapt a governance model based on your context.

    Key Benefits Achieved

    A selected and optimized governance model

    Activities

    2.1 Select and refine governance model.

    2.2 Confirm and adjust the structure.

    2.3 Review and adapt governance responsibilities and activities.

    2.4 Validate governance mandates and membership.

    Outputs

    IT governance model and adjustment triggers

    IT governance structure, responsibilities, membership, and cadence

    Governance committee charters

    3 Build Governance Process and Policy

    The Purpose

    Refine your governance practices and associate policies properly.

    Key Benefits Achieved

    A completed governance model that can be implemented with clear update triggers and review timing

    Policy alignment with the right levels of authority

    Activities

    3.1 Update your governance process.

    3.2 Align policies to mandate.

    3.3 Adjust and confirm your model.

    3.4 Identify and document update triggers and embed into review cycle.

    Outputs

    IT governance process and information flow

    IT governance policies

    Finalized governance model

    4 Embed and Automate Governance

    The Purpose

    Identify options to automate and embed governance activities and decisions.

    Key Benefits Achieved

    Simply more consistent governance activities and automate them to enhance speed and support governance delegation and empowerment

    Activities

    4.1 Identify decisions and standards that can be automated. Develop decision logic.

    4.2 Plan verification and validation approach.

    4.3 Build implementation plan.

    4.4 Develop communication strategy and messaging.

    Outputs

    Selected automation options, decision logic, and business rules

    Implementation and communication plan

    Further reading

    Make Your IT Governance Adaptable

    Governance isn't optional, so keep it simple and make it flexible.

    Table of Contents

    4 Analyst Perspective

    5 Executive Summary

    13 Governance Stages

    14 Info-Tech’s IT Governance Thought Model

    19 Info-Tech’s Approach

    23 Insight Summary

    30 Phase 1: Identify Your Governance Needs

    54 Phase 2: Select and Refine Your Governance Model

    76 Phase 3: Embed and Automate

    94 Summary of Accomplishment

    95 Additional Support

    97 Contributors

    98 Bibliography

    Make Your IT Governance Adaptable

    Governance isn't optional, so keep it simple and make it flexible.

    EXECUTIVE BRIEF

    Analyst Perspective

    Governance will always be part of the fabric of your organization. Make it adaptable so it doesn’t constrain your success.

    Photo of Valence Howden, Principal Research Director, Info-Tech Research Group

    Far too often, the purpose of information and technology (I&T) governance is misunderstood. Instead of being seen as a way to align the organization’s vision to its investment in information and technology, it has become so synonymous with compliance and control that even mentioning the word “governance” elicits a negative reaction.

    Success in modern digital organizations depends on their ability to adjust for velocity and uncertainty, requiring a dynamic and responsive approach to governance – one that is embedded and automated in your organization to enable new ways of working, innovation, and change.

    Evolutionary theory describes adaptability as the way an organism adjusts to fit a new environment, or changes to its existing environment, to survive. Applied to organizations, adaptable governance is critical to the ability to survive and succeed.

    If your governance doesn’t adjust to enable your changing business environment and customer needs, it will quickly become misaligned with your goals and drive you to failure.

    It is critical that people build an approach to governance that is effective and relevant today while building in adaptability to keep it relevant tomorrow.

    Valence Howden
    Principal Research Director, Info-Tech Research Group

    Executive Summary

    Your Challenge

    • People don’t understand the value of governance, seeing it as a hindrance to productivity and efficiency.
    • Governance is delegated to people and practices that don’t have the ability or authority to make decisions.
    • Decisions are made within committees that don’t meet frequently enough to support business velocity.
    • It is difficult to allocate time and resources to build or execute governance effectively

    Common Obstacles

    • You are unable to clearly communicate how governance adds value to your organization.
    • Your IT governance approach no longer aligns with or supports your organizational direction, goals, and work practices.
    • Governance is seen and performed as a bureaucratic control-based exercise.
    • Governance activities are not transparent.
    • The governance committee gets too deeply involved with project deep dives and daily management, derailing its effectiveness and ability to produce value.

    Info-Tech’s Approach

    • Use Info-Tech’s IT governance models to identify a base model similar to the way you are organized. Confirm your current and future placement in governance execution.
    • Adjust the model based on industry needs, your principles, regulatory requirements, and your future direction.
    • Identify where to embed or automate decision making and compliance and what is required to do so effectively.
    • Implement your governance model for success.

    Info-Tech Insight

    IT governance must be embedded and automated, where possible, to effectively meet the needs and velocity of digital organizations and modern practices and to drive success and value.

    What is governance?

    IT governance is a critical and embedded practice that ensures that information and technology investments, risks, and resources are aligned in the best interests of the organization and produce business value.

    Effective governance ensures that the right technology investments are made at the right time to support and enable your organization’s mission, vision, and goals.

    5 KEY OUTCOMES OF GOOD GOVERNANCE

    STRATEGIC ALIGNMENT

    Technology investments and portfolios are aligned with the organization's strategic objectives.

    RISK OPTIMIZATION

    Organizational risks are understood and addressed to minimize impact and optimize opportunities.

    VALUE DELIVERY

    IT investments and initiatives deliver their expected benefits.

    RESOURCE OPTIMIZATION

    Resources (people, finances, time) are appropriately allocated across the organization to optimal organizational benefit.

    PERFORMANCE MEASUREMENT

    The performance of technology investments is monitored and used to determine future courses of action and to confirm achievement of success.

    ‹–EVALUATE–DIRECT–MONITOR–›

    Why is this necessary?

    • Governance is not simply a committee or an activity that you perform at a specific point in time; it is a critical and continuously active practice that drives the success of your organization. It is part of your organization’s DNA and is just as unique, with some attributes common to all (IT governance elements), some specific to your family (industry refinements), and some specific to you (individual organization).
    • Your approach to governance needs to change over time in order to remain relevant and continue to enable value and success, but organizations rarely want to change governance once it’s in place.
    • To meet the speed and flow of practices like Lean, DevOps, and Agile, your IT governance needs to be done differently and become embedded into the way your organization works. You must adjust your governance model based on key moments of change – organizational triggers – to maintain the effectiveness of your model.

    Info-Tech Insight

    Build an optimal model quickly and implement the core elements using an iterative approach to ensure the changes provide the most value.

    The Technology Value Trinity

    Delivery of Business Value & Strategic Needs

    • DIGITAL & TECHNOLOGY STRATEGY
      The identification of objectives and initiatives necessary to achieve business goals.
    • IT OPERATING MODEL
      The model for how IT is organized to deliver on business needs and strategies.
    • INFORMATION & TECHNOLOGY GOVERNANCE
      The governance to ensure the organization and its customers get maximum value from the use of information and technology.

    All three elements of the Technology Value Trinity work in harmony to deliver business value and meet strategic needs. As one changes, the others need to change as well.

    • Digital and IT Strategy tells you what you need to achieve to be successful.
    • IT Operating Model and Organizational Design is the alignment of resources to deliver on your strategy and priorities.
    • Information & Technology Governance is the confirmation that IT’s goals and strategy align with the business’ strategy. It is the mechanism by which you continuously prioritize work to ensure that what you deliver is in line with the strategy. This oversight involves evaluating, directing, and monitoring the delivery of outcomes to ensure that the use of resources results in achieving the organization’s goals.

    Too often strategy, operating model and organizational design, and governance are considered separate practices. As a result, “strategic documents” end up being wish lists, and projects continue to be prioritized based on who shouts the loudest rather than on what is in the best interest of the organization.

    Where information & technology governance fits within an organization

    An infographic illustrating where Governance fits within an organization. The main section is titled 'Enterprise Governance and Strategy' and contains 'Value Outcomes', 'Mission and Vision', 'Goals and Objectives', and 'Guiding Principles'. These all feed into the highlighted 'Information & Technology Governance', which then contributes to 'IT Strategy', which lies outside the main section.

    I&T governance hasn’t achieved its purpose

    Governance is the means by which IT ensures that information and technology delivery and spend is aligned to business goals and delivers business outcomes. However, most CEOs continue to perceive IT as being poorly aligned to the business’ strategic goals, which indicates that governance is not implemented or executed properly.

    For I&T governance to be effective you need a clear understanding of the things that drive your organization and its success. This understanding becomes your guiding star, which is critical for effective governance. It also requires participation by all parts of the organization, not just IT.

    Info-Tech CIO/CEO Alignment Diagnostics (N=124)

    43% of CEOs believe that business goals are going unsupported by IT.

    60% of CEOs believe that improvement is required around IT’s understanding of business goals.

    80% of CIOs/CEOs are misaligned on the target role for IT.

    30% of business stakeholders are supporters (N=32,536) of their IT departments

    Common causes of poor governance

    Key causes of poor or misaligned governance

    1. Governance and its value to your organization is not well understood, often being confused or integrated with more granular management activities.
    2. Business executives fail to understand that IT governance is a function of the business and not the IT department.
    3. Poor past experiences have made “governance” a bad word in the organization. People see it as a constraint and barrier that must be circumvented to get work done.
    4. There is misalignment between accountability and authority throughout the organization, and the wrong people are involved in governance practices.
    5. There is an unwillingness to change a governance approach that has served the organization well in the past, leading to challenges when the organization starts to change practices and speed of delivery.
    6. There is a lack of data and data-related capabilities required to support good decision making and the automation of governance decisions.
    7. The goals and strategy of the organization are not known or understood, leaving nothing for IT governance to orient around.

    Key symptoms of ineffective governance committees

    1. No actions or decisions are generated. The committee produces no value and makes no decisions after it meets. The lack of value output makes the usefulness of the committee questionable.
    2. Resources are overallocated. There is a lack of clear understanding of capacity and value in work to be done, leading to consistent underestimation of required resources and poor resource allocation.
    3. Decisions are changed outside of committee. Decisions made or initiatives approved by the committee are later changed when the proper decision makers are involved or the right information becomes available.
    4. Governance decisions conflict with organizational direction. This shows an obvious lack of alignment and behavioral disconnect that work against organizational success. It is often due to not accounting for where power really exists within the structure.
    5. Consistently poor outcomes are produced from governance direction. Committee members’ lack of business acumen, relevant data, or understanding of organizational goals results in decisions that fail to drive successful measured outcomes.

    Mature your governance by transitioning from ad hoc to automated

    Organizations should look to progress in their governance stages. Ad hoc and controlled governance practices tend to be more rigid, making these a poor fit for organizations requiring higher velocity delivery or using more agile and adaptive practices.

    The goal as you progress through these stages is to delegate governance and empower teams based on your fit and culture, enabling teams where needed to make optimal decisions in real time, ensuring that they are aligned with the best interests of the organization.

    Automate governance for optimal velocity while mitigating risks and driving value.

    This puts your organization in the best position to be adaptive, able to react effectively to volatility and uncertainty.

    A graph illustrating the transition from Ad Hoc to Automated. The y-axis is 'Process Integration' and x-axis is 'Trust & Empowerment'. 'Ad Hoc: Inconsistent Decision Making' lies close to the origin, ranking low on both axes' values. 'Controlled: Authoritarian, Highly Structured' ranks slightly higher on both axes. 'Agile: Distributed & Empowered' ranks 2nd highest on both axes. 'Automated: High Velocity, Embedded & Flexible' ranks highest on both axes.

    Stages of governance

    Adaptive
    Data-Centric


    ˆ


    ˆ


    ˆ


    ˆ


    ˆ
    Traditional
    (People- and Document-Centric)

    4

    Automated Governance
    • Entrenched into organizational processes and product/service design
    • Empowered and fully delegated to maintain fit and drive organizational success and survival

    3

    Agile Governance
    • Flexible enough to support different needs in the organization and respond quickly to change
    • Driven by principles and delegated throughout the company

    2

    Controlled Governance
    • Focused on compliance and hierarchy-based authority
    • Levels of authority defined and often driven by regulatory requirements

    1

    Ad Hoc Governance
    • Not well defined or understood within the organization
    • Occurs out of necessity but often not done by the right people or bodies

    Make Governance Adaptable and Automated to Drive Success and Value

    Governance adaptiveness ensures the success of digital organizations and modern practice implementation.

    THE PROBLEM

    • The wrong people are making decisions.
    • Organizations don't understand what governance is or why it's done.
    • Governance scope and design is a bad fit, damaging the organization.
    • People think governance is optional.

    THE SOLUTION

    ESTABLISH YOUR GUIDING PRINCIPLES

    Define and establish the guiding principle that drive your organization toward success.

    • Mission & Vision
    • Business Goals & Success Criteria
    • Operating Model & Work Practices
    • Governance Scope
    • Principles
    SELECT AND REFINE YOUR MODEL

    Use Info-Tech's IT Governance Models to identify a base model similar to the way you are organized. Confirm your current and future placement in governance execution.

    IDENTIFY MODEL UPDATE TRIGGERS

    Adjust the model based on industry needs, your principles, regulatory requirements, and future direction.

    • Principles
      Select principles that allow the organization to be adaptive while still ensuring the governance continues to stay on course with pursuing its guiding star.
    • Responsibilities
      Decide on the governance responsibilities related to Oversight Level, Strategic Alignment, Value Delivery, Risk Optimization, Resource Optimization, and Performance Management.
    • Structure
      Determine at which structured level governance is appropriate: Enterprise, Strategic, Tactical, or Operational.
    • Processes
      Establish processes that will enable governance to occur such as: Embed the processes required for successful governance.
    • Membership
      Identify the Responsibility & Accountability of those who should be involved in governance processes, policies, guidelines, and responsibilities.
    • Policies
      Confirm any governing policies that need to be adhered to and considered to manage risk.
    DETERMINE AUTOMATION OPTIONS AND DECISION RULES

    Identify where to embed or automate decision making and compliance and what is required to do so effectively.

    STAGES OF GOVERNANCE

      Traditional (People- and document-centric)
    1. AD HOC GOVERNANCE
      Governance that is not well defined or understood within the organization. It occurs out of necessity but often not by the right people or bodies.
    2. CONTROLLED GOVERNANCE
      Governance focused on compliance and hierarchy-based, authority-driven control of decisions. Levels of Authority are defined and often driven by regulatory requirements.
    3. Adaptive (Data Centric)
    4. AGILE GOVERNANCE
      Governance that is flexible to support different needs and quick responses in the organization. Driven by principles and delegated throughout the company.
    5. AUTOMATED GOVERNANCE
      Governance that is entrenched and automated into the organizational processes and product/service design. Empowered and fully delegated governance to maintain fit and drive organizational success and survival.

    KEY INSIGHT

    Governance must actively adapt to changes in your organization, environment, and practices or it will drive you to failure.

    Developing governance principles

    Governance principles support the move from controlled to automated governance by providing guardrails that guide your decisions. They provide the ethical boundaries and cultural perspectives that contextualize your decisions and keep you in line with organizational values. Determining principles are global in nature.

    CONTROLLED CHANGE ACTIONS AND RATIONALE AUTOMATED
    Disentangle governance and management Move from governance focused on evaluating, directing, and monitoring strategic decisions around information and technology toward defining and automating rules and principles for decision making into processes and practices, empowering the organization and driving adaptiveness. Delegate and empower
    Govern toward value Move from identifying the organization’s mission, goals, and key drivers toward orienting IT to align with those value outcomes and embedding value outcomes into design and delivery practices. Deliver to defined outcomes
    Make risk-informed decisions Move from governance bodies using risk information to manually make informed decisions based on their defined risk tolerance toward having risk information and attestation baked into decision making across all aspects and layers of the IT organization – from design to sustainment. Embed risk decision making into processes and practices
    Measure to drive improvement Move from static lagging metrics that validate that the work being done is meeting the organization’s needs and guide future decision making toward automated governance with more transparency driven by data-based decision making and real-time data insights. Trust through real-time reporting
    Enforce standards and behavior Move from enforcing standards and behavior and managing exceptions to ensure that there are consistent outcomes and quality toward automating standards and behavioral policies and embedding adherence and changes in behavior into the organization’s natural way of working. Automate standards through automated decision rules, verification, and validation

    Find your guiding star

    MISSION AND VISION –› GOALS AND OBJECTIVES –› GUIDING PRINCIPLES –›

    VALUE

    Why your organization exists and what value it aims to provide. The purpose you build a strategy to achieve. What your organization needs be successful at to fulfill its mission. Key propositions and guardrails that define and guide expected organizational behavior and beliefs.

    Your mission and vision define your goals and objectives. These are reinforced by your guiding principles, including ethical considerations, your culture, and expected behaviors. They provide the boundaries and guardrails for enabling adaptive governance, ensuring you continue to move in the right direction for organizational success.

    To paraphrase Lewis Carroll, “If you don't know where you want to get to, it doesn't much matter which way you go.” Once you know what matters, where value resides, and which considerations are necessary to make decisions, you have consistent directional alignment that allows you to delegate empowered governance throughout the organization, taking you to the places you want to go.

    Understand governance versus management

    Don’t blur the lines between governance and management; each has a unique role to play. Confusing them results in wasted time and confusion around ownership.

    Governance

    I&T governance defines WHAT should be done and sets direction through prioritization and decision making, monitoring overall IT performance.

    Governance aligns with the mission and vision of the organization to guide IT.

    A cycle of processes split into two halves, 'Governance Processes' and 'Management Processes'. Beginning on the Management side, the processes are 'Plan', 'Build', 'Run', 'Monitor', then to the Governance side, 'Evaluate', 'Direct', 'Monitor', and back to the beginning.

    Management

    Management focuses on HOW to do things to achieve the WHAT. It is responsible for executing on, operating, and monitoring activities as determined by I&T governance.

    Management makes decisions for implementation based on governance direction.

    Data is critical to automating governance

    Documents and subjective/non-transparent decisions do not create sufficient structure to allow for the true automation of governance. Data related to decisions and aggregated risk allow you to define decision logic and rules and algorithmically embed them into your organization.

    People- and Document-Centric

    Governance drives activities through specific actors (individuals/committees) and unstructured data in processes and documents that are manually executed, assessed, and revised. There are often constraints caused by gaps or lack of adequate and integrated information in support of good decisions.

    Data-Centric

    Governance actors provide principles, parameters, and decision logic that enable the creation of code, rulesets, and algorithms that leverage organizational data. Attestation is automatic – validated and managed within the process, product, or service.

    Info-Tech’s Approach

    Define your context and build your model

    ESTABLISH YOUR GUIDING PRINCIPLES

    Define and establish the guiding principle that drive your organization toward success.

    • Mission & Vision
    • Business Goals & Success Criteria
    • Operating Model & Work Practices
    • Governance Scope
    • Principles
    SELECT AND REFINE YOUR MODEL

    Use Info-Tech's IT Governance Models to identify a base model similar to the way you are organized. Confirm your current and future placement in governance execution.

    MODEL UPDATE TRIGGERS

    Adjust the model based on industry needs, your principles, regulatory requirements, and future direction.

    • Principles
      Select principles that allow the organization to be adaptive while still ensuring the governance continues to stay on course with pursuing its guiding star.
    • Responsibilities
      Decide on the governance responsibilities related to Oversight Level, Strategic Alignment, Value Delivery, Risk Optimization, Resource Optimization, and Performance Management.
    • Structure
      Determine at which structured level governance is appropriate: Enterprise, Strategic, Tactical, or Operational.
    • Processes
      Establish processes that will enable governance to occur such as: Embed the processes required for successful governance.
    • Membership
      Identify the Responsibility & Accountability of those who should be involved in governance processes, policies, guidelines, and responsibilities.
    • Policies
      Confirm any governing policies that need to be adhered to and considered to manage risk.
    AUTOMATION OPTIONS AND DECISION RULES

    Identify where to embed or automate decision making and compliance and what is required to do so effectively.

    The Info-Tech Difference

    Define your context and build your model

    1. Quickly identify the organizational needs driving governance and your guiding star.
    2. Select and refine a base governance model based on our templates.
    3. Define and document the key changes in your organization that will trigger a need to update or revise your governance.
    4. Determine where you might be able to automate aspects of your governance.
    5. Design your decision rules where appropriate to support automated and adaptive governance.

    How to use this research

    Where are you in your governance optimization journey?

    MY GOVERNANCE IS AD HOC AND WE’RE STARTING FROM SCRATCH I NEED TO BUILD A NEW GOVERNANCE STRUCTURE OUR GOVERNANCE APPROACH IS INEFFECTIVE AND NEEDS IMPROVEMENT I NEED TO LOOK AT OPTIONS FOR AUTOMATING GOVERNANCE PRACTICES
    Step 1.1: Define Your Governance Context Step 1.2: Structure Your IT Governance Phase 2: Select and Refine Your Model Phase 3: Embed and Automate

    IT governance is about ensuring that the investment decisions made around information and technology drive the optimal organizational value, not about governing the IT department.

    In this section we will clarify your organizational context for governance and define your guiding star to orient your governance design and inform your structure.

    There is no need to start from scratch! Start with Info-Tech’s best-practice IT governance models and customize them based on your organizational context.

    The research in this section will help you to select the right base model to work from and provide guidance on how to refine it.

    Governance practices eventually stop being a good fit for a changing organization, and things that worked before become bottlenecks.

    Governing roles and committees don’t adjust well, don’t have consistent practices, and lack the right information to make good decisions.

    The research in this section will help you improve and realign your governance practices.

    Once your governance is controlled and optimized you are ready to investigate opportunities to automate.

    This phase of the blueprint will help you determine where it’s feasible to automate and embed governance, understand key governance automation practices, and develop governing business rules to move your journey forward.

    Related Research:

    If you are looking for details on specific associated practices, please see our related research:

    1. I need to establish data governance.
    2. I need to manage my project portfolio, from intake to confirmation of value.
    3. I need better risk information to support decision making.
    4. I need to ensure I am getting the expected outcomes and benefits from IT spend.
    5. I need to prioritize my product backlog or service portfolio.

    Info-Tech’s methodology for building and embedding adaptive governance

    1. Identify Your Governance Needs 2. Select and Refine Your Governance Model 3. Embed and Automate
    Phase Steps
    1. Confirm Mission, Vision, and Goals
    2. Define Scope and Principles
    3. Adjust for Culture and Finalize Context
    1. Select and Refine Your Governance Model
    2. Identify and Document Your Governance Triggers
    3. Build Your Implementation Plan
    1. Identify Decisions to Embed and Automate
    2. Plan Validation and Verification
    3. Update Implementation Plan
    Phase Outcomes
    • Governance context, guiding star, and principles
    • Completed governance model with associated decisions and policies
    • Implementation plan
    • List of automation options
    • Decision logic, rules, and rulesets
    • Validation and verification approach
    • Finalized implementation plan

    Insight summary

    Value

    To remain valuable, I&T governance must actively adapt to changes in your organization, environment, and practices, or it will drive you to failure instead of success.

    Focus

    I&T governance does not focus on the IT department. Rather, its intent is to ensure your organization makes sound decisions around investment in and use of information and technology.

    Maturity

    Your governance approach progresses in stages from ad hoc to automated as your organization matures. Your stage depends on your organizational needs and ways of working.

    Good governance

    Good governance does not equate to control and does not stifle innovation.

    Automation

    Automating governance must be done in stages, based on your capabilities, level of maturity, and amount of usable data.

    Strategy

    Establish the least amount of governance required to allow you to achieve your goals.

    Guiding star

    If you don’t establish a guiding star to align the different stakeholders in your organization, governance practices will create conflict and confusion.

    Blueprint deliverables

    Each step of this blueprint is accompanied by supporting deliverables to help you accomplish your goals:

    Key Deliverable:
    Governance Framework Model

    The governance framework model provides the design of your new governance model and the organizational context to retain stakeholder alignment and organizational satisfaction with governance.

    The model includes the structures, practices, and responsibilities to drive effective governance in your organization.

    Sample of the key blueprint deliverable 'Governance Framework Model'.

    Governance Implementation Plan

    This roadmap lays out the changes required to implement the governance model, the cultural items that need to be addressed, and anticipated timing.

    Sample of the blueprint deliverable 'Governance Implementation Plan'.

    Governance Committee Charters

    Develop a detail governance charter or term of reference for each governing body. Outline the mandate, responsibilities, membership, process, and associated policies for each.

    Sample of the blueprint deliverable 'Governance Committee Charters'.

    Blueprint benefits

    IT Benefits

    • Stronger, traceable alignment of IT decisions and initiatives to business needs.
    • Improved ability for IT to meet the changing demands and velocity of the business.
    • Better support and enablement of innovation – removing constraints and barriers.
    • Optimized governance that supports and enables modern work practices.
    • Increased value generation from IT initiatives and optimal use of IT resources.
    • Designed adaptability to ensure you remain in alignment as your business and IT environments change.

    Business Benefits

    • Clear transparent focus of IT initiatives on generating strategic business value.
    • Improved ability to measure the value and contribution of IT to business goals.
    • Alignment and integration of business/IT strategy.
    • Optimized development and use of IT capabilities to meet business needs.
    • Improved integration with corporate/enterprise governance.

    Executive Brief Case Study

    INDUSTRY Manufacturing
    SOURCE Info-Tech analyst experience

    Improving the governance approach and delegating decision making to support a change in business operation

    Challenge

    The large, multi-national organization has locations across the world but has two primary headquarters, in Europe and the United States.

    Market shifts drove an organizational shift in strategy, leading to a change in operating models, a product focus, and new work approaches across the organization.

    Much of the implementation and execution was done in isolation, and effectiveness was slowed by poor integration and conflicting activities that worked against each other.

    The product owner role was not well defined.

    Solution

    After reviewing the organization’s challenges and governance approach, we redefined and realigned its organizational and regional goals and identified outcomes that needed to be driven into their strategies.

    We also reviewed their span of control and integration requirements and properly defined decisions that could be made regionally versus globally, so that decisions could be made to support new work practices.

    We defined the product and service owner roles and the decisions each needed to make.

    Results

    We saw an improvement in the alignment of organizational activities and the right people and bodies making decisions.

    Work and practices were aimed at the same key outcomes and alignment between teams toward organizational goal improved.

    Within one year, the success rate of the organization’s initiatives increased by 22%, and the percentage of product-related decisions made by product owners increased by 50%.

    Info-Tech offers various levels of support to best suit your needs

    DIY Toolkit

    Guided Implementation

    Workshop

    Consulting

    "Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful." "Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track." "We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place." "Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project."

    Diagnostics and consistent frameworks used throughout all four options

    Guided Implementation

    A Guided Implementation (GI) is a series of calls with an Info-Tech analyst to help implement our best practices in your organization.

    A typical GI is between 5 and 8 calls over the course of 2 to 3 months.

    What does a typical GI on this topic look like?

      Phase 1: Identify Your Governance Needs

    • Call #1: Confirm your organization’s mission and vision and review your strategy and goals.
    • Call #2: Identify considerations and governance needs. Develop your guiding star and governing principles.
    • Phase 2: Select and Refine Your Model

    • Call #3: Select your base model and optimize it to meet your governance needs.
    • Call #4: Define your adjustment triggers and develop your implementation plan.
    • Phase 3: Embed and Automate

    • Call #5: Identify decisions and standards you can automate and where to embed them.
    • Call #6: Confirm levels of authority and data requirements. Establish your approach and update the implementation plan.

    Workshop Overview

    Contact your account representative for more information.
    workshops@infotech.com1-888-670-8889

    Session 1 Session 2 Session 3 Session 4 Session 5
    Activities
    Develop Your Guiding Star

    1.1 Confirm mission, vision, and goals

    1.2 Define scope and principles

    1.3 Adjust for culture and finalize context

    Define the Governance Model

    2.1 Select and refine governance model

    2.2 Confirm and adjust the structure

    2.3 Review and adapt governance responsibilities and activities

    2.4 Validate governance mandates and membership

    Build Governance Process and Policy

    3.1 Update your governance process

    3.2 Align policies to mandate

    3.3 Adjust and confirm your governance model

    3.4 Identify and document your update triggers

    3.5 Embed triggers into review cycle

    Embed and Automate Governance

    4.1 Identify decisions and standards to automate

    4.2 Plan verification and validation approach

    4.3 Build implementation plan

    4.4 Develop communication strategy and messaging

    Next Steps and Wrap-Up

    5.1 Complete in-progress outputs from previous four sessions

    5.2 Set up review time for workshop outputs and to discuss next steps

    Outcomes
    1. Governance context and goals
    2. Governance principles
    1. IT governance model and adjustment triggers
    2. IT governance structure, responsibilities, membership, and cadence
    3. Governance committee charters
    1. IT governance process and information flow
    2. IT governance policies
    3. Finalized governance model
    1. Selected automation options, decision logic, and business rules
    2. Implementation and communication plan
    1. Governance context and principles
    2. Finalized governance model and charters
    3. Finalized implementation plan

    Make Your IT Governance Adaptable

    Phase 1

    Identify your Governance Needs

    Phase 1

    • 1.1 Define Your Guiding Star
    • 1.2 Define Scope and Principles
    • 1.3 Adjust for Culture and Finalize Context

    Phase 2

    • 2.1 Choose and Adapt Your Model
    • 2.2. Identify and Document Your Governance Triggers
    • 2.3 Build Your Implementation Approach

    Phase 3

    • 3.1 Identify Decisions to Embed and Automate
    • 3.2 Plan Validation and Verification
    • 3.3 Update Implementation Plan

    This phase will walk you through the following activities:

    Identify the organization’s goals, mission, and vision that will guide governance.

    Define the scope of your governance model and the principles that will guide how it works.

    Account for organizational attitudes, behaviors, and culture related to governance and finalize your context.

    This phase involves the following participants:

    • Senior IT leadership
    • Governance leads

    Step 1.1

    Define Your Guiding Star

    Activities
    • 1.1.1 Document and interpret your strategy, mission, and vision
    • 1.1.2 Document and interpret the business and IT goals and outcomes
    • 1.1.3 Identify your operating model and work processes

    This step will walk you through the following activities:

    Review your business and IT strategy, mission, and vision to ensure understanding of organizational direction.

    Identify the business and IT goals that governance needs to align.

    Confirm your operating model and any work practices that need to be accounted for in your model.

    This step involves the following participants:

    • Senior IT leadership
    • Governance leads

    Outcomes of this step

    Identified guiding star outcomes to align governance outcomes with

    Defined operating model type and work style that impact governance design

    Identify Your Governance Needs

    Step 1.1 – Define your Guiding Star Step 1.2 – Define Scope and Principles Step 1.3 – Adjust for Culture and Finalize Context

    Govern by intent

    Find the balance for your designed governance approach

    Organic governance occurs during the formation of an organization and shifts with challenges, but it is rarely transparent and understood. It changes your culture in uncontrolled ways. Intentional governance is triggered by changes in organizational needs, working approaches, goals, and structures. It is deliberate and changes your culture to enable success.
    Stock photo of a weight scale.

    Info-Tech Insight

    Your approach to governance needs to be designed, even if your execution of governance is adaptable and delegated.

    What is your guiding star?

    Your guiding star is a combination of your organization’s mission, vision, and strategy and the goals that have been defined to meet them.

    It provides you with a consistent focal point around which I&T-related activities and projects orbit, like planets around a star.

    It generates the gravity that governance uses to keep things from straying too far away from the goal of achieving relevant value.

    1. Mission & Vision
    2. Business Goals & Success Criteria
    3. Operating Model & Work Practices
    4. Governance Scope
    5. Principles

    1.1.1 Document and interpret your strategy, mission, and vision

    30 minutes

    Input: Business strategy, IT strategy, Mission and vision statements

    Output: Updated Governance Workbook, Documented strategic outcomes and organizational aims that governance needs to achieve

    Materials: Whiteboard/flip charts, Governance Workbook

    Participants: IT senior leadership

    1. Gather your available business, digital, and IT strategy, mission, and vision information and document everything in your Governance Workbook. It’s ok if you don’t have all of it.
    2. Review and your mission and vision as a group. Discuss and document key points, including:
      • Which activities do you perform as an organization that embody your vision?
      • What key decisions and behaviors are required to ensure that your mission and vision are achievable?
      • What do you require from leadership to enable you to govern effectively?
      • What are the implications of the mission and vision on how the organization needs to work? What are the implications on decisions around opportunities and risks?

    Download the Governance Workbook

    1.1.2 Document and interpret the business and IT goals and outcomes

    60 minutes

    Input: Business strategy, Business and IT goals and related initiatives

    Output: Required success outcomes for goals, Links between IT and business goals that governance needs to align

    Materials: Whiteboard/flip charts

    Participants: IT senior leadership

    1. Document the business and IT goals that have been created to achieve the mission and vision.
    2. Discuss if there are any gaps between the goals and the mission and vision. Ask yourself – if we accomplish these goals will we have successfully achieved the mission?
    3. For each goal, define what successful achievement of the goal looks like. Starting with one goal or objective, ask:
      • How would I know I am on the right path and how will I know I have gotten there?
      • How would I know if I am not on the right path and what does a bad result look like?
    4. Document your success criteria.
    5. Brainstorm some examples of decisions that support or constrain the achievement of your goals.
    6. Repeat this exercise for your remaining goals.
    7. As a group, map IT goals to business goals.

    What is your operating model and why is it important?

    An IT operating model is a visual representation of the way your IT organization needs to be designed and the capabilities it requires to deliver on the business mission, strategic objectives, and technological ambitions.

    The model is critical in the optimization and alignment of the IT organization’s structure in order to deliver the capabilities required to achieve business goals. It is a key determinant of how governance needs to be designed and where it is implemented.

    Little visualizations of different operating models: 'Centralized', 'Decentralized', and 'Hybrid'.

    1.1.3 Identify your operating model and work practices

    60 minutes

    Input: Organizational structure, Operating model (if available)

    Output: Confirmed operating approach, Defined work practices

    Materials: Whiteboard/flip charts

    Participants: IT senior leadership

    1. Identify the way your organization functions:
      • How do we currently operate? Are we centralized, decentralized or a hybrid? Are we focused on delivering products and services? Do we provide service ourselves or do we use vendors for delivery?
      • Can we achieve our mission, goals, and strategies, if we continue to operate this way? What would we have to change in how we operate to be successful in the future?
    2. Identify your governance needs. Do we need to be more structured or more flexible to support our future ways of working?
      • If you operate in a more traditional way, consider whether you are implementing or moving toward more modern practices (e.g. Agile, DevOps, enterprise service management). Do you need to make more frequent but lower-risk decisions?
      • Is your organization ready to delegate governance culturally and in terms of business understanding? Is there enough available information to support adaptive decisions and actions?
    3. Document your operating style, expected changes in work style, and cultural readiness. You will need to consider the implications on design.

    Step 1.2

    Define Scope and Principles

    Activities
    • 1.2.1 Determine the proper scope for your governance
    • 1.2.2 Confirm your determining governing principles
    • 1.2.3 Develop your specific governing principles

    This step will walk you through the following activities:

    Identify what is included and excluded within the scope of your governance.

    Develop the determining and specific principles that provide guardrails for governance activities and decisions.

    This step involves the following participants:

    • Senior IT leadership
    • Governance leads

    Outcomes of this step

    Documented governance scope and principles to apply

    Identify Your Governance Needs

    Step 1.1 – Define your Guiding Star Step 1.2 – Define Scope and Principles Step 1.3 – Adjust for Culture and Finalize Context

    Define the context for governance

    Based on the goals and principles you defined and the operating model you selected, confirm where oversight will be necessary and at what level. Focus on the necessity to expedite and clear barriers to the achievement of goals and on the ownership of risks and compliance. Some key considerations:

    • Where in the organization will you need to decide on work that needs to be done?
    • What type of work will you need to do?
    • In what areas could there be conflicts in prioritization/resource allocation to address?
    • Who is accountable for risks to the organization and its objectives?
    • Where are your regional or business-unit-specific concerns that require focused local attention?
    • Are we using more agile, rapid delivery methods to produce work?

    Understand your governance scope

    Your governance scope helps you define the boundaries of what your governance model and practices will cover. This includes key characteristics of your organization that impact what governance needs to address.

    Sample Considerations

    • Organizational Span
      • The geographical area the organization operates within. Regional laws and requirements will affect governance delegation and standards/policy development.
    • Level of Regulation
      • Higher levels of regulation create more standards and controls for risk and compliance, impacting how authority can be delegated or automated.
    • Sourcing Model
      • Changing technology sourcing introduces additional vendor governance requirements and may impact compliance and audit.
    • Risk Posture
      • The appetite for risk organizationally, and in pockets, impacts the level of uncertainty you are willing to work within and impact decision-making authority positioning.
    • Size
      • The size of your organization impacts the approach to governance, practice implementation, and delegation of authority.
    • What Is Working Today?
      • Which elements of your current governance approach should be retained, and what are the biggest pain points that need to be addressed?
    (Source: COBIT 2019)

    1.2.1 Determine the proper scope for your governance

    60 minutes

    Input: Context information from Activity 1.1, Scoping areas

    Output: Defined scope and span of control

    Materials: Whiteboard/flip charts

    Participants: IT senior leadership

    1. Determine the scope/span of control required for your governance by:
      • Reviewing your key IT capabilities. Identify the ones where the responsibilities and decisions require oversight to ensure they meet the needs of the organization.
      • Identify what works well or poorly in your current governance approach.
      • Discuss and document the level and type of knowledge and business understanding required.
      • Identify and document any regulations, standards, or laws that apply to your organization/industry and how broadly they have to be applied.
      • Identify the organization’s risk appetite, where known, and areas where acceptable thresholds of risk have been defined. Where are key risk and opportunity decisions made? Who owns risk in your organization?
      • Identify and document the perceived role of the IT group in your organization (e.g. support, innovator, partner) and sourcing model (e.g. insource, outsource).
      • Is there sufficient information and data available in your organization to support effective decision making?

    How should your governance be structured?

    Organizations often have too many governance bodies, creating friction without value. Where that isn’t the case, the bodies are often inefficient, with gaps or overlaps in accountability and authority. Structure your governance to optimize its effectiveness, designing with the intent to have the fewest number of governing bodies to be effective, but no less than is necessary.

    Start with your operating model.

    • Understand what’s different about your governance based on whether your organization in centralized, distributed, or a different model (e.g. hybrid, product).
    • Identify and include governance structures that are mandatory due to regulation or industry.
    • Based on your context, identify how many of your governance activities should be performed together.

    Determine whether your governance should be controlled or adaptive.

    • Do you have the capability to distribute governance and is your organization empowered enough culturally?
    • Do you have sufficient standards and data to leverage? Do you have the tools and capabilities?
    • Identify governance structures that are required due to regulation or industry.

    Info-Tech Insight

    Your approach to governance needs to be designed and structured, even if your execution of governance is adaptable and delegated.

    Identify and Refine your Principles

    Confirm your defining principles based on your selection of controlled or adaptive governance. Create specific principles to clarify boundaries or provide specific guidance for teams within the organization.

    Controlled Adaptive
    Disentangle governance and management Delegate and empower
    Govern toward value Deliver to defined outcomes
    Make risk-informed decisions Embed risk into decision making
    Measure to drive improvement Trust though real-time reporting
    Enforce standards and behavior Automate decision making though established standards

    Determining Principle: Delegate and empower.

    Specific Principle: Decisions should be made at the lowest reasonable level of the organization with clarity.

    Rationale: To govern effectively with the velocity required to address business needs, governance needs to be executed deeper into the organization and organizational goals need to be clearly understood everywhere.

    Implication: Decision making needs to be delegated throughout the organization, so information and data requirements need to be identified, decision-making approach and principles need to be shared, and authority needs to be delegated clearly.

    1.2.2 Confirm your determining governance principles

    30-45 minutes

    Input: Governance Framework Model– Governance Principles

    Output: Governance workbook - Finalized list of determining principles

    Materials: Whiteboard/flip charts, Governance Workbook

    Participants: IT senior leadership

    1. Review the IT governance principles in your Governance Workbook.
    2. Within your IT senior leadership team (or IT governance working group) assign one or two principles to teams of two to three participants. Have each team identify what this would mean for your organization. Answering the questions:
      • In what ways do our current governance practices support this?
      • What are some examples of changes that would need to be made to make this a reality?
      • How would applying this principle improve your governance?
    3. Have each team present their results and compile the findings and implications in the Governance Workbook to use for future communication of the change.

    Specific governing principles

    Specific governing principles are refined principles derived from a determining principle, when additional specificity and detail is necessary. It allows you to define an approach for specific behaviors and activities. Multiple specific principles may underpin the determining one.

    A visualization of a staircase with stairs labelled, bottom to top, 'Determining Principle', 'Rationale', 'Implications', 'Specific Principles'.

    Specific Principles – Related principles that may be required to ensure the implications of the determining principal are addressed within the organization. They may be specific to individual areas and may be addressed in policies.

    Implications – The implications of this principle on the organization, specific to how and where governance is executed and the level of information and authority that would be necessary.

    Rationale – The reason(s) driving the determining principle.

    Determining Principle – A core overarching principle – a defining aspect of your governance model.

    1.2.3 Develop your specific governing principles

    30 minutes

    Input: Updated determining principles

    Output: List of specific principles linked to determining principles

    Materials: Whiteboard/flip charts, Governance Workbook

    Participants: IT senior leadership

    1. Confirm the determining principles for your governance model based on your previous discussions.
    2. Identify where to apply the principles. This is based on:
      1. Your governance scope (how much is within your span of control)
      2. The amount of data you have available
      3. Your cultural readiness for delegation
    3. Create specific principles to support the determining principles:
      1. Document the rationale driving the determining principles.
      2. Identify the implications.
      3. Create specific principles that will support the success in achieving the goals of each determining principle.
    4. Document all information on the “Governance guiding star” slide in the Governance Workbook.

    Download the Governance Workbook

    Step 1.3

    Adjust for Culture and Finalize Context

    Activities
    • 1.3.1 Identify and address the impact of attitude, behavior, and culture
    • 1.3.2 Finalize your context

    This step will walk you through the following activities:

    Identify your organizational attitude, behavior, and culture related to governance.

    Identify positives that can be leveraged and develop means to address negatives.

    Finalize the context that your model will leverage and align to.

    This step involves the following participants:

    • Senior IT leadership
    • Governance leads

    Outcomes of this step

    Downloaded tool ready to select the base governance model for your organization

    Identify Your Governance Needs

    Step 1.1 – Define your Guiding Star Step 1.2 – Define Scope and Principles Step 1.3 – Adjust for Culture and Finalize Context

    Understanding attitude, behavior, and culture

    A

    ttitude

    What people think and feel. It can be seen in their demeanor and how they react to change initiatives, colleagues, and users. This manifests in the belief that governance is a constraint that needs to be avoided or ignored – often with unintended consequences.

    A stock photo of a lightbulb over a person's head and a blackboard behind them reading 'New Mindset - data-verified= New Results'.">
    Any form of organizational change involves adjusting people’s attitudes to create buy-in and commitment.

    You need to identify and address attitudes that can lead to negative behaviors and actions or that are counter-productive.

    Understanding attitude, behavior, and culture

    B

    ehavior

    What people do. This is influenced by attitude and the culture of the organization. In governance, this manifests as people’s willingness to be governed, who pushes back, and who tries to bypass it.

    A stock photo of someone walking up a set of stairs into the distant sunlight.

    To implement change within IT, especially at a tactical and strategic level, organizational behavior needs to change.

    This is relevant because people gravitate toward stability and will resist change in an active or passive way unless you can sell the need, value, and benefit of changing their behavior and way of working.

    Understanding attitude, behavior, and culture

    C

    ulture

    The accepted and understood ways of working in an organization. The values and standards that people find normal and what would be tacitly identified to new resources. In governance terms, this is how decisions are really made and where responsibility really exists rather than what is identified formally.

    A stock photo of a compass pointing to 'VALUES'.

    The impact of the organizational or corporate “attitude” on employee behavior and attitude is often not fully understood.

    Culture is an invisible element, which makes it difficult to identify, but it has a strong impact and must be addressed to successfully embed governance models. In the case of automating governance, cultural readiness for automation is a critical success factor.

    1.3.1 Identify and address the impact of attitude, behavior, and culture

    45 minutes

    Input: Senior leadership knowledge

    Output: Updated Governance Workbook

    Materials: Governance Workbook

    Participants: IT senior leadership

    1. Break into three groups. Each group will discuss and document the positive and negative aspects of one of attitude, behavior, or culture related to governance in your organization.
    2. Each group will present and explain their list to the group.
    3. Add any additional suggestions in each area that are identified by the other groups.
    4. Identify the positive elements of attitude, behavior, and culture that would help with changing or implementing your updated governance model.
    5. Identify any challenges that will need to be addressed for the change to be successful.
    6. As a group, brainstorm some mitigations or solutions to these challenges. Document them in the Governance Workbook to be incorporated into the implementation plan.

    Download the Governance Workbook

    Attitude, behavior, and culture

    Evaluate the organization across the three contexts. The positive items represent opportunities for leveraging these characteristics with the implementation of the governance model, while the negative items must be considered and/or mitigated.

    Attitude Behavior Culture
    Positive
    Negative
    Mitigation

    1.3.2 Finalize your governance context

    30 minutes

    Input: Documented governance principles and scope from previous exercises

    Output: Finalized governance context in the Governance Workbook

    Materials: Whiteboard/flip charts, Governance Workbook

    Participants: IT senior leadership

    1. Use the information that has been gathered throughout this section to update and finalize your IT governance context.
    2. Document it in your Governance Workbook.

    Download the Governance Workbook

    Make Your IT Governance Adaptable

    Phase 2

    Select and Refine Your Governance Model

    Phase 1

    • 1.1 Define Your Guiding Star
    • 1.2 Define Scope and Principles
    • 1.3 Adjust for Culture and Finalize Context

    Phase 2

    • 2.1 Choose and Adapt Your Model
    • 2.2. Identify and Document Your Governance Triggers
    • 2.3 Build Your Implementation Approach

    Phase 3

    • 3.1 Identify Decisions to Embed and Automate
    • 3.2 Plan Validation and Verification
    • 3.3 Update Implementation Plan

    This phase will walk you through the following activities:

    Select a base governance model and refine it to suit your organization.

    Identify scenarios and changes that will trigger updates to your governance model.

    Build your implementation plan.

    This phase involves the following participants:

    • Senior IT leadership
    • Governance resources

    Step 2.1

    Choose and Adapt Your Model

    Activities
    • 2.1.1 Choose your base governance model
    • 2.1.2 Confirm and adjust the structure of your model
    • 2.1.3 Define the governance responsibilities
    • 2.1.4 Validate the governance mandates and membership
    • 2.1.5 Update your committee processes
    • 2.1.6 Adjust your associated policies
    • 2.1.7 Adjust and confirm your governance model

    This step will walk you through the following activities:

    Review and selecting your base governance model.

    Adjust the structure, responsibilities, policies, mandate, and membership to best support your organization.

    This step involves the following participants:

    • Senior IT leadership
    • Governance leads

    Outcomes of this step

    Downloaded tool ready to select the base governance model for your organization

    Select and Refine Your Governance Model

    Step 2.1 – Choose and Adapt Your Model Step 2.2 – Identify and Document Your Governance Triggers Step 2.3 – Build Implementation Approach

    Your governance framework has six key components

    GOVERNANCE FRAMEWORK

    • GUIDELINES
      The key behavioral factors that ground your governance framework
    • MEMBERSHIP
      Formalization of who has authority and accountability to make specific governance decisions
    • RESPONSIBILITIES
      The definition of which decisions and outcomes your governance structure and each governance body is accountable for
    • STRUCTURE
      Which governance bodies and roles are in place to articulate where decisions are made in the organization
    • PROCESS
      Identification of the how your governance will be executed, how decisions are made, and the inputs, outputs, and connections to related processes
    • POLICY
      Set of principles established to address risk and drive expected and required behavior

    4 layers of governance bodies

    There are traditionally 4 layers of governance in an enterprise, and organizations have governing bodies or individuals at each level

    RESPONSIBILITIES AND TYPICAL MEMBERSHIP
    ENTERPRISE Defines organizational goals. Directs or regulates the performance and behavior of the enterprise, ensuring it has the structure and capabilities to achieve its goals.

    Membership: Business executives, Board

    STRATEGIC Ensures IT initiatives, products, and services are aligned to organizational goals and strategy and provide expected value. Ensure adherence to key principles.

    Membership: Business executives, CIO, CDO

    TACTICAL Ensures key activities and planning are in place to execute strategic initiatives.

    Membership: Authorized division leadership, related IT leadership

    OPERATIONAL Ensures effective execution of day-to-day functions and practices to meet their key objectives.

    Membership: Service/product owners, process owners, architecture leadership, directors, managers

    2.1.1 Choose your base governance model

    30 minutes

    Input: Governance models templates

    Output: Selected governance model

    Materials: Whiteboard/flip charts

    Participants: IT senior leadership

    1. Download Info-Tech’s base governance models (Controlled Governance Models Template and IT Governance Program Overview) and review them to find a template that most closely matches your context from Phase 1. You can start with a centralized, decentralized, or product/service hybrid IT organization. Remove unneeded models.
    2. If you do not have documented governance today, start with a controlled model as your foundation. Continue working through this phase if you have a documented governance framework you wish to optimize using our best practices or move to Phase 3 if you are looking to automate or embed your governance activities.

    Controlled Governance Models Template

    Adaptive Governance Models Template

    2.1.2 Confirm and adjust the structure of your model

    30-45 minutes

    Input: Selected base governance model, Governance context/scope

    Output: Updated governance bodies and relationships

    Materials: Whiteboard/flip charts

    Participants: IT senior leadership

    1. Validate your selected governance body structural model.
      • Are there any governing bodies you must maintain that should replace the ones listed? In part or in full?
      • Are there any missing bodies? Look at alternative committees for examples.
      • Document the adjustments.
    2. Are there any governing bodies that are not required?
      • Based on your size and needs, can they be done within one committee?
      • Is the capability or data not in place to perform the work?
      • Document the required changes.

    There are five key areas of governance responsibility

    A cyclical visualization of the five keys areas of governance responsibility, 'Strategic Alignment', 'Value Delivery', 'Risk Management', 'Resource Management', and 'Performance Measurement'.

    STRATEGIC ALIGNMENT
    Ensures that technology investments and portfolios are aligned with the organization’s needs.

    VALUE DELIVERY
    Reviews the outcomes of technology investments and portfolios to ensure benefits realization.

    RISK MANAGEMENT
    Defines and owns the risk thresholds and register to ensure that decisions made are in line with the posture of the organization.

    RESOURCE MANAGEMENT
    Ensures that people, financial knowledge, and technology resources are appropriately allocated across the organization.

    PERFORMANCE MEASUREMENT
    Monitors and directs the performance or technology investments to determine corrective actions and understand successes.

    2.1.3 Define the governance responsibilities

    Ensure you have the right responsibilities in the right place

    45-60 minutes

    Input: Selected governance base model, Governance context

    Output: Updated responsibilities and activities, Updated activities for selected governance bodies, New or removed governing bodies

    Materials: Whiteboard/flip charts

    Participants: IT senior leadership

    1. Based on your context and model, review the responsibilities identified for each committee and confirm that they align with the mandate and the stated outcome.
    2. Identify and highlight any responsibilities and activities that would not be involved in informing and enabling the mandate of the committee.
    3. Adjust the wording of confirmed responsibilities and activities to reflect your organizational language.
    4. Review each highlighted “bad fit” activity and move it to a committee whose mandate it would support or remove it if it’s not performed in your organization.
    5. If an additional committee is required, define the mandate and scope, then include any additional responsibilities that might have been a bad fit elsewhere

    2.1.4 Validate the governance mandates and membership

    30 minutes

    Input: Selected governance base model, Updated structure and responsibilities

    Output: Adjusted mandates and refined committee membership

    Materials: Whiteboard/flip charts

    Participants: IT senior leadership

    1. Review the mandate and membership slides in your selected governance model.
    2. Adjust the mandate to ensure that it aligns to and conveys:
      1. The outcome that the committee is meant to generate for the organization.
      2. Its scope/span of control.
    3. Discuss the type of information members would require for the committee to be successful in achieving its mandate.
    4. Document the member knowledge requirement in the mandate slide of the model template.

    Determine the right membership for your governance

    One of the biggest benefits of governance committees is the perspective provided by people from various parts of the organization, which helps to ensure technology investments are aligned with strategic goals. However, having too many people – or the wrong people – involved prevents the committee from being effective. Avoid this by following these principles.

    Three principles for selecting committee membership

    1. Determine membership based on responsibilities and required knowledge.
      Organizations often make the mistake of creating committees and selecting members before defining what they will do. This results in poor governance because members don’t have the knowledge required to make decisions. Define the mandate of the committee to determine which members are the right fit.
    2. Ensure members are accountable and authorized to make the decisions.
      Effective governance requires the members to have the authority and accountability to make decisions. This ensures meetings achieve their outcome and produce value, which improves the committee’s chances of survival.
    3. Select leaders who see the big picture.
      Often committee decisions and responsibilities become tangled in the web of organizational politics. Include people, often C-level, whose attendance is critical and who have the requisite knowledge, mindset, and understanding to put business needs ahead of their own.

    2.1.5 Update your committee processes

    20 minutes

    Input: Selected governance base model, Updated structure and responsibilities

    Output: Updated committee processes

    Materials: Whiteboard/flip charts

    Participants: IT senior leadership

    1. Review the committee details based on the changes you have made in goals, mandate, and responsibilities.
    2. Identify and document changes required to the committee outputs (outcomes) and adjust the consumer of the outputs to match.
    3. Review the high-level process steps required to get to the modified output. Add required activities or remove unnecessary ones. Review the process flow. Does it make sense? Are there unnecessary steps?
    4. Review and update inputs required for the process steps and update the information/data sources.
    5. Adjust the detailed process steps to reflect the work that needs to be done to support each high-level process step that changed.

    2.1.6 Adjust your associated policies

    20 minutes

    Input: Selected governance base model, Updated structure and responsibilities

    Output: Adjusted mandates and refined committee membership

    Materials: Whiteboard/flip charts

    Participants: IT senior leadership

    1. Review the policies associated with the governing bodies in your base model. Identify the policies that apply to your organization, those that are missing, and those that are not necessary.
    2. Confirm the policies that you require.
    3. Make sure the policies and policy purposes (or risks and related behaviors the policy addresses) are matched to the governance committee that has responsibilities in that area. Move policies to the right committee.

    2.1.7 Adjust and confirm your governance model

    1. Confirm the adjustment of governance bodies, structure, and input/output linkages.
    2. Confirm revisions to decisions and responsibilities.
    3. Confirm policy and regulation/standards associations.
    4. Select related governance committee charters from the provided set and revise the charters to reflect the elements defined in your updated model.
    5. Finalize your governance model.

    Samples of slides related to adjusting and confirming governance models in the Governance Workbook.

    Step 2.2

    Identify and Document Your Governance Triggers

    Activities
    • 2.2.1 Identify and document update triggers
    • 2.2.2 Embed triggers into the review cycle

    This step will walk you through the following activities:

    Identify scenarios that will create a need to review or change your governance model.

    Update your review/update approach to receiving trigger notifications.

    This step involves the following participants:

    • Senior IT leadership
    • Governance leads

    Outcomes of this step

    Downloaded tool ready to select the base governance model for your organization

    Select and Refine Your Governance Model

    Step 2.1 – Choose and Adapt Your Model Step 2.2 – Identify and Document Your Governance Triggers Step 2.3 – Build Implementation Approach

    What are governance triggers

    Governance triggers are organizational or environmental changes within or around an organization that are inflection points that start the review and revision of governance models to maintain their fit with the organization. This is the key to adaptive governance design.

    A target with five arrows sticking out of the bullseye, 'Operating Model', 'Business Strategy', 'Mandate Change', 'Management Practices', and 'Digital Transformation'.

    2.2.1 Identify and document update triggers

    30 minutes

    Input: Governance Workbook

    Output: Updated workbook with defined and documented governance triggers, points of origin, and integration

    Materials: Whiteboard/flip charts

    Participants: IT senior leadership

    1. Open the Governance Workbook to the “Triggers” slides.
    2. Review the list of governance triggers. Retain the ones that apply to your organization, remove those you feel are unnecessary, and add any change scenarios you feel should be included.
    3. Identify where you would receive notifications of these changes and the related processes or activities that would generate these notifications, if applicable.
    4. Document any points of integration required between governance processes and the source process. Highlight any where the integration is not currently in place.

    Sample of the 'Triggers' slide in the Governance Workbook.

    2.2.2 Embed triggers into the review cycle

    30 minutes

    Input: Governance model

    Output: Review cycle update

    Materials: Whiteboard/flip charts

    Participants: IT senior leadership

    1. Identify which triggers impact the entire governance model and which impact specific committees.
    2. Add an activity for triggered review of the impacted governance model into your governance committee process.

    Step 2.3

    Build Your Implementation Approach

    Activities
    • 2.3.1 Identify and document your implementation plan
    • 2.3.2 Build your roadmap
    • 2.3.3 Build your sunshine diagram

    This step will walk you through the following activities:

    Transfer changes to the Governance Implementation Plan Template.

    Determine the timing for the implementation phases.

    This step involves the following participants:

    • Senior IT leadership
    • Governance process owner

    Outcomes of this step

    Implementation plan for adaptive governance framework model

    Select and Refine Your Governance Model
    Step 2.1 – Choose and Adapt Your Model Step 2.2 – Identify and Document Your Governance Triggers Step 2.3 – Build Implementation Approach

    2.3.1 Identify and document your implementation plan

    60 minutes

    Input: Governance model, Guiding principles, Update triggers, Cultural factors and mitigations

    Output: Implementation roadmap

    Materials: Whiteboard/flip charts

    Participants: IT senior leadership

    1. As a group, discuss the changes required to implement the governance model, the cultural items that need to be addressed, and the anticipated timing.
    2. Document the implementation activities and consolidate them into groupings/themes based on similarities or shared outcomes.
    3. Name the grouped themes for clarity and identify key dependencies between activities in each area and across themes.
    4. Identify and document your approach (e.g. continuous, phased) and high-level timeline for implementation.
    5. Document the themes and initiatives in the Governance Implementation Plan.

    Download the Governance Implementation Plan

    Illustrate the implementation plan using roadmaps

    Info-Tech recommends two different methods to roadmap the initiatives in your Governance Implementation Plan.

    Gantt Chart
    Sample of a Gantt Chart.

    This type of roadmap depicts themes, related initiatives, the associated goals, and exact start and end dates for each initiative. This diagram is useful for outlining a larger number of activities and initiatives and has an easily digestible and repeatable format.

    Sunshine Diagram
    Sample of a Sunshine Diagram.

    This type of roadmap depicts themes and their associated initiatives. The start and end dates for the initiatives are approximated based on years or phases. This diagram is useful for highlighting key initiatives on one page.

    2.3.2 Build your roadmap

    30 minutes

    Input: Governance themes and initiatives

    Output: roadmap visual

    Materials: Governance Roadmap Workbook, Governance Workbook

    Participants: CIO, IT senior leadership

    1. Open the Governance Implementation Plan and review themes and initiatives.
    2. Open the Governance Roadmap Workbook.
    3. Discuss whether the implementation roadmap should be developed as a Gantt chart, a sunshine diagram, or both.
      For the Gantt chart:
      • Input the roadmap start year and date.
      • Change the months and year in the Gantt chart to reflect the same roadmap start year.
      • Input and populate the planned start and end dates for the list of high-priority initiatives.

    Develop your Gantt chart in the Governance Roadmap Workbook

    2.3.3 Build your sunshine diagram

    30 minutes

    Input: Governance themes and initiatives

    Output: Sunshine diagram visual

    Materials: Whiteboard/flip charts, Markers, Governance Implementation Plan

    Participants: CIO, IT senior leadership

    1. Review your list of themes and initiatives.
    2. Build a model with “rays” radiating out from a central theme or objective.
    3. Using curved arcs, break the grid into timeline periods or phases.
    4. Complete your sunshine diagram in the Governance Implementation Plan.

    Customize your sunshine diagram in the Governance Implementation Plan

    Make Your IT Governance Adaptable

    Phase 3

    Embed and Automate

    Phase 1

    • 1.1 Define Your Guiding Star
    • 1.2 Define Scope and Principles
    • 1.3 Adjust for Culture and Finalize Context

    Phase 2

    • 2.1 Choose and Adapt Your Model
    • 2.2. Identify and Document Your Governance Triggers
    • 2.3 Build Your Implementation Approach

    Phase 3

    • 3.1 Identify Decisions to Embed and Automate
    • 3.2 Plan Validation and Verification
    • 3.3 Update Implementation Plan

    This phase will walk you through the following activities:

    Identify which decisions you are ready to automate.

    Identify standards and policies that can be embedded and automated.

    Identify integration points.

    Confirm data requirements to enable success.

    This phase involves the following participants:

    • IT senior leadership
    • Governance process owner
    • Product and service owners
    • Policy owners

    Step 3.1

    Identify Decisions to Embed and Automate

    Activities
    • 3.1.1 Review governance decisions and standards and the required level of authority
    • 3.1.2 Build your decision logic
    • 3.1.3 identify constraints and mitigation approaches
    • 3.1.4 Develop decision rules and principles

    This step will walk you through the following activities:

    Identify your key decisions.

    Develop your decision logic.

    Confirm decisions that could be automated.

    Identify and address constraints.

    Develop decision rules and principles.

    This step involves the following participants:

    • IT senior leadership

    Outcomes of this step

    Developed decision rules, rulesets, and principles that can be leveraged to automate governance

    Defined integration points

    Embed and Automate

    Step 3.1 – Identify Decisions to Embed and Automate Step 3.2 – Plan Validation and Verification Step 3.3 – Update Implementation Plan

    What is decision automation?

    Decision automation is the codifying of rules that connect the logic of how decisions are made with the data required to make those decisions. This is then embedded and automated into processes and the design of products and services.

    • It is well suited to governance where the same types of decisions are made on a recurring basis, using the same set of data. It requires clean, high-quality data to be effective.
    • Improvements in artificial intelligence (AI) and machine learning (ML) have allowed the creation of scenarios where a hybrid of rules and learning can improve decision outcomes.

    Key Considerations

    • Data Availability
    • Legality
    • Contingencies
    • Decision Transparency
    • Data Quality
    • Auditability

    How complexity impacts decisions

    Decision complexity impacts the type of rule(s) you create and the amount of data required. It also helps define where or if decisions can be automated.

    1. SIMPLE
      Known and repeatable with consistent and familiar outcomes – structured, causal, and easy to standardize and automate.
    2. COMPLICATED
      Less known and outcomes are not consistently repeatable. Expertise can drive standards and guidelines that can be used to automate decisions.
    3. COMPLEX
      Unknown and new, highly uncertain in terms of outcomes, impact, and data. Requires more exploration and data. Difficult to automate but can be built into the design of products and services.
    4. CHAOTIC
      Unstructured and unknown situation. Requires adaptive and immediate action without active data – requires retained human governance
    5. (Based on Dave Snowden’s Cynefin framework)

    Governance Automation Criteria Checklist

    The Governance Automation Criteria Checklist provides a view of key considerations for determining whether a governing activity or decision is a good candidate for automation.

    The criteria identify key qualifiers/disqualifiers to make it easier to identify eligibility.

    Sample of the Governance Automation Criteria Checklist.

    Download the Governance Automation Criteria Checklist

    Governance Automation Worksheet

    Sample of the Governance Automation Worksheet.

    The Governance Automation Worksheet provides a way to document your governance and systematically identify information about the decisions to help determine if automation is possible.

    From there, decision rules, logic, and rulesets can be designed in support of building a structure flow to allow for automation.

    Download the Governance Automation Worksheet

    3.1.1 Review governance decisions and standards and the required level of authority

    30 minutes

    Input: Automation Criteria Checklist, Governance Automation Worksheet, Updated governance model

    Output: Documented decisions and related authority, Selected options for automation, Updated Governance Automation Worksheet

    Materials: Whiteboard/flip charts, Governance Automation Worksheet

    Participants: IT senior leadership

    1. Identify the decisions that are made within each committee in your updated governance model and document them in the Governance Automation Worksheet.
    2. Confirm the level of authority required to make each decision.
    3. Review the automation checklist to confirm whether each decision is positioned well for automation.
    4. Select and document the decisions that are the strongest options for automation/embedding and document them in the Governance Automation Worksheet.

    What are decision rules?

    Decision rules provide specific instructions and constraints that must be considered in making decisions and are critical for automating governance.

    They provide the logical path to assess governance inputs to make effective decisions with positive business outputs.

    Inputs would include key information such as known risks, your defined prioritization matrix, portfolio value scoring, and compliance controls.

    Individual rules can be leveraged in different places.

    Some decision rule types are listed here.

    1. Statement Rules
      Natural expression of logical progression, written through logical elements
    2. Decision Tree Rules
      Decision tree with two axes that overlap to generate a decision
    3. Sequential Rules
      A sequence of decisions that move from one step to the next
    4. Expression Rule
      A particular set of rules triggered by a particular rule condition being met
    5. Truth table rules
      Combines many decision factors into one place; produces different outputs

    What are decision rulesets

    Rulesets are created to make complex decisions. Individual rule types are combined to create rulesets that are applied together to generate effective decisions. One rule will provide contextual information required for additional rules to execute in a Rule-Result-Rule-Result-Rule-Decision flow.

    A visualization of two separate rulesets made up of the decision rules on the previous slide. 'Ruleset 1' contains '1) Statement Rules', '2) Decision Tree Rules', and 5) Truth Table Rules'. 'Ruleset 2' contains '3) Sequential Rules' and '4) Expression Rule'.

    3.1.2 Build your decision logic

    30 minutes

    Input: Governance Automation Worksheet

    Output: Documented decision logic to support selected decision types and data requirements

    Materials: Whiteboard/flip charts

    Participants: IT senior leadership

    1. For each selected decision, identify the principles that drive the considerations around the decision.
    2. For each decision, develop the decision logic by defining the steps and information inputs involved in making the decision and documenting the flow from beginning to end.
    3. Determine whether this is one specific decision or a combination of different decisions (in sequence or based on decisions).
    4. Name your decision rule.

    Sample of the Governance Automation Worksheet.

    3.1.3 Identify constraints and mitigation approaches

    60 minutes
    1. Document constraints to automation of decisions related to:
      • Availability of decision automation tools
      • Decision authority change requirements
      • Data constraints
      • Knowledge requirements
      • Process adjustment requirements
      • Product/service design levels
    2. Brainstorm and identify approaches to mitigate constraints and score based on likelihood of success.
    3. Identify mitigation owners and initial timeline expectations.
    4. Document the constraints and mitigations in the Governance Workbook on the constraints and mitigations slide.

    Sample of the 'Constraints and mitigations' slide of the 'Governance Workbook'.

    3.1.4 Develop decision rules and principles

    1.5-2 hours

    Input: Governance Automation Worksheet

    Output: Defined decision integration points, Confirmed data availability sets, Decision rules, rulesets, and principles with control indicators

    Materials: Whiteboard/flip charts, Governance Automation Worksheet

    Participants: IT senior leadership

    1. Review the decision logic for those decisions that you have confirmed for automation. Identify the processes where the decision should be executed.
    2. Associate each decision with specific process steps or stages or how it would be included in software/product design.
    3. For each selected decision, identify the availability of data required to support the decision logic and the level of complexity and apply governing principles.
    4. Create the decision rules and identify data gaps.
    5. Define the decision flow and create rulesets as needed.
    6. Confirm automation requirements and define control indicators.

    Step 3.2

    Plan Validation and Verification

    Activities
    • 3.2.1 Define verification approach for embedded and automated governance
    • 3.2.2 Define validation approach for embedded and automated governance

    This step will walk you through the following activities:

    Define how decision outcomes will be measured.

    Determine how the effectiveness of automated governance will be reported.

    This step involves the following participants:

    • IT senior leadership

    Outcomes of this step

    Tested and verified automation of decisions

    Embed and Automate

    Step 3.1 – Identify Decisions to Embed and Automate Step 3.2 – Plan Validation and Verification Step 3.3 – Update Implementation Plan

    Decision rule relationship through to verification

    1. Rules

    Focus on clear decision logic

    Often represented in simple statement types and supported by data:

    IF – THEN

    IF – AND – THEN

    IF – AND NOT – THEN

    2. Rulesets

    Aggregate rules for more complex decisions

    Integrated flows between different required rules:
    Rule 1:
    (Output 1) – Rule 2
    (Output 2) – Rule 6
    Rule 6: (Output 1) – Rule 7
    3. Rule Attestation

    Verify success of automated decisions

    Attestation of embedded and automated rules with key control indicators embedded within process and products.

    Principles embedded into automated software controls.

    3.2.1 Define verification approach for embedded and automated governance

    60 minutes

    Input: Governance rules and rulesets as defined in the Governance Automation Worksheet, Defined decision outcomes

    Output: A defined measurement of effective decision outcomes, Approach to automate and/or report the effectiveness of automated governance

    Materials: Whiteboard/flip charts

    Participants: IT senior leadership

    Verify

    1. Confirm expected outcome of rules.
    2. Select a sampling of new required decisions or recently performed decisions related to areas of automation.
    3. Run the decisions through the decision rules or rule groupings that were developed and compare to parallel decisions made using the traditional approach. (These must be segregated activities.)
    4. Review the outcome of the rules and adjust based on the output. Identify areas of adjustment. Confirm that the automation meets your requirements.

    3.2.2 Define validation approach for embedded and automated governance

    60 minutes

    Input: Governance rules and rulesets as defined in the Governance Automation Worksheet, Defined decision outcomes

    Output: Defined assurance and attestation requirements, Key control indicators that can be automated

    Materials: Whiteboard/flip charts

    Participants: IT senior leadership

    Validate

    1. Develop an approach to measure automated decisions. Align success criteria to current governance KPIs and metrics.
    2. If no such metrics exist, define expected outcome. Define key risk indicators based on the expected points of automation.
    3. Establish quality assurance checkpoints within the delivery lifecycles to adjust for variance.
    4. Create triggers back to rule owners to drive changes and improvements to rules and rule groupings.

    Step 3.3

    Update Implementation Plan

    Activities
    • 3.3.1 Finalize the implementation plan

    This step will walk you through the following activities:

    Review implications and mitigations to make sure all have been considered.

    Finalize the implementation plan and roadmap.

    This step involves the following participants:

    • Senior IT leadership

    Outcomes of this step

    Completed Governance implementation plan and roadmap

    Embed and Automate

    Step 3.1 – Identify Decisions to Embed and Automate Step 3.2 – Plan Validation and Verification Step 3.3 – Update Implementation Plan

    3.3.1 Finalize the implementation plan

    30 minutes

    Input: Governance workbook, Updated governance model, Draft implementation plan and roadmap

    Output: Finalized implementation plan and roadmap

    Materials: Whiteboard/flip charts, Governance Implementation Plan

    Participants: IT senior leadership

    1. Document automation activities within phases in a governance automation theme in the Governance Implementation Plan.
    2. Review timelines in the implementation plan and where automation fits within the roadmap.
    3. Updated the implementation plan and roadmap.

    Governance Implementation Plan

    Summary of Accomplishment

    Problem Solved

    Through this project we have:

    • Improved your governance model to ensure a better fit for your organization, while creating adaptivity for the future.
    • Ensured your governance operates as an enabler of success with the proper bodies and levels of authority established.
    • Established triggers to ensure your governance model is actively adjusted to maintain its fit.
    • Developed a plan to embed and automate governance.
    • Created decision rules and principles and identified where to embed them within your practices.

    If you would like additional support, have our analysts guide you through other phases as part of an Info-Tech workshop.

    Contact your account representative for more information.

    workshops@infotech.com 1-888-670-8889

    Additional Support

    If you would like additional support, have our analysts guide you through other phases as part of an Info-Tech workshop.

    Photo of Valence Howden.

    Contact your account representative for more information.

    workshops@infotech.com 1-888-670-8889

    To accelerate this project, engage your IT team in an Info-Tech workshop with an Info-Tech analyst team.

    Info-Tech analysts will join you and your team at your location or welcome you to Info-Tech’s historic Toronto office to participate in an innovative onsite workshop.

    Related Info-Tech Research

    Improve IT Governance to Drive Business Results

    Avoid bureaucracy and achieve alignment with a minimalist approach. Align with your organizational context.

    Establish Data Governance

    Establish data trust and accountability with strong governance.

    Maximize Business Value From IT Through Benefits Realization

    Embed value and alignment confirmation into your governance to ensure you optimize IT value achievement for resource spend.

    Build a Better Product Owner

    Strengthen the product/service owner role in your organization by focusing on core capabilities and proper alignment.

    Research contributors and experts

    Photo of Sidney Hodgson, Senior Director, Industry, Info-Tech Research Group. Sidney Hodgson
    Senior Director, Industry
    Info-Tech Research Group
    • Sidney has over 30 years of experience in IT leadership roles as CIO of three organizations in Canada and the US as well as international consulting experience in the US and Asia.
    • Sid has a breadth of knowledge in IT governance, project management, strategic and operational planning, enterprise architecture, business process re-engineering, IT cost reduction, and IT turnaround management.
    Photo of David Tomljenovic, Principal Research Advisor, Industry, Info-Tech Research Group. David Tomljenovic
    Principal Research Advisor, Industry
    Info-Tech Research Group
    • David brings extensive experience from the Financial Services sector, having worked 25 years on Bay Street. Most recently he was a Corporate Finance and Strategy Advisor for Infiniti Labs (Toronto/Hong Kong), Automotive, and Smart City Accelerator, where he provided financial and mergers & acquisitions advisory services to accelerator participants with a focus on early-stage fundraising activities.

    Research contributors and experts

    Photo of Cole Cioran, Practice Lead, Applications and Agile Development, Info-Tech Research Group. Cole Cioran
    Practice Lead, Applications and Agile Development
    Info-Tech Research Group
    • Over the past 25 years, Cole has developed software; designed data, infrastructure, and software solutions; defined systems and enterprise architectures; delivered enterprise-wide programs; and managed software development, infrastructure, and business systems analysis practices.
    Photo of Crystal Singh, Research Director, Applications – Data and Information Management, Info-Tech Research Group. Crystal Singh
    Research Director, Applications – Data and Information Management
    Info-Tech Research Group
    • Crystal brings a diverse and global perspective to her role, drawing from her professional experiences in various industries and locations. Prior to joining Info-Tech, Crystal led the Enterprise Data Services function at Rogers Communications, one of Canada’s leading telecommunications companies.

    Research contributors and experts

    Photo of Carlene McCubbin, Practice Lead, CIO, Info-Tech Research Group. Carlene McCubbin
    Practice Lead, CIO
    Info-Tech Research Group
    • Carlene covers key topics in organization and leadership and specializes in governance, organizational design, relationship management, and human capital development. She led the development of Info-Tech’s Organization and Leadership practice.
    Photo of Denis Goulet, Senior Workshop Director, Info-Tech Research Group. Denis Goulet
    Senior Workshop Director
    Info-Tech Research Group
    • Denis is a transformational leader and experienced strategist who focuses on helping clients communicate, relate, and adapt for success. Having developed Governance Model and IT strategies in organizations ranging from small to billion-dollar multi-nationals, he firmly believes in a collaborative value-driven approach to work.

    Bibliography

    “2020 State of Data Governance and Automation Report.” Erwin.com, 28 Jan. 2020. Web.

    “Adaptive IT Governance.” Google search, 15 Nov. 2020.

    “Adaptive IT Governance Framework.” CIO Index, 3 Nov. 2011. Accessed 15 Nov. 2020.

    “Agile Governance Made Easy.” Agilist, n.d. Accessed 15 Nov. 2020.

    “Automating Governance — Our Work.” Humanising Machine Intelligence, n.d. Accessed 15 Nov. 2020.

    “Automation – Decisions.” IBM, 2020. Accessed 15 Oct. 2020.

    Chang, Charlotte. “Accelerating Agile through effective governance.” Medium, 22 Sept. 2020. Web.

    “COBIT 5: Enabling Processes.” ISACA, 2012. Web. Oct. 2016.

    COBIT 2019. ISACA, Dec. 2018. Web.

    Curtis, Blake. “The Value of IT Governance.” ISACA, 29 June 2020. Accessed 15 Nov. 2020.

    De Smet, Aaron. “Three Keys to Faster, Better Decisions.” McKinsey & Company, 1 May 2019. Accessed 15 Nov. 2020.

    “Decision Rules and Decision Analysis.” Navex Global, 2020. Web.

    “Decisions Automation with Business Rules Management Solution.” Sumerge, 4 Feb. 2020. Accessed 15 Nov. 2020.

    “DevGovOps – Key factors for IT governance for enterprises in a DevOps world.” Capgemini, 27 Sept. 2019. Web.

    Eisenstein, Lena. “IT Governance Checklist.” BoardEffect, 19 Feb. 2020. Accessed 15 Nov. 2020.

    “Establishing Effective IT and Data Governance.” Chartered Professional Accountants Canada, n.d. Accessed 15 Nov. 2020.

    Gandzeichuk, Ilya. “Augmented Analytics: From Decision Support To Intelligent Decision-Making.” Forbes, 8 Jan. 2020. Accessed 15 Nov. 2020.

    Georgescu, Vlad. “What Is IT Governance? Understanding From First Principles.” Plutora, 18 Oct. 2019. Web.

    Goodwin, Bill. “IT Governance in the Era of Shadow IT.” ComputerWeekly, 5 Aug. 2014. Accessed 15 Nov. 2020.

    “Governance of IT, OT and IOT.” ISACA Journal, 2019. Web.

    Gritsenko, Daria, and Matthew Wood. “Algorithmic Governance: A Modes of Governance Approach.” Regulation & Governance, 10 Nov. 2020. Web.

    Hansert, Philipp. “Adaptive IT Governance with Clausmark’s Bee4IT.” Bee360, 25 Oct. 2019. Accessed 15 Nov. 2020.

    Havelock, Kylie. “What Does Good Product Governance Look Like?” Medium. 8 Jan. 2020. Web.

    Haven, Dolf van der. “Governance of IT with ISO 38500 - A More Detailed View” LinkedIn article, 24 Oct. 2016. Accessed 15 Nov. 2020.

    Hong, Sounman, and Sanghyun Lee. “Adaptive Governance and Decentralization: Evidence from Regulation of the Sharing Economy in Multi-Level Governance.” Government Information Quarterly, vol. 35, no. 2, April 2018, pp. 299–305. Web.

    ISACA. “Monthly Seminar & Networking Dinner: CIO Dashboard.” Cvent, Feb. 2012. Accessed 15 Nov. 2020.

    ISO/IEC 38500, ISO, 2018 and ongoing.

    “IT Governance.” Kenway Consulting, n.d. Accessed 15 Nov. 2020.

    “IT Governance in the Age of COVID 19.” Union of Arab Banks Webinar, 19-21 Oct. 2020. Accessed 15 Nov. 2020.

    Jaffe, Dennis T. “Introducing the Seven Pillars of Governance.” Triple Pundit, 15 Nov. 2011. Accessed 15 Nov. 2020.

    Janssen, Marijn, and Haiko van der Voort. “Agile and Adaptive Governance in Crisis Response: Lessons from the COVID-19 Pandemic.” International Journal of Information Management, vol. 55, December 2020. Web.

    Jodya, Tiffany. “Automating Enterprise Governance within Delivery Pipelines.” Harness.io, 14 May 2020. Web.

    Kumar, Sarvesh. “AI-Based Decision-Making Automation.” Singular Intelligence, 17 June 2019. Web.

    “Lean IT Governance.” Disciplined Agile, n.d. Accessed 15 Nov. 2020.

    Lerner, Mark. “Government Tech Projects Fail by Default. It Doesn’t Have to Be This Way.” Belfer Center for Science and International Affairs, 21 Oct. 2020. Accessed 15 Nov. 2020.

    Levstek, Aleš, Tomaž Hovelja, and Andreja Pucihar. “IT Governance Mechanisms and Contingency Factors: Towards an Adaptive IT Governance Model.” Organizacija, vol. 51, no. 4, Nov. 2018. Web.

    Maccani, Giovanni, et al. “An Emerging Typology of IT Governance Structural Mechanisms in Smart Cities.” Government Information Quarterly, vol. 37, no. 4, Oct. 2020. Web.

    Magowan, Kirstie. “IT Governance vs IT Management: Mastering the Differences.” BMC Blogs, 18 May 2020. Accessed 15 Nov. 2020.

    Mazmanian, Adam. “Is It Time to Rethink IT Governance? ” Washington Technology, 26 Oct. 2020. Accessed 15 Nov. 2020.

    Mukherjee, Jayanto. “6 Components of an Automation (DevOps) Governance Model.” Sogeti, n.d. Accessed 15 Nov. 2020.

    Ng, Cindy. “The Difference Between Data Governance and IT Governance.” Inside Out Security, updated 17 June 2020. Web.

    Pearson, Garry. “Agile or Adaptive Governance Required?” Taking Care of the Present (blog), 30 Oct. 2020. Accessed 15 Nov. 2020.

    Peregrine, Michael, et al. “The Long-Term Impact of the Pandemic on Corporate Governance.” Harvard Law School Forum on Corporate Governance, 16 July 2020. Web.

    Raymond, Louis, et al. “Determinants and Outcomes of IT Governance in Manufacturing SMEs: A Strategic IT Management Perspective.” International Journal of Accounting Information Systems, vol. 35, December 2019. Web.

    Rentrop, Christopher. “Adaptive IT Governance – Foundation of a Successful Digitalization.” Business IT Cooperation Coordination Controlling (blog). May 2, 2018. Web.

    Schultz, Lisen, et al. “Adaptive Governance, Ecosystem Management, and Natural Capital.” Proceedings of the National Academy of Sciences, vol. 112, no. 24, 2015, pp. 7369–74. Web.

    Selig, Gad J. Implementing IT Governance: A Practical Guide to Global Best Practices in IT Management. Van Haren Publishing, 2008. Accessed 15 Nov. 2020.

    Sharma, Chiatan. “Rule Governance for Enterprise-Wide Adoption of Business Rules: Why Does a BRMS Implementation Need a Governance Framework?” Business Rules Journal, vol. 13, no. 4, April 2012. Accessed 15 Nov. 2020.

    Smallwood, Robert. “Information Governance, IT Governance, Data Governance – What’s the Difference?” The Data Administration Newsletter, 3 June 2020. Accessed 15 Nov. 2020.

    Snowden, Dave. "Cynefin – weaving sense-making into the fabric of our world", Cognitive Edge, 20 October 2020.

    “The Place of IT Governance in the Enterprise Governance.” Institut de la Gouvernance des Systemes d’Information, 2005. Accessed 15 Nov. 2020.

    Thomas, Mark. “Demystifying IT Governance Roles in a Dynamic Business Environment.” APMG International, 29 Oct. 2020. Webinar. Accessed 15 Nov. 2020.

    “The Four Pillars of Governance Best Practice.” The Institute of Directors in New Zealand, 4 Nov. 2019. Web.

    Wang, Cancan, Rony Medaglia, and Lei Zheng. “Towards a Typology of Adaptive Governance in the Digital Government Context: The Role of Decision-Making and Accountability.” Government Information Quarterly, vol. 35, no. 2, April 2018, pp. 306–22.

    Westland, Jason. “IT Governance: Definitions, Frameworks and Planning.” ProjectManager.com, 17 Dec. 2019. Web.

    Wilkin, Carla L., and Jon Riddett. “IT Governance Challenges in a Large Not-for-Profit Healthcare Organization: The Role of Intranets.” Electronic Commerce Research vol. 9, no. 4, 2009, pp. 351-74. Web.

    Zalnieriute, Monika, et al. “The Rule of Law and Automation of Government Decision Making.” Modern Law Review, 25 Feb. 2019. Web.

    Secure Operations in High-Risk Jurisdictions

    • Buy Link or Shortcode: {j2store}369|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Security Strategy & Budgeting
    • Parent Category Link: /security-strategy-and-budgeting

    Business operations in high-risk areas of the world contend with complex threat environments and risk scenarios that often require a unique response. But traditional approaches to security strategy often miss these jurisdictional risks, leaving organizations vulnerable to threats that range from cybercrime and data breaches to fines and penalties.

    Security leaders need to identify high-risk jurisdictions, inventory critical assets, identify vulnerabilities, assess risks, and identify security controls necessary to mitigate those risks.

    Secure operations and protect critical assets in high-risk regions

    Across risks that include insider threats and commercial surveillance, the two greatest vulnerabilities that organizations face in high-risk parts of the world are travel and compliance. Organizations can make small adjustments to their security program to address these risks:

    1. Support high-risk travel: Put measures and guidelines in place to protect personnel, data, and devices before, during, and after employee travel.
    2. Mitigate compliance risk: Consider data residency requirements, data breach notification, cross-border data transfer, and third-party risks to support business growth.

    Using these two prevalent risk scenarios in high-risk jurisdictions as examples, this research walks you through the steps to analyze the threat landscape, assess security risks, and execute a response to mitigate them.

    Secure Operations in High-Risk Jurisdictions Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Secure Operations in High-Risk Jurisdictions – A step-by-step approach to mitigating jurisdictional security and privacy risks.

    Traditional approaches to security strategy often miss jurisdictional risks. Use this storyboard to make small adjustments to your security program to mitigate security risks in high-risk jurisdictions.

    • Secure Operations in High-Risk Jurisdictions – Phases 1-3

    2. Jurisdictional Risk Register and Heat Map Tool – A tool to inventory, assess, and treat jurisdictional risks.

    Use this tool to track jurisdictional risks, assess the exposure of critical assets, and identify mitigation controls. Use the geographic heatmap to communicate inherent jurisdictional risk with key stakeholders.

    • Jurisdictional Risk Register and Heat Map Tool

    3. Guidelines for Key Jurisdictional Risk Scenarios – Two structured templates to help you develop guidelines for two key jurisdictional risk scenarios: high-risk travel and compliance risk

    Use these two templates to develop help you develop your own guidelines for key jurisdictional risk scenarios. The guidelines address high-risk travel and compliance risk.

    • Digital Safety Guidelines for International Travel
    • Guidelines for Compliance With Local Security and Privacy Laws Template

    Infographic

    Workshop: Secure Operations in High-Risk Jurisdictions

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Identify Context for Risk Assessment

    The Purpose

    Assess business requirements and evaluate security pressures to set the context for the security risk assessment.

    Key Benefits Achieved

    Understand the goals of the organization in high-risk jurisdictions.

    Assess the threats to critical assets in these jurisdictions and capture stakeholder expectations for information security.

    Activities

    1.1 Determine assessment scope.

    1.2 Determine business goals.

    1.3 Determine compliance obligations.

    1.4 Determine risk appetite.

    1.5 Conduct pressure analysis.

    Outputs

    Business requirements

    Security pressure analysis

    2 Analyze Key Risk Scenarios for High-Risk Jurisdictions

    The Purpose

    Build key risk scenarios for high-risk jurisdictions.

    Key Benefits Achieved

    Identify critical assets in high-risk jurisdictions, their vulnerabilities to relevant threats, and the adverse impact should malicious agents exploit them.

    Assess risk exposure of critical assets in high-risk jurisdictions.

    Activities

    2.1 Identify critical assets.

    2.2 Identify threats.

    2.3 Assess risk likelihood.

    2.4 Assess risk impact.

    Outputs

    Key risk scenarios

    Jurisdictional risk exposure

    Jurisdictional Risk Register and Heat Map

    3 Build Risk Treatment Roadmap

    The Purpose

    Prioritize and treat jurisdictional risks to critical assets.

    Key Benefits Achieved

    Build an initiative roadmap to reduce residual risks in high-risk jurisdictions.

    Activities

    3.1 Identify and assess risk response.

    3.2 Assess residual risks.

    3.3 Identify security controls.

    3.4 Build initiative roadmap.

    Outputs

    Action plan to mitigate key risk scenarios

    Further reading

    Secure Operations in High-Risk Jurisdictions

    Assessments often omit jurisdictional risks. Are your assets exposed?

    EXECUTIVE BRIEF

    Analyst Perspective

    Operations in high-risk jurisdictions face unique security scenarios.

    The image contains a picture of Michel Hebert.

    Michel Hébert

    Research Director

    Security and Privacy

    Info-Tech Research Group


    The image contains a picture of Alan Tang.

    Alan Tang

    Principal Research Director

    Security and Privacy

    Info-Tech Research Group


    Traditional approaches to security strategies may miss key risk scenarios that critical assets face in high-risk jurisdictions. These include high-risk travel, heightened insider threats, advanced persistent threats, and complex compliance environments. Most organizations have security strategies and risk management practices in place, but securing global operations requires its own effort. Assess the security risk that global operations pose to critical assets. Consider the unique assets, threats, and vulnerabilities that come with operations in high-risk jurisdictions. Focus on the business activities you support and integrate your insights with existing risk management practices to ensure the controls you propose get the visibility they need. Your goal is to build a plan that mitigates the unique security risks that global operations pose and secures critical assets in high-risk areas. Don’t leave security to chance.

    Executive Summary

    Your Challenge

    • Security leaders who support operations in many countries struggle to mitigate security risks to critical assets. Operations in high-risk jurisdictions contend with complex threat environments and security risk scenarios that often require a unique response.
    • Security leaders need to identify critical assets, assess vulnerabilities, catalog threats, and identify the security controls necessary to mitigate related operational risks.

    Common Obstacles

    • Securing operations in high-risk jurisdictions requires additional due diligence. Each jurisdiction involves a different risk context, which complicates efforts to identify, assess, and mitigate security risks to critical assets.
    • Security leaders need to engage the organization with the right questions and identify high-risk vulnerabilities and security risk scenarios to help stakeholders make an informed decision about how to assess and treat the security risks they face in high-risk jurisdictions.

    Info-Tech’s Approach

    Info-Tech has developed an effective approach to protecting critical assets in high-risk jurisdictions.

    This approach includes tools for:

    • Evaluating the security context of your organization’s high-risk jurisdictions.
    • Identifying security risk scenarios unique to high-risk jurisdictions and assessing the exposure of critical assets.
    • Planning and executing a response.

    Info-Tech Insight

    Organizations with global operations must contend with a more diverse set of assets, threats, and vulnerabilities when they operate in high-risk jurisdictions. Security leaders need to take additional steps to secure operations and protect critical assets.

    Business operations in high-risk jurisdictions face a more complex security landscape

    Information security risks to business operations vary widely by region.

    The 2022 Allianz Risk Barometer surveyed 2,650 business risk specialists in 89 countries to identify the most important risks to operations. The report identified cybercrime, IT failures, outages, data breaches, fines, and penalties as the most important global business risks in 2022, but their results varied widely by region. The standout finding of the 2022 Allianz Risk Barometer is the return of security risks as the most important threat to business operations. Security risks will continue to be acute beyond 2022, especially in Africa, the Middle East, Europe, and the Asia-Pacific region, where they will dwarf risks of supply chain interruptions, natural catastrophe, and climate change.

    Global operations in high-risk jurisdictions contend with more diverse threats. These security risk scenarios are not captured in traditional security strategies.

    The image contains a picture of the world map that has certain areas of the map highlighted in various shades of blue based on higher security-related business risks.

    Figures represent the number of cybersecurity risks business risk specialists selected as a percentage of all business risks (Allianz, 2022). Higher scores indicate jurisdictions with higher security-related business risks. Jurisdictions without data are in grey.

    Different jurisdictions’ commitment to cybersecurity also varies widely, which increases security risks further

    The Global Cybersecurity Index (GCI) provides insight into the commitment of different countries to cybersecurity.

    The index assesses a country’s legal framework to identify basic requirements that public and private stakeholders must uphold and the legal instruments prohibiting harmful actions.

    The 2020 GCI results show overall improvement and strengthening of the cybersecurity agenda globally, but significant regional gaps persist. Of the 194 countries surveyed:

    • 33% had no data protection legislation.
    • 47% had no breach notification measures in place.
    • 50% had no legislation on the theft of personal information.
    • 19% still had no legislation on illegal access.

    Not every jurisdiction has the same commitment to cybersecurity. Protecting critical assets in high-risk jurisdictions requires additional due diligence.

    The image contains a picture of the world map that has certain areas of the map highlighted in various shades of blue based on scores in relation to the Global Security Index.

    The diagram sets out the score and rank for each country that took part in the Global Cybersecurity Index (ITU, 2021)

    Higher scores show jurisdictions with a lower rank on the CGI, which implies greater risk. Jurisdictions without data are in grey.

    Securing critical assets in high-risk jurisdictions requires additional effort

    Traditional approaches to security strategy may miss these key risk scenarios.

    As a result, security leaders who support operations in many countries need to take additional steps to mitigate security risks to critical assets.

    Guide stakeholders to make informed decisions about how to assess and treat the security risks and secure operations.

    • Engage the organization with the right questions.
    • Identify critical assets and assess vulnerabilities.
    • Catalogue threats and build risk scenarios.
    • Identify the security controls necessary to mitigate risks.

    Work with your organization to analyze the threat landscape, assess security risks unique to high-risk jurisdictions, and execute a response to mitigate them.

    This project blueprint works through this process using the two most prevalent risk scenarios in high-risk jurisdictions: high-risk travel and compliance risk.

    Key Risk Scenarios

    • High-Risk Travel
    • Compliance Risk
    • Insider Threat
    • Advanced Persistent Threat
    • Commercial Surveillance
    The image contains a screenshot of an Info-Tech thought model regarding secure global operations in high-risk jurisdictions.

    Travel risk is the first scenario we use as an example throughout the blueprint

    • This project blueprint outlines a process to identify, assess, and mitigate key risk scenarios in high-risk jurisdictions. We use two common key risk scenarios as examples throughout the deck to illustrate how you create and assess your own scenarios.
    • Supporting high-risk travel is the first scenario we will study in-depth as an example. Business growth, service delivery, and mergers and acquisitions can lead end users to travel to high-risk jurisdictions where staff, devices, and data are at risk.
    • Compromised or stolen devices can provide threat actors with access to data that could compromise the organization’s strategic, economic, or competitive advantage or expose the organization to regulatory risk.

    The project blueprint includes template guidance in Phase 3 to help you build and deploy your own travel guidelines to protect critical assets and support end users before they leave, during their trip, and when they return.

    Before you leave

    • Identify high-risk countries.
    • Enable controls.
    • Limit what you pack.

    During your trip

    • Assume you are monitored.
    • Limit access to systems.
    • Prevent theft.

    When you return

    • Change your password.
    • Restore your devices.

    Compliance risk is the second scenario we use as an example

    • Mitigating compliance risk is the second scenario we will study as an example in this blueprint. The legal and regulatory landscape is evolving rapidly to keep step with the pace of technological change. Security and privacy leaders are expected to mitigate the risk of noncompliance as the organization expands to new jurisdictions.
    • Later sections will show how to think through at least four compliance risks, including:
      • Cross-border data transfer
      • Third-party risk management
      • Data breach notification
      • Data residency

    The project blueprint includes template guidance in Phase 3 to help you deploy your own compliance governance controls as a risk mitigation measure.

    Secure Operations in High-Risk Jurisdictions: Info-Tech’s methodology

    1. Identify Context

    2. Assess Risks

    3. Execute Response

    Phase Steps

    1. Assess business requirements
    2. Evaluate security pressures
    1. Identify risks
    2. Assess risk exposure
    1. Treat security risks
    2. Build initiative roadmap

    Phase Outcomes

    • Internal security pressures that capture the governance, policies, practices, and risk tolerance of the organization
    • External security pressures that capture the expectations of customers, regulators, legislators, and business partners
    • A heatmap that captures not only the global exposure of your critical assets but also the business processes they support
    • A security risk register to allow for the easy transfer of critical assets’ global security risk data to your organization’s enterprise risk management practice
    • A roadmap of prioritized initiatives to apply relevant controls and secure global assets
    • A set of key risk indicators to monitor and report your progress

    Blueprint deliverables

    Each step of this blueprint is accompanied by supporting deliverables to help you accomplish your goals:

    Business Security Requirements

    Identify the context for the global security risk assessment, including risk appetite and risk tolerance.

    Jurisdictional Risk Register and Heatmap

    Identify critical global assets and the threats they face in high-risk jurisdictions and assess exposure.

    Mitigation Plan

    Roadmap of initiatives and security controls to mitigate global risks to critical assets. Tools and templates to address key security risk scenarios.

    Key deliverable:

    Jurisdictional Risk Register and Heatmap

    Use the Jurisdictional Risk Register and Heatmap Tool to capture information security risks to critical assets in high-risk jurisdictions. The tool generates a world chart that illustrates the risks global operations face to help you engage the business and execute a response.

    Blueprint benefits

    Protect critical assets in high-risk jurisdictions

    IT Benefits

    Assess and remediate information security risk to critical assets in high-risk jurisdictions.

    Easily integrate your risk assessment with enterprise risk assessments to improve communication with the business.

    Illustrate key information security risk scenarios to make the case for action in terms the business understands.

    Business Benefits

    Develop mitigation plans to protect staff, devices, and data in high-risk jurisdictions.

    Support business growth in high-risk jurisdictions without compromising critical assets.

    Mitigate compliance risk to protect your organization’s reputation, avoid fines, and ensure business continuity.

    Quantify the impact of securing global operations

    The tool included with this blueprint can help you measure the impact of implementing the research

    • Use the Jurisdictional Risk Register and Heatmap Tool to describe the key risk scenarios you face, assess their likelihood and impact, and estimate the cost of mitigating measures. Working through the project in this way will help you quantify the impact of securing global operations.
    The image contains a screenshot of Info-Tech's Jurisdictional Risk Register and Heatmap Tool. The image contains a screenshot of the High-Risk Travel Jurisdiction.

    Establish Baseline Metrics

    • Review existing information security and risk management metrics and the output of the tools included with the blueprint.
    • Identify metrics to measure the impact of your risk management efforts. Focus specifically on high-risk jurisdictions.
    • Compare your results with those in your overall security and risk management program.

    ID

    Metric

    Why is this metric valuable?

    How do I calculate it?

    1.

    Overall Exposure – High-Risk Jurisdictions

    Illustrates the overall exposure of critical assets in high-risk jurisdictions.

    Use the Jurisdictional Risk Register and Heatmap Tool. Calculate the impact times the probability rating for each risk. Take the average.

    2.

    # Risks Identified – High-Risk Jurisdictions

    Informs risk tolerance assessments.

    Use the Jurisdictional Risk Register and Heatmap Tool.

    3.

    # Risks Treated – High-Risk Jurisdictions

    Informs residual risk assessments.

    Use the Jurisdictional Risk Register and Heatmap Tool.

    4.

    Mitigation Cost – High-Risk Jurisdictions

    Informs cost-benefit analysis to determine program effectiveness.

    Use the Jurisdictional Risk Register and Heatmap Tool.

    5.

    # Security Incidents – High-Risk Jurisdictions

    Informs incident trend calculations to determine program effectiveness.

    Draw the information from your service desk or IT service management tool.

    6.

    Incident Remediation Cost – High-Risk Jurisdictions

    Informs cost-benefit analysis to determine program effectiveness.

    Estimate based on cost and effort, including direct and indirect cost such as business disruptions, administrative finds, reputational damage, etc.

    7.

    TRENDS: Program Effectiveness – High-Risk Jurisdictions

    # of security incidents over time. Remediation : Mitigation costs over time

    Calculate based on metrics 5 to 7.

    Info-Tech offers various levels of support to best suit your needs.

    DIY Toolkit

    "Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful."

    Guided Implementation

    "Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track."

    Workshop

    "We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place."

    Consulting

    "Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project."

    Diagnostics and consistent frameworks are used throughout all four options.

    Guided Implementation

    What does a typical GI on this topic look like?

    Phase 1

    Call #1: Scope project requirements, determine assessment scope, and discuss challenges.

    Phase 2

    Call #2: Conduct initial risk assessment and determine risk tolerance.

    Call #3: Evaluate security pressures in high-risk jurisdictions.

    Call #4: Identify risks in high-risk jurisdictions.

    Call #5: Assess risk exposure.

    Phase 3

    Call #6: Treat security risks in high-risk jurisdictions.

    A Guided Implementation (GI) is a series of calls with an Info-Tech analyst to help implement our best practices in your organization. A typical GI is between 8 to 12 calls over the course of 4 to 6 months.

    Workshop Overview

    Contact your account representative for more information. workshops@infotech.com 1-888-670-8889

    Days 1

    Days 2-3

    Day 4

    Day 5

    Identify Context

    Key Risk Scenarios

    Build Roadmap

    Next Steps and Wrap-Up (offsite)

    Activities

    1.1.1 Determine assessment scope.

    1.1.2 Determine business goals.

    1.1.3 Identify compliance obligations.

    1.2.1 Determine risk appetite.

    1.2.2 Conduct pressure analysis.

    2.1.1 Identify assets.

    2.1.2 Identify threats.

    2.2.1 Assess risk likelihood.

    2.2.2 Assess risk impact.

    3.1.1 Identify and assess risk response.

    3.1.2 Assess residual risks.

    3.2.1 Identify security controls.

    3.2.2 Build initiative roadmap.

    5.1 Complete in-progress deliverables from previous four days.

    5.2 Set up review time for workshop deliverables and to discuss next steps.

    Deliverables

    1. Business requirements for security risk assessment
    2. Identification of high-risk jurisdictions
    3. Security threat landscape for high-risk jurisdictions
    1. Inventory of relevant threats, critical assets, and their vulnerabilities
    2. Assessment of adverse effects should threat agents exploit vulnerabilities
    3. Risk register with key risk scenarios and heatmap of high-risk jurisdictions
    1. Action plan to mitigate key risk scenarios
    2. Investment and implementation roadmap
    1. Completed information security risk assessment for two key risk scenarios
    2. Risk mitigation roadmap

    No safe jurisdictions

    Stakeholders sometimes ask information security and privacy leaders to produce a list of safe jurisdictions from which to operate. We need to help them see that there are no safe jurisdictions, only relatively risky ones. As you build your security program, deepen the scope of your risk assessments to include risk scenarios critical assets face in different jurisdictions. These risks do not need to rule out operations, but they may require additional mitigation measures to keep staff, data, and devices safe and reduce potential reputational harms.

    Traditional approaches to security strategy often omit jurisdictional risks.

    Global operations must contend with a more complex security landscape. Secure critical assets in high-risk jurisdictions with a targeted risk assessment.

    The two greatest risks are high-risk travel and compliance risk.

    You can mitigate them with small adjustments to your security program.

    Support High-Risk Travel

    When securing travel to high-risk jurisdictions, you must consider personnel safety as well as data and device security. Put measures and guidelines in place to protect them before, during, and after travel.

    Mitigate Compliance Risk

    Think through data residency requirements, data breach notification, cross-border data transfer, and third-party risks to support business growth and mitigate compliance risks in high-risk jurisdictions to protect your organization’s reputation and avoid hefty fines or business disruptions.

    Phase 1

    Identify Context

    This phase will walk you through the following activities:

    • Assess business requirements to understand the goals of the organization’s global operations, as well as its risk governance, policies, and practices.
    • Evaluate jurisdictional security pressures to understand threats to critical assets and capture the expectations of external stakeholders, including customers, regulators, legislators, and business partners, and assess risk tolerance.

    This phase involves the following participants:

    • Business stakeholders
    • IT leadership
    • Security team
    • Risk and Compliance

    Step 1.1

    Assess Business Requirements

    Activities

    1.1.1 Determine assessment scope

    1.1.2 Identify enterprise goals in high-risk jurisdictions

    1.1.3 Identify compliance obligations

    This step involves the following participants:

    • Business stakeholders
    • IT leadership
    • Security team
    • Risk and Compliance

    Outcomes of this step

    • Assess business requirements to understand the goals of the organization’s global operations, as well as its risk governance, policies, and practices.

    Focus the risk assessment on high-risk jurisdictions

    Traditional approaches to information security strategy often miss threats to global operations

    • Successful security strategies are typically sensitive to risks to different IT systems and lines of business.
    • However, securing global operations requires additional focus on high-risk jurisdictions, considering what makes them unique.
    • This first phase of the project will help you evaluate the business context of operations in high-risk jurisdictions, including:
      • Enterprise and security goals.
      • Lines of business, physical locations, and IT systems that need additional oversight.
      • Unique compliance obligations.
      • Unique risks and security pressures.
      • Organizational risk tolerance in high-risk jurisdictions.

    Focus your risk assessment on the business activities security supports in high-risk jurisdictions and the unique threats they face to bridge gaps in your security strategy.

    Identify jurisdictions with higher inherent risks

    Your security strategy may not describe jurisdictional risk adequately.

    • Security strategies list lines of business, physical locations, and IT systems the organization needs to secure and those whose security will depend on a third-party. You can find additional guidance on fixing the scope and boundaries of a security strategy in Phase 1 of Build an Information Security Strategy.
    • However, security risks vary widely from one jurisdiction to another according to:
      • Active cyber threats.
      • Legal and regulatory frameworks.
      • Regional security and preparedness capabilities.
    • Your first task is to identify high-risk jurisdictions to target for additional oversight.

    Work closely with your enterprise risk management function.

    Enterprise risk management functions are often tasked with developing risk assessments from composite sources. Work closely with them to complete your own assessment.

    Countries at heightened risk of money laundering and terrorism financing are examples of high-risk jurisdictions. The Financial Action Task Force and the U.S. Treasury publish reports three times a year that identify Non-Cooperative Countries or Territories.

    Develop a robust jurisdictional assessment

    Design an intelligence collection strategy to inform your assessment

    Strategic Intelligence

    White papers, briefings, reports. Audience: C-Suite, board members

    Tactical Intelligence

    Internal reports, vendor reports. Audience: Security leaders

    Operational intelligence

    Indicators of compromise. Audience: IT Operations

    Operational intelligence focuses on machine-readable data used to block attacks, triage and validate alerts, and eliminate threats from the network. It becomes outdated in a matter of hours and is less useful for this exercise.

    Determine travel risks to bolster your assessments

    Not all locations and journeys will require the same security measures.

    • Travel risks vary significantly according to destination, the nature of the trip, and traveler profile.
    • Access to an up-to-date country risk rating system enables your organization and individual staff to quickly determine the overall level of risk in a specific country or location.
    • Based on this risk rating, you can specify what security measures are required prior to travel and what level of travel authorization is appropriate, in line with the organization's security policy or travel security procedures.
    • While some larger organizations can maintain their own country risk ratings, this requires significant capacity, particularly to obtain the necessary information to keep these regularly updated.
    • It may be more effective for your organization to make use of the travel risk ratings provided by an external security information provider, such as a company linked to your travel insurance or travel booking service, if available.
    • Alternatively, various open-source travel risk ratings are available via embassy travel sites or other website providers.

    Without a flexible system to account for the risk exposures of different jurisdictions, staff may perceive measures as a hindrance to operations.

    Develop a tiered risk rating

    The example below outlines potential risk indicators for high-risk travel.

    Rating

    Description

    Low

    Generally secure with adequate physical security. Low violent crime rates. Some civil unrest during significant events. Acts of terrorism rare. Risks associated with natural disasters limited and health threats mainly preventable.

    Moderate

    Periodic civil unrest. Antigovernment, insurgent, or extremist groups active with sporadic acts of terrorism. Staff at risk from common and violent crime. Transport and communications services are unreliable and safety records are poor. Jurisdiction prone to natural disasters or disease epidemics.

    High

    Regular periods of civil unrest, which may target foreigners. Antigovernment, insurgent, or extremist groups very active and threaten political or economic stability. Violent crime rates high, often targeting foreigners. Infrastructure and emergency services poor. May be regular disruption to transportation or communications services. Certain areas off-limits to foreigners. Jurisdictions experiencing natural disasters or epidemics are considered high risk.

    Extreme

    Undergoing active conflict or persistent civil unrest. Risk of being caught up in a violent incident or attack is very high. Authorities may have lost control of significant portions of the country. Lines between criminality and political and insurgent violence are blurred. Foreigners are likely to be denied access to parts of the country. Transportation and communication services are severely degraded or nonexistent. Violence presents a direct threat to staff security.

    Ratings are formulated by assessing several types of risk, including conflict, political/civil unrest, terrorism, crime, and health and infrastructure risks.

    1.1.1 Determine assessment scope

    1 – 2 hours

    1. As a group, brainstorm a list of high-risk jurisdictions to target for additional assessment. Write down as many items as possible to include in:
    • Lines of business
    • Physical locations
    • IT systems

    Pay close attention to elements of the assessment that are not in scope.

  • Discuss the response and the rationale for targeting each of them for additional risk assessments. Identify security-related concerns for different lines of business, locations, user groups, IT systems, and data.
  • Record your responses and your comments in the Information Security Requirements Gathering Tool.
  • Input

    Output

    • Corporate strategy
    • IT strategy
    • Security strategy
    • Relevant threat intelligence
    • A list of high-risk jurisdictions to focus your risk assessment

    Materials

    Participants

    • Laptop
    • Projector
    • Security team
    • IT leadership
    • Business stakeholders
    • Enterprise Risk Management
    • Compliance
    • Legal

    Download the Information Security Requirements Gathering Tool

    Position your efforts in a business context

    Securing critical assets in high-risk jurisdictions is a business imperative

    • Many companies relegate their information security strategies to their IT department. Aside from the strain the choice places on a department that already performs many different functions, it wrongly implies that mitigating information security risk is simply an IT problem.
    • Managing information security risks is a business problem. It requires that organizations identify their risk appetite, prioritize relevant threats, and define risk mitigation initiatives. Business leaders can only do these activities effectively in a context that recognizes the business and financial benefits of implementing protections.
    • This is notably true of businesses with operations in many different countries. Each jurisdiction has its own set of security risks the organization must account for, as well as unique local laws and regulations that affect business operations.
    • In high-risk jurisdictions, your efforts must consider the unique operational challenges your organization may not face in its home country. Your efforts to secure critical assets will be most successful if you describe key risk scenarios in terms of their impact on business goals.
    • You can find additional guidance on assessing the business context of a security strategy in Phase 1 of Build an Information Security Strategy.

    Do you understand the unique business context of operations in high-risk jurisdictions?

    1.1.2 Identify business goals

    Estimated Time: 1-2 hours

    1. As a group, brainstorm the primary and secondary business goals of the organization. Focus your assessment on operations in high-risk jurisdictions you identified in Exercise 1.1.1. Review:
    • Relevant corporate and IT strategies.
    • The business goal definitions and indicator metrics in tab 2, “Goals Definition,” of the Information Security Requirements Gathering Tool.
  • Limit business goals to no more than two primary goals and three secondary goals. This limitation will help you prioritize security initiatives at the end of the project.
  • For each business goal, identify up to two security alignment goals that will support business goals in high-risk jurisdictions.
  • Input

    Output

    • Corporate strategy
    • IT strategy
    • Security strategy
    • Your goals for the security risk assessment for high-risk jurisdictions

    Materials

    Participants

    • Laptop
    • Projector
    • Security team
    • IT leadership
    • Business stakeholders
    • Risk Management
    • Compliance
    • Legal

    Download the Information Security Requirements Gathering Tool

    Record business goals

    Capture the results in the Information Security Requirements Gathering Tool

    1. Record the primary and secondary business goals you identified in tab 3, “Goals Cascade,” of the Information Security Requirements Gathering Tool.
    2. Next, record the two security alignment goals you selected for each business goal based on the tool’s recommendations.
    3. Finally, review the graphic diagram that illustrates your goals on tab 6, “Results,” of the Information Security Requirements Gathering Tool.
    4. Revisit this exercise whenever operations expands to a new jurisdiction to capture how they contribute to the organization’s mission and vision and how the security program can support them.
    The image contains a screenshot of Tab 3, Goals Cascade.

    Tab 3, Goals Cascade

    The image contains a screenshot of Tab 6, Results.

    Tab 6, Results

    Analyze business goals

    Assess how operating in multiple jurisdictions adds nuance to your business goals

    • Security leaders need to understand the direction of the business to propose relevant security initiatives that support business goals in high-risk jurisdictions.
    • Operating in different jurisdictions carries its own degree of risk. The organization is subject not only to the information security risks and legal frameworks of its country of origin but also to those associated with international jurisdictions.
    • You need to understand where your organization operates and how these different jurisdictions contribute to your business goals to support their performance and protect the firm’s reputation.
    • This exercise will make an explicit link between security and privacy concerns in high-risk jurisdictions, what the business cares about, and what security is trying to accomplish.

    If the organization is considering a merger and acquisition project that will expand operations in jurisdictions with different travel risk profiles, the security organization needs to revise the security strategy to ensure the organization can support high-risk travel and mitigate risks to critical assets.

    Identify compliance obligations

    Data compliance obligations loom large in high-risk jurisdictions

    The image contains four hexagons, each with their own words. SOX, PCI DSS, HIPAA, HITECH.

    Security leaders are familiar with most conventional regulatory obligations that govern financial, personal, and healthcare data in North America and Europe.

    The image contains four hexagons, each with their own words. Residency, Cross-Border Transfer, Breach Notification, Third-Party Risk Mgmt.

    Data privacy concerns, nationalism, and the economic value of data are all driving jurisdictions to adopt data residency and data localization and to shut down the cross-border transfer of data.

    The next step requires you to consider the compliance obligations the organization needs to meet to support the business as it expands to other jurisdictions through natural growth, mergers, and acquisitions.

    1.1.3 Identify compliance obligations

    Estimated Time: 1-2 hours

    1. As a group, brainstorm compliance obligations in target jurisdictions. Focus your assessment on operations in high-risk jurisdictions.
    2. Include:

    • Laws
    • Governing regulations
    • Industry standards
    • Contractual agreements
  • Record your compliance obligations and comments on tab 4, “Compliance Obligations,” of the Information Security Requirements Gathering Tool.
  • If you need to take full stock of the laws and regulations in place in the jurisdictions where you operate that you are not familiar with, consider seeking local legal counsel to help you navigate this exercise.
  • Input

    Output

    • Legal and compliance frameworks in target jurisdictions
    • Mandatory and voluntary compliance obligations for target jurisdictions

    Materials

    Participants

    • Laptop
    • Projector
    • Security team
    • IT leadership
    • Business stakeholders
    • Risk Management
    • Compliance
    • Legal

    Download the Information Security Requirements Gathering Tool

    Step 1.2

    Evaluate Security Pressures

    Activities

    1.2.1 Conduct initial risk assessment

    1.2.2 Conduct pressure analysis

    1.2.3 Determine risk tolerance

    This step involves the following participants:

    • Security team
    • Risk and Compliance
    • IT leadership (optional)

    Outcomes of this step

    Identify threats to global assets and capture the security expectations of external stakeholders, including customers, regulators, legislators, and business partners, and determine risk tolerance.

    Evaluate security pressures to set the risk context

    Perform an initial assessment of high-risk jurisdictions to set the context.

    Assess:

    • The threat landscape.
    • The security pressures from key stakeholders.
    • The risk tolerance of your organization.

    You should be able to find the information in your existing security strategy. If you don’t have the information, work through the next three steps of the project blueprint.

    The image contains a diagram to demonstrate evaluating security pressures, as described in the text above.

    Some jurisdictions carry inherent risks

    • Jurisdictional risks stem from legal, regulatory, or political factors that exist in different countries or regions. They can also stem from unexpected legal changes in regions where critical assets have exposure. Understanding jurisdictional risks is critical because they can require additional security controls.
    • Jurisdictional risk tends to be higher in jurisdictions:
      • Where the organization:
        • Conducts high-value or high-volume financial transactions.
        • Supports and manages critical infrastructure.
        • Has high-cost data or data whose compromise could undermine competitive advantage.
        • Has a high percentage of part-time employees and contractors.
        • Experiences a high rate of employee turnover.
      • Where state actors:
        • Have a low commitment to cybersecurity, financial, and privacy legislation and regulation.
        • Support cybercrime organizations within their borders.

    Jurisdictional risk is often reduced to countries where money laundering and terrorist activities are high. In this blueprint, the term refers to the broader set of information security risks that arise when operating in a foreign country or jurisdiction.

    Five key risk scenarios are most prevalent

    Key Risk Scenarios

    • High-Risk Travel
    • Compliance Risk
    • Insider Threat
    • Advanced Persistent Threat
    • Commercial Surveillance

    Security leaders who support operations in many countries need to take additional steps to mitigate security risks to critical assets. The goal of the next two exercises is to analyze the threat landscape and security pressures unique to high-risk jurisdictions, which will inform the construction of key scenarios in Phase 2. These five scenarios are most prevalent in high-risk jurisdictions. Keep them in mind as you go through the exercises in this section.

    1.2.1 Assess jurisdictional risk

    1-3 hours

    1. As a group, review the questions on tab 2, “Risk Assessment,” of the Information Security Pressure Analysis Tool.
    2. Gather the required information from subject matter experts on the following risk elements with a focus on high-risk jurisdictions:
    3. Review each question in tab 2 of the Information Security Pressure Analysis Tool and select the most appropriate response.

    Input

    Output

    • Existing security strategy
    • List of organizational assets
    • Historical data on information security incidents
    • Completed risk assessment

    Materials

    Participants

    • Information Security Pressure Analysis Tool
    • Security team
    • IT leadership
    • Risk Management

    For more information on how to complete the risk assessment questionnaire, see Step 1.2.1 of Build an Information Security Strategy.

    1.2.2 Conduct pressure analysis

    1-3 hours

    1. As a group, review the questions on tab 3, “Pressure Analysis,” of the Information Security Pressure Analysis Tool.
    2. Gather the required information from subject matter experts on the following pressure elements with a focus on high-risk jurisdictions:
    • Compliance and oversight
    • Customer expectations
    • Business expectations
    • IT expectations
  • Review each question in the questionnaire and provide the most appropriate response using the drop-down list. It may be helpful to consult with the appropriate departments to obtain their perspectives.
  • For more information on how to complete the pressure analysis questionnaire, see Step 1.3 of Build an Information Security Strategy.

    Input

    Output

    • Information on various pressure elements within the organization
    • Existing security strategy
    • Completed pressure analysis

    Materials

    Participants

    • Information Security Pressure Analysis Tool
    • Security team
    • IT leadership
    • Business leaders
    • Compliance

    A low security pressure means that your stakeholders do not assign high importance to information security. You may need to engage stakeholders with the right key risk scenarios to illustrate jurisdictional risk and generate support for new security controls.

    Download the Information Security Pressure Analysis Tool

    Assess risk tolerance

    • Risk tolerance expresses the types and amount of risk the organization is willing to accept in pursuit of its goals.
    • These expectations can help you identify, manage, and report on key risk scenarios in high-risk jurisdictions.
    • For instance, an organization with a low risk tolerance will require a stronger information security program to minimize operational security risks.
    • It’s up to business leaders to determine the risks they are willing to accept. They may need guidance to understand how system-level risks affect the organization’s ability to pursue its goals.

    A formalized risk tolerance statement can help:

    • Support risk-based security decisions that align with business goals.
    • Provide a meaningful rationale for security initiatives.
    • Improve the transparency of investments in the organization’s security program.
    • Provide guidance for monitoring inherent risk and residual risk exposure.

    The role of security professionals is to identify and analyze key risk scenarios that may prevent the organization from reaching its goals.

    1.2.3 Determine risk tolerance

    1-3 hours

    1. As a group, review the questions on tab 4, “Risk Tolerance,” of the Information Security Pressure Analysis Tool.
    2. Gather the required information from subject matter experts on the following risk tolerance elements:
    • Recent IT problems, especially downtime and data recovery issues
    • Historical security incidents
  • Review any relevant documentation, including:
    • Existing security strategy
    • Business impact assessments
    • Service-level agreements

    For more information on how to complete the risk tolerance questionnaire, see Step 1.4 of Build an Information Security Strategy.

    Input

    Output

    • Existing security strategy
    • Data on recent IT problems and incidents
    • Business impact assessments
    • Completed risk tolerance statement

    Materials

    Participants

    • Information Security Pressure Analysis Tool
    • Security team
    • IT leadership
    • Risk Management

    Download the Information Security Pressure Analysis Tool

    Review the output of the results tab

    • The organizational risk assessment provides a high-level assessment of inherent risks in high-risk jurisdictions. Use the results to build and assess key risk scenarios in Phase 2.
    • Use the security pressure analysis to inform stakeholder management efforts. A low security pressure indicates that stakeholders do not yet grasp the impact of information security on organizational goals. You may need to communicate its importance before you discuss additional security controls.
    • Jurisdictions in which organizations have a low risk tolerance will require stronger information security controls to minimize operational risks.
    The image contains a screenshot of the organizational risk assessment. The image contains a screenshot of the security pressure analysis. The image contains a screenshot of the risk tolerance curve.

    Phase 2

    Assess Security Risks to Critical Assets

    This phase will walk you through the following activities:

    • Identify critical assets, their vulnerabilities to relevant threats, and the adverse impact a successful threat event would have on the organization.
    • Assess risk exposure of critical assets in high-risk jurisdictions for each risk scenario through an analysis of its likelihood and impact.

    This phase involves the following participants:

    • Security team
    • Risk and Compliance
    • IT leadership (optional)

    Step 2.1

    Identify Risks

    Activities

    2.1.1 Identify assets

    2.1.2 Identify threats

    This step involves the following participants:

    • Security team
    • Risk and Compliance
    • IT leadership (optional)

    Outcomes of this step

    • Define risk scenarios that identify critical assets, their vulnerabilities to relevant threats, and the adverse impact a successful threat event would have on the organization.

    This blueprint focuses on mitigating jurisdictional risks

    The image contains a screenshot of the IT Risk Management Framework. The framework includes: Risk Identification, Risk Assessment, Risk Response, and Risk Governance.

    For a deeper dive into building a risk management program, see Info-Tech’s core project blueprints on risk management:

    Build an IT Risk Management Program

    Combine Security Risk Management Components Into One Program

    Draft key risk scenarios to illustrate adverse events

    Risk scenarios help decision-makers understand how adverse events affect business goals.

    • Risk-scenario building is the process of identifying the critical factors that contribute to an adverse event and crafting a narrative that describes the circumstances and consequences if it were to happen.
    • Risk scenarios set up the risk analysis stage of the risk assessment process. They are narratives that describe in detail:
      • The asset at risk.
      • The threat that can act against the asset.
      • Their intent or motivation.
      • The circumstances and threat actor model associated with the threat event.
      • The potential effect on the organization.
      • When or how often the event might occur.

    Risk scenarios are further distilled into a single sentence or risk statement that communicates the essential elements from the scenario.

    Well-crafted risk scenarios have four components

    The second phase of the project will help you craft meaningful risk scenarios

    Threat

    Exploits an

    Asset

    Using a

    Method

    Creating an

    Effect

    An actor capable of harming an asset

    Anything of value that can be affected and results in loss

    Technique an actor uses to affect an asset

    How loss materializes

    Examples: Malicious or untrained employees, cybercriminal groups, malicious state actors

    Examples: Systems, regulated data, intellectual property, people

    Examples: Credential compromise, privilege escalation, data exfiltration

    Examples: Loss of data confidentiality, integrity, or availability; impact on staff health & safety

    Risk scenarios are concise, four to six sentence narratives that describe the core elements of forecasted adverse events. Use them to engage stakeholders with the right questions and guide them to make informed decisions about how to address and treat security risks in high-risk jurisdictions.

    The next slides review five key risk scenarios prevalent in high-risk jurisdictions. Use them as examples to develop your own.

    Travel to high-risk jurisdictions requires special measures to protect staff, devices, and data

    Governmental, academic, and commercial advisors compile lists of jurisdictions that pose greater travel risks annually.

    For instance, in the US, these lists might include countries that are:

    • Subjects of travel warnings by the US Department of State.
    • Identified as high risk by other US government sources such as:
      • The Department of the Treasury Office of Foreign Assets Control (OFAC).
      • The Federal Bureau of Investigation (FBI).
      • The Office of the Director of National Intelligence (ODNI).
    • Compiled from academic and commercial sources, such as Control Risks.

    When securing travel to high-risk jurisdictions, you must consider personnel safety as well as data and device security.

    The image contains a diagram to present high-risk jurisdictions.

    The diagram presents high-risk jurisdictions based on US governmental sources (2021) listed on this slide.

    High-risk travel

    Likelihood: Medium

    Impact: Medium

    Key Risk Scenario #1

    Malicious state actors, cybercriminals, and competitors can threaten staff, devices, and data during travel to high-risk jurisdictions. Device theft or compromise may occur while traveling through airports, accessing hotel computer and phone networks, or in internet cafés or other public areas. Threat actors can exploit data from compromised or stolen devices to undermine the organization’s strategic, economic, or competitive advantage. They can also infect compromised devices with malware that delivers malicious payloads once they reconnect with home networks.

    Threat Actor:

    • Malicious state actors
    • Cybercriminals
    • Competitors

    Assets:

    • Staff
    • IT systems
    • Sensitive data

    Effect:

    • Compromised staff health and safety
    • Loss of data
    • Lost of system integrity

    Methods:

    • Identify, steal, or target mobile devices.
    • Compromise network, wireless, or Bluetooth connections.
    • Leverage stolen devices as a means of infecting other networks.
    • Access devices to track user location.
    • Activate microphones on devices to collect information.
    • Intercept electronic communications users send from high-risk jurisdictions.

    The data compliance landscape is a jigsaw puzzle of data protection and data residency requirements

    Since the EU passed the GDPR in 2016, jurisdictions have turned to data regulations to protect citizen data

    Data privacy concerns, nationalism, and the economic value of data are all driving jurisdictions to adopt data residency, breach notification, and cross-border data transfer regulations. As 2021 wound down to a close, nearly all the world’s 30 largest economies had some form of data regulation in place. The regulatory landscape is shifting rapidly, which complicates operations as organizations grow into new markets or engage in merger and acquisition activities.

    Global operations require special attention to data-residency requirements, data breach notification requirements, and cross-border data transfer regulations to mitigate compliance risk.

    The image contains a diagram to demonstrate the data regulations placed in various places around the world.

    Compliance risk

    Likelihood: Medium

    Impact: High

    Key Risk Scenario #2

    Rapid changes in the privacy and security regulatory landscape threaten organizations’ ability to meet their compliance obligations from local legal and regulatory frameworks. Organizations risk reputational damage, administrative fines, criminal charges, and loss of market share. In extreme cases, organizations may lose their license to operate in high-risk jurisdictions. Shifts in the regulatory landscape can involve additional requirements for data residency, cross-border data transfer, data breach notification, and third-party risk management.

    Threat Actor:

    • Local, regional, and national state actors

    Asset:

    • Reputation, market share
    • License to operate

    Effect:

    • Administrative fines
    • Loss of reputation, brand trust, and consumer loyalty
    • Loss of market share
    • Suspension of business operations
    • Lawsuits due to collective actions and claims
    • Criminal charges

    Methods:

    • Shifts in the privacy and security regulatory landscape, including requirements for:
      • Data residency.
      • Cross-border data transfer.
      • Data breach notification.
      • Third-party security and privacy risk management.

    The incidence of insider threats varies widely by jurisdiction in unexpected ways

    On average, companies in North America, the Middle East, and Africa had the most insider incidents in 2021, while those in the Asia-Pacific region had the least.

    The Ponemon Institute set out to understand the financial consequences that result from insider threats and gain insight into how well organizations are mitigating these risks.

    In the context of this research, insider threat is defined as:

    • Employee or contractor negligence.
    • Criminal or malicious insider activities.
    • Credential theft (imposter risk).

    On average, the total cost to remediate insider threats in 2021 was US$15.4 million per incident.

    In all regions, employee or contractor negligence occurred most frequently. Organizations in North America and in the Middle East and Africa were most likely to experience insider threat incidents in 2021.

    the image contains a diagram of the world, with various places coloured in different shades of blue.

    The diagram represents the average number of insider incidents reported per organization in 2021. The results are analyzed in four regions (Ponemon Institute, 2022)

    Insider threat

    Likelihood: Low to Medium

    Impact: High

    Key Risk Scenario #3

    Malicious insiders, negligent employees, and credential thieves can exploit inside access to information systems to commit fraud, steal confidential or commercially valuable information, or sabotage computer systems. Insider threats are difficult to identify, especially when security is geared toward external threats. They are often familiar with the organization’s data and intellectual property as well as the methods in place to protect them. An insider may steal information for personal gain or install malicious software on information systems. They may also be legitimate users who make errors and disregard policies, which places the organization at risk.

    Threat Actor:

    • Malicious insiders
    • Negligent employees
    • Infiltrators

    Asset:

    • Sensitive data
    • Employee credentials
    • IT systems

    Effects:

    • Loss of system integrity
    • Loss of data confidentiality
    • Financial loss

    Methods:

    • Infiltrators may compromise credentials.
    • Malicious or negligent insiders may use corporate email to steal or share sensitive data, including:
      • Regulated data.
      • Intellectual property.
      • Critical business information.
    • Malicious agents may facilitate data exfiltration, as well as open-port and vulnerability scans.

    The risk of advanced persistent threats is more prevalent in Central and South America and the Asia-Pacific region

    Attacks from advanced persistent threat (APT) actors are more sophisticated than traditional ones.

    • More countries will use legal indictments as part of their cyber strategy. Exposing toolsets of APT groups carried out at the governmental level will drive more states to do the same.
    • Expect APTs to increasingly target network appliances like VPN gateways as organizations continue to sustain hybrid workforces.
    • The line between APTs and state-sanctioned ransomware groups is blurring. Expect cybercriminals to wield better tools, mount more targeted attacks, and use double-extortion tactics.
    • Expect more disruption and collateral damage from direct attacks on critical infrastructure.

    Top 10 Significant Threat Actors:

    • Lazarus
    • DeathStalker
    • CactusPete
    • IAmTheKing
    • TransparentTribe
    • StrongPity
    • Sofacy
    • CoughingDown
    • MuddyWater
    • SixLittleMonkeys

    Top 10 Targets:

    • Government
    • Banks
    • Financial Institutions
    • Diplomatic
    • Telecommunications
    • Educational
    • Defense
    • Energy
    • Military
    • IT Companies
    The image contains a world map coloured in various shades of blue.
    Top 12 countries targeted by APTs (Kaspersky, 2020)

    Track notable APTs to revise your list of high-risk jurisdictions and review the latest tactics and techniques

    Governmental advisors track notable APT actors that pose greater risks.

    The CISA Shields Up site, SANS Storm Center site, and MITRE ATT&CK group site provide helpful and timely information to understand APT risks in different jurisdictions.

    The following threat actors are currently associated with cyberattacks affiliated with the Russian government.

    Activity Group

    Risks

    APT28 (GRU)

    Known as Fancy Bear, this threat group has been tied to espionage since 2004. They compromised the Hillary Clinton campaign, amid other major events.

    APT29 (SVT)

    Tied to espionage since 2008. Reportedly compromised the Democratic National Committee in 2015. Cited in the 2021 SolarWinds compromise.

    Buhtrap/RTM Group

    Group focused on financial targets since 2014. Currently known to target Russian and Ukrainian banks.

    Gamaredon

    Operating in Crimea. Aligned with Russian interests. Has previously targeted Ukrainian government officials and organizations.

    DEV-0586

    Carried out wiper malware attacks on Ukrainian targets in January 2022.

    UNC1151

    Active since 2016. Linked to information operation campaigns and the distribution of anti-NATO material.

    Conti

    Most successful ransomware gang of 2021, with US$188M revenue. Supported Russian invasion of Ukraine, threatening attacks on allied critical infrastructure.

    Sources: MITRE ATT&CK; Security Boulevard, 2022; Reuters, 2022; The Verge, 2022

    Advanced persistent threat

    Likelihood: Low to Medium

    Impact: High

    Key Risk Scenario #4

    Advanced persistent threats are state actors or state-sponsored affiliates with the means to avoid detection by anti-malware software and intrusion detection systems. These highly-skilled and persistent malicious agents have significant resources with which to bypass traditional security controls, establish a foothold in the information technology infrastructure, and exfiltrate data undetected. APTs have the resources to adapt to a defender’s efforts to resist them over time. The loss of system integrity and data confidentiality over time can lead to financial losses, business continuity disruptions, and the destruction of critical infrastructure.

    Threat Actor:

    • State actors
    • State-sponsored affiliates

    Asset:

    • Sensitive data
    • IT systems
    • Critical infrastructure

    Effects:

    • Loss of system integrity
    • Loss of data confidentiality
    • Financial loss
    • Business continuity disruptions
    • Infrastructure destruction

    Methods:

    • Persistent, consistent attacks using the most advanced threats and tactics to bypass security defenses.
    • The goal of APTs is to maintain access to networks for prolonged periods without being detected.
    • The median dwell time differs widely between regions. FireEye reported the mean dwell time for 2018:
      • Americas: 71 days
      • Europe, Middle East, and Africa: 177 days
      • Asia-Pacific: 204 days
    Sources: Symantec, 2011; FireEye, 2019

    Threat agents have deployed invasive technology for commercial surveillance in at least 76 countries since 2015

    State actors and their affiliates purchased and used invasive spyware from companies in Europe, Israel, and the US.

    • “Customers are predominantly repressive regimes looking for new ways to control the flow of information and stifle dissent. Less than 10% of suspected customers are considered full democracies by the Economist Intelligence Unit.” (Top10VPN, 2021)
    • Companies based in economically developed and largely democratic states are profiting off the technology.
    • The findings demonstrate the need to consider geopolitical realities when assessing high-risk jurisdictions and to take meaningful action to increase layered defenses against invasive malware.
    • Spyware is having an increasingly well-known impact on civil society. For instance, since 2016, over 50,000 individual phone numbers have been identified as potential targets by NSO Group, the Israeli manufacturers of the notorious Pegasus Spyware. The target list contained the phone numbers of politicians, journalists, activists, doctors, and academics across the world.
    • The true number of those affected by spyware is almost impossible to determine given that many fall victim to the technology and do not notice.
    The image contains a map of the world with various countries highlighted in shades of blue.

    Countries where commercial surveillance tools have been deployed (“Global Spyware Market Index,” Top10VPN, 2021)

    The risks and effects of spyware vary greatly

    Spyware can steal mundane information, track a user’s every move, and everything in between.

    Adware

    Software applications that display advertisements while the program is running.

    Keyboard Loggers

    Applications that monitor and record keystrokes. Malicious agents use them to steal credentials and sensitive enterprise data.

    Trojans

    Applications that appear harmless but inflict damage or data loss to a system.

    Mobile Spyware

    Surveillance applications that infect mobile devices via SMS or MMS channels, though the most advanced can infect devices without user input.

    State actors and their affiliates use system monitors to track browsing habits, application usage, and keystrokes and capture information from devices’ GPS location data, microphone, and camera. The most advanced system monitor spyware, such as NSO Group’s Pegasus, can infect devices without user input and record conversations from end-to-end encrypted messaging systems.

    Commercial surveillance

    Likelihood: Low to Medium

    Impact: Medium

    Key Risk Scenario #5

    Malicious agents can deploy malware on end-user devices with commercial tools available off the shelf to secretly monitor the digital activity of users. Attacks exploit widespread vulnerabilities in telecommunications protocols. They occur through email and text phishing campaigns, malware embedded in untested applications, and sophisticated zero-click attacks that deliver payloads without requiring user interactions. Attacks target sensitive as well as mundane information. They can be used to track employee activities, investigate criminal activity, or steal credentials, credit card numbers, or other personally identifiable information.

    Threat Actor:

    • State actors
    • State-sponsored affiliates

    Asset:

    • Sensitive data
    • Staff health and safety
    • IT systems

    Effects:

    • Data breaches
    • Loss of data confidentiality
    • Increased risk to staff health and safety
    • Misuse of private data
    • Financial loss

    Methods:

    • Email and text phishing attacks that delivery malware payloads
    • Sideloading untested applications from a third-party source rather than an official retailer
    • Sophisticated zero-click attacks that deliver payloads without requiring user interaction

    Use the Jurisdictional Risk Register and Heatmap Tool

    The tool included with this blueprint can help you draft risk scenarios and risk statements in this section.

    The risk register will capture a list of critical assets and their vulnerabilities, the threats that endanger them, and the adverse effect your organization may face.

    The image includes two screenshots of the jurisdictional risk register and heatmap tool. The image contains a screenshot of the High-Risk Travel Jurisdiction.

    Download the Jurisdictional Risk Register and Heatmap Tool

    2.1.1 Identify assets

    1 – 2 hours

    1. As a group, consider critical or mission-essential functions in high-risk jurisdictions and the systems on which they depend. Brainstorm a list of the organization’s mission-supporting assets in high-risk jurisdictions. Consider:
    • Staff
    • Critical IT systems
    • Sensitive data
    • Critical operational processes
  • On a whiteboard, brainstorm the potential adverse effect of malicious agents in high-risk jurisdictions compromising critical assets. Consider the impact on:
    • Information systems.
    • Sensitive or regulated data.
    • Staff health and safety.
    • Critical operations and objectives.
    • Organizational finances.
    • Reputation and brand loyalty

    Threat

    Exploits an

    Asset

    Using a

    Method

    Creating an

    Effect

    Inputs for risk scenario identification

    Input

    Output

    • Corporate strategy
    • IT strategy
    • Security strategy
    • Business impact analyses
    • A list of the organization’s mission-supporting assets

    Materials

    Participants

    • Laptop
    • Projector
    • Whiteboard
    • Security team
    • IT leadership
    • System owner
    • Enterprise Risk Management

    Threat

    Exploits an

    Asset

    Using a

    Method

    Creating an

    Effect

    Inputs for risk scenario identification

    The image contains an example of the activity mentioned in the text above.

    Model threats to narrow the range of scenarios

    Motives and capabilities to perform attacks on critical assets vary across different threat actors.

    Category

    Actions

    Motivation

    Sophistication

    Nation-states

    Cyberespionage, cyberattacks

    Geopolitical

    High. Dedicated resources and personnel, extensive planning and coordination.

    Proxy organizations

    Espionage, destructive attacks

    Geopolitical, Ideological, Profit

    Moderate. Some planning and support functions and technical expertise.

    Cybercrime

    Theft, fraud, extortion

    Profit

    Moderate. Some planning and support functions and technical expertise.

    Hacktivists

    Disrupt operations, attack brands, release sensitive data

    Ideological

    Low. Rely on widely available tools that require little skill to deploy.

    Insiders

    Destruction or release of sensitive data, theft, exposure through negligence

    Incompetence, Discontent

    Internal access. Acting on their own or in concert with any of the above.

    • Criminals, hacktivists, and insiders vary in sophistication. Some criminal groups demonstrate a high degree of sophistication; however, a large cyber event that damages critical infrastructure does not align with their incentives to make money at minimal risk.
    • Proxy actors conduct offensive cyber operations on behalf of a beneficiary. They may be acting on behalf of a competitor, national government, or group of individuals.
    • Nation-states engage in long-term espionage and offensive cyber operations that support geopolitical and strategic policy objectives.

    2.1.2 Identify threats

    1 – 2 hours

    1. Review the outputs from activity 1.1.1 and activity 2.1.1.
    2. Identify threat agents that could undermine the security of critical assets in high-risk jurisdictions. Include internal and external actors.
    3. Assess their motives, means, and opportunities.
    • Which critical assets are most attractive? Why?
    • What paths and vulnerabilities can threat agents exploit to reach critical assets without going through a control?
    • How could they defeat existing controls? Draw on the MITRE framework to inform your analysis.
    • Once agents defeat a control, what further attack can they launch?

    Threat

    Exploits an

    Asset

    Using a

    Method

    Creating an

    Effect

    Inputs for risk scenario identification

    Input

    Output

    • Jurisdictional assessment from activity 1.1.1
    • Critical assets from activity 2.1.1
    • Potential vulnerabilities from:
      • Security control gap analysis
      • Security risk register
    • Threat intelligence
    • MITRE framework
    • A list of critical assets, threat agents, vulnerabilities, and potential attack vectors.

    Materials

    Participants

    • Laptop
    • Projector
    • Whiteboard
    • Security team
    • Infrastructure & Operations team
    • Enterprise Risk Management

    2.1.2 Identify threats (continued)

    1 – 2 hours

    1. On a whiteboard, brainstorm how threat agents will exploit vulnerabilities in critical assets to reach their goal. Redefine attack vectors to capture what could result from a successful initial attack.

    For example:

    • State actors and cybercriminals may steal or compromise end-user devices during travel to high-risk jurisdictions using malware they embed in airport charging stations, internet café networks, or hotel business centers.
    • Compromised devices may infect corporate networks and threaten sensitive data once they reconnect to them.

    Threat

    Exploits an

    Asset

    Using a

    Method

    Creating an

    Effect

    The image contains a screenshot of activity 2.1.2 as described in the text above.

    Bring together the critical risk elements into a single risk scenario

    Summarize the scenario further into a single risk statement

    Risk Scenario: High-Risk Travel

    State actors and cybercriminals can threaten staff, devices, and data during travel to high-risk jurisdictions. Device theft or compromise may occur while traveling through airports, accessing hotel computer and phone networks, or in internet cafés or other public areas. Threat actors can exploit data from compromised or stolen devices to undermine the organization’s strategic, economic, or competitive advantage. They can also infect compromised devices with malware that delivers malicious payloads once they reconnect with home networks.

    Risk Statement

    Cybercriminals compromise end-user devices during travel to high-risk jurisdictions, jeopardizing staff safety and leading to loss of sensitive data.

    Risk Scenario: Compliance Risk

    Rapid changes in the privacy and security regulatory landscape threaten an organization’s ability to meet its compliance obligations from local legal and regulatory frameworks. Organizations that fail to do so risk reputational damage, administrative fines, criminal charges, and loss of market share. In extreme cases, organizations may lose their license to operate in high-risk jurisdictions. Shifts in the regulatory landscape can involve additional requirements for data residency, cross-border data transfer, data breach notification, and third-party risk management.

    Risk Statement

    Rapid changes in the privacy and security regulations landscape threaten our ability to remain compliant, leading to reputational and financial loss.

    Fill out the Jurisdictional Risk Register and Heatmap Tool

    The tool is populated with data from two key risk scenarios: high-risk travel and compliance risk.

    The image includes two screenshots of the Jurisdictional Risk Register and Heatmap Tool.

    1. Label the risk in Tab 3, Column B.
    2. Record your risk scenario in Tab 3, Column C.
    3. Record your risk statement in Tab 3, Column D.
    4. Identify the applicable jurisdictions in Tab 3, Column E.
    5. You can further categorize the scenario as:
      • an enterprise risk (Column G).
      • an IT risk (Column H).

    Download the Jurisdictional Risk Register and Heatmap Tool

    Step 2.2

    Assess Risk Exposure

    Activities

    2.2.1 Identify existing controls

    2.2.2 Assess likelihood and impact

    This step involves the following participants:

    • Security team
    • Risk and Compliance
    • IT leadership (optional)

    Outcomes of this step

    • Assess risk exposure for each risk scenario through an analysis of its likelihood and impact.

    Brush up on risk assessment essentials

    The next step will help you prioritize IT risks based on severity.

    Likelihood of Occurrence X Likelihood of Impact = Risk Severity

    Likelihood of occurrence: How likely the risk is to occur.

    Likelihood of impact: The likely impact of a risk event.

    Risk severity: The significance of the risk.

    Evaluate risk severity against the risk tolerance thresholds and the cost of risk response.

    Identify existing controls before you proceed

    Existing controls will reduce the inherent likelihood and impact of the risk scenario you face.

    Existing controls were put in place to avoid, mitigate, or transfer key risks your organization faced in the past. Without considering existing controls, you run the risk of overestimating the likelihood and impact of the risk scenarios your organization faces in high-risk jurisdictions.

    For instance, the ability to remote-wipe corporate-owned devices will reduce the potential impact of a device lost or compromised during travel to high-risk jurisdictions.

    As you complete the risk assessment for each scenario, document existing controls that reduce their inherent likelihood and impact.

    2.2.1 Document existing controls

    6-10 hours

    1. Document the Risk Category and Existing Controls in the Jurisdictional Risk Register and Heatmap Tool.
      • Tactical controls apply to individual risks only. For instance, the ability to remote-wipe devices mitigates the impact of a device lost in a high-risk jurisdiction.
      • Strategic controls apply to multiple risks. For instance, deploying MFA for critical applications mitigates the likelihood that malicious actors can compromise a lost device and impedes their access in devices they do compromise.

    Input

    Output

    • Risk scenarios
    • Existing controls for risk scenarios

    Materials

    Participants

    • Jurisdictional Risk Register and Heatmap Tool
    • Laptop
    • Projector
    • Security team
    • IT leadership
    • Business stakeholders
    • Enterprise Risk Management

    Download the Jurisdictional Risk Register and Heatmap Tool.

    Assess the risk scenarios you identified in Phase 1

    The risk register is the central repository for risks in high-risk jurisdictions.

    • Use the second tab of the Jurisdictional Risk Register and Heatmap Tool to create likelihood, impact, and risk tolerance assessment scales to evaluate every risk event effectively.
    • Severity-level assessment is a “first pass” of your risk scenarios that will reveal your organization’s most severe risks in high-risk jurisdictions.
    • You can incorporate expected cost calculations into your evaluation to assess scenarios in greater detail.
    • Expected cost represents how much you would expect to pay in an average year for each risk event. Expected cost calculations can help compare IT risks to non-IT risks that may not use the same scales and communicate system-level risk to the business in a language they will understand.

    Expected cost calculations may not be practical. Determining robust likelihood and impact values to produce cost estimates can be challenging and time consuming. Use severity-level assessments as a first pass to make the case for risk mitigation measures and take your lead from stakeholders.

    The image contains two screenshots of the Jurisdictional Risk Register and Heatmap Tool.

    Use the Jurisdictional Risk Register and Heatmap Tool to capture and analyze your data.

    2.2.2 Assess likelihood and impact

    6-10 hours

    1. Assign each risk scenario a likelihood of occurrence and a likely impact level that represents the impact of the scenario on the whole organization considering existing controls. Record your results in Tab 3, column R and S, respectively.
    2. You can further dissect likelihood and impact into component parameters but focus first on total likelihood and impact to keep the task manageable.
    3. As you input the first few likelihood and impact values, compare them to one another to ensure consistency and accuracy. For instance, is a device lost in a high-risk jurisdiction truly more impactful than a device compromised with commercial surveillance software?
    4. The tool will calculate the probability of risk exposure based on the likelihood and consequence associated with the scenario. The results are published in Tab 3, Column T.

    Input

    Output

    • Risk scenarios
    • Assessed the likelihood of occurrence and impact for all identified risk events

    Materials

    Participants

    • Jurisdictional Risk Register and Heatmap Tool
    • Laptop
    • Projector
    • Security team
    • IT leadership
    • Business stakeholders
    • Enterprise Risk Management

    Download the Jurisdictional Risk Register and Heatmap Tool.

    Refine your risk assessment to justify your estimates

    Document the rationale behind each value and the level of consensus in group discussions.

    Stakeholders will likely ask you to explain some of the numbers you assigned to likelihood and impact assessments. Pointing to an assessment methodology will give your estimates greater credibility.

    • Assign one individual to take notes during the assessment exercise.
    • Have them document the main rationale behind each value and the level of consensus.

    The goal is to develop robust intersubjective estimates of the likelihood and impact of a risk scenario.

    We assigned a 50% likelihood rating to a risk scenario. Were we correct?

    Assess the truth of the following statements to test likelihood assessments. In this case, do these two statements seem true?

    • The risk event will likely occur once in the next two years, all things being equal.
    • In two nearly identical organizations, one out of two will experience the risk event this year.
    The image includes a screenshot of the High-Risk Travel Jurisdictions.

    Phase 3

    Execute Response

    This phase will walk you through the following activities:

    • Prioritize and treat global risks to critical assets based on their value and exposure.
    • Build an initiative roadmap that identifies and applies relevant controls to protect critical assets. Identify key risk indicators to monitor progress.

    This phase involves the following participants:

    • Security team
    • Risk and Compliance
    • IT leadership (optional)

    Step 3.1

    Treat Security Risks

    Activities

    3.1.1 Identify and assess risk response

    This step involves the following participants:

    • Security team
    • Risk and Compliance
    • IT leadership (optional)

    Outcomes of this step

    • Prioritize and treat global risks to critical assets based on their value and exposure.

    Analyze and select risk responses

    The next step will help you treat the risk scenarios you built in Phase 2.

    Identify

    Identify risk responses.

    Predict

    Predict the effectiveness of the risk response, if implemented, by estimating the residual likelihood and impact of the risk.

    Calculate

    The tool will calculate the residual severity of the risk after applying the risk response.

    The first part of the phase outlines project activities. The second part elaborates on high-risk travel and compliance risk, the two key risk scenarios we are following throughout the project. Use the Jurisdictional Risk Register and Heatmap Tool to capture your work.

    Analyze likelihood and impact to identify response

    The image contains a diagram of he risk response analysis. Risk Transfer and Risk Avoidance has the most likelihood, and Risk Acceptance and Risk Mitigation have the most impact. Risk Avoidance has the most likelihood and most impact in regards to risk response.

    3.1.1 Identify and assess risk response

    Complete the following steps for each risk scenario.

    1. Identify a risk response action that will help reduce the likelihood of occurrence or the impact if the scenario were to occur. Indicate the type of risk response (avoidance, mitigation, transfer, acceptance, or no risk exists).
    2. Assign each risk response action a residual likelihood level and a residual impact level. This is the same step you performed in Activity 2.2.2, but you are now are estimating the likelihood and impact of the risk event after you implemented the risk response action successfully. The Jurisdictional Risk Register and Heatmap Tool will generate a residual risk severity level for each risk event.
    3. Identify the potential Risk Action Owner (Project Manager) if the response is selected and turned into an IT project, and document this in the Jurisdictional Risk Register and Heatmap Tool .
    4. For each risk event, document risk response actions, residual likelihood and impact levels, and residual risk severity level.

    Input

    Output

    • Risk scenarios from Phase 2
    • Risk scenario mitigation plan

    Materials

    Participants

    • Whiteboard/flip charts
    • Jurisdictional Risk Register and Heatmap Tool
    • Security team
    • Risk and Compliance
    • IT leadership (optional)

    Download the Jurisdictional Risk Register and Heatmap Tool

    Step 3.2

    Mitigate Travel Risk

    Activities

    3.2.1 Develop a travel policy

    3.2.2 Develop travel procedures

    3.2.3 Design high-risk travel guidelines

    This step involves the following participants:

    • Security team
    • Risk and Compliance
    • IT leadership (optional)

    Outcomes of this step

    • Prioritize and treat global risks to critical assets based on their value and exposure.

    Identify controls to mitigate jurisdictional risk

    This section provides guidance on the most prevalent risk scenarios identified in Phase 2 and provides a more in-depth examination of the two most prevalent ones, high-risk travel and compliance risk. Determine the appropriate response to each risk scenario to keep global risks to critical assets aligned with the organization’s risk tolerance.

    Key Risk Scenarios

    • High-Risk Travel
    • Compliance Risk
    • Insider Threat
    • Advanced Persistent Threat
    • Commercial Surveillance

    Travel risk is a common concern in organizations with global operations

    • The security of staff, devices, and data is one of the biggest challenges facing organizations with a global footprint. Working and traveling in unpredictable environments will aways carry a degree of risk, but organizations can do much to develop a safer and more secure working environment.
    • Compromised or stolen devices can provide threat actors with access to data that could compromise the organization’s strategic, economic, or competitive advantage or expose the organization to regulatory risk.
    • For many organizations, security risk assessments, security plans, travel security procedures, security training, and incident reporting systems are a key part of their operating language.
    • The following section provides a simple structure to help organizations demystify travel in high-risk jurisdictions.

    The image contains a diagram to present high-risk jurisdictions.

    Before you leave

    • Identify high-risk countries.
    • Enable controls.
    • Limit what you pack.

    During your trip

    • Assume you are monitored.
    • Limit access to systems.
    • Prevent theft.

    When you return

    • Change your password.
    • Restore your devices.

    Case study

    Higher Education: Camosun College

    Interview: Evan Garland

    Frame additional security controls as a value-added service.

    Situation

    The director of the international department at Camosun College reached out to IT security for additional support. Department staff often traveled to hostile environments. They were concerned malicious agents would either steal end-user devices or compromise them and access sensitive data. The director asked IT security for options that would better protect traveling staff, their devices, and the information they contain.

    Challenges

    First, controls would need to admit both work and personal use of corporate devices. Staff relied exclusively on work devices for travel to mitigate the risk of personal device theft. Personal use of corporate devices during travel was common. Second, controls needed to strike the right balance between friction and effortless access. Traveling staff had only intermittent access to IT support. Restrictive controls could prevent them from accessing their devices and data altogether.

    Solution

    IT consulted staff to discuss light-touch solutions that would secure devices without introducing too much complexity or compromising functionality. They then planned security controls that involved user interaction and others that did not and identified training requirements.

    Results

    Controls with user interaction

    Controls without user interaction

    • Multifactor authentication for college systems and collaboration platforms
    • Password manager for both work and personal use for staff for stronger passwords and practices
    • Security awareness training to help traveling staff identify potential threats while traveling through airports or accessing public Wi-Fi.
    • Drive encryption and always-on VPN to protect data at rest and in transit
    • Increased setting for phishing and spam filtering for traveling staff email
    • Enhanced anti-malware/endpoint detection and response (EDR) solution for traveling laptops

    Build a program to mitigate travel risks

    There is no one-size-fits-all solution.

    The most effective solution will take advantage of existing risk management policies, processes, and procedures at your organization.

    • Develop a framework. Outline the organization’s approach to high-risk travel, including the policies, procedures, and mechanisms put in place to ensure safe travel to high-risk jurisdictions.
    • Draft a policy. Outline the organization’s risk attitude and key security principles and define roles and responsibilities. Include security responsibilities and obligations in job descriptions of staff members and senior managers.
    • Provide flexible options. Inherent travel risk will vary from one jurisdiction to another. You will likely not find an approach that works for every case. Establish locally relevant measures and plans in different security contexts and risk environments.
    • Look for quick wins. Identify measures or requirements that you can establish quickly but that can have a positive effect on the security of staff, data, and devices.
    • Monitor and review. Undertake periodic reviews of the organization’s security approach and management framework, as well as their implementation, to ensure the framework remains effective.

    3.2.1 Develop a travel policy

    1. Work with your business leaders to build a travel policy for high-risk jurisdictions. The policy should be a short and accessible document structured around four key sections:
      • A statement on the importance of staff security and safety, the scope of the policy, and who it applies to (staff, consultants, contractors, volunteers, visitors, accompanying dependants, etc.).
      • A principles section explaining the organization’s security culture, risk attitude, and the key principles that shape the organization’s approach to staff security and safety.
      • A responsibilities section setting out the organization’s security risk management structure and the roles and actions allocated to specific positions.
      • A minimal security requirements section establishing the specific security requirements that must be in place in all locations and specific locations.
    2. Common security principles include:
    • Shared responsibility – Managing risks to staff is a shared organizational responsibility.
    • Acknowledgment of risk – Managing security will not remove all risks. Staff need to appreciate, as part of their informed consent, that they are still exposed to risk.
    • Primacy of life – Staff safety is of the highest importance. Staff should never place themselves at excessive risk to meet program objectives or protect property.
    • Proportionate risk – Risks must be assessed to ensure they are proportionate to the benefits organizational activities provide and the ability to manage those risks.
    • Right to withdraw – Staff have the right to withdraw from or refuse to take up work in a particular area due to security concerns.
    • No right to remain – The organization has the right to suspend activities that it considers too dangerous.
  • Cross-reference the organization’s other governing policies that outline requirements related to security risk management, such as the health and safety policy, access control policy, and acceptable use of security assets.
  • Input

    Output

    • List of high-risk jurisdictions
    • Risk scenarios from Phase 2
    • Data inventory and data flows
    • Travel policy for high-risk jurisdictions

    Materials

    Participants

    • Whiteboard/flip charts
    • Jurisdictional Risk Register and Heatmap Tool
    • Security team
    • Legal team
    • IT leadership
    • Risk Management

    Develop security plans for high-risk travel

    Security plans advise staff on how to manage the risk identified in assessments.

    Security plans are key country documents that outline the security measures and procedures in place and the responsibilities and resources required to implement them. Security plans should be established in high-risk jurisdictions where your organization has a regular, significant presence. Security plans must remain relevant and accessible documents that address the specific risks that exist in that location, and, if appropriate, are specific about where the measures apply and who they apply to. Plans should be updated regularly, especially following significant incidents or changes in the operating environment or activities.

    Key Components

    Critical information – One-page summary of pertinent information for easy access and quick reference (e.g. curfew times, no-go areas, important contacts).

    Overview – Purpose and scope of the document, responsibilities for security plan, organization’s risk attitude, date of completion and review date, and a summary of the security strategy and policy.

    Current Context – Summary of current operating context and overall security situation; main risks to staff, assets, and operations; and existing threats and risk rating.

    Procedures – Simple security procedures that staff should adhere to in order to prevent incidents and how to respond should problems arise. Standard operating procedures (SOPs) should address key risks identified in the assessment.

    Security levels – The organization's security levels/phases, with situational indicators that reflect increasing risks to staff in that context and location and specific actions/measures required in response to increasing insecurity.

    Incident reporting – The procedures and responsibilities for reporting security-related incidents; for example, the type of incidents to be reported, the reporting structure, and the format for incident reporting.

    Determine travel risk

    Tailor your risk response to the security risk assessment you conducted in earlier stages of this project.

    Ratings are formulated by assessing several types of risk, including conflict, political/civil unrest, terrorism, crime, and health and infrastructure risks.

    Rating

    Description (Examples)

    Recommended Action

    Low

    Generally secure with adequate physical security. Low violent crime rates. Some civil unrest during significant events. Acts of terrorism rare. Risks associated with natural disasters limited and health threats mainly preventable.

    Basic personal security, travel, and health precautions required.

    Moderate

    Periodic civil unrest. Antigovernment, insurgent, or extremist groups active with sporadic acts of terrorism. Staff at risk from common and violent crime. Transport and communications services are unreliable and safety records are poor. Jurisdiction prone to natural disasters or disease epidemics.

    Increased vigilance and routine security procedures required.

    High

    Regular periods of civil unrest, which may target foreigners. Antigovernment, insurgent, or extremist groups very active and threaten political or economic stability. Violent crime rates high and targeting of foreigners is common. Infrastructure and emergency services poor. May be regular disruption to transportation or communications services. Certain areas off-limits to foreigners. Jurisdictions experiencing a natural disaster or a disease epidemic are considered high risk.

    High level of vigilance and effective, context-specific security precautions required.

    Extreme

    Undergoing active conflict or persistent civil unrest. Risk of being caught up in a violent incident or attack is very high. Civil authorities may have lost control of significant portions of the country. Lines between criminality and political and insurgent violence are blurred. Foreigners are likely to be denied access to significant parts of the country. Transportation and communication services are severely degraded or non-existent. Violence presents a direct threat to staff security.

    Stringent security precautions essential and may not be sufficient to prevent serious incidents.

    Program activities may be suspended and staff withdrawn at very short notice.

    3.2.2 Develop travel procedures

    1. Work with your business leaders to build travel procedures for high-risk jurisdictions. The procedures should be tailored to the risk assessment and address the risk scenarios identified in Phase 2.
    2. Use the categories outlined in the next two slides to structure the procedure. Address all types of travel, detail security measures, and outline what the organization expects of travelers before, during, and after their trip.
    3. Consider the implementation of special measures to limit the impact of a potential security event, including:
      • Information end-user device loaner programs.
      • Temporary travel service email accounts.
    4. Specify what happens when staff add personal travel to their work trip to cover issues such as insurance, check-in, actual travel times, etc.
    5. Discuss the rationale for each procedure. Ensure the components align with the policy statements outlined in the high-risk travel policy developed in the previous step.

    Input

    Output

    • List of high-risk jurisdictions
    • Risk scenarios from Phase 2
    • High-risk travel policy
    • Travel procedures for high-risk jurisdictions

    Materials

    Participants

    • Whiteboard/flip charts
    • Jurisdictional Risk Register and Heatmap Tool
    • Security team
    • Legal team
    • IT leadership
    • Risk Management

    Draft procedures to mitigate travel risks

    Address all types of travel, detail security measures, and outline what the organization expects of travelers before, during, and after their trip

    Introduction

    Clarifies who the procedures apply to. Highlights any differences in travel security requirements or support provided to staff, consultants, partners, and official visitors.

    Travel risk ratings

    Explains the travel or country risk rating system, how staff access the information, the different categories and indicators, and their implications.

    Roles and responsibilities

    Clarifies the responsibilities of travelers, their line managers or contact points, and senior management regarding travel security and how this changes for destinations with higher risk ratings.

    Travel authorization

    Stipulates who in the organization authorizes travel, the various compliance measures required, and how this changes for destinations with higher risk ratings.

    Travel risk assessment

    Explains when travel risk assessments are required, the template that should be used, and who approves the completed assessments.

    Travel security procedures should specify what happens when staff add personal travel to their work trip to cover issues such as insurance, check-in, actual travel times, etc.

    Pre-travel briefings

    Outlines the information that must be provided to travelers prior to departure, the type of briefing required and who provides it, and how these requirements change as risk ratings increase.

    Security training

    Explain security training required prior to travel. This may vary depending on the country’s risk rating. Includes information on training waiver system, including justifications and authorization.

    Traveler profile forms

    Travelers should complete a profile form, which includes personal details, emergency contacts, medical details, social media footprint, and proof-of-life questions (in contexts where there are abduction risks).

    Check-in protocol

    Specifies who travelers must maintain contact with while traveling and how often, as well as the escalation process in case of loss of contact. The frequency of check-ins should reflect the increase in the risk rating for the destination.

    Emergency procedures

    Outlines the organization's emergency procedures for security and medical emergencies.

    3.2.3 Design high-risk travel guidelines

    • Supplement the high-risk travel policies and procedures with guidelines to help international travelers stay safe.
    • The document is intended for an end-user audience and should reflect your organization’s policies and procedures for the use of information and information systems during international travel.
    • Use the Digital Safety Guidelines for International Travel template in concert with this blueprint to provide guidance on what end users can do to stay safe before they leave, during their trip, and when they return.
    • Consider integrating the guidelines into specialized security awareness training sessions that target end users who travel to high-risk jurisdictions.
    • The guidelines should supplement and align with existing technical controls.

    Input

    Output

    • List of high-risk jurisdictions
    • Risk scenarios from Phase 2
    • High-risk travel policy
    • High-risk travel procedure
    • Travel guidelines for high-risk jurisdictions

    Materials

    Participants

    • Whiteboard/flip charts
    • Jurisdictional Risk Register and Heatmap Tool
    • Security team
    • Legal team
    • IT leadership
    • Risk Management

    Download the Digital Safety Guidelines for International Travel template

    Step 3.3

    Mitigate Compliance Risk

    Activities

    3.3.1 Identify data localization obligations

    3.3.2 Integrate obligations into IT system design

    3.3.3 Document data processing activities

    3.3.4 Choose the right mechanism

    3.3.5 Implement the appropriate controls

    3.3.6 Identify data breach notification obligations

    3.3.7 Integrate data breach notification into incident response

    3.3.8 Identify vendor security and data protection requirements

    3.3.9 Build due diligence questionnaire

    3.3.10 Build appropriate data processing agreement

    This step involves the following participants:

    • Security team
    • Risk and Compliance
    • IT leadership (optional)

    Outcomes of this step

    • Prioritize and treat global risks to critical assets based on their value and exposure.

    Compliance risk is a prevalent risk in organizations with a global footprint

    • The legal and regulatory landscape is evolving rapidly to keep step with the pace of technological change. Security and privacy leaders are expected to mitigate the risk of noncompliance as the organization expands to new jurisdictions.
    • Organizations with a global footprint must stay abreast of local regulations and provide risk management guidance to business leaders to support global operations.
    • This sections describes four compliance risks in this context:
      • Cross-border data transfer
      • Third-party risk management
      • Data breach notification
      • Data residency

    Compliance with local obligations

    Likelihood: Medium to High

    Impact: High

    Data Residency

    Gap Controls

    • Identify and document the data localization obligations for the jurisdictions that the organization is operating in.
    • Design and implement IT systems that satisfy the data localization requirements.
    • Comply with data localization obligations within each jurisdiction.

    Heatmap of Global Data Residency Regulations

    The image contains a screenshot of a picture of a world map with various shades of blue to demonstrate the heatmap of global data residency regulations.
    Source: InCountry, 2021

    Examples of Data Residency Requirements

    Country

    Data Type

    Local Storage Requirements

    Australia

    Personal data – heath record

    My Health Records Act 2012

    China

    Personal information — critical information infrastructure operators

    Cybersecurity law

    Government cloud data

    Opinions of the Office of the Central Leading Group for Cyberspace Affairs on Strengthening Cybersecurity Administration of Cloud Computing Services for Communist Party and Government Agencies

    India

    Government email data

    The Public Records Act of 1993

    Indonesia

    Data held by electronic system operator for the public service

    Regulation 82 concerning “Electronic System and Transaction Operation”

    Germany

    Government cloud service data

    Criteria for the procurement and use of cloud services by the federal German administration

    Russia

    Personal data

    The amendments of Data Protection Act No. 152 FZ

    Vietnam

    Data held by internet service providers

    The Decree on Management, Provision, and Use of Internet Services and Information Content Online (Decree 72)

    US

    Government cloud service data

    Defense Federal Acquisition Regulation Supplement: Network Penetration Reporting and Contracting for Cloud Services (DFARS Case 2013-D018)

    3.3.1 Identify data localization obligations

    1-2 hours

    1. Work with your business leaders to identify and document the jurisdictions where your organization is operating in or providing services and products to consumers within.
    2. Work with your legal team to identify and document all relevant data localization obligations for the data your organization generates, collects, and processes in order to operate your business.
    3. Record your data localization obligations in the table below.

    Jurisdiction

    Relevant Regulations

    Local Storage Requirements

    Date Type

    Input

    Output

    • List of jurisdictions your organization is operating in
    • Relevant security and data protection regulations
    • Data inventory and data flows
    • Completed list of data localization obligations

    Materials

    Participants

    • Guidelines for Compliance With Local Security and Privacy Laws Template
    • Privacy team
    • Security team
    • Legal team
    • IT leadership
    • Risk Management

    Download the Guidelines for Compliance With Local Security and Privacy Laws Template

    3.3.2 Integrate obligations into your IT system design

    1-2 hours

    1. Work with your IT department to design the IT architecture and systems to satisfy the data localization requirements.
    2. The table below provides a checklist for integrating privacy considerations into your IT systems.

    Item

    Consideration

    Answer

    Supporting Document

    1

    Have you identified business services that process data that will be subject to localization requirements?

    2

    Have you identified IT systems associated with the business services mentioned above?

    3

    Have you established a data inventory (i.e. data types, business purposes) for the IT systems mentioned above?

    4

    Have you established a data flow diagram for the data identified above?

    5

    Have you identified the types of data that should be stored locally?

    6

    Have you confirmed whether a copy of the data locally stored will satisfy the obligations?

    7

    Have you confirmed whether an IT redesign is needed or whether modifications (e.g. adding a server) to the IT systems would satisfy the obligations?

    8

    Have you confirmed whether access from another jurisdiction is allowed?

    9

    Have you identified how long the data should be stored?

    Input

    Output

    • Data localization obligations
    • Business services that process data that will be subject to localization requirements
    • IT systems associated with business services
    • Data inventory and data flows
    • Completed checklist of localization obligations for IT system design

    Materials

    Participants

    • Guidelines for Compliance With Local Security and Privacy Laws Template
    • Privacy team
    • Security team
    • Legal team
    • IT leadership
    • Risk Management

    Download the Guidelines for Compliance With Local Security and Privacy Laws Template

    Compliance with local obligations

    Likelihood: Medium to High

    Impact: High

    Cross-Border Transfer

    Gap Controls

    • Know where you transfer your data.
    • Identify jurisdictions that your organization is operating in and that impose different requirements for the cross-border transfer of personal data.
    • Adopt and implement a proper cross-border data transfer mechanism in accordance with applicable privacy laws and regulations.
    • Re-evaluate at appropriate intervals.

    Which cross-border transfer mechanism should I choose?

    Transfer Mechanism

    Advantages

    Disadvantages

    Standard Contractual Clauses (SCC)

    • Easy to implement
    • No DPA (data processing agreement) approval
    • Not suitable for complex data transfers
    • Do not meet business agility
    • Needs legal solution

    Binding Corporate Rules (BCRs)

    • Meets business agility needs
    • Raises trust in the organization
    • Doubles as solution for art. 24/25 of the GDPR
    • Sets high compliance maturity level
    • Takes time to draft/implement
    • Requires DPA approval (scrutiny)
    • Requires culture of compliance
    • Approved by one "lead" authority and two other "co-lead“ authorities
    • Takes usually between six and nine months for the approval process only

    Code of Conduct

    • Raises trust in the sector
    • Self-regulation instead of law
    • No code of conduct approved yet
    • Takes time to draft/implement
    • Requires DPA approval and culture of compliance
    • Needs of organization may not be met

    Certification

    • Raises trust in the organization
    • No certification schemes available yet
    • Risk of compliance at minimum necessary
    • Requires audits

    Consent

    • Legal certainty
    • Transparent
    • Administrative burden
    • Some data subjects are incapable of consenting all or nothing

    3.3.3 Document data processing activities

    1-2 hours

    1. Identify and document the following information:
      • Name of business process
      • Purposes of processing
      • Lawful basis
      • Categories of data subjects and personal data
      • Data subject categories
      • Which system the data resides in
      • Recipient categories
      • Third country/international organization
      • Documents for appropriate safeguards for international transfer (adequacy, SCCs, BCRs, etc.)
      • Description of mitigating measures

    Input

    Output

    • Name of business process
    • Categories of personal data
    • Which system the data resides
    • Third country/international organization
    • Documents for appropriate safeguards for international transfer
    • Completed list of data processing activities

    Materials

    Participants

    • Guidelines for Compliance With Local Security and Privacy Laws Template
    • Privacy team
    • Security team
    • Legal team
    • IT leadership
    • Risk Management

    Download the Guidelines for Compliance With Local Security and Privacy Laws Template

    3.3.4 Choose the right mechanism

    1-2 hours

    1. Identify jurisdictions that your organization is operating in and that impose different requirements for the cross-border transfer of personal data. For example, the EU’s GDPR and China’s Personal Information Protection Law require proper cross-border transfer mechanisms before the data transfers. Your organization should decide which cross-border transfer mechanism is the best fit for your cross-border data transfer scenarios.
    2. Use the following table to identify and document the pros and cons of each data transfer mechanism and the final decision.

    Data Transfer Mechanism

    Pros

    Cons

    Final Decision

    SCC

    BCR

    Code of Conduct

    Certification

    Consent

    Input

    Output

    • List of relevant data transfer mechanisms
    • Assessment of the pros and cons of each mechanism
    • Final decision regarding which data transfer mechanism is the best fit for your organization

    Materials

    Participants

    • Guidelines for Compliance With Local Security and Privacy Laws Template
    • Privacy team
    • Security team
    • Legal team
    • IT leadership
    • Risk Management

    Download the Guidelines for Compliance With Local Security and Privacy Laws Template

    3.3.5 Implement the appropriate controls

    1-3 hours

    • One of the most common mechanisms is standard contractual clauses (SCCs).
    • Use Info-Tech’s Standard Contractual Clauses Template to facilitate your cross-border transfer activities.
    • Identify and check whether the following core components are covered in your SCC and record the results in the table below.
    # Core Components Status Note
    1 Purpose and scope
    2 Effect and invariability of the Clauses
    3 Description of the transfer(s)
    4 Data protection safeguards
    5 Purpose limitation
    6 Transparency
    7 Accuracy and data minimization
    8 Duration of processing and erasure or return of data
    9 Storage limitation
    10 Security of processing
    11 Sensitive data
    12 Onward transfers
    13 Processing under the authority of the data importer
    14 Documentation and compliance
    15 Use of subprocessors
    16 Data subject rights
    17 Redress
    18 Liability
    19 Local laws and practices affecting compliance with the Clauses
    20 Noncompliance with the Clauses and termination
    21 Description of data processing activities, such as list of parties, description of transfer, etc.
    22 Technical and organizational measures
    InputOutput
    • Description of the transfer(s)
    • Duration of processing and erasure or return of data
    • Onward transfers
    • Use of subprocessors
    • Etc.
    • Draft of the standard contractual clauses (SCC)
    MaterialsParticipants
    • Guidelines for Compliance With Local Security and Privacy Laws Template
    • Legal team
    • Privacy team
    • Security team
    • IT leadership
    • Risk Management

    Download the Guidelines for Compliance With Local Security and Privacy Laws Template

    Compliance with local obligations

    Likelihood: High

    Impact: Medium to High

    Data Breach

    Gap Controls

    • Identify jurisdictions that your organization is operating in and that impose different obligations for data breach reporting.
    • Document the notification obligations for various business scenarios, such as controller to DPA, controller to data subject, and processor to controller.
    • Integrate breach notification obligations into security incident response process.

    Examples of Data Breach Notification Obligations

    Location

    Regulation/ Standard

    Reporting Obligation

    EU

    GDPR

    72 hours

    China

    PIPL

    Immediately

    US

    HIPAA

    No later than 60 days

    Canada

    PIPEDA

    As soon as feasible

    Global

    PCI DSS

    • Visa – immediately after breach discovered
    • Mastercard – within 24 hours of discovering breach
    • American Express – immediately after breach discovered

    Summary of US State Data Breach Notification Statutes

    The image contains a graph to show the summary of the US State Data Breach Notification Statutes.

    Source: Davis Wright Tremaine

    3.3.6 Identify data breach notification obligations

    1-2 hours

    1. Identify jurisdictions that your organization is operating in and that impose different obligations for data breach reporting.
    2. Document the notification obligations for various business scenarios, such as controller to DPA, controller to data subject, and processor to controller.
    3. Record your data breach obligations in the table below.
    Region Regulation/Standard Reporting Obligation

    Input

    Output

    • List of regions and jurisdictions your business is operating in
    • List of relevant regulations and standards
    • Documentation of data breach reporting obligations in applicable jurisdictions

    Materials

    Participants

    • Guidelines for Compliance With Local Security and Privacy Laws Template
    • Legal team
    • Privacy team
    • Security team
    • IT leadership
    • Risk Management

    Download the Guidelines for Compliance With Local Security and Privacy Laws Template

    3.3.7 Integrate data breach notification into incident response

    1-2 hours

    • Integrate breach notification obligations into the security incident response process. Understand the security incident management framework.
    • All incident runbooks follow the same process: detection, analysis, containment, eradication, recovery, and post-incident activity.
    • The table below provides a basic checklist for you to consider when implementing your data breach and incident handling process.
    # Phase Considerations Status Notes
    1 Prepare Ensure the appropriate resources are available to best handle an incident.
    2 Detect Leverage monitoring controls to actively detect threats.
    3 Analyze Distill real events from false positives.
    4 Contain Isolate the threat before it can cause additional damage.
    5 Eradicate Eliminate the threat from your operating environment.
    6 Recover Restore impacted systems to a normal state of operations.
    7 Report Report data breaches to relevant regulators and data subjects if required.
    8 Post-Incident Activities Conduct a lessons-learned post-mortem analysis.
    InputOutput
    • Security and data protection incident response steps
    • Key considerations for integrating data breach notifications into incident response
    • Data breach notifications integrated into the incident response process
    MaterialsParticipants
    • Guidelines for Compliance With Local Security and Privacy Laws Template
    • Security team
    • Privacy team
    • Legal team
    • IT leadership
    • Risk Management

    Download the Guidelines for Compliance With Local Security and Privacy Laws Template

    Compliance with local obligations

    Likelihood: High

    Impact: Medium to High

    Third-Party Risk

    Gap Controls

    • Build an end-to-end third-party security and privacy risk management process.
    • Perform internal due diligence prior to selecting a service provider.
    • Stipulate the security and privacy protection obligations of the third party in a legally binding document such as contract or data processing agreement, etc.

    End-to-End Third-Party Security and Privacy Risk Management

    1. Pre-Contract
    • Due diligence check
  • Signing of Contract
    • Data processing agreement
  • Post-Contract
    • Continuous monitoring
    • Regular check or audit
  • Termination of Contract
    • Data deletion
    • Access deprovisioning

    Examples of Vendor Security Management Requirements

    Region

    Law/Standard

    Section

    EU

    General Data Protection Regulation (GDPR)

    Article 28 (1)

    Article 46 (1)

    US

    Health Insurance Portability and Accountability Act (HIPAA)

    §164.308(b)(1)

    US

    New York Department of Financial Services Cybersecurity Requirements

    500.11(a)

    Global

    ISO 27002:2013

    15.1.1

    15.1.2

    15.1.3

    15.2.1

    15.2.2

    US

    NIST 800-53

    SA-12

    SA-12 (2)

    US

    NIST Cybersecurity Framework

    ID-SC-1

    ID-SC-2

    ID-SC-3

    ID-SC-4

    Canada

    OSFI Cybersecurity Guidelines

    4.25

    4.26

    3.3.8 Identify vendor security and data protection requirements

    1-2 hours

    • Effective vendor security risk management is an end-to-end process that includes assessment, risk mitigation, and periodic reassessments.
    • An efficient and effective assessment process can only be achieved when all stakeholders are participating.
    • Identify and document your vendor security and data protection requirements in the table below.
    Region Law/Standard Section Requirements

    Input

    Output

    • List of regions and jurisdictions your business is operating in
    • List of relevant regulations and standards
    • Documentation of vendor security and data protection obligations in applicable jurisdictions

    Materials

    Participants

    • Guidelines for Compliance With Local Security and Privacy Laws Template
    • Legal team
    • Privacy team
    • Security team
    • IT leadership
    • Risk Management

    Download the Guidelines for Compliance With Local Security and Privacy Laws Template

    3.3.9 Build due diligence questionnaire

    1-2 hours

    Perform internal due diligence prior to selecting a service provider.

    1. Build and right-size your vendor security questionnaire by leveraging Info-Tech’s Vendor Security Questionnaire template.
    2. Document your vendor security questionnaire in the table below.
    # Question Vendor Request Vendor Comments
    1 Document Requests
    2 Asset Management
    3 Governance
    4 Supply Chain Risk Management
    5 Identify Management, Authentication, and Access Control
    InputOutput
    • List of regions and jurisdictions your business is operating in
    • List of relevant regulations and standards
    • Business security and data protection requirements and expectations
    • Draft of due diligence questionnaire
    MaterialsParticipants
    • Guidelines for Compliance With Local Security and Privacy Laws Template
    • Legal team
    • Privacy team
    • Security team
    • IT leadership
    • Risk Management

    Download the Guidelines for Compliance With Local Security and Privacy Laws Template

    3.3.10 Build appropriate data processing agreement

    1-2 hours

    1. Stipulate the security and privacy protection obligations of the third party in a legally binding document such as contract or data processing agreement, etc.
    2. Leverage Info-Tech’s Data Processing Agreement Template to put the language into your legally binding document.
    3. Use the table below to check whether core components of a typical DPA are covered in your document.
    # Core Components Status Note
    1 Processing of personal data
    2 Scope of application and responsibilities
    3 Processor's obligations
    4

    Controller's obligations

    5 Data subject requests
    6 Right to audit and inspection
    7 Subprocessing
    8 Data breach management
    9 Security controls
    10 Transfer of personal data
    11 Duty of confidentiality
    12 Compliance with applicable laws
    13 Service termination
    14 Liability and damages
    InputOutput
    • Processing of personal data
    • Processor’s obligations
    • Controller’s obligations
    • Subprocessing
    • Etc.
    • Draft of data processing agreement (DPA)
    MaterialsParticipants
    • Guidelines for Compliance With Local Security and Privacy Laws Template
    • Legal team
    • Privacy team
    • Security team
    • IT leadership
    • Risk Management

    Download the Guidelines for Compliance With Local Security and Privacy Laws Template

    Summary of Accomplishment

    Problem Solved

    By following Info-Tech’s methodology for securing global operations, you have:

    • Evaluated the security context of your organization’s global operations.
    • Identified security risks scenarios unique to high-risk jurisdictions and assessed the exposure of critical assets.
    • Planned and executed a response.

    You have gone through a deeper analysis of two key risk scenarios that affect global operations:

    • Travel to high-risk jurisdictions.
    • Compliance risk.

    If you would like additional support, have our analysts guide you through an Info-Tech workshop or Guided Implementation.

    Contact your account representative for more information.

    workshop@infotech.com

    1-888-670-8889

    Additional Support

    If you would like additional support, have our analysts guide you through other phases as part of an Info-Tech Workshop.

    The image contains a picture of Michel Hebert.

    Contact your account representative for more information.

    workshops@infotech.com 1-888-670-8889

    To accelerate this project, engage your IT team in an Info-Tech workshop with an Info-Tech analyst team. Info-Tech analysts will join you and your team at your location or welcome you to Info-Tech’s historic Toronto office to participate in an innovative onsite workshop.

    The following are sample activities that will be conducted by Info-Tech analysts with your team:

    The image contains a screenshot of High-Risk Travel Jurisdictions.

    Identify High-Risk Jurisdictions

    Develop requirements to identify high-risk jurisdictions.

    The image contains a screenshot of Build Risk Scenarios.

    Build Risk Scenarios

    Build risk scenarios to capture assets, vulnerabilities, threats, and the potential effect of a compromise.

    External Research Contributors

    Ken Muir

    CISO

    LMC Security

    Premchand Kurup

    CEO

    Paramount Computer Systems

    Preeti Dhawan

    Manager, Security Governance

    Payments Canada

    Scott Wiggins

    Information Risk and Governance

    CDPHP

    Fritz Y. Jean Louis

    CISO

    Globe and Mail

    Eric Gervais

    CIO

    Ovivo Water

    David Morrish

    CEO

    MBS Techservices

    Evan Garland

    Manager, IT Security

    Camosun College

    Jacopo Fumagalli

    CISO

    Axpo

    Dennis Leon

    Governance and Security Manager

    CPA Canada

    Tero Lehtinen

    CIO

    Planmeca Oy

    Related Info-Tech Research

    Build an IT Risk Management Program

    • Build a program to identify, evaluate, assess, and treat IT risks.
    • Monitor and communicate risks effectively to support business decision making.

    Combine Security Risk Management Components Into One Program

    • Develop a program focused on assessing and managing information system risks.
    • Build a governance structure that integrates security risks within the organization’s broader approach to risk management.

    Build an Information Security Strategy

    • Build a holistic, risk-aware strategy that aligns to business goals.
    • Develop a roadmap of prioritized initiatives to implement the strategy over 18 to 36 months.

    Bibliography

    2022 Cost of Insider Threats Global Report.” Ponemon Institute, NOVIPRO, 9 Feb. 2022. Accessed 25 May 22.

    “Allianz Risk Barometer 2022.” Allianz Global Corporate & Specialty, Jan. 2022. Accessed 25 May 22.

    Bickley, Shaun. “Security Risk Management: a basic guide for smaller NGOs”. European Interagency Security Forum (EISF), 2017. Web.

    “Biden Administration Warns against spyware targeting dissidents.” New York Times, 7 Jan 22. Accessed 20 Jan 2022.

    Boehm, Jim, et al. “The risk-based approach to cybersecurity.” McKinsey & Company, October 2019. Web.

    “Cost of a Data Breach Report 2021.” IBM Security, July 2021. Web.

    “Cyber Risk in Asia-Pacific: The Case for Greater Transparency.” Marsh & McLennan Companies, 2017. Web.

    “Cyber Risk Index.” NordVPN, 2020. Accessed 25 May 22

    Dawson, Maurice. “Applying a holistic cybersecurity framework for global IT organizations.” Business Information Review, vol. 35, no. 2, 2018, pp. 60-67.

    “Framework for improving critical infrastructure cybersecurity.” National Institute of Standards and Technology, 16 Apr 2018. Web.

    “Global Cybersecurity Index 2020.” International Telecommunication Union (ITU), 2021. Accessed 25 May 22.

    “Global Risk Survey 2022.” Control Risks, 2022. Accessed 25 May 22.

    “International Travel Guidance for Government Mobile Devices.” Federal Mobility Group (FMG), Aug. 2021. Accessed 18 Nov 2021.

    Kaffenberger, Lincoln, and Emanuel Kopp. “Cyber Risk Scenarios, the Financial System, and Systemic Risk Assessment.” Carnegie Endowment for International Peace, September 2019. Accessed 11 Jan 2022.

    Koehler, Thomas R. Understanding Cyber Risk. Routledge, 2018.

    Owens, Brian. “Cybersecurity for the travelling scientist.” Nature, vol. 548, 3 Aug 2017. Accessed 19 Jan. 2022.

    Parsons, Fintan J., et al. “Cybersecurity risks and recommendations for international travellers.” Journal of Travel Medicine, vol. 1, no. 4, 2021. Accessed 19 Jan 2022.

    Quinn, Stephen, et al. “Identifying and estimating cybersecurity risk for enterprise risk management.” National Institute of Standards and Technology (NIST), Interagency or Internal Report (IR) 8286A, Nov. 2021.

    Quinn, Stephen, et al. “Prioritizing cybersecurity risk for enterprise risk management.” NIST, IR 8286B, Sept. 2021.

    “Remaining cyber safe while travelling security recommendations.” Government of Canada, 27 April 2022. Accessed 31 Jan 2022.

    Stine, Kevin, et al. “Integrating cybersecurity and enterprise risk management.” NIST, IR 8286, Oct. 2020.

    Tammineedi, Rama. “Integrating KRIs and KPIs for effective technology risk management.” ISACA Journal, vol. 4, 1 July 2018.

    Tikk, Eneken, and Mika Kerttunen, editors. Routledge Handbook of International Cybersecurity. Routledge, 2020.

    Voo, Julia, et al. “National Cyber Power Index 2020.” Belfer Center for Science and International Affairs, Harvard Kennedy School, Sept. 2020. Web.

    Zhang, Fang. “Navigating cybersecurity risks in international trade.” Harvard Business Review, Dec 2021. Accessed 31 Jan 22.

    Appendix

    Insider Threat

    Key Risk Scenario

    Likelihood: Medium to High

    Impact: High

    Gap Controls

    The image contains a picture of the Gap Controls. The controls include: Policy and Awareness, Identification, Monitoring and Visibility, which leads to Cooperation.

    • Identification: Effective and efficient management of insider threats begins with a threat and risk assessment to establish which assets and which employees to consider, especially in jurisdictions associated with sensitive or critical data. You need to pay extra attention to employees who are working in satellite offices in jurisdictions with loose security and privacy laws.
    • Monitoring and Visibility: Organizations should monitor critical assets and groups with privileged access to defend against malicious behavior. Implement an insider threat management platform that provides your organization with the visibility and context into data movement, especially cross-border transfers that might cause security and privacy breaches.
    • Policy and Awareness Training: Insider threats will persist without appropriate action and culture change. Training and consistent communication of best practices will mitigate vulnerabilities to accidental or negligent attacks. Customized training materials using local languages and role-based case studies might be needed for employees in high-risk jurisdictions.
    • Cooperation: An effective insider threat management program should be built with cross-team functions such as Security, IT, Compliance and Legal, etc.

    For more holistic approach, you can leverage our Reduce and Manage Your Organization’s Insider Threat Risk blueprint.

    Info-Tech Insight

    You can’t just throw tools at a human problem. While organizations should monitor critical assets and groups with privileged access to defend against malicious behavior, good management and supervision can help detect attacks and prevent them from happening in the first place.

    Insider threats are not industry specific, but malicious insiders are

    Industry

    Actors

    Risks

    Tactics

    Motives

    State and Local Government

    • Full-time employees
    • Current employees
    • Privileged access to personally identifiable information, financial assets, and physical property
    • Abuse of privileged access
    • Received or transferred fraudulent funds
    • Financial gain
    • Recognition
    • Benefiting foreign entity

    Information Technology

    • Equal mix of former and current employees
    • Privileged access to networks or systems as well as data
    • Highly technical attacks
    • Received or transferred fraudulent funds
    • Revenge
    • Financial gain

    Healthcare

    • Majority were full-time and current employees
    • Privileged access to customer data with personally identifiable information, financial assets
    • Abuse of privileged access
    • Received or transferred fraudulent funds
    • Financial gain
    • Entitlement

    Finance and Insurance

    • Majority were full-time and current employees
    • Authorized users
    • Electronic financial assets
    • Privileged access to customer data
    • Created or used fraudulent accounts
    • Fraudulent purchases
    • Identity theft
    • Financial gain
    • Gambling addiction
    • Family pressures
    • Multiple motivations

    Source: Carnegie Mellon University Software Engineering Institute, 2019

    Advanced Persistent Threat

    Key Risk Scenario #4

    Likelihood: Medium to High

    Impact: High

    Gap Controls

    The image contains a screenshot of the Gap Controls listed: Prevent, Detect, Analyze, Respond.

    Prevent: Defense in depth is the best approach to protect against unknown and unpredictable attacks. Effective anti-malware, diligent patching and vulnerability management, and strong human-centric security are essential.

    Detect: There are two types of companies – those who have been breached and know it, and those who have been breached and don’t know it. Ensure that monitoring, logging, and event detection tools are in place and appropriate to your organizational needs.

    Analyze: Raw data without interpretation cannot improve security and is a waste of time, money, and effort. Establish a tiered operational process that not only enriches data but also provides visibility into your threat landscape.

    Respond: Organizations can’t rely on ad hoc response anymore – don’t wait until a state of panic. Formalize your response processes in a detailed incident runbook to reduce incident remediation time and effort.

    Best practices moving forward

    Defense in Depth

    Lock down your organization. Among other tactics, control administrative privileges, leverage threat intelligence, use IP whitelisting, adopt endpoint protection and two-factor authentication, and formalize incident response measures.

    Block Indicators

    Information alone is not actionable. A successful threat intelligence program contextualizes threat data, aligns intelligence with business objectives, and then builds processes to satisfy those objectives. Actively block indicators and act upon gathered intelligence.

    Drive Adoption

    Create organizational situational awareness around security initiatives to drive adoption of foundational security measures: network hardening, threat intelligence, red-teaming exercises, and zero-day mitigation, policies, and procedures.

    Supply Chain Security

    Security extends beyond your organization. Ensure your organization has a comprehensive view of your organizational threat landscape and a clear understanding of the security posture of any managed service providers in your supply chain.

    Awareness and Training

    Conduct security awareness and training. Teach end users how to recognize current cyberattacks before they fall victim – this is a mandatory first line of defense.

    Additional Resources

    Follow only official sources of information to help you assess risk

    The image contains an image highlighting a few additional resources.

    As misinformation is a major attack vector for malicious actors, follow only reliable sources for cyberalerts and actionable intelligence. Aggregate information from these reliable sources.

    Federal Cyber Agency Alerts

    Informational Resources

    Info-Tech Insight

    The CISA Shields Up site provides the latest cyber risk updates on the Russia-Ukraine conflict and should provide the most value in staying informed.

    Endpoint Management Selection Guide

    • Buy Link or Shortcode: {j2store}65|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: End-User Computing Applications
    • Parent Category Link: /end-user-computing-applications

    Endpoint management solutions are becoming an essential solution: Deploying the right devices and applications to the right user and the need for zero-touch provisioning are indispensable parts of a holistic strategy for improving customer experience. However, selecting the right-sized platform that aligns with your requirements is a big challenge.

    Following improvements in end-user computation strategies, selection of the right endpoint management solution is a crucial next step in delivering a concrete business value.

    Our Advice

    Critical Insight

    Investigate vendors’ roadmaps to figure out which of the candidate platforms can fulfill your long-term requirements, without any unnecessary investment in features that are not currently useful for you. Make sure you don’t purchase capabilities that you will never use.

    Impact and Result

    • Determine what you require from an endpoint management solution.
    • Review the market space and product offerings, and compare capabilities of key players.
    • Create a use case and use top-level requirements to determine use cases and shortlist vendors.
    • Conduct a formal process for interviewing vendors using Info-Tech’s templates to select the best platform for your requirements.

    Endpoint Management Selection Guide Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Endpoint Management Selection Guide Storyboard – A structured guide to walk you through the endpoint management market.

    This storyboard will help you understand endpoint management solution core capabilities and prepare you to select an appropriate tool.

    • Endpoint Management Selection Guide Storyboard

    2. UEM Requirements Workbook – A template to help you build your first draft of requirements for UEM selection.

    Use this spreadsheet to brainstorm use cases and features to satisfy your requirements. This document will be help you score solutions and narrow down the field to a list of candidates who can meet your requirements.

    • UEM Requirements Workbook
    [infographic]

    Further reading

    Endpoint Management Selection Guide

    Streamline your organizational approach to selecting a right-sized endpoint management platform.

    Endpoint Management Selection Guide

    Streamline your organizational approach toward the selection of a right-sized endpoint management platform.

    EXECUTIVE BRIEF

    Analyst Perspective

    Revolutionize your endpoint management with a proper tool selection approach

    The endpoint management market has an ever-expanding and highly competitive landscape. The market has undergone tremendous evolution in past years, from device management to application deployments and security management. The COVID-19 pandemic forced organizations to service employees and end users remotely while making sure corporate data is safe and user satisfaction doesn't get negatively affected. In the meantime, vendors were forced to leverage technology enhancements to satisfy such requirements.

    That being said, endpoint management solutions have become more complex, with many options to manage operating systems and run applications for relevant user groups. With the work-from-anywhere model, customer support is even more important than before, as a remote workforce may face more issues than before, or enterprises may want to ensure more compliance with policies.

    Moreover, the market has become more complex, with lots of added capabilities. Some features may not be beneficial to corporations, and with a poor market validation, businesses may end up paying for some capabilities that are not useful.

    In this blueprint, we help you quickly define your requirements for endpoint management and narrow down a list to find the solutions that fulfill your use cases.

    An image of Mahmoud Ramin, PhD

    Mahmoud Ramin, PhD
    Senior Research Analyst, Infrastructure and Operations
    Info-Tech Research Group

    Executive Summary

    Your Challenge

    Endpoint management solutions are becoming increasingly essential – deploying the right devices and applications to the right users and zero-touch provisioning are indispensable parts of a holistic strategy for improving customers' experience. However, selecting the right-sized platform that aligns with your requirements is a big challenge.

    Following improvements in end-user computation strategies, selection of the right endpoint management solution is a crucial next step in delivering concrete business value.

    Common Obstacles

    Despite the importance of selecting the right endpoint management platform, many organizations struggle to define an approach to picking the most appropriate vendor and rolling out the solution in an effective and cost-efficient manner. There are many options available, which can cause business and IT leaders to feel lost.

    The endpoint management market is evolving quickly, making the selection process tedious. On top of that, IT has a hard time defining their needs and aligning solution features with their requirements.

    Info-Tech's Approach

    Determine what you require from an endpoint management solution.

    Review the market space and product offerings, and compare the capabilities of key players.

    Create a use case – use top-level requirements to determine use cases and short-list vendors.

    Conduct a formal process for interviewing vendors, using Info-Tech's templates to select the best platform for your requirements.

    Info-Tech Insight

    Investigate vendors' roadmaps to figure out which of the candidate platforms can fulfill your long-term requirements without any unnecessary investment in features that are not currently useful for you. Make sure you don't purchase capabilities that you will never use.

    What are endpoint management platforms?

    Our definition: Endpoint management solutions are platforms that enable IT with appropriate provisioning, security, monitoring, and updating endpoints to ensure that they are in good health. Typical examples of endpoints are laptops, computers, wearable devices, tablets, smart phones, servers, and the Internet of Things (IoT).

    First, understand differences between mobile management solutions

    • Endpoint management solutions monitor and control the status of endpoints. They help IT manage and control their environment and provide top-notch customer service.
    • These solutions ensure a seamless and efficient problem management, software updates and remediations in a secure environment.
    • Endpoint management solutions have evolved very quickly to satisfy IT and user needs:
    • Mobile Device Management (MDM) helps with controlling features of a device.
    • Enterprise Mobile Management (EMM) controls everything in a device.
    • Unified Endpoint Management (UEM) manages all endpoints.

    Endpoint management includes:

    • Device management
    • Device configuration
    • Device monitoring
    • Device security

    Info-Tech Insight

    As endpoint management encompasses a broad range of solution categories including MDM, EMM, and UEM, look for your real requirements. Don't pay for something that you won't end up using.

    As UEM covers all of MDM and EMM capabilities, we overview market trends of UEM in this blueprint to give you an overall view of market in this space.

    Your challenge: Endpoint management has evolved significantly over the past few years, which makes software selection overwhelming

    An mage showing endpoint management visualzed as positions on an iceberg. at the top is UEM, at the midpoint above the waterline is Enterprise Mobile Management, and below the water is Mobile Device Management.

    Additional challenges occur in securing endpoints

    A rise in the number of attacks on cloud services creates a need to leverage endpoint management solutions

    MarketsandMarkets predicted that global cloud infrastructure services would increase from US$73 billion in 2019 to US$166.6 billion in 2024 (2019).

    A study by the Ponemon Institute showed that 68% of respondents believe that security attacks increased over the past 12 months (2020).

    The study reveals that over half of IT security professionals who participated in the survey believe that organizations are not very efficient in securing their endpoints, mainly because they're not efficient in detecting attacks.

    IT professionals would like to link endpoint management and security platforms to unify visibility and control, to determine potential risks to endpoints, and to manage them in a single solution.

    Businesses will continue to be compromised by the vulnerabilities of cloud services, which pose a challenge to organizations trying to maintain control of their data.

    Trends in endpoint management have been undergoing a tremendous change

    In 2020, about 5.2 million users subscribed to mobile services, and smartphones accounted for 65% of connections. This will increase to 80% by 2025.
    Source: Fortune Business Insights, 2021

    Info-Tech's methodology for selecting a right-sized endpoint management platform

    1. Understand Core Features and Build Your Use Case

    2. Discover the Endpoint Management Market Space and Select the Right Vendor

    Phase Steps

    1. Define endpoint management platforms
    2. Explore endpoint management trends
    3. Classify table stakes & differentiating capabilities
    4. Streamline the requirements elicitation process for a new endpoint management platform
    1. Discover key players across the vendor landscape
    2. Engage the shortlist and select finalists
    3. Prepare for implementation

    Phase Outcomes

    1. Consensus on scope of endpoint management and key endpoint management platform capabilities
    2. Top-level use cases and requirements
    1. Overview of shortlisted vendors
    2. Prioritized list of UEM features

    Guided Implementation

    What does a typical GI on this topic look like?

    Phase 1 Phase 2

    Call #1: Understand what an endpoint management platform is and learn how it evolved. Discuss core capabilities and key trends.
    Call #2: Build a use case and define features to fulfill the use case.

    Call #3: Define your core endpoint management platform requirements.
    Call #4: Evaluate the endpoint management platform vendor landscape and shortlist viable options.
    Review implementation considerations.

    A Guided Implementation (GI) is a series of calls with an Info-Tech analyst to help implement our best practices in your organization.

    The endpoint management purchase process should be broken into segments:

    1. Endpoint management vendor shortlisting with this buyer's guide
    2. Structured approach to selection
    3. Contract review

    Info-Tech's approach

    The Info-Tech difference:
    Analyze needs

    Evaluate solutions

    Determine where you need to improve the tools and processes used to support the company.

    Determine the best fit for your needs by scoring against features.

    Assess existing solution

    Features

    Determine if your solution can be upgraded or easily updated to meet your needs.

    Determine which features will be key to your success

    Create a business case for change

    Use Cases

    A two-part business case will focus on a need to change and use cases and requirements to bring stakeholders onboard.

    Create use cases to ensure your needs are met as you evaluate features

    Improve existing

    High-Level Requirements

    Work with Info-Tech's analysts to determine next steps to improve your process and make better use of the features you have available.

    Use the high-level requirements to determine use cases and shortlist vendors

    Complementary research:

    Create a quick business case and requirements document to align stakeholders to your vision with Info-Tech's Rapid Application Selection Framework.
    See what your peers are saying about these vendors at SoftwareReviews.com.

    Info-Tech offers various levels of support to best suit your needs

    DIY Toolkit

    “Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful.”

    Guided Implementation

    “Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track.”

    Workshop

    “We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place.”

    Consulting

    “Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project.”

    Diagnostics and consistent frameworks used throughout all four options

    Phase 1

    Understand core features and build your business case

    Phase 1

    Phase 2

    Define endpoint management platforms

    Explore endpoint management trends

    Classify table stakes & differentiating capabilities

    Streamline the requirements elicitation process for a new endpoint management platform

    Discover key players across the vendor landscape

    Engage the shortlist and select finalist

    Prepare for implementation

    This phase will walk you through the following activity:

    Define use cases and core features for meeting business and technical goals

    This phase involves the following participants:

    • CIO
    • IT manager
    • Infrastructure & Applications directors
    Mobile Device Management

    Enterprise Mobile Management

    MDM applies security over corporate-owned devices.

    What is MDM and what can you do with it?

    1. MDM helps manage and control corporate owned devices.
    2. You can enforce company policies, track, monitor, and lock device remotely by an MDM.
    3. MDM helps with remote wiping of the device when it is lost or stolen.
    4. You can avoid unsecure Wi-Fi connections via MDM.

    EMM solutions solve the restrictions arose with BYOD (Bring Your Own Device) and COPE (Corporate Owned, Personally Enabled) provisioning models.

    • IT needs to secure corporate-owned data without compromising personal and private data. MDM cannot fulfill this requirement. This led to the development of EMM solutions.
    • EMM tools allow you to manage multiple device platforms through MDM protocols. These tools enforce security settings, allow you to push apps to managed devices, and monitor patch compliance through reporting.

    MDM solutions function at the level of corporate devices. Something else was needed to enable personal device management.

    Major components of EMM solutions

    Mobile Application Management (MAM)

    Allows organizations to control individual applications and their associated data. It restricts malicious apps and enables in-depth application management, configuration, and removal.

    Containerization

    Enables separation of work-related data from private data. It provides encrypted containers on personal devices to separate the data, providing security on personal devices while maintaining users' personal data.

    Mobile Content Management (MCM)

    Helps remote distribution, control, management, and access to corporate data.

    Mobile Security Management (MSM)

    Provides application and data security on devices. It enables application analysis and auditing. IT can use MSM to provide strong passwords to applications, restrict unwanted applications, and protect devices from unsecure websites by blacklisting them.

    Mobile Expense Management (MEM)

    Enables mobile data communication expenses auditing. It can also set data limits and restrict network connections on devices.

    Identity Management

    Sets role-based access to corporate data. It also controls how different roles can use data, improving application and data security. Multifactor authentication can be enforced through the identity management featured of an EMM solution.

    Unified endpoint management: Control all endpoints in a single pane of glass

    IT admins used to provide customer service such as installation, upgrades, patches, and account administration via desktop support. IT support is not on physical assistance over end users' desktops anymore.

    The rise of BYOD enhanced the need to be able to control sensitive data outside corporate network connection on all endpoints, which was beyond the capability of MDM and EMM solutions.

    • It's now almost impossible for IT to be everywhere to support customers.
    • This created a need to conduct tasks simultaneously from one single place.
    • UEM enables IT to run, manage, and control endpoints from one place, while ensuring that device health and security remain uncompromised.
    • UEM combines features of MDM and EMM while extending EMM's capabilities to all endpoints, including computers, laptops, tablets, phones, printers, wearables, and IoT.

    Info-Tech Insight

    Organizations once needed to worry about company connectivity assets such as computers and laptops. To manage them, traditional client management tools like Microsoft Configuration Manager would be enough.

    With the increase in the work-from-anywhere model, it is very hard to control, manage, and monitor devices that are not connected to a VPN. UEM solutions enable IT to tackle this challenge and have full visibility into and management of any device.

    UEM platforms help with saving costs and increasing efficiency

    UEM helps corporates save on their investments as it consolidates use-case management in a single console. Businesses don't need to invest in different device and application management solutions.

    From the employee perspective, UEM enables them to work on their own devices while enforcing security on their personal data.

    • Security and privacy are very important criteria for organizations. With the rapid growth of the work-from-anywhere model, corporate security is a huge concern for companies.
    • Working from home has forced companies to invest a lot in data security, which has led to high UEM demand. UEM solutions streamline security management by consolidating device management in a single platform.
    • With the fourth-generation industrial revolution, we're experiencing a significant rise in the use of IoT devices. UEM solutions are very critical for managing, configuring, and securing these devices.
    • There will be a huge increase in cyber threats due to automation, IoT, and cloud services. The pandemic has sped up the adoption of such services, forcing businesses to rethink their enterprise mobility strategies. They are now more cautious about security risks and remediations. Businesses need UEM to simplify device management on multiple endpoints.
    • With UEM, IT environment management gets more granular, while giving IT better visibility on devices and applications.

    UEM streamlines mundane admin tasks and simplifies user issues.

    Even with a COPE or COBO provisioning model, without any IT intervention, users can decide on when to install relevant updates. It also may lead to shadow IT.

    Endpoint management, and UEM more specifically, enables IT to enforce administration over user devices, whether they are corporate or personally owned. This is enabled without interfering with private/personal data.

    Where it's going: The future state of UEM

    Despite the fast evolution of the UEM market, many organizations do not move as fast as technological capabilities. Although over half of all organizations have at least one UEM solution, they may not have a good strategy or policies to maximize the value of technology (Tech Orchard, 2022). As opposed to such organizations, there are others that use UEM to transform their endpoint management strategy and move service management to the next level. That integration between endpoint management and service management is a developing trend (Ivanti, 2021).

    • SaaS tools like Office 365 are built to be used on multiple devices, including multiple computers. Further, the pandemic saw 47% of organizations significantly increase their use of BYOD (Cybersecurity Insiders, 2021).
    • Over 2022, 78% of people worked remotely for at least some amount of time during the week (Tech Orchard, 2022).
    • 84% of organizations believe that cybersecurity threat alarms are becoming very overwhelming, and almost half of companies believe that the best way to tackle this is through consolidating platforms so that everything will be visible and manageable through a single pane of glass (Cybersecurity Insiders, 2022).
    • The UEM market was worth $3.39 billion in 2020. It is expected to reach $53.65 billion by 2030, with an annual growth rate of 31.7% (Datamation, 2022). This demonstrates how dependent IT is becoming on endpoint management solutions.

    An image of a donut chart showing the current state of UEM Strategy.

    Only 27% of organizations have "fully deployed" UEM "with easy management across all endpoints"
    Source: IT Pro Today, 2018.

    Endpoint Management Key Trends

    • Commoditization of endpoint management features. Although their focus is the same, some UEM solutions have unique features.
    • New endpoint management paradigms have emerged. Endpoint management has evolved from client management tools (CMT) and MDM into UEM, also known as "modern management" (Ivanti, 2022).
    • One pane of glass for the entire end-user experience. Endpoint management vendors are integrating their solution into their ITSM, ITOM, digital workspace, and security products.
    • AI-powered insights. UEM tools collect data on endpoints and user behavior. Vendors are using their data to differentiate themselves: Products offer threat reports, automated compliance workflows, and user experience insights. The UEM market is ultimately working toward autonomous endpoint management (Microsoft, 2022).
    • Web apps and cloud storage are the new normal. Less data is stored locally. Fewer apps need to be patched on the device. Apps can be accessed on different devices more easily. However, data can more easily be accessed on BYOD and on new operating systems like Chrome OS.
    • Lighter device provisioning tools. Instead of managing thick images, UEM tools use lighter provisioning packages. Once set up, Autopilot and UEM device enrollment should take less time to manage than thick images.
    • UEM controls built around SaaS. Web apps and the cloud allow access from any device, even unmanaged BYOD. UEM tools allow IT to apply the right level of control for the situation – mobile application management, mobile content management, or mobile device management.
    • Work-from-anywhere and 5G result in more devices outside of your firewalls. Cloud-based management tools are not limited by your VPN connection and can scale up more easily than traditional, on-prem tools.

    Understand endpoint management table stakes features

    Determine high-level use cases to help you narrow down to specific features

    Support the organization's operating systems:
    Many UEM vendors support the most dominant operating systems, Windows and Mac; however, they are usually stronger in one particular OS than the other. For instance, Intune supports both Windows and Mac, although there are some drawbacks with MacOS management by Intune. Conversely, Jamf is mainly for MacOS and iOS management. Enterprises look to satisfy their end users' needs. The more UEM vendors support different systems, the more likely enterprises will pick them. Although, as mentioned, in some instances, enterprises may need to select more than one option, depending on their requirements.

    Support BYOD and remote environments:
    With the impact of the pandemic on work model, 60-70% of workforce would like to have more flexibility for working remotely (Ivanti, 2022). BYOD is becoming the default, and SaaS tools like Office 365 are built to be used on multiple devices, including multiple computers. As BYOD can boost productivity (Samsung Insights, 2016), you may be interested in how your prospective UEM solution will enable this capability with remote wipe (corporate wipe capability vs. wiping the whole device), data and device tracking, and user activity auditing.

    Understand endpoint management table stakes features

    Determine high-level use cases to help you narrow down to specific features

    Integration with the enterprise's IT products:
    To get everything in a single platform and to generate better metrics and dashboards, vendors provide integrations with ticketing and monitoring solutions. Many large vendors have strong integrations with multiple ITSM and ITAM platforms to streamline incident management, request management, asset management, and patch management.

    Support security and compliance policies:
    With the significant boost in work-from-anywhere, companies would like to enable endpoint security more than ever. This includes device threat detection, malware detection, anti-phishing, and more. All UEMs provide these, although the big difference between them is how well they enable security and compliance, and how flexible they are when it comes to giving conditional access to certain data.

    Provide a fully automated vs manual deployment:
    Employees want to get their devices faster, IT wants to deploy devices faster, and businesses want to enable employees faster to get them onboard sooner. UEMs have the capability to provide automated and manual deployment. However, the choice of solution depends on enterprise's infrastructure and policies. Full automation of deployment is very applicable for corporate devices, while it may not be a good option for personally owned devices. Define your user groups and provisioning models, and make sure your candidate vendors satisfy requirements.

    Plan a proper UEM selection according to your requirements

    1. Identify IT governance, policy, and process maturity
      Tools cannot compensate for your bad processes. You should improve deploying and provisioning processes before rolling out a UEM. Automation of a bad process only wraps the process in a nicer package – it does not fix the problem.
      Refer to InfoTech's Modernize and Transform Your End-User Computing Strategy for more information on improving endpoint management procedures.
    2. Consider supported operating systems, cloud services, and network infrastructure in your organization
      Most UEMs support all dominant operating systems, but some solutions have stronger capability for managing a certain OS over the other.
    3. Define enterprise security requirements
      Investigate security levels, policies, and requirements to align with the security features you're expecting in a UEM.
    4. Selection and implementation of a UEM depends on use case. Select a vendor that supports your use cases
      Identify use cases specific to your industry.
      For example, UEM use cases in Healthcare:
      • Secure EMR
      • Enforce HIPAA compliance
      • Secure communications
      • Enable shared device deployment

    Activity: Define use cases and core features for meeting business and technical goals

    1-2 hours

    1. Brainstorm with your colleagues to discuss your challenges with endpoint management.
    2. Identify how these challenges are impacting your ability to meet your goals for managing and controlling endpoints.
    3. Define high-level goals you wish to achieve in the first year and in the longer term.
    4. Identify the use cases that will support your overall goals.
    5. Document use cases in the UEM Requirements Workbook.

    Input

    • List of challenges and goals

    Output

    • Use cases to be used for determining requirements

    Materials

    • Whiteboard/flip charts
    • Laptop to record output

    Participants

    • CIO
    • IT manager
    • Infrastructure & Applications directors

    Download the UEM Requirements Workbook

    Phase 2

    Discover the endpoint management market space and select the right vendor

    Phase 1

    Phase 2

    Define endpoint management platforms

    Explore endpoint management trends

    Classify table stakes & differentiating capabilities

    Streamline the requirements elicitation process for a new endpoint management platform

    Discover key players across the vendor landscape

    Engage the shortlist and select finalist

    Prepare for implementation

    This phase will walk you through the following activity:
    Define top-level features for meeting business and technical goals
    This phase involves the following participants:

    • CIO
    • IT manager
    • Infrastructure & Applications directors
    • Project managers

    Elicit and prioritize granular requirements for your endpoint management platform

    Understanding business needs through requirements gathering is the key to defining everything about what is
    being purchased. However, it is an area where people often make critical mistakes.

    Risks of poorly scoped requirements

    • Fail to be comprehensive and miss certain areas of scope.
    • Focus on how the solution should work instead of what it must accomplish.
    • Have multiple levels of confusing and inconsistent detail in the requirements.
    • Drill down all the way to system-level detail.
    • Add unnecessary constraints based on what is done today rather than focusing on what is needed for tomorrow.
    • Omit constraints or preferences that buyers think are "obvious."

    Best practices

    • Get a clear understanding of what the system needs to do and what it is expected to produce.
    • Test against the principle of MECE – requirements should be "mutually exclusive and collectively exhaustive."
    • Explicitly state the obvious and assume nothing.
    • Investigate what is sold on the market and how it is sold. Use language that is consistent with that of the market and focus on key differentiators – not table stakes.
    • Contain the appropriate level of detail – the level should be suitable for procurement and sufficient for differentiating vendors.

    Review Info-Tech's blueprint Improve Requirements Gathering to improve your requirements gathering process.

    Consider the perspective of each stakeholder to ensure functionality needs are met

    Best of breed vs. "good enough" is an important discussion and will feed your success

    Costs can be high when customizing an ill-fitting module or creating workarounds to solve business problems, including loss of functionality, productivity, and credibility.

    • Start with use cases to drive the initial discussion, then determine which features are mandatory and which are nice-to-haves. Mandatory features will help determine high success for critical functionality and identify where "good enough" is an acceptable state.
    • Consider the implications of implementation and all use cases of:
      • Buying an all-in-one solution.
      • Integration of multiple best-of-breed solutions.
      • Customizing features that were not built into a solution.
    • Be prepared to shelve a use case for this solution and look to alternatives for integration where mandatory features cannot meet highly specialized needs that are outside of traditional endpoint management solutions.

    Pros and Cons

    An image showing the pros and cons of building vs buying

    Evaluate software category leaders through vendor rankings and awards

    SoftwareReviews
    A screenshot of softwareReviews Data Quadrant analyis.. A screenshot of softwareReviews Emotonal Fotprint analyis
    • evaluation and ranking of all software in an individual category to compare platforms across multiple dimensions.
    • Vendors are ranked by their Composite Score, based on individual feature evaluations, user satisfaction rankings, vendor capability comparisons, and likeliness to recommend the platform.
    • The Emotional Footprint is a powerful indicator of overall user sentiment toward the relationship with the vendor, capturing data across five dimensions.
    • Vendors are ranked by their Customer Experience (CX) Score, which combines the overall Emotional Footprint rating with a measure of the value delivered by the solution.

    Speak with category experts to dive deeper into the vendor landscape

    SoftwareReviews

    • Fact-based reviews of business software from IT professionals.
    • Product and category reports with state-of-the-art data visualization.
    • Top-tier data quality backed by a rigorous quality assurance process.
    • User-experience insight that reveals the intangibles of working with a vendor.

    CLICK HERE to ACCESS

    Comprehensive software reviews
    to make better IT decisions

    We collect and analyze the most detailed reviews on enterprise software from real users to give you an unprecedented view into the product and vendor before you buy.

    SoftwareReviews is powered by Info-Tech

    Technology coverage is a priority for Info-Tech, and SoftwareReviews provides the most comprehensive unbiased data on today's technology.
    With the insight of our expert analysts, our members receive unparalleled support in their buying journey.

    Get to Know the Key Players in the Endpoint Management Landscape

    The following slides provide a top-level overview of the popular players you will encounter in the endpoint management shortlisting process in alphabetical order.

    A screenshot showing a series of logos for the companies addressed later in this blueprint. It includes: Ciso; Meraki; Citrix; IBM MaaS360; Ivanti; Jamf|Pro; ManageEngine Endpoint Central; Microsoft Endpoint Manager, and VMWARE.

    Vendor scores are driven by real-world practitioner reviews via SoftwareReviews. Composite, CX, EF, and NPS scores are pulled from live data as of January 2023.

    Secure business units and enhance connection by simplifying the digital workplace

    A good option for enterprises that want a single-pane-of-glass UEM that is easy to use, with a modern-looking dashboard, high threat-management capability, and high-quality customer support.

    CISCO Meraki

    Est. 1984 | CA, USA | NASDAQ: CSCO

    8.8

    9.1

    +92

    91%

    COMPOSITE SCORE

    CX SCORE

    EMOTIONAL FOOTPRINT

    LIKELINESS TO RECOMMEND

    DOWNLOAD REPORT

    This is a Screenshot of CISCO Meraki's dashboard.

    Screenshot of CISCO Meraki's dashboard. Source: Cisco

    Strengths:

    Areas to improve:

    • Cisco Meraki offers granular control over what users can and cannot use.
    • The system is user friendly and intuitive, with a variety of features.
    • The anti-malware capability enhances security.
    • Users are very satisfied with being able to control everything in a single platform.
    • System configuration is easy.
    • Vendor relationship is very high with a rate of 96%.
    • System setup is easy, and users don't need much experience for initial configuration of devices.
    • Users are also mostly satisfied with the platform design.
    • Monitoring within the tool is easy.
    • According to SoftwareReviews' survey report, the primary reason for leaving Cisco Meraki and switching over to another vendor is functionality.
    • Regardless of the top-notch offerings and high-quality features, the product is relatively expensive. The quality and price factors make the solution a better fit for large enterprises. However, SoftwareReviews' scorecard for Cisco Meraki shows that small organizations are the most satisfied compared to the medium and large enterprises, with a net promoter score of 81%.

    Transform work experience and support every endpoint with a unified view to ensure users are productive

    A tool that enables you to access corporate resources on personal devices. It is adaptable to your budget. SoftwareReviews reports that 75% of organizations have received a discount at initial purchase or renewal, which makes it a good candidate if looking for a negotiable option.

    Citrix Endpoint Management

    Est. 1989 | TX, USA | Private

    7.9

    8.0

    8.0

    83%

    COMPOSITE SCORE

    CX SCORE

    EMOTIONAL FOOTPRINT

    LIKELINESS TO RECOMMEND

    DOWNLOAD REPORT

    Screenshot of Citrix Endpoint Management's dashboard.

    Screenshot of Citrix Endpoint Management's dashboard. Source: Citrix

    Strengths:

    Areas to improve:

    • Citrix Endpoint Management is a cloud-centric, easy-to-use UEM with an upgradable interface.
    • The solution simplifies endpoint management and provides real-time visibility and notifications.
    • Citrix allows deployments on different operating systems to meet organizations' infrastructure requirements.
    • The vendor offers different licenses and pricing models, allowing businesses of different sizes to use the tool based on their budgets and requirements.
    • Some users believe that integration with external applications should be improved.
    • Deployment is not very intuitive, making implementation process challenging.
    • User may experience some lagging while opening applications on Citrix. Application is even a bit slower when using a mobile device.

    Scale remote users, enable BYOD, and drive a zero-trust strategy with IBM's modern UEM solution

    A perfect option to boost cybersecurity. Remote administration and installation are made very easy and intuitive on the platform. It is very user friendly, making implementation straightforward. It comes with four licensing options: Essential, Deluxe, Premier, and Enterprise. Check IBM's website for information on pricing and offerings.

    IBM MaaS360

    Est. 1911 | NY, USA | NYSE: IBM

    7.7

    8.4

    +86

    76%

    COMPOSITE SCORE

    CX SCORE

    EMOTIONAL FOOTPRINT

    LIKELINESS TO RECOMMEND

    DOWNLOAD REPORT

    Screenshot of IBM MaaS360's dashboard.

    Screenshot of IBM MaaS360's dashboard. Source: IBM

    Strengths:

    Areas to improve:

    • IBM MaaS360 is easy to install and implement.
    • It has different pricing models to fit enterprises' needs.
    • MaaS360 is compatible with different operating systems.
    • Security management is one of the strongest features, making the tool perfect for organizations that want to improve cybersecurity.
    • Vendor support is very effective, and users find knowledge articles very helpful.
    • It has a very intuitive dashboard.
    • The tool can control organizational data, allowing you to apply BYOD policy.
    • AI Advisor with Watson provides AI-driven reporting and insights.
    • Working with iOS may not be as intuitive as other operating systems.
    • Adding or removing users in a user group is not very straightforward.
    • Some capabilities are limited to particular Android or iOS devices.
    • Deploying application packages may be a bit difficult.
    • Hardware deployment may need some manual work and is not fully automated.

    Get complete device visibility from asset discovery to lifecycle management and remediation

    A powerful tool for patch management with a great user interface. You can automate patching and improve cybersecurity, while having complete visibility into devices. According to SoftwareReviews, 100% of survey participants plan to renew their contract with Ivanti.

    Ivanti Neurons

    Est. 1985 | CA, USA | Private

    8.0

    8.0

    +81

    83%

    COMPOSITE SCORE

    CX SCORE

    EMOTIONAL FOOTPRINT

    LIKELINESS TO RECOMMEND

    DOWNLOAD REPORT

    Screenshot of Ivanti Neurons UEM's dashboard.

    Screenshot of Ivanti Neurons UEM's dashboard. Source: Ivanti

    Strengths:

    Areas to improve:

    • The tool is intuitive and user friendly.
    • It's a powerful security management platform, supporting multiple operating systems.
    • Ivanti Neurons is very strong in patch management and inventory management. It helps a seamless application deployment.
    • Users can install their applications via Ivanti's portal.
    • The user interface is very powerful and easy to use.
    • AI-augmented process management automates protocols, streamlining device management and application updates.
    • Vendor is very efficient in training and provides free webinars.
    • Data integration is very easy. According to SoftwareReviews, it had a satisfaction score for ease of data integration of 86%, which makes Ivanti the top solution for this capability.
    • Data analytics is powerful but complicated.
    • Setup is easy for some teams but not as easy for others, which may cause delays for implementation.
    • Software monitoring is not as good as other competitors.

    Improve your end-user productivity and transform enterprise Apple devices

    An Apple-focused UEM with a great interface. Jamf can manage and control macOS and iOS, and it is one of the best options for Apple products, according to users' sentiments. However, it may not be a one-stop solution if you want to manage non-Apple products as well. In this case, you can use Jamf in addition to another UEM. Jamf has some integrations with Microsoft, but it may not be sufficient if you want to fully manage Windows endpoints.

    Jamf PRO

    Est. 2002 | MN, USA | NASDAQ: JAMF

    8.8

    8.7

    +87

    95%

    COMPOSITE SCORE

    CX SCORE

    EMOTIONAL FOOTPRINT

    LIKELINESS TO RECOMMEND

    DOWNLOAD REPORT

    Screenshot of Jamf PRO's dashboard.

    Screenshot of Jamf PRO's dashboard. Source: Jamf

    Strengths:

    Areas to improve:

    • Jamf Pro is a unique product with an easy implementation that enables IT with minimum admin intervention.
    • It can create smart groups (based on MDM profile and user group) to automatically assign users to their pertinent apps and updates.
    • It's a very user-friendly tool, conducting device management in fewer steps than other competitors.
    • Reports are totally customizable and dynamic.
    • Notifications are easy to navigate and monitor.
    • Self-service feature enables end users to download their predefined categories of applications in the App Store.
    • It can apply single sign-on integrations to streamline user access to applications.
    • Businesses can personalize the tool with corporate logos.
    • Vendor does great for customer service when problems arise.
    • It is a costly tool relative to other competitors, pushing prospects to consider other products.
    • The learning process may be long and not easy, especially if admins do not script, or it's their first time using a UEM.

    Apply automation of traditional desktop management, software deployment, endpoint security, and patch management

    A strong choice for patch management, software deployment, asset management, and security management. There is a free version of the tool available to try get an understanding of the platform before purchasing a higher tier of the product.

    ManageEngine Endpoint Central

    Est. 1996 | India | Private

    8.3

    8.3

    +81

    88%

    COMPOSITE SCORE

    CX SCORE

    EMOTIONAL FOOTPRINT

    LIKELINESS TO RECOMMEND

    DOWNLOAD REPORT

    Screenshot of ME Endpoint Central's dashboard.

    Screenshot of ME Endpoint Central's dashboard. Source: ManageEngine

    Strengths:

    Areas to improve:

    • It supports several operating systems including Windows, Mac, Linux, Android, and iOS.
    • Endpoint Central provides end-to-end monitoring, asset management, and security in a single platform.
    • Setup is simple and intuitive, and it's easy to learn and configure.
    • The reporting feature is very useful and gives you clear visibility into dashboard.
    • Combined with ME Service Desk Plus, we can call Endpoint Central an all-in-one solution.
    • The tool provides a real-time report on devices and tracks their health status.
    • It has multiple integrations with third-party solutions.
    • Tool does not automate updates, making application updates time-consuming.
    • Sometimes, patches and software deployments fail, and the tool doesn't provide any information on the reason for the failure.
    • There is no single point of contact/account manager for the clients when they have trouble with the tool.
    • Remote connection to Android devices can sometimes get a little tedious.

    Get device management and security in a single platform with a combination of Microsoft Intune and Configuration Manager

    A solution that combines Intune and ConfigMgr's capabilities into a single endpoint management suite for enrolling, managing, monitoring, and securing endpoints. It's a very cost-effective solution for enterprises in the Microsoft ecosystem, but it also supports other operating systems.

    Microsoft Endpoint Manager

    Est. 1975 | NM, USA | NASDAQ: MSFT

    8.0

    8.5

    +83

    85%

    COMPOSITE SCORE

    CX SCORE

    EMOTIONAL FOOTPRINT

    LIKELINESS TO RECOMMEND

    DOWNLOAD REPORT

    Screenshot of MS Endpoint Manager's dashboard.

    Screenshot of MS Endpoint Manager's dashboard. Source: Microsoft

    Strengths:

    Areas to improve:

    • Licensing for the enterprises that use Windows as their primary operating system is more efficient and cost effective.
    • Endpoint Manager is very customizable, with the ability to assign personas to device groups.
    • Besides Windows, it manages other operating systems, such as Linux, Android, and iOS.
    • It creates endpoint security and compliance policies for BitLocker that streamlines data protection and security. It also provides SSO.
    • It provides very strong documentation and knowledgebase.
    • User interface is not as good as competitors. It's a bit clunky and complex to use.
    • The process of changing configurations on devices can be time consuming.
    • Sometimes there are service outages such as Autopilot failure, which push IT to deploy manually.
    • Location tracking is not very accurate.

    Simplify and consolidate endpoint management into a single solution and secure all devices with real-time, "over-the-air" modern management across all use cases

    A strong tool for managing and controlling mobile devices. It can access all profiles through Google and Apple, and it integrates with various IT management solutions.

    VMware Workspace ONE

    Est. 1998 | CA, USA | NYSE: VMW

    7.5

    7.4

    +71

    75%

    COMPOSITE SCORE

    CX SCORE

    EMOTIONAL FOOTPRINT

    LIKELINESS TO RECOMMEND

    DOWNLOAD REPORT

    Screenshot of Workspace ONE's dashboard.

    Screenshot of Workspace ONE's dashboard. Source: VMware

    Strengths:

    Areas to improve:

    • Workspace ONE provides lots of information about devices.
    • It provides a large list of integrations.
    • The solution supports various operating systems.
    • The platform has many out-of-the-box features and helps with security management, asset management, and application management.
    • The vendor has a community forum which users find helpful for resolving issues or asking questions about the solution.
    • It is very simple to use and provides SSO capability.
    • Implementation is relatively easy and straightforward.
    • Customization may be tricky and require expertise.
    • The solution can be more user friendly with a better UI.
    • Because of intensive processing, updates to applications take a long time.
    • The tool may sometimes be very sensitive and lock devices.
    • Analytics and reporting may need improvement.

    Review your use cases to start your shortlist

    Your Info-Tech analysts can help you narrow down the list of vendors that will meet your requirements.

    Next steps will include:

    1. Reviewing your requirements
    2. Checking out SoftwareReviews
    3. Shortlisting your vendors
    4. Conducting demos and detailed proposal reviews
    5. Selecting and contracting with a finalist!

    Activity: Define high-level features for meeting business and technical goals

    Input

    • List of endpoint management use cases
    • List of prioritized features

    Output

    • Vendor evaluation
    • Final list of candidate vendors

    Materials

    • Whiteboard/flip charts
    • Laptop
    • UEM Requirements Workbook

    Participants

    • CIO
    • IT manager
    • Infrastructure & Applications directors
    • Project managers

    Activity: Define top-level features for meeting business and technical goals

    As there are many solutions in the market that share capabilities, it is imperative to closely evaluate how well they fulfill your endpoint management requirements.
    Use the UEM Requirements Workbook to identify your desired endpoint solution features and compare vendor solution functionality based on your desired features.

    1. Refer to the output of the previous activity, the identified use cases in the spreadsheet.
    2. List the features you want in an endpoint solution for your devices that will fulfill these use cases. Record those features in the second column ("Detailed Feature").
    3. Prioritize each feature (must have, should have, nice to have, not required).
    4. Send this list to candidate vendors.
    5. When you finish your investigation, review the spreadsheet to compare the various offerings and pros and cons of each solution.

    Info-Tech Insight

    The output of this activity can be used for a detailed evaluation of UEM vendors. The next steps will be vendor briefing and having further discussion on technical capabilities and conducting demos of solutions. Info-Tech's blueprint, The Rapid Application Selection Framework, takes you to these next steps.

    This is a screenshot showing the high value use cases table from The Rapid Application Selection Framework.

    Download the UEM Requirements Workbook

    Leverage Info-Tech's research to plan and execute your endpoint management selection and implementation

    Use Info-Tech Research Group's blueprints for selection and implementation processes to guide your own planning.

    • Assess
    • Prepare
    • Govern & Course Correct

    This is a screenshot of the title pages from INfo-tech's Governance and management of enterprise Software Implementaton; and The Rapid Applicaton Selection Framework.

    Ensure your implementation team has a high degree of trust and communication

    If external partners are needed, dedicate an internal resource to managing the vendor and partner relationships.

    Communication

    Teams must have some type of communication strategy. This can be broken into:

    • Regularity: Having a set time each day to communicate progress and a set day to conduct retrospectives.
    • Ceremonies: Injecting awards and continually emphasizing delivery of value can encourage relationship building and constructive motivation.
    • Escalation: Voicing any concerns and having someone responsible for addressing those concerns.

    Proximity

    Distributed teams create complexity because communication can break down more easily. This can be mitigated by:

    • Location: Placing teams in proximity can close the barrier of geographical distance and time zone differences.
    • Inclusion: Making a deliberate attempt to pull remote team members into discussions and ceremonies.
    • Communication Tools: Having the right technology (e.g. video conference) can help bring teams closer together virtually.

    Trust

    Members should trust other members are contributing to the project and completing their required tasks on time. Trust can be developed and maintained by:

    Accountability: Having frequent quality reviews and feedback sessions. As work becomes more transparent, people become more accountable.

    • Role Clarity: Having a clear definition of what everyone's role is.

    Implementation with a partner typically results in higher satisfaction

    Align your implementation plans with both the complexity of the solution and internal skill levels

    Be clear and realistic in your requirements to the vendor about the level of involvement you need to be successful.

    Primary reasons to use a vendor:

    • Lack of skilled resources: For solutions with little configuration change happening after the initial installation, the ramp-up time for an individual to build skills for a single event is not practical.
    • Complexity of solution: Multiple integrations, configurations, modules, and even acquisitions that haven't been fully integrated in the solution you choose can make it difficult to complete the installation and rollout on time and on budget. Troubleshooting becomes even more complex if multiple vendors are involved.
    • Data migration: Decide what information will be valuable to transfer to the new solution and which will not benefit your organization. Data structure and residency can both be factors in the complexity of this exercise.

    This is an image of a bar graph showing the Satisfaction Net Promotor Score by Implementation type and Organization Size.

    Source: SoftwareReviews, January 2020 to January 2023, N= 20,024 unique reviews

    To ensure your SOW is mutually beneficial, download the blueprint Improve Your Statements of Work to Hold Your Vendors Accountable.

    Consider running a proof of concept if concerns are expressed about the feasibility of the chosen solution

    Proofs of concept (PoCs) can be time consuming, so make good choices on where to spend the effort

    Create a PoC charter that will enable a quick evaluation of the defined use cases and functions. These key dimensions should form the PoC.

    1. Objective – Giving an overview of the planned PoC will help to focus and clarify the rest of this section. What must the PoC achieve? Objectives should be specific, measurable, attainable, relevant, and time bound. Outline and track key performance indicators.
    2. Key Success Factors – These are conditions that will positively impact the PoC's success.
    3. Scope – High-level statement of scope. More specifically, state what is in scope and what is out of scope.
    4. Project Team – Identify the team's structure, e.g. sponsors, subject matter experts.
    5. Resource Estimation – Identify what resources (time, materials, space, tools, expertise, etc.) will be needed to build and socialize your prototype. How will they be secured?

    An image of two screenshots from Info-Tech Research Group showing documentaton used to generate effective proof of concepts.

    To create a full proof of concept plan, download the Proof of Concept Template and see the instructions in Phase 3 of the blueprint Exploit Disruptive Infrastructure Technology.

    Selecting a right-sized endpoint management platform

    This selection guide allows organizations to execute a structured methodology for picking a UEM platform that aligns with their needs. This includes:

    • Identifying and prioritizing key business and technology drivers for an endpoint management selection business case.
    • Defining key use cases and requirements for a right-sized UEM platform.
    • Reviewing a comprehensive market scan of key players in the UEM marketspace.

    This formal UEM selection initiative will map out requirements and identify technology capabilities to fill the gap for better endpoint management. It also allows a formal roll-out of a UEM platform that is highly likely to satisfy all stakeholder needs.

    If you would like additional support, have our analysts guide you through other phases as part of an Info-Tech Workshop.

    Contact your account representative for more information

    workshops@infotech.com
    1-888-670-8889

    Summary of Accomplishment

    Knowledge Gained

    • What endpoint management is
    • Historical origins and evolution of endpoint management platforms
    • Current trends and future state of endpoint management platforms

    Processes Optimized

    • Identifying use cases
    • Gathering requirements
    • Reviewing market key players and their capabilities
    • Selecting a UEM tool that fulfills your requirements

    UEM Solutions Analyzed

    • CISCO Meraki
    • Citrix Endpoint Management
    • IBM MaaS360
    • Ivanti Neurons UEM
    • Jamf Pro
    • ManageEngine Endpoint Central
    • Microsoft Endpoint Manager
    • VMware Workspace ONE

    Related Info-Tech Research

    Modernize and Transform Your End-User Computing Strategy

    This project helps support the workforce of the future by answering the following questions: What types of computing devices, provisioning models, and operating systems should be offered to end users? How will IT support devices? What are the policies and governance surrounding how devices are used? What actions are we taking and when? How do end-user devices support larger corporate priorities and strategies?

    Best Unified Endpoint Management (UEM) Software | SoftwareReviews

    Compare and evaluate Unified Endpoint Management vendors using the most in-depth and unbiased buyer reports available. Download free comprehensive 40+ page reports to select the best Unified Endpoint Management software for your organization.

    The Rapid Application Selection Framework

    This blueprint walks you through a process for a fast and efficient selection of your prospective application. You will be enabled to use a data-driven approach to select the right application vendor for your needs, shatter stakeholder expectations with truly rapid application selections, boost collaboration and crush the broken telephone with concise and effective stakeholder meetings, and lock in hard savings.

    Bibliography

    "BYOD Security Report." Cybersecurity Insiders, 2021. Accessed January 2023.
    "Cloud Infrastructure Services Market." MarketsAnd Markets, 2019. Accessed December 2022.
    Evans, Alma. "Mastering Mobility Management: MDM Vs. EMM Vs. UEM." Hexnode, 2019. Accessed November 2022.
    "Evercore-ISI Quarterly Enterprise Technology Spending Survey." Evercore-ISI, 2022. Accessed January 2023.
    "5G Service Revenue to Reach $315 Billion Globally in 2023." Jupiter Research, 2022. Accessed January 2023.
    Hein, Daniel. "5 Common Unified Endpoint Management Use Cases You Need to Know." Solutions Review, 2020. Accessed January 2023.
    "Mobile Device Management Market Size, Share & COVID-19 Impact Analysis." Fortune Business Insights, 2021. Accessed December 2022.
    Ot, Anina. "The Unified Endpoint Management (UEM) Market." Datamation, 14 Apr. 2022. Accessed Jan. 2023.
    Poje, Phil. "CEO Corner: 4 Trends in Unified Endpoint Management for 2023." Tech Orchard, 2022. Accessed January 2023.
    "The Future of UEM November 2021 Webinar." Ivanti, 2021. Accessed January 2023.
    "The Third Annual Study on the State of Endpoint Security Risk." Ponemon Institute, 2020. Accessed December 2022.
    "The Ultimate Guide to Unified Endpoint Management (UEM)." MobileIron. Accessed January 2023.
    "Trends in Unified Endpoint Management." It Pro Today, 2018. Accessed January 2023.
    Turek, Melanie. "Employees Say Smartphones Boost Productivity by 34 Percent: Frost & Sullivan Research." Samsung Insights, 3 Aug. 2016.
    "2023 State of Security Report." Cybersecurity Insiders, 2022. Accessed January 2023.
    Violino, Bob. "Enterprise Mobility 2022: UEM Adds User Experience, AI, Automation." Computerworld, 2022. Accessed January 2023.
    Violino, Bob. "How to Choose the Right UEM Platform." Computerworld, 2021. Accessed January 2023.
    Violino, Bob. "UEM Vendor Comparison Chart 2022." Computerworld, 2022. Accessed January 2023.
    Wallent, Michael. "5 Endpoint Management Predictions for 2023." Microsoft, 2022. Accessed January 2023.
    "What Is the Difference Between MDM, EMM, and UEM?" 42Gears, 2017. Accessed November 2022.

    Integrate Threat Intelligence Into Your Security Operations

    • Buy Link or Shortcode: {j2store}320|cart{/j2store}
    • member rating overall impact: 9.0/10 Overall Impact
    • member rating average dollars saved: 2 Average Days Saved
    • member rating average days saved: After each Info-Tech experience, we ask our members to quantify the real-time savings, monetary impact, and project improvements our research helped them achieve.
    • Parent Category Name: Threat Intelligence & Incident Response
    • Parent Category Link: /threat-intelligence-incident-response
    • Organizations have limited visibility into their threat landscape, and as such are vulnerable to the latest attacks, hindering business practices, workflow, revenue generation, and damaging their public image.
    • Organizations are developing ad hoc intelligence capabilities that result in operational inefficiencies, the misalignment of resources, and the misuse of their security technology investments.
    • It is difficult to communicate the value of a threat intelligence solution when trying to secure organizational buy-in and the appropriate resourcing.
    • There is a vast array of “intelligence” in varying formats, often resulting in information overload.

    Our Advice

    Critical Insight

    1. Information alone is not actionable. A successful threat intelligence program contextualizes threat data, aligns intelligence with business objectives, and then builds processes to satisfy those objectives.
    2. Your security controls are diminishing in value (if they haven’t already). As technology in the industry evolves, threat actors will inevitably adopt new tools, tactics, and procedures; a threat intelligence program can provide relevant situational awareness to stay on top of the rapidly-evolving threat landscape.
    3. Your organization might not be the final target, but it could be a primary path for attackers. If you exist as a third-party partner to another organization, your responsibility in your technology ecosystem extends beyond your own product/service offerings. Threat intelligence provides visibility into the latest threats, which can help you avoid becoming a backdoor in the next big data breach.

    Impact and Result

    • Assess the needs and intelligence requirements of key stakeholders.
    • Garner organizational buy-in from senior management.
    • Identify organizational intelligence gaps and structure your efforts accordingly.
    • Understand the different collection solutions to identify which best supports your needs.
    • Optimize the analysis process by leveraging automation and industry best practices.
    • Establish a comprehensive threat knowledge portal.
    • Define critical threat escalation protocol.
    • Produce and share actionable intelligence with your constituency.
    • Create a deployment strategy to roll out the threat intelligence program.
    • Integrate threat intelligence within your security operations.

    Integrate Threat Intelligence Into Your Security Operations Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should implement a threat intelligence program, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Plan for a threat intelligence program

    Assess current capabilities and define an ideal target state.

    • Integrate Threat Intelligence Into Your Security Operations – Phase 1: Plan for a Threat Intelligence Program
    • Security Pressure Posture Analysis Tool
    • Threat Intelligence Maturity Assessment Tool
    • Threat Intelligence Project Charter Template
    • Threat Intelligence RACI Tool
    • Threat Intelligence Management Plan Template
    • Threat Intelligence Policy Template

    2. Design an intelligence collection strategy

    Understand the different collection solutions to identify which best supports needs.

    • Integrate Threat Intelligence Into Your Security Operations – Phase 2: Design an Intelligence Collection Strategy
    • Threat Intelligence Prioritization Tool
    • Threat Intelligence RFP MSSP Template

    3. Optimize the intelligence analysis process

    Begin analyzing and acting on gathered intelligence.

    • Integrate Threat Intelligence Into Your Security Operations – Phase 3: Optimize the Intelligence Analysis Process
    • Threat Intelligence Malware Runbook Template

    4. Design a collaboration and feedback program

    Stand up an intelligence dissemination program.

    • Integrate Threat Intelligence Into Your Security Operations – Phase 4: Design a Collaboration and Feedback Program
    • Threat Intelligence Alert Template
    • Threat Intelligence Alert and Briefing Cadence Schedule Template
    [infographic]

    Enable Organization-Wide Collaboration by Scaling Agile

    • Buy Link or Shortcode: {j2store}174|cart{/j2store}
    • member rating overall impact: 8.3/10 Overall Impact
    • member rating average dollars saved: $12,989 Average $ Saved
    • member rating average days saved: 10 Average Days Saved
    • Parent Category Name: Architecture & Strategy
    • Parent Category Link: /architecture-and-strategy
    • Your organization is realizing benefits from adopting Agile principles and practices in pockets of your organization.
    • You are starting to investigate opportunities to extend Agile beyond these pilot implementations into other areas of the organization. You are looking for a coordinated approach aligned to business priorities.

    Our Advice

    Critical Insight

    • Not all lessons from a pilot project are transferable. Pilot processes are tailored to a specific project’s scope, team, and tools, and they may not account for the diverse attributes in your organization.
    • Control may be necessary for coordination. More moving parts means enforcing consistent cadences, reporting, and communication is a must if teams are not disciplined or lack good governance.
    • Scale Agile in departments tolerable to change. Incrementally roll Agile out in departments where its principles are accepted (e.g. a culture of continuous improvement, embracing failures as lessons).

    Impact and Result

    • Complete an Agile capability assessment of your pilot functional group to gauge anticipated Agile benefits. Identify the business objectives and the group drivers that are motivating a scaled Agile implementation.
    • Understand the challenges that you may face when scaling Agile. Investigate the root causes of inefficiencies that can derail your scaling initiatives.
    • Brainstorm solutions to your scaling challenges and envision a target state for your growing Agile environment. Your target state will discover new opportunities to drive more business value and eliminate current activities driving down productivity.
    • Coordinate the implementation and execution of scaling Agile initiatives with a Scaling Agile Playbook. This organic and collaborative document will lay out the process, roles, goals, and objectives needed to successfully manage your Agile environment.

    Enable Organization-Wide Collaboration by Scaling Agile Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should scale up Agile, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Gauge readiness to scale up Agile

    Evaluate the readiness of the pilot functional group and Agile development processes to adopt scaled Agile practices.

    • Enable Organization-Wide Collaboration by Scaling Agile – Phase 1: Gauge Readiness to Scale Up Agile
    • Scaling Agile Playbook Template
    • Scrum Development Process Template

    2. Define scaled Agile target state

    Alleviate scaling issues and risks and introduce new opportunities to enhance business value delivery with Agile practices.

    • Enable Organization-Wide Collaboration by Scaling Agile – Phase 2: Define Scaled Agile Target State

    3. Create implementation plan

    Roll out scaling Agile initiatives in a gradual, iterative approach and define the right metrics to demonstrate success.

    • Enable Organization-Wide Collaboration by Scaling Agile – Phase 3: Create Implementation Plan
    [infographic]

    Workshop: Enable Organization-Wide Collaboration by Scaling Agile

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Gauge Your Readiness to Scale Up Agile

    The Purpose

    Identify the business objectives and functional group drivers for adopting Agile practices to gauge the fit of scaling Agile.

    Select the pilot project to demonstrate the value of scaling Agile.

    Review and evaluate your current Agile development process and functional group structure.

    Key Benefits Achieved

    Understanding of the notable business and functional group gaps that can derail the scaling of Agile.

    Selection of a pilot program that will be used to gather metrics to continuously improve implementation and obtain buy-in for wider rollout.

    Realization of the root causes behind functional group and process issues in the current Agile implementation.

    Activities

    1.1 Assess your pilot functional group

    Outputs

    Fit assessment of functional group to pilot Agile scaling

    Selection of pilot program

    List of critical success factors

    2 Define Your Scaled Agile Target State

    The Purpose

    Think of solutions to address the root causes of current communication and process issues that can derail scaling initiatives.

    Brainstorm opportunities to enhance the delivery of business value to customers.

    Generate a target state for your scaled Agile implementation.

    Key Benefits Achieved

    Defined Agile capabilities and services of your functional group.

    Optimized functional group team structure, development process, and program framework to support scaled Agile in your context.

    Identification and accommodation of the risks associated with implementing and executing Agile capabilities.

    Activities

    2.1 Define Agile capabilities at scale

    2.2 Build your scaled Agile target state

    Outputs

    Solutions to scaling issues and opportunities to deliver more business value

    Agile capability map

    Functional group team structure, Agile development process and program framework optimized to support scaled Agile

    Risk assessment of scaling Agile initiatives

    3 Create Your Implementation Plan

    The Purpose

    List metrics to gauge the success of your scaling Agile implementation.

    Define the initiatives to scale Agile in your organization and to prepare for a wider rollout.

    Key Benefits Achieved

    Strategic selection of the right metrics to demonstrate the value of scaling Agile initiatives.

    Scaling Agile implementation roadmap based on current resource capacities, task complexities, and business priorities.

    Activities

    3.1 Create your implementation plan

    Outputs

    List of metrics to gauge scaling Agile success

    Scaling Agile implementation roadmap

    Jump Start Your Vendor Management Initiative

    • Buy Link or Shortcode: {j2store}211|cart{/j2store}
    • member rating overall impact: 9.4/10 Overall Impact
    • member rating average dollars saved: $137,332 Average $ Saved
    • member rating average days saved: 31 Average Days Saved
    • Parent Category Name: Vendor Management
    • Parent Category Link: /vendor-management
    • Each year, IT organizations spend more money “outsourcing” tasks, activities, applications, functions, and other items.
    • The increased spend and associated outsourcing leads to less control, and more risk for IT organizations. Managing this becomes a higher priority for IT, but many IT organizations are ill-equipped to do this proactively.

    Our Advice

    Critical Insight

    • Vendor management is not “plug and play” – each organization’s vendor management initiative (VMI) needs to fit its culture, environment, and goals. There are commonalites among vendor management initiatives, but the key is to adapt vendor management principles to fit your needs, not the other way around.
    • All vendors are not of equal importance to an organization. Internal resources are a scarce commodity and should be deployed so that they provide the best return on the organization’s investment. Classifying or segmenting your vendors allows you to focus your efforts on the most important vendors first, allowing your VMI to have the greatest impact possible.
    • Having a solid foundation is critical to the VMI’s ongoing success. Whether you will be creating a formal vendor management office or using vendor management techniques, tools, and templates “informally,” starting with the basics is essential. Make sure you understand why the VMI exists and what it hopes to achieve, what is in and out of scope for the VMI, what strengths the VMI can leverage and the obstacles it will have to address, and how it will work with other areas within your organization.

    Impact and Result

    • Build and implement a vendor management initiative tailored to your environment.
    • Create a solid foundation to sustain your vendor management initiative as it evolves and matures.
    • Leverage vendor management-specific tools and templates to manage vendors more proactively and improve communication.
    • Concentrate your vendor management resources on the right vendors.
    • Build a roadmap and project plan for your vendor management journey to ensure you reach your destination.
    • Build collaborative relationships with critical vendors.

    Jump Start Your Vendor Management Initiative Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should jump start a vendor management initiative, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Plan

    Organize your VMI and document internal processes, relationships, roles, and responsibilities. The main outcomes from this phase are organizational documents, a baseline VMI maturity level, and a desired future state for the VMI.

    • Jump Start Your Vendor Management Initiative – Phase 1: Plan
    • Jump – Phase 1 Tools and Templates Compendium

    2. Build

    Configure and create the tools and templates that will help you run the VMI. The main outcomes from this phase are a clear understanding of which vendors are important to you, the tools to manage the vendor relationships, and an implementation plan.

    • Jump Start Your Vendor Management Initiative – Phase 2: Build
    • Jump – Phase 2 Tools and Templates Compendium
    • Jump – Phase 2 Vendor Classification Tool
    • Jump – Phase 2 Vendor Risk Assessment Tool

    3. Run

    Begin operating the VMI. The main outcomes from this phase are guidance and the steps required to implement your VMI.

    • Jump Start Your Vendor Management Initiative – Phase 3: Run

    4. Review

    Identify what the VMI should stop doing, start doing, and continue doing as it improves and matures. The main outcomes from this phase are ways to advance the VMI and maintain internal alignment.

    • Jump Start Your Vendor Management Initiative – Phase 4: Review

    Infographic

    Workshop: Jump Start Your Vendor Management Initiative

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Plan

    The Purpose

    Getting Organized

    Key Benefits Achieved

    Defined Roles and Goals for the VMI

    Activities

    1.1 Mission Statement and Goals

    1.2 Scope

    1.3 Strengths and Obstacles

    1.4 Roles and Responsibilities – OIC Chart

    1.5 Process Mapping

    1.6 Vendor Inventory Tool (Overview)

    Outputs

    Completed Mission Statement and Goals

    List of Items In Scope and Out of Scope for the VMI

    List of Strengths and Obstacles for the VMI

    Completed OIC Chart

    Sample Process Map for One Process

    Begun Using Vendor Inventory Tool

    2 Plan/Build/Run

    The Purpose

    Build VMI Tools and Templates

    Key Benefits Achieved

    Configured Tools and Templates for the VMI Based on Its Roles and Goals

    Activities

    2.1 Maturity Assessment

    2.2 Structure and Job Descriptions

    2.3 Attributes of a Valuable Vendor

    2.4 Classification Model

    2.5 Risk Assessment Tool

    2.6 Scorecards and Feedback

    2.7 Business Alignment Meeting Agenda

    Outputs

    Completed Maturity Assessment.

    Sample Job Descriptions and Phrases.

    List of Attributes of a Valuable Vendor.

    Configured Classification Model.

    Configured Risk Assessment Tool.

    Configured Scorecard and Feedback Questions.

    Configured Business Alignment Meeting Agenda.

    3 Build/Run

    The Purpose

    Continue Building VMI Tools and Templates

    Key Benefits Achieved

    Configured Tools and Templates for the VMI Based on Its Roles and Goals

    Activities

    3.1 Relationship Alignment Document

    3.2 Vendor Orientation

    3.3 Policies and Procedures

    3.4 3-Year Roadmap

    3.5 90-Day Plan

    3.6 Quick Wins

    3.7 Reports

    3.8 Kickoff Meeting

    Outputs

    Relationship Alignment Document Sample and Checklist

    Vendor Orientation Checklist

    Policies and Procedures Checklist

    Completed 3-Year Roadmap

    Completed 90-Day Plan

    List of Quick Wins

    List of Reports

    4 Review

    The Purpose

    Review the Past 12 Months of VMI Operations and Improve

    Key Benefits Achieved

    Keeping the VMI Aligned With the Organization’s Goals and Ensuring the VMI Is Leveraging Leading Practices

    Activities

    4.1 Develop/Improve Vendor Relationships.

    4.2 Assess Compliance.

    4.3 Incorporate Leading Practices.

    4.4 Leverage Lessons Learned.

    4.5 Maintain Internal Alignment.

    4.6 Update Governances.

    Outputs

    Further reading

    Jump Start Your Vendor Management Initiative

    Create and implement a vendor management framework to begin obtaining measurable results in 90 days.

    EXECUTIVE BRIEF

    Analyst Perspective

    What is vendor management?

    When you read the phrase “vendor management,” what comes to mind? This isn’t a rhetorical question. Take your time … I’ll wait.

    Unfortunately, those words conjure up a lot of different meanings, and much of that depends on whom you ask. Those who work in the vendor management field will provide a variety of answers. To complicate matters, those who are vendor management “outsiders” will have a totally different view of what vendor management is. Why is this important? Because we need a common definition to communicate more effectively, even if the definition is broad.

    Let’s start creating a working definition that is not circular. Vendor management is not simply managing vendors. That expression basically reorders the words and does nothing to advance our cause; it only adds to the existing confusion surrounding the concept.

    Vendor management is best thought of as a spectrum or continuum with many points rather than a specific discipline like accounting or finance. There are many functions and activities that fall under the umbrella term of vendor management: some of them will be part of your vendor management initiative (VMI), some will not, and some will exist in your organization but be outside the VMI. This is the unique part of vendor management – the part that makes it fun, but also the part that leads to the confusion. For example, accounts payable sits within the accounting department almost exclusively, but contract management can sit within or outside the VMI. The beauty of vendor management is its flexibility; your VMI can be created to meet your specific needs and goals while leveraging common vendor management principles.

    Every conversation around vendor management needs to begin with “What do you mean by that?” Only then can we home in on the scope and nature of what people are discussing. “Managing vendors” is too narrow because it often ignores many of the reasons organizations create VMIs in the first place: to reduce costs, to improve performance, to improve processes, to improve relationships, to improve communication, and to manage risk better.

    Vendor management is a strategic initiative that takes the big picture into account … navigating the cradle to grave lifecycle to get the most out of your interactions and relationships with your vendors. It is flexible and customizable; it is not plug and play or overly prescriptive. Tools, principles, templates, and concepts are adapted rather than adopted as is. Ultimately, you define what vendor management is for your organization.

    We look forward to helping you on your vendor management journey no matter what it looks like. But first, let’s have a conversation about how you want to define vendor management in your environment.

    This is a picture of Phil Bode, Principal  Research Director, Vendor Management at Info-Tech Research Group.

    Phil Bode
    Principal Research Director, Vendor Management
    Info-Tech Research Group

    Executive Summary

    Your Challenge

    Each year, IT organizations “outsource” tasks, activities, functions, and other items. During 2021:

    • Spend on as-a-service providers increased 38% over 2020.*
    • Spend on managed service providers increased 16% over 2020.*
    • IT service providers increased their merger and acquisition numbers by 47% over 2020.*

    *Source: Information Services Group, Inc., 2022.

    This leads to more spend, less control, and more risk for IT organizations. Managing this becomes a higher priority for IT, but many IT organizations are ill-equipped to do this proactively.

    Common Obstacles

    As new contracts are negotiated and existing contracts are renegotiated or renewed, there is a perception that the contracts will yield certain results, output, performance, solutions, or outcomes. The hope is that these will provide a measurable expected value to IT and the organization. Oftentimes, much of the expected value is never realized. Many organizations don’t have a VMI to help:

    • Ensure at least the expected value is achieved.
    • Improve on the expected value through performance management.
    • Significantly increase the expected value through a proactive VMI.

    Info-Tech’s Approach

    Vendor management is a proactive, cross-functional lifecycle. It can be broken down into four phases:

    • Plan
    • Build
    • Run
    • Review

    The Info-Tech process addresses all four phases and provides a step-by-step approach to configure and operate your VMI. The content in this blueprint helps you quickly establish your VMI and set a solid foundation for its growth and maturity.

    Info-Tech Insight

    Vendor management is not a one-size-fits-all initiative. It must be configured:

    • For your environment, culture, and goals.
    • To leverage the strengths of your organization and personnel.
    • To focus your energy and resources on your critical vendors.

    Executive Summary

    Your Challenge

    Spend on managed service providers and as-a-service providers continues to increase. In addition, IT services vendors continue to be active in the mergers and acquisitions arena. This increases the need for a VMI to help with the changing IT vendor landscape. In 2021, there was increases of:

    38%

    Spend on As-a-Service Providers

    16%

    Spend on Managed Services Providers

    47%

    IT Services Merger & Acquisition Growth (Transactions)

    Source: Information Services Group, Inc., 2022.

    Executive Summary

    Common Obstacles

    When organizations execute, renew, or renegotiate a contract, there is an “expected value” associated with that contract. Without a robust VMI, most of the expected value will never be realized. With a robust VMI, the realized value significantly exceeds the expected value during the contract term.

    A contract’s realized value with and without a vendor management initiative

    Two bars are depicted, showing that vendor collaboration and vendor performance management exceed expected value with a VMI, but without VMI, 75% of a contract's expected value can disappear within 18 months.

    Source: Based on findings from Geller & Company, 2003.

    Executive Summary

    Info-Tech’s Approach

    A sound, cyclical approach to vendor management will help you create a VMI that meets your needs and stays in alignment with your organization as they both change (i.e. mature and grow).

    This is an image of Info-Tech's approach to VMI.  It includes the following four steps: 01 - Plan; 02 - Build; 03 - Run; 04 - Review

    Info-Tech’s Methodology for Creating and Operating Your VMI

    Phase 1: Plan Phase 2: Build Phase 3: Run Phase 4: Review

    Phase Steps

    1.1 Mission Statement and Goals
    1.2 Scope
    1.3 Strengths and Obstacles
    1.4 Roles and Responsibilities
    1.5 Process Mapping
    1.6 Charter
    1.7 Vendor Inventory
    1.8 Maturity Assessment
    1.9 Structure

    2.1 Classification Model
    2.2 Risk Assessment Tool
    2.3 Scorecards and Feedback
    2.4 Business Alignment Meeting Agenda
    2.5 Relationship Alignment Document
    2.6 Vendor Orientation
    2.7 Job Descriptions
    2.8 Policies and Procedures
    2.9 3-Year Roadmap
    2.10 90-Day Plan
    2.11 Quick Wins
    2.12 Reports

    3.1 Classify Vendors
    3.2 Conduct Internal “Kickoff” Meeting
    3.3 Conduct Vendor Orientation
    3.4 Compile Scorecards
    3.5 Conduct Business Alignment Meetings
    3.6 Work the 90-Day Plan
    3.7 Manage the 3-Year Roadmap
    3.8 Measure and Monitor Risk
    3.9 Issue Reports
    3.10 Develop/Improve Vendor Relationships
    3.11 Contribute to Other Processes

    4.1 Assess Compliance
    4.2 Incorporate Leading Practices
    4.3 Leverage Lessons Learned
    4.4 Maintain Internal Alignment
    4.5 Update Governances

    Phase Outcomes

    This phase helps you organize your VMI and document internal processes, relationships, roles, and responsibilities. The main outcomes from this phase are organizational documents, a baseline VMI maturity level, and a desired future state for the VMI. This phase helps you configure and create the tools and templates that will help you run the VMI. The main outcomes from this phase are a clear understanding of which vendors are important to you, the tools to manage the vendor relationships, and an implementation plan. This phase helps you begin operating the VMI. The main outcomes from this phase are guidance and the steps required to implement your VMI. This phase helps the VMI identify what it should stop doing, start doing, and continue doing as it improves and matures. The main outcomes from this phase are ways to advance the VMI and maintain internal alignment.

    Insight Summary

    Insight 1

    Vendor management is not “plug and play” – each organization’s vendor management initiative (VMI) needs to fit its culture, environment, and goals. While there are commonalities and leading practices associated with vendor management, your initiative won’t look exactly like another organization’s. The key is to adapt vendor management principles to fit your needs.

    Insight 2

    All vendors are not of equal importance to your organization. Internal resources are a scarce commodity and should be deployed so that they provide the best return on the organization’s investment. Classifying or segmenting your vendors allows you to focus your efforts on the most important vendors first, allowing your VMI to have the greatest impact possible.

    Insight 3

    Having a solid foundation is critical to the VMI’s ongoing success. Whether you will be creating a formal vendor management office or using vendor management techniques, tools, and templates “informally,” starting with the basics is essential. Make sure you understand why the VMI exists and what it hopes to achieve, what is in and out of scope for the VMI, what strengths the VMI can leverage and the obstacles it will have to address, and how it will work with other areas within your organization.

    Blueprint Deliverables

    The four phases of creating and running a vendor management initiative are supported with configurable tools, templates, and checklists to help you stay aligned internally and achieve your goals.

    VMI Tools and Templates

    This image contains two screenshots of Info-Tech's VMI Tools and Templates

    Build a solid foundation for your VMI and configure tools and templates to help you manage your vendor relationships.

    Key Deliverables:

    1. Jump – Phase 1 Tools and Templates Compendium
    2. Jump – Phase 2 Tools and Templates Compendium
    3. Jump – Phase 2 Vendor Classification Tool
    4. Jump – Phase 2 Vendor Risk Assessment Tool

    A suite of tools and templates to help you create and implement your vendor management initiative.

    Blueprint benefits

    IT Benefits

    • Identify and manage risk proactively.
    • Reduce costs and maximize value.
    • Increase visibility with your critical vendors.
    • Improve vendor performance.
    • Create a collaborative environment with key vendors.
    • Segment vendors to allocate resources more effectively and more efficiently.

    Business Benefits

    • Improve vendor accountability.
    • Increase collaboration between departments.
    • Improve working relationships with your vendors.
    • Create a feedback loop to address vendor or customer issues before they get out of hand or are more costly to resolve.
    • Increase access to meaningful data and information regarding important vendors.

    Establish Baseline Metrics

    Baseline metrics will be improved through:

    Using the Maturity Assessment and 90-Day Plan tools, track how well you are able to achieve your goals and objectives:

    • Did you meet the targeted maturity level for each maturity category as determined by the point system?
    • Did you finish each activity in the 90-Day Plan completely and on time?
    1-Year Maturity Roadmap(by Category) Target Maturity (Total Points) Actual Maturity (Total Points)
    Contracts 12 12
    Risk 8 7
    Vendor Selection 9 9
    Vendor Relationships 21 21
    VMI Operations 24 16
    90-Day Plan (by Activity) Activity Completed
    Finalize mission and goals; gain executive approval Yes
    Finalize OIC chart; gain buy-in from other departments Yes
    Classify top 40 vendors by spend Yes
    Create initial scorecard Yes
    Develop the business alignment meeting agenda Yes
    Conduct two business alignment meetings No
    Update job descriptions Yes
    Map two VMI processes No

    Info-Tech offers various levels of support to best suit your needs

    DIY Toolkit

    “Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful.”

    Guided Implementation

    “Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track.”

    Workshop

    “We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place.”

    Consulting

    “Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project.”

    Diagnostics and consistent frameworks used throughout all four options

    Guided Implementation

    What does a typical GI on this topic look like?

    Phase 1 Phases 2 & 3 Phase 4

    Call #1: Mission statement and goals, scope, and strengths and obstacles.

    Call #5: Classification model.

    Call #9: Policies and procedures and reports.

    Call #12: Assess compliance, incorporate leading practices, leverage lessons learned, maintain internal alignment, and update governances.

    Call #2: Roles and responsibilities and process mapping.

    Call #6: Risk assessment.

    Call #10: 3-year roadmap.

    Call #3: Charter and vendor inventory.

    Call #7: Scorecards and feedback and business alignment meetings.

    Call #11: 90-day plan and quick wins.

    Call #4: Maturity assessment and VMI structure.

    Call #8: Relationship alignment document, vendor orientation, and job descriptions.

    Workshop Overview

    Contact your account representative for more information.
    workshops@infotech.com 1-888-670-8889

    Day 1 Day 2 Day 3 Day 4
    Plan Plan/Build/Run Build/Run Review

    Activities

    1.1 Mission Statement and Goals
    1.2 Scope
    1.3 Strengths and Obstacles
    1.4 Roles and Responsibilities
    1.5 Process Mapping
    1.6 Charter
    1.7 Vendor Inventory
    1.8 Maturity Assessment
    1.9 Structure

    2.1 Classification Model
    2.2 Risk Assessment Tool
    2.3 Scorecards and Feedback
    2.4 Business Alignment Meeting Agenda
    2.5 Relationship Alignment Document
    2.6 Vendor Orientation
    2.7 Job Descriptions
    2.8 Policies and Procedures
    2.9 3-Year Roadmap
    2.10 90-Day Plan
    2.11 Quick Wins
    2.12 Reports

    3.1 Classify Vendors
    3.2 Conduct Internal “Kickoff” Meeting
    3.3 Conduct Vendor Orientation
    3.4 Compile Scorecards
    3.5 Conduct Business Alignment Meetings
    3.6 Work the 90-Day Plan
    3.7 Manage the 3-Year Roadmap
    3.8 Measure and Monitor Risk
    3.9 Issue Reports
    3.10 Develop/Improve Vendor Relationships
    3.11 Contribute to Other Processes

    4.1 Assess Compliance
    4.2 Incorporate Leading Practices
    4.3 Leverage Lessons Learned
    4.4 Maintain Internal Alignment
    4.5 Update Governances

    Deliverables

    1. Completed Mission Statement and Goals
    2. List of Items In Scope and Out of Scope for the VMI
    3. List of Strengths and Obstacles for the VMI
    4. Completed OIC Chart
    5. Sample Process Map for One Process
    6. Vendor Inventory tab
    1. Completed Maturity Assessment
    2. Sample Job Descriptions and Phrases
    3. List of Attributes of a Valuable Vendor
    4. Configured Classification Model
    5. Configured Risk Assessment Tool
    6. Configured Scorecard and Feedback Questions
    7. Configured Business Alignment Meeting Agenda
    1. Relationship Alignment Document Sample and Checklist
    2. Vendor Orientation Checklist
    3. Policies and Procedures Checklist
    4. Completed 3-Year Roadmap
    5. Completed 90-Day Plan
    6. List of Quick Wins
    7. List of Reports

    Phase 1: Plan

    Get Organized

    1.1 Mission Statement and Goals
    1.2 Scope
    1.3 Strengths and Obstacles
    1.4 Roles and Responsibilities
    1.5 Process Mapping
    1.6 Charter
    1.7 Vendor Inventory
    1.8 Maturity Assessment
    1.9 Structure

    Phase 1 Phase 2 Phase 3 Phase 4
    1.1 Mission Statement and Goals
    1.2 Scope
    1.3 Strengths and Obstacles
    1.4 Roles and Responsibilities
    1.5 Process Mapping
    1.6 Charter
    1.7 Vendor Inventory
    1.8 Maturity Assessment
    1.9 Structure

    2.1 Classification Model
    2.2 Risk Assessment Tool
    2.3 Scorecards and Feedback
    2.4 Business Alignment Meeting Agenda
    2.5 Relationship Alignment Document
    2.6 Vendor Orientation
    2.7 Job Descriptions
    2.8 Policies and Procedures
    2.9 3-Year Roadmap
    2.10 90-Day Plan
    2.11 Quick Wins
    2.12 Reports

    3.1 Classify Vendors
    3.2 Conduct Internal “Kickoff” Meeting
    3.3 Conduct Vendor Orientation
    3.4 Compile Scorecards
    3.5 Conduct Business Alignment Meetings
    3.6 Work the 90-Day Plan
    3.7 Manage the 3-Year Roadmap
    3.8 Measure and Monitor Risk
    3.9 Issue Reports
    3.10 Develop/Improve Vendor Relationships
    3.11 Contribute to Other Processes

    4.1 Assess Compliance
    4.2 Incorporate Leading Practices
    4.3 Leverage Lessons Learned
    4.4 Maintain Internal Alignment
    4.5 Update Governances

    This phase will walk you through the following activities:

    Organize your VMI and document internal processes, relationships, roles, and responsibilities. The main outcomes from this phase are organizational documents, a baseline VMI maturity level, and a desired future state for the VMI.

    This phase involves the following participants:

    • VMI team
    • Applicable stakeholders and executives
    • Procurement/Sourcing
    • IT
    • Others as needed

    Jump Start Your Vendor Management Initiative

    Phase 1: Plan

    Get organized.

    Phase 1: Plan focuses on getting organized. Foundational elements (mission statement, goals, scope, strengths and obstacles, roles and responsibilities, and process mapping) will help you define your VMI. These and the other elements of this Phase will follow you throughout the process of standing up your VMI and running it.

    Spending time up front to ensure that everyone is on the same page will help avoid headaches down the road. The tendency is to skimp (or even skip) on these steps to get to “the good stuff.” To a certain extent, the process provided here is like building a house. You wouldn’t start building your dream home without having a solid blueprint. The same is true with vendor management. Leveraging vendor management tools and techniques without the proper foundation may provide some benefit in the short term, but in the long term it will ultimately be a house of cards waiting to collapse.

    Step 1.1: Mission statement and goals

    Identify why the VMI exists and what it will achieve.

    Whether you are starting your vendor management journey or are already down the path, it is important to know why the vendor management initiative exists and what it hopes to achieve. The easiest way to document this is with a written declaration in the form of a mission statement and goals. Although this is the easiest way to proceed, it is far from easy.

    The mission statement should identify at a high level the nature of the services provided by the VMI, who it will serve, and some of the expected outcomes or achievements. The mission statement should be no longer than one or two sentences.

    The complement to the mission statement is the list of goals for the VMI. Your goals should not be a reassertion of your mission statement in bullet format. At this stage it may not be possible to make them SMART (Specific, Measurable, Achievable/Attainable, Relevant, Time-Bound/Time-Based), but consider making them as SMART as possible. Without some of the SMART parameters attached, your goals are more like dreams and wishes. At a minimum, you should be able to determine the level of success achieved for each of the VMI goals.

    Although the VMI’s mission statement will stay static over time (other than for significant changes to the VMI or organization as a whole), the goals should be re-evaluated periodically using a SMART filter and adjusted as needed.

    1.1.1: Mission statement and goals

    20-40 minutes

    1. Meet with the participants and use a brainstorming activity to list on a whiteboard or flip chart the reasons why the VMI will exist.
    2. Review external mission statements for inspiration.
    3. Review internal mission statements from other areas to ensure consistency.
    4. Draft and document your mission statement in the Phase 1 Tools and Templates Compendium, Tab 1.1 Mission Statement and Goals.
    5. Continue brainstorming and identify the high-level goals for the VMI.
    6. Review the list of goals and make them as SMART (Specific, Measurable, Achievable/Attainable, Relevant, Time-Bound/Time-Based) as possible.
    7. Document your goals in the Phase 1 Tools and Templates Compendium, Tab 1.1 Mission Statement and Goals.
    8. Obtain sign-off on the mission statement and goals from stakeholders and executives as required.

    Input

    • Brainstorming results
    • Mission statements from other internal and external sources

    Output

    • Completed mission statement and goals

    Materials

    • Whiteboard/Flip Charts
    • Jump – Phase 1 Tools and Templates Compendium, Tab 1.1 Mission Statement and Goals

    Participants

    • VMI team
    • Applicable stakeholders and executives (as needed)

    Step 1.2: Scope

    Determine what is in scope and out of scope for the VMI

    Regardless of where your VMI resides or how it operates, it will be working with other areas within your organization. Some of the activities performed by the VMI will be new and not currently handled by other groups or individuals internally; at the same time, some of the activities performed by the VMI may be currently handled by other groups or individuals internally. In addition, executives, stakeholders, and other internal personnel may have expectations or make assumptions about the VMI. As a result, there can be a lot of confusion about what the VMI does and doesn’t do, and the answers cannot always be found in the VMI’s mission statement and goals.

    One component of helping others understand the VMI landscape is formalizing the VMI scope. The scope will define boundaries for the VMI. The intent is not to fence itself off and keep others out but provide guidance on where the VMI’s territory begins and ends. Ultimately, this will help clarify the VMI’s roles and responsibilities, improve workflow, and reduce errant assumptions.

    When drafting your VMI scoping document, make sure you look at both sides of the equation (similar to what you would do when following best practices for a statement of work): Identify what is in scope and what is out of scope. Be specific when describing the individual components of the VMI scope, and make sure executives and stakeholders are on board with the final version.

    1.2.1: Scope

    20-40 minutes

    1. Meet with the participants and use a brainstorming activity to list on a whiteboard or flip chart the activities and functions in scope and out of scope for the VMI.
      1. Be specific to avoid ambiguity and improve clarity.
      2. Go back and forth between in scope and out of scope as needed; it is not necessary to list all of the in-scope items and then turn your attention to the out-of-scope items.
    2. Review the lists to make sure there is enough specificity. An item may be in scope or out of scope but not both.
    3. Use the Phase 1 Tools and Templates Compendium, Tab 1.2 Scope, to document the results.
    4. Obtain sign-off on the scope from stakeholders and executives as required.

    Input

    • Brainstorming
    • Mission statement and goals

    Output

    • Completed list of items in and out of scope for the VMI

    Materials

    • Whiteboard/Flip Charts
    • Jump – Phase 1 Tools and Templates Compendium, Tab 1.2 Scope

    Participants

    • VMI team
    • Applicable stakeholders and executives (as needed)

    Step 1.3: Strengths and obstacles

    Pinpoint the VMI’s strengths and obstacles.

    A SWOT analysis (strengths, weaknesses, opportunities, and threats) is a valuable tool, but it is overkill for your VMI at this point. However, using a modified and simplified form of this tool (strengths and obstacles) will yield significant results and benefit the VMI as it grows and matures.

    Your output will be two lists: the strengths associated with the VMI and the obstacles facing the VMI. For example, strengths could include items such as smart people working within the VMI and executive support. Obstacles could include items such as limited headcount and training required for VMI staff.

    The goals are 1) to harness the strengths to help the VMI be successful and 2) to understand the impact of the obstacles and plan accordingly. The output can also be used to enlighten executives and stakeholders about the challenges associated with their directives or requests (e.g. human bandwidth may not be sufficient to accomplish some of the vendor management activities and there is a moratorium on hiring until the next budget year).

    For each strength identified, determine how you will or can leverage it when things are going well or when the VMI is in a bind. For each obstacle, list the potential impact on the VMI (e.g. scope, growth rate, and number of vendors that can actively be part of the VMI).

    As you do your brainstorming, be as specific as possible and validate your lists with stakeholders and executives as needed.

    1.3.1: Strengths and obstacles

    20-40 minutes

    1. Meet with the participants and use a brainstorming activity to list on a whiteboard or flip chart the VMI’s strengths and obstacles.
      1. Be specific to avoid ambiguity and improve clarity.
      2. Go back and forth between strengths and obstacles as needed; it is not necessary to list all of the strengths and then turn your attention to the obstacles.
      3. It is possible for an item to be a strength and an obstacle; when this happens, add details to distinguish the situations.
    2. Review the lists to make sure there is enough specificity.
    3. Determine how you will leverage each strength and how you will manage each obstacle.
    4. Use the Phase 1 Tools and Templates Compendium, Tab 1.3 Strengths and Obstacles, to document the results.
    5. Obtain sign-off on the strengths and obstacles from stakeholders and executives as required.

    Download the Info-Tech Jump – Phase 1 Tools and Templates Compendium

    Input

    • Brainstorming
    • Mission statement and goals
    • Scope

    Output

    • Completed list of items impacting the VMI’s ability to be successful: strengths the VMI can leverage and obstacles the VMI must manage

    Materials

    • Whiteboard/Flip Charts
    • Jump – Phase 1 Tools and Templates Compendium, Tab 1.3 Strengths and Obstacles

    Participants

    • VMI team
    • Applicable stakeholders and executives (as needed)

    Step 1.4: Roles and responsibilities

    Obtain consensus on who is responsible for what.

    One crucial success factor for VMIs is gaining and maintaining internal alignment. There are many moving parts to an organization, and a VMI must be clear on the various roles and responsibilities related to the relevant processes. Some of this information can be found in the VMI’s scope, referenced in Step 1.2, but additional information is required to avoid stepping on each other’s toes since many of the processes require internal departments to work together. (For example, obtaining requirements for a request for proposal takes more than one person or one department to complete this process.) While it is not necessary to get too granular, it is imperative that you have a clear understanding of how the VMI activities will fit within the larger vendor management lifecycle (which is comprised of many sub processes) and who will be doing what.

    As we have learned through our workshops and guided implementations, a traditional RACI* or RASCI* chart does not work well for this purpose. These charts are not intuitive, and they lack the specificity required to be effective. For vendor management purposes, a higher-level view and a slightly different approach provide much better results.

    This step will lead your through the creation of an OIC* chart to determine vendor management lifecycle roles and responsibilities. Afterward, you’ll be able to say, “Oh, I see clearly who is involved in each part of the process and what their role is.”

    *RACI – Responsible, Accountable, Consulted, Informed
    *RASCI – Responsible, Accountable, Support, Consulted, Informed
    *OIC – Owner, Informed, Contributor

    This is an image of a table which shows an example of which role would be responsible for which step

    Step 1.4: Roles and responsibilities (cont.)

    Obtain consensus on who is responsible for what.

    To start, define the vendor management lifecycle steps or process applicable to your VMI. Next, determine who participates in the vendor management lifecycle. There is no need to get too granular – think along the lines of departments, subdepartments, divisions, agencies, or however you categorize internal operational units. Avoid naming individuals other than by title; this typically happens when a person oversees a large group (e.g. the CIO [chief information officer] or the CPO [chief procurement officer]). Be thorough, but the chart can get out of hand quickly. For each role and step of the lifecycle, ask whether the entry is necessary – does it add value to the clarity of understanding the responsibilities associated with the vendor management lifecycle? Consider two examples, one for roles and one for lifecycle steps: 1) Is IT sufficient or do you need IT Operations and IT Development? 2) Is “negotiate contract documents” sufficient or do you need “negotiate the contract” and “negotiate the renewal”? The answer will always depend on your culture and environment, but be wary of creating a spreadsheet that requires an 85-inch monitor to view it in its entirety.

    After defining the roles (departments, divisions, agencies) and the vendor management lifecycle steps or process, assign one of three letters to each box in your chart:

    • O – Owner – who owns the process; they may also contribute to it.
    • I – Informed – who is informed about the progress or results of the process.
    • C – Contributor – who contributes or works on the process; it can be tangible or intangible contributions.

    This activity can be started by the VMI or done as a group with representatives from each of the named roles. If the VMI starts the activity, the resulting chart should be validated by the each of the named roles.

    1.4.1: Roles and responsibilities

    1-6 hours

    1. Meet with the participants and configure the OIC Chart in the Jump – Phase 1 Tools and Templates Compendium, Tab 1.4 OIC Chart.
      1. Review the steps or activities across the top of the chart and modify as needed.
      2. Review the roles listed along the left side of the chart and modify as needed.
    2. For each activity or step across the top of the chart, assign each role a letter – O for owner of that activity or step; I for informed; or C for contributor. Use only one letter per cell.
    3. Work your way across the chart. Every cell should have an entry or be left blank if it is not applicable.
    4. Review the results and validate that every activity or step has an O assigned to it; there must be an owner for every activity or step.
    5. Obtain sign-off on the OIC chart from stakeholders and executives as required.

    Download the Info-Tech Jump – Phase 1 Tools and Templates Compendium

    Input

    • A list of activities or steps to complete a project, starting with requirements gathering and ending with ongoing risk management
    • A list of internal areas (departments, divisions, agencies, etc.) and stakeholders that contribute to completing a project

    Output

    • Completed OCI chart indicating roles and responsibilities for the VMI and other internal areas

    Materials

    • Jump – Phase 1 Tools and Templates Compendium, Tab 1.4 OIC Chart

    Participants

    • VMI team
    • Procurement/Sourcing
    • IT
    • Representatives from other areas as needed
    • Applicable stakeholders and executives as needed

    Step 1.5: Process mapping

    Diagram the workflow.

    Although policies and procedures are important, their nature can make it difficult to grasp how things work at a high level (or even at the detail level). To help bridge the gap, map the applicable processes (determined by how deep and wide you want to go) involving the VMI. To start, look at the OIC chart from Step 1.4. You can expand the breadth and depth of your mapping to include the VMI scope, the 3-year roadmap (see Step 2.9), and the processes driven by the day-to-day work within the VMI.

    Various mapping tools can be used. Three common approaches that can be mixed and matched are:

    • Traditional flowcharts.
    • Swimlane diagrams.
    • Work breakdown structures.
    This is an example of a Workflow Process Map

    Step 1.5: Process mapping (cont.)

    Diagram the workflow.

    Your goal is not to create an in-depth diagram for every step of the vendor management lifecycle. However, for steps owned by the VMI, the process map should include sufficient details for the owner and the contributors (see Step 1.4) to understand what is required of them to support that step in the lifecycle.

    For VMI processes that don’t interact with other departments, follow the same pattern as outlined above for steps owned by the VMI.

    Whatever methodology you use to create your process map, make sure it includes enough details so that readers and users can identify the following elements:

    • Input:
      • What are the inputs?
      • Where do the inputs originate or come from?
    • Process:
      • Who is involved/required for this step?
      • What happens to the inputs in this step?
      • What additional materials, tools, or resources are used or required during this step?
    • Output:
      • What are the outputs?
      • Where do the outputs go next?

    1.5.1: Process Mapping

    1-8 hours (or more)

    1. Meet with the participants and determine which processes you want to map.
      1. For processes owned by the VMI, map the entire process.
      2. For processes contributed to by the VMI, map the entire process at a high level and map the VMI portion of the process in greater detail.
    2. Select the right charts/diagrams for your output.
      1. Flowchart
      2. Swimlane diagram
      3. Modified SIPOC (Supplier, Input, Process, Output, Customer)
      4. WBS (work breakdown structure)
    3. Begin mapping the processes either in a tool or using sticky notes. You want to be able to move the steps and associated information easily; most people don’t map the entire process accurately or with sufficient detail the first time through. An iterative approach works best.
    4. Obtain signoff on the process maps from stakeholders and executives as required. A copy of the final output can be kept in the Jump – Phase 1 Tools and Templates Compendium, Tab 1.5 Process Mapping, if desired.

    Download the Info-Tech Jump – Phase 1 Tools and Templates Compendium

    Input

    • Existing processes (formal, informal, documented, and undocumented)
    • OIC chart

    Output

    • Process maps for processes contributed to or owned by the VMI

    Materials

    • Sticky Notes
    • Flowchart/process mapping software or something similar
    • (Optional) Jump – Phase 1 Tools and Templates Compendium, Tab 1.5 Process Mapping

    Participants

    • VMI team
    • Procurement/Sourcing
    • IT
    • Representatives from other areas as needed
    • Applicable stakeholders and executives (as needed)

    Step 1.6: Charter

    Document how the VMI will operate.

    As you continue getting organized by working through steps 1.1-1.5, you may want to document your progress in a charter and add some elements. Basically, a charter is a written document laying out how the VMI will operate within the organization. It clearly states the VMI’s mission, goals, scope, roles and responsibilities, and vendor governance model. In addition, it can include a list of team members and sponsors.

    Whether you create a VMI charter will largely depend on:

    • Your organization’s culture.
    • Your organization’s formality.
    • The perceived value of creating a charter.

    If you decide to create a VMI charter, this is a good place in the process to create an initial draft. As you continue working through the blueprint and your VMI matures, update the VMI charter as needed.

    VMI Charter:

    • Purpose
    • Sponsors
    • Roles
    • Responsibilities
    • Governance

    1.6.1: Charter

    1-4 hours

    1. Meet with the participants and review the template in Jump – Phase 1 Tools and Templates Compendium, Tab 1.6 Charter.
    2. Determine whether the participants will use this template or add materials to your standard charter template.
    3. Complete as much of the charter as possible, knowing that some information may not be available until later.
    4. Return to the charter as needed until it is completed.
    5. Obtain sign-off on the charter from stakeholders and executives as required.

    Download the Info-Tech Jump – Phase 1 Tools and Templates Compendium

    Input

    • Mission statement and goals
    • Scope
    • Strengths and obstacles
    • OIC chart
    • List of stakeholders and executives and their VMI roles and responsibilities

    Output

    • Completed VMI charter

    Materials

    • Jump – Phase 1 Tools and Templates Compendium, Tab 1.6 Charter
    • Your organization’s standard charter document

    Participants

    • VMI team
    • Applicable stakeholders and executives (as needed)

    Step 1.7: Vendor inventory

    Compile a list of vendors and relevant vendor information.

    As you prepare your VMI for being operational, it’s critical to identify all of your current vendors providing IT products or services to the organization. This can be tricky and may depend on how you view things internally. For example, you may have traditional IT vendors that are managed by IT, and you may have IT vendors that are managed by other internal departments (shadow IT or out-in-the-open IT). If it wasn’t determined with the help of stakeholders and executives before now, make sure you establish the purview of the VMI at this point. What types of vendors are included and excluded from the VMI?

    You may find that a vendor can be included and excluded based on the product or service they provide. A vendor may provide a service that is managed by IT and a service that is managed/controlled by another department. In this instance, a good working relationship and clearly defined roles and responsibilities between the VMI and the other department will be required. But, it all starts with compiling a list of vendors and validating the VMI’s purview (and any limitations) for the vendors with stakeholders and executives.

    Step 1.7: Vendor inventory (cont.)

    Compile a list of vendors and relevant vendor information.

    At a minimum, the VMI should be able to quickly retrieve key information about each of “its” vendors:

    • Vendor Name
    • Classification (see Steps 2.1 and 3.1)
    • Categories of Service
    • Names of Products and Services Provided
    • Brief Descriptions of Products and Services Provided
    • Annualized Vendor Spend
    • Vendor Contacts
    • Internal Vendor Relationship Owner

    Not all of this information will be available at this point, but you can begin designing or configuring your tool to meet your needs. As your VMI enters Phase 3: Run and continues to mature, you will return to this tool and update the information. For example, the vendor classification category won’t be known until Phase 3, and it can change over time.

    1.7.1: Vendor inventory

    1-10 hours

    Meet with the participants and review the Jump – Phase 1 Tools and Templates Compendium, Tab 1.7 Vendor Inventory. Determine whether the VMI wants to collect and/or monitor additional information and make any necessary modifications to the tool.

    Enter the “Annual IT Vendor Spend” amount in the appropriate cell toward the top of the spreadsheet. This is for IT spend for vendor-related activities within the VMI’s scope; include shadow IT spend and “non-shadow” IT spend if those vendors will be included in the VMI’s scope.

    Populate the data fields for your top 50 vendors by annual spend; you may need multiple entries for the same vendor depending on the nature of the products and services they provide.

    Ignore the “Classification” column for now; you will return to this later when classification information is available.

    Ignore the “Percentage of IT Budget” column as well; it uses a formula to calculate this information.

    Input

    • Data from various internal and external sources such as accounts payable, contracts, and vendor websites

    Output

    • List of vendors with critical information required to manage relationships with key vendors

    Materials

    • Jump – Phase 1 Tools and Templates Compendium, Tab 1.7 Vendor Inventory

    Participants

    • VMI team (directly)
    • Other internal and external personnel (indirectly)

    Download the Info-Tech Jump – Phase 1 Tools and Templates Compendium

    Step 1.8: Maturity assessment

    Establish a VMI maturity baseline and set an ideal future state.

    Knowing where you are and where you want to go are essential elements for any journey in the physical world, and the same holds true for your VMI journey. Start by assessing your current-state VMI maturity. This will provide you with a baseline to measure progress against. Next, using the same criteria, determine the level of VMI maturity you would like to achieve one year in the future. This will be your future-state VMI maturity. Lastly, identify the gaps and plot your course.

    The maturity assessment provides three main benefits:

    1. Focus – you’ll know what is important to you moving forward.
    2. 3-Year Roadmap (discussed more fully in Step 2.9) – you’ll have additional input for your short-term and long-term roadmap (1, 2, and 3 years out).
    3. Quantifiable Improvement – you’ll be able to measure your progress and make midcourse corrections when necessary.

    Step 1.8: Maturity assessment (cont.)

    Establish a VMI maturity baseline and set an ideal future state.

    The Info-Tech VMI Maturity Assessment tool evaluates your maturity across several criteria across multiple categories. Once completed, the assessment will specify:

    • A current-state score by category and overall.
    • A target-state score by category and overall.
    • A quantifiable gap for each criterion.
    • A priority assignment for each criterion.
    • A level of effort required by criterion to get from the current state to the target state.
    • A target due date by criterion for achieving the target state.
    • A rank order for each criterion (note: limit your ranking to your top 7 or 9).

    Many organizations will be tempted to mature too quickly. Resource constraints and other items from Step 1.3 (Strengths and Obstacles) will impact how quickly you can mature. Being aggressive is fine, but it must be tempered with a dose of reality. Otherwise, morale, perception, and results can suffer.

    1.8.1: Maturity assessment

    45-90 minutes

    1. Meet with the participants and use Jump – Phase 1 Tools and Templates Compendium, Tab 1.8 Maturity Assessment Input, to complete the first part of this activity. Provide the required information indicated below.
      1. Review each statement in column B and enter a value in the “Current” column using the drop-down menus based on how much you disagree or agree (0-4) with the statement. This establishes a baseline maturity.
      2. Repeat this process for the “Future” column using a target date of one year from now to achieve this level. This is your desired maturity.
      3. Enter information regarding priority, level of effort, and target due date in the applicable columns using the drop-down menus. (Priority levels are critical, high, medium, low, and maintain; Levels of Effort are high, medium, and low; Target Due Dates are broken into timelines: 1-3 months, 4-6 months, 7-9 months, and 10-12 months.)
    2. Review the information on Jump – Phase 1 Tools and Templates Compendium, Tab 1.8 Maturity Assessment Output; use the Distribution Tables to help you rank your top priorities. Enter a unique number into the Priority (Rank) column. Limit your ranking to the top 7 to 9 activities to provide focus.

    Input

    • Knowledge of current VMI practices and desired future states

    Output

    • VMI maturity baseline
    • Desired VMI target maturity state (in one year)
    • Prioritized areas to improve and due dates
    • Graphs and tables to identify maturity deltas and track progress

    Materials

    • Jump – Phase 1 Tools and Templates Compendium, Tab 1.8 Maturity Assessment Input
    • Jump – Phase 1 Tools and Templates Compendium, Tab 1.8 Maturity Assessment Output

    Participants

    • VMI team
    • Applicable stakeholders and executives (as needed)

    Step 1.9: Structure

    Determine the VMI’s organizational and reporting structure.

    There are two parts to the VMI structure:

    1. Organization Structure. Who owns the VMI – where does it fit on the organization chart?
    2. Reporting Structure. What is the reporting structure within the VMI – what are the job functions, titles, and solid and dotted lines of accountability?

    VMI Organization Structure

    The decision regarding who owns the VMI can follow one of two paths:

    1. The decision has already been made by the board of directors, executives, senior leadership, or stakeholders; OR
    2. The decision has not been made, and options will be reviewed and evaluated before it is implemented.

    Many organizations overlook the importance of this decision. The VMI’s position on the organization chart can aid or hinder its success. Whether the decision has already been made or not, this is the perfect time to evaluate the decision or options based on the following question: Why is the VMI being created and how will it operate? Review the documents you created during Steps 1.1-1.8 and other factors to answer this question.

    Step 1.9: Structure (cont.)

    Determine the VMI’s organizational and reporting structure.

    Based on your work product from Steps 1.1-1.8 and other factors, select where the VMI will be best located from the following areas/offices or their equivalent:

    • Chief Compliance Officer (CCO)
    • Chief Information Officer (CIO)
    • Chief Financial Officer (CFO)
    • Chief Procurement Officer (CPO)
    • Chief Operating Officer (COO)
    • Other area

    Without the proper support and placement in the organization chart, the VMI can fail. It is important for the VMI to find a suitable home with a direct connection to one of the sponsors identified above and for the VMI lead to have significant stature (aka title) within the organization. For example, if the VMI lead is a “manager” level who is four reporting layers away from the chief officer/sponsor, the VMI will have an image issue within and outside of the sponsor’s organization (as well as within the vendor community). While this is not to say that the VMI lead should be a vice president* or senior director, our experience and research indicate that the VMI and the VMI lead will be taken more seriously when the VMI lead is at least a director level reporting directly to a CXO.

    *For purposes of the example above, the reporting structure hierarchy used is manager, senior manager, director, senior director, vice president, CXO.

    Step 1.9: Structure (cont.)

    Determine the VMI’s organizational and reporting structure.

    VMI Reporting Structure

    As previously mentioned, the VMI reporting structure describes and identifies the job functions, titles, and lines of accountability. Whether you have a formal vendor management office or you are leveraging the principles of vendor management informally, your VMI reporting structure design will involve some solid lines and some dotted lines. In this instance, the dotted lines represent part-time participation or people/areas that will assist the VMI in some capacity. For example, if the VMI sits within IT, a dotted line to Procurement will show that a good working relationship is required for both parties to succeed; or a dotted line to Christina in Legal will indicate that Christina will be helping the VMI with legal issues.

    There is no one-size-fits-all reporting structure for VMIs, and your approach must leverage the materials from Steps 1.1-1.8, your culture, and your needs. By way of example, your VMI may include some or all of the following functions:

    • Contract Management
    • Relationship Management
    • Financial Management
    • Asset Management
    • Performance Management
    • Sourcing/Procurement
    • Risk Management

    Step 1.9: Structure (cont.)

    Determine the VMI’s organizational and reporting structure.

    Once you’ve identified the functional groups, you can assign titles, responsibilities, and reporting relationships. A good diagram goes a long way to helping others understand your organization. Traditional organization charts work well with VMIs, but a target diagram allows for rapid absorption of the dotted-line relationships. Review the two examples below and determine an approach that works best for you.

    An organizational Chart is depicted.  At the top of the chart is: Office of the CIO.  Below that is: VMI: Legal; Accounting & Finance; Corporate Procurement; below that are the following: Vendor Risk Management; Vendor Reporting and Analysis; Asset Management; Performance Management; Contract Management; IT Procurement Three concentric circles are depicted.  In the inner circle is the term: VMI.  In the middle circle are the terms: Reporting & Analysis; Asset Mgmt; Contract Mgmt; Performance Mgmt; It Proc; Vendor Risk.  In the outer circle are the following terms: Compliance; Finance; HR; Accounting; Procurement; Business Units; Legal; IT

    1.9.1: Structure

    15-60 minutes

    1. Meet with the participants and review decisions that have been made or options that are available regarding the VMI’s placement in the organization chart.
      1. Common options include the Chief Information Officer (CIO), Chief Financial Officer (CFO), or Chief Procurement Officer (CPO).
      2. Less common but viable options include the Chief Compliance Officer (CCO), Chief Operating Officer (COO), or another area.
    2. Brainstorm and determine the job functions and titles
    3. Define the reporting structure within the VMI.
    4. Identify the “dotted line” relationships between the VMI and other internal areas.
    5. Using flowchart, org. chart, or other similar software, reduce your results to a graphic representation that indicates where the VMI resides, its reporting structure, and its dotted-line relationships.
    6. Obtain sign-off on the structure from stakeholders and executives as required. A copy of the final output can be kept in the Jump – Phase 1 Tools and Templates Compendium, Tab 1.9 Structure, if desired.

    Input

    • Mission statement and goals
    • Scope
    • Maturity assessment results (current and target state)
    • Existing org. charts
    • Brainstorming

    Output

    • Completed org. chart with job titles and reporting structure

    Materials

    • Whiteboard/flip chart
    • Sticky notes
    • Flowchart/org. chart software or something similar
    • (Optional) Jump – Phase 1 Tools and Templates Compendium, Tab 1.9 Structure

    Participants

    • VMI team
    • VMI sponsor
    • Stakeholders and executives

    Phase 2: Build

    Create and Configure Tools, Templates, and Processes

    Phase 1Phase 2Phase 3Phase 4
    1.1 Mission Statement and Goals


    1.2 Scope

    1.3 Strengths and Obstacles

    1.4 Roles and Responsibilities

    1.5 Process Mapping

    1.6 Charter

    1.7 Vendor Inventory

    1.8 Maturity Assessment

    1.9 Structure

    2.1 Classification Model
    2.2 Risk Assessment Tool
    2.3 Scorecards and Feedback
    2.4 Business Alignment Meeting Agenda
    2.5 Relationship Alignment Document
    2.6 Vendor Orientation
    2.7 Job Descriptions
    2.8 Policies and Procedures
    2.9 3-Year Roadmap
    2.10 90-Day Plan
    2.11 Quick Wins
    2.12 Reports

    3.1 Classify Vendors
    3.2 Conduct Internal “Kickoff” Meeting
    3.3 Conduct Vendor Orientation
    3.4 Compile Scorecards
    3.5 Conduct Business Alignment Meetings
    3.6 Work the 90-Day Plan
    3.7 Manage the 3-Year Roadmap
    3.8 Measure and Monitor Risk
    3.9 Issue Reports
    3.10 Develop/Improve Vendor Relationships
    3.11 Contribute to Other Processes

    4.1 Assess Compliance
    4.2 Incorporate Leading Practices
    4.3 Leverage Lessons Learned
    4.4 Maintain Internal Alignment
    4.5 Update Governances

    This phase will walk you through the following activities:

    Configure and create the tools and templates that will help you run the VMI. The main outcomes from this phase are a clear understanding of which vendors are important to you, the tools to manage the vendor relationships, and an implementation plan.

    This phase involves the following participants:

    • VMI team
    • Applicable stakeholders and executives
    • Human Resources
    • Legal
    • Others as needed

    Jump Start Your Vendor Management Initiative

    Phase 2: Build

    Create and configure tools, templates, and processes.

    Phase 2: Build focuses on creating and configuring the tools and templates that will help you run your VMI. Vendor management is not a plug-and-play environment, and unless noted otherwise, the tools and templates included with this blueprint require your input and thought. The tools and templates must work in concert with your culture, values, and goals. That will require teamwork, insights, contemplation, and deliberation.

    During this Phase, you’ll leverage the various templates and tools included with this blueprint and adapt them for your specific needs and use. In some instances, you’ll be starting with mostly a blank slate; while in others, only a small modification may be required to make it fit your circumstances. However, it is possible that a document or spreadsheet may need heavy customization to fit your situation. As you create your VMI, use the included materials for inspiration and guidance purposes rather than as absolute dictates.

    Step 2.1: Classification model

    Configure the COST Vendor Classification Tool.

    One of the functions of a VMI is to allocate the appropriate level of vendor management resources to each vendor since not all vendors are of equal importance to your organization. While some people may be able intuitively to sort their vendors into vendor management categories, a more objective, consistent, and reliable model works best. Info-Tech’s COST model helps you assign your vendors to the appropriate vendor management category so that you can focus your vendor management resources where they will do the most good.

    COST is an acronym for Commodity, Operational, Strategic, and Tactical. Your vendors will occupy one of these vendor management categories, and each category helps you determine the nature of the resources allocated to that vendor, the characteristics of the relationship desired by the VMI, and the governance level used.

    The easiest way to think of the COST model is as a 2x2 matrix or graph. The model should be configured for your environment so that the criteria used for determining a vendor’s classification align with what is important to you and your organization. However, at this point in your VMI’s maturation, a simple approach works best. The Classification Model included with this blueprint requires minimal configuration to get you started and that is discussed on the activity slide associated with this Step 2.1.

    ↑
    Speed
    ↑
    Operational Strategic
    Commodity Tactical
    →→→
    Criticality and Risk to the Organization

    Step 2.1: Classification model (cont.)

    Configure the COST Vendor Classification Tool.

    Common Characteristics by Vendor Management Category

    Operational Strategic
    • Low to moderate risk and criticality; moderate to high spend and switching costs
    • Product or service used by more than one area
    • Price is a key negotiation point
    • Product or service is valued by the organization
    • Quality or the perception of quality is a differentiator (i.e. brand awareness)
    • Moderate to high risk and criticality; moderate to high spend and switching costs
    • Few competitors and differentiated products and services
    • Product or service significantly advances the organization’s vision, mission, and success
    • Well-established in their core industry
    Commodity Tactical
    • Low risk and criticality; low spend and switching costs
    • Product or service is readily available from many sources
    • Market has many competitors and options
    • Relationship is transactional
    • Price is the main differentiator
    • Moderate to high risk and criticality; low to moderate spend and switching costs
    • Vendor offerings align with or support one or more strategic objectives
    • Often IT vendors “outside” of IT (i.e. controlled and paid for by other areas)
    • Often niche or new vendors

    Source: Compiled in part from Stephen Guth, “Vendor Relationship Management Getting What You Paid for (And More)”

    2.1.1: Classification Model

    15-30 minutes

    1. Meet with the participants to configure the spend ranges in Jump – Phase 2 Vendor Classification Tool, Tab 1. Configuration, for your environment.
    2. Sort the data from Jump – Phase 1 Tools and Templates Compendium, Tab 1.7 Vendor Inventory, by spend; if you used multiple line items for a vendor in the Vendor Inventory tab, you will have to aggregate the spend data for this activity.
    3. Update cells F14-J14 in the Classification Model based on your actual data.
      1. Cell F14 – set the boundary at a point between the spend for your 10th and 11th ranked vendors. For example, if the 10th vendor by spend is $1,009,850 and the 11th vendor by spend is $980,763, the range for F14 would be $1,000,00+.
      2. Cell G14 – set the bottom of the range at a point between the spend for your 30th and 31st ranked vendors; the top of the range will be $1 less than the bottom of the range specified in F14.
      3. Cell H14 – set the bottom of the range slightly below the spend for your 50th ranked vendor; the top of the range will be $1 less than the bottom of the range specified in G14.
      4. Cells I14 and J14 – divide the remaining range in half and split it between the two cells; for J14 the range will be $0 to $1 less than the bottom range in I14.
    4. Ignore the other variables at this time.

    Download the Info-Tech Jump – Phase 2 Vendor Risk Assessment Tool

    Input

    • Jump – Phase 1 Tools and Templates Compendium, Tab 1.7 Vendor Inventory

    Output

    • Configured Vendor Classification Tool

    Materials

    • Jump – Phase 2 Vendor Classification Tool, Tab 1. Configuration

    Participants

    • VMI team

    Step 2.2: Risk assessment tool

    Identify risks to measure, monitor, and report on.

    One of the typical drivers of a VMI is risk management. Organizations want to get a better handle on the various risks their vendors pose. Vendor risks originate from many areas: financial, performance, security, legal, and many others. However, security risk is the high-profile risk and the one organizations often focus on almost exclusively, which leaves the organization vulnerable in other areas.

    Risk management is a program, not a project – there is no completion date. A proactive approach works best and requires continual monitoring, identification, and assessment. Reacting to risks after they occur can be costly and can have other detrimental effects on the organization. Any risk that adversely affects IT will adversely affect the entire organization.

    While the VMI won’t necessarily be quantifying or calculating the risk directly, it generally is the aggregator of risk information across the risk categories, which it then includes in its reporting function. (See Steps 2.12 and 3.8.)

    At a minimum, your risk management strategy should involve:

    • Identifying the risks you want to measure and monitor.
    • Identifying your risk appetite (the amount of risk you are willing to live with).
    • Measuring, monitoring, and reporting on the applicable risks.
    • Developing and deploying a risk management plan to minimize potential risk impact.

    Vendor risk is a fact of life, but you do have options for how you handle it. Be proactive and thoughtful in your approach, and focus your resources on what is important.

    2.2.1: Risk assessment tool

    30-90 minutes

    1. Meet with the participants to configure the risk indicators in Jump – Phase 2 Vendor Risk Assessment Tool, Tab 1. Set Parameters, for your environment.
    2. Review the risk categories and determine which ones you will be measuring and monitoring.
    3. Review the risk indicators under each risk category and determine whether the indicator is acceptable as written, is acceptable with modifications, should be replaced, or should be deleted.
    4. Make the necessary changes to the risk indicators; these changes will cascade to each of the vendor tabs. Limit the number of risk indicators to no more than seven per risk category.
    5. Gain input and approval as needed from sponsors, stakeholders, and executives as required.

    Download the Info-Tech Jump – Phase 2 Vendor Risk Assessment Tool

    Input

    • Scope
    • OIC Chart
    • Process Maps
    • Brainstorming

    Output

    • Configured Vendor Classification Tool

    Materials

    • Jump – Phase 2 Vendor Classification Tool, Tab 1. Configuration

    Participants

    • VMI team

    Step 2.3: Scorecards and feedback

    Design a two-way feedback loop with your vendors.

    A vendor management scorecard is a great tool for measuring, monitoring, and improving relationship alignment. In addition, it is perfect for improving communication between you and the vendor.

    Conceptually, a scorecard is similar to a report card you received when you were in school. At the end of a learning cycle, you received feedback on how well you did in each of your classes. For vendor management, the scorecard is also used to provide periodic feedback, but there are some different nuances and some additional benefits and objectives when compared to a report card.

    Although scorecards can be used in a variety of ways, the main focus here will be on vendor management scorecards – contract management, project management, and other types of scorecards will not be included in the materials covered in this Step 2.3 or in Step 3.4.

    Category 1 Score
    Vendor Objective A 4 ↓
    Objective B 3 ↓
    Objective C 5 ↑
    Objective D 4 !

    Step 2.3: Scorecards and feedback (cont.)

    Design a two-way feedback loop with your vendors.

    Anatomy

    The Info-Tech Scorecard includes five areas:

    • Measurement Categories. Measurement categories help organize the scorecard. Limit the number of measurement categories to three to five; this allows the parties to stay focused on what’s important. Too many measurement categories make it difficult for the vendor to understand the expectations.
    • Criteria. The criteria describe what is being measured. Create criteria with sufficient detail to allow the reviewers to fully understand what is being measured and to evaluate it. Criteria can be objective or subjective. Use three to five criteria per measurement category.
    • Measurement Category Weights. Not all of your measurement categories may be of equal importance to you; this area allows you to give greater weight to a measurement category when compiling the overall score.
    • Rating. Reviewers will be asked to assign a score to each criteria using a 1 to 5 scale.
    • Comments. A good scorecard will include a place for reviewers to provide additional information regarding the rating or other items that are relevant to the scorecard.

    An overall score is calculated based on the rating for each criteria and the measurement category weights.

    Step 2.3: Scorecards and feedback (cont.)

    Design a two-way feedback loop with your vendors.

    Goals and Objectives

    Scorecards can be used for a variety of reasons. Some of the common ones are listed below:

    • Improve vendor performance.
    • Convey expectations to the vendor.
    • Identify and recognize top vendors.
    • Increase alignment between the parties.
    • Improve communication with the vendor.
    • Compare vendors across the same criteria.
    • Measure items not included in contract metrics.
    • Identify vendors for “strategic alliance” consideration.
    • Help the organization achieve specific goals and objectives.
    • Identify and resolve issues before they impact performance or the relationship.

    Identifying your scorecard drivers first will help you craft a suitable scorecard.

    Step 2.3: Scorecards and feedback (cont.)

    Design a two-way feedback loop with your vendors.

    Info-Tech recommends starting with simple scorecards to allow you and the vendors to acclimate to the new process and information. As you build your scorecards, keep in mind that internal personnel will be scoring the vendors and the vendors will be reviewing the scorecard. Make your scorecard easy for your personnel to fill out and composed of meaningful content to drive the vendor in the right direction. You can always make the scorecard more complex in the future.

    Our recommendation of five categories is provided below. Choose three to five categories to help you accomplish your scorecard goals and objectives:

    1. Timeliness – responses, resolutions, fixes, submissions, completions, milestones, deliverables, invoices, etc.
    2. Cost – total cost of ownership, value, price stability, price increases/decreases, pricing models, etc.
    3. Quality – accuracy, completeness, mean time to failure, bugs, number of failures, etc.
    4. Personnel – skilled, experienced, knowledgeable, certified, friendly, trustworthy, flexible, accommodating, etc.
    5. Risk – adequate contractual protections, security breaches, lawsuits, finances, audit findings, etc.

    Some criteria may be applicable in more than one category. The categories above should cover at least 80% of the items that are important to your organization. The general criteria listed for each category is not an exhaustive list, but most things break down into time, money, quality, people, and risk issues.

    Step 2.3: Scorecards and feedback (cont.)

    Design a two-way feedback loop with your vendors.

    Additional Considerations

    • Even a good rating system can be confusing. Make sure you provide some examples or a way for reviewers to discern the differences between 1, 2, 3, 4, and 5. Don’t assume your “Rating Key” will be intuitive.
    • When assigning weights, don’t go lower than 10% for any measurement category. If the weight is too low, it won’t be relevant enough to have an impact on the total score. If it doesn’t “move the needle,” don’t include it.
    • Final sign-off on the scorecard template should occur outside of the VMI. The heavy lifting can be done by the VMI to create it, but the scorecard is for the benefit of the organization overall and those impacted by the vendors specifically. You may end up playing arbiter or referee, but the scorecard is not the exclusive property of the VMI. Try to reach consensus on your final template whenever possible.
    • You should notice improved ratings and total scores over time for your vendors. One explanation for this is the Pygmalion Effect: “The Pygmalion [E]ffect describes situations where someone’s high expectations improves our behavior and therefore our performance in a given area. It suggests that we do better when more is expected of us.”* Convey your expectations and let the vendors’ competitive juices take over.
    • While you’re creating your scorecard and materials to explain the process to internal personnel, identify those pieces that will help you explain it to your vendors as part of your vendor orientation (see steps 2.6 and 3.4). Leveraging pre-existing materials is a great shortcut.

    *Source: The Decision Lab, 2020

    Step 2.3: Scorecards and feedback (cont.)

    Design a two-way feedback loop with your vendors.

    Vendor Feedback

    After you’ve built your scorecard, turn your attention to the second half of the equation – feedback from the vendor. A communication loop cannot be successful without the dialogue flowing both ways. While this can happen with just a scorecard, a mechanism specifically geared toward the vendor providing you with feedback improves communication, alignment, and satisfaction.

    You may be tempted to create a formal scorecard for the vendor to use. Our recommendation is to avoid that temptation until later in your maturity or development of the VMI. You’ll be implementing a lot of new processes, deploying new tools and templates, and getting people to work together in new ways. Work on those things first.

    For now, implement an informal process for obtaining information from the vendor. Start by identifying information that you will find useful, information that will allow you to improve overall, to reduce waste or time, to improve processes, to identify gaps in skills. Incorporate these items into your business alignment meetings (see Steps 2.4 and 3.5). Create three to five good questions to ask the vendor and include these in the business alignment meeting agenda. The goal is to get meaningful feedback, and that starts with asking good questions.

    Keep it simple at first. When the time is right, you can build a more formal feedback form or scorecard. Don’t be in a rush though. So long as the informal method works, keep using it.

    2.3.1: Scorecards and feedback

    30-60 minutes

    1. Meet with the participants and brainstorm ideas for your scorecard measurement categories:
      1. What makes a vendor valuable to your organization?
      2. What differentiates a “good” vendor from a “bad” vendor?
      3. What items would you like to measure and provide feedback to the vendor to improve performance, the relationship, risk, and other areas?
    2. Select three, but no more than five, of the following measure categories: timeliness, cost, quality, personnel, and risk.
    3. Within each measurement category, list two or three criteria that you want to measure and track for your vendors; choose items that are as universal as possible rather than being applicable to one vendor or one vendor type.
    4. Assign a weight to each measurement category, ensuring that the total weight is 100% for all measurement categories.
    5. Document your results as you go in Jump – Phase 2 Tools and Templates Compendium, Tab 2.3 Scorecard.

    Download the Info-Tech Jump – Phase 2 Tools and Templates Compendium

    Input

    • Brainstorming

    Output

    • Configured scorecard template

    Materials

    • Jump – Phase 2 Tools and Templates Compendium, Tab 2.3 Scorecard

    Participants

    • VMI team
    • Applicable stakeholders and executives (as needed)

    2.3.2: Scorecards and feedback

    15-30 minutes

    1. Meet with the participants and brainstorm ideas for feedback to seek from your vendors during your business alignment meetings. During the brainstorming, identify questions to ask the vendor about your organization that will:
      1. Help you improve the relationship.
      2. Help you improve your processes or performance.
      3. Help you improve ongoing communication.
      4. Help you evaluate your personnel.
    2. Identify the top five questions you want to include in your business alignment meeting agenda. (Note: you may need to refine the actual questions from the brainstorming activity before they are ready to include in your business alignment meeting agenda.)
    3. Document both your brainstorming activity and your final results in Jump – Phase 2 Tools and Templates Compendium, Tab 2.3 Feedback. The brainstorming questions can be used in the future as your VMI matures and your feedback transforms from informal to formal. The final results will be used in Steps 2.4 and 3.5.

    Download the Info-Tech Jump – Phase 2 Tools and Templates Compendium

    Input

    • Brainstorming

    Output

    • Feedback questions to include with the business alignment meeting agenda

    Materials

    • Jump – Phase 2 Tools and Templates Compendium, Tab 2.3 Feedback

    Participants

    • VMI team
    • Applicable stakeholders and executives (as needed)

    Step 2.4: Business alignment meeting agenda

    Craft an agenda that meets the needs of the VMI.

    A business alignment meeting (BAM) is a great, multi-faceted tool to ensure the customer and the vendor stay focused on what is important to the customer at a high level. BAMs are not traditional “operational” meetings where the parties get into the details of the contracts, deal with installation problems, address project management issues, or discuss specific cost overruns. The main focus of the BAM is the scorecard (see Step 2.3), but other topics are discussed and other purposes are served. For example, you can use the BAM to develop the relationship with the vendor’s leadership team so that if escalation is ever needed, your organization is more than just a name on a spreadsheet or customer list; you can learn about innovations the vendor is working on (without the meeting turning into a sales call); you can address high-level performance trends and request corrective action as needed; you can clarify your expectations; you can educate the vendor about your industry, culture, and organization; and you can learn more about the vendor.

    As you build your BAM agenda, someone in your organization may say, “Oh, that’s just a quarterly business review (QBR) or top-to-top meeting.” However, in most instances, an existing QBR or top-to-top meeting is not the same as a BAM. Using the term QBR or top-to-top meeting instead of BAM can lead to confusion internally. The VMI may say to the business unit, Procurement, or another department, “We’re going to start running some QBRs for our strategic vendors.” The typical response is, “There’s no need to do that. We already run QBRs/top-to-top meetings with our important vendors.” This may be accompanied by an invitation to join their meeting, where you may be an afterthought, have no influence, and get five minutes at the end to talk about your agenda items. Keep your BAM separate so that it meets your needs.

    Step 2.4: Business alignment meeting agenda (cont.)

    Craft an agenda that meets the needs of the VMI.

    As previously noted, using the term BAM more accurately depicts the nature of the VMI meeting and prevents confusion internally with other meetings already occurring. In addition, hosting the BAM yourself rather than piggybacking onto another meeting ensures that the VMI’s needs are met. The VMI will set and control the BAM agenda and determine the invite list for internal personnel and vendor personnel. As you may have figured out by now, having the right customer and vendor personnel attend will be essential.

    BAMs are conducted at the vendor level … not the contract level. As a result, the frequency of the BAMs will depend on the vendor’s classification category (see Steps 2.1 and 3.1). General frequency guidelines are provided below, but they can be modified to meet your goals:

    • Commodity Vendors – Not applicable
    • Operational Vendors – Biannually or annually
    • Strategic Vendors – Quarterly
    • Tactical Vendors – Quarterly or biannually

    BAMs can help you achieve some additional benefits not previously mentioned:

    • Foster a collaborative relationship with the vendor.
    • Avoid erroneous assumptions by the parties.
    • Capture and provide a record of the relationship (and other items) over time.

    Step 2.4: Business alignment meeting agenda (cont.)

    Craft an agenda that meets the needs of the VMI.

    As with any meeting, building the proper agenda will be one of the keys to an effective and efficient meeting. A high-level BAM agenda with sample topics is set out below:

    BAM Agenda

    • Opening Remarks
      • Welcome and introductions
      • Review of previous minutes
    • Active Discussion
      • Review of open issues
      • Scorecard and feedback
      • Current status of projects to ensure situational awareness by the vendor
      • Roadmap/strategy/future projects
      • Accomplishments
    • Closing Remarks
      • Reinforce positives (good behavior, results, and performance, value added, and expectations exceeded)
      • Recap
    • Adjourn

    2.4.1: Business alignment meeting agenda

    20-45 minutes

    1. Meet with the participants and review the sample agenda in Jump – Phase 2 Tools and Templates Compendium, Tab 2.4 BAM Agenda.
    2. Using the sample agenda as inspiration and brainstorming activities as needed, create a BAM agenda tailored to your needs.
      1. Select the items from the sample agenda applicable to your situation.
      2. Add any items required based on your brainstorming.
      3. Add the feedback questions identified during Activity 2.3.2 and documented in Jump – Phase 2 Tools and Templates Compendium, Tab 2.3 Feedback.
    3. Gain input and approval from sponsors, stakeholders, and executives as required or appropriate.
    4. Document the final BAM agenda in Jump – Phase 2 Tools and Templates Compendium, Tab 2.4 BAM Agenda.

    Download the Info-Tech Jump – Phase 2 Tools and Templates Compendium

    Input

    • Brainstorming
    • Jump – Phase 2 Tools and Templates Compendium, Tab 2.3 Feedback

    Output

    • Configured BAM agenda

    Materials

    • Jump – Phase 2 Tools and Templates Compendium, Tab 2.4 BAM Agenda

    Participants

    • VMI team
    • Applicable stakeholders and executives (as needed)

    Step 2.5: Relationship alignment document

    Draft a document to convey important VMI information to your vendors.

    Throughout this blueprint, alignment is mentioned directly (e.g. business alignment meetings [Steps 2.4 and 3.5]) or indirectly implied. Ensuring you and your vendors are on the same page, have clear and transparent communication, and understand each other’s expectations is critical to fostering strong relationships. One component of gaining and maintaining alignment with your vendors is the relationship alignment document (RAD). Depending upon the scope of your VMI and what your organization already has in place, your RAD will fill in the gaps on various topics.

    Early in the VMI’s maturation, the easiest approach is to develop a short document (i.e. 1 page) or a pamphlet (i.e. the classic trifold) describing the rules of engagement when doing business with your organization. The RAD can convey expectations, policies, guidelines, and other items. The scope of the document will depend on 1) what you believe is important for the vendors to understand, and 2) any other similar information already provided to the vendors.

    The first step to drafting a RAD is to identify what information vendors need to know to stay on your good side. For example, you may want vendors to know about your gift policy (e.g. employees may not accept gifts from vendors above a nominal value such as a pen or mousepad). Next, compare your list of what vendors need to know and determine if the content is covered in other vendor-facing documents such as a vendor code of conduct or your website’s vendor portal. Lastly, create your RAD to bridge the gap between what you want and what is already in place. In some instances, you may want to include items from other documents to reemphasize them with the vendor community.

    Info-Tech Insight

    The RAD can be used with all vendors regardless of classification category. It can be sent directly to the vendors or given to them during vendor orientation (see Step 3.3)

    2.5.1: Relationship alignment document

    1-4 hours

    1. Meet with the participants and review the RAD sample and checklist in Jump – Phase 2 Tools and Templates Compendium, Tab 2.5 Relationship Alignment Doc.
    2. Determine:
      1. Whether you will create one RAD for all vendors or one RAD for strategic vendors and another RAD for tactical and operational vendors; whether you will create a RAD for commodity vendors.
      2. The concepts you want to include in your RAD(s).
      3. The format for your RAD(s) – traditional, pamphlet, or other.
      4. Whether signoff or acknowledgement will be required by the vendors.
    3. Draft your RAD(s) and work with other internal areas such as Marketing to create a consistent brand for the RADS and Legal to ensure consistent use and preservation of trademarks or other intellectual property rights and other legal issues.
    4. Review other vendor-facing documents (e.g. supplier code of conduct, onsite safety and security protocols) for consistencies between them and the RAD(s).
    5. Obtain signoff on the RAD(s) from stakeholders, sponsors, executives, Legal, Marketing, and others as needed.

    Download the Info-Tech Jump – Phase 2 Tools and Templates Compendium

    Input

    • Brainstorming
    • Vendor-facing documents, policies, and procedures

    Output

    • Completed relationship alignment document(s)

    Materials

    • Jump – Phase 2 Tools and Templates Compendium, Tab 2.5 Relationship Alignment Doc

    Participants

    • VMI team
    • Marketing, as needed
    • Legal, as needed

    Step 2.6: Vendor orientation

    Create a VMI awareness process to build bridges with your vendors.

    Vendor Orientation: 01 - Orientation; 02 - Reorientation; 03 - Debrief

    Your organization is unique. It may have many similarities with other organizations, but your culture, risk tolerance, mission, vision, and goals, finances, employees, and “customers” (those that depend on you) make it different. The same is true of your VMI. It may have similar principles, objectives, and processes to other organizations’ VMIs, but yours is still unique. As a result, your vendors may not fully understand your organization and what vendor management means to you.

    Vendor orientation is another means to helping you gain and maintain alignment with your important vendors, educate them on what is important to you, and provide closure when/if the relationship with the vendor ends. Vendor orientation is comprised of three components, each with a different function:

    • Orientation
    • Reorientation
    • Debrief

    Vendor orientation focuses on the vendor management pieces of the puzzle (e.g. the scorecard process) rather than the operational pieces (e.g. setting up a new vendor in the system to ensure invoices are processed smoothly).

    Step 2.6: Vendor orientation (cont.)

    Create a VMI awareness process to build bridges with your vendors.

    Vendor Orientation: 01 - Orientation

    Orientation

    Orientation is conceptually similar to new hire orientation for employees at your organization. Generally conducted as a meeting, orientation provides your vendors with the information they need to be successful when working with your organization. Sadly, this is often overlooked by customers; it can take months or years for vendors to figure it out by themselves. By controlling the narrative and condensing the timeline, vendor relationships and performance improve more rapidly.

    A partial list of topics for orientation is set out below:

    • Your organization’s structure
    • Your organization’s culture
    • Your relationship expectations
    • Your governances (VMI and other)
    • Their vendor classification designation (commodity, operational, strategic, or tactical)
    • The scorecard process
    • Business alignment meetings
    • Relationship alignment documents

    In short, this is the first step toward building (or continuing to build) a robust, collaborative, mutually beneficial relationship with your important vendors.

    Step 2.6: Vendor orientation (cont.)

    Create a VMI awareness process to build bridges with your vendors.

    Vendor Orientation: 02 - Reorientation

    Reorientation

    Reorientation is either identical or similar to orientation, depending upon the circumstances. Reorientation occurs for a number of reasons, and each reason will impact the nature and detail of the reorientation content. Reorientation occurs whenever:

    • There is a significant change in the vendor’s products or services.
    • The vendor has been through a merger, acquisition, or divestiture.
    • A significant contract renewal/renegotiation has recently occurred.
    • Sufficient time has passed from orientation; commonly 2 to 3 years.
    • The vendor has been placed in a “performance improvement plan” or “relationship improvement plan” protocol.
    • Significant turnover has occurred within your organization (executives, key stakeholders, and/or VMI personnel).
    • Substantial turnover has occurred at the vendor at the executive or account management level.
    • The vendor has changed vendor classification categories after the most current classification.

    As the name implies, the goal is to refamiliarize the vendor with your current VMI situation, governances, protocols, and expectations. The drivers for reorientation will help you determine its scope, scale, and frequency.

    Step 2.6: Vendor orientation (cont.)

    Create a VMI awareness process to build bridges with your vendors.

    Vendor Orientation: 03 - Debrief

    Debrief

    To continue the analogy from orientation, debrief is similar to an exit interview for an employee when their employment is terminated. In this case, debrief occurs when the vendor is no longer an active vendor with your organization – all contracts have terminated or expired, and no new business with the vendor is anticipated within the next three months.

    Similar to orientation and reorientation, debrief activities will be based on the vendor’s classification category within the COST model. Strategic vendors don’t go away very often; usually, they transition to operational or tactical vendors first. However, if a strategic vendor is no longer providing products or services to you, dig a little deeper into their experiences and allocate extra time for the debrief meeting.

    The debrief should provide you with feedback on the vendor’s experience with your organization and their participation in your VMI. In addition, it can provide closure for both parties since the relationship is ending. Be careful that the debrief does not turn into a finger-pointing meeting or therapy session for the vendor. It should be professional and productive; if it is going off the rails, terminate the meeting before more damage can occur.

    End the debrief on a high note if possible. Thank the vendor, highlight its key contributions, and single out any personnel who went above and beyond. You never know when you will be doing business with this vendor again – don’t burn bridges!

    Step 2.6: Vendor orientation (cont.)

    Create a VMI awareness process to build bridges with your vendors.

    • As you create your vendor orientation materials, focus on the message you want to convey.
    • For orientation and reorientation:
      • What is important to you that vendors need to know?
      • What will help the vendors understand more about your organization … your VMI?
      • What and how are you different from other organizations overall … in your “industry”?
      • What will help them understand your expectations?
      • What will help them be more successful?
      • What will help you build the relationship?
    • For debrief:
      • What information or feedback do you want to obtain?
      • What information or feedback to you want to give?
    • The level of detail you provide strategic vendors during orientation and reorientation may be different from the information you provide tactical and operational vendors. Commodity vendors are not typically involved in the vendor orientation process. The orientation meetings can be conducted on a one-to-one basis for strategic vendors and a one-to-many basis for operational and tactical vendors; reorientation and debrief are best conducted on a one-to-one basis. Lastly, face-to-face or video meetings work best for vendor orientation; voice-only meetings, recorded videos, or distributing only written materials seldom hit their mark or achieve the desired results.

    2.6.1: Vendor orientation

    1 to several hours

    1. Meet with the participants and review the Phase Tools and Templates Compendium, Tab 2.6 Vendor Orientation.
      1. Use the orientation checklist to identify the materials you want to create for your orientation meetings.
      2. Use the reorientation checklist to identify the materials you want to create for your reorientation meetings.
    2. The selections can be made by classification category (i.e. different items can apply to strategic, operational, and tactical vendors).
    3. Create the materials and seek input and/or approval from sponsors, stakeholders, and executives as needed.
    4. Use the debrief section of the tool to create an agenda, list the questions you want to ask vendors, and list information you want to provide to vendors. The agenda, questions, and information can be segregated by classification category.

    Download the Info-Tech Jump – Phase 2 Tools and Templates Compendium

    Input

    • Brainstorming

    Output

    • Agendas and materials for orientation, reorientation, and debrief

    Materials

    • Phase Tools and Templates Compendium, Tab 2.6 Vendor Orientation

    Participants

    • VMI team

    Step 2.7: Job descriptions

    Ensure new and existing job descriptions are up to date.

    Based on your work product from Steps 1.1-1.9, it’s time to start drafting new or modifying existing job descriptions applicable to the VMI team members. Some of the VMI personnel may be dedicated full-time to the VMI, while others may be supporting the VMI on a part-time basis. At a minimum, create or modify your job descriptions based on the categories set out below. Remember to get the internal experts involved so that you stay true to your environment and culture.

    01 Title

    This should align overall with what the person will be doing and what the person will be responsible for. Your hands may be tied with respect to titles, but try to make them intuitively descriptive if possible.

    02 Duties

    This is the main portion of the job description. List the duties, responsibilities, tasks, activities, and results expected. Again, there may be some limitations imposed by your organization, but be as thorough as possible.

    03 Qualifications

    This tends to be a gray area for many organizations, with the qualifications, certifications, and experience desired expressed in “ranges” so that good candidates are not eliminated from consideration unnecessarily.

    2.7.1: Job descriptions

    1 to several hours

    1. Meet with the participants and review the VMI structure from Step 1.9.
      1. List the positions that require new job descriptions.
      2. List the positions that require updated job descriptions.
    2. Review the other Phase 1 work product and list the responsibilities, tasks, and functions that need to be incorporated into the new and updated job descriptions.
    3. Review the sample VMI job descriptions and sample VMI job description language in Jump – Phase 2 Tools and Templates Compendium, Tab 2.7 Job Descriptions, and identify language and concepts you want to include in the new and revised job descriptions.
    4. Using your template, draft the new job descriptions and modify the existing job descriptions to synchronize with the VMI structure. Work with other internal areas such as Human Resources to ensure cultural fit and compliance.
    5. Obtain input and signoff on the job descriptions from stakeholders, sponsors, executives, Human Resources, and others as needed.
    6. Document your final job descriptions in Jump – Phase 2 Tools and Templates Compendium, Tab 2.7 Job Descriptions.

    Download the Info-Tech Jump – Phase 2 Tools and Templates Compendium

    Input

    • Brainstorming
    • Existing job descriptions
    • Work product from Phase 1

    Output

    • Job descriptions for new positions
    • Updated job descriptions for existing positions

    Materials

    • Jump – Phase 2 Tools and Templates Compendium, Tab 2.7 Job Descriptions

    Participants

    • VMI team
    • Human Resources (as needed)
    • Applicable stakeholders and executives (as needed)

    Step 2.8: Policies and procedures

    Prepare policies and procedures for VMI functions.

    Policies and procedures are often thought of as boring documents that are 1) tedious to create, 2) seldom read after creation, and 3) only used to punish people when they do something “wrong.” However, when done well, these documents:

    • Communicate expectations.
    • Capture institutional knowledge.
    • Provide guidance for decision making.
    • Help workers avoid errors and minimize risk.
    • Ensure regulatory and organizational compliance.
    • List the steps required to achieve consistent results.

    Definitions of Policies and Procedures

    Policies and procedures are essential, but they are often confused with each other. A policy is a rule, guideline, or framework for making decisions. For example, in the vendor management space, you may want a policy indicating your organization’s view on gifts from vendors. A procedure is a set of instructions for completing a task or activity. For example, staying in the vendor management space, you may want a procedure to outline the process for classifying vendors.

    Step 2.8: Policies and procedures (cont.)

    Prepare policies and procedures for VMI functions.

    Start With Your Policy/Procedure Template or Create One for Consistency

    When creating policies and procedures, follow your template. If you don’t have one (or want to see if anything is missing from your template) the following list of potential components for your governance documents is provided.* Not every concept is required. Use your judgment and err on the side of caution when drafting; balance readability and helpfulness against over documenting and over complicating.

    • Descriptive Title
    • Policy Number
    • Brief Overview
    • Purpose
    • Scope
    • The Policy or Procedure
    • Definitions
    • Revision Date
    • History
    • Related Documents
    • Keywords

    Step 2.8: Policies and procedures (cont.)

    Prepare policies and procedures for VMI functions.

    Although they are not ever going to be compared to page-turning novels, policies and procedures can be improved by following a few basic principles. By following the guidelines set out below, your VMI policies and procedures will contribute to the effectiveness of your initiative.*

    • Use short sentences.
    • Organize topics logically.
    • Use white space liberally.
    • Use mandatory language.
    • Use gender-neutral terms.
    • Write with an active voice.
    • Avoid jargon when possible.
    • Use a consistent “voice” and tone.
    • Use pictures or diagrams when they will help.
    • Write in the same tense throughout the document.
    • Use icons and colors to designate specific elements.
    • Make sure links to other policies and procedures work.
    • Define all acronyms and jargon (when it must be used).
    • Avoid a numbering scheme with more than three levels.

    *Adapted in part from smartsheet.com

    Info-Tech Insight

    Drafting policies and procedures is an iterative process that requires feedback from the organization’s leadership team.

    2.8.1: Policies and procedures

    Several hours

    1. Meet with the participants and review the sample policies and procedures topics in Jump – Phase 2 Tools and Templates Compendium, Tab 2.8 Policies and Procedures.
    2. Determine:
      1. The concepts you want to include in your policies and procedures; brainstorm for any additional concepts you want to include.
      2. The format/template for your policies and procedures.
    3. Draft your policies and procedures based on the sample topics and your brainstorming activity. Work with other internal areas such as Legal and Human Resources to ensure cultural and environmental fit within your organization.
    4. Obtain input and signoff on the policies and procedures from stakeholders, sponsors, executives, Legal, Human Resources, and others as needed.
    5. Document your final policies and procedures in Jump – Phase 2 Tools and Templates Compendium, Tab 2.8 Policies and Procedures.
    6. Publish your policies and procedures and conduct training sessions or awareness sessions as needed.

    Download the Info-Tech Jump – Phase 2 Tools and Templates Compendium

    Input

    • Existing policies and procedures (if any)
    • Existing policies and procedures template (if any)
    • Scope
    • OIC chart
    • Process maps
    • Brainstorming

    Output

    • VMI policies and procedures

    Materials

    • Jump – Phase 2 Tools and Templates Compendium, Tab 2.8 Policies and Procedures

    Participants

    • VMI team
    • Legal and Human Resources (as needed)
    • Applicable stakeholders and executives (as needed)

    Step 2.9: 3-year roadmap

    Plot your path at a high level.

    The VMI exists in many planes concurrently: 1) it operates both tactically and strategically, and 2) it focuses on different timelines or horizons (e.g. the past, the present, and the future). Creating a 3-year roadmap facilitates the VMI’s ability to function effectively across these multiple landscapes.

    The VMI roadmap will be influenced by many factors. The work product from Phase 1: Plan, input from executives, stakeholders, and internal clients, and the direction of the organization as a whole are great sources of information as you begin to build your roadmap.

    To start, identify what you would like to accomplish in Year 1. This is arguably the easiest year to complete: budgets are set (or you have a good idea what the budget will look like), personnel decisions have been made, resources have been allocated, and other issues impacting the VMI are known with a higher degree of certainty than any other year. This does not mean things won’t change during the first year of the VMI, but expectations are usually lower and the short event horizon makes things more predictable during the Year-1 ramp-up period.

    Years 2 and 3 are more tenuous, but the process is the same: identify what you would like to accomplish or roll out in each year. Typically, the VMI maintains the Year 1 plan into subsequent years and adds to the scope or maturity. For example, you may start Year 1 with BAMs and scorecards for three of your strategic vendors; during Year 2, you may increase that to five vendors; and during Year 3, you may increase that to nine vendors. Or, you may not conduct any market research during Year 1, waiting to add it to your roadmap in Year 2 or 3 as you mature.

    Breaking things down by year helps you identify what is important and the timing associated with your priorities. A conservative approach is recommended. It is easy to overcommit, but the results can be disastrous and painful.

    2.9.1: 3-year roadmap

    45-90 minutes

    1. Meet with the participants and decide how to coordinate Year 1 of your 3-year roadmap with your existing fiscal year or reporting year. Year 1 may be shorter or longer than a calendar year.
    2. Review the VMI activities listed in Jump – Phase 2 Tools and Templates Compendium, Tab 2.9 3-Year Roadmap. Use brainstorming and your prior work product from Phase 1 and Phase 2 to identify additional items for the roadmap and add them at the bottom of the spreadsheet.
    3. Starting with the first activity, determine when that activity will begin and put an X in the corresponding column; if the activity is not applicable, leave it blank or insert N/A.
    4. Go back to the top of the list and add information as needed.
      1. For any Year-1 or Year-2 activities, add an X in the corresponding columns if the activity will be expanded/continued in subsequent periods (e.g. if a Year 2 activity will continue in Year 3, put an X in Year 3 as well).
      2. Use the comments column to provide clarifying remarks or additional insights related to your plans or “X’s.” For example, “Scorecards begin in Year 1 with three vendors and will roll out to five vendors in Year 2 and nine vendors in Year 3.”
    5. Obtain signoff from stakeholders, sponsors, and executives as needed.

    Download the Info-Tech Jump – Phase 2 Tools and Templates Compendium

    Input

    • Phase 1 work product
    • Steps 2.1-2.8 work product
    • Brainstorming

    Output

    • High level 3-year roadmap for the VMI

    Materials

    • Jump – Phase 2 Tools and Templates Compendium, Tab 2.9 3-Year Roadmap

    Participants

    • VMI team
    • Applicable stakeholders and executives (as needed)

    Step 2.10: 90-day plan

    Pave your short-term path with a series of detailed quarterly plans.

    Now that you have prepared a 3-year roadmap, it’s time to take the most significant elements from the first year and create action plans for each three-month period. Your first 90-day plan may be longer or shorter if you want to sync to your fiscal or calendar quarters. Aligning with your fiscal year can make it easier for tracking and reporting purposes; however, the more critical item is to make sure you have a rolling series of four 90-day plans to keep you focused on the important activities and tasks throughout the year.

    The 90-day plan is a simple project plan that will help you measure, monitor, and report your progress. Use the Info-Tech tool to help you track:

    • Activities
    • Tasks comprising each activity
    • Who will be performing the tasks
    • An estimate of the time required per person per task
    • An estimate of the total time to achieve the activity
    • A due date for the activity
    • A priority of the activity

    The first 90-day plan will have the greatest level of detail and should be as thorough as possible; the remaining three 90-day plans will each have less detail for now. As you approach the middle of the first 90-day plan, start adding details to the next 90-day plan; toward the end of the first quarter add a high-level 90-day plan to the end of the chain. Continue repeating this cycle each quarter and consult the 3-year roadmap and the leadership team as necessary.

    90 Days

    2.10.1: 90-day plan

    45-90 minutes

    1. Meet with the participants and decide how to coordinate the first 90-day plan with your existing fiscal year or reporting cycles. Your first plan may be shorter or longer than 90 days.
    2. Looking at the Year 1 section of the 3-year roadmap, identify the activities that will be started during the next 90 days.
    3. Using the Jump – Phase 2 Tools and Templates Compendium, Tab 2.10 90-Day Plan, enter the following information into the spreadsheet for each activity to be accomplished during the next 90 days:
      1. Activity description
      2. Tasks required to complete the activity (be specific and descriptive)
      3. The people who will be performing each task
      4. The estimated number of hours required to complete each task
      5. The start date and due date for each task or the activity
    4. Validate the tasks are a complete list for each activity and the people performing the tasks have adequate time to complete the tasks by the due date(s).
    5. Assign a priority to each activity.

    Download the Info-Tech Jump – Phase 2 Tools and Templates Compendium

    Input

    • 3-year roadmap
    • Phase 1 work product
    • Steps 2.1-2.9 work product
    • Brainstorming

    Output

    • Detailed plan for the VMI for the next quarter or 90 days

    Materials

    • Jump – Phase 2 Tools and Templates Compendium, Tab 2.10 90-Day Plan

    Participants

    • VMI team
    • Applicable stakeholders and executives (as needed)

    Step 2.11: Quick wins

    Identify potential short-term successes to gain momentum and show value immediately.

    As the final step in the timeline trilogy, you are ready to identify some quick wins for the VMI. Using the first 90-day plan and a brainstorming activity, create a list of things you can do in 15 to 30 days that add value to your initiative and build momentum.

    As you evaluate your list of potential candidates, look for things that:

    • Are achievable within the stated timeline.
    • Don’t require a lot of effort.
    • Involve stopping a certain process, activity, or task; this is sometimes known as a “stop doing stupid stuff” approach.
    • Will reduce or eliminate inefficiencies; this is sometimes known as the war on waste.
    • Have a moderate to high impact or bolster the VMI’s reputation.

    As you look for quick wins, you may find that everything you identify does not meet the criteria. That’s ok … don’t force the issue. Return your focus to the 90-day plan and 3-year roadmap, and update those documents if the brainstorming activity associated with this Step 2.11 identified anything new.

    2.11.1: Quick wins

    15-30 minutes

    1. Meet with the participants and review the 3-year roadmap and 90-day plan. Determine if any item on either document can be completed:
      1. Quickly (30 days or less)
      2. With minimal effort
      3. To provide or show moderate to high levels of value or provide the VMI with momentum
    2. Brainstorm to identify any other items that meet the criteria in step 1 above.
    3. Compile a comprehensive list of these items and select up to five to pursue.
    4. Document the list in the Jump – Phase 2 Tools and Templates Compendium, Tab 2.11 Quick Wins.
    5. Manage the quick wins list and share the results with the VMI team and applicable stakeholders and executives.

    Download the Info-Tech Jump – Phase 2 Tools and Templates Compendium

    Input

    • 3-year roadmap
    • 90-day plan
    • Brainstorming

    Output

    • A list of activities that require low levels of effort to achieve moderate to high levels of value in a short period

    Materials

    • Jump – Phase 2 Tools and Templates Compendium, Tab 2.11 Quick Wins

    Participants

    • VMI team

    Step 2.12: Reports

    Construct your reports to resonate with your audience.

    Issuing reports is a critical piece of the VMI since the VMI is a conduit of information for the organization. It may be aggregating risk data from internal areas, conducting vendor research, compiling performance data, reviewing market intelligence, or obtaining relevant statistics, feedback, comments, facts, and figures from other sources. Holding onto this information minimizes the impact a VMI can have on the organization; however, the VMI’s internal clients, stakeholders, and executives can drown in raw data and ignore it completely if it is not transformed into meaningful, easily-digested information.

    Before building a report, think about your intended audience:

    • What information are they looking for … what will help them understand the big picture?
    • What level of detail is appropriate, keeping in mind the audience may not be like-minded?
    • What items are universal to all of the readers and what items are of interest to one or two readers?
    • How easy or hard will it be to collect the data … who will be providing it, how time consuming will it be?
    • How accurate, valid, and timely will the data be?
    • How frequently will each report need to be issued?

    Step 2.12: Reports (cont.)

    Construct your reports to resonate with your audience.

    Use the following guidelines to create reports that will resonate with your audience:

    • Value information over data, but sometimes data does have a place in your report.
    • Use pictures, graphics, and other representations more than words, but words are often necessary in small, concise doses.
    • Segregate your report by user; for example, general information up top, CIO information below that on the right, CFO information to the left of CIO information, etc.
    • Send a draft report to the internal audience and seek feedback, keeping in mind you won’t be able to cater to or please everyone.

    Step 2.12: Reports (cont.)

    Construct your reports to resonate with your audience.

    The report’s formatting and content display can make or break your reports.*

    • Make the report look inviting and easy to read. Use:
      • Short paragraphs and bullet points.
      • A simple layout and uncluttered, wide margins.
      • Minimal boldface, underline, or italics to attract the readers’ attention.
      • High contrast between text and background.
    • Charts, graphs, and infographics should be intuitive and tell the story on their own.
    • Make it easy to peruse the report for topics of interest.
      • Maintain consistent design features.
      • Use impactful, meaningful headings and subheadings.
      • Include callouts to draw attention to important high-level information.
    • Demonstrate the impact of the accomplishments or success stories when appropriate.
    • Finish with a simple concise summary when appropriate. Consider adding:
      • Key points for the reader to takeaway.
      • Action items or requests.
      • Plans for next reporting period.

    *Sources: Adapted and compiled in part from: designeclectic.com, ahrq.gov, and 60secondmarketer.com.

    2.12.1: Reports

    15-45 minutes

    1. Meet with the participants and review the applicable work product from Phases 1 and 2; identify qualitative and quantitative items the VMI measures, monitors, tracks, or aggregates.
    2. Determine which items will be reported and to whom (by category):
      1. Internally to personnel within the VMI
      2. Internally to personnel outside the VMI
      3. Externally to vendors
    3. Within each category above, determine your intended audiences/recipients. For example, you may have a different list of recipients for a risk report than you do a scorecard summary report. This will help you identify the number of reports required.
    4. Create a draft structure for each report based on the audience and the information being conveyed. Determine the frequency of each report and person responsible for creating for each report.
    5. Document your final choices in Jump – Phase 2 Tools and Templates Compendium, Tab 2.12 Reports.

    Download the Info-Tech Jump – Phase 2 Tools and Templates Compendium

    Input

    • Brainstorming
    • Phase 1 work product
    • Steps 2.1-2.11 work product

    Output

    • A list of reports used by the VMI
    • For each report:
    • The conceptual content
    • A list of who will receive or have access
    • A creation/distribution frequency

    Materials

    • Jump – Phase 2 Tools and Templates Compendium, Tab 2.12 Reports

    Participants

    • VMI team
    • Applicable stakeholders and executives (as needed)

    Phase 3: Run

    Implement Your Processes and Leverage Your Tools and Templates

    Phase 1 Phase 2 Phase 3 Phase 4
    1.1 Mission Statement and Goals
    1.2 Scope
    1.3 Strengths and Obstacles
    1.4 Roles and Responsibilities
    1.5 Process Mapping
    1.6 Charter
    1.7 Vendor Inventory
    1.8 Maturity Assessment
    1.9 Structure

    2.1 Classification Model
    2.2 Risk Assessment Tool
    2.3 Scorecards and Feedback
    2.4 Business Alignment Meeting Agenda
    2.5 Relationship Alignment Document
    2.6 Vendor Orientation
    2.7 Job Descriptions
    2.8 Policies and Procedures
    2.9 3-Year Roadmap
    2.10 90-Day Plan
    2.11 Quick Wins
    2.12 Reports

    3.1 Classify Vendors
    3.2 Conduct Internal “Kickoff” Meeting
    3.3 Conduct Vendor Orientation
    3.4 Compile Scorecards
    3.5 Conduct Business Alignment Meetings
    3.6 Work the 90-Day Plan
    3.7 Manage the 3-Year Roadmap
    3.8 Measure and Monitor Risk
    3.9 Issue Reports
    3.10 Develop/Improve Vendor Relationships
    3.11 Contribute to Other Processes

    4.1 Assess Compliance
    4.2 Incorporate Leading Practices
    4.3 Leverage Lessons Learned
    4.4 Maintain Internal Alignment
    4.5 Update Governances

    This phase will walk you through the following activities:

    Begin operating the VMI. The main outcomes from this phase are guidance and the steps required to implement your VMI.

    This phase involves the following participants:

    • VMI team
    • Applicable stakeholders and executives
    • Others as needed

    Jump Start Your Vendor Management Initiative

    Phase 3: Run

    Implement your processes and leverage your tools and templates.

    All of the hard work invested in Phase 1: Plan and Phase 2: Build begins to pay off in Phase 3: Run. It’s time to stand up your VMI and ensure that the proper level of resources is devoted to your vendors and the VMI itself. There’s more hard work ahead, but the foundational elements are in place. This doesn’t mean there won’t be adjustments and modifications along the way, but you are ready to use the tools and templates in the real world; you are ready to begin reaping the fruits of your labor.

    Phase 3: Run guides you through the process of collecting data, monitoring trends, issuing reports, and conducting effective meetings to:

    • Manage risk better.
    • Improve vendor performance.
    • Improve vendor relationships.
    • Identify areas where the parties can improve.
    • Improve communication between the parties.
    • Increase the value proposition with your vendors.

    Step 3.1: Classify vendors

    Begin classifying your top 25 vendors by spend.

    Step 3.1 sets the table for many of the subsequent steps in Phase 3: Run. The results of your classification process will determine: which vendors go through the scorecarding process (Step 3.4); which vendors participate in BAMs (Step 3.5); the nature and content of the vendor orientation activities (Step 3.3); which vendors will be part of the risk measurement and monitoring process (Step 3.8); which vendors will be included in the reports issued by the VMI (Step 3.9); and which vendors you will devote relationship-building resources to (Step 3.10).

    As you begin classifying your vendors, Info-Tech recommends using an iterative approach initially to validate the results from the classification model you configured in Step 2.1.

    1. Using the information from the Vendor Inventory tab (Step 1.7), identify your top 25 vendors by spend.
    2. Run your top 10 vendors by spend through the classification model and review the results.
      1. If the results are what you expected and do not contain any significant surprises, go to next page.
      2. If the results are not what you expected or contain significant surprises, look at the configuration page of the tool (Tab 1) and adjust the weights or the spend categories slightly. Be cautious in your evaluation of the results before modifying the configuration page – some legitimate results are unexpected or surprising based on bias. If you modify the weighting, review the new results and repeat your evaluation. If you modify the spend categories, review the answers on the vendor tabs to ensure that the answers are still accurate; review the new results and repeat your evaluation.

    Step 3.1: Classify vendors (cont.)

    Review your results and adjust the classification tool as needed.

    1. Run your top 11 through 25 vendors by spend through the classification model and review the results. Identify any unexpected results or surprises. Determine if further configuration makes sense and repeat the process outlined in 2.b, previous page, as necessary. If no further modifications are required, continue to 4, below.
    2. Share the preliminary results with the leadership team, executives, and stakeholders to obtain their approval or adjustments to the results.
      1. They may have questions and want to understand the process before approving the results.
      2. They may request that you move a vendor from one quadrant to another based on your organization’s roadmap, the vendor’s roadmap, or other information not available to you.
    3. Identify the vendors that will be part of the VMI at this stage – how many and which ones. Based on this number and the VMI’s scope (Step 1.2), make sure you have the resources necessary to accommodate the number of vendors participating in the VMI. Proceed cautiously and gradually increase the number of vendors participating in the VMI.

    Step 3.1: Classify vendors (cont.)

    Finalize the results and update VMI tools and templates.

    1. Update the Vendor Inventory tab (Step 1.7) to indicate the current classification status for the top 25 vendors by spend. Once your vendors have been classified, you can sort the Vendor Inventory tab by classification status to see all the vendors in that category at once.
    2. Review your 3-year roadmap (Step 2.9) and 90-day plans (Step 2.10) to determine if any modifications are needed to the activities and timelines.

    Additional classification considerations:

    • You should only have a few vendors that fit in the strategic category. As a rough guideline, no more than 5% to 10% of your IT vendors should end up in the strategic category. If you have a large number of vendors, even 5% may be too many. The classification model is an objective start to the classification process, but common sense must prevail over the “math” at the end of the day.
    • At this point, there is no need to go beyond the top 25 by spend. Most VMIs starting out can’t handle more than three to five strategic vendors initially. Allow the VMI to run a pilot program with a small sample size, work out any bugs, make adjustments, and then ramp up the VMI’s rollout in waves. Vendors can be added quarterly, biannually, or annually, depending upon the desired goals and available resources.

    Step 3.1: Classify vendors (cont.)

    Align your vendor strategy to your classification results.

    As your VMI matures, additional vendors will be part of the VMI. Review the table below and incorporate the applicable strategies into your deployment of vendor management principles over time. Stay true to your mission, goals, and scope, and remember that not all of your vendors are of equal importance.

    Operational Strategic
    • Focus on spend containment
    • Concentrate on lowering total cost of ownership
    • Invest moderately in cultivating the relationship
    • Conduct BAMs biannually or annually
    • Compile scorecards quarterly or biannually
    • Identify areas for performance and cost improvement
    • Focus on value, collaboration, and alignment
    • Review market intelligence for the vendor’s industry
    • Invest significantly in cultivating the relationship
    • Initiate executive-to-executive relationships
    • Conduct BAMs quarterly
    • Compile scorecards quarterly
    • Understand how the vendors view your organization

    Commodity

    Tactical

    • Investigate vendor rationalization and consolidation
    • Negotiate for the best-possible price
    • Leverage competition during negotiations
    • Streamline the purchasing and payment process
    • Allocate minimal VMI resources
    • Assign the lowest priority for vendor management metrics
    • Conduct risk assessments biannually or annually
    • Cultivate a collaborative relationship based on future growth plans or potential with the vendor
    • Conduct BAMs quarterly or biannually
    • Compile scorecards quarterly
    • Identify areas of performance improvement
    • Leverage innovation and creative problem solving

    Step 3.1: Classify vendors (cont.)

    Be careful when using the word “partner” with your strategic and other vendors.

    For decades, vendors have used the term “partner” to refer to the relationship they have with their clients and customers. In many regards, this is often an emotional ploy used by the vendors to get the upper hand. To fully understand the terms “partner” and “partnership” let’s evaluate them through two more-objective, less-cynical lenses.

    If you were to talk to your in-house or outside legal counsel, you may be told that partners share in profits and losses, and they have a fiduciary obligation to each other. Unless there is a joint venture between the parties, you are unlikely to have a partnership with a vendor from this perspective.

    What about a “business” partnership … one that doesn’t involve sharing profits and losses? What would that look like? Here are some indicators of a business partnership (or preferably a strategic alliance):

    • Trust and transparent communication exist.
    • You have input into the vendor’s roadmap for products and services.
    • The vendor is aligned with your desired outcomes and helps you achieve success.
    • You and the vendor are accountable for actions and inactions, with both parties being at risk.
    • There is parity in the peer-to-peer relationships between the organizations (e.g. C-Level to C-Level).
    • The vendor provides transparency in pricing models and proactively suggests ways for you to reduce costs.
    • You and the vendor work together to make each party better, providing constructive feedback on a regular basis.
    • The vendor provides innovative suggestions for you to improve your processes, performance, the bottom line, etc.
    • Negotiations are not one-sided; they are meaningful and productive, resulting in an equitable distribution of money and risk.

    Step 3.1: Classify vendors (cont.)

    Understand the implications and how to leverage the words “partner” and “partnership.”

    By now you might be thinking, “What’s all the fuss? Why does it matter?” At Info-Tech, we’ve seen firsthand how referring to the vendor as a partner can have the following impact:

    • Confidences are disclosed unnecessarily.
    • Negotiation opportunities and leverage are lost.
    • Vendors no longer have to earn the customer’s business.
    • Vendor accountability is missing due to shared responsibilities.
    • Competent skilled vendor resources are assigned to other accounts.
    • Value erodes over time since contracts are renewed without being competitively sourced.
    • One-sided relationships are established, and false assurances are provided at the highest levels within the customer organization.

    Proceed with caution when using partner or partnership with your vendors. Understand how your organization benefits from using these terms and mitigate the negatives outlined above by raising awareness internally to ensure people understand the psychology behind the terms. Finally, use the term to your advantage when warranted by referring to the vendor as a partner when you want or need something that the vendor is reluctant to provide. Bottom line: Be strategic in how you refer to vendors and know the risks.

    Step 3.2: Conduct internal “kickoff” meeting

    Raise awareness about the VMI and its mission, vision, and goals.

    To be effective, your VMI needs executive support, a clear vision, appropriate governances and tools, personnel with the right skills, and other items discussed in this blueprint. However, the VMI doesn’t exist in a vacuum … it can’t sit back and be reactive. As part of being proactive, the VMI must be aware of its brand and “market” its services. An effective way to market the VMI is to conduct an internal kickoff meeting. There are at least a couple of ways to do this:

    • Host a meeting for stakeholders, executives, and others who will be contributing to the VMI processes (but are not part of the VMI). The meeting can be part of a townhall or standalone meeting; it can be done live or via a recorded video.
    • Attend appropriate staff meetings and make your presentation.

    With either approach above or one of your choosing, keep in mind the following objectives for your kickoff meeting:

    • Make sure you provide a way for those in attendance to ask questions at that time and later. You want to create and foster a communication loop with the people who will be impacted by the VMI or participating with it.
    • Raise awareness of your existence and personnel. Tell the VMI’s story by sharing your mission statement, goals, and scope; this will help dispel (or confirm) rumors about the VMI that often lead to confusion and faulty assumptions.
    • As you share the VMI’s vision, connect the story to how the VMI will impact the organization and individuals and to how they can help. The VMI tends to be the least autonomous area within an organization; it needs the assistance of others to be successful. Convey an atmosphere of collaboration and appreciation for their help.

    Host a kickoff meeting annually to kickoff the new year. Remind people of your story, announce successes from the past year, and indicate what the future year holds. Keep it brief, make it personal for the audience, and help them connect the names of VMI personnel to faces.

    Step 3.3: Conduct vendor orientation

    Introduce your VMI to your top vendors.

    Based on the results from your vendor classification (Step 3.1) and your VMI deployment timeline, identify the vendors who will participate in the initial orientation meetings. Treat the orientation as a formal, required meeting for the vendors to attend. Determine the attendee list for your organization and the vendors, and send out invites. Ideally, you will want the account manager, a sales director or vice president, the “delivery” director or vice president, and an executive from the vendor in the meeting. From the customer side, you may need more than one or two people from the VMI to entice the vendor’s leadership team to attend; you may need attendance from your own leadership team to add weight or credibility to the meeting (unfortunately).

    Before going into the meeting, make sure everyone on your side knows their roles and responsibilities, and review the agenda. Control the agenda or the meeting is likely to get out of hand and turn into a sales call.

    Conduct orientation meetings even if the participating vendors have been doing business with you for several years. Don’t assume they know all about your organization and your VMI (even if their other clients have a VMI).

    Run two or three orientation meetings and then review the “results.” What needs to be modified? What lessons have you learned? Make any necessary adjustments and continue rolling out the orientation meetings.

    Early in the VMI’s deployment, reorientation and debrief may not be in play. As time passes, it is important to remember them! Use them when warranted to help with vendor alignment.

    Step 3.4: Compile scorecards

    Begin scoring your top vendors.

    The scorecard process typically is owned and operated by the VMI, but the actual rating of the criteria within the measurement categories is conducted by those with day-to-day interactions with the vendors, those using or impacted by the services and products provided by the vendors, and those with the skills to research other information on the scorecard (e.g. risk). Chances are one person will not be able to complete an entire scorecard by themselves. As a result, the scorecard process is a team sport comprising sub-teams where necessary.

    The VMI will compile the scores, calculate the final results, and aggregate all of the comments into one scorecard. There are two common ways to approach this task:

    1. Send out the scorecard template to those who will be scoring the vendor and ask them to return it when completed, providing them with a due date a few days before you actually need it; you’ll need time to compile, calculate, and aggregate.
    2. Invite those who will be scoring the vendor to a meeting and let the contributors use that time to score the vendors; make VMI team members available to answer questions and facilitate the process.

    Step 3.4: Compile scorecards (cont.)

    Gather input from stakeholders and others impacted by the vendors.

    Since multiple people will be involved in the scorecarding process or have information to contribute, the VMI will have to work with the reviewers to ensure that the right mix of data is provided. For example:

    • If you are tracking lawsuits filed by or against the vendor, one person from Legal may be able to provide that, but they may not be able to evaluate any other criteria on the scorecard.
    • If you are tracking salesperson competencies, multiple people from multiple areas may have valuable insights.
    • If you are tracking deliverable timeliness, several project managers may want to contribute across several projects.

    Where one person is contributing exclusively to limited criteria, make it easy for the person to identify the criteria they are to evaluate. When multiple people from the same functional area will provide insights, they can contribute individually (and the VMI will average their responses) or they can respond collectively after reaching consensus among themselves.

    After the VMI has compiled, calculated, and aggregated, share the results with executives, impacted stakeholders, and others who will be attending the BAM for that vendor. Depending upon the comments provided by internal personnel, you may need to create a sanitized version of the scorecard for the vendor.

    Make sure your process timeline has a buffer built in. You’ll be sending the final scorecard to the vendor three to five days before the BAM, and you’ll need some time to assemble the results. The scorecarding process can be perceived as a low-priority activity for people outside of the VMI, and other “priorities” will arise for them. Without a timeline buffer, the VMI may find itself behind schedule and unprepared due to things beyond its control.

    Step 3.5: Conduct business alignment meetings

    Determine which vendors will participate and how long the meetings will last.

    At their core, BAMs aren’t that different from any other meeting. The basics of running a meeting still apply, but there are a few nuances that apply to BAMs Set out below are leading practices for conducing your BAMs; adapt them to meet your needs and suit your environment.

    Who

    Initially, BAMs are conducted with the strategic vendors in your pilot program. Over time, you’ll add vendors until all of your strategic vendors are meeting with you quarterly. After that, roll out the BAMs to those tactical and operational vendors located close to the strategic quadrant in the classification model (Steps 2.1 and 3.1) and as VMI resources allow. It may take several years before you are holding regular BAMs with all of your strategic, tactical, and operational vendors.

    Duration

    Keep the length of your meetings reasonable. The first few with a vendor may need to be 60 to 90 minutes long. After that, you should be able to trim them to 45 to 60 minutes. The BAM does not have to fill the entire time. When you are done, you are done.

    Step 3.5: Conduct business alignment meetings (cont.)

    Identify who will be invited and send out invitations.

    Invitations

    Set up a recurring meeting whenever possible. Changes will be inevitable, but keeping the timeline regular works to your advantage. Also, the vendors included in your initial BAMs won’t change for twelve months. For the first BAM with a vendor, provide adequate notice; four weeks is sufficient in most instances, but calendars will fill up quickly for the main attendees from the vendor. Treat the meeting as significant and make sure your invitation reflects this. A simple meeting request will often be rejected, treated as optional, or ignored completely by the vendor’s leadership team (and maybe yours as well!).

    Invitees

    Internal invitees should include those with a vested interest in the vendor’s performance and the relationship. In addition, other functional areas may be invited based on need or interest. Be careful the attendee list doesn’t get too big. Based on this, internal BAM attendees often include representatives from IT, Sourcing/Procurement, and the applicable business units. At times, Finance and Legal are included.

    From the vendor’s side, strive to have decision makers and key leaders attend. The salesperson/account manager is often included for continuity, but a director or vice president of sales will have more insights and influence. The project manager is not needed at this meeting due to the nature of the meeting and its agenda; however, a director or vice president from the “product or service delivery” area is a good choice. Bottom line: get as high into the vendor’s organization as possible whenever possible; look at the types of contracts you have with that vendor to provide guidance on the type of people to invite.

    Step 3.5: Conduct business alignment meetings (cont.)

    Prepare for the meetings and maintain control.

    Preparation

    Send the scorecard and agenda to the vendor five days prior to the BAM. The vendor should provide you with any information you require for the meeting five days prior as well.

    Decide who will run the meeting. Some customers like to lead and others let the vendor present. How you craft the agenda and your preferences will dictate who runs the show.

    Make sure the vendor knows what materials it should bring to the meeting or have access to. This will relate to the agenda and any specific requests listed under the discussion points. You don’t want the vendor to be caught off guard and unable to discuss a matter of importance to you.

    Running the BAM

    Regardless of which party leads, make sure you manage the agenda to stay on topic. This is your meeting – not the vendor’s, not IT’s, not Procurement’s or Sourcing’s. Don’t let anyone hijack it.

    Make sure someone is taking notes. If you are running this virtually, consider recording the meeting. Check with your legal department first for any concerns, notices, or prohibitions that may impact your recording the session.

    As a reminder, this is not a sales call, and this is not a social activity. Innovation discussions are allowed and encouraged, but that can quickly devolve into a sales presentation. People can be friendly toward one another, but the relationship building should not overwhelm the other purposes.

    Step 3.5: Conduct business alignment meetings (cont.)

    Follow these additional guidelines to maximize your meetings.

    More Leading Practices

    • Remind everyone that the conversation may include items covered by various confidentiality provisions or agreements.
    • Publish the meeting minutes on a timely basis (within 48 hours).
    • Focus on the bigger picture by looking at trends over time; get into the details only when warranted.
    • Meet internally immediately beforehand to prepare – don’t go in cold; review the agenda and the roles and responsibilities for the attendees.
    • Physical meetings are better than virtual meetings, but travel constraints, budgets, and pandemics may not allow for physical meetings.

    Final Thoughts

    • When performance or the relationship is suffering, be constructive in your feedback and conversations rather than trying to assign blame; lead with the carrot rather than the stick.
    • Look for collaborative solutions whenever possible and avoid referencing the contract if possible. Communicate your willingness to help resolve outstanding issues.
    • Use inclusive language and avoid language that puts the vendor on the defensive.
    • Make sure that your meetings are not focused exclusively on the negative, but don’t paint a rosy picture where one doesn’t exist.
    • A vendor that is doing well should be commended. This is an important part of relationship building.

    Step 3.6: Work the 90-day plan

    Monitor your progress and share your results.

    Having a 90-day plan is a good start, but assuming the tasks on the plan will be accomplished magically or without any oversight can lead to failure. While it won’t take a lot of time to work the plan, following a few basic guidelines will help ensure the 90-day plan gets results and wasn’t created in vain.

    90-Day Plan: Activity 1; Activity 2; Activity 3; Activity 4; Activity 5
    1. Measure and track your progress against the initial/current 90-day plan at least weekly; with a short timeline, any delay can have a huge impact.
    2. If adjustments are needed to any elements of the plan, understand the cause and the impact of those adjustments before making them.
    3. Make adjustments ONLY when warranted. The temptation will be to push activities and tasks further out on the timeline (or to the next 90-day plan!) when there is any sort of “hiccup” along the way, especially when personnel outside the VMI are involved. Hold true to the timeline whenever possible; once you start slipping, it often becomes a habit.
    4. Report on progress every week and hold people accountable for their assignments and contributions.
    5. Take the 90-day plan seriously and treat it as you would any significant project – this is part of the VMI’s branding and image.

    Step 3.7: Manage the 3-year roadmap

    Keep an eye on the future since it will feed the present.

    The 3-year roadmap is a great planning tool, but it is not 100% reliable. There are inherent flaws and challenges. Essentially, the roadmap is a set of three “crystal balls” attempting to tell you what the future holds. The vision for Year 1 may be fairly clear, but for each subsequent year, the crystal ball becomes foggier. In addition, the timeline is constantly changing; before you know it, tomorrow becomes today and Year 2 becomes Year 1.

    To help navigate through the roadmap and maximize its potential, follow these principles:

    • Manage each year of the roadmap differently.
      • Review the Year 1 map each quarter to update your 90-day plans (See steps 2.10 and 3.6).
      • Review the Year 2 map every six months to determine if any changes are necessary. As you cycle through this, your vantage point of Year 2 will be 6 months or 12 months away from the beginning of Year 2, and time moves quickly.
      • Review the Year 3 map annually, and determine what needs to be added, changed, or deleted. Each time you review Year 3, it will be a “new” Year 3 that needs to be built.
    • Analyze the impact on the proposed modifications from two perspectives: 1) What is the impact if a requested modification is made? 2) What is the impact if a requested modification is not made?
    • Validate all modifications with leadership and stakeholders before updating the 3-year roadmap to ensure internal alignment.

    Step 3.8: Measure and monitor risk

    Understand and manage risk levels.

    Using the configured Vendor Risk Assessment Tool (Step 2.2), confirm which risks you will be measuring and monitoring and identify the vendors that will be part of the initial risk management process. Generally, organizations start measuring and monitoring risk in two to five risk categories for two or three strategic vendors. Over time, additional risk categories and/or vendors can be added in waves. Resist the temptation to add risk categories or vendors into the mix too quickly. Expanding requires resources inside and outside of the VMI.

    The VMI will rely heavily on other areas to provide input or the risk data, and the VMI needs to establish good working relationships with those areas. For example, if legal risk is something being measured and monitored, the VMI will need data from Legal on the number and nature of any lawsuits filed by or against the applicable vendors; the VMI will need data from Legal, Contract Management, or Procurement/Sourcing on the number and nature of any agreed upon deviations from your organization’s preferred contract terms that increase legal risk.

    With respect to risk, the VMI’s main role is threefold: 1) take the data obtained from others (or in some instances the VMI may have the data) and turn it into useful information, 2) monitor the risk categories over time and periodically issue reports, and 3) work with other areas to manage the risk.

    Step 3.9: Issue reports

    Inform internal personnel and vendors about trends, issues, progress, and results.

    Issuing the reports created in Step 2.12 is one of the main ways the VMI 1) will communicate with internal and external personnel and 2) track trends and information over time. Even with input from the potential reviewers of the reports, you’ll still want to seek their feedback and input periodically. It may take a few iterations until the reports are hitting their mark. You may find that a metric is no longer required, that a metric is missing completely or it is missing a component, or a formatting change would improve the report’s readability. Once a report has been “finalized,” try not to change it until you are engaged in Phase 4: Review activities. It can be unsettling for the reviewers when reports change constantly.

    Whenever possible, find ways to automate the reports. While issuing reports is critical, the function should not consume more time than necessary. Automation can remove some of the manual and repetitive tasks.

    Internal reports may need to be kept confidential. An automated dashboard or reporting tool can help lock down who has access to the information. At a minimum, the internal reports should contain a “Confidential” stamp, header, watermark, or other indicator that the materials are sensitive and should not be disclosed outside of your organization without approval.

    Reports for vendors may not need to be sent as often as reports are generated or prepared for internal personnel. Establish a cadence by classification model category and stick to it. Letting each vendor choose the frequency will make it more difficult for you to manage. The vendors can choose to ignore the report if they so choose.

    This is an image of an example of a bar graph showing ROI and Benchmark for Categories 1-6

    Step 3.10: Develop/improve vendor relationships

    Drive better performance through better relationships.

    One of the key components of a VMI is relationship management. Good relationships with your vendors provide many benefits for both parties, but they don’t happen by accident. Do not assume the relationship will be good or is good merely because your organization is buying products and services from a vendor.

    In many respects, the VMI should mirror a vendor’s sales organization by establishing relationships at multiple levels within the vendor organizations – not just with the salesperson or account manager. Building and maintaining relationships is hard work, but the return on investment makes it worthwhile.

    Business relationships are comprised of many components, not all of which have to be present to have a great relationship. However, there are some essential components. Whether you are trying to develop, improve, or maintain a relationship with a vendor, make sure you are conscious of the following:*

    • Focus your energies on strategic vendors first and then tactical and operational vendors.
    • Be transparent and honest in your communications.
    • Continue building trust by being responsive and honoring commitments (timely).
    • Create a collaborative environment and build upon common ground.
    • Thank the vendor when appropriate.
    • Resolve disputes early, avoid the “blame game,” and be objective when there are disagreements.

    Step 3.11: Contribute to other processes

    Continue assisting others and managing roles and responsibilities outside of the VMI.

    The VMI has processes that it owns and processes that it contributes to. Based on the VMI scope (Step 1.2), the OIC chart (Step 1.4), and the process mapping activities (Step 1.5), ensure that the VMI is honoring its contribution commitments. This is often easier said than done though. A number of factors can make it difficult to achieve the balance required to handle VMI processes and contribute to other processes associated with the VMI’s mission and vision. Understanding the issues is half the battle. If you see signs of these common “vampires,” take action quickly to address the situation.

    • The VMI’s first focus is often internal, and the tendency is to operate in a bubble. Classifying vendors, running BAMs, coordinating the risk process, and other inward-facing processes can consume all of the VMI’s energy. As a result, there is little time, effort, or let’s be honest, desire to participate in other processes outside of the VMI.
    • It is easy for VMI personnel to get dragged into processes and situations that are outside of its scope. This often happens when personnel join the VMI from other internal areas or departments and have good relationships with their former teammates. The relationships make it hard to say “No” when out-of-scope assistance is being requested.
    • The VMI may have “part-time” personnel who have responsibilities across internal departments, divisions, agencies, or teams. When the going gets tough and time is at a premium, people gravitate toward the easiest or most comfortable work. That work may not be VMI work.

    Phase 4: Review

    Keep Your VMI Up to Date and Running Smoothly

    Phase 1Phase 2Phase 3Phase 4
    1.1 Mission Statement and Goals


    1.2 Scope

    1.3 Strengths and Obstacles

    1.4 Roles and Responsibilities

    1.5 Process Mapping

    1.6 Charter

    1.7 Vendor Inventory

    1.8 Maturity Assessment

    1.9 Structure

    2.1 Classification Model
    2.2 Risk Assessment Tool
    2.3 Scorecards and Feedback
    2.4 Business Alignment Meeting Agenda
    2.5 Relationship Alignment Document
    2.6 Vendor Orientation
    2.7 Job Descriptions
    2.8 Policies and Procedures
    2.9 3-Year Roadmap
    2.10 90-Day Plan
    2.11 Quick Wins
    2.12 Reports

    3.1 Classify Vendors
    3.2 Conduct Internal “Kickoff” Meeting
    3.3 Conduct Vendor Orientation
    3.4 Compile Scorecards
    3.5 Conduct Business Alignment Meetings
    3.6 Work the 90-Day Plan
    3.7 Manage the 3-Year Roadmap
    3.8 Measure and Monitor Risk
    3.9 Issue Reports
    3.10 Develop/Improve Vendor Relationships
    3.11 Contribute to Other Processes

    4.1 Assess Compliance
    4.2 Incorporate Leading Practices
    4.3 Leverage Lessons Learned
    4.4 Maintain Internal Alignment
    4.5 Update Governances

    This phase will walk you through the following activities:

    Identify what the VMI should stop doing, start doing, and continue doing as it improves and matures. The main outcomes from this phase are ways to advance the VMI and maintain internal alignment.

    This phase involves the following participants:

    • VMI team
    • Applicable stakeholders and executives
    • Others as needed

    Jump Start Your Vendor Management Initiative

    Phase 4: Review

    Keep your VMI up to date and running smoothly.

    As the old adage says, “The only thing constant in life is change.” This is particularly true for your VMI. It will continue to mature; people inside and outside of the VMI will change; resources will expand or contract from year to year; your vendor base will change. As a result, your VMI needs the equivalent of a physical every year. In place of bloodwork, x-rays, and the other paces your physician may put you through, you’ll assess compliance with your policies and procedures, incorporate leading practices, leverage lessons learned, maintain internal alignment, and update governances.

    Be thorough in your actions during this Phase to get the most out of it. It requires more than the equivalent of gauging a person’s health by taking their temperature, measuring their blood pressure, and determining their body mass index. Keeping your VMI up to date and running smoothly takes hard work.

    Some of the items presented in this Phase require an annual review; others may require quarterly review or timely review (i.e. when things are top of mind and current). For example, collecting lessons learned should happen on a timely basis rather than annually, and classifying your vendors should occur annually rather than every time a new vendor enters the fold.

    Ultimately, the goal is to improve over time and stay aligned with other areas internally. This won’t happen by accident. Being proactive in the review of your VMI further reinforces the nature of the VMI itself – proactive vendor management, NOT reactive!

    Step 4.1: Assess compliance

    Determine what is functionally going well and not going well.

    Whether you have a robust set of vendor management-related policies and procedures or they are the bare minimum, gathering data each quarter and conducting an assessment each year will provide valuable feedback. The scope of your assessment should focus on two concepts: 1) are the policies and procedures being followed and 2) are the policies and procedures accurate and relevant. This approach requires parallel thinking, but it will help you understand the complete picture and minimize the amount of time required.

    Use the steps listed below (or modify them for your culture) to conduct your assessment:

    • Determine the type of assessment – formal or informal.
    • Determine the scale of the assessment – which policies and procedures will be reviewed and how many people will be interviewed.
    • Determine the compliance levels, and seek feedback on the policies and procedures – what is going well and what can be improved?
    • Review the compliance deviations.
    • Conduct a root cause analysis for the deviations.
    • Create a list of improvements and gain approval.
    • Create a plan for minimizing noncompliance in the future.
      • Improve/increase education and awareness.
      • Clarify/modify policies and procedures.
      • Add resources, tools, and people (as necessary and as allowed).

    Step 4.2: Incorporate leading practices

    Identify and evaluate what external VMIs are doing.

    The VMI’s world is constantly shifting and evolving. Some changes will take place slowly, while others will occur quickly. Think about how quickly the cloud environment has changed over the past five years versus the 15 years before that; or think about issues that have popped up and instantly altered the landscape (we’re looking at you COVID-19 and ransomware). As a result, the VMI needs to keep pace, and one of the best ways to do that is to incorporate leading practices.

    At a high level, a leading practice is a way of doing something that is better at producing a particular outcome or result or performing a task or activity than other ways of proceeding. The leading practice can be based on methodologies, tools, processes, procedures, and other items. Leading practices change periodically due to innovation, new ways of thinking, research, and other factors. Consequently, a leading practice is to identify and evaluate leading practices each year.

    Step 4.2: Incorporate leading practices (cont.)

    Update your VMI based on your research.

    • A simple approach for incorporating leading practices into your regular review process is set out below:
    • Research:
      • What other VMIs in your industry are doing.
      • What other VMIs outside your industry are doing.
      • Vendor management in general.
    • Based on your results, list specific leading practices others are doing that would improve your VMI (be specific – e.g. other VMIs are incorporating risk into their classification process).
    • Evaluate your list to determine which of these potential changes fit or could be modified to fit your culture and environment.
    • Recommend the proposed changes to leadership (with a short business case or explanation/justification, as needed) and gain approval.

    Remember: Leading practices or best practices may not be what is best for you. In some instances, you will have to modify them to fit your culture and environment; in other instances, you will elect not to implement them at all (in any form).

    Step 4.3: Leverage lessons learned

    Tap into the collective wisdom and experience of your team members.

    There are many ways to keep your VMI running smoothly, and creating a lessons learned library is a great complement to the other ways covered in this Phase 4: Review. By tapping into the collective wisdom of the team and creating a safe feedback loop, the VMI gains the following benefits:

    • Documented institutional wisdom and knowledge normally found only in the team members’ brains.
    • The ability for one team member to gain insights and avoid mistakes without having to duplicate the events leading to the insights or mistakes.
    • Improved methodologies, tools, processes, procedures, skills, and relationships.

    Many of the processes raised in this Phase can be performed annually, but a lessons learned library works best when the information is “deposited” in a timely manner. How you choose to set up your lessons learned process will depend on the tools you select and your culture. You may want to have regular “input” meetings to share the lessons as they are being deposited, or you may require team members to deposit lessons learned on a regular basis (within a week after they happen, monthly, or quarterly). Waiting too long can lead to vague or lost memories and specifics – timeliness of the deposits is a crucial element.

    Step 4.3: Leverage lessons learned (cont.)

    Create a library to share valuable information across the team.

    Lessons learned are not confined to identifying mistakes or dissecting bad outcomes. You want to reinforce good outcomes as well. When an opportunity for a lessons-learned deposit arises, identify the following basic elements:

    • A brief description of the situation and outcome.
    • What went well (if anything) and why did it go well?
    • What didn't go well (if anything) and why didn't it go well?
    • What would/could you do differently next time?
    • A synopsis of the lesson(s) learned.

    Info-Tech Insights

    The lessons learned library needs to be maintained. Irrelevant material needs to be culled periodically, and older or duplicate material may need to be archived.

    The lessons learned process should be blameless. The goal is to share insightful information … not to reward or punish people based on outcomes or results.

    Step 4.4: Maintain internal alignment

    Review the plans of other internal areas to stay in sync.

    Maintaining internal alignment is essential for the ongoing success of the VMI. Over time, it is easy to lose sight of the fact that the VMI does not operate in a vacuum; it is an integral component of a larger organization whose parts must work well together to function optimally. Focusing annually on the VMI’s alignment within the enterprise helps reduce any breakdowns that could derail the organization.

    To ensure internal alignment:

    • Review the key components of the applicable materials from Phase 1: Plan and Phase 2: Build with the appropriate members of the leadership team (e.g. executives, sponsors, and stakeholders). Not every item from those Phases and Steps needs to be reviewed, but err on the side of caution for the first set of alignment discussions, and be prepared to review each item. You can gauge the audience’s interest on each topic and move quickly when necessary or dive deeper when needed. Identify potential changes required to maintain alignment.
    • Review the strategic plans (e.g. 1-, 3-, and 5- year plans) for various portions of the organization if you have access to them or gather insights if you don’t have access.
      • If the VMI is under the IT umbrella, review the strategic plans for IT and its departments.
      • Review the strategic plans for the areas the VMI works with (e.g. Procurement, Business Units).
      • The organization itself.
    • Create and vet a list of modifications to the VMI and obtain approval.
    • Develop a plan for making the necessary changes.

    Step 4.5: Update governances

    Revise your protocols and return to the beginning of cyclical processes.

    You’re at the final Step and ready to update governances. This is comprised of two sequential paths.

    • First, use the information from Steps 4.1-4.4 to make any required modifications to the items in Phase 1: Plan, Phase 2: Build, and Phase 3: Run. For example, you may need to update your policies and procedures (Step 2.8) based on your findings in Step 4.1; or you may need to update the VMI’s scope (Step 1.2) to ensure internal alignment issues identified in Step 4.4. are accounted for.
    • Second, return to Phase 3: Run to perform the activities below; they tend to be performed annually, but use your discretion and perform them on an as-needed basis:
      • Reclassify vendors.
      • Complete a new maturity assessment.
      • Run reorientation sessions for vendors.
      • Conduct a kickoff meeting to update internal personnel.

    Other activities and tasks (e.g. scorecards and BAMs) may be impacted by the modifications made above, but the nature of their performance follows a shorter cadence. As a result, they are not specifically called out here in this Step 4.5 since they are performed on an ongoing basis. However, don’t overlook them as part of your update.

    Summary of Accomplishment

    Problem Solved

    Vendor management is a broad, often overwhelming, comprehensive spectrum that encompasses many disciplines. By now, you should have a great idea of what vendor management can or will look like in your organization. Focus on the basics first: Why does the VMI exist and what does it hope to achieve? What is its scope? What are the strengths you can leverage, and what obstacles must you manage? How will the VMI work with others? From there, the spectrum of vendor management will begin to clarify and narrow.

    Leverage the tools and templates from this blueprint and adapt them to your needs. They will help you concentrate your energies in the right areas and on the right vendors to maximize the return on your organization’s investment in the VMI of time, money, personnel, and other resources. You may have to lead by example internally and with your vendors at first, but they will eventually join you on your path if you stay true to your course.

    At the heart of a good VMI is the relationship component. Don’t overlook its value in helping you achieve your vendor management goals. The VMI does not operate in a vacuum, and relationships (internal and external) will be critical.

    Lastly, seek continual improvement from the VMI and from your vendors. Both parties should be held accountable, and both parties should work together to get better. Be proactive in your efforts, and you, the VMI, and the organization will be rewarded.

    If you would like additional support, have our analysts guide you through other phases as part of an Info-Tech workshop

    Contact your account representative for more information

    workshops@infotech.com

    1-888-670-8889

    Related Info-Tech Research

    Prepare for Negotiations More Effectively

    Don't leave negotiation preparations and outcomes to chance. Learn how to prepare for negotiations more effectively and improve your results.

    Understand Common IT Contract Provisions to Negotiate More Effectively

    Info-Tech’s guidance and insights will help you navigate the complex process of contract review and identify the key details necessary to maximize the protections for your organization.

    Capture and Market the ROI of Your VMO

    Calculating the impact or value of a vendor management office (VMO) can be difficult without the right framework and tools. Let Info-Tech’s tools and templates help you account for the contributions made by your VMO.

    Bibliography

    “Best Practices for Writing Corporate Policies and Procedures.” PowerDMS, 29 Dec. 2020. Accessed 11 January 2022.

    Duncan. “Top 10 Tips for Creating Compelling Reports.” Design Eclectic, 11 October 2019. Accessed 29 March 2022.

    Eby, Kate. “Master Writing Policies, Procedures, Processes, and Work Instructions.” 1 June 2018, updated 19 July 2021. Accessed 11 January 2022.

    “Enterprise Risk Management.” Protiviti, n.d. Accessed 16 Feb. 2017.

    Geller & Company. “World-Class Procurement — Increasing Profitability and Quality.” Spend Matters, 2003. Accessed 4 March 2019.

    Guth, Stephen. “Vendor Relationship Management Getting What You Paid for (And More).” Citizens, 26 Feb. 2015. Web.

    Guth, Stephen. The Vendor Management Office: Unleashing the Power of Strategic Sourcing. Lulu.com, 2007. Print.

    “ISG Index 4Q 2021.” Information Services Group, Inc., 2022. Web.

    “Six Tips for Making a Quality Report Appealing and Easy To Skim.” AHRQ, Oct. 2019. Accessed 29 March 2022.

    Tucker, Davis. “Marketing Reporting: Tips to Create Compelling Reports.” 60 Second Marketer, 28 March 2020. Accessed 29 March 2022.

    “Why Do We Perform Better When Someone Has High Expectations of Us?” The Decision Lab, 9 Sept. 2020. Accessed 31 January 2022.

    2020 CIO Priorities Report

    • Buy Link or Shortcode: {j2store}97|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Innovation
    • Parent Category Link: /innovation
    • The velocity and magnitude of technology changes today has increased dramatically compared to anything that has come before.
    • The velocity and magnitude of advancements in technology has always seemed unprecedented in every wave of technology change we have experienced over the past 40 years. With each new wave of innovation, “unprecedented” is redefined to a new level, and so it remains true that today’s CIO is faced with unprecedented levels of change as a direct result of emerging technologies.
    • What is different today is that we are at the point where the emerging technology itself is now capable of accelerating the pace of change even more through artificial intelligence capabilities.
    • If we are to realize the business value through the adoption of emerging technologies, CIOs must address significant challenges. We believe addressing these challenges lies in the CIO priorities for 2020.

    Our Advice

    Critical Insight

    • First there was IT/business alignment, then there was IT/business integration – both states characterized as IT “getting on the same page” as the business. In the context of emerging technologies, the CIO should no longer be focused on getting on the same page as the CEO.
    • Today it is about the CEO and the CIO collaborating to write a new book about convergence of all things: technology (infrastructure and applications), people (including vendors), process, and data.
    • Digital transformation and adoption of emerging technologies is not a goal, it is a journey – a means to the end, not the end unto itself.

    Impact and Result

    • Use Info-Tech's 2020 CIO Priorities Report to ascertain, based on our research, what areas of focus for 2020 are critical for success in adopting emerging technologies.
    • Adopting these technologies requires careful planning and consideration for what is critical to your business customers.
    • This report provides focus on the business benefits of the technology and not just the capabilities themselves. It puts the CIO in a position to better understand the true value proposition of any of today’s technology advancements.

    2020 CIO Priorities Report Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to understand the top five priorities for CIOs in 2020 and why these are so critical to success.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Refine and adapt processes

    Learn about how processes can make or break your adoption of emerging technologies.

    • 2020 CIO Priorities Report – Priority 1: Refine and Adapt Processes

    2. Re-invent IT as collaboration engine

    Learn about how IT can transform its role within the organization to optimize business value.

    • 2020 CIO Priorities Report – Priority 2: Re-Invent IT as Collaboration Engine

    3. Acquire and retain talent for roles in emerging technologies

    Learn about how IT can attract and keep employees with the skills and knowledge needed to adopt these technologies for the business.

    • 2020 CIO Priorities Report – Priority 3: Acquire and Retain Talent for Roles in Emerging Technologies

    4. Define and manage cybersecurity and cyber resilience requirements related to emerging technologies

    Understand how the adoption of emerging technologies has created new levels of risk and how cybersecurity and resilience can keep pace.

    • 2020 CIO Priorities Report – Priority 4: Define and Manage Cybersecurity and Cyber Resilience Requirements Related to Emerging Technologies

    5. Leverage emerging technology to create Wow! customer experiences

    Learn how IT can leverage emerging technology for its own customers and those of its business partners.

    • 2020 CIO Priorities Report – Priority 5: Leverage Emerging Technology to Create Wow! Customer Experiences
    [infographic]

    IT Governance

    • Buy Link or Shortcode: {j2store}22|cart{/j2store}
    • Related Products: {j2store}22|crosssells{/j2store}
    • Up-Sell: {j2store}22|upsells{/j2store}
    • member rating overall impact: 9.2/10
    • member rating average dollars saved: $124,127
    • member rating average days saved: 37
    • Parent Category Name: Strategy and Governance
    • Parent Category Link: /strategy-and-governance
    Read our concise Executive Brief to find out why you may want to redesign your IT governance, Review our methodology, and understand how we can support you in completing this process.

    Considerations for a Hub and Spoke Model When Deploying Infrastructure in the Cloud

    • Buy Link or Shortcode: {j2store}472|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Cloud Strategy
    • Parent Category Link: /cloud-strategy
    • The organization is planning to move resources to cloud or devise a networking strategy for their existing cloud infrastructure to harness value from cloud.
    • The right topology needs to be selected to deploy network level isolation, design the cloud for management efficiencies and provide access to shared services on cloud.
    • A perennial challenge for infrastructure on cloud is planning for governance vs flexibility which is often overlooked.

    Our Advice

    Critical Insight

    Don’t wait until the necessity arises to evaluate your networking in the cloud. Get ahead of the curve and choose the topology that optimizes benefits and supports organizational needs in the present and the future.

    Impact and Result

    • Define organizational needs and understand the pros and cons of cloud network topologies to strategize for the networking design.
    • Consider the layered complexities of addressing the governance vs. flexibility spectrum for your domains when designing your networks.

    Considerations for a Hub and Spoke Model When Deploying Infrastructure in the Cloud Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Considerations for a Hub and Spoke Model When Deploying Infrastructure in the Cloud Deck – A document to guide you through designing your network in the cloud.

    What cloud networking topology should you use? How do you provide access to shared resources in the cloud or hybrid infrastructure? What sits in the hub and what sits in the spoke?

    • Considerations for a Hub and Spoke Model When Deploying Infrastructure in the Cloud Storyboard
    [infographic]

    Further reading

    Considerations for a Hub and Spoke Model When Deploying Infrastructure in the Cloud

    Don't revolve around a legacy design; choose a network design that evolves with the organization.

    Analyst Perspective

    Cloud adoption among organizations increases gradually across both the number of services used and the amount those services are used. However, network builders tend to overlook the vulnerabilities of network topologies, which leads to complications down the road, especially since the structures of cloud network topologies are not all of the same quality. A network design that suits current needs may not be the best solution for the future state of the organization.

    Even if on-prem network strategies were retained for ease of migration, it is important to evaluate and identify the cloud network topology that can not only elevate the performance of your infrastructure in the cloud, but also that can make it easier to manage and provision resources.

    An "as the need arises" strategy will not work efficiently since changing network designs will change the way data travels within your network, which will then need to be adopted to existing application architectures. This becomes more complicated as the number of services hosted in the cloud grows.

    Keep a network strategy in place early on and start designing your infrastructure accordingly. This gives you more control over your networks and eliminates the need for huge changes to your infrastructure down the road.

    This is a picture of Nitin Mukesh

    Nitin Mukesh
    Senior Research Analyst, Infrastructure and Operations
    Info-Tech Research Group

    Executive Summary

    Your Challenge

    The organization is planning to move resources to the cloud or devise a networking strategy for their existing cloud infrastructure to harness value from the cloud.

    The right topology needs to be selected to deploy network level isolation, design the cloud for management efficiencies, and provide access to shared services in the cloud.

    A perennial challenge for infrastructure in the cloud is planning for governance vs. flexibility, which is often overlooked.

    Common Obstacles

    The choice of migration method may result in retaining existing networking patterns and only making changes when the need arises.

    Networking in the cloud is still new, and organizations new to the cloud may not be aware of the cloud network designs they can consider for their business needs.

    Info-Tech's Approach

    Define organizational needs and understand the pros and cons of cloud network topologies to strategize for the networking design.

    Consider the layered complexities of addressing the governance vs. flexibility spectrum for your domains when designing your networks.

    Insight Summary

    Don't wait until the necessity arises to evaluate your networking in the cloud. Get ahead of the curve and choose the topology that optimizes benefits and supports organizational needs in the present and future.

    Your challenge

    Selecting the right topology: Many organizations migrate to the cloud retaining a mesh networking topology from their on-prem design, or they choose to implement the mesh design leveraging peering technologies in the cloud without a strategy in place for when business needs change. While there may be many network topologies for on-prem infrastructure, the network design team may not be aware of the best approach in cloud platforms for their requirements, or a cloud networking strategy may even go overlooked during the migration.

    Finding the right cloud networking infrastructure for:

    • Management efficiencies
    • Network-level isolation of resources
    • Access to shared services

    Deciding between governance and flexibility in networking design: In the hub and spoke model, if a domain is in the hub, the greater the governance over it, and if it sits in the spoke, the higher the flexibility. Having a strategy for the most important domains is key. For example, some security belongs in the hub and some security belongs in the spoke. The tradeoff here is if it sits completely in the spoke, you give it a lot of freedom, but it becomes harder to standardize across the organization.

    Mesh network topology

    A mesh is a design where virtual private clouds (VPCs) are connected to each other individually creating a mesh network. The network traffic is fast and can be redirected since the nodes in the network are interconnected. There is no hierarchical relationship between the networks, and any two networks can connect with each other directly.

    In the cloud, this design can be implemented by setting up peering connections between any two VPCs. These VPCs can also be set up to communicate with each other internally through the cloud service provider's network without having to route the traffic via the internet.

    While this topology offers high redundancy, the number of connections grows tremendously as more networks are added, making it harder to scale a network using a mesh topology.

    Mesh Network on AWS

    This is an image of a Mesh Network on AWS

    Source: AWS, 2018

    Constraints

    The disadvantages of peering VPCs into a mesh quickly arise with:

    • Transitive connections: Transitive connections are not supported in the cloud, unlike with on-prem networking. This means that if there are two networks that need to communicate, a single peering link can be set up between them. However, if there are more than two networks and they all need to communicate, they should all be connected to each other with separate individual connections.
    • Cost of operation: The lack of transitive routing requires many connections to be set up, which adds up to a more expensive topology to operate as the number of networks grows. Cloud providers also usually limit the number of peering networks that can be set up, and this limit can be hit with as few as 100 networks.
    • Management: Mesh tends to be very complicated to set up, owing to the large number of different peering links that need to be established. While this may be manageable for small organizations with small operations, for larger organizations with robust cybersecurity practices that require multiple VPCs to be deployed and interconnected for communications, mesh opens you up to multiple points of failure.
    • Redundancy: With multiple points of failure already being a major drawback of this design, you also cannot have more than one peered connection between any two networks at the same time. This makes designing your networking systems for redundancy that much more challenging.
    Number of virtual networks 10 20 50 100
    Peering links required
    [(n-1)*n]/2
    45 190 1225 4950

    Proportional relationship of virtual networks to required peering links in a mesh topology

    Case study

    INDUSTRY: Blockchain
    SOURCE: Microsoft

    An organization with four members wants to deploy a blockchain in the cloud, with each member running their own virtual network. With only four members on the team, a mesh network can be created in the cloud with each of their networks being connected to each other, adding up to a total of 12 peering connections (four members with three connections each). While the members may all be using different cloud accounts, setting up connections between them will still be possible.

    The organization wants to expand to 15 members within the next year, with each new member being connected with their separate virtual networks. Once grown, the organization will have a total of 210 peering connections since each of the virtual networks will then need 14 peering connections. While this may still be possible to deploy, the number of connections makes it harder to manage and would be that much more difficult to deploy if the organization grows to even 30 or 40 members. The new scale of virtual connections calls for an alternative networking strategy that cloud providers offer – the hub and spoke topology.

    This is an image of the connections involved in a mesh network with four participants.

    Source: Microsoft, 2017

    Hub and spoke network topology

    In hub and spoke network design, each network is connected to a central network that facilitates intercommunication between the networks. The central network, also called the hub, can be used by multiple workloads/servers/services for hosting services and for managing external connectivity. Other networks connected to the hub through network peering are called spokes and host workloads.

    Communications between the workloads/servers/services on spokes pass in or out of the hub where they are inspected and routed. The spokes can also be centrally managed from the hub with IT rules and processes.

    A hub and spoke design enable a larger number of virtual networks to be interconnected as each network only needs one peered connection (to the hub) to be able to communicate with any other network in the system.

    Hub and Spoke Network on AWS

    This is an image of the Hub and Spoke Network on AWS

    What hub and spoke networks do better

    1. Ease of connectivity: Hub and spoke decreases the liabilities of scale that come from a growing business by providing a consistent connection that can be scaled easily. As more networks are added to an organization, each will only need to be connected once – to the hub. The number of connections is considerably lower than in a mesh topology and makes it easier to maintain and manage.
    2. Business agility and scalability: It is easier to increase the number of networks than in mesh, making it easier to grow your business into new channels with less time, investment, and risk.
    3. Data collection: With a hub and spoke design, all data flows through the hub – depending on the design, this includes all ingress and egress to and from the system. This makes it an excellent central network to collect all business data.
    4. Network-level isolation: Hub and spoke enables separation of workloads and tiers into different networks. This is particularly useful to ensure an issue affecting a network or a workload does not affect the rest.
    5. Network changes: Changes to a separated network are much easier to carry out knowing the changes made will not affect all the other connected networks. This reduces work-hours significantly when systems or applications need to be altered.
    6. Compliance: Compliance requirements such as SOC 1 and SOC 2 require separate environments for production, development, and testing, which can be done in a hub and spoke model without having to re-create security controls for all networks.

    Hub and spoke constraints

    While there are plenty of benefits to using this topology, there are still a few notable disadvantages with the design.

    Point-to-point peering

    The total number of total peered connections required might be lower than mesh, but the cost of running independent projects is cheaper on mesh as point-to-point data transfers are cheaper.

    Global access speeds with a monolithic design

    With global organizations, implementing a single monolithic hub network for network ingress and egress will slow down access to cloud services that users will require. A distributed network will ramp up the speeds for its users to access these services.

    Costs for a resilient design

    Connectivity between the spokes can fail if the hub site dies or faces major disruptions. While there are redundancy plans for cloud networks, it will be an additional cost to plan and build an environment for it.

    Leverage the hub and spoke strategy for:

    Providing access to shared services: Hub and spoke can be used to give workloads that are deployed on different networks access to shared services by placing the shared service in the hub. For example, DNS servers can be placed in the hub network, and production or host networks can be connected to the hub to access it, or if the central network is set up to host Active Directory services, then servers in other networks can act as spokes and have full access to the central VPC to send requests. This is also a great way to separate workloads that do not need to communicate with each other but all need access to the same services.

    Adding new locations: An expanding organization that needs to add additional global or domestic locations can leverage hub and spoke to connect new network locations to the main system without the need for multiple connections.

    Cost savings: Apart from having fewer connections than mesh that can save costs in the cloud, hub and spoke can also be used to centralize services such as DNS and NAT to be managed in one location rather than having to individually deploy in each network. This can bring down management efforts and costs considerably.

    Centralized security: Enterprises can deploy a center of excellence on the hub for security, and the spokes connected to it can leverage a higher level of security and increase resilience. It will also be easier to control and manage network policies and networking resources from the hub.

    Network management: Since each spoke is peered only once to the hub, detecting connectivity problems or other network issues is made simpler in hub and spoke than on mesh. A network manager deployed on the cloud can give access to network problems faster than on other topologies.

    Hub and spoke – mesh hybrid

    The advantages of using a hub and spoke model far exceed those of using a mesh topology in the cloud and go to show why most organizations ultimately end up using the hub and spoke as their networking strategy.

    However, organizations, especially large ones, are complex entities, and choosing only one model may not serve all business needs. In such cases, a hybrid approach may be the best strategy. The following slides will demonstrate the advantages and use cases for mesh, however limited they might be.

    Where it can be useful:

    An organization can have multiple network topologies where system X is a mesh and system Y is a hub and spoke. A shared system Z can be a part of both systems depending on the needs.

    An organization can have multiple networks interconnected in a mesh and some of the networks in the mesh can be a hub for a hub-spoke network. For example, a business unit that works on data analysis can deploy their services in a spoke that is connected to a central hub that can host shared services such as Active Directory or NAT. The central hub can then be connected to a regional on-prem network where data and other shared services can be hosted.

    Hub and spoke – mesh hybrid network on AWS

    This is an image of the Hub and spoke – mesh hybrid network on AWS

    Why mesh can still be useful

    Benefits Of Mesh

    Use Cases For Mesh

    Security: Setting up a peering connection between two VPCs comes with the benefit of improving security since the connection can be private between the networks and can isolate public traffic from the internet. The traffic between the networks never has to leave the cloud provider's network, which helps reduce a class of risks.

    Reduced network costs: Since the peered networks communicate internally through the cloud's internal networks, the data transfer costs are typically cheaper than over the public internet.

    Communication speed: Improved network latency is a key benefit from using mesh because the peered traffic does not have to go over the public internet but rather the internal network. The network traffic between the connections can also be quickly redirected as needed.

    Higher flexibility for backend services: Mesh networks can be desirable for back-end services if egress traffic needs to be blocked to the public internet from the deployed services/servers. This also helps avoid having to set up public IP or network address translation (NAT) configurations.

    Connecting two or more networks for full access to resources: For example, consider an organization that has separate networks for each department, which don't all need to communicate with each other. Here, a peering network can be set up only between the networks that need to communicate with full or partial access to each other such as finance to HR or accounting to IT.

    Specific security or compliance need: Mesh or VPC peering can also come in handy to serve specific security needs or logging needs that require using a network to connect to other networks directly and in private. For example, global organizations that face regulatory requirements of storing or transferring data domestically with private connections.

    Systems with very few networks that do not need internet access: Workloads deployed in networks that need to communicate with each other but do not require internet access or network address translation (NAT) can be connected using mesh especially when there are security reasons to keep them from being connected to the main system, e.g. backend services such as testing environments, labs, or sandboxes can leverage this design.

    Designing for governance vs. flexibility in hub and spoke

    Governance and flexibility in managing resources in the cloud are inversely proportional: The higher the governance, the less freedom you have to innovate.

    The complexities of designing an organization's networks grow with the organization as it becomes global and takes on more services and lines of business. Organizations that choose to deploy the hub and spoke model face a dilemma in choosing between governance and flexibility for their networks. Organizations need to find that sweet spot to find the right balance between how much they want to govern their systems, mainly for security- and cost-monitoring, and how much flexibility they want to provide for innovation and other operations, since the two usually tend to have an inverse relationship.

    This decision in hub and spoke usually means that the domains chosen for higher governance must be placed in the hub network, and the domains that need more flexibility in a spoke. The key variables in the following slide will help determine the placement of the domain and will depend entirely on the organization's context.

    The two networking patterns in the cloud have layered complexities that need to be systematically addressed.

    Designing for governance vs. flexibility in hub and spoke

    If a network has more flexibility in all or most of these domains, it may be a good candidate for a spoke-heavy design; otherwise, it may be better designed in a hub-centric pattern.

    • Function: The function the domain network is assigned to and the autonomy the function needs to be successful. For example, software R&D usually requires high flexibility to be successful.
    • Regulations: The extent of independence from both internal and external regulatory constraints the domain has. For example, a treasury reporting domain typically has high internal and external regulations to adhere to.
    • Human resources: The freedom a domain has to hire and manage its resources to perform its function. For example, production facilities in a huge organization have the freedom to manage their own resources.
    • Operations: The freedom a domain has to control its operations and manage its own spending to perform its functions. For example, governments usually have different departments and agencies, each with its own budget to perform its functions.
    • Technology: The independence and the ability a domain has to manage its selection and implementation of technology resources in the cloud. For example, you may not want a software testing team to have complete autonomy to deploy resources.

    Optimal placement of services between the hub and spoke

    Shared services and vendor management

    Resources that are shared between multiple projects or departments or even by the entire organization should be hosted on the hub network to simplify sharing these services. For example, e-learning applications that may be used by multiple business units to train their teams, Active Directory accessed by most teams, or even SAAS platforms such as O365 and Salesforce can leverage buying power and drive down the costs for the organization. Shared services should also be standardized across the organization and for that, it needs to have high governance.

    Services that are an individual need for a network and have no preexisting relationship with other networks or buying power and scale can be hosted in a spoke network. For example, specialized accounting software used exclusively by the accounting team or design software used by a single team. Although the services are still a part of the wider network, it helps separate duties from the shared services network and provides flexibility to the teams to customize and manage their services to suit their individual needs.

    Network egress and interaction

    Network connections, be they in the cloud or hybrid-cloud, are used by everyone to either connect to the internet, access cloud services, or access the organization's data center. Since this is a shared service, a centralized networking account must be placed in the hub for greater governance. Interactions between the spokes in a hub and spoke model happens through the hub, and providing internet access to the spokes through the hub can help leverage cost benefits in the cloud. The network account will perform routing duties between the spokes, on-prem assets, and egress out to the internet.

    For example, NAT gateways in the cloud that are managed services are usually charged by the hour, and deploying NAT on each spoke can be harder to manage and expensive to maintain. A NAT gateway deployed in a central networking hub can be accessed by all spokes, so centralizing it is a great option.

    Note that, in some cases, when using edge locations for data transfers, it may be cost effective to deploy a NAT in the spoke, but such cases usually do not apply to most organizational units.

    A centralized network hub can also be useful to configure network policies and network resources while organizational departments can configure non-network resources, which helps separate responsibilities for all the spokes in the system. For example, subnets and routes can be controlled from the central network hub to ensure standardized network policies across the network.

    Security

    While there needs to be security in the hub and the spokes individually, finding the balance of operation can make the systems more robust. Hub and spoke design can be an effective tool for security when a principal security hub is hosted in the hub network. The central security hub can collect data from the spokes as well as non-spoke sources such as regulatory bodies and threat intelligence providers, and then share the information with the spokes.

    Threat information sharing is a major benefit of using this design, and the hub can take actions to analyze and enrich the data before sharing it with spokes. Shared services such as threat intelligence platforms (TIP) can also benefit from being centralized when stationed in the hub. A collective defense approach between the hub and spoke can be very successful in addressing sophisticated threats.

    Compliance and regulatory requirements such as HIPAA can also be placed in the hub, and the spokes connected to it can make use of it instead of having to deploy it in each spoke individually.

    Cloud metering

    The governance vs. flexibility paradigm usually decides the placement of cloud metering, i.e. if the organization wants higher control over cloud costs, it should be in the central hub, whereas if it prioritizes innovation, the spokes should be allowed to control it. Regardless of the placement of the domain, the costs can be monitored from the central hub using cloud-native monitoring tools such as Azure Monitor or any third-party software deployed in the hub.

    For ease of governance and since resources are usually shared at a project level, most cloud service providers suggest that an individual metering service be placed in the spokes. The centralized billing system of the organization, however, can make use of scale and reserved instances to drive down the costs that the spokes can take advantage of. For example, billing and access control resources are placed in the lower levels in GCP to enable users to set up projects and perform their tasks. These billing systems in the lower levels are then controlled by a centralized billing system to decide who pays for the resources provisioned.

    Don't get stuck with your on-prem network design. Design for the cloud.

    1. Peering VPCs into a mesh design can be an easy way to get onto the cloud, but it should not be your networking strategy for the long run.
    2. Hub and spoke network design offers more benefits than any other network strategy to be adopted only when the need arises. Plan for the design early on and keep a strategy in place to deploy it as early as possible.
    3. Hybrid of mesh and hub and spoke will be very useful in connecting multiple large networks especially when they need to access the same resources without having to route the traffic over the internet.
    4. Governance vs. flexibility should be a key consideration when designing for hub and spoke to leverage the best out of your infrastructure.
    5. Distribute domains across the hub or spokes to leverage costs, security, data collection, and economies of scale, and to foster secure interactions between networks.

    Cloud network design strategy

    This is an image of the framework for developing a Cloud Network Design Strategy.

    Bibliography

    Borschel, Brett. "Azure Hub Spoke Virtual Network Design Best Practices." Acendri Solutions, 13 Jan. 2022. Web.
    Singh, Garvit. "Amazon Virtual Private Cloud Connectivity Options." AWS, January 2018. Web.
    "What Is the Hub and Spoke Information Sharing Model?" Cyware, 16 Aug. 2021. Web.
    Youseff, Lamia. "Mesh and Hub-and-Spoke Networks on Azure." Microsoft, Dec. 2017. Web.

    Gain Control of Cloud Integration Strategies Before they Float Away

    • Buy Link or Shortcode: {j2store}362|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Enterprise Integration
    • Parent Category Link: /enterprise-integration
    • IT is typically backlogged with tasks while the business waits to implement key solutions to remain competitive. In this competitive space, Cloud solutions offer attractive benefits to business stakeholders especially around agility and cost.
    • Moving to the Cloud involves more than outsourcing a component of the technology stack. Roles, processes, and authentication technologies need to be redefined to fit a distributed stack where parts of the IT solution space reside on-premise while the rest are in the Cloud.
    • Cloud integration means accepting loss of control in product development. A Cloud vendor will address the needs of most constituents and any high degree of customization which counteracts their business model. This makes integration a complex initiative involving two separate parties trying to align.

    Our Advice

    Critical Insight

    • Cloud integration is a fundamental commitment to change within the organization as it deeply impacts roles, processes, and technologies.
    • Be prepared to lose some degree of control of SLA management. IT will have to manage multiple Cloud SLAs and deliver a lowest common approach to the business. This may mean lowering the SLA standards previously set with on-premise solutions.
    • Cloud integration isn’t just about the technology. It is a dedication to establish solid relationships with the Cloud vendor. Understanding where the cloud solution is moving and what issues are being addressed are critical to creating an organizational road map for the future.

    Impact and Result

    • Develop a Cloud integration strategy by proactively understanding the impact of Cloud integration efforts to the organization.
    • Realize that Cloud integration will be an ongoing process of collaboration with the business, and that the initial implementation does not constitute an end.
    • Implement an integrated support structure that includes on-premise and cloud stacks.

    Gain Control of Cloud Integration Strategies Before they Float Away Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Understand the impacts of Cloud computing on Data, Application, Access, and Service Level Agreement integration

    Assess your current level of Cloud adoption and integration, focusing on solutions that are emerging in the market and the applicability to your IT environment.

    • Storyboard: Gain Control of Cloud Integration Strategies Before they Float Away
    • Cloud Integration Checklist
    • None
    [infographic]

    Understand and Apply Internet-of-Things Use Cases to Drive Organizational Success

    • Buy Link or Shortcode: {j2store}535|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Customer Relationship Management
    • Parent Category Link: /customer-relationship-management
    • The Internet of Things (IoT) is a rapidly proliferating technology – connected devices have experienced unabated growth over the last ten years.
    • The business wants to capitalize on the IoT and move the needle forward for proactive customer service and operational efficiency.
    • Moreover, IT wants to maintain its reputation as forward-thinking, and the business wants to be innovative.

    Our Advice

    Critical Insight

    • Leverage Info-Tech’s comprehensive three-phase approach to IoT projects: understand the fundamentals of IoT capabilities, assess where the IoT will drive value within the organization, and present findings to stakeholders.
    • Conduct a foundational IoT discussion with stakeholders to level set expectations about the technology’s capabilities.
    • Determine your organization’s approach to the IoT in terms of both hardware and software.
    • Determine which use case your organization fits into: three of the use cases highlighted in this report include predictive customer service, smart offices, and supply chain applications.

    Impact and Result

    • Our methodology addresses the possible issues by using a case-study approach to demonstrate the “Art of the Possible” for the IoT.
    • With an understanding of the IoT, it is possible to find applicable use cases for this emerging technology and get a leg up on competitors.

    Understand and Apply Internet-of-Things Use Cases to Drive Organizational Success Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why your organization should care about the IoT’s potential to transform the service and the workplace, and how Info-Tech will support you as you identify and build your IoT use cases.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Understand core IoT use cases

    Analyze the scope of the IoT and the three most prominent enterprise use cases.

    • Understand and Apply Internet-of-Things Use Cases to Drive Organizational Success – Phase 1: Understand Core IoT Use Cases

    2. Build the business case for IoT applications

    Develop and prioritize use cases for the IoT using Info-Tech’s IoT Initiative Framework.

    • Understand and Apply Internet-of-Things Use Cases to Drive Organizational Success – Phase 2: Build the Business Case for IoT Initiatives

    3. Present IoT initiatives to stakeholders

    Present the IoT initiative to stakeholders and understand the way forward for the IoT initiative.

    • Understand and Apply Internet-of-Things Use Cases to Drive Organizational Success – Phase 3: Present IoT Initiatives to Stakeholders
    • Internet of Things Stakeholder Presentation Template
    [infographic]

    Customer Relationship Management Platform Selection Guide

    • Buy Link or Shortcode: {j2store}529|cart{/j2store}
    • member rating overall impact: 9.2/10 Overall Impact
    • member rating average dollars saved: $14,719 Average $ Saved
    • member rating average days saved: 32 Average Days Saved
    • Parent Category Name: Customer Relationship Management
    • Parent Category Link: /customer-relationship-management
    • Customer relationship management (CRM) suites are an indispensable part of a holistic strategy for managing end-to-end customer interactions.
    • After defining an approach to CRM, selection and implementation of the right CRM suite is a critical step in delivering concrete business value for marketing, sales, and customer service.
    • Despite the importance of CRM selection and implementation, many organizations struggle to define an approach to picking the right vendor and rolling out the solution in an effective and cost-efficient manner.
    • IT often finds itself in the unenviable position of taking the fall for CRM platforms that don't deliver on the promise of the CRM strategy.

    Our Advice

    Critical Insight

    • IT needs to be a trusted partner in CRM selection and implementation, but the business also needs to own the requirements and be involved from the beginning.
    • CRM requirements dictate the components of the target CRM architecture, such as deployment model, feature focus, and customization level. Savvy application directors recognize the points in the project where the CRM architecture model necessitates deviations from a "canned" roll-out plan.
    • CRM selection is a multi-step process that involves mapping target capabilities for marketing, sales, and customer service, assigning requirements across functional categories, determining the architecture model to prioritize criteria, and developing a comprehensive RFP that can be scored in a weighted fashion.
    • Companies that succeed with CRM implementation create a detailed roadmap that outlines milestones for configuration, security, points of implementation, data migration, training, and ongoing application maintenance.

    Impact and Result

    • A CRM platform that effectively meets the needs of marketing, sales, and customer service and delivers value.
    • Reduced costs during CRM selection.
    • Reduced implementation costs and time frame.
    • Faster time to results after implementation.

    Customer Relationship Management Platform Selection Guide Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Customer Relationship Management Platform Selection Guide – Speed up the process to build your business case and select your CRM solution.

    This blueprint will help you build a business case for selecting the right CRM platform, defining key requirements, and conducting a thorough analysis and scan of the ever-evolving CRM market space.

    • Customer Relationship Management Platform Selection Guide — Phases 1-3

    2. CRM Business Case Template – Document the key drivers for selecting a new CRM platform.

    Having a sound business case is essential for succeeding with a CRM. This template will allow you to document key drivers and impact, in line with the CRM Platform Selection Guide blueprint.

    • CRM Business Case Template

    3. CRM Request for Proposal Template

    Create your own request for proposal (RFP) for your customer relationship management (CRM) solution procurement process by customizing the RFP template created by Info-Tech.

    • CRM Request for Proposal Template

    4. CRM Suite Evaluation and RFP Scoring Tool

    The CRM market has many strong contenders and differentiation may be difficult. Instead of relying solely on reputation, organizations can use this RFP tool to record and objectively compare vendors according to their specific requirements.

    • CRM Suite Evaluation and RFP Scoring Tool

    5. CRM Vendor Demo Script

    Use this template to support your business's evaluation of vendors and their solutions. Provide vendors with scenarios that prompt them to display not only their solution's capabilities, but also how the tool will support your organization's particular needs.

    • CRM Vendor Demo Script

    6. CRM Use Case Fit Assessment Tool

    Use this tool to help build a CRM strategy for the organization based on the specific use case that matches your organizational needs.

    • CRM Use-Case Fit Assessment Tool
    [infographic]

    Further reading

    Customer Relationship Management Platform Selection Guide

    Speed up the process to build your business case and select your CRM solution.

    Table of Contents

    1. Analyst Perspective
    2. Executive Summary
    3. Blueprint Overview
    4. Executive Brief
    5. Phase 1: Understand CRM Functionality
    6. Phase 2: Build the Business Case and Elicit CRM requirements
    7. Phase 3: Discover the CRM Marketspace and Prepare for Implementation
    8. Conclusion

    Analyst Perspective

    A strong CRM platform is paramount to succeeding with customer engagement.

    Modern CRM platforms are the workhorses that provide functional capabilities and data curation for customer experience management. The market for CRM platforms has seen an explosion of growth over the last five years, as organizations look to mature their ability to deliver strong capabilities across marketing, sales, and customer service.

    IT needs to be a trusted partner in CRM selection and implementation, but the business also needs to own the requirements and be involved from the get-go.

    CRM selection must be a multistep process that involves defining target capabilities for marketing, sales, and customer service, prioritizing requirements across functional categories, determining the architecture model for the CRM environment, and developing a comprehensive RFP that can be scored in a weighted fashion.

    To succeed with CRM implementation, create a detailed roadmap that outlines milestones for configuration, security, points of implementation, data migration, training, and ongoing application maintenance.

    Photo of Ben Dickie, Research Lead, Customer Experience Strategy, Info-Tech Research Group. Ben Dickie
    Research Lead, Customer Experience Strategy
    Info-Tech Research Group

    Executive Summary

    Your Challenge

    Customer Relationship Management (CRM) suites are an indispensable part of a holistic strategy for managing end-to-end customer interactions. Selecting the right platform that aligns with your requirements is a significant undertaking.

    After defining an approach to CRM, selection and implementation of the right CRM suite is a critical step in delivering concrete business value for marketing, sales, and customer service.
    Common Obstacles

    Despite the importance of CRM selection and implementation, many organizations struggle to define an approach to picking the right vendor and rolling out the solution in an effective and cost-efficient manner.

    The CRM market is rapidly evolving and changing, making it tricky to stay on top of the space.

    IT often finds itself in the unenviable position of taking the fall for CRM platforms that don’t deliver on the promise of the CRM strategy.
    Info-Tech’s Approach

    CRM platform selection must be driven by your overall customer experience management strategy: link your CRM selection to your organization’s CXM framework.

    Determine if you need a CRM platform that skews toward marketing, sales, or customer service; leverage use cases to help guide selection.

    Ensure strong points of integration between CRM and other software such as MMS. A CRM should not live in isolation; it must provide a 360-degree view.

    Info-Tech Insight

    IT must work in lockstep with its counterparts in marketing, sales, and customer service to define a unified vision for the CRM platform.

    Info-Tech’s methodology for selecting the right CRM platform

    1. Understand CRM Features 2. Build the Business Case & Elicit CRM Requirements 3. Discover the CRM Market Space & Prepare for Implementation
    Phase Steps
    1. Define CRM platforms
    2. Classify table stakes & differentiating capabilities
    3. Explore CRM trends
    1. Build the business case
    2. Streamline requirements elicitation for CRM
    3. Construct the RFP
    1. Discover key players in the CRM landscape
    2. Engage the shortlist & select finalist
    3. Prepare for implementation
    Phase Outcomes
    • Consensus on scope of CRM and key CRM capabilities
    • CRM selection business case
    • Top-level use cases and requirements
    • Completed CRM RFP
    • CRM market analysis
    • Shortlisted vendor
    • Implementation considerations

    Guided Implementation

    A Guided Implementation (GI) is a series of calls with an Info-Tech analyst to help implement our best practices in your organization.

    The CRM purchase process should be broken into segments:

    1. CRM vendor shortlisting with this buyer’s guide
    2. Structured approach to selection
    3. Contract review

    What does a typical GI on this topic look like?

    Phase 1

    Phase 2

    Phase 3

    Call #1: Understand what a CRM platform is and the “art of the possible” for sales, marketing, and customer service. Call #2: Build the business case to select a CRM.

    Call #3: Define your key CRM requirements.

    Call #4: Build procurement items such as an RFP.
    Call #5: Evaluate the CRM solution landscape and shortlist viable options.

    Call #6: Review implementation considerations.

    Info-Tech offers various levels of support to best suit your needs

    DIY Toolkit

    Guided Implementation

    Workshop

    Consulting

    "Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful." "Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track." "We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place." "Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project."

    Diagnostics and consistent frameworks used throughout all four options

    INFO~TECH RESEARCH GROUP

    Customer Relationship Management Platform Selection Guide

    Speed up the process to build your business case and select your CRM solution.

    EXECUTIVE BRIEF

    Info-Tech Research Group Inc. is a global leader in providing IT research and advice. Info-Tech’s products and services combine actionable insight and relevant advice with ready-to-use tools and templates that cover the full spectrum of IT concerns.
    © 1997-2022 Info-Tech Research Group Inc.

    What exactly is a CRM platform?

    Our Definition: A customer relationship management (CRM) platform (or suite) is a core enterprise application that provides a broad feature set for supporting customer interaction processes, typically across marketing, sales and customer service. These suites supplant more basic applications for customer interaction management (such as the contact management module of an enterprise resource planning (ERP) platform or office productivity suite).

    A customer relationship management suite provides many key capabilities, including but not limited to:

    • Account management
    • Order history tracking
    • Pipeline management
    • Case management
    • Campaign management
    • Reports and analytics
    • Customer journey execution

    A CRM suite provides a host of native capabilities, but many organizations elect to tightly integrate their CRM solution with other parts of their customer experience ecosystem to provide a 360-degree view of their customers.

    Stock image of a finger touching a screen showing a stock chart.

    Info-Tech Insight

    CRM feature sets are rapidly evolving. Focus on the social component of sales, marketing, and service management features, as well as collaboration, to get the best fit for your requirements. Moreover, consider investing in best-of-breed social media management platforms (SMMPs) and internal collaboration tools to ensure sufficient functionality.

    Build a cohesive CRM selection approach that aligns business goals with CRM capabilities.

    Info-Tech Insight

    Customers expect to interact with organizations through the channels of their choice. Now more than ever, you must enable your organization to provide tailored customer experiences.

    Customer expectations are on the rise: meet them!

    A CRM platform is a crucial system for enabling good customer experiences.

    CUSTOMER EXPERIENCE IS EVOLVING

    1. Thoughtfulness is in
        Connect with customers on a personal level
    2. Service over products
        The experience is more important than the product
    3. Culture is now number one
        Culture is the most overlooked piece of customer experience strategy
    4. Engineering and service finally join forces
        Companies are combining their technology and service efforts to create strong feedback loops
    5. The B2B world is inefficiently served
        B2B needs to step up with more tools and a greater emphasis placed on customer experience

    (Source: Forbes, 2019)

    Identifying organizational objectives of high priority will assist in breaking down business needs and CRM objectives. This exercise will better align the CRM systems with the overall corporate strategy and achieve buy-in from key stakeholders.

    A strong CRM platform supports a range of organizational objectives for customer engagement.

    Increase Revenue Enable lead scoring Deploy sales collateral management tools Improve average cost per lead via a marketing automation tool
    Enhance Market Share Enhance targeting effectiveness with a CRM Increase social media presence via an SMMP Architect customer intelligence analysis
    Improve Customer Satisfaction Reduce time-to-resolution via better routing Increase accessibility to customer service with live chat Improve first contact resolution with customer KB
    Increase Customer Retention Use a loyalty management application Improve channel options for existing customers Use customer analytics to drive targeted offers
    Create Customer-Centric Culture Ensure strong training and user adoption programs Use CRM to provide 360-degree view of all customer interactions Incorporate the voice of the customer into product development

    Succeeding with CRM selection and implementation has a positive effect on driving revenues and decreasing costs

    There are three buckets of metrics and KPIs where CRM will drive improvements

    The metrics of a smooth CRM selection and implementation process include:

    • Better alignment of CRM functionality to business needs.
    • Better functionality coverage of the selected platform.
    • Decreased licensing costs via better vendor negotiation.
    • Improved end-user satisfaction with the deployed solution.
    • Fewer errors and rework during implementation.
    • Reduced total implementation costs.
    • Reduced total implementation time.

    A successful CRM deployment drives revenue…

    • Increased customer acquisition due to enhanced accuracy of segmentation and targeting, superior lead qualification, and pipeline management.
    • Increased customer satisfaction and retention due to targeted campaigns (e.g. customer-specific deals), quicker service incident resolution, and longitudinal relationship management.
    • Increased revenue per customer due to comprehensive lifecycle management tools, social engagement, and targeted upselling of related products and services (enabled by better reporting/analytics).

    A successful CRM deployment decreases cost…

    • Deduplication of effort across business domains as marketing, sales, and service now have a common repository of customer information and interaction tools.
    • Increased sales and service agent efficiency due to their focus on selling and resolution, rather than administrative tasks and overhead.
    • Reduced cost-to-sell and cost-to-serve due to automation of activities that were manually intensive.
    • Reduced cost of accurate data due to embedded reporting and analytics functionality.

    CRM platforms sit at the core of a well-rounded customer engagement ecosystem

    At the center is 'Customer Relationship Management Platform' surrounded by 'Web Experience Management Platform', 'E-Commerce & Point-of-Sale Solutions', 'Social Media Management Platform', 'Customer Intelligence Platform', 'Customer Service Management Tools', and 'Marketing Management Suite'.

    Customer Experience Management (CXM) Portfolio

    Customer relationship management platforms are increasingly expansive in functional scope and foundational to an organization’s customer engagement strategy. Indeed, CRMs form the centerpiece for a comprehensive CXM system, alongside tools such as customer intelligence platforms and adjacent point solutions for sales, marketing, and customer service.

    Review Info-Tech’s CXM blueprint below to build a complete, end-to-end customer interaction solution portfolio that encompasses CRM alongside other critical components. The CXM blueprint also allows you to develop strategic requirements for CRM based on customer personas and external market analysis.

    Build a Strong Technology Foundation for Customer Experience Management

    Sample of the 'Build a Strong Technology Foundation for Customer Experience Management' blueprint. Design an end-to-end technology strategy to drive sales revenue, enhance marketing effectiveness, and create compelling experiences for your customers.

    View the blueprint

    Considering a CRM switch? Switching software vendors drives high satisfaction

    Eighty percent of organizations are more satisfied after changing their software vendor.

    • Most organizations see not only a positive change in satisfaction with their new vendor, but also a substantial change in satisfaction.
    • What matters is making sure your organization is well-positioned to make a switch.
    • When it comes to switching software vendors, the grass really can be greener on the other side.

    Over half of organizations are 60%+ more satisfied after changing their vendor.

    (Source: Info-Tech Research Group, "Switching Software Vendors Overwhelmingly Drives Increased Satisfaction", 2020.)

    IT is critical to the success of your CRM selection and rollout

    Today’s shared digital landscape of the CIO and CMO

    Info-Tech Insight

    Technology is the key enabler of building strong customer experiences: IT must stand shoulder to shoulder with the business to develop a technology framework for customer relationship management.

    CIO

    IT Operations

    Service Delivery and Management

    IT Support

    IT Systems and Application

    IT Strategy and Governance

    Cybersecurity
    Collaboration and Partnership

    Digital Strategy = Transformation
    Business Goals | Innovation | Leadership | Rationalization

    Customer Experience
    Architecture | Design | Omnichannel Delivery | Management

    Insight (Market Facing)
    Analytics | Business Intelligence | Machine Learning | AI

    Marketing Integration + Operating Model
    Apps | Channels | Experiences | Data | Command Center

    Master Data
    Customer | Audience | Industry | Digital Marketing Assets
    CMO

    PEO Media

    Brand Management

    Campaign Management

    Marketing Tech

    Marketing Ops

    Privacy, Trust, and Regulatory Requirements

    (Source: ZDNet, 2020)

    CRM by the numbers

    1/3

    Statistical analysis of CRM projects indicates failures vary from 18% to 69%. Taking an average of those analyst reports, about one-third of CRM projects are considered a failure. (Source: CIO Magazine, 2017)

    92%

    92% of organizations report that CRM use is important for accomplishing revenue objectives. (Source: Hall, 2020)

    40%

    In 2019, 40% of executives name customer experience the top priority for their digital transformation. (Source: CRM Magazine, 2019)

    Case Study

    Align strategy and technology to meet consumer demand.
    INDUSTRY
    Entertainment
    SOURCE
    Forbes, 2017
    Challenge

    Beginning as a mail-out service, Netflix offered subscribers a catalog of videos to select from and have mailed to them directly. Customers no longer had to go to a retail store to rent a video. However, the lack of immediacy of direct mail as the distribution channel resulted in slow adoption.

    Blockbuster was the industry leader in video retail but was lagging in its response to industry, consumer, and technology trends around customer experience.

    Solution

    In response to the increasing presence of tech-savvy consumers on the internet, Netflix invested in developing its online platform as its primary distribution channel. The benefit of doing so was two-fold: passive brand advertising (by being present on the internet) and meeting customer demands for immediacy and convenience. Netflix also recognized the rising demand for personalized service and created an unprecedented, tailored customer experience.

    Results

    Netflix’s disruptive innovation is built on the foundation of great customer experience management. Netflix is now a $28-billion company, which is tenfold what Blockbuster was worth.

    Netflix used disruptive technologies to innovatively build a customer experience that put it ahead of the long-time video rental industry leader, Blockbuster.

    CRM Buyer’s Guide

    Phase 1

    Understand CRM Features

    Phase 1

    1.1 Define CRM platforms

    1.2 Classify table stakes & differentiating capabilities

    1.3 Explore CRM trends

    Phase 2

    2.1 Build the business case

    2.2 Streamline requirements elicitation for CRM

    2.3 Construct the RFP

    Phase 3

    3.1 Discover key players in the CRM landscape

    3.2 Engage the shortlist & select finalist

    3.3 Prepare for implementation

    This phase will walk you through the following activities:

    • Set a level of understanding of CRM technology.
    • Define which CRM features are table stakes (standard) and which are differentiating.
    • Identify the “Art of the Possible” in a modern CRM from a sales, marketing, and service lens.

    This phase involves the following participants:

    • CIO
    • Applications manager
    • Project manager
    • Sales executive
    • Marketing executive
    • Customer service executive

    Understand CRM table stakes features

    Organizations can expect nearly all CRM vendors to provide the following functionality.

    Lead Management Pipeline Management Contact Management Campaign Management Customer Service Management
    • Tracks and captures a lead’s information, automatically building a profile. Leads are then qualified through contact scoring models. Assigning leads to sales is typically automated.
    • Enables oversight over future sales. Includes revenue forecasting based on past/present trends, tracking sales velocity, and identifying ineffective sales processes.
    • Tracks and stores customer data, including demography, account and billing history, social media, and contact information. Typically, records and fields can be customized.
    • Provides integrated omnichannel campaign functionality and data analysis of customer intelligence. Data insights can be used to drive new and effective marketing campaigns.
    • Provides integrated omnichannel customer experiences to provide convenient service. Includes case and ticket management, automated escalation rules, and third-party integrations.

    Identify differentiating CRM features

    While not always “must-have” functionality, these features may be the final dealbreaker when deciding between two CRM vendors.

    Image of clustered screens with various network and business icons surounding them.
    • Workflow Automation
      Automate repetitive tasks by creating workflows that trigger actions or send follow-up reminders for next steps.
    • Advanced Analytics and Reporting
      Provides customized dashboard visualizations, detailed reporting, AI-driven virtual assistants, data extraction & analysis, and ML forecasting.
    • Customizations and Open APIs
      Broad range of available customizations (e.g. for dashboards and fields), alongside ease of integration (e.g. via plugins or APIs).
    • Document Management
      Out-of-the-box centralized content repository for storing, uploading, and sharing documents.
    • Mobile Support
      Ability to support mobile devices, OSes, and platforms with a native application or HTML-based web-access.
    • Project and Task Management
      Native project and task management functionality, enhancing cross-team organization and communication.
    • Configure, Price, Quote (CPQ)
      Create and send quotes or proposals to prospective and current customers.

    Features aren’t everything – be wary of common CRM selection pitfalls

    You can have all the right features, but systemic problems will lead to poor CRM implementation. Dig out these root causes first to ensure a successful CRM selection.

    50% of organizations believe the quality of their CRM data is “very poor” or “neutral.”

    Without addressing data governance issues, CRMs will only be as good as your data.

    Source: (Validity 2020)
    27% of organizations report that bad data costs them 10% or more in lost revenue annually.
    42% rate the trust that users have in their data as “high” or “very high.”
    54% believe that sales forecasts are accurate or very accurate.
    69% attribute poor CRM governance to missing or incomplete data, followed by duplicate data, incorrect data, and expired data. Other data issues include siloed data or disparate systems.
    73% believe that they do not have a 360-degree view of their customers.

    Ensure you understand the “art of the possible” in the CRM landscape

    Knowing what is possible will help funnel which features are most suitable for your organization – having all the bells and whistles does not always equal strong ROI.

    Holistically examine the potential of any CRM solution through three main lenses: Stock image of a person working with dashboards.

    Sales

    Identify sales opportunities through recording customers’ interactions, generating leads, nurturing contacts, and forecasting revenues.
    Stock image of people experiencing digital ideas.

    Marketing

    Analyze customer interactions to identify upsell and cross-sell opportunities, drive customer loyalty, and use customer data for targeted campaigns.
    Stock image of a customer service representative.

    Customer Service

    Improve and optimize customer engagement and retention, leveraging customer data to provide round-the-clock omnichannel experiences.

    Art of the possible: Sales

    Stock image of a person working with dashboards.

    TRACK PROSPECT INTERACTIONS

    Want to engage with a prospect but don’t know what to lead with? CRM solutions can track and analyze many of the interactions a prospect has with your organization, including with fellow staff, their clickthrough rate on marketing material, and what services they are downloading on your website. This information can then auto-generate tasks to begin lead generation.

    COORDINATE LEAD SCORING

    Information captured from a prospect is generated into contact cards; missing data (such as name and company) can be auto-captured by the CRM via crawling sites such as LinkedIn. The CRM then centralizes and scores (according to inputted business rules) a lead’s potential, ensuring sales teams coordinate and keep a track of the lead’s journey without wrongful interference.

    AI-DRIVEN REVENUE FORECASTING

    Generate accurate forecasting reports using AI-driven “virtual assistants” within the CRM platform. These assistants are personal data scientists, quickly noting discrepancies, opportunities, and what-if scenarios – tasks that might take weeks to do manually. This pulled data is then auto-forecasted, with the ability to flexibly adjust to real-time data.

    Art of the possible: Marketing

    Stock image of people experiencing digital ideas.

    DRIVE LOYALTY

    Data captured and analyzed in the CRM from customer interactions builds profiles and a deeper understanding of customers’ interests. With this data, marketing teams can deliver personalized promotions and customer service to enhance loyalty – from sending a discount on a product the customer was browsing on the website, to providing notifications about delivery statuses.

    AUTOMATE WORKFLOWS

    Building customer profiles, learning spending habits, and charting a customer’s journey for upselling or cross-selling can be automated through workflows, saving hours of manual work. These workflows can immediately respond to customer enquiries or deliver offers to the customer’s preferred channel based on their prior usage.

    TARGETED CAMPAIGNING

    Information attained through a CRM platform directly informs any marketing strategy: identifying customer segments, spending habits, building a better product based on customer feedback, and identifying high-spending customers. With any new product or offering, it is straightforward for marketing teams to understand where to target their next campaign for highest impact.

    Art of the possible: Customer service

    Stock image of a customer service representative.

    OMNICHANNEL SUPPORT

    Rapidly changing demographics and modes of communications require an evolution toward omnichannel engagement. Many customers now expect to communicate with contact centers not just by voice, but via social media. Agents need customer information synced across each channel they use, meeting the customer’s needs where they are.

    INTELLIGENT SELF-SERVICE PORTALS

    Customers want their issues resolved as quickly as possible. Machine-learning self-service options deliver personalized customer experiences, which also reduce both agent call volume and support costs for the organization.

    LEVERAGING ANALYTICS

    The future of customer service is tied up with analytics. This not only entails AI-driven capabilities that fetch the agent relevant information, skills-based routing, and using biometric data (e.g. speech) for security. It also feeds operations leaders’ need for easy access to real insights about how their customers and agents are doing.

    Best-of-Breed Point Solutions

    Full CRM Suite

    Blue smiley face. Benefits
    • Features may be more advanced for specific functional areas and a higher degree of customization may be possible.
    • If a potential delay in real-time customer data transfer is acceptable, best-of-breeds provide a similar level of functionality to suites for a lower price.
    • Best-of-breeds allow value to be realized faster than suites, as they are easier and faster to implement and configure.
    • Rip and replace is easier, and vendor updates are relatively quick to market.
    Benefits
    • Everyone in the organization works from the same set of customer data.
    • There is a “lowest common denominator” for agent learning as consistent user interfaces lower learning curves and increase efficiency in usage.
    • There is a broader range of functionality using modules.
    • Integration between functional areas will be strong and the organization will be in a better position to enable version upgrades without risking invalidation of an integration point between separate systems.
    Green smiley face.
    Purple frowny face. Challenges
    • Best-of-breeds typically cover less breadth of functionality than suites.
    • There is a lack of uniformity in user experience across best-of-breeds.
    • Data integrity risks are higher.
    • Variable infrastructure may be implemented due to multiple disparate systems, which adds to architecture complexity and increased maintenance.
    • There is potential for redundant functionality across multiple best-of-breeds.
    Challenges
    • Suites exhibit significantly higher costs compared to point solutions.
    • Suite module functionality may not have the same depth as point solutions.
    • Due to high configuration availability and larger-scale implementation requirements, the time to deploy is longer than point solutions.
    Orange frowny face.
    Info-Tech Insight

    Even if a suite is missing a potential module, the proliferation of app extensions, integrations, and services could provide a solution. Salesforce’s AppExchange, for instance, offers a plethora of options to extend its CRM solution – from telephony integration, to gamification.

    CRM Buyer’s Guide

    Phase 2

    Build the Business Case & Elicit CRM Requirements

    Phase 1

    1.1 Define CRM platforms

    1.2 Classify table stakes & differentiating capabilities

    1.3 Explore CRM trends

    Phase 2

    2.1 Build the business case

    2.2 Streamline requirements elicitation for CRM

    2.3 Construct the RFP

    Phase 3

    3.1 Discover key players in the CRM landscape

    3.2 Engage the shortlist & select finalist

    3.3 Prepare for implementation

    This phase will walk you through the following activities:

    • Identify goals, objectives, challenges, and costs to inform the business case for a new CRM platform.
    • Elicit and prioritize key requirements for your platform.
    • Port the requirements into Info-Tech’s CRM RFP Template.

    This phase involves the following participants:

    • CIO
    • Applications manager
    • Project manager
    • Sales executive
    • Marketing executive
    • Customer service executive

    Right-size the CRM selection team to ensure you get the right information but are still able to move ahead quickly

    Full-Time Resourcing: At least one of these five team members must be allocated to the selection initiative as a full-time resource.

    A silhouetted figure.

    IT Leader

    A silhouetted figure.

    Technical Lead

    A silhouetted figure.

    Business Analyst/
    Project Manager

    A silhouetted figure.

    Business Lead

    A silhouetted figure.

    Process Expert(s)

    This team member is an IT director or CIO who will provide sponsorship and oversight from the IT perspective. This team member will focus on application security, integration, and enterprise architecture. This team member elicits business needs and translates them into technology requirements. This team member will provide sponsorship from the business needs perspective. Typically, a CMO or SVP of sales. These team members are the sales, marketing, and service process owners who will help steer the CRM requirements and direction.

    Info-Tech Insight

    It is critical for the selection team to determine who has decision rights. Organizational culture will play the largest role in dictating which team member holds the final say for selection decisions. For more information on stakeholder management and involvement, see this guide.

    Be prepared to define what issues you are trying to address and why a new CRM is the right approach

    Identify the current state and review the background of what you’ve done leading up to this point, goals you’ve been asked to meet, and challenges in solving known problems to help to set the stage for why your proposed solution is needed. If your process improvements have taken you as far as you can go without improved workflows or data, specify where the gaps are.
    Arrows with icons related to the text on the right merging into one arrow. Alignment

    Alignment to strategic goals is always important, but that is especially true with CRM because customer relationship management platforms are at the intersection of your organization and your customers. What are the strategic marketing, sales and customer service goals that you want to realize (in whole or in part) by improving your CRM ecosystem?

    Impact to your business

    Identify areas where your customers may be impacted by poor experiences due to inadequate or aging technology. What’s the impact on customer retention? On revenue?

    Impact to your organization

    Define how internal stakeholders within the organization are impacted by a sub-optimal CRM experience – what are their frustrations and pain points? How do issues with your current CRM environment prevent teams in sales, marketing, or service from doing their jobs?

    Impact to your department

    Describe the challenges within IT of using disparate systems, workarounds, poor data and reporting, lack of automation, etc., and the effect these challenges have on IT’s goals.

    Align the CRM strategy with the corporate strategy

    Corporate Strategy Unified Strategy CRM Strategy
    Spectrum spanning all columns.
    Your corporate strategy:
    • Conveys the current state of the organization and the path it wants to take.
    • Identifies future goals and business aspirations.
    • Communicates the initiatives that are critical for getting the organization from its current state to the future state.
    • The CRM strategy and the rationale for deploying a new CRM can be and should be linked, with metrics, to the corporate strategy and ultimate business objectives (such as improving customer acquisition, entering new segments, or improving customer lifetime value).
    Your CRM strategy:
    • Communicates the organization’s budget and spending on CRM.
    • Identifies IT initiatives that will support the business and key CRM objectives.
    • Outlines staffing and resourcing for CRM initiatives.
    CRM projects are more successful when the management team understands the strategic importance and the criticality of alignment. Time needs to be spent upfront aligning business strategies with CRM capabilities. Effective alignment between sales, marketing, customer service, operations, IT, and the business should happen daily. Alignment doesn’t just need to occur at the executive level, but also at each level of the organization.

    2.1 Create your list of goals and milestones for CRM

    1-3 hours

    Input: Corporate strategy, Target key performance indicators, End-user satisfaction results (if applicable)

    Output: Prioritized list of goals with milestones that can be met with a new or improved CRM solution

    Materials: Whiteboard/flip charts, CRM Business Case Template

    Participants: CIO, Application managers, CMO/SVP sales, Marketing, sales or service SMEs

    1. Review strategic goals to identify alignment to your CRM selection project. For example, digital transformation may be enhanced or enabled with a CRM solution that supports better outreach to key customer segments through improved campaign management.
    2. Next, brainstorm tactical goals with your colleagues.
    3. Identify specific goals the organization has set for the business that may be supported by improved customer prospecting, customer service, or analytics functionality through a better CRM solution.
    4. Identify specific goals your organization will be able to make possible with a new or improved CRM solution.
    5. Prioritize this list and lead with the most important goal that can be reached at the one-year, six-month, and three-month milestones.
    6. Document in the goals section of your business case.

    Download the CRM Business Case Template and record the outputs of this exercise in the strategic business goals, business drivers, and technical drivers slides.

    Identify what challenges exist with the current environment

    Ensure you are identifying issues at a high level, so as not to drown in detail, but still paint the right picture. Identify technical issues that are impacting customer experience or business goals. Typical complaints for CRM solutions that are old or have been outgrown include:

    1.

    Lack of a flexible, configurable customer data model that supports complex relationships between accounts and contacts.

    2.

    Lack of a flexible, configurable customer data model that supports complex relationships between accounts and contacts.

    3.

    Lack of meaningful reports and useable dashboards, or difficulty in surfacing them.

    4.

    Poor change enablement resulting in business interruptions.

    5.

    Inability to effectively automate routine sales, marketing, or service tasks at scale via a workflow tool.

    6.

    Lack of proper service management features, such as service knowledge management.

    7.

    Inability to ingest customer data at scale (for example, no ability to automatically log e-mails or calls).

    8.

    Major technical deficiencies and outages – the incumbent CRM platform goes down, causing business disruption.

    9.

    The platform itself doesn’t exist in the current state – everything is done in Microsoft Excel!

    Separate business issues from technical issues, but highlight where they’re connected and where technical issues are causing business issues or preventing business goals from being reached.

    Before switching vendors, evaluate your existing CRM to see if it’s being underutilized or could use an upgrade

    The cost of switching vendors can be challenging, but it will depend entirely on the quality of data and whether it makes sense to keep it.
    • Achieving success when switching vendors first requires reflection. We need to ask why we are dissatisfied with our incumbent software.
    • If the product is old and inflexible, the answer may be obvious, but don’t be afraid to include your incumbent in your evaluation if your issues might be solved with an upgrade.
    • Look at your use-case requirements to see where you want to take the CRM solution and compare them to your incumbent’s roadmap. If they don’t match, switching vendors may be the only solution. If your roadmaps align, see if you’re fully leveraging the solution or will be able to start working through process improvements.
    Pie graph with a 20% slice. Pie graph with a 25% slice.

    20%

    Small/Medium Enterprises

    25%

    Large Enterprises
    only occasionally or rarely/never use their software (Source: Software Reviews, 2020; N = 45,027)
    Fully leveraging your current software now will have two benefits:
    1. It may turn out that poor leveraging of your incumbent software was the problem all along; switching vendors won’t solve the problem by itself. As the data to the right shows, a fifth of small/medium enterprises and a quarter of large enterprises do not fully leverage their incumbent software.
    2. If you still decide to switch, you’ll be in a good negotiating position. If vendors can see you are engaged and fully leveraging your software, they will be less complacent during negotiations to win you over.
    Info-Tech Insight

    Switching vendors won’t improve poor internal processes. To be fully successful and meet the goals of the business case, new software implementations must be accompanied by process review and improvement.

    2.2 Create your list of challenges as they relate to your goals and their impacts

    1-2 hours

    Input: Goals lists, Target key performance indicators, End-user satisfaction results (if applicable)

    Output: Prioritized list of challenges preventing or hindering customer experiences

    Materials: Whiteboard/flip charts, CRM Business Case Template

    Participants: CIO, Application managers, CMO/SVP sales, Marketing, sales, or service SMEs

    1. Brainstorm with your colleagues to discuss your challenges with CRM today from an application and process lens.
    2. Identify how these challenges are impacting your ability to meet the goals and identify any that are creating customer-facing issues.
    3. Group together like areas and arrange in order of most impactful. Identify which of these issues will be most relevant to the business case for a new CRM platform.
    4. Document in the current-state section of your business case.
    5. Discuss and determine if the incumbent solution can meet your needs or if you’ll need to replace it with a different product.

    Download the CRM Business Case Template and document the outputs of this exercise in the current-state section of your business case.

    Determine costs of the solution

    Ensure the business case includes both internal and external costs related to the new CRM platform, allocating costs of project managers to improve accuracy of overall costs and level of success.

    CRM solutions include application costs and costs to design processes, install, and configure. These start-up costs can be a significant factor in whether the initial purchase is feasible.

    CRM Vendor Costs

    • Application licensing
    • Implementation and configuration
    • Professional services
    • Maintenance and support
    • Training
    • 3rd Party add-ons
    • Data transformation
    • Integration
    When thinking about vendor costs, also consider the matching internal cost associated with the vendor activity (e.g. data cleansing, internal support).

    Internal Costs

    • Project management
    • Business readiness
    • Change management
    • Resourcing (user groups, design/consulting, testing)
    • Training
    • Auditors (if regulatory requirements need vetting)
    Project management is a critical success factor at all stages of an enterprise application initiative from planning to post-implementation. Ensuring that costs for such critical areas are accurately represented will contribute to success.

    Download the blueprint Improve Your Statements of Work to Hold Your Vendors Accountable to define requirements for installation and configuration.

    Bring in the right resources to guarantee success. Work with the PMO or project manager to get help with creating the SOW.

    60% of IT projects are NOT finished “mostly or always” on time (Wellingtone, 2018).

    55% of IT personnel feel that the business objectives of their software projects are clear to them (Geneca, 2017).

    Document costs and expected benefits of the new CRM

    The business case should account for the timing of both expenditures and benefits. It is naïve to expect straight-line benefit realization or a big-bang cash outflow related to the solution implementation. Proper recognition and articulation of ramp-up time will make your business case more convincing.

    Make sure your timelines are realistic for benefits realization, as these will be your project milestones and your metrics for success.

    Example:
    Q1-Q2 Q3-Q6 Q6 Onwards

    Benefits at 25%

    At the early stages of an implementation, users are still learning the new system and go-live issues are being addressed. Most of the projected process improvements are likely to be low, zero, or even negative.

    Benefits at 75%

    Gradually, as processes become more familiar, an organization can expect to move closer to realizing the forecasted benefits or at least be in a position to recognize a positive trend toward their realization.

    Benefits at 100%

    In an ideal world, all projected benefits are realized at 100% or higher. This can be considered the stage where processes have been mastered, the system is operating smoothly, and change has been broadly adopted. In reality, benefits are often overestimated.

    Costs at 50%

    As with benefits, some costs may not kick in until later in the process or when the application is fully operational. In the early phases of implementation, factor in the cost of overlapping technology where you’ll need to run redundant systems and transition any data.

    Costs at 100%

    Costs are realized quicker than benefits as implementation activities are actioned, licensing and maintenance costs are introduced, and resourcing is deployed to support vendor activities internally. Costs that were not live in the early stages are an operational reality at this stage.

    Costs at 100%+

    Costs can be expected to remain relatively static past a certain point, if estimates accurately represented all costs. In many instances, costs can exceed original estimates in the business case, where costs were either underestimated, understated, or missed.

    2.3 Document your costs and expected benefits

    1-2 hours

    Input: Quotes with payment schedule, Budget

    Output: Estimated payment schedule and cost breakdown

    Materials: Spreadsheet or whiteboard, CRM Business Case Template

    Participants: CIO, Application managers, CMO/SVP sales, Marketing, sales, or service SMEs

    1. Estimate costs for the CRM solution. If you’re working with a vendor, provide the initial requirements to quote; otherwise, estimate as closely as you’re able.
    2. Calculate the five-year total cost for the solution to ensure the long-term budget is calculated.
    3. Break down costs for licenses, implementation, training, internal support, and hardware or hosting fees.
    4. Determine a reasonable breakdown of costs for the first year.
    5. Identify where residual costs of the old system may factor in if there are remaining contract obligations during the technology transition.
    6. Create a list of benefits expected to be realized within the same timeline.

    Sample of the table on the previous slide.

    Download the CRM Business Case Template and document the outputs of this exercise in the current-state section of your business case.

    Identify risks and dependencies to mitigate barriers to success as you look to roll out a CRM suite

    A risk assessment will be helpful to better understand what risks need to be mitigated to make the project a success and what risks are pending should the solution not be approved or be delayed.

    Risk Criteria Relevant Questions
    Timeline Uncertainty
    • How much risk is associated with the timeline of the CRM project?
    • Is this timeline realistic and can you reach some value in the first year?
    Success of Similar Projects
    • Have we undertaken previous projects that are similar?
    • Were those successful?
    • Did we note any future steps for improvement?
    Certainty of Forecasts
    • Where have the numbers originated?
    • How comfortable are the sponsors with the revenue and cost forecasts?
    Chance of Cost Overruns
    • How likely is the project to have cost overruns?
    • How much process and design work needs to be done prior to implementation?
    Resource Availability
    • Is this a priority project?
    • How likely are resourcing issues from a technical and business perspective?
    • Do we have the right resources?
    Change During Delivery
    • How volatile is the area in which the project is being implemented?
    • Are changes in the environment likely?
    • How complex are planned integrations?

    2.4 Identify risks to the success of the solution rollout and mitigation plan

    1-2 hours

    Input: List of goals and challenges, Target key performance indicators

    Output: Prioritized list of challenges preventing or hindering improvements for the IT teams

    Materials: Whiteboard/flip charts, CRM Business Case Template

    Participants: CIO, Application managers, CMO/SVP sales, Marketing, sales, or service SMEs

    1. Brainstorm with your colleagues to discuss potential roadblocks and risks that could impact the success of the CRM project.
    2. Identify how these risks could impact your project.
    3. Document the ones that are most likely to occur and derail the project.
    4. Discuss potential solutions to mitigate risks.

    Download the CRM Business Case Template and document the outputs of this exercise in the risk and dependency section of your business case. If the risk assessment needs to be more complex, complete the Risk Indicator Analysis in Info-Tech’s Business Case Workbook.

    Start requirements gathering by identifying your most important use cases across sales, marketing, and service

    Add to your business case by identifying which top-level use cases will meet your goals.

    Examples of target use cases for a CRM project include:

    • Enhance sales acquisition capabilities (i.e. via pipeline management)
    • Enhance customer upsell and cross-sell capabilities
    • Improve customer segmentation and targeting capabilities for multi-channel marketing campaigns
    • Strengthen customer care capabilities to improve customer satisfaction and retention (i.e. via improved case management and service knowledge management)
    • Create actionable insights via enhanced reporting and analytics

    Info-Tech Insight

    Lead with the most important benefit and consider the timeline. Can you reach that goal and report success to your stakeholders within the first year? As you look toward that one-year goal, you can consider secondary benefits, some of which may be opportunities to bring early value in the solution.

    Benefits of a successful deployment of use cases will include:
    • Improved customer satisfaction
    • Improved operational efficiencies
    • Reduced customer turnover
    • Increased platform uptime
    • License or regulatory compliance
    • Positioned for growth

    Typically, we see business benefits in this order of importance. Lead with the outcome that is most important to your stakeholders.

    • Net income increases
    • Revenue generators
    • Cost reductions
    • Improved customer service

    Consider perspectives of each stakeholder to ensure functionality needs are met and high satisfaction results

    Best of breed vs. “good enough” is an important discussion and will feed your success.

    Costs can be high when customizing an ill-fitting module or creating workarounds to solve business problems, including loss of functionality, productivity, and credibility.

    • Start with use cases to drive the initial discussion, then determine which features are mandatory and which are nice-to-haves. Mandatory features will help determine high success for critical functionality and identify where “good enough” is an acceptable state.
    • Consider the implications to implementation and all use cases of buying an all-in-one solution, integration of multiple best-of-breed solutions, or customizing features that were not built into a solution.
    • Be prepared to shelve a use case for this solution and look to alternatives for integration where mandatory features cannot meet highly specialized needs that are outside of traditional CRM solutions.

    Pros and Cons

    Build vs. Buy

    Multi-Source Best of Breed

    Flexibility
    vs.
    architectural complexity

    Vendor Add-Ons & Integrations

    Lower support costs
    vs.
    configuration

    Multi-source Custom

    Flexibility
    vs.
    high skills requirements

    Single Source

    Lower support costs
    vs.
    configuration

    2.5 Define use cases and high-level features for meeting business and technical goals

    1-2 hours

    Input: List of goals and challenges

    Output: Use cases to be used for determining requirements

    Materials: Whiteboard/flip charts, CRM Business Case Template

    Participants: CIO, Application managers, CMO/SVP sales, Marketing, sales, or service SMEs

    1. Identify the key customer engagement use cases that will support your overall goals as defined in the previous section.
    2. The following slide has examples of use case domains that will be enhanced from a CRM platform.
    3. Define high-level goals you wish to achieve in the first year and longer term. If you have more specific KPIs to add, and it is a requirement for your organization’s documentation, add them to this section.
    4. Take note of where processes will need to be improved to benefit from these use-case solutions – the tools are only as good as the process behind them.

    Download the CRM Business Case Template and document the outputs from this exercise in the current-state section of your business case.

    Understand the dominant use-case scenarios across organizations to narrow the list of potential CRM solutions

    Sales
    Enablement

    • Generate leads through multiple channels.
    • Rapidly sort, score, and prioritize leads based on multiple criteria.
    • Create in-depth sales forecasts segmented by multiple criteria (territory, representative, etc.).

    Marketing
    Management

    • Manage marketing campaigns across multiple channels (web, social, email, etc.).
    • Aggregate and analyze customer data to generate market intelligence.
    • Build and deploy customer-facing portals.

    Customer Service
    Management

    • Generate tickets, and triage customer service requests through multiple channels.
    • Track customer service interactions with cases.
    • There is a need to integrate customer records with contact center infrastructure.
    Info-Tech Insight

    Use your understanding of the CRM use case to accelerate the vendor shortlisting process. Since the CRM use case has a direct impact on the prioritization of a platform’s features and capabilities, you can rapidly eliminate vendors from contention or designate superfluous modules as out-of-scope.

    2.5.1 Use Info-Tech’s CRM Use-Case Fit Assessment Tool to align your CRM requirements to the vendor use cases

    30 min

    Input: Understanding of business objectives for CRM project, Use-Case Fit Assessment Tool

    Output: Use-case suitability

    Materials: Use-Case Fit Assessment Tool

    Participants: Core project team, Project managers

    1. Use the Use-Case Fit Assessment Tool to understand how your unique business requirements map into which CRM use case.
    2. This tool will assess your answers and determine your relative fit against the use-case scenarios.
    3. Fit will be assessed as “Weak,” “Moderate,” or “Strong.”
      1. Consider the common pitfalls, which were mentioned earlier, that can cause IT projects to fail. Plan and take clear steps to avoid or mitigate these concerns.
      2. Note: These use-case scenarios are not mutually exclusive, meaning your organization can align with one or more scenarios based on your answers. If your organization shows close alignment to multiple scenarios, consider focusing on finding a more robust solution and concentrate your review on vendors that performed strongly in those scenarios or meet the critical requirements for each.

    Download the CRM Use-Case Fit Assessment Tool

    Once you’ve identified the top-level use cases a CRM must support, elicit, and prioritize granular platform requirements.

    Understanding business needs through requirements gathering is the key to defining everything about what is being purchased, yet it is an area where people often make critical mistakes.

    Info-Tech Insight

    To avoid creating makeshift solutions, an organization needs to gather requirements with the desired future state in mind.

    Risks of poorly scoped requirements

    • Fail to be comprehensive and miss certain areas of scope
    • Focus on how the solution should work instead of what it must accomplish
    • Have multiple levels of detail within the requirements, which are inconsistent and confusing
    • Drill all the way down into system-level detail
    • Add unnecessary constraints based on what is done today rather than focusing on what is needed for tomorrow
    • Omit constraints or preferences that buyers think are “obvious”

    Best practices

    • Get a clear understanding of what the system needs to do and what it is expected to produce
    • Test against the principle of MECE – requirements should be “mutually exclusive and collectively exhaustive”
    • Explicitly state the obvious and assume nothing
    • Investigate what is sold on the market and how it is sold. Use language that is consistent with that of the market and focus on key differentiators – not table stakes
    • Contain the appropriate level of detail – the level should be suitable for procurement and sufficient for differentiating vendors

    Prioritize requirements to assist with vendor selection: focus on priority requirements linked to differentiated capabilities

    Prioritization is the process of ranking each requirement based on its importance to project success. Hold a meeting for the domain SMEs, implementation SMEs, project managers, and project sponsors to prioritize the requirements list. At the conclusion of the meeting, each requirement should be assigned a priority level. The implementation SMEs will use these priority levels to ensure efforts are targeted toward the proper requirements and to plan features available on each release. Use the MoSCoW Model of Prioritization to effectively order requirements.


    Pyramid of the MoSCoW Model.
    The MoSCoW model was introduced by Dai Clegg of Oracle UK in 1994.

    The MoSCoW Model of Prioritization

    Requirements must be implemented for the solution to be considered successful.

    Requirements that are high priority should be included in the solution if possible.

    Requirements are desirable but not necessary and could be included if resources are available.

    Requirements won’t be in the next release, but will be considered for the future releases.

    Base your prioritization on the right set of criteria

    Effective Prioritization Criteria

    Criteria

    Description

    Regulatory & Legal Compliance These requirements will be considered mandatory.
    Policy Compliance Unless an internal policy can be altered or an exception can be made, these requirements will be considered mandatory.
    Business Value Significance Give a higher priority to high-value requirements.
    Business Risk Any requirement with the potential to jeopardize the entire project should be given a high priority and implemented early.
    Likelihood of Success Especially in “proof of concept” projects, it is recommended that requirements have good odds.
    Implementation Complexity Give a higher priority to low implementation difficulty requirements.
    Alignment With Strategy Give a higher priority to requirements that enable the corporate strategy.
    Urgency Prioritize requirements based on time sensitivity.
    Dependencies A requirement on its own may be low priority, but if it supports a high-priority requirement, then its priority must match it.

    2.6 Identify requirements to support your use cases

    1-2 hours

    Input: List of goals and challenges

    Output: Use cases to be used for determining requirements

    Materials: Whiteboard/flip charts, Vendor Evaluation Workbook

    Participants: CIO, Application managers, CMO/SVP sales, Marketing, sales, or service SMEs

    1. Work with the team to identify which features will be most important to support your use cases. Keep in mind there will be some features that will require more effort to implement fully. Add that into your project plan.
    2. Use the features lists on the following slides as a guide to get started on requirements.
    3. Prioritize your requirements list into mandatory features and nice-to-have features (or use the MoSCoW model from the previous slides). This will help you to eliminate vendors who don’t meet bare minimums and to score remaining vendors.
    4. Use this same list to guide your vendor demos.

    Our Improve Requirements Gathering blueprint provides a deep dive into the process of eliciting, analyzing, and validating requirements if you need to go deeper into effective techniques.

    CRM features

    Table stakes vs. differentiating

    What is a table stakes/standard feature?

    • Certain features are standard for all CRM tools, but that doesn’t mean they are all equal.
    • The existence of features doesn’t guarantee their quality or functionality to the standards you need. Never assume that “Yes” in a features list means you don’t need to ask for a demo.
    • If Table Stakes are all you need from your CRM solution, the only true differentiator for the organization is price. Otherwise, dig deeper to find the best price to value for your needs.

    What is a differentiating/additional feature?

    • Differentiating features take two forms:
      • Some CRM platforms offer differentiating features that are vertical specific.
      • Other CRM platforms offer differentiating features that are considered cutting edge. These cutting-edge features may become table stakes over time.

    Table stakes features for CRM

    Account Management Flexible account database that stores customer information, account history, and billing information. Additional functionality includes: contact deduplication, advanced field management, document linking, and embedded maps.
    Interaction Logging and Order History Ability to view all interactions that have occurred between sales teams and the customer, including purchase order history.
    Basic Pipeline Management View of all opportunities organized by their current stage in the sales process.
    Basic Case Management The ability to create and manage cases (for customer service or order fulfilment) and associate them with designated accounts or contacts.
    Basic Campaign Management Basic multi-channel campaign management (i.e. ability to execute outbound email campaigns). Budget tracking and campaign dashboards.
    Reports and Analytics In-depth reports on CRM data with dashboards and analytics for a variety of audiences.
    Mobile Support Mobile access across multiple devices (tablets, smartphones and/or wearables) with access to CRM data and dashboards.

    Additional features for CRM

    Customer Information Management Customizable records with detailed demographic information and the ability to created nested accounts (accounts with associated sub-accounts or contact records).
    Advanced Case Management Ability to track detailed interactions with members or constituents through a case view.
    Employee Collaboration Capabilities for employee-to-employee collaboration, team selling, and activity streams.
    Customer Collaboration Capabilities for outbound customer collaboration (i.e. the ability to create customer portals).
    Lead Generation Capabilities for generating qualified leads from multiple channels.
    Lead Nurturing/Lead Scoring The ability to evaluate lead warmth using multiple customer-defined criteria.
    Pipeline and Deal Management Managing deals through cases, providing quotes, and tracking client deliverables.

    Additional features for CRM (Continued)

    Marketing Campaign Management Managing outbound marketing campaigns via multiple channels (email, phone, social, mobile).
    Customer Intelligence Tools for in-depth customer insight generation and segmentation, predictive analytics, and contextual analytics.
    Multi-Channel Support Capabilities for supporting customer interactions across multiple channels (email, phone, social, mobile, IoT, etc.).
    Customer Service Workflow Management Capabilities for customer service resolution, including ticketing and service management.
    Knowledge Management Tools for capturing and sharing CRM-related knowledge, especially for customer service.
    Customer Journey Mapping Visual workflow builder with automated trigger points and business rules engine.
    Document Management The ability to curate assets and attachments and add them to account or contact records.
    Configure, Price, Quote The ability to create sales quotes/proposals from predefined price lists and rules.

    2.7 Put it all together – port your requirements into a robust RFP template that you can take to market!

    1-2 hours
    1. Once you’ve captured and prioritized your requirements – and received sign-off on them from key stakeholders – it’s time to bake them into a procurement vehicle of your choice.
    2. For complex enterprise systems like a CRM platform, Info-Tech recommends that this should take the form of a structured RFP document.
    3. Use our CRM RFP Template and associated CRM RFP Scoring Tool to jump-start the process.
    4. The next step will be conducting a market scan to identify contenders, and issuing the RFP to a shortlist of viable vendors for further evaluation.

    Need additional guidance on running an effective RFP process? Our Drive Successful Sourcing Outcomes with a Robust RFP Process has everything you need to ace the creation, administration and assessment of RFPs!

    Samples of the CRM Request for Proposal Template and CRM Suite Evaluation and RFP Scoring Tool.

    Download the CRM Request for Proposal Template

    Download the CRM Suite Evaluation and RFP Scoring Tool

    Identify whether vertical-specific CRM platforms are a best fit

    In mature vendor landscapes (like CRM) vendors begin to differentiate themselves by offering vertical-specific platforms, modules, or feature sets. These feature sets accelerate the implantation, decrease the platform’s learning curve, and drive user adoption. The three use cases below cover the most common industry-specific offerings:

    Public Sector

    • Constituent management and communication.
    • Constituent portal deployment for self-service.
    • Segment constituents based on geography, needs and preferences.

    Education

    • Top-level view into the student journey from prospect to enrolment.
    • Track student interactions with services across the institution.
    • Unify communications across different departments.

    Financial Services

    • Determine customer proclivity for new services.
    • Develop self-service banking portals.
    • Track longitudinal customer relationships from first account to retirement management.
    Info-Tech Insight

    Vertical-specific solutions require less legwork to do upfront but could cost you more in the long run. Interoperability and vendor viability must be carefully examined. Smaller players targeting niche industries often have limited integration ecosystems and less funding to keep pace with feature innovation.

    Rein-in ballooning scope for CRM selection projects

    Stretching the CRM beyond its core capabilities is a short-term solution to a long-term problem. Educate stakeholders about the limits of CRM technology.

    Common pitfalls for CRM selection

    • Tangential capabilities may require separate solutions. It is common for stakeholders to list features such as “content management” as part of the new CRM platform. While content management goes hand in hand with the CRM’s ability to manage customer interactions, document management is best handled by a standalone platform.

    Keeping stakeholders engaged and in line

    • Ballooning scope leads to stakeholder dissatisfaction. Appeasing stakeholders by over-customizing the platform will lead to integration and headaches down the road.
    • Make sure stakeholders feel heard. Do not turn down ideas in the midst of an elicitation session. Once the requirements-gathering sessions are completed, the project team has the opportunity to mark requirements as “out of scope” and communicate the reasoning behind the decision.
    • Educate stakeholders on the core functionality of CRM. Many stakeholders do not know the best-fit use cases for CRM platforms. Help end users understand what CRM is good at and where additional technologies will be needed.
    Stock image of a man leaping with a balloon.

    CRM Buyer’s Guide

    Phase 3

    Discover the CRM Market Space & Prepare for Implementation

    Phase 1

    1.1 Define CRM platforms

    1.2 Classify table stakes & differentiating capabilities

    1.3 Explore CRM trends

    Phase 2

    2.1 Build the business case

    2.2 Streamline requirements elicitation for CRM

    2.3 Construct the RFP

    Phase 3

    3.1 Discover key players in the CRM landscape

    3.2 Engage the shortlist & select finalist

    3.3 Prepare for implementation

    This phase will walk you through the following activities:

    • Dive into the key players of the CRM vendor landscape.
    • Understand best practices for building a vendor shortlist.
    • Understand key implementation considerations for CRM.

    This phase involves the following participants:

    • CIO
    • Applications manager
    • Project manager
    • Sales executive
    • Marketing executive
    • Customer service executive

    Consolidating the Vendor Shortlist Up-Front Reduces Downstream Effort

    Put the “short” back in shortlist!

    • Radically reduce effort by narrowing the field of potential vendors earlier in the selection process. Too many organizations don’t funnel their vendor shortlist until nearing the end of the selection process. The result is wasted time and effort evaluating options that are patently not a good fit.
    • Leverage external data (such as SoftwareReviews) and expert opinion to consolidate your shortlist into a smaller number of viable vendors before the investigative interview stage and eliminate time spent evaluating dozens of RFP responses.
    • Having fewer RFP responses to evaluate means you will have more time to do greater due diligence.
    Stock image of river rapids.

    Review your use cases to start your shortlist

    Your Info-Tech analysts can help you narrow down the list of vendors that will meet your requirements.

    Next steps will include:
    1. Reviewing your requirements
    2. Checking out SoftwareReviews
    3. Shortlisting your vendors
    4. Conducting demos and detailed proposal reviews
    5. Selecting and contracting with a finalist!
    Image of a person presenting a dashboard of the steps on the left.

    Get to know the key players in the CRM landscape

    The proceeding slides provide a top-level overview of the popular players you will encounter in the CRM shortlisting process.

    Logos of the key players in the CRM landscape (Salesforce, Microsoft, Oracle, HubSpot, etc).

    Evaluate software category leaders through vendor rankings and awards

    SoftwareReviews

    Sample of SoftwareReviews' Data Quadrant Report. Title page of SoftwareReviews' Data Quadrant Report. The Data Quadrant is a thorough evaluation and ranking of all software in an individual category to compare platforms across multiple dimensions.

    Vendors are ranked by their Composite Score, based on individual feature evaluations, user satisfaction rankings, vendor capability comparisons, and likeliness to recommend the platform.

    Sample of SoftwareReviews' Emotional Footprint. Title page of SoftwareReviews' Emotional Footprint. The Emotional Footprint is a powerful indicator of overall user sentiment toward the relationship with the vendor, capturing data across five dimensions.

    Vendors are ranked by their Customer Experience (CX) Score, which combines the overall Emotional Footprint rating with a measure of the value delivered by the solution.

    Speak with category experts to dive deeper into the vendor landscape

    SoftwareReviews

    Icon of a person.


    Fact-based reviews of business software from IT professionals.

    Icon of a magnifying glass over a chart.


    Top-tier data quality backed by a rigorous quality assurance process.

    CLICK HERE to ACCESS

    Comprehensive software reviews to make better IT decisions

    We collect and analyze the most detailed reviews on enterprise software from real users to give you an unprecedented view into the product and vendor before you buy.

    Icon of a tablet.


    Product and category reports with state-of-the-art data visualization.

    Icon of a phone.


    User-experience insight that reveals the intangibles of working with a vendor.

    SoftwareReviews is powered by Info-Tech

    Technology coverage is a priority for Info-Tech, and SoftwareReviews provides the most comprehensive unbiased data on today’s technology. Combined with the insights of our expert analysts, our members receive unparalleled support in their buying journey.

    Logo for Salesforce.
    Est. 1999 | CA, USA | NYSE: CRM

    bio

    Link for their Twitter account. Link for their LinkedIn profile. Link for their website.
    Sales Cloud Enterprise allows you to be more efficient, more productive, more everything than ever before as it allows you to close more deals, accelerate productivity, get more leads, and make more insightful decisions.

    SoftwareReviews’ Enterprise CRM Rankings

    Strengths:
    • Breadth of features
    • Quality of features
    • Sales management functionality
    Areas to Improve:
    • Cost of service
    • Ease of implementation
    • Telephony and contact center management
    Logo gif for SoftwareReviews.
    8.0
    COMPOSITE SCORE
    8.3
    CX SCORE
    +77
    EMOTIONAL FOOTPRINT
    83%
    LIKELINESS TO RECOMMEND
    DOWNLOAD REPORT 600
    REVIEWS
    Vendor scores are driven by real-world practitioner reviews via SoftwareReviews. Composite, CX, EF and NPS scores pulled from live data as of June 2022. Rankings and ”strengths” and ”areas to improve” pulled from January 2022 Category Report.
    Sample of a Salesforce screen. Vendor Pulse rating. How often do we hear about Salesforce from our members for CRM? 'Very Frequently'.
    History of Salesforce in a vertical timeline.
    *Pricing correct as of August 2021. Listed in USD and absent discounts.
    See pricing on vendor’s website for latest information.
    Logo for Salesforce.

    “Salesforce is the pre-eminent vendor in the CRM marketplace and is a force to be reckoned with in terms of the breadth and depth of its capabilities. The company was an early disruptor in the category, placing a strong emphasis from the get-go on a SaaS delivery model and strong end-user experience. This allowed them to rapidly gain market share at the expense of more complacent enterprise application vendors. A series of savvy acquisitions over the years has allowed Salesforce to augment their core Sales and Service Clouds with a wide variety of other solutions, from e-commerce to marketing automation to CPQ. Salesforce is a great fit for any organization looking to partner with a market leader with excellent functional breadth, strong interoperability, and a compelling technology and partner ecosystem. All of this comes at a price, however – Salesforce prices at a premium, and our members routinely opine that Salesforce’s commercial teams are overly aggressive – sometimes pushing solutions without a clear link to underpinning business requirements.”

    Ben Dickie
    Research Practice Lead, Info-Tech Research Group

    Sales Cloud Essentials Sales Cloud Professional Sales Cloud Enterprise Sales Cloud Ultimate
    • Starts at $25*
    • Per user/mo
    • Small businesses after basic functionality
    • Starts at $75*
    • Per user/mo
    • Mid-market target
    • Starts at $150*
    • Per user/mo
    • Enterprise target
    • Starts at $300*
    • Per user/mo
    • Strong upmarket feature additions
    Logo for Microsoft.


    Est. 1975 | WA, USA | NYSE: MSFT

    bio

    Link for their Twitter account.Link for their LinkedIn profile.Link for their website.
    Dynamics 365 Sales is an adaptive selling solution that helps your sales team navigate the realities of modern selling. At the center of the solution is an adaptive, intelligent system – prebuilt and ready to go – that actively monitors myriad signals and distills them into actionable insights.

    SoftwareReviews’ Enterprise CRM Rankings

    Strengths:

    • Business value created
    • Analytics and reporting
    • Lead management

    Areas to Improve:

    • Quote, contract, and proposals
    • Vendor support
    Logo gif for SoftwareReviews.
    8.1
    COMPOSITE SCORE
    8.3
    CX SCORE
    +84
    EMOTIONAL FOOTPRINT
    82%
    LIKELINESS TO RECOMMEND
    DOWNLOAD REPORT 198
    REVIEWS
    Vendor scores are driven by real-world practitioner reviews via SoftwareReviews. Composite, CX, EF and NPS scores pulled from live data as of June 2022. Rankings and ”strengths” and ”areas to improve” pulled from January 2022 Category Report.
    Sample of a Microsoft screen.Vendor Pulse rating. How often do we hear about Microsoft Dynamics from our Members? 'Very Frequently'.

    History of Microsoft in a vertical timeline.

    *Pricing correct as of June 2022. Listed in USD and absent discounts.
    See pricing on vendor’s website for latest information.
    Logo for Microsoft.
    “”

    “Microsoft Dynamics 365 is a strong and compelling player in the CRM arena. While Microsoft is no stranger to the CRM space, their offerings here have seen steady and marked improvement over the last five years. Good functional breadth paired with a modern user interface and best-in-class Microsoft stack compatibility ensures that we consistently see them on our members’ shortlists, particularly when our members are looking to roll out CRM capabilities alongside other components of the Dynamics ecosystem (such as Finance, Operations, and HR). Today, Microsoft segments the offering into discrete modules for sales, service, marketing, commerce, and CDP. While Microsoft Dynamics 365 is a strong option, it’s occasionally mired by concerns that the pace of innovation and investment lags Salesforce (its nearest competitor). Additionally, the marketing module of the product is softer than some of its competitors, and Microsoft themselves points organizations with complex marketing requirements to a strategic partnership that they have with Adobe.”

    Ben Dickie
    Research Practice Lead, Info-Tech Research Group

    D365 Sales Professional D365 Sales Enterprise D365 Sales Premium
    • Starts at $65*
    • Per user/mo
    • Midmarket focus
    • Starts at $95*
    • Per user/mo
    • Enterprise focus
    • Starts at $135*
    • Per user/mo
    • Enterprise focus with customer intelligence
    Logo for Oracle.


    Est. 1977 | CA, USA | NYSE: ORCL

    bio

    Link for their Twitter account.Link for their LinkedIn profile.Link for their website.
    Oracle Engagement Cloud (CX Sales) provides a set of capabilities to help sales leaders transition smoothly from sales planning and execution through customer onboarding, account management, and support services.

    SoftwareReviews’ Enterprise CRM Rankings

    Strengths:

    • Quality of features
    • Activity and workflow management
    • Analytics and reporting

    Areas to Improve:

    • Marketing management
    • Product strategy & rate of improvement
    Logo gif for SoftwareReviews.
    7.8
    COMPOSITE SCORE
    7.9
    CX SCORE
    +77
    EMOTIONAL FOOTPRINT
    78%
    LIKELINESS TO RECOMMEND
    DOWNLOAD REPORT 140
    REVIEWS
    Vendor scores are driven by real-world practitioner reviews via SoftwareReviews. Composite, CX, EF and NPS scores pulled from live data as of June 2022. Rankings and ”strengths” and ”areas to improve” pulled from January 2022 Category Report.
    Sample of an Oracle screen.Vendor Pulse rating. How often do we hear about Oracle from our members for CRM? 'Frequently'.

    History of Oracle in a vertical timeline.

    Logo for Oracle.

    “Oracle is long-term juggernaut of the enterprise applications space. Their CRM portfolio is diverse – rather than a single stack, there are multiple Oracle solutions (many made by acquisition) that support CRM capabilities – everything from Siebel to JD Edwards to NetSuite to Oracle CX applications. The latter constitute Oracle’s most modern stab at CRM and are where the bulk of feature innovation and product development is occurring within their portfolio. While historically seen as lagging behind other competitors like Salesforce and Microsoft, Oracle has made excellent strides in improving their user experience (via their Redwoods design paradigm) and building new functional capabilities within their CRM products. Indeed, SoftwareReviews shows Oracle performing well in our most recent peer-driven reports. Nonetheless, we most commonly see Oracle as a pricier ecosystem play that’s often subordinate to a heavy Oracle footprint for ERP. Many of our members also express displeasure with Oracle as a vendor and highlight their heavy-handed “threat of audit” approach. ”

    Ben Dickie
    Research Practice Lead, Info-Tech Research Group

    Oracle CX Sales - Pricing Opaque:

    “Request a Demo”

    Logo for SAP.


    Est. 1972 | Germany | NYSE: SAP

    bio

    Link for their Twitter account.Link for their LinkedIn profile.Link for their website.
    SAP is the third-largest independent software manufacturer in the world, with a presence in over 120 countries. Having been in the industry for over 40 years, SAP is perhaps best known for its ERP application, SAP ERP.

    SoftwareReviews’ Enterprise CRM Rankings

    Strengths:

    • Ease of data integration

    Areas to Improve:

    • Lead management
    • Marketing management
    • Collaboration
    • Usability & intuitiveness
    • Analytics & reporting
    Logo gif for SoftwareReviews.
    7.4
    COMPOSITE SCORE
    7.8
    CX SCORE
    +74
    EMOTIONAL FOOTPRINT
    75%
    LIKELINESS TO RECOMMEND
    DOWNLOAD REPORT 108
    REVIEWS
    Vendor scores are driven by real-world practitioner reviews via SoftwareReviews. Composite, CX, EF and NPS scores pulled from live data as of June 2022. Rankings and ”strengths” and ”areas to improve” pulled from January 2022 Category Report.
    Sample of a SAP screen.Vendor Pulse rating. How often do we hear about SAP from our members for CRM? 'Occasionally'.

    History of SAP in a vertical timeline.

    *Pricing correct as of August 2021. Listed in USD and absent discounts.
    See pricing on vendor’s website for latest information.
    Logo for SAP.

    “SAP is another mainstay of the enterprise applications market. While they have a sound breadth of capabilities in the CRM and customer experience space, SAP consistently underperforms in many of our relevant peer-driven SoftwareReviews reports for CRM and adjacent areas. CRM seems decidedly a secondary focus for SAP, behind their more compelling play in the enterprise resource planning (ERP) space. Indeed, most instances where we see SAP in our clients’ shortlists, it’s as an ecosystem play within a broader SAP strategy. If you’re blue on the ERP side, looking to SAP’s capabilities on the CRM front makes logical sense and can help contain costs. If you’re approaching a CRM selection from a greenfield lens and with no legacy vendor baggage for SAP elsewhere, experience suggests you’ll be better served by a vendor that places a higher degree of primacy on the CRM aspect of their portfolio.”

    Ben Dickie
    Research Practice Lead, Info-Tech Research Group

    SAP CRM - Pricing Opaque:

    “Request a Demo”

    Logo for pipedrive.


    Est. 2010 | NY, USA | Private

    bio

    Link for their Twitter account.Link for their LinkedIn profile.Link for their website.
    Pipedrive brings together the tools and data, the platform focuses sales professionals on fundamentals to advance deals through their pipelines. Pipedrive's goal is to make sales success inevitable - for salespeople and teams.

    SoftwareReviews’ Enterprise CRM Rankings

    Strengths:

    • Sales Management
    • Account & Contact Management
    • Lead Management
    • Usability & Intuitiveness
    • Ease of Implementation

    Areas to Improve:

    • Customer Service Management
    • Marketing Management
    • Product Strategy & Rate of Improvement
    Logo gif for SoftwareReviews.
    8.3
    COMPOSITE SCORE
    8.4
    CX SCORE
    +85
    EMOTIONAL FOOTPRINT
    85%
    LIKELINESS TO RECOMMEND
    DOWNLOAD REPORT 262
    REVIEWS
    Vendor scores are driven by real-world practitioner reviews via SoftwareReviews. Composite, CX, EF and NPS scores pulled from live data as of June 2022. Rankings and ”strengths” and ”areas to improve” pulled from January 2022 Category Report.
    Sample of a Pipedrive screen.Vendor Pulse rating. How often do we hear about Pipedrive from our members for CRM? 'Occasionally'.

    History of Pipedrive in a vertical timeline.

    *Pricing correct as of June 2022. Listed in USD and absent discounts.
    See pricing on vendor’s website for latest information.
    Logo for Pipedrive.

    “A relatively new offering, Pipedrive has seen explosive growth over the last five years. They’re a vendor that has gone from near-obscurity to popping up frequently on our members’ shortlists. Pipedrive’s secret sauce has been a relentless focus on high-velocity sales enablement. Their focus on pipeline management, lead assessment and routing, and a good single pane of glass for sales reps has driven significant traction for the vendor when sales enablement is the driving rationale behind rolling out a new CRM platform. Bang for your buck is also strong with Pipedrive, with the vendor having a value-driven licensing and implementation model.

    Pipedrive is not without some shortcomings. It’s laser-focus on sales enablement is at the expense of deep capabilities for marketing and service management, and its profile lends itself better to SMBs and lower midmarket than it does large organizations looking for enterprise-grade CRM.”

    Ben Dickie
    Research Practice Lead, Info-Tech Research Group

    Essential Advanced Professional Enterprise
    • Starts at $12.50*
    • Per user/mo
    • Small businesses after basic functionality
    • Starts at $24.90*
    • Per user/mo
    • Small/mid-sized businesses
    • Starts at $49.90*
    • Per user/mo
    • Lower mid-market focus
    • Starts at $99*
    • Per user/mo
    • Enterprise focus
    Logo for SugarCRM.


    Est. 2004 | CA, USA | Private

    bio

    Link for their Twitter account.Link for their LinkedIn profile.Link for their website.
    Produces Sugar, a SaaS-based customer relationship management application. SugarCRM is backed by Accel-KKR.

    SoftwareReviews’ Enterprise CRM Rankings

    Strengths:

    • Ease of customization
    • Product strategy and rate of improvement
    • Ease of IT administration

    Areas to Improve:

    • Marketing management
    • Analytics and reporting
    Logo gif for SoftwareReviews.
    8.4
    COMPOSITE SCORE
    8.8
    CX SCORE
    +92
    EMOTIONAL FOOTPRINT
    84%
    LIKELINESS TO RECOMMEND
    DOWNLOAD REPORT 97
    REVIEWS
    Vendor scores are driven by real-world practitioner reviews via SoftwareReviews. Composite, CX, EF and NPS scores pulled from live data as of June 2022. Rankings and ”strengths” and ”areas to improve” pulled from January 2022 Category Report.
    Sample of a SugarCRM screen.Vendor Pulse rating. How often do we hear about SugarCRM from our members for CRM? 'Frequently'.
    History of SugarCRM in a vertical timeline.
    *Pricing correct as of August 2021. Listed in USD and absent discounts.
    See pricing on vendor’s website for latest information.
    Logo for SugarCRM.

    “SugarCRM offers reliable baseline capabilities at a lower price point than other large CRM vendors. While SugarCRM does not offer all the bells and whistles that an Enterprise Salesforce plan might, SugarCRM is known for providing excellent vendor support. If your organization is only after standard features, SugarCRM will be a good vendor to shortlist.

    However, ensure you have the time and labor power to effectively implement and train on SugarCRM’s solutions. SugarCRM does not score highly for user-friendly experiences, with complaints centering on outdated and unintuitive interfaces. Setting up customized modules takes time to navigate, and SugarCRM does not provide a wide range of native integrations with other applications. To effectively determine whether SugarCRM does offer a feasible solution, it is recommended that organizations know exactly what kinds of integrations and modules they need.”

    Thomas Randall
    Research Director, Info-Tech Research Group

    Sugar Professional Sugar Serve Sugar Sell Sugar Enterprise Sugar Market
    • Starts at $52*
    • Per user/mo
    • Min. 3 users
    • Small businesses
    • Starts at $80*
    • Per user/mo
    • Min. 3 users
    • Focused on customer service
    • Starts at $80*
    • Per user/mo
    • Min. 3 users
    • Focused on sales automation
    • Starts at $80*
    • Per user/mo
    • Min. 3 users
    • On-premises, mid-sized businesses
    • Starts at $1000*
    • Priced per month
    • Min. 10k contacts
    • Large enterprise
    Logo for .


    Est. 2006 | MA, USA | HUBS (NYSE)

    bio

    Link for their Twitter account.Link for their LinkedIn profile.Link for their website.
    Develops software for inbound customer service, marketing, and sales. Software includes CRM, SMM, lead gen, SEO, and web analytics.

    SoftwareReviews’ Enterprise CRM Rankings

    Strengths:

    • Breadth of features
    • Product strategy and rate of improvement
    • Ease of customization

    Areas to Improve:

    • Ease of data integration
    • Customer service management
    • Telephony and call center management
    Logo gif for SoftwareReviews.
    8.3
    COMPOSITE SCORE
    8.4
    CX SCORE
    +84
    EMOTIONAL FOOTPRINT
    86%
    LIKELINESS TO RECOMMEND
    DOWNLOAD REPORT 97
    REVIEWS
    Vendor scores are driven by real-world practitioner reviews via SoftwareReviews. Composite, CX, EF and NPS scores pulled from live data as of June 2022. Rankings and ”strengths” and ”areas to improve” pulled from January 2022 Category Report.
    Sample of a HubSpot screen.Vendor Pulse rating. How often do we hear about HubSpot from our members for CRM? 'Frequently'.

    History of HubSpot in a vertical timeline.

    *Pricing correct as of August 2021. Listed in USD and absent discounts
    See pricing on vendor’s website for latest information.
    Logo for HubSpot.

    “ HubSpot is best suited for small to mid-sized organizations that need a range of CRM tools to enable growth across sales, marketing campaigns, and customer service. Indeed, HubSpot offers a content management solution that offers a central storage location for all customer and marketing data. Moreover, HubSpot offers plenty of freemium tools for users to familiarize themselves with the software before buying. However, though HubSpot is geared toward growing businesses, smaller organizations may not see high ROI until they begin to scale. The “Starter” and “Professional” plans’ pricing is often cited by small organizations as a barrier to commitment, and the freemium tools are not a sustainable solution. If organizations can take advantage of discount behaviors from HubSpot (e.g. a startup discount), HubSpot will be a viable long-term solution. ”

    Thomas Randall
    Research Director, Info-Tech Research Group

    Starter Professional Enterprise
    • Starts at $50*
    • Per month
    • Min. 2 users
    • Small businesses
    • Starts at $500*
    • Per month
    • Min. 5 users
    • Small/mid-sized businesses
    • Starts at $1200*
    • Billed yearly
    • Min. 10 users
    • Mid-sized/small enterprise
    Logo for Zoho.


    Est. 1996 | India | Private

    bio

    Link for their Twitter account.Link for their LinkedIn profile.Link for their website.
    Zoho Corporation offers a cloud software suite, providing a full operating system for CRM, alongside apps for finance, productivity, HR, legal, and more.

    SoftwareReviews’ Enterprise CRM Rankings

    Strengths:

    • Business value created
    • Breadth of features
    • Collaboration capabilities

    Areas to Improve:

    • Usability and intuitiveness
    Logo gif for SoftwareReviews.
    8.7
    COMPOSITE SCORE
    8.9
    CX SCORE
    +92
    EMOTIONAL FOOTPRINT
    85%
    LIKELINESS TO RECOMMEND
    DOWNLOAD REPORT 152
    REVIEWS
    Vendor scores are driven by real-world practitioner reviews via SoftwareReviews. Composite, CX, EF and NPS scores pulled from live data as of June 2022. Rankings and ”strengths” and ”areas to improve” pulled from January 2022 Category Report.
    Sample of a Zoho screen.Vendor Pulse rating. How often do we hear about Zoho from our members for CRM? 'Occasionally'.

    History of Zoho in a vertical timeline.

    *
    See pricing on vendor’s website for latest information.
    Logo for Zoho.

    “Zoho has a long list of software solutions for businesses to run end to end. As one of Zoho’s earliest software releases, though, ZohoCRM remains a flagship product. ZohoCRM’s pricing is incredibly competitive for mid/large enterprises, offering high business value for its robust feature sets. For those organizations that already utilize Zoho solutions (such as its productivity suite), ZohoCRM will be a natural extension.

    However, small/mid-sized businesses may wonder how much ROI they can get from ZohoCRM, when much of the functionality expected from a CRM (such as workflow automation) cannot be found until one jumps to the “Enterprise” plan. Given the “Enterprise” plan’s pricing is on par with other CRM vendors, there may not be much in a smaller organization’s eyes that truly distinguishes ZohoCRM unless they are already invested Zoho users.”

    Thomas Randall
    Research Director, Info-Tech Research Group

    Standard Professional Enterprise Ultimate
    • Starts at $20*
    • Per user/mo
    • Small businesses after basic functionality
    • Starts at $35*
    • Per user/mo
    • Small/mid-sized businesses
    • Adds inventory management
    • Starts at $50*
    • Per user/mo
    • Mid-sized/small enterprise
    • Adds Zia AI
    • Starts at $65*
    • Per user/mo
    • Enterprise
    • Bundles Zoho Analytics
    Logo for Zendesk.


    Est. 2009 | CA, USA | ZEN (NYSE)

    bio

    Link for their Twitter account.Link for their LinkedIn profile.Link for their website.
    Software developer for customer service. Founded in Copenhagen but moved to San Francisco after $6 million Series B funding from Charles River Ventures and Benchmark Capital.

    SoftwareReviews’ Enterprise CRM Rankings

    Strengths:

    • Quality of features
    • Breadth of features
    • Vendor support

    Areas to Improve:

    • Business value created
    • Ease of customization
    • Usability and intuitiveness
    Logo gif for SoftwareReviews.
    7.8
    COMPOSITE SCORE
    7.9
    CX SCORE
    +80
    EMOTIONAL FOOTPRINT
    72%
    LIKELINESS TO RECOMMEND
    DOWNLOAD REPORT 50
    REVIEWS
    Vendor scores are driven by real-world practitioner reviews via SoftwareReviews. Composite, CX, EF and NPS scores pulled from live data as of June 2022. Rankings and ”strengths” and ”areas to improve” pulled from January 2022 Category Report.
    Sample of a Zendesk screen.Vendor Pulse rating. How often do we hear about Zendesk from our members for CRM? 'Rarely'.

    History of Zendesk in a vertical timeline.

    *Pricing correct as of August 2021. Listed in USD and absent discounts
    See pricing on vendor’s website for latest information.
    Logo for Zendesk.

    “Zendesk’s initial growth was grounded in word-of-mouth advertising, owing to the popularity of its help desk solution’s design and functionality. Zendesk Sell has followed suit, receiving strong feedback for the breadth and quality of its features. Organizations that have already reaped the benefits of Zendesk’s customer service suite will find Zendesk Sell a straightforward fit for their sales teams.

    However, it is important to note that Zendesk Sell is predominantly focused on sales. Other key components of a CRM, such as marketing, are less fleshed out. Organizations should ensure they verify what requirements they have for a CRM before choosing Zendesk Sell – if sales process requirements (such as forecasting, call analytics, and so on) are but one part of what the organization needs, Zendesk Sell may not offer the highest ROI for the pricing offered.”

    Thomas Randall
    Research Director, Info-Tech Research Group

    Sell Team Sell Professional Sell Enterprise
    • Starts at $19*
    • Per user/mo
    • Max. 3 users
    • Small businesses
    • Basic functionality
    • Starts at $49*
    • Per user/mo
    • Small/mid-sized businesses
    • Advanced analytics
    • Starts at $99*
    • Per user/mo
    • Mid-sized/small enterprise
    • Task automation

    Speak with category experts to dive deeper into the vendor landscape

    Icon of a person.
    Fact-based reviews of business software from IT professionals.
    Icon of a magnifying glass over a chart.
    Top-tier data quality backed by a rigorous quality assurance process.
    CLICK HERE to ACCESS

    Comprehensive software reviews to make better IT decisions

    We collect and analyze the most detailed reviews on enterprise software from real users to give you an unprecedented view into the product and vendor before you buy.

    Icon of a tablet.
    Product and category reports with state-of-the-art data visualization.
    Icon of a phone.
    User-experience insight that reveals the intangibles of working with a vendor.

    SoftwareReviews is powered by Info-Tech

    Technology coverage is a priority for Info-Tech, and SoftwareReviews provides the most comprehensive unbiased data on today’s technology. Combined with the insights of our expert analysts, our members receive unparalleled support in their buying journey.

    Conduct a day of rapid-fire vendor demos

    Zoom in on high-value use cases and answers to targeted questions

    Make sure the solution will work for your business

    Give each vendor 90 to 120 minutes to give a rapid-fire presentation. We suggest the following structure:

    • 30 minutes: company introduction and vision
    • 60 minutes: walk-through of two or three high-value demo scenarios
    • 30 minutes: targeted Q&A from the business stakeholders and procurement team
    To ensure a consistent evaluation, vendors should be asked analogous questions, and a tabulation of answers should be conducted.
    How to challenge the vendors in the investigative interview
    • Change the visualization/presentation.
    • Change the underlying data.
    • Add additional data sets to the artifacts.
    • Collaboration capabilities.
    • Perform an investigation in terms of finding BI objects and identifying previous changes, and examine the audit trail.
    Rapid-fire vendor investigative interview

    Invite vendors to come onsite (or join you via video conference) to demonstrate the product and to answer questions. Use a highly targeted demo script to help identify how a vendor’s solution will fit your organization’s particular business capability needs.

    Graphic of an alarm clock.
    To kick-start scripting your demo scenarios, leverage our CRM Demo Script Template.

    A vendor scoring model provides a clear anchor point for your evaluation of CRM vendors based on a variety of inputs

    A vendor scoring model is a systematic method for effectively assessing competing vendors. A weighted-average scoring model is an approach that strikes a strong balance between rigor and evaluation speed.

    Info-Tech Insight

    Even the best scoring model will still involve some “art” rather than science – scoring categories such as vendor viability always entails a degree of subjective interpretation.

    How do I build a scoring model?

    • Start by shortlisting the key criteria you will use to evaluate your vendors. Functional capabilities should always be a critical category, but you’ll also want to look at criteria such as affordability, architectural fit, and vendor viability.
    • Depending on the complexity of the project, you may break down some criteria into sub-categories to assist with evaluation (for example, breaking down functional capabilities into constituent use cases so you can score each one).
    • Once you’ve developed the key criteria for your project, the next step is weighting each criterion. Your weightings should reflect the priorities for the project at hand. For example, some projects may put more emphasis on affordability, others on vendor partnership.
    • Using the information collected in the subsequent phases of this blueprint, score each criterion from 1-100, then multiply by the weighting factor. Add up the weighted scores to arrive at the aggregate evaluation score for each vendor on your shortlist.

    What are some of the best practices?

    • While the criteria for each project may vary, it’s helpful to have an inventory of repeatable criteria that can be used across application selection projects. The next slide contains an example that you can add or subtract from.
    • Don’t go overboard on the number of criteria: five to 10 weighted criteria should be the norm for most projects. The more criteria (and sub-criteria) you must score against, the longer it will take to conduct your evaluation. Always remember, link the level of rigor to the size and complexity of your project! It’s possible to create a convoluted scoring model that takes significant time to fill out but yields little additional value.
    • Creation of the scoring model should be a consensus-driven activity among IT, procurement, and the key business stakeholders – it should not be built in isolation. Everyone should agree on the fundamental criteria and weights that are employed.
    • Consider using not just the outputs of investigative interviews and RFP responses to score vendors, but also third-party review services like SoftwareReviews.

    Define how you’ll score CRM proposals and demos

    Define key CRM selection criteria for your organization – this should be informed by the following goals, use cases, and requirements covered in the blueprint.

    Criteria

    Description

    Functional CapabilitiesHow well does the vendor align with the top-priority functional requirements identified in your accelerated needs assessment? What is the vendor’s functional breadth and depth?
    AffordabilityHow affordable is this vendor? Consider a three-to-five-year total cost of ownership (TCO) that encompasses not just licensing costs, but also implementation, integration, training, and ongoing support costs.
    Architectural FitHow well does this vendor align with our direction from an enterprise architecture perspective? How interoperable is the solution with existing applications in our technology stack? Does the solution meet our deployment model preferences?
    ExtensibilityHow easy is it to augment the base solution with native or third-party add-ons as our business needs may evolve?
    ScalabilityHow easy is it to expand the solution to support increased user, data, and/or customer volumes? Are there any capacity constraints of the solution?
    Vendor ViabilityHow viable is this vendor? Are they an established player with a proven track record, or a new and untested entrant to the market? What is the financial health of the vendor? How committed are they to the particular solution category?
    Vendor VisionDoes the vendor have a cogent and realistic product roadmap? Are they making sensible investments that align with your organization’s internal direction?
    Emotional FootprintHow well does the vendor’s organizational culture and team dynamics align to yours?
    Third-Party Assessments and/or ReferencesHow well-received is the vendor by unbiased, third-party sources like SoftwareReviews? For larger projects, how well does the vendor perform in reference checks (and how closely do those references mirror your own situation)?

    Decision Point: Select the Finalist

    After reviewing all vendor responses to your RFP, conducting vendor demos, and running a pilot project (if applicable), the time has arrived to select your finalist.

    All core selection team members should hold a session to score each shortlisted vendor against the criteria enumerated on the previous slide – based on an in-depth review of proposals, the demo sessions, and any pilots or technical assessments.

    The vendor that scores the highest in aggregate is your finalist.

    Congratulations – you are now ready to proceed to final negotiation and inking a contract. This blueprint provides a detailed approach on the mechanics of a major vendor negotiation.

    Leverage Info-Tech’s research to plan and execute your CRM implementation

    Use Info-Tech Research Group’s three phase implementation process to guide your own planning.
    The three phases of software implementation: 'Assess', 'Prepare', 'Govern & Course Correct'. Sample of the 'Governance and Management of Enterprise Software Implementation' blueprint.

    Establish and execute an end-to-end, agile framework to succeed with the implementation of a major enterprise application.

    Visit this link

    Prepare for implementation: establish a clear resourcing plan

    Organizations rarely have sufficient internal staffing to resource a CRM project on their own. Consider the options for closing the gap in internal resource availability.

    The most common project resourcing structures for enterprise projects are:
    Your own staff +
    1. Management consultant
    2. Vendor consultant
    3. System integrator
    Info-Tech Insight

    When contemplating a resourcing structure, consider:

    • Availability of in-house implementation competencies and resources.
    • Timeline and constraints.
    • Integration environment complexity.

    Consider the following:

    Internal vs. External Roles and Responsibilities

    Clearly delineate between internal and external team responsibilities and accountabilities, and communicate this to your technology partner up front.

    Internal vs. External Accountabilities

    Accountability is different than responsibility. Your vendor or SI partner may be responsible for completing certain tasks, but be careful not to outsource accountability for the implementation – ultimately, the internal team will be accountable.

    Partner Implementation Methodologies

    Often vendors and/or SIs will have their own preferred implementation methodology. Consider the use of your partner's implementation methodology; however, you know what will work for your organization.

    Establish team composition

    1 – 2 hours

    Input: Skills assessment, Stakeholder analysis, Vendor partner selection

    Output: Team composition

    Materials: Sticky notes, Whiteboard, Markers

    Participants: Project team

    Use Info-Tech’s Governance and Management of Enterprise Software Implementation to establish your team composition. Within that blueprint:

    1. Assess the skills necessary for an implementation. Inventory the competencies required for the implementation project team. Map your internal resources to each competency as applicable.
    2. Select your internal implementation team. Determine who needs to be involved closely with the implementation. Key stakeholders should also be considered as members of your implementation team.
    3. Identify the number of external consultants/support required for implementation. Consider your in-house skills, timeline considerations, integration environment complexity, and cost constraints as you make your team composition plan. Be sure to dedicate an internal resource to managing the vendor and partner relationships.
    4. Document the roles and responsibilities, accountabilities, and other expectations of your team as they relate to each step of the implementation.

    Governance and Management of Enterprise Software Implementation

    Sample of the 'Governance and Management of Enterprise Software Implementation' blueprint.Follow our iterative methodology with a task list focused on the business must-have functionality to achieve rapid execution and to allow staff to return to their daily work sooner.

    Visit this link

    Ensure your implementation team has a high degree of trust and communication

    If external partners are needed, dedicate an internal resource to managing the vendor and partner relationships.

    Communication

    Teams must have some type of communication strategy. This can be broken into:
    • Regularity: Having a set time each day to communicate progress and a set day to conduct retrospectives.
    • Ceremonies: Injecting awards and continually emphasizing delivery of value can encourage relationship-building and constructive motivation.
    • Escalation: Voicing any concerns and having someone responsible for addressing those concerns.

    Proximity

    Distributed teams create complexity as communication can break down. This can be mitigated by:
    • Location: Placing teams in proximity can close the barrier of geographical distance and time zone differences.
    • Inclusion: Making a deliberate attempt to pull remote team members into discussions and ceremonies.
    • Communication tools: Having the right technology (e.g. video conference) can help bring teams closer together virtually.

    Trust

    Members should trust other members are contributing to the project and completing their required tasks on time. Trust can be developed and maintained by:
    • Accountability: Having frequent quality reviews and feedback sessions. As work becomes more transparent, people become more accountable.
    • Role clarity: Having a clear definition of what everyone’s role is.

    Plan for your implementation of CRM based on deployment model

    Place your CRM application into your IT landscape by configuring and adjusting the tool based on your specific deployment method.

    Icon of a housing development.
    On-Premises

    1. Identify custom features and configuration items
    2. Train developers and IT staff on new software investment
    3. Install software
    4. Configure software
    5. Test installation and configuration
    6. Test functionality

    Icon of a cloud upload.
    SaaS-based

    1. Train developers and IT staff on new software investment
    2. Set up connectivity
    3. Identify VPN or internal solution
    4. Check firewalls
    5. Validate bandwidth regulations

    Integration is a top IT challenge and critical to the success of the CRM suite

    CRM suites are most effective when they are integrated with ERP and MarTech solutions.

    Data interchange between the CRM solution and other data sources is necessary

    Formulate a comprehensive map of the systems, hardware, and software with which the CRM solution must be able to integrate. Customer data needs to constantly be synchronized: without this, you lose out on one of the primary benefits of CRM. These connections must be bidirectional for maximum value (i.e. marketing data to the CRM, customer data to MMS).
    Specialized projects that include an intricate prospect or customer list and complex rules may need to be built by IT The more custom fields you have in your CRM suite and point solutions, the more schema mapping you will have to do. Include this information in the RFP to receive guidance from vendors on the ease with which integration can be achieved.

    Pay attention to legacy apps and databases

    If you have legacy CRM, POS, or customer contact software, more custom code will be required. Many vendors claim that custom integration can be performed for most systems, but custom comes at a cost. Don’t just ask if they can integrate; ask how long it will take and for references from organizations which have been successful in this.
    When assessing the current application portfolio that supports CRM, the tendency will be to focus on the applications under the CRM umbrella, relating mostly to marketing, sales, and customer service. Be sure to include systems that act as inputs to, or benefit due to outputs from, the CRM or similar applications.

    CRM data flow

    Example of a CRM data flow.

    Be sure to include enterprise applications that are not included in the CRM application portfolio. Popular systems to consider for POIs include billing, directory services, content management, and collaboration tools.

    Sample CRM integration map

    Sample of a CRM integration map.

    Scenario: Failure to address CRM data integration will cost you in the long run

    A company spent $15 million implementing a new CRM system in the cloud and decided NOT to spend an additional $1.5 million to do a proper cloud DI tool procurement. The mounting costs followed.

    Cost Element – Custom Data Integration

    $

    2 FTEs for double entry of sales order data $ 100,000/year
    One-time migration of product data to CRM $ 240,000 otc
    Product data maintenance $ 60,000/year
    Customer data synchronization interface build $ 60,000 otc
    Customer data interface maintenance $ 10,000/year
    Data quality issues $ 100,000/year
    New SaaS integration built in year 3 $ 300,000 otc
    New SaaS integration maintenance $ 150,000/year

    Cost Element – Data Integration Tool

    $

    DI strategy and platform implementation $1,500,000 otc
    DI tool maintenance $ 15,000/year
    New SaaS integration point in year 3 $ 300,000 otc
    Thumbs down color coded red to the adjacent chart. Custom integration is costing this organization $300,000/year for one SaaS solution.
    Thumbs up color coded blue to the adjacent chart.

    The proposed integration solution would have paid for itself in 3-4 years and saved exponential costs in the long run.

    Proactively address data quality in the CRM during implementation

    Data quality is a make-or-break issue in a CRM platform; garbage in is garbage out.
    • CRM suites are one of the leading offenders for generating poor-quality data. As such, it’s important to have a plan in place for structuring your data architecture in such a way the poor data quality is minimized from the get-go.
    • Having a plan for data quality should precede data migration efforts; some types of poor data quality can be mitigated prior to migration.
    • There are five main types of poor-quality data found in CRM platforms.
      • Duplicate data: Duplicate records can be a major issue. Leverage dedicated deduplication tools to eliminate them.
      • Stale data: Out-of-date customer information can reduce the usefulness of the platform. Use automated social listening tools to help keep data fresh.
      • Incomplete data: Records with missing info limit platform value. Specify data validation parameters to mandate that all fields are filled in.
      • Invalid and conflicting data: These can create cascading errors. Establishing conflict resolution rules in ETL tools for data integration can lessen issues.
    Info-Tech Insight

    If you have a complex POI environment, appoint data stewards for each major domain and procure a deduplication tool. As the complexity of CRM system-to-system integrations increases, so will the chance that data quality errors will crop up – for example, bidirectional POI with other sources of customer information dramatically increase the chances of conflicting/duplicate data.

    Profile data, eliminate dead weight, and enforce standards to protect data

    Identify and eliminate dead weight

    Poor data can originate in the firm’s CRM system. Custom queries, stored procedures, or profiling tools can be used to assess the key problem areas.

    Loose rules in the CRM system may lead to records of no significant value in the database. Those rules need to be fixed, but if changes are made before the data is fixed, users could encounter database or application errors, which will reduce user confidence in the system.

    • Conduct a data flow analysis: map the path that data takes through the organization.
    • Use a mass cleanup to identify and destroy dead weight data. Merge duplicates either manually or with the aid of software tools. Delete incomplete data, taking care to reassign related data.
    • COTS packages typically allow power users to merge records without creating orphaned records in related tables, but custom-built applications typically require IT expertise.

    Create and enforce standards and policies

    Now that the data has been cleaned, it’s important to protect the system from relapsing.

    Work with business users to find out what types of data require validation and which fields should have changes audited. Whenever possible, implement drop-down lists to standardize values and make programming changes to ensure that truncation ceases.

    • Truncated data is usually caused by mismatches in data structures during either one-time data loads or ongoing data integrations.
    • Don’t go overboard on assigning required fields; users will just put key data in note fields.
    • Discourage the use of unstructured note fields: the data is effectively lost except if it gets subpoenaed.
    Info-Tech Insight

    Data quality concerns proliferate with the customization level of your platform. The more extensive the custom integration points and module/database extensions that you have made, the more you will need to have a plan in place for managing data quality from a reactive and proactive standpoint.

    Create a formal communication process throughout the CRM implementation

    Establish a comprehensive communication process around the CRM enterprise roll-out to ensure that end users stay informed.

    The CRM kick-off meeting(s) should encompass: 'The high-level application overview', 'Target business-user requirements', 'Target quality of service (QoS) metrics', 'Other IT department needs', 'Tangible business benefits of application', 'Special consideration needs'. The overall objective for interdepartmental CRM kick-off meetings is to confirm that all parties agree on certain key points and understand platform rationale and functionality.

    The kick-off process will significantly improve internal communications by inviting all affected internal IT groups, including business units, to work together to address significant issues before the application process is formally activated.

    Department groups or designated trainers should take the lead and implement a process for:

    • Scheduling CRM platform roll-out/kick-off meetings.
    • Soliciting preliminary input from the attending groups to develop further training plans.
    • Establishing communication paths and the key communication agents from each department who are responsible for keeping lines open moving forward.

    Ensure requirements are met with robust user acceptance testing

    User acceptance testing (UAT) is a test procedure that helps to ensure end-user requirements are met. Test cases can reveal bugs before the suite is implemented.

    Five Secrets of UAT Success

    Bracket with colors corresponding the adjacent list items.

    1

    Create the plan With the information collected from requirements gathering, create the plan. Make sure this information is added to the main project plan documentation.

    2

    Set the agenda The time allotted will vary depending on the functionality being tested. Ensure that the test schedule allows for the resolution of issues and discussion.

    3

    Determine who will participate Work with the relevant stakeholders to identify the people who can best contribute to system testing. Look for experienced power users who have been involved in earlier decision making about the system.

    4

    Highlight acceptance criteria Together with the UAT group, pinpoint the criteria to determine system acceptability. Refer back to requirements specified in use cases in the initial requirements-gathering stages of the project.

    5

    Collect end user feedback Weaknesses in resolution workflow design, technical architecture, and existing customer service processes can be highlighted and improved on with ongoing surveys and targeted interviews.

    Calculate post-deployment metrics to assess measurable value of the project

    Track the post-deployment results from the project and compare the metrics to the current state and target state.

    CRM Selection and Implementation Metrics
    Description Formula Current or Estimated Target Post-Deployment
    End-User Satisfaction # of Satisfied Users
    # of End Users
    70% 90% 85%
    Percentage Over/Under Estimated Budget Amount Spent - 100%
    Budget
    5% 0% 2%
    Percentage Over/Under Estimated Timeline Project Length - 100%
    Estimated Timeline
    10% -5% -10%

    CRM Strategy Metrics
    Description Formula Current or Estimated Target Post-Deployment
    Number of Leads Generated (per month) # of Leads Generated 150 200 250
    Average Time to Resolution (in minutes) Time Spent on Resolution
    # of Resolutions
    30 minutes 10 minutes 15 minutes
    Cost per Interaction by Campaign Total Campaign Spending
    # of Customer Interactions
    $17.00 $12.00 $12.00

    Select the Right CRM Platform

    CRM technology is critical to facilitate an organization’s relationships with customers, service users, employees, and suppliers. Having a structured approach to building a business case, defining key requirements, and engaging with the right shortlist of vendors to pick the best finalist is crucial.

    This selection guide allows organizations to execute a structured methodology for picking a CRM that aligns with their needs. This includes:
    • Alignment and prioritization of key business and technology drivers for a CRM selection business case.
    • Identification of key use cases and requirements for CRM.
    • Construction of a robust CRM RFP.
    • A strong market scan of key players.
    • A survey of crucial implementation considerations.
    This formal CRM selection initiative will drive business-IT alignment, identify sales and marketing automation priorities, and allow for the rollout of a platform that’s highly likely to satisfy all stakeholder needs.

    If you would like additional support, have our analysts guide you through other phases as part of an Info-Tech workshop.

    Contact your account representative for more information.
    workshops@infotech.com
    1-888-670-8889

    Insight summary

    Stakeholder satisfaction is critical to your success

    Choosing a solution for a single use case and then expanding it to cover other purposes can be a way to quickly gain approvals and then make effective use of dollars spent. However, this can also be a nightmare if the product is not fit for purpose and requires significant customization effort for future use cases. Identify use cases early, engage stakeholders to define success, and recognize where you need to find balance between a single off-the-shelf CRM platform and adjacent MarTech or sales enablement systems.

    Build a business case

    An effective business case isn’t a single-purpose document for obtaining funding. It can also be used to drive your approach to product selection, requirements gathering, and ultimately evaluating stakeholder and user satisfaction.

    Use your business case to define use cases and milestones as well as success.

    Balance process with technology

    A new solution with old processes will result in incremental increased value. Evaluate existing processes and identify opportunities to improve and remove workarounds. Then define requirements.

    You may find that the tools you have would be adequate with an upgrade and tool optimization. If not, this exercise will prepare you to select the right solution for your current and future needs.

    Drive toward early value

    Lead with the most important benefit and consider the timeline. Most stakeholders will lose interest if they don’t realize benefits within the fist year. Can you reach your goal and report success within that timeline?

    Identify secondary, incremental customer engagement improvements that can be made as you work toward the overall goal to be achieved at the one-year milestone.

    Related Info-Tech Research

    Stock image of an office worker. Build a Strong Technology Foundation for Customer Experience Management
    • Any CRM project needs to be guided by the broader strategy around customer engagement. This blueprint explores how to create a strong technology enablement approach for CXM using voice of the customer analysis.
    Stock image of a target with arrows. Improve Requirements Gathering
    • 70% of projects that fail do so because of poor requirements. If you need to double-click on best practices for eliciting, analyzing, and validating requirements as you build up your CRM picklist and RFP, this blueprint will equip you with the knowledge and tools you need to hit the ground running.
    Stock image of a pen on paper. Drive Successful Sourcing Outcomes with a Robust RFP Process
    • Managing a complex RFP process for an enterprise application like a CRM platform can be a challenging undertaking. This blueprint zooms into how to build, run, administer, and evaluate RFP responses effectively.

    Bibliography

    “Doomed From the Start? Why a Majority of Business and IT Teams Anticipate Their Software Development Projects Will Fail.” Geneca, 25 Jan. 2017. Web.

    Hall, Kerrie. “The State of CRM Data Management 2020.” Validity. 27 April 2020. Web.

    Hinchcliffe, Dion. “The Evolving Role of the CIO and CMO in Customer Experience.” ZDNet, 22 Jan. 2020. Web.

    Klie, L. “CRM Still Faces Challenges, Most Speakers Agree: CRM Systems Have Been Around for Decades, but Interoperability and Data Siloes Still Have to Be Overcome.” CRM Magazine, vol. 23, no. 5, 2019, pp. 13-14.

    Markman, Jon. "Netflix Knows What You Want... Before You Do." Forbes. 9 Jun. 2017. Web.

    Morgan, Blake. “50 Stats That Prove The Value Of Customer Experience.” Forbes, 24 Sept. 2019. Web.

    Taber, David. “What to Do When Your CRM Project Fails.” CIO Magazine, 18 Sept. 2017. Web.

    “The State of Project Management Annual Survey 2018.” Wellingtone, 2018. Web.

    “The History of Microsoft Dynamics.” Eswelt. 2021. Accessed 8 June 2022.

    “Unlock the Mysteries of Your Customer Relationships.” Harvard Business Review. 1 July 2014. Accessed 30 Mar. 2016.

    Next-Generation InfraOps

    • Buy Link or Shortcode: {j2store}457|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Operations Management
    • Parent Category Link: /i-and-o-process-management
    • Traditional IT capabilities, activities, organizational structures, and culture need to adjust to leverage the value of cloud, optimize spend, and manage risk.
    • Different stakeholders across previously separate teams rely on one another more than ever, but rules of engagement do not yet exist.

    Our Advice

    Critical Insight

    • By defining your end goals and framing solutions based on the type of visibility and features you need, you can enable speed and reliability without losing control of the work.

    Impact and Result

    • Understand the xOps spectrum and what approaches benefit your organization.
    • Make sense of the architectural approaches and enablement tools available to you.
    • Evolve from just improving your current operations to a continuous virtuous cycle of development and deployment.

    Next-Generation InfraOps Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Next-Generation InfraOps Storyboard – A deck that will help you use Ops methodologies to build a virtuous cycle.

    This storyboard will help you understand the spectrum of different Agile xOps working modes and how best to leverage them and build an architecture and toolset that support rapid continuous IT operations

    • Next-Generation InfraOps Storyboard
    [infographic]

    Further reading

    Next-Generation InfraOps

    Embrace the spectrum of Ops methodologies to build a virtuous cycle.

    Executive summary

    Your Challenge

    IT Operations continue to be challenged by increasing needs for scale and speed, often in the face of constrained resources and time. For most, Agile methodologies have become a foundational part of tackling this problem. Since then, we've seen Agile evolve into DevOps, which started a trend into different categories of "xOps" that are too many to count. How does one make sense of the xOps spectrum? What is InfraOps and where does it fit in?

    Common Obstacles

    Ultimately, all these methodologies and approaches are there to serve the same purpose: increase effectiveness through automation and improve governance through visibility. The key is to understand what tools and methodologies will deliver actual benefits to your IT operation and to the organization as a whole.

    Info-Tech's Approach

    By defining your end goals and framing solutions based on the type of visibility and features you need, you can enable speed and reliability without losing control of the work.

    1. Understand the xOps spectrum and what approaches will benefit your organization.
    2. Make sense of the architectural approaches and enablement tools available to you.
    3. Evolve from just improving your current operations to a continuous virtuous cycle of development and deployment.

    Info-Tech Insight

    InfraOps, when applied well, should be the embodiment of the governance policies as expressed by standards in architecture and automation.

    Project overview

    Understand the xOps spectrum

    There are as many different types of "xOps" as there are business models and IT teams. To pick the approaches that deliver the best value to your organization and that align to your way of operating, it's important to understand the different major categories in the spectrum and how they do or don't apply to your IT approach.

    How to optimize the Ops in DevOps

    InfraOps is one of the major methodologies to address a key problem in IT at cloud scale: eliminating friction and error from your deliveries and outputs. The good news is there are architectures, tools, and frameworks you can easily leverage to make adopting this approach easier.

    Evolve to integration and build a virtuous cycle

    Ultimately your DevOps and InfraOps approaches should embody your governance needs via architecture and process. As time goes on, however, both your IT footprint and your business environment will shift. Build your tools, telemetry, and governance to anticipate and adapt to change and build a virtuous cycle between development needs and IT Operations tools and governance.

    The xOps spectrum

    This is an image of the xOps spectrum. The three main parts are: Code Acceleration (left), Governance(middle), and Infrastructure Acceleration (right)

    xOps categories

    There is no definitive list of x's in the xOps spectrum. Different organizations and teams will divide and define these in different ways. In many cases, the definitions and domains of various xOps will overlap.

    Some of the commonly adopted and defined xOps models are listed here.

    Shift left? Shift right?

    Cutting through the jargon

    • Shifting left is about focusing on the code and development aspects of a delivery cycle.
    • Shifting right is about remembering that infrastructure and tools still do matter.

    Info-Tech Insight

    Shifting left or right isn't an either/or choice. They're more like opposite sides of the same coin. Like the different xOps approaches, usually more than one shift approach will apply to your IT Operations.

    IT Operations in the left-right spectrum

    Shifting from executing and deploying to defining the guardrails and standards

    This is an image of the left-right spectrum for your XOps position

    Take a middle-out approach

    InfraOps and DevOps aren't enemies; they're opposite sides of the same coin.

    • InfraOps is about the automation and standardization of execution. It's an essential element in any fully automated CI/CD pipeline.
    • Like DevOps, InfraOps is built on similar values (the pillars of DevOps).
    • It builds on the principle of Lean to focus on removing friction, or turn-and-type activities, from the pipeline/process.
    • In InfraOps, one of the key methods for removing friction is through automation of the interstitia between different phases of a DevOps or CI/CD cycle.

    Optimize the Ops in DevOps

    Focus on eliminating friction

    This is an image of an approach to optimizing the ops in DevOps.

    With the shift from execution to governing and validating, the role of deployment falls downstream of IT Operations.

    IT Operations needs to move to a mindset that focuses on creating the guardrails, enforced standards, and compliance rules that need to be used downstream, then apply those standards using automation and tooling to remove friction and error from the interstitia (the white spaces between chevrons) of the various phases.

    InfraOps tools

    Four quadrants in the shape of a human head, in the boxes are the following: Hyperconverged Infrastructure; Composable Infrastructure; Infrastructure as code and; Automation and Orchestration

    Info-Tech Insight

    Your tools can be broken into two categories:

    • Infrastructure Architecture
      • HCI vs. CI
    • Automation Tooling
      • IaC and A&O

    Keep in mind that while your infrastructure architecture is usually an either/or choice, your automation approach should use any and all tooling that helps.

    Infrastructure approach

    • Hyperconverged

    • Composable

    Hyperconverged Infrastructure (HCI)

    Hyperconvergence is the next phase of convergence, virtualizing servers, networks, and storage on a single server/storage appliance. Capacity scales as more appliances are added to a cluster or stack.
    The disruptive departure:

    • Even though servers, networks, and storage were each on their own convergence paths, the three remained separate management domains (or silos). Even single-SKU converged infrastructures like VCE Vblocks are still composed of distinct server, network, and storage devices.
    • In hyperconvergence, the silos collapse into single-software managed devices. This has been disruptive for both the vendors of technology solutions (especially storage) and for infrastructure management.
    • Large storage array vendors are challenged by hyperconvergence alternatives. IT departments need to adapt IT skills and roles away from individual management silos and to more holistic service management.

    A comparison between converged and hyperconverged systems.

    Info-Tech Insight

    HCI follows convergence trends of the past ten years but is also a departure from how IT infrastructure has traditionally been provisioned and managed.

    HCI is at the same time a logical progression of infrastructure convergence and a disruptive departure.

    Hyperconverged (HCI) – SWOT

    HCI can be the foundation block for a fully software defined data center, a prerequisite for private cloud.

    Strengths

    • Potentially lower TCO through further infrastructure consolidation, reducing CapEx and OpEx expenditures through facilities optimization and cost consolidation.
    • Operations in particular can be streamlined, since storage, network connections, and processors/memory are all managed as abstractions via a single control pane.
    • HCI comes with built-in automation and analytics that lead to quicker issue resolution.

    Opportunities

    • Increased business agility by paving the way for a fully software defined infrastructure stack and cloud automation.
    • Shift IT human assets from hardware asset maintainers and controllers to service delivery managers.
    • Better able to compete with external IT service alternatives.
    • Move toward a hybrid cloud service offering where the service catalog contains both internal and external offerings.

    Key attributes of a cloud are automation, resource elasticity, and self-service. This kind of agility is impossible if physical infrastructure needs intervention.

    Info-Tech Insight

    Virtualization alone does not a private cloud make, but complete stack virtualization (software defined) running on a hands-off preconfigured HCI appliance (or group of appliances) provides a solid foundation for building cloud services.

    Hyperconverged (HCI) – SWOT

    Silo-busting and private cloud sound great, but are your people and processes able to manage the change?

    Weaknesses

    • HCI typically scales out linearly (CPU & storage). This does not suit traditional scale-up applications such as high-performance databases and large-capacity data warehouses.
    • Infrastructure stacks are perceived as more flexible for variable growth across segments. For example, if storage is growing but processing is not, storage can scale separately from processing.

    Threats

    • HCI will be disruptive to roles within IT. Internal pushback is a real threat if necessary changes in skills and roles are not addressed.
    • HCI is not a simple component replacement but an adoption of a different kind of infrastructure. Different places in the lifecycles for each of storage, network, and processing devices could make HCI a solution where there is no immediate problem.

    In traditional infrastructure, performance and capacity are managed as distinct though complementary jobs. An all-in-one approach may not work.

    Composable Infrastructure (CI)

    • Composable infrastructure in many ways represents the opposite of an HCI approach. Its focus is on further disaggregating resources and components used to build systems.
      • Unlike traditional cloud virtual systems, composable infrastructure provides virtual bare metal resources, allowing tightly coupled resources like CPU, RAM, and GPU – or any device/card/module – to be released back and forth into the resource pool as required by a given workload.
      • This is enabled by the use of high-speed, low-latency PCI Express (PCI-e) and Compute Express Link (CXL) fabrics that allow these resources to be decoupled.
      • It also supports the ability to present other fabric types critical for building out enterprise systems (e.g. Ethernet, InfiniBand).
    • Accordingly, CI systems are also based on next-generation network architecture that supports moving critical functions to the network layer, which enables more efficient use of the application-layer resources.

    Composable Infrastructure (CI)

    • CI may also leverage network-resident data/infrastructure processing units (DPUs/IPUs), which offload many network, security, and storage functions.
      • As new devices and functions become available, they can be added into the catalog of resources/functions available in a CI pool.

    Use Case Example: Composable AI flow

    Data Ingestion > Data Cleaning/Tagging > Training > Conclusion
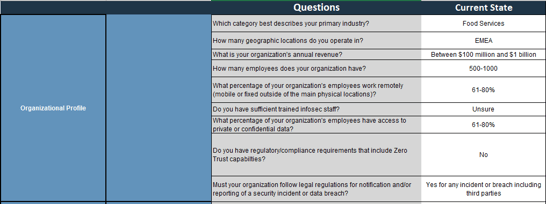
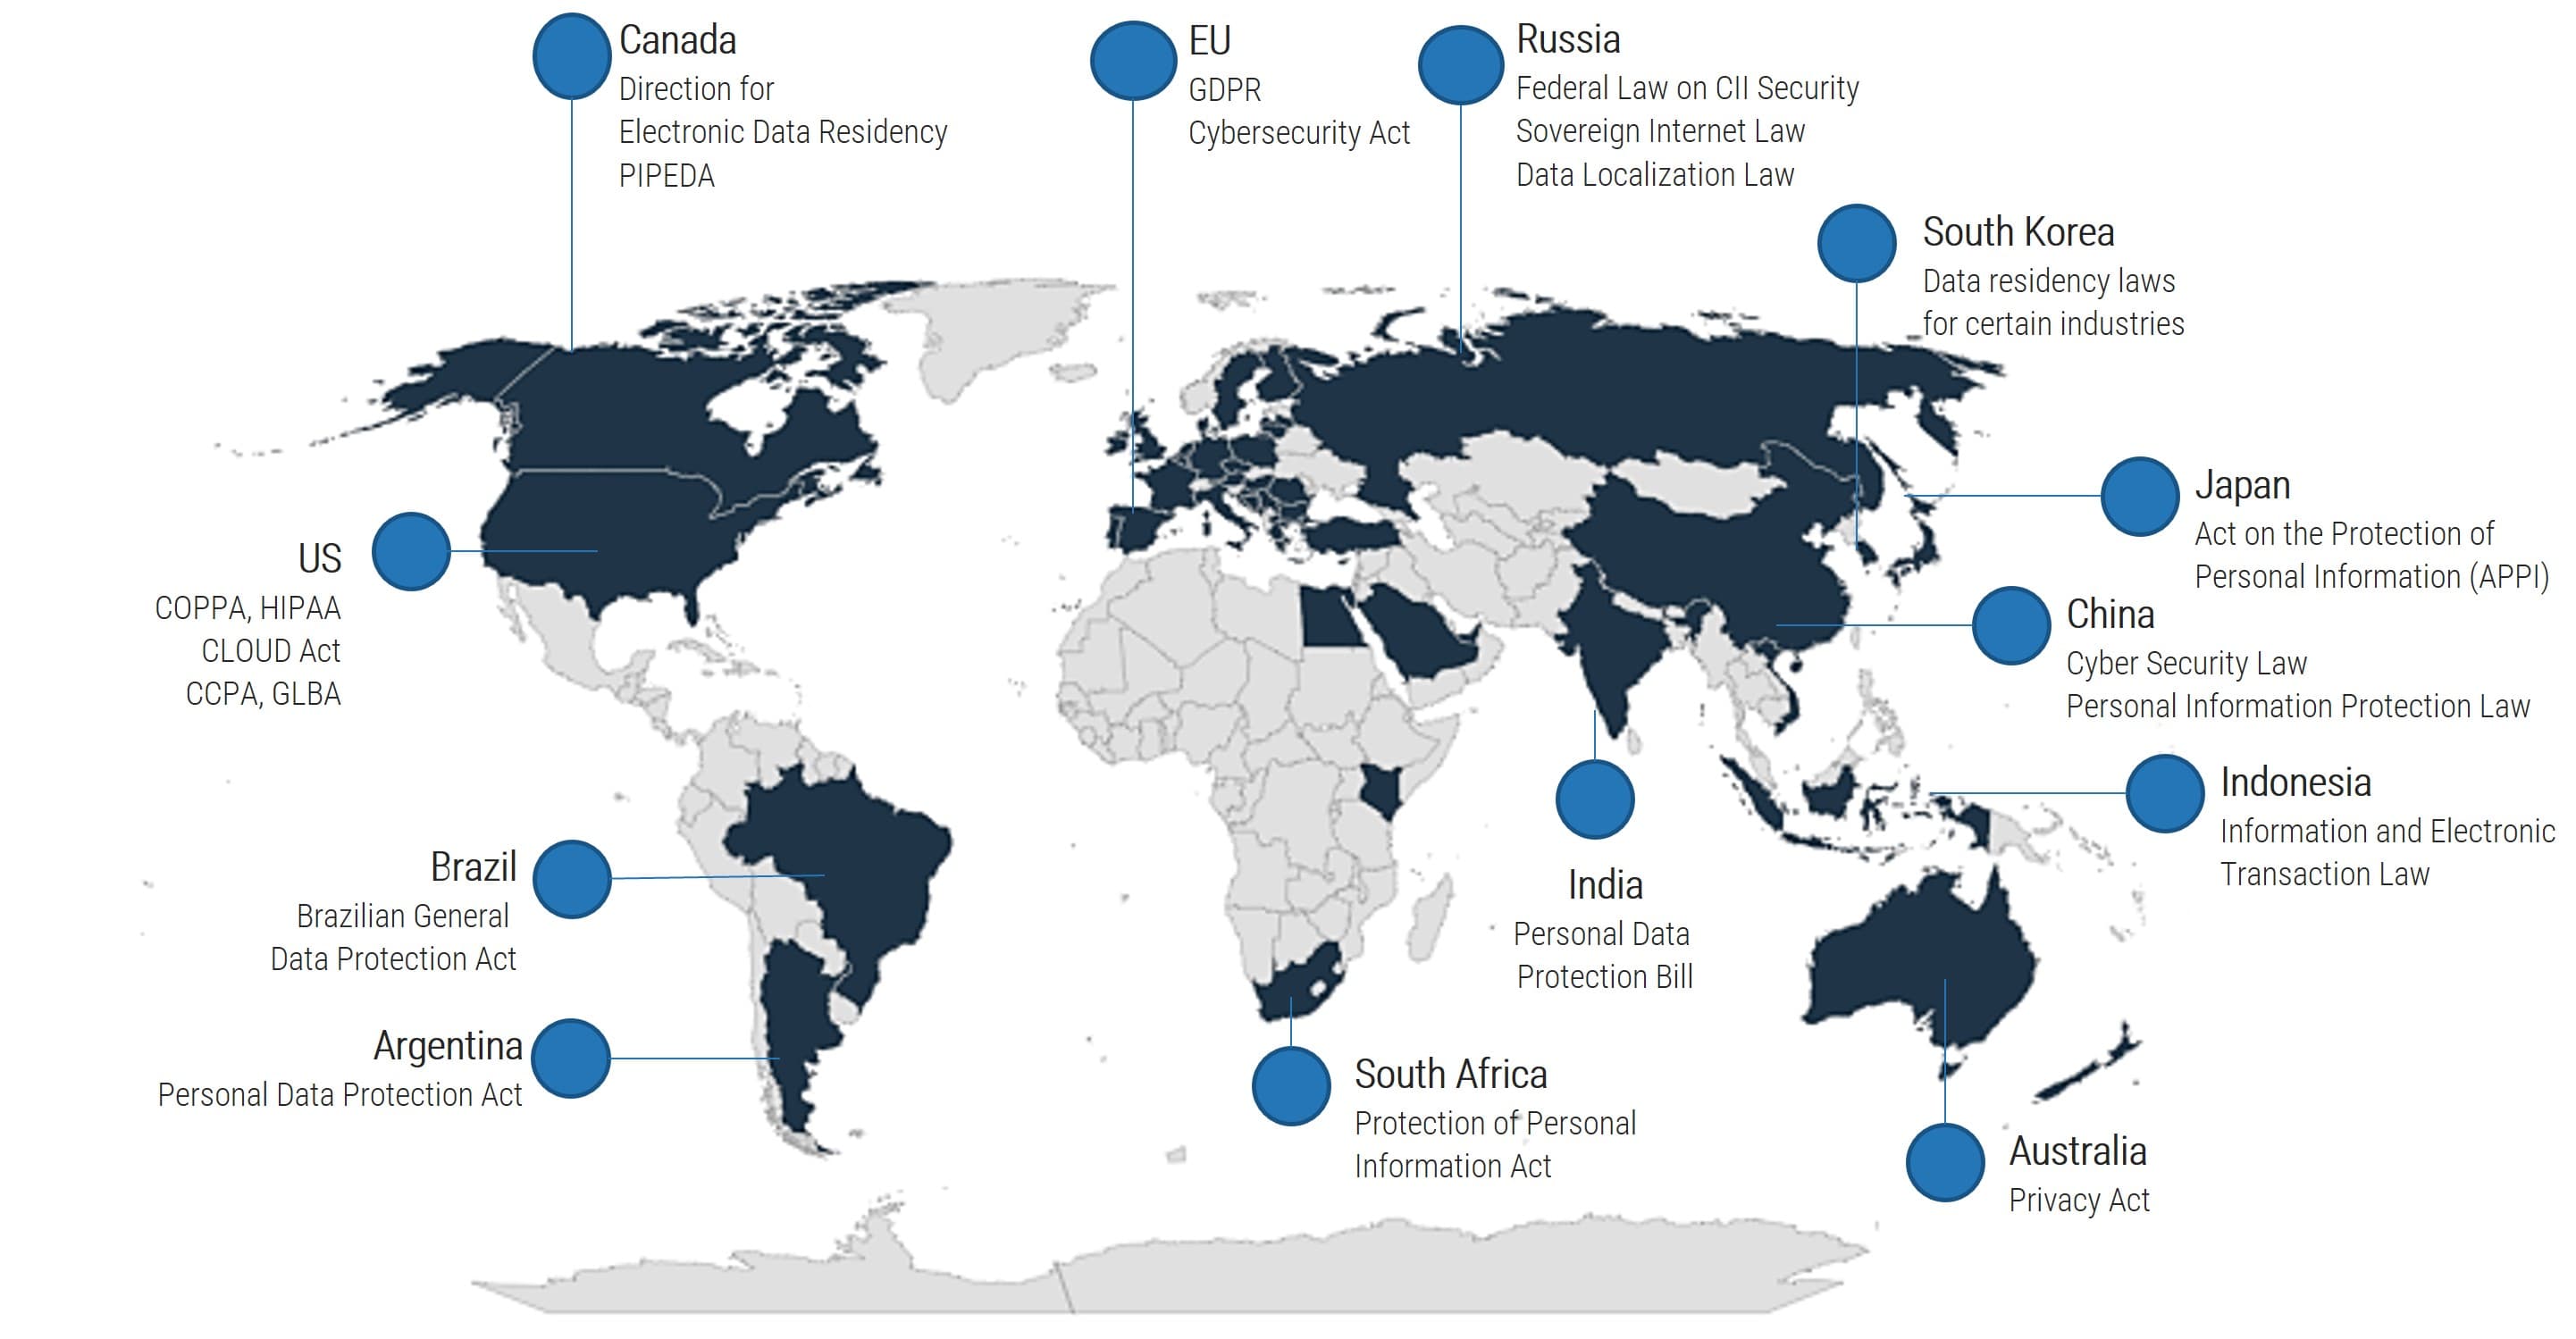
    • At each phase of the process, resources, including specialized hardware like memory and GPU cores, can be dynamically allocated and reallocated to the workload on demand

    Composable Infrastructure (CI)

    Use cases and considerations

    Where it's useful

    • Enable even more efficient allocation/utilization of resources for workloads.
    • Very large memory or shared memory requirements can benefit greatly.
    • Decouple purchasing decisions for underlying resources.
    • Leverage the fabric to make it easier to incrementally upgrade underlying resources as required.
    • Build "the Impossible Server."

    Considerations

    • Requires significant footprint/scale to justify in many cases
    • Not necessarily good value for environments that aren't very volatile and heterogeneous in terms of deployment requirements
    • May not be best value for environments where resource-stranding is not a significant issue

    Info-Tech Insight

    Many organizations using a traditional approach report resource stranding as having an impact of 20% or more on efficiency. When focusing specifically on the stranding of memory in workloads, the number can often approach 40%.

    The CI ecosystem

    This is an image of the CI ecosystem.

    • The CI ecosystem has many players, large and small!
    • Note that the CI ecosystem is dependent on a large ecosystem of underlying enablers and component builders to support the required technologies.

    Understanding the differences

    This image shows the similarities and differences between traditional, cloud, hyperconverged, and composable.

    Automation approach

    • Infrastructure as Code
    • Automation & Orchestration
    • Metaorchestration

    Infrastructure as Code (IaC)

    Infrastructure as code (IaC) is the process of managing and provisioning computer data centers through machine-readable definition files rather than physical hardware configuration or interactive configuration tools.

    Before IaC, IT personnel would have to manually change configurations to manage their infrastructure. Maybe they would use throwaway scripts to automate some tasks, but that was the extent of it.

    With IaC, your infrastructure's configuration takes the form of a code file, making it easy to edit, copy, and distribute.

    Info-Tech Insight
    IaC is a critical tool in enabling key benefits!

    • Reduced costs
    • Increased scalability, flexibility, and speed
    • Better consistency and version control
    • Reduced deployment errors

    Infrastructure as Code (IaC)

    1. IaC uses a high-level descriptive coding language to automate the provisioning of IT infrastructure. This eliminates the need to manually provision and manage servers, OS, database connections, storage, and other elements every time we want to develop, test, or deploy an application.
    2. IaC allows us to define the computer systems on which code needs to run. Most commonly, we use a framework like Chef, Ansible, Puppet, etc., to define their infrastructure. These automation and orchestration tools focus on the provisioning and configuring of base compute infrastructure.
    3. IaC is also an essential DevOps practice. It enables teams to rapidly create and version infrastructure in the same way they version source code and to track these versions so as to avoid inconsistency among IT environments that can lead to serious issues during deployment.
    • Idempotence is a principle of IaC. This means a deployment command always sets the target environment into the same configuration, regardless of the environment's starting state.
      • Idempotency is achieved by either automatically configuring an existing target or discarding the existing target and recreating a fresh environment.

    Automation/Orchestration

    Orchestration describes the automated arrangement, coordination, and management of complex computer systems, middleware, and services.

    This usage of orchestration is often discussed in the context of service-oriented architecture, virtualization, provisioning, converged infrastructure, and dynamic data center topics. Orchestration in this sense is about aligning the business request with the applications, data, and infrastructure.

    It defines the policies and service levels through automated workflows,
    provisioning, and change management. This creates an application-aligned infrastructure that can be scaled up or down based on the needs of each application.

    As the requirement for more resources or a new application is triggered, automated tools now can perform tasks that previously could only be done by multiple administrators operating on their individual pieces of the physical stack.

    Orchestration also provides centralized management of the resource pool, including billing, metering, and chargeback for consumption. For example, orchestration reduces the time and effort for deploying multiple instances of a single application.

    Info-Tech Insight

    Automation and orchestration tools can be key components of an effective governance toolkit too! Remember to understand what data can be pulled from your various tools and leveraged for other purposes such as cost management and portfolio roadmapping.

    Automation/Orchestration

    There are a wide variety of orchestration and automation tools and technologies.

    Configuration Management

    Configuration Management

    The logos for companies which fall in each of the categories in the column to the left of the image.

    CI/CD
    Orchestration

    Container
    Orchestration

    Cloud-Specific
    Orchestration

    PaaS
    Orchestration

    Info-Tech Insight

    Automation and orchestration tools and software offerings are plentiful, and many of them have a different focus on where in the application delivery ecosystem they provide automation functionality.

    Often there are different tools for different deployment and service models as well as for different functional phases for each service model.

    Automation/Orchestration

    Every tool focuses on different aspects or functions of the deployment of resources and applications.

    • Resources
      • Compute
      • Storage
      • Network
    • Extended Services
      • Platforms
      • Infrastructure Services
      • Web Services
    • Application Assets
      • Images
      • Templates
      • Containers
      • Code

    Info-Tech Insight

    Let the large ecosystem of tools be your ally. Leverage the right tools where needed and then address the complexity of tools using a master orchestration scheme.

    Metaorchestration

    A Flow chart for the approach to metaorchestration.

    Additionally, most tools do not cover all aspects required for most automation implementations, especially in hybrid cloud scenarios.

    As such, often multiple tools must be deployed, which can lead to fragmentation and loss of unified controls.

    Many enterprises address this fragmentation using a cloud management platform approach.

    One method of achieving this is to establish a higher layer of orchestration – an "orchestrator of orchestrators," or metaorchestration.

    In complex scenarios, this can be a challenge that requires customization and development.

    InfraOps tools ecosystem

    Toolkit Pros Cons Tips
    HCI Easy scale out Shift in skills required Good for enabling automation and hybridization with current-gen public cloud services
    CI Maximal workload resource efficiency Investment in new fabrics and technologies Useful for very dynamic or highly scalable workloads like AI
    IaC Error reduction and standardization Managing drift in standards and requirements Leverage a standards and exception process to keep track of drift
    A&O Key enabler of DevOps automation within phases Usually requires multiple toolsets/frameworks Use the right tools and stitch together at the metaorchestration layer
    Metaorchestration Reduces the complexity of a diverse A&O and IaC toolkit Requires understanding of the entire ecosystems of tools used Key layer of visibility and control for governance

    Build a virtuous cycle

    Remember, the goal is to increase speed AND reliability. That's why we focus on removing friction from our delivery pipelines.

    • The first step is to identify the points of friction in your cycle and understand the intensity and frequency of these friction points.
    • Depending on your delivery and project management methodology, you'll have a different posture of the different tools that make sense for your pipeline.
    • For example, if you are focused on delivering raw resources for sysadmins and/or you're in a Waterfall methodology where the friction points are large but infrequent, hyperconverged is likely to delivery good value, whereas tools like IaC and orchestration may not be as necessary.

    Info-Tech Insight

    Remember that, especially in modern and rapid methodologies, your IT footprint can drift unexpectedly. This means you need a real feedback mechanism on where the friction moves to next.

    This is particularly important in more Agile methodologies.

    Activity: Map your IT operations delivery

    Identify your high-friction interstitial points

    • Using the table below, or a table modified to your delivery phases, map out the activities and tasks that are not standardized and automated.
    • For the incoming and outgoing sections, think about what resources and activities need to be (or could be) created, destroyed, or repurposed to efficiently manage each cycle and the spaces between cycles.
    Plan Code Test Deploy Monitor
    Incoming Friction
    In-Cycle Friction
    Outgoing Friction

    Info-Tech Insight

    Map your ops groups to the delivery cycles in your pipeline. How many delivery cycles do you have or need?

    Good InfraOps is a reflection of governance policies, expressed by standards in architecture and automation.

    Related Info-Tech Research

    Evaluate Hyperconverged Infrastructure for Your Infrastructure Roadmap

    • This Info-Tech note covers evaluation of HCI platforms.

    Design Your Cloud Operations

    • This Info-Tech blueprint covers organization of operations teams for various deployment and Agile modes.

    Bibliography

    Banks, Ethan, host. "Choosing Your Next Infrastructure." Datanauts, episode 094, Packet Pushers, 26 July 2017. Podcast.
    "Composable Infrastructure Solutions." Hewlett Packard Canada, n.d. Web.
    "Composable Infrastructure Technology." Liqid Inc., n.d. Web.
    "DataOps architecture design." Azure Architecture Center, Microsoft Learn, n.d. Web.
    Tan, Pei Send. "Differences: DevOps, ITOps, MLOps, DataOps, ModelOps, AIOps, SecOps, DevSecOps." Medium, 5 July 2021. Web.

    Prepare an Actionable Roadmap for Your PMO

    • Buy Link or Shortcode: {j2store}358|cart{/j2store}
    • member rating overall impact: 9.5/10 Overall Impact
    • member rating average dollars saved: $103,124 Average $ Saved
    • member rating average days saved: 55 Average Days Saved
    • Parent Category Name: Project Management Office
    • Parent Category Link: /project-management-office
    • Problems with project management offices (PMOs) often start with a lack of a clear definition of what the PMO is actually about and what the organization does.
    • Few organizations provide the minimum required services, and many are not using their PMOs effectively. Many people see the PMO as nothing more than the “project document police,” i.e. a source of red tape rather than a helpful support system. This impacts staffing and hiring.
    • The PMO is often misunderstood as a center for project management governance when it also needs to facilitate the communication of project data from project teams to decision makers to ensure that appropriate decisions get made around resourcing, approval of new projects, etc.
    • Accountability is something that is not clearly defined for many activities that flow through the PMO. Business leaders, project workers, and project managers are rarely as aligned as they need to be.

    Our Advice

    Critical Insight

    • There is a gap in the perception of the actual role of the PMO in many organizations by different stakeholder groups. Many people see the PMO as police that produce red tape rather than a helpful support system. Those that need to present a coherent plan to leadership to champion the need for a PMO often have an uphill battle.
    • Determine the PMO’s role and needs and then determine your staff needs based on that PMO.
    • Staff the PMO according to its actual role and needs. Don’t rush to the assumption that PMO staff starts with accomplished project managers.
    • The difference in a winning PMO is determined by a roadmap or plan created at the beginning.

    Impact and Result

    • Define a PMO with functions that work for you based on the needs of your organization and the gaps in services. A “fit-for-purpose” PMO is the right kind of PMO for your organization.
    • Determine your PMO staffing needs. Our approach to building a PMO starts by analyzing the staffing requirements of your PMO mandate.
    • Create purpose-built role descriptions. Once you understand the staff and skills you’ll need to succeed, we have job description aids you’ll need to fill the roles.

    Prepare an Actionable Roadmap for Your PMO Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Prepare and Actionable Roadmap for Your PMO – An actionable deck to help you establish a valuable PMO.

    Before setting up or re-structuring a PMO, organizational need should not only be taken into consideration but used as a foundation. Phase 1 of this blueprint will help you define the services that your PMO should provide to your organization, instead of the one-size-fits-all approach that doesn’t work.

    • Prepare an Actionable Roadmap for Your PMO – Phases 1-3

    2. PMO Role Definition Tool – An Excel tool to help you define the services of your PMO.

    Use the PMO Role Definition Tool to establish your PMO current state and the service gaps you may have. Use the results to determine the role your PMO should play within your organization.

    • PMO Role Definition Tool

    3. PMO Project Charter – A template to formalize your PMO and make sure everyone is on the same page.

    The PMO Project Charter shares the vision to achieve consensus between stakeholders and projects and initiatives of the PMO. Use this template to jump-start your PMO project.

    • PMO Project Charter

    4. Blank Job Description Template – A template to create different job descriptions from.

    Use this template to create your job descriptions from scratch.

    • Blank Job Description Template

    5. Portfolio Manager Job Description – A clear and realistic job description template for a Portfolio Manager.

    The Portfolio Manager will oversee the business of discovering unsatisfied needs, articulating them as project demand, and organizing appropriate responses. Your customers are the people who approve projects, and you will service them.

    • Portfolio Manager

    6. PMO Job Description Builder Workbook – An Excel tool to help you access PMO staffing requirements.

    This tool will help you assess staffing requirements to facilitate project management, business analysis, and organizational change management outcomes.

    • PMO Job Description Builder Workbook

    7. PMO Strategic Plan – A template to help you compose a PMO strategy.

    This template will help you compose a PMO strategy. Follow the steps in the blueprint to complete the strategy.

    • PMO Strategic Plan

    8. Organizational Change Impact Analysis Tool – An Excel tool to analyze the impact of change to the organization.

    Use the Organizational Change Impact Analysis Tool to analyze the effects of a change across the organization, and to assess the likelihood of adoption to right-size your OCM efforts.

    • Organizational Change Impact Analysis Tool

    9. PMO MS Project Plan – A template to map out timeline for completing the tasks to create your PMO.

    Use this tool to determine the next steps and assign tasks to the appropriate people.

    • PMO MS Project Plan Sample

    Infographic

    Workshop: Prepare an Actionable Roadmap for Your PMO

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Define

    The Purpose

    Get a common understanding of your PMO options.

    Determine where you are and engage leadership.

    Key Benefits Achieved

    A clear vision for your PMO and an articulated reason for establishing it.

    An understanding of you PMO goals and which challenges it sets to address.

    Activities

    1.1 PPM Current State Scorecard

    1.2 SWOT Analysis

    1.3 Current State and Leadership Engagement

    1.4 PMO Mandate and Vision

    Outputs

    PPM Current State Scorecard Results

    SWOT Results

    PMO Role Development Tool

    PMO Charter

    2 Staff

    The Purpose

    Identify organizational design.

    Build job descriptions.

    Key Benefits Achieved

    An analysis of staffing requirements of your PMO that aligns with your mandate from phase 1.

    Job description aids to fill the necessary roles.

    Activities

    2.1 Right, Wrong, Missing, Confusing

    2.2 PMO Function, Roles, and Responsibilities

    2.3 Job Descriptions

    Outputs

    Right, Wrong, Missing, Confusing Results

    Job Description Survey Tool

    Job Description Templates

    3 Plan

    The Purpose

    Create a roadmap.

    Key Benefits Achieved

    An actionable roadmap that can be presented to leadership and implemented.

    Activities

    3.1 Roadmap Hierarchy and Staffing and Sizing

    3.2 Governance and Authority

    Outputs

    PMO Roadmap Draft

    Governance Authority

    4 Change

    The Purpose

    Set up governance and OCM.

    Key Benefits Achieved

    An introduction to the concept of governance and tools for a change impact analysis.

    Activities

    4.1 Analyze the impact of the change across multiple dimensions and stakeholder groups.

    4.2 Gain sponsorship.

    Outputs

    Organizational Change Impact Analysis Tool

    Sponsor Template

    Further reading

    Prepare an Actionable Roadmap for Your PMO

    Turn planning into action with a realistic PMO timeline.

    EXECUTIVE BRIEF

    Analyst Perspective

    Prepare an actionable roadmap for your PMO.

    Photo of Ugbad Farah, PMP, Senior Research Analyst, PPM, Info-Tech Research Group

    We all have junk drawers somewhere in our homes, and we probably try not to think about what’s going on in there. We’re just happy that they close and that the contents are concealed from anyone living in or passing through the house.

    What goes in these junk drawers? Things that don’t have a home, things you don’t know what to do with, and things you don’t have the time or desire to deal with. Eventually, the drawer gets full, and it doesn’t serve you anymore because you can’t add anything else to it. Instead of cleaning the drawer and keeping the things you need, you throw everything away in one sweep. One day you will start the process again.

    The junk drawer is like your project management office (PMO). The PMO is given projects that are barely scoped, projects that don’t have clear sponsors, and ad hoc administrative tasks you don’t have the time or desire to deal with. Inevitably, your PMO is out of capacity. This happens rather quickly, since it’s understaffed. You question its purpose because you made it a junk drawer. You even think about closing it. One day you will start the process again.

    Use this blueprint to stop the madness. Learn how to properly define, staff, and plan a roadmap of a PMO that will actually serve your organization.

    Ugbad Farah, PMP
    Senior Research Analyst, PPM
    Info-Tech Research Group

    Your challenge

    This research is designed to help organizations that are facing these challenges:

    • No visibility into projects
    • The organization views the PMO as unnecessary overhead
    • The PMO is not properly staffed to support the organization’s needs
    • Project managers/staff aren’t providing information or following processes
    • Leadership and sponsors are disengaged

    Pie chart of 'IT Time Allocation by Area'. The grey section on the bottom left represents 'Projects and Project Portfolio Management, 11.5%'.
    IT is responsible for many different business services. The data from Info-Tech’s IT Staffing diagnostic shows that 11.5% of staff time is spent on projects and project portfolio management. (Source: Info-Tech IT Staffing Benchmark Report)

    PMOs can’t do everything and be all things to all people. Define limits with a strong mandate and effective staffing. Make sure you have the skills and capacity to support required PMO functions.

    Project management chaos

    PMOs get pulled into the day-to-day project and resourcing issues, making it difficult to focus on running a portfolio:

    1. Teammates seem unphased by overdue tasks and missed milestones.
    2. Fire drills may happen more often than planned projects.
    3. Resources are allocated and then redirected to something more urgent.
    4. Communication that’s stuck in silos, leading to confusion about priorities.
    5. Due dates mysteriously shift without explanation.
    6. Project teams are more focused on the due date than adoption and outcomes.

    Common obstacles

    IT and PMO leaders face several challenges.

    • Many people see the PMO as nothing more than the “project document police,” i.e. a source of red tape rather than a helpful support system. This impacts staffing and hiring.
    • The PMO is often misunderstood as a center for project management governance, when it also needs to facilitate the communication of project data from project teams to decision makers to ensure that appropriate decisions get made around resourcing, approval of new projects, etc.
    • Accountability is something that is not clearly defined for many activities that flow through the PMO. Business leaders, project workers, and project managers are rarely as aligned as they need to be.

    The Reality

    68% — Sixty-eight percent of stakeholders see their PMOs as sources of unnecessary bureaucratic red tape. (Source: KeyedIn, 2014)

    50% — Fifty percent of PMOs close within the first three years due to such things as poorly defined mandates and poor leadership. (Source: KeyedIn, 2014)

    Info-Tech’s approach

    Prepare an Actionable Roadmap for Your PMO

    The Info-Tech difference:

    1. Get a departmental job description first. Defining your PMO may not be as simple as it seems. Explore the boundaries of portfolio, project, resource, and organizational change management before jumping ahead with processes and tools.
    2. The staffing plan should come before your long-term plan. Get buy-in around your definition of the roles needed to run your PMO before articulating a long-term plan. Too often, plans have been accepted without the commensurate level of staffing. Our approach gives you a chance to put hiring on the roadmap as a predecessor to accountability.
    3. Keep your eye on the ball. Build your PMO around the operational imperative to recognize completed projects as an early milestone in broader changes. In other words, projects exist to create change.

    Prepare an Actionable Roadmap for your PMO

    Turn planning into action with a realistic PMO timeline.

    50% of PMOs close within the first 3 years.

    Logo for Info-Tech.


    Logo for ITRG.

    01 Define

    DEFINE THE RIGHT KIND OF PMO

    Establish the purpose of your PMO. Identify organizational needs to fill in gaps instead of duplicating efforts.

    LOGICAL FALLACY
    “If we approve more work, we'll get more done.”

    A properly run portfolio reconciles demand (project requests) to supply (available people) and drives throughput by approving the amount of projects that can get done.

    02 Staff

    STAFF THE PMO FOR RESILIENCE

    Analyze the staffing requirements for your PMOs mandate. Create purpose-built role descriptions.

    FALSE ASSUMPTION
    “Our best project manager should run the PMO.”

    Your best project manager should be running projects and, no, they shouldn't do both.

    03 Plan

    PREPARE AN ACTIONABLE ROADMAP

    The difference in a winning PMO is determined by a roadmap or plan created at the beginning. Leaders should understand the full scope of the plan before committing their teams to the project.

    COMMON MISTAKE
    “We'll get great at project management now and worry about portfolio management later.”

    Too often, PMOs focus on project management rigor and plan to do portfolio management after that's done. But few successfully maintain the process long enough to get there. If you start with portfolio management, leadership might soften their demands for project management rigor.

    04 Execute

    ALIGN TO STRATEGIC PLAN

    Use the power of organizational change management to ensure success and adoption. Iterate through the finer points of planning and execution to deploy the kind of PMO defined in step 1, with the people described in step 2, and the strategic roadmap articulated in step 3.

    PROJECT MYOPIA
    “Let's focus on delivering the project on time so we can move on to our next project.”

    Don't forget why the idea got approved in the first place. The goal is to sustain beneficial business outcomes well beyond the completion of your project.

    Info-Tech’s methodology for Preparing an Actionable Roadmap for Your PMO

    1. Define the PMO 2. Staff the PMO 3. Prepare a Roadmap
    Phase Steps
    1. Get a Common Understanding of Your PMO Options
    2. Determine Where You Are and Engage Leadership
    1. Identify Organizational Design
    2. Build Job Descriptions
    1. Create Roadmap
    2. Governance and OCM
    Phase Outcomes A clear vision for your PMO and an articulated reason for establishing it.
    An understanding of your PMO goals and which challenges it sets to address.
    An analysis of staffing requirements of your PMO that aligns with your mandate from phase 1. Job descriptions help to fill the necessary roles. An actionable roadmap that can be presented to leadership and implemented. An introduction to the concept of governance and tools for a change impact analysis.

    Insight summary

    Overarching insight

    There is a gap in the perception of the actual role of the PMO in many organizations by different stakeholder groups. Many people see the PMO police that produce red tape rather than a helpful support system. Those that need to present a coherent plan to leadership championing the need for a PMO often have an uphill battle.

    Phase 1 insight

    Determine the PMO’s role and needs and then determine your staff needs based on that PMO.

    PMO leaders are all too often set up to fail, left to make successes out of PMOs that:

    1. have poorly defined mandates;
    2. lack the proper resourcing to support the services the organization requires; or
    3. lack executive leadership, vision, and backing.

    Phase 2 insight

    Staff the PMO according to its actual role and needs. Don’t rush to the assumption that PMO staff starts with accomplished project managers.

    Many organizations have PMOs of one person, and it is simply not a long-term recipe for success. People in this situation have a lot of weight on their shoulders and feel like they are being set up to fail. It is very challenging for anyone to run a PMO alone without support or administrative help.

    Phase 3 insight

    The difference in a winning PMO is determined by a roadmap or plan created at the beginning.

    When you are determining what your PMO will provide in the future, it is important to align the ambition of the PMO with the maturity of the business. Too often, a lot of effort is spent trying to convince businesses of the value of a PMO.

    Blueprint deliverables

    Each step of this blueprint is accompanied by supporting deliverables to help you accomplish your goals:

    PMO Role Definition Tool Sample of the PMO Role Definition Tool deliverable. PMO Project Charter Template Sample of the PMO Project Charter Template deliverable.
    Blank Job Description Template
    Sample of the Blank Job Description Template deliverable.
    Sample Job Descriptions
    Sample of the Sample Job Descriptions deliverable.
    PMO Job Description Builder Workbook
    Sample of the PMO Job Description Builder Workbook deliverable.

    Blueprint deliverables

    Each step of this blueprint is accompanied by supporting deliverables to help you accomplish your goals:

    PMO Strategic Plan
    Sample of the PMO Strategic Plan deliverable.
    PMO MS Project Plan Sample
    Sample of the PMO MS Project Plan Sample deliverable.
    Organizational Change Impact Analysis Tool
    Sample of the Organizational Change Impact Analysis Tool deliverable.

    Benefits

    IT Benefits

    • Determine how you can fill gaps and not duplicate efforts to bring value to your organization.
    • Ensure that key PMO capabilities like portfolio management, project management, and organizational change management are in balance.
    • Staffing is purpose-driven. Avoid putting good people in the wrong role.

    Business Benefits

    • Intake and governance have a primary focus and are not merely afterthoughts of someone primarily focused on project management methodology.
    • Avoid unrealistic commitments by ensuring better upfront analysis of ability to execute.
    • Ensure appropriately mandated sponsor management.

    Info-Tech offers various levels of support to best suit your needs

    DIY Toolkit

    Guided Implementation

    Workshop

    Consulting

    "Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful." "Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track." "We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place." "Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project."

    Diagnostics and consistent frameworks used throughout all four options

    Guided Implementation

    A Guided Implementation (GI) is a series of calls with an Info-Tech analyst to help implement our best practices in your organization.

    A typical GI is 8 to 12 calls over the course of 4 to 6 months.

    What does a typical GI on this topic look like?

      Phase 1

    • Call #1: Scope requirements, objectives, and your specific challenges.
    • Call #2: Assess current state and determine PMO role/type.
    • Call #3: Complete job description survey.
    • Phase 2

    • Call #4: Analyze survey results and complete FTE analysis.
    • Call #5: Discuss necessary roles and create job descriptions.
    • Phase 3

    • Call #6: Discuss business goals and priorities.
    • Call #7: Identify and prioritize initiatives on roadmap.
    • Call #8: Discuss governance and organizational change.
    • Call #9: Summarize results in strategic plan and discuss next steps.

    Workshop Overview

    Contact your account representative for more information.
    workshops@infotech.com1-888-670-8889

    Day 1 Day 2 Day 3 Day 4 Day 5
    Activities
    Define

    1.1 Review PPM Current State Scorecard Results

    1.2 Get a Common Understanding of Your PMO Options

    1.3 Conduct SWOT Analysis

    1.4 Current State and Leadership Engagement

    1.5 PMO Mandate and Vision

    Staff

    2.1 Identify Organizational Design

    2.2 Right, Wrong, Missing, Confusing

    2.3 PMO Function, Roles, and Responsibilities

    2.4 Job Descriptions

    Plan

    3.1 Roadmap Top-Level Hierarchy

    3.2 Roadmap Second-Level Hierarchy

    3.2 Staffing and Sizing

    3.3 Reconcile and Finalize Roadmap

    3.4 Governance and Authority

    Change

    4.1 Importance of OCM

    4.2 Sponsorship

    4.3 Analyze the Impact of the Change Across Multiple Dimensions and Stakeholder Groups

    Next Steps and Wrap-Up (offsite)

    5.1 Complete in-progress deliverables from previous four days.

    5.2 Set up review time for workshop deliverables and to discuss next steps.

    Deliverables
    1. PPM Current State Scorecard
    2. SWOT Results
    3. PMO Role Development Tool
    4. PMO Charter
    1. Right, Wrong, Missing, Confusing Results
    2. Job Description Survey Tool
    3. Job Description Templates
    1. PMO Roadmap Draft
    2. Governance and Authority Activity
    1. Organizational Change Impact Analysis Tool
    2. Sponsor Template
    1. Completed PMO Roadmap draft
    2. PMO Strategic Plan draft

    Prepare an Actionable Roadmap for Your PMO

    Phase 1

    Define the Right Kind of PMO

    Phase 1

    • 1.1 Get a Common Understanding of Your PMO Options
    • 1.2 Determine Where You Are and Engage Your Leadership

    Phase 2

    • 2.1 Identify Organizational Design
    • 2.2. Build Job Descriptions

    Phase 3

    • 3.1 Create Roadmap
    • 3.2 Governance and OCM

    A PMO may not simply be an office of project managers

    Project management offices are evolving and taking on activities that differ from company to company.

    1915 1930s 1950s 1980s 1990s
    Frederick Taylor introduces the PMO with the implementation of the scientific management method and the increase in the number and complexity of projects. The US Air Corps creates a Project Office function to monitor aircraft development (probably the first record of the term being used). The US military starts developing complex missile systems. Each weapon system was composed of several sub-projects grouped together in system program offices (SPOs). This built the structures underlying the traditional PMO. The Project Office concept exported to construction and IT. The PMO gains a lot of momentum with professional associations and project management certifications becoming recognized industry standards.

    Organizations are confused about what a PMO is, whether they should have one, and what it should do

    PMBOK

    The responsibilities of a PMO can range from providing project management support functions to the direct management of one or more projects. The PMO is an organizational body assigned with various responsibilities related to the centralized and coordinated management of those projects under its domain.

    The PMO may play a role in supporting strategic alignment and delivering organizational value, integrating data and information for organizational strategic projects, and evaluating how higher-level strategic objectives are being fulfilled.

    COBIT

    The PMO can be responsible for portfolio maintenance, setting a standard approach for project and program and portfolio management.

    OPM

    The PMO is an organizational body assigned with various responsibilities related to the centralized and coordinated management of those projects under its domain.

    In an effort to set a standard, the governance frameworks have over complicated it for most of us.

    Use Info-Tech’s framework to create the PMO that works for your organization

    Determine the Services Your PMO Will Provide
    Manage your PMO services in alignment with your mandate and your organization’s needs.

    Establish Your PMO’s Mandate
    Figure out the purpose of your PMO and write it down so it’s clear to your leadership. Align your mandate to the organization’s needs.

    Ensure Organizational Needs Are Being Met
    Before you can decide on what your PMO will do, find out who’s doing what in your organization so you can fill gaps instead of duplicating efforts.

    Hierarchy of PMO Needs
    Hierarchy of PMO needs with 'Organizational Needs' as the base, 'PMO Mandate' in the middle, and 'PMO Services' at the top.

    Info-Tech Insight

    Consider the principles of Maslow’s Hierarchy of Needs, which view the lower tiers of the hierarchy as fundamentally required to validate the pursuit of the higher tiers.

    Step 1.1

    Get a Common Understanding of Your PMO Options

    Activities
    • 1.1.1 Review PMO Types
    • 1.1.2 SWOT Analysis

    This step will walk you through the following activities:

    • Review Info-Tech’s PMO Types
    • Complete a Strengths, Weaknesses, Opportunities, and Threats Analysis

    This step involves the following participants:

    • PMO director and/or portfolio manager
    • PMO staff/stakeholders
    • Project managers

    Outcomes of this step

    • Current state analysis
    Define the Right Kind of PMO
    Step 1.1 Step 1.2

    People mistake the PMO as only an office with project managers

    It sounded simple enough, but no one could really explain what it meant.

    PMOs are often born out of necessity or desperation. A traumatic event happens, and leadership decides that it wouldn’t have happened had there been a “Project Management Office.” The phrase itself is often quite reassuring and offers the hope of some sort of sanity and order.

    People may not really be able to explain what a PMO is, but they do have a common understanding that it should solve all project management issues. But simply prescribing the “PMO” as a remedy for every organizational alignment is not going to be sufficient. There are different types of PMOs and more importantly there are different types of organizations.

    Screenshot of a Google search for 'what is a project management office'.
    Google and the Google logo are trademarks of Google LLC.

    The PMI has described what a PMO could be

    The PMI does not have a standard for PMOs like it does for things like project, program, and portfolio management. Its PMO definitions should be used as more of a reference point than a best practice.

    But what should it do?

    • Supportive: Provides a consultative role to projects by supplying templates, best practices, training, access to information, and lessons learned from previous projects.
    • Controlling: Provides support and requires compliance through various means.
    • Directive: Takes control of the projects by directly executing them.

    The PMI described three types of PMOs. These three types are well known in the industry, but they are essentially characteristics and do little to help people understand the functions and services of a PMO. There continue to be questions about the role a PMO should play in an organization and how it’s supposed to add value.

    Stock photo of two sticky notes reading 'project' and 'management'.

    Thousands of practitioners came together at the 2012 PMI Symposium and expanded upon PMBOK’s PMO types

    1. Managing
      Manages the work in projects and programs.
    2. Consulting
      Serves as an experience-based consultative body to project managers.
    3. Project Repository
      Repository of previous project documentation, lessons learned, etc.
    4. Enterprise PMO
      Provides PMO services to the organization.
    5. Center of Excellence
      Creates the standard and methodologies and provides tools.
    6. Managerial
      Manages the project and program managers, and eventually, other project resources.
    7. Delivery
      Manages the project and programs.

    1.1.1 Leverage Info-Tech’s PMO types to anchor yourself

    We have narrowed it down to five types of PMOs.

    ePMO
    Icon for ePMO.
    IT PMO
    Icon for IT PMO.
    PMO
    Icon for PMO.
    CMO
    Icon for CMO.
    CoE
    Icon for CoE.
    Enterprise
    Highest level PMO, typically responsible to align project and program work to strategy-significant projects or programs for the entire organization. Could include both IT and business units.
    IT
    IT PMOs provide project-related support for IT project portfolios. For many organizations PMOs originate in IT departments because of the structure required for technology-related projects.
    Project/Program
    Provides project-related tactical service as an entity to support a specific project or program. Can be dismantled when program is done.
    Change
    Change management offices (CMO) help build change management capabilities and enable change readiness in organizations.
    Excellence
    These centers differ in size and mode of organization, depending on their subject and scope. They support project work by providing the organizations with standard methodologies and tools.

    What is your definition of a PMO?

    Use this model to clearly show what is in and out of scope.

    ePMO IT PMO PMO CMO CoE
    PPM Reporting for enterprise portfolio and the financial/human resources needed to deliver them X
    PPM Finance for project/portfolio capital and expense X X
    PPM Customer Management – the customers, sponsors of the project X X
    PPM Strategy Management – projects and programs relate to corporate X X X
    PPM Program Management – related projects in the portfolio X X X
    PPM Time Accounting X X x
    PPM Business Relationship Management (BRM) X X
    PPM Project Information System (PMIS) – organization of project information X X
    PPM Administrative Support – general assistance with Portfolio X
    PPM Record Keeping – Enterprise Information X X
    RM Forecasting X
    PM Quality Assurance X X
    PM Procurement and Vendor Management X X X
    PM Project Status Reporting X X
    PM PM Services X X X
    PM Training X
    PM PM SOP X
    OCM Adoption X X
    OCM Change Management X X
    OCM Benefits Attainment X X
    OCM Forecast Benefits X X
    OCM Track Benefits X X
    GOV Intake X
    GOV Governance X X
    GOV Reporting X X X X

    Use Info-Tech’s PMO function matrix to help provide role definitions for your PMO

    Info-Tech’s potential PMO capabilities are in the header of the table below. These are the services a PMO may (or may not) provide depending on the needs of the organization.

    Portfolio Management Resource Management Project Management Organizational Change Management PMO Governance
    Recordkeeping and bookkeeping Strategy management Assessment of available supply of people and their time Project status reporting PM SOP
    (e.g. feed the portfolio, project planning, task managing)
    Benefits management Technology and infrastructure
    Reporting Financial management HR Security
    PMIS Intake Matching supply to demand based on time, cost, scope, and skill set requirements Procurement and vendor management Legal Financial
    CRM/RM/BRM Program management
    Tracking of utilization based on the allocations Quality Intake
    Time Accounting PM services
    (e.g. staffing project managers or coordinators)
    Quality assurance Organizational change management Project progress, visibility, and process
    Forecasting of utilization via supply-demand reconciliation Closure and lessons learned
    Administrative support PM Training

    The rest of this blueprint will help you choose the right capabilities and accompanying job functions for your PMO.

    Various options for specific PMO job functions are listed below each capability. PMO leaders need to decide which of these functions are required for their organization.

    1.1.2 SWOT analysis

    45-60 minutes

    Input: Current PMO governance documents and SOPs

    Output: An assessment of current strengths, opportunities, threats, and weaknesses of capabilities in previous slide

    Materials: Whiteboard/flip charts, Sticky notes

    Participants: PMO director and/or portfolio manager, PMO staff/stakeholders, Project managers

    Perform a SWOT analysis to assess the current state of PMO capabilities covered on the previous slide.

    The purpose of the SWOT is to begin to define the goals of this implementation by assessing your project management, portfolio management, resource management, organizational change management, and governance capabilities and cultivating alignment around the most critical opportunities and challenges.

    Follow these steps to complete the SWOT analysis:

    1. Have participants discuss and identify strengths, weaknesses, opportunities, and threats.
    2. Spend roughly 60 minutes on this. Use a whiteboard, flip chart, or PowerPoint slide to document results of the discussion as points are made.
    3. Make sure results are recorded and saved either using the template provided in the next slide or by taking a picture of the whiteboard or flip chart.

    1.1.2 Sample SWOT analysis

    Strengths

    • Knowledge, skills, and talent of project staff.
    • We have fairly effective project management processes.
    • Motivation to get things done when priorities, goals, and action plans are clear.

    Weaknesses

    • IT-business communication and alignment.
    • No standards are currently in place across departments. Staff are unsure which templates to use and how/when/why to use them.
    • There are no formal intake structures in place. Projects are approved and it’s up to us to “figure it out.”
    • We have no prioritization practices to keep up with constantly changing priorities and shifts in the marketplace.

    Opportunities

    • Establish portfolio discipline to improve IT-business communication through more effective and efficient project coordination.
    • Stronger initiation processes should translate to smoother project execution.
    • Establish more disciplined and efficient weekly/monthly project reporting practices that should facilitate more effective communication with senior leaders.

    Threats

    • Risk of introducing burdensome processes and documentation that takes more time away from getting things done.
    • We tried to formalize a PMO in the past and it failed after eight months.
    • We have no insight into project resourcing.

    Step 1.2

    Determine Where You Are and Engage Your Leadership

    Activities
    • 1.2.1 Assess Current State
    • 1.2.2 Gap Analysis
    • 1.2.3 Vision Exercise
    • 1.2.4 PMO Charter
    • 1.2.5 Strategic Planning

    This step will walk you through the following activities:

    • Assess the current state of your PPM/PM services using the PMO Role Definition Tool
    • Determine current gaps in your services and processes using the PMO Role Definition Tool
    • Discuss the vison for your PMO
    • Start creating your PMO charter

    This step involves the following participants:

    • PMO director and/or portfolio manager
    • PMO staff/stakeholders
    • Project managers

    Outcomes of this step

    • Results of PMO Role Definition Tool
    • PMO vision
    • PMO charter

    Define the Right Kind of PMO

    Step 1.1 Step 1.2

    Why do organizations need a PMO?

    Stock image of a man thinking.

    “If a company is not a project-oriented organization, there’s less of a need for a PMO. If they are project-focused though, they should have one. Otherwise, who’s driving the delivery of their projects? Who’s establishing their methodology? How are they managing resources efficiently?” (Mary Hubbard, PMP, director of the PMO at Siemens Government Technologies Inc., A PMI Global Executive Council Member)

    Signs you might need a PMO:

    • A lack of project transparency.
    • Significant discrepancies in project results.
    • Poor customer satisfaction rates.
    • An inability to cost projects accurately.
    • A high percentage of delayed or cancelled projects.
    • High project failure rates.
    • Poor alignment of project activity and business strategy investments.
    • Inconsistent project management processes and methodologies.
    • A lack of collaboration and knowledge sharing.
    • Little to no resource training to meet IT and business needs.
    • A lack of resource management for utilization and capacity.
    • Little to no visibility into project, program, and portfolio-level status.

    Why does your organization need a PMO?

    Observe the needs of your organization before deciding on services to support it.
    • Observe what is and what is not in place. Look for existing processes, tools, and systems and evidence that they are being followed. You might already have some pieces in place; the question becomes what to keep and what not to keep.
    • What does your organization look like?
      • Name
      • Population
      • Current Project Lifecycle
      • IT Services Team
      • # of Unique Applications
      • Annual Budget
    • Gather a list of potential areas for improvement where a PMO can add value. Once a list is established, convert it to a prioritized queue of initiatives. A key item on your list should be how projects go from beginning to end so you can understand the potential issues and opportunities with your current project delivery.
    Stock image of a hierarchy mapped out over a birds eye view of people.

    Ideally, we wouldn’t invest in project, portfolio, or OCM because they’re overhead processes without any direct value…

    …but you need to spend just enough to demonstrate you are a diligent steward of the assets under your administration.

    Organizational Change Management

    • Well-run projects can fail without OCM.
    • More than anyone else, it’s up to the sponsor to pursue outcomes.

    Project Management

    • Determine the current project management standards and methodologies.
    • Uncover any forms and templates that are currently in use.
    • If there is a lack of project management knowledge among current or future staff, you will need to do some training.

    Portfolio Management

    • Who currently approves projects and who will be approving them in the future?
    • Who is accountable for approving too many projects?
    • What roles does resource capacity play? Is it constrained or do you approve everything?
    • Are the resources in your PMO full-time?
    • How big is your portfolio?
    • How much do you spend on resources (hours or months)?

    Governance

    • Governance can mean many different things: intake, finance, over-sight of existing projects, resource management, technology and architecture, and process.
    • Don’t try to introduce governance without considering the people who may already be governing different areas.
    • Consider what things can be done without getting executive approval.

    Define your PMO’s role in the organization

    Use Info-Tech’s PMO Role Definition Tool to help establish your PMO’s future state.

    • Use Info-Tech’s PMO Role Definition Tool to figure out the functions your PMO should provide.
    • The current-state analysis uses specific questions to assess how you are doing things now and provide you with some situational awareness.
    • The gap analysis uses another set of specific questions to uncover the holes in your organization and the services that are not being provided.
    • Based on the answers you gave to the questions, the tool will populate the functions that your PMO should provide to your organization: the services your organization needs.
    • Use the outputs to start looking into missing functions and ultimately start building or re-establishing the responsibilities of your PMO.
    • Consider having multiple team members answer all the questions to establish alignment and get realistic data.

    Sample of the PMO Role Definition Tool.

    Download the PMO Role Definition Tool

    Hey, you don’t to have to spend anything on portfolio, project, and organizational change management! Assuming of course…

    • You have enough people to do all your projects
    • All projects are getting done on time
    • Your customers and employees are happy
    • You have complete visibility into the portfolio
    • Your projects align with your corporate strategy
    • Your projects align with your operational needs
    • Your strategic and operational needs are in harmony
    • You have the right skills
    • You are using all resources provided to you
    • People self-identify the right work and independently do that work
    • Time is not wasted
    • The work is production-ready (i.e. high quality)
    • Vendors honor their commitments
    • The sponsor is confident they’re getting what was committed
    • You have sufficient reports for the portfolio
    • Stakeholders make it through transitions with minimal resistance
    • The organization is prepared to adopt the outcomes of projects
    • The sponsors’ forecasted benefits are realized
    • Stakeholders are aware of the need for change
    • Stakeholders transition well from current to future state

    Use the tool on the next slide to see where you may need to spend.

    1.2.1 Assess the current state of your project environment

    20-30 minutes

    Input: Understanding of current project portfolio environment

    Output: Completed current state survey

    Materials: Tab 1 of Info-Tech’s PMO Role Definition Tool

    Participants: PMO director and/or portfolio manager, PMO staff/stakeholders, Project managers

    Screenshot from tab 1 of Info-Tech’s PMO Role Definition Tool.

    Screenshot from tab 1 of Info-Tech’s PMO Role Definition Tool. There are three columns: '#', 'Question', and 'Answer'.

    There are 20 current-state questions in column C. Together, the questions address the five capabilities in Info-Tech’s PMO function matrix (slide 28).

    Use the drop-down menu in column D to answer Agree, Somewhat Agree, Neutral, Somewhat Disagree, or Disagree to each question in column C.

    The questions are broad by design. Answer them honestly and select “neutral” if anything is not applicable.

    1.2.2 Set your target state needs to identify gaps

    15-30 minutes

    Input: Reflection on the question, “If I/We do nothing, someone in the organization is…”

    Output: Completed target state survey

    Materials: Tab 2 of Info-Tech’s PMO Role Definition Tool

    Participants: PMO director and/or portfolio manager, PMO staff/stakeholders, Project managers

    Screenshot from tab 2 of Info-Tech’s PMO Role Definition Tool.

    Screenshot from tab 2 of Info-Tech’s PMO Role Definition Tool. There are four columns: '#', 'Question', 'Answer', and 'Department'.

    Each question in column C of tab 2 should be answered in the context of, “If I do nothing, someone in the organization is…”

    Answer each question by using the drop-down menu in column D to select “Yes,” “No,” “I don’t know,” or “N/A.”

    If “Yes” include the department or area that is responsible.

    Hierarchy of PMO needs with 'Organizational Needs' highlighted. 'Organizational Needs' at the base, 'PMO Mandate' in the middle, and 'PMO Services' at the top.

    Review the preliminary list of your potential PMO functions

    Tab 3 of the PMO Role Definition Tool contains a customized version of Info-Tech’s PMO definition matrix, based upon your inputs in the previous two tabs.

    Screenshot from tab 3 of Info-Tech’s PMO Role Definition Tool. It is titled 'PMO Functions and Groups' and contains a table with five columns: 'Portfolio Management', 'Resource Management', 'Project Management', 'Organizational Change Management', and 'Governance'. Each column contains high level recommendations, and at the bottom of the columns are outputs.

    The name of the box is the group the function belongs to.

    These outputs are based on the answers to the questions on the previous 2 tabs.

    In each group’s box are high-level recommendations.

    Consider your stakeholders

    Who benefits from the new or updated PMO structure?

    In a matrix environment, understanding the challenges other teams are facing is a core requirement of an effective PMO. The best way to understand this is through direct engagement like conducting interviews and taking surveys with management and members of other teams.

    Ask yourself these questions about your PMO:

    • Are we doing the right things?
    • Do we know the current status of projects?
    • Are we managing, escalating, and resolving project issues?
    • Do PMs have the right training?
    • What is our overall utilization?

    A PMO should be structured to provide service to the organization. View it as a business, serving the stakeholders.

    1.2.3 Complete this vision exercise to produce an initial mandate for a new/improved PMO

    45-60 minutes

    Input: Outputs from SWOT analysis

    Output: An initial PMO mandate

    Materials: Whiteboard/flip charts, Sticky notes

    Participants: PMO director and/or portfolio manager, PMO staff/stakeholders, Project managers

    Now that you have an idea of the services your organization needs from steps 1.1 and 1.2 of this blueprint, you can discuss the target state of your PMO.

    Follow these steps to complete the SWOT analysis:

    1. Each person writes one aspect of a future state that would solve the issues described in the SWOT analysis (activity 1.1.1). Use sticky notes and post them on the whiteboard.
    2. As a group, identify which of these aspects would be good candidates for embodying the “core element” of your PMO’s new mandate.
    3. From the aspects gathered, have everyone individually come up with a statement of one to two sentences they think captures the overall theme and vision of this PMO.
    4. Collectively choose the best statement to use as the working mandate for your new project management office. This mandate can be modified as needed in the time leading up the creation and launch of your PMO.

    Hierarchy of PMO needs with 'PMO Mandate' highlighted. 'Organizational Needs' at the base, 'PMO Mandate' in the middle, and 'PMO Services' at the top.

    1.2.4 Use Info-Tech’s PMO Project Charter template to help capture your mandate and obtain approval

    3-4 hours

    Input: Activity 1.2.3, Logical considerations for PMO deployment (see bulleted list on this slide)

    Output: An assessment of current strengths, opportunities, threats, and weaknesses of capabilities in previous slide

    Materials: Whiteboard/flip charts, Sticky notes

    Participants: PMO director and/or portfolio manager, PMO staff/stakeholders, Project managers

    A successful PMO will offer a range of services which business units can rely on. The aim of the PMO charter is to outline what is in scope for the PMO and what services it will initially offer.

    A project charter serves several important functions. It organizes the project so you can make efficient and effective resource allocation decisions. It also communicates important details about the project purpose, scope definition, and project parameters.

    To use this template, simply modify or delete all information in grey text and convert the remaining text to black before printing or sending. Sections within the Template include:

    1. PMO Mandate
    2. Goals & Benefits
    3. Scope Definition
    4. Key PMO Stakeholders
    5. Projected Timeline for Implementation
    6. Project Roles and Responsibilities
    7. High-Level Budget
    8. High-Level Risk Assessment

    Sample of the PMO Project Charter Template.

    Download the PMO Project Charter Template

    Engage leadership to refine target-state expectations

    Stock image of a person with a megaphone. ?
    Will project managers be included in the PMO? Which projects and programs will be in the PMO’s mandate?
    ?
    Will the PMO have decision-making authority? If so, how much and on what issues?
    ?
    Where in the organizational structure will the PMO report?

    “Changing the perception of project management from ‘busy work’ to ‘valued efforts’ is easier when the PMO is properly aligned.” (Project Management Institute, October 2009)

    Don’t assume your PMO is merely tactical

    It can help drive strategy instead of just being a technical arm.

    Strategic

    Stock image of a business person.

    Tactical

    Strategic Alignment
    Leadership assumes that your presence will optimize the alignment of projects to corporate strategy.
    Process Adherence
    Leadership assumes you’re all about process.
    Portfolio Thinking
    Leadership assumes that you’re thinking about the overall throughput of projects through the portfolio.
    Project Thinking
    Leadership assumes you’re not thinking beyond the boundaries of a single project at any given time.
    Outcomes Focused
    Leadership assumes that you’re focused on the outcomes forecast by sponsors.
    Timeline Focused
    Leadership assumes you’re focused on delivering projects on time.

    Info-Tech Insight

    A key success factor for a PMO is to take part of strategic conversations; when they are left out, it creates a barrier. The PMO is the connective tissue between strategy and tactics. Don’t risk your benefits by not having the PMO Director at the table before you make decisions.

    Avoid the disconnect

    Create a strategic plan with project professionals at the table.

    • Strategic plans should guide organizations to future states, yet many don’t ever get used. This is because there is a disconnect between the people creating the strategic plan and the people being asked to implement it. Strategic planners don’t often develop their plans with the help of project managers who can ensure the plan is transferred into a working operational plan.
    • Strategic planners are broad thinkers with high-level plans whereas project professionals often work in the trenches. The disconnect between the two can often result in cost overruns, delays in implementation, low worker morale, and an overall chaotic work environment.
    • By putting strategic planners and project managers together to work on the strategic planning process, they can see what the other sees and plan accordingly.
    • Twenty-seven percent more projects are executed successfully when a company’s structure and resources align with their strategy (KPMG, 2017).

    “The failure to build a bridge between the strategic planning process and project management’s planning process is a major reason strategic plans don’t work.” (Bruce McGraw, Project/Programme Manager)

    1.2.5 Strategic planning

    1 hour

    To create a strategic plan that provides value, recognize that the strategic plan for the PMO is not the PMO charter.

    • The PMO charter is the organizational mandate for the PMO. It defines the role, purpose and functions of the PMO. It articulates who the PMO's sponsors and customers are, the services that it offers, and the staffing and support structures required to deliver those services. And, it assumes that a decision to have a PMO has already been made.
    • A strategic plan enables the PMO to play an essential role in achieving a company’s business goals, setting out clear objectives and then providing a roadmap on how to achieve them. A strategic plan maps the tools and resources necessary to achieve successful project outcomes.

    To create a results-driven strategic plan for your PMO, it is helpful to follow a top-down format:

    • Start by going through the list on the right and update the strategic plan.
    • What are the top project-related issues and opportunities you want your PMO to address and what’s the value to the business of trusting them?

    Vision: this needs to be a vivid and common image
    Mission: this is the special assignment that is given to a group
    Goals: these are broad statements of future conditions
    Objectives: these are operational statements that indicate how much and by when (e.g. deliverables or intangible objectives like productivity)
    Strategies: these are the set of actions that need to take place
    Needs: these are the things required to carry out the strategy
    Critical Success Factors: these are the key areas of activity in which favorable results are necessary to reach the goal

    Download the PMO Strategic Plan

    Prepare an Actionable Roadmap for Your PMO

    Phase 2

    Staff Your PMO for Resilience

    Phase 1

    • 1.1 Get a Common Understanding of Your PMO Options
    • 1.2 Determine Where You Are and Engage Your Leadership

    Phase 2

    • 2.1 Identify Organizational Design
    • 2.2. Build Job Descriptions

    Phase 3

    • 3.1 Create Roadmap
    • 3.2 Governance and OCM

    Info-Tech’s approach

    Follow our two-step approach to successfully staff your PMO.

    1. Determine your PMO staffing needs.
      Our approach to building a PMO starts by analyzing the staffing requirements of your PMO mandate.
    2. Create purpose-built role descriptions.
      Once you have an understanding of the staff and skills you’ll need to succeed, we have job description aids you’ll need to fill the roles.

    The Info-Tech difference:

    1. Save time developing a purpose-built approach. There is no one-size-fits-all approach to PMO staffing. The advice and tools in this research will help you quickly determine your unique staffing needs and guide your next steps to get the staffing you need.
    2. Leverage insider research. We’ve worked with thousands of PMOs and have seen the good, the bad, and the ugly of PMO staffing. The approach in this research is informed by client successes and will help you avoid the common mistakes that drive PMO failure.

    IT staff allocation for project work

    Projects and Project Portfolio Management

    58.3% — 58% of respondents feel they have the appropriate staffing level to execute project management effectively. (Source: Info-Tech IT Staffing Benchmark Report)

    59.8% — 59% feel they have the appropriate staffing level to execute requirements gathering effectively. (Source: Info-Tech IT Staffing Benchmark Report)

    The GDP contributions from project-oriented industries are forecasted to reach $20.2 trillion over the next 20 years. (Source: “Project Management: Job Growth and Talent Gap” Project Management Institute, 2017)

    Info-Tech Insight

    Project work is only going to increase, and in general, people are dissatisfied with their current staffing levels.

    Step 2.1

    Identify Organizational Design

    Activities
    • 2.1.1 Right, Wrong, Missing, Confusing
    • 2.1.2 Map Your Current Structure
    • 2.1.3 Inventory Assessment
    • 2.1.4 Job Description Survey

    This step will walk you through the following activities:

    • Complete a Right, Wrong, Missing, Confusing analysis
    • Determine your current organizational/PMO structure
    • Assess your current inventory
    • Complete the job description survey

    This step involves the following participants:

    • PMO director and/or portfolio manager
    • PMO staff/stakeholders
    • Project managers

    Outcomes of this step

    • Current-state analysis
    • Job description survey results

    Staff Your PMO for Resilience

    Step 2.1 Step 2.2

    2.1.1 Right, wrong, missing, confusing

    30-45 minutes

    Input: Current PMO process, Current PMO org. chart

    Output: An assessment of current things that are being done right and wrong and what is currently missing and confusing

    Materials: Whiteboard/flip charts, Sticky notes

    Participants: PMO director and/or portfolio manager, PMO staff, Project managers

    Perform a right, wrong, missing, confusing analysis to assess the current state of your PMO and its staff.

    The purpose of this exercise is to begin to define the goals of this implementation by assessing your staffing capabilities and cultivating alignment around the most critical opportunities and challenges.

    Follow these steps to complete the analysis:

    1. Have participants discuss what is wrong, right, missing, and confusing.
    2. Spend roughly 45 minutes on this. Use a whiteboard, flip chart, or PowerPoint slide to document results of the discussion as points are made.
    3. Make sure results are recorded and saved by taking a picture of the whiteboard or flip chart.

    Organizational types

    1. Functional
      Functional organizations are structured around the functions the organization needs to be performed.
    2. Projectized
      Projectized organizations are organized around projects for maximal project management effectiveness.
    3. Matrix
      Matrix organizations have structures that blend the characteristics of functional and projectized organizations.

    Functional organization

    The traditional hierarchical organizational structure.

    A functional hierarchical structure with 'Functional Managers' highlighted and the note 'Project coordination'. 'Chief Executive' at the top, 'Functional Managers' in the middle, and 'Staff' at the bottom.
    Adapted from ProjectEngineer, 2019
    1. Employees are organized by specialties like human resources, information technology, sales, marketing, administration, etc.
    2. The project management role will be performed by a team member of a functional area under the management of a functional manager.
    3. Resources for the project will need to be negotiated for with the functional managers, and the accessibility of those resources will be based on business conditions. Any escalations of issues would need to be taken to the functional manager.
    4. The project management role would act more like a project coordinator who does not usually carry the title of project manager.
    5. Project management is considered a part-time responsibility. Of all the organizational types, this one tends to be the most difficult for the project manager. The project manager lacks the authority to assign resources and must acquire people and other resources from multiple functional managers.
    6. Because the project manager has little to no authority, the project can take longer to complete than in other organizational structures, and there is generally no recognized project management methodology or best practices.

    Projectized organization

    The majority of project resources are involved in project work.

    A projectized hierarchical structure with a single project hierarchy highlighted and the note 'Project coordination'. 'Chief Executive' at the top, 'Project Managers' in the middle, and 'Staff' at the bottom.
    Adapted from ProjectEngineer, 2019
    1. The project manager has increased independence and authority and is a full-time member of a project organization. They have project resources available to them, such as project coordinators, project schedulers, business analysts, and plan administrators.
    2. The project manager is responsible to the sponsor and/or senior management. The project manager has authority and control of the budget, and any escalation of issues would be taken to the sponsor.
    3. Given that the project resources report to the project manager versus the functional area, there may be a decrease in the subject matter expertise of the team members.
    4. Team members are usually co-located within the same office or virtually co-located to maximize communication effectiveness.
    5. There can be some functional units within the organization; however, those units play a supportive role, without authority over the project manager.
    6. There is no defined hierarchy. Resources are brought together specifically for the purpose of a project. At the end of each project, resources are either reassigned to another project or returned to a resource pool.

    Matrix organization

    A combination of functional and projectized.

    A matrix hierarchical structure with the lowest row highlighted and the note 'Project coordination'. 'Chief Executive' at the top, 'Functional Managers' in the middle, mainly 'Staff' at the bottom, except one 'Project Manager' who coordinates across functions.
    Adapted from ProjectEngineer, 2019
    1. A matrix organization is a blended organizational structure. Although a functional hierarchy is still in place, the project manager is recognized as a valuable position and is given more authority to manage the project and assign resources.
    2. Matrix organizations can be classified as weak, balanced, or strong based on the relative authority of the functional manager and project manager. If the project manager is given more of a project coordinator role, then the organization is considered a weak matrix. If the project manager is given much more authority on resources and budget spending, the organization is considered a strong matrix.
    3. Matrix structures evolve in response to the rise of large-scale projects in contemporary organizations. These projects require efficient processing of large amounts of information.
    4. Working in a matrix organization is challenging and structurally complex. Employees have dual reporting relationships – generally to both a functional manager and a project and/or product manager. However, if done well, it offers the best of both worlds.
    5. The matrix organization structure usually exists in large and multi-project organizations. Here they can move employees whenever and wherever their services are needed. The matrix structure has the flexibility to transfer the organization’s talent by considering employees to be shared resources.

    The project management office

    The vast majority of PMOs are understaffed and underequipped.

    • They are often born out of necessity or desperation.
    • They have no long-terms goals; they tend to go from year to year trying to meet the organization’s needs.
    • They don’t have clear mandates, so it is difficult to determine how they are providing value.
    • Over time (and sometimes even from day one), project management offices find that other tasks fall into their area of responsibility. This often happens when the work has nowhere else to go.
    • Resource management is the challenge, both in terms of being able to allocate skilled resources to projects and within the PMO itself. Staffing gaps within the PMO are often met by individuals wearing more than one hat.

    A stock photo of a circle of chairs in a field being occupied by only two people.

    2.1.2 Map your current structure

    30 minutes to 1 hour

    Input: Current org. charts and PMO structures, Info-Tech’s PMO Function Matrix

    Output: Structure chart

    Materials: Whiteboard/flip charts

    Participants: PMO director and/or portfolio manager, PMO staff, Project managers

    1. As a group, review your current organizational and PMO structure.
    2. Map out both, or if your PMO is small, map out how it fits into the overall structure.
      • Make sure to think about your process, reporting structures, and escalation hierarchies.
      • Consider the capabilities on slide 59 as you work.
      • Use the sample structure on the next page as a guide.

    Stock image of a business hierarchy.

    Sample PMO structure

    Sample PMO structure with 'PMO Director' at the top. 'Portfolio Administrator' below, but not directly in charge of others. Then 'Program Manager', 'Change Manager', 'Resource Management Analyst', 'Business Relationship Manager', and 'Business Analyst' all report to the PMO Director. Below 'Program Manager' are two 'Project Managers' then 'Project Coordinator'. Stock photo of a hand placing a puzzle piece of a business person on it into a puzzle.

    Info-Tech’s PMO Function Matrix

    Info-Tech’s potential PMO capabilities are in the header of the table below.

    Portfolio Management Resource Management Project Management Organizational Change Management PMO Governance
    Recordkeeping and bookkeeping Strategy management Assessment of available supply of people and their time Project status reporting PM SOP
    (e.g. feed the portfolio, project planning, task managing)
    Benefits management Technology and infrastructure
    Reporting Financial management HR Security
    PMIS Intake Matching supply to demand based on time, cost, scope, and skill set requirements Procurement and vendor management Legal Financial
    CRM/RM/BRM Program management
    Tracking of utilization based on the allocations Quality Intake
    Time Accounting PM services
    (e.g. staffing project managers or coordinators)
    Quality assurance Organizational change management Project progress, visibility, and process
    Forecasting of utilization via supply-demand reconciliation Closure and lessons learned
    Administrative support PM Training

    2.1.3 Inventory assessment

    30-45 minutes

    Input: Understanding of your current situation regarding project intake and process

    Output: Survey results

    Materials: Whiteboard/flip charts

    Participants: PMO director and/or portfolio manager, PMO staff, Project managers

    When staffing your PMO, it is important to understand your current situation regarding project intake and process.

    Answer the following questions, and be as detailed as possible:

    • What is your project intake process?
    • How many projects do you currently have?
    • How many people lead projects?
    • Are those who lead projects distributed (federated) or centralized?
    • What tools do you use to manage your portfolio, projects, and resources?

    Stock image of a magnifying glass over an idea lightbulb surrounded by the six classic question words.

    2.1.4 Job description survey

    45 minutes to 1 hour

    Input: Tab 1 of the PMO Job Description Builder Workbook

    Output: List of current projects, processes, and tools

    Materials: PMO Job Description Builder Workbook

    Participants: PMO director and/or portfolio manager, PMO staff, Project managers

    On tab 1 of the PMO Job Description Builder Workbook, use the survey to help determine potential role requirements across various project portfolio management, project management, business analysis, and organizational change management activities.

    Follow these steps to complete the survey:

    1. Consider the role that you are trying to fill.
    2. Read each question carefully and use the drop-down menu to answer whether the activity in column C is a core, ancillary, or out-of-scope job duty.

    Download the PMO Job Description Builder Workbook

    2.1.4 Job description survey continued

    Sample of the Job Description Survey with questions and responses.

    Step 2.2

    Build Job Descriptions

    Activities
    • 2.2.1 Analyze Survey Results
    • 2.2.2 FTE Analysis
    • 2.2.3 Create Your Job Descriptions

    This step will walk you through the following activities:

    • Complete the PMO Job Description Builder Workbook
    • Create job descriptions

    This step involves the following participants:

    • PMO director and/or portfolio manager
    • PMO staff/stakeholders
    • Project managers

    Outcomes of this step

    • PMO org. chart
    • Completed job descriptions

    Staff Your PMO for Resilience

    Step 2.1 Step 2.2

    2.2.1 Analyze survey results

    30 minutes

    Tab 2 of the PMO Job Description Builder Workbook shows the survey results from tab 1.

    The job activities are ranked in a prioritized list. The analysis will help you determine if you require a portfolio manager, program manager, project manager, business analyst, organizational change manager, or a combination.

    Follow these steps to analyze your results:

    • Digest the prioritized ranking. The job activities are ranked in a prioritized list (from most essential to the role to least essential) in column D. The core process or capability that corresponds to each activity is listed in column C.
    • Use the drop-down menu in column F to decide if the core job duties and ancillary job duties will or will not be included in the role description. Out-of-scope activities will automatically be removed.

    Screenshot of the 'Job Description Survey Results' from the PMO Job Description Builder Workbook.

    Download the PMO Job Description Builder Workbook

    2.2.2 FTE analysis

    30 minutes

    Input: Tab 3 of the PMO Job Description Builder Workbook

    Output: Total estimated monthly time commitments, Preliminary FTE analysis

    Materials: PMO Job Description Builder Workbook

    Participants: PMO director and/or portfolio manager, PMO staff, Project managers

    Tab 3 of the PMO Job Description Builder Workbook is used to complete the FTE analysis.

    Download the PMO Job Description Builder Workbook

    2.2.2 FTE analysis continued

    Screenshot of the 'FTE analysis' on tab 3 of the PMO Job Description Builder Workbook. It has a table with columns for 'Rank', 'Process', 'Activity', and 'Est. Monthly Time Commitments (aka Column E)' with note 'Base these initial estimates on the number of projects and project teams, as well as the number of internal and external customers and stakeholders'. There is also a table of totals with a pie chart of the 'Distribution of Role Responsibilities'. The value for 'Total Estimated Monthly Timing Commitment' is in cell J5, and the note for the value of 'Preliminary FTE Analysis' is 'If your preliminary FTE analysis comes out to be more than 1 FTE, you may want to revisit your analysis on tabs 1 and 2 to further limit this role, or to further delineate it across multiple roles and FTEs'.

    On tab 3, use column E to estimate the monthly time commitments required for each activity in the role.

    Tip: Base estimates on the number of projects and project teams as well as the number of internal and external stakeholders across the portfolio(s) of projects and programs.

    Cell J5 will provide a preliminary recommended FTE count for the role.

    Job description content

    Screenshot of the 'Job Description Content' section of the PMO Job Description Builder Workbook.

    This is an output tab based on your analysis in tabs 1 and 2. Copy and paste the content and add it under the relevant heading in Info-Tech's Blank Job Description Template later in this blueprint.

    Screenshot of the 'Blank Job Description Template' section of the PMO Job Description Builder Workbook.

    For each capability you are including in your job description, there is a list of common certifications. These can also be copied and pasted into the Blank Job Description Template.

    Download the PMO Job Description Builder Workbook

    How to determine the roles in your PMO

    It’s not black and white.

    While your PMO should have someone to lead the team, aside from that it’s hard to be specific about the exact roles your PMO needs without understanding the needs of your organization.

    This is why it’s important to define your PMO first. Your team members should best support the function and capabilities of your PMO.

    For example:

    • If you want to provide a training program to project managers, you’ll need your PMO to have people with experience delivering training and with experience having done the job before.
    • If your PMO provides management information and deep portfolio analysis, you’ll need someone on the team who knows their way around data analysis tools.

    You should have a mix of skills in the PMO team, each complementing the others. You may have administrators and coordinators, data analysts and software experts, trainers, coaches, and senior managers.

    “If you want to go fast, go alone. If you want to go far, go together.” (African proverb)

    Managing projects and building PMOs are not the same thing

    Your best project manager should be running projects, and, no, they can’t do both.

    • Your new PMO needs a leader to get it off the ground, but don’t assume that the best project manager is best suited to build the PMO. The goal-oriented passion of a successful project manager may prove to be antithetical to the forward-looking finesse and political acumen needed to develop and staff the PMO as an organizational unit. Avoid the common mistake of promoting effective people into positions where they become ineffective, a concept often referred to as “The Peter Principle.”
    • You can’t determine if your best project manager fits the PMO leadership role if the PMO’s role isn’t clearly defined. Carefully define and clearly articulate the PMO’s role to understand the skill set needed to develop and lead your PMO.
    • Project managers often propose to create a PMO without considering the fit with project portfolio management and organizational change management. If the leadership doesn’t understand the magnitude of what is being requested, they may well think a project manager is best suited to run the PMO. The prestige and/or compensation is attractive, but project managers will often spin their wheels and naturally focus on what they know how to do: manage projects. Start with a PMO design to align with business expectations.

    The Peter Principle

    The Peter Principle was first introduced by Canadian sociologist Laurence Johnston Peter describing the pitfalls of bureaucratic organizations. The original principle states that "in a hierarchically structured administration, people tend to be promoted up to their level of incompetence.” The principle is based on the observation that whenever someone succeeds at their job, the organizational response is to promote them, thus people will continue to be promoted until they reach a point where they’re no longer excelling at their job. At that point, they would no longer be promoted. Followed to its logical conclusion, organizations will continue to take successful people and rotate them to new positions until they are no longer effective.

    PMO Director/Lead

    Job overviews for different kinds of PMO directors.

    The job descriptions on the next few pages are associated with the descriptive headings, but it is important to recognize that these diverse roles can all fall under the job title of PMO director.

    Portfolio Management

    As PMO director, you will oversee the throughput of IT projects using portfolio management, project management, and organizational change management disciplines.

    You and your team will directly manage the intake of new project requests, the preparation of evaluation-ready project proposals, and the handoff of approved project initiation documents to project managers in other departments. You will forecast and track the availability of people to do the project work throughout the project life cycle. You will publish monthly and annual portfolio reporting based on information collected from the project teams, and you will oversee the closure of projects with follow-up reporting to those who approved them.

    From time to time, the PMO may be required to identify projects that should be frozen or canceled based on criteria set forth by the leadership and/or industry best practices.

    While currently out of scope, successful candidates should be comfortable with the possibility that the PMO may required to develop full life cycle organizational change management in the future. As well, experienced project managers in the PMO may be required to manage high-risk, high-visibility projects from time to time.

    PMO Director/Lead

    Job overviews for different kinds of PMO directors.

    Project Management

    As PMO director, you will oversee a team of professional project managers who are responsible for the company’s high-risk, high-visibility, and strategic projects.

    You and your team will receive initiation documents and assigned resourcing for approved projects from the company’s authorized decision makers. You will manage the fulfillment of the project requirements, providing regular status updates to project and portfolio stakeholders and escalating concerns when projects are struggling to meet their commitments for scope, cost, and timelines.

    Over time, the PMO will take on an increasing role in organizational change management. The PMO will transition its focus from project delivery to business outcomes. Over time, the PMO will transition project sponsors from articulating requirements to delivering results.

    Project Policy

    As PMO director, you will oversee the establishment, support, and promotion of company-wide standards for project management.

    You and your team will modernize and maintain the company policy manuals and processes for everything related to project management. You will adapt our legacy PMBOK-based standards to cover iterative project management approaches as well as the more formal approaches required for construction projects, outsourced projects, and a wide variety of non-IT projects.

    PMO Director/Lead

    Job overviews for different kinds of PMO directors.

    Project Governance

    As PMO director, you will oversee the governance of project spending, delivery, and impact.

    You and your team will ensure that project proposals address the broad needs of the organization via strategic alignment, operational alignment, appropriateness of timing, identification and management of risk, and ability to execute. You will represent the needs and interests of the shareholder, ratepayer, or constituent by validating adherence to the organization’s published policies for project, portfolio, and organizational change management.

    The PMO is independent from the broader information technology division and will retain a mandate to ensure transparency and disclosure relative to the consumption of the organization’s scarce resources in the pursuit of high-risk IT projects.

    Stock photo of a compass pointing in the direction of leadership.

    Info-Tech sample job descriptions

    Use the sample job descriptions available with this blueprint as a guide when creating your descriptions.

    1. PMO Director
    2. Portfolio Manager
    3. Portfolio Administrator
    4. Project Manager
    5. Project Coordinator
    6. Resource Management Analyst
    1. Program Manager
    2. Change Manager
    3. Business Analyst
    4. Business Relationship Manager
    5. Product Owner
    6. Scrum Master

    Stock photo of a pen resting on a 'job duties' section of a job description.

    2.2.3 Create your job descriptions

    30 minutes

    Input: PMO Job Description Builder Workbook

    Output: Job descriptions

    Materials: Blank Job Description Template

    Participants: PMO director and/or portfolio manager, PMO staff, Project managers

    When you’ve determined the roles you need, you can start creating your job descriptions. If none of our out-of-the-box, pre-populated job description templates suit your needs, use the results of Info-Tech’s PMO Job Description Builder Workbook and the Blank Job Description Template to create your purpose-built job description.

    Follow these steps to create your job description:

    1. Copy the content from tab 4 of the PMO Job Description Builder Workbook and paste it under the relevant headings in the “Responsibilities” section of the Blank Job Description Template. Delete any unused headings if they are not relevant to your role. Additionally, use the list of common certifications on tab 4 of the Workbook to inform that section of the Blank Job Description Template.
    2. Use the sample job descriptions on the blueprint landing page as a guide for filling out the remaining sections of the document.

    Download the Blank Job Description Template

    2.2.3 Create your job descriptions continued

    Screenshot of the Blank Job Description Template.

    Prepare an Actionable Roadmap for Your PMO

    Phase 3

    Prepare an Actionable Roadmap for Your PMO

    Phase 1

    • 1.1 Get a Common Understanding of Your PMO Options
    • 1.2 Determine Where You Are and Engage Your Leadership

    Phase 2

    • 2.1 Identify Organizational Design
    • 2.2. Build Job Descriptions

    Phase 3

    • 3.1 Create Roadmap
    • 3.2 Governance and OCM

    Having a strategy is essential but real value and benefits are delivered through projects

    9.9% of every dollar is wasted due to poor project performance

    52% of projects are delivered to stakeholder satisfaction

    51% of projects are likely to meet original the goal and business intent
    (Source: Project Management Institute, 2018)

    You’re always going to have troubled projects

    Have the organizational discipline to step away from the mess and develop a plan.

    • The world of modern project management has been in place for over 50 years and yet business leaders still seem to put the pressure on troubled projects instead of broken processes.
    • With higher portfolio maturity comes higher performance, warranting investment in the PMO.
    • Instead of alternative cost-reduction measures, such as stopping an individual project, we find that PMO resources (or the entire PMO) are being cut. In most cases, this demonstrates a lack of understanding of the value of portfolio management processes and related impacts.
    • Plan for a series of improvements over time so you’re not continually using your PMO resources on troubled projects. Instead, maintain an ongoing focus on improvement.

    Stock photo of an axe stuck in a piece of wood.
    “If I had six hours to chop down a tree, I’d spend the first four hours sharpening the axe.” (Anonymous woodsman)

    All improvements cannot be done at once

    • The difference in a winning PMO is determined by a roadmap or plan created at the beginning.
    • Leaders should understand the full scope of the plan before committing their teams to the project.
    • All improvements cannot be done at once. The best PMOs create an approach of overall governance and strictly adhere to it. After the approach is defined, a roadmap can be plotted, executed, and delivered effectively.
    • The exercise of creating a roadmap is less about the plan and more about raising the level of understanding for stakeholders.
    • We often find that the PMO is ahead of the business's views of how the PMO can support and add value to the business. A lot of effort is spent trying to convince businesses of the value of a PMO, usually without complete success.
    • The PMO needs to align to the strategic goals of the business, providing the business understands or accepts that alignment. By aligning your roadmap activities to business drivers, you are more likely to get ownership from the business for the initiatives.
    Stock image of a winding path between two map markers.

    A PMO can benefit your business and organization as a whole

    Your PMO can:

    1. Help to align the project or portfolio with a focus on the future strategy of the organization.
    2. Be a mechanism to deliver projects successfully, keep them on track, and report when scheduling, budget, and other scope issues could derail the project.
    3. Create a portfolio of projects and understand the links and dependencies between the projects. This provides you with a bird's-eye view to make better decisions based on changes as they arise.
    4. Facilitate better communications with customers and stakeholders.
    5. Enforce project management governance and ensure consistent standards throughout the organization.
    6. Strategize on how to best use shared resources and best use them productively.

    “If you run projects and the projects have a significant level of cost or have significant level of impact, then you can really benefit from a PMO. Certainly, the larger the projects, the bigger the budget, the more there are projects, then the more you can benefit from a PMO.” (Michael Fritsch, Vice President PMO, Confoe)

    “PMOs are there to ensure project and program success and that’s critical because organizations deliver value through projects and programs.” (Brian Weiss, Vice President, Practitioner Career Development, Project Management Institute)

    Step 3.1

    Create Roadmap

    Activities
    • 3.1.1 Business Goals
    • 3.1.2 Roadmap
    • 3.1.3 Resources

    This step will walk you through the following activities:

    • Determine business goals
    • Create roadmap
    • Establish resources

    This step involves the following participants:

    • PMO director and/or portfolio manager
    • PMO staff/stakeholders
    • Project managers

    Outcomes of this step

    • PMO roadmap aligned to business goals

    Prepare an Actionable Roadmap for Your PMO

    Step 3.1 Step 3.2

    3.1.1 Business goals and priorities

    30 minutes

    Input: Business strategies and goals, Current PMO org. chart

    Output: An initial short, medium, long-term roadmap of initiatives

    Materials: Whiteboard/flip charts, Sticky notes, Slide 83

    Participants: IT leaders/CIO, PMO director and/or portfolio manager, PMO staff, Project managers

    When you are determining what your PMO will provide in the future, it is important to align the ambition of the PMO with the maturity of the business. Too often, a lot of effort is spent trying to convince businesses of the value of a PMO.

    Before you develop your roadmap, try to seek out the key strategies that the business is currently driving to get the proper ownership for the proposed initiatives.

    • What does leadership want to accomplish?
    • What are the key strategies the business is currently driving?
    • What are the current pain points?

    Once you’ve established the business strategies, start mapping out your initiatives:

    • For each initiative, consider the activities you think will work best to take you from your current to future state. It’s okay to keep this high level, we will break them down later in the blueprint.
    • Don’t place activities on a roadmap with dates yet. Use the table on the next slide to record the activities against each initiative at a high level.
    Current State Business Strategies PMO Initiatives Future State Business Strategies
    Short Term Medium Term Long Term
    Portfolio Management Project Intake Process
    Triage Process
    Project Levelling
    Book of Record
    Approval
    Prioritization
    Reporting
    Resource Allocation
    Resource Management
    Project Management Standardize Project Management
    Methodologies
    PM Training
    Organizational Change Management Benefits
    Governance Project progress, visibility, and process
    Documentation

    3.1.2 Create your roadmap

    1-2 hours

    Services should be introduced gradually and your PMO roadmap should clearly highlight this and explain when key deliverables will be achieved.

    Consider the below top-level tasks and add any others that pertain to your organization:

    • Enable Transition
    • Establish Governance
    • Organizational Chart
    • Technology and Infrastructure
    • Develop Portfolio Management Capabilities and Guidelines
    • Standardize Project Management Methodology
    • Organizational Change Management
    • Strategy Management

    Download Info-Tech’s PMO MS Project Plan Sample to see a full list of top-level tasks and second-level tasks. Once done, you can visually plot the tasks on a roadmap. See the next few slides for roadmap visuals.

    Stock photo of median lines on a road with the years 2021-2023 painted between them.

    Download the PMO MS Project Plan Sample

    Screenshot of PMO MS Project Plan Sample

    Screenshot of PMO MS Project Plan Sample with notes point out the headings as 'Top-level hierarchy' and the list contents as 'Second-level-hierarchy'.

    Sample roadmap

    A sample roadmap with column headers 'Task' and 'Q1', 'Q2', 'Q3', 'Q4', and 'Q1' with 3 months beneath each quarter. Under 'Task' are 'Establish Tradition', 'Establish Governance', 'Organizational Chart', and 'Technology and Infrastructure'; these are the 'Top-level-hierarchy'. There are arrows laid out in the table cross section with different steps; these are the 'Second-level hierarchy'.

    Sample roadmap

    A sample roadmap with monthly column headers 'Jan' through 'Jun'. Rows are 'Develop Portfolio Management Capabilities and Guidelines', 'Standardize Project Management Methodology', and 'Design Resource Management Process'. There are processes laid out in the table cross section that are color-coded as 'Completed', 'In progress', and 'Planned'.

    Consider the resources you will need

    Use these Info-Tech resources to make sure your roadmap will be successful.

    Finances – Understand and be transparent about the real costs of your project.

    People – Strategize according to skill sets and availability. Use the org. chart in phase 2 of this blueprint as a starting place (slide 58).

    Assets – Determine the tangible resources you may buy like software and licenses.

    Stock photo of a thinking man.

    3.1.3 Define resources

    30 minutes

    Input: Project documentation, Current resources

    Output: List of resources for your PMO

    Materials: Whiteboard/flip charts

    Participants: IT leaders/CIO, PMO director and/or portfolio manager, PMO staff, Project managers

    Resources for your projects include staff, equipment, and materials. Resource management at the PMO level will help you manage those resources, get visibility into projects, and keep them moving forward. Be sure to consider the resources that will get your PMO off the ground.

    Determine the resources you currently have and the resources your PMO will need and add them to your strategic plan:

    1. Finances — It’s essential that you know, and are transparent about, the real cost of creating your PMO and new process. Don’t forget to consider post deployment costs as well.
    2. People — Every project depends on the skill sets that individual team members bring to the table. Strategize according to these skill sets and their availability for the duration of a project. Some team members may have other work responsibilities and limited time for the project, so you need to accommodate this.
    3. Assets — These include the tangible resources you may have to buy, lease, or arrange for, such as workspace, software and licenses, computer hardware, testing equipment, and so on.

    Step 3.2

    Governance and OCM

    Activities
    • 3.2.1 Governance
    • 3.2.2 OCM
    • 3.2.3 Perform a Change Impact Analysis
    • 3.2.4 Determine Dimensions of Change
    • 3.2.5 Determine Depth of Impact

    This step will walk you through the following activities:

    • Assess/understand governance
    • Conduct impact analysis

    This step involves the following participants:

    • PMO director and/or portfolio manager
    • PMO staff/stakeholders
    • Project managers

    Outcomes of this step

    • Governance Structures
    • Organizational Change Management Impact Analysis Tool

    Prepare an Actionable Roadmap for Your PMO

    Step 3.1 Step 3.2

    Clearly define the authority your PMO will have

    The following section includes slides from Info-Tech’s Make Governance Adaptable blueprint. Download the blueprint to dive deeper into IT governance.

    Governance is an important part of building a strong PMO. A PMO governance framework defines the authority and the support it requires to maximize portfolio and project management capabilities throughout the business. It should sit within your overall governance framework and as the PMO matures, its roles and responsibilities will also change to adapt with business demands and additional capabilities.

    Your framework can:

    • Specify PMO authority
    • Introduce and apply process standards, polices, and directives as it pertains to project and portfolio management
    • Facilitate executive and leadership involvement
    • Foster a collaborative environment between the PMO and the business

    A PMO governance framework enables PMO leaders to establish the common guidelines and manage the distribution of authority given to the PMO.

    Visit Make Your IT Governance Adaptable

    Stock photo of a group working together.

    Common causes of poor governance

    Key causes of poor or misaligned governance
    1. Governance and its value to your organization is not well understood, often being confused or integrated with more granular management activities.
    2. Business executives fail to understand that IT governance is a function of the business and not the IT department.
    3. Poor past experiences have made “governance” a bad word in the organization – a constraint and barrier that must be circumvented to get work done.
    4. There is misalignment between accountability and authority throughout the organization, and the wrong people are involved in governance practices.
    5. There is an unwillingness to change a governance approach that has served the organization well in the past, leading to challenges when the organization starts to change practices and speed of delivery.
    6. There is a lack of data and data-related capabilities required to support good decision making and the automation of governing decisions.
    7. The goals and strategy of the organization are not known or understood, leaving nothing for IT governance to orient around.
    Five key symptoms of ineffective governance committees
    1. No actions or decisions are generated – The committee produces no value and makes no decisions after it meets. The lack of value output makes the usefulness of the committee questionable.
    2. Overallocation of resources – There is a lack of clear understanding of capacity and value in work to be done, leading to consistent underestimation of required resources and resource overallocation.
    3. Decisions are changed outside of committee – Decisions that are made or initiatives that are approved are changed when the proper decision makers are involved or the right information becomes available.
    4. Decisions conflict with organizational direction – Governance decisions conflict with organizational needs, showing a visible lack of alignment and behavioral disconnects that work against organizational success. Often due to power that’s not accounted for within the structure.
    5. Consistently poor outcomes are produced from governance direction – Lack of business acumen in members and relevant data or understanding of organizational goals drives poor measured outcomes from the decisions made in the committee.

    IT PMO

    Chair:
    Updated:

    Mandate

    Ensure business value is achieved through information and technology (IT) investments by aligning strategic objectives and client needs with IT initiatives and their outcomes.

    Committee Goals

    • Maximize throughput of the most valuable projects
    • Ensure visibility of current and pending projects
    • Minimize resource waste and optimize of alignment of skills to assignments
    • Clarify accountability for post-project benefits attainment and facilitate the tracking/reporting of those benefits
    • Drive approval and prioritization of IT initiatives based on their alignment with business goals and strategy
    • Establish a consistent process for handling intake/demand

    Committee Metrics

    • % of approved IT initiatives that measure benefit achievement upon completion
    • % of IT initiatives with direct alignment to organizational strategic direction
    • % of initiatives approved by exception

    Decisions and responsibilities by purpose

    Responsibilities
    STRATEGIC ALIGNMENT

    Ensure initiatives align with organizational objectives
    Embed strategic goals and prioritization approach within process
    Define intake approach

    VALUE DELIVERY
    • Ensure all IT initiatives have a defined value expectation (excepting innovation activities)
    • Approve and prioritize IT initiatives based on value
    RISK MANAGEMENT

    Assess risk as a factor of prioritizing and approving initiatives

    RESOURCE MANAGEMENT

    Decide on the allocation of IT resources

    PERFORMANCE MEASUREMENT

    Ensure process is in place to measure and validate performance of IT initiatives

    Committee Membership
    Role

    CIO, Product Owner, Service Owner, IT VPs, BRM, PMO Director, CISO/CRO

    Individual

    IT Steering Committee

    Chair:
    Updated:

    Mandate

    Ensure business value is achieved through information and technology (IT) investments by aligning strategic objectives and client needs with IT initiatives and their outcomes.

    Committee Goals

    • Align IT initiatives with organizational goals
    • Evaluate, approve, and prioritize IT initiatives
    • Approve IT strategy
    • Reinforce (if provided) or establish risk appetite and threshold
    • Confirm value achievement of approved initiatives
    • Set target investment mix and optimize IT resource utilization

    Committee Metrics

    • % of approved IT initiatives that meet or exceed value expectation
    • % of IT initiatives with direct alignment to organizational strategic direction
    • Level of satisfaction with IT decision making
    • % of initiatives approved by exception

    Committee Overview

    Committee Name Committee Membership Mandate
    Executive Leadership Committee CEO, CFO, CTO, CDO, CISO/CRO, CIO, Enterprise Architect/Chief Architect, CPO Provide strategic and operational leadership to the company by establishing goals, developing strategy, and directing/validating strategic execution.
    Enterprise Risk Committee CISO/CRO, CPO, Enterprise Risk Manager, BU Leaders, CFO, CTO, CDO Govern enterprise risks to ensure that risk information is available and integrated to support governance decision making. Ensure the definition of the organizational risk posture and that an enterprise risk approach is in place.
    IT Steering Committee CIO, Product Owner, Service Owner, IT VPs, BRM, PMO Director, CISO/CRO Ensure business value is achieved through information and technology (IT) investments by aligning strategic objectives and client needs with IT initiatives and their outcomes.
    IT Risk Council IT Risk Manager, CISO, IT Directors Govern IT risks within the context of business strategy and objectives to align the decision-making processes towards the achievement of performance goals. It will also ensure that a risk management framework is in place and risk posture (risk appetite/threshold) is defined.
    PPM Portfolio Manager, Project Managers, BRMs Ensure the best alignment of IT initiatives and program activity to meet the goals of the business.
    Architectural Review Board Service/Product Owners, Enterprise Architects, Chief Architect, Domain Architects Ensure enterprise and related architectures are managed and applied enterprise-wise. Ensure the alignment of IT initiatives to business strategy and architecture and compliance to regulatory standards. Establish architectural standards and guidelines. Review and recommend initiatives.
    Change Advisory Board Service/Product Owner, Change Manager, IT Directors or Managers Ensure changes are assessed, prioritized, and approved to support the change management purpose of optimizing the throughput of successful changes with a minimum of disruption to business function.

    Decisions and responsibilities by purpose

    Responsibilities
    STRATEGIC ALIGNMENT
    • Ensure initiatives align with organizational objectives
    • Approve strategies and policies that ensure the organization benefits from IT
    • Propose innovative uses of IT to enable the business to compete and perform better
    • Make decisions that account for human preferences and behavior
    VALUE DELIVERY
    • Validate the achievement of benefits from IT initiatives
    • Ensure all IT initiatives have a defined value expectation (excepting innovation activities)
    • Ensure stakeholder value and value drivers are understood
    • Prioritize IT work based on value
    • Define a prioritization approach with stakeholders
    RISK MANAGEMENT
    • Ensure creation, maintenance, and observation of policies and procedures, ensuring conformance where needed
    • Ensure ethical behavior in IT
    • Ensure IT meets the requirements of laws, regulations, and contracts
    • Develop or reinforce the risk appetite and threshold
    • Ensure risk management framework is in place
    RESOURCE MANAGEMENT
    • Identify the target investment mix
    • Decide on the allocation of IT resources
    • Define required IT capabilities
    PERFORMANCE MEASUREMENT
    • Confirm that IT supports business processes with the right capabilities and capacity
    • Ensure data is up to date and secure
    • Monitor the extent to which prioritization of IT resources matches organizational objectives
    • Measure extent to which IT supports the business
    • Measure adherence to regulations
    Committee Membership
    Role

    CIO, Product Owner, Service Owner, IT VPs, BRM, PMO Director, CISO/CRO

    Individual

    Sample Governance Model

    A sample governance model with four levels and roles dispersed throughout the levels with arrows indicating hierarchy. The levels are 'Enterprise: Defines organizational goals. Directs or regulates the performance and behavior of the enterprise, ensuring it has the structure and capabilities to achieve its goals', 'Strategic: Ensures IT initiatives, products, and services are aligned to organizational goals and strategy and provide expected value. Ensure adherence to key principles', 'Tactical: Ensures key activities and planning are in place to execute strategic initiatives', and 'Operational: Ensures effective execution of day-to-day functions and practices to meet their key objectives'. Roles in Enterprise are 'Board', 'Executive Leadership Committee', and 'Enterprise Risk Committee'. Roles in Strategic are 'IT Steering Committee', plus three half in Strategic, 'IT PMO', 'Architectural Review Board', and 'IT Risk Council'. One role is half in Strategic and half in Tactical, 'Change Advisory Board'.

    3.2.1 Governance and authority

    1-3 hours

    Input: List of key tasks

    Output: Initial Authority Map

    Materials: Whiteboard/flip charts, Sticky notes, Strategic Plan

    Participants: IT leadership, Portfolio Manager (PMO Director), PMO Admin Team, Project Managers

    Now that you’ve determined the activities on your roadmap, it’s important to determine who is going to be responsible for the following:

    • Intake Scoring
    • Project Approvals
    • Staffing and Resource Management
    • Portfolio Reporting
    • Communications and Organizational Change Management
    • Benefits Attainment
    • Formalized Project Closure
    1. For each task have participants discuss who is ultimately accountable for the decision and who has the ultimate authority to make that decision.
    2. Place the sticky notes on the swim lanes in the strategic plan to represent the area or person has authority over it.
    3. Add all initiatives to your PMO governance framework.

    Download the PMO Strategic Plan

    Governance and Authority

    Committee Name Committee Membership
    Executive Leadership Committee CEO, CFO, CTO, CDO, CISO/CRO, CIO, Enterprise Architect/Chief Architect, CPO
    Enterprise Risk Committee CISO/CRO, CPO, Enterprise Risk Manager, BU Leaders, CFO, CTO, CDO
    IT Steering Committee CIO, Product Owner, Service Owner, IT VPs, BRM, PMO Director, CISO/CRO
    IT Risk Council IT Risk Manager, CISO, IT Directors,
    PPM Portfolio Manager, Project Managers, BRMs
    Architectural Review Board Service/Product Owners, Enterprise Architects, Chief Architect, Domain Architects
    Change Advisory Board Service/Product Owner, Change Manager, IT Directors or Managers

    PMO Governance Framework

    PMO Authority
    • Resource Management
    • Customer Relationship
    • Vendor & Contractor Relationships
    • Intake and Scoring
    • Project Approvals
    • Organizational Change Management
    Standards and Policies
    • Portfolio Management Process
    • Project Governance
    Guidelines
    • Project Classification Guidelines
    Executive Oversight
    • Establish Steering Committees
    • Sponsorship
    • Spending Authorization
    • Execution Oversight
    • Spending Cessation
    • Benefits Attainment
    • Organizational Change Management

    Customize groupings as appropriate.

    Document key achievements governance initiatives.

    Completed projects aren’t necessarily successful projects

    The constraints that drive project management (time, scope, and budget) are insufficient for driving the overall success of project efforts.

    For instance, a project may come in on time, on budget, and in scope, but…

    • …if users and stakeholders fail to adopt…
    • …and the intended benefits are not achieved...

    …then that “successful project” represents a massive waste of the organization’s time and resources.

    Organizational change management (OCM) is a supplement to project management that is needed to ensure the intended value is realized. It is the practice through which the PMO or other body can improve user adoption rates and maximize project benefits. Without it, IT might finish the project but the business might fail to recognize the intended benefits.

    Start with next step and refer to Info-Tech research on OCM for a deeper dive. Impact analysis is the cornerstone of any OCM strategy. By shining a light on considerations that might have otherwise escaped project planners and decision makers, an impact analysis is an essential component to change management and project success.

    Change Impact Analysis

    1. It is important to establish a process for analyzing how the change of your PMO roadmap processes will impact different areas of the business and how to manage these impacts. Analyze change impacts across multiple dimensions to ensure nothing is overlooked.
    2. A thorough analysis of change impacts will help the PMO processes:
      • Bypass avoidable problems.
      • Remove non-fixed barriers to success.
      • Acknowledge and minimize the impacts of unavoidable barriers.
      • Identify and leverage potential benefits.
      • Measure the success of the change.

    3.2.2 Perform a change impact analysis to make your planning more complete

    Use Info-Tech’s Organizational Change Impact Analysis Tool to weigh all the factors involved in the change.

    Info-Tech’s Organizational Change Impact Analysis Tool helps to document the change impact across multiple dimensions, enabling you to review the analysis with others to ensure that the most important impacts are captured. The tool also helps to effectively monitor each impact throughout project execution.

    • Change impact considerations can include products, services, states, provinces, cultures, time zones, legal jurisdictions, languages, colors, brands, subsidiaries, competitors, departments, jobs, stores, locations, etc.
    • Each of these dimensions is an MECE (Mutually Exclusive, Collectively Exhaustive) list of considerations that could be impacted by the change. For example, a North American retail chain might consider “Time Zones” as a key dimension, which could break down as Newfoundland, Atlantic, Eastern, Central, Mountain, and Pacific.

    Sample of the Organizational Change Impact Analysis Tool.

    Download the Organizational Change Impact Analysis Tool

    3.2.3 Assess the current state of your project environment

    15 minutes

    The “2. Set Up” tab of the Impact Tool is where you enter project-specific data pertaining to the change initiative.

    The inputs on this tab are used to auto-populate fields and drop-down menus on subsequent tabs of the analysis.

    Document the stakeholders (by individual or group) associated with the project who will be subject to the impacts.

    You are allowed up to 15 entries. Try to make this list comprehensive. Missing any key stakeholders will threaten the value of this activity as a whole.

    If you find that you have more than 15 individual stakeholders, you can group individuals into stakeholder groups.

    Sample of the Impact Analysis Tool Set-Up Tab. There is a space for 'Project Name' and a list of 'Project Stakeholders'.
    Keep in mind…

    An impact analysis is not a stakeholder management exercise.

    Impact assessments cover:

    • How the change will affect the organization.
    • How individual impacts might influence the likelihood of adoption.

    Stakeholder management covers:

    • Resistance/objections handling.
    • Engagement strategies to promote adoption.

    We will cover the latter in the next step.

    3.2.4 Determine the relevant considerations for analyzing the change impacts

    15-30 minutes

    Use the survey on tab 3 of the Impact Analysis Tool to determine the dimensions of change that are relevant.

    The impact analysis is fueled by the 13-question survey on tab 3 of the tool.

    This survey addresses a comprehensive assortment of change dimensions, ranging from customer-facing considerations to employee concerns, to resourcing, logistical, and technological questions.

    Once you have determined the dimensions that are impacted by the change, you can go on to assess how individual stakeholders and stakeholder groups are affected by the change.

    Sample of the Change Impact Survey on tab 3 of the Impact Analysis Tool.
    Screenshot of tab “3. Impact Survey,” showing the 13-question survey that drives the impact analysis.

    Ideally, the survey should be performed by a group of project stakeholders together. Use the drop-down menus in column K to record your responses.

    Impacts will be felt differently by different stakeholders and stakeholder groups

    As you assess change impacts, keep in mind that no impact will be felt the same across the organization. Depth of impact can vary depending on the frequency (will the impact be felt daily, weekly, monthly?), the actions necessitated by it (e.g. will it change the way the job is done or is it simply a minor process tweak?), and the anticipated response of the stakeholder (support, resistance, indifference?).

    Use the Organizational Change Depth Scale below to help visualize various depths of impact. The deeper the impact, the tougher the job of managing change will be.

    Procedural
    Behavioral
    Interpersonal
    Vocational
    Cultural
    Procedural change involves changes to explicit procedures, rules, policies, processes, etc. Behavioral change is similar to procedural change, but goes deeper to involve the changing tacit or unconscious habits. Interpersonal change goes beyond behavioral change to involve changing relationships, teams, locations, reporting structures, and other social interactions. Vocational change requires acquiring new knowledge and skills and accepting the loss or decline in the value or relevance of previously acquired knowledge and skills. Cultural change goes beyond interpersonal and vocational change to involve changing personal values, social norms, and assumptions about the meaning of good vs. bad or right vs. wrong.
    Example: providing sales reps with mobile access to the CRM application to let them update records from the field. Example: requiring sales reps to use tablets equipped with a custom mobile application for placing orders from the field. Example: migrating sales reps to work 100% remotely. Example: migrating technical support staff to field service and sales support roles. Example: changing the operating model to a more service-based value proposition or focus.

    3.2.5 Determine the depth of each impact for each stakeholder group

    1-3 hours

    Tab “4. Impact Analysis” of the Analysis Tool contains the meat of the impact analysis activity.

    1. The “Impact Analysis” tab is made up of 13 change impact tables (see next slide for a screenshot of one of these tables).
      • You may not need to use all 13 tables. The number of tables you use coincides with the number of “yes” responses you gave in the previous tab.
      • If you do not need all 13 impact tables (i.e. if you do not answer “yes” to all thirteen questions in tab 2) the unused/unnecessary tables will not auto-populate.
    2. Use one table per change impact. Each of your “yes” responses from tab 3 will auto-populate at the top of each change impact table. You should go through each of your “yes” responses in turn.
    3. Analyze how each impact will affect each stakeholder or stakeholder group touched by the project.
      • Column B in each table will auto-populate with the stakeholder groups from the Set-Up tab.
    4. Use the drop-down menus in columns C, D, and E to rate the frequency of each impact, the actions necessitated by each impact, and the anticipated response of each stakeholder group.
      • Each of the options in these drop-down menus is tied to a ranking table that informs the ratings on the two subsequent tabs.
    5. If warranted, you can use the “Comments” cells in column F to note the specifics of each impact for each stakeholder/group.

    See the next slide for an accompanying screenshot of a change impact table from tab 4 of the Analysis Tool.

    Screenshot of “Impact Analysis” tab

    Screenshot of the Impact analysis tab of the Analysis Tool.

    The stakeholder groups entered on the Set Up tab will auto-populate in column B of each table.

    Your “yes” responses from the survey tab will auto-populate in the cells to the right of the “Change Impact” cells.

    Use the drop-down menus in this column to select how often the impact will be felt for each group (e.g. daily, weekly, periodically, one time, or never).

    “Actions” include “change to core job duties,” “change to how time is spent,” “confirm awareness of change,” etc.

    Use the drop-down menus to hypothesize what the stakeholder response might be. For the purpose of this impact analysis, a guess is fine. A more detailed communication plan can be created later.

    Review your overall impact rating to help assess the likelihood of change adoption

    Use the “Overall Impact Rating” on tab 5 to help right-size your OCM efforts.

    Based upon your assessment of each individual impact, the Analysis Tool will provide you with an “Overall Impact Rating” in tab 5.

    • This rating is an aggregate of each of the individual change impact tables used during the analysis and the rankings assigned to each stakeholder group across the frequency, required actions, and anticipated response columns.
    Projects in the red zone should have maximum change governance, applying a full suite of OCM tools and templates as well as revisiting the impact analysis exercise regularly to help monitor progress.

    Increased communication and training efforts, as well as cross-functional partnerships, will also be key for success.

    Projects in the yellow zone also require a high level of change governance.
    Screenshot of 'Overall Impact Rating' scale on tab 5 of the Analysis Tool.
    To free up resources for those OCM initiatives that require more discipline, projects in the green zone can ease up in their OCM efforts somewhat. With a high likelihood of adoption as is, stakeholder engagement and communication efforts can be minimized somewhat for these projects, so long as the PMO is in regular contact with key stakeholders.

    Use the other outputs on tab 5 to help structure your OCM efforts

    In addition to the overall impact rating, tab 5 has other outputs that will help you assess specific impacts and how the overall change will be received by stakeholders.

    Screenshot of the Impact Analysis Outputs on tab 5 of the Analysis Tool. There are tables ranking risk impacts and stakeholders, as well as an impact zone map.

    This table displays the highest risk impacts based on frequency and action inputs on tab 4.

    Here you’ll find the stakeholders, ranked again based on frequency and action, who will be most impacted by the proposed changes.

    These are the five stakeholders most likely to support changes, based on the Anticipated Response column on tab 4.

    The stakeholder groups entered on the Set Up tab will auto-populate in column B of each table.

    In addition to these outputs, this tab also lists top five change resistors and has an impact register and list of potential impacts to watch out for (i.e. your “maybe” responses from tab 3).

    Establish Baseline Metrics

    Baseline metrics will be improved through:

    • A strong PMO is one than can link performance to the overall goals of the organization.
    • Use these examples of KPIs to measure success.
    Metric KPI
    Portfolio Performance Return on Investment (ROI) for projects and programs
    Alignment of spend with objectives
    Resource Utilization Rate (hours allocated to projects actual vs. allocation)
    Customer/Stakeholder Satisfaction
    # of strategic projects approved vs. completed
    Project/Program Performance % of completed projects (planned vs. actual)
    % of projects completed on time (based on original due date)
    % of projects completed on budget
    % of projects delivering their expected business outcomes
    Actual delivery of benefits vs. planned benefits
    % of customer satisfaction
    Project manager satisfaction rating
    PMO % of approved IT initiatives that measure benefit achievement upon completion
    % of IT initiatives with direct alignment to organizational strategic direction

    Summary of Accomplishment

    Problem Solved

    Knowledge Gained
    • PMO Options and “Best Practices”
    • PMO Types
    • Key PMO Functions/Services

    The PMO staffing model that you use will depend on many different factors. It is in your hands to create and define what your staffing needs are for your organization.

    The success of your PMO is linked to the plan you create before executing on it.

    Processes Optimized
    • Establishing organizational need.
    • Getting situational awareness to build a solid foundation for the PMO.
    • Identifying organizational design and establishing PMO structure and staffing needs.
    • Creating an actionable roadmap.

    If you would like additional support, have our analysts guide you through other phases as part of an Info-Tech workshop.

    Contact your account representative for more information.

    workshops@infotech.com 1-888-670-8889

    Summary of Accomplishment

    Problem Solved

    Deliverables Completed
    • PMO Role Development Tool
    • Initial PMO Mandate
    • PMO Job Description Builder Workbook
    • PMO job descriptions
    • PMO Strategic Plan
    • Organizational Change Impact Analysis Tool

    If you would like additional support, have our analysts guide you through other phases as part of an Info-Tech workshop.

    Contact your account representative for more information.

    workshops@infotech.com 1-888-670-8889

    Additional Support

    If you would like additional support, have our analysts guide you through other phases as part of an Info-Tech workshop.

    Photo of Ugbad Farah.

    Contact your account representative for more information.

    workshops@infotech.com 1-888-670-8889

    To accelerate this project, engage your IT team in an Info-Tech workshop with an Info-Tech analyst team.

    Info-Tech analysts will join you and your team at your location or welcome you to Info-Tech’s historic Toronto office to participate in an innovative onsite workshop.

    The following are sample activities that will be conducted by Info-Tech analysts with your team:

    Sample of the Job Description Survey activity.
    Job Description Survey
    Use the survey to help determine potential role requirements across various project portfolio management, project management, business analysis, and organizational change management activities.
    Sample of the Job Descriptions builder activity.
    Create Your Job Descriptions
    Use the job descriptions as a guide when creating your own job descriptions based on the outputs from the tool.

    Related Info-Tech Research

    Stock photo of two people looking over their finances. Develop a Project Portfolio Management Strategy
    Time is money; spend it wisely.
    Stock photo of a hand with a pen resting on paper. Establish Realistic IT Resource Management Practices
    Holistically balance IT supply and demand to avoid overallocation.
    Stock photo of light bending through a tunnel. Tailor Project Management Processes to Fit Your Projects
    Spend less time managing processes and more time delivering results.

    Related Info-Tech Research

    Stock photo of a group working on a project. Optimize IT Project Intake, Approval, and Prioritization
    Decide which IT projects to approve and when to start them.
    Stock photo of a round table silhouetted in front of a window. Master Organizational Change Management Practices
    PMOs, if you don’t know who is responsible for org change, it’s you.
    Stock photo of the nose of a fighter jet. Set a Strategic Course of Action for the PMO in 100 Days
    Use your first 100 days as PMO leader to define a mandate for long-term success.

    Bibliography

    Alexander, Moira. “How to Develop a PMO Strategic Plan.” CIO, 11 July 2018. Web.

    Barlow, Gina, Andrew Tubb, and Grant Riley. “Driving Business Performance. Project Management Survey 2017.” KPMG, 2017. Accessed 11 Jan. 2022.

    Brennan, M. V., and G. Heerkens. “How we went from zero project management to PMO implementation—a real life story.” Paper presented at PMI® Global Congress 2009—North America, Orlando, FL. Project Management Institute, 13 October 2009. Web.

    Casey, W., and W. Peck. “Choosing the right PMO setup.” PM Network, vol. 15, no. 2, 2001, pp. 40-47. Web.

    “COBIT 2019 Framework Governance and Management Objectives.” ISACA, 2019. PDF.

    Crawford, J. K. “Staffing your strategic project office: seven keys to success.” Paper presented at Project Management Institute Annual Seminars & Symposium, San Antonio, TX. Project Management Institute, 2002. Web.

    Davis, Stanley M., and Paul R. Lawrence. “Problems of Matrix Organizations.” Harvard Business Review, May 1978. Web.

    Dow, William D. “Chapter 6: The Tactical Guide for Building a PMO.” Dow Publishing, 2012. PDF.

    Giraudo, L., and E. Monaldi. “PMO evolution: from the origin to the future.” Paper presented at PMI® Global Congress 2015—EMEA, London, England. Project Management Institute, 11 May 2015. Web.

    Greengard, S. “No PMO? Know when you need one.” PM Network, vol. 27, no. 12, 2013, pp. 44-49. Web.

    Hobbs, J. B., and M. Aubry. “What research is telling us about PMOs.” Paper presented at PMI® Global Congress 2009—EMEA, Amsterdam, North Holland, The Netherlands. Project Management Institute, May 2009. Web.

    Jordan, Andy. “Staffing the Strategic PMO.” ProjectManagement.com, 24 October 2016. Web.

    Lang, Greg. “5 Questions to Answer When Building a Roadmap.” LinkedIn, 2 October 2016. Accessed 15 Apr. 2021.

    Manello, Carl. “Establish a PMO Roadmap.” LinkedIn, 10 February 2021. Accessed 29 Mar. 2021.

    Martin, Ken. “5 Steps to Set Up a Successful Project Management Office.” BrightWork, 9 July 2018. Accessed 29 Mar. 2021.

    Miller, Jen A. “What Is a Project Management Office (PMO) and Do You Need One?” CIO, 19 October 2017. Accessed 16 Apr. 2021.

    Needs, Ian. “Why PMOs Fail: 5 Shocking PMO Statistics.” KeyedIn, 6 January 2014. Web.

    Ovans, Andrea. “Overcoming the Peter Principle.” Harvard Business Review, 22 December 2014. Web.

    PMI®. “A Guide to the Project Management Body of Knowledge.” 6th Ed. Project Management Institute, 2017.

    PMI®. “Ahead of the Curve: Forging a Future-Focused Culture.” Pulse of the Profession. Project Management Institute, 11 February 2020. Accessed 21 April 2021.

    PMI®. “Project Management: Job Growth and Talent Gap.” Project Management Institute, 2017. Web.

    PMI®. “Pulse of the Profession: Success in Disruptive Times.” Project Management Institute, 2018. Web.

    PMI®.“The Project Management Office: In Sync with Strategy.” Project Management Institute, March 2012. Web.

    “Project Management Organizational Structures.” PM4Dev, 2016. Web.

    Rincon, I. “Building a PMO from the ground up: Three stories, one result.” Paper presented at PMI® Global Congress 2014—North America, Phoenix, AZ. Project Management Institute, 26 October 2014. Web.

    Roseke, Bernie. “The 4 Types of Project Organizational Structure.” ProjectEngineer, 16 August 2019. Web.

    Sexton, Peter. “Project Delivery Performance: AIPM and KPMG Project Management Survey 2020 - KPMG Australia.” KPMG, 9 November 2020. Web.

    The Change Management Office (CMO). Prosci, n.d. Accessed 7 July 2021.

    “The New Face of Strategic Planning.” Project Smart, 27 March 2009. Accessed 29 Mar. 2021.

    “The State of Project Management Annual Survey.” Wellington PPM Intelligence, 2018. Web.

    “The State of the Project Management Office : Enabling Strategy Execution Excellence.” PM Solutions Research, 2016. Web.

    Wagner, Rodd. “New Evidence The Peter Principle Is Real - And What To Do About It.” Forbes, 10 April 2018. Accessed 14 Apr. 2021.

    Wright, David. “Developing Your PMO Roadmap.” Paper presented at PMI® Global Congress 2012—North America, Vancouver, British Columbia, Canada. Project Management Institute, 2012. Accessed 29 March 2021.

    IT Organizational Design

    • Buy Link or Shortcode: {j2store}32|cart{/j2store}
    • Related Products: {j2store}32|crosssells{/j2store}
    • member rating overall impact: 9.1/10
    • member rating average dollars saved: $83,392
    • member rating average days saved: 21
    • Parent Category Name: People and Resources
    • Parent Category Link: /people-and-resources

    The challenge

    • IT can ensure full business alignment through an organizational redesign.
    • Finding the best approach for your company is difficult due to many frameworks and competing priorities.
    • External competitive influences and technological trends exacerbate this.

    Our advice

    Insight

    • Your structure is the critical enabler of your strategic direction. Structure dictates how people work together and how they can fill in their roles to create the desired business value. 
    • Constant change is killing for an organization. You need to adapt, but you need a stable baseline and make sure the change is in line with the overall strategy and company context.
    • A redesign is only successful if it really happens. Shifting people into new positions is not enough to implement a redesign. 

    Impact and results 

    • Define your redesign principles. They will act as a manifesto to your change. It also provides for a checklist, ensuring that the structure does not deviate from the business strategy.
    • Visualize the new design with a customized operating model for your company. It must demonstrate how IT creates value and supports the business value creation chains.
    • Define the future-state roles, functions, and responsibilities to enable your IT department to support the business effectively.

    The roadmap

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    Get started

    Our concise executive brief explains to you the challenges associated with the organizational redesign. We'll show you our methodology and the ways we can help you in completing this.

    Define your organizational design principles and select your operating model

    The design principles will govern your organizational redesign; Align the principles with your business strategy.

    • Redesign Your IT Organizational Structure – Phase 1: Craft Organizational Design Principles and Select an IT Operating Model (ppt)
    • Organizational Design Communications Deck (ppt)

    Customize the selected IT operating model to your company

    Your operating model must account for the company's nuances and culture.

    • Redesign Your IT Organizational Structure – Phase 2: Customize the IT Operating Model (ppt)
    • Operating Models and Capability Definition List (ppt)

    Design the target-state of your IT organizational structure

    Go from an operating model to the structure fit for your company.

    • Redesign Your IT Organizational Structure – Phase 3: Architect the Target-State IT Organizational Structure (ppt)
    • Organizational Design Capability RACI Chart (xls)
    • Work Unit Reference Structures (Visio)
    • Work Unit Reference Structures (pdf)

    Communicate the benefits of the new structure

    Change does not come easy. People will be anxious. Craft your communications to address critical concerns and obtain buy-in from the organization. If the reorganization will be painful, be up-front on that, and limit the time in which people are uncertain.

    • Redesign Your IT Organizational Structure – Phase 4: Communicate the Benefits of the New Organizational Structure (ppt)


    Cost Optimization

    • Buy Link or Shortcode: {j2store}14|cart{/j2store}
    • Related Products: {j2store}14|crosssells{/j2store}
    • Up-Sell: {j2store}14|upsells{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Financial Management
    • Parent Category Link: /financial-management
    Minimize the damage of IT cost cuts

    2020 Security Priorities Report

    • Buy Link or Shortcode: {j2store}245|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Security Strategy & Budgeting
    • Parent Category Link: /security-strategy-and-budgeting

    Use this deck to learn what projects security practitioners are prioritizing for 2020. Based on a survey of 460 IT security professionals, this report explains what you need to know about the top five priorities, including:

    • Signals and drivers
    • Benefits
    • Critical uncertainties
    • Case study
    • Implications

    While the priorities should in no way be read as prescriptive, this research study provides a high-level guide to understand that priorities drive the initiatives, projects, and responsibilities that make up organizations' security strategies.

    Our Advice

    Critical Insight

    There is always more to do, and if IT leaders are to grow with the business, provide meaningful value, and ascend the ladder to achieve true business partner and innovator status, aggressive prioritization is necessary. Clearly, security has become a priority across organizations, as security budgets have continued to increase over the course of 2019. 2020’s priorities highlight that data security has become the thread that runs through all other security priorities, as data is now the currency of the modern digital economy. As a result, data security has reshaped organizations’ priorities to ensure that data is always protected.

    Impact and Result

    Ultimately, understanding how changes in technology and patterns of work stand to impact the day-to-day lives of IT staff across seniority and industries will allow you to evaluate what your priorities should be for 2020. Ensure that you’re spending your time right. Use data to validate. Prioritize and implement.

    2020 Security Priorities Report Research & Tools

    Start here – read the Executive Brief

    This storyboard will help you understand what projects security practitioners are prioritizing for 2020.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Data security

    Data security often rubs against other organizational priorities like data quality, but organizations need to understand that the way they store, handle, and dispose of data is now under regulatory oversight.

    • 2020 Security Priorities Report – Priority 1: Data Security

    2. Cloud security

    Cloud security means that organizations can take advantage of automation tools not only for patching and patch management but also to secure code throughout the SDLC. It is clear that cloud will transform how security is performed.

    • 2020 Security Priorities Report – Priority 2: Cloud Security

    3. Email security

    Email security is critical, since email continues to be one of the top points of ingress for cyberattacks from ransomware to business email compromise.

    • 2020 Security Priorities Report – Priority 3: Email Security

    4. Security risk management

    Security risk management requires organizations to make decisions based on their individual risk tolerance on such things as machine learning and IoT devices.

    • 2020 Security Priorities Report – Priority 4: Security Risk Management

    5. Security awareness and training

    Human error continues to be a security issue. In 2020, organizations should tailor their security awareness and training to their people so that they are more secure not only at work but also in life.

    • 2020 Security Priorities Report – Priority 5: Security Awareness and Training
    [infographic]

    Build a Vendor Security Assessment Service

    • Buy Link or Shortcode: {j2store}318|cart{/j2store}
    • member rating overall impact: 9.0/10 Overall Impact
    • member rating average dollars saved: $17,501 Average $ Saved
    • member rating average days saved: 17 Average Days Saved
    • Parent Category Name: Threat Intelligence & Incident Response
    • Parent Category Link: /threat-intelligence-incident-response
    • Vendor security risk management is a growing concern for many organizations. Whether suppliers or business partners, we often trust them with our most sensitive data and processes.
    • More and more regulations require vendor security risk management, and regulator expectations in this area are growing.
    • However, traditional approaches to vendor security assessments are seen by business partners and vendors as too onerous and are unsustainable for information security departments.

    Our Advice

    Critical Insight

    • An efficient and effective assessment process can only be achieved when all stakeholders are participating.
    • Security assessments are time-consuming for both you and your vendors. Maximize the returns on your effort with a risk-based approach.
    • Effective vendor security risk management is an end-to-end process that includes assessment, risk mitigation, and periodic re-assessments.

    Impact and Result

    • Develop an end-to-end security risk management process that includes assessments, risk treatment through contracts and monitoring, and periodic re-assessments.
    • Base your vendor assessments on the actual risks to your organization to ensure that your vendors are committed to the process and you have the internal resources to fully evaluate assessment results.
    • Understand your stakeholder needs and goals to foster support for vendor security risk management efforts.

    Build a Vendor Security Assessment Service Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should build a vendor security assessment service, review Info-Tech’s methodology, and understand the three ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Define governance and process

    Determine your business requirements and build your process to meet them.

    • Build a Vendor Security Assessment Service – Phase 1: Define Governance and Process
    • Vendor Security Policy Template
    • Vendor Security Process Template
    • Vendor Security Process Diagram (Visio)
    • Vendor Security Process Diagram (PDF)

    2. Develop assessment methodology

    Develop the specific procedures and tools required to assess vendor risk.

    • Build a Vendor Security Assessment Service – Phase 2: Develop Assessment Methodology
    • Service Risk Assessment Questionnaire
    • Vendor Security Questionnaire
    • Vendor Security Assessment Inventory

    3. Deploy and monitor process

    Implement the process and develop metrics to measure effectiveness.

    • Build a Vendor Security Assessment Service – Phase 3: Deploy and Monitor Process
    • Vendor Security Requirements Template
    [infographic]

    Workshop: Build a Vendor Security Assessment Service

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Define Governance and Process

    The Purpose

    Understand business and compliance requirements.

    Identify roles and responsibilities.

    Define the process.

    Key Benefits Achieved

    Understanding of key goals for process outcomes.

    Documented service that leverages existing processes.

    Activities

    1.1 Review current processes and pain points.

    1.2 Identify key stakeholders.

    1.3 Define policy.

    1.4 Develop process.

    Outputs

    RACI Matrix

    Vendor Security Policy

    Defined process

    2 Define Methodology

    The Purpose

    Determine methodology for assessing procurement risk.

    Develop procedures for performing vendor security assessments.

    Key Benefits Achieved

    Standardized, repeatable methodologies for supply chain security risk assessment.

    Activities

    2.1 Identify organizational security risk tolerance.

    2.2 Develop risk treatment action plans.

    2.3 Define schedule for re-assessments.

    2.4 Develop methodology for assessing service risk.

    Outputs

    Security risk tolerance statement

    Risk treatment matrix

    Service Risk Questionnaire

    3 Continue Methodology

    The Purpose

    Develop procedures for performing vendor security assessments.

    Establish vendor inventory.

    Key Benefits Achieved

    Standardized, repeatable methodologies for supply chain security risk assessment.

    Activities

    3.1 Develop vendor security questionnaire.

    3.2 Define procedures for vendor security assessments.

    3.3 Customize the vendor security inventory.

    Outputs

    Vendor security questionnaire

    Vendor security inventory

    4 Deploy Process

    The Purpose

    Define risk treatment actions.

    Deploy the process.

    Monitor the process.

    Key Benefits Achieved

    Understanding of how to treat different risks according to the risk tolerance.

    Defined implementation strategy.

    Activities

    4.1 Define risk treatment action plans.

    4.2 Develop implementation strategy.

    4.3 Identify process metrics.

    Outputs

    Vendor security requirements

    Understanding of required implementation plans

    Metrics inventory

    Build a Data Architecture Roadmap

    • Buy Link or Shortcode: {j2store}124|cart{/j2store}
    • member rating overall impact: 8.8/10 Overall Impact
    • member rating average dollars saved: $8,846 Average $ Saved
    • member rating average days saved: 23 Average Days Saved
    • Parent Category Name: Data Management
    • Parent Category Link: /data-management
    • Data architecture involves many moving pieces requiring coordination to provide greatest value from data.
    • Data architects are at the center of this turmoil and must be able to translate high-level business requirements into specific instructions for data workers using complex data models.
    • Data architects must account for the constantly growing data and application complexity, more demanding needs from the business, an ever-increasing number of data sources, and a growing need to integrate components to ensure that performance isn’t compromised.

    Our Advice

    Critical Insight

    • Data architecture needs to evolve with the changing business landscape. There are four common business drivers that put most pressure on archaic architectures. As a result, the organization’s architecture must be flexible and responsive to changing business needs.
    • Data architecture is not just about models. Viewing data architecture as just technical data modeling can lead to structurally unsound data that does not serve the business.
    • Data is used differently across the layers of an organization’s data architecture, and the capabilities needed to optimize use of data change with it. Architecting and managing data from source to warehousing to presentation requires different tactics for optimal use.

    Impact and Result

    • Have a framework in place to identify the appropriate solution for the challenge at hand. Our three-phase practical approach will help you build a custom and modernized data architecture.
      • Identify and prioritize the business drivers in which data architecture changes would create the largest overall benefit, and determine the corresponding data architecture tiers that need to be addressed.
      • Discover the best-practice trends, measure your current state, and define the targets for your data architecture tactics.
      • Build a cohesive and personalized roadmap for restructuring your data architecture. Manage your decisions and resulting changes.

    Build a Data Architecture Roadmap Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why your organization should optimize its data architecture as it evolves with the drivers of the business to get the most from its data.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Prioritize your data architecture with business-driven tactics

    Identify the business drivers that necessitate data architecture improvements, then create a tactical plan for optimization.

    • Build a Business-Aligned Data Architecture Optimization Strategy – Phase 1: Prioritize Your Data Architecture With Business-Driven Tactics
    • Data Architecture Driver Pattern Identification Tool
    • Data Architecture Optimization Template

    2. Personalize your tactics to optimize your data architecture

    Analyze how you stack up to Info-Tech’s data architecture capability model to uncover your tactical plan, and discover groundbreaking data architecture trends and how you can fit them into your action plan.

    • Build a Business-Aligned Data Architecture Optimization Strategy – Phase 2: Personalize Your Tactics to Optimize Your Data Architecture
    • Data Architecture Tactical Roadmap Tool
    • Data Architecture Trends Presentation

    3. Create your tactical data architecture roadmap

    Optimize your data architecture by following tactical initiatives and managing the resulting change brought on by those optimization activities.

    • Build a Business-Aligned Data Architecture Optimization Strategy – Phase 3: Create Your Tactical Data Architecture Roadmap
    • Data Architecture Decision Template
    [infographic]

    Workshop: Build a Data Architecture Roadmap

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Identify the Drivers of the Business for Optimizing Data Architecture

    The Purpose

    Explain approach and value proposition.

    Review the common business drivers and how the organization is driving a need to optimize data architecture.

    Understand Info-Tech’s five-tier data architecture model.

    Determine the pattern of tactics that apply to the organization for optimization.

    Key Benefits Achieved

    Understanding of the current data architecture landscape.

    Priorities for tactical initiatives in the data architecture practice are identified.

    Target state for the data quality practice is defined.

    Activities

    1.1 Explain approach and value proposition.

    1.2 Review the common business drivers and how the organization is driving a need to optimize data architecture.

    1.3 Understand Info-Tech’s five-tier data architecture model.

    1.4 Determine the pattern of tactics that apply to the organization for optimization.

    Outputs

    Five-tier logical data architecture model

    Data architecture tactic plan

    2 Determine Your Tactics For Optimizing Data Architecture

    The Purpose

    Define improvement initiatives.

    Define a data architecture improvement strategy and roadmap.

    Key Benefits Achieved

    Gaps, inefficiencies, and opportunities in the data architecture practice are identified.

    Activities

    2.1 Create business unit prioritization roadmap.

    2.2 Develop subject area project scope.

    2.3 Subject area 1: data lineage analysis, root cause analysis, impact assessment, business analysis

    Outputs

    Business unit prioritization roadmap

    Subject area scope

    Data lineage diagram

    3 Create a Strategy for Data Quality Project 2

    The Purpose

    Define improvement initiatives.

    Define a data quality improvement strategy and roadmap.

    Key Benefits Achieved

    Improvement initiatives are defined.

    Improvement initiatives are evaluated and prioritized to develop an improvement strategy.

    A roadmap is defined to depict when and how to tackle the improvement initiatives.

    Activities

    3.1 Create business unit prioritization roadmap.

    3.2 Develop subject area project scope.

    3.3 Subject area 1: data lineage analysis, root cause analysis, impact assessment, business analysis.

    Outputs

    Business unit prioritization roadmap

    Subject area scope

    Data lineage diagram

    Further reading

    Build a Data Architecture Roadmap

    Optimizing data architecture requires a plan, not just a data model.

    ANALYST PERSPECTIVE

    Integral to an insight-driven enterprise is a modern and business-driven data environment.

    “As business and data landscapes change, an organization’s data architecture needs to be able to keep pace with these changes. It needs to be responsive so as to not only ensure the organization continues to operate efficiently but that it supports the overall strategic direction of the organization.

    In the dynamic marketplace of today, organizations are constantly juggling disruptive forces and are finding the need to be more proactive rather than reactive. As such, organizations are finding their data to be a source of competitive advantage where the data architecture has to be able to not only support the increasing amount, sources, and rate at which organizations are capturing and collecting data but also be able to meet and deliver on changing business needs.

    Data architecture optimization should, therefore, aid in breaking down data silos and creating a more shared and all-encompassing data environment for better empowering the business.” (Crystal Singh, Director, Research, Data and Information Practice, Info-Tech Research Group)

    Our understanding of the problem

    This Research Is Designed For:
    • Data architects or their equivalent, looking to optimize and improve the efficiency of the capture, movement and storage of data for a variety of business drivers.
    • Enterprise architects looking to improve the backbone of the holistic approach of their organization’s structure.
    This Research Will Help You:
    • Identify the business drivers that are impacted and improved by best-practice data architecture.
    • Optimize your data architecture using tactical practices to address the pressing issues of the business to drive modernization.
    • Align the organization’s data architecture with the grander enterprise architecture.
    This Research Will Also Assist:
    • CIOs concerned with costs, benefits, and the overall structure of their organizations data flow.
    • Database administrators tasked with overseeing crucial elements of the data architecture.
    This Research Will Help Them:
    • Get a handle on the current situation of data within the organization.
    • Understand how data architecture affects the operations of the data sources within the enterprise.

    Executive summary

    Situation

    • The data architecture of a modern organization involves many moving pieces requiring coordination to provide greatest value from data.
    • Data architects are at the center of this turmoil and must be able to translate high-level business requirements into specific instructions for data workers using complex data models.

    Complication

    • Data architects must account for the constantly growing data and application complexity, and more demanding needs from the business.
    • There is an ever-increasing number of data sources and a growing need to integrate components to ensure that performance isn’t compromised.
    • There isn’t always a clearly defined data architect role, yet the responsibilities must be filled to get maximum value from data.

    Resolution

    • To deal with these challenges, a data architect must have a framework in place to identify the appropriate solution for the challenge at hand.
      • Identify and prioritize the business drivers in which data architecture changes would create the largest overall benefit, and determine the corresponding data architecture tiers that need to be addressed to customize your solution.
      • Discover the best practice trends, measure your current state, and define the targets for your data architecture tactics.
      • Build a cohesive and personalized roadmap for restructuring your data architecture. Manage your decisions and resulting changes.

    Info-Tech Insight

    1. Data architecture is not just about models. Viewing data architecture as just technical data modeling can lead to a data environment that does not aptly serve or support the business. Identify the priorities of your business and adapt your data architecture to those needs.
    2. Changes to data architecture are typically driven by four common business driver patterns. Use these as a shortcut to understand how to evolve your data architecture.
    3. Data is used differently across the layers of an organization’s data architecture; therefore, the capabilities needed to optimize the use of data change with it. Architecting and managing data from source to warehousing to presentation requires different tactics for optimal use.

    Your data is the foundation of your organization’s knowledge and ability to make decisions

    Data should be at the foundation of your organization’s evolution.

    The transformational insights that executives are constantly seeking to leverage can be uncovered with a data practice that makes high quality, trustworthy information readily available to the business users who need it.

    50% Organizations that embrace data are 50% more likely to launch products and services ahead of their competitors. (Nesta, 2016)

    Whether hoping to gain a better understanding of your business or trying to become an innovator in your industry, any organization can get value from its data regardless of where you are in your journey to becoming a data-driven enterprise:

    Business Monitoring
    • Data reporting
    • Uncover inefficiencies
    • Monitor progress
    • Track inventory levels
    Business Insights
    • Data analytics
    • Expose patterns
    • Predict future trends
    Business Optimization
    • Data-based apps
    • Build apps to automate actions based on insights
    Business Transformation
    • Monetary value of data
    • Create new revenue streams
    (Journey to Data Driven Enterprise, 2015)

    As organizations seek to become more data driven, it is imperative to better manage data for its effective use

    Here comes the zettabyte era.

    A zettabyte is a billion terabytes. Organizations today need to measure their data size in zettabytes, a challenge that is only compounded by the speed at which the data is expected to move.

    Arriving at the understanding that data can be the driving force of your organization is just the first step. The reality is that the true hurdles to overcome are in facing the challenges of today’s data landscape.

    Challenges of The Modern Data Landscape
    Data at rest Data movement
    Greater amounts Different types Uncertain quality Faster rates Higher complexity

    “The data environment is very chaotic nowadays. Legacy applications, data sprawl – organizations are grappling with what their data landscape looks like. Where are our data assets that we need to use?” (Andrew Johnston, Independent Consultant)

    Solution

    Well-defined and structured data management practices are the best way to mitigate the limitations that derive from these challenges and leverage the most possible value from your data.

    Refer to Info-Tech’s capstone Create a Plan For Establishing a Business-Aligned Data Management Practice blueprint to understand data quality in the context of data disciplines and methods for improving your data management capabilities.

    Data architecture is an integral aspect of data management

    Data Architecture

    The set of rules, policies, standards, and models that govern and define the type of data collected and how it is used, stored, managed, and integrated within the organization and its database systems.

    In general, the primary objective of data architecture is the standardization of data for the benefit of the organization.

    54% of leading “analytics-driven” enterprises site data architecture as a required skill for data analytics initiatives. (Maynard 2015)

    MYTH

    Data architecture is purely a model of the technical requirements of your data systems.

    REALITY

    Data architecture is largely dependent on a human element. It can be viewed as “the bridge between defining strategy and its implementation”. (Erwin 2016)

    Functions

    A strong data architecture should:

    • Define, visualize, and communicate data strategy to various stakeholders.
    • Craft a data delivery environment.
    • Ensure high data quality.
    • Provide a roadmap for continuous improvement.

    Business value

    A strong data architecture will help you:

    • Align data processes with business strategy and the overall holistic enterprise architecture.
    • Enable efficient flow of data with a stronger focus on quality and accessibility.
    • Reduce the total cost of data ownership.

    Data architects must maintain a comprehensive view of the organization’s rapidly proliferating data

    The data architect:
    • Acts as a “translator” between the business and data workers to communicate data and technology requirements.
    • Facilitates the creation of the data strategy.
    • Manages the enterprise data model.
    • Has a greater knowledge of operational and analytical data use cases.
    • Recommends data management policies and standards, and maintains data management artifacts.
    • Reviews project solution architectures and identifies cross impacts across the data lifecycle.
    • Is a hands-on expert in data management and warehousing technologies.
    • Is not necessarily it’s own designated position, but a role that can be completed by a variety of IT professionals.

    Data architects bridge the gap between strategic and technical requirements:

    Visualization centering the 'Data Architect' as the bridge between 'Data Workers', 'Business', and 'Data & Applications'.

    “Fundamentally, the role of a data architect is to understand the data in an organization at a reasonable level of abstraction.” (Andrew Johnston, Independent Consultant)

    Many are experiencing the pains of poor data architecture, but leading organizations are proactively tackling these issues

    Outdated and archaic systems and processes limit the ability to access data in a timely and efficient manner, ultimately diminishing the value your data should bring.

    59%

    of firms believe their legacy storage systems require too much processing to meet today’s business needs. (Attivio, Survey Big Data decision Makers, 2016)

    48%

    of companies experience pains from being reliant on “manual methods and trial and error when preparing data.” (Attivio, Survey Big Data decision Makers, 2016)

    44%
    +
    22%

    44% of firms said preparing data was their top hurdle for analytics, with 22% citing problems in accessing data. (Data Virtualization blog, Data Movement Killed the BI Star, 2016)

    Intuitive organizations who have recognized these shortcomings have already begun the transition to modernized and optimized systems and processes.

    28%

    of survey respondents say they plan to replace “data management and architecture because it cannot handle the requirements of big data.” (Informatica, Digital Transformation: Is Your Data Management Ready, 2016)

    50%

    Of enterprises plan to replace their data warehouse systems and analytical tools in the next few years. (TDWI, End of the Data Warehouse as we know it, 2017)

    Leading organizations are attacking data architecture problems … you will be left behind if you do not start now!

    Once on your path to redesigning your data architecture, neglecting the strategic elements may leave you ineffective

    Focusing on only data models without the required data architecture guidance can cause harmful symptoms in your IT department, which will lead to organization-wide problems.

    IT Symptoms Due to Ineffective Data Architecture

    Poor Data Quality

    • Inconsistent, duplicate, missing, incomplete, incorrect, unstandardized, out of date, and mistake-riddled data can plague your systems.

    Poor Accessibility

    • Delays in accessing data.
    • Limits on who can access data.
    • Limited access to data remotely.

    Strategic Disconnect

    • Disconnect between owner and consumer of data.
    • Solutions address narrow scope problems.
    • System barriers between departments.
    Leads to Poor Organizational Conditions

    Inaccurate Insights

    • Inconsistent and/or erroneous operational and management reports.
    • Ineffective cross-departmental use of analytics.

    Ineffective Decision Making

    • Slow flow of information to executive decision makers.
    • Inconsistent interpretation of data or reports.

    Inefficient Operations

    • Limits to automated functionality.
    • Increased divisions within organization.
    • Regulatory compliance violations.
    You need a solution that will prevent the pains.

    Follow Info-Tech’s methodology to optimize data architecture to meet the business needs

    The following is a summary of Info-Tech’s methodology:

    1

    1. Prioritize your core business objectives and identify your business driver.
    2. Learn how business drivers apply to specific tiers of Info-Tech’s five-tier data architecture model.
    3. Determine the appropriate tactical pattern that addresses your most important requirements.
    Visualization of the process described on the left: Business drivers applying to Info-Tech's five-tier data architecture, then determining tactical patterns, and eventually setting targets of your desired optimized state.

    2

    1. Select the areas of the five-tier architecture to focus on.
    2. Measure current state.
    3. Set the targets of your desired optimized state.

    3

    1. Roadmap your tactics.
    2. Manage and communicate change.
    A roadmap leading to communication.

    Info-Tech will get you to your optimized state faster by focusing on the important business issues

    First Things First

    1. Info-Tech’s methodology helps you to prioritize and establish the core strategic objectives behind your goal of modernizing data architecture. This will narrow your focus to the appropriate areas of your current data systems and processes that require the most attention.

    Info-Tech has identified these four common drivers that lead to the need to optimize your data architecture.

    • Becoming More Data Driven
    • Regulations and Compliance
    • Mergers and Acquisitions
    • New Functionality or Business Rule

    These different core objectives underline the motivation to optimize data architecture, and will determine your overall approach.

    Use the five-tier architecture to provide a consumable view of your data architecture

    Every organization’s data system requires a unique design and an assortment of applications and storage units to fit their business needs. Therefore, it is difficult to paint a picture of an ideal model that has universal applications. However, when data architecture is broken down in terms of layers or tiers, there exists a general structure that is seen in all data systems.

    Info-Tech's Five Tier Data Architecture. The five tiers being 'Sources' which includes 'Apps', 'Excel and other documents', and 'Access database(s)'; 'Integration and Translation' the 'Movement and transformation of data'; 'Warehousing' which includes 'Data Lakes & Warehouse(s) (Raw Data)'; 'Analytics' which includes 'Data Marts', 'Data Cube', 'Flat Files', and 'BI Tools'; and 'Presentation' which includes 'Reports' and 'Dashboards'.

    Thinking of your data systems and processes in this framework will allow you to see how different elements of the architecture relate to specific business operations.

    1. This blueprint will demonstrate how the business driver behind your redesign requires you to address specific layers of the five-tier data architecture.
    1. Once you’ve aligned your business driver to the appropriate data tiers, this blueprint will provide you with the best practice tactics you should apply to achieve an optimized data architecture.

    Use the five-tier architecture to prioritize tactics to improve your data architecture in line with your pattern

    Info-Tech’s Data Architecture Capability Model
    Info-Tech’s Data Architecture Capability Model featuring the five-tier architecture listing 'Core Capabilities' and 'Advanced Capabilities' within each tier, and a list of 'Cross Capabilities' which apply to all tiers.
    1. Based on your business driver, the relevant data tiers, and your organization’s own specific requirements you will need to establish the appropriate data architecture capabilities.
    2. This blueprint will help you measure how you are currently performing in these capabilities…
    3. And help you define and set targets so you can reach your optimized state.
    1. Once completed, these steps will be provided with the information you will need to create a comprehensive roadmap.
    2. Lastly, this blueprint will provide you with the tools to communicate this plan across your organization and offer change management guidelines to ensure successful adoption.
    Info-Tech Insight

    Optimizing data architecture requires a tactical approach, not a passive approach.

    The demanding task of optimization requires the ability to heavily prioritize. After you have identified why, determine how using our pre-built roadmap to address the four common drivers.

    Do not forget: data architecture is not a standalone concept; it fits into the more holistic design of enterprise architecture

    Data Architecture in Alignment

    Data architecture can not be designed to simply address the focus of data specialists or even the IT department.

    It must act as a key component in the all encompassing enterprise architecture and reflect the strategy and design of the entire business.

    Data architecture collaborates with application architecture in the delivery of effective information systems, and informs technology architecture on data related infrastructure requirements/considerations

    Please refer to the following blueprints to see the full picture of enterprise architecture:

    A diagram titled 'Enterprise Architecture' with multiple forms of architecture interacting with each other. At the top is 'Business Architecture' which feeds into 'Data Architecture' and 'Application Architecture' which feed into each other, and influence 'Infrastructure Architecture' and 'Security Architecture'.
    Adapted from TOGAF
    Refer to Phase C of TOGAF and Bizbok for references to the components of business architecture that are used in data architecture.

    Info-Tech’s data architecture optimization methodology helped a monetary authority fulfill strict regulatory pressures

    CASE STUDY

    Industry: Financial
    Source: Info-Tech Consulting
    Symbol for 'Monetary Authority Case Study'. Look for this symbol as you walk through the blueprint for details on how Info-Tech Consulting assisted this monetary authority.

    Situation: Strong external pressures required the monetary authority to update and optimize its data architecture.

    The monetary authority is responsible for oversight of the financial situation of a country that takes in revenue from foreign incorporation. Due to increased pressure from international regulatory bodies, the monetary authority became responsible for generating multiple different types of beneficial ownership reports based on corporation ownership data within 24 hours of a request.

    A stale and inefficient data architecture prevented the monetary authority from fulfilling external pressures.

    Normally, the process to generate and provide beneficial ownership reports took a week or more. This was due to multiple points of stale data architecture, including a dependence on outdated legacy systems and a broken process for gathering the required data from a mix of paper and electronic sources.

    Provide a structured approach to solving the problem

    Info-Tech helped the monetary authority identify the business need that resulted from regulatory pressures, the challenges that needed to be overcome, and actionable tactics for addressing the needs.

    Info-Tech’s methodology was followed to optimize the areas of data architecture that address the business driver.

    • External Requirements
    • Business Driver
        Diagnose Data Architecture Problems
      • Outdated architecture (paper, legacy systems)
      • Stale data from other agencies
      • Incomplete data
          Data Architecture Optimization Tactics
        1. Optimized Source Databases
        2. Improved Integration
        3. Data Warehouse Optimization
        4. Data Marts for Reports
        5. Report Delivery Efficiency

    As you walk through this blueprint, watch for additional case studies that walk through the details of how Info-Tech helped this monetary authority.

    This blueprint’s three-step process will help you optimize data architecture in your organization

    Phase 1
    Prioritize Your Data Architecture With Business-Driven Tactics
    Phase 2
    Personalize Your Tactics to Optimize Your Data Architecture
    Phase 3
    Create Your Tactical Data Architecture Roadmap
    Step 1: Identify Your Business Driver for Optimizing Data Architecture
    • Learn about what data architecture is and how it must evolve with the drivers of the business.
    • Determine the business driver that your organization is currently experiencing.
    • Data Architecture Driver Pattern Identification Tool

    Step 2: Determine Actionable Tactics to Optimize Data Architecture
    • Create your data architecture optimization plan to determine the high-level tactics you need to follow.
    • Data Architecture Optimization Template

    Step 1: Measure Your Data Architecture Capabilities
    • Determine where you currently stand in the data architecture capabilities across the five-tier data architecture.
    • Data Architecture Tactical Roadmap Tool

    Step 2: Set a Target for Data Architecture Capabilities
    • Identify your targets for the data architecture capabilities.
    • Data Architecture Tactical Roadmap Tool

    Step 3: Identify the Tactics that Apply to Your Organization
    • Understand the trends in the field of data architecture and how they can help to optimize your environment.
    • Data Architecture Trends Presentation

    Step 1: Personalize Your Data Architecture Roadmap
    • Personalize the tactics across the tiers that apply to you to build your personalized roadmap.
    • Data Architecture Tactical Roadmap Tool

    Step 2: Manage Your Data Architecture Decisions and the Resulting Changes
    • Document the changes in the organization’s data architecture.
    • Data architecture involves change management – learn how data architects should support change management in the organization.
    • Data Architecture Decision Template

    Use these icons to help direct you as you navigate this research

    Use these icons to help guide you through each step of the blueprint and direct you to content related to the recommended activities.

    A small monochrome icon of a wrench and screwdriver creating an X.

    This icon denotes a slide where a supporting Info-Tech tool or template will help you perform the activity or step associated with the slide. Refer to the supporting tool or template to get the best results and proceed to the next step of the project.

    A small monochrome icon depicting a person in front of a blank slide.

    This icon denotes a slide with an associated activity. The activity can be performed either as part of your project or with the support of Info-Tech team members, who will come onsite to facilitate a workshop for your organization.

    Info-Tech offers various levels of support to best suit your needs

    DIY Toolkit

    Guided Implementation

    Workshop

    Consulting

    "Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful." "Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track." "We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place." "Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project."

    Diagnostics and consistent frameworks used throughout all four options

    Build a Business-Aligned Data Architecture Optimization Strategy – project overview

    PHASE 1
    Prioritize Your Data Architecture With Business-Driven Tactics
    PHASE 2
    Personalize Your Tactics to Optimize Your Data Architecture
    PHASE 3
    Create Your Tactical Data Architecture Roadmap
    Supporting Tool icon

    Best-Practice Toolkit

    1.1 Identify Your Business Driver for Optimizing Data Architecture

    1.2 Determine Actionable Tactics to Optimize Data Architecture

    2.1 Measure Your Data Architecture Capabilities

    2.2 Set a Target for Data Architecture Capabilities

    2.3 Identify the Tactics that Apply to Your Organization

    3.1 Personalize Your Data Architecture Roadmap

    3.2 Manage Your Data Architecture Decisions and the Resulting Changes

    Guided Implementations

    • Understand what data architecture is, how it aligns with enterprise architecture, and how data architects support the needs of the business.
    • Identify the business drivers that necessitate the optimization of the organization’s data architecture.
    • Create a tactical plan to optimize data architecture across Info-Tech’s five-tier logical data architecture model.
    • Understand Info-Tech’s tactical data architecture capability model and measure the current state of these capabilities at the organization.
    • Determine the target state of data architecture capabilities.
    • Understand the trends in the field of data architecture and identify how they can fit into your environment.
    • Use the results of the data architecture capability gap assessment to determine the priority of activities to populate your personalized data architecture optimization roadmap.
    • Understand how to manage change as a data architect or equivalent.
    Associated Activity icon

    Onsite Workshop

    Module 1:
    Identify the Drivers of the Business for Optimizing Data Architecture
    Module 2:
    Create a Tactical Plan for Optimizing Data Architecture
    Module 3:
    Create a Personalized Roadmap for Data Architecture Activities

    Workshop overview

    Contact your account representative or email Workshops@InfoTech.com for more information.

    Preparation

    Workshop Day 1

    Workshop Day 2

    Workshop Day 3

    Workshop Day 4

    Workshop Day 5

    Organize and Plan Workshop Identify the Drivers of the Business for Optimizing Data Architecture Determine the Tactics For Optimizing Data Architecture Create Your Roadmap of Optimization Activities Create Your Personalized Roadmap Create a Plan for Change Management

    Morning Activities

    • Finalize workshop itinerary and scope.
    • Identify workshop participants.
    • Gather strategic documentation.
    • Engage necessary stakeholders.
    • Book interviews.
    • 1.1 Explain approach and value proposition.
    • 1.2 Review the common business drivers and how the organization is driving a need to optimize data architecture.
    • 2.1 Create your data architecture optimization plan.
    • 2.2 Interview key business stakeholders for input on business drivers for data architecture.
    • 3.1 Align with the enterprise architecture by interviewing the enterprise architect for input on the data architecture optimization roadmap.
    • 4.1 As a group, determine the roadmap activities that are applicable to your organization and brainstorm applicable initiatives.
    • 5.1 Use the Data Architecture Decision Documentation Template to document key decisions and updates.

    Afternoon Activities

    • 1.3 Understand Info-Tech’s Five-Tier Data Architecture.
    • 1.4 Determine the pattern of tactics that apply to the organization for optimization.
    • 2.3 With input from the business and enterprise architect, determine the current data architecture capabilities.
    • 3.3 With input from the business and enterprise architect, determine the target data architecture capabilities.
    • 4.2 Determine the timing and effort of the roadmap activities.
    • 5.2 Review best practices for change management.
    • 5.3 Present roadmap and findings to the business stakeholders and enterprise architect.

    Deliverables

    • Workshop Itinerary
    • Workshop Participant List
    1. Five-Tier Logical Data Architecture Model
    2. Data Architecture Tactic Plan
    1. Five-Tier Data Architecture Capability Model
    1. Data Architecture Tactical Roadmap
    1. Data Architecture Tactical Roadmap
    1. Data Architecture Decision Template

    Build a Business-Aligned Data Architecture Optimization Strategy

    PHASE 1

    Prioritize Your Data Architecture With Business-Driven Tactics

    Phase 1 outline

    Associated Activity icon Call 1-888-670-8889 or email GuidedImplementations@InfoTech.com for more information.

    Complete these steps on your own, or call us to complete a guided implementation. A guided implementation is a series of 2-3 advisory calls that help you execute each phase of a project. They are included in most advisory memberships.

    Guided Implementation 1: Prioritize Your Data Architecture With Business-Driven Tactics

    Proposed Time to Completion: 2 weeks
    Step 1.1: Identify Your Business Driver for Optimizing Data Architecture Step 1.2: Determine Actionable Tactics to Optimize Data Architecture
    Start with an analyst kick-off call:
    • Understand what data architecture is, what it is not, and how it fits into the broader enterprise architecture program.
    • Determine the drivers that fuel the need for data architecture optimization.
    Review findings with analyst:
    • Understand the Five-Tier Data Architecture Model and how the drivers of the business inform your priorities across this logical model of data architecture.
    Then complete these activities…
    • Complete the Data Architecture Driver Pattern Identification Tool.
    Then complete these activities…
    • Create a tactical data architecture optimization plan based on the business driver input.
    With these tools & templates:
    • Data Architecture Driver Pattern Identification Tool
    With these tools & templates:
    • Data Architecture Optimization Template

    Phase 1 Results & Insights

    • Data Architecture is not just about data models. The approach that Phase 1 guides you through will help to not only plan where you need to focus your efforts as a data architect (or equivalent) but also give you guidance in how you should go about optimizing the holistic data architecture environment based on the drivers of the business.

    Phase 1 will help you create a strategy to optimize your data architecture using actionable tactics

    In this phase, you will determine your focus for optimizing your data architecture based on the business drivers that are commonly felt by most organizations.

    1. Identify the business drivers that necessitate data architecture optimization efforts.
    2. Understand Info-Tech’s Five-Tier Data Architecture, a logical architecture model that will help you prioritize tactics for optimizing your data architecture environment.
    3. Identify tactics for optimizing the organization’s data architecture across the five tiers.

    “To stay competitive, we need to become more data-driven. Compliance pressures are becoming more demanding. We need to add a new functionality.”

    Info-Tech’s Five-Tier Data Architecture:

    1. Data Sources
    2. Data Integration and Translation
    3. Data Warehousing
    4. Data Analytics
    5. Data Presentation

    Tactical plan for Data Architecture Optimization

    Phase 1, Step 1: Identify Your Business Driver for Optimizing Data Architecture

    PHASE 1

    1.1 1.2
    Identify Your Business Driver for Optimizing Data Architecture Determine Actionable Tactics to Optimize Data Architecture

    This step will walk you through the following activities:

    • Understand how data architecture fits into the organization’s larger enterprise architecture.
    • Understand what data architecture is and how it should be driven by the business.
    • Identify the driver that is creating a need for data architecture optimization.

    This step involves the following participants:

    • Data Architect
    • Enterprise Architect

    Outcomes of this step

    • A starting point for the many responsibilities of the data architect role. Balancing business and technical requirements can be challenging, and to do so you need to first understand what is driving the need for data architecture improvements.
    • Holistic understanding of the organization’s architecture environment, including enterprise, application, data, and technology architectures and how they interact.

    Data architecture involves planning, communication, and understanding of technology

    Data Architecture

    A description of the structure and interaction of the enterprise’s major types and sources of data, logical data assets, physical data assets, and data management resources (TOGAF 9).

    The subject area of data management that defines the data needs of the enterprise and designs the master blueprints to meet those needs (DAMA DMBOK, 2009).

    IBM (2007) defines data architecture as the design of systems and applications that facilitate data availability and distribution across the enterprise.

    Definitions vary slightly across major architecture and management frameworks.

    However, there is a general consensus that data architecture provides organizations with:

    • Alignment
    • Planning
    • Road mapping
    • Change management
    • A guide for the organization’s data management program

    Data architecture must be based on business goals and objectives; developed within the technical strategies, constraints, and opportunities of the organization in support of providing a foundation for data management.

    Current Data Management
    • Alignment
    • Planning
    • Road mapping
    Goal for Data Management

    Info-Tech Insight

    Data Architecture is not just data models. Data architects must understand the needs of the business, as well as the existing people and processes that already exist in the organization to effectively perform their job.

    Review how data architecture fits into the broader architectural context

    A flow diagram starting with 'Business Processes/Activities' to 'Business Architecture' which through a process of 'Integration' flows to 'Data Architecture' and 'Application Architecture', the latter of which also flows into to the former, and they both flow into 'Technology Architecture' which includes 'Infrastructure' and 'Security'.

    Each layer of architecture informs the next. In other words, each layer has components that execute processes and offer services to the next layer. For example, data architecture can be broken down into more granular activities and processes that inform how the organization’s technology architecture should be arranged.

    Data does not exist on its own. It is informed by business architecture and used by other architectural domains to deliver systems, IT services, and to support business processes. As you build your practice, you must consider how data fits within the broader architectural framework.

    The Zachman Framework is a widely used EA framework; within it, data is identified as the first domain.

    The framework aims to standardize artifacts (work-products) within each architectural domain, provides a cohesive view of the scope of EA and clearly delineates data components. Use the framework to ensure that your target DA practice is aligned to other domains within the EA framework.

    'The Zachman Framework for Enterprise Architecture: The Enterprise Ontology', a complicated framework with top and bottom column headers and left and right row headers. Along the top are 'Classification Names': 'What', 'How', 'Where', 'Who', 'When', and 'Why'. Along the bottom are 'Enterprise Names': 'Inventory Sets', 'Process Flows', 'Distribution Networks', 'Responsibility Assignments', 'Timing Cycles', and 'Motivation Intentions'. Along the left are 'Audience Perspectives': 'Executive Perspective', 'Business Mgmt. Perspective', 'Architect Perspective', 'Engineer Perspective', 'Technician Perspective', and 'Enterprise Perspective'. Along the right are 'Model Names': 'Scope Contexts', 'Business Concepts', 'System Logic', 'Technology Physics', 'Tool Components', and 'Operations Instances'.
    (Source: Zachman International)

    Data architects operate in alignment with the other various architecture groups

    Data architects operate in alignment with the other various architecture groups, with coordination from the enterprise architect.

    Enterprise Architect
    The enterprise architect provides thought leadership and direction to domain architects.

    They also maintain architectural standards across all the architectural domains and serve as a lead project solution architect on the most critical assignments.

    • Business Architect
      A business subject matter expert who works with the line-of-business team to assist in business planning through capability-based planning.
    • Security Architect
      Plays a pivotal role in formulating the security strategy of the organization, working with the business and CISO/security manager. Recommends and maintains security standards, policies, and best practices.
    • Infrastructure Architect
      Recommends and maintains standards across the compute, storage, and network layers of the organization. Reviews project solution architectures to ensure compliance with infrastructure standards, regulations, and target state blueprints.
    • Application Architect
      Manages the business effectiveness, satisfaction, and maintainability of the application portfolio. Conduct application architecture assessments to document expected quality attribute standards, identify hotspots, and recommend best practices.
    • Data Architect
      Facilitates the creation of data strategy and has a greater understanding of operational and analytical data use cases. Manages the enterprise data model which includes all the three layers of modelling - conceptual, logical, and physical. Recommends data management policies and standards, and maintains data management artefacts. Reviews project solution architectures and identifies cross impacts across the data lifecycle.

    As a data architect, you must maintain balance between the technical and the business requirements

    The data architect role is integral to connecting the long-term goals of the business with how the organization plans to manage its data for optimal use.

    Data architects need to have a deep experience in data management, data warehousing, and analytics technologies. At a high level, the data architect plans and implements an organization’s data, reporting, and analytics roadmap.

    Some of the role’s primary duties and responsibilities include:

    1. Data modeling
    2. Reviewing existing data architecture
    3. Benchmark and improve database performance
    4. Fine tune database and SQL queries
    5. Lead on ETL activities
    6. Validate data integrity across all platforms
    7. Manage underlying framework for data presentation layer
    8. Ensure compliance with proper reporting to bureaus and partners
    9. Advise management on data solutions

    Data architects bridge the gap between strategic and technical requirements:

    Visualization centering the 'Data Architect' as the bridge between 'Data Workers', 'Business', and 'Data & Applications'.

    “Fundamentally, the role of a data architect is to understand the data in an organization at a reasonable level of abstraction.” (Andrew Johnston, Independent Consultant)

    Info-Tech Insight

    The data architect role is not always clear cut. Many organizations do not have a dedicated data architect resource, and may not need one. However, the duties and responsibilities of the data architect must be carried out to some degree by a combination of resources as appropriate to the organization’s size and environment.

    Understand the role of a data architect to ensure that essential responsibilities are covered in the organization

    A database administrator (DBA) is not a data architect, and data architecture is not something you buy from an enterprise application vendor.

    Data Architect Role Description

    • The data architect must develop (along with the business) a short-term and long-term vision for the enterprise’s data architecture.
    • They must be able to create processes for governing the identification, collection, and use of accurate and valid metadata, as well as for tracking data quality, completeness, and redundancy.
    • They need to create strategies for data security, backup, disaster recovery, business continuity, and archiving, and ensure regulatory compliance.

    Skills Necessary

    • Hands-on experience with data architecting and management, data mining, and large-scale data modeling.
    • Strong understanding of relational and non-relational data structures, theories, principles, and practices.
    • Strong familiarity with metadata management.
    • Knowledge of data privacy practices and laws.

    Define Policies, Processes, and Priorities

    • Policies
      • Boundaries of the data architecture.
      • Data architecture standards.
      • Data architecture security.
      • Responsibility of ownership for the data architecture and data repositories.
      • Responsibility for data architecture governance.
    • Processes
      • Data architecture communication.
      • Data architecture change management.
      • Data architecture governance.
      • Policy compliance monitoring.
    • Priorities
      • Align architecture efforts with business priorities.
      • Close technology gaps to meet service level agreements (SLAs).
      • Determine impacts on current or future projects.

    See Info-Tech’s Data Architect job description for a comprehensive description of the data architect role.

    Leverage data architecture frameworks to understand how the role fits into the greater Enterprise Architecture framework

    Enterprise data architectures are available from industry consortiums such as The Open Group (TOGAF®), and open source initiatives such as MIKE2.0.

    Logo for The Open Group.

    The Open Group TOGAF enterprise architecture model is a detailed framework of models, methods, and supporting tools to create an enterprise-level architecture.

    • TOGAF was first developed in 1995 and was based on the Technical Architecture Framework for Information Management (TAFIM) developed by the US Department of Defense.
    • TOGAF includes application, data, and infrastructure architecture domains providing enterprise-level, product-neutral architecture principles, policies, methods, and models.
    • As a member of The Open Group, it is possible to participate in ongoing TOGAF development initiatives.

    The wide adoption of TOGAF has resulted in the mapping of it to several other industry standards including CoBIT and ITIL.

    Logo for MIKE2.0.

    MIKE2.0 (Method for an Integrated Knowledge Environment), is an open source method for enterprise information management providing a framework for information development.

    • SAFE (Strategic Architecture for the Federated Enterprise) provides the technology solution framework for MIKE2.0
    • SAFE includes application, presentation, information, data, Infrastructure, and metadata architecture domains.

    Info-Tech Best Practice

    If an enterprise-level IT architecture is your goal, TOGAF is likely a better model. However, if you are an information and knowledge-based business then MIKE2.0 may be more relevant to your business.

    The data architect must identify what drives the need for data from the business to create a business-driven architecture

    As the business landscape evolves, new needs arise. An organization may undergo new compliance requirements, or look to improve their customer intimacy, which could require a new functionality from an application and its associated database.

    There are four common scenarios that lead to an organization’s need to optimize its data architecture and these scenarios all present unique challenges for a data architect:

    1. Becoming More Data Driven As organizations are looking to get more out of their data, there is a push for more accurate and timely data from applications. Data-driven decision making requires verifiable data from trustworthy sources. Result: Replace decisions made on gut or intuition with real and empirical data - make more informed and data-driven decisions.
    2. New Functionality or Business Rule In order to succeed as business landscapes change, organizations find themselves innovating on products or services and the way they do things. Changes in business rules, product or service offering, and new functionalities can subsequently demand more from the existing data architecture. Result: Prepare yourself to successfully launch new business initiatives with an architecture that supports business needs.
    3. Mergers and Acquisitions If an organization has recently acquired, been acquired, or is merging with another, the technological implications require careful planning to ensure a seamless fit. Application consolidation, retirement, data transfer, and integration points are crucial. Result: Leverage opportunities to incorporate and consolidate new synergistic assets to realize the ROI.
    4. Risk and Compliance Data in highly regulated organizations needs to be kept safe and secure. Architectural decisions around data impact the level of compliance within the organization. Result: Avoid the fear of data audits, regulatory violations, and privacy breaches.

    Info-Tech Best Practice

    These are not the only reasons why data architects need to optimize the organization’s data architecture. These are only four of the most common scenarios, however, other business needs can be addressed using the same concept as these four common scenarios.

    Use the Data Architecture Driver tool to identify your focus for data architecture

    Supporting Tool icon 1.1 Data Architecture Driver Pattern Identification Tool

    Follow Info-Tech’s process of first analyzing the needs of the business, then determining how best to architect your data based on these drivers. Data architecture needs to be able to rapidly evolve to support the strategic goals of the business, and the Data Architecture Driver Pattern Identification Tool will help you to prioritize your efforts to best do this.

    Tab 2. Driver Identification

    Objective: Objectively assess the most pressing business drivers.

    Screenshot of the Data Architecture Driver Pattern Identification Tool, tab 2.

    Tab 3. Tactic Pattern Plan, Section 1

    Purpose: Review your business drivers that require architectural changes in your environment.

    Screenshot of the Data Architecture Driver Pattern Identification Tool, tab 3, section 1.

    Tab 3. Tactic Pattern Plan, Section 2

    Purpose: Determine a list of tactics that will help you address the business drivers.

    Screenshot of the Data Architecture Driver Pattern Identification Tool, tab 3, section 2.

    Step
    • Evaluate business drivers to determine the data architecture optimization priorities and tactics.
    Step
    • Understand how each business driver relates to data architecture and how each driver gives rise to a specific pattern across the five-tier data architecture.
    Step
    • Review the list of high-level tactics presented to optimize your data architecture across the five tier architecture.

    Identify the drivers for improving your data architecture

    Associated Activity icon 1.1.1 1 hour

    INPUT: Data Architecture Driver tool assessment prompts.

    OUTPUT: Identified business driver that applies to your organization.

    Materials: Data Architecture Driver Pattern Identification Tool

    Participants: Data architect, Enterprise architect

    Instructions

    In Tab 2. Driver Identification of the Data Architecture Driver Pattern Identification Tool, assess the degree to which the organization is feeling the pains of the four most common business drivers:

    1. Is there a present or growing need for the business to be making data-driven decisions?
    2. Does the business want to explore a new functionality and hence require a new application?
    3. Is your organization acquiring or merging with another entity?
    4. Is your organization’s regulatory environment quick to change and require stricter reporting?

    Data architecture improvements need to be driven by business need.

    Screenshot of the Data Architecture Driver Pattern Identification Tool, tab 2 Driver Identification.
    Tab 2. Driver Identification

    “As a data architect, you have to understand the functional requirements, the non-functional requirements, then you need to make a solution for those requirements. There can be multiple solutions and multiple purposes.” (Andrew Johnston, Independent Consultant)

    Interview the business to get clarity on business objectives and drivers

    Associated Activity icon 1.1.2 1 hour per interview

    INPUT: Sample questions targeting the activities, challenges, and opportunities of each business unit

    OUTPUT: Sample questions targeting the activities, challenges, and opportunities of each business unit

    Materials: Data Architecture Driver Pattern Identification Tool

    Participants: Data architect, Business representatives, IT representatives

    Identify 2-3 business units that demonstrate enthusiasm for or a positive outlook on improving how organizational data can help them in their role and as a unit.

    Conducting a deep-dive interview process with these key stakeholders will help further identify high-level goals for the data architecture strategy within each business unit. This process will help to secure their support throughout the implementation process by giving them a sense of ownership.

    Key Interview Questions:

    1. What are your primary activities? What do you do?
    2. What challenges do you have when completing your activities?
    3. How is poor data impacting your job?
    4. If [your selected domain]’s data is improved, what business issues would this help solve?

    Request background information and documentation from stakeholders regarding the following:

    • What current data management policies and processes exist (that you know of)?
    • Who are the data owners and end users?
    • Where are the data sources within the department stored?
    • Who has access to these data sources?
    • Are there existing or ongoing data issues within those data sources?

    Interview the enterprise architect to get input on the drivers of the business

    Associated Activity icon 1.1.3 2 hours

    INPUT: Data Architecture Driver tool assessment prompts.

    OUTPUT: Identified business driver that applies to your organization.

    Materials: Data Architecture Driver Pattern Identification Tool

    Participants: Data architect, Enterprise architect

    Data architecture improvements need to be driven by business need.

    Instructions

    As you work through Tab 2. Driver Identification of the Data Architecture Driver Pattern Identification Tool, consult with the enterprise architect or equivalent to assist you in rating the importance of each of the symptoms of the business drivers. This will help you provide greater value to the business and more aligned objectives.

    Screenshot of the Data Architecture Driver Pattern Identification Tool, tab 2 Driver Identification.
    Tab 2. Driver Identification

    Once you know what that need is, go to Step 2.

    Phase 1, Step 2: Establish Actionable Tactics to Optimize Data Architecture

    PHASE 1

    1.11.2
    Identify Your Business Driver for Optimizing Data ArchitectureDetermine Actionable Tactics to Optimize Data Architecture

    This step will walk you through the following activities:

    • Understand Info-Tech’s five-tier data architecture to begin focusing your architectural optimization.
    • Create your Data Architecture Optimization Template to plan your improvement tactics.
    • Prioritize your tactics based on the five-tier architecture to plan optimization.

    This step involves the following participants:

    • Data Architect
    • Enterprise Architect
    • DBAs

    Outcomes of this step

    • A tactical and prioritized plan for optimizing the organization’s data architecture according to the needs of the business.

    To plan a business-driven architecture, data architects need to keep the organization’s big picture in mind

    Remember… Architecting an organization involves alignment, planning, road mapping, design, and change management functions.

    Data architects must be heavily involved with:

    • Understanding the short- and long-term visions of the business to develop a vision for the organization’s data architecture.
    • Creating processes for governing the identification, collection, and use of accurate and valid data, as well as for tracking data quality, completeness, and redundancy.
    • They need to create strategies for data security, backup, disaster recovery, business continuity, and archiving, and ensure regulatory compliance.

    To do this, you need a framework. A framework provides you with the holistic view of the organization’s data environment that you can use to design short- and long-term tactics for improving the use of data for the needs of the business.

    Use Info-Tech’s five-tier data architecture to model your environment in a logical, consumable fashion.

    Info-Tech Best Practice

    The more complicated an environment is, the more need there is for a framework. Being able to pick a starting point and prioritize tasks is one of the most difficult, yet most essential, aspects of any architect’s role.

    The five tiers of an organization’s data architecture support the use of data throughout its lifecycle

    Info-Tech’s five-tier data architecture model summarizes an organization’s data environment at a logical level. Data flows from left to right, but can also flow from the presentation layer back to the warehousing layer for repatriation of data.

    Info-Tech's Five Tier Data Architecture. The five tiers being 'Sources' which includes 'App1 ', 'App2', 'Excel and other documents', 'Access database(s)', 'IOT devices', and 'External data feed(s) & social media'; 'Integration and Translation' which includes 'Solutions: SOA, Point to Point, Manual Loading, ESB , ETL, ODS, Data Hub' and 'Functions: Scrambling Masking Encryption, Tokenizing, Aggregation, Transformation, Migration, Modeling'; 'Warehousing' which includes 'Data Lakes & Warehouse(s) (Raw Data)', 'EIM, ECM, DAM', and 'Data Lakes & Warehouse(s) (Derived Data)'; 'Analytics' which includes 'Data Marts', 'Data Cube', 'Flat Files', 'BI Tools', and the 'Protected Zone: Data Marts - BDG Class Ref. MDM'; and 'Presentation' which includes 'Formulas', 'Thought Models', 'Reports', 'Dashboards', 'Presentations', and 'Derived Data (from analytics activities)'.

    Use the Data Architecture Optimization Template to build your improvement roadmap

    Supporting Tool icon 1.2 Data Architecture Optimization Template

    Download the Data Architecture Optimization Template.

    Overview

    Use this template to support your team in creating a tactical strategy for optimizing your data architecture across the five tiers of the organization’s architecture. This template can be used to document your organization’s most pressing business driver, the reasons for optimizing data architecture according to that driver, and the tactics that will be employed to address the shortcomings in the architecture.

    Sample of Info-Tech’s Data Architecture Optimization Template. Info-Tech’s Data Architecture Optimization Template Table of Contents
    1. Build Your Current Data Architecture Logical Model Use this section to document the current data architecture situation, which will provide context for your plan to optimize your data architecture.
    2. Optimization Plan Use this section to document the tactics that will be employed to optimize the current data architecture according to the tactic pattern identified by the business driver.

    Fill out as you go

    As you read about the details of the five-tier data architecture model in the following slides, start building your current logical data architecture model by filling out the sections that correspond to the various tiers. For example, if you identified that the most pressing business driver is becoming compliant with regulations, document the sources of data required for compliance, as well as the warehousing strategy currently being employed. This will help you to understand the organization’s data architecture at a logical level.

    Tier 1 represents all of the sources of your organization’s data

    Tier 1 of Info-Tech's Five Tier Data Architecture, 'Sources', which includes 'App1 ', 'App2', 'Excel and other documents', 'Access database(s)', 'IOT devices', and 'External data feed(s) & social media'.
    –› Data to integration layer

    Tier 1 is where the data enters the organization.

    All applications, data documents such as MS Excel spreadsheets, documents with table entries, manual extractions from other document types, user-level databases including MS Access and MySQL, other data sources, data feeds, big datasets, etc. reside here.

    This tier typically holds the siloed data that is so often not available across the enterprise because the data is held within department-level applications or systems. This is also the layer where transactions and operational activities occur and where data is first created or ingested.

    There are any number of business activities from transactions through business processes that require data to flow from one system to another, so it is often at this layer we see data created more than once, data corruption occurs, manual re-keying of data from system to system, and spaghetti-like point-to-point connections are built that are often fragile. This is usually the single most problematic area within an enterprise’s data environment. Application- or operational-level (siloed) reporting often occurs at this level.

    Info-Tech Best Practice

    An optimized Tier 1 has the following attributes:

    • Rationalized applications
    • Operationalized database administration
    • Databases governed, monitored, and maintained to ensure optimal performance

    Tier 2 represents the movement of data

    Tier 2 of Info-Tech's Five Tier Data Architecture, 'Integration and Translation', which includes 'Solutions: SOA, Point to Point, Manual Loading, ESB , ETL, ODS, Data Hub' and 'Functions: Scrambling Masking Encryption, Tokenizing, Aggregation, Transformation, Migration, Modeling'.
    –› Data to Warehouse Environment

    Find out more

    For more information on data integration, see Info-Tech’s Optimize the Organization’s Data Integration Practices blueprint.

    Tier 2 is where integration, transformation, and aggregation occur.

    Regardless of how you integrate your systems and data stores, whether via ETL, ESB, SOA, data hub, ODS, point-to-point, etc., the goal of this layer is to move data at differing speeds for one of two main purposes:

    1) To move data from originating systems to downstream systems to support integrated business processes. This ensures the data is pristine through the process and improves trustworthiness of outcomes and speed to task and process completion.

    2) To move data to Tier 3 - The Data Warehouse Architecture, where data rests for other purposes. This movement of data in its purest form means we move raw data to storage locations in an overall data warehouse environment reflecting any security, compliance and other standards in our choices for how to store.

    Also, this is where data is transformed for unique business purpose that will also be moved to a place of rest or a place of specific use. Data masking, scrambling, aggregation, cleansing and matching, and other data related blending tasks occur at this layer.

    Info-Tech Best Practice

    An optimized Tier 2 has the following attributes:

    • Business data glossary is leveraged
    • ETL is governed
    • ETL team is empowered
    • Data matching is facilitated
    • Canonical data model is present

    Tier 3 is where data comes together from all sources to be stored in a central warehouse environment

    Tier 3 is where data rests in long-term storage.

    This is where data rests (long-term storage) and also where an enterprise’s information, documents, digital assets, and any other content types are stored. This is also where derived and contrived data creations are stored for re-use, and where formulas, thought models, heuristics, algorithms, report styles, templates, dashboard styles, and presentations-layer widgets are all stored in the enterprise information management system.

    At this layer there may be many technologies and many layers of security to reflect data domains, classifications, retention, compliance, and other data needs. This is also the layer where data lakes exist as well as traditional relational databases, enterprise database systems, enterprise content management systems, and simple user-level databases.

    Info-Tech Best Practice

    An optimized Tier 3 has the following attributes:

    • Data warehouse is governed
    • Data warehouse operations and planning
    • Data library is comprehensive
    • Four Rosetta Stones of data are in place: BDG, data classification, reference data, master data.
    Data from integration layer –›
    Tier 3 of Info-Tech's Five Tier Data Architecture, 'Data Warehouse Environment' which includes 'Data Lakes & Warehouse(s) (Raw Data)', 'EIM, ECM, DAM'.
    –› Analytics

    Find out more

    For more information on Data Warehousing, see Info-Tech’s Build an Extensible Data Warehouse Foundation and Drive Business Innovation With a Modernized Data Warehouse Environment blueprints.

    Tier 4 is where knowledge and insight is born

    Tier 4 represents data being used for a purpose.

    This is where you build fit-for-purpose data sets (marts, cubes, flat files) that may now draw from all enterprise data and information sources as held in Tier 3. This is the first place where enterprise views of all data may be effectively done and with trust that golden records from systems of record are being used properly.

    This is also the layer where BI tools get their greatest use for performing analysis. Unlike Tier 3 where data is at rest, this tier is where data moves back into action. Data is brought together in unique combinations to support reporting, and analytics. It is here that the following enterprise analytic views are crafted:
    Exploratory, Inferential, Causal, Comparative, Statistical, Descriptive, Diagnostic, Hypothesis, Predictive, Decisional, Directional, Prescriptive

    Info-Tech Best Practice

    An optimized Tier 4 has the following attributes:

    • Reporting meets business needs
    • Data mart operations are in place
    • Governance of data marts, cubes, and BI tools in place
    Warehouse Environment –›
    Tier 4 of Info-Tech's Five Tier Data Architecture, 'Analytics', which includes 'Data Marts', 'Data Cube', 'Flat Files', and 'BI Tools'.
    –› Presentation

    Find out more

    For more information on BI tools and strategy, see Info-Tech’s Select and Implement a Business Intelligence and Analytics Solution and Build a Next Generation BI with a Game-Changing BI Strategy blueprints.

    The presentation layer, Tier 5, is where data becomes presentable information

    Tier 5 represents data in knowledge form.

    This is where the data and information combine in information insight mapping methods (presentations, templates, etc.). We craft and create new ways to slice and dice data in Tier 4 to be shown and shared in Tier 5.

    Templates for presenting insights are extremely valuable to an enterprise, both for their initial use, and for the ability to build deeper, more insightful analytics. Re-use of these also enables maximum speed for sharing, consuming the outputs, and collective understanding of these deeper meanings that is a critical asset to any enterprise. These derived datasets and the thought models, presentation styles, templates, and other derived and contrived assets should be repatriated into the derived data repositories and the enterprise information management systems respectively as shown in Tier 3.

    Find out more

    For more information on enterprise content management and metadata, see Info-Tech’s Develop an ECM Strategy and Break Open Your DAM With Intuitive Metadata blueprints.

    Tier 5 of Info-Tech's Five Tier Data Architecture, 'Presentation', which includes 'Formulas', 'Thought Models', 'Reports', 'Dashboards', 'Presentations', and 'Derived Data (from analytics activities)'. The 'Repatriation of data' feeds the derived data back into Warehousing.

    Info-Tech Best Practice

    An optimized Tier 5 has the following attributes:

    • Metadata creation is supervised
    • Metadata is organized
    • Metadata is governed
    • Content management capabilities are present

    Info-Tech Insight

    Repatriation of data and information is an essential activity for all organizations to manage organizational knowledge. This is the activity where information, knowledge, and insights that are stored in content form are moved back to the warehousing layer for long-term storage. Because of this, it is crucial to have an effective ECM strategy as well as the means to find information quickly and efficiently. This is where metadata and taxonomy come in.

    As a data architect, you must prioritize your focus according to business need

    Determine your focus.

    Now that you have an understanding of the drivers requiring data architecture optimization, as well as the current data architecture situation at your organization, it is time to determine the actions that will be taken to address the driver.

    1. Business driver

    Screenshot of Data Architecture Driver Pattern Identification Tool, Tab 2. Tactic Pattern Plan.
    Data Architecture Driver Pattern Identification Tool, Tab 2. Tactic Pattern Plan

    3. Documented tactic plan

    Data Architecture Optimization Template

    2. Tactics across the five tiers

    Another screenshot of Data Architecture Driver Pattern Identification Tool, Tab 2. Tactic Pattern Plan.

    The next four slides provide an overview of the priorities that accompany the four most common business drivers that require updates to a stale data architecture.

    Business driver #1: Adding a new functionality to an application can have wide impacts on data architecture

    Does the business wants to add a new application or supplement an existing application with a new functionality?

    Whether the business wants to gain better customer intimacy, achieve operational excellence, or needs to change its compliance and reporting strategy, the need for collecting new data through a new application or a new functionality within an existing application can arise. This business driver has the following attributes:

    • Often operational oriented and application driven.
    • An application is changed through an application version upgrade, migration to cloud, or application customization, or as a result of application rationalization or changes in the way that application data is generated.
    • However, not all new functionalities trigger this scenario. Non-data-related changes, such as a new interface, new workflows, or any other application functionality changes that do not involve data, will not have data architecture impacts.
    Stock photo of someone using a smartphone with apps.
    Modified icon for Tools & Templates. When this business driver arises, data architects should focus on optimizing architecture at the source tier and the integration of the new functionality. Tactics for this business driver should address the following pattern:
    Tiers 1 and 2 highlighted.

    Business driver #2: Organizations today are looking to become more data driven

    Does the business wants to better leverage its data?

    An organization can want to use its data for multiple reasons. Whether these reasons include improving customer experience or operational excellence, the data architect must ensure that the organization’s data aggregation environment, reporting and analytics, and presentation layer are assessed and optimized for serving the needs of the business.

    “Data-drivenness is about building tools, abilities, and, most crucially, a culture that acts on data.” (Carl Anderson, Creating a Data-Driven Organization)

    Tactics for this business driver should address the following pattern:
    Tiers 3, 4, and 5 highlighted.
    Modified icon for Tools & Templates. When this business driver arises, data architects should focus on optimizing architecture at the source tier and the integration of the new functionality.
    Stock photo of someone sitting at multiple computers with analytics screens open.
    • This scenario is typically project driven and analytical oriented.
    • The business is looking to leverage data and information by processing data through BI tools and self-service.
    • Example: The organization wants to include new third-party data, and needs to build a new data mart to provide a slice of data for analysis.

    Business driver #3: Risk and compliance demands can put pressure on outdated architectures

    Is there increasing pressure on the business to maintain compliance requirements as per regulations?

    An organization can want to use its data for multiple reasons. Whether these reasons include improving customer experience or operational excellence, the data architect must ensure that the organization’s data aggregation environment, reporting and analytics, and presentation layer are assessed and optimized for serving the needs of the business.

    There are different types of requirements:
    • Can be data-element driven. For example, PII, PHI are requirements around data elements that are associated with personal and health information.
    • Can be process driven. For example, some requirements restrict data read/write to certain groups.
    Stock photo of someone pulling a block out of a Jenga tower.
    Modified icon for Tools & Templates. When this business driver arises, data architects should focus on optimizing architecture where data is stored: at the sources, the warehouse environment, and analytics layer. Tactics for this business driver should address the following pattern:
    Tiers 1, 3, and 4 highlighted.

    Business driver #4: Mergers and acquisitions can require a restructuring of the organization’s data architecture

    Is the organization looking to acquire or merge with another organization or line of business?

    There are three scenarios that encompass the mergers and acquisitions business driver for data architecture:

    1. The organization acquires/merges with another organization and wants to integrate the data.
    2. The organization acquires/merges a subset of an organization (a line of business, for example) and wants to integrate the data.
    3. The organization acquires another organization for competitive purposes, and does not need to integrate the data.
    Regardless of what scenario your organization falls into, you must go through the same process of identifying the requirements for the new data:
    1. Understand what data you are getting.
      The business may acquire another organization for the data, for the technology, and/or for algorithms (for example). If the goal is to integrate the new data, you must understand if the data is unstructured, structured, how much data, etc.
    2. Plan for the integration of the new data into your environment.
      Do you have the expertise in-house to integrate the data? Database structures and systems are often mismatched (for example, acquired company could have an Oracle database whereas you are an SAP shop) and this may require expertise from the acquired company or a third party.
    3. Integrate the new data.
      Often, the extraction of the new data is the easy part. Transforming and loading the data is the difficult and costly part.
    “As a data architect, you must do due diligence of the acquired firm. What are the workflows, what are the data sources, what data is useful, what is useless, what is the value of the data, and what are the risks of embedding the data?” (Anonymous Mergers and Acquisitions Consultant)
    Modified icon for Tools & Templates. When this business driver arises, data architects should focus on optimizing architecture at the source tier, the warehousing layer, and analytics. Tiers 1, 3, and 4 highlighted.

    Determine your tier priority pattern and the tactics that you should address based on the business drivers

    Associated Activity icon 1.2.1 30 minutes

    INPUT: Business driver assessment

    OUTPUT: Tactic pattern and tactic plan

    Materials: Data Architecture Driver Pattern Identification Tool, Data Architecture Optimization Template

    Participants: Data architect, Enterprise architect

    Instructions
    1. After you have assessed the organization’s business driver on Tab 1. Driver Identification, move to Tab 2. Tactic Pattern Plan.
    2. Here, you will find a summary of the business driver that applies to you, as well as the tier priority pattern that will help you to focus your efforts for data architecture.
    3. Document the Tier Priority Pattern and associated tactics in Section 2. Optimization Plan of the Data Architecture Optimization Plan.
    Screenshot of Data Architecture Driver Tool.
    Data Architecture Driver Tool
    Arrow pointing right. Sample of Data Architecture Optimization Template
    Data Architecture Optimization Template

    Info-Tech Insight

    Our approach will help you to get to the solution of the organization’s data architecture problems as quickly as possible. However, keep in mind that you should still address the other tiers of your data architecture even if they are not part of the pattern we identified. For example, if you need to become more data driven, don’t completely ignore the sources and the integration of data. However, to deliver the most and quickest value, focus on tiers 3, 4, and 5.

    This phase helped you to create a tactical plan to optimize your data architecture according to business priorities

    Phase 1 is all about focus.

    Data architects and those responsible for updating an organization’s data architecture have a wide-open playing field with which to take their efforts. Being able to narrow down your focus and generate an actionable plan will help you provide more value to the organization quickly and get the most out of your data.

      Phase 1
      • Business Drivers
        • Tactic Pattern
          • Tactical Plan

    Now that you have your prioritized tactical plan, move to Phase 2. This phase will help you map these priorities to the essential capabilities and measure where you stack up in these capabilities. This is an essential step in creating your data architecture roadmap and plan for coming years to modernize the organization’s data architecture.

    To identify what the monetary authority needed from its data architecture, Info-Tech helped determine the business driver

    CASE STUDY

    Industry: Financial
    Source: Info-Tech Consulting
    Symbol for 'Monetary Authority Case Study'.

    Part 1

    Prior to receiving new external requirements, the monetary Authority body had been operating with an inefficient system. Outdated legacy systems, reports in paper form, incomplete reports, and stale data from other agencies resulted in slow data access. The new requirements demanded speeding up this process.

    Diagram comparing the 'Original Reporting' requirement of 'Up to 7 days' vs the 'New Requirement' of 'As soon as 1 hour'. The steps of reporting in that time are 'Report Request', 'Gather Data', and 'Make Report'.

    Although the organization understood it needed changes, it first needed to establish what were the business objectives, and which areas of their architecture they would need to focus on.

    The business driver in this case was compliance requirements, which directed attention to the sources, aggregation, and insights tiers.

    Tiers 1, 3, and 4 highlighted.

    Looking at the how the different tiers relate to certain business operations, the organization uncovered the best practise tactics to achieving an optimized data architecture.

    1. Source Tactics: 3. Warehousing Tactics: 4. Analytics Tactics:
    • Identify data sources
    • Ensure data quality
    • Properly catalogue data
    • Properly index data
    • Provide the means for data accessibility
    • Allow for data reduction/space for report building

    Once the business driver had been established, the organization was able to identify the specific areas it would eventually need to evaluate and remedy as needed.

    If you want additional support, have our analysts guide you through this phase as part of an Info-Tech Workshop Associated Activity icon

    Book a workshop with our Info-Tech analysts:

    Photo of an Info-Tech analyst.
    • To accelerate this project, engage your IT team in an Info-Tech workshop with an Info-Tech analyst team.
    • Info-Tech analyst will join you and your team onsite at your location or welcome you to Info-Tech's historic Toronto office to participate in an innovative onsite workshop.
    • Contact your account manager (www.infotech.com/account), or email Workshops@InfoTech.com for more information.

    The following are sample activities that will be conducted by Info-Tech analysts with your team:

    1.1.1

    Sample of activity 1.1.1 'Identify the drivers for improving your data architecture'. Identify the business driver that will set the direction of your data architecture optimization plan.

    In this activity, the facilitator will guide the team in identifying the business driver that is creating the need to improve the organization’s data architecture. Data architecture needs to adapt to the changing needs of the business, so this is the most important step of any data architecture improvements.

    1.2.1

    Sample of activity 1.2.1 'Determine your tier priority pattern and the tactics that you should address based on the business drivers'. Determine the tactics that you will use to optimize data architecture.

    In this activity, the facilitator will help the team create a tactical plan for optimizing the organization’s data architecture across the five tiers of the logical model. This plan can then be followed when addressing the business needs.

    Build a Business-Aligned Data Architecture Optimization Strategy

    PHASE 2

    Personalize Your Tactics to Optimize Your Data Architecture

    Phase 2 will determine your tactics that you should implement to optimize your data architecture

    Business Drivers
    Each business driver requires focus on specific tiers and their corresponding capabilities, which in turn correspond to tactics necessary to achieve your goal.
    New Functionality Risk and Compliance Mergers and Acquisitions Become More Data Driven
    Tiers 1. Data Sources 2. Integration 3. Warehousing 4. Insights 5. Presentation
    Capabilities Current Capabilities
    Target Capabilities
    Example Tactics Leverage indexes, partitions, views, and clusters to optimize performance.

    Cleanse data source.

    Leverage integration technology.

    Identify matching approach priorities.

    Establish governing principles.

    Install performance enhancing technologies.

    Establish star schema and snowflake principles.

    Share data via data mart.

    Build metadata architecture:
    • Data lineage
    • Sharing
    • Taxonomy
    • Automatic vs. manual creation

    Phase 2 outline

    Associated Activity icon Call 1-888-670-8889 or email GuidedImplementations@InfoTech.com for more information.

    Complete these steps on your own, or call us to complete a guided implementation. A guided implementation is a series of 2-3 advisory calls that help you execute each phase of a project. They are included in most advisory memberships.

    Guided Implementation 2: Personalize Your Tactics to Optimize Your Data Architecture

    Proposed Time to Completion: 2 weeks
    Step 2.1: Measure Your Data Architecture Capabilities Step 2.2: Set a Target for Data Architecture Capabilities Step 2.3: Identify the Tactics That Apply to Your Organization
    Start with an analyst kick-off call:
    • Understand Info-Tech’s data architecture capability model to begin identifying where to develop tactics for optimizing your data architecture.
    Review findings with analyst:
    • Understand Info-Tech’s data architecture capability model to begin identifying where to develop tactics for optimizing your data architecture.
    Finalize phase deliverable:
    • Learn about the trends in data architecture that can be leveraged to develop tactics.
    Then complete these activities…
    • Measure your current state across the tiers of the capability model that will help address your business driver.
    Then complete these activities…
    • Measure your target state for the capabilities that will address your business driver.
    Then complete these activities…
    • Review the tactical roadmap that was created with guidance from the capability gap analysis.
    With these tools & templates:
    • Data Architecture Tactical Roadmap Tool
    With these tools & templates:
    • Data Architecture Tactical Roadmap Tool
    With these tools & templates:
    • Data Architecture Trends Presentation Template

    Phase 2 Results & Insights

    • Data architecture is not just data models. Understand the essential capabilities that your organization needs from its data architecture to develop a tactical plan for optimizing data architecture across its people, processes, and technology.

    Phase 2, Step 1: Measure Your Data Architecture Capabilities

    PHASE 2

    2.1 2.2 2.3
    Measure Your Data Architecture Capabilities Set a Target for Data Architecture Capabilities Identify the Tactics That Apply to Your Organization

    This step will walk you through the following activities:

    • As you walk through the data architecture capability model, measure your current state in each of the relevant capabilities.
    • Distinguish between essential and nice-to-have capabilities for your organization.

    This step involves the following participants:

    • Data Architect

    Outcomes of this step

    • A framework for generating a tactical plan for data architecture optimization.
    • Knowledge of the various trends in the data architecture field that can be incorporated into your plan.

    To personalize your tactical strategy, you must measure up your base data architecture capabilities

    What is a capability?

    Capabilities represent a mixture of people, technology, and processes. The focus of capability design is on the outcome and the effective use of resources to produce a differentiating capability or an essential supporting capability.

    To personalize your tactics, you have to understand what the essential capabilities are across the five tiers of an organization’s data architecture. Then, assess where you currently stand in these capabilities and where you need to go in order to build your optimization plan.

    'Capability' as a mixture of 'People', 'Technology', 'Process', and 'Assets'.

    Info-Tech’s data architecture capability model can be laid over the five-tier data architecture to understand the essential and advanced capabilities that an organization should have, and to build your tactical strategy for optimizing the organization’s data architecture across the tiers.

    Use Info-Tech’s data architecture capability model as a resource to assess and plan your personalized tactics

    Info-Tech’s data architecture capability model can be laid over the five-tier data architecture to understand the essential and advanced capabilities that an organization should have, and to build your tactical strategy for optimizing the organization’s data architecture across the tiers.

    Info-Tech’s Data Architecture Capability Model featuring the five-tier architecture listing 'Core Capabilities' and 'Advanced Capabilities' within each tier, and a list of 'Cross Capabilities' which apply to all tiers.

    Use the Data Architecture Tactical Roadmap Tool to create a tailored plan of action

    Supporting Tool icon 2.1.1 Data Architecture Tactical Roadmap Tool

    Instructions

    Use the Data Architecture Tactical Roadmap Tool as your central tool to develop a tactical plan of action to optimize the organization’s data architecture.

    This tool contains the following sections:

    1. Business Driver Input
    2. Capability Assessment
    3. Capability Gap Analysis
    4. Tactical Roadmap
    5. Metrics
    6. Initiative Roadmap

    INFO-TECH DELIVERABLE

    Sample of the Info-Tech deliverable Data Architecture Tactical Roadmap Tool.

    Benefits of using this tool:

    • Comprehensive documentation of data architecture capabilities present in leading organizations.
    • Generates an accurate architecture roadmap for your organization that is developed in alignment with the broader enterprise architecture and related architectural domains.

    To create a plan for your data architecture priorities, you must first understand where you currently stand

    Now that you understand the business problem that you are trying to solve, it is time to take action in solving the problem.

    The organization likely has some of the capabilities that are needed to solve the problem, but also a need to improve other capabilities. To narrow down the capabilities that you should focus on, first select the business driver that was identified in Phase 1 in Tab 1. Business Driver Input of the Data Architecture Tactical Roadmap Tool. This will customize the roadmap tool to deselect the capabilities that are likely to be less relevant to your organization.

    For Example: If you identified your business driver as “becoming more data-driven”, you will want to focus on measuring and building out the capabilities within Tiers 3, 4, and 5 of the capability model.

    Data Architecture Capability Model
    Info-Tech’s Data Architecture Capability Model with tiers 3, 4, and 5 highlighted.

    Note

    If you want to assess your organization for all of the capabilities across the data architecture capability model, select “Comprehensive Data Architecture Assessment” in Tab 1. Business Driver Input of the Data Architecture Tactical Roadmap Tool.

    Determine your current state across the related architecture tiers

    Associated Activity icon 2.1.2 1 hour

    INPUT: Current data architecture capabilities.

    OUTPUT: An idea of where you currently stand in the capabilities.

    Materials: Data Architecture Tactical Roadmap Tool

    Participants: Data architect, Enterprise architect, Business representatives

    Use the Data Architecture Tactical Roadmap Tool to evaluate the baseline and target capabilities of your practice in terms of how data architecture is approached and executed.

    Instructions
    1. Invite the appropriate stakeholders to participate in this exercise.
    2. On Tab 2. Practice Components, assess the current and target states of each capability on a scale of 1–5.
    3. Note: “Ad hoc” implies a capability is completed, but randomly, informally, and without a standardized method.
      These results will set the baseline against which you will monitor performance progress and keep track of improvements over time.
    To assess data architecture maturity, Info-Tech uses the Capability Maturity Model Integration (CMMI) program for rating capabilities on a scale of 1 to 5:

    1 = Initial/Ad hoc

    2 = Developing

    3 = Defined

    4 = Managed and Measurable

    5 = Optimized

    Info-Tech Insight

    Focus on Early Alignment. Assessing capabilities within specific people’s job functions can naturally result in disagreement or debate, especially between business and IT people. Objectively facilitate any debate and only finalize capability assessments when there is full alignment. Remind everyone that data architecture should ultimately serve business needs wherever possible.

    Phase 2, Step 2: Set a Target for Data Architecture Capabilities

    PHASE 2

    2.12.22.3
    Measure Your Data Architecture CapabilitiesSet a Target for Data Architecture CapabilitiesIdentify the Tactics That Apply to Your Organization

    This step will walk you through the following activities:

    • Determine your target state in each of the relevant capabilities.
    • Distinguish between essential and nice-to-have capabilities for your organization.

    This step involves the following participants:

    • Data Architect

    Outcomes of this step

    • A holistic understanding of where the organization’s data architecture currently sits, where it needs to go, and where the biggest gaps lie.

    To create a plan for your data architecture priorities, you must also understand where you need to get to in the future

    Keep the goal in mind by documenting target state objectives. This will help to measure the highest priority gaps in the organization’s data architecture capabilities.

    Example driver = Becoming more data driven Arrow pointing right. Info-Tech’s Data Architecture Capability Model with tiers 3, 4, and 5 highlighted. Arrow pointing right. Current Capabilities Arrow pointing right. Target Capabilities
    Gaps and Priorities
    Stock photo of a hand placing four shelves arranged as stairs. On the first step is a mini-cut-out of a person walking.

    Determine your future state across the relevant tiers of the data architecture capability model

    Associated Activity icon 2.2.1 2 hours

    INPUT: Current state of data architecture capabilities.

    OUTPUT: Target state of data architecture capabilities.

    Materials: Data Architecture Tactical Roadmap Tool

    Participants: Data architect

    The future of data architecture is now.

    Determine the state of data architecture capabilities that the organization needs to reach to address the drivers of the business.

    For example: If you identified your business driver as “becoming more data driven”, you will want to focus on the capabilities within Tiers 3, 4, and 5 of the capability model.

    Driver = Becoming more data driven Arrow pointing right. Info-Tech’s Data Architecture Capability Model with tiers 3, 4, and 5 highlighted. Arrow pointing right. Target Capabilities

    Identify where gaps in your data architecture capabilities lie

    Associated Activity icon 2.2.2 1 hour

    INPUT: Current and target states of data architecture capabilities.

    OUTPUT: Holistic understanding of where you need to improve data architecture capabilities.

    Materials: Data Architecture Tactical Roadmap Tool

    Participants: Data architect

    Visualization of gap assessment of data quality practice capabilities

    To enable deeper analysis on the results of your capability assessment, Tab 4. Capability Gap Analysis in the Data Architecture Tactical Roadmap Tool creates visualizations of the gaps identified in each of your practice capabilities and related data management practices. These diagrams serve as analysis summaries.

    Gap Assessment of Data Source Capabilities

    Sample of the Data Architecture Tactical Roadmap Tool, tab 4. Capability Gap Analysis.

    Use Tab 3. Data Quality Practice Scorecard to enhance your data quality project.

    1. Enhance your gap analyses by forming a relative comparison of total gaps in key practice capability areas, which will help in determining priorities.
    2. Put these up on display to improve discussion in the gap analyses and prioritization sessions.
    3. Improve the clarity and flow of your strategy template, final presentations, and summary documents by copying and pasting the gap assessment diagrams.

    Phase 2, Step 3: Identify the Tactics That Apply to Your Organization

    PHASE 2

    2.12.22.3
    Measure Your Data Architecture CapabilitiesSet a Target for Data Architecture CapabilitiesIdentify the Tactics That Apply to Your Organization

    This step will walk you through the following activities:

    • Before making your personal tactic plan, identify the trends in data architecture that can benefit your organization.
    • Understand Info-Tech’s data architecture capability model.
    • Initiate the Data Architecture Roadmap Tool to begin creating a roadmap for your optimization plan.

    This step involves the following participants:

    • Data Architect

    Outcomes of this step

    • A framework for generating a tactical plan for data architecture optimization.
    • Knowledge of the various trends in the data architecture field that can be incorporated into your plan.

    Capitalize on trends in data architecture before you determine the tactics that apply to you

    Stop here. Before you begin to plan for optimization of the organization’s data environment, get a sense of the sustainability and scalability of the direction of the organization’s data architecture evolution.

    Practically any trend in data architecture is driven by an attempt to solve one or more the common challenges of today’s tumultuous data landscape, otherwise known as “big data.” Data is being produced in outrageous amounts, at very high speeds, and in a growing number of types and structures.

    To meet these demands, which are not slowing down, you must keep ahead of the curve. Consider the internal and external catalysts that might fuel your organization’s need to modernize its data architecture:

    Big Data

    Data Storage

    Advanced analytics

    Unstructured data

    Integration

    Hadoop ecosystem

    The discussion about big data is no longer about what it is, but how do businesses of all types operationalize it.

    Is your organization currently capturing and leveraging big data?

    Are they looking to do so in the near future?

    The cloud

    The cloud offers economical solutions to many aspects of data architecture.

    Have you dealt with issues of lack of storage space or difficulties with scalability?

    Do you need remote access to data and tools?

    Real-time architecture

    Advanced analytics (machine learning, natural language processing) often require data in real-time. Consider Lambda and Kappa architectures.

    Has your data flow prevented you from automation, advanced analytics, or embracing the world of IoT?

    Graph databases

    Self-service data access allows more than just technical users to participate in analytics. NoSQL can uncover buried relationships in your data.

    Has your organization struggled to make sense of different types of unstructured data?

    Is ETL enough?

    What SQL is to NoSQL, ETL is to NoETL. Integration techniques are being created to address the high variety and high velocity of data.

    Have your data scientists wasted too much time and resources in the ETL stage?

    Read the Data Architecture Trends Presentation to understand the current cutting edge topics in data architecture

    Supporting Tool icon 2.1 Data Architecture Trends Presentation

    The speed at which new technology is changing is making it difficult for IT professionals to keep pace with best practices, let alone cutting edge technologies.

    The Info-Tech Data Architecture Trends Presentation provides a glance at some of the more significant innovations in technology that are driving today’s advanced data architectures.

    This presentation also explains how these trends relate to either the data challenges you may be facing, or the specific business drivers you are hoping to bring to your organization.

    Sample of the Data Architecture Trends Presentation.
    Data Architecture Trends Presentation

    Gaps between your current and future capabilities will help you to determine the tactics that apply to you

    Now that you know where the organization currently stands, follow these steps to begin prioritizing the initiatives:

    1. What are you trying to accomplish? Determine target states that are framed in quantifiable objectives that can be clearly communicated. The more specific the objectives are the better.
    2. Evaluate the “delta,” or difference between where the organization currently stands and where it needs to go. This will be expressed in terms of gap closure strategies, and will help clarify the initiatives that will populate the road map.
    3. Determine the relative business value of each initiative, as well as the relative complexities of successfully implementing them. These scores should be created with stakeholder input, and then plotted in an effort/transition quadrant map to determine where the quickest and most valuable wins lie.
    Current State Gap Closure Strategies Target State Data Architecture Tactical Roadmap
    • Organization objectives
    • Functional needs
    • Current operating models
    • Technology assets
    Initiatives involving:
    • Organizational changes
    • Functional changes
    • Technology changes
    • Process changes
    • Performance objectives (revenue growth, customer intimacy, growth of organization)
    • Operating model improvements
    • Prioritized, simplified, and compelling vision of how the organization will optimize data architecture

    (Source: “How to Build a Roadmap”)

    Info-Tech Insight

    Optimizing data architecture requires a tactical approach, not a passive approach. The demanding task of optimization requires the ability to heavily prioritize. After you have identified why, determine how using our pre-built roadmap to address the four common drivers.

    Each of the layers of an organization’s data architecture have associated challenges to optimization

    Stop! Before you begin, recognize these “gotchas” that can present roadblocks to creating an effective data architecture environment.

    Before diving headfirst into creating your tactical data architecture plan, documenting the challenges associated with each aspect of the organization’s data architecture can help to identify where you need to focus your energy in optimizing each tier. The following table presents the common challenges across the five tiers:

    Source Tier

    Integration Tier

    Warehousing Tier

    Analytics Tier

    Presentation Tier

    Inconsistent data models Performance issues Scalability of the data warehouse Data currency, flexibility Model interoperability
    Data quality measures: data accuracy, timeliness, accessibility, relevance Duplicated data Infrastructure needed to support volume of data No business context for using the data in the correct manner No business context for using the data in the correct manner
    Free-form field and data values beyond data domain Tokenization and other required data transformations Performance
    Volume
    Greedy consumers can cripple performance
    Insufficient infrastructure
    Inefficiencies in building the data mart Report proliferation/chaos (“kitchen sink dashboards”)
    Reporting out of source systems DB model inefficiencies
    Manual errors;
    Application usability
    Elasticity

    Create metrics before you plan to optimize your data architecture

    Associated Activity icon 2.2.3 1 hour

    INPUT: Tactics that will be used to optimize data architecture.

    OUTPUT: Metrics that can be used to measure optimization success.

    Materials: Data Architecture Tactical Roadmap Tool

    Participants: Data architect

    Metrics will help you to track your optimization efforts and ensure that they are providing value to the organization.

    There are two types of metrics that are useful for data architects to track and measure: program metrics and project metrics. Program metrics represent the activities that the data architecture program, which is the sum of multiple projects, should help to improve. Project metrics are the more granular metrics that track each project.

    Program Metrics

    • TCO of IT
      • Costs associated with applications, databases, data maintenance
      • Should decrease with better data architecture (rationalized apps, operationalized databases)
    • Cost savings:
      • Retiring a legacy system and associated databases
      • Consolidated licensing
      • Introducing shared services
    • Data systems under maintenance (maintenance burden)
    • End-user data requests fulfilled
    • Improvement of time of delivery of reports and insights

    Project Metrics

    • Percent of projects in alignment with EA
    • Percent of projects compliant with the EA governance process (architectural due diligence rate)
    • Reducing time to market for launching new products
      • Reducing human error rates
      • Speeding up order delivery
      • Reducing IT costs
      • Reducing severity and frequency of security incidents

    Use Tab 6. Metrics of the Data Architecture Tactical Roadmap Tool to document and track metrics associated with your optimization tactics.

    Use Info-Tech’s resources to build your data architecture capabilities

    The following resources from Info-Tech can be used to improve the capabilities that were identified as having a gap. Read more about the details of the five-tier architecture in the blueprints below:

    Data Governance

    Data architecture depends on effective data governance. Use our blueprint, Enable Shared Insights With an Effective Data Governance Engine to get more out of your architecture.

    Data Quality

    The key to maintaining high data quality is a proactive approach that requires you to establish and update strategies for preventing, detecting, and correcting errors. Find out more on how to improve data quality with Info-Tech’s blueprint, Restore Trust in Your Data Using a Business-Aligned Data Quality Management Approach.

    Master Data Management

    When you start your data governance program, you will quickly realize that you need an effective MDM strategy for managing your critical data assets. Use our blueprint, Develop a Master Data Management Strategy and Roadmap to Better Monetize Data to get started with MDM.

    Data Warehouse

    The key to maintaining high data quality is a proactive approach that requires you to establish and update strategies for preventing, detecting, and correcting errors. Find out more on how to improve data quality with Info-Tech’s blueprint, Drive Business Innovation With a Modernized Data Warehouse Environment.

    With the optimal tactics identified, the monetary authority uncovered areas needing improvement

    CASE STUDY

    Industry: Financial
    Source: Info-Tech Consulting
    Symbol for 'Monetary Authority Case Study'.

    Part 2

    After establishing the appropriate tactics based on its business driver, the monetary authority was able to identify its shortcomings and adopt resolutions to remedy the issues.

    Best Practice Tactic Current State Solution
    Tier 1 - Data Sources Identify data sources Data coming from a number of locations. Create data model for old and new systems.
    Ensure data quality Internal data scanned from paper and incomplete. Data cleansing and update governance and business rules for migration to new system.
    External sources providing conflicting data.
    Tier 3 - Data Warehousing Data catalogue Data aggregated incompletely. Built proper business data glossary for searchability.
    Indexing Data warehouse performance sub-optimal. Architected data warehouse for appropriate use (star schema).
    Tier 4 - Data Analytics Data accessibility Relevant data buried in warehouse. Build data marts for access.
    Data reduction Accurate report building could not be performed in current storage. Built interim solution sandbox, spin up SQL database.

    Establishing these solutions provided the organization with necessary information to build their roadmap and move towards implementing an optimized data architecture.

    If you want additional support, have our analysts guide you through this phase as part of an Info-Tech Workshop Associated Activity icon

    Book a workshop with our Info-Tech analysts:

    Photo of a Info-Tech analyst.
    • To accelerate this project, engage your IT team in an Info-Tech workshop with an Info-Tech analyst team.
    • Info-Tech analyst will join you and your team onsite at your location or welcome you to Info-Tech's historic Toronto office to participate in an innovative onsite workshop.
    • Contact your account manager (www.infotech.com/account), or email Workshops@InfoTech.com for more information.

    The following are sample activities that will be conducted by Info-Tech analysts with your team:

    2.1.1 – 2.2.2

    Sample of activities 2.1.1 and 2.2.2, the first being 'Determine your current state across the related architecture tiers'. Evaluate your current capabilities and design your target data quality practice from two angles

    In this assessment and planning activity, the team will evaluate the current and target capabilities for your data architecture’s ability to meet business needs based on the essential capabilities across the five tiers of an organization’s architectural environment.

    2.2.3

    Sample of activity 2.2.3 'Create metrics before you plan to optimize your data architecture'. Create metrics to track the success of your optimization plan.

    The Info-Tech facilitator will guide you through the process of creating program and project metrics to track as you optimize your data architecture. This will help to ensure that the tactics are helping to improve crucial business attributes.

    Build a Business-Aligned Data Architecture Optimization Strategy

    PHASE 3

    Create Your Tactical Data Architecture Roadmap

    Phase 3 outline

    Associated Activity icon Call 1-888-670-8889 or email GuidedImplementations@InfoTech.com for more information.

    Complete these steps on your own, or call us to complete a guided implementation. A guided implementation is a series of 2-3 advisory calls that help you execute each phase of a project. They are included in most advisory memberships.

    Guided Implementation 3: Create Your Tactical Data Architecture Roadmap

    Proposed Time to Completion: 2 weeks
    Step 3.1: Personalize Your Data Architecture RoadmapStep 3.2: Manage Your Data Architecture Decisions and the Resulting Changes
    Start with an analyst kick-off call:
    • Review the tactical plan that addresses the business drivers by optimizing your data architecture in the relevant focus areas.
    Review findings with analyst:
    • Discuss and review the roadmap of optimization activities, including dependencies, timing, and ownership of activities.
    • Understand how change management is an integral aspect of any data architecture optimization plan.
    Then complete these activities…
    • Create your detailed data architecture initiative roadmap.
    Then complete these activities…
    • Create your Data Architecture Decision Template to document the changes that are going to be made to optimize your data architecture environment.
    • Review how change management fits into the data architecture improvement program.
    With these tools & templates:
    • Data Architecture Tactical Roadmap Tool
    With these tools & templates:
    • Data Architecture Decision Template

    Phase 3 Results & Insights

    • Phase 3 will help you to build a personalized roadmap and plan for optimizing data architecture in your organization. In carrying out this roadmap, changes will, by necessity, occur. Therefore, an integral aspect of a data architect’s role is change management. Use the resources included in Phase 3 to smoothen the change management process.

    Phase 3, Step 1: Personalize Your Data Architecture Roadmap

    PHASE 3

    3.1 3.2
    Personalize Your Data Architecture Roadmap Manage Your Data Architecture Decisions and the Resulting Changes

    This step will walk you through the following activities:

    • Determine the timing, effort, and ownership of the recommended optimization initiatives.
    • Brainstorm initiatives that are not yet on the roadmap but apply to you.

    This step involves the following participants:

    • Data Architect
    • DBAs
    • Enterprise Architect

    Outcomes of this step

    • A roadmap of specific initiatives that map to the tactical plan for optimizing your organization’s data architecture.
    • A plan for communicating high-level business objectives to data workers to address the issues of the business.

    Now that you have tactical priorities, identify the actionable steps that will lead you to an optimized data architecture

    Phase 1 and 2 helped you to identify tactics that address some of the most common business drivers. Phase 3 will bring you through the process of practically planning what those tactics look like in your organization’s environment and create a roadmap to plan how you will generate business value through optimization of your data architecture environment.

    Diagram of the three phases and the goals of each one. The first phase says 'Identify your data architecture business driver' and highlights 'Business Driver 3' out of four to focus on in Phase 2. Phase 2 says 'Optimization tactics across the five-tier logical data architecture' and identifies four of six 'Tactics' to use in Phase 3. Phase 3 is a 'Practical Roadmap of Initiatives' and utilizes a timeline of initiatives in which to apply the chosen tactics.

    Use the Data Architecture Tactic Roadmap Tool to personalize your roadmap

    Supporting Tool icon 3.1.1 Data Architecture Tactic Roadmap Tool
    Generating Your Roadmap
    1. On Tab 5. Tactic and Initiative Planning, you will find a list of tactics that correspond to every capability that applies to your chosen driver and where there is a gap. In addition, each tactic has a sequence of “Suggested Initiatives,” which represent the best-practice steps that you should take to optimize your data architecture according to your priorities and gaps.
    2. Customize this list of initiatives according to your needs.
    3. The Gantt chart is generated in Tab 7. Initiative Roadmap, and can be used to organize your plan and ensure that all of the essential aspects of optimizing data architecture are addressed.
    4. The roadmap can be used as an “executive brief” roadmap and as a communication tool for the business.
    Screenshot of the Data Architecture Tactic Roadmap Tool, Tab 5. Tactic and Initiative Planning.
    Tab 5. Tactic and Initiative Planning

    Screenshot of the Data Architecture Tactic Roadmap Tool, Tab 7. Initiative Roadmap.
    Tab 7. Initiative Roadmap

    Determine the details of your data architecture optimization activities

    Associated Activity icon 3.1.2 1 hour

    INPUT: Timing of initiatives for optimizing data architecture.

    OUTPUT: Optimization roadmap

    Materials: Data Architecture Tactic Roadmap Tool

    Participants: Data architect, Enterprise Architect

    Instructions

    1. With the list of suggested activities in place on Tab 5. Tactic and Initiative Planning, select whether or not the initiatives will be included in the roadmap. By default, all of the initiatives are set to “Yes.”
    2. Plan the sequence, starting time, and length of each initiative, as well as the assigned responsibility of the initiative in Tab 5. Tactic and Initiative Planning of the Data Architecture Tactic Roadmap Tool.
    3. The tool will a generate a Gantt chart based on the start and length of your initiatives.
    4. The Gantt chart is generated in Tab 7. Initiative Roadmap.
    Screenshot of the Data Architecture Tactic Roadmap Tool, Tab 5. Tactic and Initiative Planning. Tab 5. Tactic and Initiative Planning Screenshot of the Data Architecture Tactic Roadmap Tool, Tab 7. Initiative Roadmap. Tab 7. Initiative Roadmap

    Info-Tech Insight

    The activities that populate the roadmap can be taken as best practice activities. If you want an actionable, comprehensive, and prescriptive plan for optimizing your data architecture, fill in the timing of the activities and print the roadmap. This can serve as a rapid communication tool for your data architecture plan to the business and other architects.

    Optimizing data architecture relies on communication between the business and data workers

    Remember: Data architects bridge the gap between strategic and technical requirements of data.

    Visualization centering the 'Data Architect' as the bridge between 'Data Workers', 'Business', and 'Data & Applications'.

    Therefore, as you plan the data and its interactions with applications, it is imperative that you communicate the plan and its implications to the business and the data workers. Stock photo of coworkers communicating.
    Also remember: In Phase 1, you built your tactical data architecture optimization plan.
    Sample 1 of the Data Architecture Optimization Template. Sample 2 of the Data Architecture Optimization Template.
    Use this document to communicate your plan for data architecture optimization to both the business and the data workers. Socialize this document as a representation of your organization’s current data architecture as well as where it is headed in the future.

    Communicate your data architecture optimization plan to the business for approval

    Associated Activity icon 3.1.3 2 hours

    INPUT: Data Architecture Tactical Roadmap

    OUTPUT: Communication plan

    Materials: Data Architecture Optimization Template

    Participants: Data Architect, Business representatives, IT representatives

    Instructions

    Begin by presenting your plan and roadmap to the business units who participated in business interviews in activity 1.1.3 of Phase 1.

    If you receive feedback that suggests that you should make revisions to the plan, consult Info-Tech Research Group for suggestions on how to improve the plan.

    If you gain approval for the plan, communicate it to DBAs and other data workers.

    Iterative optimization and communication plan:
    Visualization of the Iterative optimization and communication plan. 'Start here' at 'Communicate Plan and Roadmap to the Business', and then continue in a cycle of 'Receive Approval or Suggested Modifications', 'Get Advice for Improvements to the Plan', 'Revise Plan', and back to the initial step until you receive 'Approval', then 'Present to Data Workers'.

    With a roadmap in place, the monetary authority followed a tactical and practical plan to repair outdated data architecture

    CASE STUDY

    Industry: Financial
    Source: Info-Tech Consulting
    Symbol for 'Monetary Authority Case Study'.

    Part 3

    After establishing the appropriate tactics based on its business driver, the monetary authority was able to identify its shortcomings and adopt resolutions to remedy the issues.

    Challenge

    A monetary authority was placed under new requirements where it would need to produce 6 different report types on its clients to a regulatory body within a window potentially as short as 1 hour.

    With its current capabilities, it could complete such a task in roughly 7 days.

    The organization’s data architecture was comprised of legacy systems that had poor searchability. Moreover, the data it worked with was scanned from paper, regularly incomplete and often inconsistent.

    Solution

    The solution first required the organization to establish the business driver behind the need to optimize its architecture. In this case, it would be compliance requirements.

    With Info-Tech’s methodology, the organization focused on three tiers: data sources, warehousing, and analytics.

    Several solutions were developed to address the appropriate lacking capabilities. Firstly, the creation of a data model for old and new systems. The implementation of governance principles and business rules for migration of any data. Additionally, proper indexing techniques and business data glossary were established. Lastly, data marts and sandboxes were designed for data accessibility and to enable a space for proper report building.

    Results

    With the solutions established, the monetary authority was given information it needed to build a comprehensive roadmap, and is currently undergoing the implementation of the plan to ensure it will experience its desired outcome – an optimized data architecture built with the capacity to handle external compliance requirements.

    Phase 3, Step 2: Manage Your Data Architecture Decisions and the Resulting Changes

    PHASE 3

    3.13.2
    Personalize Your Data Architecture RoadmapManage Your Data Architecture Decisions and the Resulting Changes

    This step will walk you through the following activities:

    • With a plan in place, document the major architectural decisions that have been and will be made to optimize data architecture.
    • Create a plan for change and release management, an essential function of the data architect role.

    This step involves the following participants:

    • Data Architect
    • Enterprise Architect

    Outcomes of this step

    • Resources for documenting and managing the inevitable change associated with updates to the organization’s data architecture environment.

    To implement data architecture changes, you must plan to accommodate the issues that come with change

    Once you have a plan in place, one the most challenging aspects of improving an organization is yet to come…overcoming change!

    “When managing change, the job of the data architect is to avoid unnecessary change and to encapsulate necessary change.

    You must provide motivation for simplifying change, making it manageable for the whole organization.” (Andrew Johnston, Independent Consultant)

    Stock photo of multiple hands placing app/website design elements on a piece of paper.

    Create roadmap

    Arrow pointing down.

    Communicate roadmap

    Arrow pointing down.

    Implement roadmap

    Arrow pointing down.

    Change management

    Use the Data Architecture Decision Template when architectural changes are made

    Supporting Tool icon 3.2 Data Architecture Decision Template
    Document the architectural decisions made to provide context around changes made to the organization’s data environment.

    The goal of this Data Architecture Decision Template is to provide data architects with a template for managing the changes that accompany major architectural decisions. As you work through the Build a Business-Aligned Data Architecture Optimization Strategy blueprint, you will create a plan for tactical initiatives that address the drivers of the business to optimize your data architecture. This plan will bring about changes to the organization’s data architecture that need change management considerations.

    Document any major changes to the organization’s data architecture that are required to evolve with the organization’s drivers. This will ensure that major architectural changes are documented, tracked, and that the context around the decision is maintained.

    “Environment is very chaotic nowadays – legacy apps, sprawl, ERPs, a huge mix and orgs are grappling with what our data landscape look like? Where are our data assets that we need to use?” (Andrew Johnston, Independent Consultant)

    Sample of the Data Architecture Decision Template.

    Use Info-Tech’s Data Architecture Decision Template to document any major changes in the organization’s data architecture.

    Leverage Info-Tech’s resources to smooth change management

    As changes to the architectural environment occur, data architects must stay ahead of the curve and plan the change management considerations that come with major architectural decisions.

    “When managing change, the job of the data architect is to avoid unnecessary change and to encapsulate necessary change.

    You must provide motivation for simplifying change, making it manageable for the whole organization.” (Andrew Johnston, Independent Consultant)

    See Info-Tech’s resources on change management to smooth changes:
    Banner for the blueprint set 'Optimize Change Management' with subtitle 'Turn and face the change with a right-sized change management process'.
    Sample of the Optimize Change Management blueprint.

    Change Management Blueprint

    Sample of the Change Management Roadmap Tool.

    Change Management Roadmap Tool

    Use Info-Tech’s resources for effective release management

    As changes to the architectural environment occur, data architects must stay ahead of the curve and plan the release management considerations around new hardware and software releases or updates.

    Release management is a process that encompasses the planning, design, build, configuration, and testing of hardware and software releases to create a defined set of release components (ITIL). Release activities can include the distribution of the release and supporting documentation directly to end users. See Info-Tech’s resources on Release Management to smooth changes:

    Banner for the blueprint set 'Take a Holistic View to Optimize Release Management' with subtitle 'Build trust by right-sizing your process using appropriate governance'.
    Samples of the Release Management blueprint.

    Release Management Blueprint

    Sample of the Release Management Process Standard Template.

    Release Management Process Standard Template

    If you want additional support, have our analysts guide you through this phase as part of an Info-Tech Workshop Associated Activity icon

    Book a workshop with our Info-Tech analysts:

    Photo of a Info-Tech analyst.
    • To accelerate this project, engage your IT team in an Info-Tech workshop with an Info-Tech analyst team.
    • Info-Tech analyst will join you and your team onsite at your location or welcome you to Info-Tech's historic Toronto office to participate in an innovative onsite workshop.
    • Contact your account manager (www.infotech.com/account), or email Workshops@InfoTech.com for more information.

    The following are sample activities that will be conducted by Info-Tech analysts with your team:

    3.1.1

    Sample of activity 3.1.2 'Determine the timing of your data architecture optimization activities'. Create your personalized roadmap of activities.

    In this activity, the facilitator will guide the team in evaluating practice gaps highlighted by the assessment, and compare these gaps at face value so general priorities can be documented. The same categories as in 3.1.1 are considered.

    3.1.3

    Sample of activity 3.1.3 'Communicate your Data Architecture Optimization Plan to the business for approval'. Communicate your data architecture optimization plan.

    The facilitator will help you to identify the optimal medium and timing for communicating your plan for optimizing your data architecture.

    Insight breakdown

    Insight 1

    • Data architecture needs to evolve along with the changing business landscape. There are four common business drivers that put most pressure on archaic architectures. As a result, the organization’s architecture must be flexible and responsive to changing business needs.

    Insight 2

    • Data architecture is not just about models.
      Viewing data architecture as just technical data modeling can lead to structurally unsound data that does not serve the business.

    Insight 3

    • Data is used differently across the layers of an organization’s data architecture, and the capabilities needed to optimize use of data change with it. Architecting and managing data from source to warehousing to presentation requires different tactics for optimal use.

    Summary of accomplishment

    Knowledge Gained

    • An understanding of what data architecture is, how data architects can provide value to the organization, and how data architecture fits into the larger enterprise architecture picture.
    • The capabilities required for optimization of the organization’s data architecture across the five tiers of the logical data architecture model.

    Processes Optimized

    • Prioritization and planning of data architect responsibilities across the five tiers of the five-tier logical data architecture model.
    • Roadmapping of tactics that address the most common business drivers of the organization.
    • Architectural change management.

    Deliverables Completed

    • Data Architecture Driver Pattern Identification Tool
    • Data Architecture Optimization Template
    • Data Architecture Trends Presentation
    • Data Architecture Roadmap Tool
    • Data Architecture Decision Template

    Research contributors and experts

    Photo of Ron Huizenga, Senior Product Manager, Embarcadero Technologies, Inc. Ron Huizenga, Senior Product Manager
    Embarcadero Technologies, Inc.

    Ron Huizenga has over 30 years of experience as an IT executive and consultant in enterprise data architecture, governance, business process reengineering and improvement, program/project management, software development, and business management. His experience spans multiple industries including manufacturing, supply chain, pipelines, natural resources, retail, healthcare, insurance, and transportation.

    Photo of Andrew Johnston, Architect, Independent Consultant. Andrew Johnston, Architect Independent Consultant

    An independent consultant with a unique combination of managerial, commercial, and technical skills, Andrew specializes in the development of strategies and technical architectures that allow businesses to get the maximum benefit from their IT resources. He has been described by clients as a "broad spectrum" architect, summarizing his ability to engage in many problems at many levels.

    Research contributors

    Internal Contributors
    Logo for Info-Tech Research Group.
    • Steven J. Wilson, Senior Director, Research & Advisory Services
    • Daniel Ko, Research Manager
    • Bernie Gilles, Senior Director, Research & Advisory Services
    External Contributors
    Logo for Embarcadero.
    Logo for Questa Computing. Logo for Geha.
    • Ron Huizenga, Embercardo Technologies
    • Andrew Johnston, Independent Consultant
    • Darrell Enslinger, Government Employees Health Association
    • Anonymous Contributors

    Bibliography

    Allen, Mark. “Get the ETL Out of Here.” MarkLogic. Sep, 2016. Web. 25 Apr 2017.[http://www.marklogic.com/blog/get-the-etl-out-of-here/]

    Anadiotis, George. “Streaming hot: Real-time big data architecture matters.” ZDNet. Jan, 2017. Web. 25 Apr 2017. [http://www.zdnet.com/article/streaming-hot-real-time-big-data-architecture-matters/]

    Aston, Dan. “The Economic value of Enterprise Architecture and How to Show It.” Erwin. Aug, 2016. Web. 20 Apr 2017. [http://erwin.com/blog/economic-value-enterprise-architecture-show/]

    Baer, Tony. “2017 Trends to Watch: Big Data.” Ovum. Nov, 2016. Web. 25 Apr 2017.

    Bmc. “Benefits & Advantages of Hadoop.” Bmc. Web. 25 Apr 2017. [http://www.bmcsoftware.ca/guides/hadoop-benefits-business-case.html]

    Boyd, Ryan, et al. “Relational vs. Graph Data Modeling” DZone. Mar 2016. Web. 25 Apr 2017. [https://dzone.com/articles/relational-vs-graph-data-modeling]

    Brahmachar, Satya. “Theme To Digital Transformation - Journey to Data Driven Enterprise” Feb, 2015. Web. 20 Apr 2017. [http://satyabrahmachari-thought-leader.blogspot.ca/2015/02/i-smac-theme-to-digital-transformation.html]

    Capsenta. “NoETL.” Capsenta. Web. 25 Apr 2017. [https://capsenta.com/wp-content/uploads/2015/03/Capsenta-Booklet.pdf]

    Connolly, Shaun. “Implementing the Blueprint for Enterprise Hadoop” Hortonworks. Apr, 2014. Web. 25 Apr 2017. https://hortonworks.com/blog/implementing-the-blue...

    Forbes. “Cloud 2.0: Companies Move From Cloud-First To Cloud-Only.” Forbes. Apr, 2017. Web. 25 Apr 2017. [https://www.forbes.com/sites/vmware/2017/04/07/cloud-2-0-companies-move-from-cloud-first-to-cloud-only/#5cd9d94a4d5e]

    Forgeat, Julien. “Lambda and Kappa.” Ericsson. Nov 2015. Web 25 Apr 2017. [https://www.ericsson.com/research-blog/data-knowledge/data-processing-architectures-lambda-and-kappa/]

    Grimes, Seth. “Is It Time For NoETL?” InformationWeek. Mar, 2010. Web. 25 Apr 2017. [http://www.informationweek.com/software/information-management/is-it-time-for-noetl/d/d-id/1087813]

    Gupta, Manav. et al. “How IB‹ leads in building big data analytics solutions in the cloud.” IBM. Feb, 2016. Web. 25 Apr 2017. [https://www.ibm.com/developerworks/cloud/library/cl-ibm-leads-building-big-data-analytics-solutions-cloud-trs/index.html#N102DE]

    “How To Build A Roadmap.” Hub Designs Magazine. Web 25 Apr 2017. [https://hubdesignsmagazine.com/2011/03/05/how-to-build-a-roadmap/]

    IBM. “Top industry use cases for stream computing.” IBM. Oct, 2015. Web. 25 Apr 2017. [https://www-01.ibm.com/common/ssi/cgi-bin/ssialias?htmlfid=IMW14704USEN]

    Mateos-Garcia, Juan, et al. “Skills Of The Datavores.” Nesta. July. 2015. Web. 8 Aug 2016. [https://www.nesta.org.uk/sites/default/files/skills_of_the_datavores.pdf].

    Maynard, Steven. “Analytics: Don’t Forget The Human Element” Forbes. 2015. Web. 20 Apr. 2017. [http://www.ey.com/Publication/vwLUAssets/EY-Forbes-Insights-Data-and-Analytics-Impact-Index-2015/$FILE/EY-Forbes-Insights-Data-and-Analytics-Impact-Index-2015.pdf]

    Neo4j. “From Relational to Neo4j.” Neo4j. Web. 25 Apr 2017. [https://neo4j.com/developer/graph-db-vs-rdbms/#_from_relational_to_graph_databases]

    NoETL “NoETL.” NoETL. Web. 25 Apr 2017. [http://noetl.org/]

    Nolan, Roger. “Digital Transformation: Is Your Data Management Ready?” Informatica. Jun, 2016. Web. 20 Apr 2017. [https://blogs.informatica.com/2016/06/10/digital-transformation-data-management-ready/#fbid=hmBYQgS6hnm]

    OpsClarity. “2016 State of Fast Data & Streaming Applications.” OpsClarity. Web. 25 Apr 2017. [https://www.opsclarity.com/wp-content/uploads/2016/07/2016FastDataSurvey.pdf]

    Oracle. “A Relational Database Overview.” Oracle. Web. 25 Apr 2017. [https://docs.oracle.com/javase/tutorial/jdbc/overview/database.html]

    Ponemon Institute LLC. “Big Data Cybersecurity Analytics Research Repor.t” Cloudera. Aug, 2016. Web. 25 Apr 2017. [https://www.cloudera.com/content/dam/www/static/documents/analyst-reports/big-data-cybersecurity-analytics-research-report.pdf]

    Sanchez, Jose Juan. “Data Movement Killed the BI Star.” DV Blog. May, 2016. Web. 20 Apr. 2017. [http://www.datavirtualizationblog.com/data-movement-killed-the-bi-star/]

    SAS. “Hadoop; What it is and why does it matter?” SAS. Web. 25 Apr 2017. [https://www.sas.com/en_ca/insights/big-data/hadoop.html#hadoopusers]

    Schumacher, Robin. “A Quick Primer on graph Databases for RDBMS Professionals.” Datastax. Jul, 2016. Web. 25 Apr 2017. [http://www.datastax.com/2016/07/quick-primer-on-graph-databases-for-rdbms-professionals]

    Swoyer, Steve. “It’s the End of the Data Warehouse as We Know It.” TDWI. Jan, 2017. Web. 20 Apr. 2017. [https://upside.tdwi.org/articles/2017/01/11/end-of-the-data-warehouse-as-we-know-it.aspx]

    Webber, Jim, and Ian Robinson. “The Top 5 Use Cases of Graph Databases.” Neo4j. 2015. Web. 25 Apr 2017. [http://info.neo4j.com/rs/773-GON-065/images/Neo4j_Top5_UseCases_Graph%20Databases.pdf]

    Zachman Framework. [https://www.zachman.com/]

    Zupan, Jane. “Survey of Big Data Decision Makers.” Attiv/o. May, 2016. Web. 20 Apr 2017. [https://www.attivio.com/blog/post/survey-big-data-decision-makers]

    Drive Business Value With Off-the-Shelf AI

    • Buy Link or Shortcode: {j2store}205|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Business Intelligence Strategy
    • Parent Category Link: /business-intelligence-strategy
    • Understanding the impact of the machine learning/AI component that is built into most of the enterprise products and tools and its role in the implementation of the solution.
    • Understanding the most important aspects that the organization needs to consider while planning the implementation of the AI-powered product.

    Our Advice

    Critical Insight

    • Organizations are faced with multiple challenges trying to adopt AI solutions. Challenges include data issues, ethics and compliance considerations, business process challenges, and misaligned leadership goals.
    • When choosing the right product to meet business needs, organizations need to know what questions to ask vendors to ensure they fully understand the implications of buying an AI/ML product.
    • To guarantee the success of your off-the-shelf AI implementation and ensure it delivers value, you must start with a clear definition of the business case and an understanding of your data.

    Impact and Result

    To guarantee success of the off-the-shelf AI implementation and deliver value, in addition to formulating a clear definition of the business case and understanding of data, organizations should also:

    • Know what questions to ask vendors while evaluating AI-powered products.
    • Measure the impact of the project on business and IT processes.

    Drive Business Value With Off-the-Shelf AI Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Drive Business Value With Off-the-Shelf AI Deck – A step-by-step approach that will help guarantee the success of your Off-the-Shelf AI implementation and ensure it delivers business value

    Use this practical and actionable framework that will guide you through the planning of your Off-the-Shelf AI product implementation.

    • Drive Business Value With Off-the-Shelf AI Storyboard

    2. Off-the-Shelf AI Analysis – A tool that will guide the analysis and planning of the implementation

    Use this analysis tool to ensure the success of the implementation.

    • Off-the-Shelf AI Analysis

    Infographic

    Further reading

    Drive Business Value With Off-the-Shelf AI

    A practical guide to ensure return on your Off-the-Shelf AI investment

    Executive Summary

    Your Challenge
    • Understanding the impact of the machine learning/AI component that is built into most of the enterprise products and tools and its role in the implementation of the solution.
    • What are the most important aspects that organizations needs to consider while planning the implementation of the AI-powered product?
    Common Obstacles
    • Organizations are faced with multiple challenges trying to adopt an AI solution. Challenges include data issues, ethics and compliance considerations, business process challenges, and misaligned leadership goals.
    • When choosing the right product to meet business needs, organizations need to know what questions to ask vendors to ensure they fully understand the implications of buying an AI/ML product.
    Info-Tech’s Approach

    Info-Tech’s approach includes a framework that will guide organizations through the process of the Off-the-Shelf AI product selection.

    To guarantee success of the Off-the-Shelf AI implementation and deliver value, organization should start with clear definition of the business case and an understanding of data.

    Other steps include:

    • Knowing what questions to ask vendors to evaluate AI-powered products.
    • Measuring the impact of the project on your business and IT processes.
    • Assessing impact on the organization and ensure team readiness.

    Info-Tech Insight

    To guarantee the success of your Off-the-Shelf AI implementation and ensure it delivers value, you must start with a clear definition of the business case and an understanding of your data.

    Info-Tech offers various levels of support to best suit your needs

    DIY Toolkit

    Guided Implementation

    Workshop

    Consulting

    "Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful." "Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track." "We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place." "Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project."

    Diagnostics and consistent frameworks used throughout all four options

    Getting value out of AI and machine learning investments

    92.1%

    of companies say they are achieving returns on their data and AI investments

    91.7%

    said they were increasing investments in data and AI

    26.0%

    of companies have AI systems in widespread production
    However, CIO Magazine identified nine main hurdles to AI adoption based on the survey results:
    • Data issues
    • Business process challenges
    • Implementation challenges and skill shortages
    • Costs of tools and development
    • Misaligned leadership goals
    • Measuring and proving business value
    • Legal and regulatory risks
    • Cybersecurity
    • Ethics
    • (Source: CIO, 2019)
    “Data and AI initiatives are becoming well established, investments are paying off, and companies are getting more economic value from AI.” (Source: NewVantage, 2022.)

    “67% of companies are currently using machine learning, and 97% are using or planning to use it in the next year.” (Source: Deloitte, 2020)

    AI vs. ML

    Machine learning systems learn from experience and without explicit instructions. They learn patterns from data then analyze and make predictions based on past behavior and the patterns learned.

    Artificial intelligence is a combination of technologies and can include machine learning. AI systems perform tasks mimicking human intelligence such as learning from experience and problem solving. Most importantly, AI is making its own decisions without human intervention.

    The AI system can make assumptions, test these assumptions, and learn from the results.

    (Level of decision making required increases from left to right)
    Statistical Reasoning
    Infer relationships between variables

    Statistical models are designed to find relationships between variables and the significance of those relationships.

    Machine Learning:
    Making accurate predictions

    Machine learning is a subset of AI that discovers patterns from data without being explicitly programmed to do so.

    Artificial Intelligence
    Dynamic adaptation to novelty

    AI systems choose the optimal combination of methods to solve a problem. They make assumptions, reassess the model, and reevaluate the data.

    “Machine learning is the study of computer algorithms that improve automatically through experience.” (Tom Mitchell, 1997)

    “At its simplest form, artificial intelligence is a field, which combines computer science and robust datasets, to enable problem-solving.” (IBM, “What is artificial intelligence?”)

    Types of Off-the-Shelf AI products and solutions

    ML/AI-Powered Products Off-the-Shelf Pre-built and Pre-trained AI/ML Models
    • AI/ML capabilities built into the product and might require training as part of the implementation.
    • Off-the-Shelf ML/AI Models, pre-built, pre-trained, and pre-optimized for a particular task. For example, language models or image recognition models that can be used to speed up and simplify ML/AI systems development.
    Examples of OTS tools/products: Examples of OTS models:

    The data inputs for these models are defined, the developer has to conform to the provided schema, and the data outputs are usually fixed due to the particular task the OTS model is built to solve.

    Insight summary

    Overarching insight:

    To guarantee the success of your Off-the-Shelf AI implementation and ensure it delivers value, you must start with a clear definition of the business case and an understanding of your data.

    Business Goals

    Question the value that AI adds to the tool you are evaluating. Don’t go after the tool simply because it has an AI label attached to it. AI/ML capabilities might add little value but increase implementation complexity. Define the problem you are solving and document business requirements for the tool or a model.

    Data

    Know your data. Determine data requirements to:

    • Train the model during the implementation and development.
    • Run the model in production.

    People/Skills

    Define the skills required for the implementation and assemble the team that will support the project from requirements to deployment and support, through its entire lifecycle. Don’t forget about production support and maintenance.

    Choosing an AI-Powered Tool

    No need to reinvent the wheel and build a product you can buy, but be prepared to work around tool limitations, and make sure you understand the data and the model the tool is built on.

    Choosing an AI/ML Model

    Using Off-the-Shelf-AI models enables an agile approach to system development. Faster POC and validation of ideas and approaches, but the model might not be customizable for your requirements.

    Guaranteeing Off-the-Shelf AI Implementation Success

    Info-Tech Insight

    To guarantee the success of your Off-the-Shelf AI implementation and ensure it delivers value, you must start with a clear definition of the business case and an understanding of your data.

    Why do you need AI in your toolset?
    Business Goals

    Clearly defined problem statement and business requirements for the tool or a model will help you select the right solution that will deliver business value even if it does not have all the latest bells and whistles.

    Small chevron pointing right.
    Do you know the data required for implementation?
    Data

    Expected business outcome defines data requirements for implementation. Do you have the right data required to train and run the model?

    Large chevron pointing right.
    Is your organization ready for AI?
    People/Team/ Skills

    New skills and expertise are required through all phases of the implementation: design, build, deployment, support, and maintenance, as well as post-production support, scaling, and adoption.

    Data Architecture/ Infrastructure

    New tool or model will impact your cloud and integration strategy. It will have to integrate with the existing infrastructure, in the cloud or on prem.

    Large chevron pointing right.
    What questions do you need to ask when choosing the solution?
    Product/ Tool or Model Selection

    Do you know what model powers the AI tool? What data was used to train the tool and what data is required to run it? Ask the right questions.

    Small chevron pointing right.
    Are you measuring impact on your processes?
    Business and IT Processes

    Business processes need to be defined or updated to incorporate the output of the tool back into the business processes to deliver value.

    IT governance and support processes need to accommodate the new AI-powered tool.

    Small chevron pointing right.
    Realize and measure business value of your AI investment
    Value

    Do you have a clear understanding of the value that AI will bring to your organization?Optimization?Increased revenue?Operational efficiency?

    Introduction of Off-the-Shelf AI Requires a Strategic Approach

    Business Goals and Value Data People/Team/ Skills Infrastructure Business and IT Processes
    AI/ML–powered tools
    • Define a business problem that can be solved with either an AI-powered tool or an AI/ML pre-built model that will become part of the solution.
    • Define expectations and assumptions around the value that AI can bring.
    • Document business requirements for the tool or model.
    • Define the scope for a prototype or POC.
    • Define data requirements.
    • Define data required for implementation.
    • Determine if the required data can be acquired or captured/generated.
    • Document internal and external sources of data.
    • Validate data quality (define requirements and criteria for data quality).
    • Define where and how the data is stored and will be stored. Does it have to be moved or consolidated?
    • Define all stakeholders involved in the implementation and support.
    • Define skills and expertise required through all phases of the implementation: design, build, deployment, support, and maintenance.
    • Define skills and expertise required to grow AI practice and achieve the next level of adoption, scaling, and development of the tool or model POC.
    • Define infrastructure requirements for either Cloud, Software-as-a-Service, or on-prem deployment of a tool or model.
    • Define how the tool is integrated with existing systems and into existing infrastructure.
    • Determine the cost to deploy and run the tool/model.
    • Define processes that need to be updated to accommodate new functionality.
    • Define how the outcome of the tool or a model (e.g. predictions) are incorporated back into the business processes.
    • Define new business and IT processes that need to be defined around the tool (e.g. chatbot maintenance; analysis of the data generated by the tool).
    Off-the-shelf AI/ML pre-built models
    • Define the business metrics and KPIs to measure success of the implementation against.
    • Determine if there are requirements for a specific data format required for the tool or a model.
    • Determine if there is a need to classify/label the data (supervised learning).
    • Define privacy and security requirements.
    • Define requirements for employee training. This can be vendor training for a tool or platform training in the case of a pre-built model or service.
    • Define if ML/AI expertise is required.
    • Is the organization ready for ML/AI? Conduct an AI literacy survey and understand team’s concerns, fears, and misconceptions and address them.
    • Define requirements for:
      • Data migration.
      • Security.
      • AI/ML pipeline deployment and maintenance.
    • Define requirements for operation and maintenance of the tool or model.
    • Confirm infrastructure readiness.
    • How AI and its output will be used across the organization.

    Define Business Goals and Objectives

    Why do you need AI in your toolset? What value will AI deliver? Have a clear understanding of business benefits and the value AI delivers through the tool.

    • Define a business problem that can be solved with either an AI-powered tool or AI/ML pre-built model.
    • Define expectations and assumptions around the value that AI can bring.
    • Document business requirements for a tool or model.
    • Start with the POC or a prototype to test assumptions, architecture, and components of the solution.
    • Define business metrics and KPIs to measure success of the implementation.

    Info-Tech Insight

    Question the value that AI adds to the tool you are evaluating. Don’t go after the tool simply because it has an AI label attached to it. AI/ML capabilities might add little value but increase implementation complexity. Define the problem you are solving and document business requirements for the tool or a model.

    Venn diagram of 'Applied Artificial Intelligence (AAI)' with a larger circle at the top, 'Machine Learning (ML)', and three smaller ovals intersecting, 'Computer Vision', 'Natural Language Processing (NLP)', and 'Robotic Process Automation (RPA)'.

    AAI solutions and technologies are helping organizations make faster decisions and predict future outcomes such as:

    • Business process automation
    • Intelligent integration
    • Intelligent insights
    • Operational efficiency improvement
    • Increase revenue
    • Improvement of existing products and services
    • Product and process innovation

    1. Use Info-Tech’s Off-the-Shelf AI Analysis Tool to define business drivers and document business requirements

    2-3 hours
    Screenshot of the Off-the-Shelf AI Analysis Tool's Business Drivers tab, a table with columns 'AI/ML Tool or Model', 'Use Case', 'Business problem / goal for AI/ML use case', 'Description', 'Business Owner (Primary Stakeholder)', 'Priority', 'Stakeholder Groups Impacted', 'Requirements Defined? Yes/No', 'Related Data Domains', and 'KPIs'. Use the Business Drivers tab to document:
    • Business objectives of the initiative that might drive the AI/ML use case.
    • The business owner or primary stakeholder who will help to define business value and requirements.
    • All stakeholders who will be involved or impacted.
    • KPIs that will be used to assess the success of the POC.
    • Data required for the implementation.
    • Use the Business Requirements tab to document high-level requirements for a tool or model.
    • These requirements will be used while defining criteria for a tool selection and to validate if the tool or model meets your business goals.
    • You can use either traditional BRD format or a user story to document requirements.
    Screenshot of the Off-the-Shelf AI Analysis Tool's Business Requirements tab, a table with columns 'Requirement ID', 'Requirement Description / user story', 'Requirement Category', 'Stakeholder / User Role', 'Requirement Priority', and 'Complexity (point estimates)'.

    Download the Off-the-Shelf AI Analysis Tool

    1. Define business drivers and document business requirements

    Input

    • Strategic plan of the organization
    • Data strategy that defines target data capabilities required to support enterprise strategic goals
    • Roadmap of business and data initiatives to support target state of data capabilities

    Output

    • Prioritized list of business use cases where an AI-powered tool or AI/ML can deliver business value
    • List of high-level requirements for the selected use case

    Materials

    • Whiteboard/Flip Charts
    • Off-the-Shelf-AI Analysis Tool, “Business Drivers” and “Business Requirements” tabs

    Participants

    • CIO
    • Senior business and IT stakeholders
    • Data owner(s)
    • Data steward(s)
    • Enterprise Architect
    • Data Architect
    • Data scientist/Data analyst

    Understand data required for implementation

    Do you have the right data to implement and run the AI-powered tool or AI/ML model?

    Info-Tech Insight

    Know your data. Determine data requirements to:

    • Train the model during the implementation and development, and
    • Run the model in production
    AvailabilityArrow pointing rightQualityArrow pointing rightPreparationArrow pointing rightBias, Privacy, SecurityArrow pointing rightData Architecture
    • Define what data is required for implementation, e.g. customer data, financial data, product sentiment.
    • If the data is not available, can it be acquired, gathered, or generated?
    • Define the volume of data required for implementation and production.
    • If the model has to be trained, do you have the data required for training (e.g. dictionary of terms)? Can it be created, gathered, or acquired?
    • Document internal and external sources of data.
    • Evaluate data quality for all data sources based on the requirements and criteria defined in the previous step.
    • For datasets with data quality issues, determine if the data issues can be resolved (e.g. missing values are inferred). If not, can this issue be resolved by using other data sources?
    • Engage a Data Governance organization to address any data quality concerns.
    • Determine if there are requirements for a specific data format required for the tool or model.
    • Determine if there is a need to classify/label or tag the data. What are the metadata requirements?
    • Define whether or not the implementation team needs to aggregate or transform the data before it can be used.
    • Define privacy requirements, as these might affect the availability of the data for ML/AI.
    • Define data bias concerns and considerations. Do you have datasheets for datasets that will be used in this project? What datasets cannot be used to prevent bias?
    • What are the security requirements and how will they affect data storage, product selection, and infrastructure requirements for the tool and overall solution?
    • Define where and how the data is currently stored and will be stored.
    • Does it have to be migrated or consolidated? Does it have to be moved to the cloud or between systems?
    • Is a data lake or data warehouse a requirement for this implementation as defined by the solution architecture?

    2. Use Info-Tech’s Off-the-Shelf AI Analysis Tool to document data requirements

    2-3 hours

    Use the Data tab to document the following for each data source or dataset:
    • Data Domain – e.g. Customer data
    • Data Concept – e.g. Customer
    • Data Internally Accessible – Identify datasets that are required for the implementation even if the data might not be available internally. Work on determining if the data ca be acquired externally or collected internally.
    • Source System – define the primary source system for the data, e.g. Salesforce
    • Target System (if applicable) – Define if the data needs to be migrated/transferred. For example, you might use a datalake or data warehouse for the AI/ML solution or migrate data to the cloud.
    • Classification/Taxonomy/Ontology
    • Data Steward
    • Data Owner
    • Data Quality – Data quality indicator
    • Refresh Rate – Frequency of data refresh. Indicate if the data can be accessed in real time or near-real time

    Screenshot of the Off-the-Shelf AI Analysis Tool's Data tab, a spreadsheet table with the columns listed to the left and below.
    • Retention – Retention policy requirements
    • Compliance Requirements – Define if data has to comply with any of the regulatory requirements, e.g. GDPR
    • Privacy, Bias, and Ethics Considerations – Privacy Act, PIPEDA, etc. Identify if the dataset contains sensitive information that should be excluded from the model, such as gender, age, race etc. Indicate fairness metrics, if applicable.

    Download the Off-the-Shelf AI Analysis Tool

    2. Document data requirements

    Input

    • Documented business use cases from Step 1.
    • High-level business requirements from Step 1.
    • Data catalog, data dictionaries, business glossary
    • Data flows and data architecture

    Output

    • High-level data requirements
    • List of data sources and datasets that can be used for the implementation
    • Datasets that need to be collected or acquired externally

    Materials

    • Whiteboard/Flip Charts
    • Off-the-Shelf AI Analysis Tool, “Data” tab

    Participants

    • CIO
    • Business and IT stakeholders
    • Data owner(s)
    • Data steward(s)
    • Enterprise Architect
    • Data Architect
    • Data scientist/Data analyst

    Is Your Organization Ready for AI?

    Assess organizational readiness and define stakeholders impacted by the implementation. Build the team with the right skillset to drive the solution.

    • Implementation of the AI/ML-powered Off-the-Shelf Tool or an AI/ML model will require a team with a combination of skills through all phases of the project, from design of the solution to build, production, deployment, and support.
    • Document the skillsets required and determine the skills gap. Before you start hiring, depending on the role, you might find talent within the organization to join the implementation team with little to no training.
    • AI/ML resources that may be needed on your team driving AI implementation (you might consider bringing part-time resources to fill the gaps or use vendor developers) are:
      • Data Scientist
      • Machine Learning Engineer
      • Data Engineer
      • Data Architect
      • AI/ML Ops engineer
    • Define training requirements. Consider vendor training for a tool or platform.
    • Plan for future scaling and the growing of the solution and AI practice. Assess the need to apply AI in other business areas. Work with the team to analyze use cases and prioritize AI initiatives. As the practice grows, grow your team expertise.
    • Identify the stakeholders who will be affected by the AI implementation.
    • Work with them to understand and address any concerns, fears, or misconceptions around the role of AI and the consequences of bringing AI into the organization.
    • Develop a communication and change management plan to educate everyone within the organization on the application and benefits of using AI and machine learning.

    Info-Tech Insight:

    Define the skills required for the implementation and assemble the team that will support the project through its entire lifecycle. Don’t forget about production, support, and maintenance.

    3. Build your implementation team

    1-2 hours

    Input: Solution conceptual design, Current resource availability

    Output: Roles required for the implementation of the solution, Resources gap analysis, Training and hiring plan

    Materials: Whiteboard/Flip charts, Off-the-Shelf AI Analysis Tool, “People and Team” tab

    Participants: Project lead, HR, Enterprise Architect

    1. Review your solution conceptual design and define implementation team roles.
    2. Document requirements for each role.
    3. Review current org chart and job descriptions and identify skillset gaps. Draft an action plan to fill in the roles.
    4. Use Info-Tech’s Off-the-Shelf AI Analysis Tool's People and Team tab to document team roles for the entire implementation, including design, build/implement, deployment, support and maintenance, and future development.

    Screenshot of the Off-the-Shelf AI Analysis Tool's People and Team tab, a table with columns 'Design', 'Implement', 'Deployment', 'Support and Maintenance', and 'Future Development'.

    Download the Off-the-Shelf AI Analysis Tool

    Cloud, SaaS or On Prem – what are my options and what is the impact?

    Depending on the architecture of the solution, define the impact on the current infrastructure, including system integration, AI/ML pipeline deployment, maintenance, and data storage

    • Data Architecture: use the current data architecture to design the architecture for an AI-powered solution. Assess changes to the data architecture with the introduction of a new tool to make sure it is scalable enough to support the change.
    • Define infrastructure requirements for either Cloud, Software-as-a-Service, or on-prem deployment of a tool or model.
    • Define how the tool will be integrated with existing systems and into existing infrastructure.
    • Define requirements for:
      • Data migration and data storage
      • Security
      • AI/ML pipeline deployment, production monitoring, and maintenance
    • Define requirements for operation and maintenance of the tool or model.
    • Work with your infrastructure architect and vendor to determine the cost of deploying and running the tool/model.
    • Make a decision on the preferred architecture of the system and confirm infrastructure readiness.

    Download the Create an Architecture for AI blueprint

    4. Use Info-Tech’s Off-the-Shelf AI Analysis Tool to document infrastructure decisions

    2-3 hours

    Input: Solution conceptual design

    Output: Infrastructure requirements, Infrastructure readiness assessment

    Materials: Whiteboard/Flip charts, Off-the-Shelf AI Analysis Tool, “Infrastructure” tab

    Participants: Infrastructure Architect, Solution Architect, Enterprise Architect, Data Architect, ML/AI Ops Engineer

    1. Work with Infrastructure, Data, Solution, and Enterprise Architects to define your conceptual solution architecture.
    2. Define integration and storage requirements.
    3. Document security requirements for the solution in general and the data specifically.
    4. Define MLOps requirements and tools required for ML/AI pipeline deployment and production monitoring.
    5. Use Info-Tech’s Off-the-Shelf AI Analysis Tool's Infrastructure tab to document requirements and decisions around Data and Infrastructure Architecture.

    Screenshot of the Off-the-Shelf AI Analysis Tool's Infrastructure tab, a table with columns 'Cloud, SaaS or On-Prem', 'Data Migration Requirements', 'Data Storage Requirements', 'Security Requirements', 'Integrations Required', and 'AI/ML Pipeline Deployment and Maintenance Requirements'.

    Download the Off-the-Shelf AI Analysis Tool

    What questions do you need to ask vendors when choosing the solution?

    Take advantage of Info-Tech’s Rapid Application Selection Framework (RASF) to guide tool selection, but ask vendors the right questions to understand implications of having AI/ML built into the tool or a model

    Data Model Implementation and Integration Deployment Security and Compliance
    • What data (attributes) were used to train the model?
    • Do you have datasheets for the data used?
    • How was data bias mitigated?
    • What are the data labeling/classification requirements for training the model?
    • What data is required for production? E.g. volume; type of data, etc.
    • Were there any open-source libraries used in the model? If yes, how were vulnerabilities and security concerns addressed?
    • What algorithms are implemented in the tool/model?
    • Can model parameters be configured?
    • What is model accuracy?
    • Level of customization required for the implementation to meet our requirements.
    • Does the model require training? If yes, can you provide details? Can you estimate the effort required?
    • Integration capabilities and requirements.
    • Data migration requirements for tool operation and development.
    • Administrator console – is this functionality available?
    • Implementation timeframe.
    • Is the model or tool deployable on premises or in the cloud? Do you support hybrid cloud and multi-cloud deployment?
    • What cloud platforms are your product/model integrated with (AWS, Azure, GCP)?
    • What are the infrastructure requirements?
    • Is the model containerized/ scalable?
    • What product support and product updates are available?
    • Regulatory compliance (GDPR, PIPEDA, HIPAA, PCI DSS, CCPA, SOX, etc.)?
    • How are data security risks addressed?

    Use Info-Tech’s Off-the-Shelf AI Analysis Tool, “Vendor Questionnaire” tab to track vendor responses to these questions.

    Are you measuring impact on your processes?

    Make sure that you understand the impact of the new technology on the existing business and IT processes.

    And make sure your business processes are ready to take advantage of the benefits and new capabilities enabled by AI/ML.

    Process automation, optimization, and improvement enabled by the technology and AI/ML-powered tools allow organizations to reduce manual work, streamline existing business processes, improve customer satisfaction, and get critical insights to assist decision making.

    To take full advantage of the benefits and new capabilities enabled by the technology, make sure that business and IT processes reflect these changes:

    • Processes that need to be updated.
    • How the outcome of the tool or a model (e.g. predictions) is incorporated into the existing business processes and the processes that will monitor the accuracy of the outcome and monitor performance of the tool or model.
    • New business and IT processes that need to be defined for the tool (e.g. chatbot maintenance, analysis of the data generated by the tool, etc.).

    5. Document the Impact on Business and IT Processes

    2-3 hours

    Input: Solution design, Existing business and IT processes

    Output: Documented updates to the existing processes, Documented new business and IT processes

    Materials: Whiteboard/Flip charts, Off-the-Shelf AI Analysis Tool, “Business and IT Processes” tab

    Participants: Project lead, Business stakeholders, Business analyst

    1. Review current business processes affected by the implementation of the AI/ML- powered tool or model. Define the changes that need to be made. The changes might include simplification of the process due to automation of some of the steps. Some processes will need to be redesigned and some processes might become obsolete.
    2. Document high-level steps for any new processes that need to be defined around the AI/ML-powered tool. An example of such a process would be defining new IT and business processes to support a new chatbot.
    3. Use Info-Tech’s Off-the-Shelf AI Analysis Tool's Business and IT Processes tab, to document process changes.

    Screenshot of the Off-the-Shelf AI Analysis Tool's Business and IT Processes tab, a table with columns 'Existing business process affected', 'New business process', 'Stakeholders involved', 'Changes to be made', and 'New Process High-Level Steps'.

    Download the Off-the-Shelf AI Analysis Tool

    AI-powered Tools – Considerations

    PROS:
    • Enhanced functionality, allows the power of AI without specialized skills (e.g., Mathematica – recognizing patterns in data).
    • Might be a cheaper option compared to building a solution in-house (chatbot, for ex.).

    Info-Tech Insight:

    No need to reinvent the wheel and build the product you can buy, but be prepared to work around tool limitations, and make sure you understand the data and the model the tool is built on.

    CONS:
    • Dependency on the service provider.
    • The tool might not meet all the business requirements without customization.
    • Bias can be built into the tool:
      • Work with the vendor to understand what data was used to train the model.
      • From the perspective of ethics and bias, learn what model is implemented in the tool and what data attributes the model uses.

    Pre-built/pre-trained models – what to keep in mind when choosing

    PROS:
    • Lower cost and less time to development compared to creating and training models from scratch (e.g. using image recognition models or pre-trained language models like BERT).
    • If the pre-trained and optimized model perfectly fits your needs, the model accuracy might be high and sufficient for your scenario.
    • Off-the-Shelf AI models are useful for creating prototypes or POCs, for testing a hypothesis, and for validating ideas and requirements.
    • Usage of Off-the-Shelf models shortens the development cycle and reduces investment risks.
    • Language models are particularly useful if you don’t have data to train your own model (a “small data” scenario).
    • Infrastructure and model training cost reduction.
    CONS:
    • Might be a challenge to deploy and maintain the system in production.
    • Lack of flexibility: you might not be able to configure input or output parameters to your requirements. For example, a pre-built sentiment analysis model might return four values (“positive,” “negative,” “neutral,” and “mixed”), but your solution will require only two or three values.
    • Might be a challenge to comply with security and privacy requirements.
    • Compliance with privacy and fairness requirements and considerations: what data was used to pretrain the model?
    • If open-source libraries were used to create the model, how will vulnerabilities, risks, and security concerns be addressed?

    Info-Tech Insight:

    Using Off-the-Shelf AI models enables an agile approach to system development – faster POC and validation of ideas and approaches, but the model might not be customizable for your requirements.

    Metrics

    Metrics and KPIs for this project will depend on the business goals and objectives that you will identify in Step 1 of the tool selection process.

    Metrics might include:

    • Reduction of time spent on a specific business process. If the tool is used to automate certain steps of a business process, this metric will measure how much time was saved, in minutes/hours, compared to the process time before the introduction of the tool.
    • Accuracy of prediction. This metric would measure the accuracy of estimations or predictions compared to the same estimations done before the implementation of the tool. It can be measured by generating the same prediction or estimation using the AI-powered tool or using any methods used before the introduction of the tool and comparing the results.
    • Accuracy of the search results. If the AI-powered tool is a search engine, compare a) how much time it would take a user to find an article or a piece of content they were searching for using new tool vs. previous techniques, b) how many steps it took the user to locate the required article in the search results, and c) the location of the correct piece of content in the search result list (at the top of the search result list or on the tenth page).
    • Time spent on manual tasks and activities. This metric will measure how much time, in minutes/hours, is spent by the employees or users on manual tasks if the tool automates some of these tasks.
    • Reduction of business process steps (if the steps are being automated). To derive this metric, create a map of the business process before the introduction of the AI-powered tool and after, and determine if the tool helped to simplify the process by reducing the number of process steps.

    Bibliography

    Adryan, Boris. “Is it all machine learning?” Badryan, Oct. 20, 2015. Accessed Feb. 2022.

    “AI-Powered Data Management Platform.” Informatica, N.d. Accessed Feb 2022.

    Amazon Rekognition. “Automate your image and video analysis with machine learning.” AWS. N.d. Accessed Feb 2022.

    “Artificial Intelligence (AI).” IBM Cloud Education, 3 June 2020. Accessed Feb 2022.

    “Artificial intelligence (AI) vs machine learning (ML).” Microsoft Azure Documentation. Accessed Feb. 2022.

    “Avante Garde in the Realm of AI” SearchUnify Cognitive Platform. Accessed Feb 2022.

    “Azure Cognitive Services.” Microsoft. N.d. Accessed Feb 2022.

    “Becoming an AI-fueled organization. State of AI in the enterprise, 4th edition,” Deloitte, 2020. Accessed Feb. 2022.

    “Coveo Predictive Search.” Coveo, N.d. Accessed Feb 2022.

    ”Data and AI Leadership. Executive Survey 2022. Executive Summary of Findings.” NewVantage Partners. Accessed Feb 2022.

    “Einstein Discovery in Tableau.” Tableau, N.d. Accessed Feb 2022.

    Korolov, Maria. “9 biggest hurdles to AI adoption.” CIO, Feb 26, 2019. Accessed Feb 2022.

    Meel, Vidushi. “What Is Deep Learning? An Easy to Understand Guide.” visio.ai. Accessed Feb. 2022.

    Mitchell, Tom. “Machine Learning,” McGraw Hill, 1997.

    Stewart, Matthew. “The Actual Difference Between Statistics and Machine Learning.” Towards Data Science, Mar 24, 2019. Accessed Feb 2022.

    “Sentiment analysis with Cognitive Services.” Microsoft Azure Documentation. Accessed February 2022.

    “Three Principles for Designing ML-Powered Products.” Spotify Blog. Oct 2019, Accessed Feb 2022.

    “Video Intelligence API.” Google Cloud Platform. N.d. Accessed Feb 2022

    Select Your Data Platform

    • Buy Link or Shortcode: {j2store}346|cart{/j2store}
    • member rating overall impact: 10.0/10 Overall Impact
    • member rating average dollars saved: $62,999 Average $ Saved
    • member rating average days saved: 20 Average Days Saved
    • Parent Category Name: Data Management
    • Parent Category Link: /data-management

    Every organization needs a data management (DM) platform that enables the DM capabilities required. This could be a daunting task because:

    • Every organization has a unique set of requirements for the DM platform.
    • Software products are difficult to compare because every vendor provides a unique set of features.
    • Software vendors are interested in getting as large a footprint as possible.
    • Some products from different categories offer the same functionalities.
    • Some products are just not compatible.

    Our Advice

    Critical Insight

    • Technology requirements start with the business goals.
    • Data platform selection should be based on common best practices and, at the same time, be optimized for the organization’s specific needs and goals and support an evolutionary platform development.
    • What is best for one organization may be totally unacceptable for another – all for very valid reasons.

    Impact and Result

    Understand your current environment and use proven reference architecture patterns to expedite building the data management platform that matches your needs.

    • Use a holistic approach.
    • Understand your goals and priorities.
    • Picture your target-state architecture.
    • Identify your current technology coverage.
    • Select the software covering the gaps in technology enablement based on feature/functional enablement descriptions as well as vendor and deployment preferences.

    Select Your Data Platform Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out what challenges are typically in the way of designing a data platform, review Info-Tech’s methodology, and understand how we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Select your data platform

    Assess your current environment, find the right reference architecture pattern, and match identified capabilities with software features.

    • Data Platform Design Assessment
    • Reference Architecture Pattern

    Infographic

    Make the Case for Legacy Application Modernization

    • Buy Link or Shortcode: {j2store}613|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Selection & Implementation
    • Parent Category Link: /selection-and-implementation
    • Organizations are under continual pressure to deliver faster, with shorter time-to-market, while introducing new products and services at the same time.
    • You and your team have concerns that your existing portfolio of applications is not up to the task.
    • While you understand the need for more investments to modernize your portfolio, your leadership does not appreciate what is required.

    Our Advice

    Critical Insight

    • Legacy modernization is a process, not a single event.
    • Your modernization approach requires you to understand your landscape and decide on a path that minimizes business continuity risks, keeps the investments under control, and is prepared for surprises but always has your final state in mind.

    Impact and Result

    • Evaluate the current state, develop a legacy application strategy, and execute in an agile manner.
    • When coupled with a business case and communications strategy, this approach gives the organization a clear decision-making framework that will maximize business outcomes and deliver value where needed.

    Make the Case for Legacy Application Modernization Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Make the Case for Legacy Application Modernization Storyboard – Understand legacy application modernization in the context of your organization, assess your landscape of applications, and define prioritization and disposition.

    This blueprint provides the steps necessary to build your own enterprise application implementation playbook that can be deployed and leveraged by your implementation teams.

    • Make the Case for Legacy Application Modernization Storyboard

    2. Make the Case for Legacy Application Modernization Presentation Template – The key output from leveraging this research is a presentation to pitch the modernization process.

    Build a proposal deck to make the case for legacy application modernization for your stakeholders. This will contain a definition of what a legacy application is in the context of your organization, a list of candidate applications to modernize, and a disposition strategy for each selected application.

    • Make the Case for Legacy Application Modernization Presentation Template
    [infographic]

    Further reading

    Make the Case for Legacy Application Modernization

    Revamp your business potential to improve agility, security, and user experience while reducing costs.

    Analyst Perspective

    An old application may have served us reliably, but it can prevent us from pursuing future business needs.

    Legacy systems remain well-embedded in the fabric of many organizations' application portfolios. They were often custom-built to meet the needs of the business. Typically, these are core tools that the business leverages to accomplish its goals.

    A legacy application becomes something we need to address when it no longer supports our business goals, is no longer supportable, bears an unsustainable ownership cost, or poses a threat to the organization's cybersecurity or compliance.

    When approaching your legacy application strategy, you must navigate a complex web of business, stakeholder, software, hardware, resourcing, and financial decisions. To complicate matters, the full scope of required effort is not immediately clear. Years of development are embedded in these legacy applications, which must be uncovered and dealt with appropriately.

    IT leaders require a proactive approach for evaluating the current state, developing a legacy application strategy, and executing in an agile manner. When coupled with a business case and communications strategy, the organization will have a clear decision-making framework that will maximize business outcomes and deliver value where needed.

    Ricardo de Oliveira, Research Director, Enterprise Applications

    Ricardo de Oliveira
    Research Director, Enterprise Applications
    Info-Tech Research Group

    Executive Summary

    Your Challenge Common Obstacles Info-Tech's Approach
    • Organizations face continual pressure to decrease time-to-market while also introducing new products and services.
    • You and your team have concerns that the existing application portfolio is not up to the task.
    • While you may understand the need for greater investment to modernize your portfolio, leadership does not appreciate what is required.
    • For well-established organizations, applications can have a long lifespan. Employees who are used to existing tools and processes often resist change.
    • Modernization plans can be substantial, but budget and resources are limited.
    • Poor documentation of legacy applications can make it challenging to know what to modernize and how to do it effectively.
    • There are concerns that any changes will have material impacts on business continuity.
    • Info-Tech will enable you to build a proposal deck to make the case for legacy application modernization for your stakeholders. This will assist with:
      • Defining what a legacy application is in the context of your organization.
      • Creating a list of candidate applications for modernization.
      • Articulating the right disposition strategy for each selected applications.
      • Laying out what is next on your modernization journey.

    Info-Tech Insight
    Legacy modernization is a process, not a single event. Your modernization approach requires you to understand your landscape and decide on a path that minimizes business continuity risks, keeps investments under control, and is prepared for surprises but always has your final state in mind.

    An approach to making the case for legacy application modernization

    Understand
    Assess the challenges, lay out the reasons, define your legacy, and prepare to remove the barriers to modernization.
    Assess
    Determine the benefits by business capability. Leverage APM foundations to select the candidate applications and prioritize.
    Legacy Application Modernization
    Define
    Use the prioritized application list to drive the next steps to modernization.

    Legacy application modernization is perceived as necessary to remain competitive

    The 2022 State CIO Survey by NASCIO shows that legacy application modernization jumped from fifth to second in state CIO priorities.

    "Be patient and also impatient. Patient because all states have a lot of legacy tech they are inheriting and government is NOT easy. But also, impatient because there is a lot to do - make your priorities clear but also find out what the CIO needs to accomplish those priorities."

    Source: NASCIO, 2022

    State CIO Priorities

    US government agencies feel pressured to deal with legacy applications

    In fiscal year 2021, the US government planned to spend over $100 billion on information technology. Most of that was to be used to operate and maintain existing systems, including legacy applications, which can be both more expensive to maintain and more vulnerable to hackers. The Government Accountability Office (GAO) identified:

    • 10 critical federal IT legacy systems
    • In operation between 8 and 51 years
    • Collectively cost $337 million per year to operate and maintain

    Source: U.S. Government Accountability Office, 2021

    Example: In banking, modern platforms are essential

    Increasing competition from fintech 73% of financial services executives perceive retail banking as being the most susceptible to fintech disruption (PwC, 2016)
    Growing number of neo-banks The International Monetary Fund (IMF) notes the fast growth of fintech in financial services is creating systemic risk to global financial stability (IMF, 2022)
    Access to data and advanced analytics Estimated global bank revenue lost due to poor data is 15% to 25% (MIT, 2017)
    Shifting client expectations/demographics 50% of Gen X, millennials, and Gen Z use a digital bank to provide their primary checking account (Finextra, 2022)
    Generational transfer of wealth It is estimated that up to US$68 trillion in wealth will be transferred from baby boomers (Forbes, 2021)

    Case Study

    Delta takes off with a modernized blend of mainframes and cloud

    INDUSTRY: Transportation
    SOURCE: CIO Magazine, 2023

    Challenge
    The airline has hundreds of applications in the process of moving to the cloud, but most main capabilities are underpinned by workloads on the mainframe and will remain so for the foreseeable future.
    Some of those workloads include travel reservation systems and crew scheduling systems - mission-critical, 24/7 applications that are never turned off.
    Solution
    Delta has shifted to a hybrid architecture, with a customer experience transformation that makes the most of the cloud's agility and the mainframe's dependability.
    Delta's foray into the cloud began about two years ago as the pandemic brought travel to a virtual halt. The airline started migrating many front-end and distributed applications to the cloud while retaining traditional back-end workloads on the mainframe.
    Results
    Hybrid infrastructures are expected to remain in complex industries such as airlines and banking, where high availability and maximum reliability are non-negotiable.
    While some CIOs are sharpening their mainframe exit strategies by opting for a steep journey to the cloud, mainframes remain ideal for certain workloads.

    Phase 1: Make the Case for Legacy Application Modernization

    Phase 1
    1.1 Understand your challenges
    1.2 Define legacy applications
    1.3 Assess your barriers
    1.4 Find the impacted capabilities
    1.5 Define candidate applications
    1.6 Now, Next, Later

    This phase will walk you through the following activities:

    • Understand your challenges with modernization
    • Define legacy applications in your context
    • Assess your barriers to modernization
    • Find the impacted capabilities and their benefits
    • Define candidate applications and dispositions

    This phase involves the following participants:

    • Application group leaders
    • Individual application owners

    Application Portfolio Management

    • Buy Link or Shortcode: {j2store}28|cart{/j2store}
    • Related Products: {j2store}28|crosssells{/j2store}
    • member rating overall impact: 9.1/10
    • member rating average dollars saved: $81,275
    • member rating average days saved: 20
    • Parent Category Name: Applications
    • Parent Category Link: /applications

    The challenge

    • The chances are that you, too, have too many or far too many applications in your organization. You will not be alone. Almost 60% of companies report the same issue. 
    • That is due to poorly managed portfolios.
    • Your application managers now need to support too many non-critical applications, and they spend insufficient time on the vital applications.
    • You can rarely find the required pieces to rationalize your portfolio in one place. You will need to find the resources and build a team.
    • The lack of standard practices to define the value that each application in a portfolio provides to the company causes misalignments.

    Our advice

    Insight

    • There is no silver bullet solution. Going too rigid in your approach causes delays in value realization through application portfolio management. It may even prevent this altogether. Define flexible inputs to your portfolio and align closely with your business goals.

    Impact and results 

    • Define the outputs of your application rationalization effort, with clear roles and responsibilities.
    • Tailor the application rationalization framework (ARF) to your company's motivations, goals, and limitations.
    • Apply various application assessments to build a clear picture of your portfolio.
    • Build an application portfolio roadmap that shows your target state based on your rationalization decisions.

    The roadmap

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    Get started

    Our concise executive brief shows you why you should rationalize your application portfolio using a tailored framework for your company. We'll show you our methodology and the ways we can help you in handling this.

    Lay the foundations

    Define why you want to rationalize your application portfolio. Define the end state and scope. Build your action plan.

    • Build an Application Rationalization Framework – Phase 1: Lay Your Foundations (ppt)
    • Application Rationalization Tool (xls)

    Plan the application rationalization framework

    Understand what the core assessments are that you perform in these rationalizations. Define your framework and how rigorous you want to apply the reviews based on your business context.

    • Build an Application Rationalization Framework – Phase 2: Plan Your Application Rationalization Framework (ppt)

    Test and adapt your application rationalization framework (ARF)

    Our tool allows you to test the elements of your ARF. Then do a retrospective and adapt based on your experience and desired outcomes. 

    • Build an Application Rationalization Framework – Phase 3: Test and Adapt Your Application Rationalization Framework (ppt)
    • Application TCO Calculator (xls)
    • Value Calculator (xls)

    Initiate your roadmap

    Review your dispositions to ensure they align with your goals. 

    • Build an Application Rationalization Framework – Phase 4: Initiate Your Roadmap (ppt)
    • Disposition Prioritization Tool (xls)


    Manage Third-Party Service Security Outsourcing

    • Buy Link or Shortcode: {j2store}539|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Security Processes & Operations
    • Parent Category Link: /security-processes-and-operations
    • A lack of high-skill labor increases the cost of internal security, making outsourcing more appealing.
    • It is unclear what processes could or should be outsourced versus what functions should remain in-house.
    • It is not feasible to have 24/7/365 monitoring in-house for most firms.

    Our Advice

    Critical Insight

    • You are outsourcing support, not accountability, unless you preface that with your customer.
    • For most of you, you won’t have a choice – you’ll have to outsource high-end security skills to meet future needs.
    • Third-party service providers may be able to more effectively remediate threats because of their large, disparate customer base and wider scope.

    Impact and Result

    • Documented obligations and processes. This will allow you to determine which solution (outsourcing vs. insourcing) allows for the best use of resources, and maintains your brand reputation.
    • A list of variables and features to rank potential third-party providers vs. internal delivery to find which solution provides the best fit for your organization.
    • Current limitations of your environment and the limitations of third parties identified for the environments you are looking to mature.
    • Security responsibilities determined that can be outsourced, and which should be outsourced in order to gain resource allocation and effectiveness, and to improve your overall security posture.
    • The limitations or restrictions for third-party usage understood.

    Manage Third-Party Service Security Outsourcing Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to understand how to avoid common mistakes when it comes to outsourcing security, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. What to outsource

    Identify different responsibilities/functions in your organization and determine which ones can be outsourced. Complete a cost analysis.

    • Manage Third-Party Service Security Outsourcing – Phase 1: What to Outsource
    • Insourcing vs. Outsourcing Costing Tool

    2. How to outsource

    Identify a list of features for your third-party provider and analyze.

    • Manage Third-Party Service Security Outsourcing – Phase 2: How to Outsource
    • MSSP Selection Tool
    • Checklist for Third-Party Providers

    3. Manage your third-party provider

    Understand how to align third-party providers to your organization.

    • Manage Third-Party Service Security Outsourcing – Phase 3: Manage Your Third-Party Provider
    • Security Operations Policy for Third-Party Outsourcing
    • Third-Party Security Policy Charter Template
    [infographic]

    Mandate Data Valuation Before It’s Mandated

    • Buy Link or Shortcode: {j2store}121|cart{/j2store}
    • member rating overall impact: 8.0/10 Overall Impact
    • member rating average dollars saved: $25,000 Average $ Saved
    • member rating average days saved: 10 Average Days Saved
    • Parent Category Name: Data Management
    • Parent Category Link: /data-management
    • Data can be valuable if used properly or dangerous when mishandled.
    • The organization needs to understand the value of their data before they can establish proper data management practice.
    • Data is not considered a capital asset unless there is a financial transaction (e.g. buying or selling data assets).
    • Data valuation is not easy, and it costs money to collect, store, and maintain data.

    Our Advice

    Critical Insight

    • Data always outlives people, processes, and technology. They all come and go, while data remains.
    • Oil is a limited resource, data is not. Contrary to oil, data is likely to grow over time.
    • Data is likely to outlast all other current popular financial instruments including currency, assets, or commodities.
    • Data is used internally and externally and can easily be replicated or combined.
    • Data is beyond currency, assets, or commodities and needs to be a category of its own.

    Impact and Result

    • Every organization must calculate the value of their data. This will enable organizations to become truly data-driven.
    • Too much time has been spent arguing different methods of valuation. An organization must settle on valuation that is acceptable to all its stakeholders.
    • Align data governance and data management to data valuation. Often organizations struggle to justify data initiatives due to lack of visibility in data valuation.
    • Establish appropriate roles and responsibilities and ensure alignment to a common set of goals as a foundation to get the most accurate future data valuation for your organization.
    • Assess organization data assets and implementation roadmap that considers the necessary competencies and capabilities and their dependencies in moving towards the higher maturity of data assets.

    Mandate Data Valuation Before It’s Mandated Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to understand the value associated with the organization's data. Review Info-Tech’s methodology for assessing data value and justifying your data initiatives with a value proposition.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Demystify data valuation

    Understand the benefits of data valuation.

    • Mandate Data Valuation Before It’s Mandated – Phase 1: Demystify Data Valuation

    2. Data value chain

    Learn about the data value chain framework and preview the step-by-step guide to start collecting data sources.

    • Mandate Data Valuation Before It’s Mandated – Phase 2: Data Value Chain

    3. Data value assessment

    Mature your data valuation by putting in the valuation dimensions and metrics. Establish documented results that can be leveraged to demonstrate value in your data assets.

    • Mandate Data Valuation Before It’s Mandated – Phase 3: Data Value Assessment
    [infographic]

    Workshop: Mandate Data Valuation Before It’s Mandated

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Understand the Value of Data Valuation

    The Purpose

    Explain data valuation approach and value proposition.

    Key Benefits Achieved

    A clear understanding and case for data valuation.

    Activities

    1.1 Review common business data sources and how the organization will benefit from data valuation assessment.

    1.2 Understand Info-Tech’s data valuation framework.

    Outputs

    Organization data valuation priorities

    2 Capture Organization Data Value Chain

    The Purpose

    Capture data sources and data collection methods.

    Key Benefits Achieved

    A clear understanding of the data value chain.

    Activities

    2.1 Assess data sources and data collection methods.

    2.2 Understand key insights and value proposition.

    2.3 Capture data value chain.

    Outputs

    Data Valuation Tool

    3 Data Valuation Framework

    The Purpose

    Leverage the data valuation framework.

    Key Benefits Achieved

    Capture key data valuation dimensions and align with data value chain.

    Activities

    3.1 Introduce data valuation framework.

    3.2 Discuss key data valuation dimensions.

    3.3 Align data value dimension to data value chain.

    Outputs

    Data Valuation Tool

    4 Plan for Continuous Improvement

    The Purpose

    Improve organization’s data value.

    Key Benefits Achieved

    Continue to improve data value.

    Activities

    4.1 Capture data valuation metrics.

    4.2 Define data valuation for continuous monitoring.

    4.3 Create a communication plan.

    4.4 Define a plan for continuous improvements.

    Outputs

    Data valuation metrics

    Data Valuation Communication Plan

    ChatGPT Beyond the hype. What can it do for you?

    ChatGPT Beyond The Hype Tymans Group

    Summary of the deck.

    ChatGPT is a generative AI tool developed by OpenAI, a non-profit founded by Silicon Valley titans, including Elon Musk and Sam Altman. It is designed to interact with users in a way that mimics human dialogue. The tool became available via a research release on November 30, 2022, and was an immediate hit – within a week; it attracted more than a million users. Functionally, ChatGPT is designed to answer questions, but it is not the first one. The concept has existed for decades. While it is very powerful, it has also attracted criticism. 

    IT Operations, strategy

    Register to read more …

    Build Your Data Quality Program

    • Buy Link or Shortcode: {j2store}127|cart{/j2store}
    • member rating overall impact: 9.1/10 Overall Impact
    • member rating average dollars saved: $40,241 Average $ Saved
    • member rating average days saved: 33 Average Days Saved
    • Parent Category Name: Data Management
    • Parent Category Link: /data-management
    • Experiencing the pitfalls of poor data quality and failing to benefit from good data quality, including:
      • Unreliable data and unfavorable output.
      • Inefficiencies and costly remedies.
      • Dissatisfied stakeholders.
    • The chances of successful decision-making capabilities are hindered with poor data quality.

    Our Advice

    Critical Insight

    • Address the root causes of your data quality issues and form a viable data quality program.
      • Be familiar with your organization’s data environment and business landscape.
      • Prioritize business use cases for data quality fixes.
      • Fix data quality issues at the root cause to ensure proper foundation for your data to flow.
    • It is important to sustain best practices and grow your data quality program.

    Impact and Result

    • Implement a set of data quality initiatives that are aligned with overall business objectives and aimed at addressing data practices and the data itself.
    • Develop a prioritized data quality improvement project roadmap and long-term improvement strategy.
    • Build related practices such as artificial intelligence and analytics with more confidence and less risk after achieving an appropriate level of data quality.

    Build Your Data Quality Program Research & Tools

    Start here – read the Executive Brief

    Read our concise Executive Brief to find out why you should establish a data quality program, review Info-Tech’s methodology, and understand the four ways we can support you in completing this project.

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Define your organization’s data environment and business landscape

    Learn about what causes data quality issues, how to measure data quality, what makes a good data quality practice in relation to your data and business environments.

    • Business Capability Map Template

    2. Analyze your priorities for data quality fixes

    Determine your business unit priorities to create data quality improvement projects.

    • Data Quality Problem Statement Template
    • Data Quality Practice Assessment and Project Planning Tool

    3. Establish your organization’s data quality program

    Revisit the root causes of data quality issues and identify the relevant root causes to the highest priority business unit, then determine a strategy for fixing those issues.

    • Data Lineage Diagram Template
    • Data Quality Improvement Plan Template

    4. Grow and sustain your data quality practices

    Identify strategies for continuously monitoring and improving data quality at the organization.

    Infographic

    Workshop: Build Your Data Quality Program

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Define Your Organization’s Data Environment and Business Landscape

    The Purpose

    Evaluate the maturity of the existing data quality practice and activities.

    Assess how data quality is embedded into related data management practices.

    Envision a target state for the data quality practice.

    Key Benefits Achieved

    Understanding of the current data quality landscape

    Gaps, inefficiencies, and opportunities in the data quality practice are identified

    Target state for the data quality practice is defined

    Activities

    1.1 Explain approach and value proposition

    1.2 Detail business vision, objectives, and drivers

    1.3 Discuss data quality barriers, needs, and principles

    1.4 Assess current enterprise-wide data quality capabilities

    1.5 Identify data quality practice future state

    1.6 Analyze gaps in data quality practice

    Outputs

    Data Quality Management Primer

    Business Capability Map Template

    Data Culture Diagnostic

    Data Quality Diagnostic

    Data Quality Problem Statement Template

    2 Create a Strategy for Data Quality Project 1

    The Purpose

    Define improvement initiatives

    Define a data quality improvement strategy and roadmap

    Key Benefits Achieved

    Improvement initiatives are defined

    Improvement initiatives are evaluated and prioritized to develop an improvement strategy

    A roadmap is defined to depict when and how to tackle the improvement initiatives

    Activities

    2.1 Create business unit prioritization roadmap

    2.2 Develop subject areas project scope

    2.3 By subject area 1 data lineage analysis, root cause analysis, impact assessment, and business analysis

    Outputs

    Business Unit Prioritization Roadmap

    Subject area scope

    Data Lineage Diagram

    3 Create a Strategy for Data Quality Project 2

    The Purpose

    Define improvement initiatives

    Define a data quality improvement strategy and roadmap

    Key Benefits Achieved

    Improvement initiatives are defined

    Improvement initiatives are evaluated and prioritized to develop an improvement strategy

    A roadmap is defined to depict when and how to tackle the improvement initiatives

    Activities

    3.1 Understand how data quality management fits in with the organization’s data governance and data management programs

    3.2 By subject area 2 data lineage analysis, root cause analysis, impact assessment, and business analysis

    Outputs

    Data Lineage Diagram

    Root Cause Analysis

    Impact Analysis

    4 Create a Strategy for Data Quality Project 3

    The Purpose

    Determine a strategy for fixing data quality issues for the highest priority business unit

    Key Benefits Achieved

    Strategy defined for fixing data quality issues for highest priority business unit

    Activities

    4.1 Formulate strategies and actions to achieve data quality practice future state

    4.2 Formulate a data quality resolution plan for the defined subject area

    4.3 By subject area 3 data lineage analysis, root cause analysis, impact assessment, and business analysis

    Outputs

    Data Quality Improvement Plan

    Data Lineage Diagram

    5 Create a Plan for Sustaining Data Quality

    The Purpose

    Plan for continuous improvement in data quality

    Incorporate data quality management into the organization’s existing data management and governance programs

    Key Benefits Achieved

    Sustained and communicated data quality program

    Activities

    5.1 Formulate metrics for continuous tracking of data quality and monitoring the success of the data quality improvement initiative

    5.2 Workshop Debrief with Project Sponsor

    5.3 Meet with project sponsor/manager to discuss results and action items

    5.4 Wrap up outstanding items from the workshop, deliverables expectations, GIs

    Outputs

    Data Quality Practice Improvement Roadmap

    Data Quality Improvement Plan (for defined subject areas)

    Further reading

    Build Your Data Quality Program

    Quality Data Drives Quality Business Decisions

    Executive Brief

    Analyst Perspective

    Get ahead of the data curve by conquering data quality challenges.

    Regardless of the driving business strategy or focus, organizations are turning to data to leverage key insights and help improve the organization’s ability to realize its vision, key goals, and objectives.

    Poor quality data, however, can negatively affect time-to-insight and can undermine an organization’s customer experience efforts, product or service innovation, operational efficiency, or risk and compliance management. If you are looking to draw insights from your data for decision making, the quality of those insights is only as good as the quality of the data feeding or fueling them.

    Improving data quality means having a data quality management practice that is sustainably successful and appropriate to the use of the data, while evolving to keep pace with or get ahead of changing business and data landscapes. It is not a matter of fixing one data set at a time, which is resource and time intensive, but instead identifying where data quality consistently goes off the rails, and creating a program to improve the data processes at the source.

    Crystal Singh

    Research Director, Data and Analytics

    Info-Tech Research Group

    Executive Summary

    Your Challenge

    Your organization is experiencing the pitfalls of poor data quality, including:

    • Unreliable data and unfavorable output.
    • Inefficiencies and costly remedies.
    • Dissatisfied stakeholders.

    Poor data quality hinders successful decision making.

    Common Obstacles

    Not understanding the purpose and execution of data quality causes some disorientation with your data.

    • Failure to realize the importance/value of data quality.
    • Unsure of where to start with data quality.
    • Lack of investment in data quality.

    Organizations tend to adopt a project mentality when it comes to data quality instead of taking the strategic approach that would be all-around more beneficial in the long term.

    Info-Tech’s Approach

    Address the root causes of your data quality issues by forming a viable data quality program.

    • Be familiar with your organization’s data environment and business landscape.
    • Prioritize business use cases for data quality fixes.
    • Fixing data quality issues at the root cause to ensure a proper foundation for your data to flow.

    It is important to sustain best practices and grow your data quality program.

    Info-Tech Insight

    Fix data quality issues as close as possible to the source of data while understanding that business use cases will each have different requirements and expectations from data quality.

    Data is the foundation of your organization’s knowledge

    Data enables your organization to make decisions.

    Reliable data is needed to facilitate data consumers at all levels of the enterprise.

    Insights, knowledge, and information are needed to inform operational, tactical, and strategic decision-making processes. Data and information are needed to manage the business and empower business processes such as billing, customer touchpoints, and fulfillment.

    Raw Data

    Business Information

    Actionable Insights

    Data should be at the foundation of your organization’s evolution. The transformational insights that executives are constantly seeking can be uncovered with a data quality practice that makes high-quality, trustworthy information readily available to the business users who need it.

    98% of companies use data to improve customer experience. (Experian Data Quality, 2019)

    High-Level Data Architecture

    The image is a graphic, which at the top shows different stages of data, and in the lower part of the graphic shows the data processes.

    Build Your Data Quality Program

    1. Data Quality & Data Culture Diagnostics Business Landscape Exercise
    2. Business Strategy & Use Cases
    3. Prioritize Use Cases With Poor Quality

    Info-Tech Insight

    As data is ingested, integrated, and maintained in the various streams of the organization's system and application architecture, there are multiple points where the quality of the data can degrade.

    1. Understand the organization's data culture and data quality environment across the business landscape.
    2. Prioritize business use cases with poor data quality.
    3. For each use case, identify data quality issues and requirements throughout the data pipeline.
    4. Fix data quality issues at the root cause.
    5. As data flow through quality assurance monitoring checkpoints, monitor data to ensure good quality output.

    Insight:

    Proper application of data quality dimensions throughout the data pipeline will result in superior business decisions.

    Data quality issues can occur at any stage of the data flow.

    The image shows the flow of data through various stages: Data Creation; Data Ingestion; Data Accumulation and Engineering; Data Delivery; and Reporting & Analytics. At the bottom, there are two bars: the left one labelled Fix data quality root causes here...; and the right reads: ...to prevent expensive cures here.

    The image is a legend that accompanies the data flow graphic. It indicates that a white and green square icon indicates Data quality dimensions; a red cube indicates a potential point of data quality degradation; the pink square indicates Root cause of poor data quality; and a green flag indicates Quality Assurance Monitoring.

    Prevent the domino effect of poor data quality

    Data is the foundation of decisions made at data-driven organizations.

    Therefore, if there are problems with the organization’s underlying data, this can have a domino effect on many downstream business functions.

    Let’s use an example to illustrate the domino effect of poor data quality.

    Organization X is looking to migrate their data to a single platform, System Y. After the migration, it has become apparent that reports generated from this platform are inconsistent and often seem wrong. What is the effect of this?

    1. Time must be spent on identifying the data quality issues, and often manual data quality fixes are employed. This will extend the time to deliver the project that depends on system Y by X months.
    2. To repair these issues, the business needs to contract two additional resources to complete the unforeseen work. The new resources cost $X each, as well as additional infrastructure and hardware costs.
    3. Now, the strategic objectives of the business are at risk and there is a feeling of mistrust in the new system Y.

    Three key challenges impacting the ability to deliver excellent customer experience

    30% Poor data quality

    30% Method of interaction changing

    30% Legacy systems or lack of new technology

    95% Of organizations indicated that poor data quality undermines business performance.

    (Source: Experian Data Quality, 2019)

    Maintaining quality data will support more informed decisions and strategic insight

    Improving your organization’s data quality will help the business realize the following benefits:

    Data-Driven Decision Making

    Business decisions should be made with a strong rationale. Data can provide insight into key business questions, such as, “How can I provide better customer satisfaction?”

    89% Of CIOs surveyed say lack of quality data is an obstacle to good decision making. (Larry Dignan, CIOs juggling digital transformation pace, bad data, cloud lock0in and business alignment, 2020)

    Customer Intimacy

    Improve marketing and the customer experience by using the right data from the system of record to analyze complete customer views of transactions, sentiments, and interactions.

    94% Percentage of senior IT leaders who say that poor data quality impinges business outcomes. (Clint Boulton, Disconnect between CIOs and LOB managers weakens data quality, 2016)

    Innovation Leadership

    Gain insights on your products, services, usage trends, industry directions, and competitor results to support decisions on innovations, new products, services, and pricing.

    20% Businesses lose as much as 20% of revenue due to poor data quality. (RingLead Data Management Solutions, 10 Stats About Data Quality I Bet You Didn’t Know)

    Operational Excellence

    Make sure the right solution is delivered rapidly and consistently to the right parties for the right price and cost structure. Automate processes by using the right data to drive process improvements.

    10-20% The implementation of data quality initiatives can lead to reductions in corporate budget of up to 20%. (HaloBI, 2015)

    However, maintaining data quality is difficult

    Avoid these pitfalls to get the true value out of your data.

    1. Data debt drags down ROI – a high degree of data debt will hinder you from attaining the ROI you’re expecting.
    2. Lack of trust means lack of usage – a lack of confidence in data results in a lack of data usage in your organization, which negatively effects strategic planning, KPIs, and business outcomes.
    3. Strategic assets become a liability – bad data puts your business at risk of failing compliance standards, which could result in you paying millions in fines.
    4. Increased costs and inefficiency – time spent fixing bad data means less workload capacity for your important initiatives and the inability to make data-based decisions.
    5. Barrier to adopting data-driven tech – emerging technologies, such as predictive analytics and artificial intelligence, rely on quality data. Inaccurate, incomplete, or irrelevant data will result in delays or a lack of ROI.
    6. Bad customer experience – Running your business on bad data can hinder your ability to deliver to your customers, growing their frustration, which negatively impacts your ability to maintain your customer base.

    Info-Tech Insight

    Data quality suffers most at the point of entry. This is one of the causes of the domino effect of data quality – and can be one of the most costly forms of data quality errors due to the error propagation. In other words, fix data ingestion, whether through improving your application and database design or improving your data ingestion policy, and you will fix a large majority of data quality issues.

    Follow Our Data & Analytics Journey

    Data Quality is laced into Data Strategy, Data Management, and Data Governance.

    • Data Strategy
      • Data Management
        • Data Quality
        • Data Governance
          • Data Architecture
            • MDM
            • Data Integration
            • Enterprise Content Management
            • Information Lifecycle Management
              • Data Warehouse/Lake/Lakehouse
                • Reporting and Analytics
                • AI

    Data quality is rooted in data management

    Extract Maximum Benefit Out of Your Data Quality Management.

    • Data management is the planning, execution, and oversight of policies, practices, and projects that acquire, control, protect, deliver, and enhance the value of data and information assets (DAMA, 2009).
    • In other words, getting the right information, to the right people, at the right time.
    • Data quality management exists within each of the data practices, information dimensions, business resources, and subject areas that comprise the data management framework.
    • Within this framework, an effective data quality practice will replace ad hoc processes with standardized practices.
    • An effective data quality practice cannot succeed without proper alignment and collaboration across this framework.
    • Alignment ensures that the data quality practice is fit for purpose to the business.

    The DAMA DMBOK2 Data Management Framework

    • Data Governance
      • Data Quality
      • Data Architecture
      • Data Modeling & Design
      • Data Storage & Operations
      • Data Security
      • Data Integration & Interoperability
      • Documents & Content
      • Reference & Master Data
      • Data Warehousing & Business Intelligence
      • Meta-data

    (Source: DAMA International)

    Related Info-Tech Research

    Build a Robust and Comprehensive Data Strategy

    • People often think that the main problems they need to fix first are related to data quality when the issues transpire at a much larger level. This blueprint is the key to building and fostering a data-driven culture.

    Create a Data Management Roadmap

    • Refer to this blueprint to understand data quality in the context of data disciplines and methods for improving your data management capabilities.

    Establish Data Governance

    • Define an effective data governance strategy and ensure the strategy integrates well with data quality with this blueprint.

    Info-Tech’s methodology for Data Quality

    Phase Steps 1. Define Your Organization’s Data Environment and Business Landscape 2. Analyze Your Priorities for Data Quality Fixes 3. Establish Your Organization’s Data Quality Program 4. Grow and Sustain Your Data Quality Practice
    Phase Outcomes This step identifies the foundational understanding of your data and business landscape, the essential concepts around data quality, as well as the core capabilities and competencies that IT needs to effectively improve data quality. To begin addressing specific, business-driven data quality projects, you must identify and prioritize the data-driven business units. This will ensure that data improvement initiatives are aligned to business goals and priorities. After determining whose data is going to be fixed based on priority, determine the specific problems that they are facing with data quality, and implement an improvement plan to fix it. Now that you have put an improvement plan into action, make sure that the data quality issues don’t keep cropping up. Integrate data quality management with data governance practices into your organization and look to grow your organization’s overall data maturity.

    Info-Tech Insight

    “Data Quality is in the eyes of the beholder.”– Igor Ikonnikov, Research Director

    Data quality means tolerance, not perfection

    Data from Info-Tech’s CIO Business Vision Diagnostic, which represents over 400 business stakeholders, shows that data quality is very important when satisfaction with data quality is low.

    However, when data quality satisfaction hit a threshold, it became less important.

    The image is a line graph, with the X-axis labelled Satisfaction with Data Quality, and the Y axis labelled Rated Importance for Data Quality. The line begins high, and then descends. There is text inside the graph, which is transcribed below.

    Respondents were asked “How satisfied are you with the quality, reliability, and effectiveness of the data you use to manage your group?” as well as to rank how important data quality was to their organization.

    When the business satisfaction of data quality reached a threshold value of 71-80%, the rated importance reached its lowest value.

    Info-Tech Insight

    Data needs to be good, but truly spectacular data may go unnoticed.

    Provide the right level of data quality, with the appropriate effort, for the correct usage. This blueprint will help you to determine what “the right level of data quality” means, as well as create a plan to achieve that goal for the business.

    Data Roles and Responsibilities

    Data quality occurs through three main layers across the data lifecycle

    Data Strategy

    Data Strategy should contain Data Quality as a standard component.

    ← Data Quality issues can occur throughout at any stage of the data flow →

    DQ Dimensions

    Timeliness – Representation – Usability – Consistency – Completeness – Uniqueness – Entry Quality – Validity – Confidence – Importance

    Source System Layer

    • Data Resource Manager/Collector: Enters data into a database and ensures that data collection sources are accurate

    Data Transformation Layer

    • ETL Developer: Designs data storage systems
    • Data Engineer: Oversees data integrations, data warehouses and data lakes, data pipelines
    • Database Administrator: Manages database systems, ensures they meet SLAs, performances, backups
    • Data Quality Engineer: Finds and cleanses bad data in data sources, creates processes to prevent data quality problems

    Consumption Layer

    • Data Scientist: Gathers and analyses data from databases and other sources, runs models, and creates data visualizations for users
    • BI Analyst: Evaluates and mines complex data and transforms it into insights that drive business value. Uses BI software and tools to analyze industry trends and create visualizations for business users
    • Data Analyst: Extracts data from business systems, analyzes it, and creates reports and dashboards for users
    • BI Engineer: Documents business needs on data analysis and reporting and develops BI systems, reports, and dashboards to support them
    Data Creation → [SLA] Data Ingestion [ QA] →Data Accumulation & Engineering → [SLA] Data Delivery [QA] →Reporting & Analytics
    Fix Data Quality root causes here… → to prevent expensive cures here.

    Executive Brief Case Study

    Industry: Healthcare

    Source: Primary Info-Tech Research

    Align source systems to maximize business output.

    A healthcare insurance agency faced data quality issues in which a key business use case was impacted negatively. Business rules were not well defined, and default values instead of real value caused a concern. When dealing with multiple addresses, data was coming from different source systems.

    The challenge was to identify the most accurate address, as some were incomplete, and some lacked currency and were not up to date. This especially challenged a key business unit, marketing, to derive business value in performing key activities by being unable to reach out to existing customers to advertise any additional products.

    For this initiative, this insurance agency took an economic approach by addressing those data quality issues using internal resources.

    Results

    Without having any MDM tools or having a master record or any specific technology relating to data quality, this insurance agency used in-house development to tackle those particular issues at the source system. Data quality capabilities such as data profiling were used to uncover those issues and address them.

    “Data quality is subjective; you have to be selective in terms of targeting the data that matters the most. When getting business tools right, most issues will be fixed and lead to achieving the most value.” – Asif Mumtaz, Data & Solution Architect

    Info-Tech offers various levels of support to best suit your needs

    DIY Toolkit

    "Our team has already made this critical project a priority, and we have the time and capability, but some guidance along the way would be helpful."

    Guided Implementation

    "Our team knows that we need to fix a process, but we need assistance to determine where to focus. Some check-ins along the way would help keep us on track."

    Workshop

    "We need to hit the ground running and get this project kicked off immediately. Our team has the ability to take this over once we get a framework and strategy in place."

    Consulting

    "Our team does not have the time or the knowledge to take this project on. We need assistance through the entirety of this project."

    Diagnostic and consistent frameworks are used throughout all four options.

    Guided Implementation

    What does a typical GI on this topic look like?

    Phase 1 Phase 2 Phase 3 Phase 4
    • Call #1: Learn about the concepts of data quality and the common root causes of poor data quality.
    • Call #2: Identify the core capabilities of IT for improving data quality on an enterprise scale.
    • Call #3: Determine which business units use data and require data quality remediation.
    • Call #4: Create a plan for addressing business unit data quality issues according to priority of the business units based on value and impact of data.
    • Call #5: Revisit the root causes of data quality issues and identify the relevant root causes to the highest priority business unit.
    • Call #6: Determine a strategy for fixing data quality issues for the highest priority business unit.
    • Call #7: Identify strategies for continuously monitoring and improving data quality at the organization.
    • Call #8: Learn how to incorporate data quality practices in the organization’s larger data management and data governance frameworks.
    • Call #9: Summarize results and plan next steps on how to evolve your data landscape.

    A Guided Implementation (GI) is a series of calls with an Info-Tech analyst to help implement our best practices in your organization.

    A typical GI is between eight to twelve calls over the course of four to six months.

    Workshop Overview

    Contact your account representative for more information. workshops@infotech.com 1-888-670-8889

    Day 1 Day 2 Day 3 Day 4 Day 5
    Define Your Organization’s Data Environment and Business Landscape Create a Strategy for Data Quality Project 1 Create a Strategy for Data Quality Project 2 Create a Strategy for Data Quality Project 3 Create a Plan for Sustaining Data Quality
    Activities
    1. Explain approach and value proposition.
    2. Detail business vision, objectives, and drivers.
    3. Discuss data quality barriers, needs, and principles.
    4. Assess current enterprise-wide data quality capabilities.
    5. Identify data quality practice future state.
    6. Analyze gaps in data quality practice.
    1. Create business unit prioritization roadmap.
    2. Develop subject areas project scope.
    3. By subject area 1:
    • Data lineage analysis
    • Root cause analysis
    • Impact assessment
    • Business analysis
    1. Understand how data quality management fits in with the organization’s data governance and data management programs.
    2. By subject area 2:
    • Data lineage analysis
    • Root cause analysis
    • Impact assessment
    • Business analysis
    1. Formulate strategies and actions to achieve data quality practice future state.
    2. Formulate data quality resolution plan for defined subject area.
    3. By subject area 3:
    • Data lineage analysis
    • Root cause analysis
    • Impact assessment
    • Business analysis
    1. Formulate metrics for continuous tracking of data quality and monitoring the success of the data quality improvement initiative.
    2. Workshop Debrief with Project Sponsor.
    • Meet with project sponsor/manager to discuss results and action items.
    • Wrap up outstanding items from the workshop, deliverables expectations, GIs.
    Deliverables
    1. Data Quality Management Primer
    2. Business Capability Map Template
    3. Data Culture Diagnostic
    4. Data Quality Diagnostic
    5. Data Quality Problem Statement Template
    1. Business Unit Prioritization Roadmap
    2. Subject area scope
    3. Data Lineage Diagram
    1. Data Lineage Diagram
    2. Root Cause Analysis
    3. Impact Analysis
    1. Data Lineage Diagram
    2. Data Quality Improvement Plan
    1. Data Quality Practice Improvement Roadmap
    2. Data Quality Improvement Plan (for defined subject areas)

    Phase 1

    Define Your Organization’s Data Environment and Business Landscape

    Build Your Data Quality Program

    Data quality is a methodology and must be treated as such

    A comprehensive data quality practice includes appropriate business requirements gathering, planning, governance, and oversight capabilities, as well as empowering technologies for properly trained staff, and ongoing development processes.

    Some common examples of appropriate data management methodologies for data quality are:

    • The data quality team has the necessary competencies and resources to perform the outlined workload.
    • There are processes that exist for continuously evaluating data quality performance capabilities.
    • Improvement strategies are designed to increase data quality performance capabilities.
    • Policies and procedures that govern data quality are well-documented, communicated, followed, and updated.
    • Change controls exist for revising policies and procedures, including communication of updates and changes.
    • Self-auditing techniques are used to ensure business-IT alignment when designing or recalibrating strategies.

    Effective data quality practices coordinate with other overarching data disciplines, related data practices, and strategic business objectives.

    “You don’t solve data quality with a Band-Aid; you solve it with a methodology.” – Diraj Goel, Growth Advisor, BC Tech

    Data quality can be defined by four key quality indicators

    Similar to measuring the acidity of a substance with a litmus test, the quality of your data can be measured using a simple indicator test. As you learn about common root causes of data quality problems in the following slides, think about these four quality indicators to assess the quality of your data:

    • Completeness – Closeness to the correct value. Encompasses accuracy, consistency, and comparability to other databases.
    • Usability – The degree to which data meets current user needs. To measure this, you must determine if the user is satisfied with the data they are using to complete their business functions.
    • Timeliness – Length of time between creation and availability of data.
    • Accessibility – How easily a user can access and understand the data (including data definitions and context). Interpretability can also be used to describe this indicator.

    Info-Tech Insight

    Quality is a relative term. Data quality is measured in terms of tolerance. Perfect data quality is both impossible and a waste of time and effort.

    How to get investment for your data quality program

    Follow these steps to convince leadership of the value of data quality:

    “You have to level with people, you cannot just start talking with the language of data and expect them to understand when the other language is money and numbers.” – Izabela Edmunds, Information Architect at Mott MacDonald

    1. Perform Phases 0 & 1 of this blueprint as this will offer value in carrying out the following steps.
    2. Build credibility. Show them your understanding of data and how it aligns to the business.
    3. Provide tangible evidence of how significant business use cases are impacted by poor quality data.
    4. Present the ROI of fixing the data quality issues you have prioritized.
    5. Explain how the data quality program will be established, implemented, and sustained.
    6. Prove the importance of fixing data quality issues at the source and how it is the most efficient, effective, and cost-friendly solution.

    Phase 1 deliverables

    Each of these deliverables serve as inputs to detect key outcomes about your organization and to help complete this blueprint:

    1. Data Culture Diagnostic

    Use this report to understand where your organization lies across areas relating to data culture.

    While the Quality & Trust area of the report might be most prevalent to this blueprint, this diagnostic may point out other areas demanding more attention.

    Please speak to your account manager for access

    2. Business Capability Map Template

    Perform this process to understand the capabilities that enable specific value streams. The output of this deliverable is a high-level view of your organization’s defined business capabilities.

    Download this tool

    Info-Tech Insight

    Understanding your data culture and business capabilities are foundational to starting the journey of data quality improvement.

    Key deliverable:

    3. Data Quality Diagnostic

    The Data Quality Report is designed to help you understand, assess, and improve key organizational data quality issues. This is where respondents across various areas in the organization can assess Data Quality across various dimensions.

    Download this tool

    Data Quality Diagnostic Value

    Prioritize business use cases with our data quality dimensions.

    • Complete this diagnostic for each major business use case. The output from the Data Culture Diagnostic and the Business Capability Map should help you understand which use cases to address.
    • Involve all key stakeholders involved in the business use case. There may be multiple business units involved in a single use case.
    • Prioritize the business use cases that need the most attention pertaining to data quality by comparing the scores of the Importance and Confidence data quality dimensions.

    If there are data elements that are considered of high importance and low confidence, then they must be prioritized.

    Sample Scorecard

    The image shows a screen capture of a scorecard, with sample information filled in.

    The image shows a screen capture of a scorecard, with sample information filled in.

    Poor data quality develops due to multiple root causes

    After you get to know the properties of good quality data, understand the underlying causes of why those indicators can point to poor data quality.

    If you notice that the usability, completeness, timeliness, or accessibility of the organization’s data is suffering, one or more of the following root causes are likely plaguing your data:

    Common root causes of poor data quality, through the lens of Info-Tech’s Five-Tier Data Architecture:

    The image shows a graphic of Info-Tech's Five-Tier Data Architecture, with root causes of poor data quality identified. In the data creation and ingestion stages, the root causes are identified as Poor system/application design, Poor database design, Inadequate enterprise integration. The root causes identified in the latter stages are: Absence of data quality policies, procedures, and standards, and Incomplete/suboptimal business processes

    These root causes of poor data quality are difficult to avoid, not only because they are often generated at an organization’s beginning stages, but also because change can be difficult. This means that the root causes are often propagated through stale or outdated business processes.

    Data quality problems root cause #1:

    Poor system or application design

    Application design plays one of the largest roles in the quality of the organization’s data. The proper design of applications can prevent data quality issues that can snowball into larger issues downstream.

    Proper ingestion is 90% of the battle. An ounce of prevention is worth a pound of cure. This is true in many different topics, and data quality is one of them. Designing an application so that data gets entered properly, whether by internal staff or external customers, is the single most effective way to prevent data quality issues.

    Some common causes of data quality problems at the application/system level include:

    • Too many open fields (free-form text fields that accept a variety of inputs).
    • There are no lookup capabilities present. Reference data should be looked up instead of entered.
    • Mandatory fields are not defined, resulting in blank fields.
    • No validation of data entries before writing to the underlying database.
    • Manual data entry encourages human error. This can be compounded by poor application design that facilitates the incorrect data entry.

    Data quality problems root cause #2:

    Poor database design

    Database design also affects data quality. How a database is designed to handle incoming data, including the schema and key identification, can impact the integrity of the data used for reporting and analytics.

    The most common type of database is the relational database. Therefore, we will focus on this type of database.

    When working with and designing relational databases, there are some important concepts that must be considered.

    Referential integrity is a term that is important for the design of relational database schema, and indicates that table relationships must always be consistent.

    For table relationships to be consistent, primary keys (unique value for each row) must uniquely identify entities in columns of the table. Foreign keys (field that is defined in a second table but refers to the primary key in the first table) must agree with the primary key that is referenced by the foreign key. To maintain referential integrity, any updates must be propagated to the primary parent key.

    Info-Tech Insight

    Other types of databases, including databases with unstructured data, need data quality consideration. However, unstructured data may have different levels of quality tolerance.

    At the database level, some common root causes include:

    1. Lack of referential integrity.
    2. Lack of unique keys.
    3. Don’t have restricted data range.
    4. Incorrect datatype, string fields that can hold too many characters.
    5. Orphaned records.

    Databases and People:

    Even though database design is a technology issue, don’t forget about the people.

    A lack of training employees on database permissions for updating/entering data into the physical databases is a common problem for data quality.

    Data quality problems root cause #3:

    Improper integration and synchronization of enterprise data

    Data ingestion is another category of data-quality-issue root causes. When moving data in Tier 2, whether it is through ETL, ESB, point-to-point integration, etc., the integrity of the data during movement and/or transformation needs to be maintained.

    Tier 2 (the data ingestion layer) serves to move data for one of two main purposes:

    • To move data from originating systems to downstream systems to support integrated business processes.
    • To move data to Tier 3 where data rests for other purposes. This movement of data in its purest form means we move raw data to storage locations in an overall data warehouse environment reflecting any security, compliance and other standards in our choices for how to store. Also, it is where data is transformed for unique business purpose that will also be moved to a place of rest or a place of specific use. Data cleansing and matching and other data-related blending tasks occur at this layer.

    This ensures the data is pristine throughout the process and improves trustworthiness of outcomes and speed to task completion.

    At the integration layer, some common root causes of data quality problems include:

    1. No data mask. For example, zip code should have a mask of five numeric characters.
    2. Questionable aggregation, transformation process, or incorrect logic.
    3. Unsynchronized data refresh process in an integrated environment.
    4. Lack of a data matching tool.
    5. Lack of a data quality tool.
    6. Don’t have data profiling capability.
    7. Errors with data conversion or migration processes – when migrating, decommissioning, or converting systems – movement of data sets.
    8. Incorrect data mapping between data sources and targets.

    Data quality problems root cause #4:

    Insufficient and ineffective data quality policies and procedures

    Data policies and procedures are necessary for establishing standards around data and represent another category of data-quality-issue root causes. This issue spans across all five of the 5 Tier Architecture.

    Data policies are short statements that seek to manage the creation, acquisition, integrity, security, compliance, and quality of data. These policies vary amongst organizations, depending on your specific data needs.

    • Policies describe what to do, while standards and procedures describe how to do something.
    • There should be few data policies, and they should be brief and direct. Policies are living documents and should be continuously updated to respond to the organization’s data needs.
    • The data policies should highlight who is responsible for the data under various scenarios and rules around how to manage it effectively.

    Some common root causes of data quality issues related to policies and procedures include:

    1. Policies are absent or out of date.
    2. Employees are largely unaware of policies in effect.
    3. Policies are unmonitored and unenforced.
    4. Policies are in multiple locations.
    5. Multiple versions of the same policy exist.
    6. Policies are managed inconsistently across different silos.
    7. Policies are written poorly by untrained authors.
    8. Inadequate policy training program.
    9. Draft policies stall and lose momentum.
    10. Weak policy support from senior management.

    Data quality problems root cause #5:

    Inefficient or ineffective business processes

    Some common root causes of data quality issues related to business processes include:

    1. Multiple entries of the same record leads to duplicate records proliferating in the database.
    2. Many business definitions of data.
    3. Failure to document data manipulations when presenting data.
    4. Failure to train people on how to understand data.
    5. Manually intensive processes can result in duplication of effort (creates room for errors).
    6. No clear delineation of dependencies of business processes within or between departments, which leads to a siloed approach to business processes, rather than a coordinated and aligned approach.

    Business processes can impact data quality. How data is entered into systems, as well as employee training and knowledge about the correct data definitions, can impact the quality of your organization’s data.

    These problematic business process root causes can lead to:

    Duplicate records

    Incomplete data

    Improper use of data

    Wrong data entered into fields

    These data quality issues will result in costly and inefficient manual fixes, wasting valuable time and resources.

    Phase 1 Summary

    1. Data Quality Understanding

    • Understanding that data quality is a methodology and should be treated as such.
    • Data quality can be defined by four key indicators which are completeness, usability, timeliness, and accessibility.
    • Explained how to get investment for your data quality program and showcasing its value to leadership.

    2. Phase 0 Deliverables

    Introduced foundational tools to help you throughout this blueprint:

    • Complete the Data Culture Diagnostic and Business Capability Map Template as they are foundational in understanding your data culture and business capabilities to start the journey of data quality improvement.
    • Involve key relevant stakeholders when completing the Data Quality Diagnostic for each major business use case. Use the Importance and Confidence dimensions to help you prioritize which use case to address.

    3. Common Root Causes

    Addressed where multiple root causes can occur throughout the flow of your data.

    Analyzed the following common root causes of data quality:

    1. Poor system or application design
    2. Poor database design
    3. Improper integration and synchronization of enterprise data
    4. Insufficient and ineffective data quality policies and procedures
    5. Inefficient or ineffective business processes

    Phase 2

    Analyze Your Priorities for Data Quality Fixes

    Build Your Data Quality Program

    Business Context & Data Quality

    Establish the business context of data quality improvement projects at the business unit level to find common goals.

    • To ensure the data improvement strategy is business driven, start your data quality project evaluation by understanding the business context. You will then determine which business units use data and create a roadmap for prioritizing business units for data quality repairs.
    • Your business context is represented by your corporate business vision, mission, goals and objectives, differentiators, and drivers. Collectively, they provide essential information on what is important to your organization, and some hints on how to achieve that. In this step, you will gather important information about your business view and interpret the business view to establish a data view.

    Business Vision

    Business Goals

    Business Drivers

    Business Differentiators

    Not every business unit uses data to the same extent

    A data flow diagram can provide value by allowing an organization to adopt a proactive approach to data quality. Save time by knowing where the entry points are and where to look for data flaws.

    Understanding where data lives can be challenging as it is often in motion and rarely resides in one place. There are multiple benefits that come from taking the time to create a data flow diagram.

    • Mapping out the flow of data can help provide clarity on where the data lives and how it moves through the enterprise systems.
    • Having a visual of where and when data moves helps to understand who is using data and how it is being manipulated at different points.
    • A data flow diagram will allow you to elicit how data is used in a different use case.

    Info-Tech’s Four-Column Model of Data will help you to identify the essential aspects of your data:

    Business Use Case →Used by→Business Unit →Housed in→Systems→Used for→Usage of the Data

    Not every business unit requires the same standard of data quality

    To prioritize your business units for data quality improvement projects, you must analyze the relative importance of the data they use to the business. The more important the data is to the business, the higher the priority is of fixing that data. There are two measures for determining the importance of data: business value and business impact.

    Business Value of Data

    Business value of data can be evaluated by thinking about its ties to revenue generation for the organization, as well as how it is used for productivity and operations at the organization.

    The business value of data is assessed by asking what would happen to the following parameters if the data is not usable (due to poor quality, for example):

    • Loss of Revenue
    • Loss of Productivity
    • Increased Operating Costs

    Business Impact of Data

    Business impact of data should take into account the effects of poor data on both internal and external parties.

    The business impact of data is assessed by asking what the impact would be of bad data on the following parameters:

    • Impact on Customers
    • Impact on Internal Staff
    • Impact on Business Partners

    Value + Impact = Data Priority Score

    Ensure that the project starts on the right foot by completing Info-Tech’s Data Quality Problem Statement Template

    Before you can identify a solution, you must identify the problem with the business unit’s data.

    Download this tool

    Use Info-Tech’s Data Quality Problem Statement Template to identify the symptoms of poor data quality and articulate the problem.

    Info-Tech’s Data Quality Problem Statement Template will walk you through a step-by-step approach to identifying and describing the problems that the business unit feels regarding its data quality.

    Before articulating the problem, it helps to identify the symptoms of the problem. The following W’s will help you to describe the symptoms of the data quality issues:

    What

    Define the symptoms and feelings produced by poor data quality in the business unit.

    Where

    Define the location of the data that are causing data quality issues.

    When

    Define how severe the data quality issues are in frequency and duration.

    Who

    Define who is affected by the data quality problems and who works with the data.

    Info-Tech Best Practice

    Symptoms vs. Problems. Often, people will identify a list of symptoms of a problem and mistake those for the problem. Identifying the symptoms helps to define the problem, but symptoms do not help to identify the solution. The problem statement helps you to create solutions.

    Define the project problem to articulate the purpose

    1 hour

    Input

    • Symptoms of data quality issues in the business unit

    Output

    • Refined problem description

    Materials

    • Data Quality Problem Statement Template

    Participants

    • Data Quality Improvement Project team
    • Business line representatives

    A defined problem helps you to create clear goals, as well as lead your thinking to determine solutions to the problem.

    A problem statement consists of one or two sentences that summarize a condition or issue that a quality improvement team is meant to address. For the improvement team to fix the problem, the problem statement therefore has to be specific and concise.

    Instructions

    1. Gather the Data Quality Improvement Project Team in a room and start with an issue that is believed to be related to data quality.
    2. Ask what are the attributes and symptoms of that reality today; do this with the people impacted by the issue. This should be an IT and business collaboration.
    3. Draw your conclusions of what it all means: what have you collectively learned?
    4. Consider the implications of your conclusions and other considerations that must be taken into account such as regulatory needs, compliance, policy, and targets.
    5. Develop solutions – Contain the problem to something that can be solved in a realistic timeframe, such as three months.

    Download the Data Quality Problem Statement Template

    Case Study

    A strategic roadmap rooted in business requirements primes a data quality improvement plan for success.

    MathWorks

    Industry

    Software Development

    Source

    Primary Info-Tech Research

    As part of moving to a formalized data quality practice, MathWorks leveraged an incremental approach that took its time investigating business cases to support improvement actions. Establishing realistic goals for improvement in the form of a roadmap was a central component for gaining executive approval to push the project forward.

    Roadmap Creation

    In constructing a comprehensive roadmap that incorporated findings from business process and data analyses, MathWorks opted to document five-year and three-year overall goals, with one-year objectives that supported each goal. This approach ensured that the tactical actions taken were directed by long-term strategic objectives.

    Results – Business Alignment

    In presenting their roadmap for executive approval, MathWorks placed emphasis on communicating the progression and impact of their initiatives in terms that would engage business users. They focused on maintaining continual lines of communication with business stakeholders to demonstrate the value of the initiatives and also to gradually shift the corporate culture to one that is invested in an effective data quality practice.

    “Don’t jump at the first opportunity, because you may be putting out a fire with a cup of water where a fire truck is needed.” – Executive Advisor, IT Research and Advisory Firm

    Use Info-Tech’s Practice Assessment and Project Planning Tool to create your strategy for improving data quality

    Assess IT’s capabilities and competencies around data quality and plan to build these as the organization’s data quality practice develops. Before you can fix data quality, make sure you have the necessary skills and abilities to fix data quality correctly.

    The following IT capabilities are developed on an ongoing basis and are necessary for standardizing and structuring a data quality practice:

    • Meeting Business Needs
    • Services and Projects
    • Policies, Procedures, and Standards
    • Roles and Organizational Structure
    • Oversight and Communication
    • Data Quality of Different Data Types

    Download this Tool

    Data Handling and Remediation Competencies:

    • Data Standardization: Formatting values into consistent standards based on industry standards and business rules.
    • Data Cleansing: Modification of values to meet domain restrictions, integrity constraints, or other business rules for sufficient data quality for the organization.
    • Data Matching: Identification, linking, and merging related entries in or across sets of data.
    • Data Validation: Checking for correctness of the data.

    After these capabilities and competencies are assessed for a current and desired target state, the Data Quality Practice Assessment and Project Planning Tool will suggest improvement actions that should be followed in order to build your data quality practice. In addition, a roadmap will be generated after target dates are set to create your data quality practice development strategy.

    Benchmark current and identify target capabilities for your data quality practice

    1 hour

    Input

    • Current and desired data quality practices in the organization

    Output

    • Assessment of where the gaps lie in your data quality practice

    Materials

    • Data Quality Practice Assessment and Project Planning Tool

    Participants

    • Data Quality Project Lead
    • Business Line Representatives
    • Business Architects

    Use the Data Quality Practice Assessment and Project Planning Tool to evaluate the baseline and target capabilities of your practice in terms of how data quality is approached and executed.

    Download this Tool

    Instructions

    1. Invite the appropriate stakeholders to participate in this exercise. Examples:
      1. Business executives will have input in Tab 2
      2. Unique stakeholders: communications expert or executive advisors may have input
    2. On Tab 2: Practice Components, assess the current and target states of each capability on a scale of 1–5. Note: “Ad hoc” implies a capability is completed, but randomly, informally, and without a standardized method.

    These results will set the baseline against which you will monitor performance progress and keep track of improvements over time.

    Info-Tech Insight

    Focus on early alignment. Assessing capabilities within specific people’s job functions can naturally result in disagreement or debate, especially between business and IT people. Remind everyone that data quality should ultimately serve business needs wherever possible.

    Visualization improves the holistic understanding of where gaps exist in your data quality practice

    To enable deeper analysis on the results of your practice assessment, Tab 3: Data Quality Practice Scorecard in the Data Quality Practice Assessment and Project Planning Tool creates visualizations of the gaps identified in each of your practice capabilities and related data management practices. These diagrams serve as analysis summaries.

    Gap assessment of “Meeting Business Needs” capabilities

    The image shows a screen capture of the Gap assessment of 
“Meeting Business Needs” capabilities, with sample information filled in.

    Visualization of gap assessment of data quality practice capabilities

    The image shows a bar graph titled Data Quality Capabilities.

    1. Enhance your gap analyses by forming a relative comparison of total gaps in key practice capability areas, which will help in determining priorities.
    • Example: In Tab 2 compare your capabilities within “Policies, Procedures, and Standards.” Then in Tab 3, compare your overall capabilities in “Policies, Procedures, and Standards” versus “Empowering Technologies.”
  • Put these up on display to improve discussion in the gap analyses and prioritization sessions.
  • Improve the clarity and flow of your strategy template, final presentations, and summary documents by copying and pasting the gap assessment diagrams.
  • Before engaging in the data quality improvement project plan, receive signoff from IT regarding feasibility

    The final piece of the puzzle is to gain sign-off from IT.

    Hofstadter's law: It always takes longer than you expect, even when you take into account Hofstadter’s Law.

    This means that before engaging IT in data quality projects to fix the business units’ data in Phase 2, IT must assess feasibility of the data quality improvement plan. A feasibility analysis is typically used to review the strengths and weaknesses of the projects, as well as the availability of required skills and technologies needed to complete them. Use the following workflow to guide you in performing a feasibility analysis:

    Project evaluation process:

    Present capabilities

    • Operational Capabilities
    • System Capabilities
    • Schedule Capabilities
      • Summary of Evaluation Results
        • Recommendations/ modifications to the project plan

    Info-Tech Best Practice

    While the PMO identifies and coordinates projects, IT must determine how long and for how much.

    Conduct gap analysis sessions to review and prioritize the capability gaps

    1 hour

    Input

    • Current and Target State Assessment

    Output

    • Documented initiatives to help you get to the target state

    Materials

    • Data Quality Practice Assessment and Project Planning Tool

    Participants

    • Data Quality team
    • IT representatives

    Instructions

    • Analyze Gap Analysis Results – As a group, discuss the high-level results on Tab 3: Data Quality Practice Score. Discuss the implications of the gaps identified.
    • Do a line-item review of the gaps between current and target levels for each assessed capability by using Tab 2: Practice Components.
    • Brainstorm Alignment Strategies – Brainstorm the effort and activities that will be necessary to support the practice in building its capabilities to the desired target level. Ask the following questions:
      • What activities must occur to enable this capability?
      • What changes/additions to resources, process, technology, business involvement, and communication must occur?
    • Document Data Quality Initiatives – Turn activities into initiatives by documenting them in Tab 4. Data Quality Practice Roadmap. Review the initiatives and estimate the start and end dates of each one.
    • Continue to evaluate the assessment results in order to create a comprehensive set of data quality initiatives that support your practice in building capabilities.

    Download this Tool

    Create the organization’s data quality improvement strategy roadmap

    1 hour

    Input

    • Data quality practice gaps and improvement actions

    Output

    • Data quality practice improvement roadmap

    Materials

    • Data Quality Practice Assessment and Project Planning Tool

    Participants

    • Data Quality Project Lead
    • Business Executives
    • IT Executives
    • Business Architects

    Generating Your Roadmap

    1. Plan the sequence, starting time, and length of each initiative in the Data Quality Practice Assessment and Project Planning Tool.
    2. The tool will generate a Gantt chart based on the start and length of your initiatives.
    3. The Gantt chart is generated in Tab 4: Data Quality Practice Roadmap, and can be used to organize and ensure that all of the essential aspects of data quality are addressed.

    Use the Practice Roadmap to plan and improve data quality capabilities

    Download this Tool

    Info-Tech Best Practice

    To help get you started, Info-Tech has provided an extensive list of data quality improvement initiatives that are commonly undertaken by organizations looking to improve their data quality.

    Establish Baseline Metrics

    Baseline metrics will be improved through:

    2 hours

    Create practice-level metrics to monitor your data quality practice.

    Instructions:

    1. Establish metrics for both the business and IT that will be used to determine if the data quality practice development is effective.
    2. Set targets for each metric.
    3. Collect current data to calculate the metrics and establish a baseline.
    4. Assign an owner for tracking each metric to be accountable for performance.
    Metric Current Goal
    Usage (% of trained users using the data warehouse)
    Performance (response time)
    Performance (response time)
    Resource utilization (memory usage, number of machine cycles)
    User satisfaction (quarterly user surveys)
    Data quality (% values outside valid values, % fields missing, wrong data type, data outside acceptable range, data that violates business rules. Some aspects of data quality can be automatically tracked and reported)
    Costs (initial installation and ongoing, Total Cost of Ownership including servers, software licenses, support staff)
    Security (security violations detected, where violations are coming from, breaches)
    Patterns that are used
    Reduction in time to market for the data
    Completeness of data that is available
    How many "standard" data models are being used
    What is the extra business value from the data governance program?
    How much time is spent for data prep by BI & analytics team?

    Phase 2 summary

    As you improve your data quality practice and move from reactive to stable, don’t rest and assume that you can let data quality keep going by itself. Rapidly changing consumer requirements or other pains will catch up to your organization and you will fall behind again. By moving to the proactive and predictive end of the maturity scale, you can stay ahead of the curve. By following the methodology laid out in Phase 1, the data quality practices at your organization will improve over time, leading to the following results:

    Chaotic

    Before Data Quality Practice Improvements

    • No standards to data quality

    Reactive

    Year 1

    • Processes defined
    • Data cleansing approach to data quality

    Stable

    Year 2

    • Business rules/ stewardship in place
    • Education and training

    Proactive

    Year 3

    • Data quality practices fully in place and embedded in the culture
    • Trusted and intelligent enterprise

    (Global Data Excellence, Data Excellence Maturity Model)

    Phase 3

    Establish Your Organization’s Data Quality Program

    Build Your Data Quality Program

    Create a data lineage diagram to map the data journey and identify the data subject areas to be targeted for fixes

    It is important to understand the various data that exist in the business unit, as well as which data are essential to business function and require the highest degree of quality efforts.

    Visualize your databases and the flow of data. A data lineage diagram can help you and the Data Quality Improvement Team visualize where data issues lie. Keeping the five-tier architecture in mind, build your data lineage diagram.

    Reminder: Five-Tier Architecture

    The image shows the Five-Tier Architecture graphic.

    Use the following icons to represent your various data systems and databases.

    The image shows four icons. They are: the image of a square and a computer monitor, labelled Application; the image of two sheets of paper, labelled Desktop documents; the image of a green circle next to a computer monitor, labelled Web Application; and a blue cylinder labelled Database.

    Use Info-Tech’s Data Lineage Diagram to document the data sources and applications used by the business unit

    2 hours

    Input

    • Data sources and applications used by the business unit

    Output

    • Data lineage diagram

    Materials

    • Data Lineage Diagram Template

    Participants

    • Business Unit Head/Data Owner
    • Business Unit SMEs
    • Data Analysts/Architects

    Map the flow and location of data within a business unit by creating a system context diagram.

    Gain an accurate view of data locations and uses: Engage business users and representatives with a wide breadth of knowledge-related business processes and the use of data by related business operations.

    1. Sit down with key business representatives of the business unit.
    2. Document the sources of data and processes in which they’re involved, and get IT confirmation that the sources of the data are correct.
    3. Map out the sources and processes in a system context diagram.

    Download this Tool

    Sample Data Lineage Diagram

    The image shows a sample data lineage diagram, split into External Applications and Internal Applications, and showing the processes involved in each.

    Leverage Info-Tech’s Data Quality Practice Assessment and Project Planning Tool to document business context

    1 hour

    Input

    • Business vision, goals, and drivers

    Output

    • Business context for the data quality improvement project

    Materials

    • Data Quality Practice Assessment and Project Planning Tool

    Participants

    • Data Quality project lead
    • Business line representatives
    • IT executives

    Develop goals and align them with specific objectives to set the framework for your data quality initiatives.

    In the context of achieving business vision, mission, goals, and objectives and sustaining differentiators and key drivers, think about where and how data quality is a barrier. Then brainstorm data quality improvement objectives that map to these barriers. Document your list of objectives in Tab 5. Prioritize business units of the Data Quality Practice Assessment and Project Planning Tool.

    Establishing Business Context Example

    Healthcare Industry

    Vision To improve member services and make service provider experience more effective through improving data quality and data collection, aggregation, and accessibility for all the members.
    Goals

    Establish meaningful metrics that guide to the improvement of healthcare for member effectiveness of health care providers:

    • Data collection
    • Data harmonization
    • Data accessibility and trust by all constituents.
    Differentiator Connect service consumers with service providers, that comply with established regulations by delivering data that is accurate, trusted, timely, and easy to understand to connect service providers and eliminate bureaucracy and save money and time.
    Key Driver Seamlessly provide a healthcare for members.

    Download this Tool

    Document the identified business units and their associated data

    30 minutes

    Input

    • Business units

    Output

    • Documented business units to begin prioritization

    Materials

    • Data Quality Practice Assessment and Project Planning Tool

    Participants

    • Project Manager

    Instructions

    1. Using Tab 5: Prioritize Business Units of the Data Quality Practice Assessment and Project Planning Tool, document the business units that use data in the organization. This will likely be all business units in the organization.
    2. Next, document the primary data used by those business units.
    3. These inputs will then be used to assess business unit priority to generate a data quality improvement project roadmap.

    The image shows a screen capture of Tab 5: Prioritize Business Units, with sample information inputted.

    Reminder – Not every business unit requires the same standard of data quality

    To prioritize your business units for data quality improvement projects, you must analyze the relative importance of the data they use to the business. The more important the data is to the business, the higher the priority is of fixing that data. There are two measures for determining the importance of data: business value and business impact.

    Business Value of Data

    Business value of data can be evaluated by thinking about its ties to revenue generation for the organization, as well as how it is used for productivity and operations at the organization.

    The business value of data is assessed by asking what would happen to the following parameters if the data is not usable (due to poor quality, for example):

    • Loss of Revenue
    • Loss of Productivity
    • Increased Operating Costs

    Business Impact of Data

    Business impact of data should take into account the effects of poor data on both internal and external parties.

    The business impact of data is assessed by asking what the impact would be of bad data on the following parameters:

    • Impact on Customers
    • Impact on Internal Staff
    • Impact on Business Partners

    Value + Impact = Data Priority Score

    Assess the business unit priority order for data quality improvements

    2 hours

    Input

    • Assessment of value and impact of business unit data

    Output

    • Prioritization list for data quality improvement projects

    Materials

    • Data Quality Practice Assessment and Project Planning Tool

    Participants

    • Project Manager
    • Data owners

    Instructions

    Instructions In Tab 5: Prioritize Business Units of the Data Quality Practice Assessment and Project Planning Tool, assess business value and business impact of the data within each documented business unit.

    Use the ratings High, Medium, and Low to measure the financial, productivity, and efficiency value and impact of each business unit’s data.

    In addition to these ratings, assess the number of help desk tickets that are submitted to IT regarding data quality issues. This parameter is an indicator that the business unit’s data is high priority for data quality fixes.

    Download this Tool

    Create a business unit order roadmap for your data quality improvement projects

    1 hour

    Input

    • Rating of importance of data for each business unit

    Output

    • Roadmap for data quality improvement projects

    Materials

    • Data Quality Practice Assessment and Project Planning Tool

    Participants

    • Project Manager
    • Product Manager
    • Business line representatives

    Instructions

    After assessing the business units for the business value and business impact of their data, the Data Quality Practice Assessment and Project Planning Tool automatically assesses the prioritization of the business units based on your ratings. These prioritizations are then summarized in a roadmap on Tab 6: Data Quality Project Roadmap. The following is an example of a project roadmap:

    The image shows an example of a project roadmap, with three business units listed vertically along the left hand side, and a Gantt chart showing the time periods in which each Business Unit would work. At the bottom, a table shows the Length of the Project in days (100), and the start date for the first project.

    On Tab 6, insert the timeline for your data quality improvement projects, as well as the starting date of your first data quality project. The roadmap will automatically update with the chosen timing and dates.

    Download this Tool

    Identify metrics at the business unit level to track data quality improvements

    As you improve the data quality for specific business units, measuring the benefits of data quality improvements will help you demonstrate the value of the projects to the business.

    Use the following table to guide you in creating business-aligned metrics:

    Business Unit Driver Metrics Goal
    Sales Customer Intimacy Accuracy of customer data. Percent of missing or incomplete records. 10% decrease in customer record errors.

    Marketing

    Customer Intimacy Accuracy of customer data. Percent of missing or incomplete records. 10% decrease in customer record errors.
    Finance Operational Excellence Relevance of financial reports. Decrease in report inaccuracy complaints.
    HR Risk Management Accuracy of employee data. 10% decrease in employee record errors.
    Shipping Operational Excellence Timeliness of invoice data. 10% decrease in time to report.

    Info-Tech Insight

    Relating data governance success metrics to overall business benefits keeps executive management and executive sponsors engaged because they are seeing actionable results. Review metrics on an ongoing basis with those data owners/stewards who are accountable, the data governance steering committee, and the executive sponsors.

    Case Study

    Address data quality with the right approach to maximize the ROI

    EDC

    Industry: Government

    Source: Environment Development of Canada (EDC)

    Challenge

    Environment Development Canada (EDC) would initially identify data elements that are important to the business purely based on their business instinct.

    Leadership attempted to tackle the enterprise’s data issues by bringing a set of different tools into the organization.

    It didn’t work out because the fundamental foundational layer, which is the data and infrastructure, was not right – they didn't have the foundational capabilities to enable those tools.

    Solution

    Leadership listened to the need for one single team to be responsible for the data persistence.

    Therefore, the data platform team was granted that mandate to extensively execute the data quality program across the enterprise.

    A data quality team was formed under the Data & Analytics COE. They had the mandate to profile the data and to understand what quality of data needed to be achieved. They worked constantly with the business to build the data quality rules.

    Results

    EDC tackled the source of their data quality issues through initially performing a data quality management assessment with business stakeholders.

    From then on, EDC was able to establish their data quality program and carry out other key initiatives that prove the ROI on data quality.

    Begin your data quality improvement project starting with the highest priority business unit

    Now that you have a prioritized list for your data quality improvement projects, identify the highest priority business unit. This is the business unit you will work through Phase 3 with to fix their data quality issues.

    Once you have initiated and identified solutions for the first business unit, tackle data quality for the next business unit in the prioritized list.

    The image is a graphic labelled as Phase 2. On the left, there is a vertical arrow pointing upward labelled Priority of Business Units. Next to it, there are three boxes, with downward pointing arrows between them, each box labelled as each Business Unit's Data Quality Improvement Project. From there an arrow points right to a circle. Inside the circle are the steps necessary to complete the data quality improvement project.

    Create and document your data quality improvement team

    1 hour

    Input

    • Individuals who fit the data quality improvement plan team roles

    Output

    • Project team

    Materials

    • Data Quality Improvement Plan Template

    Participants

    • Data owner
    • Project Manager
    • Product Manager

    The Data Quality Improvement Plan is a concise document that should be created for each data quality project (i.e. for each business unit) to keep track of the project.

    Instructions

    1. Meet with the data owner of the business unit identified for the data quality improvement project.
    2. Identify individuals who fit the data quality improvement plan team roles.
    3. Using the Data Quality Improvement Plan Template to document the roles and individuals who will fit those roles.
    4. Have an introductory meeting with the Improvement team to clarify roles and responsibilities for the project.

    Download this Tool

    Team role Assigned to
    Data Owner [Name]
    Project Manager [Name]
    Business Analyst/BRM [Name]
    Data Steward [Name]
    Data Analyst [Name]

    Document the business context of the Data Quality Improvement Plan

    1 hour

    Input

    • Project team
    • Identified data attributes

    Output

    • Business context for the data quality improvement plan

    Materials

    • Data Quality Improvement Plan Template

    Participants

    • Data owner
    • Project Sponsor
    • Product owner

    Data quality initiatives have to be relevant to the business, and the business context will be used to provide inputs to the data improvement strategy. The context can then be used to determine exactly where the root causes of data quality issues are, which will inform your solutions.

    Instructions

    The business context of the data quality improvement plan includes documenting from previous activities:

    1. The Data Quality Improvement Team.
    2. Your Data Lineage Diagram.
    3. Your Data Quality Problem Statement.

    Info-Tech Best Practice

    While many organizations adopt data quality principles, not all organizations express them along the same terms. Have multiple perspectives within your organization outline principles that fit your unique data quality agenda. Anyone interested in resolving the day-to-day data quality issues that they face can be helpful for creating the context around the project.

    Download this tool

    Now that you have a defined problem, revisit the root causes of poor data quality

    You previously fleshed out the problem with data quality present in the business unit chosen as highest priority. Now it is time to figure out what is causing those problems.

    In the table below, you will find some of the common categories of causes of data quality issues, as well as some specific root causes.

    Category Description
    1. System/Application Design Ineffective, insufficient, or even incorrect system/application design accepts incorrect and missing data elements to the source applications and databases. The data records in those source systems may propagate into systems in tiers 2, 3, 4, and 5 of the 5-tier architecture, creating domino and ripple effects.
    2. Database design Database is created and modeled in an incorrect manner so that the management of the data records is incorrect, resulting in duplicated and orphaned records, and records that are missing data elements or records that contain incorrect data elements. Poor operational data in databases often leads to issues in tiers 2, 3, 4, and 5.
    3. Enterprise Integration Data or information is improperly integrated, transformed, masked, and aggregated in tier 2. In addition, some data integration tasks might not be timely, resulting in out-of-date data or even data that contradicts with other data. Enterprise integration is a precursor of loading a data warehouse and data marts. Issues in this layer affect tier 3, 4 and 5 on the 5-tier architecture.
    4. Policies and Procedures Policies and procedures are not effectively used to reinforce data quality. In some situations, policy gaps are found. In others, policies are overlapped and duplicated. Policies may also be out-of-date or too complex, affecting the users’ ability to interpret the policy objectives. Policies affect all tiers in the 5-tier architecture.
    5. Business Processes Improper business process design introduces poor data into the data systems. Failure to create processes around approving data changes, failure to document key data elements, and failure to train employees on the proper uses of data make data quality a burning problem.

    Leverage a root cause analysis approach to pinpoint the origins of your data issues

    A root cause analysis is a systematic approach to decompose a problem into its components. Use fishbone diagrams to help reveal the root causes of data issues.

    The image shows a fishbone diagram on the left, which starts with Process on the left, and then leads to Application and Integration, and then Database and Policies. This section is titled Root causes. The right hand section is titled Lead to problems with data... and includes 4 circles with the word or in between each. The circles are labelled: Completeness; Usability; Timeliness; Accessibility.

    Info-Tech recommends five root cause categories for assessing data quality issues:

    Application Design. Is the issue caused by human error at the application level? Consider internal employees, external partners/suppliers, and customers.

    Database Design. Is the issue caused by a particular database and stems from inadequacies in its design?

    Integration. Data integration tools may not be fully leveraged, or data matching rules may be poorly designed.

    Policies and Procedures. Do the issues take place because of lack of governance?

    Business Processes. Do the issues take place due to insufficient processes?

    For Example:

    When performing a deeper analysis of your data issues related to the accuracy of the business unit’s data, you would perform a root cause analysis by assessing the contribution of each of the five categories of data quality problem root causes:

    The image shows another fishbone diagram, with example information filled in. The first section on the left is titled Application Design, and includes the text: Data entry problems lead to incorrect accounting entries. The second is Integration, and includes the text: Data integration tools are not fully leveraged. The third section is Policies, and includes the text: No policy on standardizing name and address. The last section is Database design, with text that reads: Databases do not contain unique keys. The diagram ends with an arrow pointing right to a blue circle with Accuracy in it.

    Leverage a combination of data analysis techniques to identify and quantify root causes

    Info-Tech Insight

    Including all attributes of the key subject area in your data profiling activities may produce too much information to make sense of. Conduct data profiling primarily at the table level and undergo attribute profiling only if you are able to narrow down your scope sufficiently.

    Data Profiling Tool

    Data profiling extracts a sample of the target data set and runs it through multiple levels of analysis. The end result is a detailed report of statistics about a variety of data quality criteria (duplicate data, incomplete data, stale data, etc.).

    Many data profiling tools have built-in templates and reports to help you uncover data issues. In addition, they quantify the occurrences of the data issues.

    E-Discovery Tool

    This supplements a profiling tool. For Example, use a BI tool to create a custom grouping of all the invalid states (e.g. “CAL,” “AZN,” etc.) and visualize the percentage of invalid states compared to all states.

    SQL Queries

    This supplements a profiling tool. For example, use a SQL statement to group the customer data by customer segment and then by state to identify which segment–state combinations contain poor data.

    Identify the data issues for the particular business unit under consideration

    2 hours

    Input

    • Issues with data quality felt by the business unit
    • Data lineage diagram

    Output

    • Categorized data quality issues

    Materials

    • Whiteboard, markers, sticky notes
    • Data Quality Improvement Plan Template

    Participants

    • Data quality improvement project team
    • Business line representatives

    Instructions

    1. Gather the data quality improvement project team in a room, along with sticky notes and a whiteboard.
    2. Display your previously created data lineage diagram on the whiteboard.
    3. Using color-coded sticky notes, attach issues to each component of the data lineage diagram that team members can identify. Use different colors for the four quality attributes: Completeness, Usability, Timeliness, and Accessibility.

    Example:

    The image shows the data lineage diagram that has been shown in previous sections. In addition, the image shows 4 post-its arranges around the diagram, labelled: Usability; Completeness; Timeliness; and Accessibility.

    Map the data issues on fishbone diagrams to identify root causes

    1 hour

    Input

    • Categorized data quality issues

    Output

    • Completed fishbone diagrams

    Materials

    • Whiteboard, markers, sticky notes
    • Data Quality Improvement Plan Template

    Participants

    • Data quality improvement project team

    Now that you have data quality issues classified according to the data quality attributes, map these issues onto four fishbone diagrams.

    The image shows a fishbone diagram, which is titled Example: Root cause analysis diagram for data accuracy.

    Download this Tool

    Get to know the root causes behind system/application design mistakes

    Suboptimal system/application design provides entry points for bad data.

    Business Process
    Usually found in → Tier 1 Tier 2 Tier 3 Tier 4 Tier 5
    Issue Root Causes Usability Completeness Timeliness Accessibility
    Insufficient data mask No data mask is defined for a free-form text field in a user interface. E.g. North American phone number should have 4 masks – country code (1-digit), area code (3-digit), and local number (7-digit). X X
    Too many free-form text fields Incorrect use of free-form text fields (fields that accept a variety of inputs). E.g. Use a free-form text field for zip code instead of a backend look up. X X
    Lack of value lookup Reference data is not looked up from a reference list. E.g. State abbreviation is entered instead of being looked up from a standard list of states. X X
    Lack of mandatory field definitions Mandatory fields are not identified and reinforced. Resulting data records with many missing data elements. E.g. Some users may fill up 2 or 3 fields in a UI that has 20 non-mandatory fields. X

    The image shows a fishbone diagram, with the following sections, from left to right: Application Design; Integration; Processes; Policies; Database Design; Data Quality Measure. The Application Design section is highlighted.

    Get to know the root causes behind common database design mistakes

    Improper database design allows incorrect data to be stored and propagated.

    Business Process
    Usually found in → Tier 1 Tier 2 Tier 3 Tier 4 Tier 5
    Issue Root Causes Usability Completeness Timeliness Accessibility
    Incorrect referential integrity Referential integrity constraints are absent or incorrectly implemented, resulting in child records without parent records, or related records are updated or deleted in a cascading manner. E.g. An invoice line item is created before an invoice is created. X X
    Lack of unique keys Lack of unique keys creating scenarios where record uniqueness cannot be guaranteed. E.g. Customer records with the same customer_ID. X X
    Data range Fail to define a data range for incoming data, resulting in data values that are out of range. E.g. The age field is able to store an age of 999. X X
    Incorrect data type Incorrect data types are used to store data fields. E.g. A string field is used to store zip codes. Some users use that to store phone numbers, birthdays, etc. X X

    The image shows a fishbone diagram, with the following sections, from left to right: Application Design; Integration; Processes; Policies; Database Design; Data Quality Measure. The Database Design section is highlighted

    Get to know the root causes behind enterprise integration mistakes

    Improper data integration or synchronization may create poor analytical data.

    Business Process
    Usually found in → Tier 1 Tier 2 Tier 3 Tier 4 Tier 5
    Issue Root Causes Usability Completeness Timeliness Accessibility
    Incorrect transformation Transformation is done incorrectly. A wrong formula may have been used, transformation is done at the wrong data granularity, or aggregation logic is incorrect. E.g. Aggregation is done for all customers instead of just active customers. X X
    Data refresh is out of sync Data is synchronized at different intervals, resulting in a data warehouse where data domains are out of sync. E.g. Customer transactions are refreshed to reflect the latest activities but the account balance is not yet refreshed. X X
    Data is matched incorrectly Fail to match records from disparate systems, resulting in duplications and unmatched records. E.g. Unable to match customers from different systems because they have different cust_ID. X X
    Incorrect data mapping Fields from source systems are not properly matched with data warehouse fields. E.g. Status fields from different systems are mixed into one field. X X

    The image shows a fishbone diagram, with the following sections, from left to right: Application Design; Integration; Processes; Policies; Database Design; Data Quality Measure. The Integration section is highlighted

    Get to know the root causes behind policy and procedure mistakes

    Suboptimal policies and procedures undermine the effect of best practices.

    Business Process
    Usually found in → Tier 1 Tier 2 Tier 3 Tier 4 Tier 5
    Issue Root Causes Usability Completeness Timeliness Accessibility
    Policy Gaps There are gaps in the policy landscape in terms of some missing key policies or policies that are not refreshed to reflect the latest changes. E.g. A data entry policy is absent, leading to inconsistent data entry practices. X X
    Policy Communications Policies are in place but the policies are not communicated effectively to the organization, resulting in misinterpretation of policies and under-enforcement of policies. E.g. The data standard is created but very few developers are aware of its existence. X X
    Policy Enforcement Policies are in place but not proactively re-enforced and that leads to inconsistent application of policies and policy adoption. E.g. Policy adoption is dropping over time due to lack of reinforcement. X X
    Policy Quality Policies are written by untrained authors and they do not communicate the messages. E.g. A non-technical data user may find a policy that is loaded with technical terms confusing. X X

    The image shows a fishbone diagram, with the following sections, from left to right: Application Design; Integration; Processes; Policies; Database Design; Data Quality Measure. The Policies section is highlighted

    Get to know the root causes behind common business process mistakes

    Ineffective and inefficient business processes create entry points for poor data.

    Business Process
    Usually found in → Tier 1 Tier 2 Tier 3 Tier 4 Tier 5
    Issue Root Causes Usability Completeness Timeliness Accessibility
    Lack of training Key data personnel and business analysts are not trained in data quality and data governance, leading to lack of accountability. E.g. A data steward is not aware of downstream impact of a duplicated financial statement. X X
    Ineffective business process The same piece of information is entered into data systems two or more times. Or a piece of data is stalled in a data system for too long. E.g. A paper form is scanned multiple times to extract data into different data systems. X X
    Lack of documentation Fail to document the work flows of the key business processes. A lack of work flow results in sub-optimal use of data. E.g. Data is modeled incorrectly due to undocumented business logic. X X
    Lack of integration between business silos Business silos hold on to their own datasets resulting in data silos in which data is not shared and/or data is transferred with errors. E.g. Data from a unit is extracted as a data file and stored in a shared drive with little access. X X

    The image shows a fishbone diagram, with the following sections, from left to right: Application Design; Integration; Processes; Policies; Database Design; Data Quality Measure. The Processes section is highlighted

    Phase 3 Summary

    1. Data Lineage Diagram
    • Creating the data lineage diagram is recommended to help visualize the flow of your data and to map the data journey and identify the data subject areas to be targeted for fixes.
    • The data lineage diagram was leveraged multiple times throughout this Phase. For example, the data lineage diagram was used to document the data sources and applications used by the business unit
  • Business Context
    • Business context was documented through the Data Quality Practice Assessment and Project Planning Tool.
    • The same tool was used to document identified business units and their associated data.
    • Metrics were also identified at the business unit level to track data quality improvements.
  • Common Root Causes
    • Leverage a root cause analysis approach to pinpoint the origins of your data quality issues.
    • Analyzed and got to know the root causes behind the following:
      1. System/application design mistakes
      2. Common database design mistakes
      3. Enterprise integration mistakes
      4. Policies and procedures mistakes
      5. Common business processes mistakes
  • Phase 4

    Grow and Sustain Your Data Quality Program

    Build Your Data Quality Program

    For the identified root causes, determine the solutions for the problem

    As you worked through the previous step, you identified the root causes of your data quality problems within the business unit. Now, it is time to identify solutions.

    The following slides provide an overview of the solutions to common data quality issues. As you identify solutions that apply to the business unit being addressed, insert the solution tables in Section 4: Proposed Solutions of the Data Quality Improvement Plan Template.

    All data quality solutions have two components to them:

    • Technology
    • People

    For the next five data quality solution slides, look for the slider for the contributions of each category to the solution. Use this scale to guide you in creating solutions.

    When designing solutions, keep in mind that solutions to data quality problems are not mutually exclusive. In other words, an identified root cause may have multiple solutions that apply to it.

    For example, if an application is plagued with inaccurate data, the application design may be suboptimal, but also the process that leads to data being entered may need fixing.

    Data quality improvement strategy #1:

    Fix data quality issues by improving system/application design.

    Technology

    Application Interface Design

    Restrict field length – Capture only the characters you need for your application.

    Leverage data masks – Use data masks in standardized fields like zip code and phone number.

    Restrict the use of open text fields and use reference tables – Only present open text fields when there is a need. Use reference tables to limit data values.

    Provide options – Use radio buttons, drop-down lists, and multi-select instead of using open text fields.

    Data Validation at the Application Level

    Validate data before committing – Use simple validation to ensure the data entered is not random numbers and letters.

    Track history – Keep track of who entered what fields.

    Cannot submit twice – Only design for one-time submission.

    People

    Training

    Data-entry training – Training that is related to data entry, creating, or updating data records.

    Data resolution training – Training data stewards or other dedicated data personnel on how to resolve data records that are not entered properly.

    Continuous Improvement

    Standards – Develop application design principles and standards.

    Field testing – Field data entry with a few people to look for abnormalities and discrepancies.

    Detection and resolution – Abnormal data records should be isolated and resolved ASAP.

    Application Testing

    Thorough testing – Application design is your first line of defence against poor data. Test to ensure bad data is kept out of the systems.

    Case Study

    HMS

    Industry: Healthcare

    Source: Informatica

    Improve your data quality ingestion procedures to provide better customer intimacy for your users

    Healthcare Management Systems (HMS) provides cost containment services for healthcare sponsors and payers, and coordinates benefits services. This is to ensure that healthcare claims are paid correctly to both government agencies and individuals. To do so, HMS relies on data, and this data needs to be of high quality to ensure the correct decisions are made, the right people get the correct claims, and the appropriate parties pay out.

    To improve the integrity of HMS’s customer data, HMS put in place a framework that helped to standardize the collection of high volume and highly variable data.

    Results

    Working with a data quality platform vendor to establish a framework for data standardization, HMS was able to streamline data analysis and reduce new customer implementations from months to weeks.

    HMS data was plagued with a lack of standardization of data ingestion procedures.

    Before improving data quality processes After improving data quality processes
    Data Ingestion Data Ingestion
    Many standards of ingestion. Standardized data ingestion
    Data Storage Data Storage
    Lack of ability to match data, creating data quality errors.
    Data Analysis Data Analysis
    = =
    Slow Customer Implementation Time 50% Reduction in Customer Implementation Time

    Data quality improvement strategy #2:

    Fix data quality issues using proper database design.

    Technology

    Database Design Best Practices

    Referential integrity – Ensure parent/child relationships are maintained in terms of cascade creation, update, and deletion.

    Primary key definition – Ensure there is at least one key to guarantee the uniqueness of the data records, and primary key should not allow null.

    Validate data domain – Create triggers to check the data values entered in the database fields.

    Field type and length – Define the most suitable data type and length to hold field values.

    One-Time Data Fix (more on the next slide)

    Explore solutions – Where to fix the data issues? Is there a case to fix the issues?

    Running profiling tools to catch errors – Run scans on the database with defined criteria to identify occurrences of questionable data.

    Fix a sample before fixing all records – Use a proof-of-concept approach to explore fix options and evaluate impacts before fixing the full set.

    People

    The DBA Team

    Perform key tasks in pairs – Take a pair approach to perform key tasks so that validation and cross-check can happen.

    Skilled DBAs – DBAs should be certified and accredited.

    Competence – Assess DBA competency on an ongoing basis.

    Preparedness – Develop drills to stimulate data issues and train DBAs.

    Cross train – Cross train team members so that one DBA can cover another DBA.

    Data quality improvement strategy #3:

    Improve integration and synchronization of enterprise data.

    Technology

    Integration Architecture

    Info-Tech’s 5-Tier Architecture – When doing transformations, it is good practice to persist the integration results in tier 3 before the data is further refined and presented in tier 4.

    Timing, timing, and timing – Think of the sequence of events. You may need to perform some ETL tasks before other tasks to achieve synchronization and consistence.

    Historical changes – Ensure your tier 3 is robust enough to include historical data. You need to enable type 2 slowly, changing dimension to recreate the data at a point in time.

    Data Cleansing

    Standardize – Leverage data standardization to standardize name and address fields to improve matching and integration.

    Fuzzy matching – When there are no common keys between datasets. The datasets can only be matched by fuzzy matching. Fuzzy matching is not hard science; define a confidence level and think about a mechanism to deal with the unmatched.

    People

    Reporting and Documentations

    Business data glossary and data lineage – Define a business data glossary to enhance findability of key data elements. Document data mappings and ETL logics.

    Create data quality reports – Many ETL platforms provide canned data quality reports. Leverage those quality reports to monitor the data health.

    Code Review

    Create data quality reports – Many ETL platforms provide canned data quality reports. Leverage those quality reports to monitor the data health.

    ARB (architectural review board) – All ETL codes should be approved by the architectural review board to ensure alignment with the overall integration strategy.

    Data quality improvement strategy #4:

    Improve data quality policies and procedures.

    Technology

    Policy Reporting

    Data quality reports – Leverage canned data quality reports from the ETL platforms to monitor data quality on an on-going basis. When abnormalities are found, provoke the right policies to deal with the issues.

    Store policies in a central location that is well known and easy to find and access. A key way that technology can help communicate policies is by having them published on a centralized website.

    Make the repository searchable and easily navigable. myPolicies helps you do all this and more.

    myPolicies helps you do all this and more.

    Go to this link

    People

    Policy Review and Training

    Policy review – Create a schedule for reviewing policies on a regular basis – invite professional writers to ensure polices are understandable.

    Policy training – Policies are often unread and misread. Training users and stakeholders on policies is an effective way to make sure those users and stakeholders understand the rationale of the policies. It is also a good practice to include a few scenarios that are handled by the policies.

    Policy hotline/mailbox – To avoid misinterpretation of the policies, a policy hotline/mailbox should be set up to answer any data policy questions from the end users/stakeholders.

    Policy Communications

    Simplified communications – Create handy one-pagers and infographic posters to communicate the key messages of the polices.

    Policy briefing – Whenever a new data project is initiated, a briefing of data policies should be given to ensure the project team follows the policies from the very beginning.

    Data quality improvement strategy #5:

    Streamline and optimize business processes.

    Technology

    Requirements Gathering

    Data Lineage – Leverage a metadata management tool to construct and document data lineage for future reference.

    Documentations Repository – It is a best practice to document key project information and share that knowledge across the project team and with the stakeholder. An improvement understanding of the project helps to identify data quality issues early on in the project.

    “Automating creation of data would help data quality most. You have to look at existing processes and create data signatures. You can then derive data off those data codes.” – Patrick Bossey, Manager of Business Intelligence, Crawford and Company

    People

    Requirements Gathering

    Info-Tech’s 4-Column Model – The datasets may exist but the business units do not have an effective way of communicating the quality needs. Use our four-column model and the eleven supporting questions to better understand the quality needs. See subsequent slides.

    I don’t know what the data means so I think the quality is poor – It is not uncommon to see that the right data presented to the business but the business does not trust the data. They also do not understand the business logic done on the data. See our Business Data Glossary in subsequent slides.

    Understand the business workflow – Know the business workflow to understand the manual steps associated with the workflow. You may find steps in which data is entered, manipulated, or consumed inappropriately.

    “Do a shadow data exercise where you identify the human workflows of how data gets entered, and then you can identify where data entry can be automated.” – Diraj Goel, Growth Advisor, BC Tech

    Brainstorm solutions to your data quality issues

    4 hours

    Input

    • Data profiling results
    • Preliminary root cause analyses

    Output

    • Proposals for data fix
    • Fixed issues

    Materials

    • Data Quality Improvement Plan Template

    Participants

    • Business and Data Analysts
    • Data experts and stewards

    After walking through the best-practice solutions to data quality issues, propose solutions to fix your identified issues.

    Instructions

    1. Review Root Cause Analyses: Revisit the root cause analysis and data lineage diagram you have generated in Step 3.2. to understand the issues in greater details.
    2. Characterize Each Issue: You may need to generate a data profiling report to characterize the issue. The report can be generated by using data quality suites, BI platforms, or even SQL statements.
    3. Brainstorm the Solutions: As a group, discuss potential ways to fix the issue. You can tackle the issues by approaching from these areas:
    Solution Approaches
    Technology Approach
    People Approach

    X crossover with

    Problematic Areas
    Application/System Design
    Database Design
    Data Integration and Synchronization
    Policies and Procedures
    Business Processes
    1. Document and Communicate: Document the solutions to your data issues. You may need to reuse or refer to the solutions. Also brainstorm some ideas on how to communicate the results back to the business.

    Download this Tool

    Sustaining your data quality requires continuous oversight through a data governance practice

    Quality data is the ultimate outcome of data governance and data quality management. Data governance enables data quality by providing the necessary oversight and controls for business processes in order to maintain data quality. There are three primary groups (at right) that are involved in a mature governance practice. Data quality should be tightly integrated with all of them.

    Define an effective data governance strategy and ensure the strategy integrates well with data quality with Info-Tech’s Establish Data Governance blueprint.

    Visit this link

    Data Governance Council

    This council establishes data management practices that span across the organization. This should be comprised of senior management or C-suite executives that can represent the various departments and lines of business within the organization. The data governance council can help to promote the value of data governance, facilitate a culture that nurtures data quality, and ensure that the goals of the data governance program are well aligned with business objectives.

    Data Owners

    Identifying the data owner role within an organization helps to create a greater degree of accountability for data issues. They often oversee how the data is being generated as well as how it is being consumed. Data owners come from the business side and have legal rights and defined control over a data set. They ensure data is available to the right people within the organization.

    Data Stewards

    Conflict can occur within an organization’s data governance program when a data steward’s role is confused with that of the steering committee’s role. Data stewards exist to enforce decisions made about data governance and data management. Data stewards are often business analysts or power users of a particular system/dataset. Where a data owner is primarily responsible for access, a data steward is responsible for the quality of a dataset.

    Integrate the data quality management strategy with existing data governance committees

    Ongoing and regular data quality management is the responsibility of the data governance bodies of the organization.

    The oversight of ongoing data quality activities rests on the shoulders of the data governance committees that exist in the organization.

    There is no one-size-fits-all data governance structure. However, most organizations follow a similar pattern when establishing committees, councils, and cross-functional groups. They strive to identify roles and responsibilities at a strategic, tactical, and operational level:

    The image shows a pyramid, with Executive Sponsors at the top, with the following roles in descending order: DG Council; Steering Committee; Working Groups; Data Owners and Data Stewards; and Data Users. Along the left side of the pyramid, there are three labels, in ascending order: Operational, Tactical, and Strategic.

    The image is a flow chart showing project roles, in two sections: the top section is labelled Governing Bodies, and the lower section is labelled Data Quality Improvement Team. There is a note indicating that the Data Owner reports to and provides updates regarding the state of data quality and data quality initiatives.

    Create and update the organization’s Business Data Glossary to keep up with current data definitions

    2 hours

    Input

    • Metrics and goals for data quality

    Output

    • Regularly scheduled data quality checkups

    Materials

    • Business Data Glossary Template
    • Data Quality Dashboard

    Participants

    • Data steward

    A crucial aspect of data quality and governance is the Business Data Glossary. The Business Data Glossary helps to align the terminology of the business with the organization’s data assets. It allows the people who interact with the data to quickly identify the applications, processes, and stewardship associated with it, which will enhance the accuracy and efficiency of searches for organization data definitions and attributes, enabling better access to the data. This will, in turn, enhance the quality of the organization’s data because it will be more accurate, relevant, and accessible.

    Use the Business Data Glossary Template to document key aspects of the data, such as:

    • Definition
    • Source System
    • Possible Values
    • Data Steward
    • Data Sensitivity
    • Data Availability
    • Batch or Live
    • Retention

    Data Element

    • Mkt-Product
    • Fin-Product

    Info-Tech Insight

    The Business Data Glossary ensures that the crucial data that has key business use by key business systems and users is appropriately owned and defined. It also establishes rules that lead to proper data management and quality to be enforced by the data owners.

    Download this Tool

    Data Steward(s): Use the Data Quality Improvement Plan of the business unit for ongoing quality monitoring

    Integrating your data quality strategy into the organization’s data governance program requires passing the strategy over to members of the data governance program. The data steward role is responsible for data quality at the business unit level, and should have been involved with the creation and implementation of the data quality improvement project. After the data quality repairs have been made, it is the responsibility of the data steward to regularly monitor the quality of the business unit’s data.

    Create Improvement Plan ↓
    • Data Quality Improvement Team identifies root cause issues.
    • Brainstorm solutions.
    Implement Improvement Plan ↓
    • Data Quality Improvement Team works with IT.
    Sustain Improvement Plan
    • Data Steward should regularly monitor data quality.

    Download this tool

    See Info-Tech’s Data Steward Job Description Template for a detailed understanding of the roles and responsibilities of the data steward.

    Responsible for sustaining

    The image shows a screen capture of a document entitled Business Context & Subject Area Selection.

    Develop a business-facing data quality dashboard to show improvements or a sudden dip in data quality

    One tool that the data steward can take advantage of is the data quality dashboard. Initiatives that are implemented to address data quality must have metrics defined by business objectives in order to demonstrate the value of the data quality improvement projects. In addition, the data steward should have tools for tracking data quality in the business unit to report issues to the data owner and data governance steering committee.

    • Example 1: Marketing uses data for direct mail and e-marketing campaigns. They care about customer data in particular. Specifically, they require high data quality in attributes such as customer name, address, and product profile.
    • Example 2: Alternatively, Finance places emphasis on financial data, focusing on attributes like account balance, latency in payment, credit score, and billing date.

    The image is Business dashboard on Data Quality for Marketing. It features Data Quality metrics, listed in the left column, and numbers for each quarter over the course of one year, on the right.

    Notes on chart:

    General improvement in billing address quality

    Sudden drop in touchpoint accuracy may prompt business to ask for explanations

    Approach to creating a business-facing data quality dashboard:

    1. Schedule a meeting with the functional unit to discuss what key data quality metrics are essential to their business operations. You should consider the business context, functional area, and subject area analyses you completed in Phase 1 as a starting point.
    2. Discuss how to gather data for the key metrics and their associated calculations.
    3. Discuss and decide the reporting intervals.
    4. Discuss and decide the unit of measurement.
    5. Generate a dashboard similar to the example. Consider using a BI or analytics tool to develop the dashboard.

    Data quality management must be sustained for ongoing improvements to the organization’s data

    • Data quality is never truly complete; it is a set of ongoing processes and disciplines that requires a permanent plan for monitoring practices, reviewing processes, and maintaining consistent data standards.
    • Setting the expectation to stakeholders that a long-term commitment is required to maintain quality data within the organization is critical to the success of the program.
    • A data quality maintenance program will continually revise and fine-tune ongoing practices, processes, and procedures employed for organizational data management.

    Data quality is a program that requires continual care:

    →Maintain→Good Data →

    Data quality management is a long-term commitment that shifts how an organization views, manages, and utilizes its corporate data assets. Long-term buy-in from all involved is critical.

    “Data quality is a process. We are trying to constantly improve the quality over time. It is not a one-time fix.” – Akin Akinwumi, Manager of Data Governance, Startech.com

    Define a data quality review agenda for data quality sustainment

    2 hours

    Input

    • Metrics and goals for data quality

    Output

    • Regularly scheduled data quality checkups

    Materials

    • Data Quality Diagnostic
    • Data Quality Dashboard

    Participants

    • Data Steward

    As a data steward, you are responsible for ongoing data quality checks of the business unit’s data. Define an improvement agenda to organize the improvement activities. Organize the activities yearly and quarterly to ensure improvement is done year-round.

    Quarterly

    • Measure data quality metrics against milestones. Perform a regular data quality health check with Info-Tech’s Data Quality Diagnostic.
    • Review the business unit’s Business Data Glossary to ensure that it is up to date and comprehensive.
    • Assess progress of practice area initiatives (time, milestones, budget, benefits delivered).
    • Analyze overall data quality and report progress on key improvement projects and corrective actions in the executive dashboard.
    • Communicate overall status of data quality to oversight body.

    Annually

    • Calculate your current baseline and measure progress by comparing it to previous years.
    • Set/revise quality objectives for each practice area and inter-practice hand-off processes.
    • Re-evaluate/re-establish data quality objectives.
    • Set/review data quality metrics and tracking mechanisms.
    • Set data quality review milestones and timelines.
    • Revisit data quality training from an end-user perspective and from a practitioner perspective.

    Info-Tech Insight

    Do data quality diagnostic at the beginning of any improvement plan, then recheck health with the diagnostic at regular intervals to see if symptoms are coming back. This should be a monitoring activity, not a data quality fixing activity. If symptoms are bad enough, repeat the improvement plan process.

    Take the next step in your Data & Analytics Journey

    After establishing your data quality program, look to increase your data & analytics maturity.

    • Artificial Intelligence (AI) is a concept that many organizations strive to implement. AI can really help in areas such as data preparation. However, implementing AI solutions requires a level of maturity that many organizations are not at.
    • While a solid data quality foundation is essential for AI initiatives being successful, AI can also ensure high data quality.
    • An AI analytics solution can address data integrity issues at the earliest point of data processing, rapidly transforming these vast volumes of data into trusted business information. This can be done through Anomaly detection, which flags “bad” data, identifying suspicious anomalies that can impact data quality. By tracking and evaluating data, anomaly detection gives critical insights into data quality as data is processed. (Ira Cohen, The End to a Never-Ending Story? Improve Data Quality with AI Analytics, anodot, 2020)

    Consider… “Garbage in, garbage out.”

    Lay a solid foundation by addressing your data quality issues prior to investing heavily in an AI solution.

    Related Info-Tech Research

    Are You Ready for AI?

    • Use AI as a compelling event to expedite funding, resources, and project plans for your data-related initiatives. Check out this note to understand what it takes to be ready to implement AI solutions.

    Get Started With Artificial Intelligence

    • Current AI technology is data-enabled, automated, adaptive decision support. Once you believe you are ready for AI, check out this blueprint on how to get started.

    Build a Data Architecture Roadmap

    • The data lineage diagram was a key tool used in establishing your data quality program. Check out this blueprint and learn how to optimize your data architecture to provide greatest value from data.

    Create an Architecture for AI

    • Build your target state architecture from predefined best practice building blocks. This blueprint assists members first to assess if they have the maturity to embrace AI in their organization, and if so, which AI acquisition model fits them best.

    Phase 4 Summary

    1. Data Quality Improvement Strategy
    • Brainstorm solutions to your data quality issues using the following data quality improvement strategies as a guide:
      1. Fix data quality issues by improving system/application design
      2. Fix data quality issues using proper database design
      3. Improve integration and synchronization of enterprise data
      4. Improve data quality policies and procedures
      5. Streamline and optimize business processes
  • Sustain Your Data Quality Program
    • Quality data is the ultimate outcome of data governance and data quality management.
    • Sustaining your data quality requires continuous oversight through a data governance practice.
    • There are three primary groups (Data Governance Council, Data Owners, and Data Stewards) that are involved in a mature governance practice.
  • Grow Your Data & Analytics Maturity
    • After establishing your data quality program, take the next step in increasing your data & analytics maturity.
    • Good data quality is the foundation of pursuing different ways of maximizing the value of your data such as implementing AI solutions.
    • Continue your data & analytics journey by referring to Info-Tech’s quality research.
  • Research Contributors and Experts

    Izabela Edmunds

    Information Architect Mott MacDonald

    Akin Akinwumi

    Manager of Data Governance Startech.com

    Diraj Goel

    Growth Advisor BC Tech

    Sujay Deb

    Director of Data Analytics Technology and Platforms Export Development Canada

    Asif Mumtaz

    Data & Solution Architect Blue Cross Blue Shield Association

    Patrick Bossey

    Manager of Business Intelligence Crawford and Company

    Anonymous Contributors

    Ibrahim Abdel-Kader

    Research Specialist Info-Tech Research Group

    Ibrahim is a Research Specialist at Info-Tech Research Group. In his career to date he has assisted many clients using his knowledge in process design, knowledge management, SharePoint for ECM, and more. He is expanding his familiarity in many areas such as data and analytics, enterprise architecture, and CIO-related topics.

    Reddy Doddipalli

    Senior Workshop Director Info-Tech Research Group

    Reddy is a Senior Workshop Director at Info-Tech Research Group, focused on data management and specialized analytics applications. He has over 25 years of strong industry experience in IT leading and managing analytics suite of solutions, enterprise data management, enterprise architecture, and artificial intelligence–based complex expert systems.

    Andy Neill

    Practice Lead, Data & Analytics and Enterprise Architecture Info-Tech Research Group

    Andy leads the data and analytics and enterprise architecture practices at ITRG. He has over 15 years of experience in managing technical teams, information architecture, data modeling, and enterprise data strategy. He is an expert in enterprise data architecture, data integration, data standards, data strategy, big data, and development of industry standard data models.

    Crystal Singh

    Research Director, Data & Analytics Info-Tech Research Group

    Crystal is a Research Director at Info-Tech Research Group. She brings a diverse and global perspective to her role, drawing from her professional experiences in various industries and locations. Prior to joining Info-Tech, Crystal led the Enterprise Data Services function at Rogers Communications, one of Canada’s leading telecommunications companies.

    Igor Ikonnikov

    Research Director, Data & Analytics Info-Tech Research Group

    Igor is a Research Director at Info-Tech Research Group. He has extensive experience in strategy formation and execution in the information management domain, including master data management, data governance, knowledge management, enterprise content management, big data, and analytics.

    Andrea Malick

    Research Director, Data & Analytics Info-Tech Research Group

    Andrea Malick is a Research Director at Info-Tech Research Group, focused on building best practices knowledge in the enterprise information management domain, with corporate and consulting leadership in enterprise architecture and content management (ECM).

    Natalia Modjeska

    Research Director, Data & Analytics Info-Tech Research Group

    Natalia Modjeska is a Research Director at Info-Tech Research Group. She advises members on topics related to AI, machine learning, advanced analytics, and data science, including ethics and governance. Natalia has over 15 years of experience in developing, selling, and implementing analytical solutions.

    Rajesh Parab

    Research Director, Data & Analytics Info-Tech Research Group

    Rajesh Parab is a Research Director at Info-Tech Research Group. He has over 20 years of global experience and brings a unique mix of technology and business acumen. He has worked on many data-driven business applications. In his previous architecture roles, Rajesh created a number of product roadmaps, technology strategies, and models.

    Bibliography

    Amidon, Kirk. "Case Study: How Data Quality Has Evolved at MathWorks." The Fifth MIT Information Quality Industry Symposium. 13 July 2011. Web. 19 Aug. 2015.

    Boulton, Clint. “Disconnect between CIOs and LOB managers weakens data quality.” CIO. 05 February 2016. Accessed June 2020.

    COBIT 5: Enabling Information. Rolling Meadows, IL: ISACA, 2013. Web.

    Cohen, Ira. “The End to a Never-Ending Story? Improve Data Quality with AI Analytics.” anodot. 2020.

    “DAMA Guide to the Data Management Body of Knowledge (DAMA-DMBOK Guide).” First Edition. DAMA International. 2009. Digital. April 2014.

    "Data Profiling: Underpinning Data Quality Management." Pitney Bowes. Pitney Bowes - Group 1 Software, 2007. Web. 18 Aug. 2015.

    Data.com. “Data.com Clean.” Salesforce. 2016. Web. 18 Aug. 2015.

    “Dawn of the CDO." Experian Data Quality. 2015. Web. 18 Aug. 2015.

    Demirkan, Haluk, and Bulent Dal. "Why Do So Many Analytics Projects Fail?" The Data Economy: Why Do so Many Analytics Projects Fail? Analytics Magazine. July-Aug. 2014. Web.

    Dignan, Larry. “CIOs juggling digital transformation pace, bad data, cloud lock-in and business alignment.” ZDNet. 11 March 2020. Accessed July.

    Dumbleton, Janani, and Derek Munro. "Global Data Quality Research - Discussion Paper 2015." Experian Data Quality. 2015. Web. 18 Aug. 2015.

    Eckerson, Wayne W. "Data Quality and the Bottom Line - Achieving Business Success through a Commitment to High Quality Data." The Data Warehouse Institute. 2002. Web. 18 Aug. 2015.

    “Infographic: Data Quality in BI the Costs and Benefits.” HaloBI. 2015 Web.

    Lee, Y.W. and Strong, D.M. “Knowing-Why About Data Processes and Data Quality.” Journal of Management Information Systems. 2004.

    “Making Data Quality a Way of Life.” Cognizant. 2014. Web. 18 Aug. 2015.

    "Merck Serono Achieves Single Source of Truth with Comprehensive RIM Solutions." www.productlifegroup.com. ProductLife Group. 15 Apr. 2015. Web. 23 Nov. 2015.

    Myers, Dan. “List of Conformed Dimensions of Data Quality.” Conformed Dimensions of Data Quality (CDDQ). 2019. Web.

    Redman, Thomas C. “Make the Case for Better Data Quality.” Harvard Business Review. 24 Aug. 2012. Web. 19 Aug. 2015.

    RingLead Data Management Solutions. “10 Stats About Data Quality I Bet You Didn’t Know.” RingLead. Accessed 7 July 2020.

    Schwartzrock, Todd. "Chrysler's Data Quality Management Case Study." Online video clip. YouTube. 21 April. 2011. Web. 18 Aug. 2015

    “Taking control in the digital age.” Experian Data Quality. Jan 2019. Web.

    “The data-driven organization, a transformation in progress.” Experian Data Quality. 2020. Web.

    "The Data Quality Benchmark Report." Experian Data Quality. Jan. 2015. Web. 18 Aug. 2015.

    “The state of data quality.” Experian Data Quality. Sept. 2013. Web. 17 Aug. 2015.

    Vincent, Lanny. “Differentiating Competence, Capability and Capacity.” Innovation Management Services. Web. June 2008.

    “7 ways poor data quality is costing your business.” Experian Data Quality. July 2020. Web.

    Enter Into Mobile Development Without Confusion and Frustration

    • Buy Link or Shortcode: {j2store}282|cart{/j2store}
    • member rating overall impact: N/A
    • member rating average dollars saved: N/A
    • member rating average days saved: N/A
    • Parent Category Name: Mobile Development
    • Parent Category Link: /mobile-development
    • IT managers don’t know where to start when initiating a mobile program.
    • IT has tried mobile development in the past but didn't achieve success.
    • IT must initiate a mobile program quickly based on business priorities and needs a roadmap based on best practices.

    Our Advice

    Critical Insight

    • Form factors and mobile devices won't drive success – business alignment and user experience will. Don't get caught up with the latest features in mobile devices.
    • Software emulation testing is not true testing. Get on the device and run your tests.
    • Cross form-factor testing cannot be optimized to run in parallel. Therefore, anticipate longer testing cycles for cross form-factor testing.

    Impact and Result

    • Prepare your development, testing, and deployment teams for mobile development.
    • Get a realistic assessment of ROI for the launch of a mobile program.

    Enter Into Mobile Development Without Confusion and Frustration Research & Tools

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    1. Make the Case for a Mobile Program

    Understand the current mobile ecosystem. Use this toolkit to help you initiate a mobile development program.

    • Storyboard: Enter Into Mobile Development Without Confusion and Frustration

    2. Assess Your Dev Process for Readiness

    Review and evaluate your current application development process.

    3. Prepare to Execute Your Mobile Program

    Prioritize your mobile program based on your organization’s prioritization profile.

    • Mobile Program Tool

    4. Communicate with Stakeholders

    Summarize the execution of the mobile program.

    • Project Status Communication Worksheet
    [infographic]

    Workshop: Enter Into Mobile Development Without Confusion and Frustration

    Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.

    1 Build your Future Mobile Development State

    The Purpose

    Understand the alignment of stakeholder objectives and priorities to mobile dev IT drivers.

    Assess readiness of your organization for mobile dev.

    Understand how to build your ideal mobile dev process.

    Key Benefits Achieved

    Identify and address the gaps in your existing app dev process.

    Build your future mobile dev state.

    Activities

    1.1 Getting started

    1.2 Assess your current state

    1.3 Establish your future state

    Outputs

    List of key stakeholders

    Stakeholder and IT driver mapping and assessment of current app dev process

    List of practices to accommodate mobile dev

    2 Prepare and Execute your Mobile Program

    The Purpose

    Assess the impact of mobile dev on your existing app dev process.

    Prioritize your mobile program.

    Understand the dev practice metrics to gauge success.

    Key Benefits Achieved

    Properly prepare for the execution of your mobile program.

    Calculate the ROI of your mobile program.

    Prioritize your mobile program with dependencies in mind.

    Build a communication plan with stakeholders.

    Activities

    2.1 Conduct an impact analysis

    2.2 Prepare to execute

    2.3 Communicate with stakeholders

    Outputs

    Impact analysis of your mobile program and expected ROI

    Mobile program order of execution and project dependencies mapping

    List of dev practice metrics

    IT Strategy

    • Buy Link or Shortcode: {j2store}20|cart{/j2store}
    • Related Products: {j2store}20|crosssells{/j2store}
    • Up-Sell: {j2store}20|upsells{/j2store}
    • member rating overall impact: 9.3/10
    • member rating average dollars saved: $105,465
    • member rating average days saved: 35
    • Parent Category Name: Strategy and Governance
    • Parent Category Link: strategy-and-governance
    Success depends on IT initiatives clearly aligned to business goals.

    Requirements Gathering

    • Buy Link or Shortcode: {j2store}49|cart{/j2store}
    • Related Products: {j2store}49|crosssells{/j2store}
    • member rating overall impact: 9.5/10
    • member rating average dollars saved: $33,901
    • member rating average days saved: 23
    • Parent Category Name: Project Portfolio Management and Projects
    • Parent Category Link: /ppm-and-projects

    The challenge

    • The number reason projects fail because from the outset, what people wanted was not clear.
    • Without proper due diligence, IT will deliver projects that fail to meet business expectations and fail to provide business value.
    • If you failed to accurately capture the needs and desires, your projects are set up for costly rework. That will hurt your business's financial performance and result in damage to your relationship with your business partners.
    • Even with requirements gathering processes in place, your business analysts may not have the required competencies to execute them.

    Our advice

    Insight

    • You need to gather requirements with your organizations' end-state in mind. That requires IT and business alignment.
    • You would be good to create a set of standard operating procedures around requirements gathering. But many companies fail to do so.
    • Bring standardization and conformity to your requirements gathering processes via a centralized center of excellence. That brings cohesion and uniformity to your practice.
    • It is critical that your business analysts have the necessary competencies to execute your processes and that they ask the right questions.

    Impact and results 

    • Better requirements analysis will result in shorter cycle timed and reduced project rework and overhead.
    • You will enjoy better relationships with your business partners, greater stakeholder satisfaction, and gradually a better standing of IT.
    • Most importantly, the applications and systems you deliver will contain all must-haves and some nice-to-haves. Your minimal viable deliverable will start to create business value immediately.

    The roadmap

    Besides the small introduction, subscribers and consulting clients within this management domain have access to:

    Get started.

    Read our executive brief to understand why you should invest in optimizing requirements gathering in your company. We show you how we can support you.

    Build the target state

    Fully understand the target needs of the requirements gathering process.

    • Build a Strong Approach to Business Requirements Gathering – Phase 1: Build the Target State for the Requirements Gathering Process (ppt)
    • Requirements Gathering SOP and BA Playbook (doc)
    • Requirements Gathering Maturity Assessment (xls)
    • Project Level Selection Tool (xls)
    • Business Requirements Analyst (doc)
    • Requirements Gathering Communication Tracking Template (xls)

    Develop best practices to gather business requirements

    • Build a Strong Approach to Business Requirements Gathering – Phase 2: Define the Elicitation Process (ppt)
    • Business Requirements Document Template (xls)
    • Scrum Documentation Template (doc)

    Analyze and validate requirements

    Standardize your frameworks for analysis and validation of the business requirements

    • Build a Strong Approach to Business Requirements Gathering – Phase 3: Analyze and Validate Requirements (ppt)
    • Requirements Gathering Documentation Tool (xls)
    • Requirements Gathering Testing Checklist (doc)

    Build your requirements gathering governance action plan

    Formalize governance.

    • Build a Strong Approach to Business Requirements Gathering – Phase 4: Create a Requirements Governance Action Plan (ppt)
    • Requirements Traceability Matrix (xls)


    This site and all contents is © 2026 Tymans Group BV